Archive · UK and Ireland

2nd CISO 360 UK

This event took place on 28–29 April 2026 at Sheraton Grand Hotel & Spa, Edinburgh.

Date28–29 April 2026
VenueSheraton Grand Hotel & Spa, Edinburgh

Many thanks for joining the 2nd CISO 360 UK, 28-29 April 2026, hosted at the Sheraton Grand Hotel & Spa Edinburgh, Scotland.

  • “I found it really insightful, to see and hear from so many CISOs was great” James Hardy, Senior Security Assurance Manager, OVO Energy
  • “One of the most insightful conferences for security professionals, focusing on top class sessions and panels, embedding vendors to provide actual knowledge rather than sales pitches” Danielle Sudai, Security Operations and Automation Manager, Deliveroo
  • “Pulse conferences provide a very well-rounded event and great Speakers, great location and relevant vendors” Lee Morton, Head of Cyber Security, GBG plc
  • “CISO 360 UKI was one of the most valuable cybersecurity events I’ve attended. What stood out was the quality of conversation. Honest, practical, and grounded in real-world experience. No noise, no generic messaging, just leaders sharing what is actually happening inside organisations today. The panel discussions, particularly around security team morale and resilience, reflected challenges many of us are facing. It created space for open dialogue on prioritisation, leadership, and how we build sustainable security functions. The networking was equally strong. Meaningful conversations with peers, new connections, and shared insights that extend beyond the event itself. A well-run event that brings the right people together to focus on what matters. My biggest takeaway was the importance of decision clarity. Security teams are not only stretched by workload, but by unclear priorities and ownership. The organisations that are making progress are the ones aligning security with business outcomes and making deliberate, informed risk decisions.” Malcolm Kafesu, Global IT Security & Governance Manager, Ontic Engineering & Manufacturing
  • “The conference was a congregation of true leadership across the speaker and attendees. Vendors were respectful of the ethos of the event and supported having thought-provoking conversations. The presentations were engaging, well-balanced, and covered a large breath of relevant and timely topics. This was a wonderful conference with the attendees made to feel valued and included throughout the event. The overwhelming unity of the collective community, and joint appreciation to resilience being key.” Margus Lind, Vulnerability Management and Assurance Lead, Tesco Bank / Barclays

View Photo Gallery 2026Download Post- Event Presentation materials📅 Agenda 2026Reports and White PapersTestimonials 

Key Themes (partial list, in research)

  1. AI + Quantum: Prepare for the new frontiers in security
  2. Operational Resilience: First-hand experiences of DORA compliance and surviving and thriving in complex and interconnected threat and regulatory landscapes
  3. Threat Intelligence + Fusion: Leveraging converging trends, challenges and opportunities
  4. CISO GRC Toolkit: Critical updates. What to work towards? How Are We Strengthening the Foundations
  5. Supply Chain Security: Navigating risks in an interconnected world

Why Attend?

  • Stay future-focused on AI risks, roles and opportunities: Gain insights to stay ahead of business and technology challenges outside of your immediate sphere.
  • Benchmark with CISOs and cybersecurity practitioners by key verticals: FinSec, EnergySec..
  • Build trusted connections: Progress thought-leadership with leading CISOs and senior practitioners from the UK and Ireland in a trusted, secure environment.
  • Engage in collaborative projects: Participate in dynamic discussions and projects with innovators, investors, and thought leaders.

Be part of this landmark event and leave inspired, connected, and ready to elevate your cybersecurity strategy.

Agenda-at-a-Glance

Day One, Tuesday 28 April 2026

  • 12:30-13:00: Welcome Lunch
  • 13:00-15:45: CISO 360 UK Conference
  • 15:45-23:00: Edinburgh Evening Experience – Networking Activities
    • 16:00-17:00: Drinks at The Sheraton Grand Hotel- One Square bar and terrace
    • 17:00-18:30: Haunted Vault Tour
    • 19:00-23:00: Dinner at the National Museum of Scotland

Day Two, Wednesday 29 April 2026

  • 07:00-09:00: Optional Hike Up Arthur’s Seat
  • 10:00-16:00: CISO 360 UK Conference
  • 16:00-16:30: Sponsors’ Prize Draw, Drinks and Goodbyes


Speaker Panel – CISO 360 UK 2026 (partial List)
Read more


Gemma Ungoed-Thomas
Senior Fellow, King’s College London
Recent Director for State Threats, Cyber and Technology, UK Cabinet Office

Dr. Abdullah A.I. Alnajem
Head of Cybersecurity
Saudi Enaya Cooperative Insurance Co.
Saudi Arabia

Paula Kershaw
Managing Director – Chief Controls Officer – Cyber & Resilience
Barclays

Nick Gertesian
CISO
eClinical Solutions
USA

Gary Hayslip
CISO in Residence
Halcyon
USA

Lee Morton
Head of Cyber Security
GBG Plc

Paul Colnan
CISO
NewDay
UK

Danielle Sudai
Security Operations Manager
Deliveroo

Dr. Sally Leivesley
Managing Director, Newrisk Limited
& Visiting Professor, Department of Civil and Environmental Engineering, Imperial College, London

Alan Jenkins
Fractional CISO
The Cyber Security Navigator

Jonathan Armstrong
Partner
Punter Southall

Lady Olga Maitland
President
Defense and Security Forum

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to the Pulse team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good! Afterwards the meal sponsored by Qualys was fantastic. Pulse go out of their way to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

Anchor Partners 2026

Many thanks to our 2026 sponsors - 2nd CISO 360 UKI - Edinburgh

Platinum Protectors

Sapphire Sentinels

Emerald Enforcers

CISO 360 Innovators

Agenda: 2nd CISO 360 UK & Ireland – Edinburgh 2026

Download Agenda 

Speakers CISO 360 UK 2026

The 2026 programme is currently being developed, if you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda sara.hook@pulseconferences.com.

Keynote Speakers and Speaker Panel of 2026 CISOs and Luminaries (partial list)

Gemma Ungoed-Thomas

Gemma Ungoed-Thomas

Keynote speaker. Senior Fellow, King’s College London. Recent Director for State Threats, Cyber and Technology in the UK Cabinet Office

Gemma Ungoed-Thomas is a Senior Fellow at King’s College London, working on issues at the intersection of national security, cyber power, emerging technology and democratic resilience. She brings extensive experience from senior roles in the UK government, where she led national strategy on state threats, cyber security and technology policy. Until March 2026, Gemma served as Director for State Threats, Cyber and Technology in the UK Cabinet Office. In this role she led national strategy at the intersection of security, advanced technology and resilience. She helped shape the UK’s £2 billion National Cyber Strategy, developed the UK’s first Counter State Threats Strategy, and co-chaired the National Cyber Advisory Board, bringing together senior leaders across government, industry and civil society to strengthen systemic resilience. She also served as Principal Adviser to the Prime Minister–chaired Science and Technology Committee. During her time in government, Gemma coordinated aspects of the UK’s support to Ukraine following the Russian invasion and led work to manage the UK’s risk exposure to hostile state activity, including malicious cyber and physical attacks. Gemma has extensive experience in strategy, crisis management and national security decision-making. She previously served as Private Secretary to the Prime Minister for Home Affairs and National Security, leading cross-government responses to counter-terrorism incidents, national cyber attacks and major crises, including the Afghanistan evacuation. At the National Cyber Security Centre (NCSC), Gemma established and led national incident response teams and helped build the UK’s cyber incident response capability, overseeing multidisciplinary operations responding to the most significant national cyberattacks. She coordinated real-time operational response and strategic decision-making for ministers, industry leaders and critical infrastructure. Earlier in her career she held senior roles at GCHQ, leading cross-government cyber defence initiatives and contributing to the development of the UK’s first National Offensive Cyber Strategy. Her work focuses on resilience as a strategic pillar of national power, integrating behavioural insight, adaptive governance and international cooperation. She has advanced resilience frameworks with Five Eyes partners, the EU and the United States, and contributes to debates on democratic resilience, responsible AI governance and the security implications of emerging technologies.

Lady Olga Maitland

Lady Olga Maitland

Keynote speaker. Founder, Defense and Security Forum – Global defence and security expert and commentator

Lady Olga Maitland is a long-standing campaigner on defence and security, shaped by front line political experience and decades of work across diplomacy, media and business. As a Member of Parliament , 1992 – 1997, she advocated for strong UK and European security. Her commitment to defence began earlier, in 1983 when she founded Families for Defence to counter unilateral disarmament narratives and reinforced Britain’s commitment to NATO. In 1991, Lady Olga founded The Defence and Security Forum to bring together global leaders, shaping international security – a mission that continues today. Her earlier career as a Fleet St columnist for the Sunday Express and Daily Mail honed her public engagement skills. Alongside her commercial and governance roles, Lady Olga speaks internationally on hybrid warfare., geopolitical risk, and the rising threats facing the UK and Europe, offering clear, actionable guidance for leaders navigating instability. Currently she is also Advisory Board member Audere International and Honorary President Algeria British Business Council. She is a special adviser to a number of dignitaries and a widely sought after speaker at all major conferences on several corporate governance issues.

President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International (UK)

Dr. Abdullah A.I. Alnajem

Dr. Abdullah A.I. Alnajem

Head of Cybersecurity Saudi Enaya Cooperative Insurance Co.

I’m a Certified Nuclear Cybersecurity Professional, licensed to cybersecure Nuclear Power Plants. A Cybersecurity Career Ambassador in collaboration with a CoI that’s led by NICE, NIST, U.S. Department of Commerce. I was educated in the USA and the UK with current work experience as a Chief Information Security Officer (CISO) for the Insurance Sector and previously as a Financial Analyst & as an advisor for Securing Card Payment Systems. Successfully managed fueling systems projects to modernize fuel (Petrol) stations with a leading U.S. global fueling systems manufacturer and a European manufacturer. I had implemented and operated the Cybersecurity Program for an insurance firm. Initially, I started as a Financial Anslyst and Risk Modeler at Riyad Bank and a Regional Supervisor for Corporate Banking. Knowledgeable about the leading fueling systems manufacturer, Gilbarco Veeder-root, a Vontier firm. I was educated at George Mason University (GMU), USA (2003), and at The University of Manchester, UK (2015). My aim is to create safe and modernized fuel stations with advanced and secure Automation and Payment systems while detecting and preventing Cyber Fraud.

Adam Hawthorne

Head of Commercial, Census Labs

Adam has been working in the cyber security industry for 15 years starting his career out at NCC Group and since holding positions in organisations like Mandiant and Trend Micro. More recently starting a journey to develop his own security consultancy and re-entering the sales market to build out the go to market strategy at Census Labs.

Alan Jenkins

Alan Jenkins

Fractional CISO, The Cyber Security Navigator

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

https://www.linkedin.com/in/alanjenkins/

Alex Lindl

Alex Lindl

Head of Information Security, Aegon UK

Alex is a certified CISO and has a wide ranging experience in technical, project, customer service, managerial and development roles as well as his current focus on information & cyber security. At the moment Alex heads up Information Security for Aegon UK and in previous roles Alex has build security operations functions, information security management systems and threat intelligence functions across roles with Aberdeen, Royal Bank of Scotland and Vodafone.

Alex Harland

Alex Harland

Co-Founder and CEO, AI Score

Alex Harland is a security and technology leader with two decades of experience delivering world-class strategic risk, crisis, and security management across defence, government, and private sectors. Beginning his career within Military Intelligence, Alex led intelligence and risk operations across multiple high-stakes geopolitical environments, developing a deep expertise in strategic decision-making under pressure.

Following his military service, Alex joined GCHQ, where he became a founding member of the UK’s National Cyber Security Centre (NCSC). There, he provided cyber security consultancy, incident response, and crisis leadership during some of the most significant cyber attacks to impact the UK.

Transitioning to the private sector, Alex shaped the cyber security and technology landscape of ComparetheMarket, one of the UK’s leading fintech brands, by driving a bold and innovative security transformation across modern cloud technologies.

Today, as Co-Founder and CEO of AI Score, Alex leads a mission to redefine how organisations understand, measure, and manage artificial intelligence performance and risk. His leadership combines a deep technical foundation with a strategic vision for trustworthy, transparent, and resilient AI systems.

Ben Armstrong

Ben Armstrong

Co-Founder, Cytix

With nearly a decade of experience in pentesting, Ben brings a wealth of commercial expertise to the AppSec sector. Known for insights into the evolving AppSec testing landscape and the effective utilisation of tools and technology driving teams today.

Cian Heasley

Cian Heasley

Principal Consultant, Acumen Cyber

Cian Heasley is a Principal Consultant at Acumen Cyber and a cybersecurity threat specialist who has run threat intelligence programs and built threat hunting functions in previous roles. For the last 3 years he was the Head of Threat at Adarma Security, having previously worked as a consultant in SIEM onboarding and detection and response. He is a Mitre ATT&CK and Sigma contributor and has presented at security conferences across the UK on topics ranging from mobile surveillance apps to the history of ransomware.

Chris Wallis

Chris Wallis

Founder & CEO, Intruder

Chris Wallis has over a decade of experience in cyber security, having previously provided counsel on the cybersecurity operations of numerous FTSE 100 companies, as well as blue teams defending critical national infrastructure. He founded Intruder with a clear mission 10 years ago to solve the overload crisis in vulnerability management and Intruder is now protecting over 3,000 companies worldwide.

Danielle Sudai

Danielle Sudai

Security Operations Manager, Deliveroo

Danielle Sudai manages the Security Operations and Automation team at Deliveroo, managing and optimising all Organisational Cloud Assets and SaaS solutions’ security monitoring and identifying real-time threats and security breaches.

Danielle was also a Cloud Security Engineer. In her career, she co-engineered a CSPM internal solution, reviewed and governed different cloud services from a security perspective, Cloud IAM misconfigurations and KMS services automation.

Findlay Whitelaw

Findlay Whitelaw

Field CISO, Exabeam

Findlay is a recognised thought leader, specialising in insider threats and security operations, with her career spanning security operations, consultancy and leadership roles. A published author and award-winning practitioner, her professional interests include tackling human-centric cyber risks and leveraging advanced technologies to address modern challenges. Her research and practical insights empower organisations to strengthen resilience and manage insider threats in an evolving digital landscape.

Gary R. Hayslip

Gary R. Hayslip

Senior Security Advisor in Residence, Halcyon

Gary Hayslip is an experienced Global Security Executive with a proven track record of delivering innovative security programs that protect billion-dollar enterprises at every touchpoint. He is intensely focused on driving continuous improvement to maximize the efficiency of security programs while minimizing costs. As an insightful thought leader, he possesses strong business acumen and a commitment to organizational mission, values, and goals. He has demonstrated the ability to collaborate with all levels of an organization to champion new ideas, gain buy-in, and build consensus. Hayslip brings extensive experience in information technology, security leadership, physical security, and risk management to his role as the Senior Security Advisor | Field CISO for Halcyon.ai. His previous executive positions include multiple roles as Chief Information Security Officer, Chief Information Officer, Deputy Director of IT, and Chief Privacy Officer for the U.S. Navy (Active Duty), the U.S. Navy (Federal Government employee), the City of San Diego, California, Webroot Software, and SoftBank Investments (Vision Fund & Vision Fund II).

Hayslip is a proven cybersecurity expert with excellent communication and public speaking skills. He is skilled at explaining complex security and risk concepts to audiences with different levels of knowledge. Hayslip has earned a reputation as a highly effective communicator, author, and keynote speaker. He co-authored the “CISO Desk Reference Guide: A Practical Guide for CISOs – Volumes 1 & 2,” “The Executive Primer: An Executive’s Guide to Security Programs,” “Developing Your Cybersecurity Career Path,” and the “The Essential Guide to Cybersecurity for SMBs.” He recently coauthored and published “Mastering Third Party Risk,” a guide aimed specifically for security practitioners to help them manage the risk exposure to organizations from vendors and supply chains. These books are among the top resources for helping CISOs improve their leadership and business skills. Hayslip currently serves as an independent director on several boards and advises various other security and technology firms. He is an active member of the cybersecurity community and belongs to professional organizations such as ISC2, NACD, ISACA, and Infragard. Hayslip holds several professional certifications, including CISSP, CISA, and CRISC, and has earned a BS in Information Systems Management from the University of Maryland, University College, and an MBA from San Diego State University.

LinkedIn Profile: http://www.linkedin.com/in/ghayslip

Greg Day

Greg Day

SVP & CISO, Cybersecurity Wisdom

Greg Day, SVP & CISO at Cybersecurity Wisdom, is a respected cybersecurity leader whose career began in 1991 at Dr Solomon’s/McAfee. He has held consultancy and senior leadership roles, including CTO and CISO positions at Symantec, FireEye/Mandiant, Palo Alto Networks, and Cybereason.

Now semi-retired, he provides fractional CISO services and advisory expertise. Greg has supported boards, start-ups, and VC/PE firms, working with thousands of organisations across the public sector and Global 2000 companies in North America and EMEA. He is also an author, spokesperson, and blogger with a strong passion for cybersecurity.

He has advised organisations including the World Economic Forum, NATO, and Europol, and contributed to EU and UK policy discussions. He has led the Hackers & Threats stream at RSAC for over a decade and looking to give back mentors emerging cybersecurity leaders, including chairing RSAC EMEA CISO Bootcamps

Dave Henderson

Dave Henderson

Sales Director - UKI, Synack

With a 20-year career spanning the breadth of vulnerability management and offensive security, Dave currently serves as Sales Director for UK and Ireland at Synack. He specialises in helping organisations simulate authentic cyber threats to drive meaningful risk reduction rather than just meeting compliance standards.
His track record includes roles at Hackuity, Vectra AI and NCC Group, prior to joining Synack.
A dedicated cyclist and father of two, Dave spends his downtime chasing PBs on the road, fuelled by an addiction to managing the flames of his outdoor pizza oven and devouring the results.

James Gosnold

James Gosnold

Head of Cyber Security, Ilkari

With over 25 years of experience in Cyber Security, James has built and led security functions, both supplier end end user side, across some of the most diverse environments imaginable — from UK Gov to the world of iGaming, via energy, aviation and logistics. That breadth has shaped a pragmatic, no-nonsense approach to security that’s equally at home in a board conversation about risk as it is in the technical weeds of a SOC.

A CISSP, CCSP, and newly certified IAPP AI Governance Professional (AIGP), James has operated across the full spectrum of cyber disciplines — from offensive security and threat intelligence to GRC and compliance programmes including ISO27001 & SOC 2. As a former UK Government-listed security adviser and a regular on the conference circuit, he brings real-world perspective on what it actually takes to build and sustain security capability in organisations where the threat landscape, regulatory pressure and available resources rarely align neatly.

Jenny Kalenderidis

Interim Managing Director & Executive Chair Reliance Cyber

James Kwaan

James Kwaan

Senior Operations Threat Manager, LBG

Now cyber operations manager at Lloyds banking group, former CISO and Global DPO, James Kwaan is a recognised expert in his field, having covered AI, simulation, energy and financial services for several blue-chip companies. He has managed and mitigated cyber security incidents since 2007 and has set up and run incident response and cyber intelligence teams. He has in depth knowledge of Geopolitics actively participating in professional groups. An active contribute to the MITRE Center for Threat Informed Defense, he is president of ISC2 Scotland and has won several prizes and accolades for his contributions to the cyber security field – helping other professional succeed in their careers.

Jonathan Armstrong

Jonathan Armstrong

Partner, Punter Southall

Jonathan is an experienced lawyer based at Punter Southall Law in London working on compliance & technology. He is also a Professor at Fordham Law School teaching a new post-graduate course on international compliance and a Director at L-EV8 working to increase cybersecurity skills on boards.

Jonathan’s professional practice includes advising organisations on risk and compliance across Europe. This includes work on:

  • Prevention (e.g. putting in place policies and procedures);
  • Training (including state of the art video learning); and
  • Cure (such as investigations and dealing with regulatory authorities).

Jonathan has handled legal matters in more than 60 countries. He has handled more than 250 data breaches and has worked extensively with technology legislation including GDPR, NIS2, DORA & the EU AI Act. He has conducted a wide range of investigations of various shapes and sizes, a request to appear before a UK Parliamentary enquiry and led clients through real and simulated bet-the-company situations.

Jonathan is also regarded as an acknowledged expert on AI and he currently serves on the New York State Bar Association’s AI Task Force looking at the impact of AI on law and regulation. Jonathan also sits on the Law Society AI Group.

Jonathan is a co-author of LexisNexis’ definitive work on technology law, “Managing Risk: Technology & Communications”. In addition to being a lawyer, Jonathan is a Fellow of The Chartered Institute of Marketing. He has spoken at conferences in the US, Japan, Korea, Canada, China, Brazil, Singapore, Vietnam, Mexico, the Middle East & across Europe.

Jonathan qualified as a lawyer in the UK in 1991 and has focused on technology and risk and governance matters for more than 25 years. Jonathan has been selected as one of the Thomson Reuters stand-out lawyers for 2024 – an honour bestowed on him every year since the survey began. Thomson Reuters has listed Jonathan as the 6th most influential figure in risk, compliance and fintech in the UK. Jonathan is listed as a Super Lawyer and has been listed in Legal Experts from 2002 to date.

John White

Field CISO EMEA, torq

Jonny Herd

Jonny Herd

CISO, Zenobe

A highly effective and resourceful CIO/CISO with a proven track record of transforming complex SaaS environments into secure, compliant, and highly efficient operational powerhouses. I excel at building and leading global, cross-functional teams to deliver ambitious security objectives, drive digital transformation, and achieve critical business outcomes. My extensive background in operations, engineering, and deep security & compliance expertise enables me to future-proof large-scale cloud infrastructures and optimise SaaS business operations for sustained growth and resilience.

Ken Munro

Ken Munro

Founder and CEO, Pen Test Partners

25+ years in cyber security. Successful trade sale of SecureTest to NCC. Briefed boards of BoE, LSEG, Tesco. Regulatory / government: Briefed EU Parliament, UK Parliamentary groups, US gov agencies. He’s heavily involved in lobbying for regulatory change and sits on industry accreditation groups.

Lee Morton

Lee Morton

Head of Cyber Security, GBG Plc

An accomplished Head of Cyber Security/CISO and international keynote speaker, experienced in delivering highly engaging, interactive presentations that translate complex technical topics into clear, relatable insights for both technical and non‑technical audiences. Known for bringing energy, storytelling, and practicality to stages around the world—ensuring audiences are not only informed, but genuinely entertained.

Brings extensive expertise in designing, building, and leading large-scale cyber security programmes across global enterprises. Proven success managing security operations, cyber risk, data protection, and security architecture across regions including Africa, Asia, Australia, Europe, and North America.

Specialises in the development of enterprise security strategies aligned with leading frameworks such as NIST, NIS2, DORA, and CIS, while ensuring ongoing compliance with GDPR, ISO 27001, NDPR, Cyber Essentials, PCI‑DSS, and region‑specific regulatory requirements.

Experienced in delivering complex projects through both internal teams and outsourced operating models, creating scalable security capabilities that strengthen resilience and support business growth.

Malcolm Kafesu

Malcolm Kafesu

Global IT Security and Governance Manager, Ontic

Malcolm Kafesu is an IT Security and Governance Manager at Ontic, specialising in global cybersecurity governance, risk, compliance and organisational resilience. He leads global security with a focus on people, decisions, and behaviour as the drivers of real cyber resilience. He is known for his “Human Firewall” approach, highlighting how leadership, not tooling, shapes cyber outcomes.

Martyn Booth

Martyn Booth

CISO, dunnhumby

Martyn is Chief information security officer at dunnhumby, the world’s largest consumer data analytics organisation. He runs a large team and is an experienced cyber security practitioner, with over 20 years experience in the field, spanning big-4 consulting and running large teams. He advises multiple VCs and start ups, operates at board level and is seen as a strategic partner to the businesses that he advises. His technical background, coupled with his MBA for Durham, enables him to operate at the highest levels of business with a deep technical understanding of the security domain.

Marcus Vaughan

Marcus Vaughan

Cofounder, iluminr

Marcus Vaughan is Cofounder at iluminr, working with CISOs and resilience leaders to test and strengthen critical response capability in real-world conditions. His work helps security leaders evidence readiness to boards and regulators with data grounded in actual response.

Michael Colao

Michael Colao

CISO / CSO / Cyber Underwriter Luminary

Experienced CSO/CISO and Cyber Underwriter with than 25 years experience in financial services. Has a strong side-interest in computer forensics and in the management of digital evidence. Graduated from the Massachusetts Institute of Technology (MIT) in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services primarily in London.

Nick Gertesian

Nick Gertesian

CISO, eClinical Solutions US)

Nick Gerteisen is a cybersecurity leader with over 20 years of experience in developing, implementing and optimizing cybersecurity programs protecting digital health, medical technology and SaaS organizations. Nick has experience leading large scale security transformations, regulatory compliance initiatives, and risk management programs for global organizations.

Nick has built and scaled cybersecurity teams, integrating security frameworks into product development lifecycles and ensuring compliance across multiple domains such as FedRAMP, SOC2, GDPR and HIPAA-HiTrust. His expertise spans Governance Risk & Compliance, Identity and Access Management, Security Operations, Threat Modeling, Threat Intelligence, Cloud Security, Product and Application Security and Secure SDLC-DevSecOps.Previously serving in leadership roles at Smith + Nephew, Insulet Corporation and Mark43, he has influenced medical technology cybersecurity standards, collaborated with regulatory bodies and driven innovative security strategies for enterprise and product security. Nicholas continues to influence the future of digital and medical cybersecurity practices through speaking or chairing multiple cybersecurity and industry events per year.”

Owanate Bestman

Owanate Bestman

Director, Bestman Solutions

Owanate is the founder of Bestman Solutions, a firm dedicated to helping leaders hire cyber security professionals. He advises CISOs and Executives on market factors that impact their growth plans and designs bespoke solutions to address this. Firmly embedded in the cyber security space, he possesses a global core network of well-respected and proven security specialists. Owanate has spent almost a decade recruiting in the Cyber Security field. Before this, he recruited Technology and Operational Risk specialists and successfully staffed a number of high profile banking regulatory programmes. He is also a keen industry speaker and writer for security associations and international publications. Outside of Security and staffing, Owanate is interested in all things Martial Arts.

Oliver Brown

Oliver Brown

CCO, Wire

Oliver is a commercial leader with more than 15 years of experience in the information technology, software, and services industry. He is known for building strong relationships with customers, partners, and colleagues, and for delivering innovative, customer focused solutions that drive business growth, operational efficiency, and measurable value.

As Chief Commercial Officer, Oliver leads the global go to market strategy and oversees teams across sales, marketing, customer success and support, partnerships, pre sales, solution delivery, and revenue operations. Drawing on experience across both the private and public sector, he designs and executes multi-channel strategies that deliver measurable results and create meaningful impact for customers and organizations alike.

Oliver’s focus is on strengthening brand awareness, driving sustainable revenue growth, and delivering exceptional experiences for prospects, customers, and partners.

Pete Hoddinott

Pete Hoddinott

Managing Director, QCC

Pete is an accomplished business leader with more than 40 years of experience in the Defence, Security, Cyber and Technology sectors. He has a proven record of leading complex organisations, delivering strategic growth, and managing large-scale operations across international markets.

Pete is the Managing Director of QCC Global Ltd, the world’s leading provider of Technical Surveillance Counter Measures (TSCM), Cyber TSCM, Digital & Mobile Forensics, and counter-eavesdropping services.

In this role, Pete drives the overall strategy, performance, and global growth of a company that has completed operations in more than 105 countries, with companies established in UK, Singapore, Dubai and Ireland.

Prior to joining QCC Global, Pete served as Managing Director of L3Harris Intelligence and Cyber International (ICI) business and prior to this as Managing Director of Thales Cyber & Consulting UK.

Pete holds a BSc in Mathematical Studies and is a Fellow of the Association for Project Management (FAPM) as well as a Member of the Institute of Directors.

Based in Somerset, Pete is married to Charlotte with four children. Away from work, Pete enjoys shooting, golf, skiing and classic cars.

Paul Colnan

Paul Colnan

CISO, NewDay

Paul Colnan is the CISO at NewDay, financial services. Paul has 15 years of cyber security experience, including advising some of the world’s largest brands and he works with the board to enable secure and trusted commerce. He has an ‘ethical hacker’ background, which helps him tackle complex security issues, but he also cares about driving effective change through clear leadership and communication. Paul has been a CISO in various sectors, including fintech, logistics, and manufacturing, and before joining NewDay he was CISO at ION, he was an Executive Director at JP Morgan Chase, where he held security roles in retail banking, M&A and cloud platform security teams. He was CISO of Revolut and Group CISO of Unipart Group. Paul likes aviation and is pursuing his private pilot’s licence in his spare time.

Paula Kershaw

Paula Kershaw

Managing Director - Chief Controls Officer - Cyber and Resilience, Barclays

Paula Kershaw is a senior Cybersecurity, Resilience, and Operational Risk leader with more than 30 years of financial services experience across both traditional and challenger banking environments. Her most recent roles as Chief Controls Officer for Security & Resilience Barclays and UK & Europe CISO at HSBC provide a unique perspective regarding balancing technical and business outcomes with appropriate risk & control challenge and oversight and translating complex cyber and resilience risk into governance decisions that boards can own and act on.

Richard Holland

Richard Holland

Field CISO, Quorum Cyber (UK)

Richard Holland is Field CISO at Quorum Cyber. He has over 25 years’ experience working in various sectors from higher education, local government, housing, aerospace, defence, finance, and outsourcing. Prior to joining Quorum Cyber, Richard held several senior positions, including Assistant Director of Office CIO at Queen Mary University of London, Head of IT Systems and Cyber Security at Notting Hill Genesis, Assistant Director Technology Innovation at London Borough of Waltham Forest, and Head of Business Solutions at Genesis Housing Association.

Rob Hillier

Rob Hillier

Technical Assurance Lead, Aviva

With over three years of experience as Co-Founder and CEO of Validato, I lead a team dedicated to enhancing cybersecurity through advanced threat simulation and risk assessment solutions. Validato focuses on identifying vulnerabilities and empowering organizations to strengthen their detection and protection capabilities against evolving cyber threats. As an experienced professional with a strong background in sales, marketing, and new business development, I am driven by a passion for helping organizations reduce cyber risk exposure. At Elasticito, I have contributed to guiding clients in mitigating external and internal risks while developing sustainable security measures. My work is underpinned by a commitment to fostering collaboration and building long-term partnerships with clients and stakeholders.

Professor Robert Coles

Professor Robert Coles

Consultant, DSSmith plc

Robert has over 35 years of audit, risk and cybersecurity experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG. Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School. Robert also holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, and Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University of Brighton.

Dr. Roddy Gow

Dr. Roddy Gow

OBE, CEO, Asia Scotland Institute

Roddy Gow, OBE Chairman of the Asia Scotland Trust, is the Founder and Chairman of the Asia Scotland Institute. He is also the Founding Partner of Canongate Partners, an international executive search and consulting firm.

He was previously the Chief Executive of Asia House, London, where he drove its mission to educate and inform the people of the UK about the region extending from the Gulf to Japan. He is a member of the King’s Bodyguard for Scotland (Royal Company of Archers) and holds an MA degree from Trinity College, Cambridge, in Fine Arts and Architecture.

Dr Sally Leivesley

Dr Sally Leivesley

Managing Director, Newrisk Limited & Visiting Professor, Imperial College, London, Department of Civil and Environmental Engineering

Dr Leivesley, sally@newrisk.com works on generic solutions to catastrophic risks to critical infrastructure across all disciplines and contributes practical applications to government policy and business. She has been a Panel adviser to for the British IET and CPNI supported publication for Cyber Security in the Built Environment.
As an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business Dr Leivesley has worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks.
As an international media commentator she has commentated for BBC World Service and other news outlets on extreme threats – Chinese spy balloon over USA nuclear missile site, uranium package at London Heathrow airport, cyber; terrorism; aviation losses; nuclear reactor explosions; Kabul 2021 evacuation; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents.

Dr Leivesley has held international scientific meetings on issues of catastrophic risk including risks of emerging nuclear weapons, infrastructure resilience including cyber, Covid-19 solutions and hazardous near-earth objects.
She was director of two disaster recovery units in Australia (weather and chemical incidents) and trained by British Home Office as Scientific Advisor holding a Cold War appointment as on all aspects of nuclear war.
PhD London University; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute for Defence Studies, and the British Information Assurance Advisory Council Community.

Simon Riggs

Simon Riggs

CISO, OneAdvanced

Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Simon was recently interim CISO at John Lewis, McKesson UK and Avon. Prior to these roles, he was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.

Stephen Khan

Stephen Khan

Chief Information Security Officer, Cognizant

Stephen is an information and cyber security practitioner, and international speaker with 20+ years of experience working for global firms across financial services, healthcare, and defence. Stephen has held senior group level positions at firms including HSBC, RBS, GSK, and Siemens with experience of global regulatory and cyber security frameworks to drive execution and implementation for the management of risks to support business strategies especially as technology and business models are changing at pace. Stephen is passionate about people and shares his knowledge and experience by coaching and mentoring senior leaders, and young people to achieve their potential. He believes people come into the workplace to do their best work, so leaders need to provide a positive empowered culture allowing teams to thrive and deliver the best outcomes through people, process, and technology. He contributes to Cyber Security community as Chairman of Club-CISO advisory board by engaging with 500+ global CISO executives on important matters affecting cyber security and risk leaders and their organisations. He supports the wider industry and academia through his board membership of Research Institute for Sociotechnical Cyber Security (RISCS), and advisory member of ISC2 UK cyber security council. Stephen is former Chairman of White Hat Ball which is a Cyber Security charity supporting the amazing work performed by NSPCC Childline in the protection of vulnerable young people. Stephen’ current role is Chief Information Security Officer – EMEA & APJ at Cognizant Technology Services, where he is an amazing team of global business information security officers protecting top tier companies from cyber risks covering UKI, EMEA, APAC, India, Australia across all industry verticals. As one of the largest global professional services companies Cognizant help our clients modernize technology, reimagine processes and transform experiences so they can stay ahead in our fast-changing world.

Tarek Kuzbari

Tarek Kuzbari

Vice President EMEA, Picus Security

Tarek Kuzbari is a seasoned leader with 20+ years of experience in the Technology Media and Telecommunications (TMT) sector, specializing in international market expansion, revenue growth, and P&L management. He has held senior roles at HUMAN, Cybereason, Bitdefender, Group-IB, SABA Software, and Kaspersky, managing $58m ARR across regions including MEA, APAC, and Eastern Europe. Tarek, an acknowledged industry influencer, has been listed among the top “30 under 30” by Gulf businesses and ACN’s “Top 25 Most Powerful Executives in the Middle East”. He also earned a spot in Network Middle East’s “Top Executives in the Security Industry in the Middle East”. He holds an MBA from London Business School and actively supports NGOs like Agastya International Foundation and the Grow Movement.


Networking Events – 2nd CISO 360 UK

YOU’RE INVITED! JOIN MEMORABLE DEDICATED NETWORKING EVENTS
Complimentary – A Crucial Part of the CISO 360 UK Experience

Networking Lunches at the Sheraton Grand Hotel & Spa Edinburgh

Tuesday 28 April – Arrive in time for lunch and get acquainted with CISO peers before the sessions start!
Wednesday 29 April – During the conference, you’ll enjoy a delicious hot buffet and have plenty of time to continue the conversations with peers

Sheraton Grand Hotel

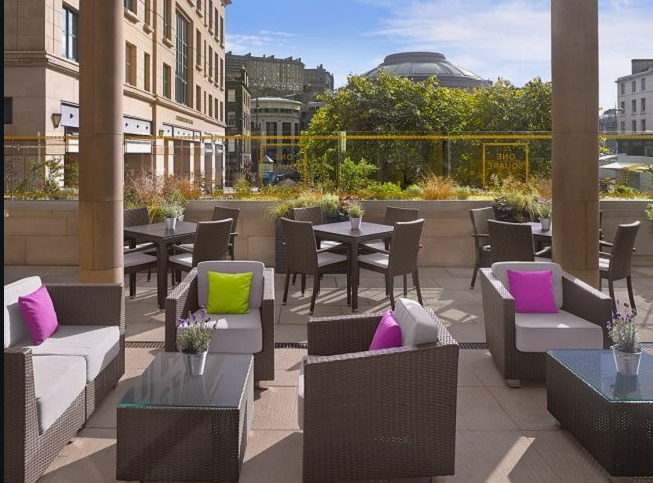
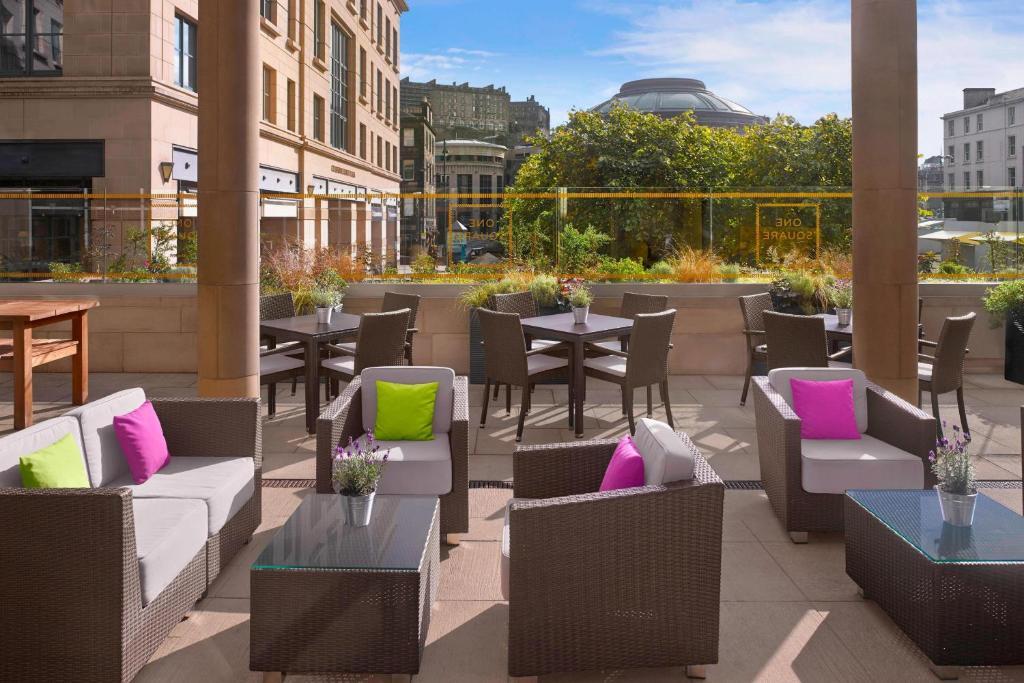
Terrace Networking Reception at One Square
Security conversations along Edinburgh’s iconic Festival Square terrace overlooking the Castle.

Tuesday 28 April – 16:00-17:00

At the close of Day One, delegates are invited to continue the conversation in style at One Square, the bar and restaurant at the Sheraton Grand Hotel & Spa Edinburgh, located at Festival Square in the heart of the city.

With the weather set to be lovely, we will be gathering outside on the One Square Terrace, where guests can enjoy stunning views of Edinburgh Castle in a relaxed and vibrant open-air setting—perfect for unwinding after a full day of discussions.

One Square is renowned for its premium selection of drinks, offering the ideal backdrop for CISO 360 delegates to connect, reflect, and continue conversations in an informal setting.

After the reception, we will head off together for the Vaults tour.

One Square

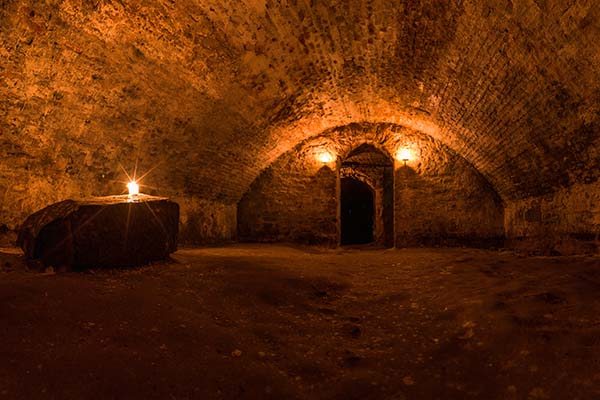
The Candlelit Vaults Walk
Step beneath the surface into The Vaults and hidden layers.

Tuesday 28 April – 17:00-18:30
Beneath Edinburgh’s cobbled streets, through an unmarked doorway on South Bridge, lies a hidden world carved in stone in 1788, a place of shadow economies, illicit trade, survival, and stories the city never wrote into its official record. Once home to taverns, workshops, distilleries, and later the city’s forgotten, these chambers have held secrets for over two centuries. We venture underneath Edinburgh’s Royal Mile for terrifying ghost stories on this guided tour of the city’s underground which includes the Edinburgh Vaults, stone circle vault, and a torture exhibition. It’s a setting that reminds us: resilience is rarely built in comfort and that trust can be forged in unusual spaces!.

Edinburgh Vaults

CISO 360 Dinner | National Museum of Scotland
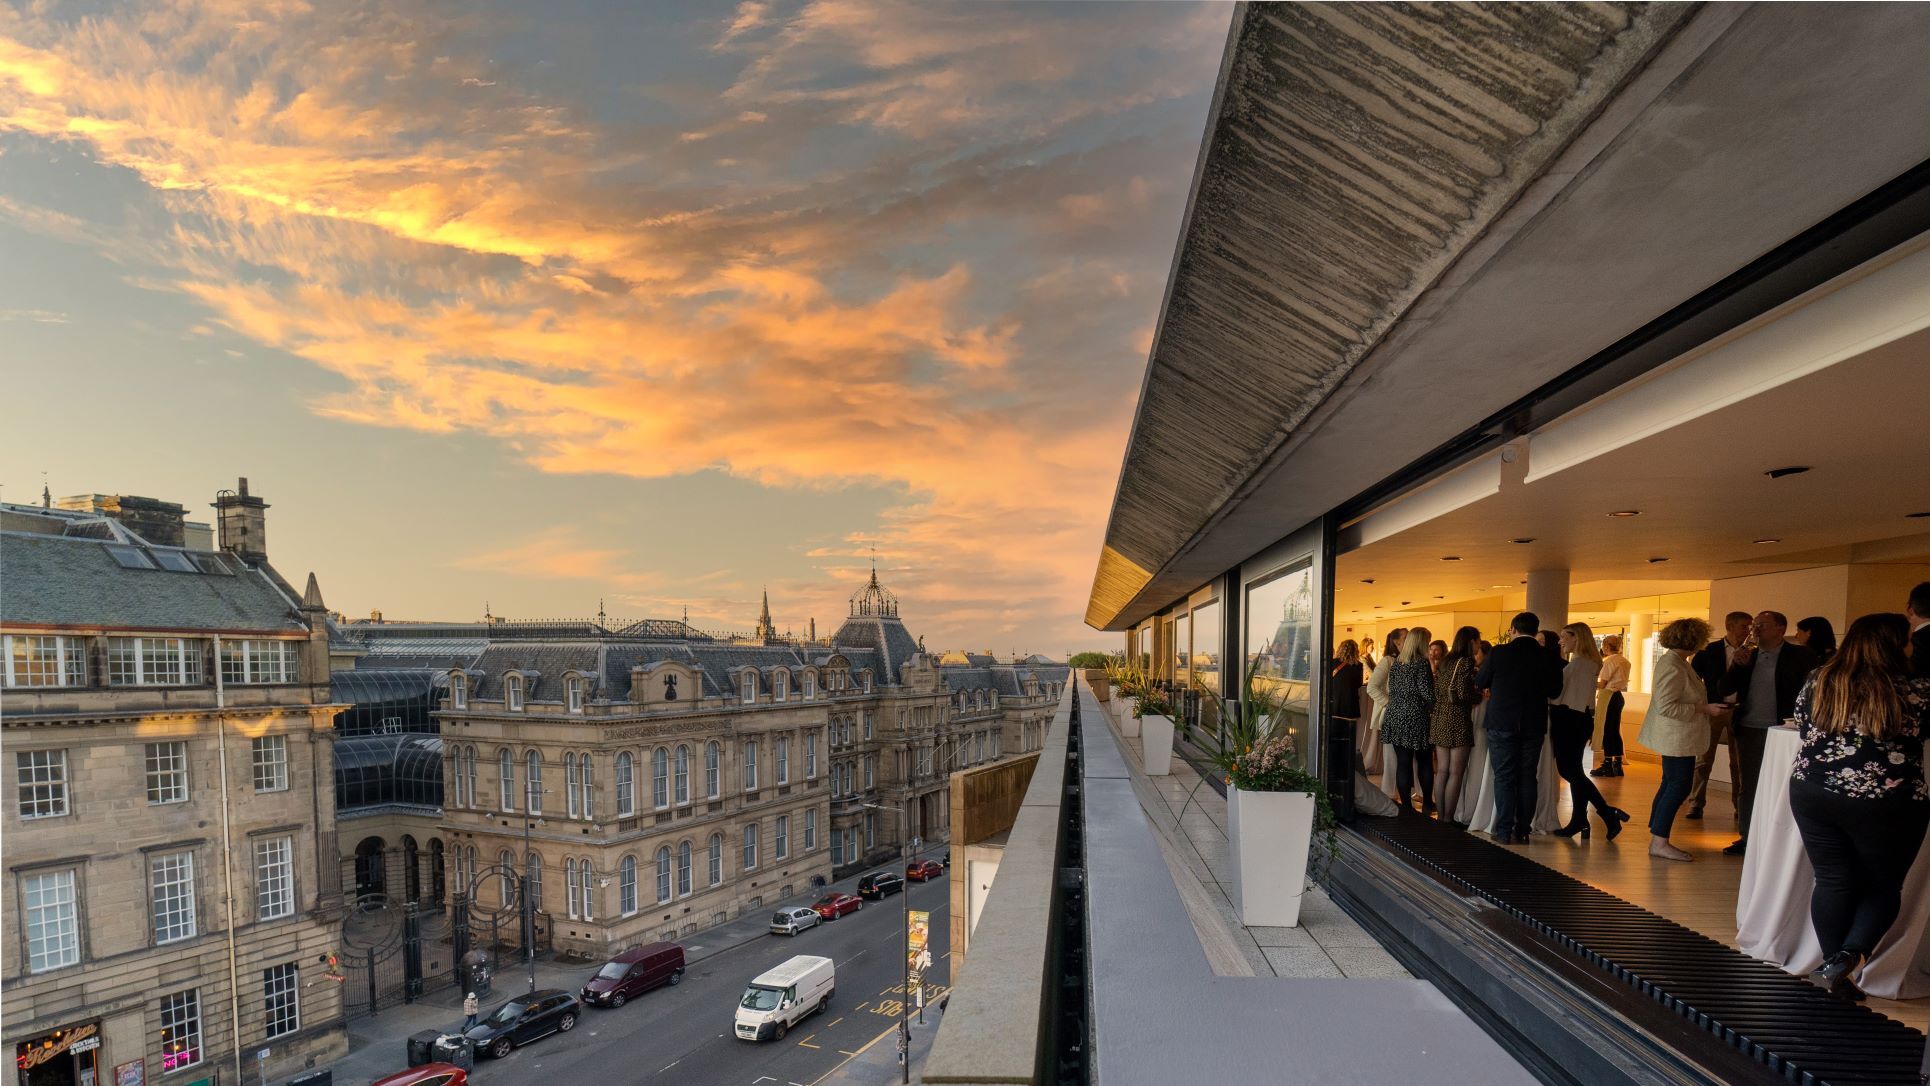
Skyline Dinner with views towards Edinburgh Castle.

Tuesday 28 April -19:00-23:00
Emerging from the Vaults, the evening continues with the CISO 360 Dinner at the iconic National Museum of Scotland. These dinners are intentionally conversational, informal, and off-the-record reflecting the trusted spirit that defines the CISO 360 community. Set high above the city, the museum’s rooftop space offers floor-to-ceiling windows and a stunning outlook across Edinburgh’s Old Town, with unrivalled views towards Edinburgh Castle. It is the perfect setting for security leaders to continue discussions in a relaxed environment building relationships, and reflecting on the day’s conversations while overlooking one of Europe’s most historic cityscapes.

National Museum of Scotland dinner

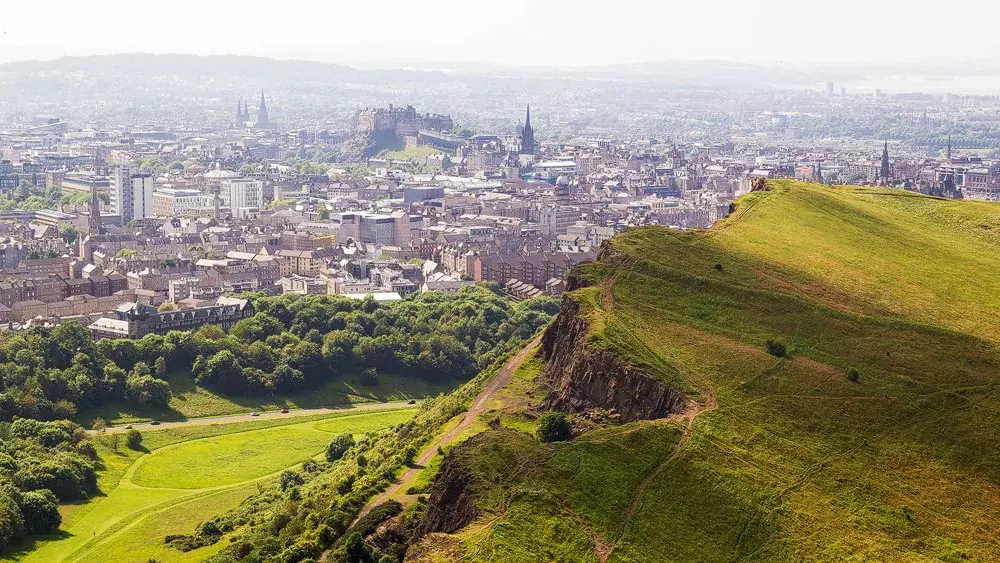
CISO 360 Hike Up Arthur’s Seat!
A hill walk with peers in the heart of the city.

Optional Hike up Arthur’s Seat!
Wednesday 29 April – 07:00-09:00

Arthur’s Seat, an ancient volcano in Holyrood Park, Edinburgh, offers a popular 2-3 hour (approx. 4.75km) hike with panoramic city views. The summit (251m) requires a steep, rocky climb. Proper footwear is advised due to muddy/rocky paths, which are strenuous but rewarding. Bond with peers in the wild and be back in time for breakfast and to refresh, all before the start of conference day two!

Arthur’s Seat

Platinum Protectors

Reliance Cyber

Reliance Cyber delivers world class cybersecurity services tailored to the unique needs of our customers. With extensive in-house expertise and advanced technology, we protect organisations across a wide range of sectors—from enterprise to government—against the most sophisticated threats, including those from nation-state actors. Our teams safeguard critical assets, people, data, and reputations, allowing customers to focus on their core business objectives with confidence.

www.reliancecyber.com

Exabeam

Exabeam is a leader in intelligence and automation that powers security operations for the world’s smartest companies. As a global cybersecurity innovator, Exabeam provides industry-proven, security-focused, and flexible solutions for faster, more accurate threat detection, investigation, and response (TDIR). Cutting-edge technology enhances security operations centre performance, optimising workflows and accelerating time to resolution. With consistent leadership in AI innovation and a proven track record in security information and event management (SIEM) and user behaviour analytics, Exabeam empowers global security teams to combat cyberthreats, mitigate risk, and streamline operations.

Real Intelligence. Real Security. Real Fast.

Learn more at www.exabeam.com

Intruder

Intruder was founded in 2015 to help solve the information overload crisis in vulnerability management. Having worked both as an ethical hacker for tier one companies, and for blue teams defending critical national infrastructure, Founder Chris Wallis noticed that while vulnerability management tools were great at finding issues, they were less useful when it came to prioritizing them, tracking them, and timely alerting when problems arose. Quite simply – the most important issues were often getting lost in the noise.

Intruder’s mission from day one has been to help divide the needles from the haystack, focusing on what matters, while ignoring the rest. Effective cyber security is about getting the basics right. Intruder helps you do that, saving time on the easy stuff, so you can focus on the rest.

Since its inception in 2015, Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, and was included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK. It is now proud to have over 3,000 happy customers all over the world.
https://www.intruder.io/

Picus Security

Picus Security shows you what’s working in your defenses and what isn’t, why it matters, and how to fix it. The pioneer in continuous security validation, Picus now delivers autonomous exposure validation by converging breach & attack simulation and automated pentesting into one unified platform. Picus Swarm augments your team with self-orchestrating AI agents that ingest real-time signals and operate 24×7 within the guardrails you define. With 75+ integrations and the industry’s highest customer satisfaction ratings, Picus gives security teams the validated, context-rich speed they need to outpace AI-driven adversaries.

www.picussecurity.com

Torq

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Working alongside your SecOps team, Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats and integrates with your entire security stack to turn alerts into action.
https://torq.io/

Sapphire Sentinels

Wire

Wire is the enterprise-class secure workspace platform, delivering a full suite of messaging, audio, video, and enterprise content management for use at scale by teams while staying protected by the industry’s most stringent security. Wire protects digital collaboration with unified access control based, end-to-end encryption powered by the MLS standard that is frictionless, reassuring, and always on. Wire provides the enterprise-class alternative to collaboration suites offered by tech giants whose business models monetize their customers’ sensitive data, compromise sovereign control, and leave dangerous security holes in their products by design. Wire erases the barrier between the productive collaboration that users want and the data protection, privacy, compliance, and control that organizations need. Wire is trusted by the world’s most security-sensitive government and defense agencies, global enterprises, and millions of users around the world.
https://wire.com/

iluminr

iluminr is a capability intelligence platform built for real-world resilience. We combine full-length simulations with high-frequency Microsimulations to map how organizations coordinate, decide, and adapt when complexity hits – across strategic, operational, and cyber domains. Leaders use iluminr to replace best guesses with live evidence. Our platform tracks how capability plays out over time, revealing friction points, improvement signals, and trends that static plans and annual tests miss. Designed for highly regulated and high-impact industries, iluminr helps CISOs, security leaders, leadership teams, and boards make resilience observable, measurable, and improvable – without waiting for a crisis to find out.

www.iluminr.io

Emerald Enforcers

Pen Test Partners

Pen Test Partners is an independent cybersecurity consultancy specialising in penetration testing, research, GRC consultancy, and incident response.

We help organisations identify and address real security weaknesses by safely testing systems, networks, applications, and connected devices. Our work covers penetration testing, GRC consultancy, digital forensics, and incident response, with a focus on realistic attack paths and business-relevant risk.

We have deep experience in complex and safety-critical environments, including maritime, aviation, automotive, OT, and IoT systems, where interconnected platforms and third-party dependencies increase impact. From ships and aircraft to vehicles, EV chargers, and connected infrastructure, if it is connected, we can test it.

https://www.pentestpartners.com/

Acumen Cyber

At Acumen, we protect modern businesses from the complexities of cyber threats 24/7. Our commitment is to ensure your business operates seamlessly, free from the disruption of cyber incidents.
We don’t just offer security software; we are architects delivering your peace of mind. Rooted in our deep understanding of the rapidly evolving threat landscape, we are dedicated to innovation and advancement within the industry, staying ahead of the pace of continuous threat so you don’t have to.
www.acumencyber.com

Synack

Synack’s Penetration Testing as a Service platform manages customers’ attack surfaces by discovering new assets, pentesting for critical vulnerabilities and gaining visibility into the root causes of security risks. We are committed to making the world more secure by harnessing a talented, vetted community of security researchers to deliver continuous penetration testing and vulnerability management, with actionable results. Synack’s PTaaS platform has uncovered more than 83,500 exploitable vulnerabilities to date, protecting a growing list of Global 2000 customers and U.S. agencies in a FedRAMP Moderate Authorized environment. For more information, please visit www.synack.com

CISO 360 Innovators

Validato

Validato is a UK founded cyber adversary simulation vendor. The Validato platform simulates cyber threat behaviours, based on the MITRE ATT&CK framework, to validate the effectiveness of security controls.
https://validato.io

QCC Global

QCC Global owns by far the world’s largest & most advanced commercially held arsenal of TSCM equipment and has significantly more TSCM engineers than any other provider, all of whom hold current commercial and government vetting.

As the world’s largest Counter-eavesdropping company, QCC Global has a long and rich history in the Technical Surveillance Counter Measures (TSCM) and Cyber Forensics.

QCC Global is globally respected for our Pro Bono academic and technology contributions to the counter-surveillance, cyber forensics & information security sectors and for its efforts to raise standards wherever possible.

QCC Global mission is about “Keeping your business, your business”

www.qccglobal.com

Quorum Cyber

Anecdotes

Spoiler alert: you’re about to fail. Again. You’re not going to know if your policies are actually being implemented, you won’t have a clear view of your risk posture, and forget about achieving continuous compliance. An enterprise GRC program running on traditional technology is gonna disappoint 100% of the time. Traditional is where GRC goes to die.
‍
To manage GRC today, you need more than just automation—you need a revolution. You need a continuous flow of data, collected directly from your organization’s systems, and AI that assists with everything from collecting that data to automatically testing and monitoring it in the context of each use case.
‍
Anecdotes’ AI-native GRC platform is built on a foundation of complete, accurate, and structured data, automatically collected from your systems and trusted by the world’s largest enterprises and auditors. With AI embedded across every task—audits, risk management, continuous control monitoring, and everything in between—you can finally do GRC right.

www.anecdotes.ai

Census Labs

Cytix

Cytix is the AppSec layer that focuses testing where it matters. Application security is still built around finding risk after software is written. In reality, the most serious issues are introduced much earlier as software changes. Cytix analyses every developer ticket before production, identifying only the changes most likely to introduce real security risk. By focusing on change rather than code alone, Cytix directs AppSec testing to where it actually matters and closes the blind spots between scanners and pentests. CREST-accredited. Available as SaaS or a fully managed service.

www.cytix.io

Who Joins?

By Designation

  • Chief Information Security Officer (CISO)
  • Chief Security Officer (CSO)
  • Director / Head of Cybersecurity
  • Director / Head of Cyber Threat Intelligence
  • BISO / CIRO
  • CTO, CIO, CRO
  • Chief Security Architect / Senior Security Architect
  • Director / Head of Security Infrastructure
  • Director / Head of Networks, Applications, Cloud
  • Director / Head of Technology Innovation
  • Director / Head of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer

By Verticals

  • Financial Services – including Insurance
  • Energy – power, water and critical national infrastructure companies
  • Extractives – mining, oil and gas
  • Pharmaceuticals and health
  • Consumer goods
  • Manufacturing
  • Retail
  • Transport and logistics
  • Government departments

Venue and Accommodation

Sheraton Grand Hotel & Spa Edinburgh

1 Festival Sq, Edinburgh EH3 9SR
Website

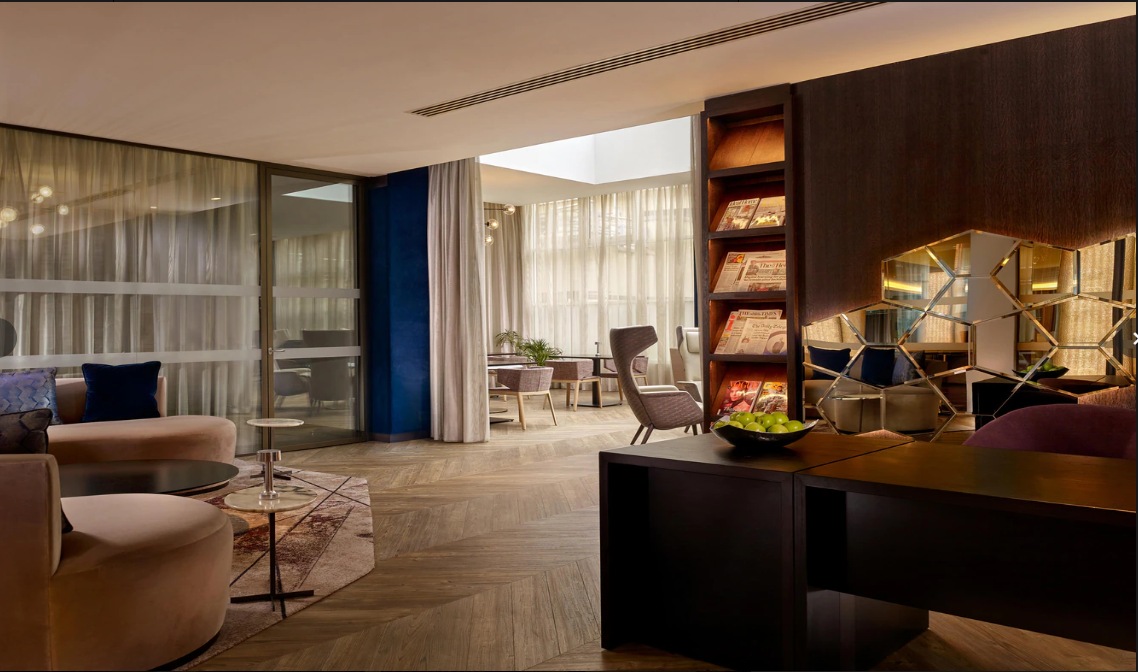
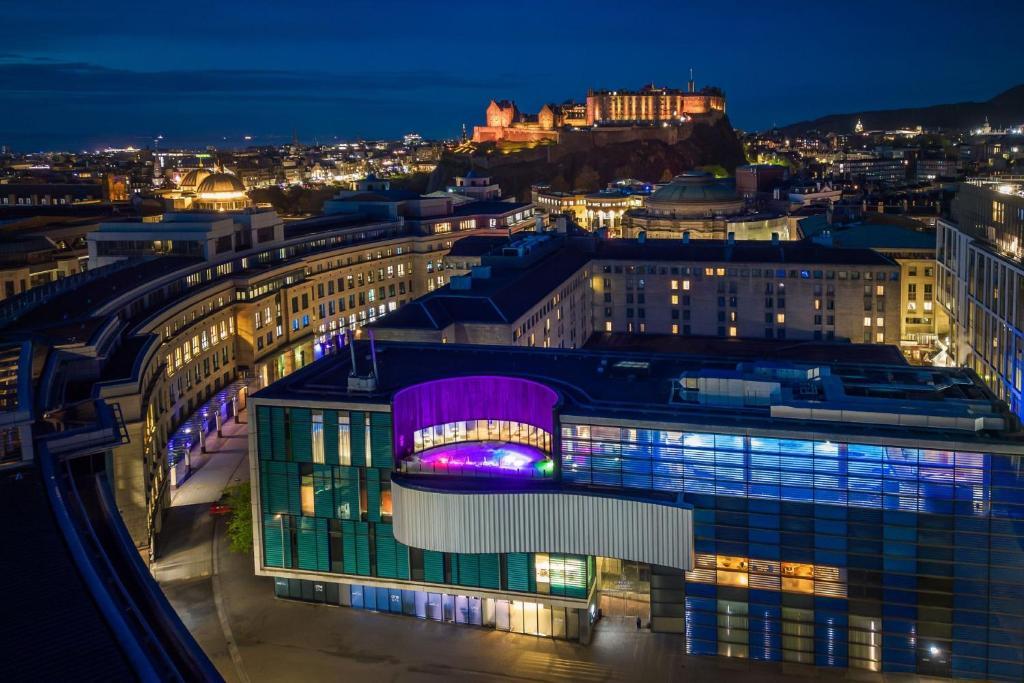
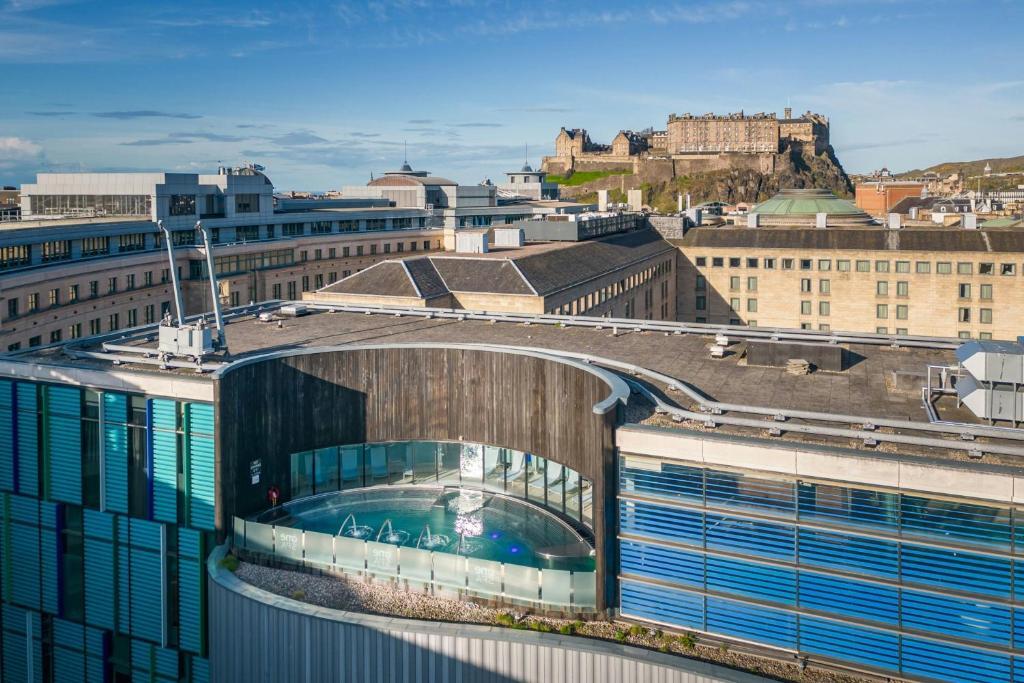
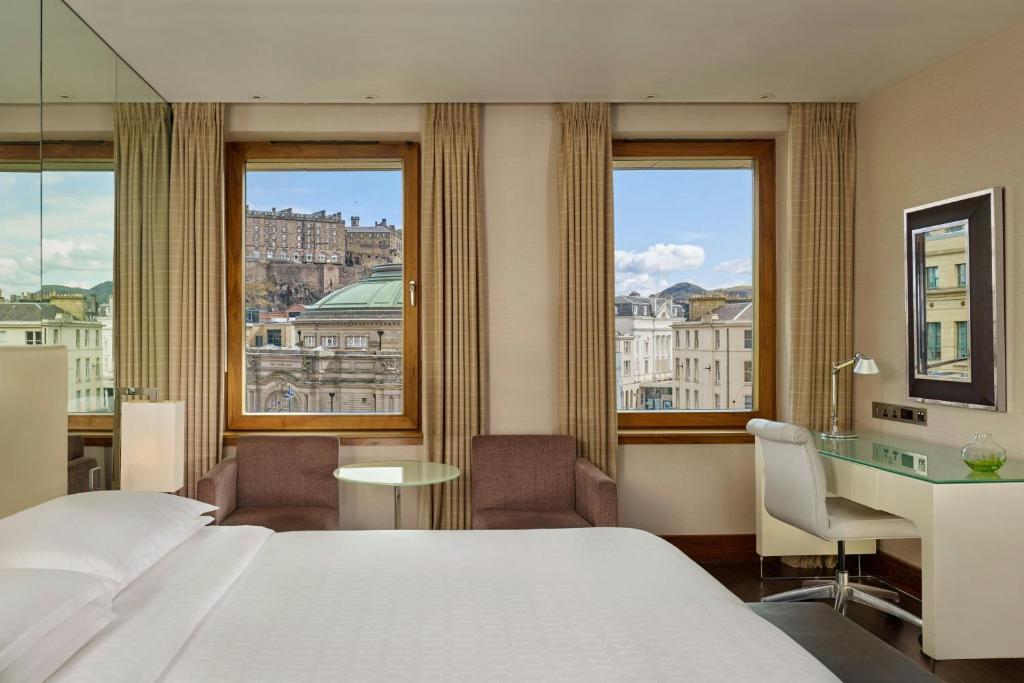
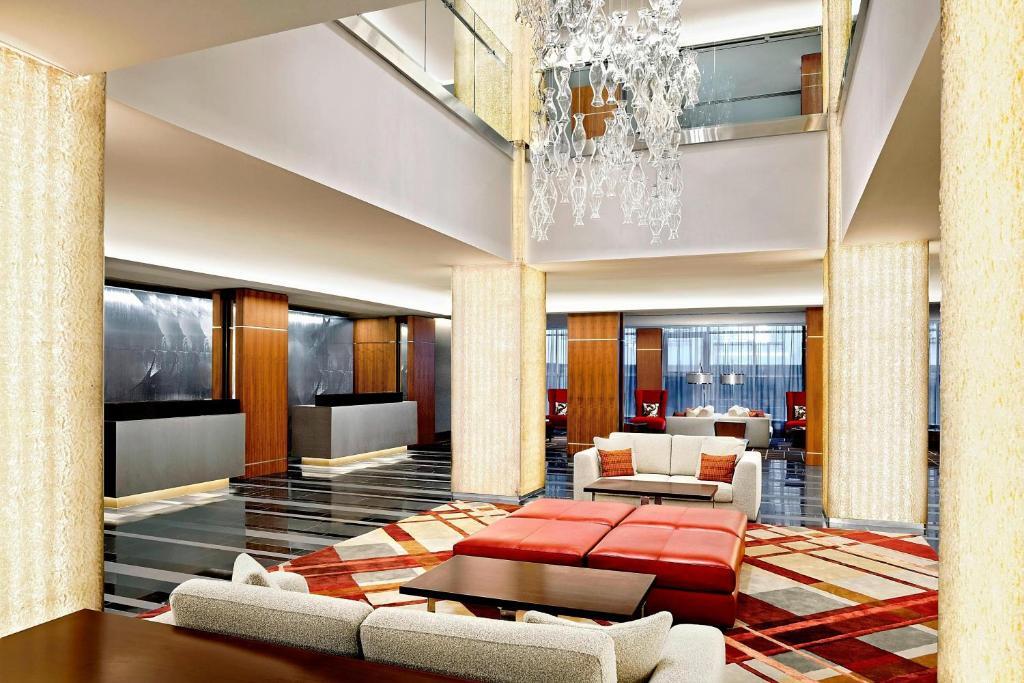
The 2nd CISO 360 UK – 2026 will be hosted at the Sheraton Grand Hotel & Spa in the heart of Edinburgh.

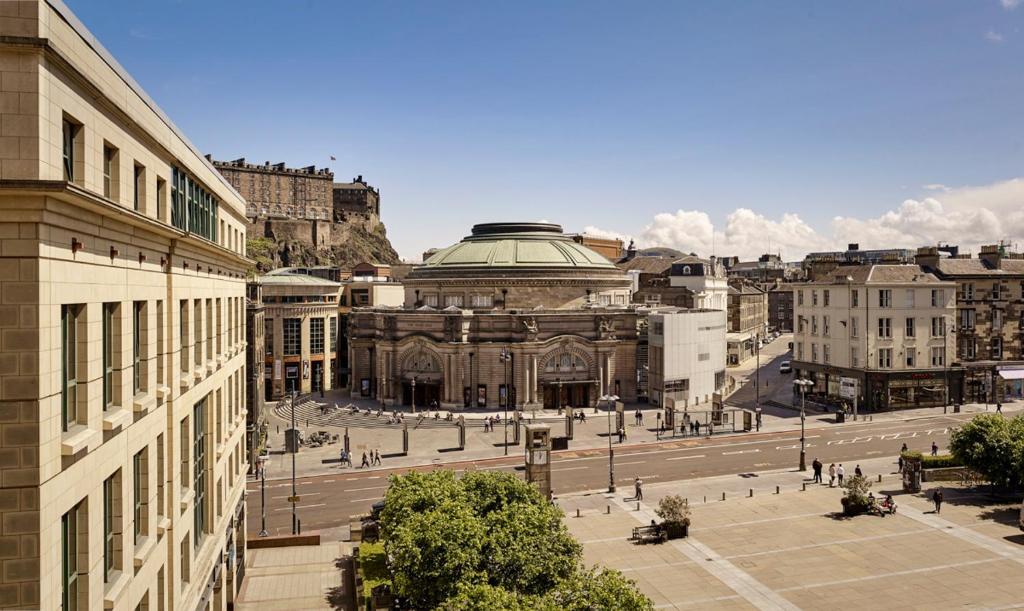
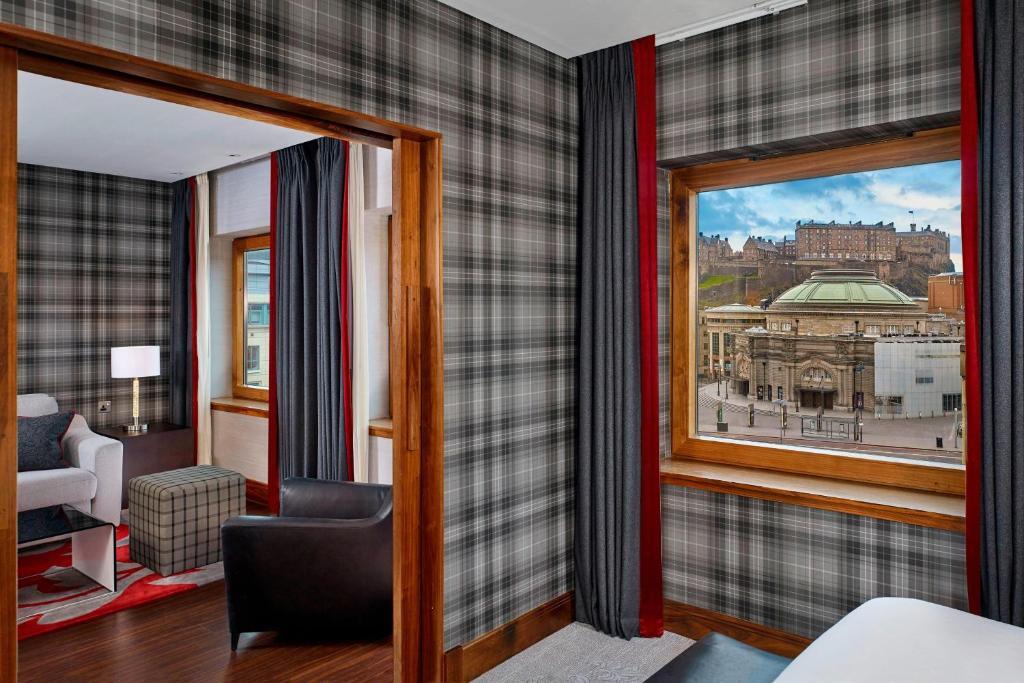
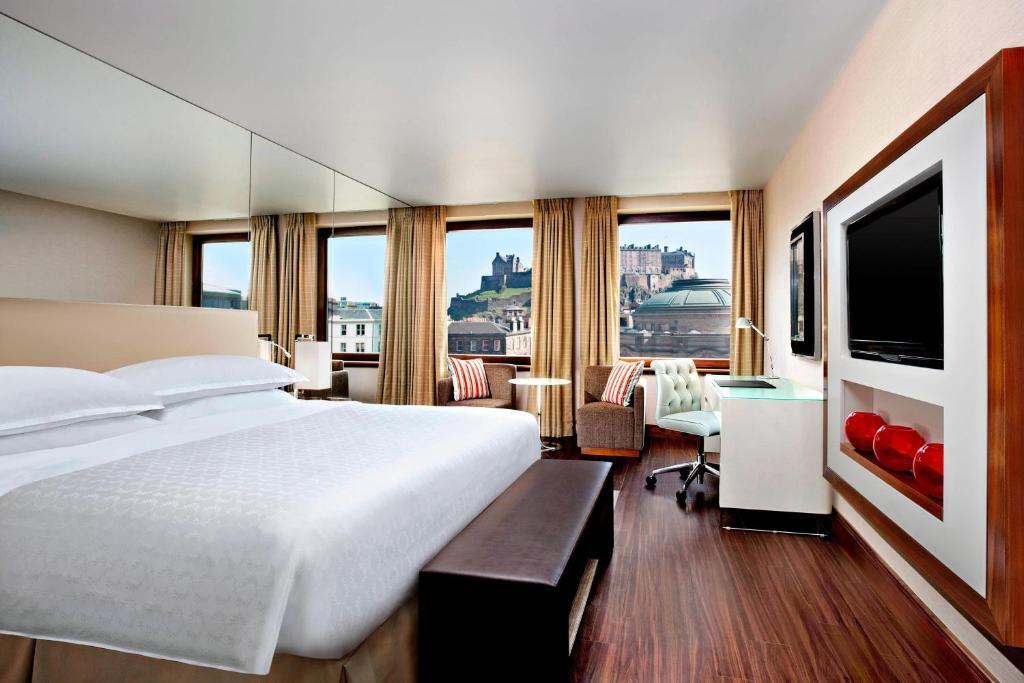
Overlooking Edinburgh Castle, the hotel is situated within the city’s financial district, adjacent to the West End business and entertainment area. It is just a five-minute walk from Princes Street and approximately 500 metres from Edinburgh Castle, offering delegates a central, well-connected setting for two days of focused security leadership dialogue.

Alternative accommodation
If you are looking for alternative accommodation nearby, we can recommend the following hotels, all within 10 minutes’ walking distance from the Sheraton Grand.
The Hoxton, Edinburgh
Four Points Flex by Sheraton Edinburgh
Eleven Stafford Street

Discounted Accommodation

The discounted accommodation at the Sheraton has sold out but please email operations@pulseconferences.com to receive the best available rate for participants of the CISO 360 UKI. Alternative hotels within walking distance can also be found below.

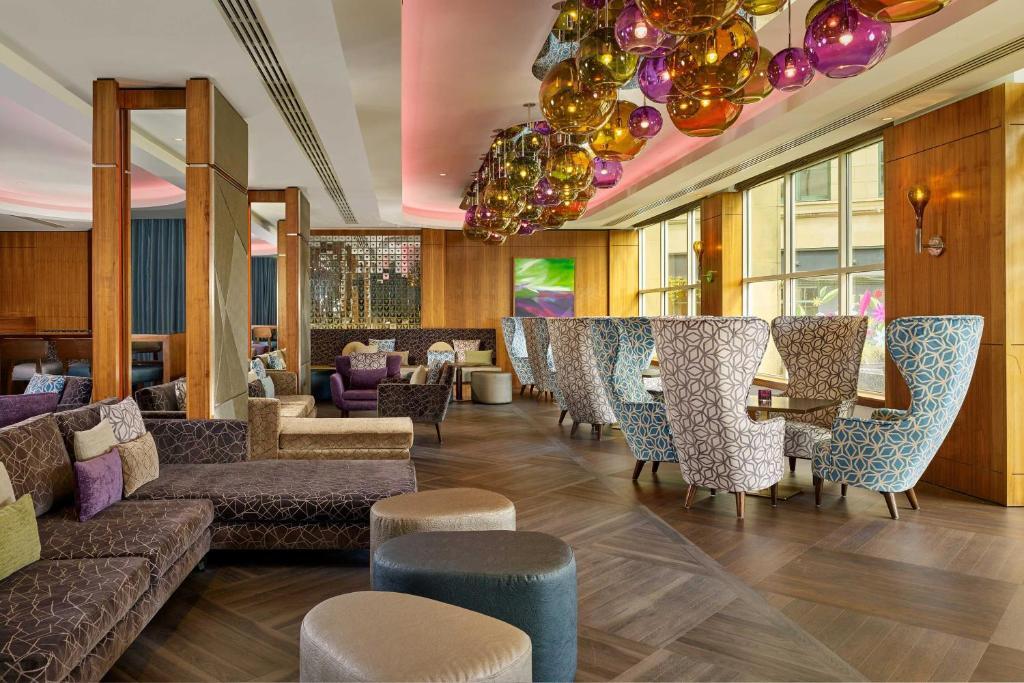
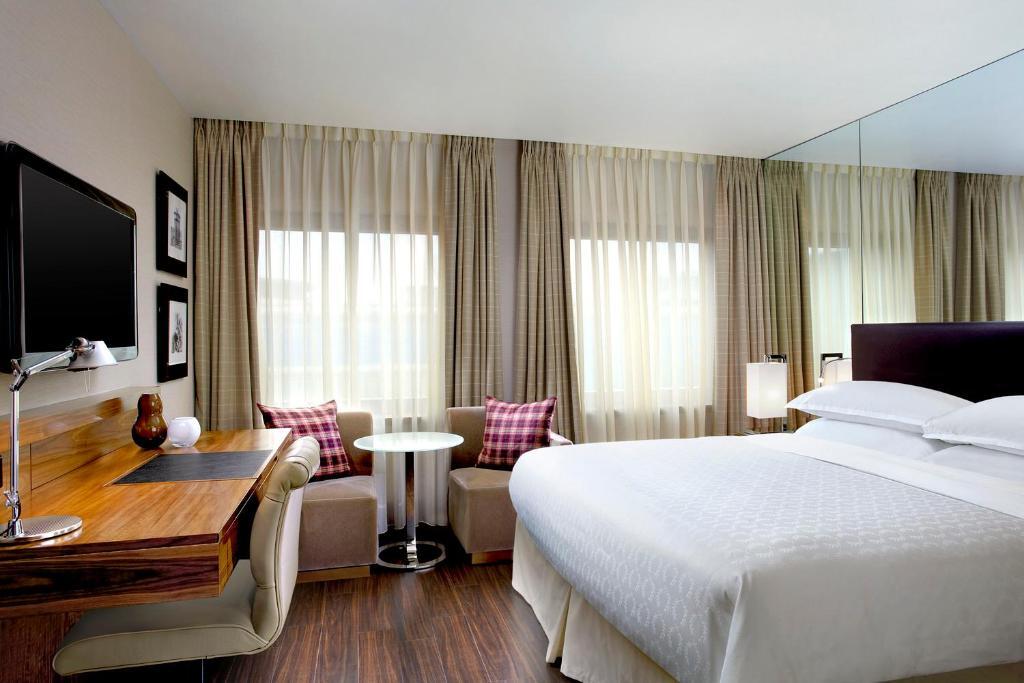
Rooms combine comfort and understated luxury, featuring complimentary Wi-Fi, flat-screen satellite TV, generous seating areas and spacious bathrooms with separate bath and walk-in shower – creating space to prepare, reflect and recharge between sessions.

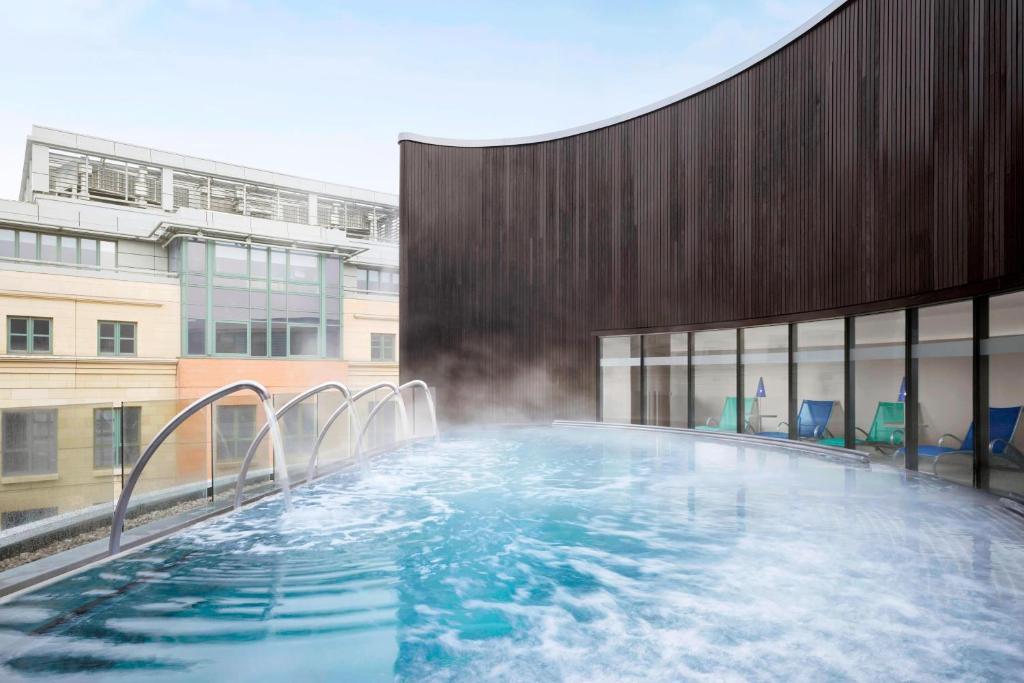
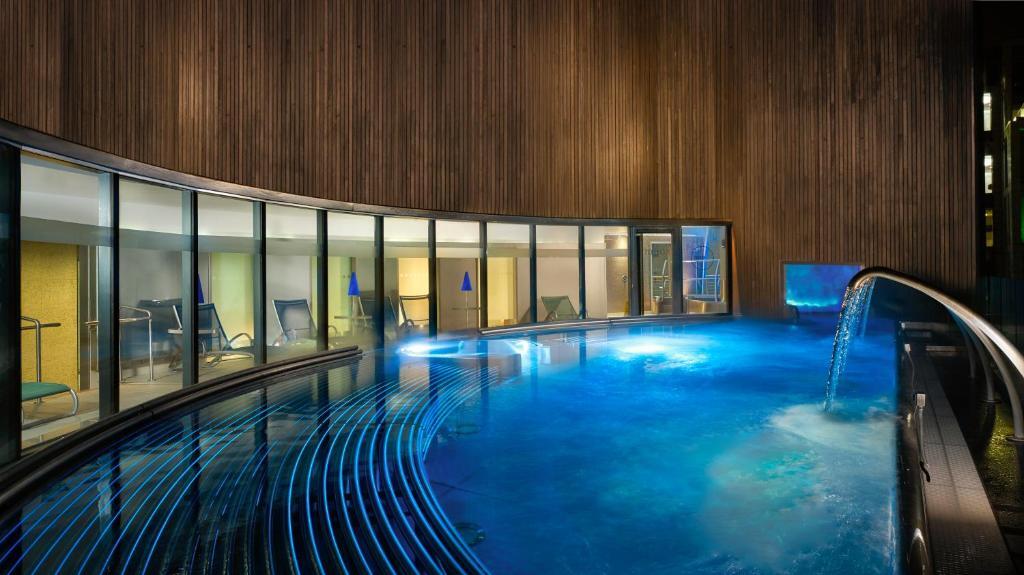
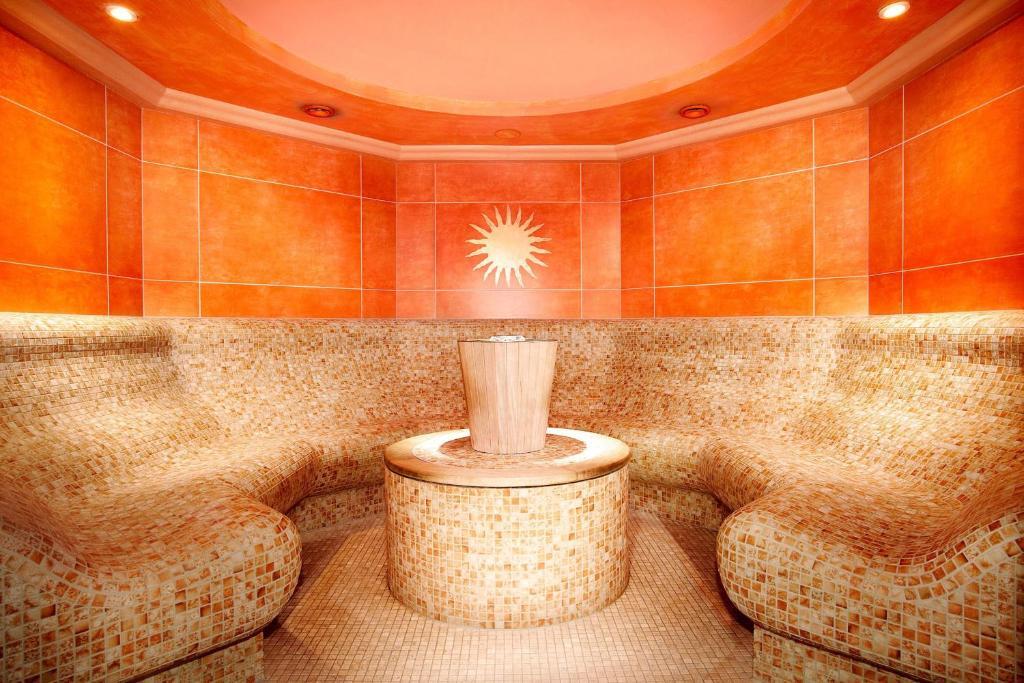
Attendees may also enjoy preferential access to the recently renovated Escape at One Thermal Suite and Rooftop Hydropool, an opportunity to unwind while continuing informal peer conversations. Spa experiences are charged separately and should be booked in advance with the hotel.

Conference Space at Sheraton Grand Hotel & Spa Edinburgh

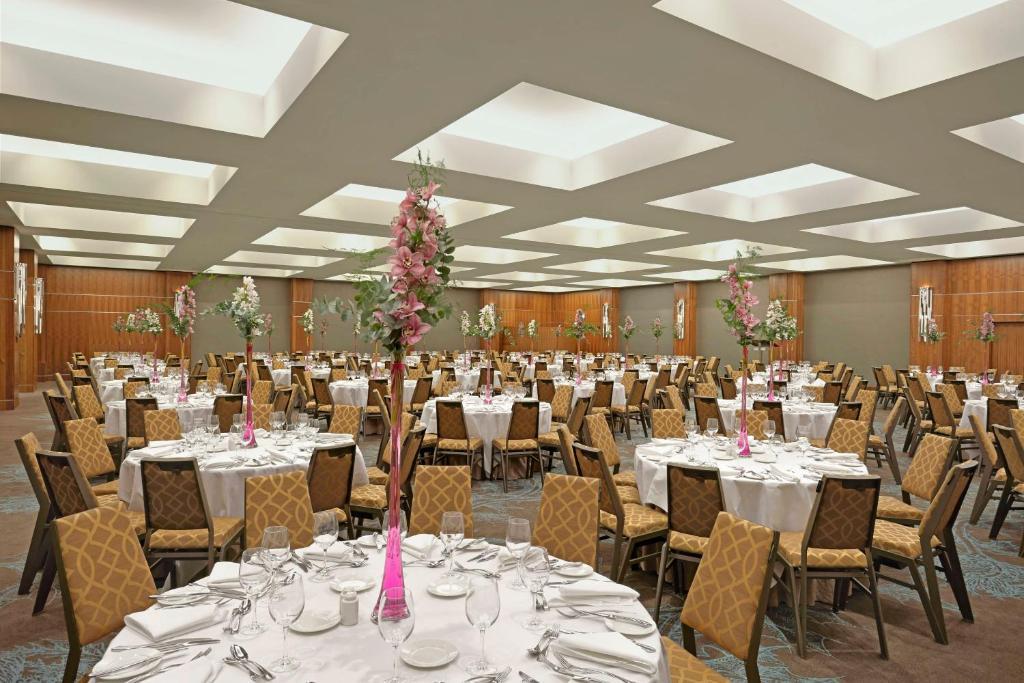
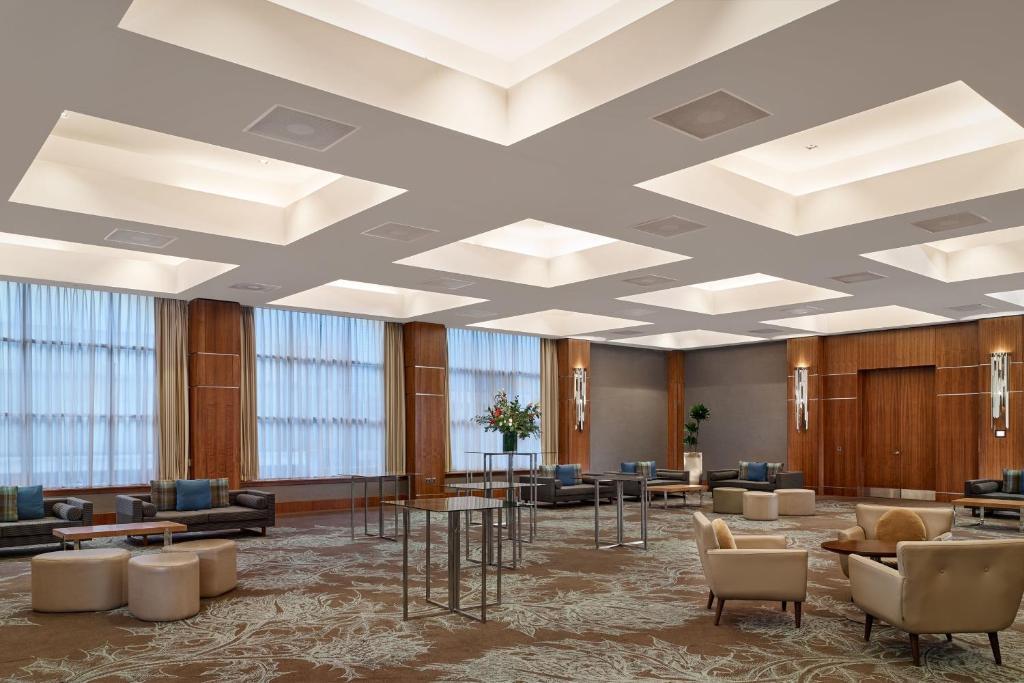
The Edinburgh Suite provides a spacious and comfortable setting for the 2nd CISO 360 UK Conference across both days, offering an environment designed for focused discussion and executive-level exchange.

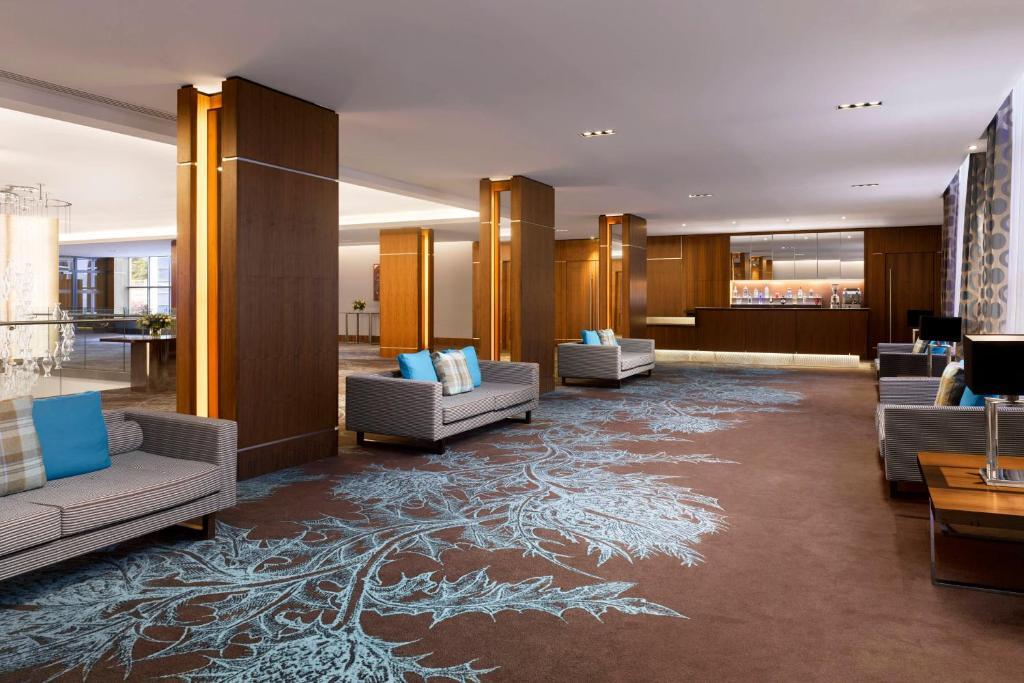
Our Networking and Innovation Hub will be hosted directly outside the suite, creating a seamless flow between conference sessions and peer engagement, encouraging meaningful conversations, solution discovery and continued dialogue throughout the event.

Location – Sheraton Grand Hotel & Spa Edinburgh

Set in Festival Square, this contemporary hotel is located just 1 mile from Edinburgh Waverley Station and approximately 7 miles from Edinburgh Airport.

Adjacent to The Exchange and directly across the square from Usher Hall, the hotel is just a one-minute walk from the Edinburgh International Conference Centre. With convenient taxi access at the main entrance and an additional pedestrian entrance on the second floor, guests enjoy quick and easy walking access to Princes Street and central Edinburgh.

Venue

Testimonials CISO 360 Series

“CISO 360 UKI was one of the most valuable cybersecurity events I’ve attended. What stood out was the quality of conversation. Honest, practical, and grounded in real-world experience. No noise, no generic messaging, just leaders sharing what is actually happening inside organisations today. The panel discussions, particularly around security team morale and resilience, reflected challenges many of us are facing. It created space for open dialogue on prioritisation, leadership, and how we build sustainable security functions. The networking was equally strong. Meaningful conversations with peers, new connections, and shared insights that extend beyond the event itself. A well-run event that brings the right people together to focus on what matters. My biggest takeaway was the importance of decision clarity. Security teams are not only stretched by workload, but by unclear priorities and ownership. The organisations that are making progress are the ones aligning security with business outcomes and making deliberate, informed risk decisions.” Malcolm Kafesu, Global IT Security & Governance Manager, Ontic Engineering & Manufacturing

“The conference was a congregation of true leadership across the speaker and attendees. Vendors were respectful of the ethos of the event and supported having thought-provoking conversations. The presentations were engaging, well-balanced, and covered a large breath of relevant and timely topics. This was a wonderful conference with the attendees made to feel valued and included throughout the event. The overwhelming unity of the collective community, and joint appreciation to resilience being key.” Margus Lind, Vulnerability Management and Assurance Lead, Tesco Bank / Barclays

I found it really insightful, to see and hear from so many CISOs was great
James Hardy, Senior Security Assurance Manager, OVO Energy

One of the most insightful conferences for security professionals, focusing on top class sessions and panels, embedding vendors to provide actual knowledge rather than sales pitches Danielle Sudai, Security Operations and Automation Manager, Deliveroo

Pulse conferences provide a very well-rounded event and great Speakers, great location and relevant vendors
Lee Morton, Head of Cyber Security, GBG plc.

Very well organised event, with effective utilization of the time.
Senior Product Security Architect, Temenos (UK)

A convenient, well organised and highly relevant event with great speakers and topics.
Head of IT Security, Causaly (UK)

Leaders in the field were present in the room and provided adequate knowledge to the discussions.
Manager, Cyber Security Authority (UK)

Very well organised and paced – great spread of participants and topics
Advisor, SH Risk Ltd (UK)

Great presentations and networking opportunity
Lead BISO, Computacenter (UK)

Great blend of discussing key topics, with plenty of opportunities to meet and network with peers.
CISO (UK)

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”

CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”

CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”

Regional Executive, KnowBe4 (The Netherlands)

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”

CTO and Co-Founder, JIT (Israel)

“Great conference! From the beginning, the level of participant engagement was very high. The content was very informative and the presenters very knowledgeable. Every aspect of Global CISO 360 was extraordinarily well done. I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”

Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”

Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well. Content and organization made this an excellent event!”

CISO, Infopercept (UK)

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”

Senior Consultant, DHC AG (Switzerland)

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”

Global Deputy CISO, Cushman & Wakefield

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –

CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”

CISO & DPO, 360 Treasury Systems AG, Germany

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”

GemServ, a Talan Group company (UK)

“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy”

Senior Cybersecurity, Lafarge Holcim

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”

Director, Bestman Solutions

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”

CMO, SailPoint

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”

CEO, Cordery

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”

CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”

Director, Security, Laureate International Universities Malaysia

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”

Senior Account Executive, Hack the Box (Greece)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”

COO, Risk Ledger (UK)

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”

Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”

Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”

CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”

Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”

Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”

Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”

Director, Resilient. World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”

Technology Services Head of Cyber Security, DWP (UK)

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP

“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica

“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!” Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”,

CISO, Channel 4

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV

“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations” Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Excellent conference, brilliantly put together.”
Director, Bridewell Consulting

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

https://vimeo.com/738781773

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP

CISO 360 testimonial videos