Archive · UK and Ireland

CISO 360 UK

This event took place on 2025.

Date2025
VenueThe Castle Hotel, Windsor, UK

Thank you to everyone who attended CISO 360 UK in Windsor this March 2025.

We hope you can join us for the 2nd CISO 360 UK conference! Save the dates. Registration is open for 2026.

2026 Event Details:

Location: Edinburgh
Dates: 28-29 April 2026

CISO 360 UK & Ireland was hosted in Windsor!

Securing Tomorrow, Navigating Complexity, Driving Resilience

CISO 360 UKI, created and hosted by Pulse Conferences, where CISOs and cybersecurity leaders gathered for an energetic and impactful event that is focused on core priorities and by key verticals.

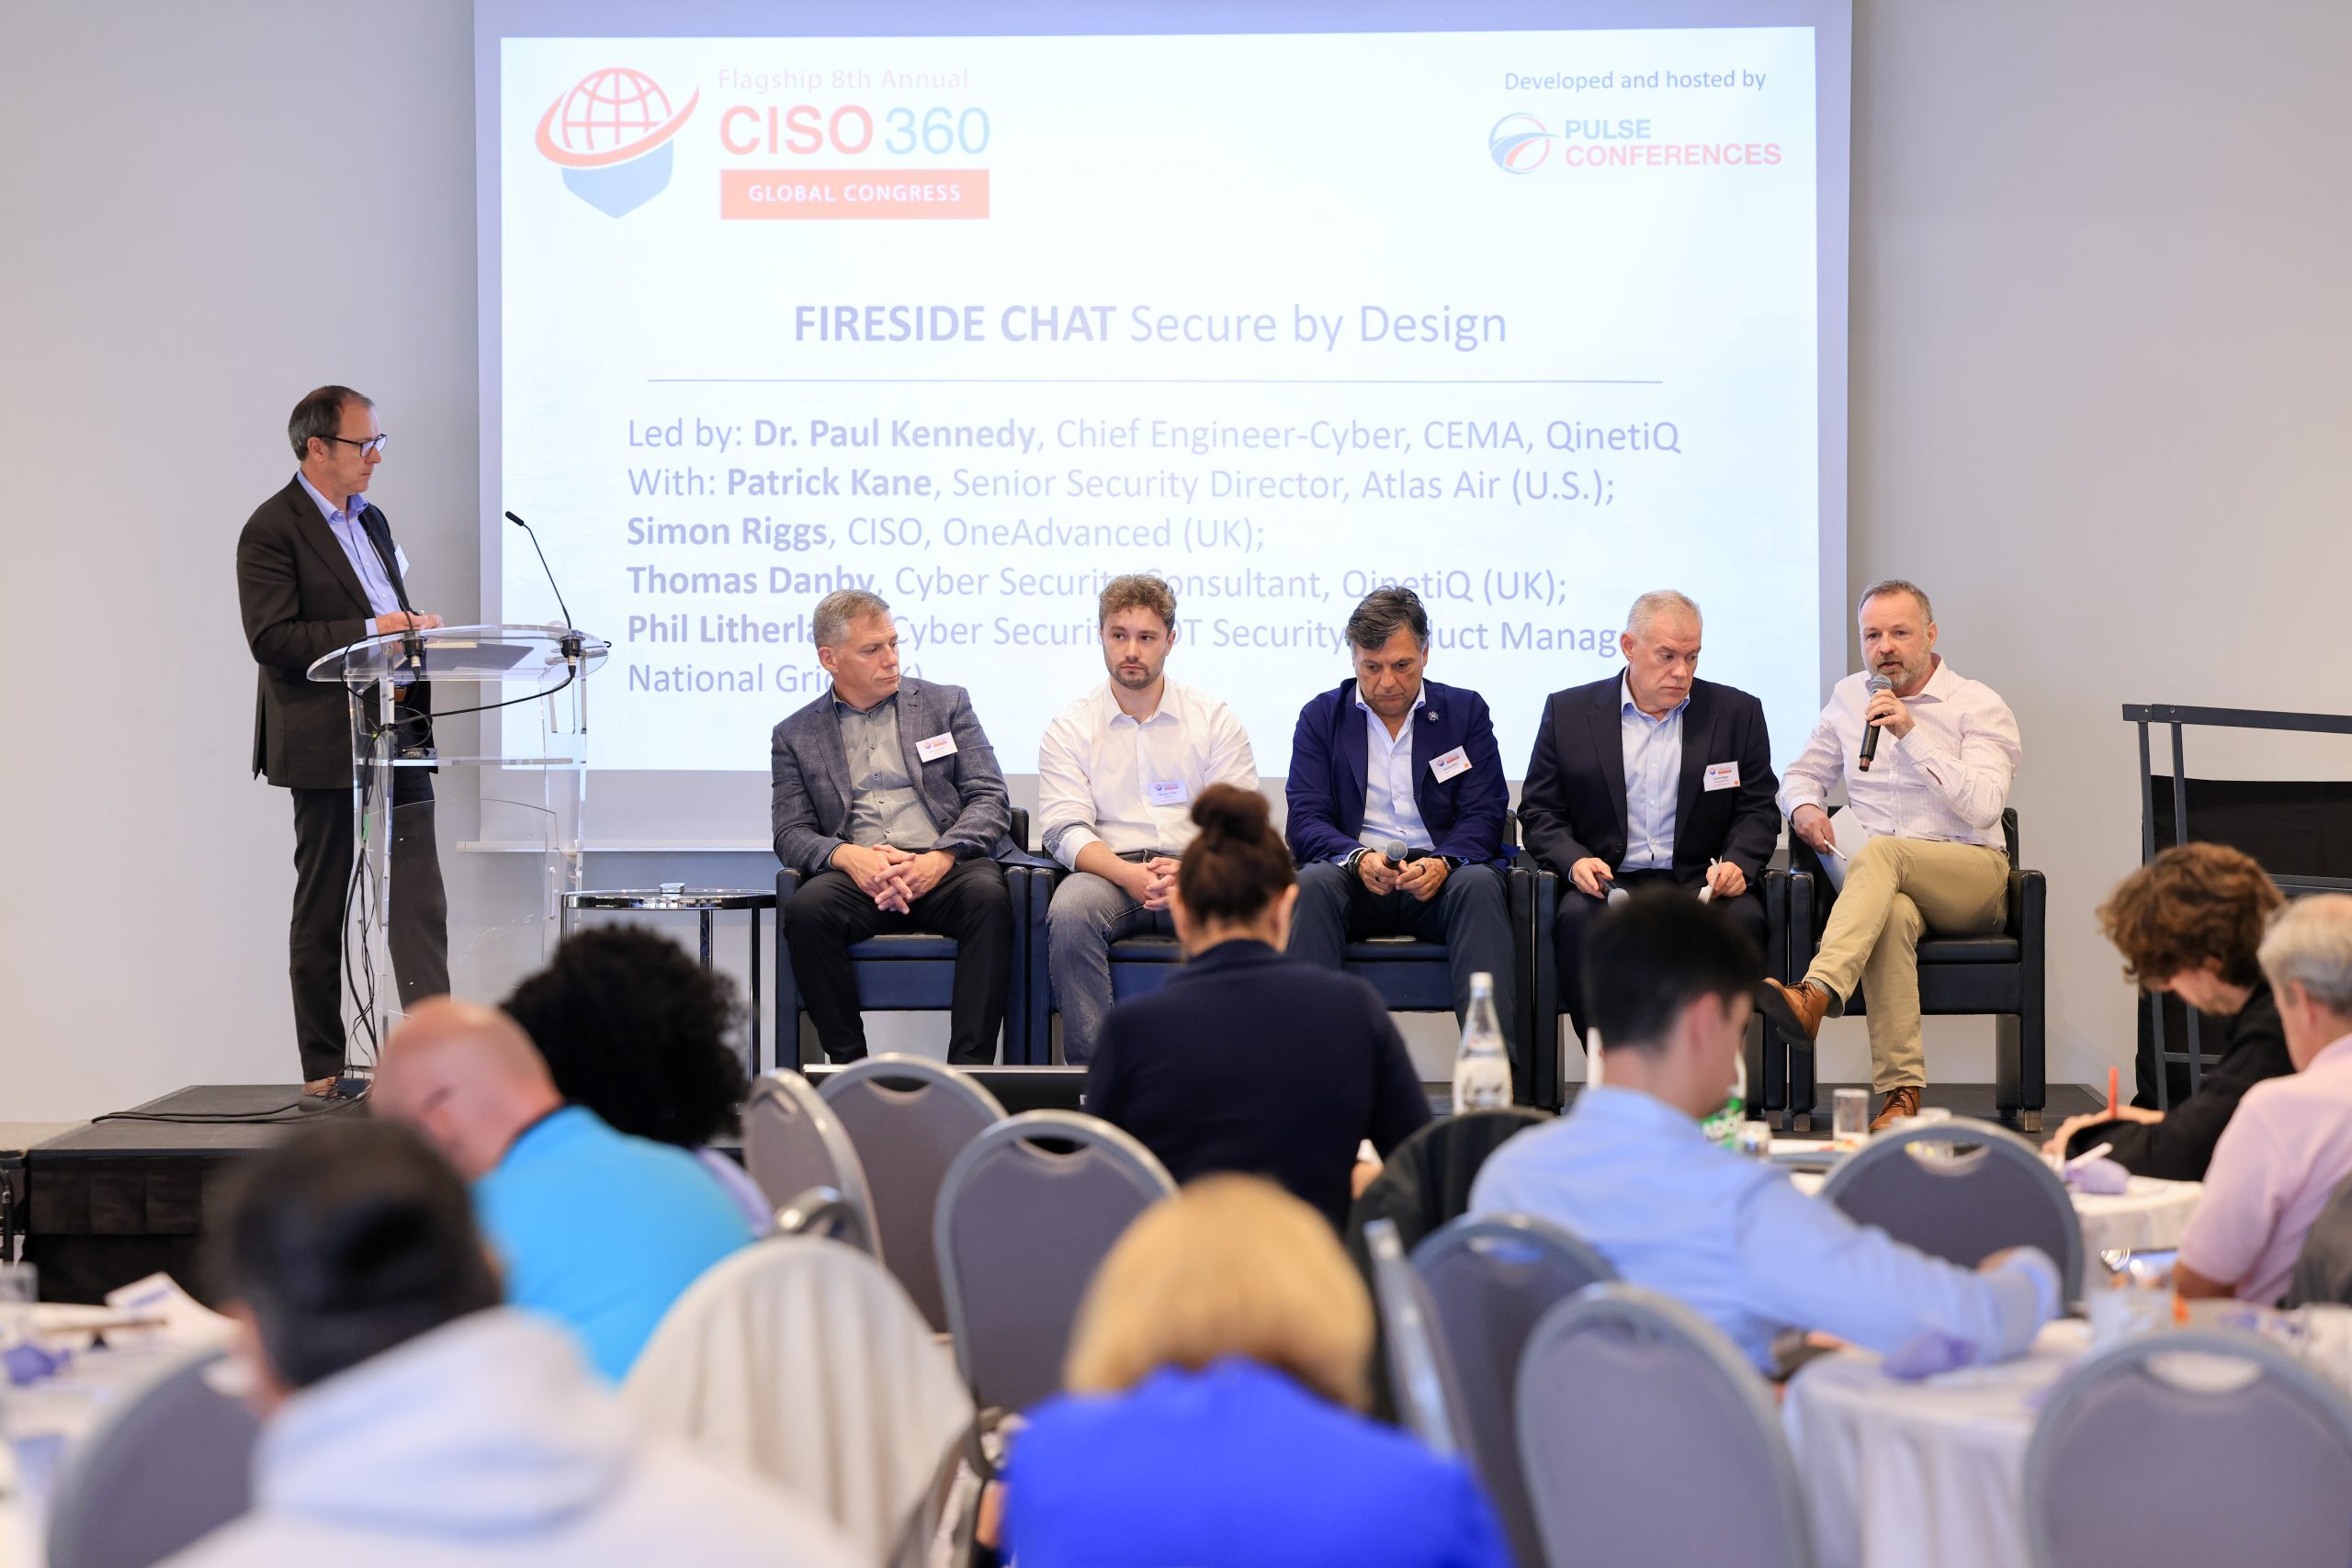
CISOs shared their strategies, exploring emerging trends, and benchmarking the latest tools and tactics to address the rapidly evolving cybersecurity landscape. Participants challenged the status quo through case studies, fireside chats, roundtables, and the highly anticipated CISO 360 Roundtable: AI and Quantum. Evening networking events, cultural experiences, and an exclusive dinner provided the perfect setting for forging lasting professional relationships and strengthening the cybersecurity community.

Event Details:
Location:
The Castle Hotel – Windsor – UK
Dates: 18-19 March 2025

View highlights video from CISO 360 UKI 2025


Key Themes for CISO 360 UKI 2025 included:

  1. AI + Quantum: Prepare for the new frontiers in security
  2. Operational Resilience: First-hand experiences of DORA compliance and surviving and thriving in complex and interconnected threat and regulatory landscapes
  3. Threat Intelligence + Fusion: Leveraging converging trends, challenges and opportunities
  4. CISO GRC Toolkit: Critical updates. What to work towards in 2025? How Are We Strengthening the Foundations? Core Controls for 2025
  5. Supply Chain Security: Navigating risks in an interconnected world

Why Attend?

  • Stay future-focused on AI risks, roles and opportunities: Gain insights to stay ahead of business and technology challenges outside of your immediate sphere.
  • Benchmark with CISOs and cybersecurity practitioners by key verticals: FinSec, EnergySec..
  • Build trusted connections: Progress thought-leadership with leading CISOs and senior practitioners from the UK and Ireland in a trusted, secure environment.
  • Engage in collaborative projects: Participate in dynamic discussions and projects with innovators, investors, and thought leaders.

Be part of this landmark event and leave inspired, connected, and ready to elevate your cybersecurity strategy.

Agenda-at-a-Glance

  • 18 March: CISO 360 Roundtable, Reception and Dinner
    • 3.30 pm-4 pm: Afternoon tea
    • 4 pm-6.30 pm: Quantum AI Bootcamp – A Roundtable discussion, no presentations.
    • 6.30 pm-11 pm: Evening networking reception and dinner included.
    • (Optional) Overnight at the venue, The Castle Hotel Windsor
  • 19 March: CISO 360 UKI Conference
    • 8 am-4.30 pm: Full-day main conference featuring dynamic sessions, expert panels, and networking opportunities.
    • 4.30 pm: Conclusions to depart by late afternoon


CISO 360 UKI Speakers 2025 (partial list)

Carolyn Brown
Chief Information Officer
British Medical Association

Sudha Iyer
Head Cybersecurity Architect
Citi

Dr. Leila Nova
CISO IberoLatAm
Allianz

Lady Olga Maitland
Founder
Defense and Security Forum

Dr Runli Guo
Founder and CEO
AI Dionic

Jonathan Armstrong
Partner
Punter Southall

Steve Hill
Former Group CISO
Credit Suisse

Barry Coatsworth
Cybersecurity Advisor
UK Government

Dr. Sally Leivesley
Managing Director, Newrisk Limited
Member, Register of Security Engineers and Specialists

Sandip Wadje
Managing Director and Global Head of Emerging Technology Risks
BNP Paribas

Dr Meera Sarna
CEO
Cystel

Alan Jenkins
The Cyber Security Navigator

View highlights from a recent CISO 360 event


“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to the Pulse team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good! Afterwards the meal sponsored by Qualys was fantastic. Pulse go out of their way to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

Anchor Partners 2025

Many thanks to Sponsors of CISO 360 UK 2025 (partial list)

Platinum Protectors

Sapphire Sentinels

CISO 360 Innovators

Supporting Organisation

Provisional Timings

If you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda teampulse@pulseconferences.com.

Evening social events are included in the CISO 360 experience. All participants are invited and encouraged to join the networking events.

Tuesday 18 March 2025
CISO 360 Roundtable

Quantum Insights and AI Opportunities – Sharing intelligence, predictions and preparations.

A focused, peer-to-peer gathering designed to explore the opportunities, risks, and preparations for AI and Quantum Computing. Join senior cybersecurity leaders for an afternoon of meaningful discussions and networking in a trusted, closed-door setting.

15:00-16:00 Arrivals, light lunch/ afternoon tea

16:00-18:30 CISO 360 UK Roundtable Discussion – AI Opportunities and Risk Mitigations. Quantum Preparations

18:30-20:30 Networking Drinks

20:30-23:00 Dinner

Wednesday 19 March 2025
CISO 360 Conference

Cybersecurity Strategies to Build Resilience and Trust

Join us for a full day of insights, collaboration, and innovation tailored for cybersecurity leaders. This event will bring together CISOs and cybersecurity practitioners as well as CIOs, regulators, investors and security professionals across industries to explore strategies for addressing today’s most pressing challenges.

08:00-08:30 Coffee

08:30-09:00 Opening

09:00-10:45 Sessions

10:45-12:00 Networking Break and 1-2-1 Speed Meetings

12:00-13:30 Lunch

13:30-15:45 Sessions

15:45-16:15 Networking Break and Sponsors’ Prize Draw. Goodbyes

Speakers CISO 360 UK 2025

The 2025 programme is currently being developed, the latest event flyer and programme can always be found on the downloads tab.

If you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda sara.hook@pulseconferences.com.

Meet our 2025 Panel of CISOs and Luminaries (partial list)

Alan Jenkins

The Cyber Security Navigator

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

Barry Coatesworth CISO

UK Government

Barry Coatesworth, FCIIS, CISSP
Senior Security Government Advisor & Cybersecurity Leader
Barry Coatesworth is a globally recognized cybersecurity expert with a track record of shaping security strategies in financial services, public sector, and critical infrastructure. As a trusted advisor to governments and global enterprises, he has led security transformations, built high-performing teams, and developed regulatory frameworks that protect millions. Currently advising the UK’s national pension dashboard program, Barry plays a key role in securing the financial well-being of millions of UK citizens. A recipient of the IFSEC Global Influencer Award and a Lifetime Achievement Award at the Cyber OSPAs, he continues to mentor future cybersecurity leaders while speaking at major industry conferences.

Carolyn Brown

Chief Information Officer, British Medical Association

The BMA’s mission is to look after doctors so that they can look after you.

The CIO is accountable for the development and delivery of the IT & Digital Strategy and capabilities which support the BMA Group in the fulfilment of its mission.

Danielle Sudai

Security Operations Manager, Deliveroo

Danielle Sudai manages the Security Operations and Automation team at Deliveroo, managing and optimising all Organisational Cloud Assets and SaaS solutions’ security monitoring and identifying real-time threats and security breaches.

Danielle was also a Cloud Security Engineer. In her career, she co-engineered a CSPM internal solution, reviewed and governed different cloud services from a security perspective, Cloud IAM misconfigurations and KMS services automation.

Emili Evripidou

Senior ICT Security and Risk Manager, Klarna

Emili Evripidou, CCSP, CISM, CISSP, PMP, MSc

Emili is a seasoned risk management leader with 15 years of experience in financial services, payments, and energy. She specialises in Governance, Risk and Compliance helping organisations navigate complex security challenges. Currently a Senior Manager at Klarna Bank, she is driving AI innovation in risk assessment. Emili has held leadership roles at Accenture, Deloitte, EY, and Hellenic Bank, advising on major transformation projects. Passionate about diversity in security, she founded the Women in Security group with 3,000+ members. She is a recognised speaker at industry conferences and a contributor to leading cybersecurity publications.

Ivan Milenkovic

Vice President Cyber Risk Technology, Qualys

Ivan Milenkovic is a Vice President for Cyber Risk Technology at Qualys, a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions designed to streamline and consolidate customers’ security and compliance solutions in a single platform. Ivan has over 20 years of experience aligning complex technology landscapes and fluctuating risks with business objectives. His professional background includes serving as Group CISO at a $4.8bn multi-national BPO, leading a cyber advisory business, and holding multiple advisory board positions. Ivan is a Certified Information Security Officer (S-CISO®) and instructor for the CISO2.0 course by SECO Institute. His ongoing pursuit of domain knowledge continues at Lancaster University, where he is a Cyber MBA candidate in the first NCSC-accredited programme in the UK.

Jake Bernades

CISO, Anecdotes

Jake Bernardes is a seasoned CISO with extensive experience spanning technical consultancy, advisory roles, and executive leadership. Throughout his career, Jake has worked and lived across the globe, amassing deep insights into building and scaling security programs for growth-stage and enterprise organizations alike. A proven expert in developing robust security and IT functions, Jake equally specializes in driving go-to-market strategies for security-focused products, particularly for international companies expanding into the U.S. market. His holistic approach to cybersecurity enables businesses to align their security posture with operational and strategic goals, ensuring resilience in today’s evolving threat landscape. Jake’s dedication to innovation and his practical understanding of security challenges make him a trusted partner to companies navigating complex regulatory environments and seeking scalable security solutions. He was an early adopter of many GRC solutions and have served in multiple customer advisory boards prior to joining Anecdotes, where he continues to lead with a vision of empowering organizations through smarter, data-driven compliance management.

James Clifford

Regional Manager, Exabeam

James started his career in Information Security in the late 1990’s working in the desktop anti-virus software field, progressing to email security in the early 2000’s where he joined Microsoft’s security team during the trustworthy computing era. James now works in the threat detection and investigation response marketplace holding the position of Regional Sales Manager at Exabeam. During his spare time, he is an avid volunteer at The National Museum of Computing located at Bletchley Park.

Jaya Agnihotri

Purple Team Lead, ICBC

Jaya is a seasoned cybersecurity professional with 13 years of specialized experience in the financial sector and consulting services, including roles at Capital One, Wells Fargo, Deloitte, and Accenture. She possesses a unique blend of expertise across various cybersecurity domains, such as Cyber Assurance, Governance, Risk, and Compliance, Product Security, and Cloud Security.

In her current role at ICBC Standard Bank, Jaya leads the Purple Team and independently manages various cyber assurance projects.

She excels at leading cross-functional teams of varying sizes, optimizing security processes, minimizing cyber risk, and ensuring compliance with industry regulations.

Jonathan Armstrong

Partner, Punter Southall

Jonathan is an experienced lawyer based at Punter Southall Law in London working on compliance & technology. He is also a Professor at Fordham Law School teaching a new post-graduate course on international compliance and a Director at L-EV8 working to increase cybersecurity skills on boards.

Jonathan’s professional practice includes advising organisations on risk and compliance across Europe. This includes work on:

  • Prevention (e.g. putting in place policies and procedures);
  • Training (including state of the art video learning); and
  • Cure (such as investigations and dealing with regulatory authorities).

Jonathan has handled legal matters in more than 60 countries. He has handled more than 250 data breaches and has worked extensively with technology legislation including GDPR, NIS2, DORA & the EU AI Act. He has conducted a wide range of investigations of various shapes and sizes, a request to appear before a UK Parliamentary enquiry and led clients through real and simulated bet-the-company situations.

Jonathan is also regarded as an acknowledged expert on AI and he currently serves on the New York State Bar Association’s AI Task Force looking at the impact of AI on law and regulation. Jonathan also sits on the Law Society AI Group.

Jonathan is a co-author of LexisNexis’ definitive work on technology law, “Managing Risk: Technology & Communications”. In addition to being a lawyer, Jonathan is a Fellow of The Chartered Institute of Marketing. He has spoken at conferences in the US, Japan, Korea, Canada, China, Brazil, Singapore, Vietnam, Mexico, the Middle East & across Europe.

Jonathan qualified as a lawyer in the UK in 1991 and has focused on technology and risk and governance matters for more than 25 years. Jonathan has been selected as one of the Thomson Reuters stand-out lawyers for 2024 – an honour bestowed on him every year since the survey began. Thomson Reuters has listed Jonathan as the 6th most influential figure in risk, compliance and fintech in the UK. Jonathan is listed as a Super Lawyer and has been listed in Legal Experts from 2002 to date.

Jonny Herd

VP of Information Security & Enterprise Tech, Paddle

A highly effective and resourceful business leader who thrives in SaaS businesses with complex and challenging environments with a proven record of dealing with business issues and addressing a company’s most difficult challenges.
A history of building and managing globally distributed and culturally diverse teams as well as collaborating with stakeholders across all areas of the business to deliver security and compliance objectives, digital transformation projects and strategic business goals.
Draws on an extensive background in operations and solution engineering and combines with broad security expertise to transform, change and future-proof very large-scale cloud infrastructures and SaaS business operations

Haydn Brooks

Co-Founder and CEO, Risk Ledger

Coming from a background in cyber risk specialising in supply chain security, Haydn quickly recognised the huge process issues, sunk cost, lost opportunities, and valuable business hours wasted by clients and suppliers alike, all trying to run disparate supply chain assurance programmes in a mutually exclusive way. This led Haydn to co-found Risk Ledger, the technology platform that combines a security governance platform with a secure social network. Haydn’s team is innovating and pushing mutual supply chain assurance and security governance into the twenty second century.

Forbes List 30 Under 30 – Manufacturing & Industry
Winner of the 2019 Cyber Den Award sponsored by the UK Government’s National Cyber Security Centre
Winner of the 2019 Most Innovative Cyber Company Award sponsored by TechUK.

Kev Eley

Vice President UKI, Exabeam

Kev Eley is Vice President UKI at Exabeam. For nearly three decades he has delivered expert insight and solutions to the IT and software industry, dedicating 15 years specifically to cybersecurity and fraud detection. He has been personally involved in over 150 security information and event management (SIEM), User and Entity Behaviour Analytics (UEBA) and Security Analytics deployments, with a core focus on customer success and value realisation.

Previous to Exabeam, Kev held notable positions at IBM, Microsoft, TrapX Security, Egress Software Technologies and LogRhythm. He possesses a keen interest in all aspects of cyber and its impact on business and society and has worked across a wide variety of sectors, including financial services, utilities, the public sector and more.


Dr. Leila Nova

CISO, IberoLatAm Allianz (Germany)

Leila, currently, heads the Cyber Risk Management at Allianz Group, a global leader in insurance and asset management. With prior experience at SWIFT and EUROCLEAR, she has a strong understanding of the challenges faced by organisations in balancing cyber risk and compliance. With a PhD in physics and a background in teaching and research, she is a sought-after speaker on the topic of cyber security for executives. Additionally, her advocacy in the field of AI for good highlights her dedication to using technology for the greater good and promoting sustainable solutions to save the environment and species.

LR

Lorne Rolinson

CYBER Community Manager and Product Associate, The Hacking Games

Lorne is a computer scientist with a background in philosophy and a passion for cybersecurity. A recent Oxford graduate, she has been involved in the cybersecurity community since she was 11. Now a Product Associate at The Hacking Games, she explores the intersection of security, technology, and ethics.

Leandro Ferreira

Head of Cybersecurity, Brazil Superior Court of Justice

Leandro Ferreira is a cybersecurity expert with extensive experience in digital security for public institutions. He led the cyber crisis response at Brazil’s Superior Court of Justice (STJ), managing one of the country’s most high-profile cyber incidents. He has advised government bodies on cybersecurity resilience, delivered talks at national and international conferences, and co-authored

I Am Hacked! What Now?

, a book on cyber crisis management. Currently, he is engaged in initiatives to enhance cybersecurity maturity across Brazilian public institutions, bridging the gap between policy leaders and operational cybersecurity.

Mantas Marcinkevicius

Chief Information Security Officer (CISO), Lloyd’s List Intelligence

Currently the CISO of a 300-year-old “startup”, Mantas is redefining Cybersecurity with a focus on convenience, transparency, and business alignment – cutting through fear and friction to drive real, sustainable security outcomes. With over a decade of technical and leadership experience spanning public and private sectors, he specialises in cyber risk, regulatory compliance and security strategy, and enabling security as a competitive advantage. Known for this pragmatic approach, he helps organisations navigate complex threats while ensuring security fuels growth rather than hinders it.

Dr. Meera Sarma

CEO, Cystel and Member of All Party Parliamentary Group on Cyber Security

Dr Meera Sarma spent years as a cybersecurity researcher profiling hackers, examining facets of cyber-crime and the deep links to physical terrorism and the dark web, and subsequently, a PhD on hackers (information systems) at the University of London. Meera has worked with a number of public and private sector agencies in consulting roles. With 20 years of cumulative experience in consulting as well researching and publishing in areas of cybersecurity, digital transformation, and AI/Quantum Computing, and contributing to the UK’s Parliamentary Office of Science and. Technology as an expert on Cybersecurity and Quantum Computing. Dr Sarma set upCybersecurity and Quantum Computing company, Cystel, that is underpinned by scientific research and years of experience in the field.

Mark Logsdon

CISO, NHS

Mark is Chief Information Security Officer for NHS England having joined from UKHSA (Test and Trace) where he was head of Cyber Assurance and Oversight. With over 30 years of experience in security, Mark has held a number of high profile roles in the public and private sectors. He has a strong business focus seeing security as a business enabler. At every opportunity Mark seeks to manage the needs of business against those of security and risk. Outside of work, Mark works to raise much needed funds for NSPCC Childline. He is a member and former Chair of the WhiteHat Ball Committee which to date has raised over £2M for the NSPCC. less

Martyn Booth

CISO, dunnhumby

Martyn is Chief information security officer at dunnhumby, the world’s largest consumer data analytics organisation. He runs a large team and is an experienced cyber security practitioner, with over 20 years experience in the field, spanning big-4 consulting and running large teams. He advises multiple VCs and start ups, operates at board level and is seen as a strategic partner to the businesses that he advises. His technical background, coupled with his MBA for Durham, enables him to operate at the highest levels of business with a deep technical understanding of the security domain.

Dr. Nishant Sood

Director, L-EV8 RTC

Nish is triple qualified in medicine, law and economics. He has started, run and advised businesses and governmental organisations at board-level across multiple industries and sectors, in the UK and abroad. Nish originally trained and worked as a doctor for a number of years, both in the NHS and internationally, predominantly in the fields of acute medicine and intensive care. After cross-qualifying into law, he worked as a lawyer at a leading law firm, initially specialising in corporate and commercial work, with a focus on the health sector, before expanding into intellectual property. Subsequently, Nish left law establishing a health clinic in the UK and a health consultancy business abroad, and remains active in the latter. He later rejoined the law to project manage and provide specialist support in a multi-jurisdictional pharmaceutical litigation. Following its successful conclusion, he remained part-time in law, but pivoted towards the commercial aspects of law firms – leading on strategy, consultancy and innovation – while also maintaining his personal business interests, before having to give up the former due to expansion of the latter. With his varied educational and professional background, Nish has acquired a wealth of board-level experience of a diverse nature. Some of this has been obtained by serving on the Board of his own companies as Chair (or other Director in rotation), while other elements have been acquired through experience over many years of advising other companies’ or institutions’ boards as an appointed member, Non-Executive Director, secondee or specialist advisor, in both private and public sectors. Outside of formal work, Nish provides career advice and mentoring for university students as an Alumni Fellow, and volunteers for a national medical charity’s support helpline for patients and their carers.

Lady Olga Maitland

President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International (UK)

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.

Dr. Oliver Farnan

Head of Research, Reliance Cyber

Dr. Oliver Farnan has expertise in offensive security, advanced threats, and nation-state cyber policy. With a rich background in cybersecurity, Oliver has held diverse roles, including as an officer in the Royal Signals, a postdoctoral research position at Oxford University, and as the Global Head of Information Security for the INGO Oxfam. Holding a PhD in Cybersecurity, Oliver combines academic research with practical security operations, empowering organisations to effectively navigate emerging cyber threats.

Paul Colnan

CISO, NewDay

Paul Colnan is the CISO at NewDay, financial services. Paul has 15 years of cyber security experience, including advising some of the world’s largest brands and he works with the board to enable secure and trusted commerce. He has an ‘ethical hacker’ background, which helps him tackle complex security issues, but he also cares about driving effective change through clear leadership and communication. Paul has been a CISO in various sectors, including fintech, logistics, and manufacturing, and before joining NewDay he was CISO at ION, he was an Executive Director at JP Morgan Chase, where he held security roles in retail banking, M&A and cloud platform security teams. He was CISO of Revolut and Group CISO of Unipart Group. Paul likes aviation and is pursuing his private pilot’s licence in his spare time.

Phil Pate

VP and GM EMA, Alert Media

A successful SaaS GTM leader with proven history of delivering exceptionally high growth within international markets. I build and lead successful first and second line sales teams to deliver new market penetration & growth in multinational enterprise customers.
I believe that it is the team that makes the difference, and focus on inspirational leadership, teamwork and individual empowerment to cultivate high performance and growth. While providing servant leadership to optimise productivity, remove impediments and foster development.

Specialties: Leadership, GTM Strategy, New Business, New Market Penetration, Management, Organisational Capability, SaaS, Sales, Enterprise Software, IT Managed Services, GRC, Operational Resilience, Risk, DevOps, Governance, Compliance, Major Incident Response.

Dr Runli Guo

Founder and CEO, AI Dionic

Dr Runli Guo, the Founder and CEO of AI Dionic. She is the driving force behind the organisation’s mission to deliver enterprise-grade AI agents with trust, security, and technological sophistication. As a former CISO with a PhD in artificial intelligence, Runli identified a pressing need for robust and reliable AI agents designed specifically for enterprise use. AI Dionic’s current focus is on the applications of Agentic AI in proactive reduction of enterprise risks including strategic risks, financial risks, operational risks, compliance and regulatory risks, tech and cyber risks as well as supply chain risks. Previously Runli has held leadership roles at FTSE 250 and Fortune 500 companies. She was the former CISO at Gett, IT Security Manager at AXA Health, and the Global Head of Digital Cybersecurity Initiatives at Marsh McLennan. Winner of the “Top 30 UK CISO” Award in 2022 by CSO Online.

Sean Turner

CISO, Twinstake

Sean is a CISO and a software engineering leader. He has worked at multiple FinTech companies including a leadership position at cryptocurrency exchange, Kraken. His technical specialties include Identity Management and Cloud Native Computing.

Sudha E. Iyer

Chief Cybersecurity Architect- Digital Assets, Data, Citi

Sudha is the founding member of Post quantum working group at FSISAC and specialises in financial sector Cryptography focused architectures such as digital assets, confidential compute and post quantum cryptography. Experienced visionary with a demonstrated history of building high performing teams that deliver mission-critical results for financial industry risk reduction. A people focused leader with ultimate focus on results in production through inspirational approaches. Ability to leverage strong understanding on complex business, technical and risk baselines and apply quantitative techniques to collaboratively create solutions to business problems. Deep expertise in building measurable and scalable ROI focused risk remediation strategies, operating models in financial space to prepare the industry and my current enterprise towards the next digital readiness.

Sandip Wadje

Managing Director and Global Head of Emerging Technology Risks, BNP Paribas

Sandip Wadje is Managing Director and Global Head of Emerging Technology Risks at BNP Paribas since 2017 where he is focused on governance and oversight of emerging technology domains such as cloud, artificial intelligence, digital assets, and quantum. Sandip also leads group-wide oversight on all aspects of “outside-in” intelligence collection with a particular focus on external attack surface, geopolitical risks, social media liquidity risk, cyber-posture of corporate clients and emerging threats such as deep fakes or synthetic identities. Sandip also represents the bank at various external forums. Sandip has been a member of European Cybercrime Centres (EC3) Financial Services Advisory Group since September 2017 and is also co-chair of European Financial Roundtable (EFR) Cyber Experts Group since February 2020. EFR comprises of 25 leading Financial Institutions in the UK & Europe and is represented by Chairman / CEO’s of the participating institutions. He has over 24 years of experience in cybersecurity, operational risk, IT risk, internal controls, and compliance. Sandip has a hands on technology background and his previous stints include BT Global Services, RiskIQ, SecureWorks, KPMG, JPMorgan Chase, and Deloitte.

Dr Sally Leivesley

Managing Director Newrisk Limited UK, Member of the Register of Security Engineers and Specialists, international media commentator on cyber, catastrophic risks, terrorism and nuclear war (UK)

Dr Leivesley, sally@newrisk.com works on generic solutions to catastrophic risks to critical infrastructure across all disciplines and contributes practical applications to government policy and business. She has been a Panel adviser to for the British IET and CPNI supported publication for Cyber Security in the Built Environment.
As an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business Dr Leivesley has worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks.
As an international media commentator she has commentated for BBC World Service and other news outlets on extreme threats – Chinese spy balloon over USA nuclear missile site, uranium package at London Heathrow airport, cyber; terrorism; aviation losses; nuclear reactor explosions; Kabul 2021 evacuation; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents.

Dr Leivesley has held international scientific meetings on issues of catastrophic risk including risks of emerging nuclear weapons, infrastructure resilience including cyber, Covid-19 solutions and hazardous near-earth objects.
She was director of two disaster recovery units in Australia (weather and chemical incidents) and trained by British Home Office as Scientific Advisor holding a Cold War appointment as on all aspects of nuclear war.
PhD London University; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute for Defence Studies, and the British Information Assurance Advisory Council Community.

Steve Hill

Former Group CISO, Credit Suisse, Strategic Adviser; Strategic Adviser, PwC and Dell Technologies

Steve is an independent Senior Board Adviser helping clients navigate geopolitical risks, national security, and cybersecurity/resilience challenges.

Steve served in the UK Government for over three decades in a variety of National Security roles countering transnational threats such as terrorism, espionage and proliferation. In 2017, he was Deputy Director in the National Security Secretariat of the UK Cabinet Office, with responsibility for aspects of cybersecurity policy. Subsequently, Steve served in a senior of senior executive roles at Credit Suisse including Global Head of Technology, Cyber and Third Party Risk, head of Operational Resilience and Group CISO.

Steve is a senior visiting research fellow at King’s College, London, and a member of the Dell Technologies Global Security Advisory Board.

Zofia Kolodziej

Marketing & Operations Executive, The Hacking Games

Zofia is a Marketing & Operations Associate at The Hacking Games. She holds a Bachelor’s degree in Psychology with Criminology, as well as a Master’s in Mental Health. Her interest in cybersecurity was sparked when her family became victims of a cybercrime. Having previously worked towards accreditation as a behavioural psychotherapist, Zofia now focuses primarily on the human aspect of cybersecurity. Outside of her professional career, Zofia has an impressive athletic background as a former member of the Polish National Volleyball Team

Platinum Protectors

Qualys

Qualys, Inc. (NASDAQ: QLYS) is a leading provider of disruptive cloud-based security, compliance and IT solutions with more than 10,000 subscription customers worldwide, including a majority of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and automate their security and compliance solutions onto a single platform for greater agility, better business outcomes, and substantial cost savings.

The Qualys Enterprise TruRisk Platform leverages a single agent to continuously deliver critical security intelligence while enabling enterprises to automate the full spectrum of vulnerability detection, compliance, and protection for IT systems, workloads and web applications across on premises, endpoints, servers, public and private clouds, containers, and mobile devices. Founded in 1999 as one of the first SaaS security companies, Qualys has strategic partnerships and seamlessly integrates its vulnerability management capabilities into security offerings from cloud service providers, including Oracle Cloud Infrastructure, Amazon Web Services, the Google Cloud Platform and Microsoft Azure, along with a number of leading managed service providers and global consulting organizations.

www.qualys.com

Risk Ledger

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

Interested in learning more? Visit https://riskledger.com/.

Exabeam

Exabeam is a global cybersecurity leader that delivers AI-driven security operations. High-integrity data ingestion, powerful analytics, and workflow automation power the industry’s most advanced self-hosted and cloud-native security operations platform for threat detection, investigation, and response (TDIR). With a history of leadership in SIEM and UEBA, and a legacy rooted in AI, Exabeam empowers global security teams to combat cyberthreats, mitigate risk, and streamline security operations.

Learn more at www.exabeam.com.

Reliance Cyber

Reliance Cyber delivers world class cybersecurity services tailored to the unique needs of our customers. With extensive in-house expertise and advanced technology, we protect organisations across a wide range of sectors—from enterprise to government—against the most sophisticated threats, including those from nation-state actors. Our teams safeguard critical assets, people, data, and reputations, allowing customers to focus on their core business objectives with confidence.

www.reliancecyber.com

Sapphire Sentinels

Data

Data is the fastest growing attack surface in the world. Cyera is a pioneer in the data security space that empowers security leaders at Paramount Pictures, Mercury Financial, and others, to discover their data attack surface, control the use of data, monitor, detect, and quickly remediate risk. What makes Cyera unique is its agentless design that deploys in just five minutes across any environment – and its AI-powered classification engine that auto-learns over time, and delivers 95% accuracy. With Cyera, security leaders can focus on enabling their business to safely use data in all the ways they see fit – both now, and into the future.

www.cyera.io

Control Risks

Control Risks is a global specialist risk consultancy that provides threat monitoring and security intelligence for the world’s leading organisations.

Think of us as your team of experts on watch for you 24/7, covering all areas of risk, security, crisis management and incident response.

We identify the risks and potential threats you might face; helping you to prepare and respond with the knowledge and skills you need to protect your people, business, data, and assets.

We also watch for any reputation risks. This way, you’ll be ready to make informed decisions about any incidents that may affect your operations – quickly.

We can seamlessly integrate with your existing risk management program and team. Instantly bolstering your capabilities with ‘on-tap’ access to the depth and strength of our risk and security expertise.

www.controlrisks.com/one

CISO 360 Innovators

AI Dionic

AI Dionic’s mission is to deliver enterprise-grade AI agents with trust, security, and technological sophistication. Our founders have identified a pressing need for robust and reliable AI agents designed specifically for enterprise GenAI adoption. AI Dionic’s current focus is on the applications of Agentic AI in proactive reduction of enterprise risks including strategic risks, financial risks, operational risks, compliance and regulatory risks, tech and cyber risks as well as supply chain risks.

www.ai-dionic.com

AlertMedia

AlertMedia helps organizations protect their people and business through all phases of an emergency. Our award-winning threat intelligence, emergency communication, and travel risk management solutions help companies of all sizes identify, respond to, and recover from critical events faster and with greater confidence. AlertMedia supports critical communication for thousands of leading businesses—including DHL, JetBlue, Coca-Cola Bottling, In-N-Out, and Walmart—in more than 130 countries.

Learn more at www.alertmedia.com

BSS

BSS helps you manage 3rd Party Security Risks with optimized processes, coordinated assessments, and advanced cyber tools. Our practical approach cuts through the noise to reveal real risks. BSS supports your company’s transformations and daily demands, acting as an expert, friendly extension of your team. Our results align with your risk frameworks and reporting formats. Our unique blend of skills and platforms translates complex issues into business terms, empowering all teams to make informed decisions. BSS assists 3rd parties in improving their security and conducting critical tests to understand risks. Beyond initial assessments, BSS offers ongoing monitoring and investigation of real-world issues, helping you present a compelling, evidence-based risk story.

020 7936 8999
Cyber3RM@bss.uk.com
www.cyber3RM.com

Supporting Organisation

ISF Black Removebg Previewcrop

Founded in 1989, the Information Security Forum (ISF) is an independent organisation that is driven by its Members – ranging from Fortune 500 and Forbes 2000 listed corporations, to public-sector bodies and government departments.

Our business-driven solutions provide organisations with the guidance, tools and methodologies needed to tackle the wide-ranging governance, risk and compliance challenges impacting businesses around the world today.

www.securityforum.org

Who Joins?

By Designation

  • Chief Information Security Officer (CISO)
  • Chief Security Officer (CSO)
  • Director / Head of Cybersecurity
  • Director / Head of Cyber Threat Intelligence
  • BISO / CIRO
  • CTO, CIO, CRO
  • Chief Security Architect / Senior Security Architect
  • Director / Head of Security Infrastructure
  • Director / Head of Networks, Applications, Cloud
  • Director / Head of Technology Innovation
  • Director / Head of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer

By Verticals

  • Financial Services – including Insurance
  • Energy – power, water and critical national infrastructure companies
  • Extractives – mining, oil and gas
  • Pharmaceuticals and health
  • Consumer goods
  • Manufacturing
  • Retail
  • Transport and logistics
  • Government departments

Venue and Accommodation

The Castle Hotel Windsor

18 High St, Windsor SL4 1ER
www.castlehotelwindsor.com

CISO 360 UK will be hosted at the historic and elegant Castle Hotel, in the heart of Windsor.

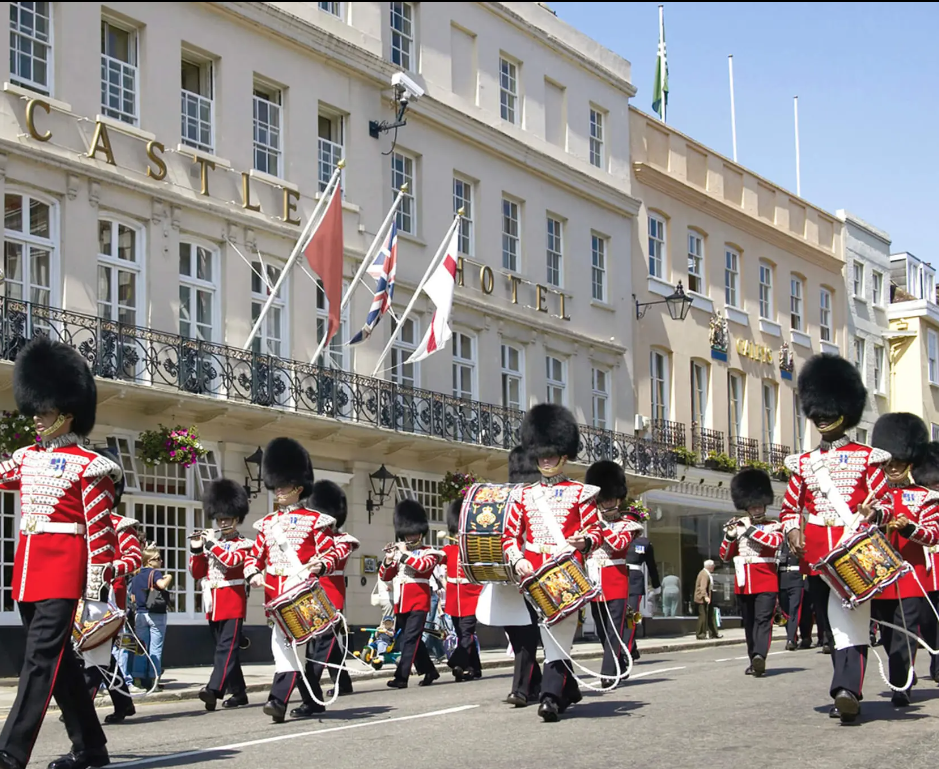
The Castle Hotel Windsor is situated amongst some of the most historic examples of architecture in the United Kingdom. The hotel itself dates back to the 1600s and sits opposite the magnificent Windsor Guildhall, with royal attractions such as Windsor Castle.

As one of the most opulent buildings in Windsor, it is clear to see why the aristocracy has played such an important role in The Castle Hotel Windsor’s history. With eight Royal Warrants, it is renowned worldwide for its links to the British monarchy. Today, The Castle Hotel Windsor retains this reputation and has been lovingly restored to preserve the atmosphere and elegance of its rich history.

Discounted Accommodation

Pulse can offer a special rate of £180.00 per room per night including breakfast based on single occupancy. (*£10 per person supplement for Double Occupancy).

To book your discounted accommodation:

  • Call the hotel directly 01753 851 577 (option 1 for reservations) or email reservations@suttonhotelcollection.com and quote reference 334562 to get the discounted accommodation rate.
  • Rooms are limited and only available until 12th March
  • Credit/Debit card details are required to guarantee the reservations. No payment will be taken from the card unless authorised to do so by the guest.
  • Rooms are available from 3:00pm on the day of arrival.
  • *Cancellation policy for all bedrooms: 30 days prior to arrival.

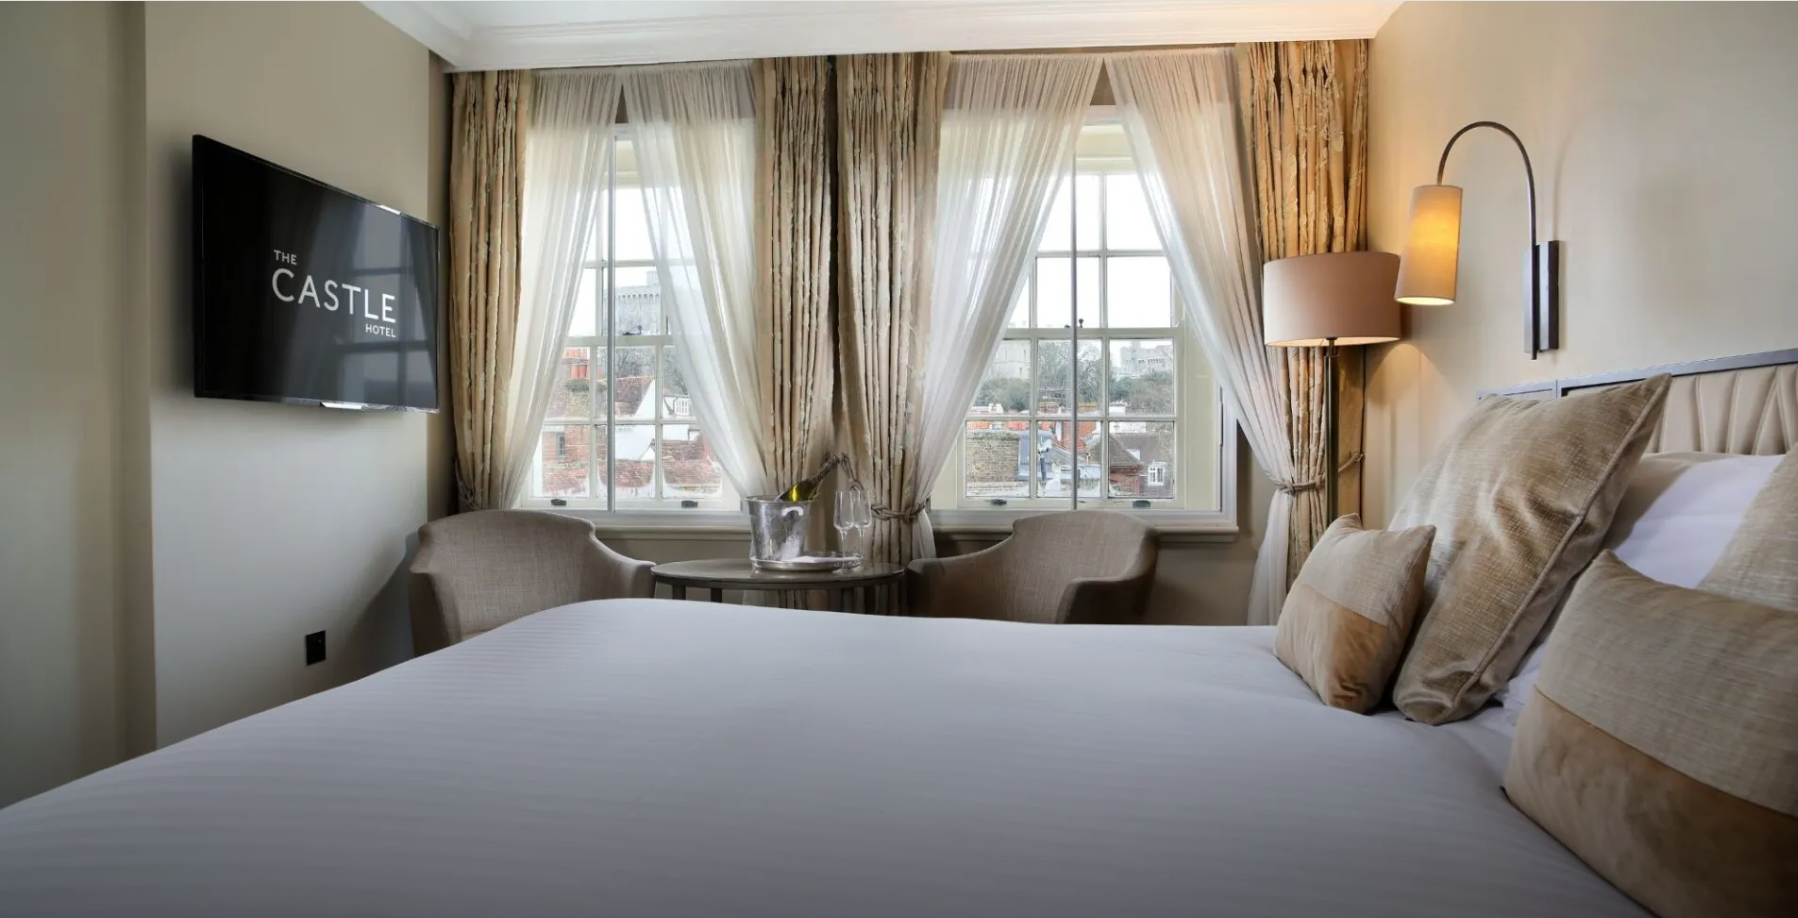
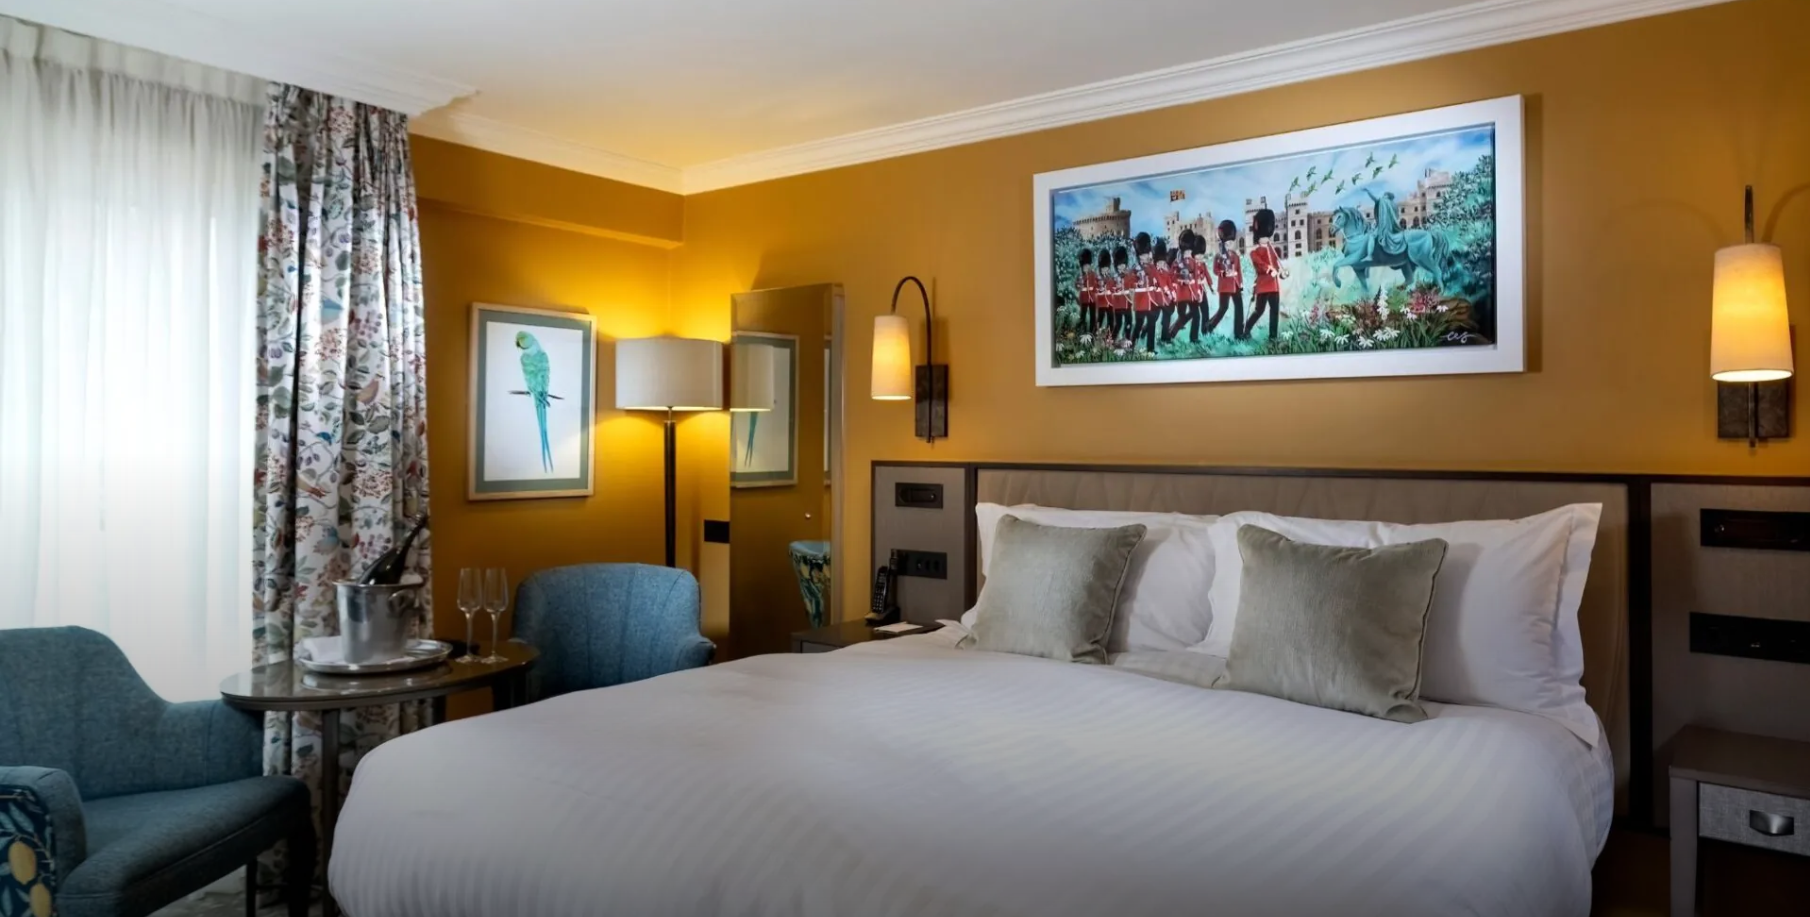
The Castle hotel offers elegant and classic bedrooms that all have that little extra touch that you need from a stay away from home. Blending historic features with contemporary amenities including bespoke artwork in selected rooms to deliver the outmost comfort and relaxation. Beds made for dreaming, sleek interior design details, flat screen TVs and complimentary mineral water, organic toiletries and high-speed WiFi.

Conference venue

The Castle Hotel offers Windsor’s largest events centre, boasting 10 versatile and fully equipped meeting rooms. Having achieved both a Gold Green Meetings award and retained the Gold Green Tourism Award for the second consecutive year,

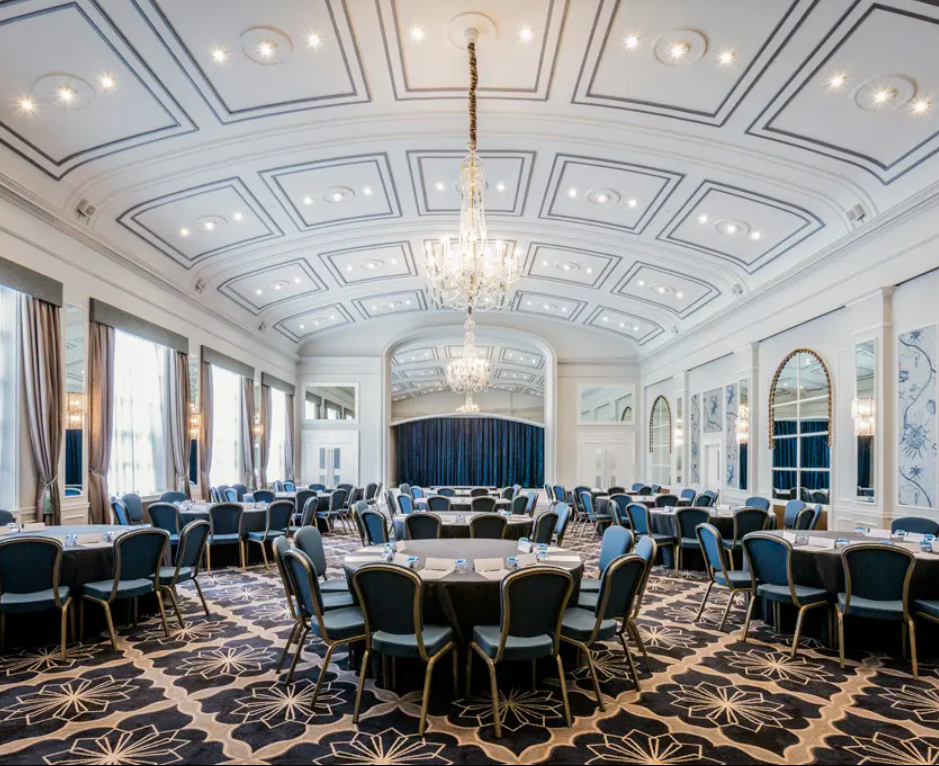
CISO 360 UK will be hosted in the Windsor Suite, Windsor’s largest and most iconic ballroom. With its breath-taking vaulted ceilings and majestic chandeliers, the Windsor Suite has a rich history and has played host to royalty and aristocracy.

CISO 360 UK will take over the the full conference centre exclusively so our networking hub will be hosted right outside the main ballroom with a separate connected space for our speed meeting sessions. The castle hotel event centre offers plenty space for all our participants to network together.

Location

The Castle Hotel Windsor
18 High St, Windsor SL4 1ER
www.castlehotelwindsor.com

The Castle Hotel has an excellent location in the centre of Windsor. The hotel is only a few minutes’ walk from both Windsor & Eton Central and Windsor and Eton Riverside train stations.

By Car

If you are using a sat nav to reach our car park, please input the postcode SL4 1ER and the entrance is via Bachelors Acre. We can accommodate over 100 cars on a first-come, first-serve basis and overnight parking costs £30 per vehicle. The hotel also have a charging point for electric vehicles.

By Train

Two major train stations are nearby: Windsor Central and Windsor Riverside. From here, guests can reach London Paddington or London Waterloo in a little under an hour.

By Plane

The Castle Hotel Windsor is conveniently accessible for both local and international visitors. Heathrow Airport is just 15 minutes’ drive away.

The Castle Hotel Windsor

Testimonials CISO 360 Series

Very well organised event, with effective utilization of the time.
Senior Product Security Architect, Temenos (UK)

A convenient, well organised and highly relevant event with great speakers and topics.
Head of IT Security, Causaly (UK)

Leaders in the field were present in the room and provided adequate knowledge to the discussions.
Manager, Cyber Security Authority (UK)

Very well organised and paced – great spread of participants and topics
Advisor, SH Risk Ltd (UK)

Great presentations and networking opportunity
Lead BISO, Computacenter (UK)

Great blend of discussing key topics, with plenty of opportunities to meet and network with peers.
CISO (UK)

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”

CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”

CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”

Security Operations Manager, Right Move

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”

Regional Executive, KnowBe4 (The Netherlands)

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”

CTO and Co-Founder, JIT (Israel)

“Great conference!  From the beginning, the level of participant engagement was very high.  The content was very informative and the presenters very knowledgeable.  Every aspect of Global CISO 360 was extraordinarily well done.  I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”

Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”

Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well.  Content and organization made this an excellent event!”

CISO, Infopercept (UK)

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”

Senior Consultant, DHC AG (Switzerland)

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”

Global Deputy CISO, Cushman & Wakefield

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”

VP Information Security EMEA, Northern Trust

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –

CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”

CISO & DPO, 360 Treasury Systems AG, Germany

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”

CTO, Quod Orbis

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”

GemServ, a Talan Group company (UK)

“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy”

Senior Cybersecurity, Lafarge Holcim

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”

Director, Bestman Solutions

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”

CMO, SailPoint

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” 

CEO, Cordery

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”

CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”

Chief Scientist and SVP of AI, Dataminr

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”

Director, Security, Laureate International Universities Malaysia

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”

CISO European Investment Bank

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”

Director of the Internal Control Office, Comiss
ão do Mercado de Valores Mobiliários

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”

Senior Account Executive, Hack the Box (Greece)       

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”

CTO UK, Qualys

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”

COO, Risk Ledger (UK)

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”

CEO and Founder, Praxis Security

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”

CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”

Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”

Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”

Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”

CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”

Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”

Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”

Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”

Director, Resilient. World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”

Technology Services Head of Cyber Security, DWP (UK)
“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica

“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!” Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”,

CISO, Channel 4

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV

“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations” Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Excellent conference, brilliantly put together.”
Director, Bridewell Consulting

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP