
7th Talk to the Board: CISO 360 Conference
Wednesday 6 November 2025.
Talk to the Board. Talk Business with CISOs.
The 360° Exchange Between Security Leaders and the Boardroom. Bridging Strategy, Innovation, Trust and Resilience.
Event Details:
📍 Location: St Pancras Renaissance Hotel – London
🗓️ Date: Thursday 6 November 2025
⏰ Time: 08:30-23:00
Photo Gallery 7th Talk to the Board: CISO 360 2025
The business event for CISOs and their supply chain. Meet with board directors in a unique and collaborative setting to accelerate security leadership.
As the CISO role continues to evolve covering AI, digital transformation impact, governance, compliance, their relationship with the Board may also change. Ultimately, CISO success increasingly depends on leaders who can balance technical excellence with human factors while maintaining strong board relationships to build sustainable, resilient teams, while clearly demonstrating security’s value to the board. We are thrilled to announce that the 8th Talk to the Board: CISO 360 will return for the 8th edition. The event will be hosted on Wednesday 4 November 2026 in central London.
Talk to the Board is the only dialogue between CISOs, Board Directors from across different functional areas, this year will include the vital CFO view. NEDs and other non-security C-Suite are invited to partake, encouraging further 360 cross-functional dialogues between CISOs and, crucially, with their supply chain.
Join and share candid 360 perspectives, where different angles clash and complement each other. The tensions and different perspectives will be both engaging and educational!
Key highlights include:
- A Unique Opportunity: Question a Board without consequences. Gain unfiltered insights by testing the questions you’ve always wanted to ask. Hear Directors success and war stories!
- Cross-Functional Perspectives: Hear from non-security leaders, including NEDs and functional heads, on how cybersecurity fits within business strategy, governance, and operations.
- Master Crisis Communication: Increase readiness to respond capacity – how can we better communicate during a crisis. Re-energise your approach to leading teams.
- Inspire Cultural Change and Well-Being: Explore innovative awareness, well-being and transformation campaigns that foster organisational buy-in and collaboration.
- Lessons from the Top: Directors share stories of success, challenges, and growth, with insights into key areas like employee well-being and resilience.
- Strategic Insights: Gain valuable context on the Board’s view of cybersecurity, corporate security and their future priorities.
- Speak Business Language: Develop communication skills to articulate your challenges in a way that resonates with leadership. Speak to the Board in a way that makes them understand your pain points.
What’s New for 2026!
🌟 Fresh Boardroom Perspectives
This year’s Directors Panel brings voices from across the C-suite, including, for the first time, the critical CFO view.
🌟 Inside the Boardroom
Respected CISOs share their real board decks, revealing the key messages and reasoning behind decisions.
🌟 AI Through the Board’s Eyes
New director insights: How do boards view AI for security and security for AI? Do they truly understand the trade-offs? Where do they see cybersecurity as a competitive advantage?
🌟 Bring a Board Director
CISOs are encouraged to bring a board director to better understand the trade-offs between business innovation and resilience and understand how CISO think as a group. Our aim is to actively support CISOs by enabling strategic dialogue with board directors. We’re not only preaching to the converted.
Secure your seat today.
Complimentary for CISOs, CSOs and security practitioners – for an unparalleled opportunity to engage, learn, and align with the perspectives that drive boardroom decision-making!

Why do CISOs attend?
“The theme of CISO Exchange 360 and Talk to the Board, for me, is absolutely spot on. Coming here and engaging with the board to validate what resonates with them is very special and powerful. We have silos of silos in companies. But criminals don’t have silos. They don’t have borders or boundaries. So, to win the fight, we must come together and build coalitions of capability and bridge across the boundaries we live in so we can stop the enemy and kick them out of our networks and our organisations. This event is fantastic. It’s a great forum. Board members and IT people speak different languages. We must learn to communicate effectively to help make rational decisions within a context that matters. So, this event, this forum, is exactly what I’m looking for.” Michael Beaupre, Head of Cyber Security, Hays
“The great thing about Pulse is that you get different perspectives outside of our core market. So it’s perfect for me to come here and get that completely different perspective and speak to people at the level that Pulse Conferences attract. Talk to the Board is interesting because the business dimension is the most important thing about cybersecurity. Speaking to the board brings me that business dimension to cybersecurity. As a sponsor, we get so much value out of these events, not just from potential clients but for people to partner with, and we get different perspectives on what the market is and what other people are prioritising.” Dr. Paul Kennedy, Chief Engineer – Cyber and CEMA, QinetiQ
“It’s so rare to have that opportunity to hear it directly from the CISOs and the board. So what more could you ask for if you’re up and reporting to boards and you need to communicate with them effectively? It’s a unique opportunity. What is important for them? For anyone thinking of coming to a Pulse Conferences event, just do it. Block out that time, make the commitment and realise that it’s an investment not only in your company and what your company needs from you but also in your professional development.”
Katherine Leivesley, Head of Legal, Offer and Sourcing, Kingfisher PLC
Why do our Board Directors attend Talk to the Board: CISO 360?
“I wanted to be part of Talk to the Board because I’ve always been so fascinated by technology, particularly cyber attacks and the cyber risk. I’ve learnt about how lonely and vulnerable the CISO feels. I’ve been a CEO a few times and always felt the CEO took the can for everything. I was hearing that from some of the attendees, and as boards, we need to think about how we can be more of a support for the CISOs so that they don’t feel so under threat. If your world is looking at cyber risk and you’re a CISO, I would come to this event and get involved because you are sharing and gaining simultaneously.”
Dame Inga Beale, Former CEO, Lloyd’s of London
“Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. Great to have board and CISO side of the equation together. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.”
Robert Hannigan, Former Director, GCHQ
“It was a really interesting panel, Talk to the Board, and great to meet people from across the cybersecurity profession, to hear their concerns and to help them to understand all the different issues that Boards need to deal with and where cybersecurity may rank on their list of priorities.”
Lorraine Heggessey, Former Controller, BBC 1
“A rich discussion with very interesting themes emerging for myself. Both the audience and panel found the event very interesting and informative.”
Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar
“It’s great to hear from board executives and have CISOs sit alongside them, asking questions. It’s a sort of reversal of the status quo.”
Jonathan Luff, Co-Founder, CyLon Ventures
“Talk to the Board provides a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”
Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)
“… how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics”
Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics
Why do our Sponsors join Talk to the Board: CISO 360?
“Talk to the Board. It’s been so fruitful and fantastic. We particularly found the 1-2-1 speed meetings useful. We covered a lot of ground in a short time. We’ve met some great new contacts, and I’d definitely come again!”
Holly Steele, Senior Vice President EMEA & UK Marketing, BlueVoyant
“Great to be back at a Pulse event! We love this event, Talk to the Board: CISO 360. It’s just so good to be able to network and interact with people and to have relaxed conversations, especially timing-wise towards the end of the year. People have gone through pressures and challenges and the good things that have happened. We can all collaborate and talk to each other. Interesting panel topics that fundamentally pinpoint where we’re heading in 2025 and beyond!”
James Alliband, Head of Marketing, Risk Ledger
“The key take-away of Talk to the Board: CISO 360 is the calibre of the individuals who attend. I’ve done these events over many years and I’m incredibly impressed with the team. They pulled this off brilliantly! I’ve had conversations with people who have budge, make decisions and who want to know about cybersecurity technologies that Mastercard cyber intelligence has.”
EMEA Strategic Alliances Director, Mastercard
“Pulse has exceeded expectations again in terms of the event they put on Talk to the Board: CISO 360. The content and 1-2-1 meetings are the important factor for us, and on the social side where we get to socialise with CISOs!”
Matt Middleton-Leal, Managing Director, EMEA, Qualys
Post-Event Report. Download here
Many thanks to our 2025 Sponsors
Platinum Protector
Sapphire Sentinel
Emerald Enforcer
Supporting Organisation
With thanks to our sponsors
Sponsors
Who attends
By Designation
Participants will include CISOs and CSOs in addition to:
- Chairperson
- CEO
- Non-Executive Directors, Board Member, Audit & Risk Committee Member
- CFO, CRO, GC, COO, CTO, CIO, CMO, HR
- Chief Information Security Officer
- Director of Cybersecurity / Head of Cyber Threat Intelligence
- Head of Governance
- Head of Innovation
- Director of Digital Risk
- Chief Data Officer
- Chief Privacy Officer
- Heads of Corporate Security/Resilience
By Sector
All private and public sectors are welcome to attend.
2025 Speakers – 7th Talk to the Board: CISO 360
Our programmes are organic to ensure that we bring you the very latest perspectives. If you would be interested in getting involved as a Speaker, please let us know! Email: teampulse@pulseconferences.com. We would also very much value your input into companies, topics or specific persons you may like to see on our agendas. These are your agendas.
Meet Our 2025 Board Directors (partial list)
7th Talk to the Board: CISO 360
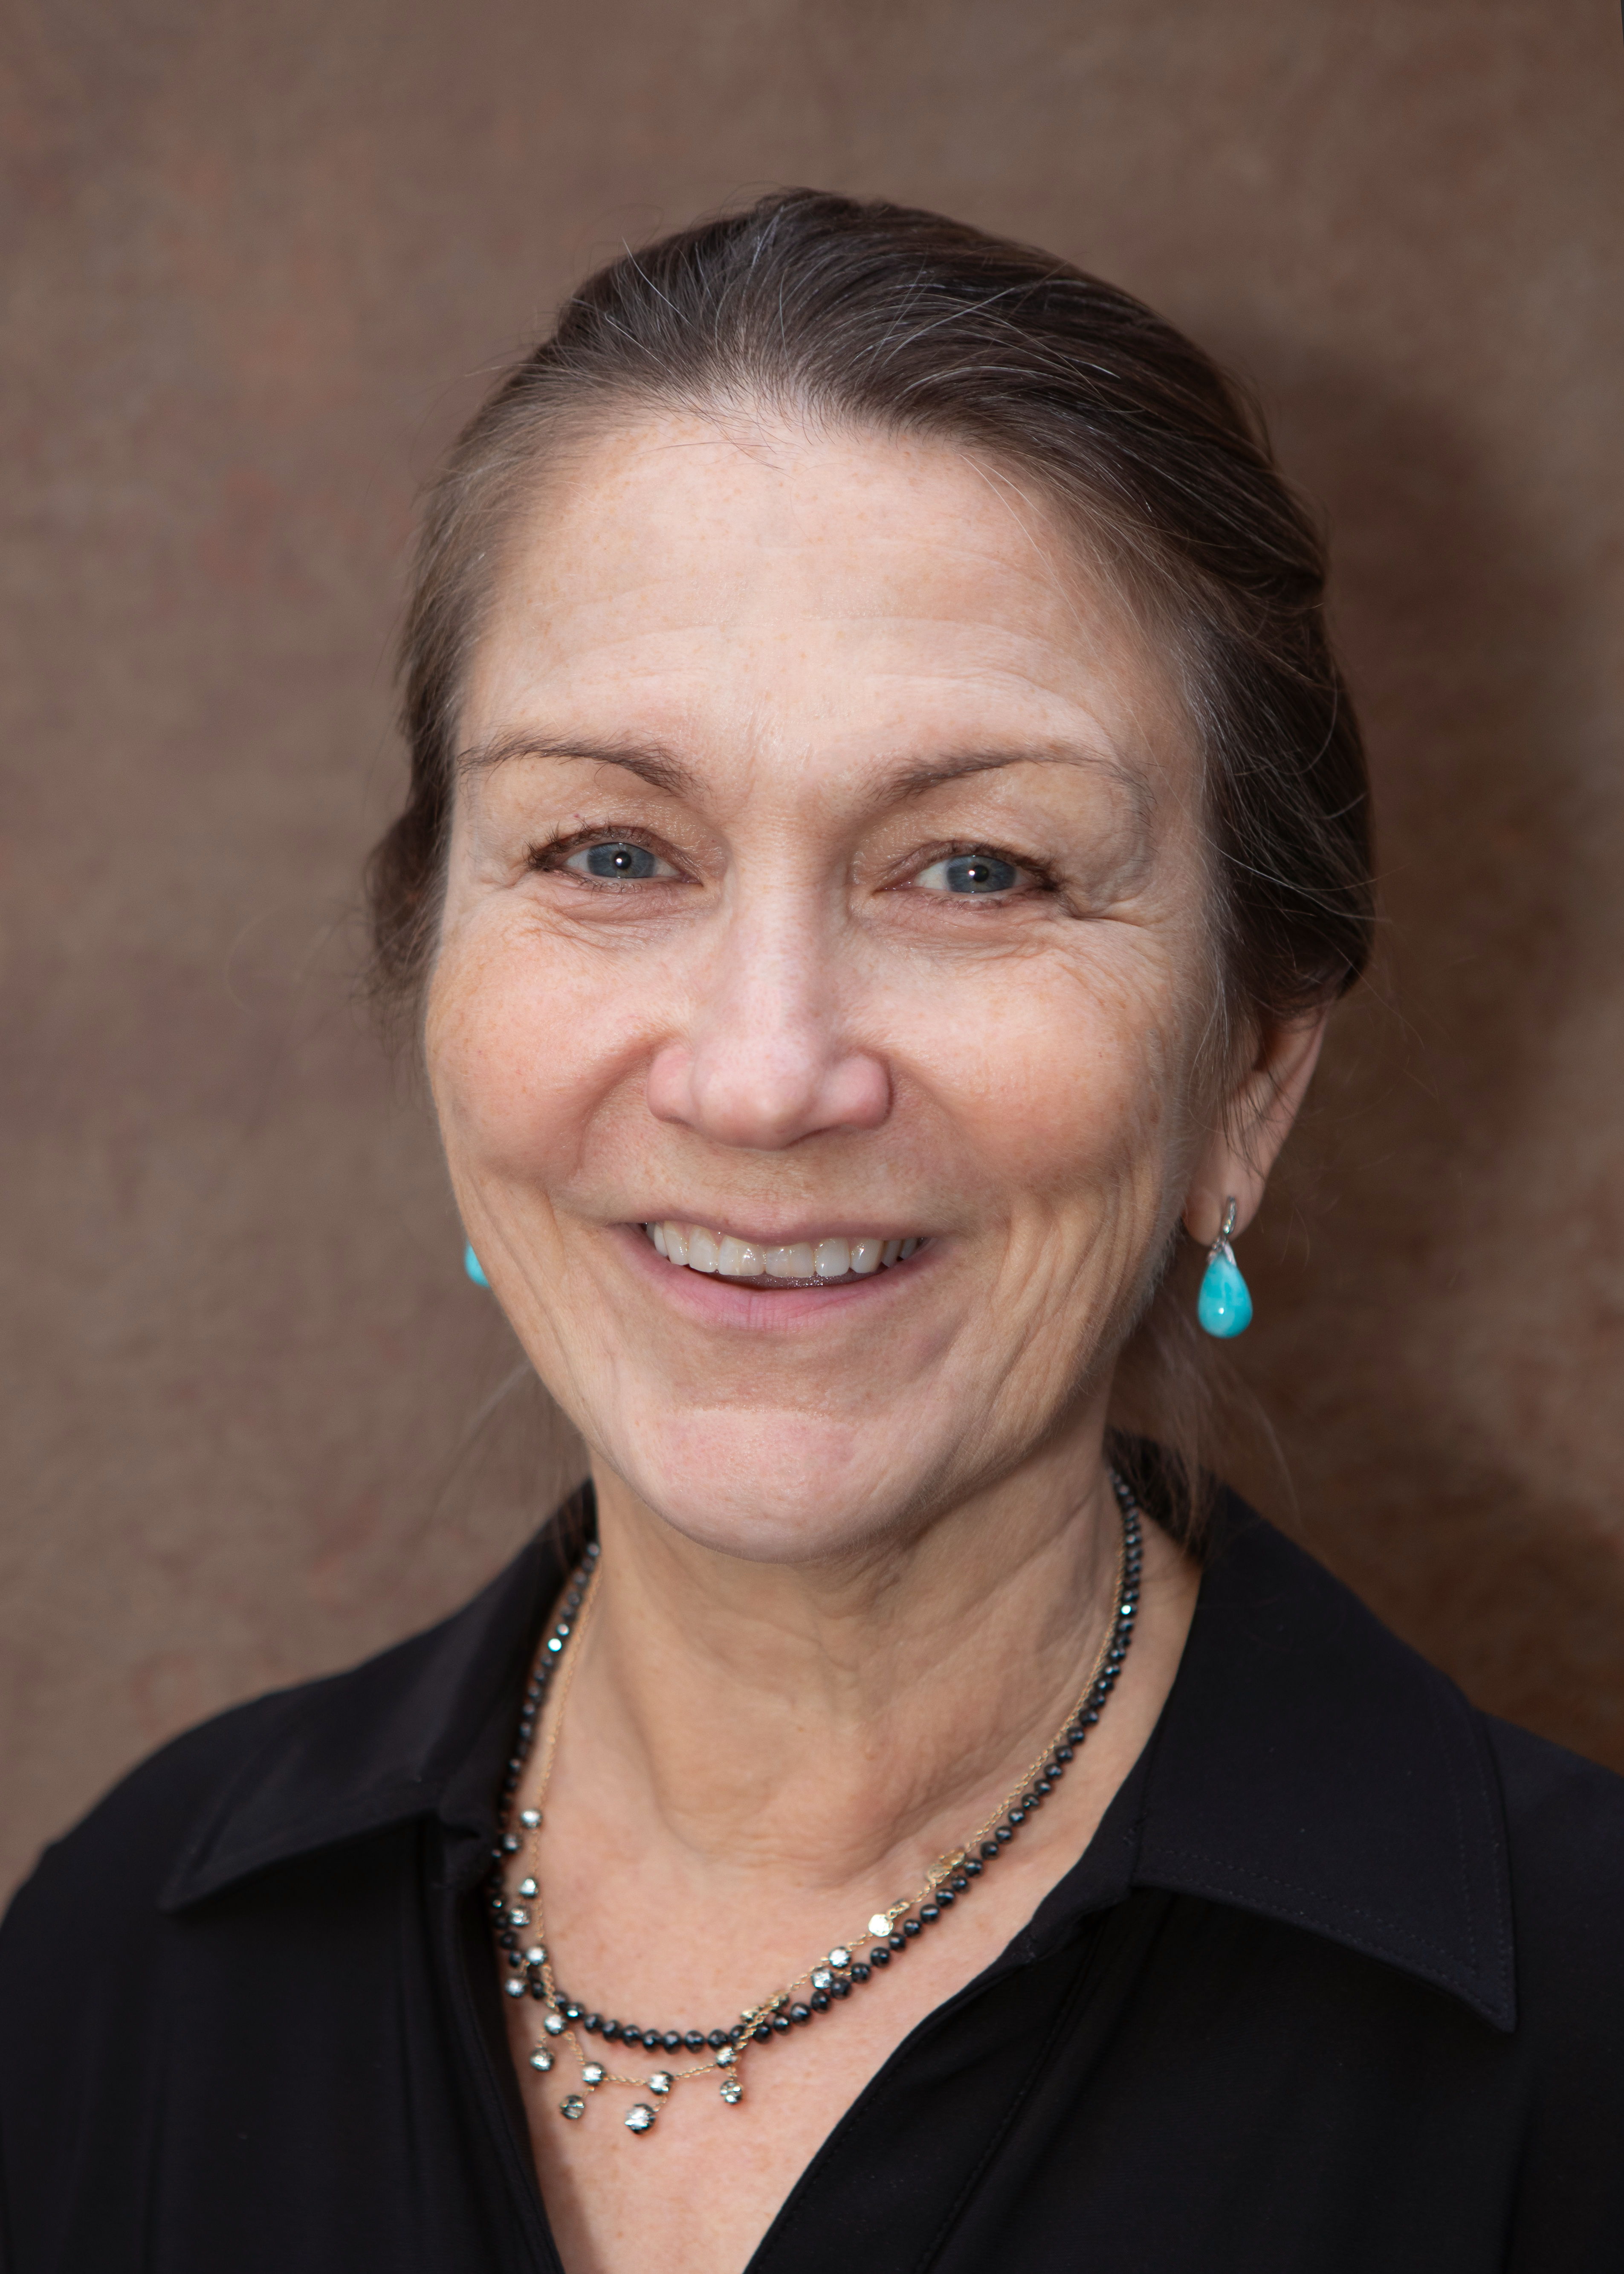 Susan Hooper
Non Executive Director, Uber
Non Executive Director, Chair of the Remuneration Committee, ESG Lead, DNED Workforce engagement, Moonpig
Susan sits on the Board of Uber UK, and Moonpig plc where she is Chair of Remco, Designated Workforce and ESG Lead. She is a Co-Founder of Chapter Zero, an organisation dedicated to providing education, insight and support on climate change to Non-Executive Board Directors and Chairs. Susan is also an Ambassador for the World Travel & Tourism Council and is an Association Member for Bupa.
Susan is involved in several start-ups in carbon capture and sustainability. Prior to her plural career, Susan was Managing Director of British Gas Residential Services, a £1.8bn revenue division, leading the Service and Repair, Central Heating Installations, Electrical Services, and Dyno-Rod business units. She joined British Gas from the Acromas Group where she was Chief Executive of the Travel division, responsible for Saga Holidays, Hotels and Cruises, the AA Travel division, and Titan Travel. Previously, she held senior roles at Royal Caribbean International, Avis Europe, PepsiCo International, McKinsey & Co, and Saatchi & Saatchi, living in seven countries worldwide.
She was previously Chair of Tangle Teezer, Carbon Gap and of Caresourcer.com. She has held several non-executive directorships including: Department for Exiting the European Union (DExEU), Wizz Air plc, Courtaulds plc, Royal & Sun Alliance plc, Transcom, First Choice Ltd., S.C Johnson, Whitbread plc, Affinity Water and The Rank Group plc. Susan was also a member of the Advisory Board of the LUISS Business School in Rome.
Susan has a BA from the Johns Hopkins University in Baltimore, MD, and an MA from the Johns Hopkins School of Advanced International Studies (S.A.I.S.) in Washington DC. She is fluent in German and Italian.
Susan lives near London with her husband. She loves being outdoors and enjoys combining sailing, travel and photography.
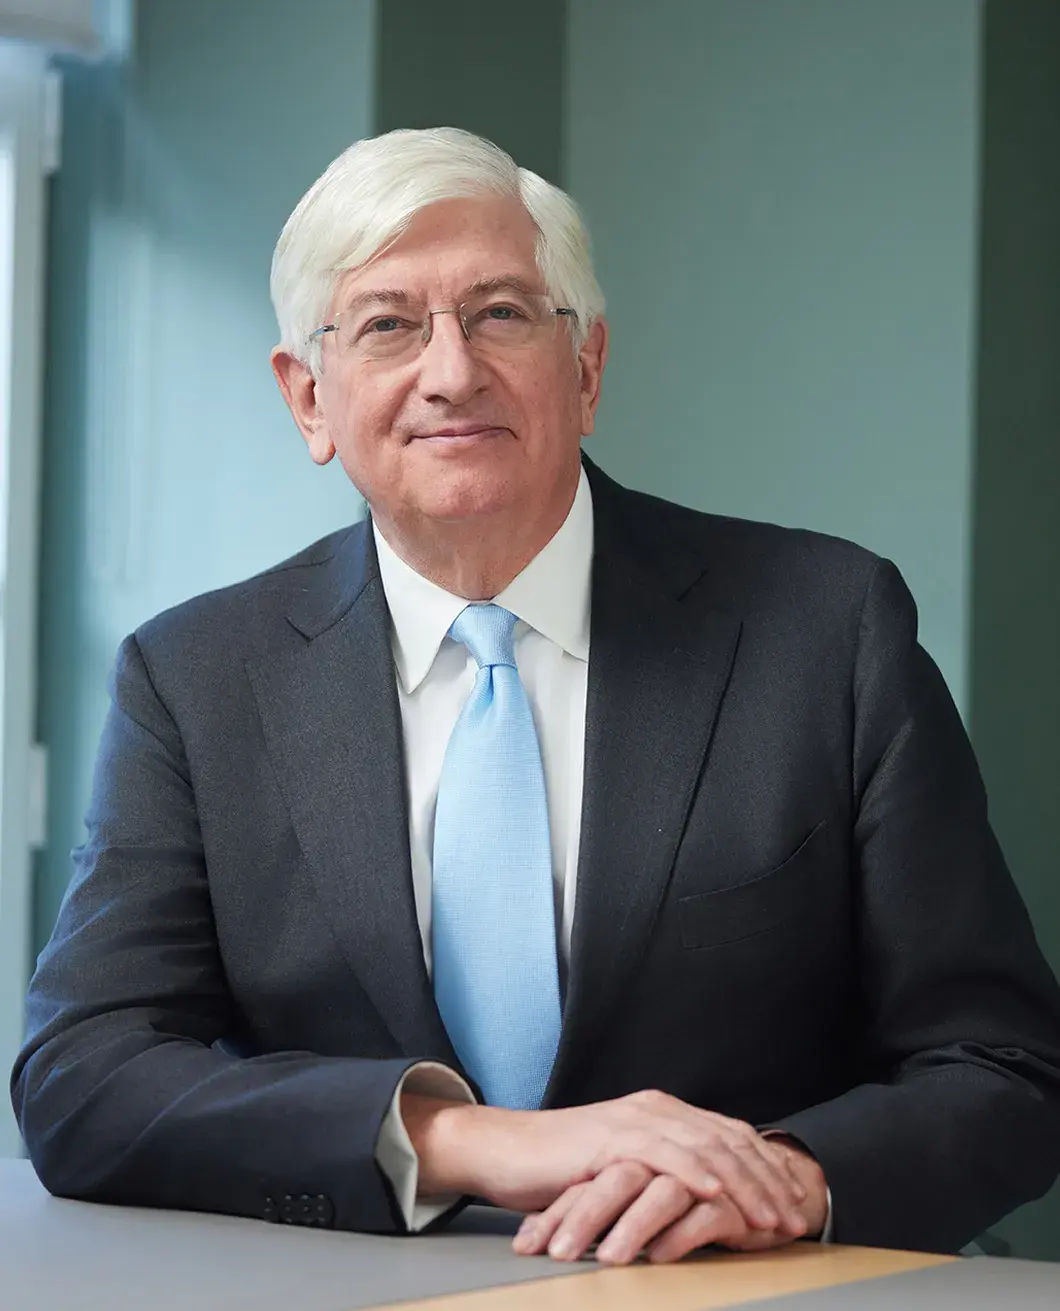 Dr Mark Carawan
Board Member and Chair of the Board Audit Committee, The Bank of London Group
Board Member and Chair of the Risk Committee, Euroclear UK and International
Mark Carawan has a wealth of experience in governance, risk management, regulatory compliance, audit, ethics, conduct and culture matters globally. Mark is a member of Council and Chair of the Audit Committee at the University of Liverpool and a Senior Fellow at the New York University School of Law Program for Corporate Compliance and Enforcement (PCCE). Mark is a Board member and Chair of the Board Audit Committee at The Bank of London Group and a member of the Board and Chair of the Risk Committee at Euroclear UK and International.
Mark’s professional career includes serving in New York as Citigroup’s Chief Compliance Officer (CCO) and member of the Citigroup Executive Committee. Mark was previously the Citigroup Chief Internal Auditor. Prior to these assignments, Mark was the Barclays Group Chief Internal Auditor based in London. Mark has formerly been a partner both at Deloitte, specializing in enterprise-wide risk management, and at Andersen, where he managed the Financial Sector Restructuring Division globally.
Mark received his B.A. in Classics from Rutgers University in the USA, a Ph.D. in Humanity from St. Andrews University in the United Kingdom, and is a Chartered Accountant, a Chartered Internal Auditor, a Certified Internal Auditor, and Fellow of the Chartered Institute of Management. Mark, an Eagle Scout, is Chair of the Greater New York Councils of the Scouting America, and is a Corporation Member at Woods Hole Oceanographic Institution in Massachusetts.
Mark’s interests include skiing, scuba diving, swimming, hiking and opera.
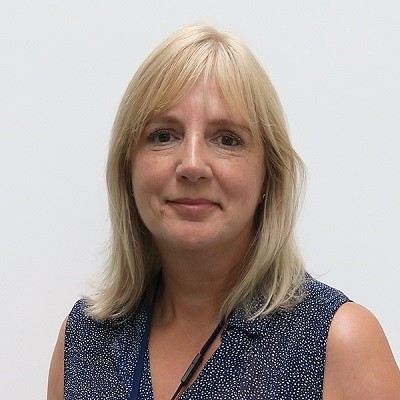
Carolyn Brown
Chief Information Officer at the British Medical Association (BMA). Board Trustee, Association for Project Management.
Carolyn is the Chief Information Officer at the British Medical Association (BMA), which is a trade union and professional services association supporting doctors across the UK. She is responsible for the technology and digital strategy, the BMA’s business intelligence and data security. Carolyn is a member of the BMA’s executive leadership team. Carolyn has held senior technology leadership roles in a variety of private and not for profit sectors for 30 years, with a steep learning curve on project management at a very early stage of her career. Carolyn holds a degree in German Literature, a postgraduate diploma in Digital Marketing, an MBA and a Computer Science Masters. In her spare time, Carolyn enjoys dog walks and playing tennis.
 Peter Davies
Former CEO, Air Malta
CEO, Airline Management Group
Peter Davies was appointed Chief Executive Officer of Air Malta in March 2011 and tasked with restructuring the business. He currently leads the Airline Management Group, a business he founded with his extensive network of professional contacts to diagnose and deliver solutions for the strategic needs of legacy airlines, especially for medium sized and smaller nations.
He joined Malta’s national airline following his position as Managing Director of Air Southwest in the UK. Peter has over 35 years experience in the aviation industry, both in passenger and express cargo operations and has served as CEO of Caribbean Airlines in the West Indies and SN Brussels Airlines, which he successfully launched as Sabena’s successor. During his term, Peter restored the airline’s stability after two years of operation by rationalising the airline’s network and internal processes and focusing on yield management on European and African routes.
Prior to that he was Chief Operating Officer for DHL Express USA where he was responsible for over 10,000 people and realised a significant turnaround in profitability and increased sales margins from 4% to 12%. Before that, he was Regional Director for DHL Europe where he established DHL as the leader in express delivery across emerging markets in Central, Southern and Eastern Europe.
In 2006 Peter accepted the appointment as Chief Executive of BWIA West Indies Airways which closed later that year. A new regional airline Caribbean Airlines of which Peter was Chief Executive commenced operations in January 2007.
Air Southwest, SN Brussels Airlines and BWIA West Indies Airways required extensive re-organisation, change and transformation. Sabena went bust and SN Brussels was the phoenix which rose from its ashes. Sabena had made a profit only twice in its 70 year history whereas SN Brussels Airlines made a profit immediately and is still going strong. Likewise, BWIA West Indies Airways made a profit only twice in its 66 year history. Peter recommended to the Trinidadian government that they close it and launch a new airline, Caribbean Airlines. After only a few months there was a discernible difference in the punctuality and financial performance of the airline.
Customer service has always been the driving force behind his many business achievements, and Peter is a compelling speaker on service, culture, leadership and change.
Meet Our 2025 CISOs and Luminary Speakers (partial list)
7th Talk to the Board: CISO 360
Recent Directors on the Talk to the Board Panel have included:
- Lorraine Heggessey, Former Controller of BBC One
- Josephine Fairley, Co-Founder, Green & Black’s
- Dame Inga Beale, former CEO, Lloyd’s of London
- Mike Coupe, Fomer CEO, Sainsbury’s
- Roger Flynn, Former CEO and leader in transformation change, Virgin, British Airways, Prudential
- Rupert Lee-Browne, Group Chief Executive, Caxton
- Daniel Bobroff, Founder and CEO, DUWL, and Former Co-Founder, ASOS Ventures
- Laura Tenison MBE, Former Founder & CEO, JoJo Maman Bébé
- Haydn Brooks, CEO & Co-Founder, Risk Ledger
- Dr. Alan Knight OBE, Group Director of Sustainability, Drax
- Julian Wheatland, former Chair of SCL Group and COO and CFO of Cambridge Analytica
Stephen Hill
Former Group CISO, Credit Suisse
Steve Hill is an independent strategic adviser, helping Boards to navigate geopolitics, national security and cybersecurity challenges. Steve served as the Group CISO at Credit Suisse and deputy Group CISO at UBS until August 2024. His previous appointments at Credit Suisse included Global Head of Operational Resilience and Group Head of Technology, Cyber and Third Party Risk.
Steve served in the British Government for over thirty years, including as Deputy Director in the National Security Secretariat of the UK Cabinet Office, with responsibility for aspects of cybersecurity policy. For over thirty years, Steve worked at the Foreign and Commonwealth Office in a variety of National Security roles with a focus on transnational threats including terrorism and weapons proliferation. He served overseas in Vienna, Washington, Dubai, Kabul and New York. Steve is a senior visiting research fellow at King’s College, London. He sits on several global advisory boards including those of Dell Technologies, Venari and Twine.
Lady Olga Maitland
President, Defence and Security Forum
Alan Jenkins
Trusted Advisor, Interim CISO, Principal Consultant, NED
Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.
Victoria Brasier
Director of Information Governance and Management, Sky
James Duggan
Solutions Architect Lead for UKI, Synack
James is a Solutions Architect at Synack, the leading crowdsourced security testing company, where he manages the UK and Ireland region. He helps organisations strengthen their cybersecurity through Synack’s human-led, AI-augmented testing platform, enabling them to test faster, at scale, and on-demand.
James provides clients with strategic insights into systemic problems. His background is in cybersecurity across diverse sectors, including Government, Defence, and Security. His experience spans areas such as business intelligence, the delivery of quantum-resistant secure communications systems, and large-scale cloud migrations.”
Antonio Ramos
Executive Manager of LEET Security, an Uptime Company.
Antonio Ramos is one of the leading experts in Spain and Europe in cybersecurity and information systems auditing. He developed his professional career at EY as Director of Technology Risks and at S21sec, in various management positions with responsibility for Managed Security Services.
He holds the most prestigious certifications: CISA, CISM, CRISC, CCSK, ITIL, COBIT 5, etc. He has been president and vice-president of ISACA Madrid, is a member of the ENISA List of Experts, a trainer of auditors and information security managers, and a member of the European Commission’s Stakeholder Cybersecurity Certification Group (SCCG).
He is currently the CEO of LEET Security, an Uptime company, which he founded 13 years ago.
Michael Colao
Former Chief Underwriter Direct and Indirect Risks, AXA XL
Dr. Oliver Farnan
Head of Research,Reliance Cyber
Dr. Oliver Farnan is the Head of Research at Reliance Cyber, with expertise in offensive security, advanced threats, and nation-state cyber policy. With a rich background in cybersecurity, Oliver has held diverse roles, including as an officer in the Royal Signals, a postdoctoral research position at Oxford University, and as the Global Head of Information Security for the INGO Oxfam. Holding a PhD in Cybersecurity, Oliver combines academic research with practical security operations, empowering organisations to effectively navigate emerging cyber threats.
Quentyn Taylor
Senior Director‚ Product, Information Security and Global Incident Response , Canon Europe Middle East and Africa
Quentyn Taylor is Director of Information Security at Canon Europe, Middle East and Africa. Using the power of stories and his own experience of testing products to destruction; Quentyn has embraced building business relationships across the world whilst driving Canon’s strategy and educating business customers to minimise their security risk. Before joining Canon, Quentyn has worked in a variety of industries such as Internet service providers as well as startup businesses.
Vasilis Razos
Head of Information Security Risk, Informa
Vasilis Razos is Head of Information Security Risk at Informa, a FTSE-100 international B2B events, digital services and academic publishing company. Vasilis has 14 years of cybersecurity experience, with a focus on risk management. Before Informa, he worked in global companies in a variety of industries, including financial services and telecoms. Vasilis holds the CISSP and CISSP-ISSMP certifications and is a member of the FAIR Institute for cyber and operational risk management. https://www.linkedin.com/in/vasilis-razos-79308a23/
Simon Riggs
CISO, OneAdvanced
Justin Kuruvilla
Chief Cyber Security Strategist, Risk Ledger
Martyn Booth
CISO, dunnhumby
Matt Middleton-Leal
Managing Director, EMEA North and South, Qualys
With 20 years spent working in the security industry, Matt brings significant experience to his role at Qualys. He has worked for many organisations, specialising in areas such as risk management, identity and access management, application, network and database security. Matt most recently held the position of General Manager EMEA and Board member at Netwrix Corporation. Previous to this role Matt was V.P. Northern Europe at CyberArk Software, where he oversaw five consecutive years of 45%+ per annum revenue growth. Prior to CyberArk he held the position of Business unit executive at IBM Security Systems. Matt joined IBM from CA where he had spent six years, working on their largest information security projects. Matt is a CISSP® – Certified Information Systems Security Professional.
Sponsors
Risk Ledger
Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.
The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.
With help from insights like this, many of our customers have improved their supplier contracts.
Interested in learning more? Visit https://riskledger.com/.
Reliance Cyber
Reliance Cyber is your specialist cybersecurity operations partner, focused solely on identifying, preventing and responding to breaches. We combine deep engineering and powerful automation with a constant human-in-the-loop approach for all our services. Our best-in-class technology reduces your threat exposure, while our experts work to detect and resolve breaches faster. As your trusted partner in an increasingly complex landscape, we defend your business continuity. We turn your security into a competitive advantage, enabling you to focus on your goals with confidence
Qualys
Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.
Gurucul
Gurucul is a security analytics company founded in data science that delivers radical clarity about cyber risk. Our REVEAL platform analyzes enterprise data at scale using machine learning and artificial intelligence. Instead of useless alerts, you get real-time, actionable information about true threats and their associated risk. The platform is open, flexible, cloud native and cost optimized. Organizations can save 50% or more while achieving complete data control, visibility, searchability, and analytics within a single console. Industry analysts have recognized our platform as a Visionary in the 2024 Gartner(R) Market Quadrant(TM) for SIEM for the third-consecutive year. Our solutions are used by Global 1000 enterprises and government agencies to minimize their cybersecurity risk. To learn more, visit Gurucul.com and follow us on LinkedIn and Twitter.
LEET Security
LEET Security is an independent rating agency, set up for the sole purpose of developing and managing a labelling system to reliably rate the information security posture of organizations and their third-party ICT service providers/partners.
Since its inception in 2010, the LEET Security cyber rating agency compiled and updates the risk and control measures defined in the main international regulations, standards, and best practices including National Institute of Standards and Technology (NIST), General Data Protection Regulation (GDPR), Payment Card Industry Data Security Standard (PCI-DSS) & International Standards Organization (ISO-27001) & Esquema Nacional de Seguridad/ National Security Framework (ENS) among others. Using its proprietary and tested methodology LEET classifies and groups the defined controls to provide a security posture ‘score’ which is attested by the LEET Stamp with a detailed report.
The LEET Security rating provides confidence to customers and users that cyber security risks are identified and characterized within any services utilizing digital infrastructure for any aspect of service delivery across enterprise-owned digital services and infrastructure and third-party partners. The rating clearly indicates an organizations commitment and investment into measuring, monitoring, and hardening their security posture, providing full transparency to the security measures implemented. For more information, please visit www.leetsecurity.com.
Synack
Synack’s Penetration Testing as a Service platform manages customers’ attack surfaces by discovering new assets, pentesting for critical vulnerabilities and gaining visibility into the root causes of security risks. We are committed to making the world more secure by harnessing a talented, vetted community of security researchers to deliver continuous penetration testing and vulnerability management, with actionable results. Synack’s PTaaS platform has uncovered more than 83,500 exploitable vulnerabilities to date, protecting a growing list of Global 2000 customers and U.S. agencies in a FedRAMP Moderate Authorized environment. For more information, please visit www.synack.com
Cybervadis
Mitigate third-party cyber risks. With confidence.
CyberVadis is a trusted solution for mitigating third-party cyber risks. We combine the speed of automation with the reliability of a team of information security experts, providing evidence-based assessments. Our comprehensive, scalable and managed solution enables you to effectively reduce risks across your entire supply chain.
The ISF
The ISF is a leading authority on information security and risk management. A not-for-profit organisation, we provide independent opinion and guidance on all aspects of information security. We deliver practical solutions to overcome the wide-ranging information security and risk management challenges that impact business.
For more information, visit: www.securityforum.org
Venue
The 7th Talk to the Board: CISO 360 will be hosted at the iconic landmark of St. Pancras Autograph Collection London.
St. Pancras Autograph Collection Hotel London Euston Road, London, NW1 2AR
St. Pancras, London, Autograph Collection
For over 152 years, the St. Pancras London, Autograph Collection Hotel has stood as a stunning testament to Victorian Gothic revival architecture – a beacon of pioneering design and elegance. Originally unveiled as the Midland Grand Hotel in 1873, it was designed not only as a place of luxury but also as a bold symbol of innovation. From the introduction of hydraulic lifts to the first revolving door in the UK, the building was ahead of its time. Its soaring vaulted ceilings, majestic Grand Staircase and the iconic clock that towers above the city continue to shape the London skyline and captivate all who pass by. Where past and present converge, St. Pancras London, Autograph Collection Hotel continues to be a living monument of timeless design, innovation and connection – a place where history and style effortlessly unite.
Main Event Space: Hansom Hall
Nestled within a stunning historic setting, this iconic venue seamlessly blends Victorian grandeur with modern amenities. Paying homage to one of London’s most iconic modes of transportation, The Hansom Hall is steeped in the rich history of the Hansom Cab. Invented by Joseph Hansom in 1834, the Hansom Cab was a lightweight, two-wheeled carriage designed for speed and manoeuvrability, a staple of London’s streets until 1947. The St. Pancras Autograph Collection’s Hansom Hall and Bar occupies what was once the cobbled driveway where these carriages would collect passengers arriving at the station. In 2023, the hotel proudly supported the Poppy Cabs initiative, offering a meeting point for drivers assisting veterans on Remembrance Sunday. The space remains distinctive, offering a quintessentially British experience that seamlessly blends past and present. Its history, rooted in the bustling arrival of Victorian travellers, continues to influence its vibrant atmosphere today.
Networking Reception: The Ladies’ Smoking Room
The networking reception will be hosted in the historic Ladies’ Smoking Room and on the terrace with heaters. These spaces offer a distinctive setting for corporate gatherings or social events, all within the heart of London. Every corner of the hotel reflects a sense of connection, from its original architectural details to its role as a meeting point for ideas and cultures, much like it was in its Victorian heyday. For those seeking solace amidst the city’s bustle, St. Pancras Spa provides a tranquil escape.
Directions
By Underground
The nearest tube station is King’s Cross St. Pancras – on lines: Circle, Hammersmith & City, Metropolitan, Northern, Piccadilly, Victoria. This is a 2-minute walk from the venue.
By Bus
Bus routes 46, 63, 214, N63 stop at St Pancras International Station (M), directly adjacent to the hotel.
Bus routes 30, 73, 91, 205, 390, N73, N91, N205 stop at St Pancras International Station (A), on the opposite side of the hotel.
Bus routes 46, 63, 214, N63 stop at King’s Cross Station (D), a short walk from the hotel.
Bus routes 30, 73, 91, 205, 390, N73, N91, N205 stop at King’s Cross Station (E), another short walk from the hotel.
By Car
The hotel offers valet parking at £80 per day or £20 per hour.
- St. Pancras NCP Car Park (Pancras Road): Located 0.1 miles from the hotel.
Alternatively, nearby car parks include:
- Matilda Street Car Park: Approximately a 12-minute walk from the hotel.
- Euston Road Car Park (entrance via Duke’s Road): About a 10-minute walk from the hotel.
Note: The hotel is located outside of London’s Congestion Charge Zone and ULEZ.
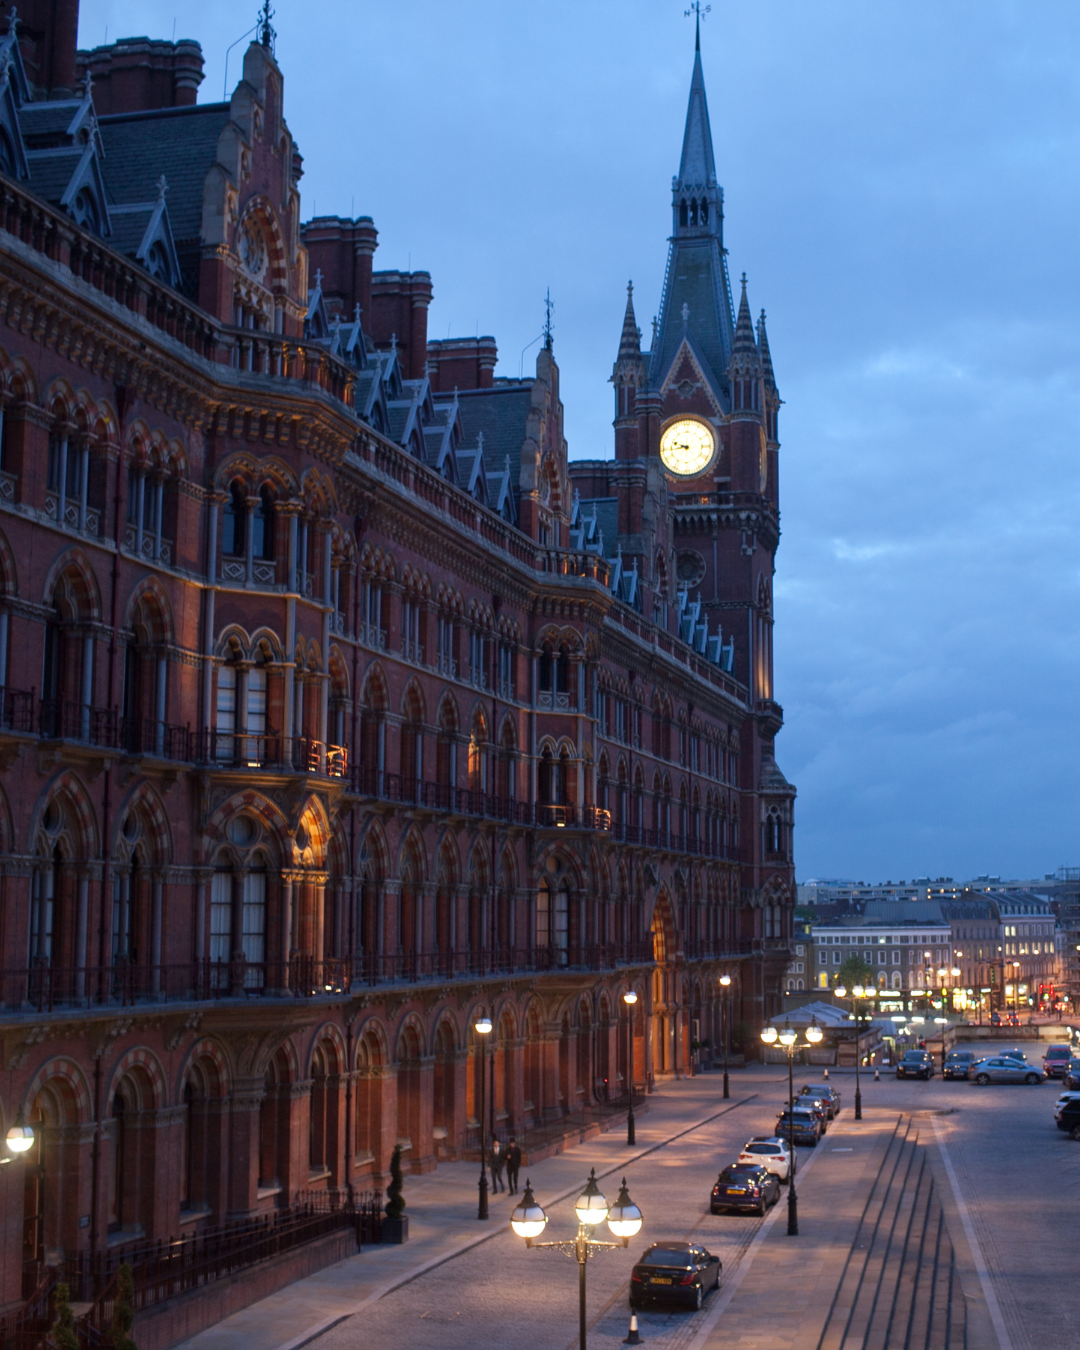
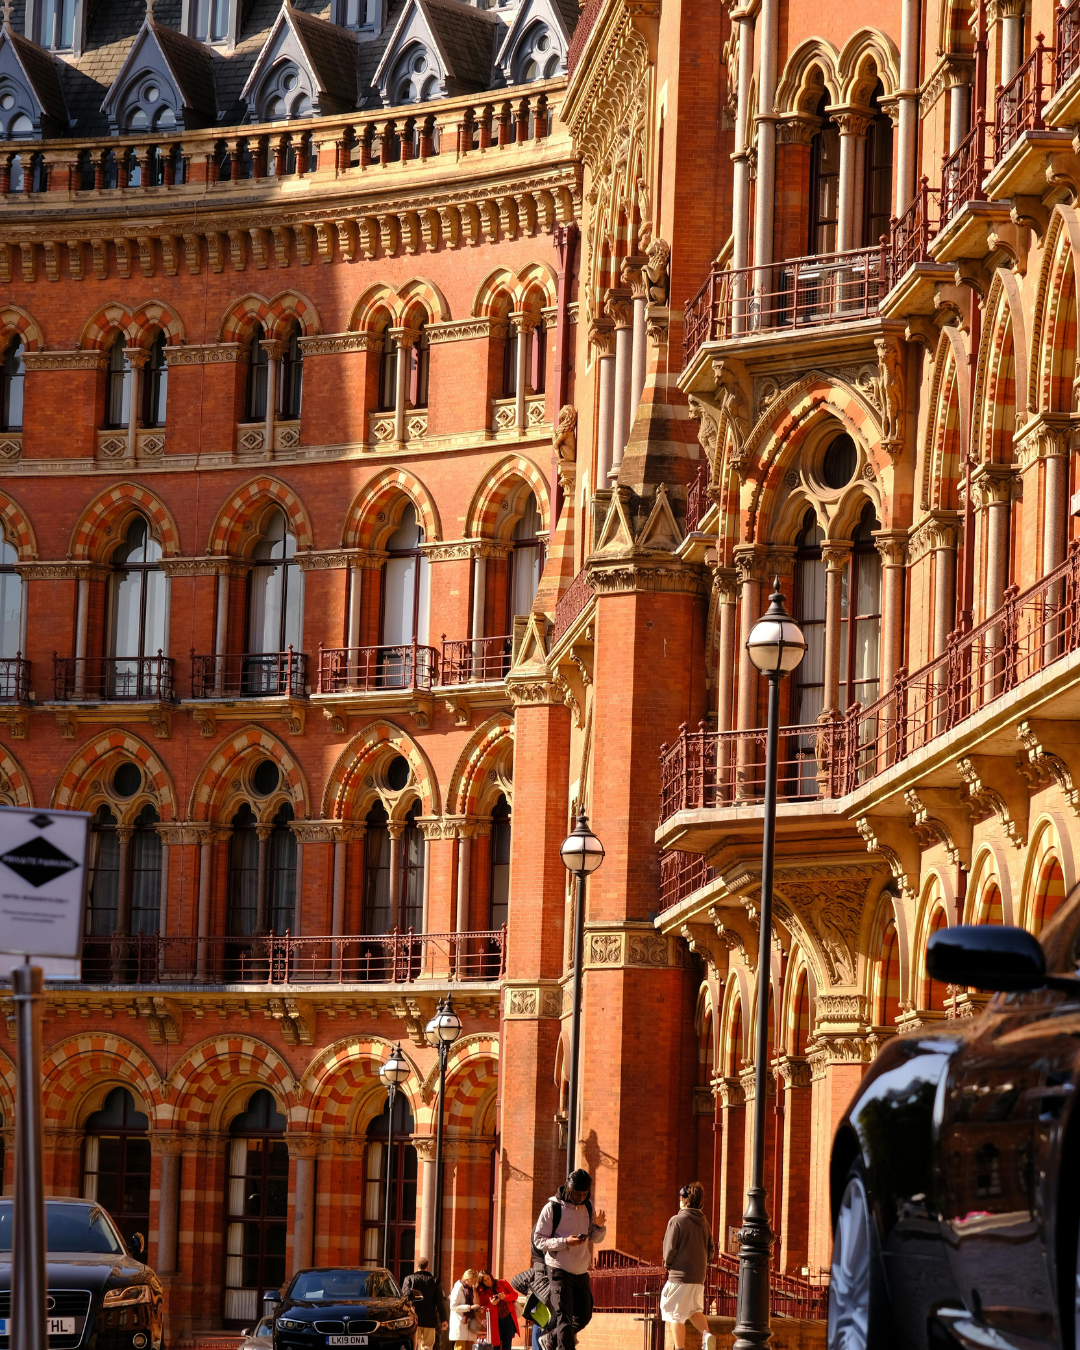
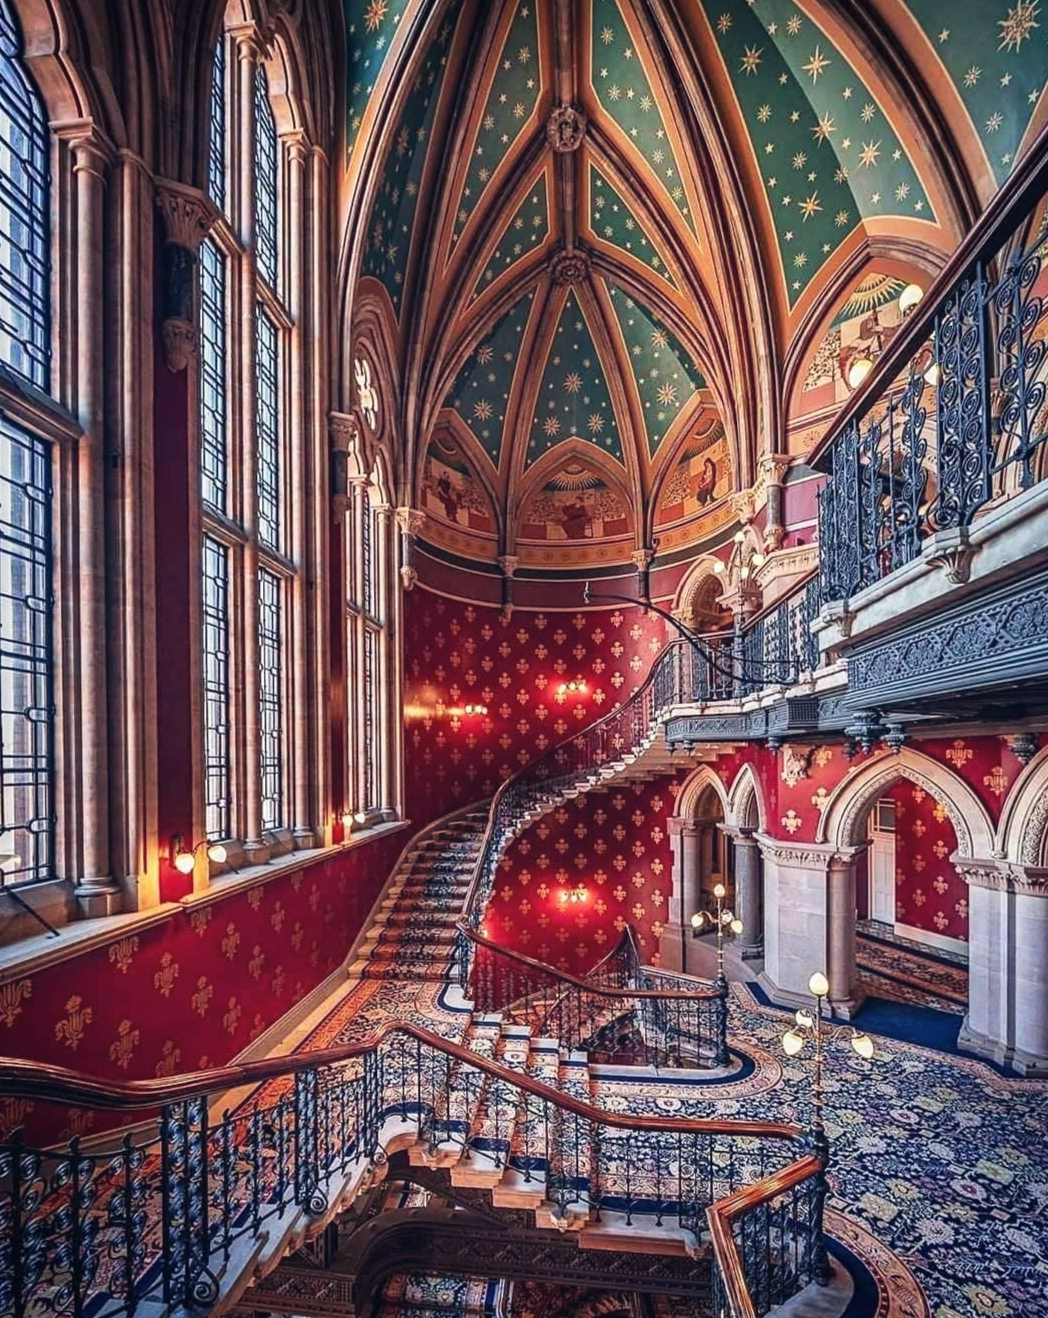
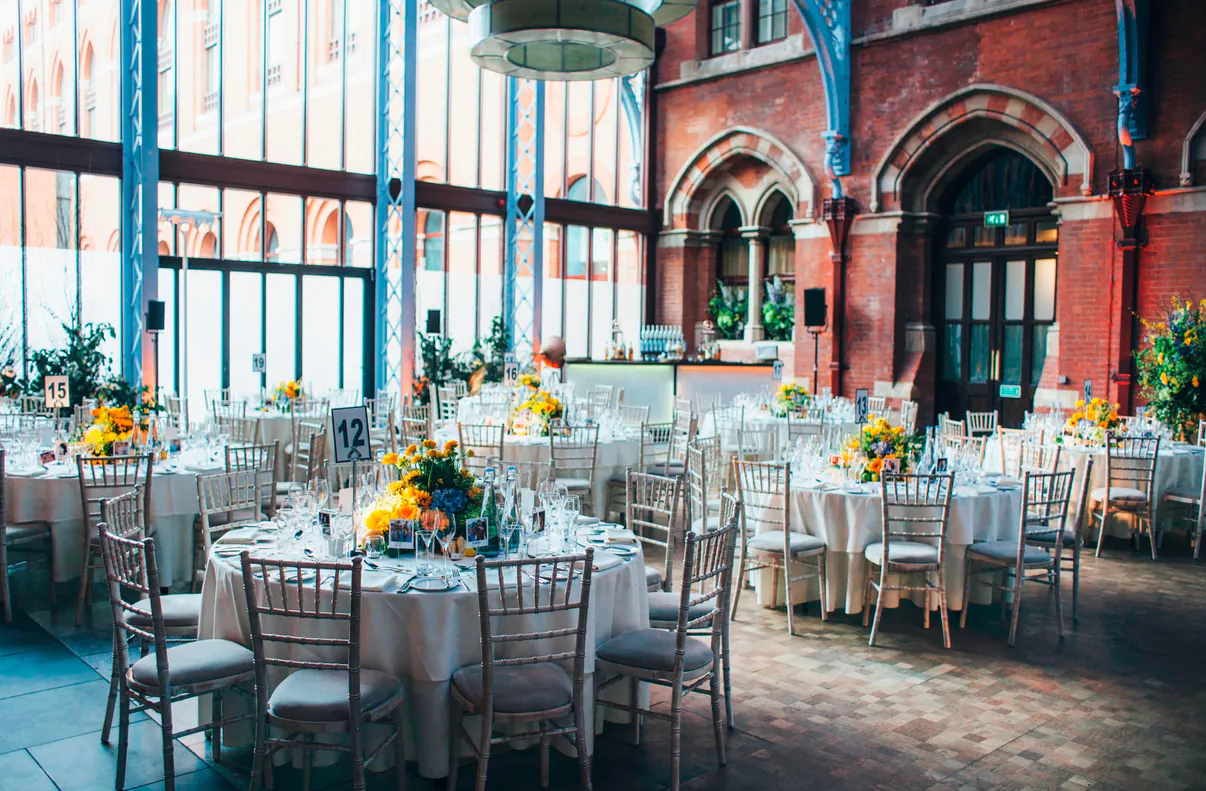
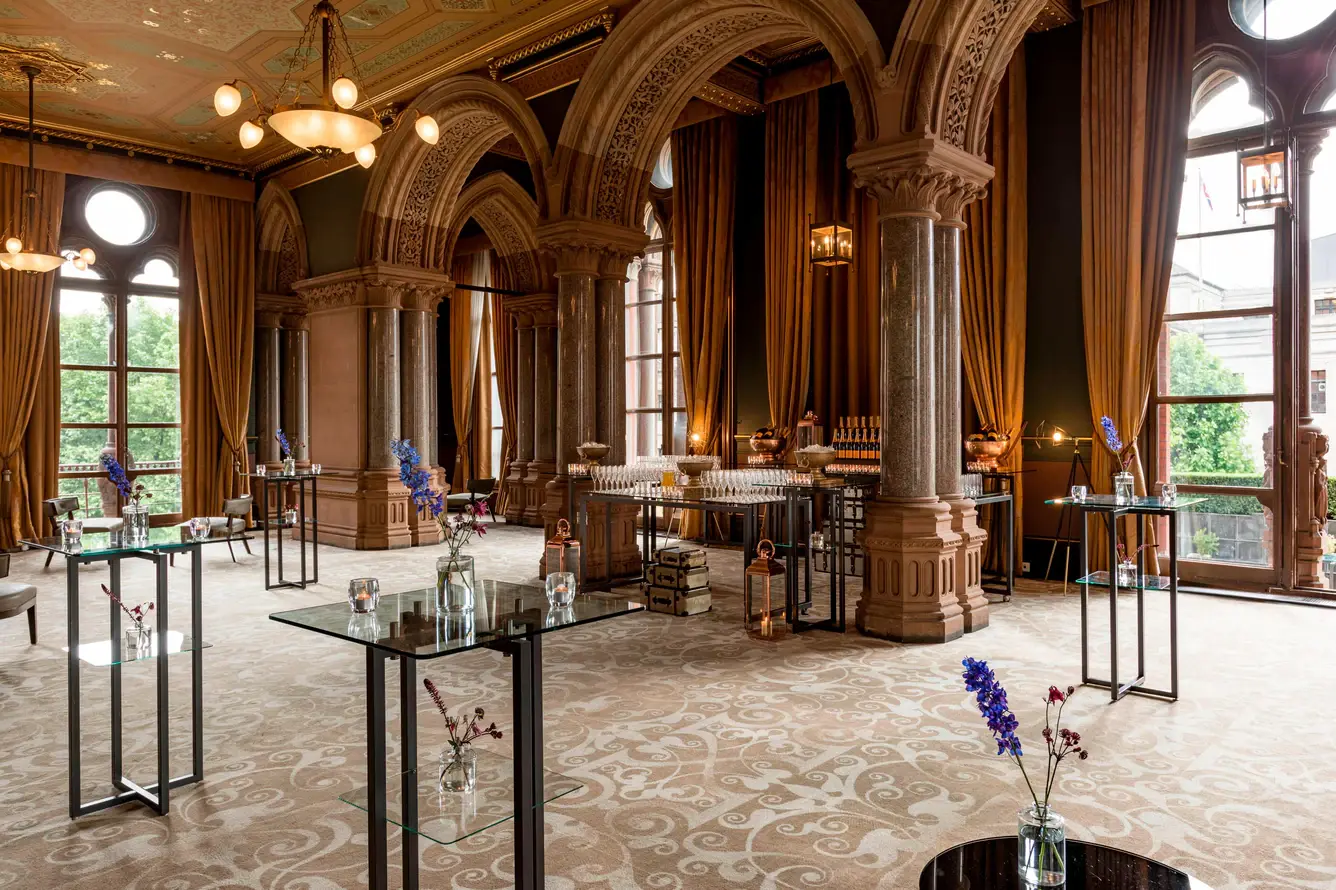
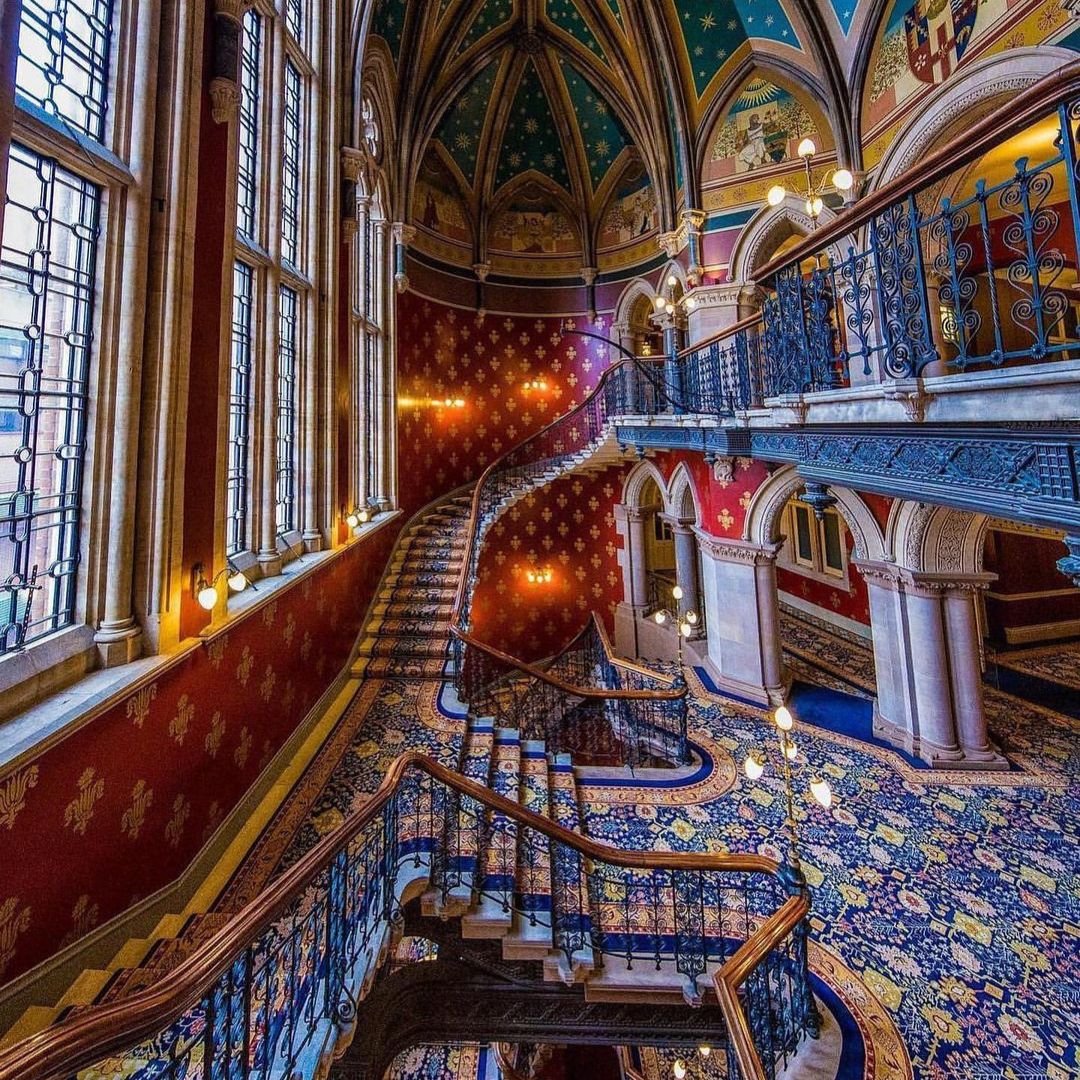
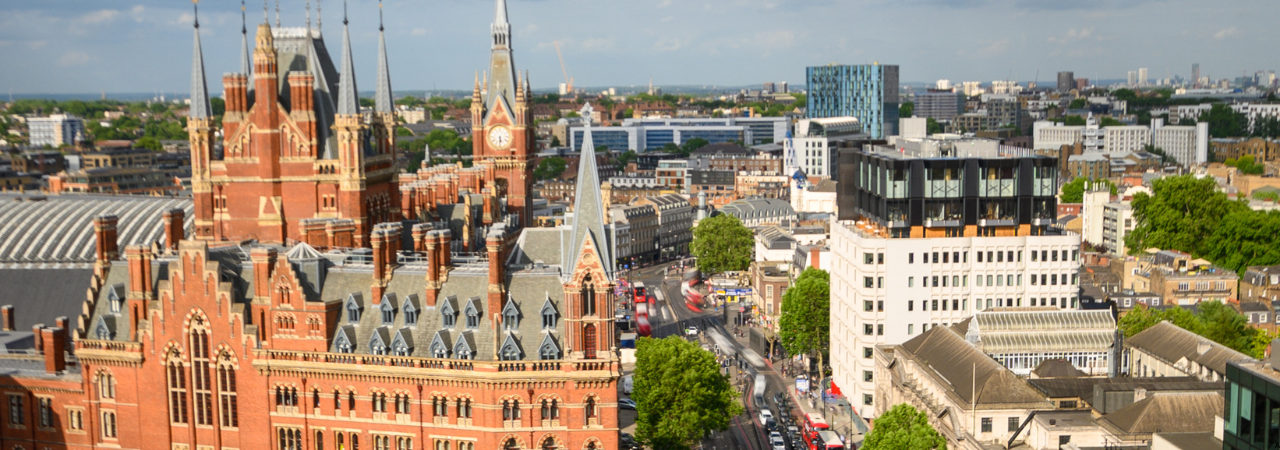
Photo Gallery 7th Talk to the Board: CISO 360 2025
Photo Gallery 2024

Highlights Video 2024
Downloads – Talk to the Board: CISO 360
Download "I am attending" banner 2025