Archive · Talk to the Board

5th Cyber Exchange 360: Talk to the Board

This event took place on 6 November 2024 at London Marriott Hotel Grosvenor Square. The pages below are kept as a record of the programme, speakers and sponsors.

DATE6 November 2024
VENUELondon Marriott Hotel Grosvenor Square

Welcome to the 5th Cyber Exchange 360: Talk to the Board

SAVE THE 2024 DATE!
6th Talk to the Board returns to the Science Museum on 6 November 2024!

A Reciprocal Exchange with CISOs, the Board and Supply Chain
Time to Redefine CISO Purpose and Cybersecurity Leadership

‘Talk to the Board’ is back – the only reciprocal exchange with CISOs, the Board and Supply Chain. Ask questions you would ideally like to discuss with your own Board, but with no consequences!

Many thanks to those who joined us at the 5th Cyber Exchange 360: Talk to the Board

8 November 2023 | London Marriott Grosvenor Square

The 5th Cyber Exchange 360: Talk to the Board Conference, created and hosted by Pulse Conferences, was hosted at The Marriott Grosvenor Square in London, 8 November 2023.

Our programme provides refreshing and ground-breaking perspectives on cybersecurity – a rare opportunity to question a Board – but with no consequences! Talk frankly and test questions that you would ideally like to ask of your own Board. Increase readiness to respond capacity – how can we better communicate during a crisis. Learn from successful examples of corporate awareness and transformation campaigns. Hear the biggest learnings from Directors as they share success and war stories on business areas including employee well being. Gain context through Board perspectives on where cybersecurity sits and be privy to future business predictions. Engage with the Board in a way that makes them understand your pain points. Compare key metrics and test them on the Board.

This unprecedented event aims to revolutionise the way large enterprises approach cybersecurity.

Why this event? Breaking Barriers…

This event is not your ordinary infosec conference. It fosters a reciprocal dialogue between esteemed Enterprise Board Directors and forward-thinking CISOs and information security practitioners. Together, participants – Sponsors, Speakers, Delegates alike – will advance the conversation and explore innovative strategies to tackle the evolving cyber landscape.

Our aim

CISOs will leave the event armed with new ideas and questions to engage their own board and with an enhanced vision of how to deepen the relationships and communications that they have with their own directors to be able to scale up cybersecurity strategy within their organisations effectively.

We are delighted to announce this next chapter in the ground-breaking series, ‘Talk to the Board’, the premier conference designed to facilitate such direct interaction.

We look forward to the next reciprocal discussion between CISOs who will question a new panel of Board of Directors from listed companies.

Elevating cybersecurity

Our programme provides a refreshing non-security perspectives on cybersecurity – and rare opportunity to talk frankly and test questions that participants would ideally like to ask their own Board, with invited Directors spanning the various functional board roles that make up a board, CEO, CMO, HR, CTO…

Questions that are sure to be raised

What are the skills, behaviours and mind set required to lead the security agenda in a pressured, complex and competing business environment and how to create a culture where cybersecurity is considered central to the way companies think and behave? Where does cybersecurity sit in the list of highest Board risks and opportunities? How has this changed in the past year and what are new expectations of CISOs and security leaders? How can we measure and communicate cybersecurity in a measured way?

Areas that are certain to be raised in this open exchange with Board Directors from large organisations –

  • Changing nature of the consumer
  • Changing risk landscape
  • Corporate responsibility
  • Crisis management
  • Data management and privacy issues
  • Digital transformation
  • Ethical frameworks for the way we manage and audit data, innovation and technology
  • Fake news and social media
  • Fintech
  • Future workplace people and skills
  • Global supply chains
  • Insurance
  • Leadership
  • Long-term Planning
  • Marketing
  • Modernising tradition – a journey of cultural and technological change
  • Rapid Growth
  • Scaling businesses
  • Supply chain
  • Sustainability and decarbonisation for businesses
  • Technology commercialisation
  • Role of ‘purpose’ in business


Talk to the Board – Meet our 2023 Panel of Directors
Read more…

Dame Inga Beale
Former CEO, Lloyd’s of London

Mike Coupe
Former CEO, Sainsbury’s

Alan Knight OBE
Group Director of Sustainability, Drax & Senior Associate, CISL

Julian Wheatland
Formerly Chairman of SCL Group and COO & CFO of the Cambridge Analytica / SCL group of companies

Meet our 2023 Panel of CISOs including
Read more…

Michael Beaupre
Head of Cyber Security, Hays

Derek Cheng
CISO, Deliveroo

Agenda Timings
All networking functions are to be confirmed. Details to be provided in due course.

08:00-08:30 Arrivals and Coffee

08:30-13:00 Cyber Exchange 360 – Case studies, keynotes, fireside chats and hosted table think tanks

13:00-14:00 Lunch

14:00-15:00 Talk to the Board – Panel of Board Directors from large companies are questioned by CISOs

15:00-15:30 Short Comfort Break and Sponsors’ Prize Draw

15:30-17:00 Talk to the Board – Panel of Board Directors continues…
17:00-19:30 Networking Reception and Entertainment. London Marriott Grosvenor Square. Kindly sponsored by

e2e-1

19:30-22:00 Talk to the Board Supper at Selfridge’s. Alto by San Carlo – The Rooftop Selfridge’s. Kindly sponsored by 

riskrecon_by_mc_rgb_pos

As a CISO why attend

  • Increase readiness to respond capacity – how can we better communicate during a crisis
  • Learn from successful examples of corporate awareness and transformation campaigns
  • Hear the learnings from Directors as they share success and war stories
  • Gain context! Board perspectives on where cybersecurity sits and useful predictions
  • Speak to the Board in a way that makes them understand your pain points
  • Compare key metrics and test them on the Board
  • Re-energise your approach to driving change and leading teams

As a Board Director why attend

“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them to champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.” Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey

“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”
Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)

“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics”
Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics

Many thanks to our 2023 Sponsors!

Platinum and Networking Reception, Marriott Grosvenor Square

Platinum and Supper at Selfridge's, The Rooftop

Platinum

Gold

Supporting Association


Highlights Video- 4th Cyber exchange 360: Talk to the Board


WITH THANKS TO OUR SPONSORS

360 Series Sponsors

Sponsorship opportunities

Programme – 5th Cyber Exchange 360: Talk to the Board, 8 November 2023

Topics and speakers for the 5th Cyber Exchange 360: Talk to the Board, 8 November 2023 are in progress. Our programmes are organic to ensure that we bring you the very latest perspectives! If you would be interested in getting involved as a Speaker, please let us know! Email: teampulse@pulseconferences.com. We would also very much value your input into companies, topics or specific persons you may like to see on our agendas, which are your agendas.

View Flyer 2023 

Our programmes are organic to ensure that we bring you the very latest perspectives. If you would be interested in getting involved as a Speaker, please let us know! Email: teampulse@pulseconferences.com. We would also very much value your input into companies, topics or specific persons you may like to see on our agendas. These are your agendas.

Talk to the Board – Meet our 2023 Panel of Directors to date

Meet our esteemed Co-Chairpersons


Profile photo of Olga MaitlandLady Olga Maitland

Lady Olga has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.


Profile photo of Alan JenkinsAlan Jenkins

Alan is a security practitioner of long standing, who has bridged both the Physical and Cyber domains in his career while always keeping an eye on the People aspects also. After a lengthy spell as an RAF Police officer, he has held a variety of roles at increasing levels of seniority in the commercial world, including CISO & Group Security Coordinator at a FTSE100 business. He is currently a Consultant, Trusted Advisor, Visiting Lecturer, Mentor & NED.


Meet our 2023 Panel of CISOs and Luminaries to date

Inga-Beale-LSB

Dame Inga Beale

Former CEO, Lloyd’s of London

Dame Inga Beale took over the helm of the 330-year-old City financial institution Lloyd’s of London in 2014, after working in senior leadership roles in some of the world’s largest insurance companies. With over three decades of global business experience she was awarded her Damehood in 2017 for services to the UK economy. Before joining Lloyd’s, Inga was Group CEO of Canopius with its principal operations at Lloyd’s. Prior to that she was on the Global Management Board of Zurich Insurance Group. Earlier roles include Group CEO of Swiss reinsurer Converium, and a variety of international leadership positions for GE Insurance Solutions. She started her career as an underwriter with Prudential in 1982.? During her time at Lloyd’s, Inga developed a culture of innovation and inclusion. She expanded the company’s reach to new, high-growth markets including Asia and the Middle East, and delivered some of Lloyd’s strongest financial results. As the first female CEO of Lloyd’s, she played a key role in changing cultural perceptions and highlighting the importance of diversity and inclusion. Under her leadership, Lloyd’s launched a number of diversity initiatives, including the Dive In Festival, which grew to become the only world-wide insurance industry diversity and inclusion event. Drawing on her own experience at Lloyd’s, Inga discusses what it means to lead cultural change and steer a company through a technological transition without losing its core character. Her talks uncover how successful transformation means establishing a balance between tradition and history, and modernity and innovation. Moreover, she tackles breaking glass ceilings, and building inclusive environments within the workplace. Inga also analyses the reasons behind a lack of trust in both governments and the corporate sector, as well as the rise in public emphasis on corporate responsibility, purpose, ethics and sustainable business models. Inga is a Patron of Insuring Women’s Futures, an alliance of insurance and personal finance professionals helping to improve women’s long-term financial resilience. She is also an ambassador of Stonewall’s Development Council, and was awarded a Damehood for her influential work in driving the inclusion agenda for women and the LGBT community. She has served as President of the UK Chartered Insurance Institute, a member of the Geneva Association Board, and a member of the UK Government’s Financial Services Trade and Investment Board. She now has a portfolio of non-executive director roles for a variety of multinational companies.

Mike-Coupe

Mike Coupe

Former CEO, Sainsbury’s

Mike Coupe is considered to be a leading business authority. Coupe held the position of CEO for Sainsbury plc from 2014-2020. Before retiring he is credited for turning the company around, through top-level trading, marketing, and online operations. As a business speaker, he instills in his corporate audiences the essential skills he used to lead a market, and share his experience of directing one of the UK’s most established organisations. Coupe joined Sainsbury’s in 2004. Immediately making a positive impression on the company, he rose through the ranks and was appointed responsible for online operations, marketing, and trading in 2010. In 2014, Mike was named CEO of Sainsbury’s, following in the footsteps of Justin King. Using his expert knowledge, he quickly established a strategic review to stay ahead of the evolving retail market. Mike championed Sainsbury’s journey ahead of the competition through a complete digital transformation. From till-free stores to the digitisation of Nectar, the UK’s largest loyalty scheme, through a website and an app, he revolutionised the retail giant’s day to day practices. Coupe lead the business from making 5% of online sales to an impressive 20% and growing. Additional influential roles include the Executive Board Director of Asda and Non-Executive Director at Greene King plc. In 2020, Mike announced Sainsbury’s new, more sustainable operations. The company has invested £1 billion into achieving net-zero carbon emissions by 2040, setting the standard for other supermarkets. Mike himself described the decision, stating that “we must recognise that living well now also means living sustainably”, reflecting his commitment to the environment. Mike was director of Covid-19 testing at England’s Test and Trace agency from September through to December 2020 and has been appointed as a non-executive director on the board of NHS England from January 2021.

Alan-Knight-OBE

Alan Knight OBE

Group Director of Sustainability, Drax and Senior Associate, CISL

Alan has over 30 years’ experience of working with global companies and governments on sustainability. In April 2021 he joined Drax as the Group Director of Sustainability. Drax’s ambition is to be the world’s first carbon
negative power station and is the largest producer of biomass for energy. Prior to that, for seven years Alan was in the steel and mining sector as the Global Head of Sustainable Development for ArcelorMittal. He was Co-chairman of Responsible Steel and served on the steering board of the Initiative for Responsible Mining. Alan created and chaired the Ebola Private Sector Mobilisation Group, which was a collaboration of over 100 companies sharing best practice and coordinating the corporate response to Ebola in West Africa. For this he was made a Clinton Global Citizen honouree in 2015. Previous to that he was Sustainability Director for Business and the Community (BITC) where he oversaw all their Corporate Sustainability Programmes. He advised the Virgin Group on sustainable development for seven years. Previously he has worked with global companies as diverse as B&Q where he led their entire Sustainability programme for 10 years. He was instrumental in founding and developing the Forest Stewardship Council. He held similar roles in the Parent company Kingfisher and SABMiller, the multibillion brewery company. For nine years he was a commissioner with the Sustainable Development Commission and he introduced the concept of “choice editing” into the product policy debate. He was awarded the OBE in June 1998, in 2005 the US-based Rainforest Alliance presented him with a lifelong award and in 2013 he was made an Honorary Fellow of the Society for the Environment.

Julian-Wheatland

Julian Wheatland

Formerly Chairman of SCL Group and COO and CFO of the Cambridge Analytica / SCL group of companies

Julian Wheatland was formerly Chairman of SCL Group and COO & CFO of the Cambridge Analytica / SCL group of companies. From 2015 to 2018 he oversaw the growth of the group into one of the most influential data analytics companies in the world, employing ground-breaking analytics technology and targeted communications which have shaped the advertising industry and the debate around data privacy and personal data. In 2018, following the media controversy surrounding Cambridge Analytica, Wheatland stepped into the role of Group CEO in order to “clean up the mess”.

Julian is a veteran of fast-growing technology companies and an expert in the opportunities, pitfalls and dangers that scaling technology businesses can bring. He is a serial entrepreneur who has spent 25 years investing in, managing and advising breakthrough technology companies: matching their strategies to markets, managing the challenges of rapid growth, and delivering value for customers and investors.

Julian Wheatland now serves as CEO of Brava Systems, the Enterprise Management System for the real estate industry. He began his career at PA Consulting, advising clients on the impact and opportunities created by online innovation. He moved into fund management in the mid-noughties investing into early stage cleantech and security tech companies and, from there, founded Hatton International, a specialist technology commercialisation business.

Prior to Brava Systems, Julian was CEO of Cornerstone FS plc, a fintech company which he listed on AIM in 2021. He speaks publicly on managing tech growth, technology strategy and marketing, entrepreneurship, data ethics and the impact of AI on corporate operations.


derek-cheng

Derek Cheng

CISO, Deliveroo

Derek is an experienced leader with over 20 years of professional experience in cyber security and risk management. He is currently the CISO for Deliveroo, where he is developing and implementing a security strategy and roadmap to support the company’s ambitious goals. Prior to Deliveroo, Derek was the Chief Security Officer for TalkTalk, where he joined post their cyber attack in 2015 to rebuild the brand and protect TalkTalk’s critical infrastructure, assets, and customer data. He is also currently the CISO Advisor for Square Enix West, where he is helping build and steer their cyber security programme, and on the Advisory Panel for AND Digital overseeing their Cyber Security strategy.

Previously, Derek was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, he spent over 6 years at Deloitte where he managed and performed a multitude of information security and risk management engagements for global Fortune 500 companies across various industries.


JL-headshot-2021

Jonathan Luff

Co-Founder, Epsilon Advisory Partners, and CyLon Ventures

Jonathan Luff is the co-founder of Epsilon Advisory Partners, and CyLon Ventures, advising and investing in outstanding technology companies since 2013. Companies in the CyLon portfolio include Tessian, Immersive Labs, Senseon, Zamna, Dig Security, and Worldr, collectively valued at more than $1bn. From 1998-2012 he served in the British Diplomatic Service, and as an advisor to the Prime Minister at 10 Downing Street, specialising in national security issues, technology and innovation. He has lived and worked in London, Paris, Cairo, Riyadh and Baghdad.

peter-ling

Peter Ling

VP Global Cyber Security Alliances, RiskRecon by Mastercard - Canada

With 28 years’ experience in the Cybersecurity space, Peter is a seasoned global practitioner and technology pioneer, having created numerous offerings in this space. His background spans from operational security response management, systems engineering, and complex technical vendor integrations — to strategic alliances throughout the security and risk markets. His areas of expertise are in Public Key Cryptography (PKI), Secure Communications, Endpoint Protection and Threat & Risk management. He has developed and brought dozens of security products to market internationally and is on a constant journey, assisting partners and clients as the Cybersecurity market continues to meet the challenges of the day.

Mate-Barany

Máté Barany

Enterprise Account Executive, Ping Identity (UK)

Máté Barany has over 12 years of experience working on complex implementation projects across EMEA. Previously as a Solutions Architect and now as an Account Executive, the key to Máté’s success is focusing on the End User Experience – implementing a “Customer First” approach when working with Partners and Customers – while at the same time ensuring key business and technical requirements are met. Máté loves a challenge and believes there is always room for improvement.

Mike-BeaupreBio-768x741-1

Mike Beaupre

Head of Cyber Security, Hays AG (Germany)

Michael is a technology leader with over 28 years of experience in guiding international public sector organizations, DAX 30 businesses, and mid-sized international firms through strategic technology initiatives.

He is an expert in digitization and IT transformation and a thought leader in cyber security, organizational risk management, and IT compliance.

He advises small and large enterprises ranging in size from 20 to 220,000 employees in the medical, pharmaceutical, biotech, translation, and manufacturing industries worldwide, just to name a few.

Throughout his career Michael has led complex, diverse organizations toward enhanced operations while saving hundreds of millions in operating costs.

He is passionate about mentorship, coaching, and removing cultural barriers. He was born in the USA, raised in Texas, and has travelled the world helping people maximize potential. Michael lives in Germany and is focused on family, volunteer work, and supporting a multitude of international clients at Hays.

rob-demain

Rob Demain

Founder and CEO, e2e-assure

Rob started e2-assure after realising that the traditional delivery model for Security Operations Centres (SOCs), focused on technology over people and processes, wasn’t working. Organisations were struggling to resource their teams, struggling to deploy, onboard, and tune their SIEM tools, and as a result, failing to build an effective security operation. Nearly 10 years on, e2e-assure is a thriving intelligence-led threat detection and response SOC that focuses on working with its customers and partners to deliver effective, 24/7/365 security operations.

PKHeadShot

Dr Paul Kennedy

Chief Engineer - Cyber and CEMA, QinetiQ

Dr Paul Kennedy is Chief Engineer – Cyber and CEMA with over 10 years of experience in operational cyber security. At QinetiQ, Paul has worked on cybersecurity for the F-35 combat jet and has worked with the MOD in developing novel cryptographic techniques and advising senior stakeholders on future developments in cryptography. A former RAF Officer, he has worked in military cyber and communications across the UK, NATO, and in the Falkland Islands. Describing himself as a recovering academic, he was previously an Engineering Degree Programme Leader at the University of Glasgow.

PM

Paul Mackie

CISO, Fern Trading, (UK)

With over two decades of dedicated service in the field of cybersecurity, Paul Mackie has established himself as an inspiring and trusted professional in the industry.

His unwavering commitment to helping world-class businesses understand and effectively manage their security risks, coupled with his focus on pragmatic and proportionate controls, has helped ensure consistent value and return of defensive investment for the firms he has worked with.

Paul possesses the ability to identify emerging trends and bring teams together for mutual success. His problem-solving skills enable him to quickly address root issues and deliver pragmatic and practical solutions. His driving force is an unwavering dedication to delivering outstanding quality and making a positive difference in the world.

As a highly capable information security professional, Paul has successfully delivered strategic transformations, provided effective management, conducted comprehensive assurance, offered valuable consultancy, and demonstrated exemplary security leadership to both UK based and global businesses including Associated British Foods, The Bank of
England, Octopus Investments, Gatwick Airport, The ANZ Bank, NTT DoComo, and King’s College London.

Currently serving as the CISO for Fern Trading, Paul is responsible for a multi-billion-pound portfolio business operating in the telecommunications, renewable energy, construction, and healthcare sectors, where he continues to excel in driving strategic security initiatives and fostering a culture of resilience within the portfolio firms.

Haydn-Brooks

Haydn Brooks

CEO, Risk Ledger

Coming from a background in cyber risk specialising in supply chain security, I quickly recognised the huge process issues, sunk cost, lost opportunities, and valuable business hours wasted by clients and suppliers alike, all trying to run disparate supply chain assurance programmes in a mutually exclusive way.

This led me to co-found Risk Ledger, the technology platform that combines a security governance platform with a secure social network. Clients using our platform have seen their cost of running a supply chain security programme reduce by over 70% whilst collecting better quality and more actionable data over their suppliers.

Risk Ledger is the enabler for assurance programmes to:
● rapidly and easily scale across whole supply chain networks;
● allow the electronic collection of self-assessed assurance data;
● deliver continuous real time monitoring & alerts of supplier security controls;
● provide the tools for just one FTE to run entire assurance programme for 1000’s of suppliers.

Take a look at the Risk Ledger web site (https://riskledger.com) to see our growing client list serving multiple industry sectors, FTSE100 companies, leading commercial enterprises and key government departments.

I and my team are innovating and pushing mutual supply chain assurance and security governance into the twenty second century. Come and join us on the journey!

🏆 2022 Financial Times Tech Champion – https://www.ft.com/content/dd04f86d-14a1-4359-9c94-0225c564bf02

🏆 Forbes List 30 Under 30 – Manufacturing & Industry.

🏆 Winner of the 2019 Cyber Den Award sponsored by the UK Government’s National Cyber Security Centre.

🏆 Winner of the 2019 Most Innovative Cyber Company Award sponsored by TechUK.

Sam-Barfoot

Sam Barfoot

Security Leader, Checkmarx

As a highly motivated security leader, experienced in designing and building security first solutions, I possess the key skills for full stack on-premise and cloud development. Experienced in a range of large and small scale projects allows me to apply in-depth technical knowledge and industry experience to deliver the most appropriate solution.
Translating technical requirements to business stakeholders ensuring transparency and understanding. With a desire to continuously improve and learn, I have a passion for innovation and enjoy working both independently and/or within a team to achieve targets.

360 Series Sponsors

All Sponsors Banner

No typical industry barrier – natural integration between R&D technology leaders, CIOs, CISOs and Cyber Threat Intelligence Directors – we are all part of the security discussion! A friendly business community focus and dedicated networking events will transform the Cyber Exchange 360 & Talk to the Board 2020 into an unmissable experience.

Fully immersive programme
Contribute to dynamic debates, think tanks, breakfast briefing, boardroom, technology innovation sessions for CISOs. Input to co-branded best practice output reports.

Quality-matched and part of the same solution
We invite companies to partner that are of genuine interest to the audience. Productive meetings that are part of the solution.

Real-time, results-driven benchmarking
Integrated technology to deliver ‘live’ metrics directly from the CISO and cyber threat intelligence community.

Benefit from a unique quality and balance
Participants are carefully balanced to ensure the right people are in the room.

The Pulse team has 15 years+ experience of connecting cybersecurity leaders across the world. We are uniquely positioned through well-honed global networks and as stakeholder in the cybersecurity community approach to work thoroughly on your wish lists of companies, persons or countries to increase the chances of you meeting face to face with the contacts that are most critical for your business across a wide range of markets.

Grow brand awareness by being at the same table as your target business prospects. Cyber Exchange 360 & Talk to the Board brings world-class CISOs, cybersecurity leaders and risk managers around the same table as you to develop best practices and standards. We will position your company and offering as a thought-leader amongst peers.

Connect with new and existing clients as a fully integrated partner. You and your team will be an integral part of the programme and a dedicated networking schedule. We guarantee you will leave with a wealth of new business connections, and new professional friends!

Demonstrate security innovation with new and existing clients. Place your CEO, CTO, CIO, CISO, R&D executives on the podium or co-present a case study with a client. Fine-tune your market solutions, messages and approaches to further enable secure platforms.

Shaping the security agenda…. No typical industry barrier between buy and sell – natural integration between R&D technology leaders, CIOs, CISOs and Cyber Threat Intelligence Directors – we are all part of the security discussion!

Trusted environment – The entire event is held under the Chatham House Rule. Input to co-branded best practice output reports.

www.threatlocker.com/

Sponsorship opportunities

Riskrecon By Mc Pos

RiskRecon by Mastercard enables you to easily achieve better risk outcomes for your enterprise and your supply chain. RiskRecon’s cybersecurity ratings and assessments make it easy for you to understand and act on your risks, delivering accurate, risk-prioritized action plans custom-tuned to match your risk priorities. RiskRecon traces its beginnings to 2011 when our founder, Kelly White, asked himself, “Is it possible to measure the security program quality of any company simply by looking its Internet-facing presence?” Kelly is a long-time information security practitioner and bank CISO who witnessed first-hand the need for adapting third-party risk controls to meet the new challenges resulting from decentralized IT and SaaS apps. He has many years of hands-on experiencing building big data and analytics solutions to detect fraud and security vulnerabilities in high-velocity transaction environments. Like most organizations at the time, his bank’s third-party risk management assessments relied heavily on questionnaires and other vendor attestations. This approach worked well ten years ago with a small number of large vendors, mostly in-house deployments, purchases controlled by central IT, and a well-defined set of Internet vulnerabilities. With the decentralization of IT purchasing and rapid adoption of SaaS, this approach was becoming less effective and more resource-intensive. What if instead of trying to use the “old” risk management model, his institution could trust an objective source that automatically pinpointed specific gaps in any organization’s security programs and performance? Questionnaires and surveys are helpful in evaluating one’s intent but provide little verifiable insight into actual practices and discipline. After realizing there were no such solution available, he decided to build his own. After testing and validating his solution with many peers, Kelly decided to pursue the idea full time and founded RiskRecon, officially incorporating in October of 2015. RiskRecon is headquartered in Salt Lake City, UT with a presence in Boston, MA and representatives around the world.

www.riskrecon.com

www.mastercard.us/en-us.html

E2e

Our vision at e2e-assure is to provide the most advanced and effective Threat Detection & Response service in the country. We are committed to outpacing threat actors, innovating rapidly to pre-empt and disrupt their tactics and techniques. With an understanding that every organisation is at a different stage in its cybersecurity journey, we are set up to meet customers where they are with options to accelerate their security posture evolution both tactically and strategically. Our modular service portfolio provides defined detection outcomes aligned to the Mitre Att&ck framework and offers targeted attack disruption and active response, ensuring our customers are always one step ahead of potential threats. Our approach to safeguarding clients is proactive and immediate. We actively respond to critical alerts with immediate containment actions, ensuring that businesses remain secure, resilient, and prosperous.

www.e2e-assure.com

www.emergentriskinternational.com

At Ping Identity

At Ping Identity, we believe in making digital experiences both secure and seamless for all users, without compromise. That’s digital freedom. We let enterprises combine our best-in-class identity solutions with third-party services they already use to remove passwords, prevent fraud, support Zero Trust, or anything in between. This can be accomplished through a simple drag-and-drop canvas. That’s why more than half of the Fortune 100 choose Ping Identity to protect digital interactions from their users while making experiences frictionless. Learn more at www.pingidentity.com. 

Visit website

QinetiQ

QinetiQ is an integrated global security and defence company. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way. We address today’s rapidly changing cyber security environment, with decades of experience protecting the most highly targeted organisations and securing the most critical operations. With our defence-grade solutions, rigorous threat checks and our understanding of defending against the most persistent threats, we can help you build digital resilience so you can face the future with greater certainty.

www.qinetiq.com/

https://www.qinetiq.com/en/

Visit website

Qualys

Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.

For more information, please visit www.qualys.com

Visit website

Checkmarx

 Checkmarx is constantly pushing the boundaries of Application Security Testing to make security seamless and simple for the world’s developers while giving CISOs the confidence and control they need. As the AppSec testing leader, we provide the industry’s most comprehensive solutions, giving development and security teams unparalleled accuracy, coverage, visibility, and guidance to reduce risk across all components of modern software – including proprietary code, open source, APIs, and infrastructure as code. Over 1,600 customers, including half of the Fortune 50, trust our security technology, expert research, and global services to securely optimize development at speed and scale. For more information, visit our website, check out our blog, or follow us on LinkedIn. 

Visit website

Risk Ledger Log

Did you know 60% of organisations have suffered a security breach through a third party? It’s understandable – the traditional processes are broken. Organisations face a burden of ineffective, inefficient admin. ‘Point in time’ cybersecurity assessments make for poor-quality data that goes out of date fast, offering little protection.

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

Interested in learning more? Visit https://riskledger.com/.

Visit website

ClubCISO

ClubCISO is a global community of ‘in role’ information security leaders working in public and private sector organisations, founded and funded by Telstra Purple. We are a community of peers, working together to help shape the future of the profession. We are a non-commercial organisation with over 700 members helping to define, support, and promote the critical role and value of information security in business and society. Through ClubCISO, members can build their networks, support and coach their peers, solve problems, and create practical guidance that moves the industry forward.

For more information, visit: www.clubciso.org

Visit website

Who attends

By Designation

Participants will include CISOs and CSOs in addition to:

  • Chairperson
  • CEO
  • Non-Executive Directors, Board Member, Audit & Risk Committee Member
  • CFO, CRO, GC, COO, CTO, CIO, CMO, HR
  • Chief Information Security Officer
  • Director of Cybersecurity / Head of Cyber Threat Intelligence
  • Head of Governance
  • Head of Innovation
  • Director of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer
  • Heads of Corporate Security/Resilience

By Sector

All private and public sectors are welcome to attend.

Venue and Accommodation

London Marriott Grosvenor Square

Grosvenor Square, London W1K 6JP
www.marriott.com/en-us/hotels/londt-london-marriott-hotel-grosvenor-square

The 5th Cyber Exchange 360: Talk to the Board will be hosted at the prestigious London Marriott, Grosvenor Square.

This 5-star, luxury hotel is perfectly situated in the upscale Mayfair neighbourhood, minutes from Oxford Street’s world-class shopping, Hyde Park and iconic landmarks.

Enjoy scenic views of Grosvenor Square or the private gardens; indulge in steakhouse dining at Gordon Ramsay Bar & Grill, or sample modern fare at Lucky Cat by Gordon Ramsay, an Asian Eating House and vibrant late-night lounge. Unwind with a craft cocktail in the hotel’s 1920’s-inspired award-winning speakeasy bar, The Luggage Room.

Conference venue

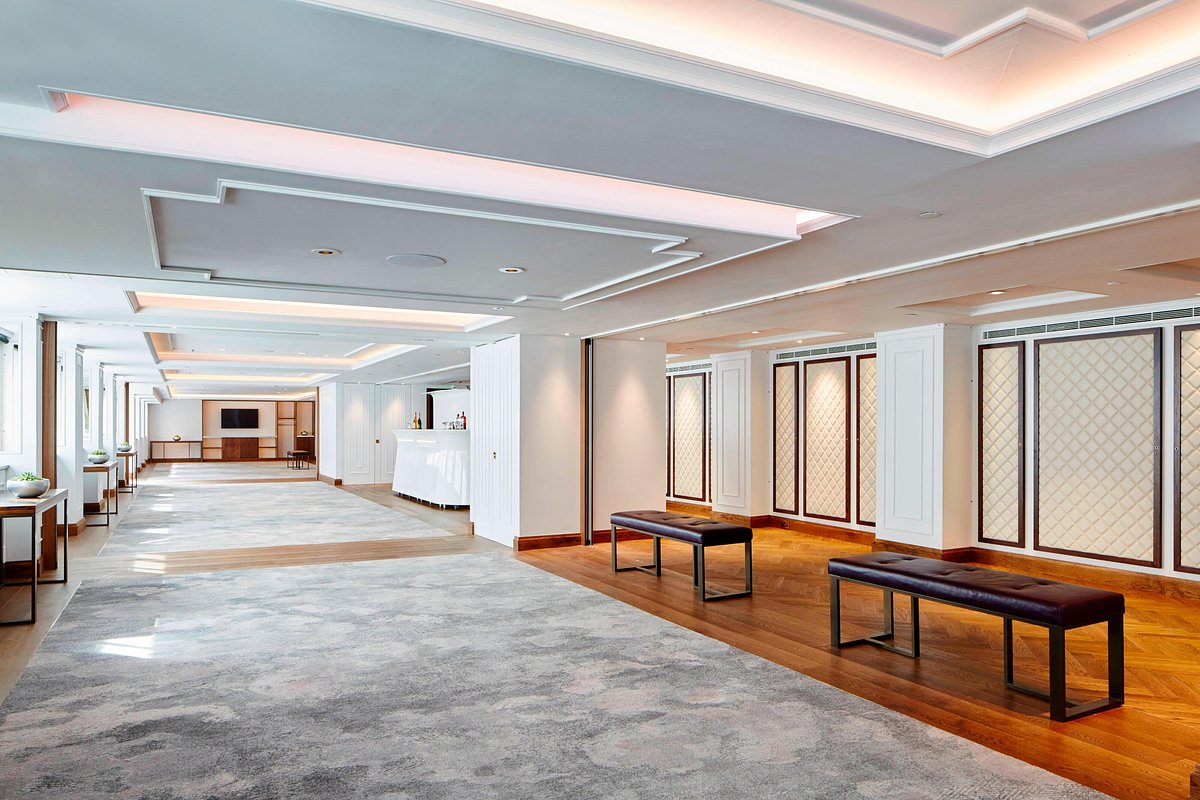
The London Marriott Grosvenor Square offers a newly renovated venue space, which is imbued with natural daylight, making it ideal for business or social gatherings complemented by expert catering and audio-visual resources.

5th Cyber Exchange 360: Talk to the Board will be hosted in The Westminster Ballroom which totals 762 square meters and is one of London’s largest pillar-free spaces with beautiful high ceiling and chandeliers. Our networking hub will be hosted directly in connection to the ballroom where all coffee breaks and lunch will be hosted.

Location

London Marriott, Grosvenor Square
Grosvenor Square, London W1K 6JP

www.marriott.com/en-us/hotels/londt-london-marriott-hotel-grosvenor-square
Tel: + 44 20-74931232

Travel – Closest Stations:
Oxford Street / John Lewis is 455 meters away, 7 min walk.
Selfridges (BX) is 652 meters away, 9 min walk.
Oxford Circus is 673 meters away, 10 min walk.
Bond Street is 720 meters away, 10 min walk.
Green Park is 1056 meters away, 14 min walk.

whitehall-suite

Gallery from our 5th Cyber Exchange 360: Talk to the Board
London Marriott Grosvenor Square

View the initial Photo gallery below.

*Please check back early next week for additional images of the networking, and lovely dinner at Alto by San Carlo on the Rooftop of Selfridge’s.


2023 Downloads – 5th Cyber Exchange 360: Talk to the Board

Brochure 2023

Brochure 2023

Photo Gallery 2023

Photo Gallery 2023

Testimonials

CYBEREXCHANGE360_RGB-2“I wanted to be part of the Cyber Exchange 360 and Talk to the Board event because I’ve always been so fascinated by technology, particularly what it brings on the dark side – the dark underbelly of technology being cyber attacks and the cyber risk. Being from the world of insurance, I was hoping to share some of my experience with assessing risk and managing risk because, fundamentally, this is what the CISOs are trying to do. I think they’re doing an amazing job, but cybercriminals are always faster and quicker than any of us, so we must stay alert. I’ve learnt about how lonely and vulnerable the CISO feels. I’ve been a CEO a few times and always felt the CEO took the can for everything. I thought then that people working lower in the organisation wouldn’t feel so vulnerable. But I was hearing that from some of the attendees, and as boards, we need to think about how we can be more of a support for them so that they don’t feel so lonely and perhaps under threat. If your world is looking at cyber risk and you’re a CISO, I would come to this event and get involved because you are sharing and gaining simultaneously.” Dame Inga Beale, Former CEO, Lloyd’s of London 

CYBEREXCHANGE360_RGB-1

 “The great thing about Pulse Conferences events is you get a different perspective from our core market. So it’s perfect for me to come here and get that completely different perspective and speak to people at the level that Pulse Conferences attract. Talk to the Board is interesting because the business dimension is the most important thing about cyber security. So, speaking to the board brings me that business dimension to cyber security. As a sponsor, we get so much value out of these events, not just from potential clients but for people to partner with, and we get different perspectives on what the market is and what other people are prioritising.” Dr. Paul Kennedy, Chief Engineer – Cyber and CEMA, QinetiQ 

CYBEREXCHANGE360_RGB-1

“The theme of CISO Exchange 360 and Talk to the Board, for me, is absolutely spot on. We must bridge the gap between the IT community and the board members, because we’re all fighting against the same enemy. We have competitors in the business who steal our market share. We have competitors in cyber security who steal our intellectual property and money. And so a competitor is a competitor. Coming here and talking to the board and helping validate what resonates with them to help the IT community have their voice heard by the board members is very special and powerful. We have silos of silos in companies. But criminals don’t have silos. They don’t have borders or boundaries. So, to win the fight, we must come together and build coalitions of capability and bridge across the boundaries we live in so we can stop the enemy and kick them out of our networks and our organisations. This event is fantastic. It’s a great forum. It’s a great opportunity. Anytime you can connect to another individual on a human level, person to person, it’s powerful. Board members and IT people speak different languages. We must learn to communicate effectively to help make rational decisions within a context that matters. So this event, this forum, is exactly what I’m looking for.” Michael Beaupre, Head of Cyber Security, Hays

“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.” Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey

“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics” Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics

“First class organisation and presentations. I would highly recommend Pulse conferences for those Senior Managers who need to get value from their time and attendance and for the quality of guest speakers” Ray Jackson, CISO, Telrock Systems Ltd

“It’s a great event with some high-calibre attendees, and the turnout has been impressive. The one-to-ones provide a superb opportunity to spend some focused time with key customers. And it was brilliant to have one of our teams hosting one for the roundtables around CISO practical tips. It’s a unique in that it is a closed community. You get more one-on-one time than you would do at another conference.” Remco Postma, Sales Leader, SailPoint

“The day has been great. I enjoyed a lot of good conversations. I’ve spent time with interesting companies and interesting people. Pulse always uses thrilling venues, and the Science Museum in London is special. What’s unique is that CISOs can talk to the board – they have opinions and they want to share them, and also listen to the guidance offered.” Scott Daly, Commercial Manager, HUMAN

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” Deborah Saffer, Global Deputy CISO, Cushman & Wakefield

CISO-360-Congress-2021

Genevieve-Landricombe-testimonial-Linkedin


CISO-360-Congress-2021-1

Dan-Panesar-testimonial-Linkedin

Owanate-Bestman-testimonial-Linkedin

CISO-360-Congress-2021-1

Responses-to-Owanate-testimonial-Linkedin

CISO-360-Congress-2021

Scott-Nicholson-testimonial-Linkedin

CISO-360-Congress-2021-1


“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions

 CISO-360-Congress-2021

Sophie-Jdouri-testimonial-Linkedin

CISO-360-Congress-2021-1

Trude-Palmer-testimonial-Linkedin

CISO-360-Congress-2021

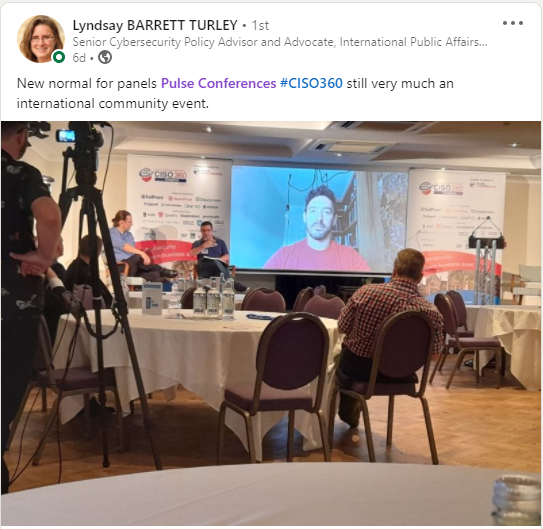
Lyndsay-Barrett-Turley-testimonial-Linkedin

CISO-360-Congress-2021-1

Club-CISO-testimonial-Linkedin

CISO-360-Congress-2021-1

Brian-Brackenborough-testimonial-Linkedin

4TH-CISO-360-CONGRESS-1

Jomnathan-Colette-comment-linkedIn

CISO360Congress2019-Rome-and-dates-colour

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS

 CISO360Congress2019-Rome-and-dates-colour

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This is my second CISO Exchange 360 and Talk to the Board and, once more, it’s a great mix of enterprise professionals, security professionals and senior leaders. It’s always a good atmosphere; people get to ask questions in a setting they might not ordinarily have the chance. I’ve been coming to Pulse Conferences events for a few years now. I think the Pulse team run amazing events. They’re always covering relevant subjects, the audience gets involved, and the speakers are a good mix of generalists and specialists. It’s great to hear from board executives and have CISOs sit alongside them, asking questions. It’s a sort of reversal of the status quo.” Jonathan Luff, Co-Founder, CyLon Ventures 

CYBEREXCHANGE360_RGB-1

“The agenda of Talk to the Board was a big pull. I’ve heard of Pulse Conferences, but this was my first CISO event. I saw the questions posed and the incredible line-up of people speaking, and I knew I had to be in the room. It’s so rare to have that opportunity to hear it directly from the CISOs and the board. So what more could you ask for if you’re up and reporting to boards and you need to communicate with them effectively? It’s a unique opportunity. What is important for them? For anyone thinking of coming to a Pulse Conferences event, just do it. Block out that time, make the commitment and realise that it’s an investment not only in your company and what your company needs from you but also in your professional development.” Katherine Leivesley, Head of Legal, Offer and Sourcing, Kingfisher PLC

“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.” Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)

“The emerging consensus from Talk to the Board was how challenging it is for CISOs to present cyber risk to the board in an intelligible way for non-technical people. The challenge for the board is then to understand that and take action. Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. It’s great to have board and CISO side of the equation together at this event. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.” Robert Hannigan, Chairman, BlueVoyant. Former Director, GCHQ

“As ever, an excellent opportunity to have time infront of executives who are likely to be very similar to the executives that all CISOs are likely to have to bring on side. It gave fascinating insights, and some I will certainly be using in the future.” Julia Harris, Information Security Assurance and Compliance Director, Flight Centre Travel Ltd

“I’ve had a few good sessions with various organisations. Looking at what’s going on across the industry and how organisations are doing things slightly differently has been very interesting. The need for greater collaboration is a key message. It is a fantastic event, and the venue at the Science Museum is the perfect size: I’ve had a breadth of conversations, but it’s small enough to have one-to-one discussions.” Andrew Kelly, Principal Consultant, QinetiQ

“It was a fantastic day. It is great to be back in London and meeting people again. Pulse events are always absolutely amazing. As usual it was such a diverse group of people from so many different departments – finance, manufacturing and so on – and they are all at a certain level where you start to understand strategy and where the industry is going in the UK. I probably learnt more than the people I spoke with, so it’s been brilliant.” Paul Baird, UK Chief Technology Security Officer, Qualys

 “Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” Jonathan Armstrong, CEO, Cordery  

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK 

CISO-360-Congress-2021-1

Responses-to-Pulse-Post-testimonial-Linkedin

CISO-360-Congress-2021-1

CyberCMO 360 GROWTH Summit Logo WHITE-1

CISO-360-Congress-2021-1

Marillise-de-Villers-testimonial-Linkedin

CISO-360-Congress-2021-1

Oliver-Rochford-testimonial-Linkedin

CISO-360-Congress-2021-1


“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys

 CISO-360-Congress-2021-1

Bridewell-testimonial-Linkedin

CISO-360-Congress-2021-1

Alan-Jenkins-Becky-Pinkard-testimonial-Linkedin

4TH-CISO-360-CONGRESS-1


“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World

 4TH-CISO-360-CONGRESS-1


“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions

 Mena-testimolinal

CISO360Congress2019-Rome-and-dates-colour

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP

 CISO360Congress-Asia & Oceania


“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia

 CISO360Congress2019-Rome-and-dates-colour

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint


4TH-CISO-360-CONGRESS-1


“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP

 4TH-CISO-360-CONGRESS-1


“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

 4TH-CISO-360-CONGRESS-1


“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

 4TH-CISO-360-CONGRESS-1


“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica

 CISO360Congress-Asia & Oceania


“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

 CISO360Congress-Asia & Oceania


“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

 CISO360Congress2019-Rome-and-dates-colour

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack


CISO360Congress2019-Rome-and-dates-colour


Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

 CISO360Congress2019-Rome-and-dates-colour

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85

 CISO360Congress-Dubai-Logo-1-1024x361small


“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“

Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

 LOGO1-2nd-CISO-360-Congress-Lisbon-1


“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin


LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh

— Holly Foxcroft (@holly_foxcroft) 21 June 2018

LOGO1-2nd-CISO-360-Congress-Lisbon-1


“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London


LOGO1-2nd-CISO-360-Congress-Lisbon-1


“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

 CISO360Congress2019-Rome-and-dates-colour


“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

 CISO360Congress2019-Rome-and-dates-colour


“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group


CISO360Congress2019-Rome-and-dates-colour


“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint


LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin


LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

 LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO

— Viktor Polic (@ViktorPolic) 26 June 2018

LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4


CISO360Congress2019-Rome-and-dates-colour


“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal


CISO360Congress2019-Rome-and-dates-colour


“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller


CISO360Congress
 

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

 LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018

CISO360Congress


“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland


Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

 CISO360Congress


““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
 

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018

High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018

CISO360Congress


“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government


CISO360Congress2019-Rome-and-dates-colour


“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

 CISO360Congress


“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV

CISO360Congress


“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum


CISO360Congress


““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

 CISO360Congress


““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

 CISO360Congress


““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting


Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

CISO360Congress-Dubai-Logo-1-1024x361small


“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)


Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

 LOGO-2nd-CISO-360-Congress-2018-WITH-Lisbon


“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP


In Action

Testimonials – CISO 360 Global Congress

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”
CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”
CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”
CTO and Co-Founder, JIT (Israel)

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”
Regional Executive, KnowBe4 (The Netherlands)

“Great conference! From the beginning, the level of participant engagement was very high. The content was very informative and the presenters very knowledgeable. Every aspect of Global CISO 360 was extraordinarily well done. I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”
Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”
Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well. Content and organization made this an excellent event!”
CISO, Infopercept (UK)

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”
Senior Account Executive, Hack the Box (Greece)

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”
GemServ, a Talan Group company (UK)

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”
COO, Risk Ledger (UK)

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”
CISO & DPO, 360 Treasury Systems AG, Germany

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Director, Security, Laureate International Universities Malaysia

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Director, Bestman Solutions

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
CMO, SailPoint

“Insights and experience shared by industry leaders will definitely help me and my organisation in course correcting the strategy”
Senior Cybersecurity, Lafarge Holcim

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
CEO, Cordery

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”
CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Global Deputy CISO, Cushman & Wakefield

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”
Senior Consultant, DHC AG (Switzerland)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”
Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”
CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”
Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”
Director, Resilient World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
Technology Services Head of Cyber Security, DWP (UK)

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the CISO 360 Congress. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.”
Peter Wood, Naturally Cyber LLP

“Excellent conference”
Barbara Aung, CISO, Telefonica

“This was great, we have a lot of good take away’s and loved the lessons learned!”
Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting”
CMO, Vectra

“If you want to hear real CISO experiences, you must attend this event!”
CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
CMO, NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
CMO, SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
CMO, Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Telstra

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ”
Supporting Organisation, ClubCISO

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”,
President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!”
CISO, GOPA International Energy (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”,
Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
CISO, Channel 4

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ”
Director Sales, Sailpoint

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

CISO 360 Congress created a strong platform for peer review, cross pollination of idea and networking.”
CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
CSO, Logista Portugal

“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Cygenta (USA)

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Cygenta (USA)

“Excellent conference, brilliantly put together.”
Director, Bridewell

“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Director of Information Security EMEA, Canon Europe (UK)

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Corporate Security Manager, Logista (Portugal)

“Marvellous event, well-run, packed with useful content you can use”,
Technology Services Head of Security, DWP

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV (Spain)

“Refreshing views of security topics for knowledge improvement!”
CISO, Bank Credibom (Portugal)

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv