
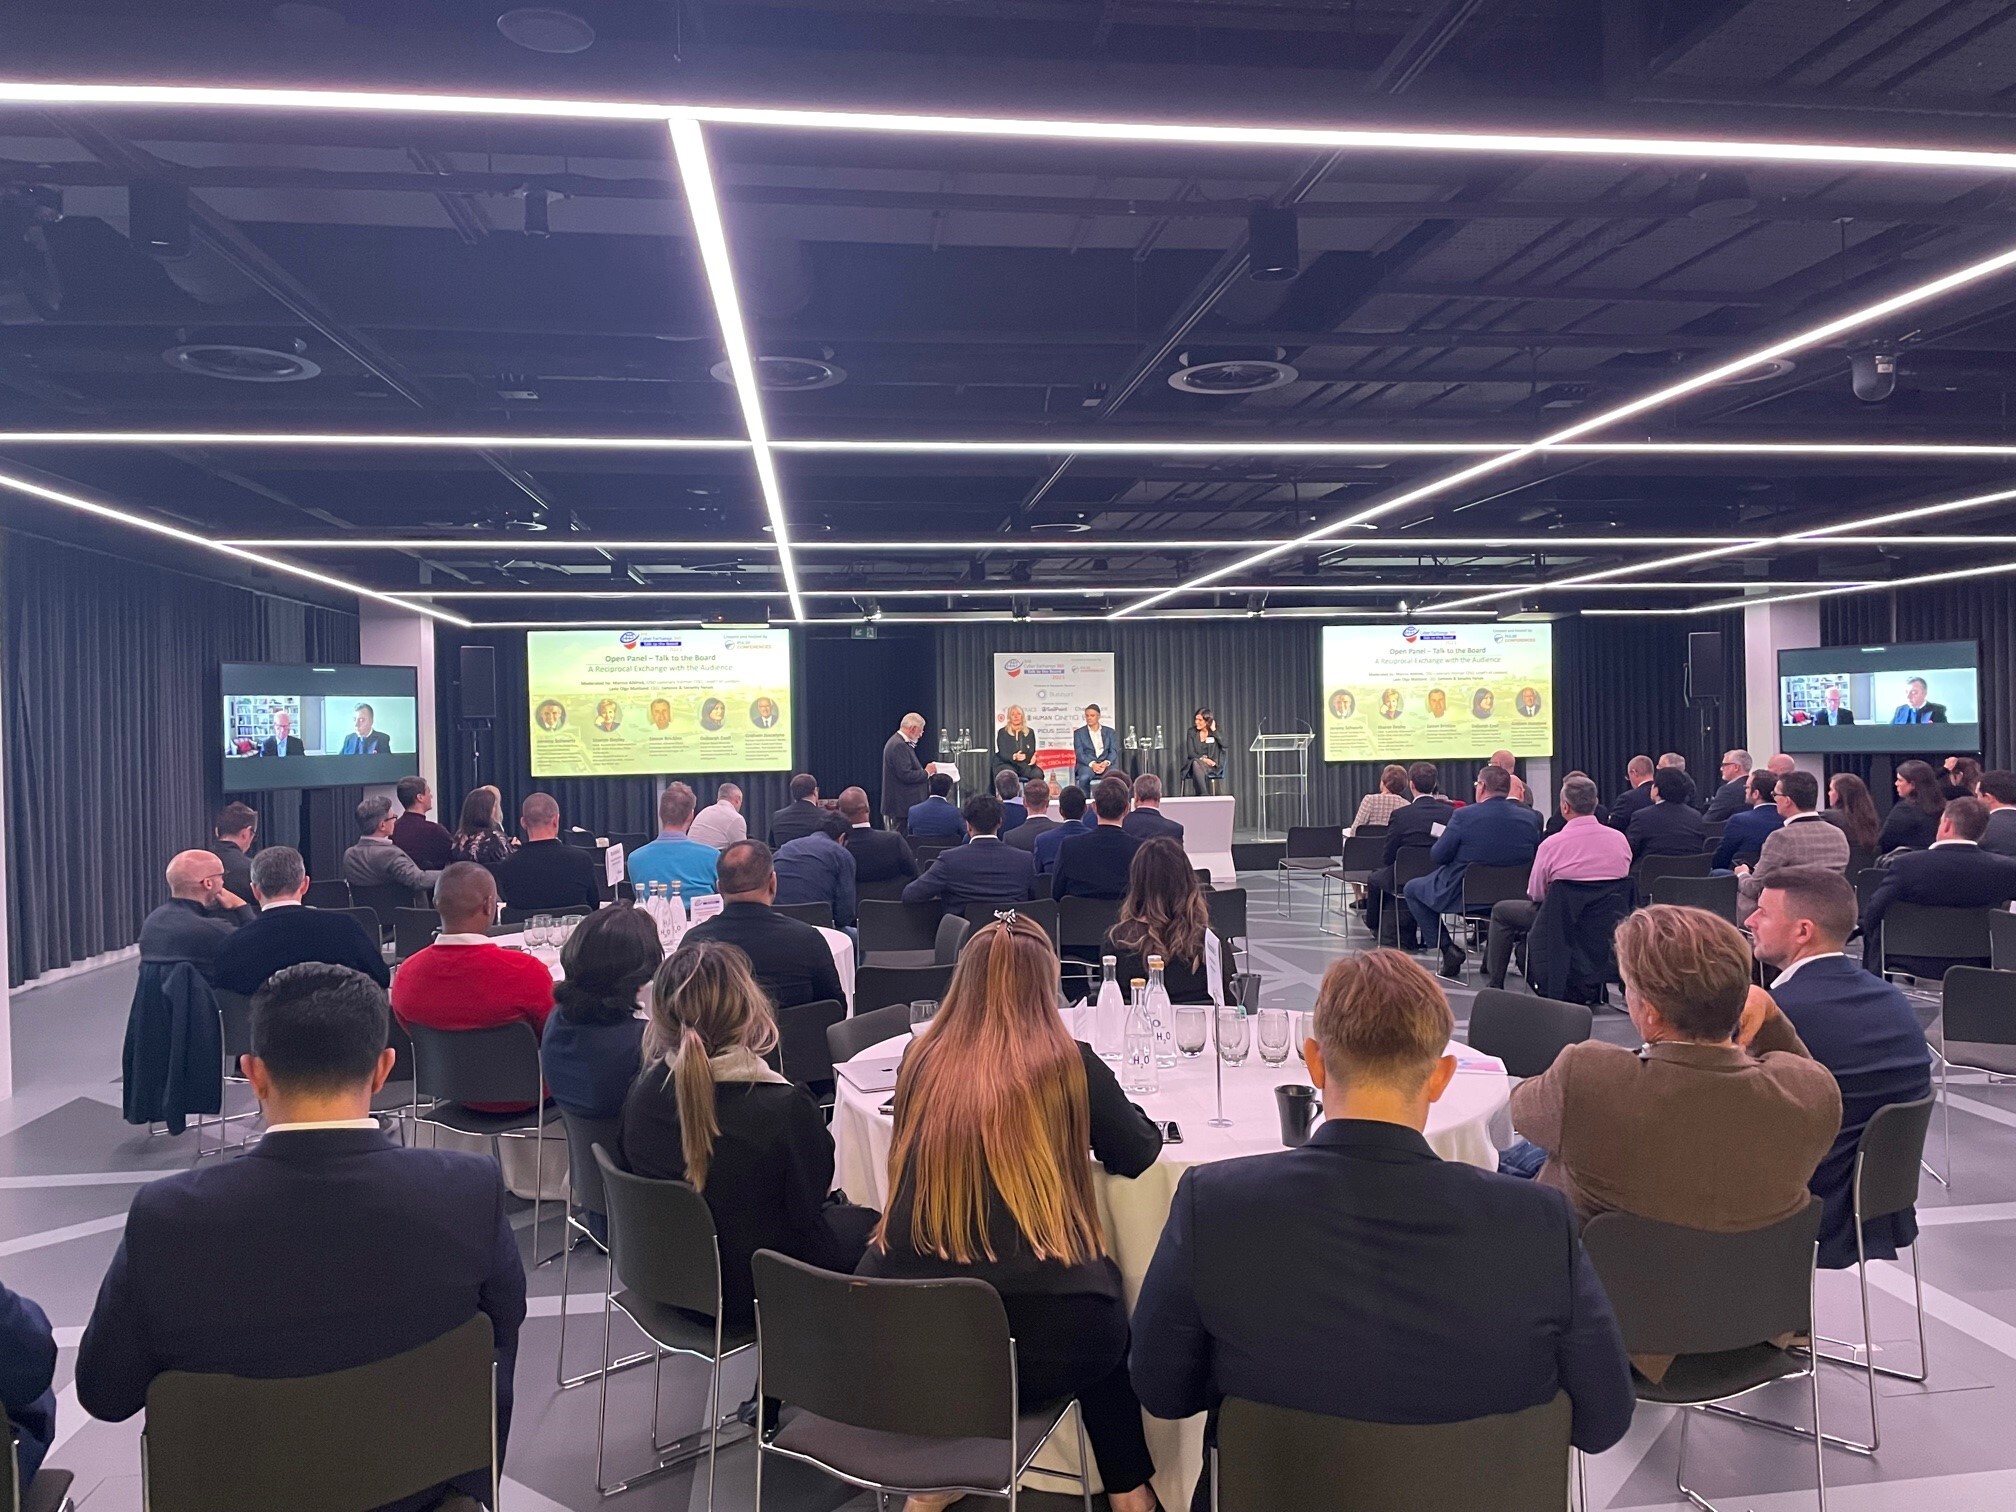
Thank you to everyone who participated in this years’ 4th Cyber Exchange 360: Talk to the Board at the Waldorf Hotel London, 1 November. This was another ground-breaking reciprocal discussion between Board Members, CISO/CSO and C-Suite. CISOs questioned a panel of Board of Directors and compared cyber risk strategy and tactics with peers.
We look forward to seeing you at the 5th Cyber Exchange 360: Talk to the Board conference next year. Save the date – Wednesday 8 November 2023, London!
View Highlights Video- 4th Cyber exchange 360: Talk to the Board
Download Post Event Report 2022.
Talk to the Board!
A rare opportunity to ask the questions you would ideally like to ask your own Board – but with no consequences!
Spanning industry sectors and functional board roles from CEO, CMO, HR, guests attended the 4th Cyber Exchange 360: Talk to the Board Conference, created and hosted by Pulse Conferences at The Waldorf Hotel London on 1 November 2022.
Our programme provided refreshing and refreshing non-security perspectives on cybersecurity – and rare opportunity to talk frankly and test questions that participants would ideally like to ask their own Board.
What are the skills, behaviours and mind set required to lead the security agenda in a pressured, complex and competing business environment and how to create a culture where cybersecurity is considered central to the way companies think and behave? Where does cybersecurity sit in the list of highest Board risks and opportunities? How has this changed in the past year and what are new expectations of CISOs and security leaders?
These are just some of the questions that were tackled in this open exchange with Board Directors from large organisations in a business agenda that covered –
- Building Resilience and Preparedness to Respond to Any Crisis
- Communicating with the Board
- Marketing, Influencing and Collaborating
- Governance, Compliance, Risk
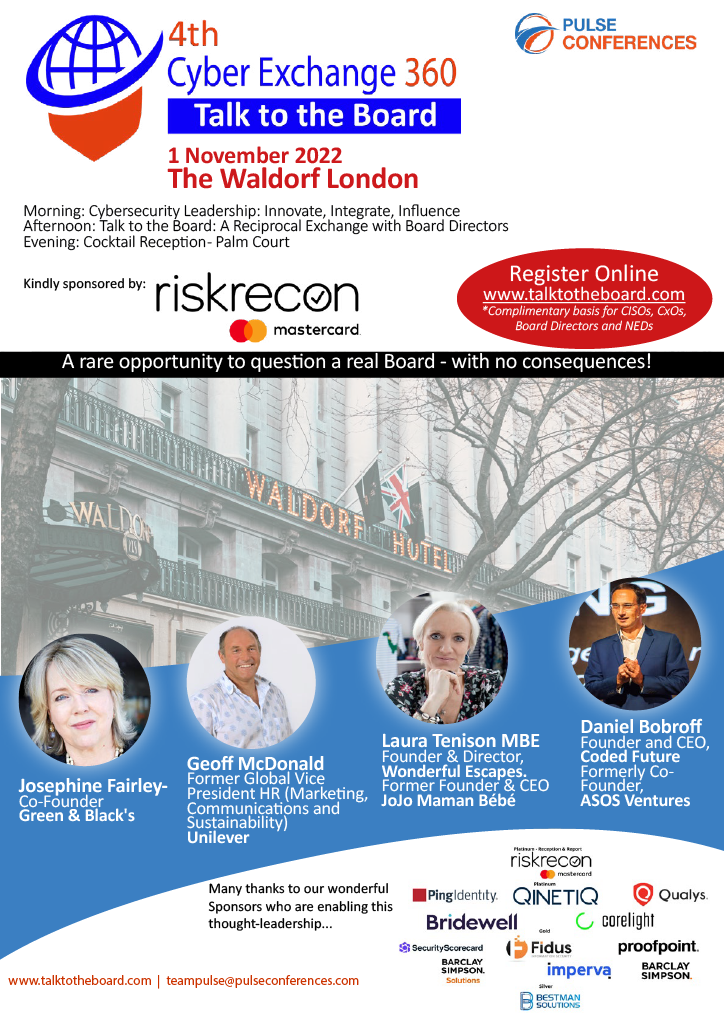
Our Panel of Board Directors for Talk to the Board 2022 covered various sectors and functional board roles.
- Josephine Fairley
Co-Founder, Green & Black’s - Geoff McDonald
Former Global Vice President HR (Marketing, Communications and Sustainability), Unilever - Laura Tenison MBE
Founder & Director, Wonderful Escapes. Former Founder & CEO, JoJo Maman Bébé - Daniel Bobroff
Founder and CEO, Coded Future Formerly Co-Founder, ASOS Ventures
Agenda at a Glance – November 2022
 Morning – Cyber Exchange 360 (08:30-13:30)
CISOs participate in immersive case studies, fireside chats, keynotes. Benchmark strategies and be inspired!
Lunch – Buffet (13:30-14:30)
Network with peers over a delicious buffet lunch in the Palm Court.
Afternoon – Talk to the Board (14:30-17:00)
Reciprocal exchange: CISOs are invited to ‘talk to the board’ and ask the questions they would ideally like to ask their own Board of directors – and without any consequences!
 Evening Cocktail Reception (17:00-20:00) – Palm Court, The Waldorf. Kindly Sponsored by: RiskRecon, A Mastercard Company
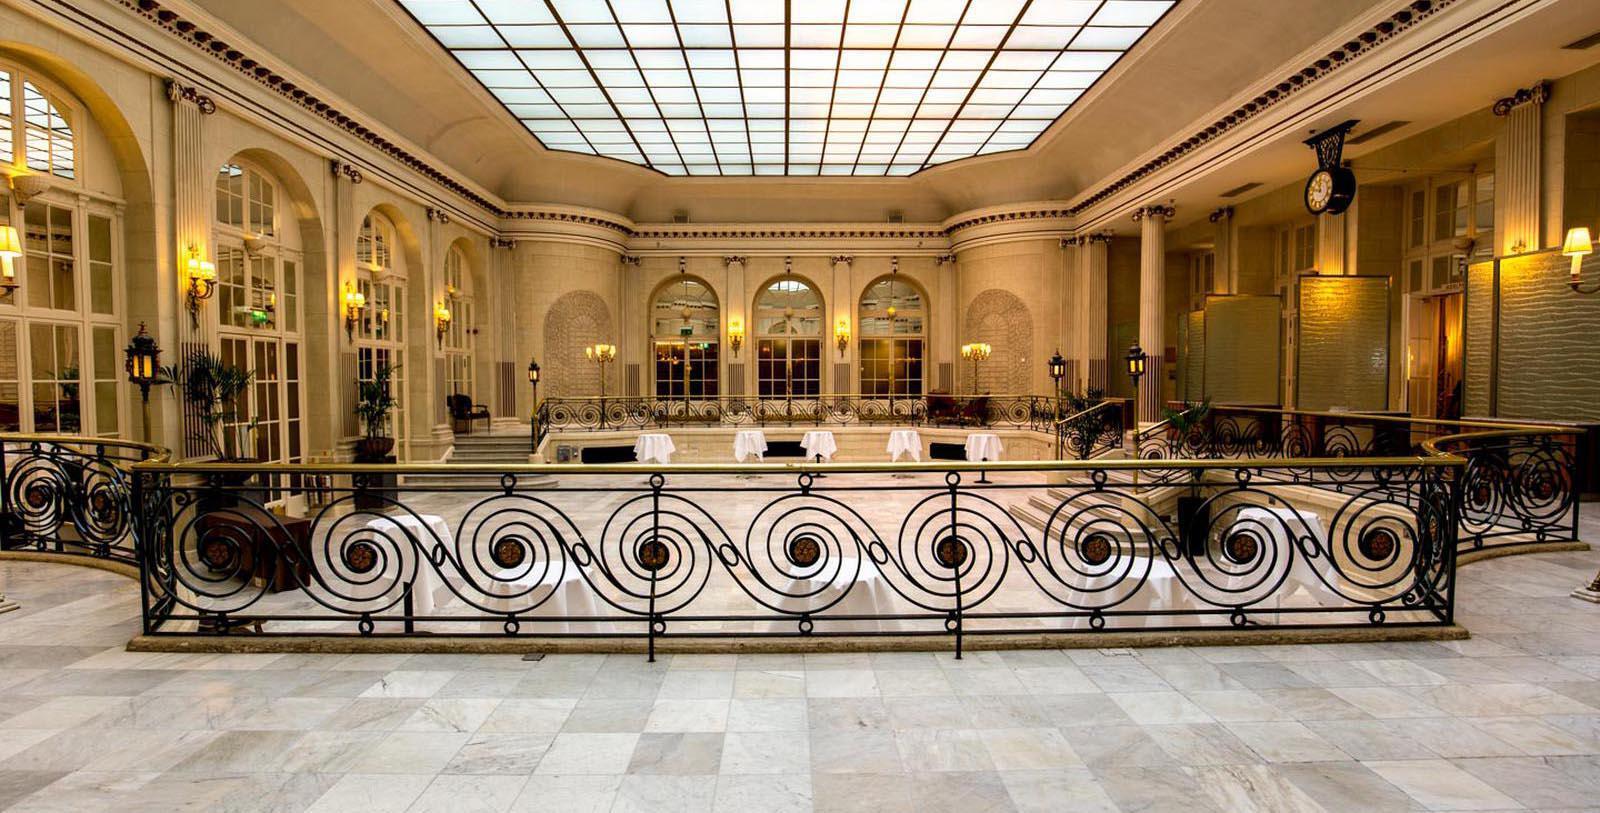
Continue the networking directly outside the conference room in the wonderful Palm Court in the iconic Waldorf. Built in the 1800s, the hotel blends Edwardian grandeur with modern comfort, and it is said that the directors of the 1997 film Titanic took inspiration from the Palm Court space. Cocktails and canapés will be served while guests enjoy a Gatsby-style, modern swing band who will take songs from the last four decades and put their own swinging spin and vintage stylings to create an incredible entertainment experience!
Download the invitation – no need to register separately, this is part of the conference experience!
 Evening CISO 360 Dinner Roundtable (18:30-21:00) – One Aldwych, Private Dining. Kindly sponsored by: Qualys
Numbers are strictly limited to 15 CISOs only, this discussion will focus on ‘What does good risk mitigation look like in today’s heightened threat environment?’
Read more about the dinner and register here separately – subject to availability
As a CISO why attend
- Increase readiness to respond capacity – how can we better communicate during a crisis
- Learn from successful examples of corporate awareness and transformation campaigns
- Hear the learnings from Directors as they share success and war stories
- Gain context! Board perspectives on where cybersecurity sits and useful predictions
- Speak to the Board in a way that makes them understand your pain points
- Compare key metrics and test them on the Board
- Re-energise your approach to driving change and leading teams
As a Board Director why attend
“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them to champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.” Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey
“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”
Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)
“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics”
Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics
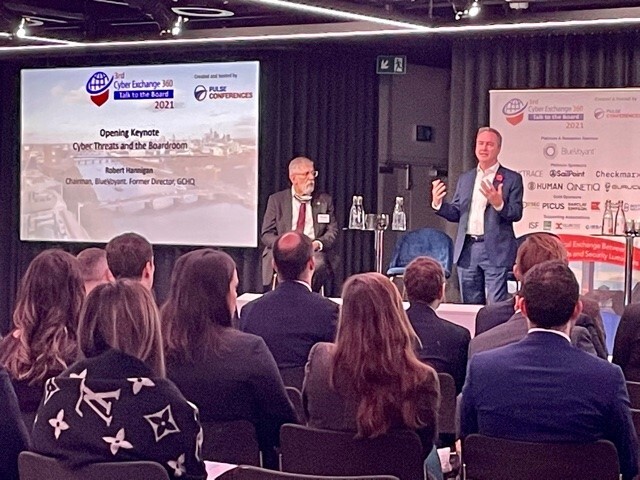
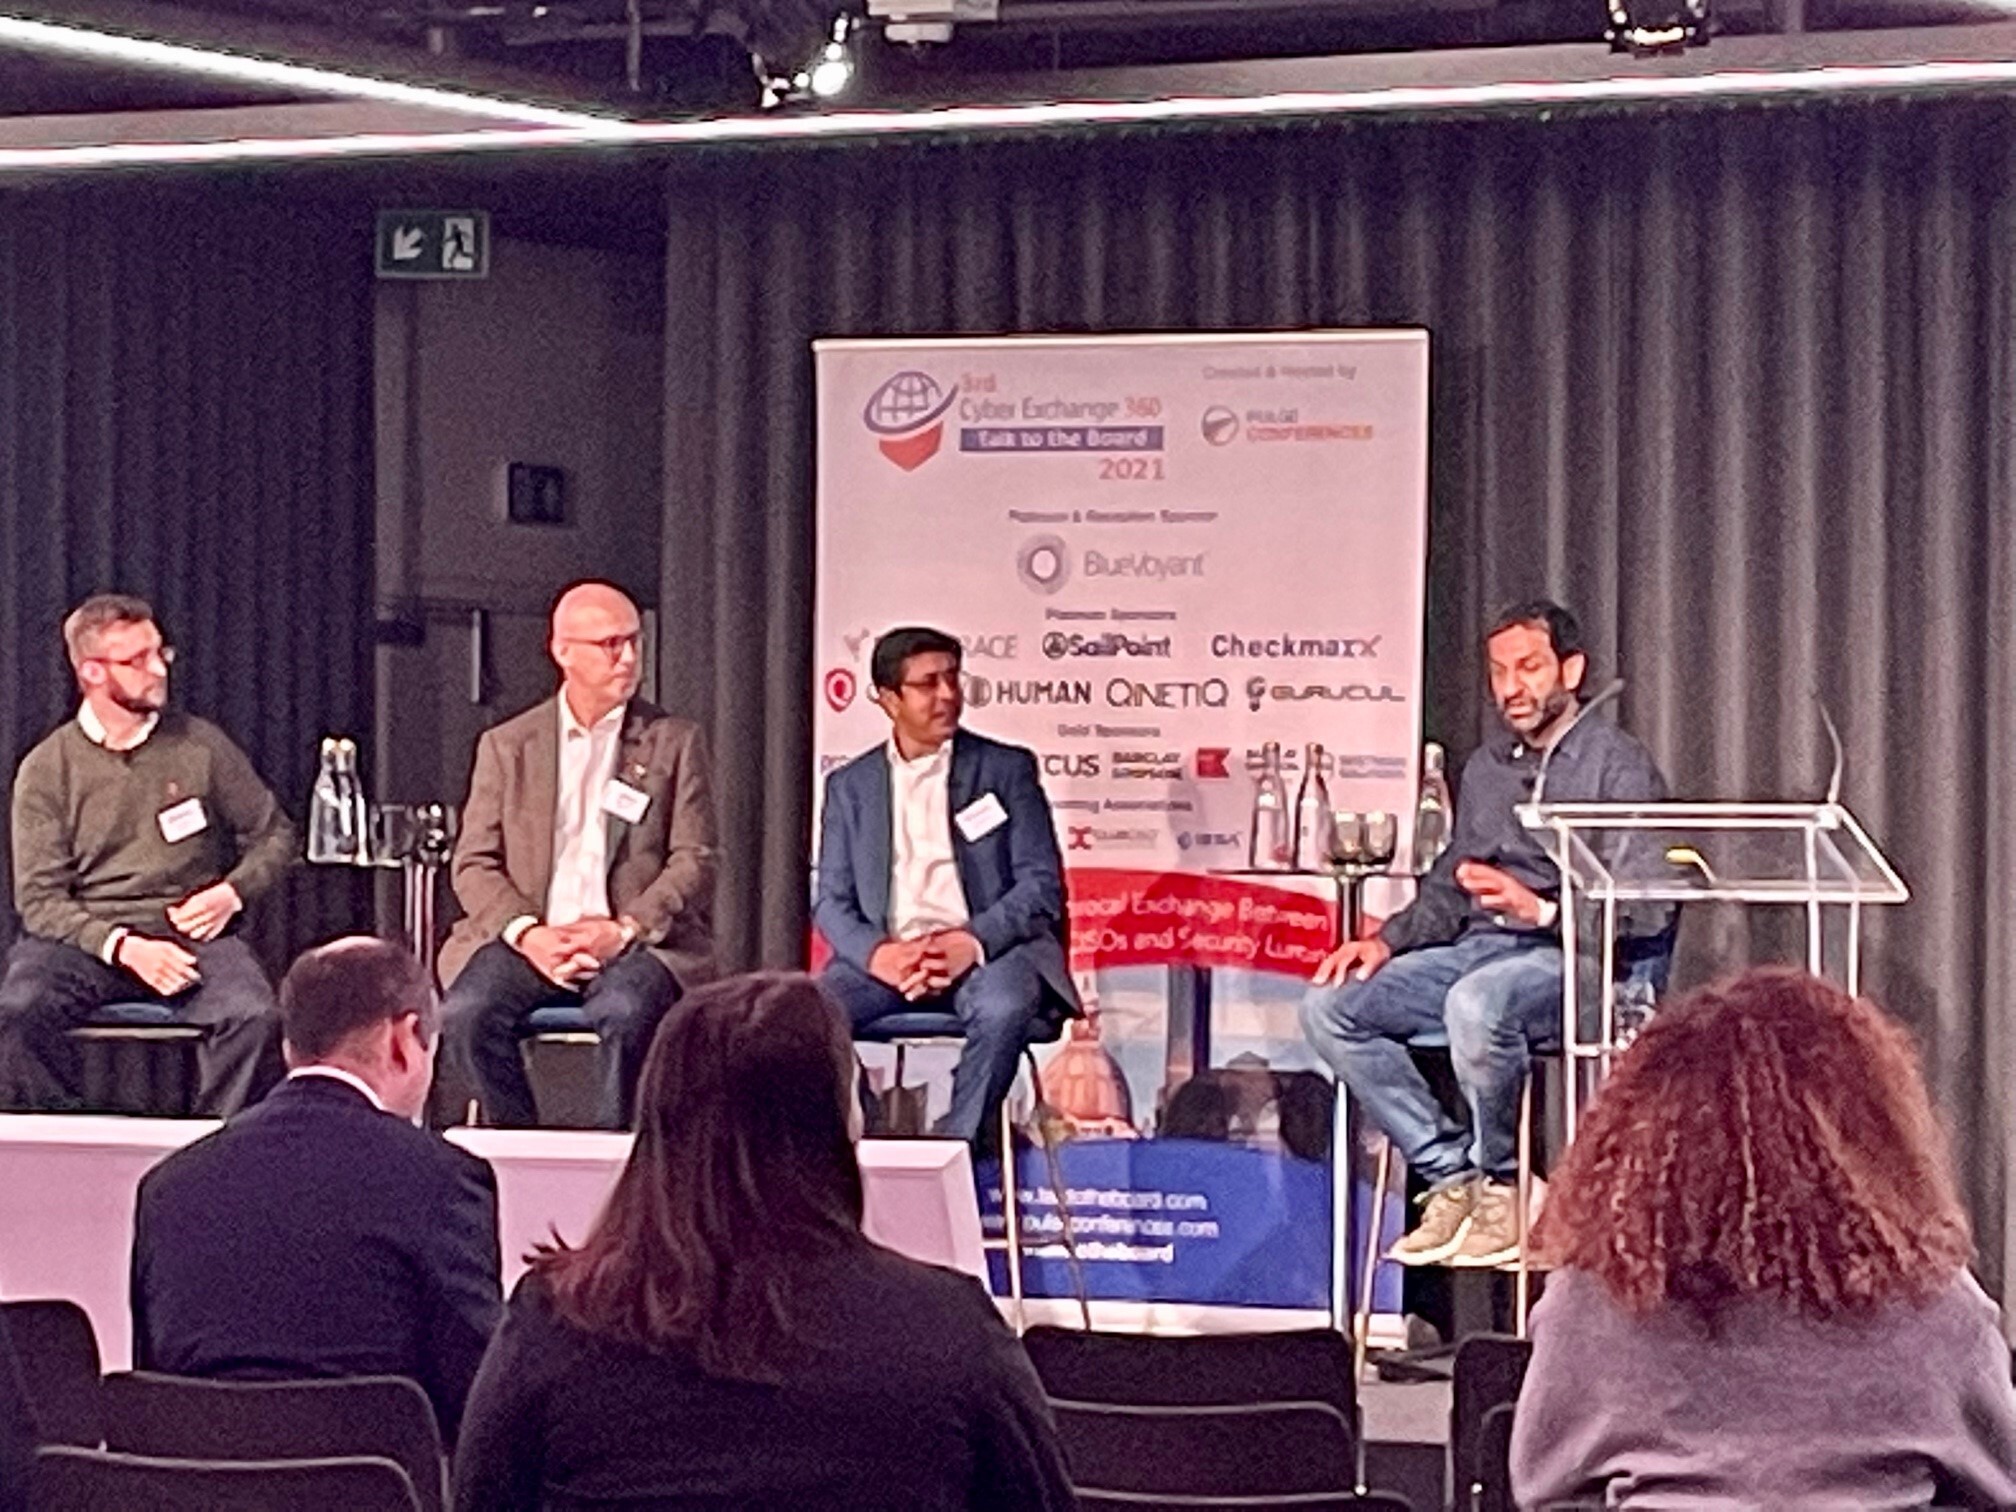
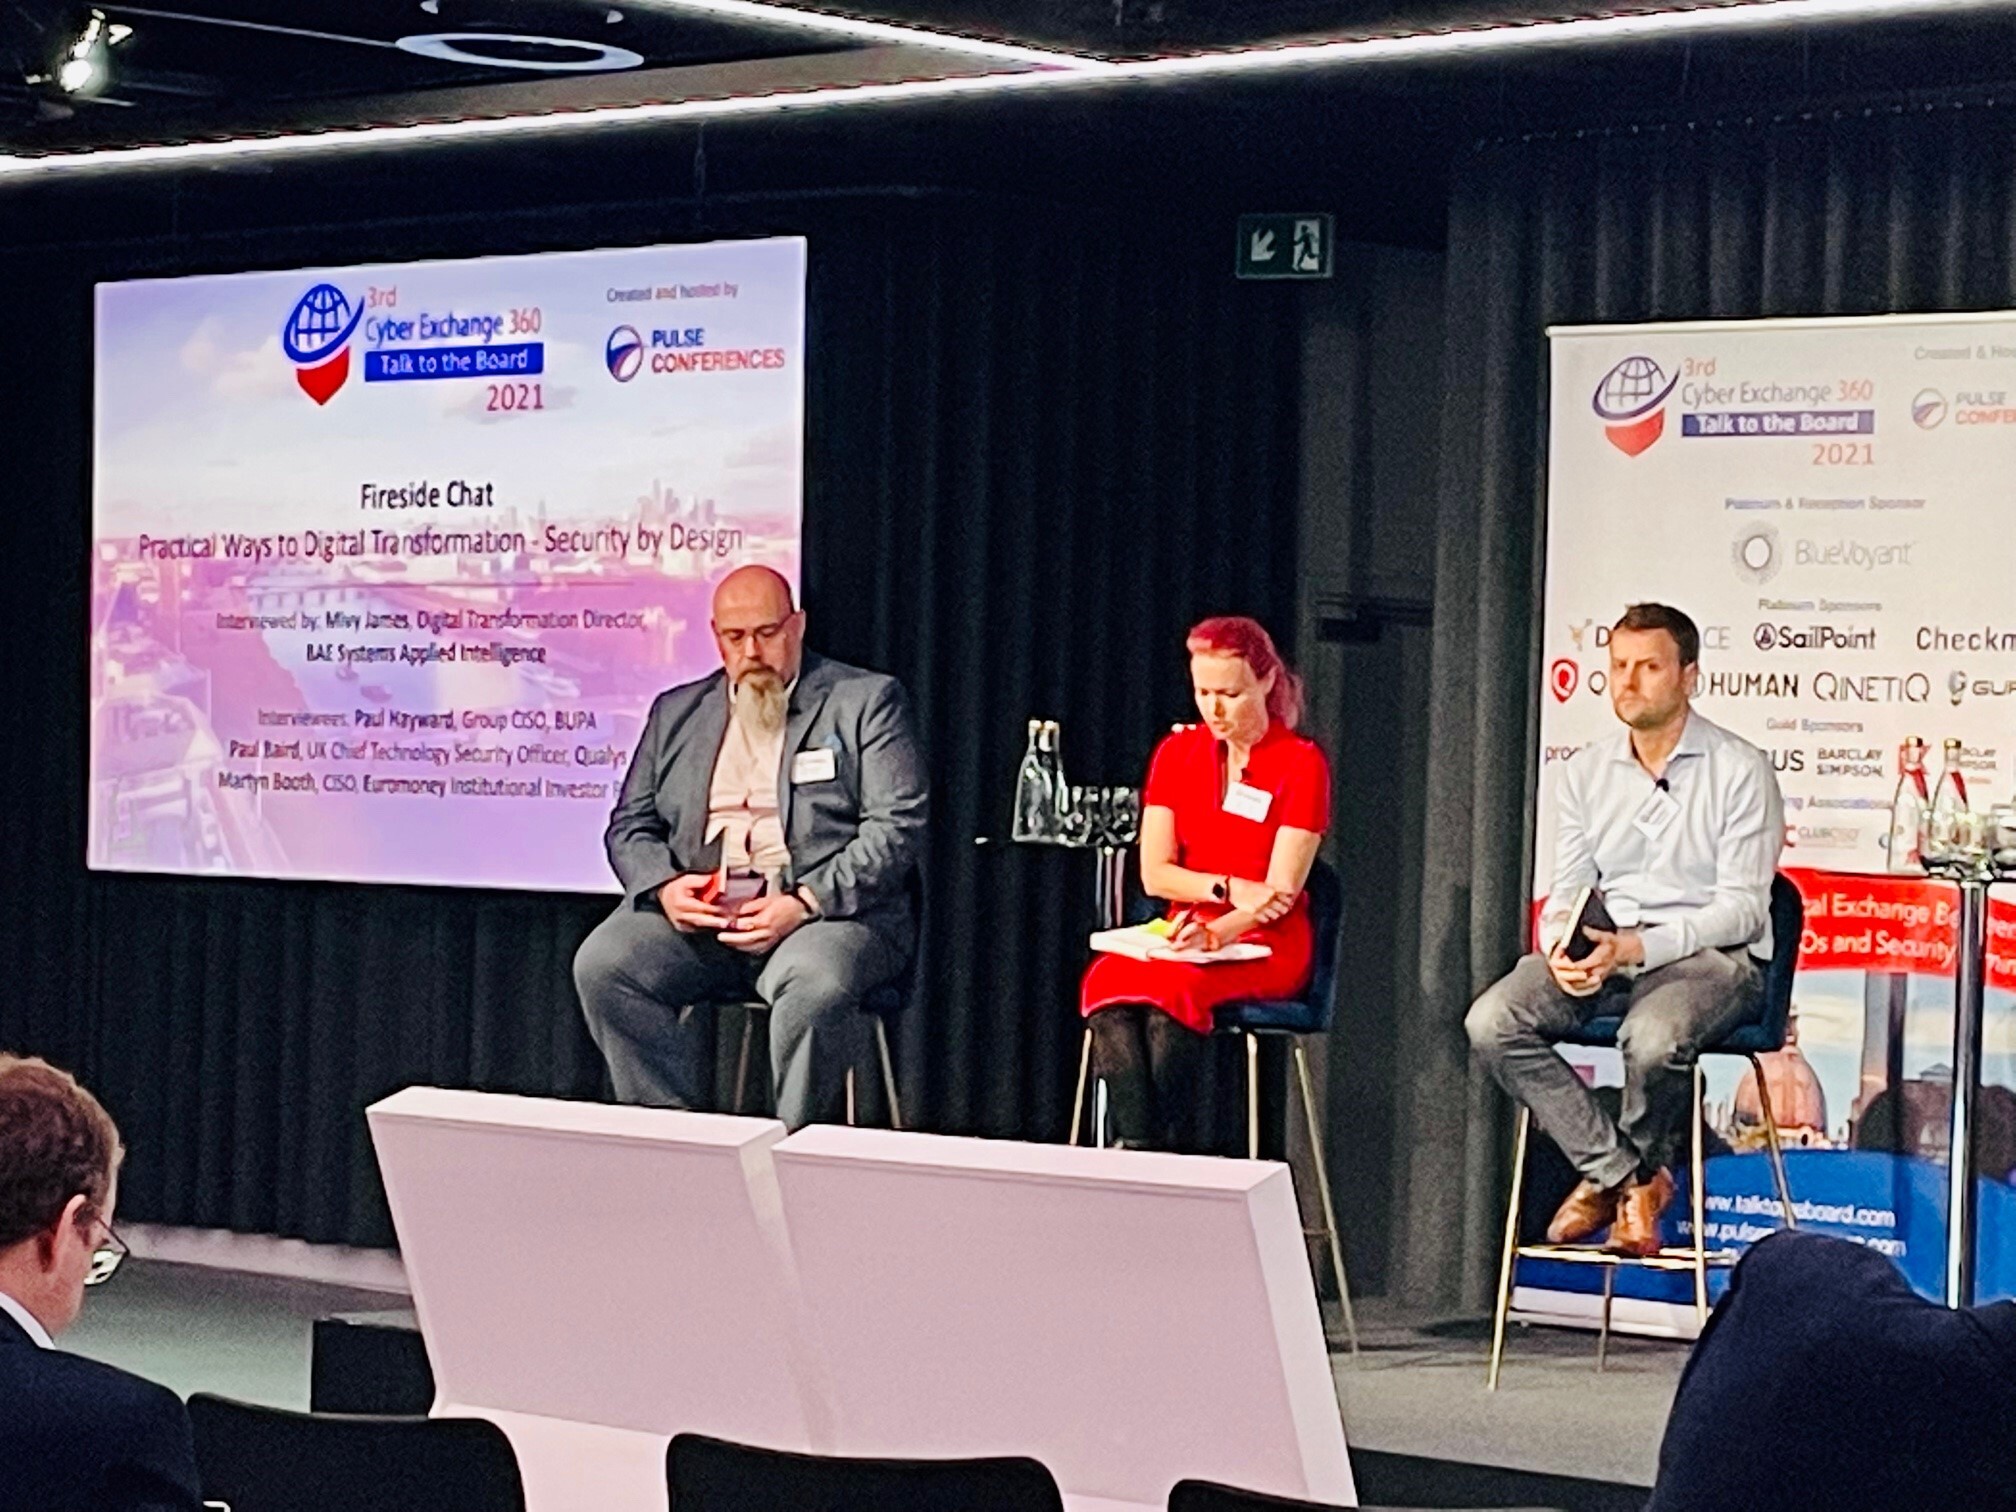
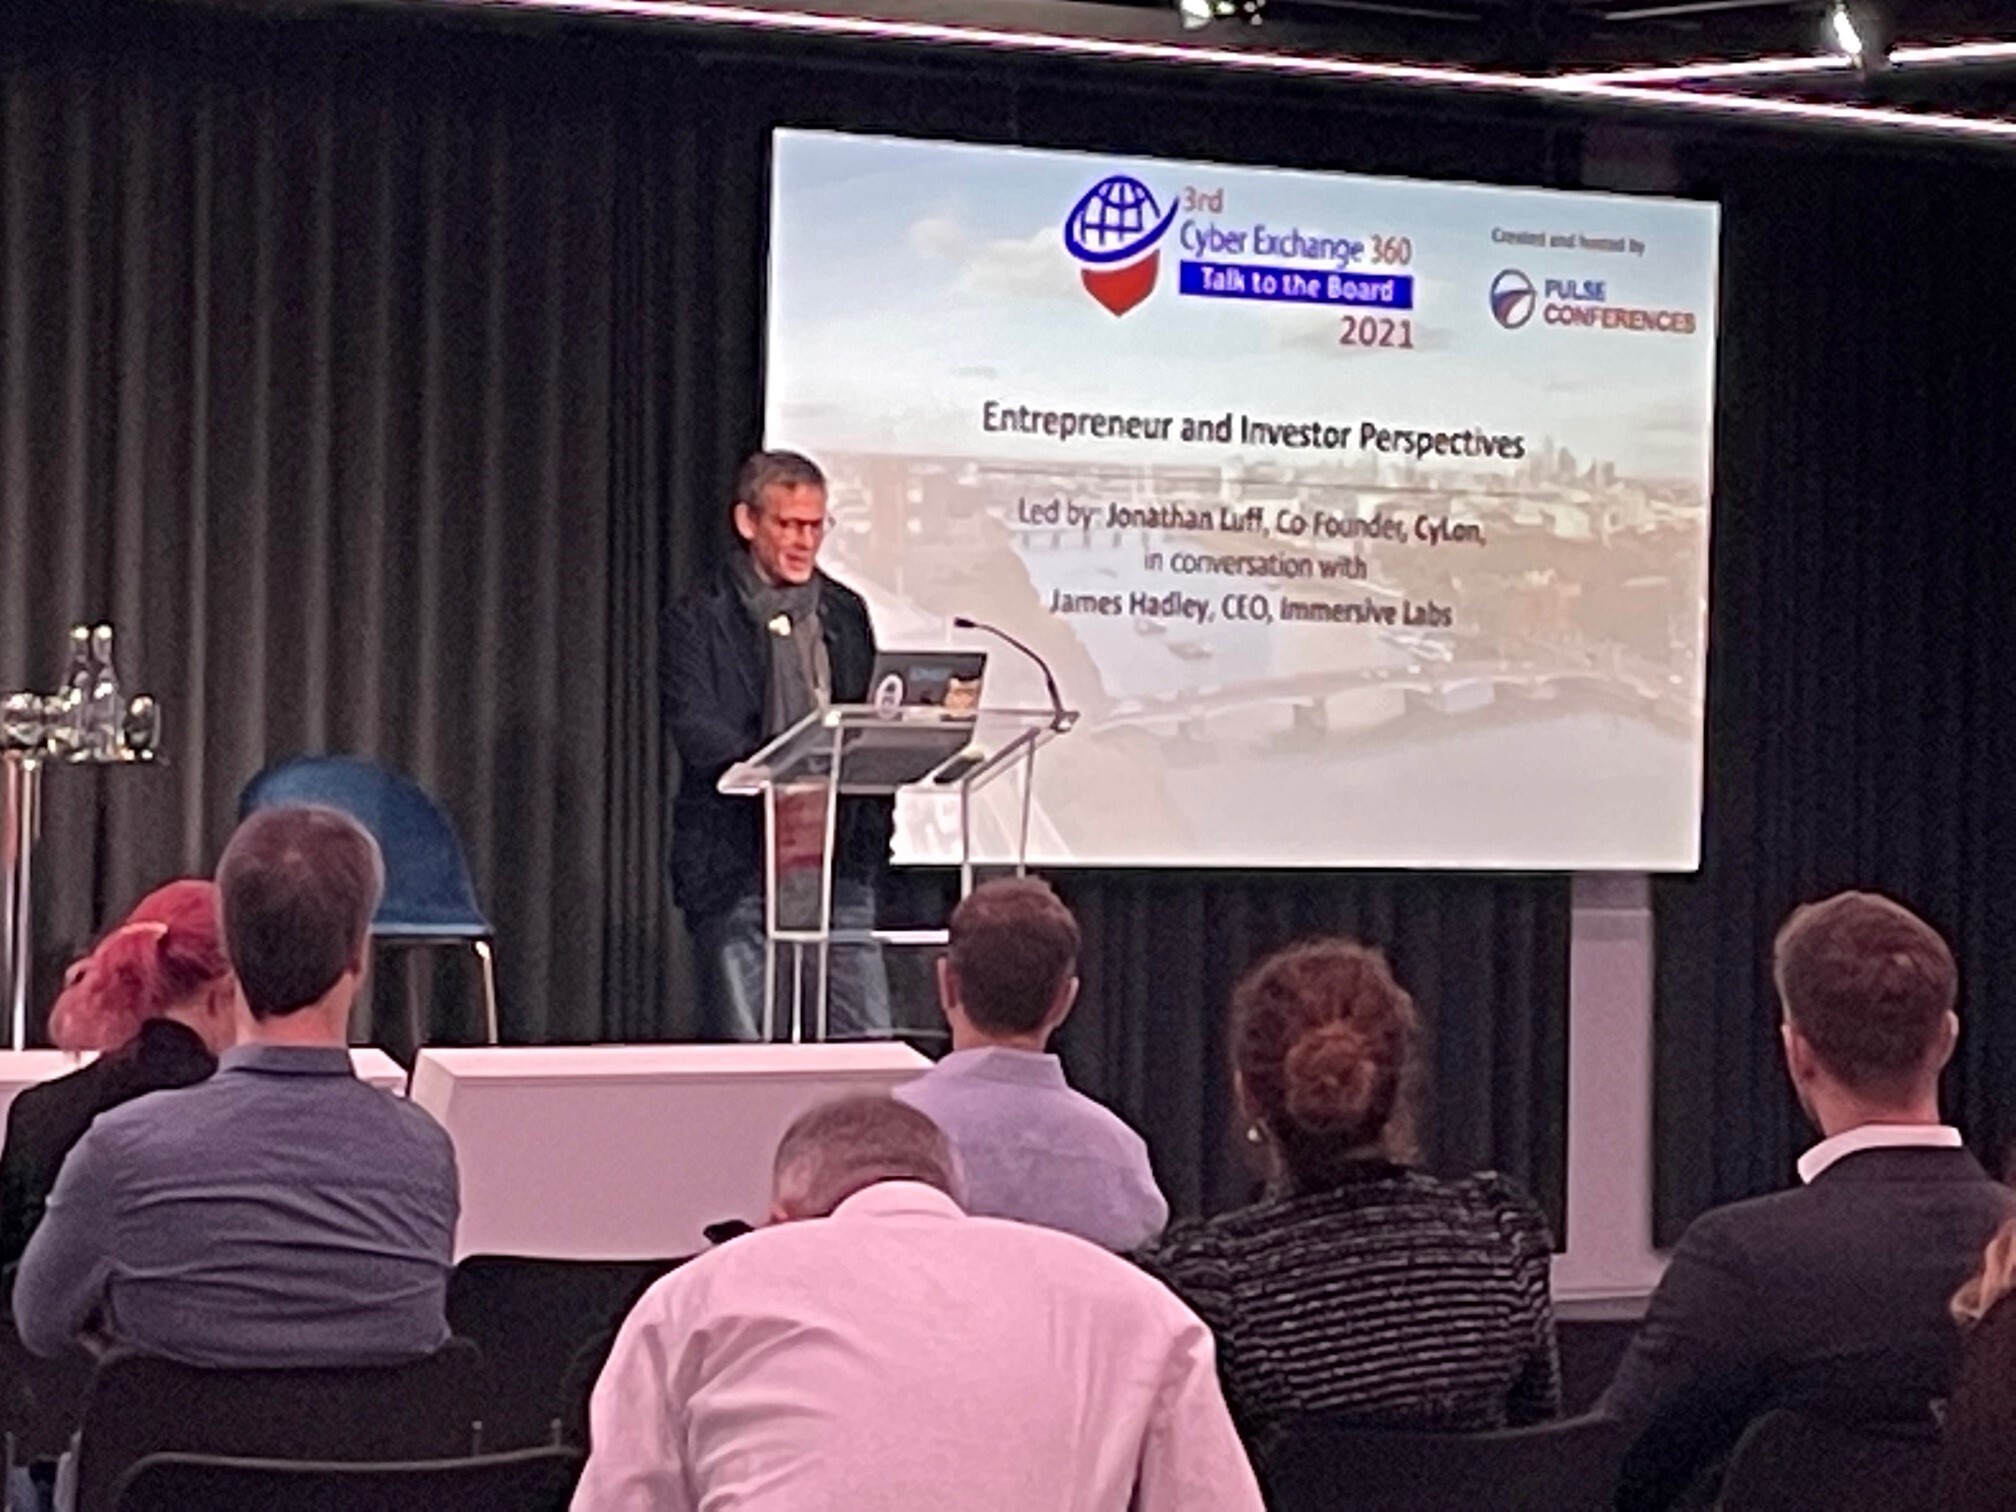
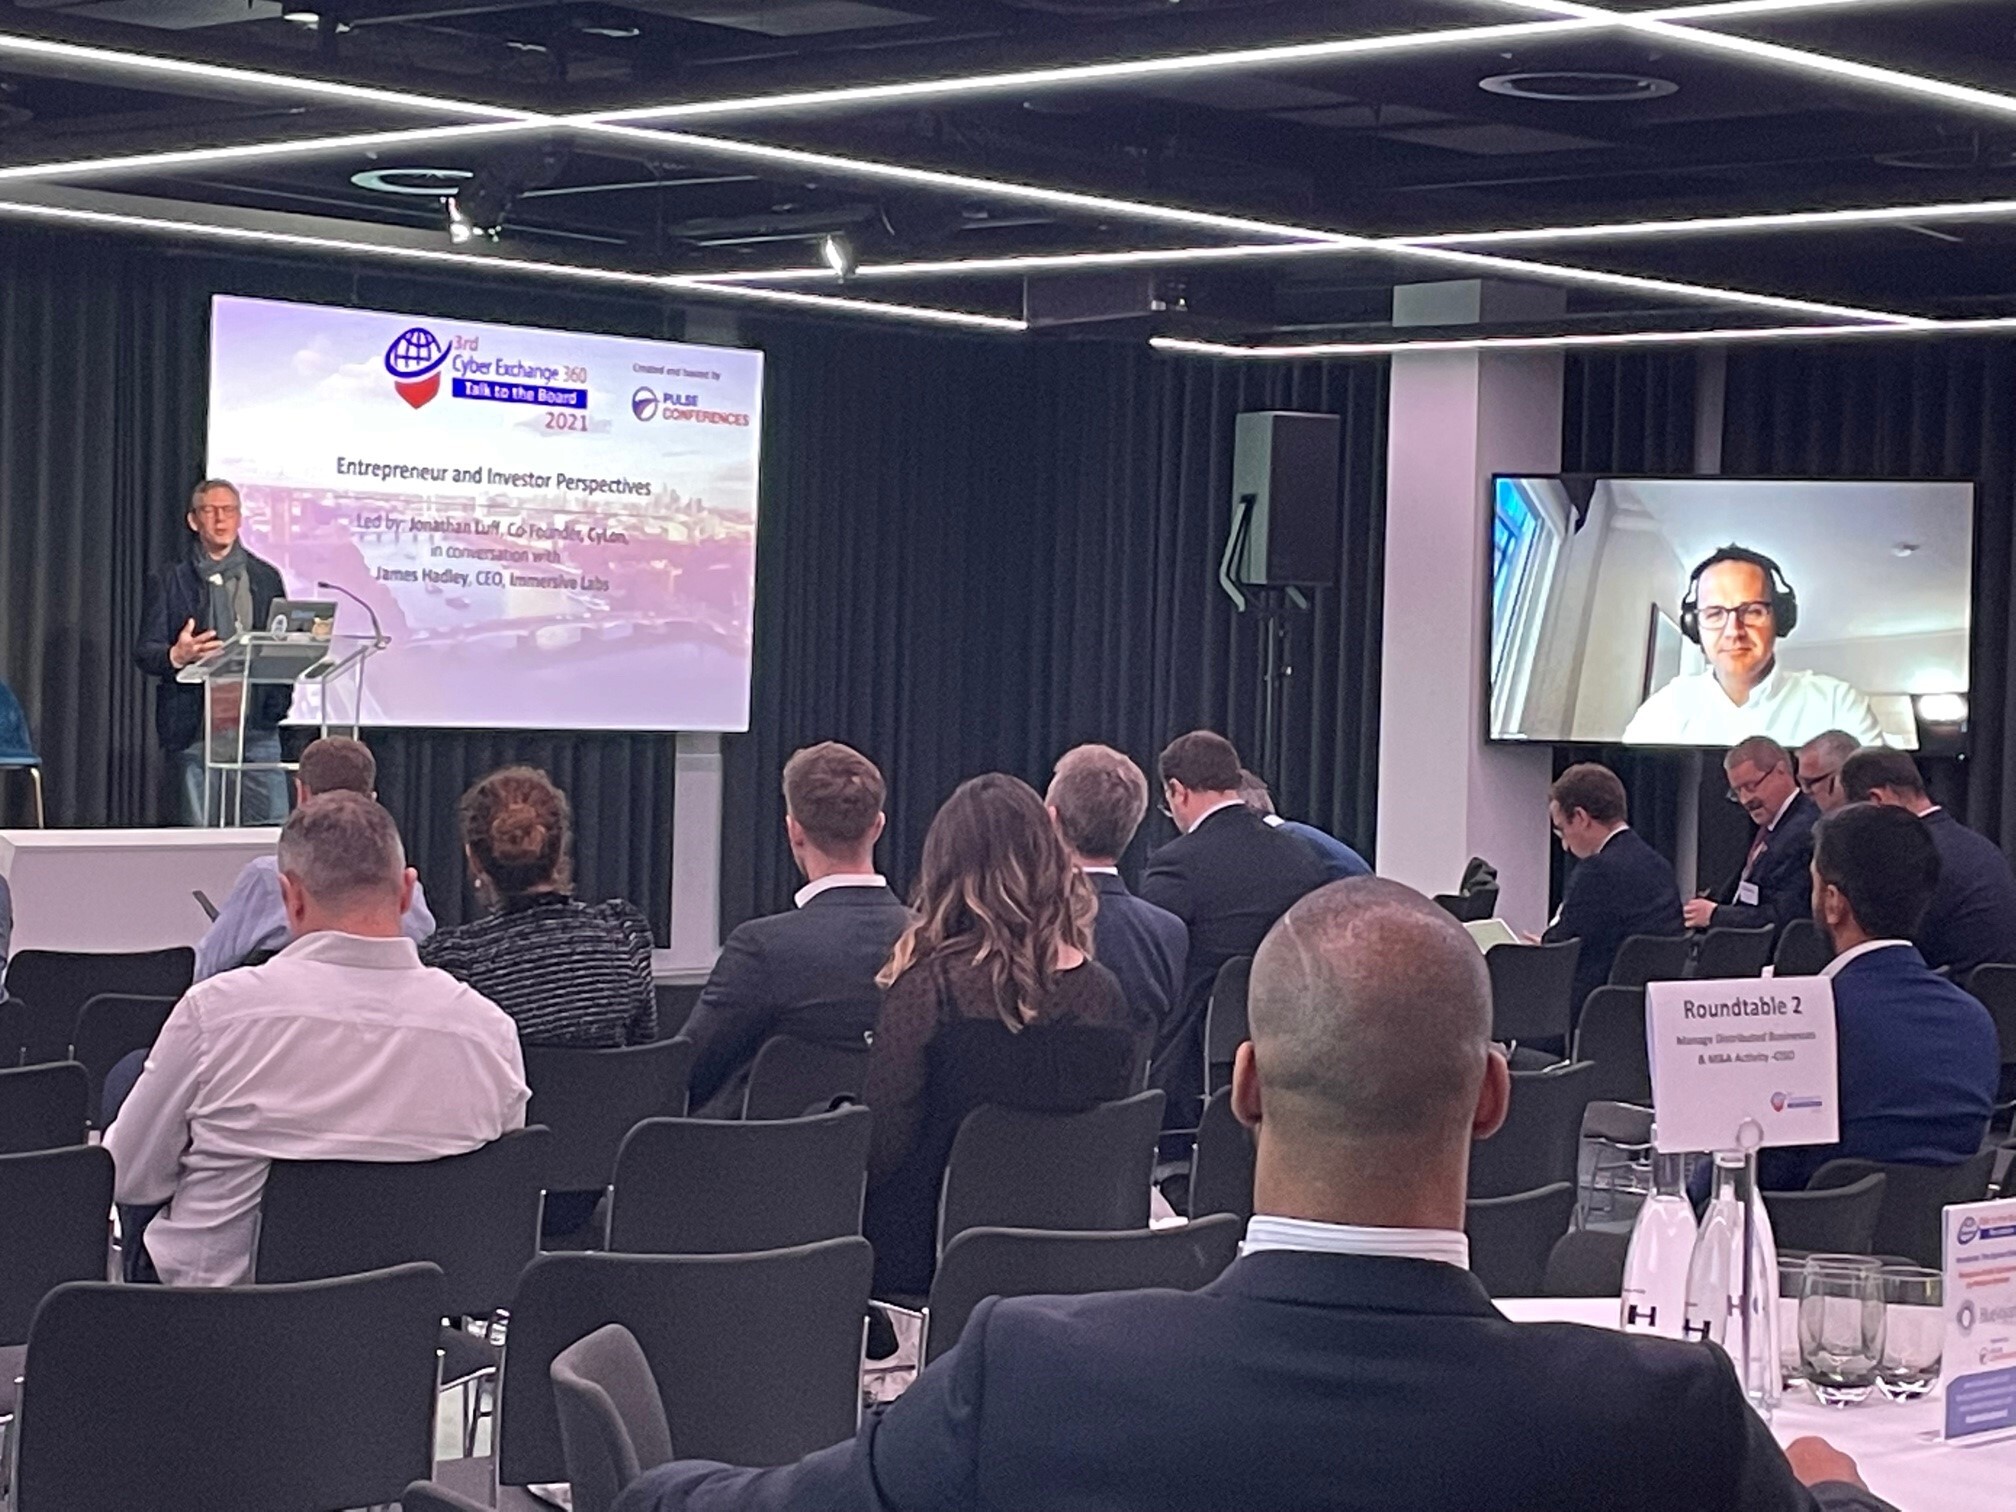
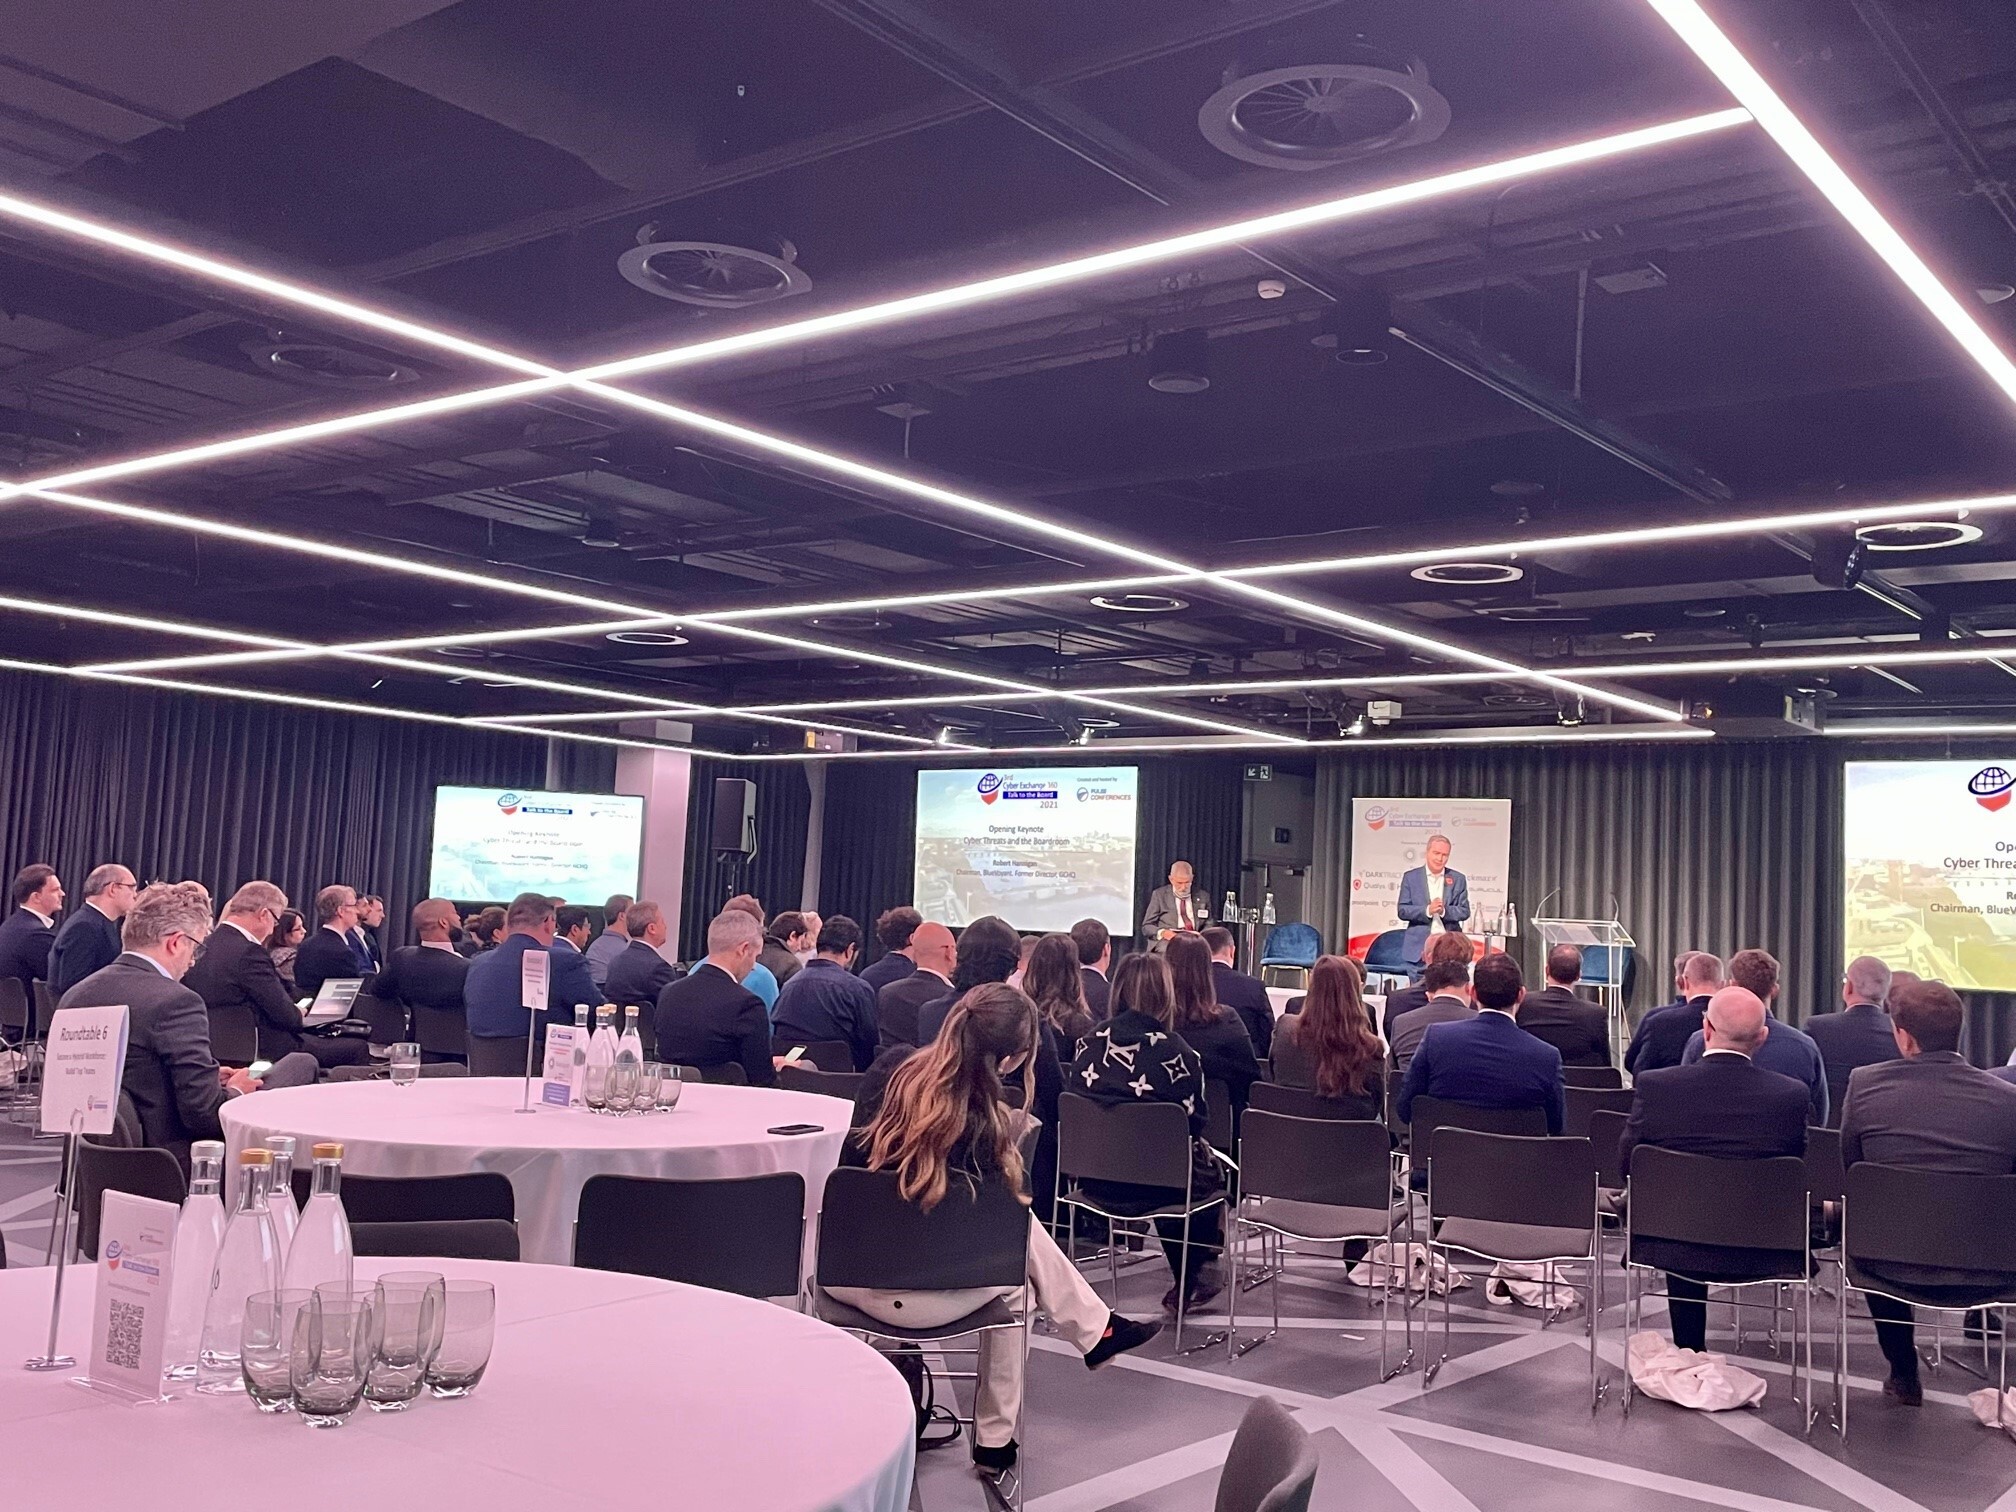
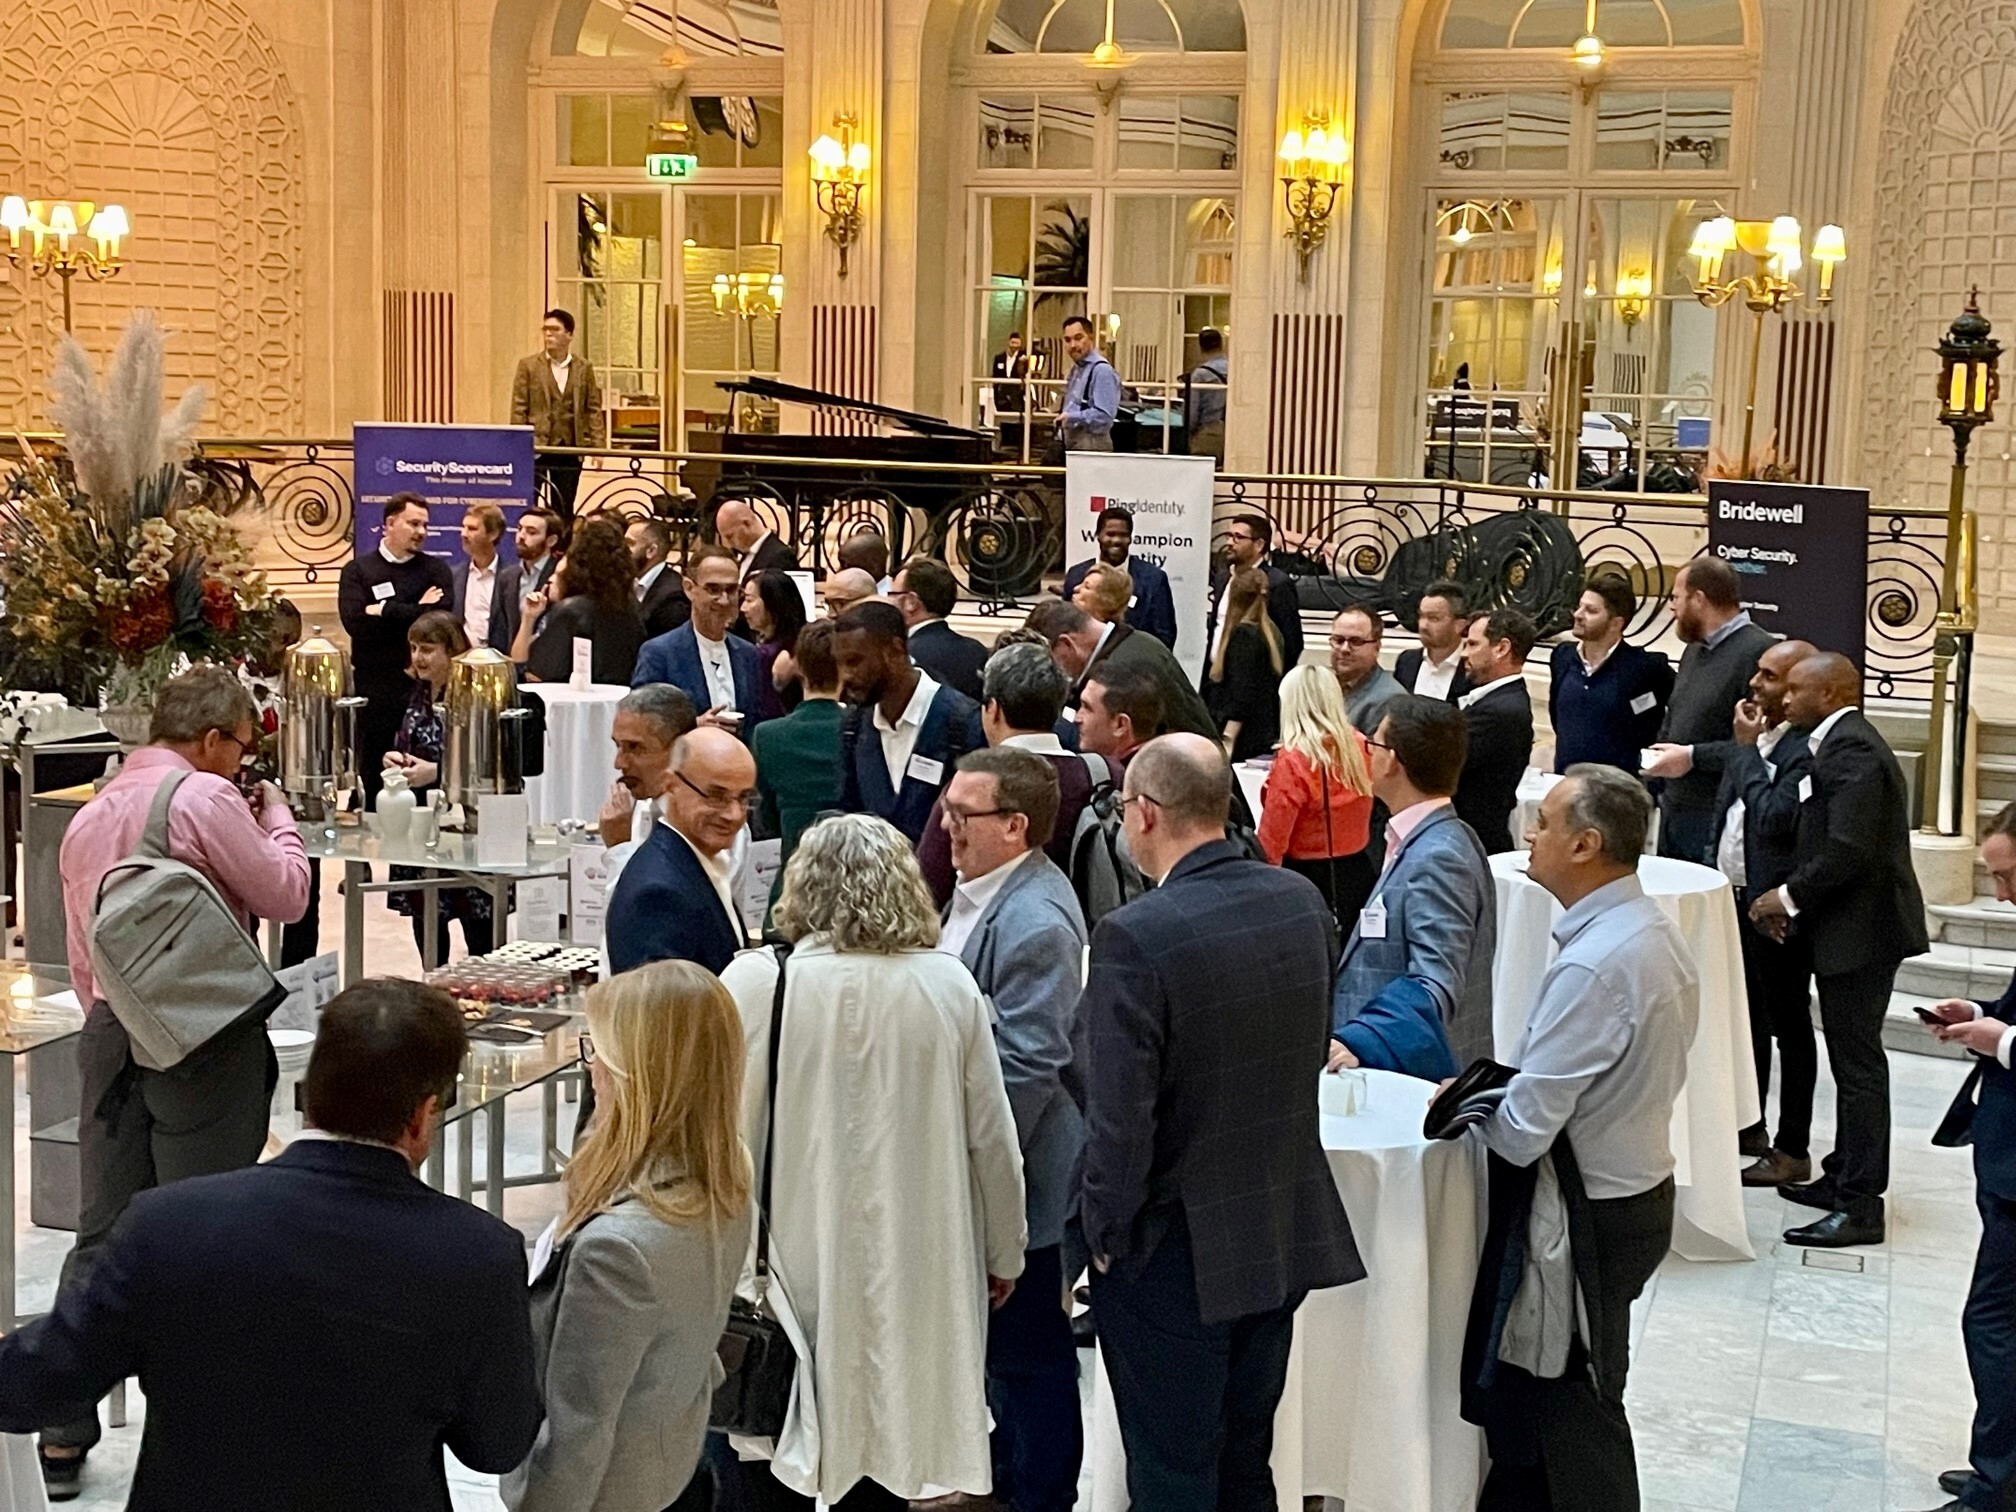
View images from the recent 2021 Cyber Exchange 360: Talk to the Board Conference!
Sponsors 2022 - to date
Platinum - Networking Reception
Platinum
Gold
Silver
Supporting Association
Highlights Video- 4th Cyber exchange 360: Talk to the Board
With thanks to our sponsors
360 Series Sponsors
Sponsorship opportunities
Who attends
By Designation
Participants will include CISOs and CSOs in addition to:
- Chairperson
- CEO
- Non-Executive Directors, Board Member, Audit & Risk Committee Member
- CFO, CRO, GC, COO, CTO, CIO, CMO, HR
- Chief Information Security Officer
- Director of Cybersecurity / Head of Cyber Threat Intelligence
- Head of Governance
- Head of Innovation
- Director of Digital Risk
- Chief Data Officer
- Chief Privacy Officer
- Heads of Corporate Security/Resilience
By Sector
All private and public sectors are welcome to attend.
Programme – 4th Cyber Exchange 360: Talk to the Board, 1 November 2022
Download 2022 AgendaAgenda at a Glance
Morning – Cyber Exchange 360 (08:30-13:30)
CISOs participate in immersive case studies, fireside chats, keynotes. Benchmark strategies and be inspired!
Lunch – Buffet (13:30-14:30)
Network with peers over a delicious buffet lunch in the Palm Court.
Afternoon – Talk to the Board (14:30-17:00)
Reciprocal exchange: CISOs are invited to ‘talk to the board’ and ask the questions they would ideally like to ask their own Board of directors – and without any consequences!
Evening Cocktail Reception (17:00-20:00) – Palm Court, The Waldorf. Kindly Sponsored by: RiskRecon, A Mastercard Company
Continue the networking directly outside the conference room in the wonderful Palm Court in the iconic Waldorf. Built in the 1800s, the hotel blends Edwardian grandeur with modern comfort, and it is said that the directors of the 1997 film Titanic took inspiration from the Palm Court space. Cocktails and canapés will be served while guests enjoy a Gatsby-style, modern swing band who will take songs from the last four decades and put their own swinging spin and vintage stylings to create an incredible entertainment experience!
Download the invitation – no need to register separately, this is part of the conference experience!
Evening CISO 360 Dinner Roundtable (18:30-21:00) – One Aldwych, Private Dining. Kindly sponsored by: Qualys
Numbers are strictly limited to 15 CISOs only, this discussion will focus on ‘What does good risk mitigation look like in today’s heightened threat environment?’
Read more about the dinner and register here separately – subject to availability
Topics and speakers for the 4th Cyber Exchange 360: Talk to the Board, 1 November 2022 are in continuous development. Our programmes are organic to ensure that we bring you the very latest perspectives! If you would be interested in getting involved as a Speaker, please let us know! Email: teampulse@pulseconferences.com. We would also very much value your input into companies, topics or specific persons you may like to see on our agendas, which are your agendas.
Speakers for the 4th Cyber Exchange 360: Talk to the Board 2022
Chaired by
Meet the Talk to the Board Panel of Board Directors 2022
Meet the Speaker Panel 2022 including (to date)
Marcus Alldrick
Former CISO, Lloyd’s of London. Currently Digital Risk Management, Security and Compliance Advisor
Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer.
In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.
Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc.
Lady Olga Maitland
President, Defence and Security Forum and Chairman of the Advisory Board, Audere International
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Josephine Fairley
Co-Founder, Green and Black's
Jo Fairley is a serial entrepreneur best known for creating the Green & Black’s brand in 1991, which she ran with her husband and which was bought by Cadbury’s in 2005. She is a award-winning author & journalist, Jo is author of a series bestselling books on health and beauty and is a regular columnist, feature writer and journalist for the world’s leading magazines. The first-ever product to carry the UK Fairtrade Mark, for the past nine years, Green & Black’s has the ‘coolest food brand’ in Britain (according to the Cool Brands Survey), and now a $100 million a year brand. Still a working journalist, Jo has written for a wide range of newspapers and magazines from The Times to The Mail on Sunday’s YOU Magazine, and as a ‘Wonder Woman’ business guru for Telegraph Woman Online. Jo is in demand as a brand consultant, alongside her own ventures which have included an organic bakery and natural food store and a nine-room wellbeing centre in her home town of Hastings. Most recently, she created and launched The Perfume Society, which works with the fragrance industry seeking to improve individuals’ sense of smell in a pleasurable and engaging way
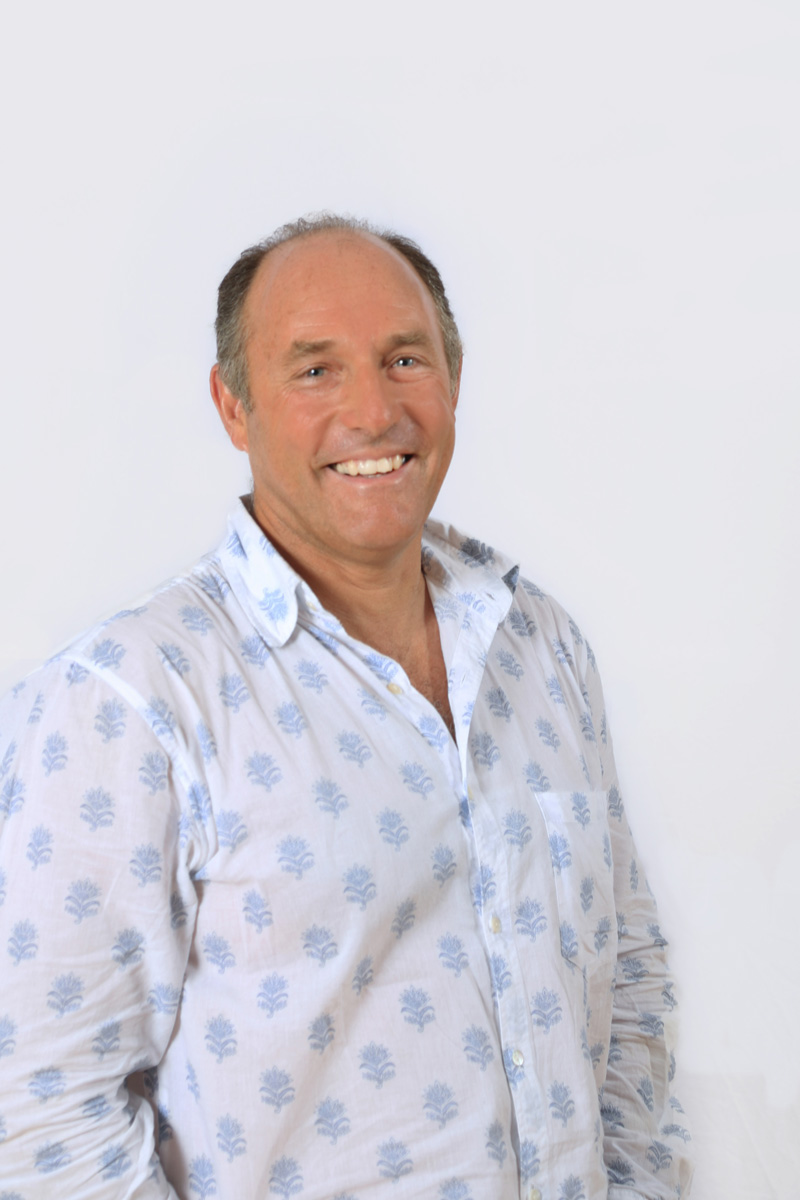
Geoff McDonald
Former Global Vice President HR (Marketing, Communications and Sustainability), Unilever
Geoff’s background in teaching, HR, marketing, communications and sustainability is considerable. During his 25 years with Unilever (a global corporation with a turnover of £50 billion, 170,000 employees in 90 countries around the world), his experience has been truly global working across Africa, the Middle-East and Turkey, Australasia and Asia, Europe and the Americas. Geoff’s HR experience has spanned leadership and talent development, organisation change, capability development with particular reference to marketing, and business transformation with purpose at its core. Early in his career he was responsible for graduate recruitment and development, talent, acquisitions and development across Unilever’s emerging markets. Under his leadership he developed Unilever’s global talent and leadership centre of expertise. More recently he devoted his time, energy and effort to leading ground-breaking work where the HR function has played a central role in transforming Unilever’s business model with purpose at its core. Today McDonald is very much sought after as a speaker, inspiring and provoking organisations to put purpose and well-being at the centre of everything they do. His experience in Unilever, under the pupilage of Paul Polman, allows him to provide very practical insights and to speak on how to go about truly embedding PURPOSE and address the taboo associated with wellbeing (particularly mental health) within a large global multinational organisation. With this experience comes some real learning on what may or may not work. He recently had the opportunity to engage with Pope Francis on how we create a more sustainable and inclusive economy through his work with the Global Foundation. McDonald is devoting a significant amount of time to consulting to organisations, helping them define and embed Purpose as a driver of growth and profitability. He was recently appointed as Strategic Advisor to the global PR and communications firm Burson-Marsteller in the area of Corporate Purpose and Organisation Change. He too consults on how to address the stigma linked to depression and anxiety in the workplace, with a particular emphasis on raising awareness of these issues and providing some practical strategies as to how one might go about addressing this growing modern illness. He is a very active campaigner for breaking the stigma associated with Mental Health in the Corporate world and has participated in a number of BBC programmes and campaigns regarding this subject, as well as writing and producing articles for the Huffington Post, the Financial Times and HR related journals. He previously convened a meeting at No 10 Downing Street with David Cameron and CEOs from Footsie 100 Companies to address their role and agree actions to break stigma in the corporate world. He too provided some support to the Royal Foundation (Princes William, Harry and Kate) in their mental health campaign. McDonald is a co-founder of a network called ‘Minds@Work’, which has grown from 14 members to over 1000 in two years. Its purpose being to inspire and equip individuals to break the stigma of mental ill health in the organisations they work in. He has also recently been appointed as an Advisor to the Global Mental Health Campaign and has been asked to join the Prince’s Trust Youth Opportunity Taskforce with the purpose of creating change that will unlock the potential in the UK’s youth.
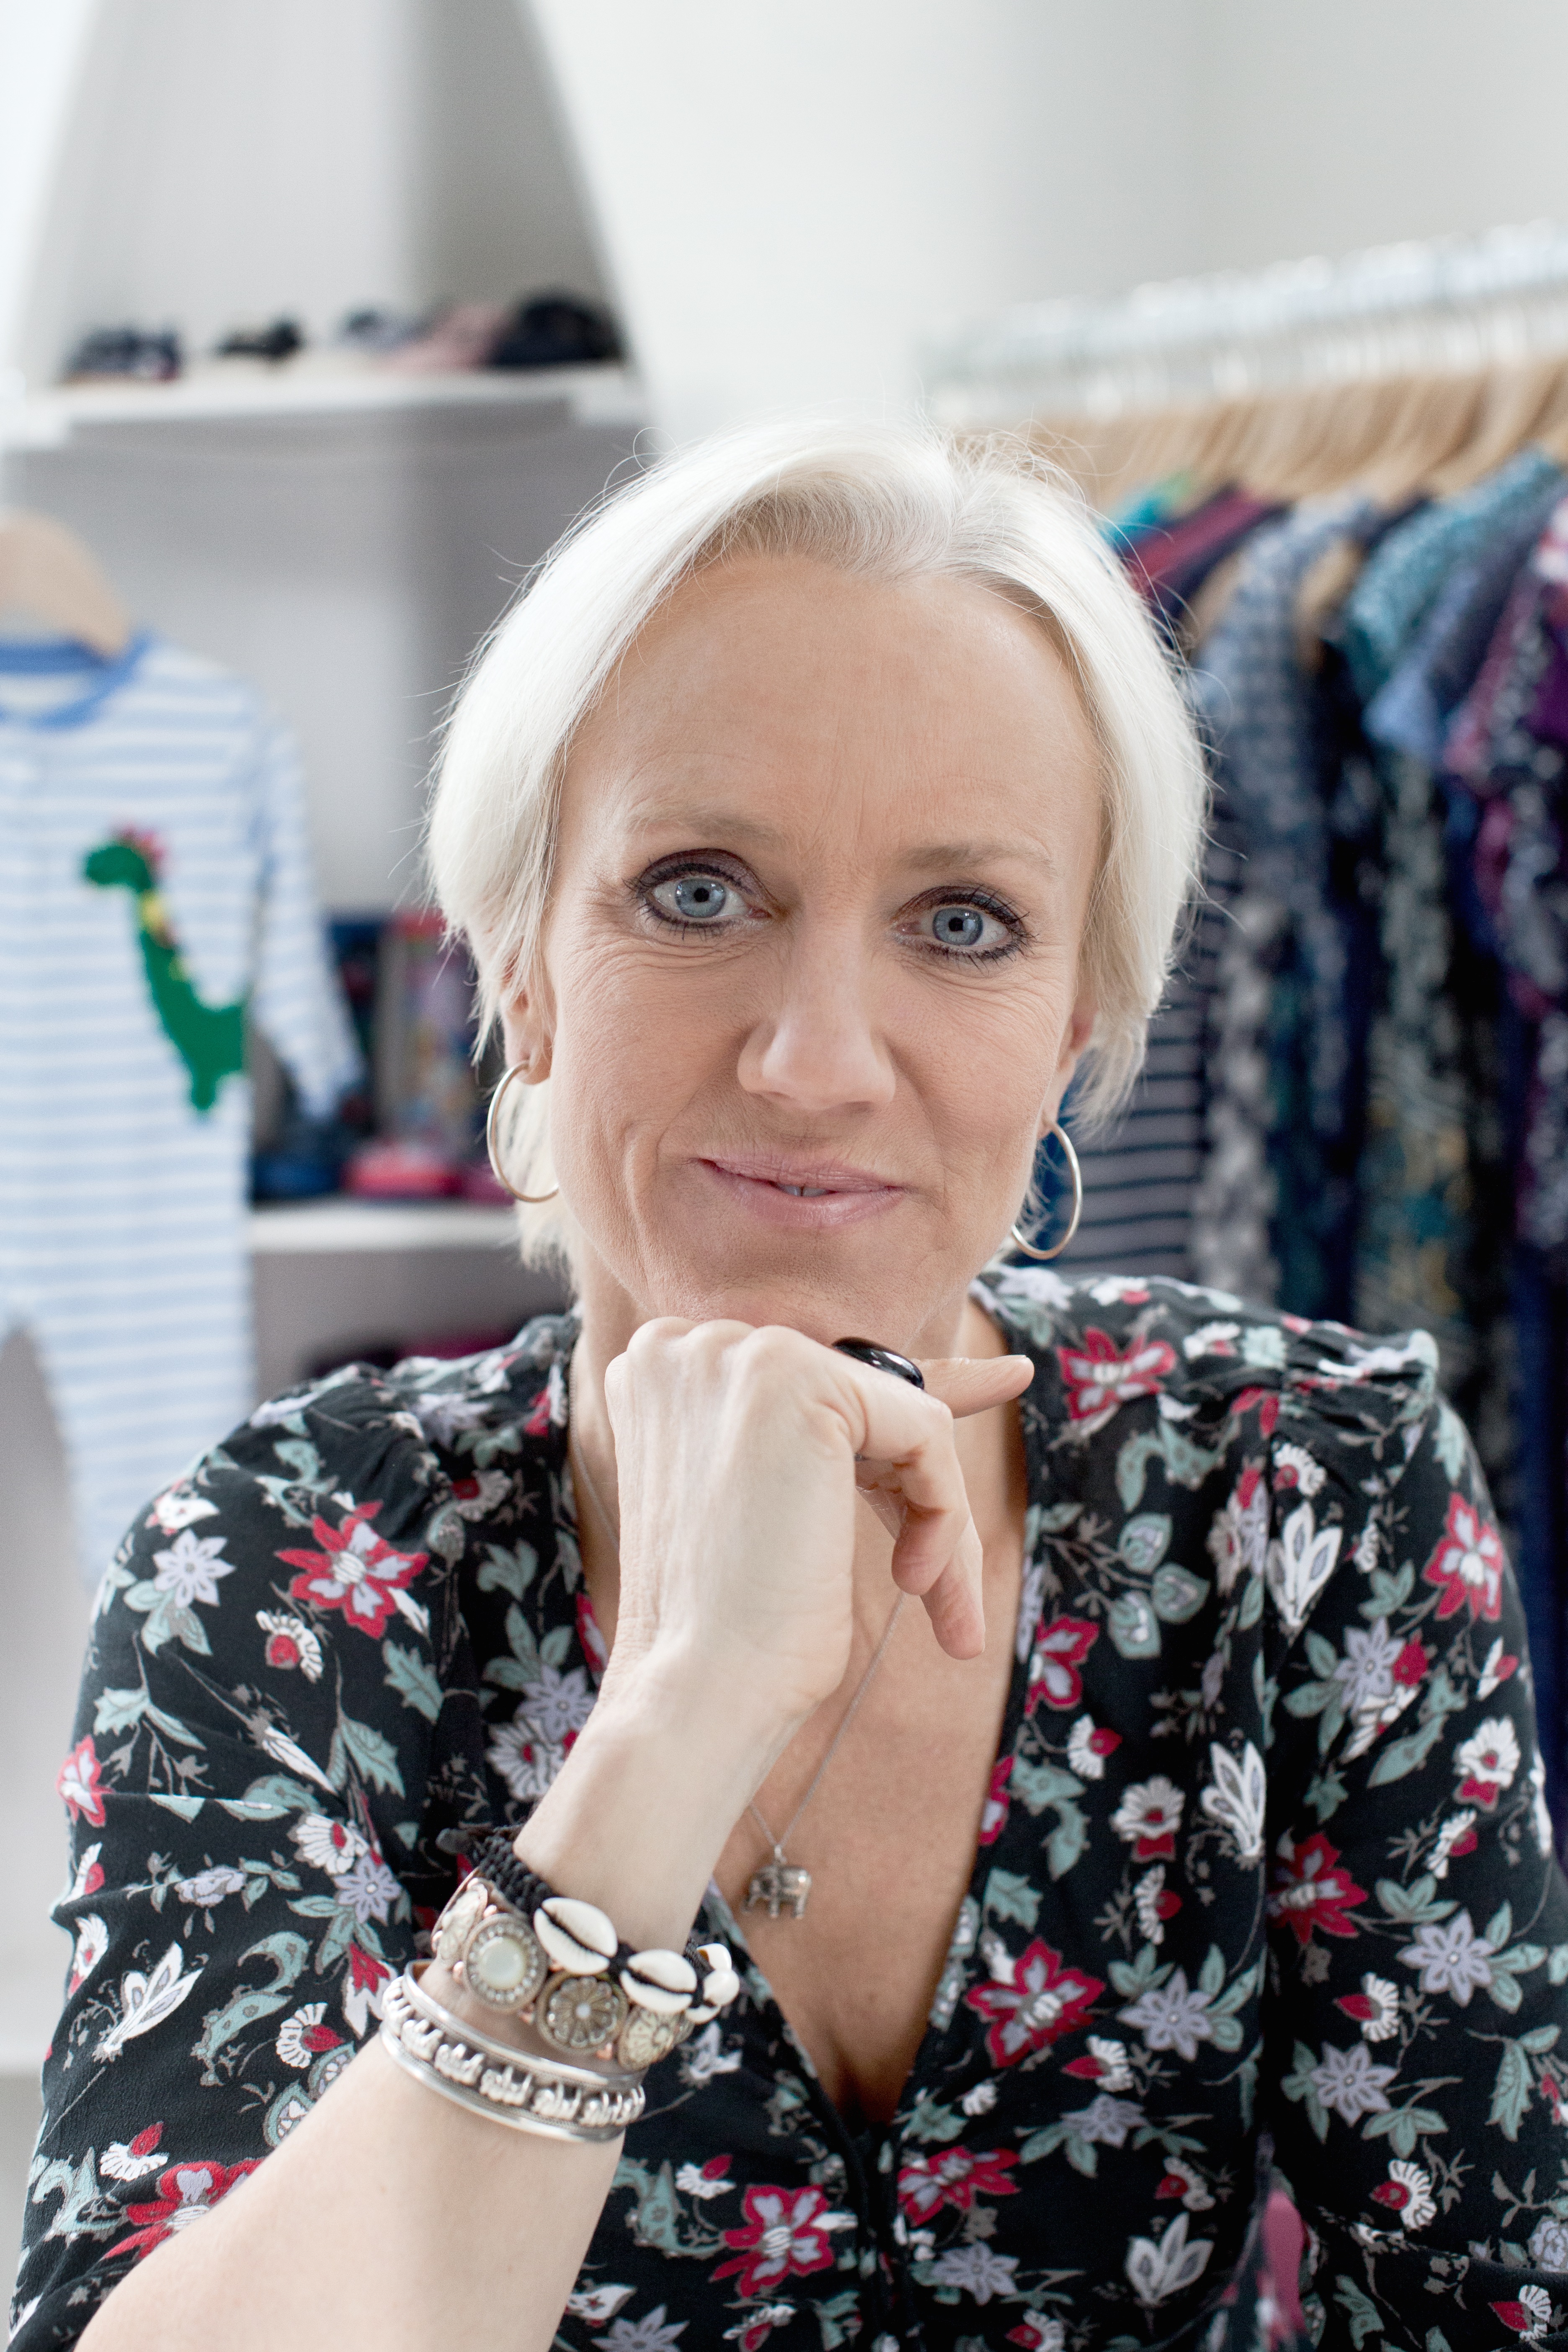
Laura Tenison MBE
Founder & Director, Wonderful Escapes. Former Founder & CEO, JoJo Maman Bébé
Until Spring 2022, Laura Tenison was the Founder and CEO of the UK’s leading specialist Parent and Baby Brand, JoJo Maman Bébé. The business was digital first, supported by a large portfolio of localised stores across the UK and ROI with growing international trade sales into the US, EU and Middle East. Laura instigated a total sale of the business to NEXT Plc and Davidson Kempner PE, leaving the board in place to run the company as a standalone brand in order to maintain its exceptional market position and value.
Laura grew JoJo organically from start-up in 1993 to become the UK and Ireland’s leading independent brand in the sector with a team of 1,000. Pre the Covid-19 pandemic, JoJo also benefitted from a wholly owned US subsidiary, with stores, e-commerce, trade sales and a DC.
Since launch, the business delivered exceptional product innovation and fashion design, bringing to market hundreds of new styles and nursery items, which have since become family essentials.
Under Laura’s leadership JoJo was a trailblazer in better business practices, including; leading the way for inclusivity and diversity in modelling, using recycled materials, employee profit share schemes, employing those serving prison sentences, offering job opportunities to past asylum seekers, managing a charity based in Africa, counting numerous Down’s Syndrome employees among the team, up-cycling shop-fit and even being a dog friendly work place. This ethos of putting people and the planet above profit resulted in JoJo achieving Certified B Corporation status.
Her new passion is to bring business colleagues together to engage in collaborative thinking and creativity, delivering the antithesis of digital working. The luxury accommodation and extraordinary venue allows dispersed teams to congregate, share experiences, good locally sourced food & drink and form loyal bonds with each other and their employers. www.wonderfulescapes.co.uk
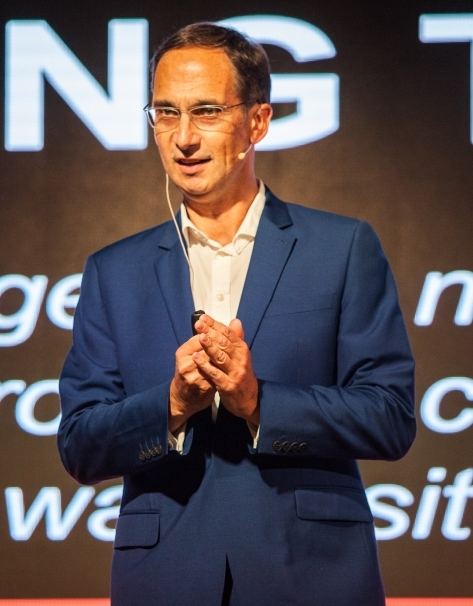
Daniel Bobroff Founder and CEO
Coded Future Formerly Co-Founder ASOS Ventures
One of the world’s leading retail technology speakers, Daniel Bobroff believes in the power of everyone to be a game changer. Passionate about the digitalization of retail and the changing customer experience, his unusual journey has led to a unique perspective that informs many of the world’s best-known retailers, agencies and brands. He is motivational and visionary, but always provides a roadmap. Daniel is the founder of Coded Futures, a creative technology advisory firm focused on the future of retail, and formerly the co-founder and Investment Director of ASOS Ventures, the online fashion company’s venture capital division. In over two decades as an innovator, entrepreneur, mentor and investor, he has pioneered advertising in video games, developed chart topping video games that sold in their millions, and is, today, a leading thought leader and keynote speaker in the world of retail and fashion technology. Daniel is acknowledged as the pioneer of in-game advertising – “selling Mario to the admen” – starting an advertising medium that is today an eightbillion-dollar market. He built Microtime, the first – and for over a decade the leading – digital advertising agency for in-game advertising and advergaming. Close contact to the gaming world led Daniel to build and lead Deibus Studios, a video games developer with studios in both the UK and France and which emerged as a leading talent for extreme sports, creating games for PlayStation, Xbox and Nintendo, achieving combined sales in excess of 50 million units. Daniel has founded, invested in and led companies within a range of innovative technologies including virtual reality, visual search, e-commerce and ad-tech. At the world-leading online fashion retailer ASOS, Daniel created the company’s venture capital arm. His mission was to identify and invest in the latest innovations within retail and fashion technology. He built an enviable network of cutting-edge retail tech talent, developing partnerships covering the latest in marketing, production and customer experience. Scouting for the latest innovations across retail’s value chain, Daniel talks about the technology driven future of retail. He evangelizes the need for personal, immediate, and interactive mobile experiences, new filters, the importance of culture and how all retail businesses will become technology businesses. He is a highly sought-after international speaker, recently delivering keynote addresses for the Retail Institute, Salesforce, Google and Facebook.
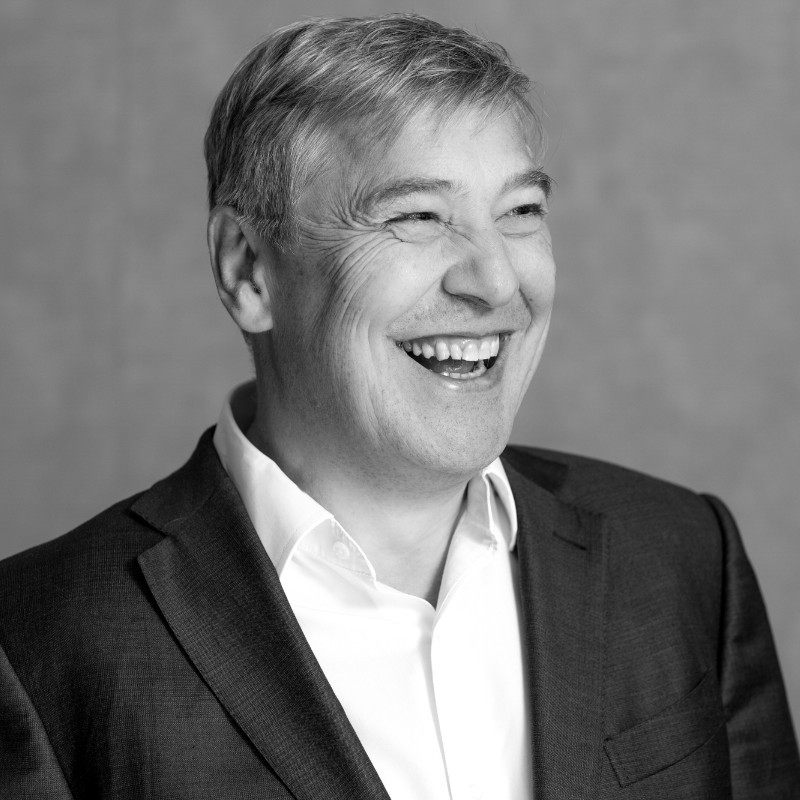
Robin Dargue
Former CIO, WPP. Current, Hallo Healthcare Group
Robin’s focus was to execute the transformation of WPP Groups IT environment to enable the group’s current strategic direction. Robin joined WPP from Alcatel-Lucent, where he held the role of Executive Vice-President for Business and IT Transformation, and was a member of the Alcatel-Lucent Management Committee. Prior to this, Robin was a business leader in both Royal Mail and Diageo, in charge of business and IT-based transformation programmes. At Royal Mail, he oversaw the introduction of a number of new technology-led products and services for customers, while executing the modernisation of the organisation’s technology assets. Robin is now with Hallo Healthcare Group.
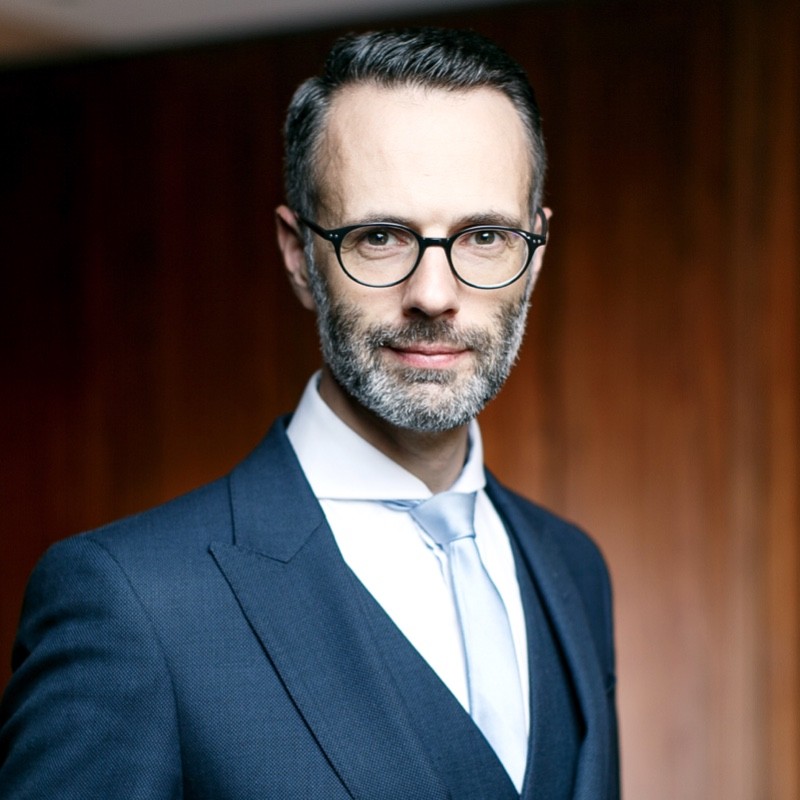
Dimitri Chichlo
Independent Non-Executive Director, Vice-Chairman JSC Ukreximbank (Switzerland/Ukraine)
A French and Swiss citizen, Dimitri Chichlo started his career in Ukraine in 2004, then moved to Switzerland in 2009, working mainly for international financial institutions in the fields of operational risk and cybersecurity. In 2017, he completed an Executive MBA at INSEAD. In 2019, he joined the Supervisory board of Ukreximbank, the third largest and State-owned bank in Ukraine, as vice-chairman and chair of the Operations and Digital Committee. In 2020, he founded his consultancy practice in cybersecurity and digital transformation, AndSecure. Since February 24th, 2022, he is actively involved into providing humanitarian support to Ukraine. He currently lives in Geneva. JSC Ukreximbank is one of the three largest Ukrainian banks and the largest in the country’s network of correspondent banks. The National Bank of Ukraine classifies JSC Ukreximbank as a systemically important bank. The country (represented by the Cabinet of Ministers) owns the entire block of shares, which means that the bank is 100 percent state-owned.
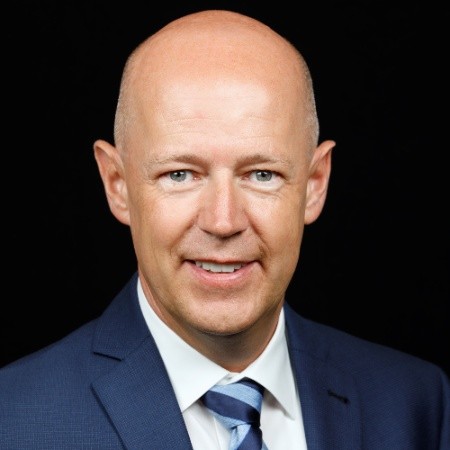
Andreas Wuchner
MD, Wuchner Securitties
Andreas Wuchner is an experienced and recognized senior executive leader with extensive international general management experience of global diversified businesses and a proven track record. He has held positions in Switzerland, Germany, USA, Australia and the United Kingdom.
Andreas served as General Manager (CIO), Chief Information Security Officer (CISO), Head IT Security & Operations, Head IT Risk Control and Head IT Risk Management / Governance & Compliance for several large scale and international organizations including Novartis Pharmaceuticals, UBS, Deutsche Bank, Credit Suisse and Hewlett Packard. He also served on company advisory and supervisory boards helping cyber start-up organizations with his experience in Strategic planning, go-to Market activities, financing advice for seed funding and round A to C plus product/service design.
As an Angel Investor Andreas invests in Cyber Security organizations where he then participates actively in the growth and future of the organization in scope. With more than 25 years of experience and knowledge in all aspects of Information Security, IT-Security & Information Risk management, Andreas supports clients all over the world with his own 2 companies. His special focus areas are within highly regulated environments such as life science and financial services.
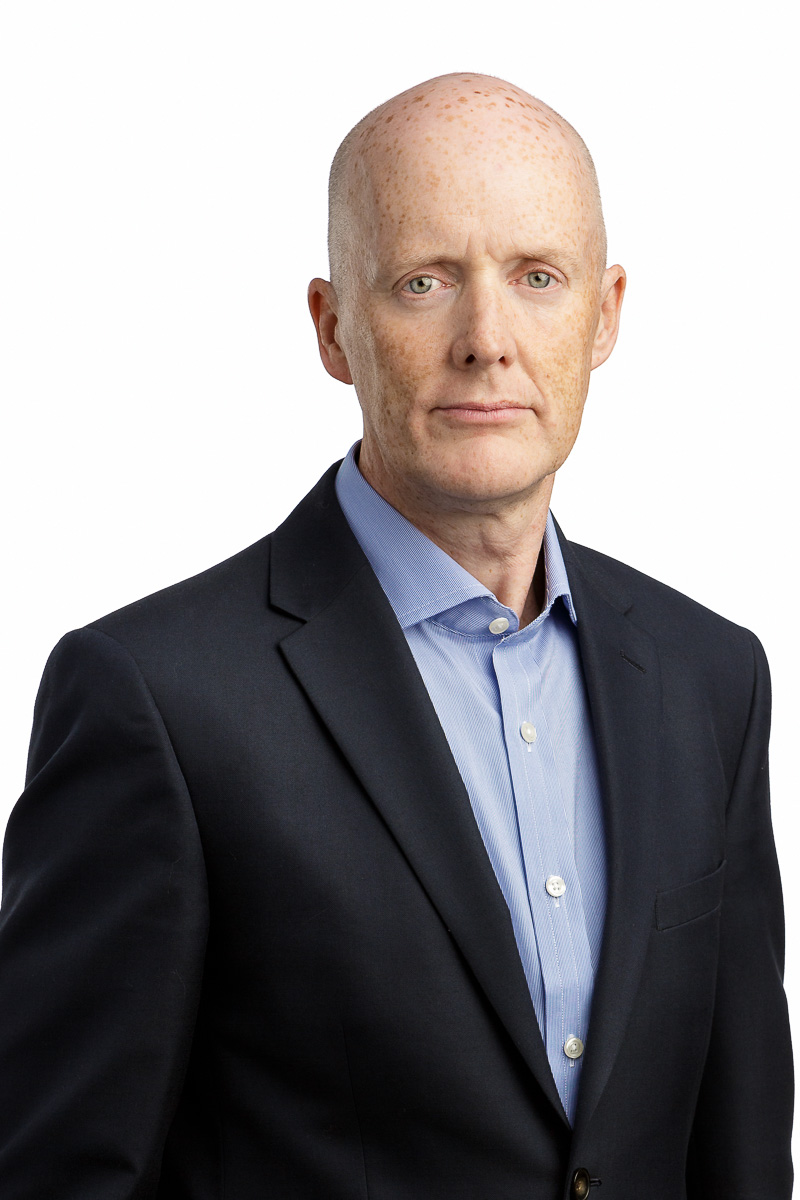
Andrew Rose
Resident CISO EMEA, Proofpoint
Andrew is the Resident CISO at Proofpoint, which he joined in 2021 from Mastercard, where he was the Chief Security Officer of their subsidiary firm, Vocalink, a firm which provides the transactional backbone of the financial services industry in the UK.
Prior to that Andrew held the CISO role at the UK’s Air Traffic Control provider, NATS, where he oversaw a security transformation and contributed to the design of the next generation air traffic control system. Andrew has also held CISO roles at two top tier global law firms, Allen & Overy LLP and Clifford Chance LLP. In between these roles, Andrew was a Principal Analyst at Forrester Research where he covered the role of the CISO and Security Culture & Awareness as two of his speciality areas.
Andrew was recognized as “European CISO of the year” (2018), and has previously won awards for devising and leading the “Best security awareness program” (2015).
Andrew holds a Master’s degree in information security, is a regular speaker at global security conferences and has contributed to media outlets such as the Wall Street Journal, the Financial Times, the Washington Post, Wired magazine and the Times newspaper. Andrew also appeared in the CNBC documentary entitled “Rise of the Machines”.
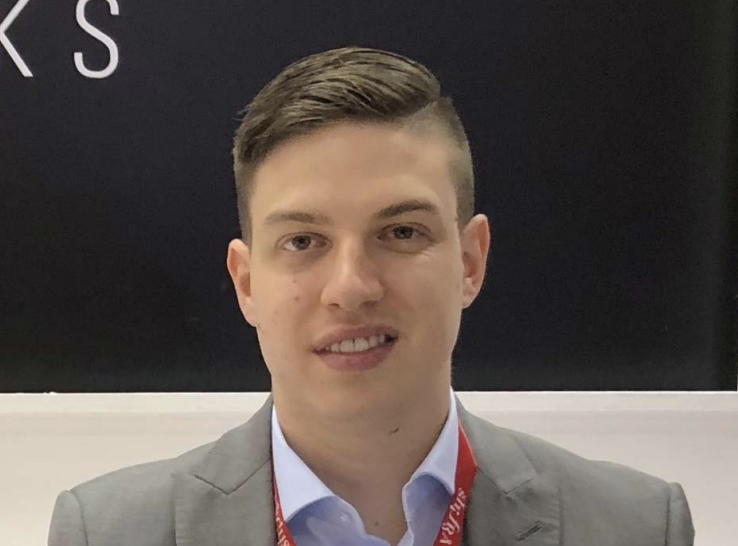
Ashley Nurcombe
Systems Engineer, Corelight
Ashley “AJ” Nurcombe is a highly passionate and driven technologist with a proven track record of competency in the field of Security, Networks, DLT and Mobility, with over a decade of relevant experience.
Broad experience in the most advanced Cybersecurity fields with superior technical abilities, highly reliable, well-rounded, seasoned IT Security professional, AJ has delivered keynote talks across North America, Europe and the GCC.
You may know AJ from his keynote tours on “Rome was not built in a day, and neither was roaming – The Future of Wireless networking”, “Going Bankless – Distributed Consensus in Finance”, and “Zeek and Ye Shall Find – NDR for the Modern SOC”
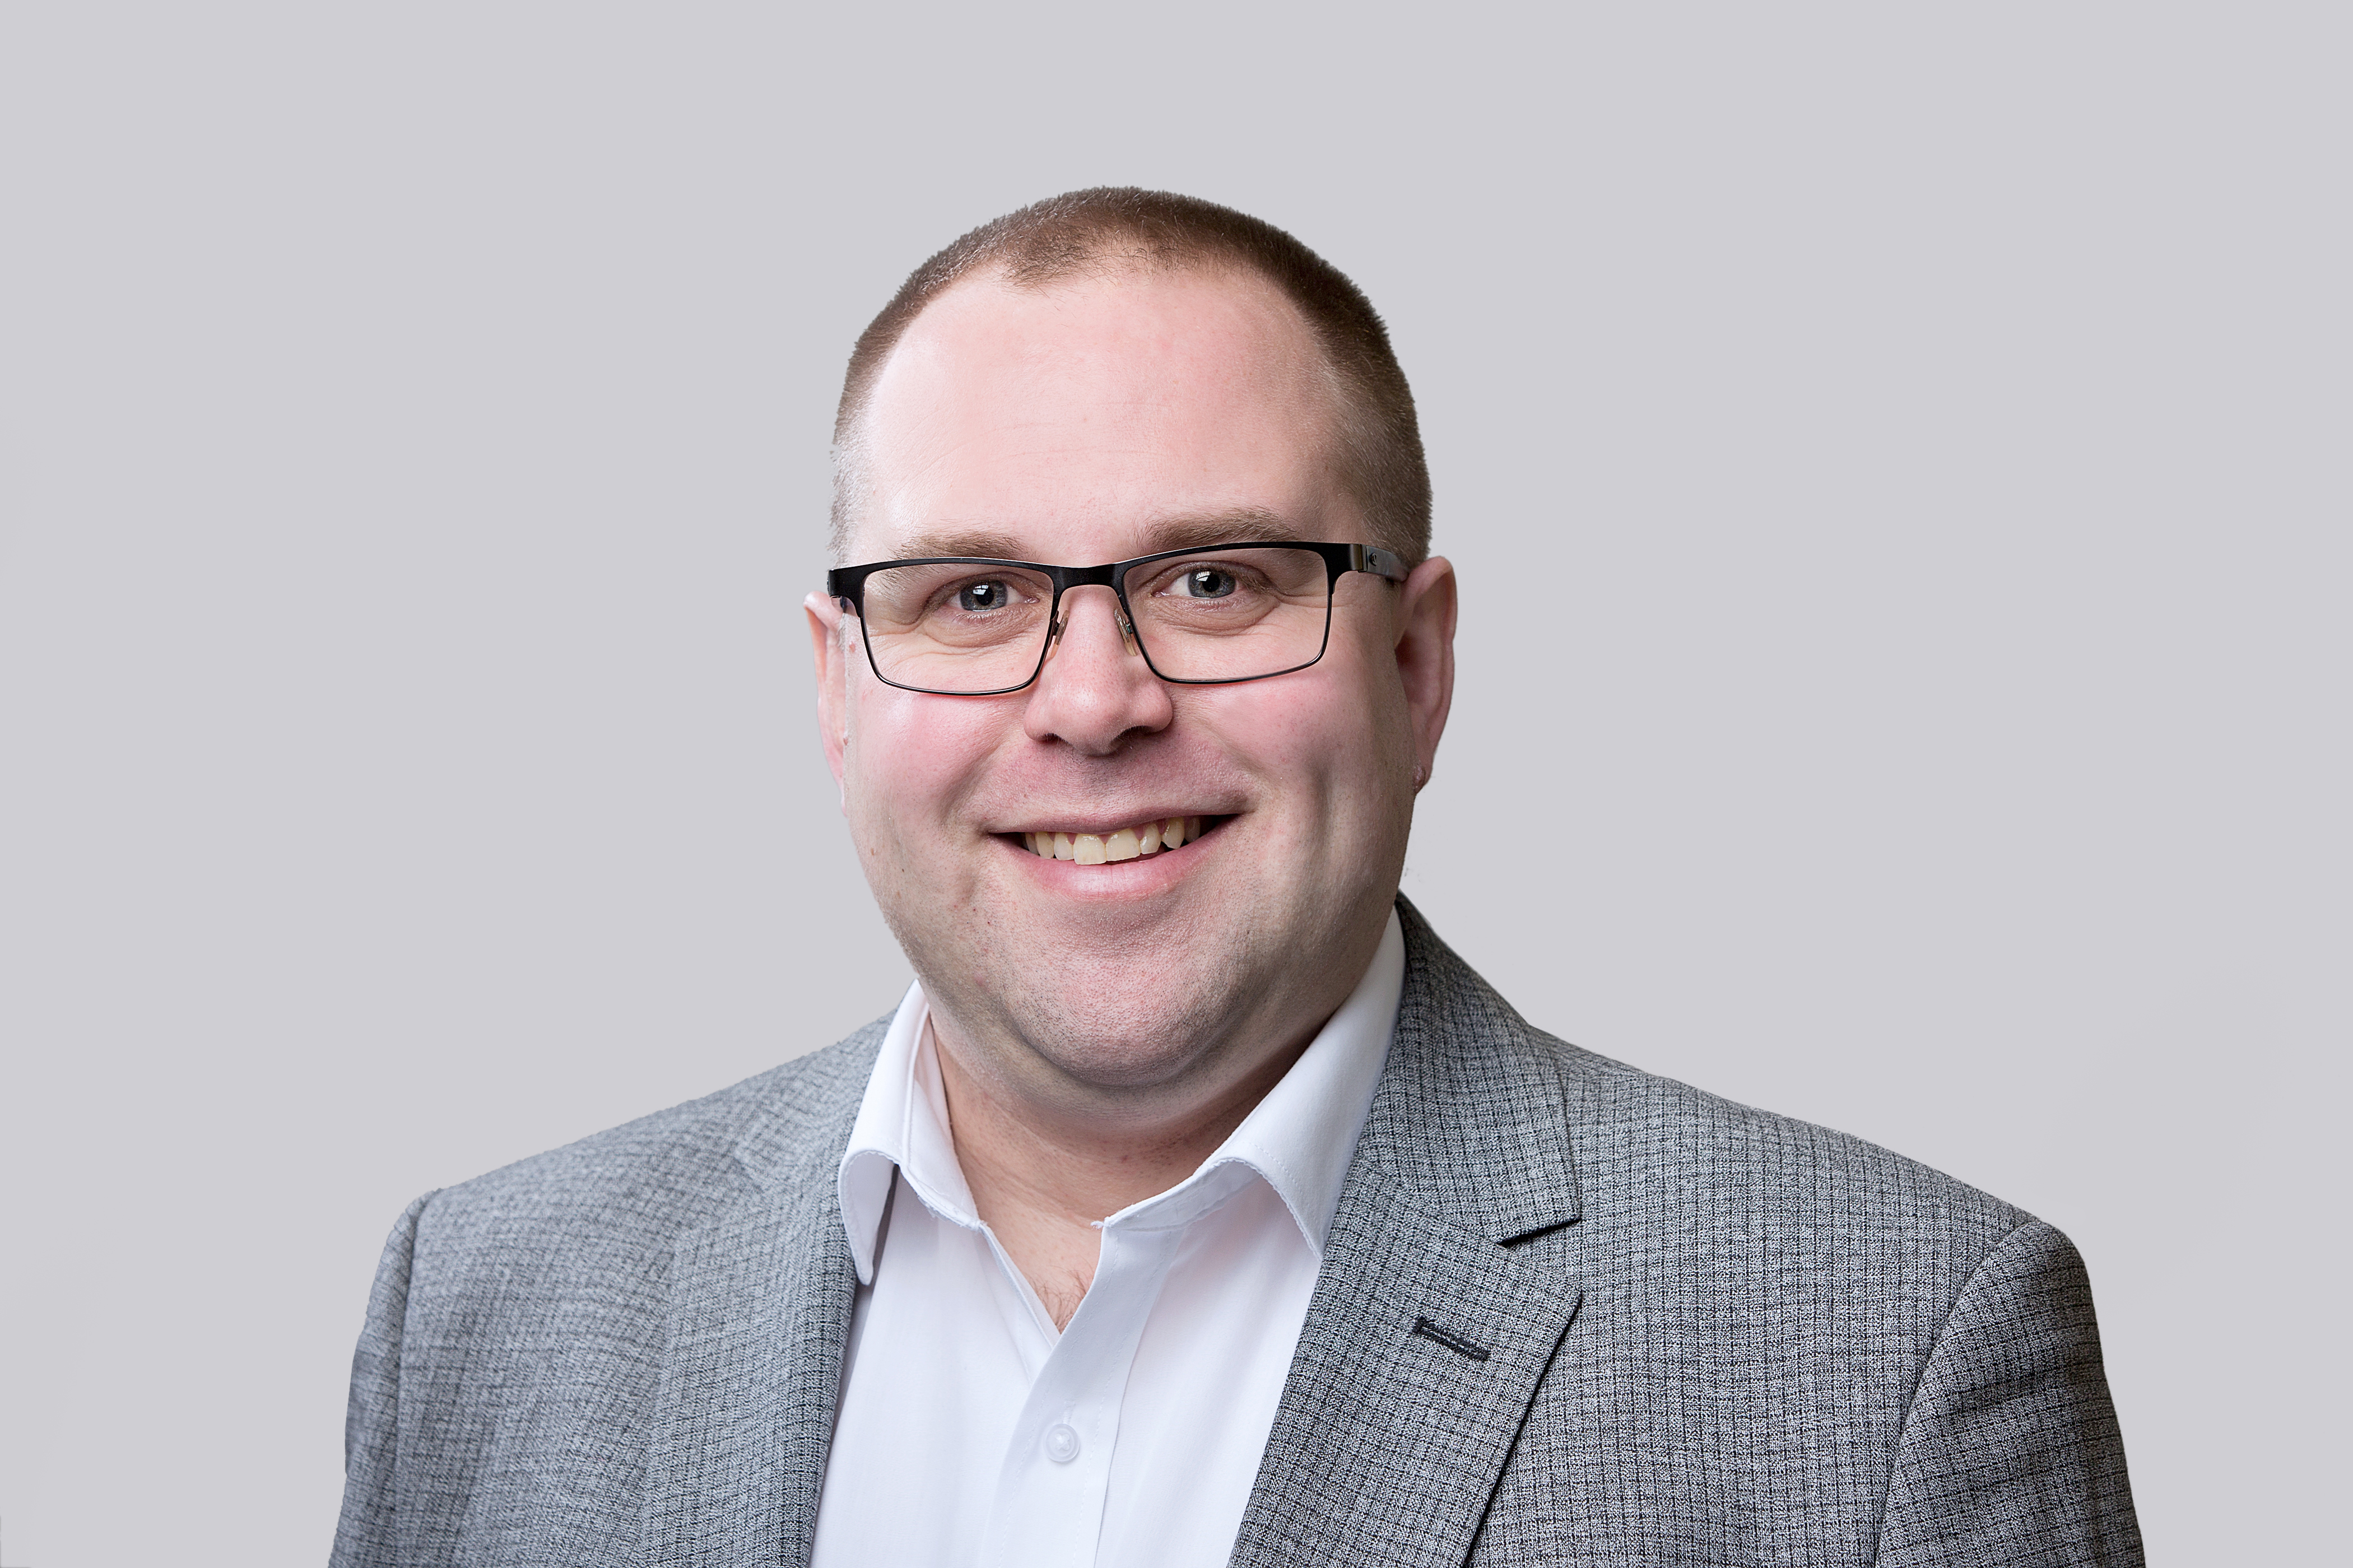
Craig Moores
Principal Lead Consultant, Bridewell
Craig joined Bridewell in 2022 as a Principal Lead Consultant, where he provides expert cyber security consultancy and leadership to clients across critical sectors. In his role, he guides organisations in information security, risk management, PCI DSS, strategic planning, and business auditing. With a strong technical and leadership background, Craig has worked with organisations across FinTech and financial services, CNI, and retail and luxury brands. He also holds numerous certifications from leading industry bodies including CISSP, CAA ASSURE, and is a PCI CSS Qualified Security Assessor.
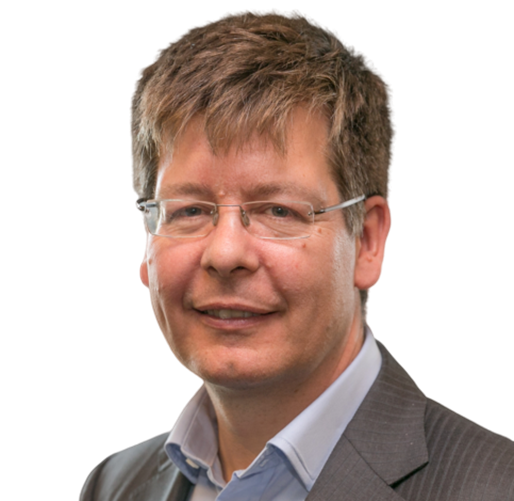
Kevin Duffey
Chief Executive, Cyber Rescue Alliance; Co-Chair of Cyber Committee, Security Institute; and Advisor, Police Digital Security Centre UK
Kevin Duffey is Chief Executive of the Cyber Rescue Alliance, Co-Chair of Cyber Committee at The Security Institute, and Advisor to the Police Digital Security Centre in the UK. Cyber Rescue is a leading specialist in helping Boardroom Executives to measure, monitor and mitigate potential harm from fast-evolving evolving cyber-attacks. Cyber Rescue helps executives at hundreds of large & medium sized firms worldwide. Members include the Bank of China, Janus Henderson, Kaplan, Penguin, Petrofac, Phoenix, Rothschilds, Sainsbury’s, Tesco, Virgin and regulators in several countries.
Kevin enjoyed two careers before his current role.
- In “Cyber,” Kevin was CEO Nordics, CEO Asia, and a UK Board Member at Britain’s largest IT systems integrator, Logica (now CGI). He led digital innovation for banks, telcos and governments in over 20 countries, with clients ranging from GCHQ and the MoD, to the Reserve Bank of India and the Government of the Philippines.
- In “Rescue,” Kevin was Group GM at International SOS, where he oversaw the evacuation of 4,000 people from Egypt and Libya during the Arab Spring. He deployed response to the Fukushima nuclear crisis in Japan and the Ebola crisis in Sierra Leone. He was then headhunted to run G4S International, managing staff in 30 countries as they moved billions of dollars of gold and high-denomination currencies. Kevin joined Cyber Rescue in 2015.
Kevin welcomes contact from delegates, at Kevin.Duffey@CyberRescue.co.uk or via LinkedIn, at https://www.linkedin.com/in/kevduffey/
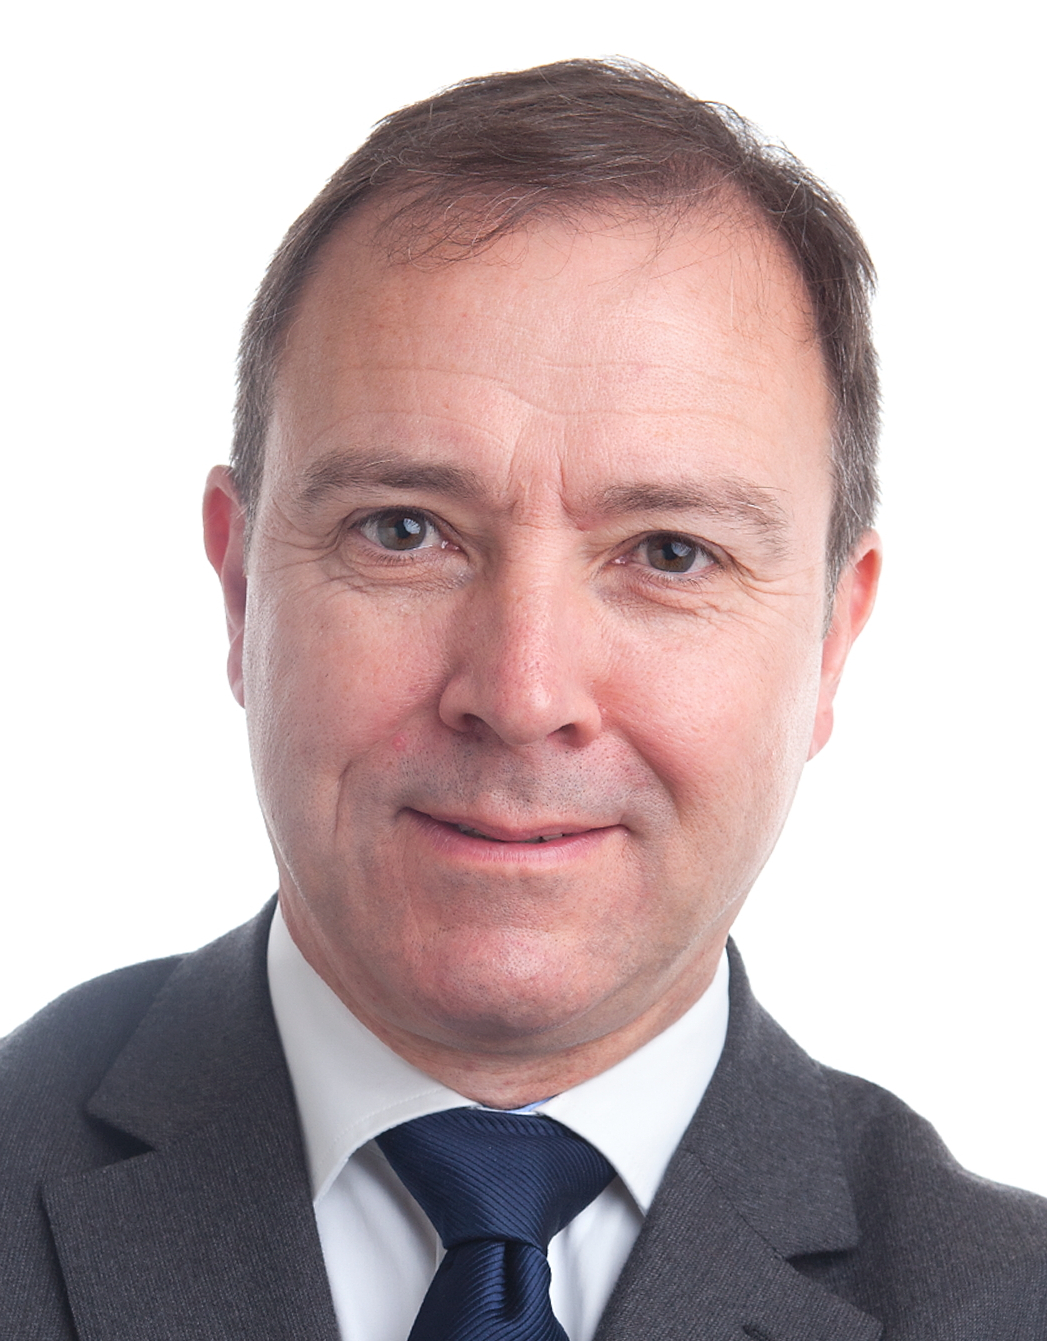
Dr Paul Kennedy
Principal Cyber Security Consultant and Chartered Engineer, QinetiQ
Dr Paul Kennedy is a Principal Cyber Security Consultant and Chartered Engineer with over 10 years of experience in operational cyber security. At QinetiQ, Paul has worked on cybersecurity for the F-35 combat jet and has worked with the MOD in developing novel cryptographic techniques and advising senior stakeholders on future developments in cryptography. A former RAF Officer, he has worked in military cyber and communications across the UK, NATO, and in the Falkland Islands. Describing himself as a recovering academic, he was previously an Engineering Degree Programme Leader at the University of Glasgow.
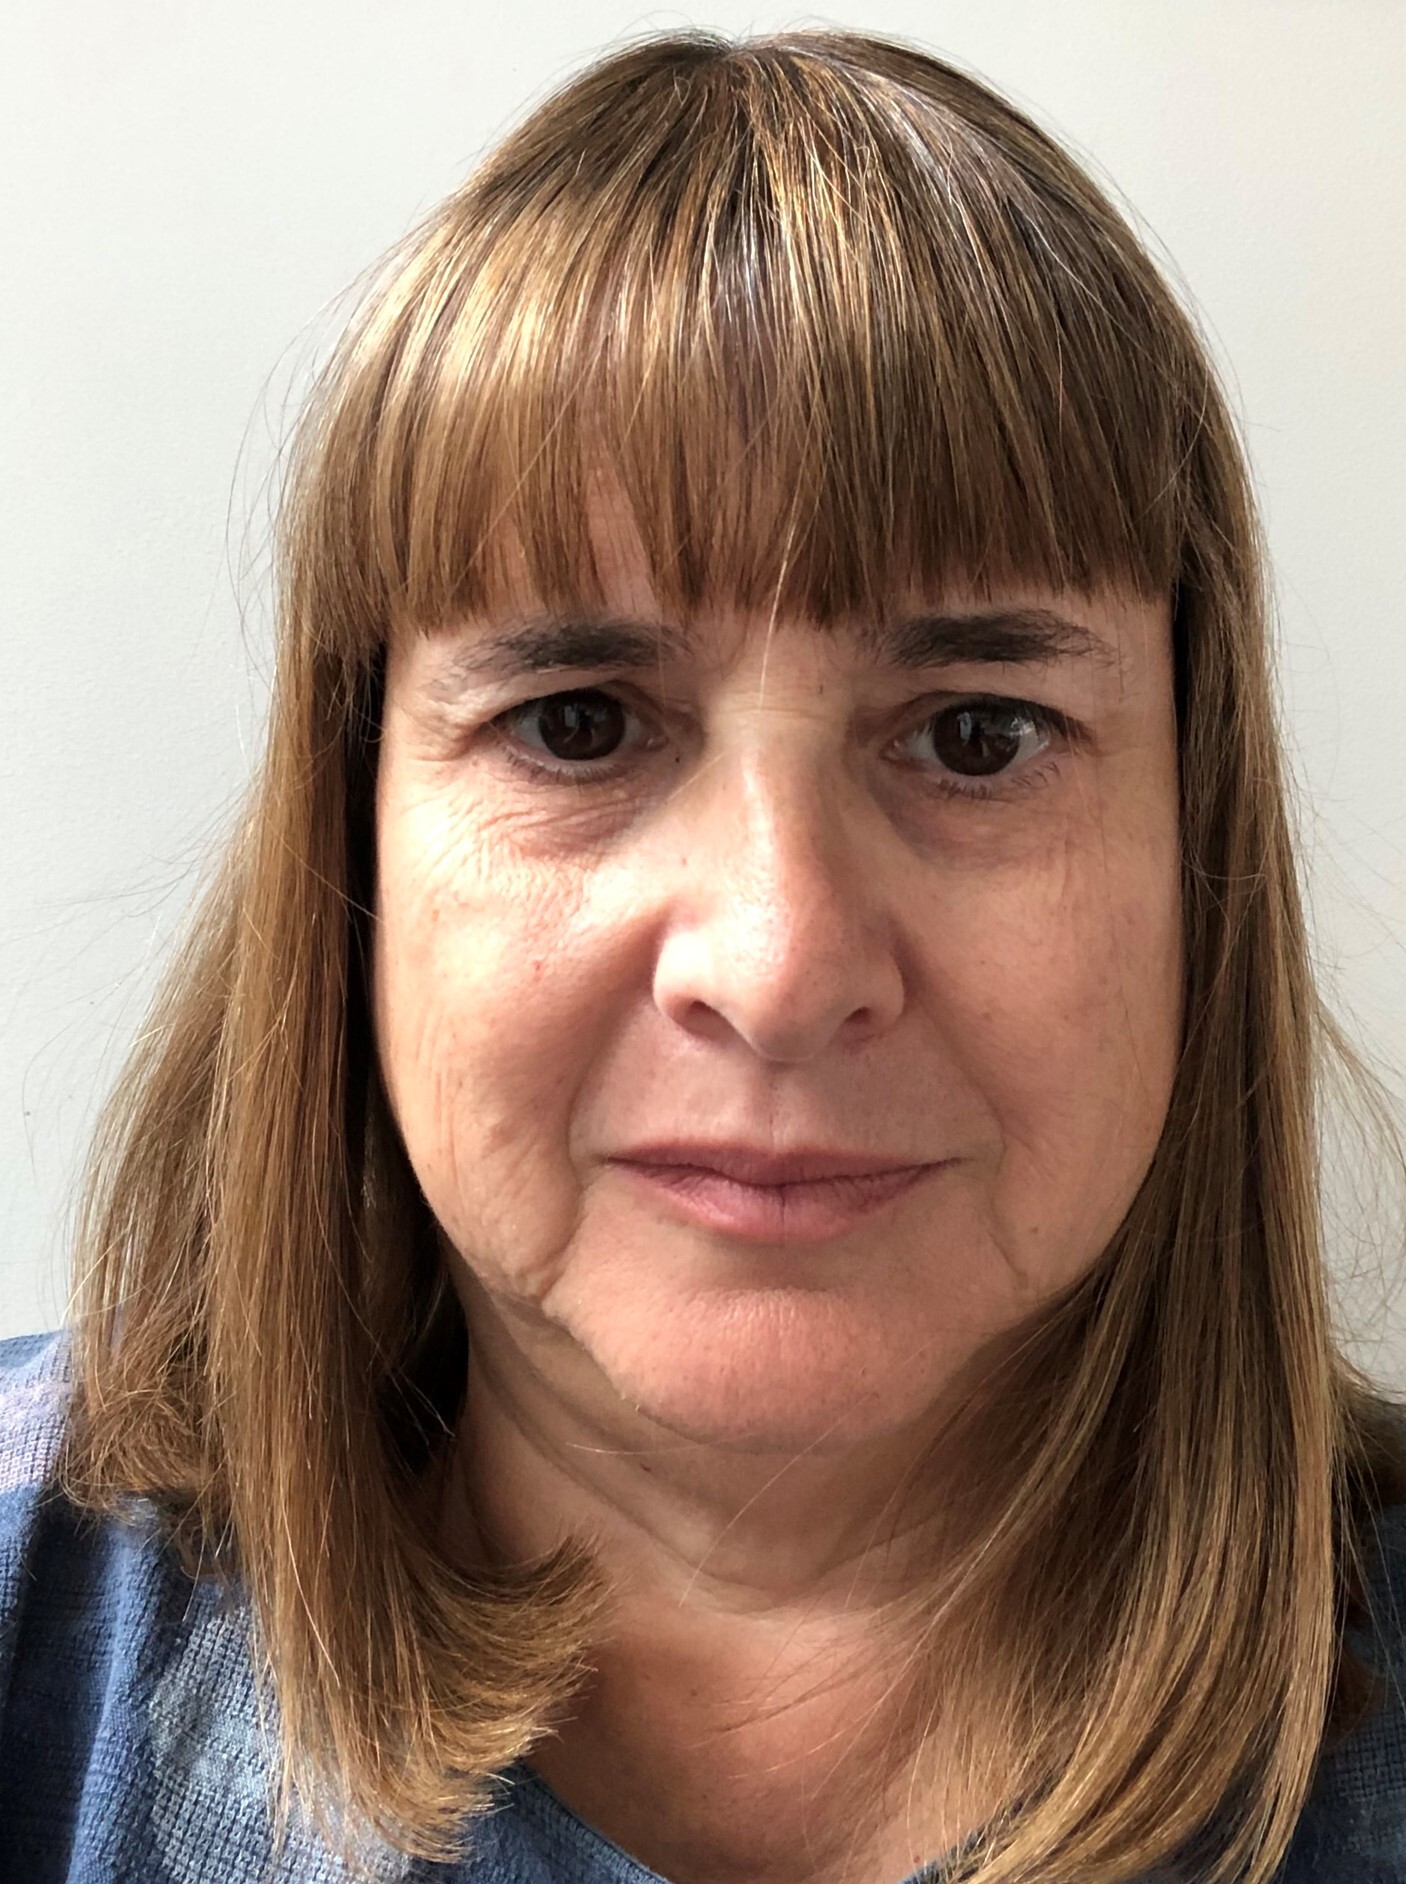
Deborah Saffer
Director Information Security, Liberty Specialty Markets
Deborah has over 25 years of information security and organisational resilience knowledge skills and experience, operating in complex and demanding environments, delivering strategic frameworks in line with the risk appetite of the organisations she has worked for.
Deborah has a wealth of experience as a leading information security and crisis management professional, with a strong track record in successfully delivering security assurance to organisations across multiple industry sectors, significantly at Royal Mail and at the global commercial real estate company, Cushman & Wakefield. Deborah has recently joined Liberty Speciality Markets as their Director of Information Security.
A substantial part of her career has been in the finance industry where she successfully implemented continuous improvement programmes in both information security and crisis management.’
Dr. Richard Hoad
MSc. C. Eng, FIET, SMIEEE, Chief Scientist & Capability Leader, QinetiQ
Richard is a Chief Scientist and Capability Leader at QinetiQ Ltd. Richard has undertaken many years of research studying disruptive effects on Critical Infrastructure assets, particularly for high impact low frequency events. He has helped operators of essential services understand their risk to novel disruptive threats and has developed tools, techniques and products which support improved resilience of the Critical Infrastructure. Richard is the author of over 70 peer reviewed technical and journal papers on the topics above. He is a Fellow of the Institute of Engineering and Technology (IET), registered with the Engineering Council UK (ECUK) as a Chartered Engineer (C.Eng.) a HPEM Fellow of the SUMMA foundation; a QinetiQ Fellow; and a Member of the Register of Security Engineers and Specialists (RSES).
Toks Oladuti
Global Deputy Chief Information Security Officer, Dentons
Toks is responsible for the global delivery of information security at Dentons, the world’s largest law firm. He has over 20 years’ experience working in security, technology and privacy, across a number of industries.
Toks is an experienced and strategic business risk leader. He has a particular passion for strategy and team building and development. His core skillset, developed over the years includes security operations and architecture, risk management and risk driven investment, data protection, compliance and audits, and enterprise culture, awareness and training.
Toks has contributed to the business and technology community through information sharing, groups, speaking engagements and multi-industry networking. As strong supporter of education and schools, he has provided advice in areas of security, data protection, user awareness and cloud transformation.
Peter Ling
Vice President, Cyber and Intelligence Solutions Global Cybersecurity Alliances and Cyber Resilience Programs, Mastercard
With 28 years’ experience in the Cybersecurity space, Peter is a seasoned global practitioner and technology pioneer, having created numerous offerings in this space. His background spans from operational security response management, systems engineering, and complex technical vendor integrations — to strategic alliances throughout the security and risk markets. His areas of expertise are in Public Key Cryptography (PKI), Secure Communications, Endpoint Protection and Threat & Risk management. He has developed and brought dozens of security products to market internationally and is on a constant journey, assisting partners and clients as the Cybersecurity market continues to meet the challenges of the day.
Jonathan Armstrong
Partner, Cordery
Jonathan is an experienced lawyer who advises multinational companies on matters involving risk, compliance and technology across Europe. He has handled legal matters in more than 60 countries involving emerging technology, corporate governance, reputation, internal investigations, marketing, branding and global privacy policies. Jonathan has counselled a range of clients on breach prevention, mitigation and response.
Jonathan is one of three co-authors of the LexisNexis definitive work on technology law, “Managing Risk: Technology & Communications”. He is a frequent broadcaster for the BBC and other channels and appeared on BBC News 24 as the studio guest on the Walport Review. Jonathan features again in the Thomson Reuters Stand Out Lawyers for 2022 where he has been featured every year since the survey began.
Interestingly, Jonathan is Co-Chair of the New York State Bar Association’s Rapid Response Committee (RRC) and a member of the Section’s Executive Committee. The RRC responds to world events on behalf of NYSBA. Activities have included support for lawyers and the judiciary in Poland, France, the UK, Ecuador, Spain, Cameroon, Austria, Afghanistan, Mexico, Myanmar & Indonesia. The RRC also made representations after the collapse of the EU-US Safe Harbor scheme for data transfer and is currently heavily involved in assisting the Ukrainian Bar Association in some of their efforts. He has also led the RRC’s relations with other non-profit and advocacy groups. This is a voluntary position.
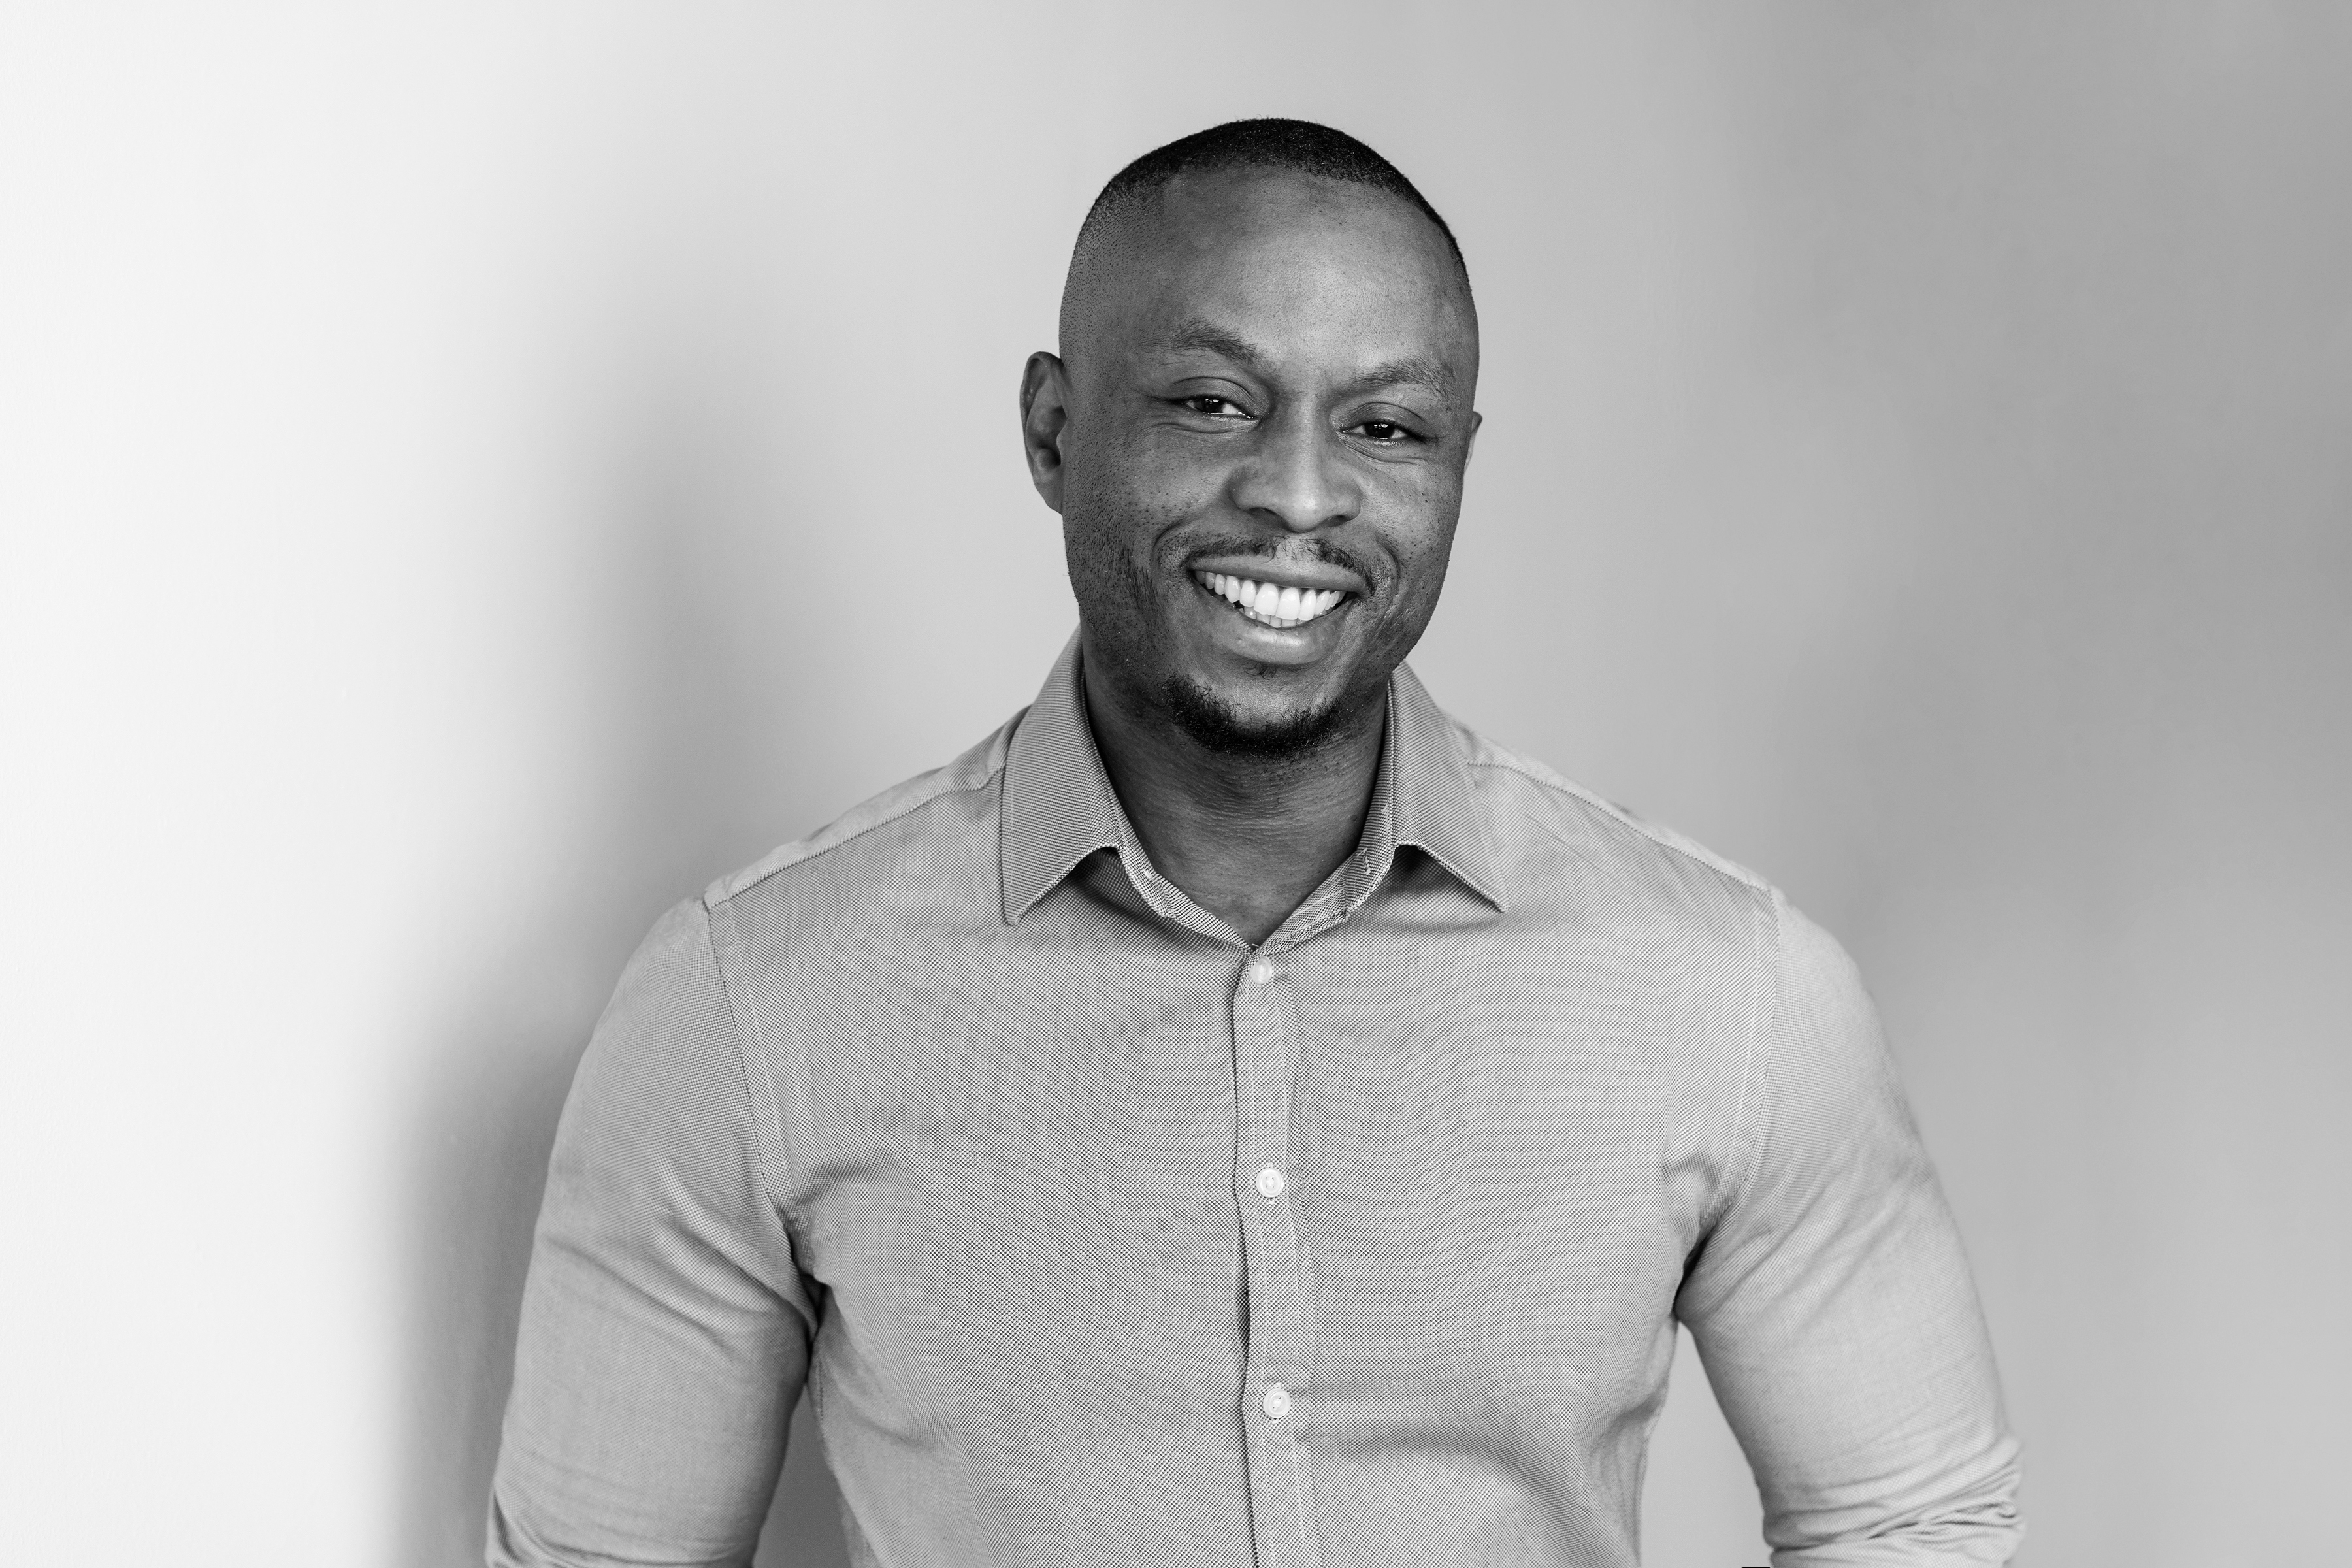
Owanate Bestman
Director, Bestman Solutions
Owanate is the founder of Bestman Solutions, a firm dedicated to helping leaders hire cyber security professionals. He advises CISOs and Executives on market factors that impact their growth plans and designs bespoke solutions to address this. Firmly embedded in the cyber security space, he possesses a global core network of well-respected and proven security specialists.
Owanate has spent almost a decade recruiting in the Cyber Security field. Before this, he recruited Technology and Operational Risk specialists and successfully staffed a number of high profile banking regulatory programmes.
He is also a keen industry speaker and writer for security associations and international publications. Outside of Security and staffing, Owanate is interested in all things Martial Arts.
Máté Barany
Enterprise Executive, Ping Identity
Máté Barany has over 12 years of experience working on complex implementation projects across EMEA. Previously as a Solutions Architect and now as an Account Executive, the key to Máté’s success is focusing on the End User Experience – implementing a “Customer First” approach when working with Partners and Customers – while at the same time ensuring key business and technical requirements are met. Máté loves a challenge and believes there is always room for improvement.
Tim Ayling
VP Cyber Security Specialist EMEA, Imperva
Tim currently serves as the EMEA AVP cybersecurity sales specialists at Imperva. With over 20 years’ experience in the cybersecurity and anti-fraud industry, Tim began his career in technical support, and moved on to System Engineering. He began his leadership career when he established Entrust Inc. in Australia in 2003 and was made Vice-President Asia Pacific in 2006. Following this he has held numerous leadership roles in large cybersecurity vendors, including Trend Micro, RSA Security, and now Kaspersky Labs, as well as spending time in the cyber-security practise of KPMG.
Ashley Nurcombe
Systems Engineer, Corelight
Vicki Gavin
Head of Information Security and Compliance, Kaplan International
Vicki Gavin is Head of Information Security & Compliance at Kaplan International and also Former Chair of The Women’s Security Society.
Kaplan International is a leading provider of international education. Students travel to study with Kaplan International Languages from over 150 countries around the world Kaplan offers programs for students to enter UK, USA and Australian university degree courses at undergraduate, postgraduate and doctorate level. Successful completion at the required level guarantees entrance to one of more than 1,000 degree courses at dozens of partner Universities.
Vicki is a recognized expert in security, privacy and resilience. She was Chairperson of the Women’s Security Society and has won Cybersecurity Woman of the Year and Unsung Hero, Marathon (Wo)man awards.
Currently Vicki is Head of Information Security & Risk Management for Kaplan International, having previously held leadership positions with Cyber Rescue Alliance, Artemis Fund Management, Kensington Mortgages, The Economist, Barclaycard, Barclays Bank, Barclays Capital, Dresdner Kleinwort Wasserstein and the Toronto Stock Exchange. Vicki is MBCI and CRISC Certified, holds a BSc in Physics and a Postgraduate Diploma in Teaching Adults..
Holly Foxcroft
Head of Neurodiversity Research in Cyber, Stott and May
Holly Foxcroft, is head of neurodiversity in cyber research and consulting at recruitment consultancy Stott and May. Holly is a Royal Navy veteran who began her cyber career at Advanced Resource Managers, a Portsmouth-based cyber recruitment specialist. She became a champion of neurodiversity in the industry in 2014, when her son was diagnosed with autism, and has since thrown herself into researching the subject, including putting herself through university as a single mother and campaigning for change. “Driving for change to be neuroinclusive and supporting the neurominority community is my passion. Winning the [Diversity Champion] award for me is shining a light that mine and other neuroinclusive supporters’ work is really being recognised in the field of diversity and cyber” In her role at Stott and May, Foxcroft is working on the development of policies in best practice, guidance, training and consulting around neurodiversity in cyber, and better supporting neurodivergent cyber professionals, not just through the recruitment process, but through effecting cultural change and challenging biases in the workplace.
360 Series Sponsors
All Sponsors Banner As At March
Sponsorship opportunities
RiskRecon
RiskRecon, a Mastercard Company, enables you to achieve better risk outcomes for your enterprise and your digital supply chain. RiskRecon’s cybersecurity ratings and assessments make it easy for you to understand and act on your risks, delivering accurate, risk-prioritized action plans custom-tuned to match your risk priorities. Learn more about RiskRecon and request a demo at www.riskrecon.com.
At Ping Identity
At Ping Identity, we believe in making digital experiences both secure and seamless for all users, without compromise. That’s digital freedom. We let enterprises combine our best-in-class identity solutions with third-party services they already use to remove passwords, prevent fraud, support Zero Trust, or anything in between. This can be accomplished through a simple drag-and-drop canvas. That’s why more than half of the Fortune 100 choose Ping Identity to protect digital interactions from their users while making experiences frictionless. Learn more at www.pingidentity.com.
QinetiQ
QinetiQ is an integrated global security and defence company. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way. We address the weaknesses of the piecemeal solutions on the market today by providing end-to-end security across every level of your digital ecosystem. With our defence-grade security technologies, rigorous threat checks and system-wide managed cyber security service we can help you build digital resilience, so you can face the future with greater certainty.
Bridewell
Bridewell is a cyber security services company that specialises in protecting and transforming critical business functions for some of the world’s leading organisations.
Their consultants work with clients to deliver end-to-end services that solve their security and business challenges. Bridewell’s specialists are highly accredited by major industry bodies and have extensive experience delivering services across cyber security, managed security, penetration testing, and data privacy.
Founded in 2013, Bridewell is headquartered in the UK where it runs a 24/7 Security Operations Centre (SOC) and has a growing presence in the US to further support global clients.
For more information, visit www.bridewell.com
Corelight
From the Acropolis to the edge of space, defenders have sought the high ground in order to see farther and turn back attacks. Corelight delivers a commanding view of your network so you can outsmart and outlast adversaries. We capture, interpret, and connect the data that means everything to defenders.
Qualys
Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.
For more information, please visit www.qualys.com
We
We are a handpicked, passionate, team of security professionals providing Penetration Testing and Cyber Security Consulting services throughout the UK and worldwide. We work with each client from the scoping through to the report delivery and all following remediation to ensure you have our full attention throughout the entire process. Fidus are a CHECK, TIGER and Cyber Scheme approved company with CREST qualified consultants.
Security Scorecard As Sep
Imperva
Imperva is the comprehensive digital security leader on a mission to help organizations protect their data and all paths to it. Only Imperva protects all digital experiences, from business logic to APIs, microservices, and the data layer, and from vulnerable, legacy environments to cloud-first organizations. Customers around the world trust Imperva to protect their applications, data, and websites from cyber attacks. With an integrated approach combining edge, application security, and data security, Imperva protects companies ranging from cloud-native start-ups to global multi-nationals with hybrid infrastructure. Imperva Threat Research and our global intelligence community keep Imperva ahead of the threat landscape and seamlessly integrate the latest security, privacy, and compliance expertise into our solutions.
BS White Background
Local knowledge. Global resources. Specialist consultants. Barclay Simpson is an international recruitment consultancy that specialises in recruiting information and cyber security professionals. Since 2001, we have provided end-to-end information security recruitment solutions, including permanent, interim and executive hires from analysts through to CISOs, so organisations can create an information security function that’s both fit for purpose and future-proof. Whether sourcing a single hire, an interim manager, or building a security function from scratch, our extensive network and niche specialist knowledge make Barclay Simpson ideally positioned to support your security needs.
Today
Today’s attacks target people. Cybercriminals are increasingly shifting their focus from targeting infrastructure, to targeting people with social engineering attacks.These people-centric cyberattacks require a people-centric cyber defence.
Over 85% of breaches involve a human element, which is why 75% of the Fortune 100 rely on Proofpoint’s leading people-centric security and compliance solutions to mitigate their most critical risks, from ransomware, business email compromise (BEC), and supply chain threats to data loss across cloud, endpoint, web, and email. This includes the top 5 banks, 7 of the top 10 global retailers, half of the top 10 global pharma companies, and 14 of the top 15 research universities.
Every day, Proofpoint analyses an incredible data set of more than 2.6 billion email messages, 49 billion URLs, 1.9 billion attachments, 28.2 million cloud accounts and over 500 million events associated with potential data loss. This gives us and our customers unmatched visibility into the threat landscape.
More information is available at www.proofpoint.com/uk
Barclay Simpson Solutions
Barclay Simpson Solutions helps empower our clients to achieve business transformation success. We combine our proven industry talent expertise with effective and measurable project & service ownership and reporting. We work in partnership with our sister organisation (Barclay Simpson Associates) to ensure our advisory and project service flexibility utilises industry leading consultants, maintaining our overall strong position in the solutions market. Supporting our clients by providing comprehensive, outcome based engagements operated through a project services (Statement of Work) framework to ensure performance and delivery, Barclay Simpson Solutions provides expertise in project and service outcomes across the following areas, please click on any listed service offering for more information: Project Engagement Services: Governance & Assurance; Cyber Security & Info Sec; Risk & Compliance; Audit.
Bestman Solutions
Bestman Solutions is a specialist cyber security practice. We are built on over 15 years of experience, placing some of the world’s brightest minds in the security and technology sector.
Over the years, we have developed a diverse network of well-respected and proven security specialists, both contract and permanent, from mid to senior level.
We offer exclusive access to top cyber security experts. In cyber security, established relationships get you far. Because of our founders’ longevity in this area, we have been able to build an associate model, giving us exclusive access to the top experts within their given security fields. With offices in London and Texas, we work with a global portfolio of clients on key hires, contractor placements, multi-hire, and statement of work projects.
Surf
“Modern enterprise has increasingly made use of SaaS/browser based applications, presenting growing security risks which are heightened in today’s remote workforce reality.
SURF addresses this risk by establishing a secure endpoint Zero-Trust environment, without compromising a seamless user experience. Our solution is a timely shift from VDI/RBI/SSE to our new browser technology, which facilitates secure access to the corporate resources from anywhere and any managed/unmanaged device. In this way SURD offers an identity-based browser solution with minimal disruption to the user experience.
The SURF’s platform also enables the implementation of adjacent services like extension mgmt, DLP, malicious content disarm/reconstruction and phishing prevention. ”
Venue – 4th Cyber Exchange 360 – Talk to the Board
The Waldorf Hilton, London
Aldwych, London, WC2B 4DD, United Kingdom
www.hilton.com/en/hotels/lonwahi-the-waldorf-hilton-london/
The 4th Cyber Exchange 360 – Talk to the Board will be hosted at the iconic Waldorf, a London hotel built in the 1800s.
Blending Edwardian grandeur with modern comfort, the Waldorf sits in the center of London’s glitzy theatre district and is just a four-minute walk from the Royal Opera House. Covent Garden, The British Museum, and Trafalgar Square are all within a mile of our door. The event spaces for Our meetings and events space includes Palm Court which the 1997 film, Titanic took inspiration from for its production.
Location
The Waldorf Hilton, London
Aldwych, London, WC2B 4DD, United Kingdom
The Waldorf Hilton London is 6 min walk from Covent Garden, and will give you easy access to London’s major landmarks and main shopping districts.
Closest tube stations:
Covent Garden station: 7 minute walk
Temple station: 9 minute walk
Embankment station: 10 minute walk
Closest train stations:
Charring Cross Station: 7 minute walk
Waterloo train station: 14 minute walk
Gallery – 4th Cyber Exchange 360: Talk to the Board

2022 Downloads – 4th Cyber Exchange 360: Talk to the Board
Download Post Event Report Cyber Exchange 360:Talk to the Board
 Download Post-Event Report 2022
View Gallery from the 4th Cyber Exchange 360:Talk to the Board
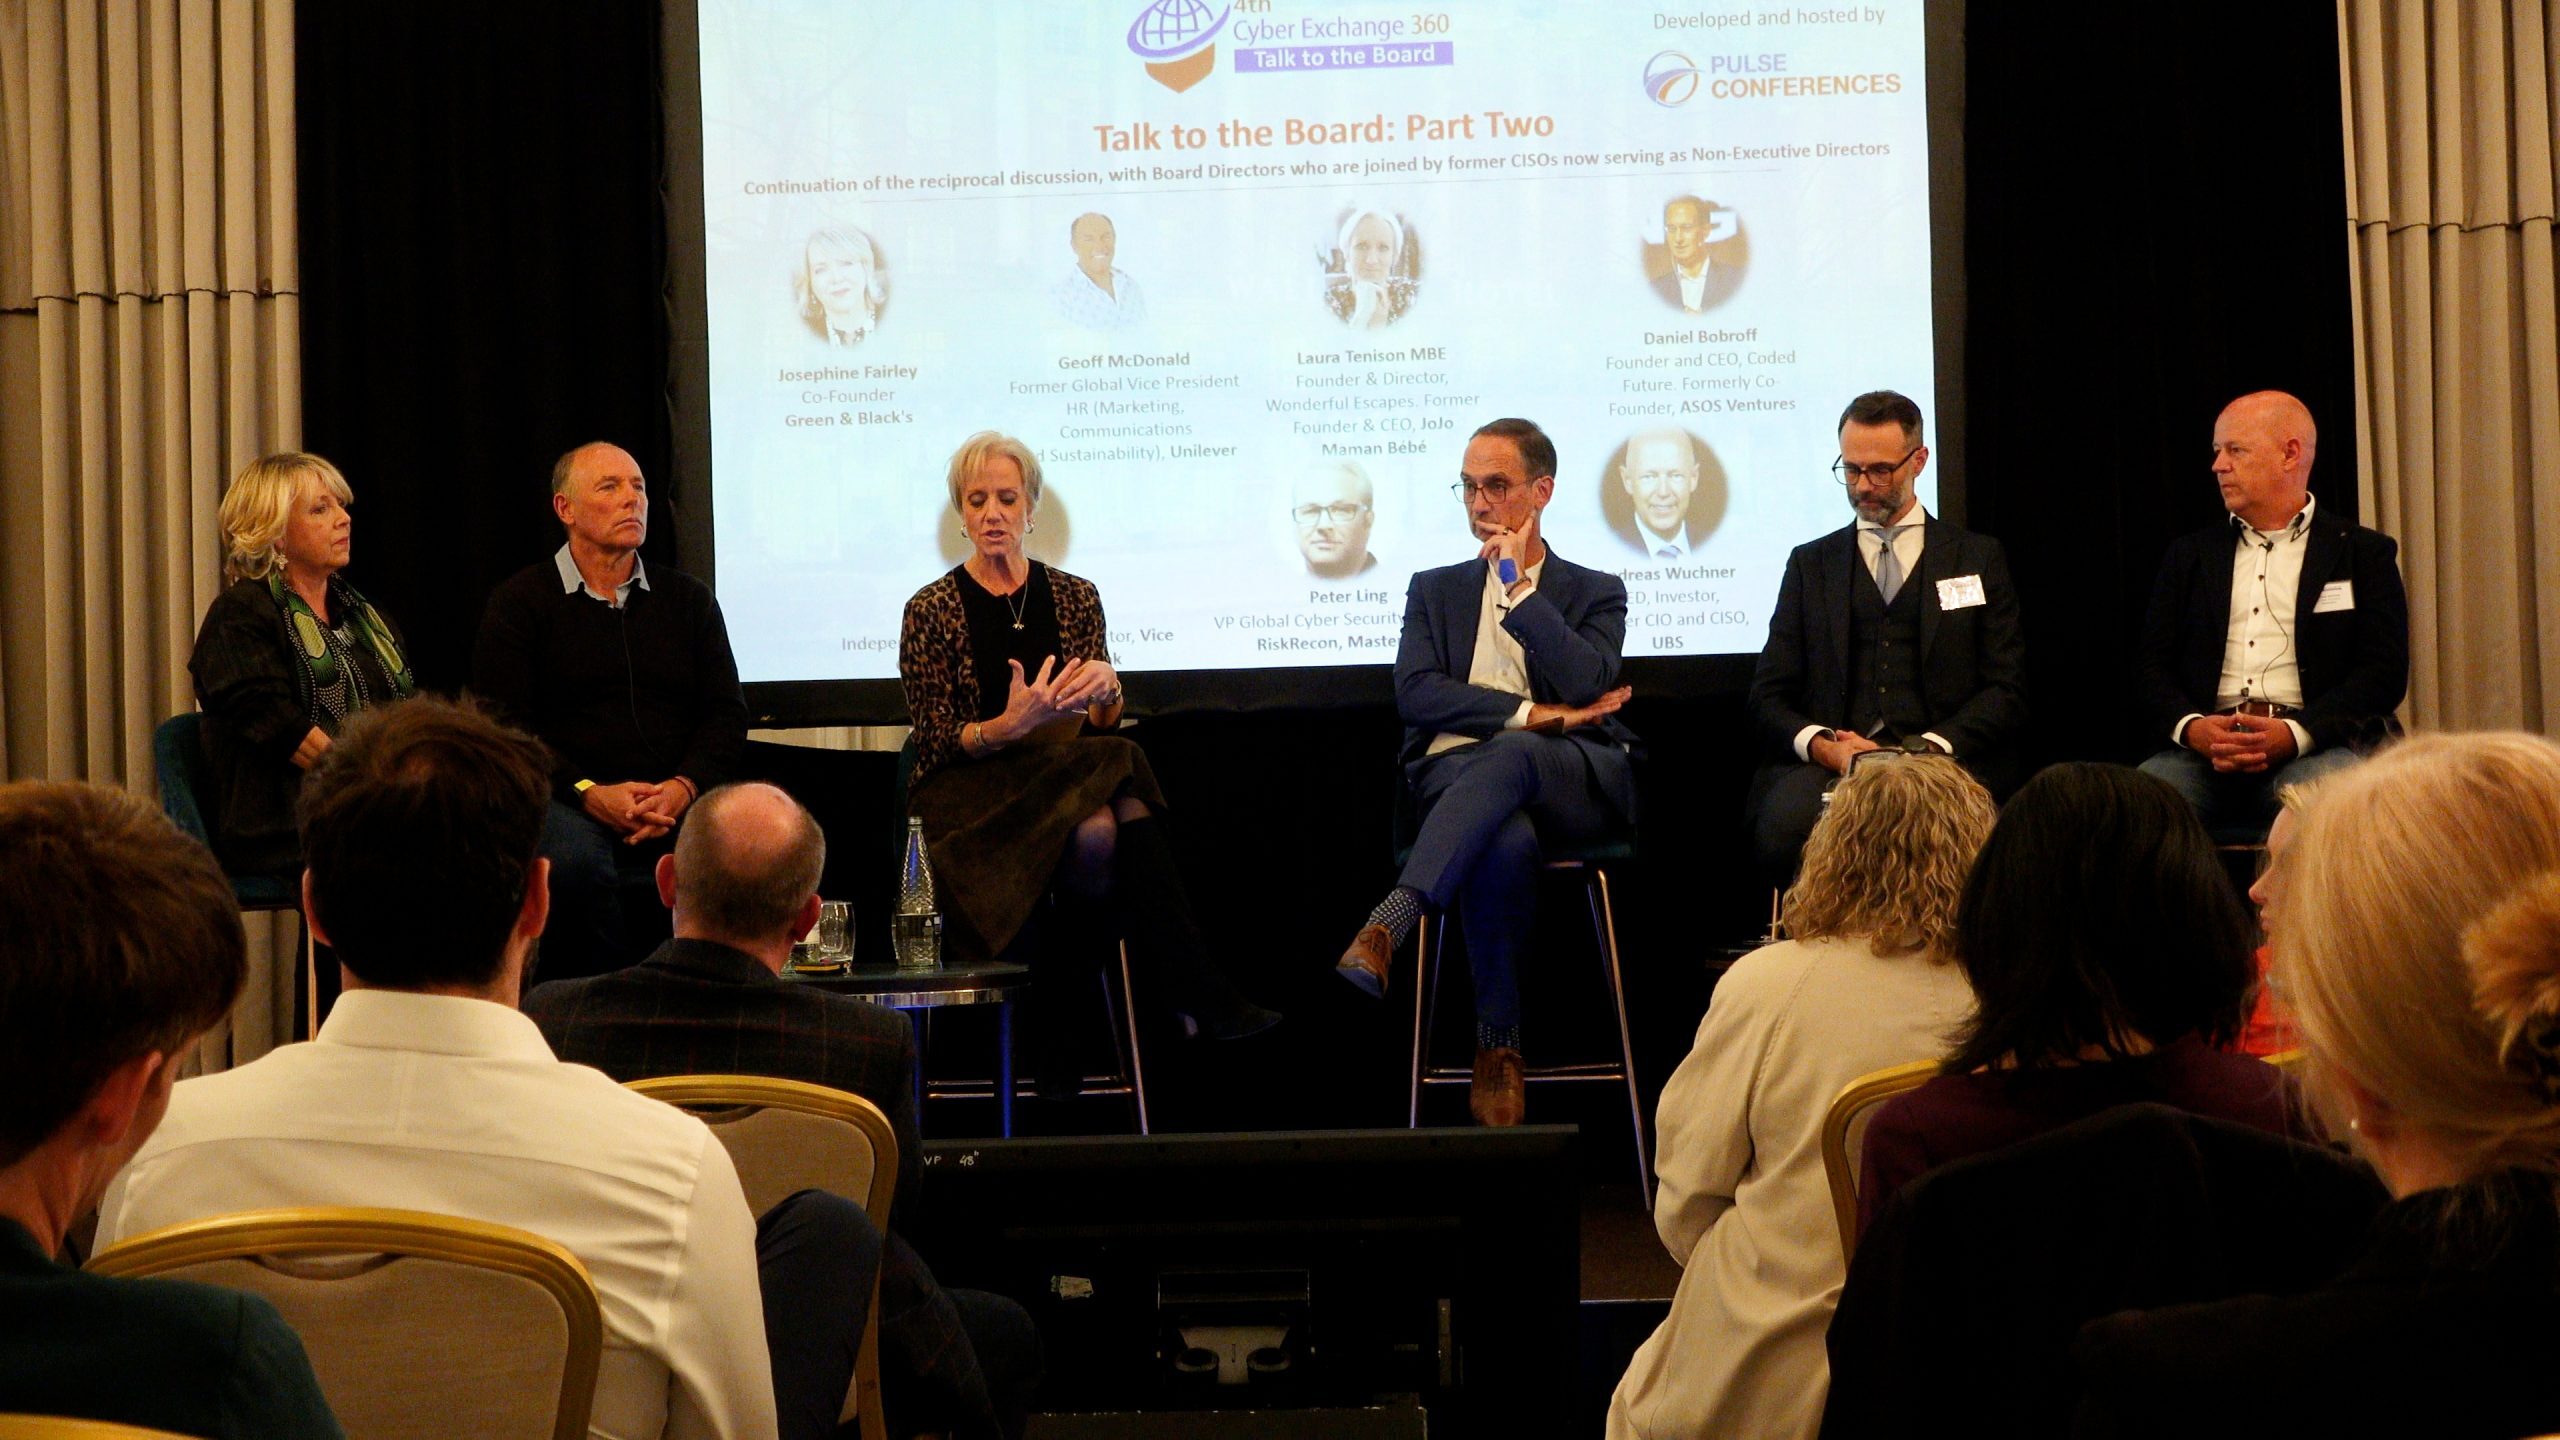 View Photo Gallery 2022!
Highlights Video- 4th Cyber exchange 360: Talk to the Board
 View Highlights Video
Download Programme 4th Cyber Exchange 360:Talk to the Board
 Download Full 2022 Flyer
Share your feedback – 4th Cyber Exchange 360:Talk to the Board
 Share Feedback!
Testimonials
“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them
champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.” Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey
“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics”
Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics
 “First class organisation and presentations. I would highly recommend Pulse conferences for those Senior Managers who need to get value from their time and attendance and for the quality of guest speakers” Ray Jackson, CISO, Telrock Systems Ltd
““It’s a great event with some high-calibre attendees, and the turnout has been impressive. The one-to-ones provide a superb opportunity to spend some focused time with key customers. And it was brilliant to have one of our teams hosting one for the roundtables around CISO practical tips. It’s a unique in that it is a closed community. You get more one-on-one time than you would do at another conference.” Remco Postma, Sales Leader, SailPoint
““The day has been great. I enjoyed a lot of good conversations. I’ve spent time with interesting companies and interesting people. Pulse always uses thrilling venues, and the Science Museum in London is special. What’s unique is that CISOs can talk to the board – they have opinions and they want to share them, and also listen to the guidance offered.” Scott Daly, Commercial Manager, HUMAN
 “It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Deborah Saffer, Global Deputy CISO, Cushman & Wakefield
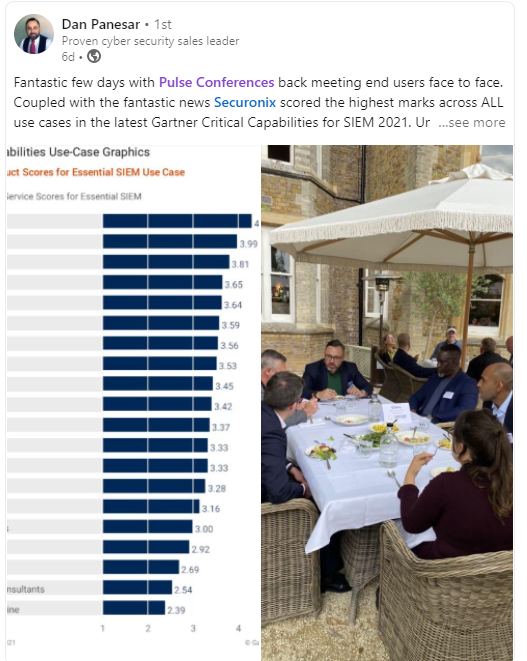
“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions
 “Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim
 “Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”
Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)
“The emerging consensus from Talk to the Board was how challenging it is for CISOs to present cyber risk to the board in an intelligible way for non-technical people. The challenge for the board is then to understand that and take action. Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. It’s great to have board and CISO side of the equation together at this event. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.” Robert Hannigan, Chairman, BlueVoyant. Former Director, GCHQ
““As ever, an excellent oipportunity to have time infront of executives who are likely to be very similar to the executives that all CISOs are likely to have to bring on side. It gave fascinating insights, and some I will certainly be using in the future.” Julia Harris, Information Security Assurance and Compliance Director, Flight Centre Travel Ltd
““I’ve had a few good sessions with various organisations. Looking at what’s going on across the industry and how organisations are doing things slightly differently has been very interesting. The need for greater collaboration is a key message. It is a fantastic event, and the venue at the Science Museum is the perfect size: I’ve had a breadth of conversations, but it’s small enough to have one-to-one discussions.” Andrew Kelly, Principal Consultant, QinetiQ
“
“It was a fantastic day. It is great to be back in London and meeting people again. Pulse events are always absolutely amazing. As usual it was such a diverse group of people from so many different departments – finance, manufacturing and so on – and they are all at a certain level where you start to understand strategy and where the industry is going in the UK. I probably learnt more than the people I spoke with, so it’s been brilliant.” Paul Baird, UK Chief Technology Security Officer, Qualys
“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
Jonathan Armstrong, CEO, Cordery
“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK
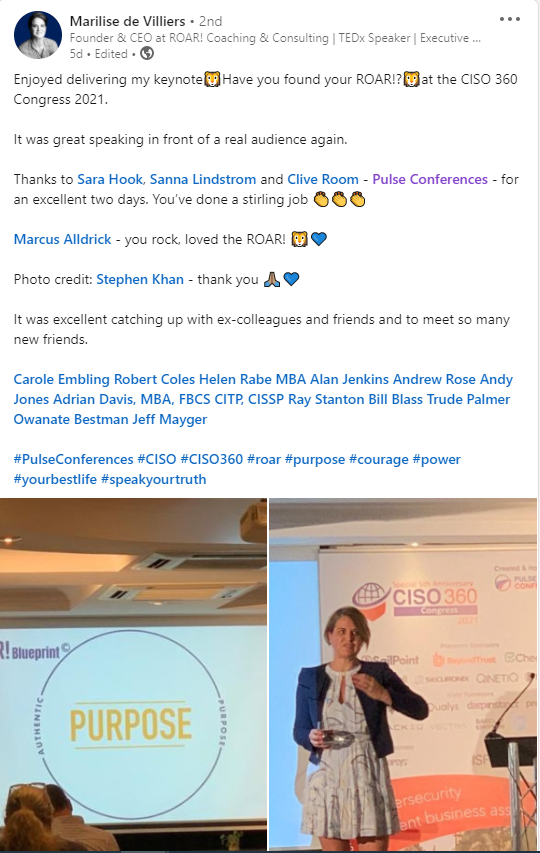
“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys
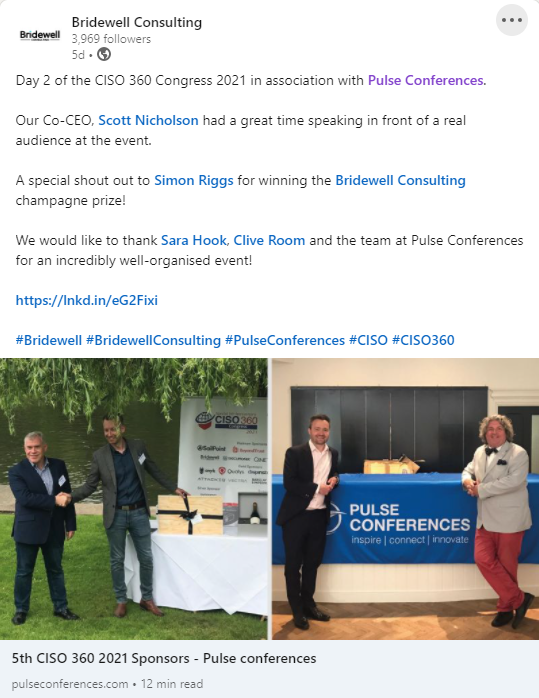
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World
“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
 “A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint
“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra
“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica
“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“
Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter
 “CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint
“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018