
Registration is now closed
Health and Safety MeasuresThank you to everyone who joined Pulse in November 2021 for the third edition of this ground-breaking reciprocal discussion between Board Members, CISO/CSO and C-Suite!
• question a real Board of Directors
• connect with peers to benchmark cyber risk strategy
Talk to the Board!
A rare opportunity to ask the questions you would ideally like to ask your own Board – but with no consequences!
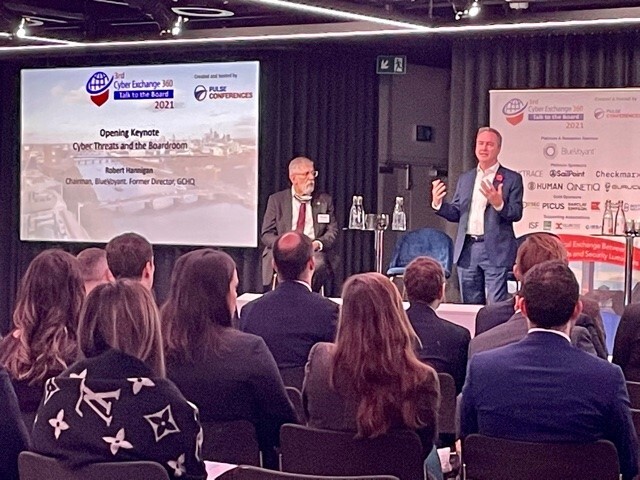
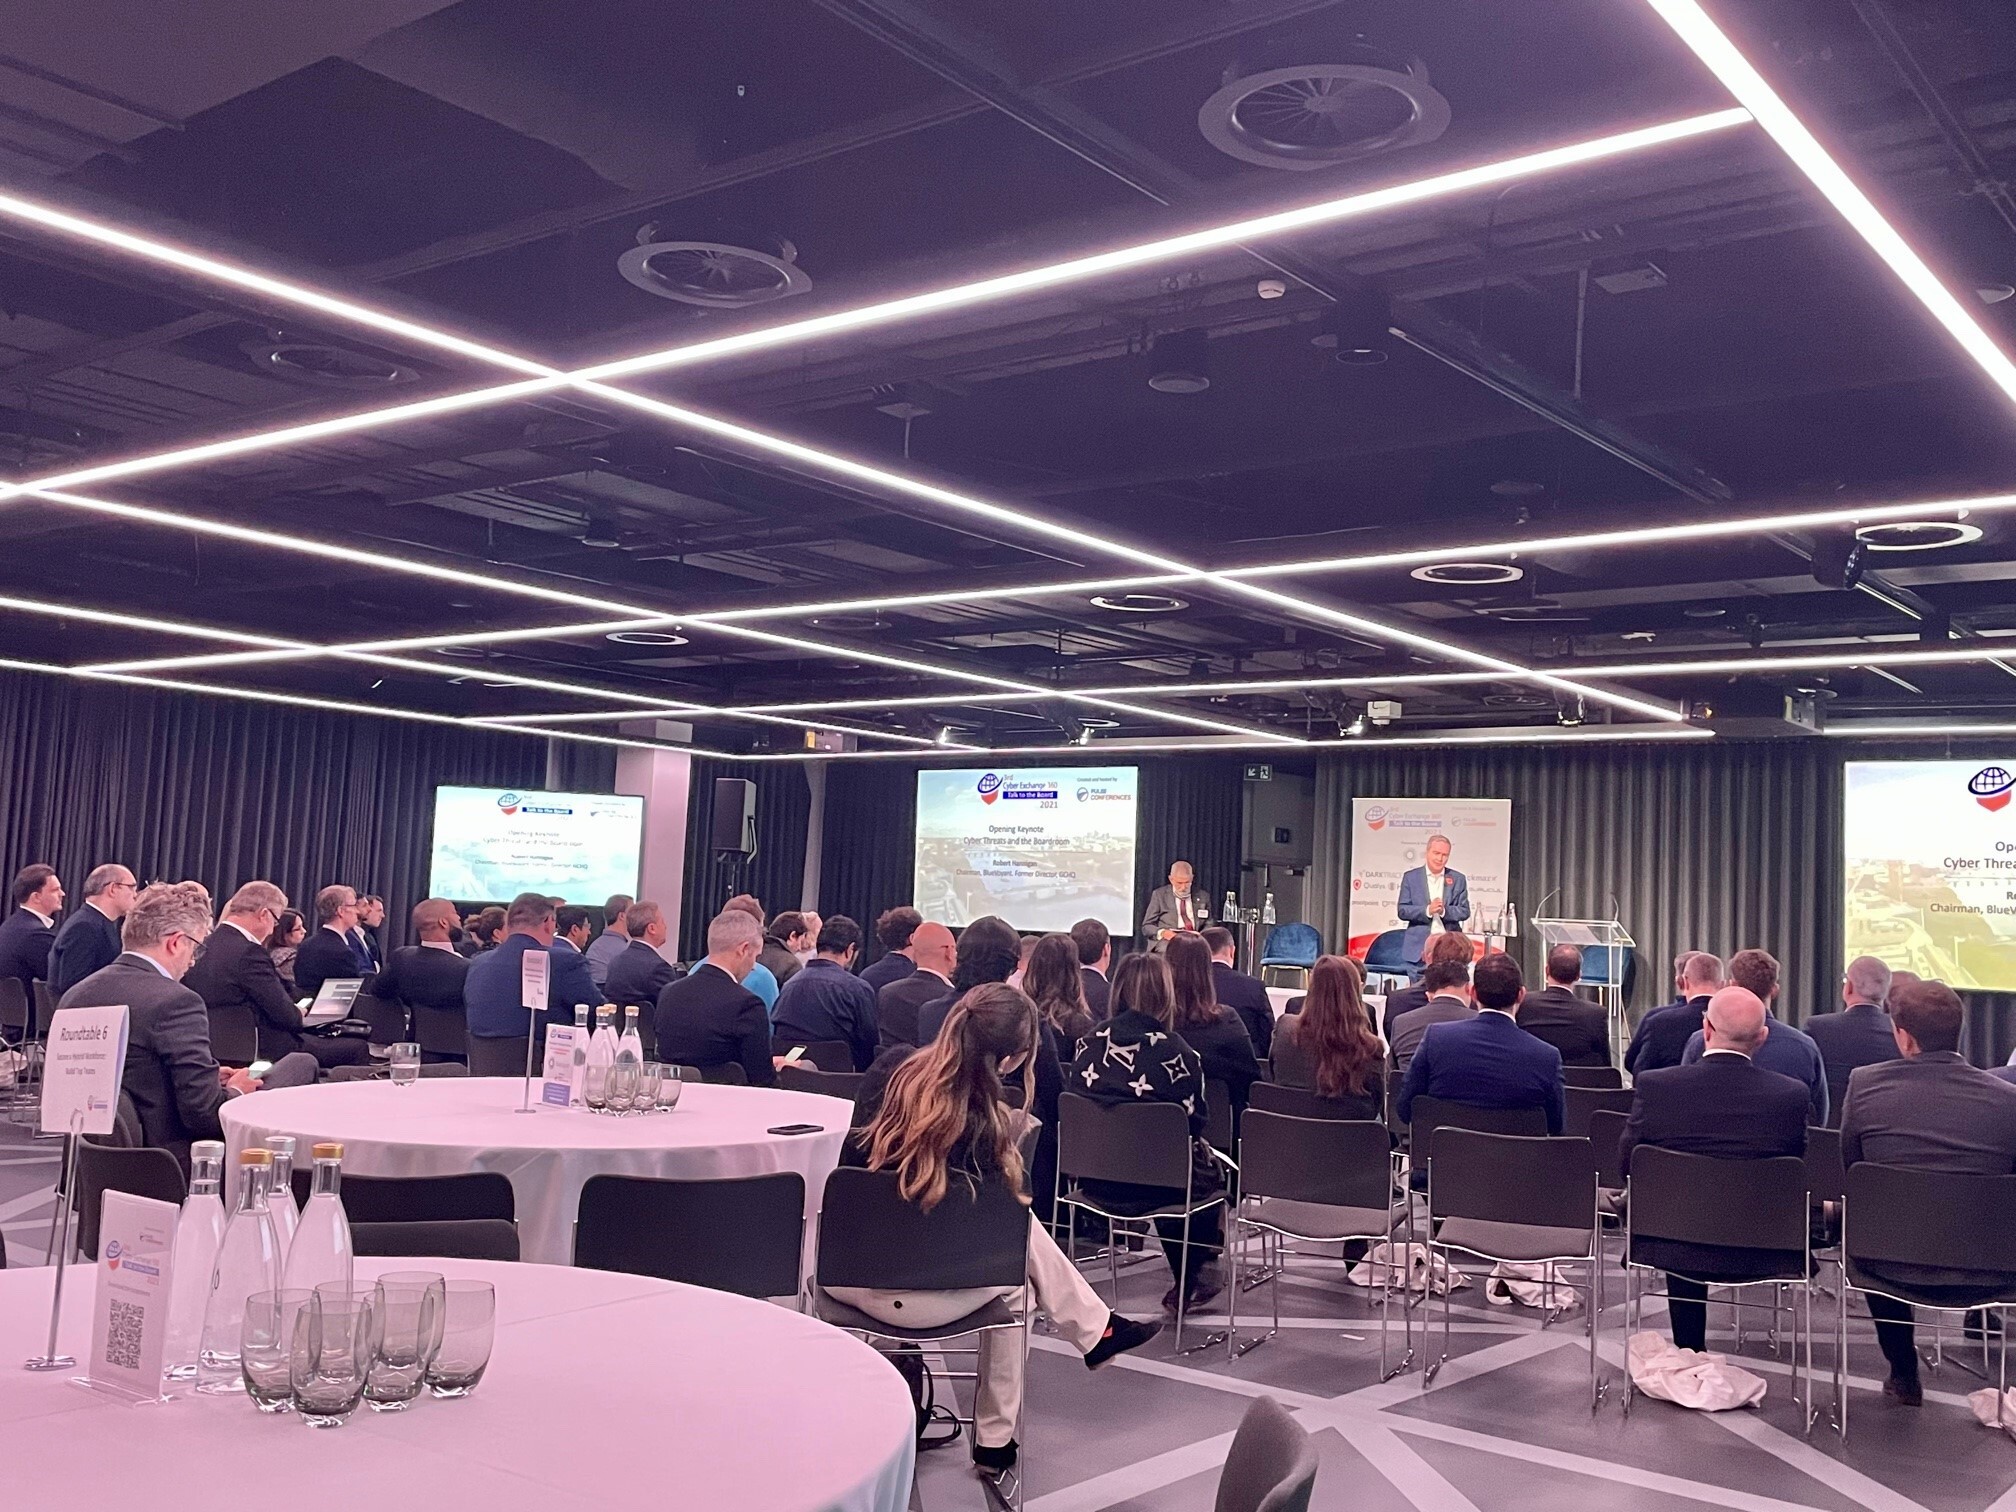
We were honoured that the 2021 conference was opened by Robert Hannigan, Chairman of BlueVoyant, the former Director of GCHQ who shared his experiences on Cyber Threats and the Boardroom, Pulse Conferences was delighted to welcome participants to the 3rd Cyber Exchange: Talk to the Board at the Science Museum London.
What are the skills, behaviours and mind set required to lead the security agenda in a pressured, complex and competing business environment and how to create a culture where cybersecurity is considered central to the way companies think and behave? Where does cybersecurity sit in the list of highest Board risks and opportunities? How has this changed in the past year and what are new expectations of CISOs and security leaders?
These were just some of the questions that were tackled in this open exchange with Board Directors from large organisations in a business agenda that included –
- People, Process, Technology through Transformation & Change
- Resilience & Preparedness to Respond to Any Crisis
- Communication, Engagement & Influence
- Sustainable Business, Governance & Employee Well-Being
This ultimate sound-boarding conference gave today’s CISOs, CSOs and cybersecurity chiefs the opportunity to interact directly with a panel of Enterprise Board Directors. Pulse was delighted to form a super panel of Enterprise Board Directors and Non-Executive Directors, our Board, for a rare and reciprocal exchange with security chiefs. This was a golden opportunity for Board directors and CISOs and CSOs to take stock of where they are on the journey to strengthen resilience and accelerate digital transformation amidst an everchanging landscape and threat horizon. Given that the past 18 months saw many risk registers blown out of the water, the 2021 agenda promises to be an unforgettable discussion!
Our ‘2021 Fantasy Board’ of real directors covering various sectors and roles included:
- Simon Brickles, Chairman, Gibraltar Stock Exchange Group; Director Risk, Governance and Legal, Casino Group in the UK
- Sharon Baylay, Chair, Restore plc; Remuneration & ESG Chair, Hyve plc; Chair, Eurowag plc. Former Board Positions at Microsoft and the BBC. Former Chair, Ted Baker plc.
- Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics
- Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey
- Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)
Testimonials and Key Takeaways from Cyber Exchange 360: Talk to the Board
Co-chairpersons
“Collaboration is the key takeaway. It always has been, but it is about communication, cooperation and collaboration. This underpins so much of what we do. There were some great learnings from the morning sessions – many of the topics are not at board level, but they contribute towards depicting the risk to the board or the executive team, the audit committee, and so on. I love being chairman and thrive on it because being at Pulse is a constant learning experience. Also it’s a great team to work with. Pulse events bring everybody together in a very collaborative environment, the practitioners, the advisors, the consultants, and the vendors, among whom we have some wonderful sponsors. It’s all about knowledge sharing. Don’t get seduced by the sexy bits of security. Never forget the fundamentals, because without them you are insecure.”
Marcus Alldrick, CISO Luminary (Conference Chairperson)
“A Pulse Talk to the Board conference is so managed that there is a strong feeling of intimacy and frankness. This brings the best out if everyone with sage advice for both sides .The Board speakers were open about the challenges they face from all quarters. One former Board member (Sharon) felt that to be successful he/she need to be curious and interested. To listen carefully and ask questions. The CISO need to be concrete in explaining the situation in business terms and offer solutions not just problems. As a co-chairman of the Talk to Board afternoon session I was struck by the openness on both sides. It takes two sides to make a successful team, regular informal contact is an essential part of it.. both with the executive board and NED s. The variety of experience by the Board speakers made for a lively and fulfilling session.
Lady Olga Maitland, President, Defence and Security Forum (Talk to the Board Co-Chairperson)
Board Directors
“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them to champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.”
Jeremy Schwartz
“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.” Graham Joscelyne
“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics”
Deborah Exell
As a CISO why attend
- Talk frankly and test questions that you would like to ask of your your own Board!
- Gain context! A helicopter view on where cybersecurity sits and Board priorities
- Re-energise your approach to driving change and leading teams to influence culture
- Hear about new expectations of security from Board Directors of large companies
- Increase awareness on how to maintain integrity of operations during a crisis
- Understand more about Board Directors’ responsibilities and liabilities
- Speak to the Board in a way that makes them understand your pain points
- Compare key metrics with CISO peers in the morning sessions and hear proven ways to quantify and communicate with the Board during the afternoon Board Directors Panel!
As a Board Director why attend
- Gain insights about how CISOs as a group think, feel and interact with their Board to better understand how you can best support your own teams to develop secure cultures
- Meet CISOs from across sectors and reconfirm the right questions to ask their own teams
- Improve understanding of the latest cybersecurity threat horizon, CISO pain points, security culture and workforce challenges
2021 Agenda at a Glance
Morning – Cyber Exchange 360
Following the Opening Keynote by Robert Hannigan, Chairman, BlueVoyant. Former Director, GCHQ, participate in immersive case studies, fireside chats, keynotes: Led by, with and for CISOs Benchmark strategies and be inspired by case studies and discussions with experienced CISOs, CSOs and other c-level executives on areas relating to cybersecurity and cyber risk.
Afternoon – Talk to the Board
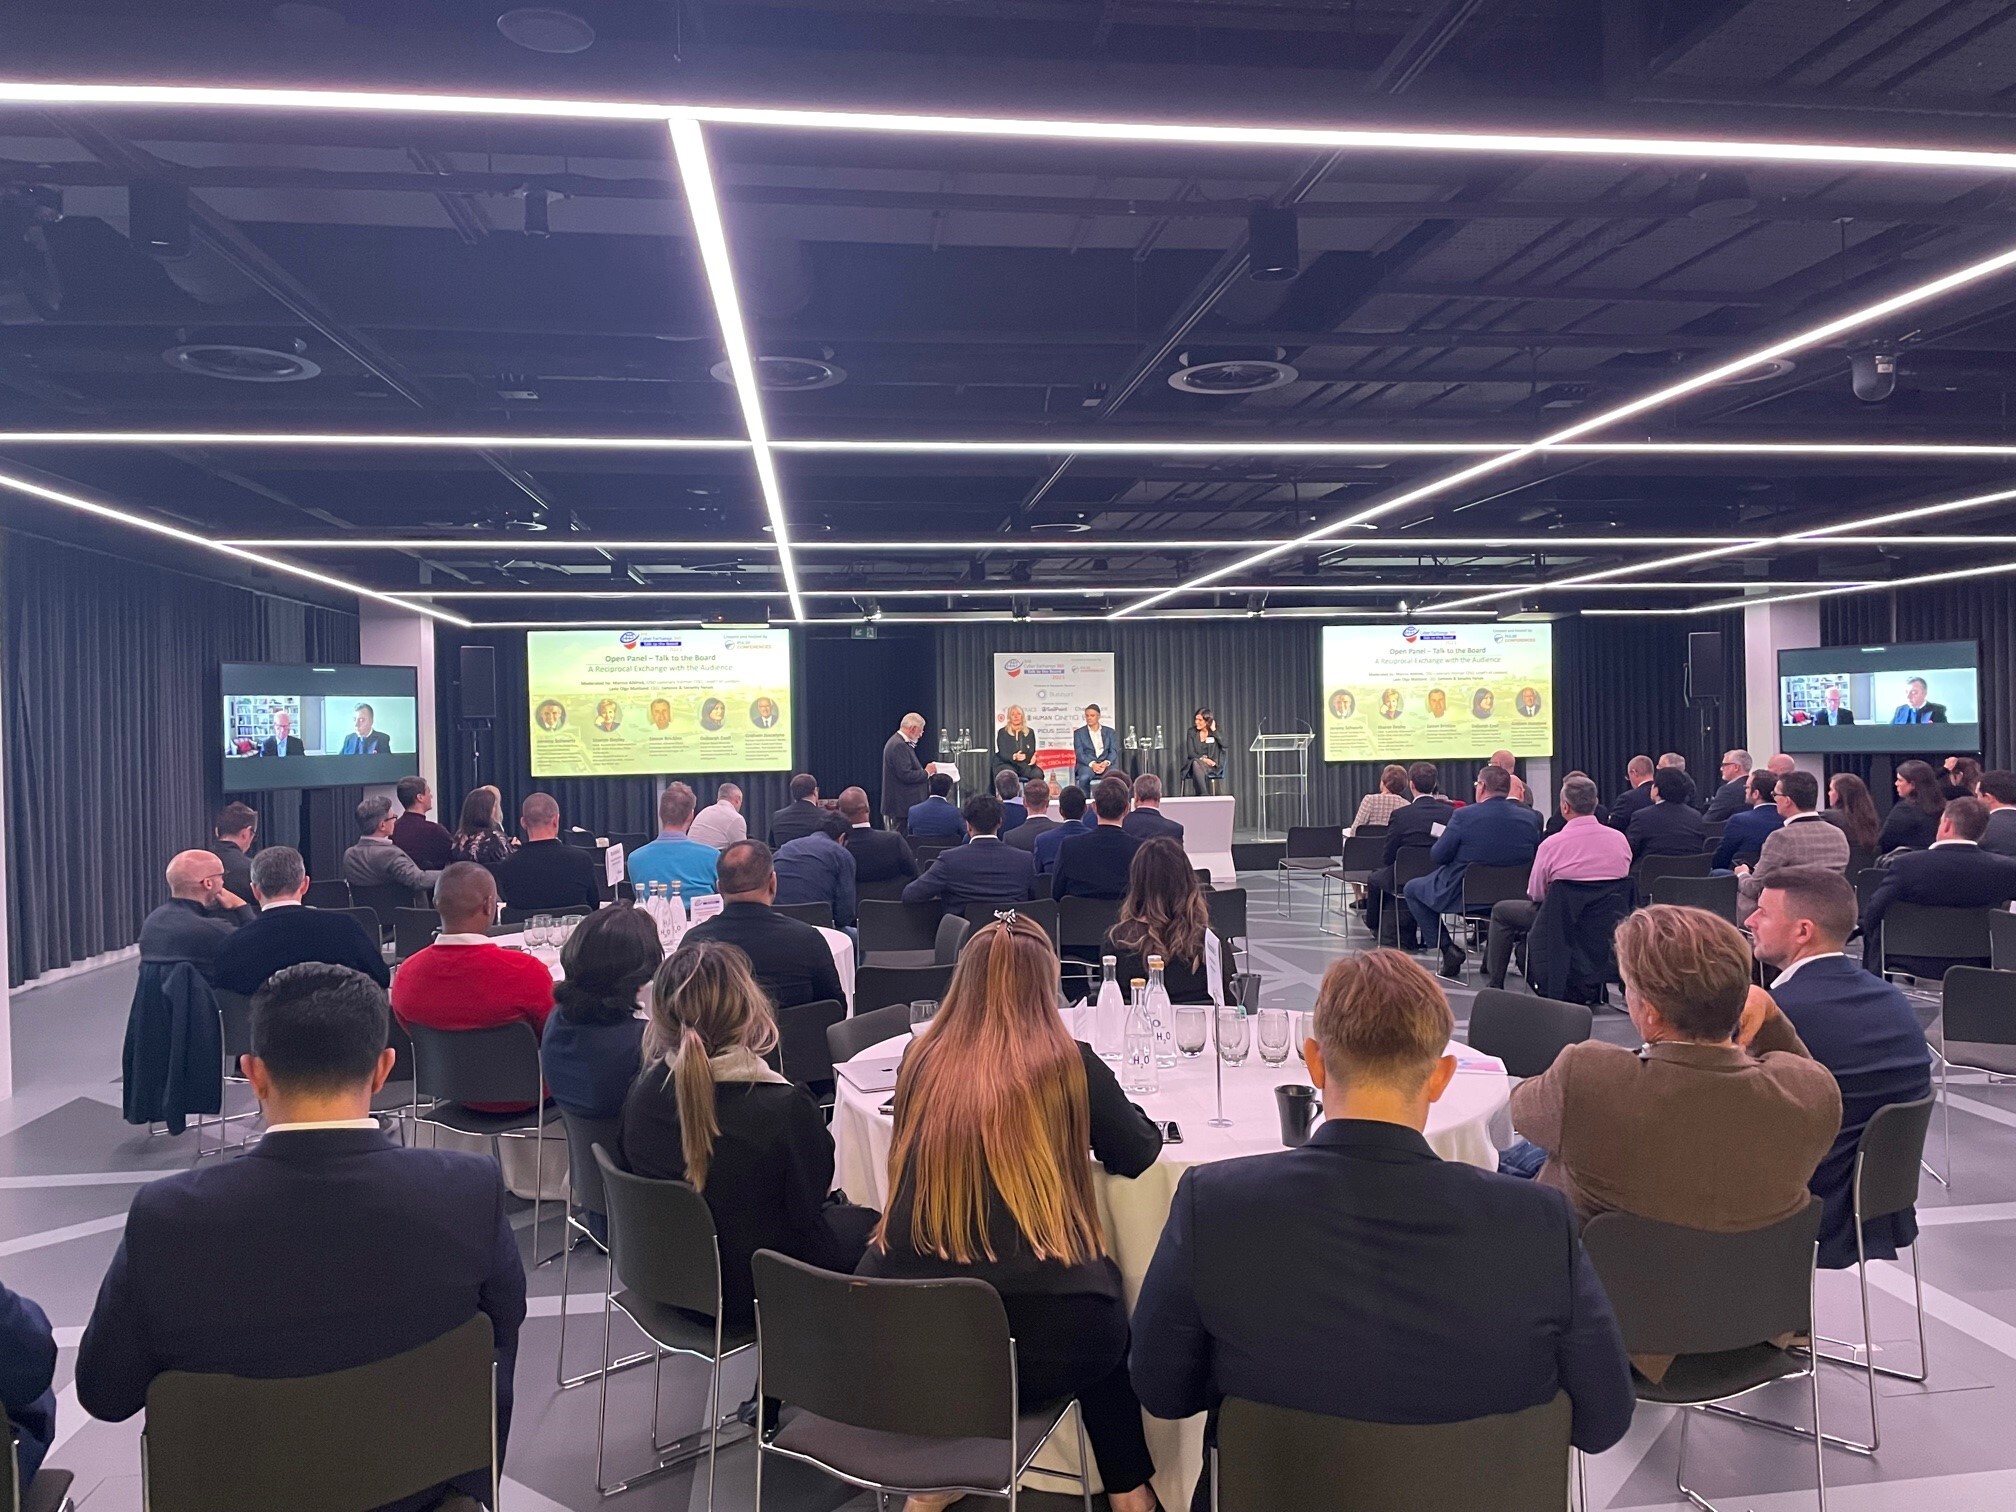
Reciprocal exchange: A Panel of Board Directors with CISOs! Attending CISOs are invited to ‘talk to the board’ and ask the questions they would ideally like to ask their own Board of directors if they had the chance – and without any consequences! Board Executives spanning Chairman, CEO, CFO, CIO, CMO, HR roles from well-known organisations across industry sectors will share their views and predictions on business risk, technology trends, resilience strategies and emerging expectations.
Evening – Reception at Wonderlab. Kindly Sponsored by BlueVoyant
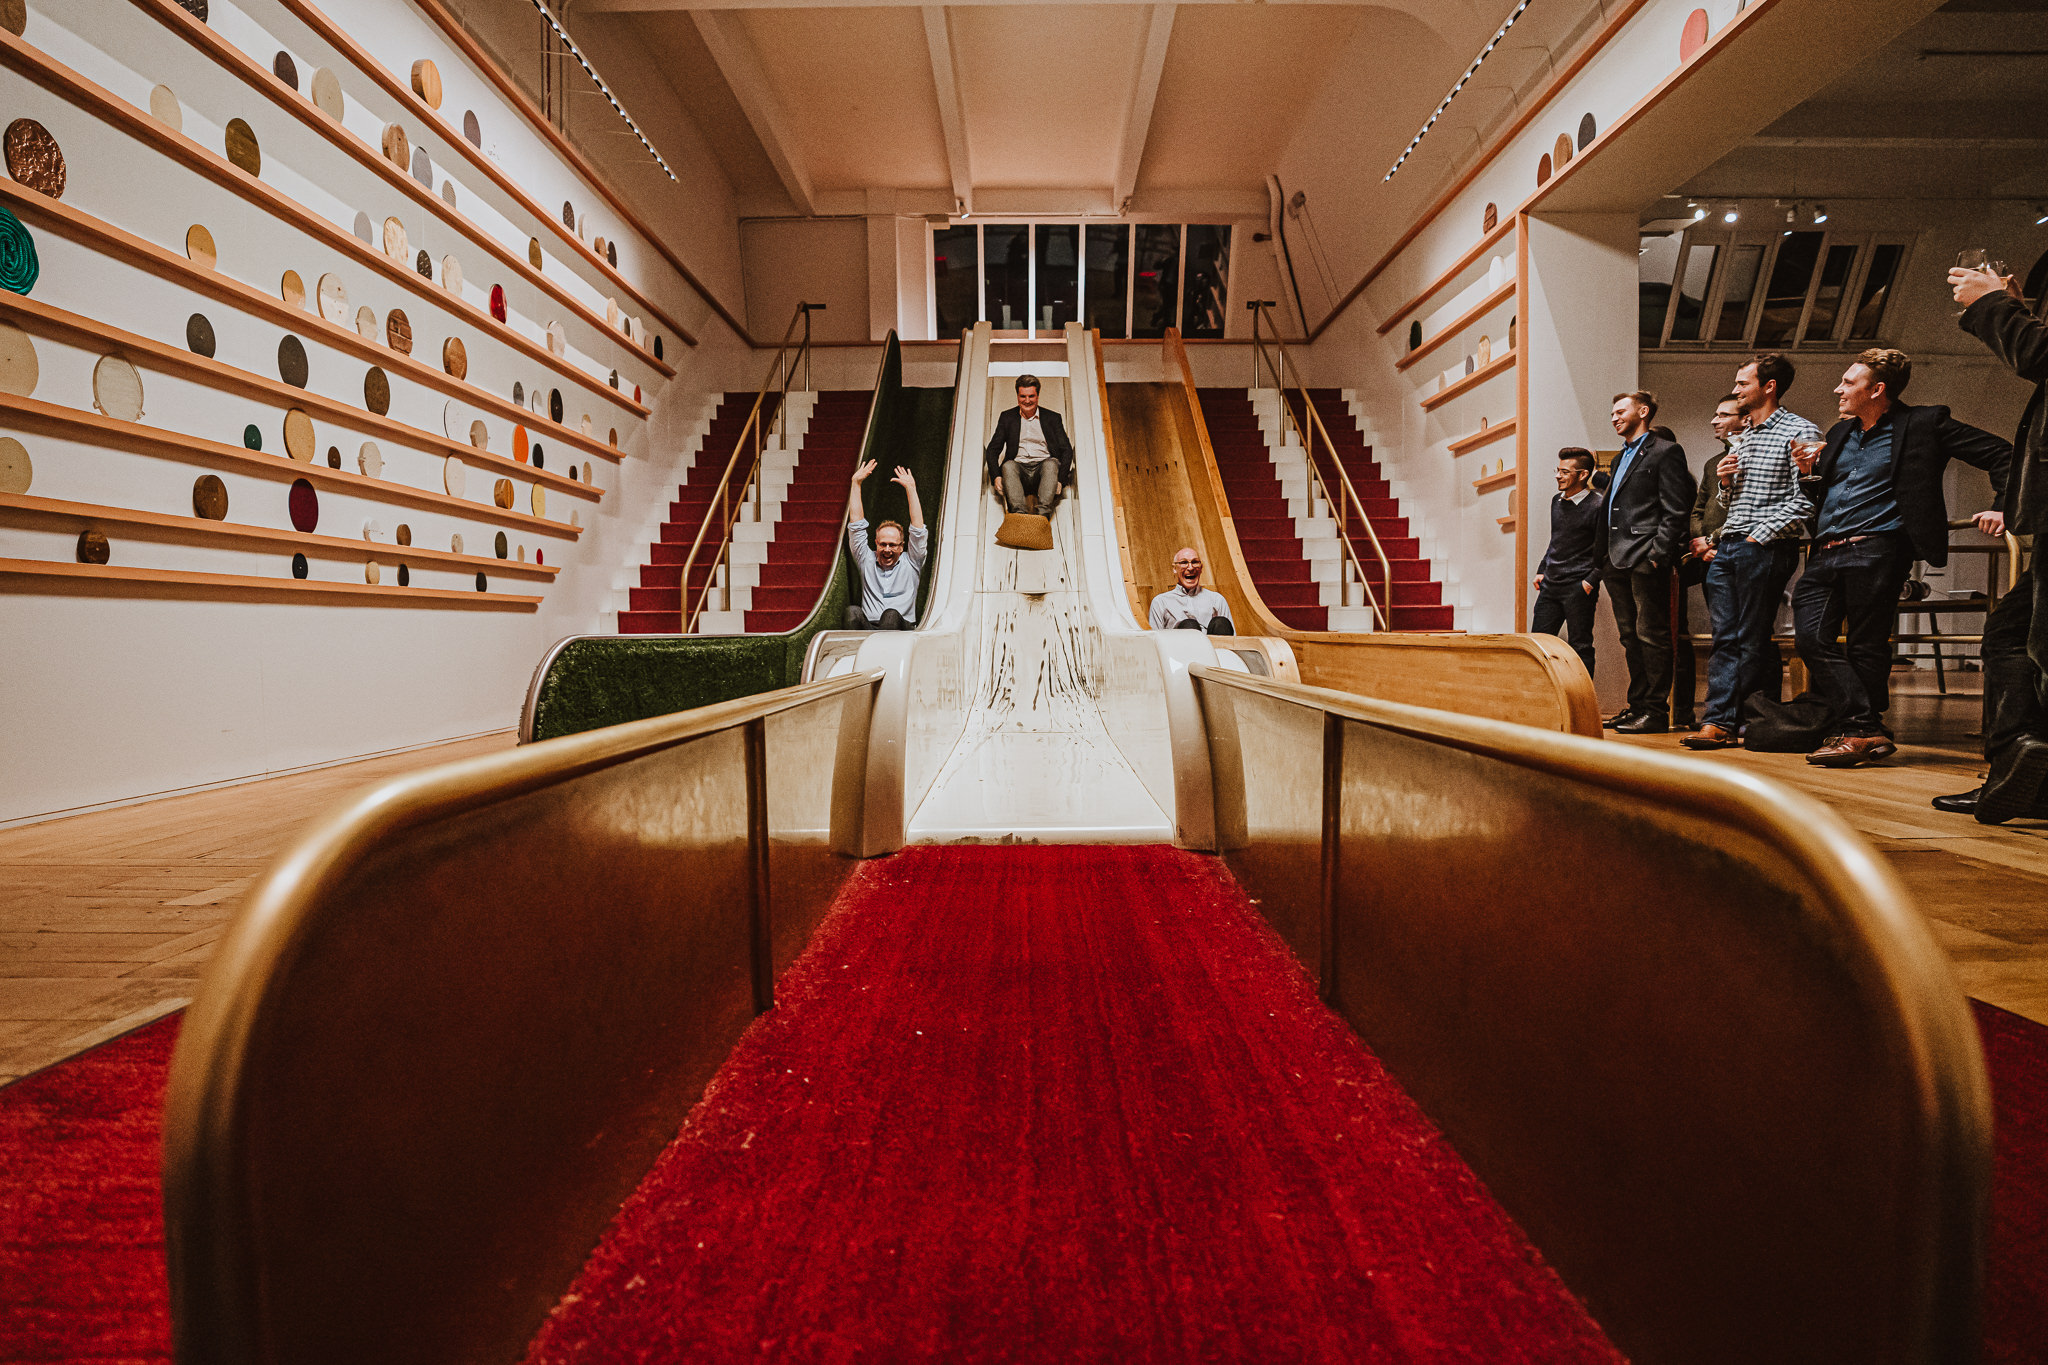
To conclude the day, join us for drinks, canapés and networking at the Talk to the Board evening reception on 10 November from 17:00-20:00. This is a chance to meet your peers, talk to the Board Directors enjoy the delights and exhibits in this inspiring and immersive space! Science Museum ‘Explainers’ will be on hand to explain how the exhibits work!
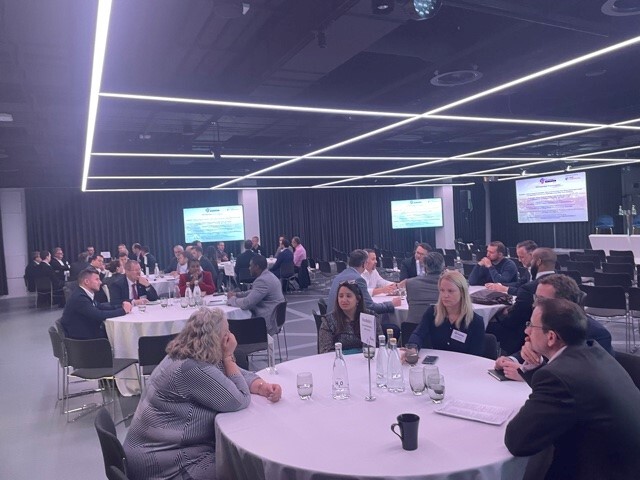
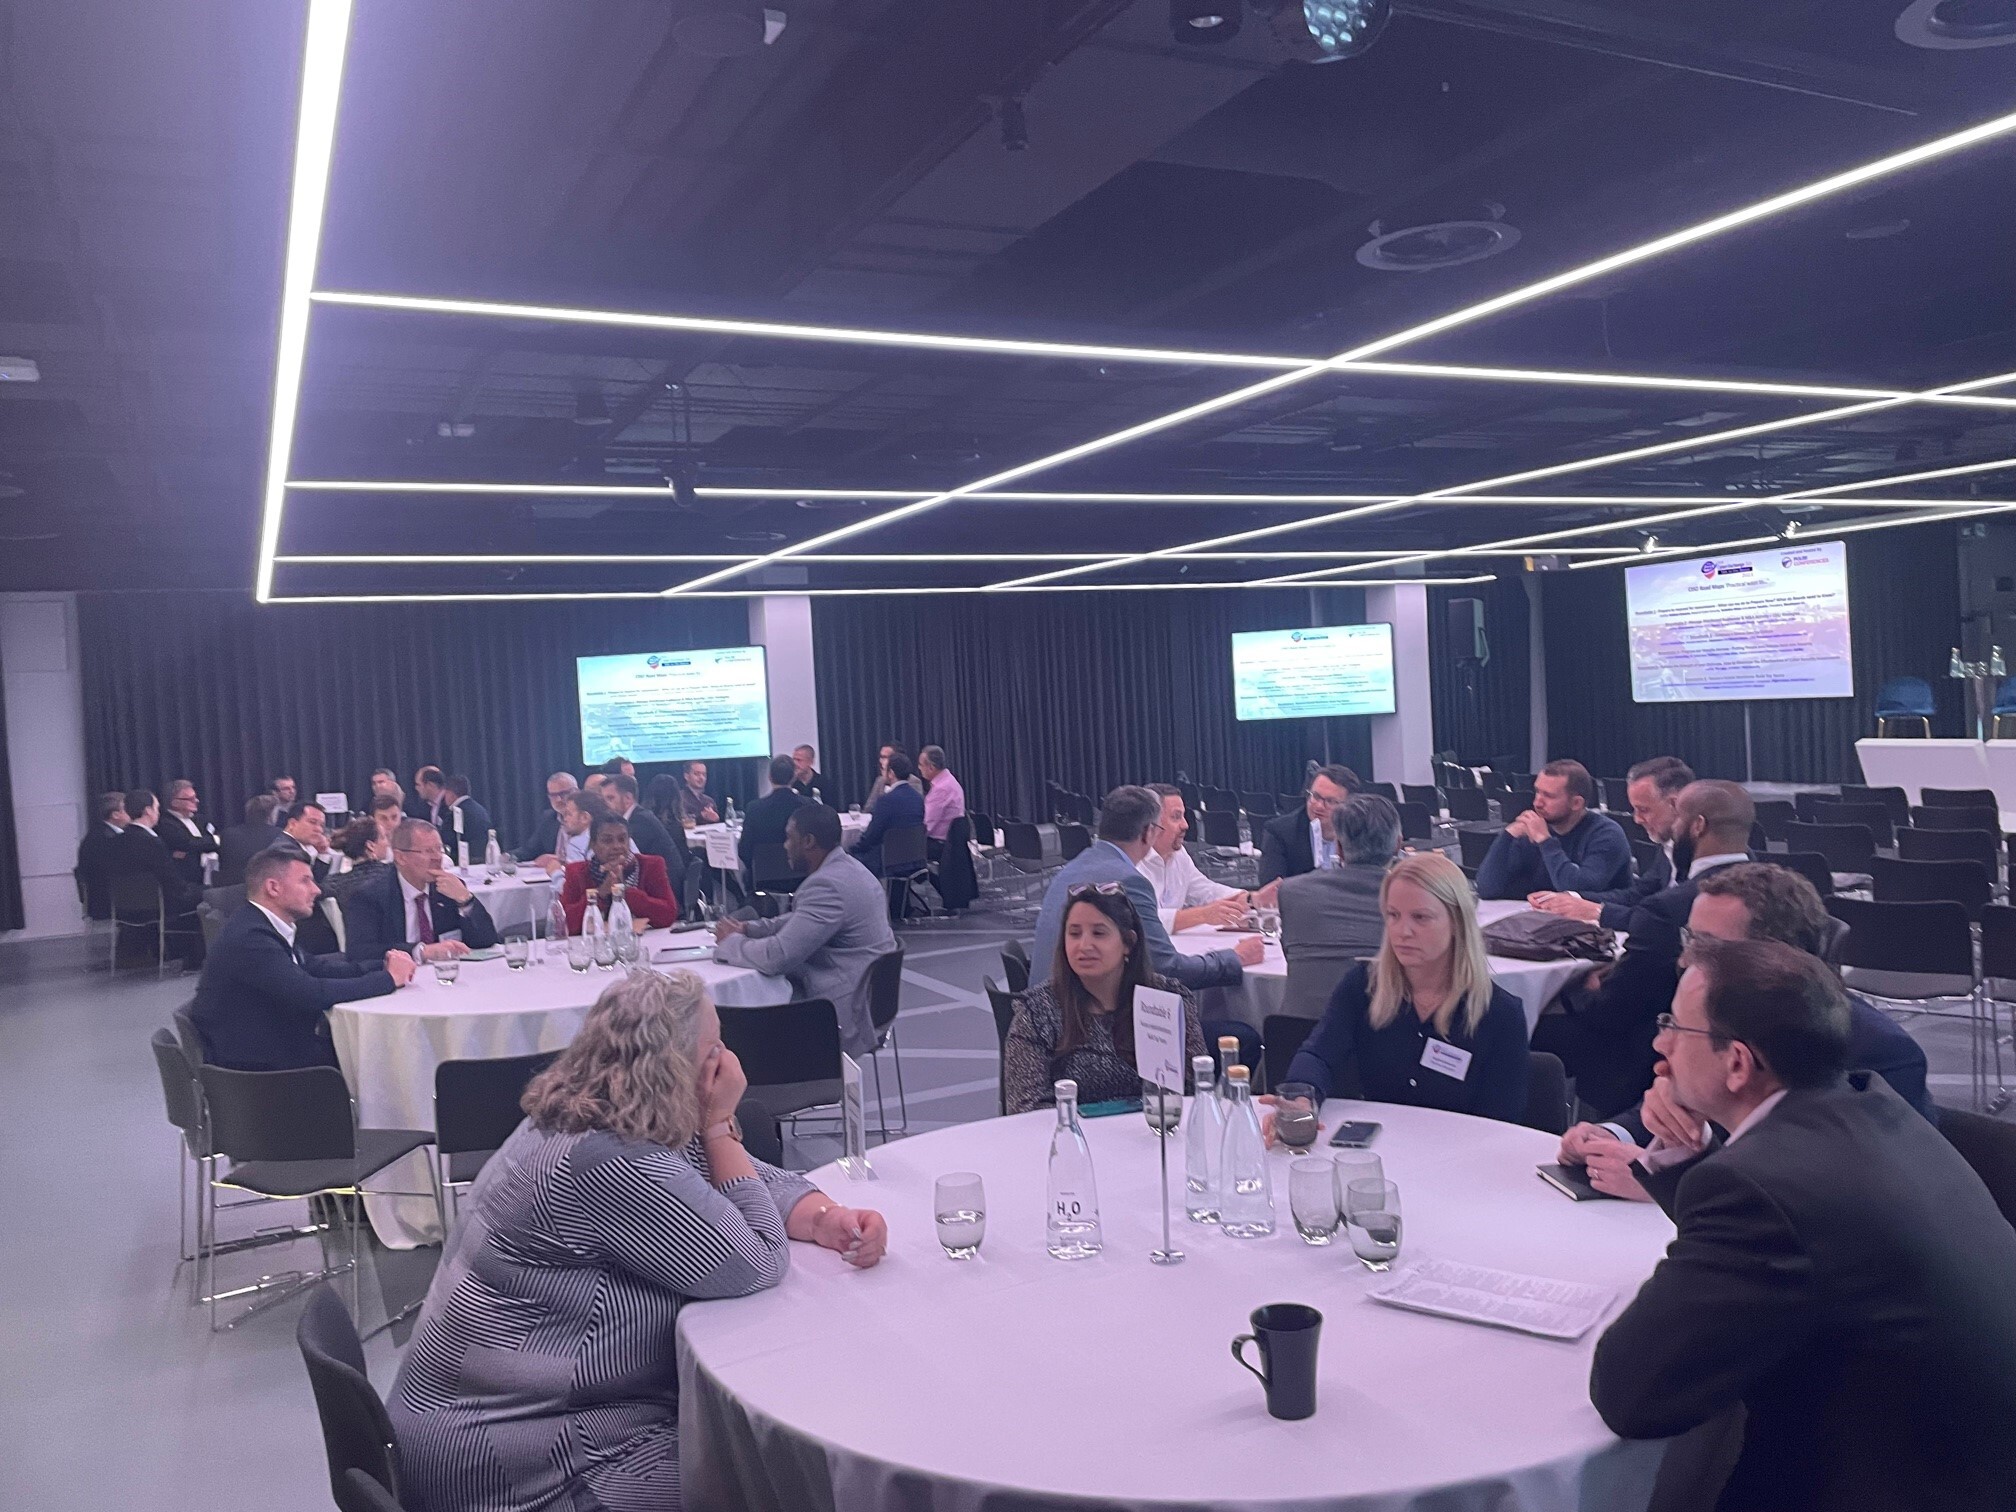
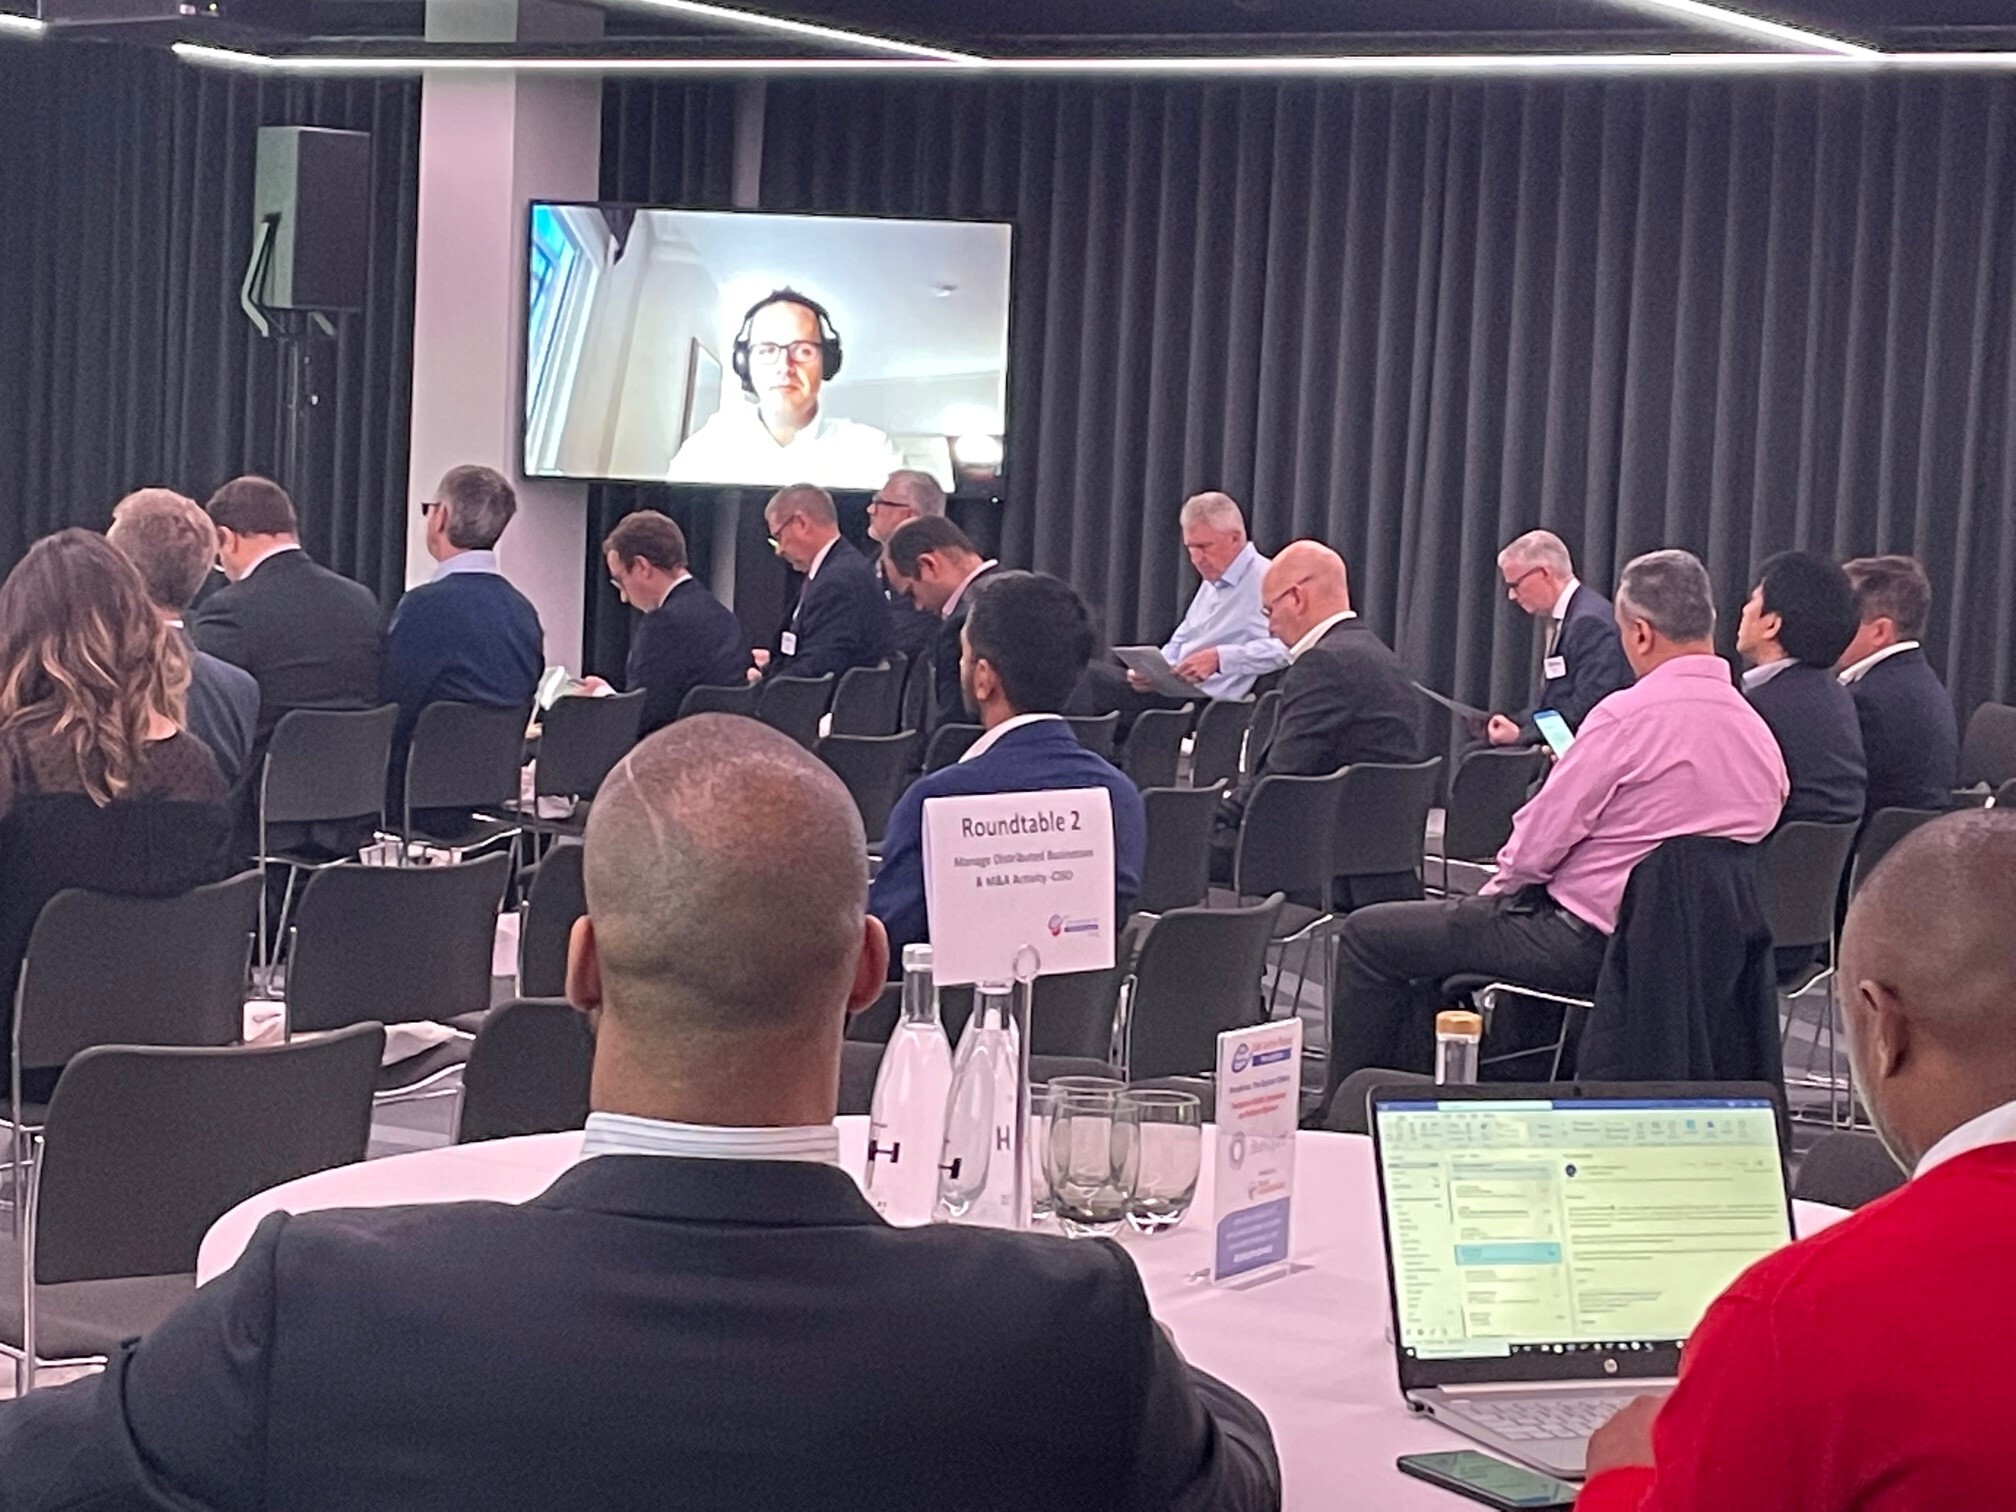
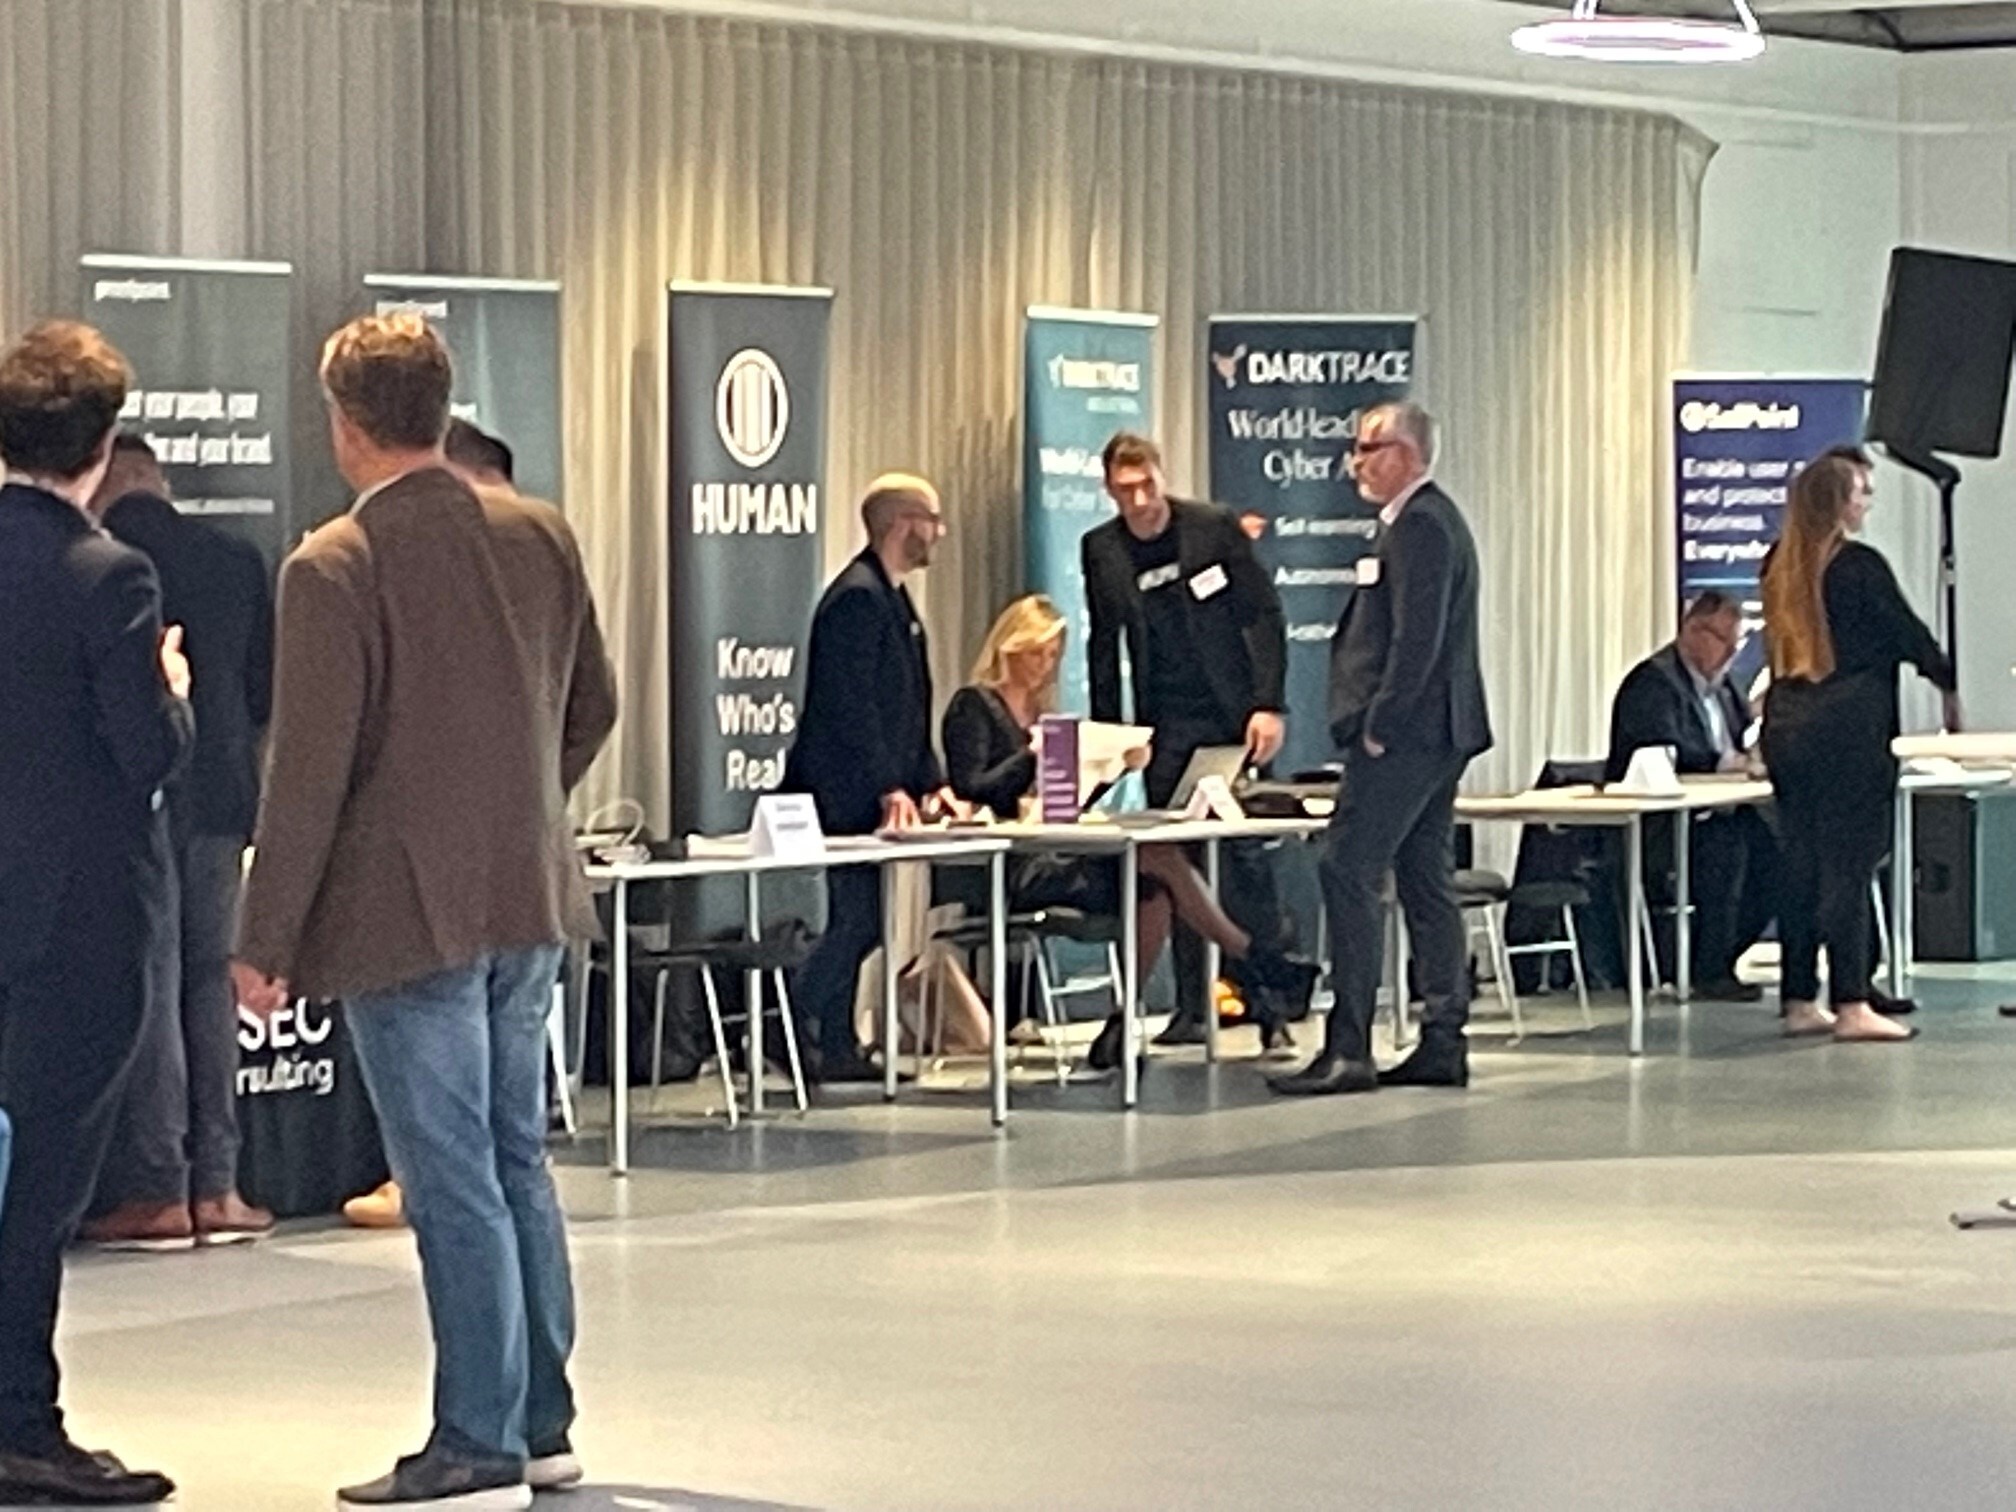
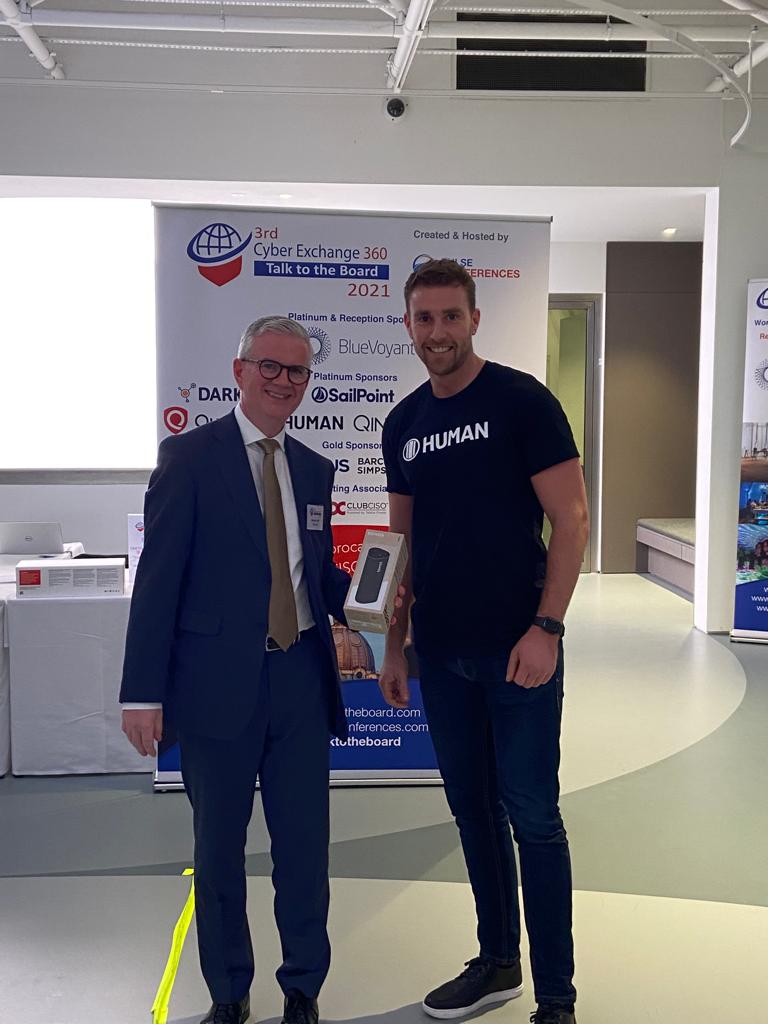
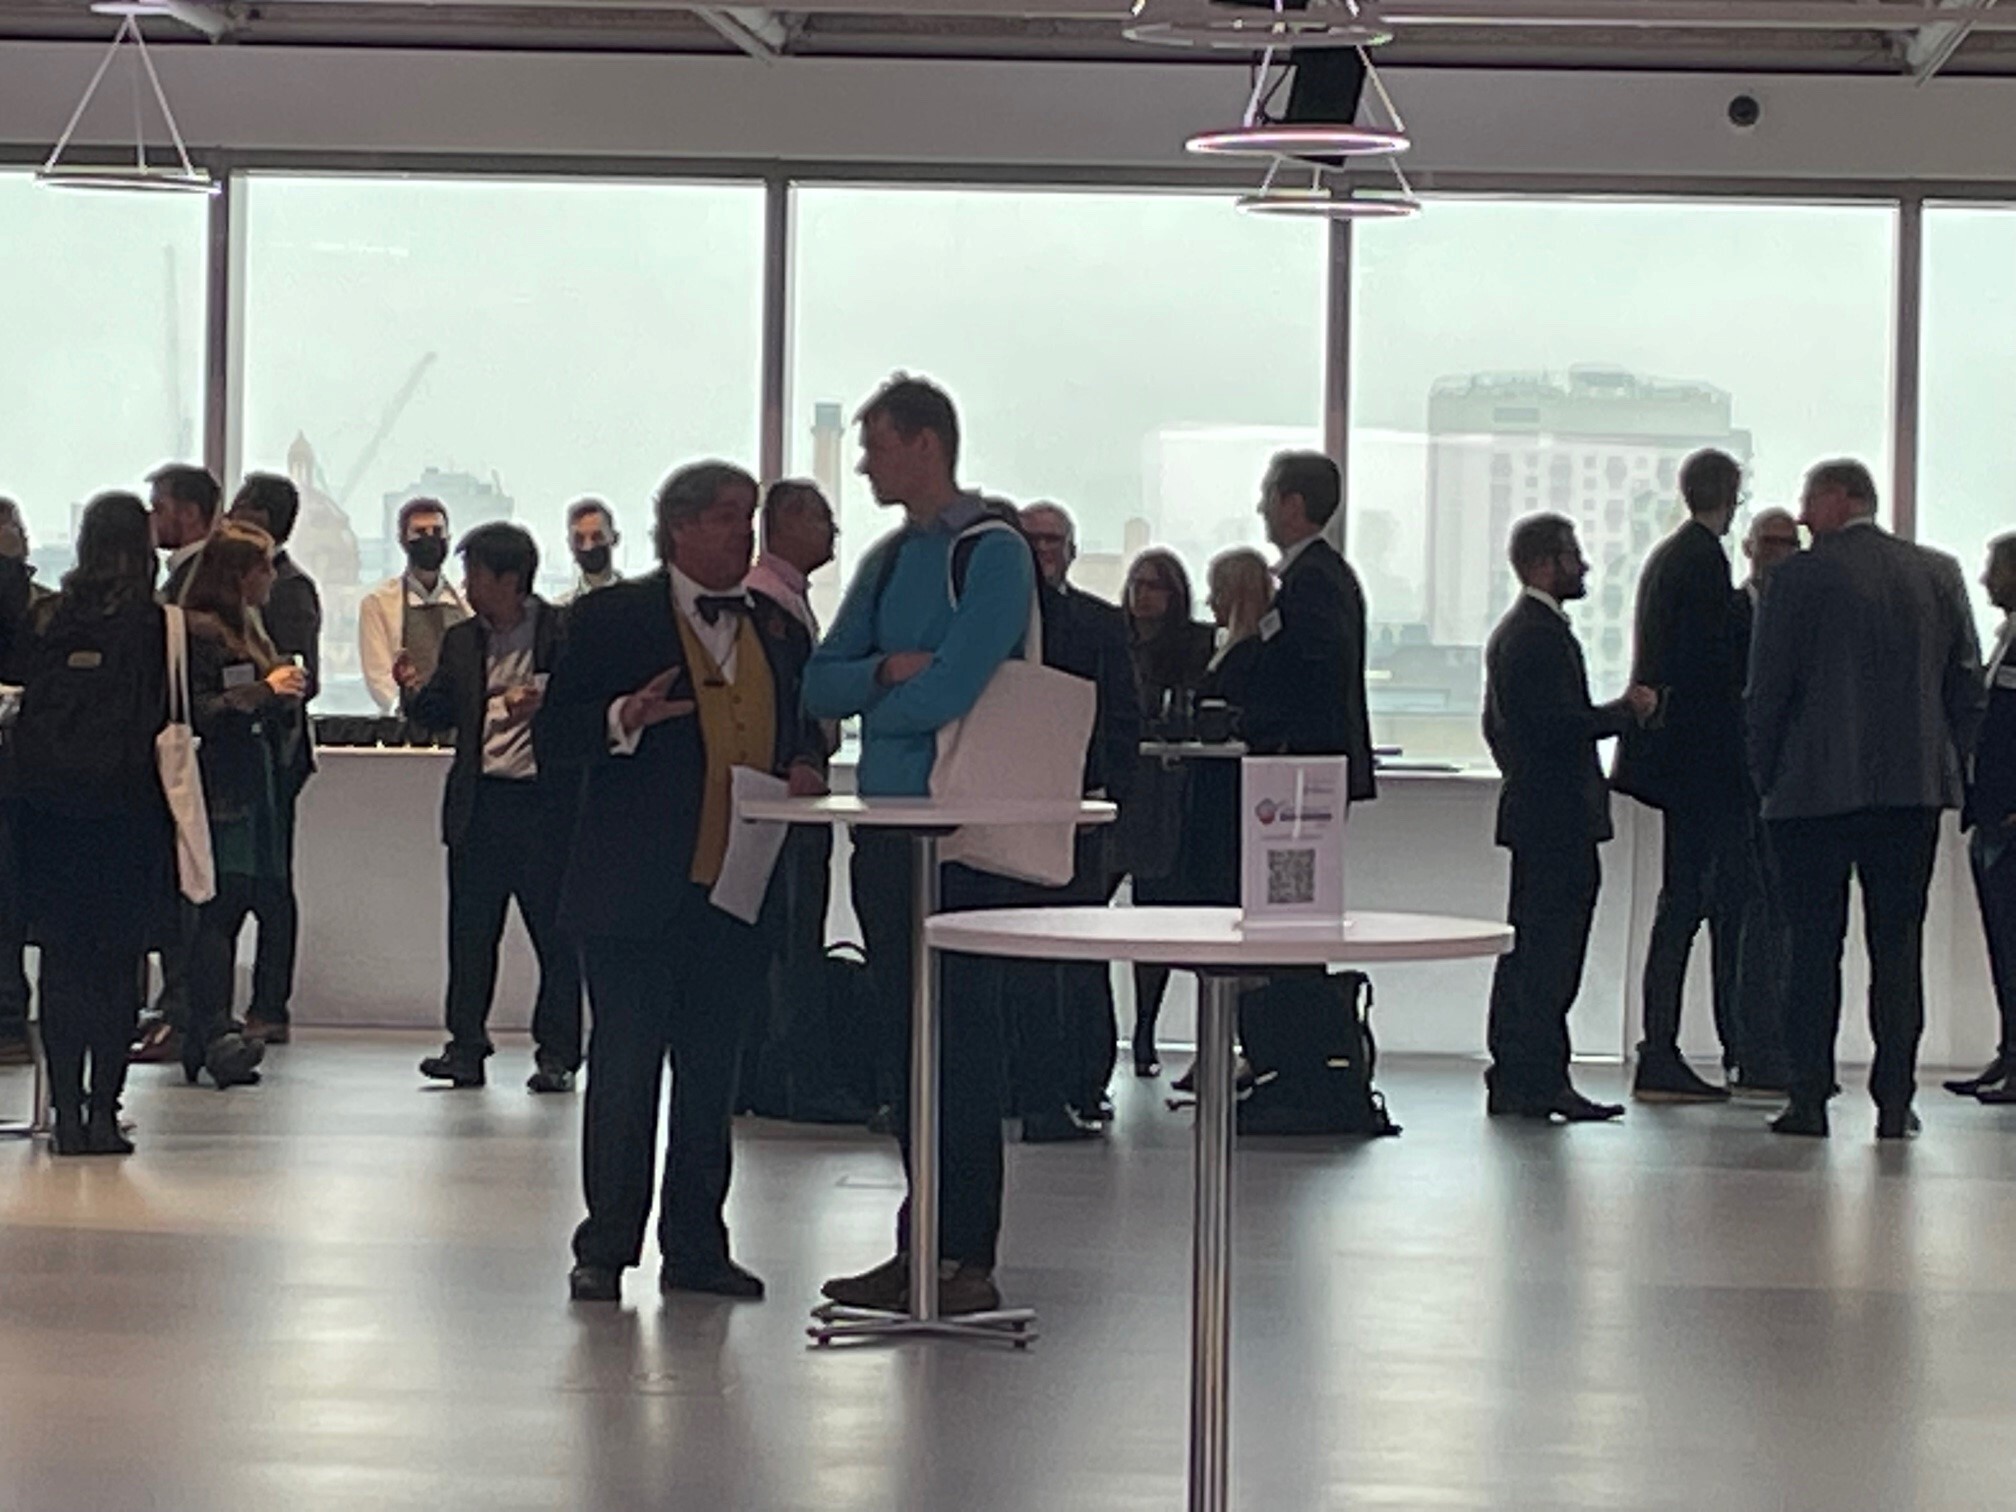
View images from the recent 2021 Cyber Exchange 360: Talk to the Board Conference!
Welcome to our Sponsors
Platinum Sponsor and Sponsor of Networking in Wonderlab, Science Museum
Platinum Sponsor 2022
Gold Sponsors
Welcome, you are registering for an Advisory pass for
3rd Cyber Exchange 360 – Talk to the Board, 10 November 2021
With thanks to our sponsors
Sponsors

Sponsorship Opportunities
2|Sec – The Gold Standard In Penetration Testing
Who attends
By Designation
Participants will include CISOs and CSOs in addition to:
- Chairperson
- CEO
- Non-Executive Directors, Board Member, Audit & Risk Committee Member
- CFO, CRO, GC, COO, CTO, CIO, CMO, HR
- Chief Information Security Officer
- Director of Cybersecurity / Head of Cyber Threat Intelligence
- Head of Governance
- Head of Innovation
- Director of Digital Risk
- Chief Data Officer
- Chief Privacy Officer
- Heads of Corporate Security/Resilience
By Sector
All private and public sectors are welcome to attend.
Speakers for the 3rd Cyber Exchange 360: Talk to the Board 2021
Opening Keynote by
Chaired by
The Board Directors Panel
The Speaker Panel includes
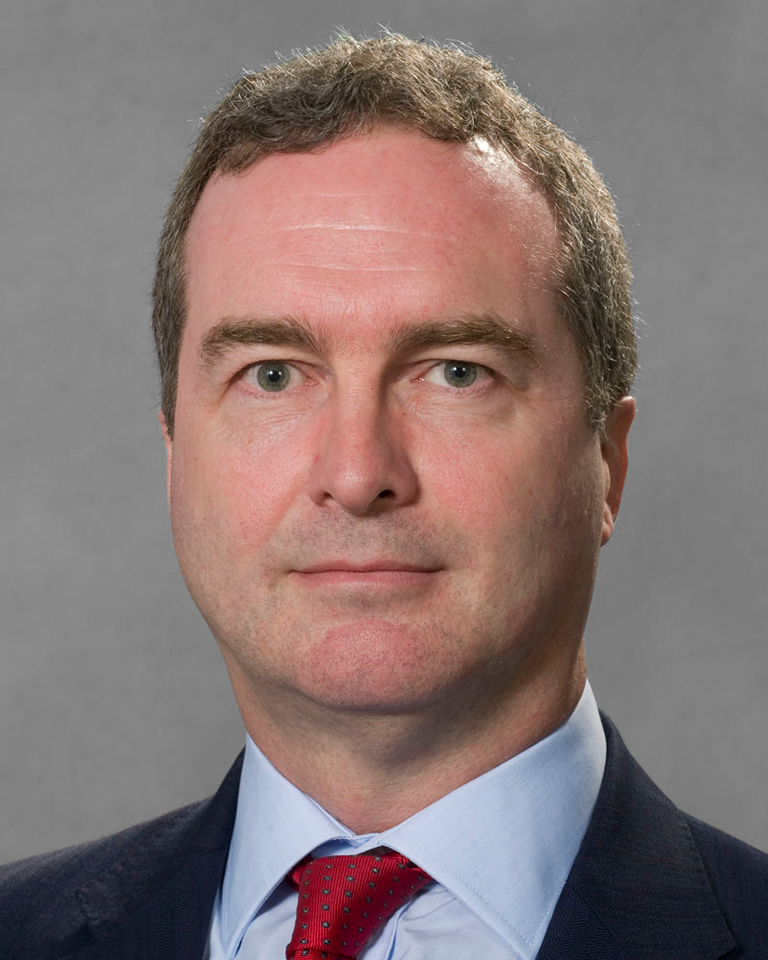
Robert Hannigan
Chairman, BlueVoyant. Former Director, GCHQ
Robert Hannigan is a renowned cybersecurity specialist with an extensive background in public service. He currently serves as Director of BlueVoyant, and as an adviser to a number of international companies such as McKinsey & Company, Hiscox and Immersive Labs. During his 20 years of public service, Robert served as Director of the Government Communications Headquarters (GCHQ), the UK’s largest intelligence and security agency, where he led the creation of the UK’s National Cybersecurity Centre (NCSC). Prior to that, he worked as principal adviser to Prime Minister Tony Blair on the Northern Ireland peace process.
Robert has been deeply involved in shaping UK Government’s approach to national cybersecurity, from the creation of the first UK Cyber Security Strategy for Prime Minister Gordon Brown, to framing the coalition Government’s ambition of making the UK “the safest place to live and do business online” against a rising tide of cyber security incidents. He has often shared his view that governments cannot do this alone but only in partnership with industry. Having studied classics at the University of Oxford, Robert continued his education at Heythrop College, University of London. After an early career in the private sector, Robert was appointed as Deputy Director of Communications for the Northern Ireland Office in 2000, progressing to Director-General, Political, in 2005. Robert had a role in the Northern Ireland peace process and was singled out in Tony Blair’s autobiography, where he is described as “a great young official who had taken over as the main Number 10 person [on Northern Ireland]”.
In 2007, Robert was appointed as the Prime Minister’s Security Adviser, as well as the Head of Security, Intelligence and Resilience at the Cabinet Office, responsible for coordination between the intelligence services and government. Notably, Robert led the review into the loss of the nation’s child benefit data, a major data breach incident; the subsequent report is informally called the “Hannigan Report”. Robert moved to the Foreign and Commonwealth Office as the Director-General of Defence and Intelligence in 2010, where he served for four years. In 2014, Robert was appointed as the Director of the GCHQ where his major external change to the organisation during his tenure was the creation of the NCSC as an operational part of GCHQ. At the opening of NCSC’s London headquarters in 2017, Robert described the historical line between Bletchley Park and the NCSC and set out the challenge of cyber security at a national level. In February 2017, Hannigan was appointed to the UK Government’s new Defence Innovation Advisory Panel.
Following his resignation as Director of GCHQ in 2017, Robert was widely credited with bringing greater transparency to GCHQ, not least through the use of cryptographic puzzles; his Christmas card puzzle in 2015 inspired some 600,000 attempts worldwide to solve it. This led to the publication of The GCHQ Puzzle Book in 2016, which became a Christmas best-seller and raised £240k for the Heads Together mental health charities by April 2017.
Describing his move to the private sector, Robert says: “I felt it was a good time to go into cybersecurity – I spent over 20 years in government setting up the NCSC and GCHQ. I felt there was a big demand for what I could accomplish in the private sector. I want to make the UK the safest place to do business online and believe that governments cannot do it alone. The cybersecurity industry has the resources and skills and knows where attacks are happening.” Robert has previously stated that “however much [large US technology companies] may dislike it, they have become the command and control networks of choice for terrorists and criminals” and that GCHQ and its sister agencies “cannot tackle these challenges at scale without greater support from the private sector”, arguing that most Internet users “would be comfortable with a better and more sustainable relationship between the [intelligence] agencies and the tech companies”.
Over the years Robert has received numerous commendations. He was appointed Companion of the Order of St Michael and St George (CMG) in the 2013 New Year Honours for services to national security. He was made an Honorary Fellow of Wadham College, Oxford in 2015 and became a Fellow of the Institute of Engineering and Technology in 2017. Robert is also one of the few non-US citizens known to have been awarded the US National Intelligence Distinguished Public Service Medal. Currently Robert is a Distinguished Fellow of the Royal United Services Institute and a Senior Fellow of Harvard’s Belfer Center for Science and International Affairs. He also continues to serve as a Trustee at Bletchley Park Trust, home of British World War Two codebreaking, described by Robert as “the place where the digital world started from.”
Robert lives in the UK with his wife and has two children. He enjoys playing tennis and is a Chelsea F.C. supporter. With his wife being Irish, Robert also follows sports such as hurling and Irish football.
Describing his professional motives, Robert says he is “all about raising the baseline of security and helping people and companies to get better” and he is not interested in adopting “scare tactics” when speaking with journalists.
Robert has made frequent interventions on cyber security issues and can talk knowledgably about the following:
- Government cybersecurity strategy – how should a government organise itself and what is the correct intersection between government and industry?
- Geo-politics and nation state cyberthreats – including Russian, North Korea and China.
- Sophistication of cyber crime groups
- Privacy and regulation
- Mental health and neurodiversity
- The encryption debate – this is not necessarily a cybersecurity issue but relates to how law enforcement and the tech sector work together.
- Vulnerability in video conferencing apps such as Zoom – the privacy aspect of an app but not cybersecurity and public policy, i.e. what is useful and what safe.
- The cyber skills gap and the required “culture shift” within Boardrooms to meet cyber threats.
Marcus Alldrick
Former CISO, Lloyd’s of London. Currently Digital Risk Management, Security and Compliance Advisor
Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer.
In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.
Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc.
Simon Brickles
Chairman, Gibraltar Stock Exchange Group; Director Risk, Governance and Legal, Casino Group in the UK
Simon is currently Chairman of the Gibraltar Stock Exchange which is using blockchain technology to improve clearing and settlement. He also acts as General Counsel for a casino group based in the UK. He is a former Head of AIM at the London Stock Exchange and has served as a director on various stock exchange boards in Europe, including as CEO. In such roles he has had ultimate responsibility for rolling out new trading platforms for various types of securities. He has served as a NED on various listed and non-listed companies in Financial Services, Investor Relations and even Mining. Simon sits on various bodies in the Third Sector including the Norfolk Community Foundation. He is a former barrister and was educated at Cambridge University.
Sharon Baylay
Chair, Restore plc; Remuneration & ESG Chair, Hyve plc; Chair, Eurowag plc. Former Board Positions at Microsoft and the BBC. Former Chair, Ted Baker plc.
With a career in the tech sector that spans three decades, backed by extensive commercial and marketing expertise – most notably Board positions at Microsoft and the BBC – Sharon’s executive career has been dominated by roles that have helped transform consumer behaviour through the utilisation and implementation of technology. Sharon received the Microsoft Chairman’s Award for sustainable innovation from Bill Gates in 2004 and when she moved onto work for the BBC went straight onto the Executive Board as Director of Marketing, Communications and Audiences. In 2008 Sharon also joined the BBC Worldwide Board, and became Non-Exec Director of both Freesat and Digital UK. Since leaving the BBC, Sharon has developed an extensive portfolio career and currently holds several Non-Executive Directorships including Chair at Restore plc and Remuneration & ESG Chair at Hyve plc; Chair at Eurowag plc. Sharon was also formerly Chair of Ted Baker plc. Sharon also Chair’s private equity-backed businesses – Unique X Ltd – specialising in Cinema delivery software, Foundation SP Ltd – specialising in Digital Transformation consultancy services and DriveWorks Ltd, developer of DriveWorks design and automation software. Sharon was a finalist for the Dame Helen Alexander “NED to Watch” award in 2018, and previously a finalist for Chairman of the Year in 2016 and is a huge advocate for more diversity on Boards. Sharon runs the “So you want to be an NED” programme to support aspiring NED candidates (https://www.sharonbaylay.com/how-to-become-a-non-exec-director/) and is an Advanced Coach and Mentor, with a client list that includes top-tier executives from many global brands. Sharon is also a Fellow of the Chartered Institute of Marketing and an active Member of Women in Advertising and Communications London (WACL).
Deborah Exell
Former Board Member, Head of Human Capital & Business Transformation, Getronics. Current CEO, Exell Intell
Deborah is now owner, founder and CEO of EXELL INTELL, a strategic partner of WILL EXELL and is a recognised leader in business transformation, known by clients for strategy development and vision. She developed her unique blend of applied research and commercial practice in Asia, Middle East, Europe and America. As a board member and CEO advisor, she has been tested in some of the most complex and challenging turnaround programmes of the last 20 years – in banking, technology and consumer brand retail. Deborah was co-founder and Managing Partner of WILL EXELL specializing in helping leaders shape and deliver strategy, with a particular emphasis on organisational alignment. She worked with Fidelity International, Nespresso, Experian, Glencore & Getronics during her 4 years as an active partner in the business. Deborah has held senior positions as MD Organisation Development Unit at Deutsche Bank; Group Head Organisation Development at NatWest Group; Group Head Organisation Development at Lloyd’s Banking Group; Human Capital Advisor to Corporate Change Programmes at Connectology; Global SVP Human Capital Development and Transformation; The Coca-Cola Company; Global SVP Human Capital Development and Transformation at American Express. A content expert, Deborah holds an MSc in Industrial & Organisational Psychology and a BA in Political Economics.
Jeremy Schwartz
Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey
A pioneer of competitive, sustainable business practices, Jeremy Schwartz is the multinational CEO who led The Body Shop, Pandora and Conival PLC. Earlier in his career, Schwartz was the Managing Director for L’Oréal UK, and Marketing Director for News International, Coca-Cola and Sainsbury’s. Currently, he is Chairman of the Kantar Sustainability and Inclusion practice and advisor to McKinsey’s Business Transformation practice. As CEO of The Body Shop, Schwartz created the ground-breaking and highly successful vegan ranges, persuaded authorities around the world to protect endangered strips of rainforest, and travelled to the Amazon to source new ingredients and protect biodiversity by creating an income for local indigenous groups. At Coca-Cola, Schwartz created the multi-billion dollar Coke Zero brand, at L’Oréal he launched the iconic “Because You’re Worth it” line, and at Pandora he led the transition from stores to e-commerce focus, resulting in a 300% increase in share price. As a leading innovator, Schwartz has demonstrated that a company can be both a force for good and a successful profitable business. With his 8 New Skills of Leadership, he identifies the step-by-step practical business tools that enable leaders and companies to increase performance and hit extraordinary goals. He addresses engaging stakeholders, transforming profit and loss, the future of work, and digitisation. At the heart of this ethos lies the need to tackle the fear of change which so often stymies individuals and organisations.
Graham Joscelyne
Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)
Graham Joscelyne CA(SA), CIA, CRMA is a South African and USA citizen and an experienced professional who has focused on governance, risk and assurance activities for many years.
He led the internal audit function in a large Southern African listed group of companies, was appointed Auditor General of the World Bank Group and now consults to senior leadership in the UN Organization and multilateral development institutions management and boards on the topics of internal auditing, risk, governance, ethics & Integrity, and social & environmental issues.
He has chaired and been a member of audit committees for The Global Fund to Fight Aids, Tuberculosis, and Malaria, the World Food Programme, the UN Population Fund, the International Center for Tropical Agriculture, and the CGIAR. Currently, he sits on the Advisory Committee for Internal Oversight for the UNRWA and the Audit and Risk Committee for ACBF.
Andrew Kelly
Principal Consultant, QinetiQ
Andrew Kelly is Principal Consultant in the Cyber & Information team and Technical Lead for Cyber Security, Supply Chain and Telecoms Resilience at QinetiQ. Andrew has put to use over 20 years experience in both the public and private sector to provide leadership across a range of programmes and clients. More recently Andrew was Chief Information Security Officer for the Emergency Services Network and has had significant involvement with the UK Telecoms Lab and recently undertook a number of projects on behalf of Cabinet Office to improve Supply Chain Security.
Andrew Rose
Resident CISO EMEA, Proofpoint
Andrew is the Resident CISO at Proofpoint, which he joined in 2021 from Mastercard, where he was the Chief Security Officer of their subsidiary firm, Vocalink, a firm which provides the transactional backbone of the financial services industry in the UK.
Prior to that Andrew held the CISO role at the UK’s Air Traffic Control provider, NATS, where he oversaw a security transformation and contributed to the design of the next generation air traffic control system. Andrew has also held CISO roles at two top tier global law firms, Allen & Overy LLP and Clifford Chance LLP. In between these roles, Andrew was a Principal Analyst at Forrester Research where he covered the role of the CISO and Security Culture & Awareness as two of his speciality areas.
Andrew was recognized as “European CISO of the year” (2018), and has previously won awards for devising and leading the “Best security awareness program” (2015).
Andrew holds a Master’s degree in information security, is a regular speaker at global security conferences and has contributed to media outlets such as the Wall Street Journal, the Financial Times, the Washington Post, Wired magazine and the Times newspaper. Andrew also appeared in the CNBC documentary entitled “Rise of the Machines”.
Bev Allen
Head of Information Security Assurance, Quilter
An information security professional for quite some time, Bev delivers operational and strategic privacy, information security and information risk management, development and delivery of information security and privacy policies and standards, and information security training. She has worked in a variety of culturally diverse organisations and industries. Currently, Bev is working with tools to analyse and produce data-driven metrics and indicators, using that data to measure and monitor control performance, failures and gaps, to underpin and drive corrective action, and to support information security assurance reviews. Previous roles include Group Risk Manager with Photo Box; Head of Operational Security with Sopra Steria; Information Assurance Compliance Manager with Schroders and Information Security Manager with EDF. Bev has an Executive MBA from Cass Business School and an BA (Hons) degree in Economics & Politics. She is CISA, COBIT 5, ISO 27001 qualified and is proactive in the security industry.
Chris Gunner
Group CISO, Pepper Group
Chris is an Information Security professional, with experience ranging as CISO delivering firm-wide strategy to client-facing delivery as a cyber consultant in a variety of roles and industries. I’m a strong exponent that security is something a business does across the enterprise; it must be built into processes and policies across the organisation in a way that keeps the place running. Information security experience in government, legal and financial services, encompassing: cyber security strategy, ISO27001 certification, third party assurance, security policy frameworks, and operational resilience, business continuity and IT disaster recovery. How can we help organisations understand the threats to their information, today and in the future?
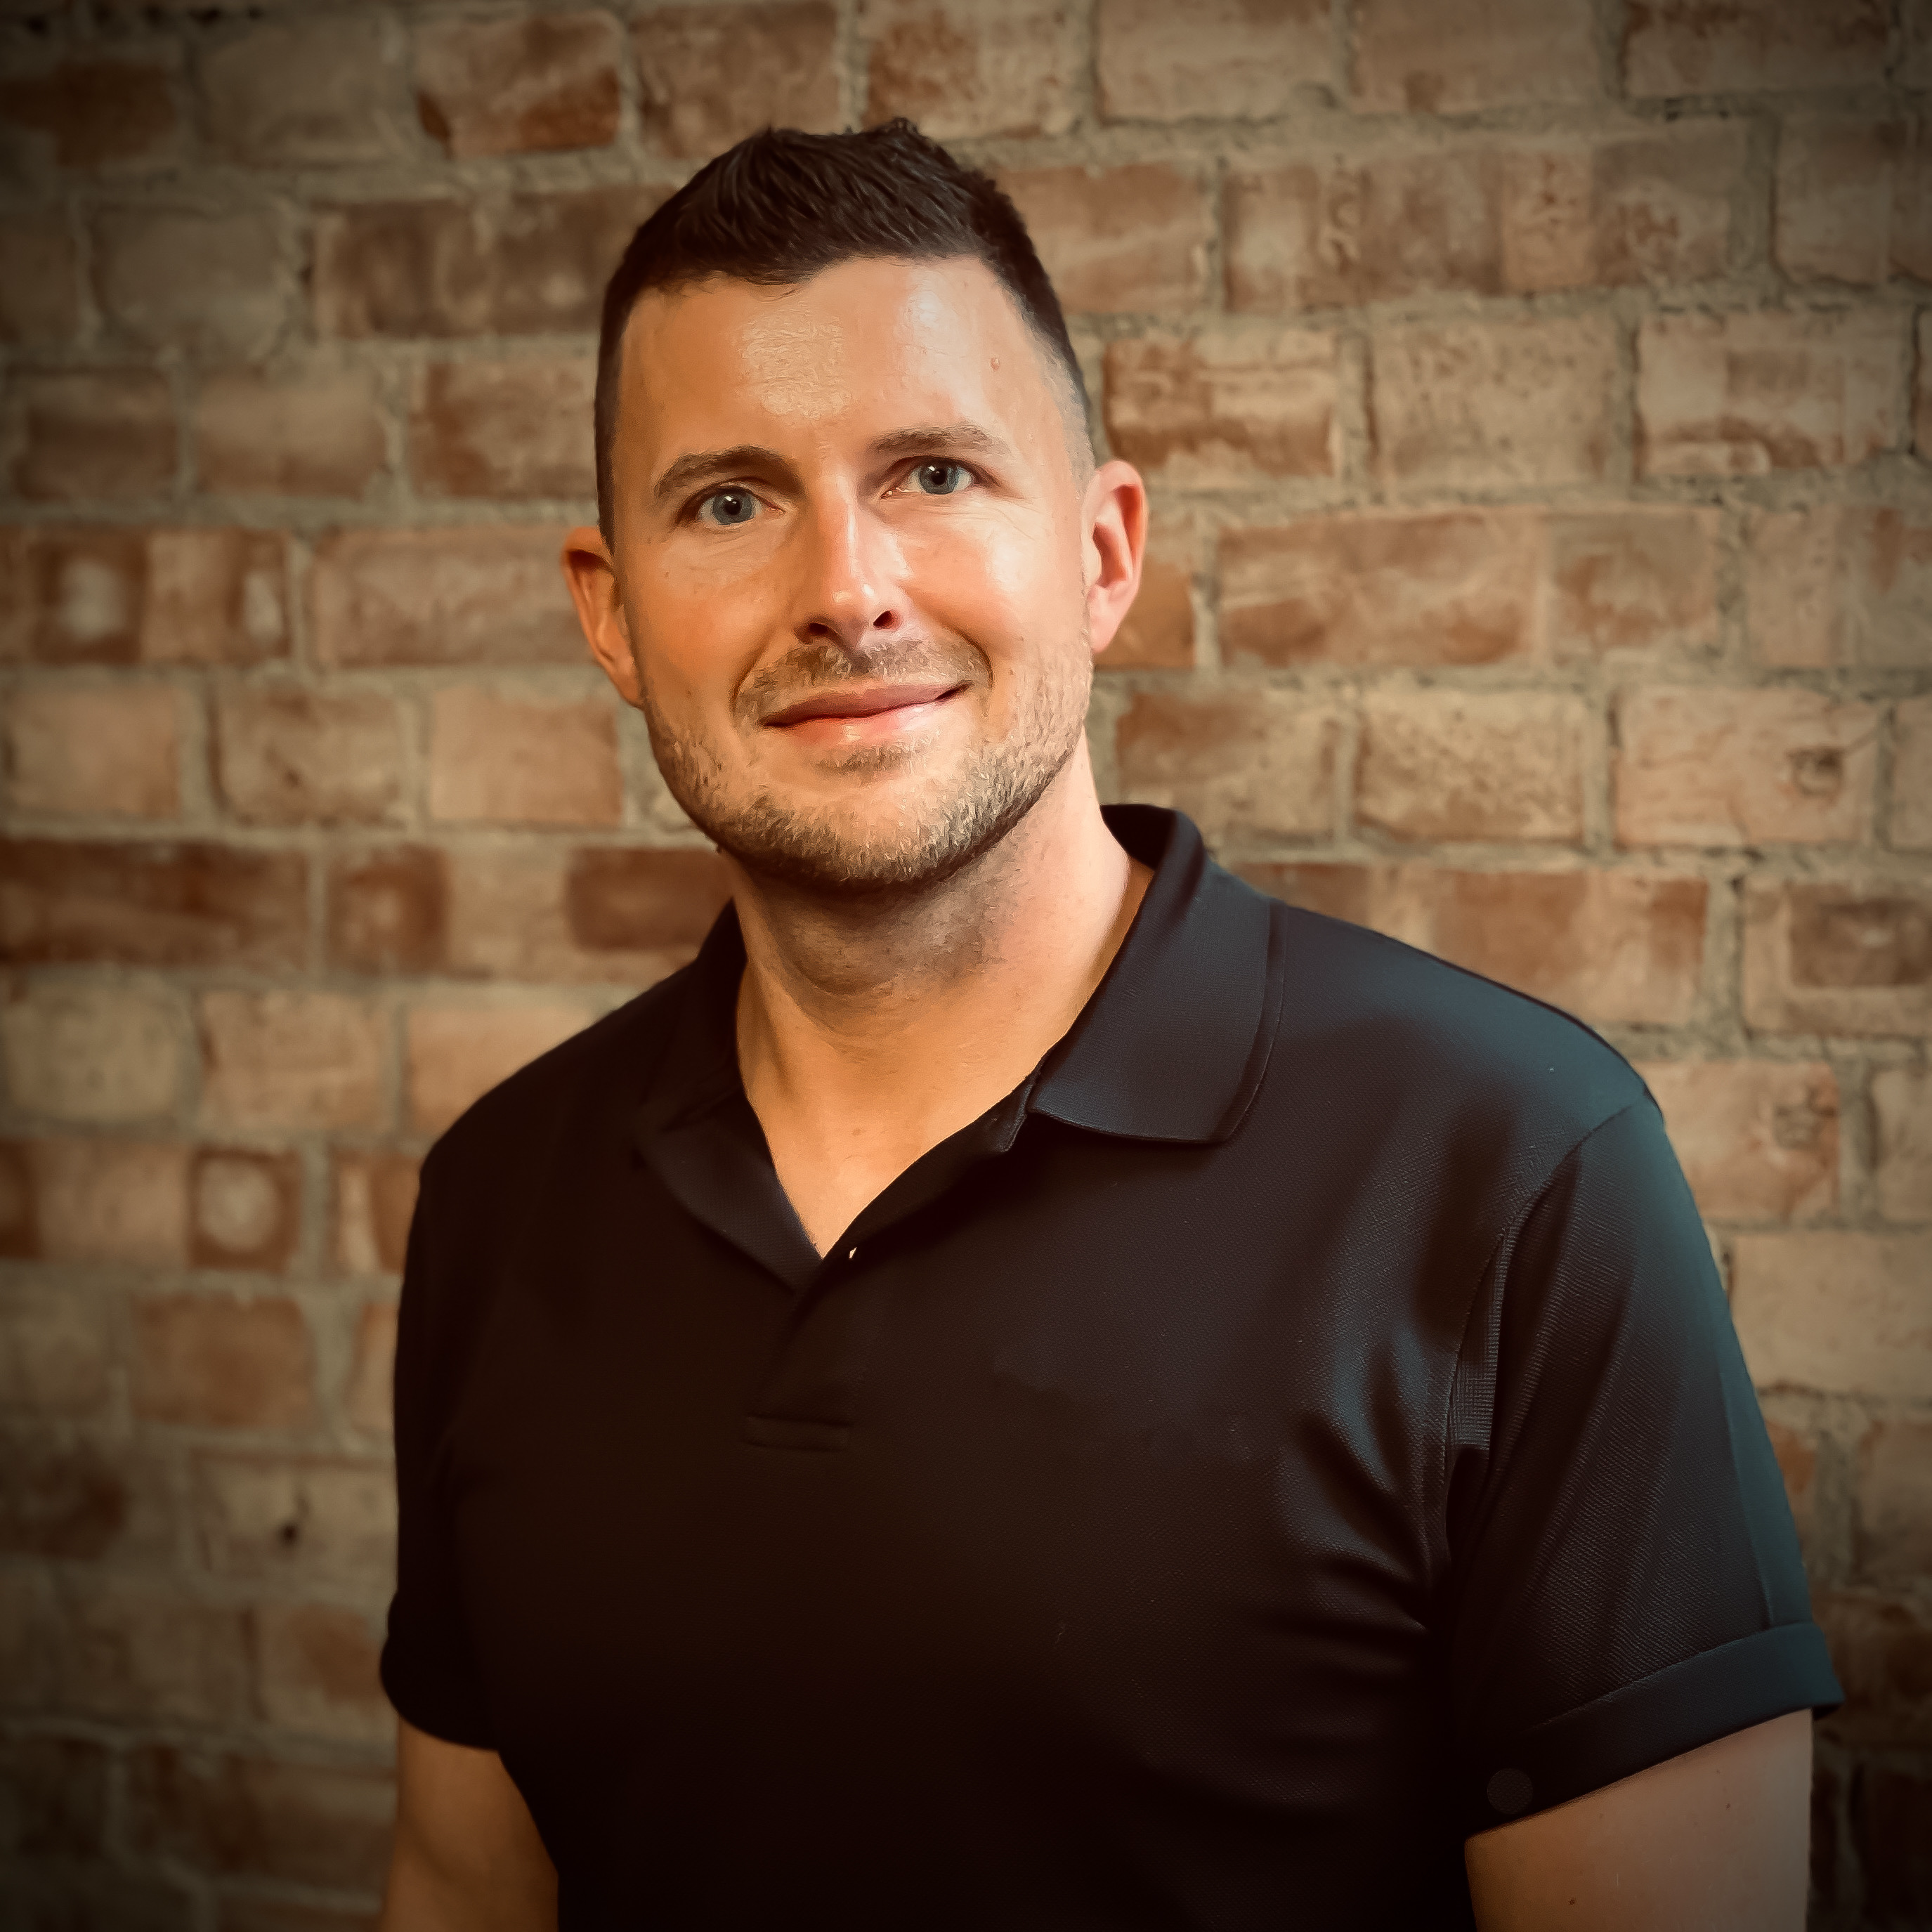
Danny King
Senior Identity Security Engineer, SailPoint
With experience across the industry, and with a history of successful data security projects, Danny is a now a senior identity security engineer with SailPoint – taking a consultative approach to identity challenges, with key focus on time to value and risk reduction, across both public and private sectors. Prior to SailPoint, Danny spent 10 years at Barclays in a variety of information security roles, followed by 3 years as a solution engineer at Varonis Systems.
Graham Edwards
Head of Cyber Security, Yorkshire Water
A successful senior Chief Information Security Officer and Operational Risk Director with a proven track record in multi-cultural and multi-national organisations, Graham bridges technical and business disciplines and communicates at all levels. He has extensive knowledge of Information Security, Cyber Security, Physical Security, BCDR, Operational Risk, Crisis Management, Data Protection, Financial Crime and Compliance. The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. Graham also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He then held the position of Director of Data Security at Nationwide Building Society before taking the role as Head of Information Security at Camelot Lottery Solutions. Graham is currently Interim Head of Cyber Security at Yorkshire Water. He has a master’s degree in Information Security from Royal Holloway.
James Frampton
CISO, Managing Director, Head of IT Risk, Security and Control, MUFG
A career starting in retail with Marks & Spencer to the current role as CISO of MUFG EMEA. In addition to the retail and finance sectors, I have worked in the Beverages, Recruitment and Public Sector. I have covered Operations, Warehousing, Marketing, Project and Programme Management and many Technical roles. This has given me wide experience, seeing different approaches to similar problems. I am a big investor in people and enjoy observing and learning from different styles, approaches and behaviours. I look forward to sharing some of that experience with you.

James Tamblin
President, BlueVoyant UK (Marclay Associates recently acquired by BlueVoyant)
James is a Senior Partner at Marclay with over 15 years’ experience in cyber security and risk management. He oversees our consultancy services, building and managing the firm’s team of cyber consultants, forensics experts and investigators. A commissioned military officer, James graduated in the top third of his class from the military academy in Sandhurst in 2002, going on to a distinguished career which saw service in the airborne forces prior to deployment across Eastern Europe and the Middle East in a covert intelligence role. Prior to leaving the military in 2009 , James was in command of an intelligence unit overseas working with liaison partners to combat threats to National Security. James had developed and grown the delivery function at Marclay, refining the company’s information security auditing practice and leading many of the crisis response and investigative engagements. James has been instrumental in the company’s growth and has created the client facing ethos that Marclay has developed a reputation for. James is well known across boardrooms in the UK and overseas, frequently providing briefings to senior stakeholders who appreciate James’s ability to clearly articulate technical issues in easy to understand briefings whilst remaining focussed on the key risks that need addressing. James has engaged with FTSE100 boards, Premier League Chairmen and royalty with success. James holds a Bachelor of Science in Computation (with honours) from UMIST and is currently UK HM Government SC (security check) cleared.
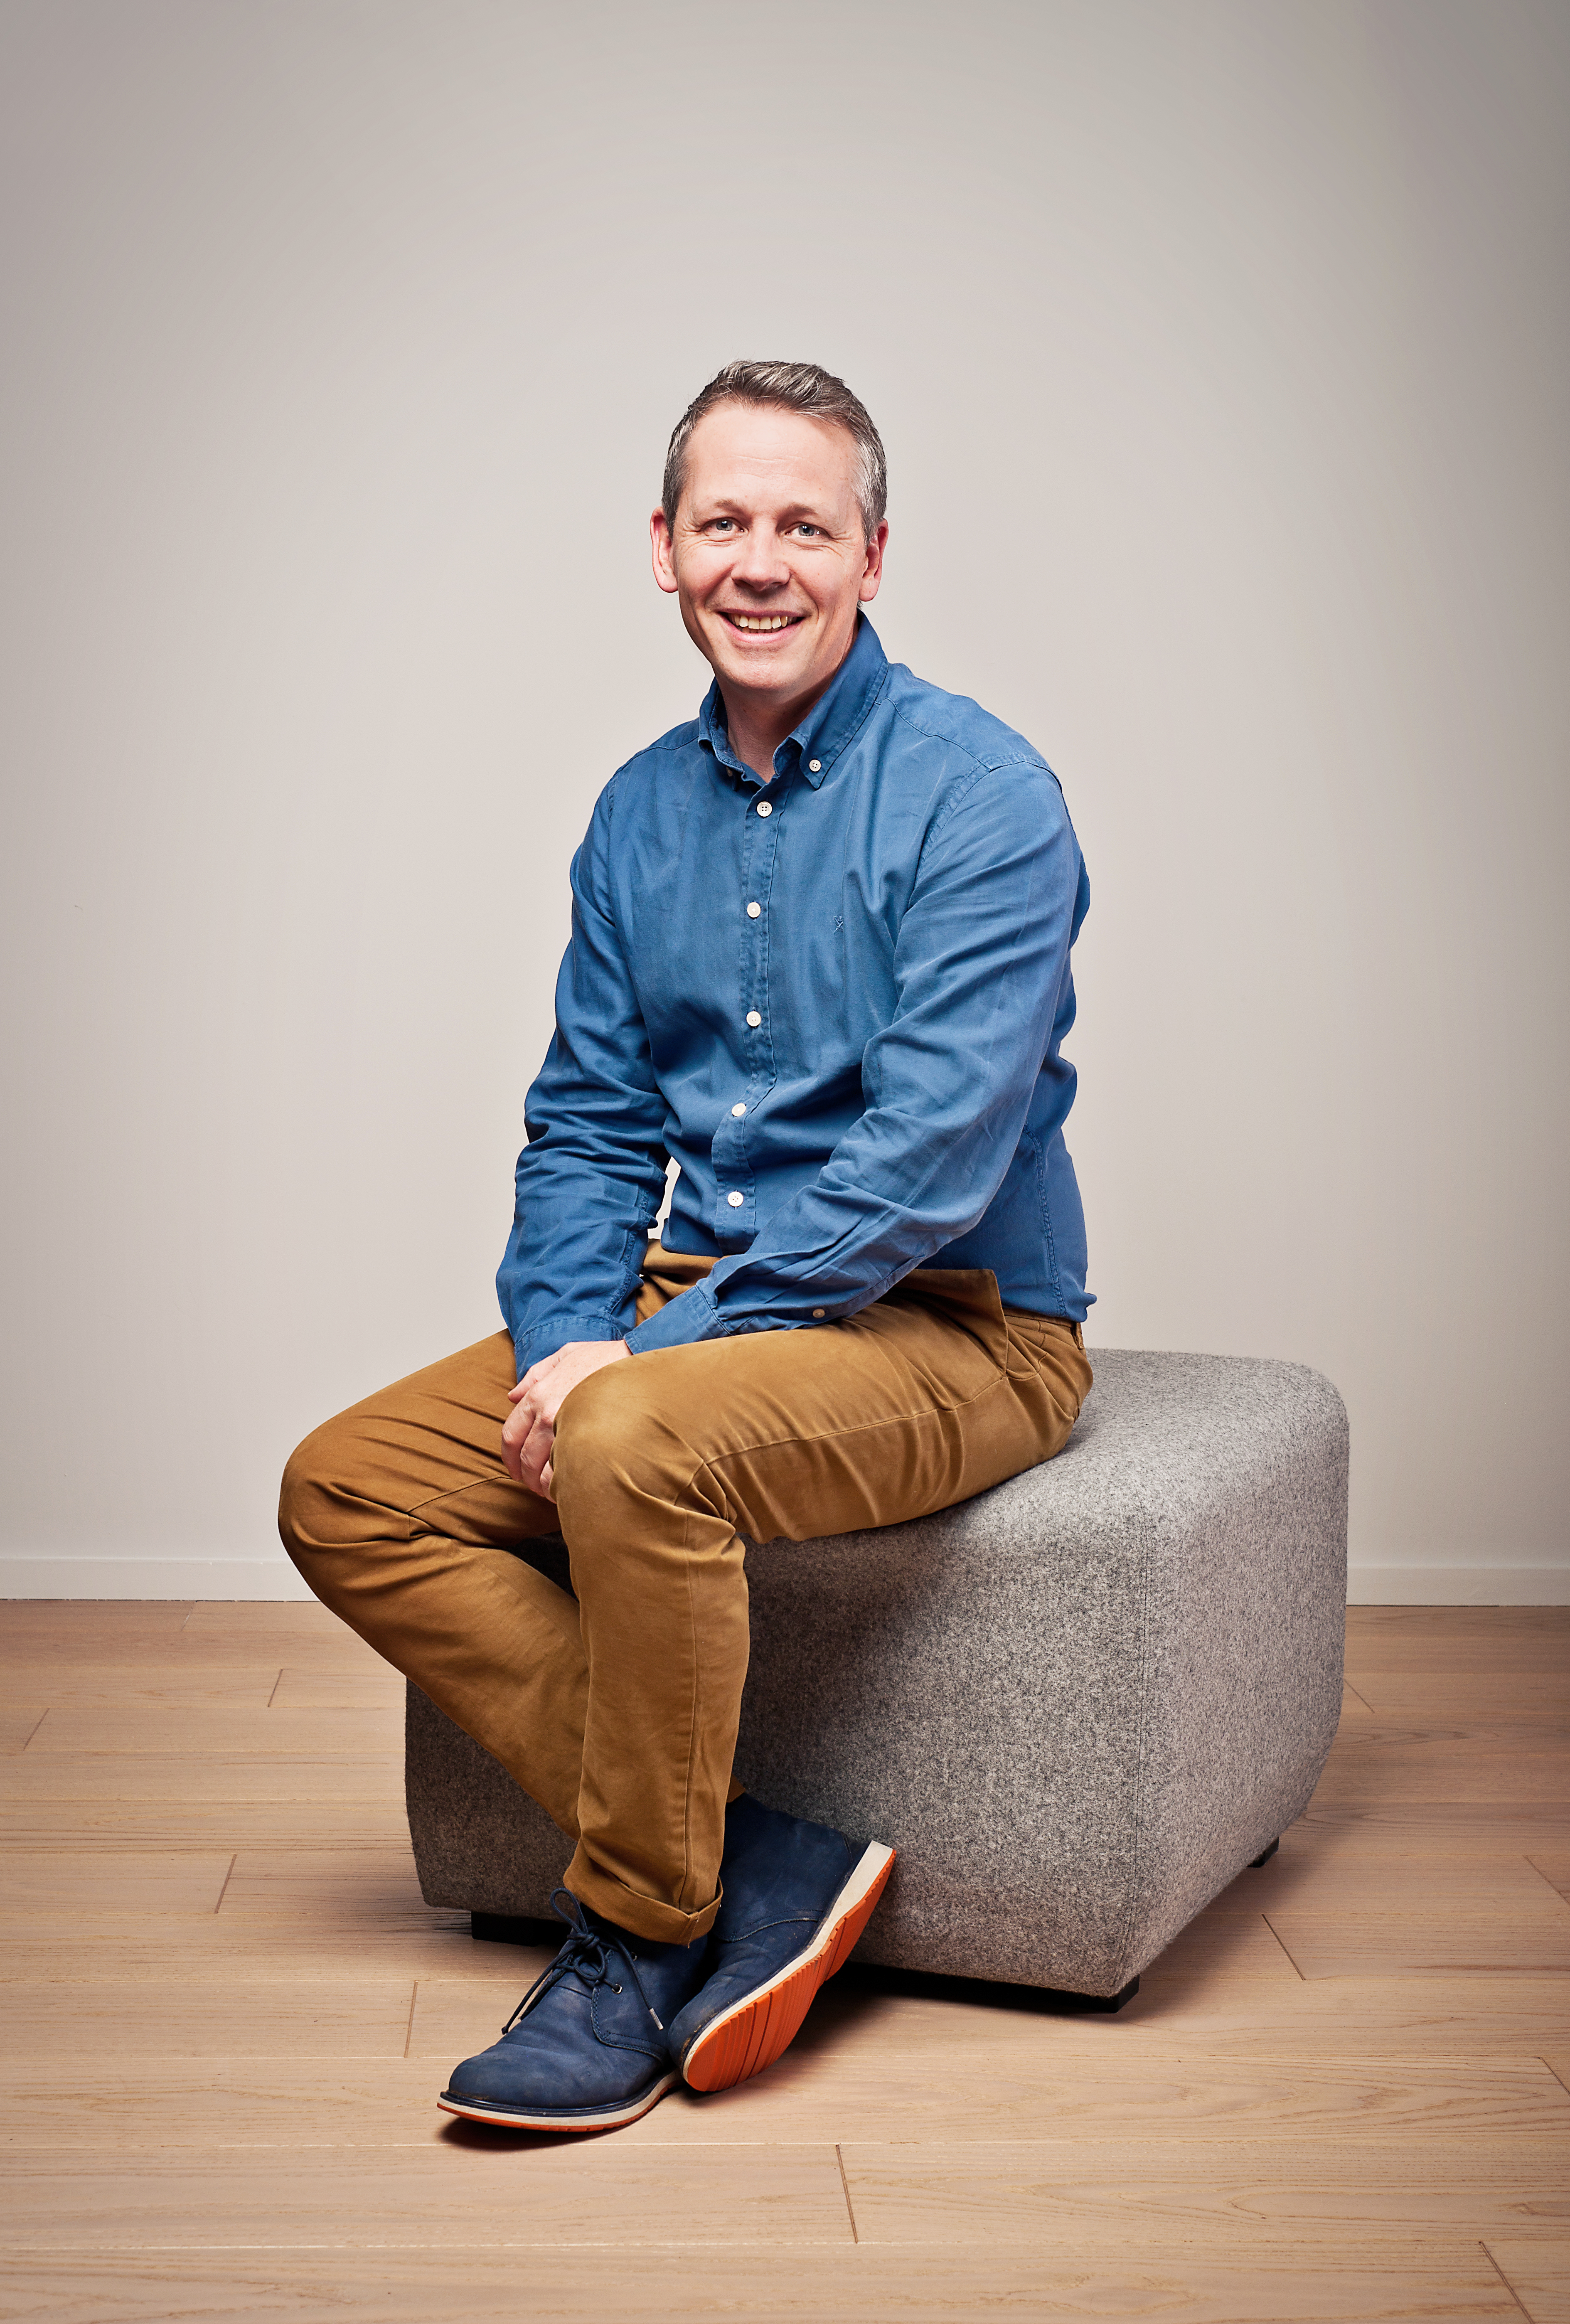
Jonathan Luff
Co-Founder, CyLon
Jonathan is the co-founder of CyLon, which has supported the growth of 100+ cyber security startups across Europe, Asia and the Middle East to a collective valuation of $1bn+. Before founding CyLon, Jonathan was a senior British Diplomat, serving in a variety of roles for the UK Government, including as an advisor to UK Prime Minister David Cameron. He also co-founded Epsilon Advisory Partners, a strategy and growth firm working with world-leading global technology companies and investors.
Julia Harris
Information Security Assurance and Compliance Director – Corporate, Flight Centre Travel Group
Prior to her current role at Flight Centre Travel Group, Julia was Head of Information Protection and Assurance Post Office where she was a strategic leader and trusted advisor with accountability, vision and insights to identify, recommend and plan appropriate Information Assurance Strategy that engendered trust in Post Office brands, drove growth, modernisation and innovation by influencing the business priorities and development, whilst ensuing information assets were protected in line with business strategy, and legal and regulatory requirements. Julia has also held senior cybersecurity roles at BGL and she was Director of Information Security at Rank Group.
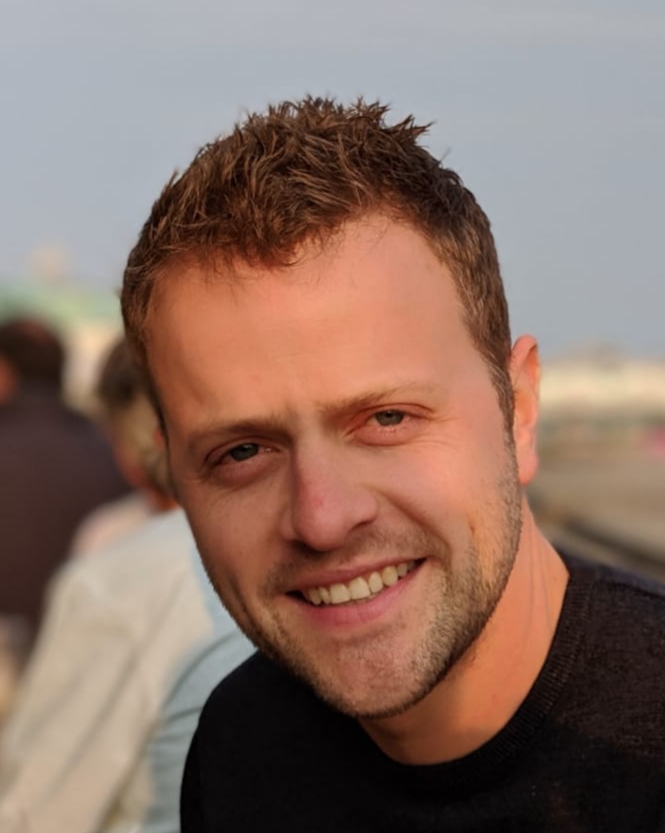
Martyn Booth
CISO, Euromoney Institutional Investor PLC
Martyn is an experienced information security leader and CISO, working at board level to define information security strategy and then manage teams to implement that strategy. Martyn works with clients in a flexible and proactive way to meet stringent security requirements and adaptive needs, enabling businesses to work in a flexible way by reactively designing security processes and technical controls that support the business rather than inhibit it. Specialties: Risk, Compliance, Governance, Awareness, Security Architecture, application architecture, ISO 27001, PCI DSS, policy and information security strategy.
Michele Peroli
Head of Cyber Services, 2|Sec Consulting
Michele Peroli is a highly-focused, energetic, determined and well-rounded senior security consultant. After his bachelor and master’s degrees in computer science, Michele continued his career with a PhD, focused on model checking and automated penetration testing. He then moved to a consultancy position where he helped securing organisation across many industries and lead teams of varying sizes to undertake large multinational projects. He is currently the head of cyber services at 2|Sec consulting.
Mivy James FBCS
Digital Transformation Director, BAE Systems Applied Intelligence
Mivy James has been an IT professional for over 20 years. Prior to joining BAe systems Applied Intelligence in 2005 she worked for several international IT consultancies and corporations. Mivy started her career as an analyst / programmer after completing a degree in Computer Science and Maths and soon moved into technical leadership and system design. Mivy has worked for a range of clients across UK government on everything from cutting edge technology research to the strategic design of multi-billion pound programmes. Mivy is enthusiastic about technology and particularly keen to encourage women to follow careers in the IT profession, she is the founder & chair of Applied Intelligence’s gender balance network. Outside of work Mivy pursues a variety of hobbies including travel and outdoor sports.
Munawar Valiji
Chief Information Security Officer, Trainline
Mun Valiji is a passionate C-suite Cyber & Privacy executive and Advisory Board member with twenty five years experience of delivering business-enabling, transformative security programs across multiple sectors. Mun currently reports to the Trainline Operating Board helping shape a deliver a pragmatic security and privacy strategy. Previous to this he led the cyber programs Sainsbury’s Group, News Corp and spent some time at Citi and Deloitte. Mun’s early career was established at JP Morgan Chase where he was VP responsible for leading the bank’s security threat and vulnerability management program globally. Mun sits on several customer advisory boards and a number of national security councils.
Lady Olga Maitland
President, Defence and Security Forum and Chairman of the Advisory Board, Audere International
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Paul Haywood
Group CISO, BUPA
Paul Haywood is the group chief information security officer for Bupa. Paul is responsible for the global approach to information security across the Bupa Group, including identifying, evaluating, and reporting on risks and meeting compliance and regulatory requirements. Paul has a honours degree in mathematics and a master’s in strategic information systems.
Paul Baird
Chief Technology Security Officer, Qualys UK
Paul moved from Scotland to London in the late 90’s to start his first IT job as a systems administrator for Elonex PLC, at the time one of the biggest UK P.C. manufacturers. Being exposed to multiple vendor operating systems and enterprise applications early on in his career gave him the opportunity to learn a broad range of skills in a short period of time which in turn allowed him to shape his career. Paul has always worked within an I.T. function, having the opportunity to wear many hats has helped him progress into the highest levels of System Engineering / Architecture. Wanting to make the move into cyber he seized the opportunity when it came about and has never looked back. After building a security ethos in a UK FTSE 250 from the ground up he took on the challenge of building a new SOC function within Jaguar Land Rover before his final move to Qualys. Joining Qualys in February of 2021 as the UK and North EMEA Chief Technical Security Officer Paul is helping to drive Qualys’ vision at C-Level across the customer and partner base. Supporting the Qualys sales teams with his knowledge and experience of delivering cyber security operations to enterprise customers at a global scale. Paul will be representing Qualys at forums and conferences to help support the wider cyber security community. Paul mantra is “Perfection is not a destination; it is a never-ending journey”
Peter Draper
Technical Director EMEA, Gurucul
Peter has almost 30 years of experience working with vendors, partners and customers covering Networking, Performance Management, Cyber Security, and Analytics and has worked as an external consultant across the globe solving customer and business issues. Peter’s focus for the last 10 years has been on bringing Analytics to bear on multiple business challenges but predominantly Cyber Risk and remediation.
Professor Dr Robert Coles
Board Director/NED
Dr. Robert Coles is the Director of Cumberland House Consulting Ltd, specialising in cyber security strategy, programme delivery and Non-Exec and Board Advisory roles. He is also an Honorary Professor at UCL and Visiting Professor at Royal Holloway, University of London. He holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Chair of the Crossword Cybersecurity PLC advisory board, member of the advisory boards for Think Cyber Ltd, UK bank, a US pharmaceutical and the Government of Singapore Ministry of Health and member of the Tech-Nation Cybersecurity judging panel. Robert has over 30 years of cybersecurity experience and has held a number of Chief Information Security Officer positions, including for the NHS and health and care system, GSK, National Grid and Merrill Lynch. In all these roles, he owned the information security risk and was responsible for providing leadership across the organisations. He was accountable to the Executive and their Boards for establishing information security strategy and direction, building information security teams and delivering the information security change programme. Prior to these CISO roles, he held a number of “head of” roles at Royal Bank of Scotland, and was the first lead partner, and set up, KPMG’s Information Security Services for EMEA. Robert has extensive links with major industry information security networking groups and government security agencies. He also has links with a number of universities and participates in leading edge research, particularly with Royal Holloway where he is an Executive Sponsor for the Institute of Information Security Innovation, and Cranfield University where he is an executive sponsor for the Cyber Masters Programme. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics.
Dr. Runli Guo
CISO, Gett
Sam Barfoot
Security Architect, Checkmarx
Stephen Khan
CISO Office, Department of Health and Social Care
Stephen is an experienced senior leader and corporate executive with over 20+ years of cross sector experience implementing successful cyber programmes in demanding global environments including Financial Services, Pharmaceuticals, and Healthcare (HSBC, RBS, GSK, SIEMENS). He provides strategic vision, leadership, and technology expertise with a proven track record for effective cyber risk management and digital business enablement. With deep technical expertise in cyber security and enterprise cyber security risk management, Stephen has built a strong track record of creating and leading global strategic change initiatives to drive tangible digital business benefits and outcomes. Prior to his current role, Stephen was Global Head of Technology and Cyber Security Risk; Security Architecture & Engineering at HSBC. Before this, Stephen was at RBS and held the position of Global Head Security Strategy, Architecture and Engineering; and Global Head of Security Transformation programmes. He is currently Chairman of an executive cyber industry forum (ClubCISO) and Chairman of both The White Hat Ball, which has raised £2m+ over the last 15 years to support UK NSPCC and The White Hat Rally which supports Barnardo’s, a UK charity. He is also a Board member of RISCS which is funded by UK National Cyber Security Centre, a partnership between public, private, and academic organisations to support development of key areas which advanced cyber security across organisations.
Tim Ager
VP EMEA, Picus Security
Tim has been working in the cybersecurity industry for over 20 years and has a passion for helping organisations defend against the latest cyber threats. He is an advocate of continuous security validation and how it empowers security teams to better understand, measure and mitigate risks.
Email: tim.ager@picussecurity.com
Toby Lewis
Global Head of Threat Analysis, Darktrace
Prior to joining Darktrace, Toby spent 15 years in the UK Government’s cyber security threats response unit, including as the UK National Cyber Security Centre’s Deputy Technical Director for Incident Management. He has specialist expertise in Security Operations, having worked across Cyber Threat Intelligence, Incident Management, and Threat Hunting. He has presented at several high-profile events, including the NCSC’s flagship conference, CyberUK, the SANS CyberThreat conference, and the Cheltenham Science Festival. He was a lead contributor to the first CyberFirst Girls Competition, championing greater gender diversity in STEM and cyber security. Toby is a Certified Information Systems Security Professional (CISSP) and holds a Master’s in Engineering from the University of Bristol.
Sponsors
Nominet
Nominet has been at the heart of the internet for over 20 years running the .UK internet infrastructure, keeping it safe and secure. In providing registry services for top level domains, it has a wealth of experience in running and protecting the Domain Name System (DNS) as well as analysing threats within the DNS traffic.
This expertise underpins its cyber security solutions that protect governments and global enterprises from constant attack. NTX uses machine learning to reduce risk on your network and eliminates threats before they cause harm. It analyses DNS traffic for known and unknown bad in real time to predict, detect and block cyber threats.
Providing your security teams with visibility and protection against critical threats such as malware, phishing, data theft and DNS hijacking, NTX narrows the window of compromise by identifying malicious domains, on average, one week faster than other network security solutions. NTX is an easy-to-deploy solution used by commercial clients worldwide, as well as the UK Government and over 400 of its public bodies as part of the Protective DNS service we provide.
Checkmarx
Checkmarx is the Software Exposure Platform for the enterprise. Over 1,400 organizations around the globe rely on Checkmarx to measure and manage software risk at the speed of DevOps. Checkmarx serves five of the world’s top 10 software vendors, four of the top American banks, and many government organizations and Fortune 500 enterprises, including SAP, Samsung, and Salesforce.com.
Learn more at www.checkmarx.com.
https://www.facebook.com/Checkmarx.Source.Code.Analysis
https://www.youtube.com/user/CheckmarxResearchLab
https://twitter.com/checkmarx
https://www.linkedin.com/company/checkmarx/
Barclay Simpson
Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury. www.barclaysimpson.com
Cylance BB Horz Black
Cylance develops artificial intelligence to deliver prevention-first, predictive security solutions that change how organizations manage their endpoints. Cylance provides full spectrum predictive threat prevention and visibility across the enterprise to combat the most notorious and advanced cybersecurity attacks. With AI-based malware prevention, threat hunting, automated detection and response, and expert security services, Cylance protects the endpoint without increasing staff workload or costs. We call it The Science of Safe.
Learn more at www.cylance.com
Optiv
A TEN
however, delivers national and international cultural change communication programmes on Employee Information & Cyber Security Awareness and Education, a sector we have worked in for twelve years. During this time we have helped many of the FTSE 150 and Fortune 500 organisations improve their Information Security by targeting their weakest link, their people and educating them in the importance of Information Security behaviour. We create bespoke solutions that are evolved after analysing an organisation’s culture, brand, values and behaviours. This enables us to create tailored programmes that appeal to the target audience from both a content and creative perspective. This honed methodology has been proven, via measurement to have great impact on supporting the mitigation of the human behaviour risk.
Synack
Synack, the leader in crowdsourced security testing, helps organizations protect themselves from cyber attacks. By leveraging the world’s best ethical hackers and an AI-enabled platform, Synack helps organizations find and fix critical security issues and provides valuable security intelligence on digital assets. The Synack platform delivers data-driven insights to help organizations understand their risk from a hacker’s perspective and then mitigate that risk with a hacker’s help. These insights secure critical infrastructure and leading brands and businesses around the world- Synack protects leading global banks, DoD classified assets, and close to $1 trillion in Fortune 500 revenue. For more information visit us at www.synack.com
Sponsorship Opportunities
TTTB
Ping Identity
Ping Identity is the Intelligent Identity solution for the enterprise. We enable companies to achieve Zero Trust identity-defined security and more personalized, streamlined user experiences. The Ping Intelligent Identity™ platform provides customers, workforce, and partners with access to cloud, mobile, SaaS and on-premises applications across the hybrid enterprise. Over half of the Fortune 100 choose us for our identity expertise, open standards, and partnerships with companies including Microsoft and Amazon. We provide flexible identity solutions that accelerate digital business initiatives, delight customers, and secure the enterprise through multi-factor authentication, single sign-on, access management, intelligent API security, directory, and data governance capabilities.
For more information, visit www.pingidentity.com
At BlueVoyant
At BlueVoyant, we recognize that effective cybersecurity requires active prevention and defense across both your organization and supply chain. Our proprietary data, analytics and technology, coupled with deep expertise, works as a force multiplier to secure your full ecosystem.
Accuracy. Actionability. Timeliness. Scalability.
Founded in 2017 by former Fortune 500 and former government cyber officials, BlueVoyant is headquartered in New York City and has offices in Maryland, Tel Aviv, San Francisco, Manila, Toronto, London, Latin America and Budapest. Visit www.bluevoyant.com.
QinetiQ
QinetiQ is an integrated global security and defence company. Operating at the leading edge of science and engineering and employing over 6,000 people, including more than 3,000 scientists and engineers. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way.
Uniting our own and others’ technology and know-how to provide distinctive specialist services and products that address our customers’ most pressing challenges. We are integrated across the life cycle of critical equipment and infrastructure, undertaking creative research and development, enabling test and evaluation and delivering operational readiness through training and rehearsal.
Create it. Test it. Use it.
SailPoint
SailPoint: The Power of Identity™
SailPoint, the leader in enterprise identity governance, brings the Power of Identity to customers around the world. SailPoint’s open identity platform gives organizations the power to enter new markets, scale their workforces, embrace new technologies, innovate faster and compete on a global basis. As both an industry pioneer and market leader in identity governance, SailPoint delivers security, operational efficiency and compliance to enterprises with complex IT environments. SailPoint’s customers are among the world’s largest companies in a wide range of industries, including: 7 of the top 15 banks, 4 of the top 6 healthcare insurance and managed care providers, 9 of the top 15 property and casualty insurance providers, 5 of the top 15 pharmaceutical companies, and 11 of the largest 15 federal agencies.
Checkmarx
Checkmarx is constantly pushing the boundaries of Application Security Testing to make security seamless and simple for the world’s developers while giving CISOs the confidence and control they need. As the AppSec testing leader, we provide the industry’s most comprehensive solutions, giving development and security teams unparalleled accuracy, coverage, visibility, and guidance to reduce risk across all components of modern software – including proprietary code, open source, APIs, and infrastructure as code. Over 1,600 customers, including half of the Fortune 50, trust our security technology, expert research, and global services to securely optimize development at speed and scale. For more information, visit our website, check out our blog, or follow us on LinkedIn.
Qualys
Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance. For more information, please visit www.qualys.com
HUMAN Horiz Black
HUMAN (formally White Ops) is a cybersecurity company that protects enterprises from bot attacks to keep digital experiences human. We have the most advanced Human Verification Engine that protects applications, APIs and digital media from bot attacks, preventing losses and improving the digital experience for real humans. Today we verify the humanity of more than 10 trillion interactions per week for some of the largest companies and internet platforms. Protect your digital business with HUMAN.
To Know Who’s Real, visit www.humansecurity.com
USE THIS ONE Darktrace
Gurucul
Gurucul is a global cyber security and fraud analytics company that is changing the way organizations protect their most valuable assets, data and information from insider and external threats both on-premises and in the cloud. Gurucul’s real-time security analytics and fraud analytics technology combines machine learning behavior profiling with predictive risk-scoring algorithms to predict, prevent and detect breaches and fraud. Gurucul technology is used by Global Fortune 1000 companies and government agencies to fight cyber fraud, IP theft, insider threats and account compromise. The company is based in Los Angeles. To learn more, visit Gurucul and follow us on LinkedIn and Twitter.
Proofpoint
Proofpoint is a leading cybersecurity company that protects organizations’ greatest assets and biggest risks: their people. With an integrated suite of cloud-based solutions, we help companies around the world stop targeted threats, safeguard their data, and make their users more resilient against cyber attacks. Leading organizations of all sizes, including more than half of the Fortune 1000, rely on us for people-centric security and compliance solutions that mitigate their most critical risks across email, the cloud, social media, and the web.
Sec LogoNEW
2|Sec – The Gold Standard In Penetration Testing
Picus Security
Picus Security is a leading Breach and Attack Simulation (BAS) vendor, enabling organisations to test, measure and improve the effectiveness of their cyber security controls through automated and continuous offensive and defensive security testing. Picus’ complete security control validation platform challenges organisations’ cyber-security controls at prevention and detection layers by simulating over 10,000 threats and attack scenarios. This includes the latest types of malware and ransomware as well as MITRE ATT&CK techniques. Crucially, the Picus platform not only identifies defensive weaknesses as well as threat coverage and visibility gaps, it supplies content to help mitigate them too. This includes prevention signatures as well as detection rules for SIEM and EDR tools – removing the need for security teams to create and test their own. Unlike other tools and assessments, Picus enables security leaders to understand and measure an organisation’s cyber security posture at any moment in time. It provides insights into the impact of infrastructure changes and security improvements, and helps guide and prioritise future investment decisions. Gartner, which lists Breach and Attack Simulation as a Top Security and Risk Management Trend for 2021 has named Picus a ‘Cool Vendor’’. The company is cited by Frost & Sullivan as one of the most innovative players in the BAS market. Picus has hundreds of clients worldwide, with offices in EMEA, North America and APAC. Its technology partners include Cisco, IBM, Fortinet, Microsoft, Splunk and VMware.
Think Cyber 4x
Think Cyber Security deliver measurable secure behaviour change for their customers. The company’s multi-award winning Redflags™ Real-time Security Awareness product applies behavioural and learning science theory to deliver context-sensitive, just-in-time guidance. For example, when users are about to click links, visit certain web pages, enter their username into a web page, handle attachments, etc. Redflags™ won techUK Cyber Innovator of the Year 2021 and SC Awards Best Professional Training Programme 2020. It offers the toolkit organisations need to: manage operational risk from cyber-attacks directed at staff including phishing and ransomware; meet compliance goals; keep content refreshed and relevant; target specific behaviours and specific users; all whilst allowing staff to get on with their jobs, to achieve business goals.
BS White Background
Local knowledge. Global resources. Specialist consultants.
Barclay Simpson is an international recruitment consultancy that specialises in recruiting information and cyber security professionals. Since 2001, we have provided end-to-end information security recruitment solutions, including permanent, interim and executive hires from analysts through to CISOs, so organisations can create an information security function that’s both fit for purpose and future-proof. Whether sourcing a single hire, an interim manager, or building a security function from scratch, our extensive network and niche specialist knowledge make Barclay Simpson ideally positioned to support your security needs.
Our specialist markets:
Security Leadership: CSO / CISO, Director of Information Security, Head of IT Risk, Head of Security Operations, Head of Security Architecture, Cyber Programme Director
Governance, Risk & Compliance: IT & Cyber Risk, IT Resilience, Information Risk, Security Controls & Assurance, 3rd Party Risk & Supplier Assurance
Security Architecture & Engineering: Security Architecture, Security Engineering, Cloud Security, Application Security, DevSecOps
Cyber Operations & Incident Response: Security Operations, Incident Response, Threat Intelligence, Threat & Vulnerability Management, Penetration Testing
Data Protection & Data Privacy: DPO, Data Privacy, Data Protection, Data Security, Data Governance, GDPR
Cyber Transformation & IAM: Cyber / Risk Transformation, Project & Programme Management, Regulatory Change, Cyber Education & Awareness, Identity & Access Management
Consultative approach – From business strategy and advisory services through to implementation and transition strategies, our information and cyber security recruitment services are fully tailored to your needs.
BESTMAN SOLUTIONS
Venue
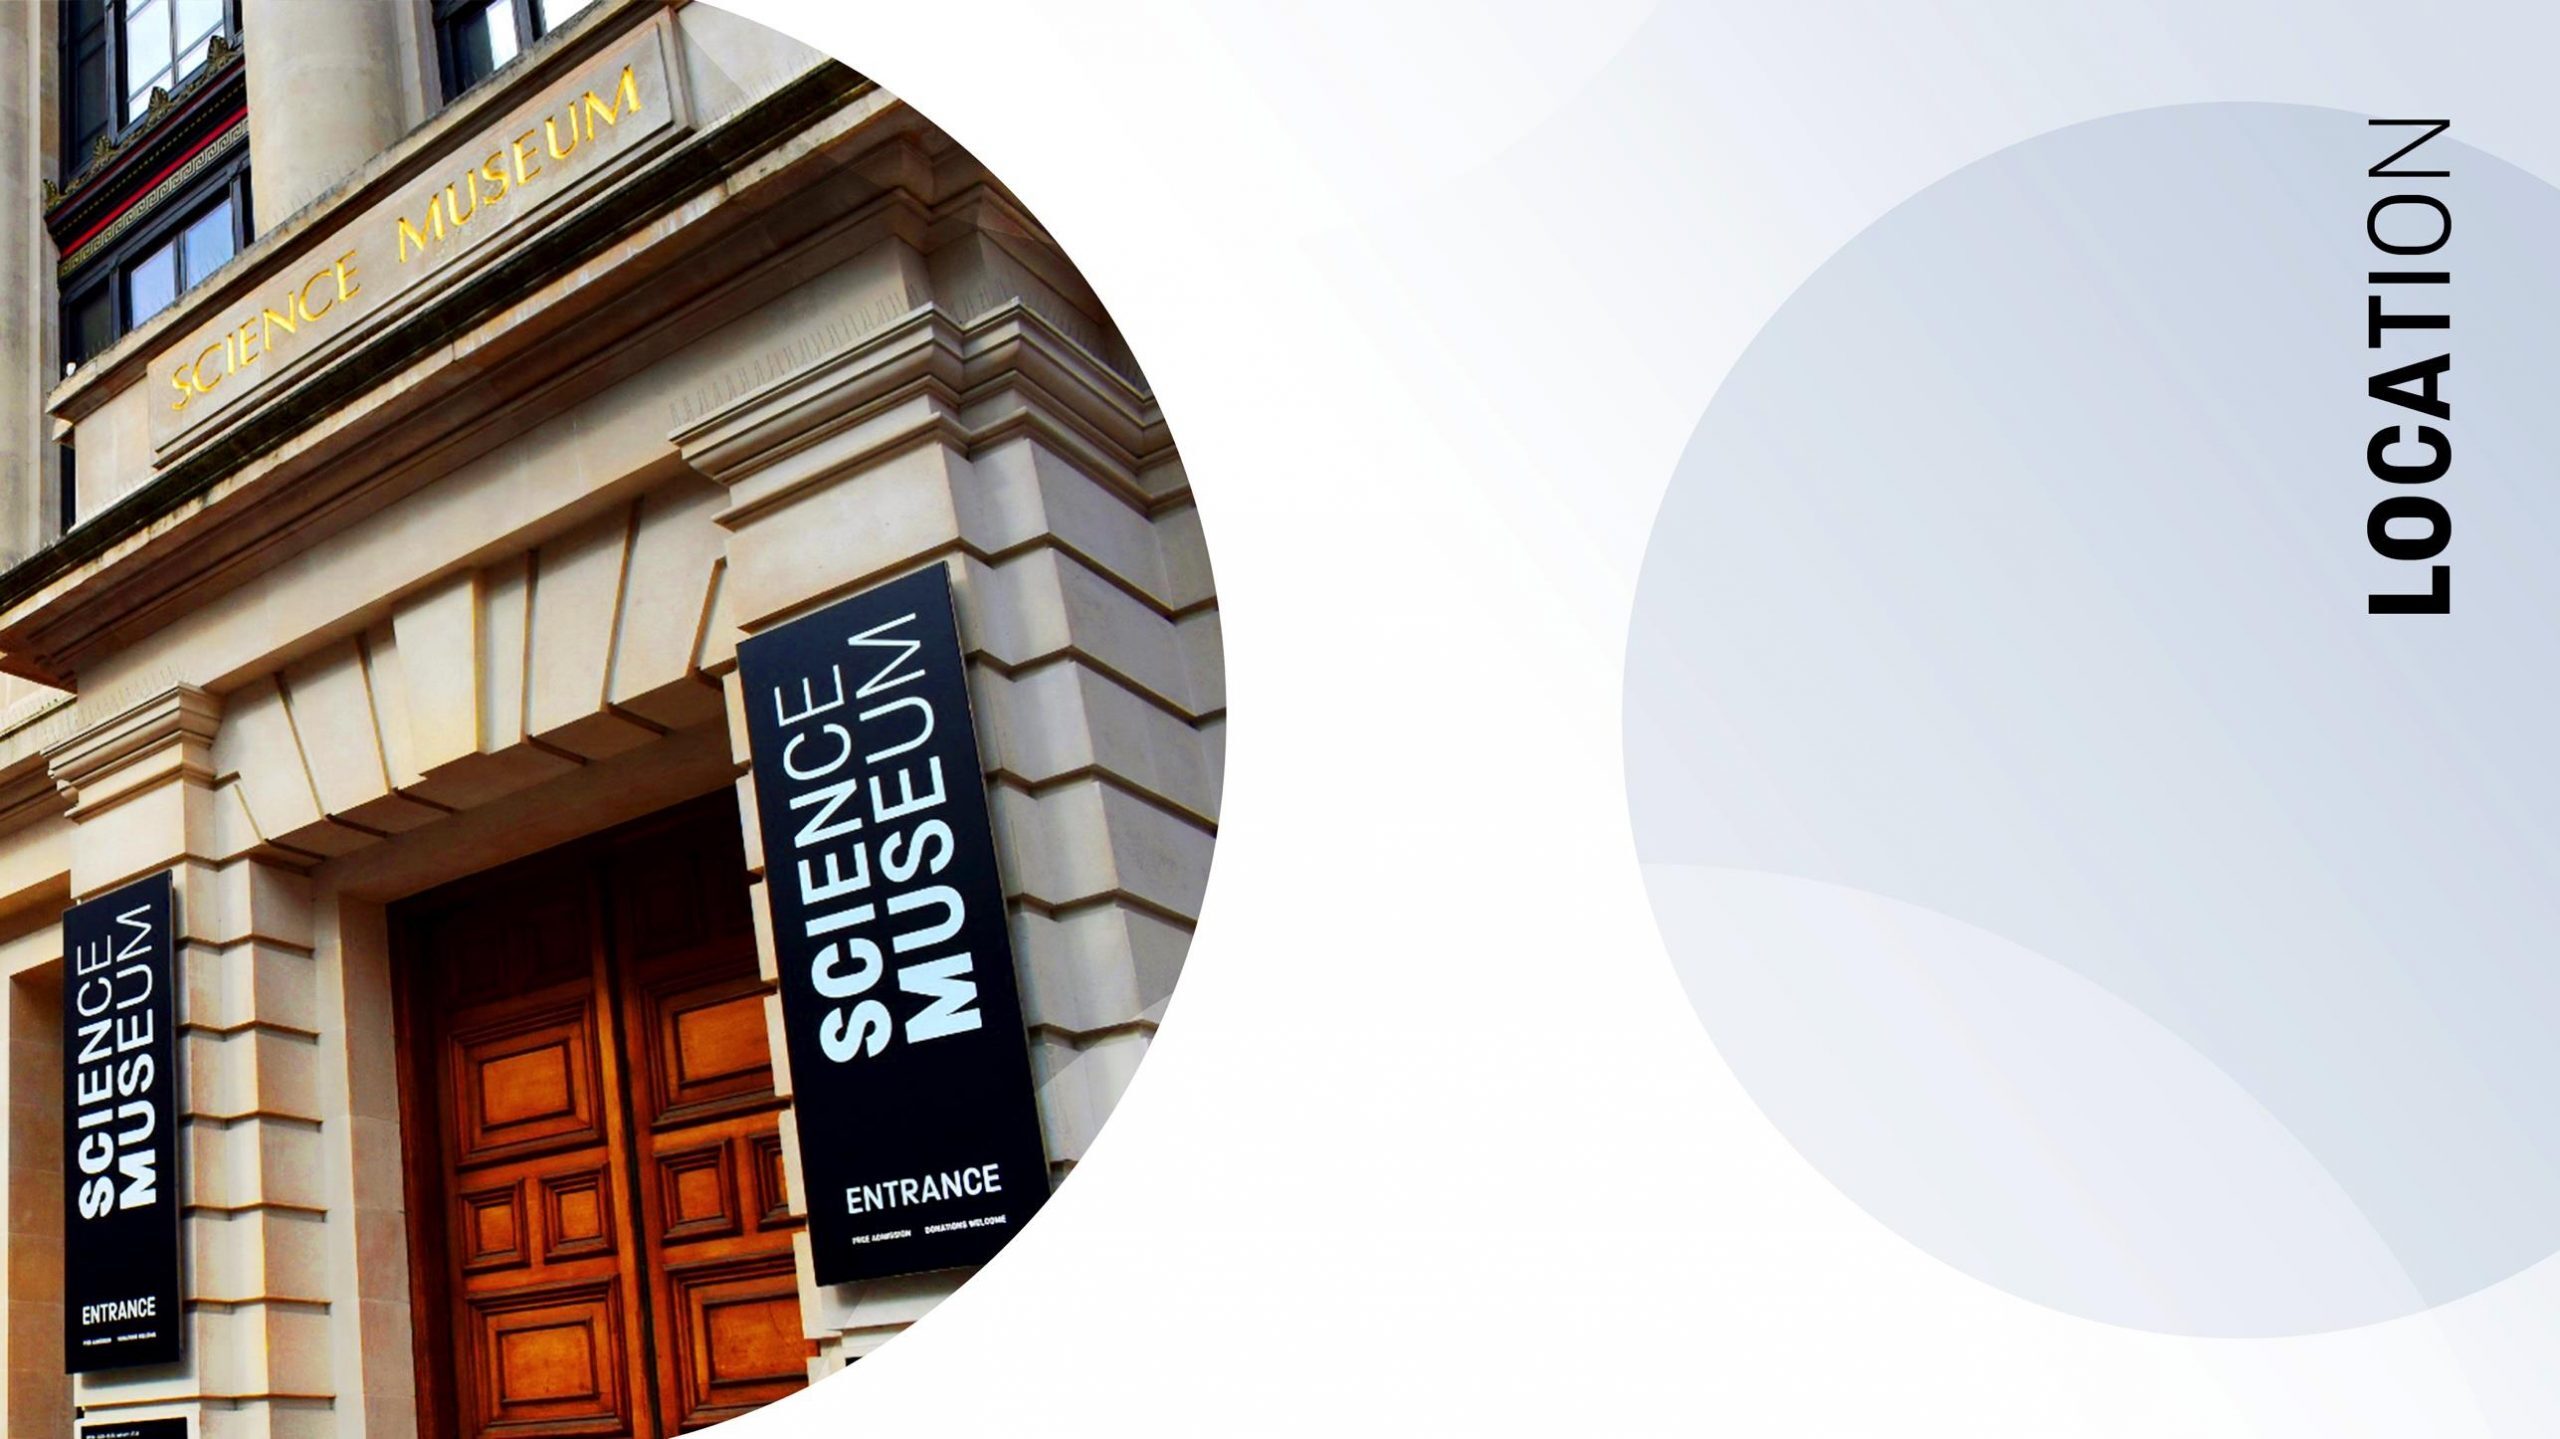
Science Museum, London
Groups Entrance – Illuminate Science Museum, Imperial College Road
South Kensington, London, SW7 2DD
www.sciencemuseum.org.uk
We are thrilled that the Science Museum in London will be the venue for this years’ 3rd Cyber Exchange 360: Talk to the Board. An inspiring landmark with award-winning exhibitions, iconic objects and stories of incredible scientific, technological and medical advancement and achievement.
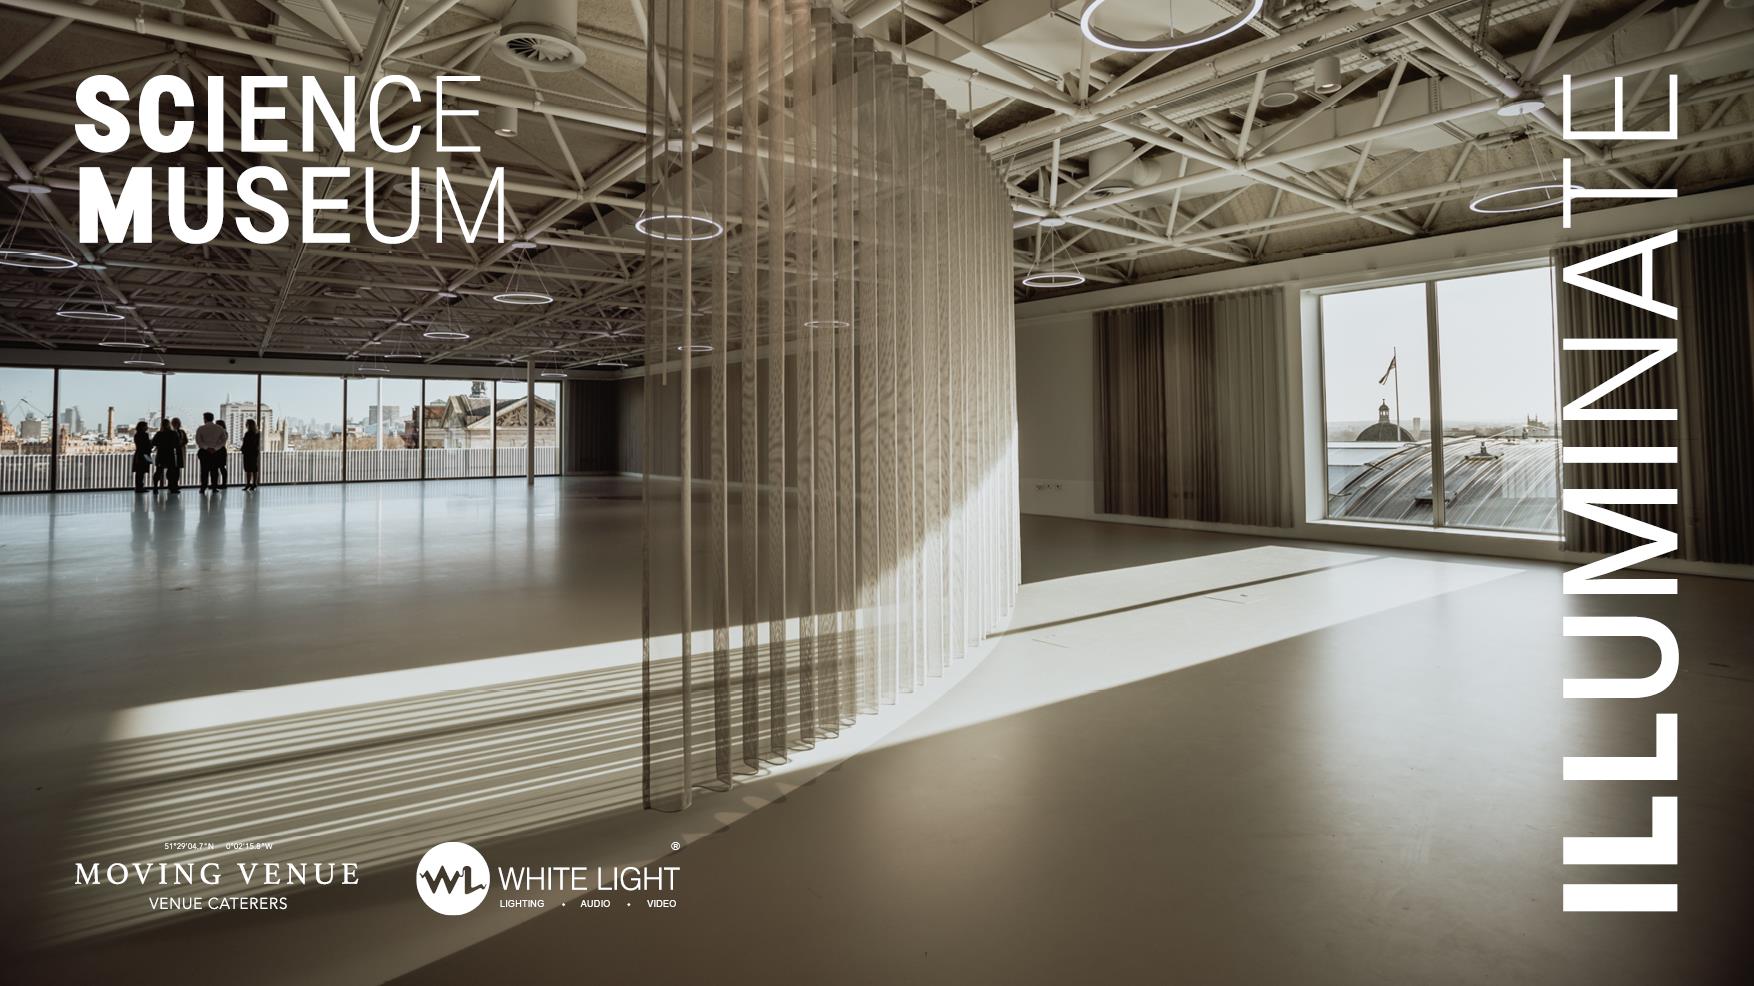
Main event space – Illuminate
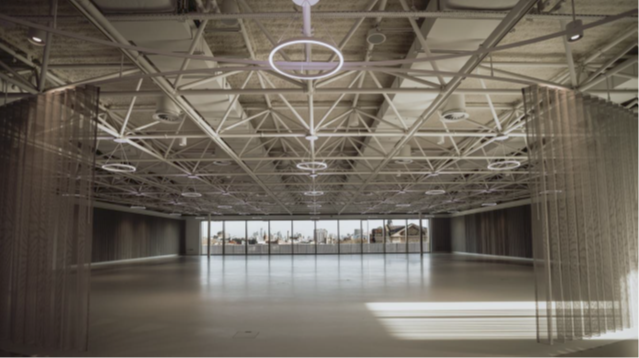
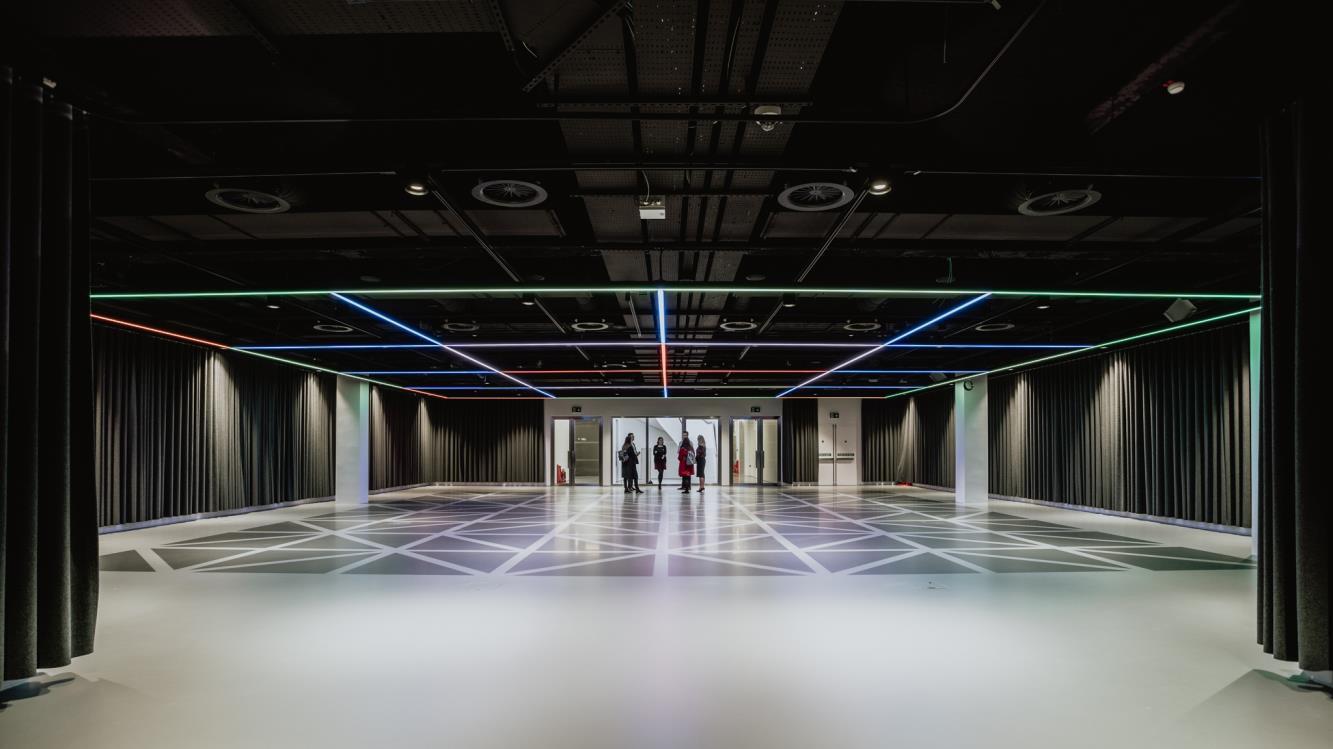
Illuminate is the world-class event space located in the heart of the Science Museum where the conference will be hosted. This space is a progressive new award-winning venue situated on Levels 4 and 5 of the Science Museum. Among the unique features of this new space is a panoramic window, offering stunning views of the City and an abundance of natural daylight, a key element in ensuring a productive meeting or conference experience.
Networking Reception in Wonderlab: The Equinor Gallery
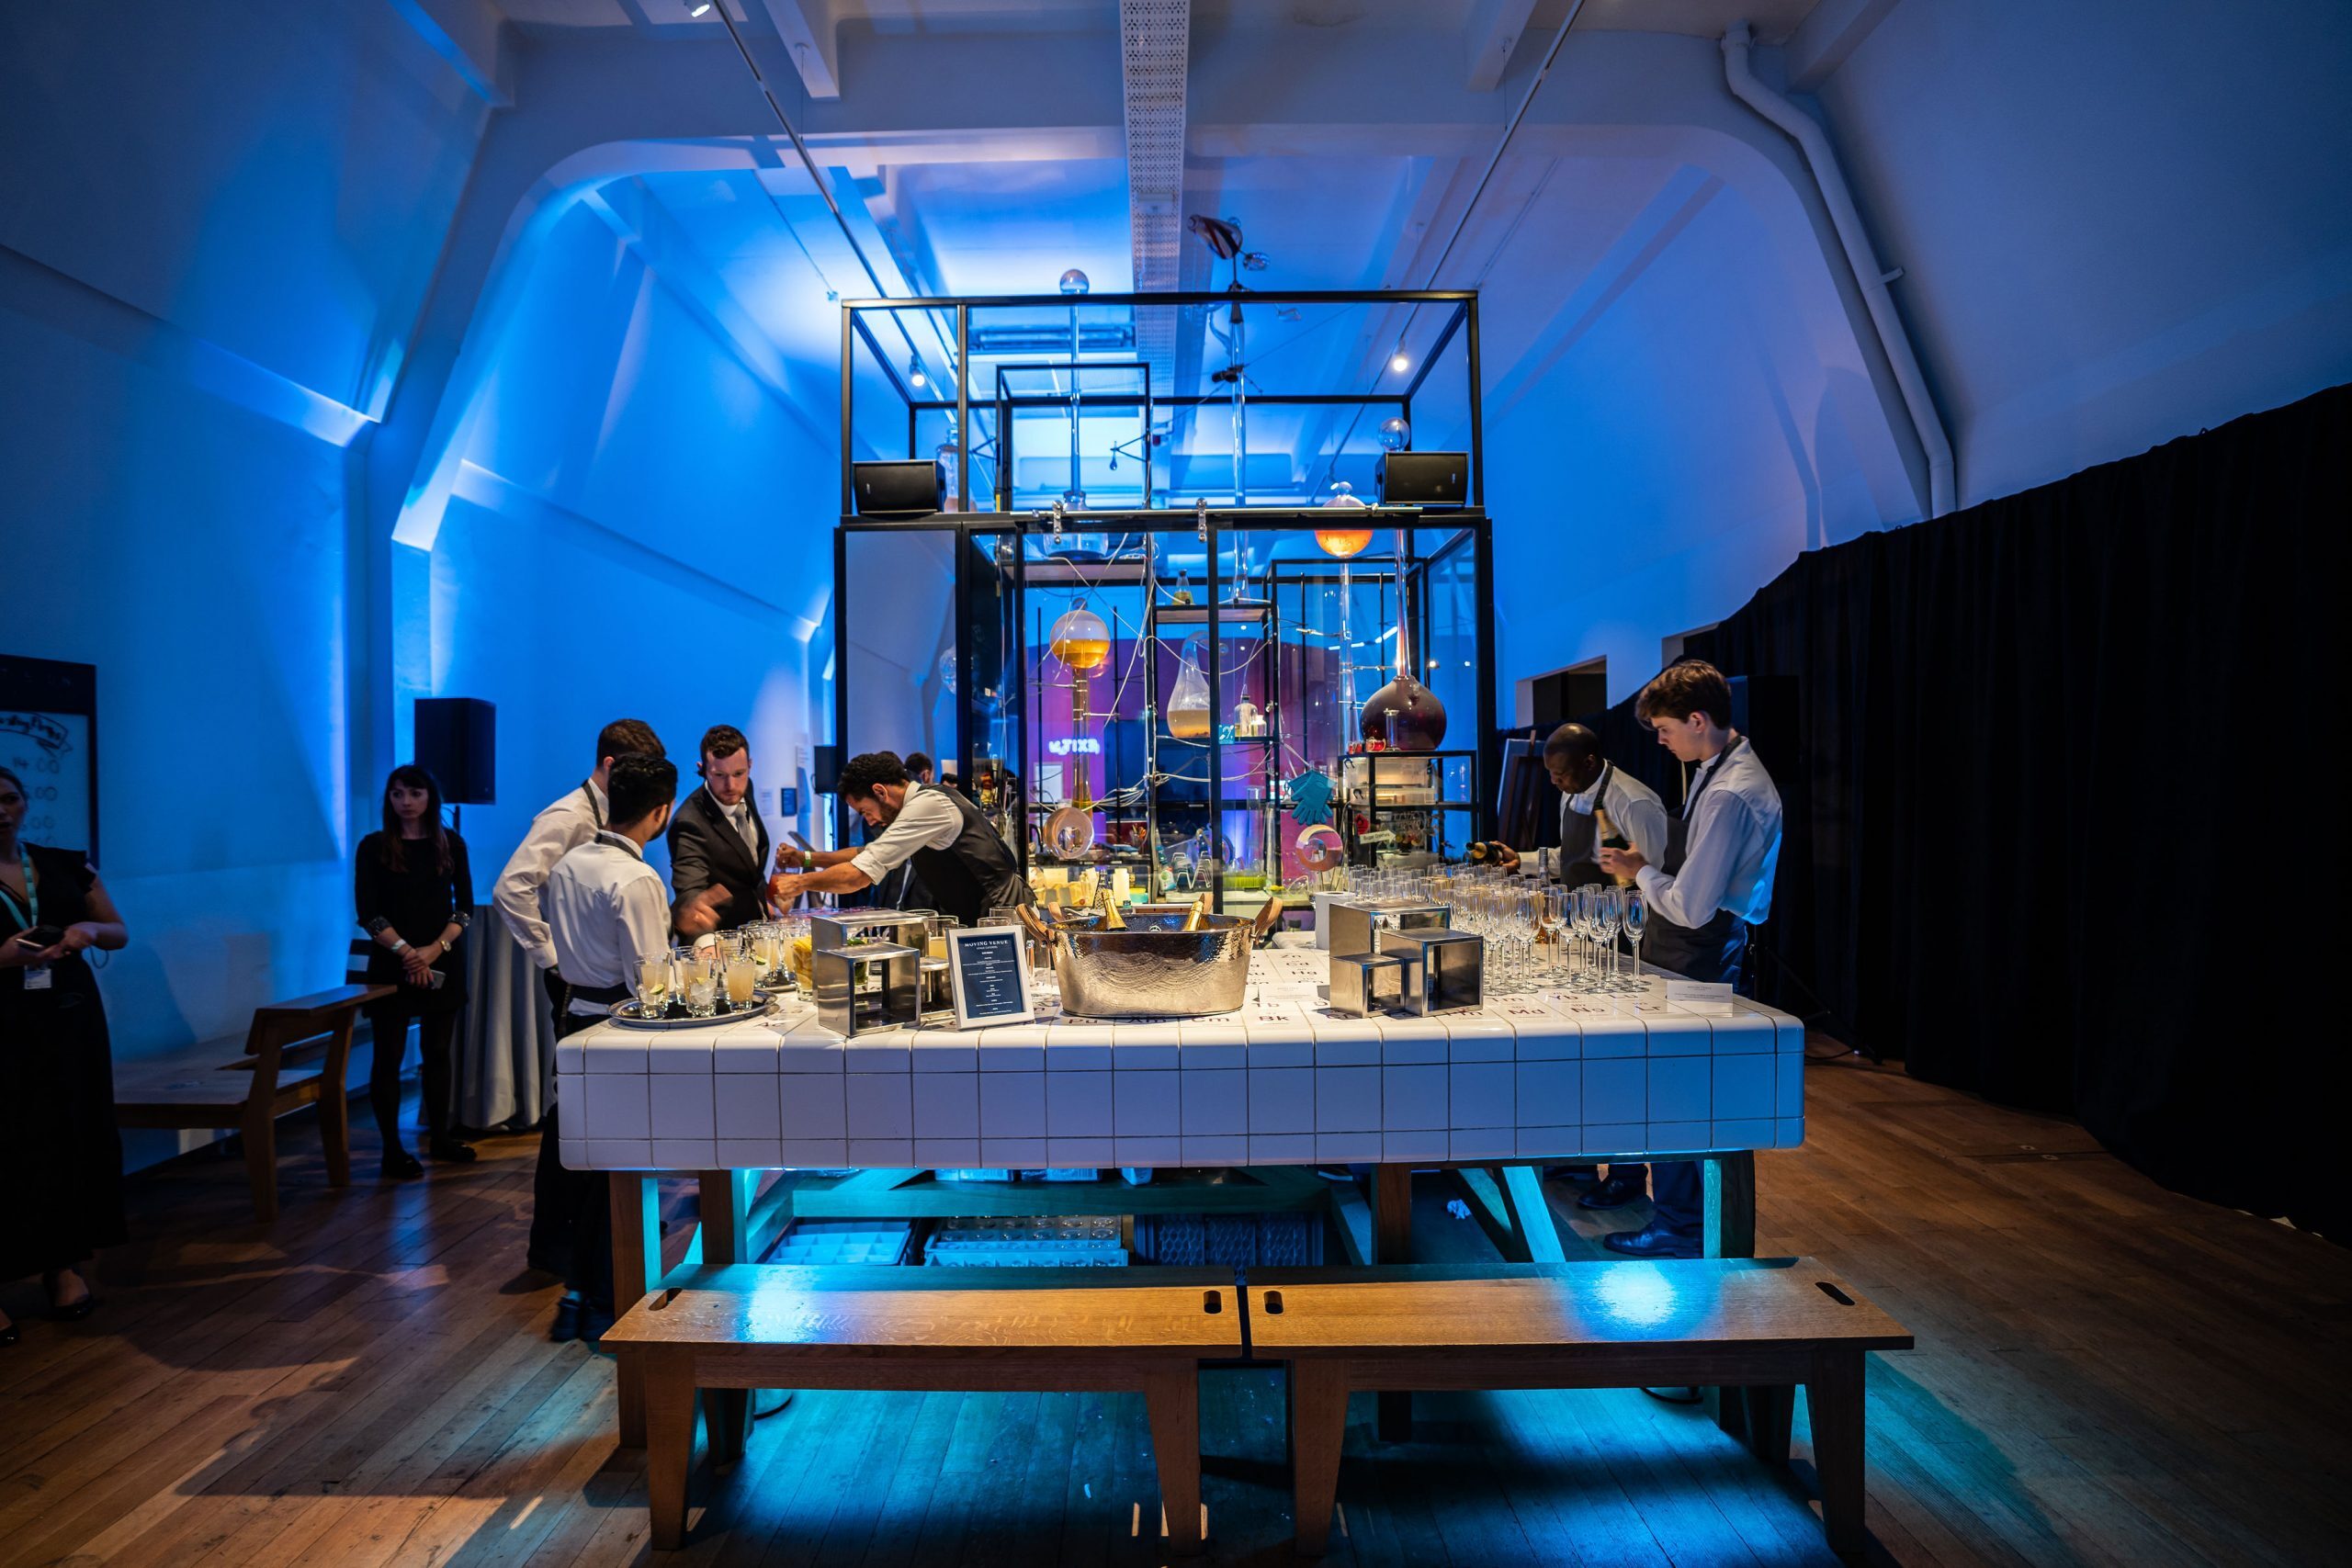
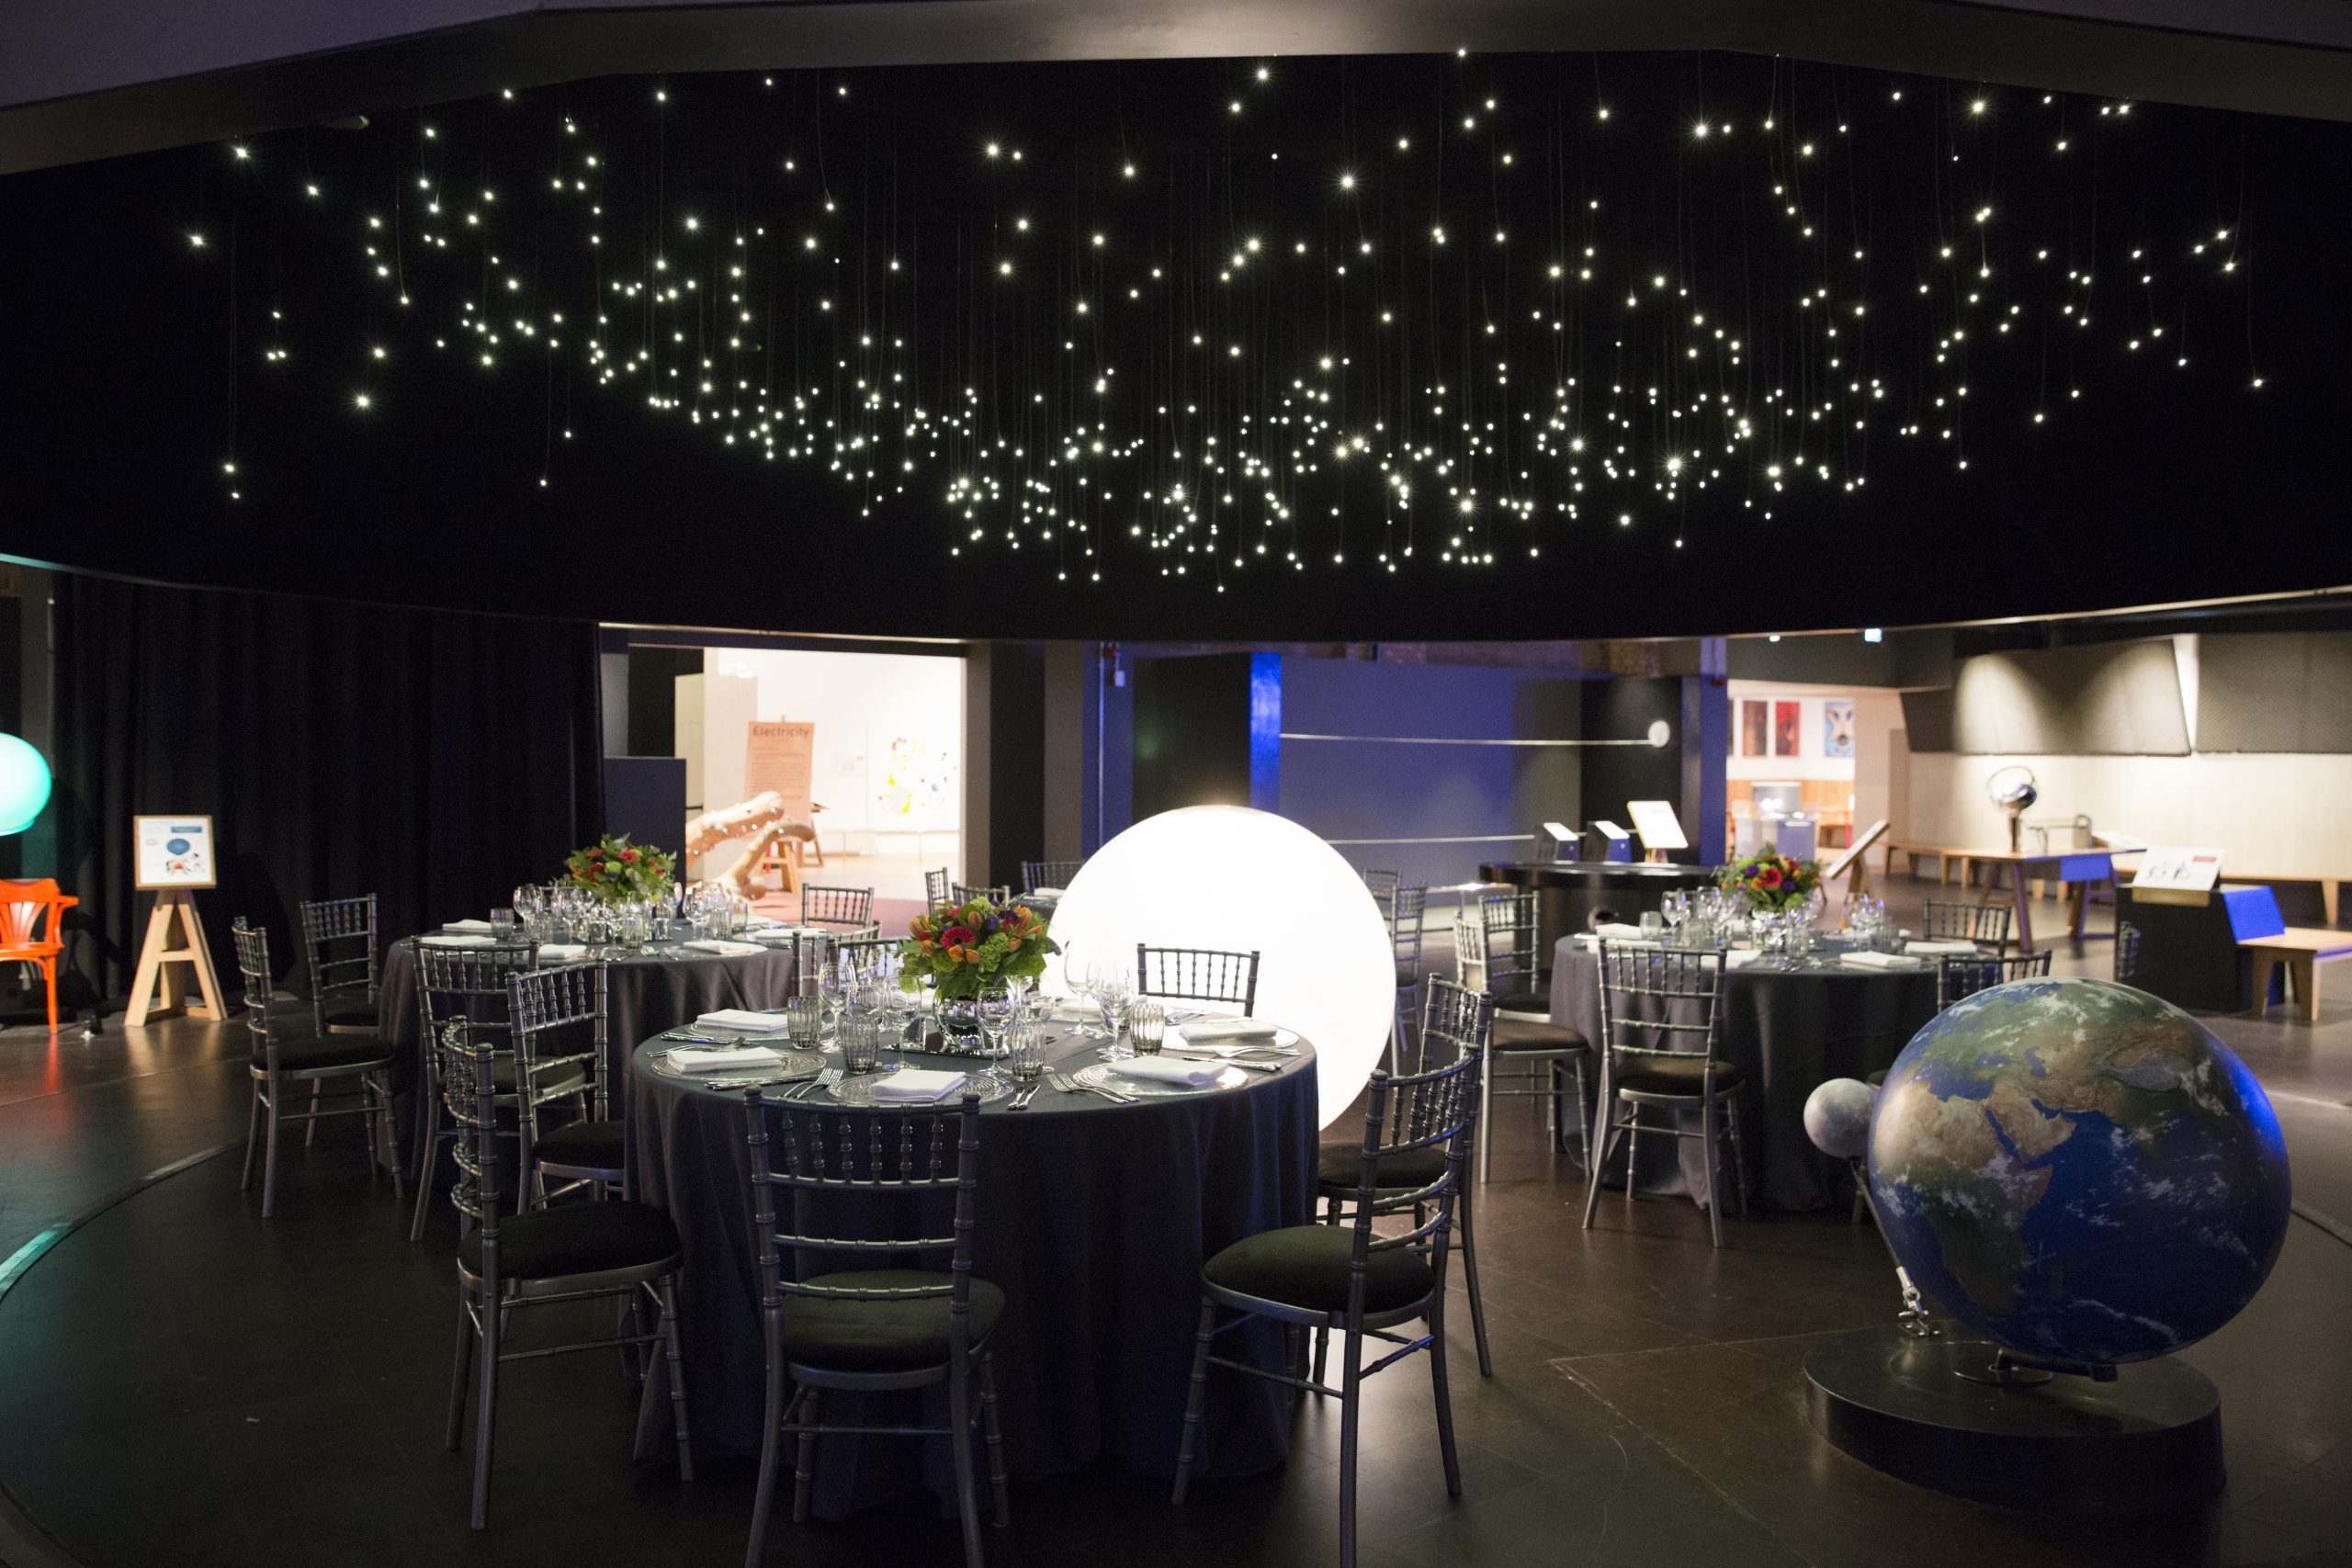
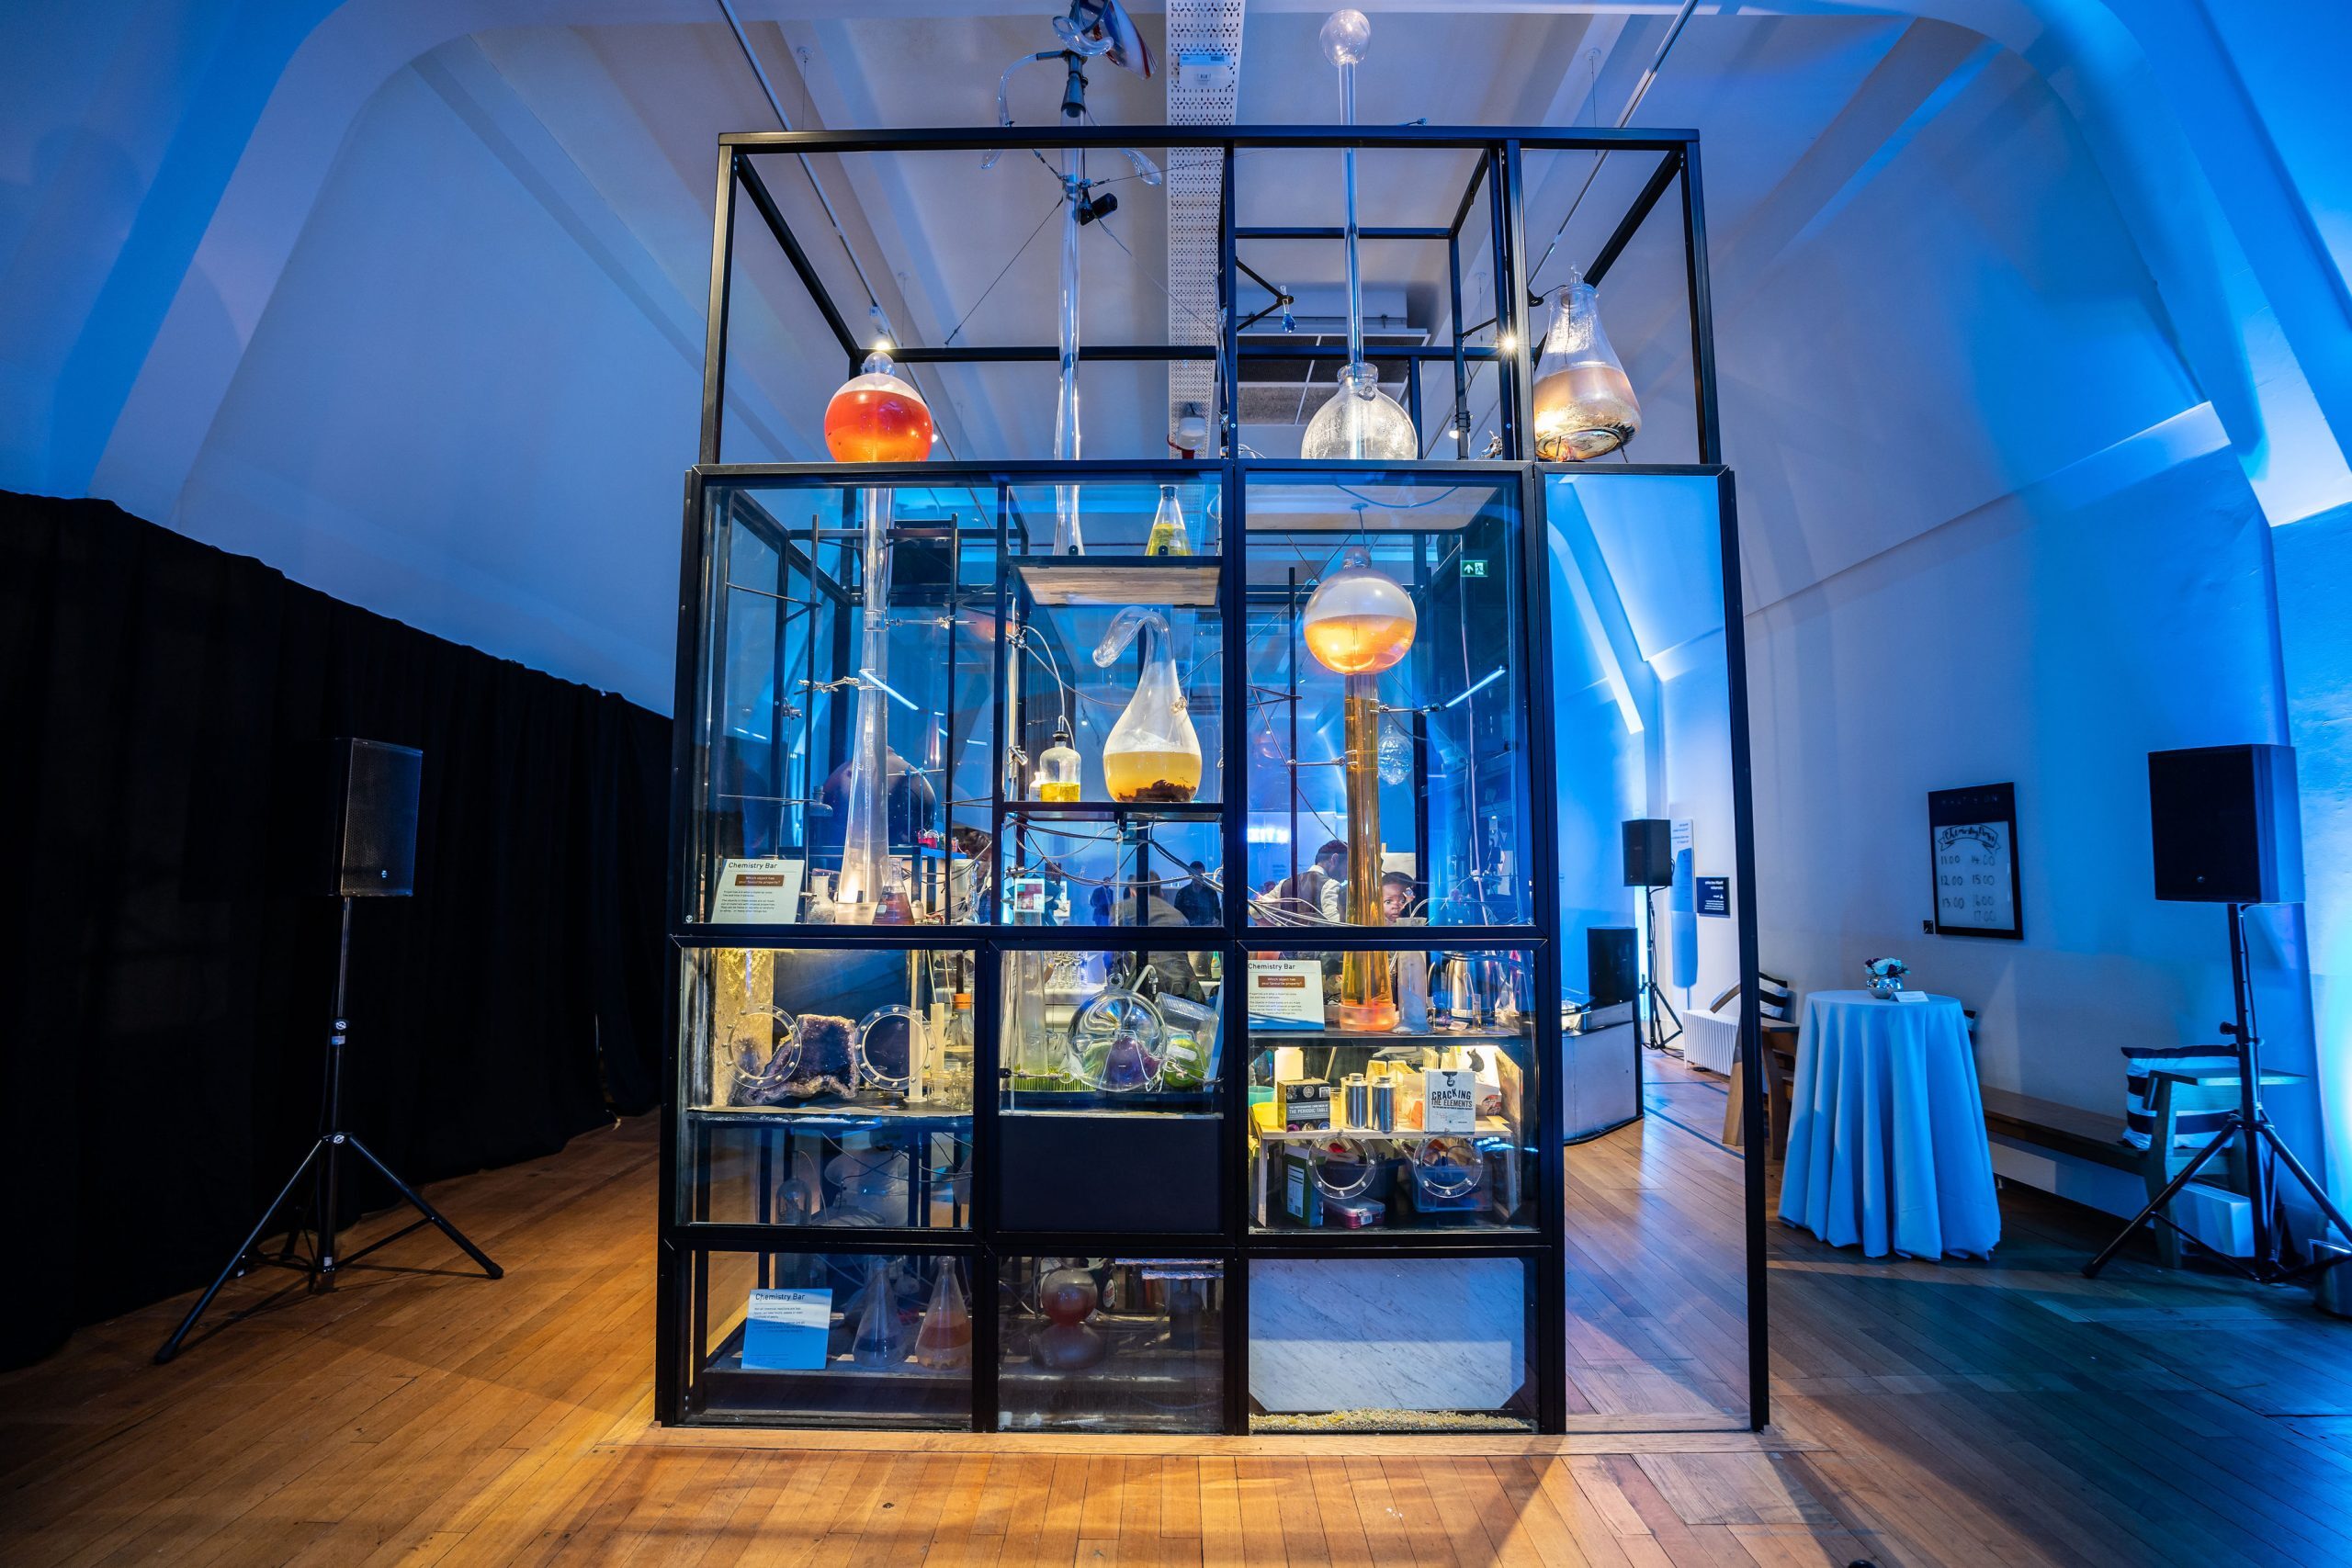
The networking reception with drinks and canapes at the end of the day will be downstairs in Wonderlab: The Equinor Gallery. “Fuel your imagination and immerse yourself in a world of wonder in the spectacular interactive gallery, Wonderlab: The Equinor Gallery. Get hands-on with real scientific phenomena. Order live experiments at the Chemistry Bar, see live lightning demos at the giant Tesla coil, play with physical forces on giant slides or enjoy a drink under a canopy of stars as the world rotates at the giant interactive orrery!”
Recommended accommodation nearby
If you are traveling to London for Cyber Exchange 360: Talk to the Board, Pulse can recommend a variety of hotels within walking distance to the Science Museum.
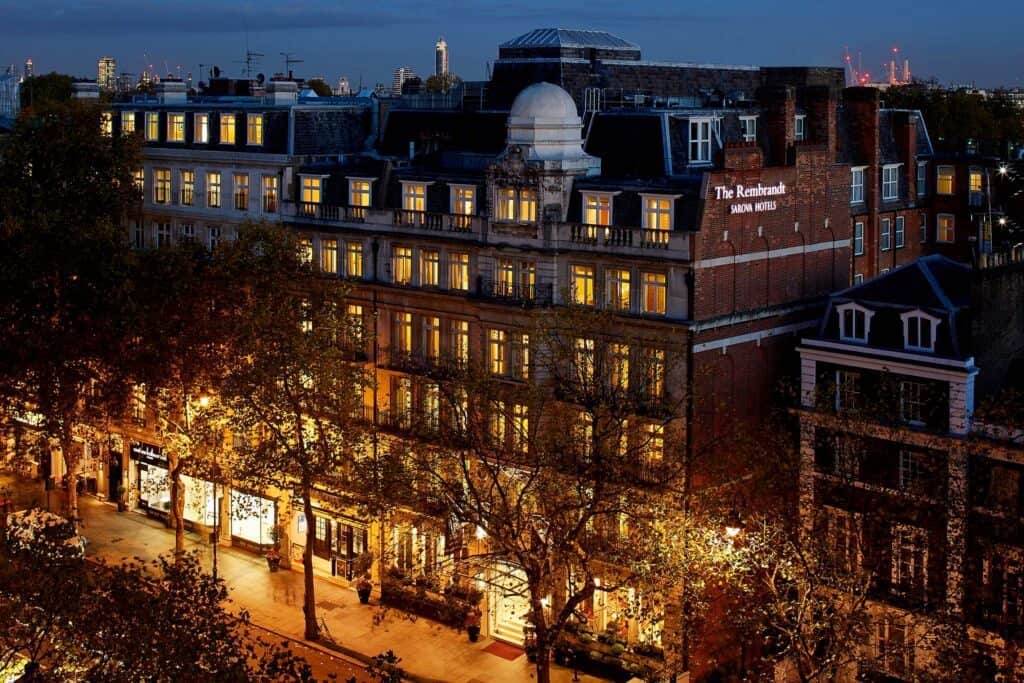
The Rembrandt Hotel
www.sarova-rembrandthotel.com
11 Thurloe Pl, South Kensington, London SW7 2RS
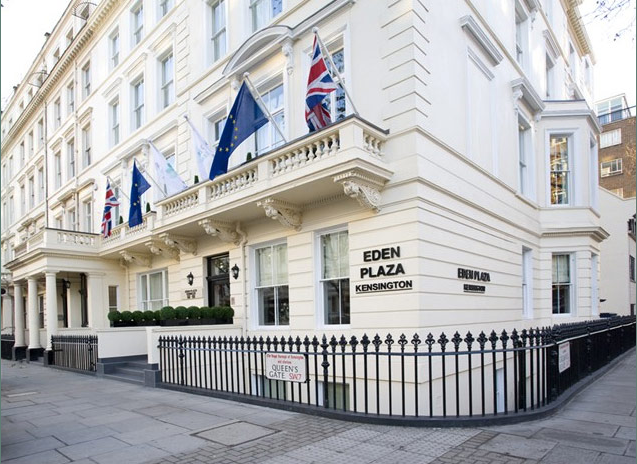
Eden Plaza Kensington
www.edenplazakensington.co.uk
68-69 Queen’s Gate, South Kensington, London SW7 5JT
The Queen’s Gate Hotel
www.thequeensgatehotel.com
31-34 Queen’s Gate, South Kensington,
The Gore London – Starhotels Collezione
www.starhotelscollezione.com/en/our-hotels/the-gore-london/
190 Queen’s Gate, South Kensington, London SW7 5EX
Location
Science Museum
Exhibition Road, South Kensington, London SW7 2DD
Science Museum is located in South Kensington with beautiful surroundings and walking distance to some of London’s most famous landmarks such as Royal Albert Hall, Hyde Park, and Kensington Palace.
Directions
By underground
The nearest tube station is South Kensington. This is on the District and Circle lines and is a 5-minute walk from the museum. Gloucester Road tube station is also on the District, Circle and Piccadilly lines and is a 15-minute walk from the museum
By Bus
Bus routes 14, 49, 70, 74, 345, 360, 414, 430 and C1 stop outside South Kensington Underground Station.
Bus routes 9, 10, 52, 452 and 70 stop outside the Royal Albert Hall on Kensington Gore.
By car
The nearest pay and display car parking is in Prince Consort Road and Queen’s Gate. Royal Borough of Kensington and Chelsea have more information about parking near the museum.


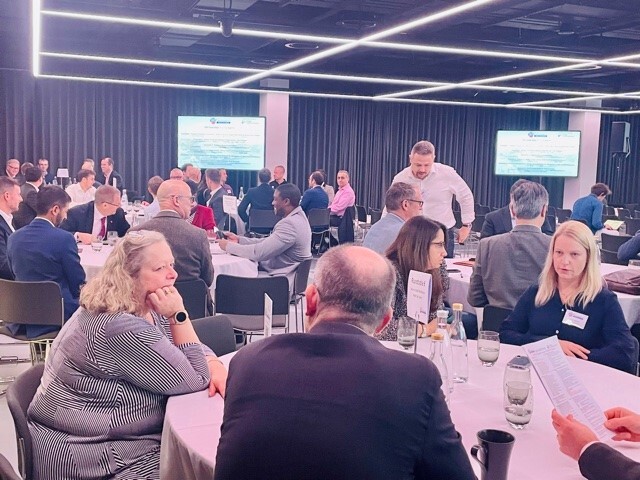
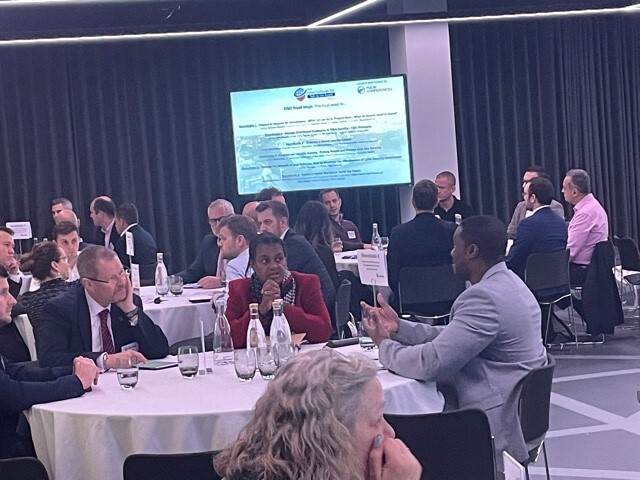
Gallery – 3th Cyber Exchange 360: Talk to the Board
Downloads – Cyber Exchange 360: Talk to the Board
Information 2021 Event
 Download 2021 Flyer & AgendaDownload Health and Safety Measures
Materials from Previous Event
 Download Post Event ReportComputer Weekly Article - Growing board focus on cyber risk challenges
On the Pulse Blog: Benchmarking the Board Conversation
Testimonials – CISO 360 series
 “Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra
“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim
“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica
 “Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS
 “If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World
“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“
Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter
 “CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint
“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018