
The Expanded Cyber 360 Exchange & Talk to the Board will be hosted 11-12 November 2020 in London
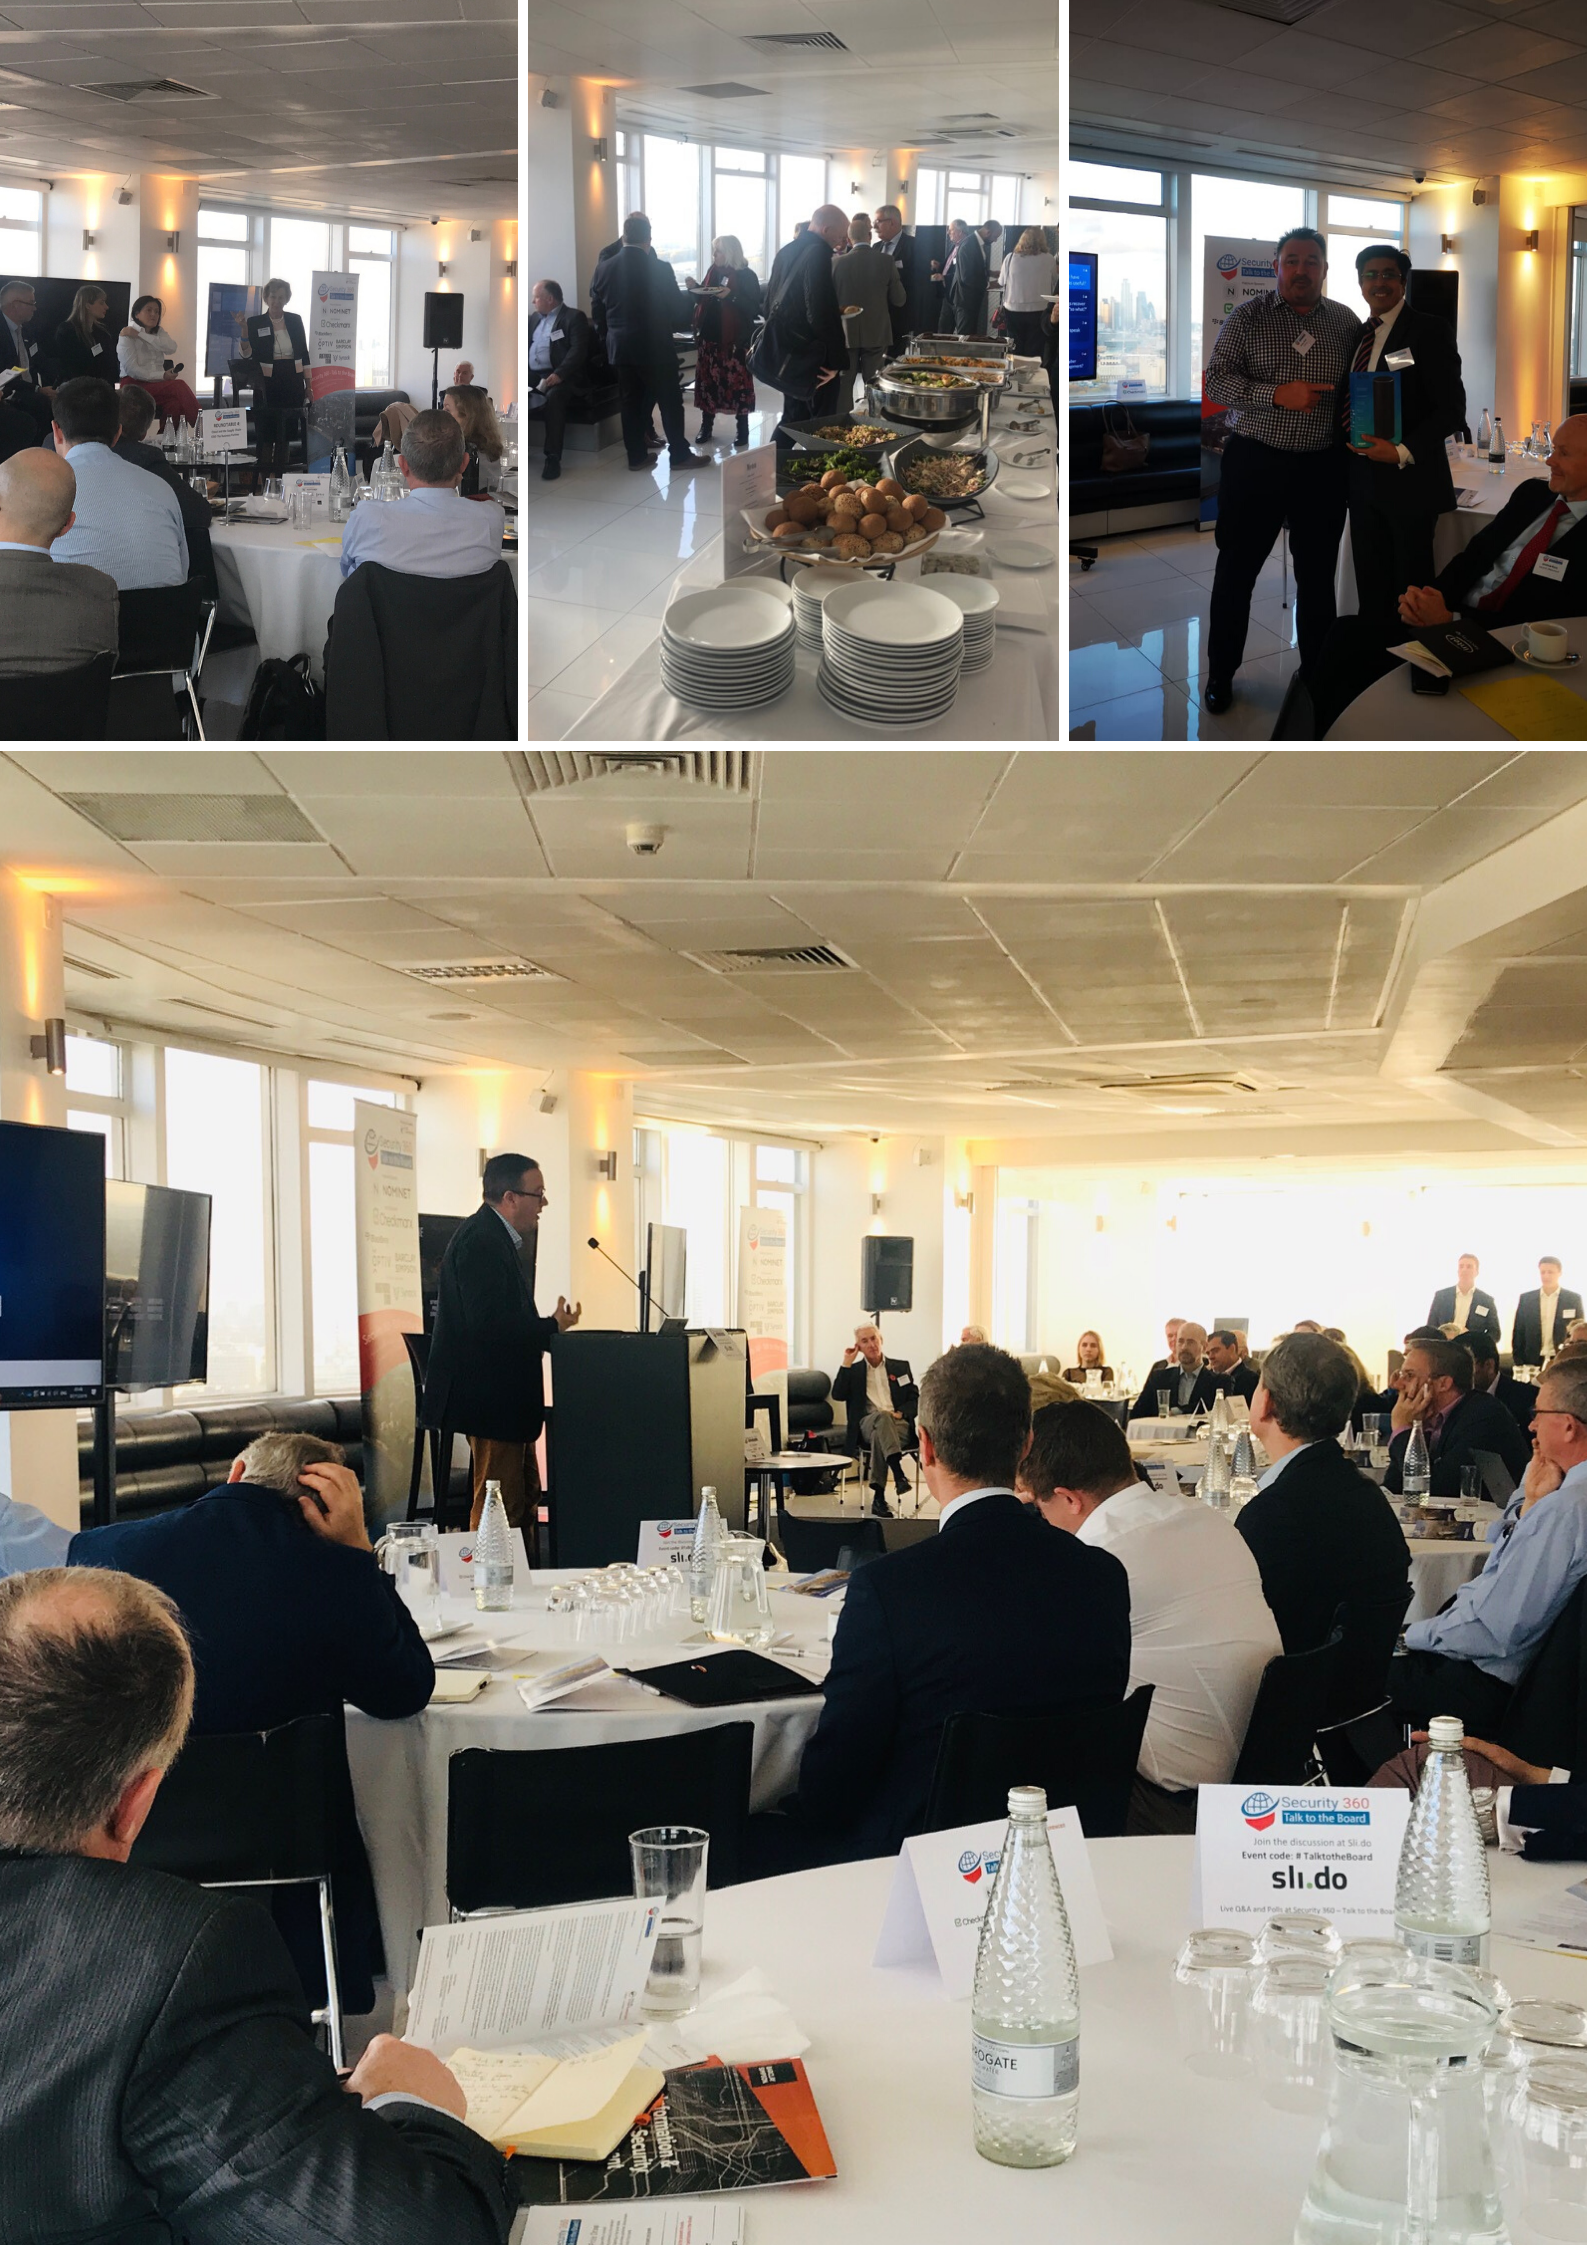
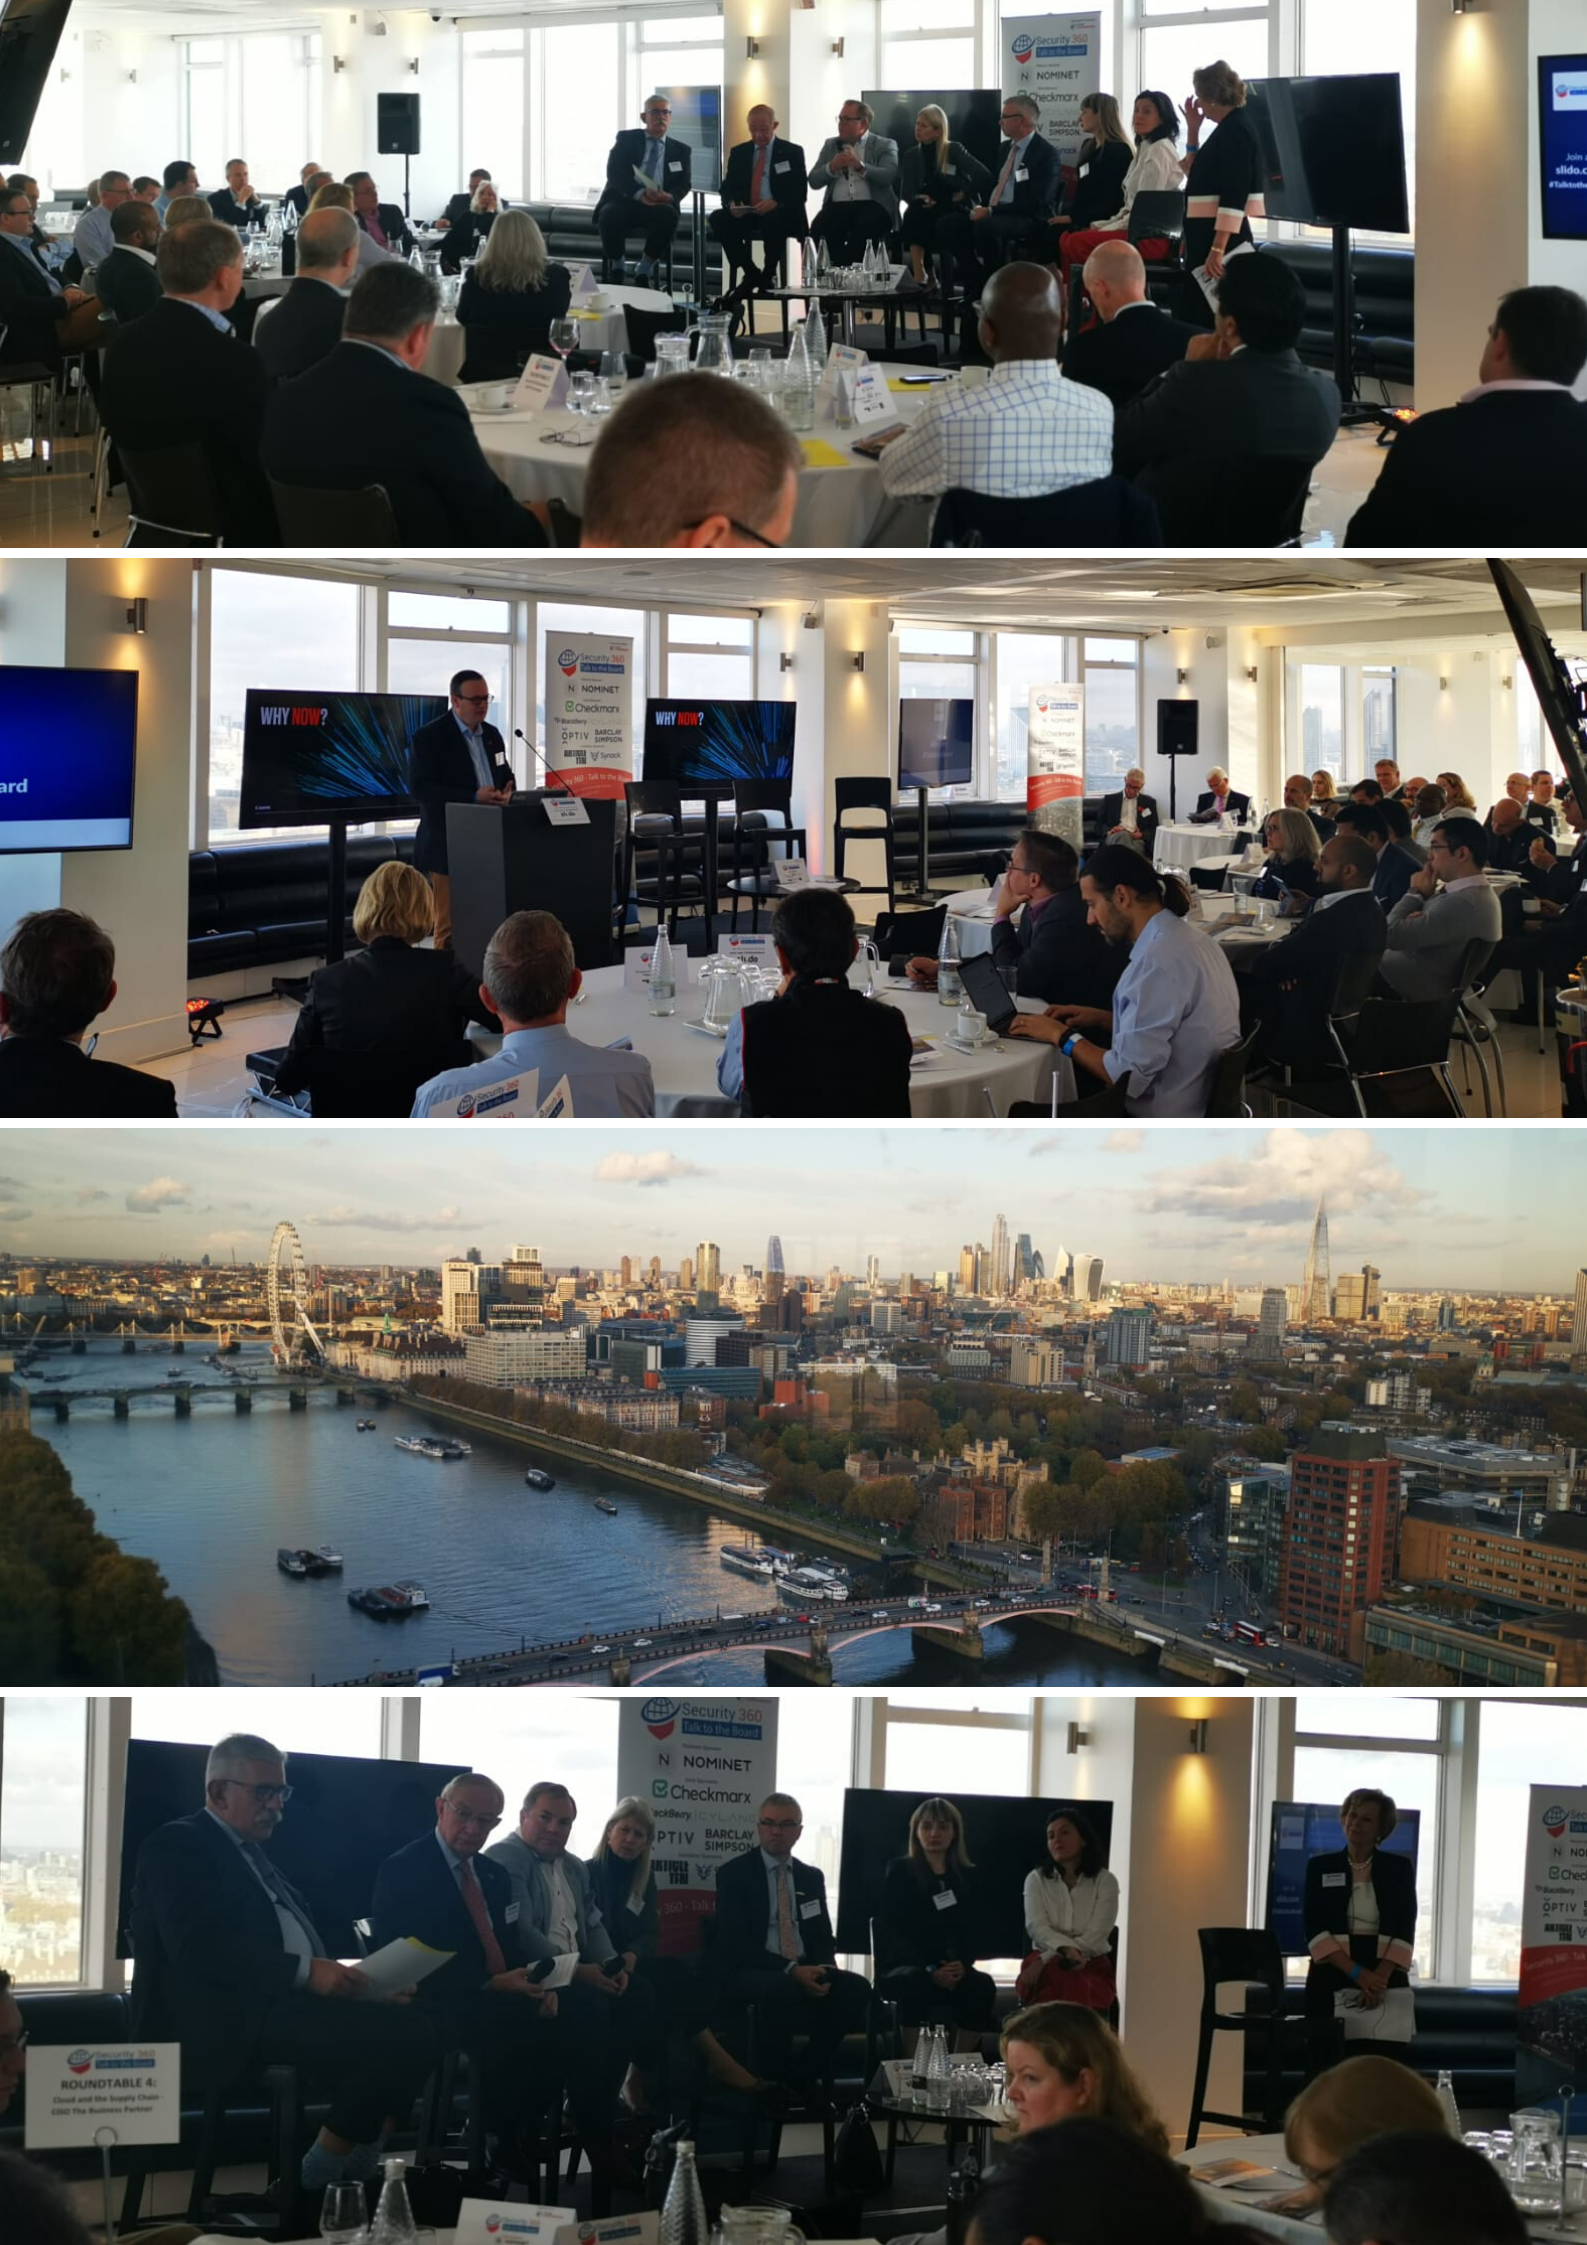
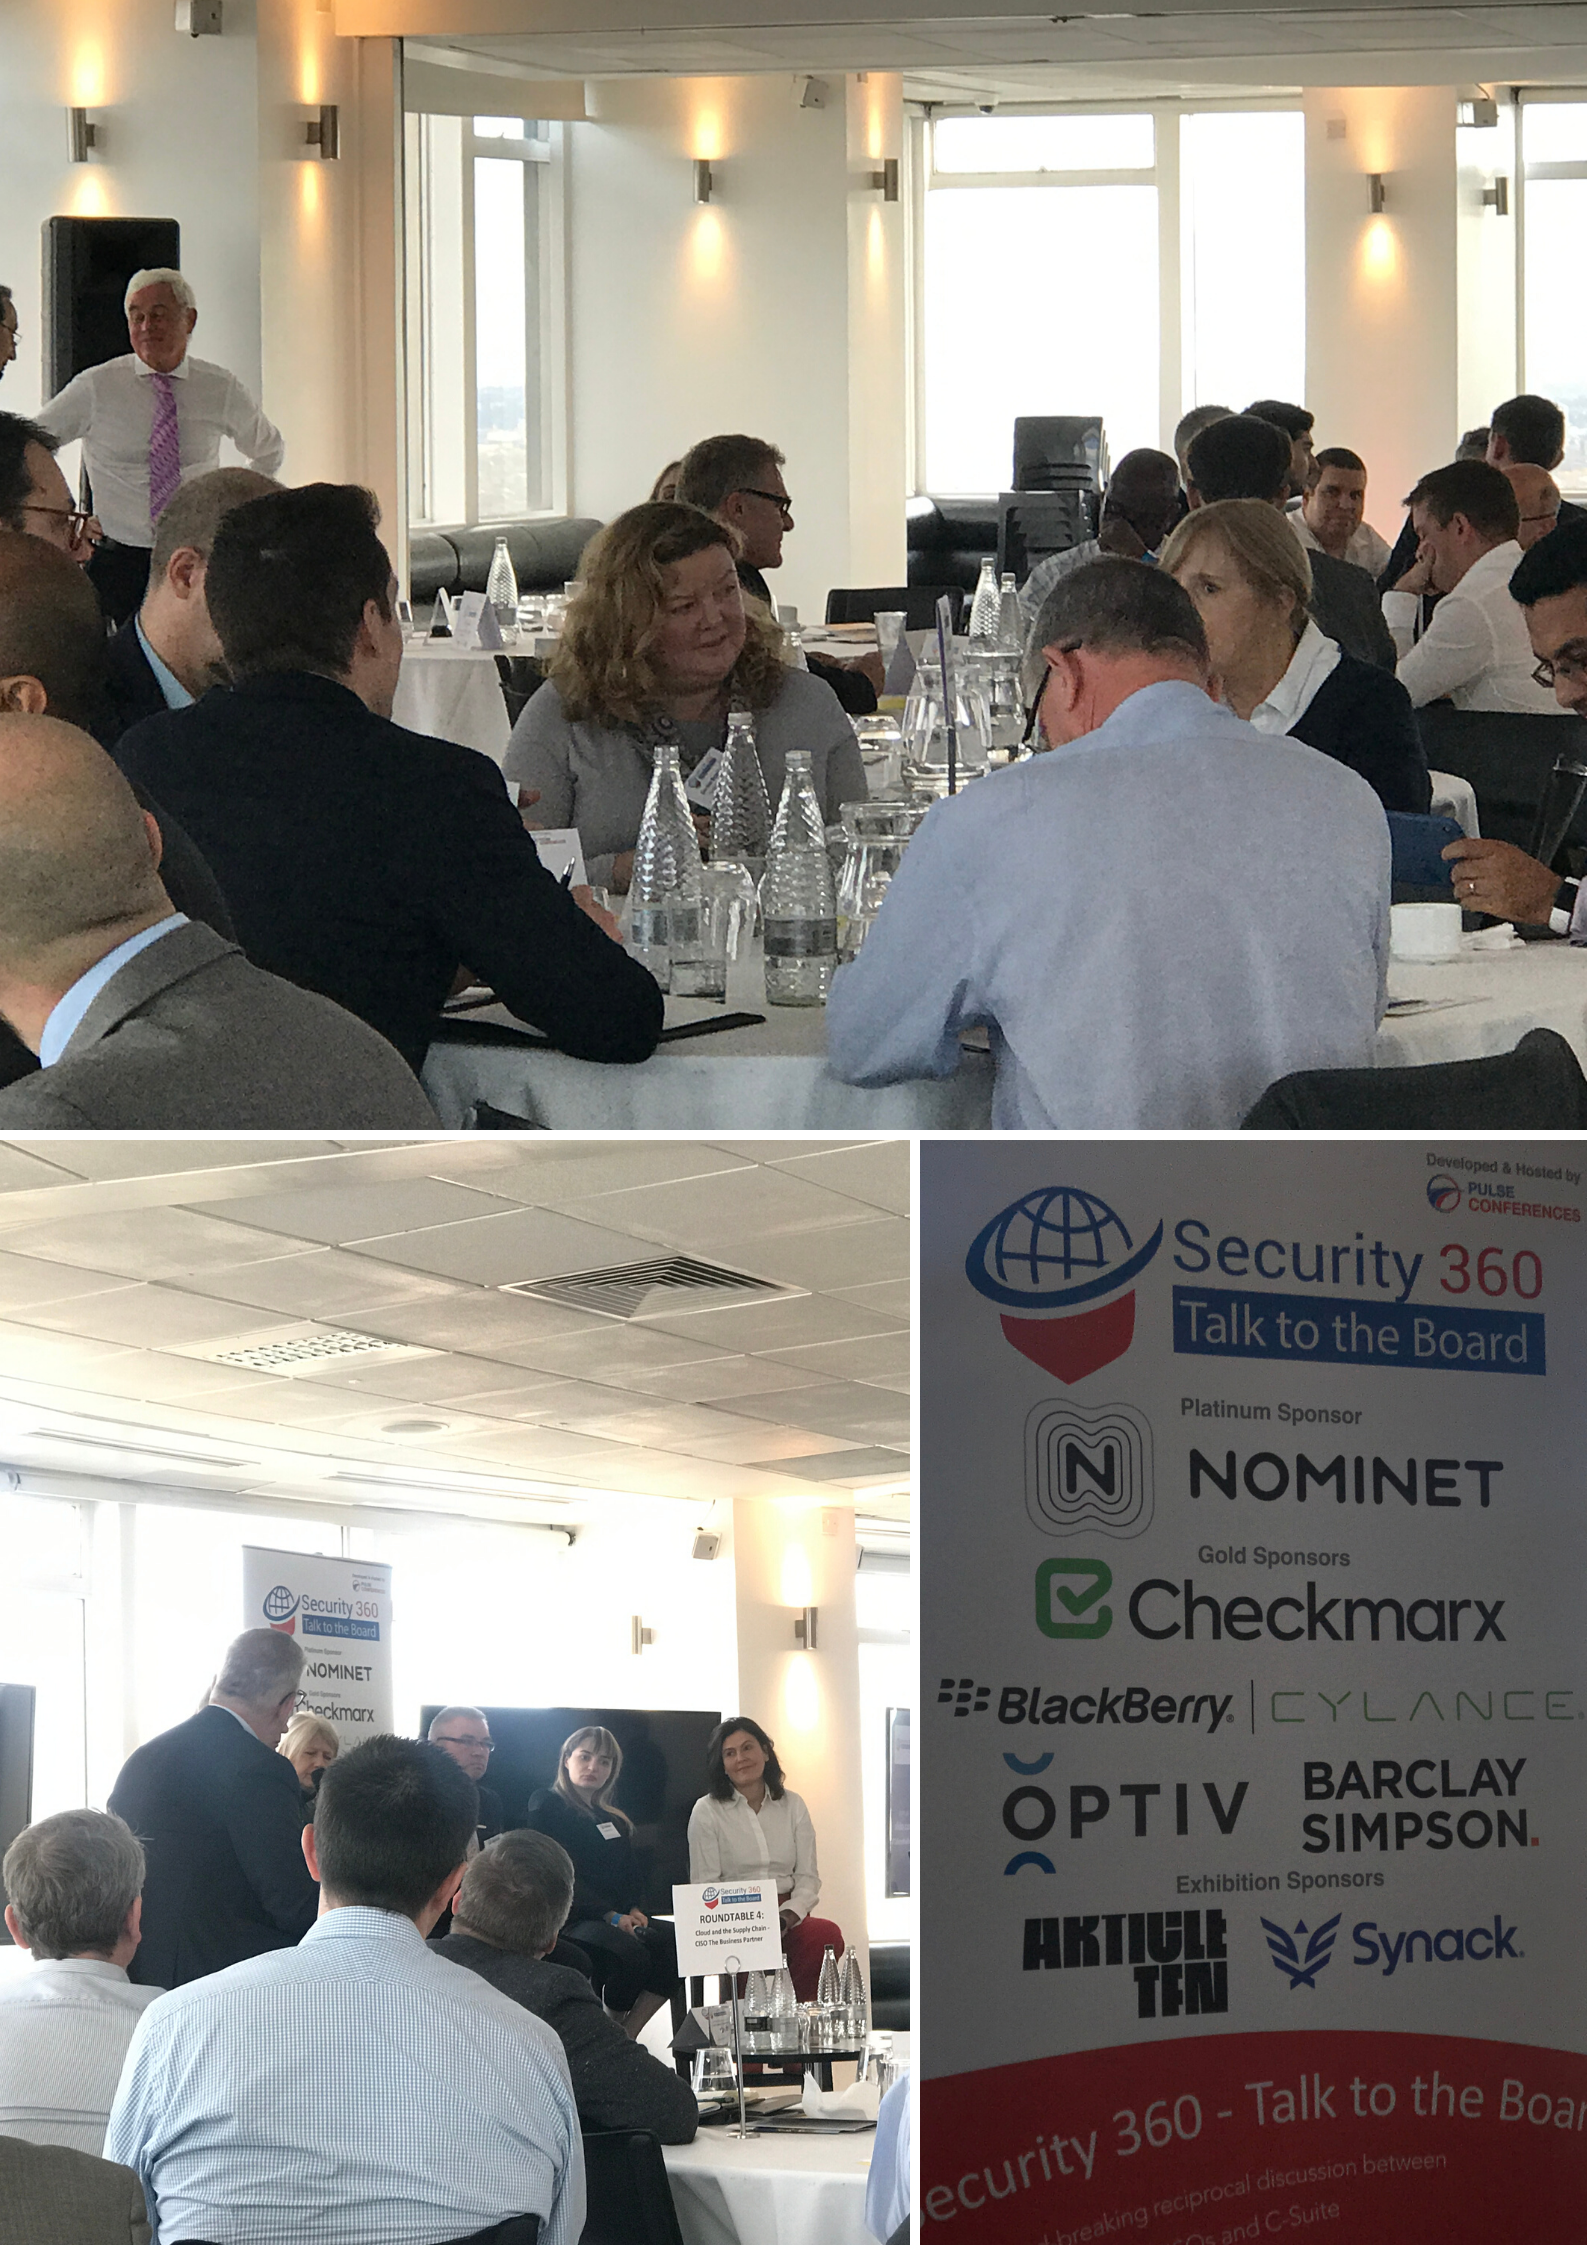
Thank you to everyone who attended Security 360-Talk to the Board, 7 November 2019 at Atmosphere 29 in London!
“This conference is different in a very positive way – producing new insights where others just repeat the same old content”
Mark Nicholls, Head of Information Security, Peabody
A ground-breaking reciprocal discussion between Board Members, CISO/CSO and C-Suite
• question a real Board of Directors
• connect with peers to benchmark cyber risk strategy
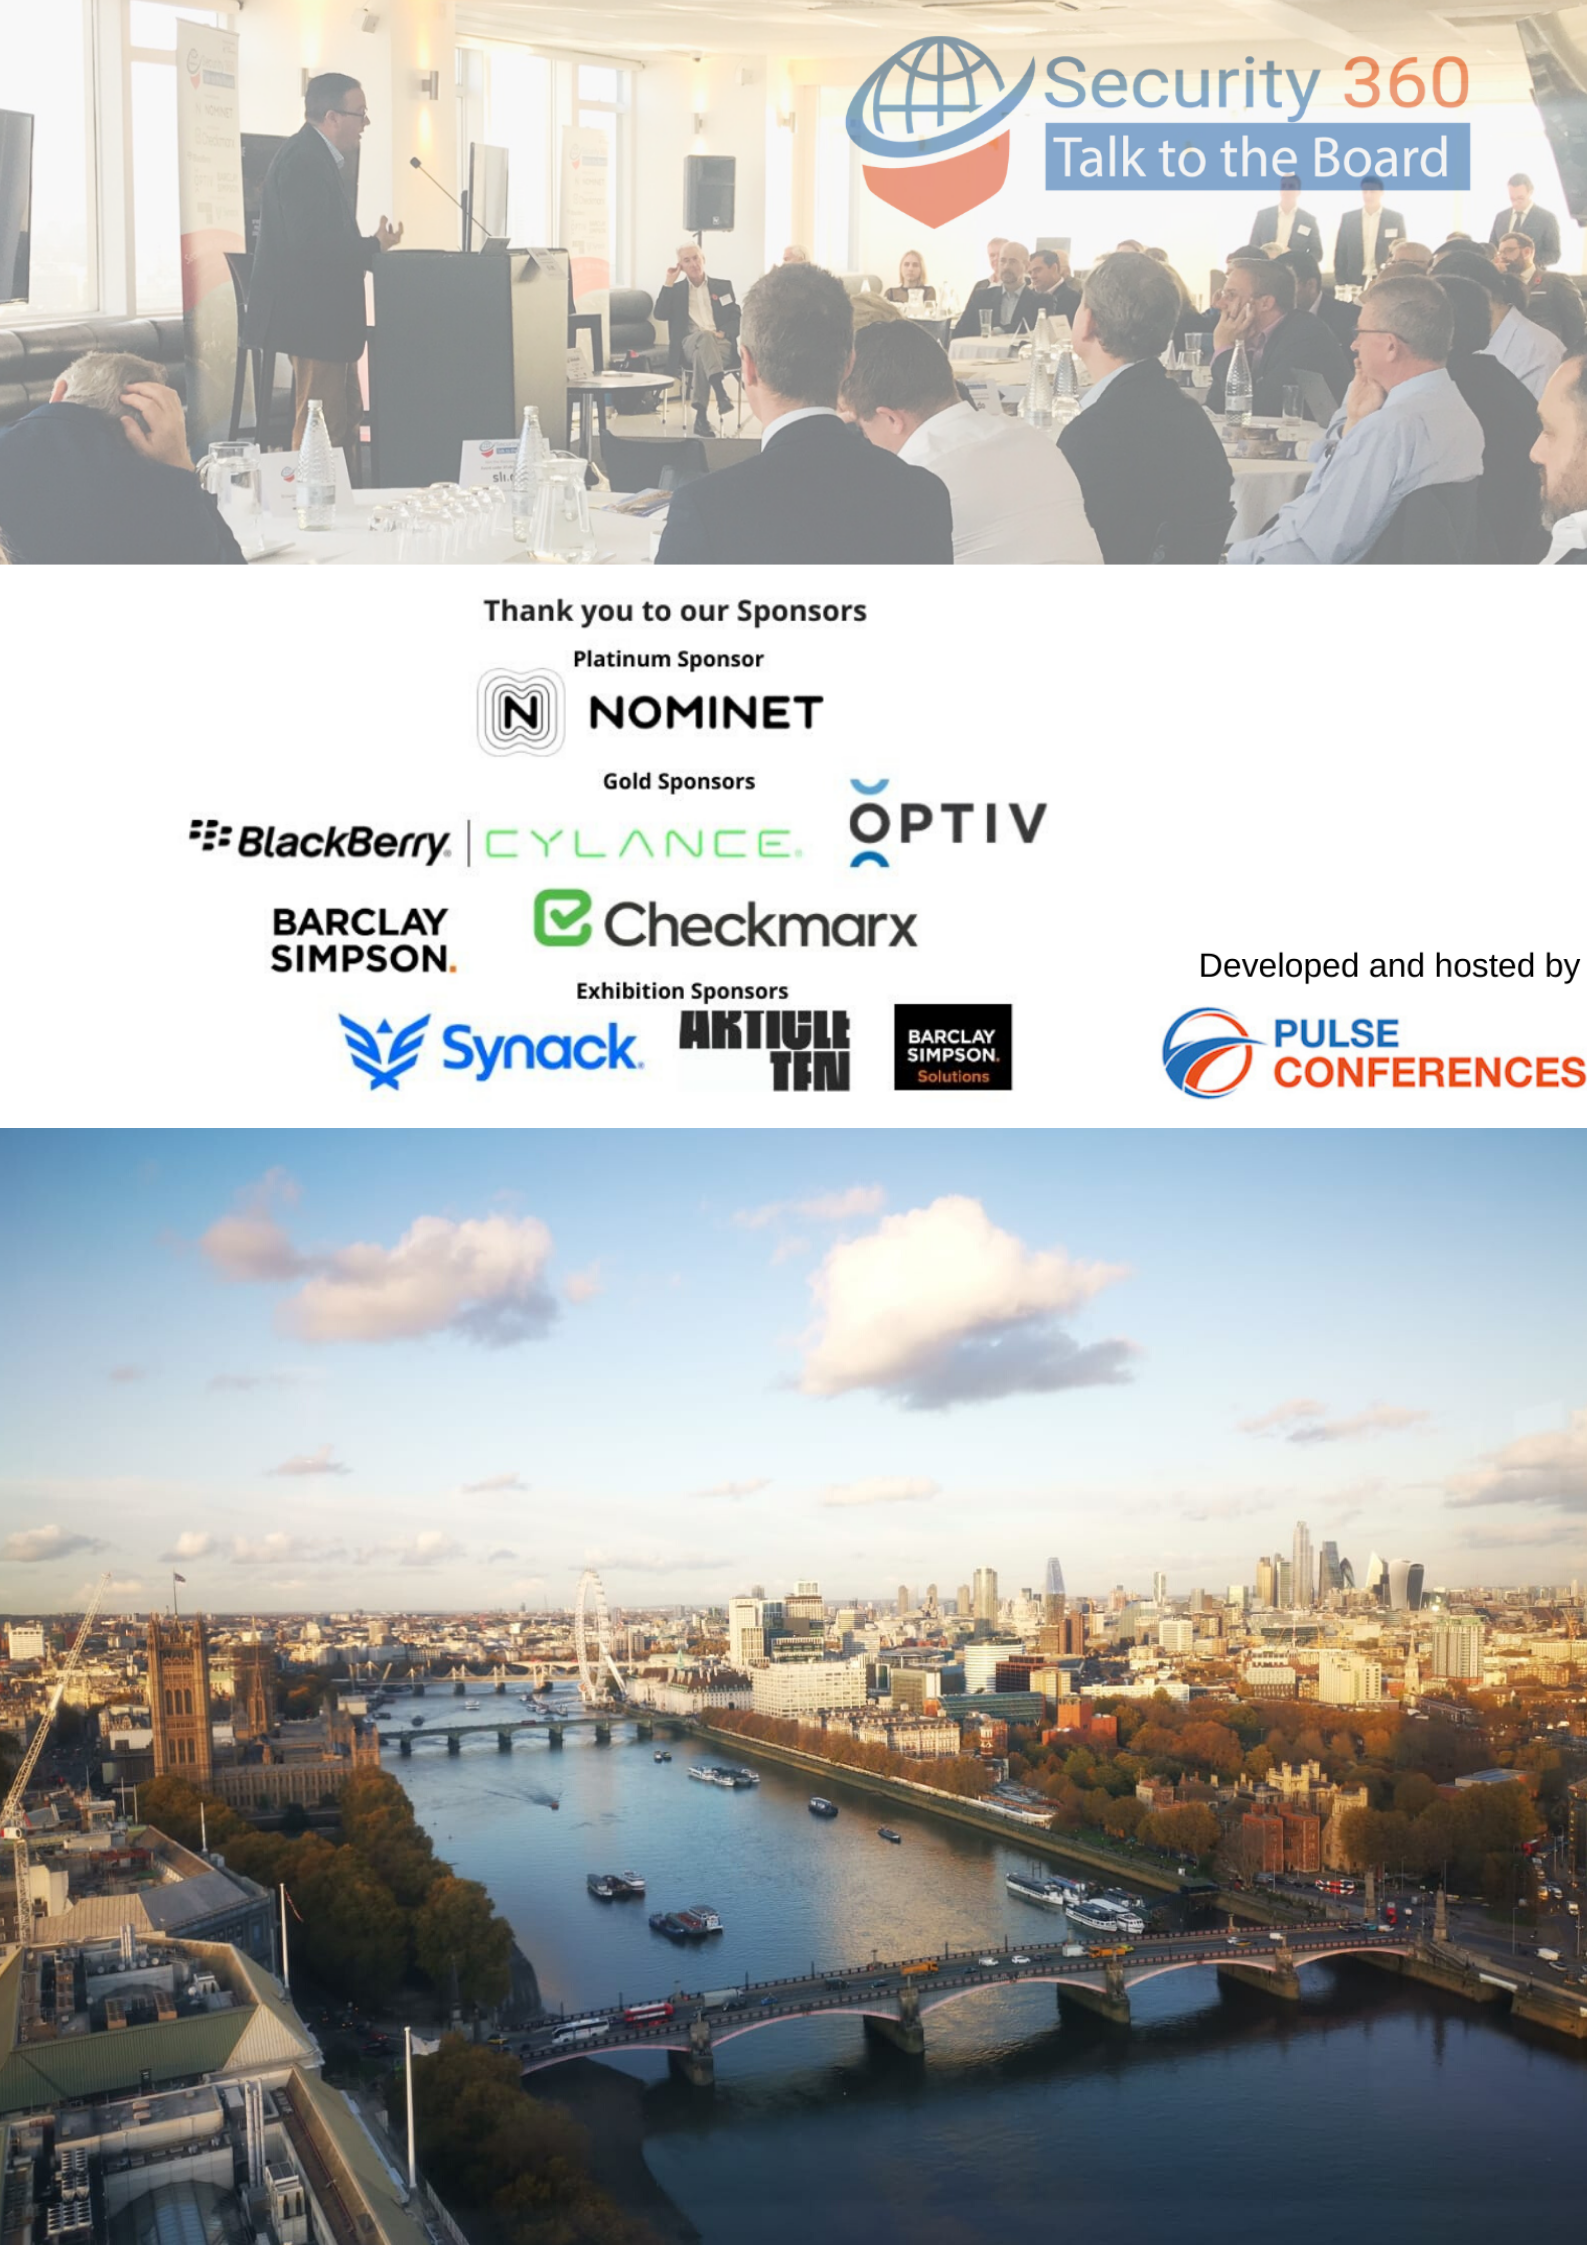
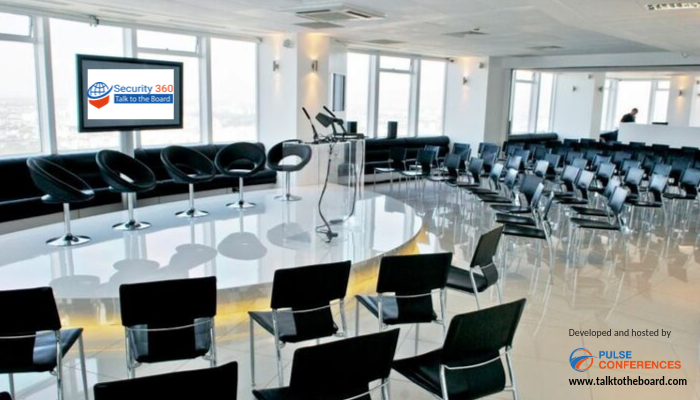
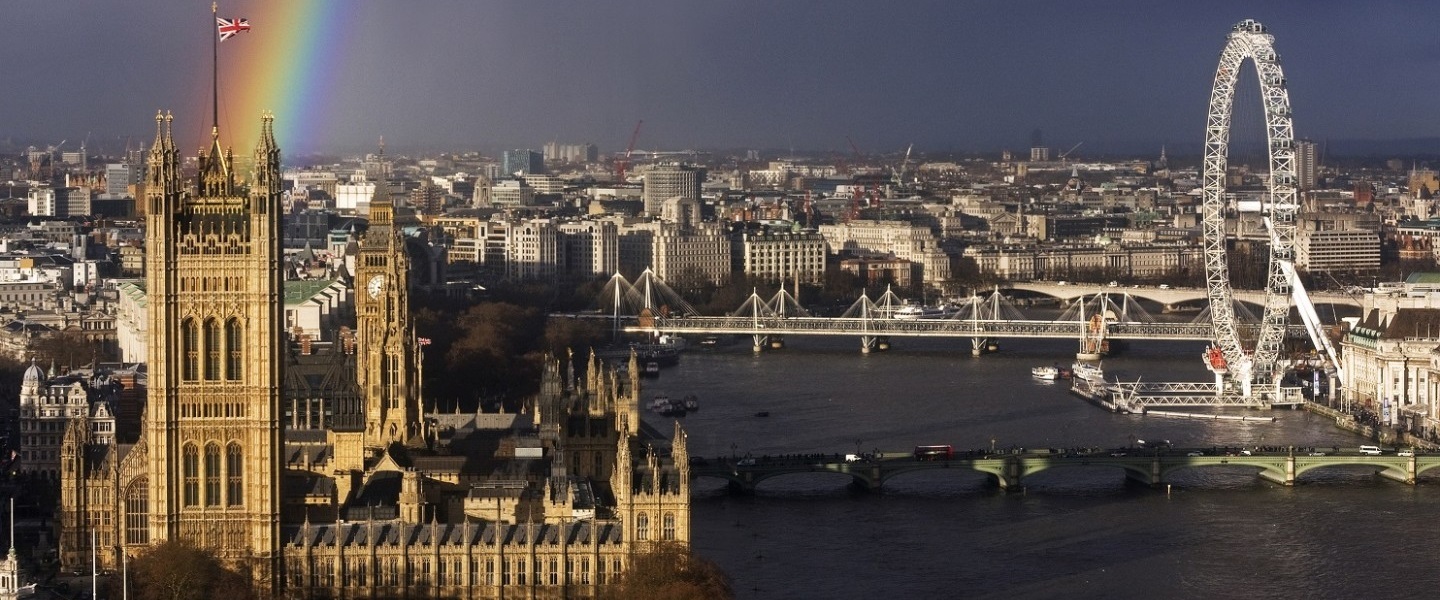
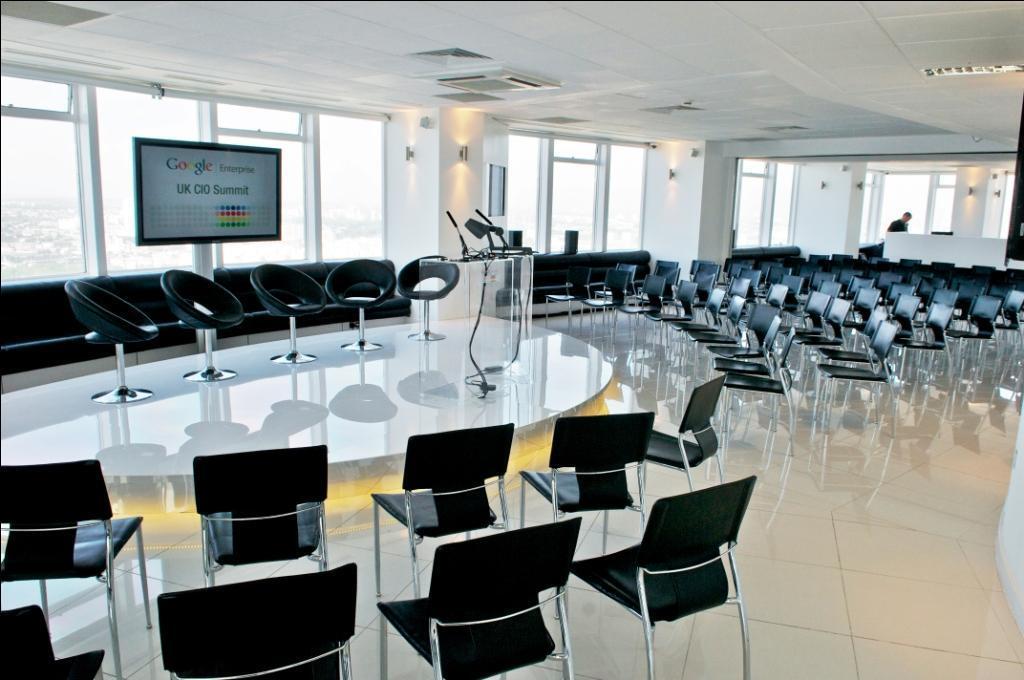
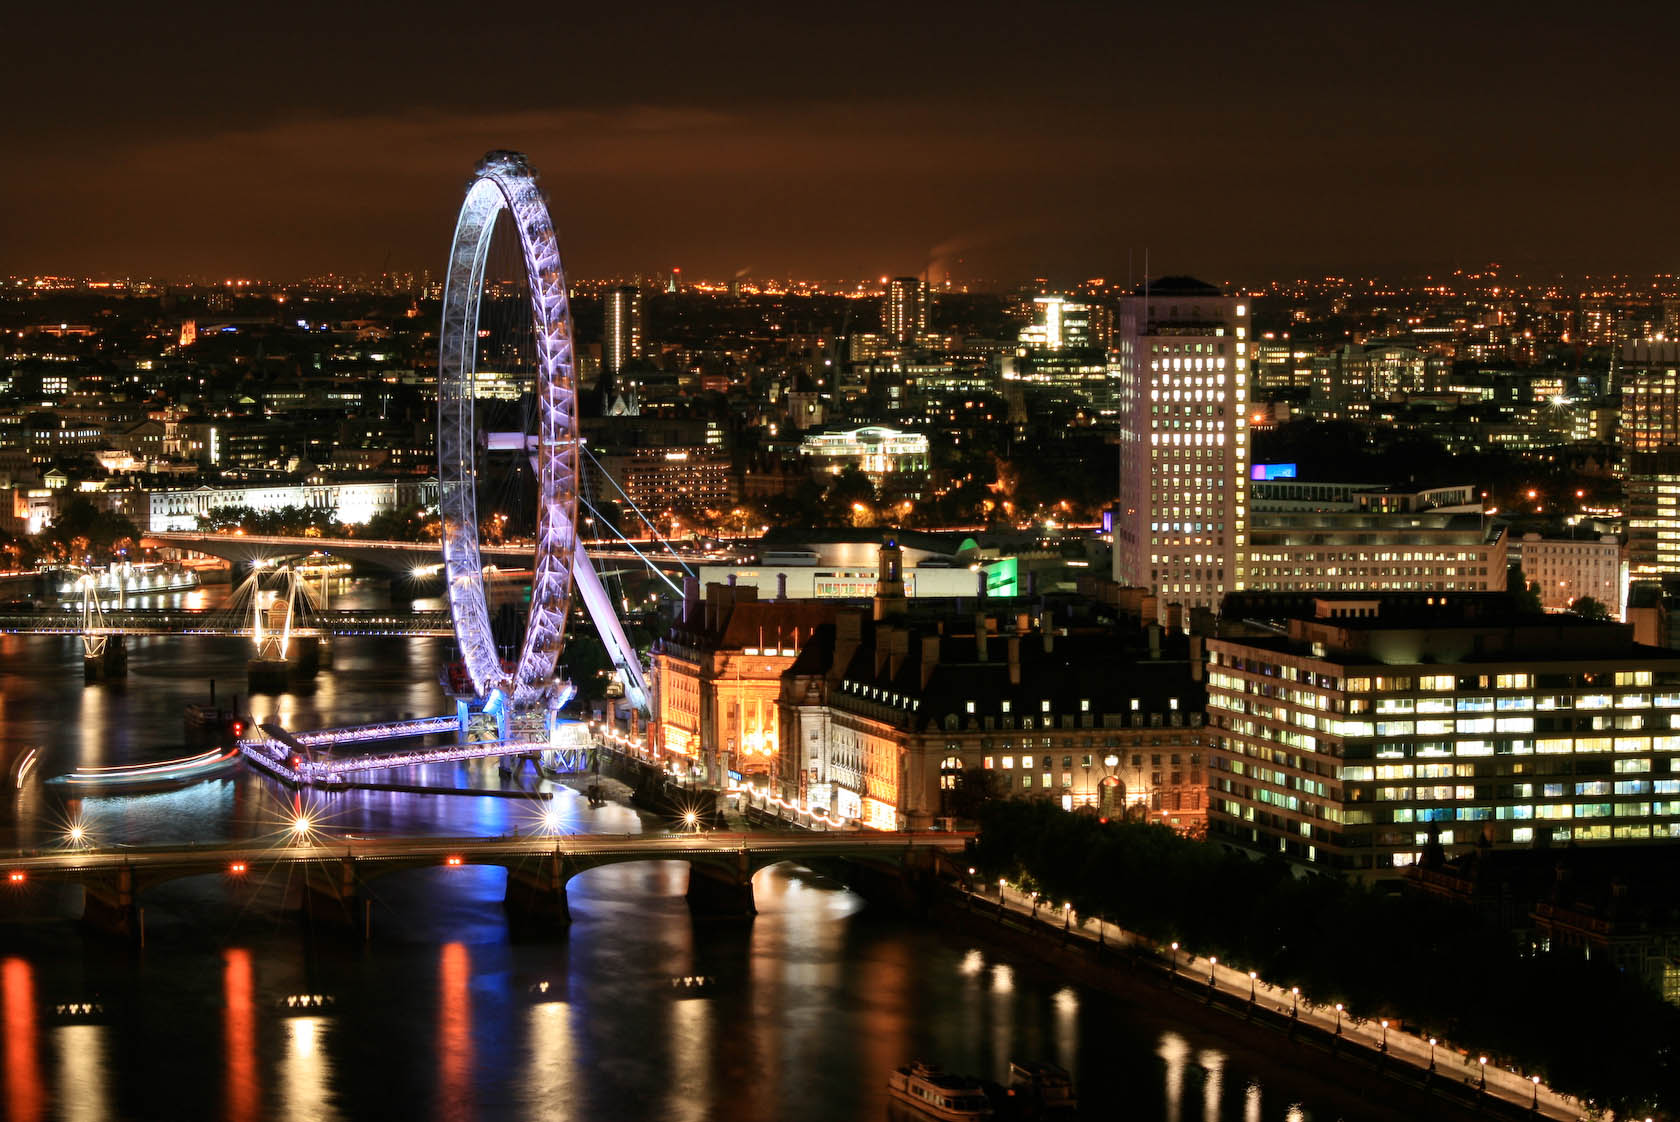
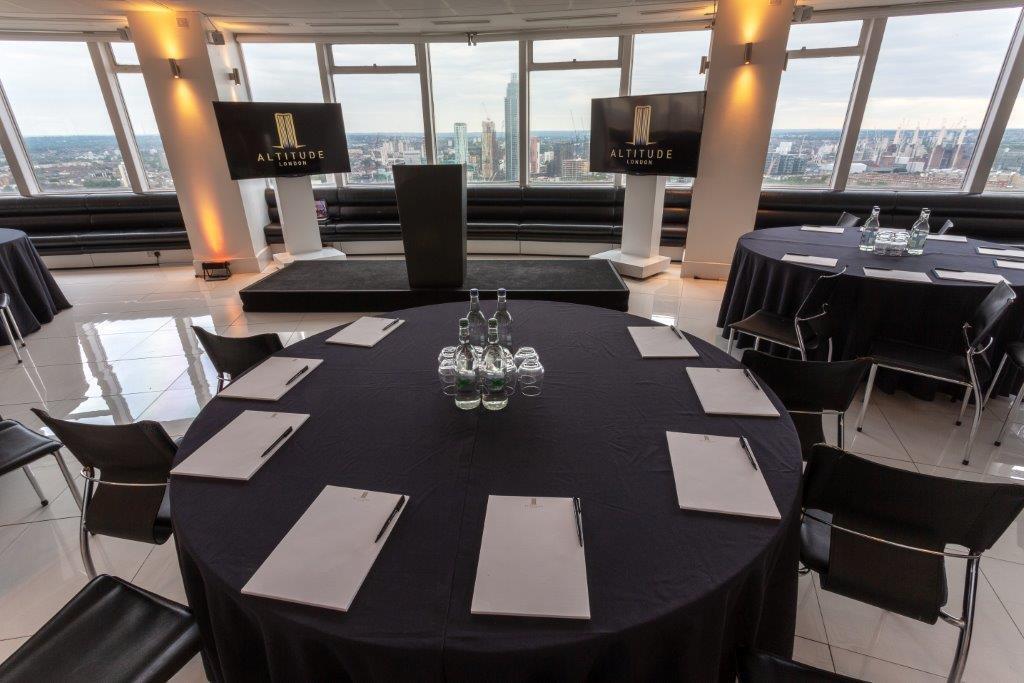
This unique one-day conference was hosted Thursday 7 November at Atmosphere 29, a unique space near Westminster that benefits from stunning wraparound views of the City of London and beyond.
This sound-boarding think tank enabled guests to directly interact with and question a panel of Board Directors from various large companies.
Agenda Timings at a Glance
08:45-15:45 Talk to the Board Conference – Atmosphere 29
15:45-17:00 Reception – Atmosphere 29
17:30-22:00 Spying Room, Morpeth Arms
 Download Pulse Innovate Report from Talk to the Board 2018 here!
As a CISO/CSO, why attend?
- A rare chance to question a real Board – with no consequences!
- Unique opportunity to find out what the perspective is of board members towards cybersecurity.
- To appreciate the importance first hand of speaking to the board in a way that makes them understand and care.
- Reciprocal exchange. A chance for the panel of Board Members to explain what they would like to hear from them or how they would like security leaders to communicate better.
- Immersive – all invited guests are expected to contribute to the discussions that will be held under the Chatham House Rule.
- Networking – the day ends with a networking reception!
- Pulse Innovate Report – receive practical take-aways on cyber risk and security as part of the Enterprise Risk Management strategy at Board level, and as part of a robust business.
As a Board Director or Non-Executive Director, why attend?
- Gain insights about how CISO/CSO as a group think and feel about current relations with the board, risk metrics, security investment and reporting structures, to better communicate with their own security teams.
- Exchange views on emerging expectations and strategy and it is a unique chance to hear directly from cyber security experts on how to manage cyber threats in a consistent, practical and ethical way.
- A rare opportunity for the Board (and CISOs) to hear directly from the investor community what new standards and expectations on managing and mitigating cyber risk will be – especially following recent PRI engagements on managing cyber risk in a responsible way.
Plan for the Day
Morning – Security 360
Benchmark strategies and be inspired by case studies and discussions with experienced CISOs, CSOs and other c-level executives on areas relating to cybersecurity and cyber risk. The main audience of CISOs and CSOs will be augmented this year by invitations to c-suite including but not limited to CROs, CAEs, CCOs, COOs, CIOs, GCs.
- Geopolitical and Threat Horizon
- Security Leadership and Culture
- Innovation and Investment
- Financial Crime and Convergence
- Response, Catastrophe and Lines of Defence
Afternoon – Talk to the Board
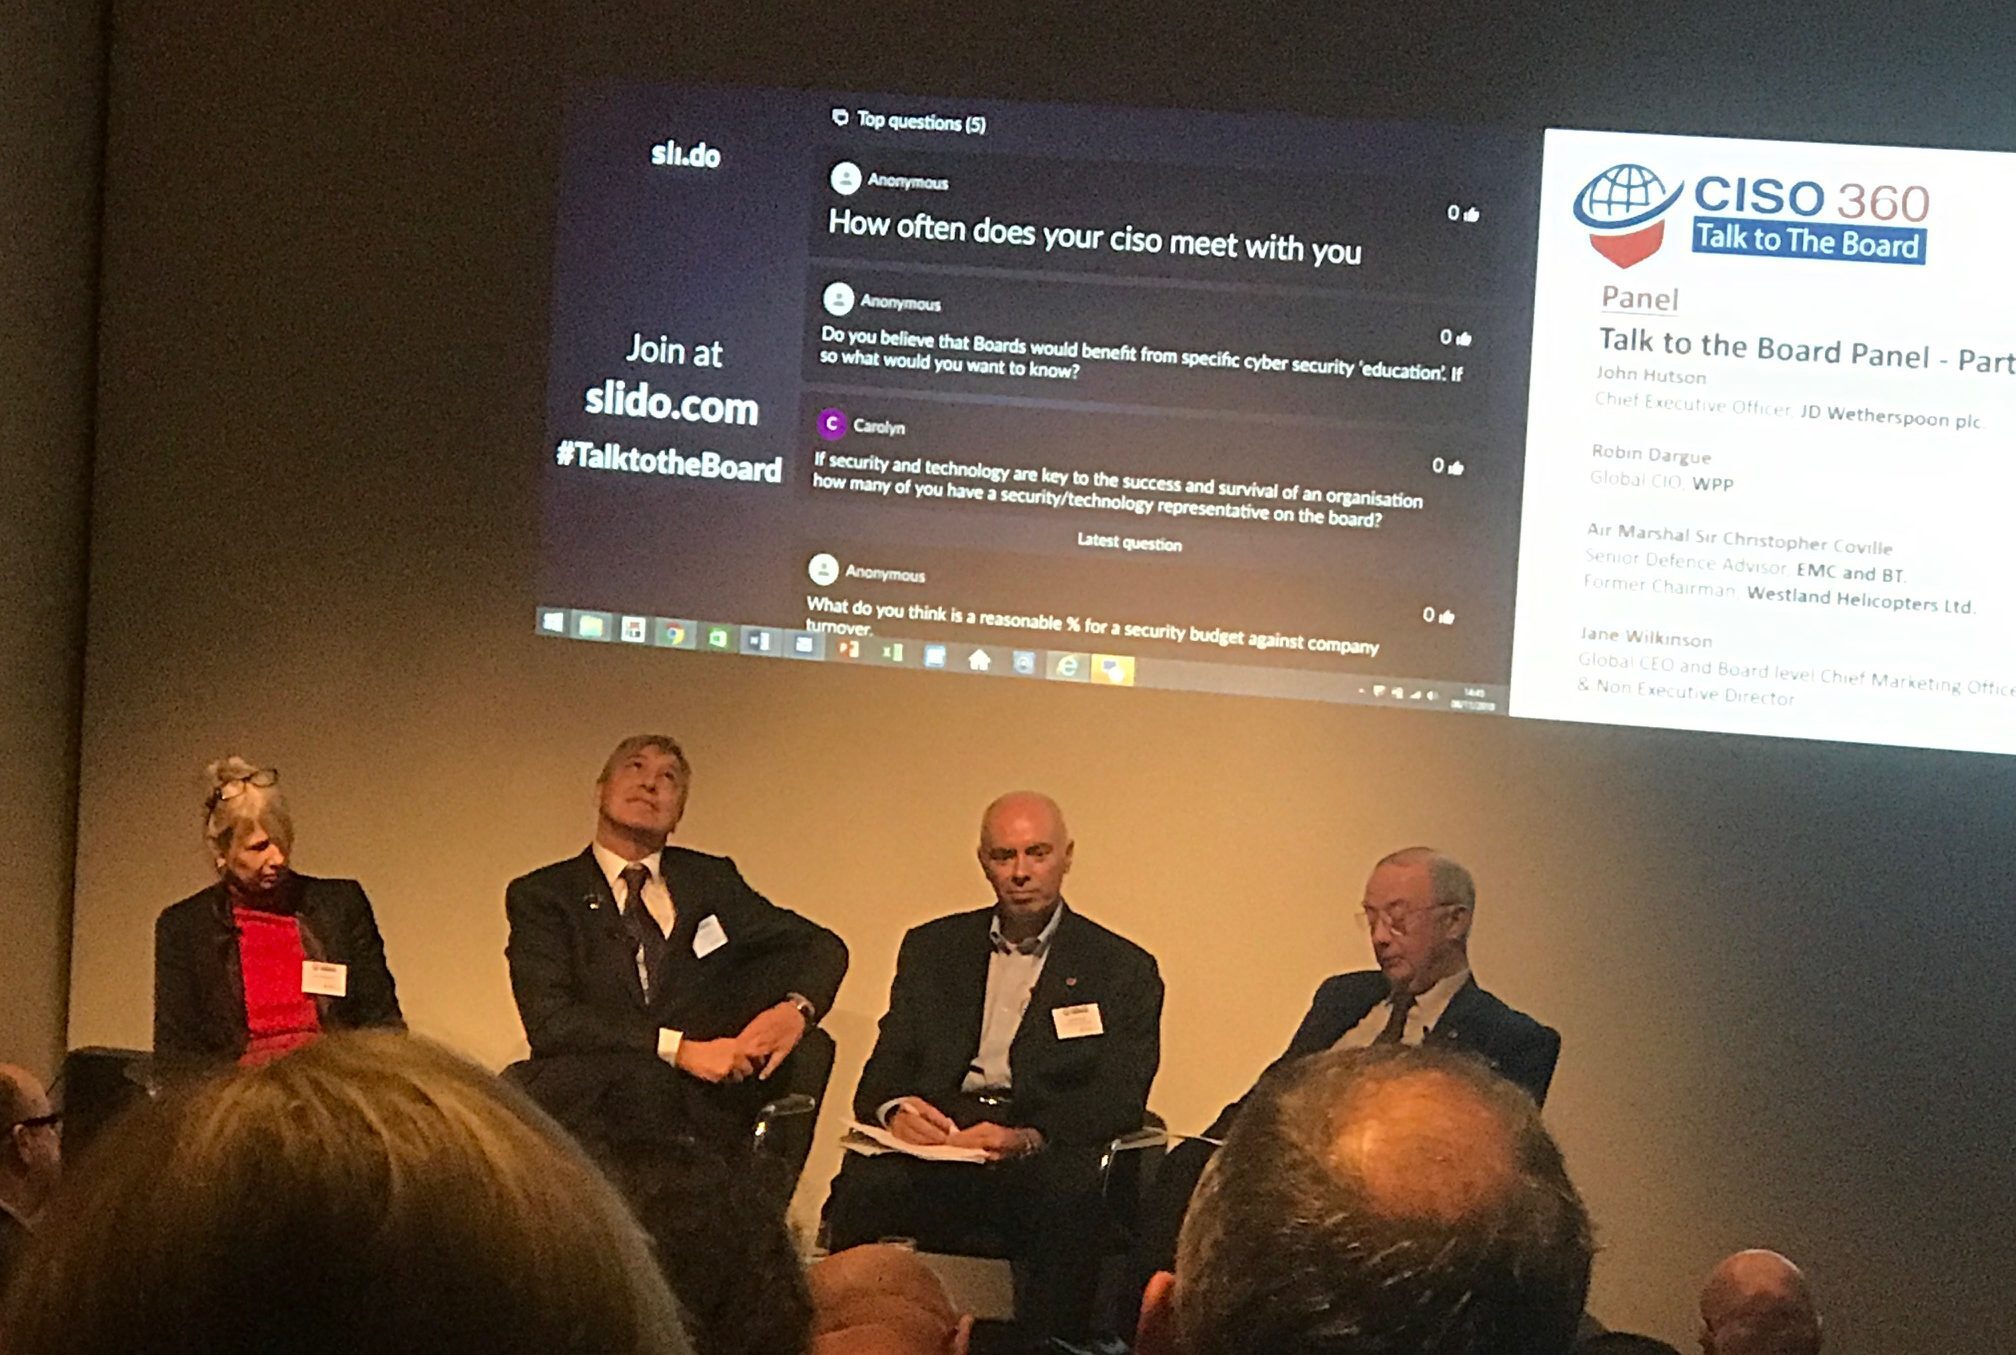
Guests are invited to ‘talk to the board’ and ask the questions they would ideally like to ask their own Board of directors if they had the chance – and without any consequences! Board Executives spanning Chairman, CEO, CFO, CIO, CMO, HR roles from well-known organisations will share their views on cyber risk and cyber security, offering rare and candid insights to the CISO/CSO community. Two afternoon open panel discussions will hosted in amphitheatre style. Board Directors from large companies will interact with the audience on the strategic, operational and tactical questions around security that are set to change the way we view cyber risk and expectations for doing business over the next ten years.
Progressing the discussion – Following a recap on where Talk to the Board ‘Round One’ left off in November 2018, the panels will probe gaps and expectations and will seek to build relationships between the Board and security c-suite.
Backdrop – It became clear from discussions at the inaugural Talk to the Board, developed and hosted by Pulse Conferences last year, that cybersecurity leaders and board directors are on a journey toward appreciating the others’ point of view. Individual journeys vary and, for many, much remains to be understood. Strengthening resilience to cyber risk may begin by both Board directors and CISOs taking stock of where they are on this journey. Now more than ever, it is critical for CISO/CSOs, and other risk, compliance and governance functions to think more collaboratively with a less siloed approach about the risks and the impacts of security. This think tank addresses both cybersecurity and technology risk challenges on the horizon as well as cross-company strategies for effectively communicating key risks. By attending, you will hear how security is playing a strategic role for organisations and how the security c-suite is approaching resource and cross-functional alliances and progress.
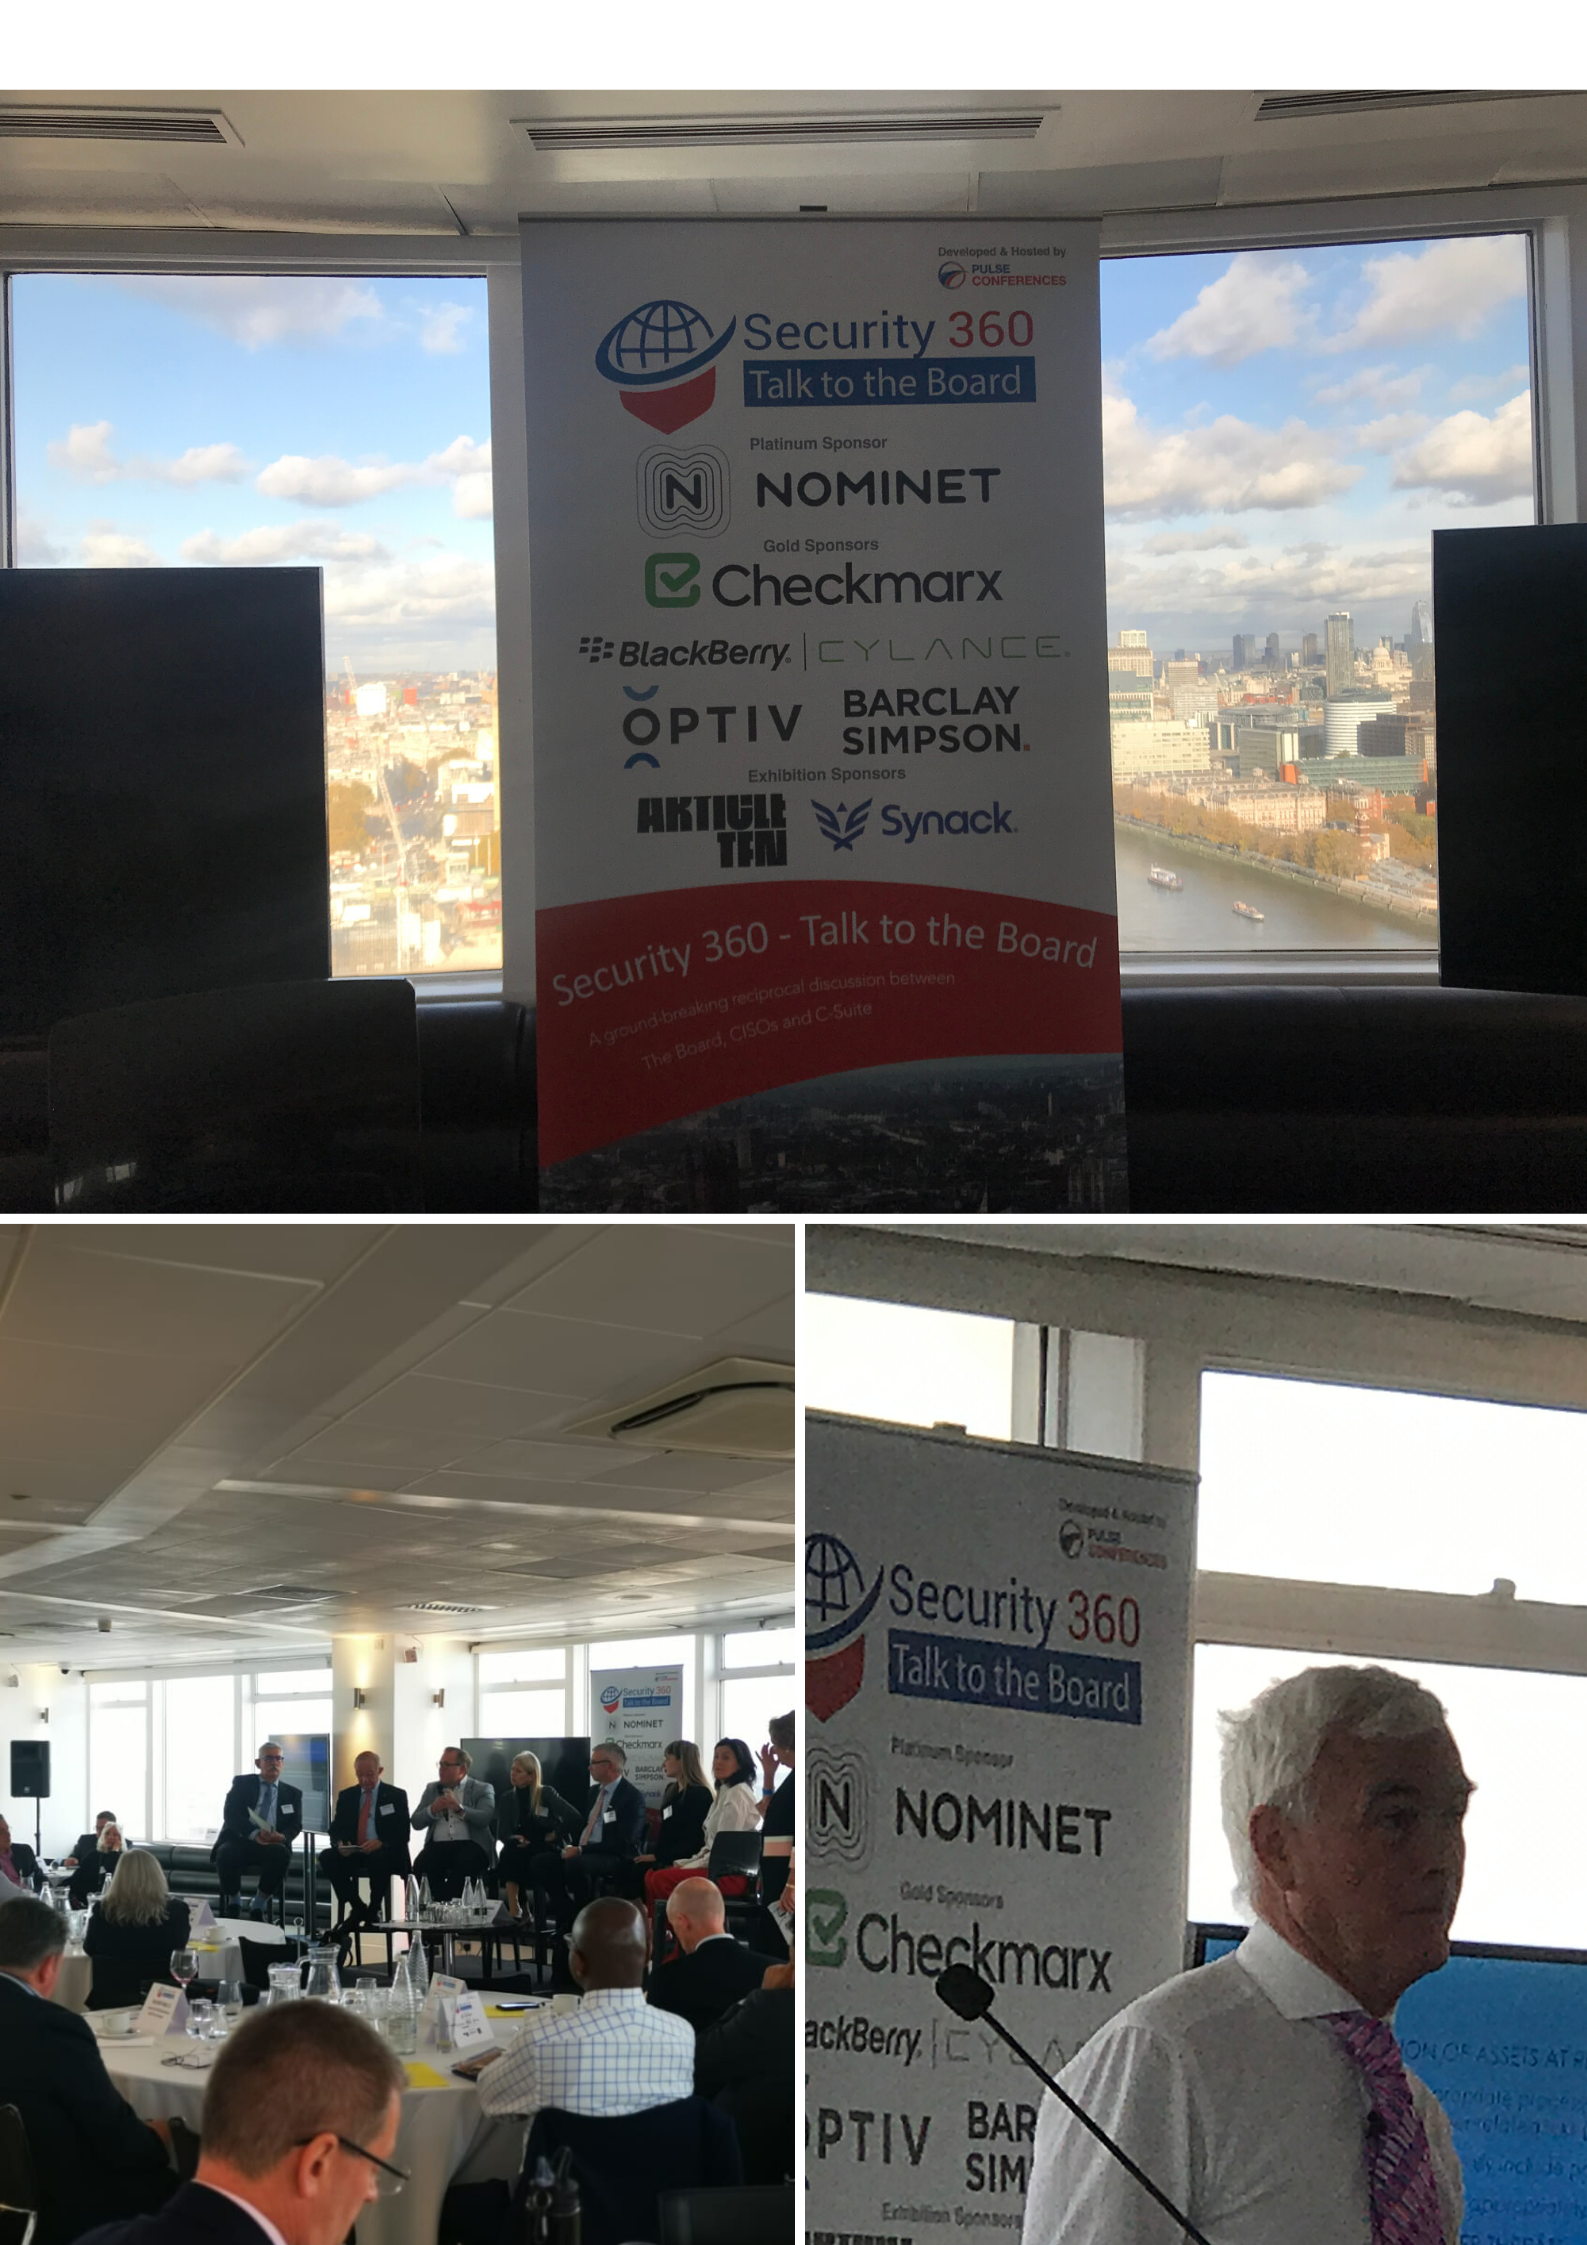
View photos from this years' Talk to the Board!
2019 Sponsors
Platinum Sponsor
Gold Sponsors
Exhibition Sponsors
Benchmarking the Board Conversation on Cybersecurity
– One Year On….
Written by our inhouse editor, Lyndsay Turley, an experienced communicator and cybersecurity advocate.
 Last November Pulse conferences held its first Talk to the Board event, a unique opportunity to step outside of the Pulse 360 CISO/cybersecurity community and take stock of growing appreciation for the risks that our delegates manage daily. The experience shared in the room demonstrated that while the conversation in the boardroom may have been early in its development, it was not focused on basic concepts. It also challenged widely- held perceptions, providing a snap-shot of a journey that an increasing number from both sides of the conversation had begun. Nearly one year on with approach of the next Security 360 – Talk to the Board conference, 7 November, we have been reviewing points made, setting a benchmark for marking how this conversation may have progressed.
Perhaps the most obvious observation shared underlined why members of corporate boards can be unresponsive to the proliferating demands for them to be more knowledgeable in cybersecurity. Our panellists of four board directors, including people serving as non- executive and management board directors in four different sectors – advertising and public relations, publishing, retail hospitality, and aerospace— were all well versed in managing crises. They also reassured the room that they were very receptive to being told there is uncertainty, particularly during a crisis. Their expectation was to be informed, and to be able to rely on technical competence within the management team. Their focus, straight forward: “I need to understand your biggest fears about this breach, your next steps to investigate the scale of the problem, and what can be done about it.”
It was clear that responding to this expectation relied on relationships built around relevant and real context, not theoretical possibilities. Our panel took pains to emphasise that this does not mean that everything must be expressed in terms of a return on investment. They were all actively seeking assurance that not just the risks, but also the impact on their business could be understood and addressed. The room was advised, for example, to expect questions aimed at the ability to ensure delivery of their proposals, confirming adequate consultation across the organisation. This was a mandate that reached beyond the ongoing debate around an independent reporting line, and many advocated being within IT leaves the CISO better positioned to deliver against their aims. They were also advised to show vision, and project the total “ask“ for their programme, or the fit of a project within a programme, rather than focus on a discrete budget.
All of our board panellists also confirmed that their businesses—most of them long-established concerns—were in the midst of transformation in response to either globalisation and or disruptive competition, both underpinned by new technical capabilities. It’s a dynamic that is focusing attention around cyber risks right across the economy. The inherent challenges were illustrated in more detail at our subsequent CISO 360 Congress in June, where delegates agreed that the levels of change and complexity, meant they currently struggle to understand their role within companies that don’t themselves understand what they are doing. They rely on collaborative networks and discovery of the “undocumented business strategy” to gain visibility of what is driving risk.
Our board panel would have appreciated these insights. They recognised the risks as critical, and the landscape complex. Each shared experience that demonstrated different priorities, styles and overall levels of maturity in their treatment of cyber risk. There was no defined formula for success beyond advising the need to understand board aims, and assure conversations could be very personalised: “It should take work, time and effort to understand their point of view to understand what they are worried about.”
Our panel also admitted they could do more to progress the conversation by addressing gaps in communication, and clarifying accountability for their roles in setting culture, managing a crisis, and generally assuring adequate knowledge to assess strategic concern. Notably, our panel pointed to our audience of over 70 cybersecurity leaders, as essential to helping them do that.
After several hours facing their questions, one panellist summed up a home truth for all in the room, and anyone looking to influence investment and support in a landscape of competing priorities. “There isn’t a secret pot of money for special things.”
This year, Talk to the Board becomes Security 360 – Talk to the Board, acknowledging the growing concerns over cyber physical risks coming from both our CISO and CSO 360 communities. Download the Pulse Innovate Report CISO 360 Talk to the Board for a more detailed review of the developing corporate response to cyber risk, and come along on Thursday 7 November to play your role in progressing the debate. Register here www.talktotheboard.com. Attendance is complimentary if you are a senior CISO or practicing CxO working for a bank, corporate or government entity as opposed to being a provider or advisor to the security community.
With thanks to our sponsors
Sponsors

Who attends
By Designation
Participants will include CISOs and CSOs in addition to:
- Chairman
- CEO
- Non-Executive Directors, Board Member, Audit & Risk Committee Member
- CFO, CRO, GC, COO, CTO, CIO, CMO, HR
- Chief Information Security Officer
- Director of Cybersecurity / Head of Cyber Threat Intelligence
- Head of Governance
- Head of Innovation
- Director of Digital Risk
- Chief Data Officer
- Chief Privacy Officer
- Heads of Corporate Security/Resilience
By Sector
All private and public sectors are welcome to attend.
Speakers for Security 360-Talk to the Board 2019
The speaker panel for 2019 is currently being produced. We would very much value your input into companies, topics or specific persons you may like to see present. Please email teampulse@pulseconferences.com if you would like to suggest speakers for this event.
Chaired by:
Board Directors including:
Speaker Panel of CISOs and CxO including:
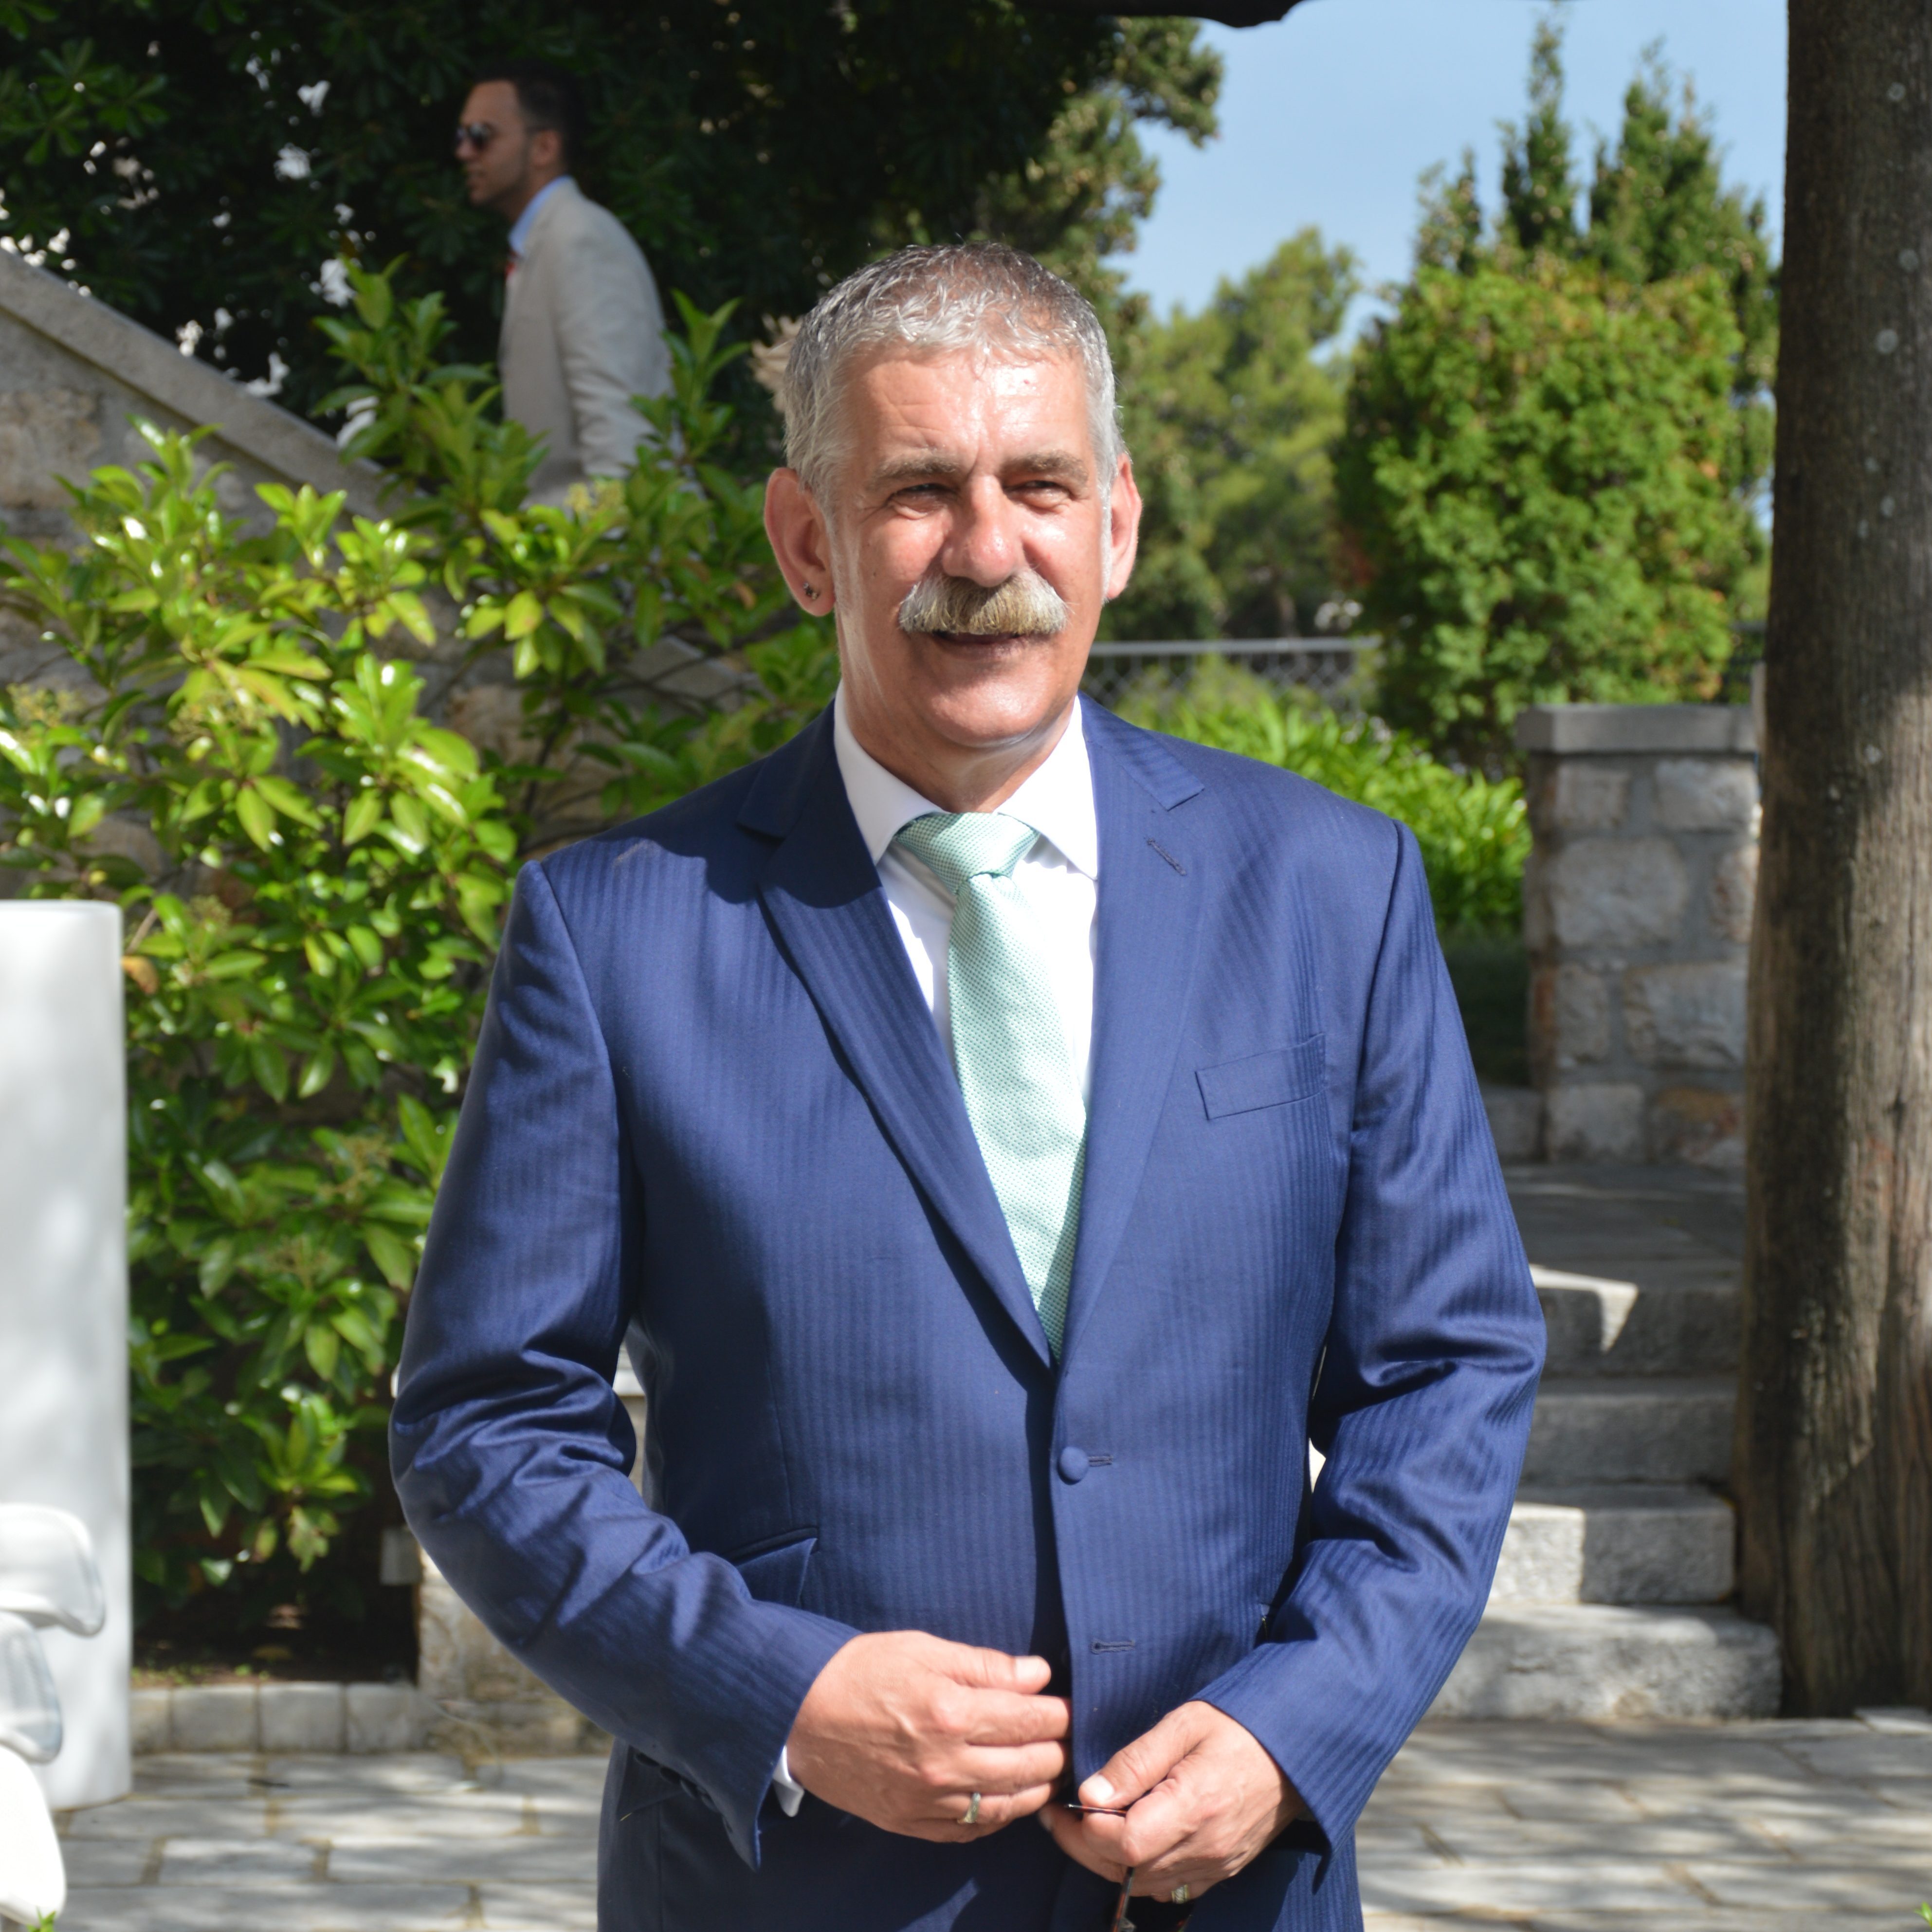
Marcus Alldrick
Former CISO, Lloyd’s of London. Currently Digital Risk Management, Security and Compliance Advisor
Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer.
In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.
Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc.
Sir Christopher Coville Senior Security Advisor
SecureCloud+, Former Senior Defence Advisor, EMC and BT, Former Chairman, Westland Helicopters Ltd
Air Marshal Sir Christopher Coville was born in Liverpool in 1945, and joined the Royal Air Force in 1964 as a Flight Cadet at the RAF College Cranwell. After flying training, he served several tours of duty as an operational Lightning and Phantom pilot in the Air Defence role. His early career included staff and command appointments, including commanding No 111 (Fighter) Squadron, a spell in the Falkland Islands in 1983 as Officer Commanding Operations Wing, and later command of RAF Coningsby, where he flew the Tornado F3 and displayed the Hurricane and Spitfire of the Battle of Britain Memorial Flight. He is also a qualified helicopter pilot, having converted to Gazelle and Whirlwind. In July 1992, on promotion to Air Vice-Marshal, he was appointed Air Officer Commanding Training Group, with responsibility for all RAF Air and Ground Training, as well as overall supervision of the Red Arrows. In September 1994 he became Assistant Chief of Defence Staff Operational Requirements (Air Systems), in which post he oversaw the largest re-equipment programme for the RAF since the War, and had responsibility for the MOD’s Air Research Programme. On promotion to Air Marshal in 1998, he was appointed as Deputy Commander-in-Chief, Allied Forces Central Europe. In this role, he was responsible for development of NATO’s Combined Joint Task Force (CJTF), and he was involved at the Operational Level of Command in the conflict in the Balkans. Additionally, he was charged with leading the Czech Republic and Polish Armed Forces successful integration into the integrated military structure of NATO. He assumed the appointment of Air Member for Personnel (an RAF Board position as the RAF’s HR Director) and Commander-in-Chief Personnel and Training Command in March 2001, and retired from the regular RAF in May 2003. He continued flying in the RAFVR, on the Tutor aircraft in support of the Air Cadet Organisation, until May 2012, when he finally left the service after 50 years flying in uniform. He has since recommenced gliding with the Devon and Somerset Gliding Club, and is the Hon President of No 2 Flying Training School, the home of Air Cadet gliding.. The Air Marshal was awarded The Queen’s Commendation for Valuable Services in the Air in 1988, the CB in the 1995 New Year’s Honours List and became a Knight Commander of the Order of the Bath in the New Year’s Honours List of 2000. In recognition of his work integrating the Czech Republic’s Armed Forces into NATO, he was awarded the nation’s Gold Commemorative Medal in 2001. He is a Fellow of both the Royal Aeronautical Society and the Chartered Institute of Personnel and Development, and is a founder graduate of the Open University. From 1995-2003, he was President of RAF football, President of Combined Services FA in 2003, and an Honorary Vice-President of the Football Association from 1996-2003. He is now President of the RAF Veteran’s team. Sir Christopher has enjoyed a successful second career in business and in the Third Sector. He is past Chairman of Westland Helicopters Ltd (2005-February 2011), and past Chairman of the European Aerospace Companies’ Rotorcraft Group (2004-12). From 2003-20010 he was President of the Aircrew Association. He was until 2017 Senior Defence and Security Advisor to Dell EMC/RSA, a global ICT Company, where he established a national reputation for his campaign to promote Cyber as a major UK commercial opportunity. Indeed, in recognition of his leadership role in Cyber, her is a member of the Information Assurance Advisory Council (IAAC) community of interest, and is a member of the Security Awareness Special Interest Group (SASIG). In addition, he was until August 2014 Chairman of the Forces Pension Society, and is past-President of the Regular Forces Employment Association and a Life Vice-President of the European Area of RAFA. He sits on the Councils of several civilian and service charities, and has recently embarked on a part time career as a Guest Lecturer on cruise ships. From 2014-2018, he assumed the Chair of the British Helicopter Association, which represents the interests of all civilian helicopter operators and manufacturers, and was a full Council Member of the European Helicopter Association. A keen glider pilot, he was appointed President of Air Cadet Gliding in June 2015. Since 2017, he has been Chairman of the Strategy Board of the Aviation Skills Partnership (ASP).
Deborah Exell
Board Member, Head of Human Capital & Business Transformation, Getronics
Jane Wilkinson
International MD and CMO and Non Executive
Jane is an international MD & CMO – with expertise and experience in leading and transforming digital tech content and data subscriptions and a proven record of accelerating revenue and profit growth in data, media, B2C and B2B businesses. Jane is currently Executive Advisor to high-growth digital tech B2B/B2C content and data subscription businesses. She is a Non-Executive Director of TMT Analysis, a tech start-up providing data and analysis to the telecoms Industry. Prior to this, for the past 17 years Jane was Chief Marketing Officer at Euromoney Institutional Investor Plc and a Board Director of this FTSE 250 international information company.
Paul Excell
Chairman/NED, Global CxO, Investor, Executive Coach and Board Advisor
Paul is a Chairman/NED, Global CxO, investor, executive coach and board advisor with an impressive track record of delivering business growth in global organisations large and small (Startups, ScaleUps, Corporates) – uniquely combining startup speed at scale. As Founder and CEO at Innovation Excelerated and Executive Chair, Global iLabs he drives an innovative portfolio of high growth, disruptive technology start-ups/scale ups plus coaching and Board advisory services. He a founding member and Executive Director at ScaleUp Group – successfully growing several UK scaleups with experience from £4bn+ in exits. He was previously Chief Customer Innovation Officer, Group Technology Officer and SVP Global Services at BT where he launched many innovative services and global businesses supporting revenues of >£3bn plus was a member of several global boards and the main Group Diversity, Risk and Technology Boards. He is an alumnus of London Business School, University of Essex and University of York. He started his career as a Apprentice and Professional Technician and working in the family retail business. He is a Chartered Engineer (CEng), Fellow of Institute of Engineering and Technology (FIET), Fellow of Institute of IT (FBCS) and Freeman of the City of London.
Peter Wanless
Chief Executive, NSPCC
Peter Wanless, CB is an English executive and former civil servant. Since 2013, he has been the chief executive officer of the National Society for the Prevention of Cruelty to Children (NSPCC). After joining the Civil Service, Peter held a variety of posts at the HM Treasury, including Head of Private Finance Policy, and Principal Private Secretary to three Cabinet Ministers. Peter later held senior positions within the Department for Education and Skills and its successor the Department for Children, Schools and Families. He was CEO of the Big Lottery Fund between February 2008 and May 2013. Since June 2013, he has been the chief executive officer of the National Society for the Prevention of Cruelty to Children (NSPCC). He is a non-executive director of The Kemnal Academies Trust (TKAT), which operates academy schools in South East England. In the 2007 New Year Honours, he was appointed Companion of the Order of the Bath (CB) for his role as Director of School Performance and Reform in the Department for Education and Skills.
Ali Zeb
CISO, The British Land Company Plc.
Ali specialises in security transformation of businesses, delivering global information security at strategic, tactical and operational level. He has over 19 years’ experience in IT and Information Security within the Finance sector. Alongside heading global security, Ali has been appointed as GRC and Data Protection Officer for many organisations. Ali is currently Chief Information Security Officer at The British Land Company Plc.. A FTSE 100 real estate investment company with a property portfolio around £17 billion which includes exciting developments such as Regent’s Place, Broadgate, Paddington Central and the most significant opportunity at Canada Water, where British Land have amassed a 53-acre scheme and are now master planning a new urban centre for London. Prior to this he was Group Chief Information Security Officer at MS Amlin. He is a member of FCA Insurance Sector Cyber Coordination Group (ISCCG) and Lloyds Cross Market Cyber Risk Forum.
David Cripps
Director of Security, Pay.UK
David has over 30 years’ experience as a Chief Information Security Officer in the Finance Sector, a Magic Circle law firm and a FinTech Startup, specialising in information risk, cyber security and data protection.
In addition to his technology background (he has a degree in Electronics and is a CISSP, a CISM and a CISA), David has a masters in Internet and Telecoms Law (LLM).
Outside of work, David’s current interest is historic encryption devices and he has been assisting Bletchley Park with some exhibits and often presents to local schools on “keeping secrets” to help promote science and technology (STEM) as a career.
Dan Panesar
VP EMEA Sales - Cyber Solutions, Nominet
Dan has a real passion for technology, in particular information security and has more than 14 years working in and building very successful leading-edge technology sales teams. He started out in various new business sales roles before progressing into exec leadership with innovative cyber security start-up Sipera Systems, the first worldwide market leader in solutions for the rapid, simple and secure adoption of Unified Communications (UC). Backed by several high-profile VCs including Sequoia Capital. Sipera Systems achieved huge success and in 2012 was wholly acquired by Avaya Inc., one of the largest Unified Communications and Contact Centre software vendors in the world, for a reported double digit multiple. At the end of 2015 the lure of a start-up led Dan to Certes Networks an innovator in encryption management. Here Dan led the EMEA business to successive years double digit growth, working with some of the most security conscious organisations and governments across the world. Dan’s true passion to champion UK Cyber Security innovation has been a constant motivation and since 2015 he has been working with several UK-based cyber security start-ups through the Cylon – Cyber London accelerator programme. In 2019 this passion to work with a UK founded Cyber start up led him to Nominet Cyber where he leads the EMEA business.
Denise Beardon
Head of Information Security Engagement, Pinsent Masons
Denise Beardon is Head of Information Security Engagement at Pinsent Masons, an international law firm. Prior to joining Pinsent Masons, she worked for The Security Company, a security awareness consultancy, where she was responsible for the creation and implementation of their behavioural change methodology including qualitative and quantitative baseline research. During the past ten years, Denise has worked on many successful behavioural change programmes for a number of high profile organisations. Denise is committed to exploring the interaction between human behaviour and technology and understanding why people do what they do. This insight provides her with the ability to deliver tailored strategic behavioural change programmes that ensure the individual does not feel undermined but empowered to make the right choices. By using behavioural psychology at the heart of her programmes, Denise aims to bring positive change to any cyber security culture. Prior to entering the world of cyber security awareness, Denise was internal communications manager for Cambridge Constabulary following a successful career in marketing communications in the private sector. She has a Masters in Crime Writing from the University East Anglia and is working on her debut novel.
Graham Edwards
Head Of Information Security, Camelot Lottery Solutions
The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS, ING and most recently Nationwide Building Society. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning,
compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He currently holds the position of Interim Head of Group Security at Camelot Lottery Solutions, where he is responsible for Information, IT, Cyber and Physical Security and their associated risk functions. Graham has a master’s degree in Information Security from Royal Holloway.
Dinis Cruz
CISO
Dinis Cruz is a CISO and Transformation Agent, focused on creating teams and environments where security is an enabler and accelerator for the business, while securing and protecting the digital assets from existing threats. Dinis was nominated for CISO of the Year 2019 at #CyberSecurityAwards.
Dinis is also writing a book called Generation Z Developers (but useful for all Generations) available from Amazon: https://www.amazon.co.uk/Gen-Developers-concepts-generation-developers/dp/1724194607
Graham Ayre
Internal Auditor, ArgoGlobal
Graham currently acts as a self-employed Internal Audit consultant and has over 35 years’ experience as both an external and internal auditor, his present assignment being with a Lloyd’s syndicate. Prior to becoming a consultant in 2016 he spent nearly 20 years acting as the Head of Internal Audit or Senior Internal Audit Manager in a number of UK financial services companies including Gocompare.com (one of the principal price comparison service providers), Ageas Insurance Limited (a general insurance company) and the Lincoln Financial Group companies based in the UK (which provided life assurance, personal pensions and investment services). Graham started his career with Ernst & Young where he qualified as a chartered accountant and worked for over 13 years, mainly as an external auditor. Apart from working in the UK, he spent a year working overseas for Ernst &Young in Papua New Guinea and Australia. While working in Papua New Guinea he encountered some more unusual audit clients such as a crocodile farm and the Papua New Guinea Post Office and Telecommunications Corporation. Outside of his job, Graham is a committee member of the Insurance Internal Audit Group in the UK and serves as a school governor at two schools. He has spoken on audit and regulatory matters at a number of external conferences.
Dr John I. Meakin
CISO and Cybersecurity Advisor (Recently Group CISO, GSK)
Dr. Meakin retired as the Chief Security & Risk Officer at Burberry in mid 2017 and now advises businesses on cyber risk, including security product companies, Fintech startups and some larger international companies. In this role he works with some leading cyber security consultancies, including Cydefence. During 2018 he also acted as interim Chief Information Security Officer at GlaxoSmithKline. Dr. Meakin is a specialist in information and systems security with more than 25 years’ experience. Prior to Burberry he was Chief Security Officer for the luxury goods conglomerate Richemont International SA in Geneva, with oversight of physical, information and cyber security. Previously, he has built and led security functions in a range of Banks, notably the Royal Bank of Scotland, Dresdner Bank and Standard Chartered Bank. He has also been Chief Information Security Officer of BP and Reuters. He was a founding board member of the Jericho Forum, and has served on the Customer Advisory Boards of several specialist security product companies as well as Microsoft, IBM and HPE. He is a regular speaker at industry conferences and public forums on a variety of risk and security topics. He has a Ph.D. in experimental solid-state physics from Cambridge University.
Quentyn Taylor
Director Information Security EMEA, Canon Europe
Quentyn has a wealth of experience in both the IT and information security arenas and, in recent years, has focused his attention on building business relationships across the world. Quentyn has driven Canon’s strategy to highlight the importance of document security and help business customers to minimise their security risk. Quentyn strongly believes in educating users about the importance of a comprehensive, overall security framework that will allow Canon’s business customers to improve security in a cost-effective way. During his career, Quentyn has worked in a variety of industries for a number of organisations including outsourced service providers, Internet service providers as well as Dotcom businesses, before moving to Canon in 2000.
Ray Stanton
Business Executive Leader, CSO, NED & Cyber Resilience Advisor
An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CiSO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.
Lady Olga Maitland
President, Defence and Security Forum (and Chairman, Copenhagen Compliance)
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Simon Staffell
Head of Public Affairs, Nominet
Simon Staffell is head of global public affairs at Nominet, where he represents the company’s mission to use technology to improve connectivity, security and inclusivity. He was previously a civil servant and diplomat, serving in the Washington DC, Cairo and a number of roles in Whitehall. He holds a PhD in politics and has specialised in international diplomacy, national security, counter-terrorism, cyber security and the Middle East. He was previously an adjunct Professor at Georgetown University’s Department of Foreign Service.
Sponsors
Nominet
Nominet has been at the heart of the internet for over 20 years running the .UK internet infrastructure, keeping it safe and secure. In providing registry services for top level domains, it has a wealth of experience in running and protecting the Domain Name System (DNS) as well as analysing threats within the DNS traffic.
This expertise underpins its cyber security solutions that protect governments and global enterprises from constant attack. NTX uses machine learning to reduce risk on your network and eliminates threats before they cause harm. It analyses DNS traffic for known and unknown bad in real time to predict, detect and block cyber threats.
Providing your security teams with visibility and protection against critical threats such as malware, phishing, data theft and DNS hijacking, NTX narrows the window of compromise by identifying malicious domains, on average, one week faster than other network security solutions. NTX is an easy-to-deploy solution used by commercial clients worldwide, as well as the UK Government and over 400 of its public bodies as part of the Protective DNS service we provide.
Checkmarx
Checkmarx is the Software Exposure Platform for the enterprise. Over 1,400 organizations around the globe rely on Checkmarx to measure and manage software risk at the speed of DevOps. Checkmarx serves five of the world’s top 10 software vendors, four of the top American banks, and many government organizations and Fortune 500 enterprises, including SAP, Samsung, and Salesforce.com.
Learn more at www.checkmarx.com.
https://www.facebook.com/Checkmarx.Source.Code.Analysis
https://www.youtube.com/user/CheckmarxResearchLab
https://twitter.com/checkmarx
https://www.linkedin.com/company/checkmarx/
Barclay Simpson
Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury. www.barclaysimpson.com
Cylance BB Horz Black
Cylance develops artificial intelligence to deliver prevention-first, predictive security solutions that change how organizations manage their endpoints. Cylance provides full spectrum predictive threat prevention and visibility across the enterprise to combat the most notorious and advanced cybersecurity attacks. With AI-based malware prevention, threat hunting, automated detection and response, and expert security services, Cylance protects the endpoint without increasing staff workload or costs. We call it The Science of Safe.
Learn more at www.cylance.com
Optiv
A TEN
however, delivers national and international cultural change communication programmes on Employee Information & Cyber Security Awareness and Education, a sector we have worked in for twelve years. During this time we have helped many of the FTSE 150 and Fortune 500 organisations improve their Information Security by targeting their weakest link, their people and educating them in the importance of Information Security behaviour. We create bespoke solutions that are evolved after analysing an organisation’s culture, brand, values and behaviours. This enables us to create tailored programmes that appeal to the target audience from both a content and creative perspective. This honed methodology has been proven, via measurement to have great impact on supporting the mitigation of the human behaviour risk.
Synack
Synack, the leader in crowdsourced security testing, helps organizations protect themselves from cyber attacks. By leveraging the world’s best ethical hackers and an AI-enabled platform, Synack helps organizations find and fix critical security issues and provides valuable security intelligence on digital assets. The Synack platform delivers data-driven insights to help organizations understand their risk from a hacker’s perspective and then mitigate that risk with a hacker’s help. These insights secure critical infrastructure and leading brands and businesses around the world- Synack protects leading global banks, DoD classified assets, and close to $1 trillion in Fortune 500 revenue. For more information visit us at www.synack.com
Venue
Security 360 – Talk to the Board will be hosted at Atmosphere 29, situated in the tallest building in Westminster on the bank of the River Thames with stunning wraparound views of London and beyond. Atmosphere 29 is an ultra-modern, contemporary space located on the 29th floor of the Millbank Tower.
Register nowDownload event brochureBus – The following buses all stopping within a very short walking distance of the venue:
3 – runs to and from Crystal Palace and Trafalgar Square.77 – runs to and from Waterloo and Tooting Station.
87 – runs to and from Aldwych and Wandsworth.
507 – runs to and from Waterloo and Victoria.
C10 – runs to and from Canada Water and Victoria.
N3, N87 also run a night service.
Atmosphere 29
Atmosphere Venues
Millbank Tower, 21 – 24 Millbank,
Westminster, London SW1P 4QP
www.atmospherevenues.com
Atmosphere Venues has exceptional transport links with rail, tube. river, road and bus
Rail – Atmosphere Venues are close to London Waterloo and Waterloo East (20 minutes walking), Victoria (20 minutes walking) and Vauxhall (10 minutes walking) train stations.
Tube –Atmosphere Venues have access to Circle, District, Jubilee, Waterloo & City, Victoria and Bakerloo Line Stations. The nearest stations are: Pimlico (Victoria Line, 8 minutes walking), Victoria (Victoria Line, 20 minutes walking), St James’s Park (District and Circle Lines, 14 minutes walking), Westminster (District and Jubilee Lines, 15 minutes walking), Waterloo (Jubilee, Northern, Bakerloo, and Waterloo & City Lines, 20 minutes walking) and Vauxhall (Victoria Line, 10 minutes walking).
River – Atmosphere Venues have the Millbank Millennium Pier directly opposite the building, where you can get river taxis and river cruises along the Thames
Downloads: Security 360-Talk to the Board
Download 2018 Pulse innovate report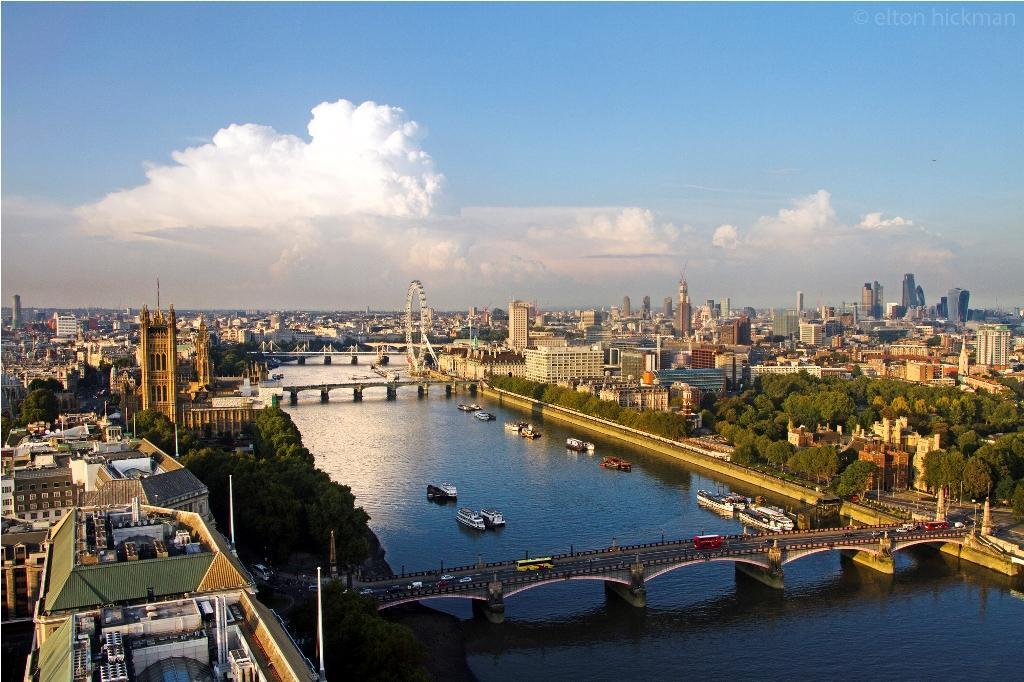 Download Brochure 2019
 On the Pulse Blog: Benchmarking the Board Conversation on Cybersecurity – One Year On….
Testimonials – Pulse 360 series
 “If you want to hear real CISO experiences, you must attend this event!” –Chuan-Wei Hoo, CISO, ST Engineering, Singapore
 “Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” – Thomas Foster, SailPoint
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” – Martyn Booth, CISO, Euromoney Institutional Investor PLC
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” – Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
– Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” – Catherine Coale, Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” – Joe Breen, Company85
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” – James Gosnold, Technology Services Head of Cyber Security, DWP
““A very thoughtful event, great networking and industrial expertise in the room to learn from!” – Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Philippe Besson, Europe Industries- Security Officer, Air Liquide GMS
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” – NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” – Colette Hanley, Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” – Ben Bulpett, SailPoint
“By far the best event for 2018 I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Ali Zeb, Group CISO and Group DPO, MS Amlin
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding lineup of events from your organization!“
Christopher Rollan, Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
– Ali Zeb, CISO, MS Amlin
”Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Joe Dauncey, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
– David Colbourne, Information Security Manager, Lloyd’s of London
“”The best speaker line-up of any security conference in Europe!”
– Michael Colao, Head of UK Security, AXA
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, Brian Brackenborugh, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Sérgio Gonçalves, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” – Chucks Ojeme, CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic
networking opportunities, facilitating very interesting thought provoking conversations”
– Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
 “Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Quentyn Taylor, Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared
their knowledge and experience with their peers in an open and collaborative manner under Chatham house
rules. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during 1×1 networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISO’s across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
– Stephen Khan, Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
Pedro Cunha, CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
-Sponsor testimonial, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, James Kwaan, President, (ISC)2 Scotland Chapter
“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” Luis Vilares, GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the
Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors,
but with less pressure. Excellent!”
– Irene Corpuz, Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” – James Chuka, Sailpoint
“”I found CISO360 Conference a great place to share ideas about current and future problems”
– Sonia Morales, Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
– Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
– Ramón Serres, Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO360 conference in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO360 and
look forward to this conference going from strength to strength”
– FC, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together. Look forward to the next one.”
– Anthony Young, Partner, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!“
Irene Corpuz, Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018