
1st Talk to the Board
6 November 2018
London Transport Museum – Covent Garden, London
Pulse would like to say a massive ‘thank you’ to all speakers, sponsors and delegates that participated in Talk to the Board, 6 November 2018!
A reciprocal discussion between Board Members, CISOs and C-Suite
• question a real Board |
• connect with CISO and C-Suite peers|
• benchmark cyber risk strategy |
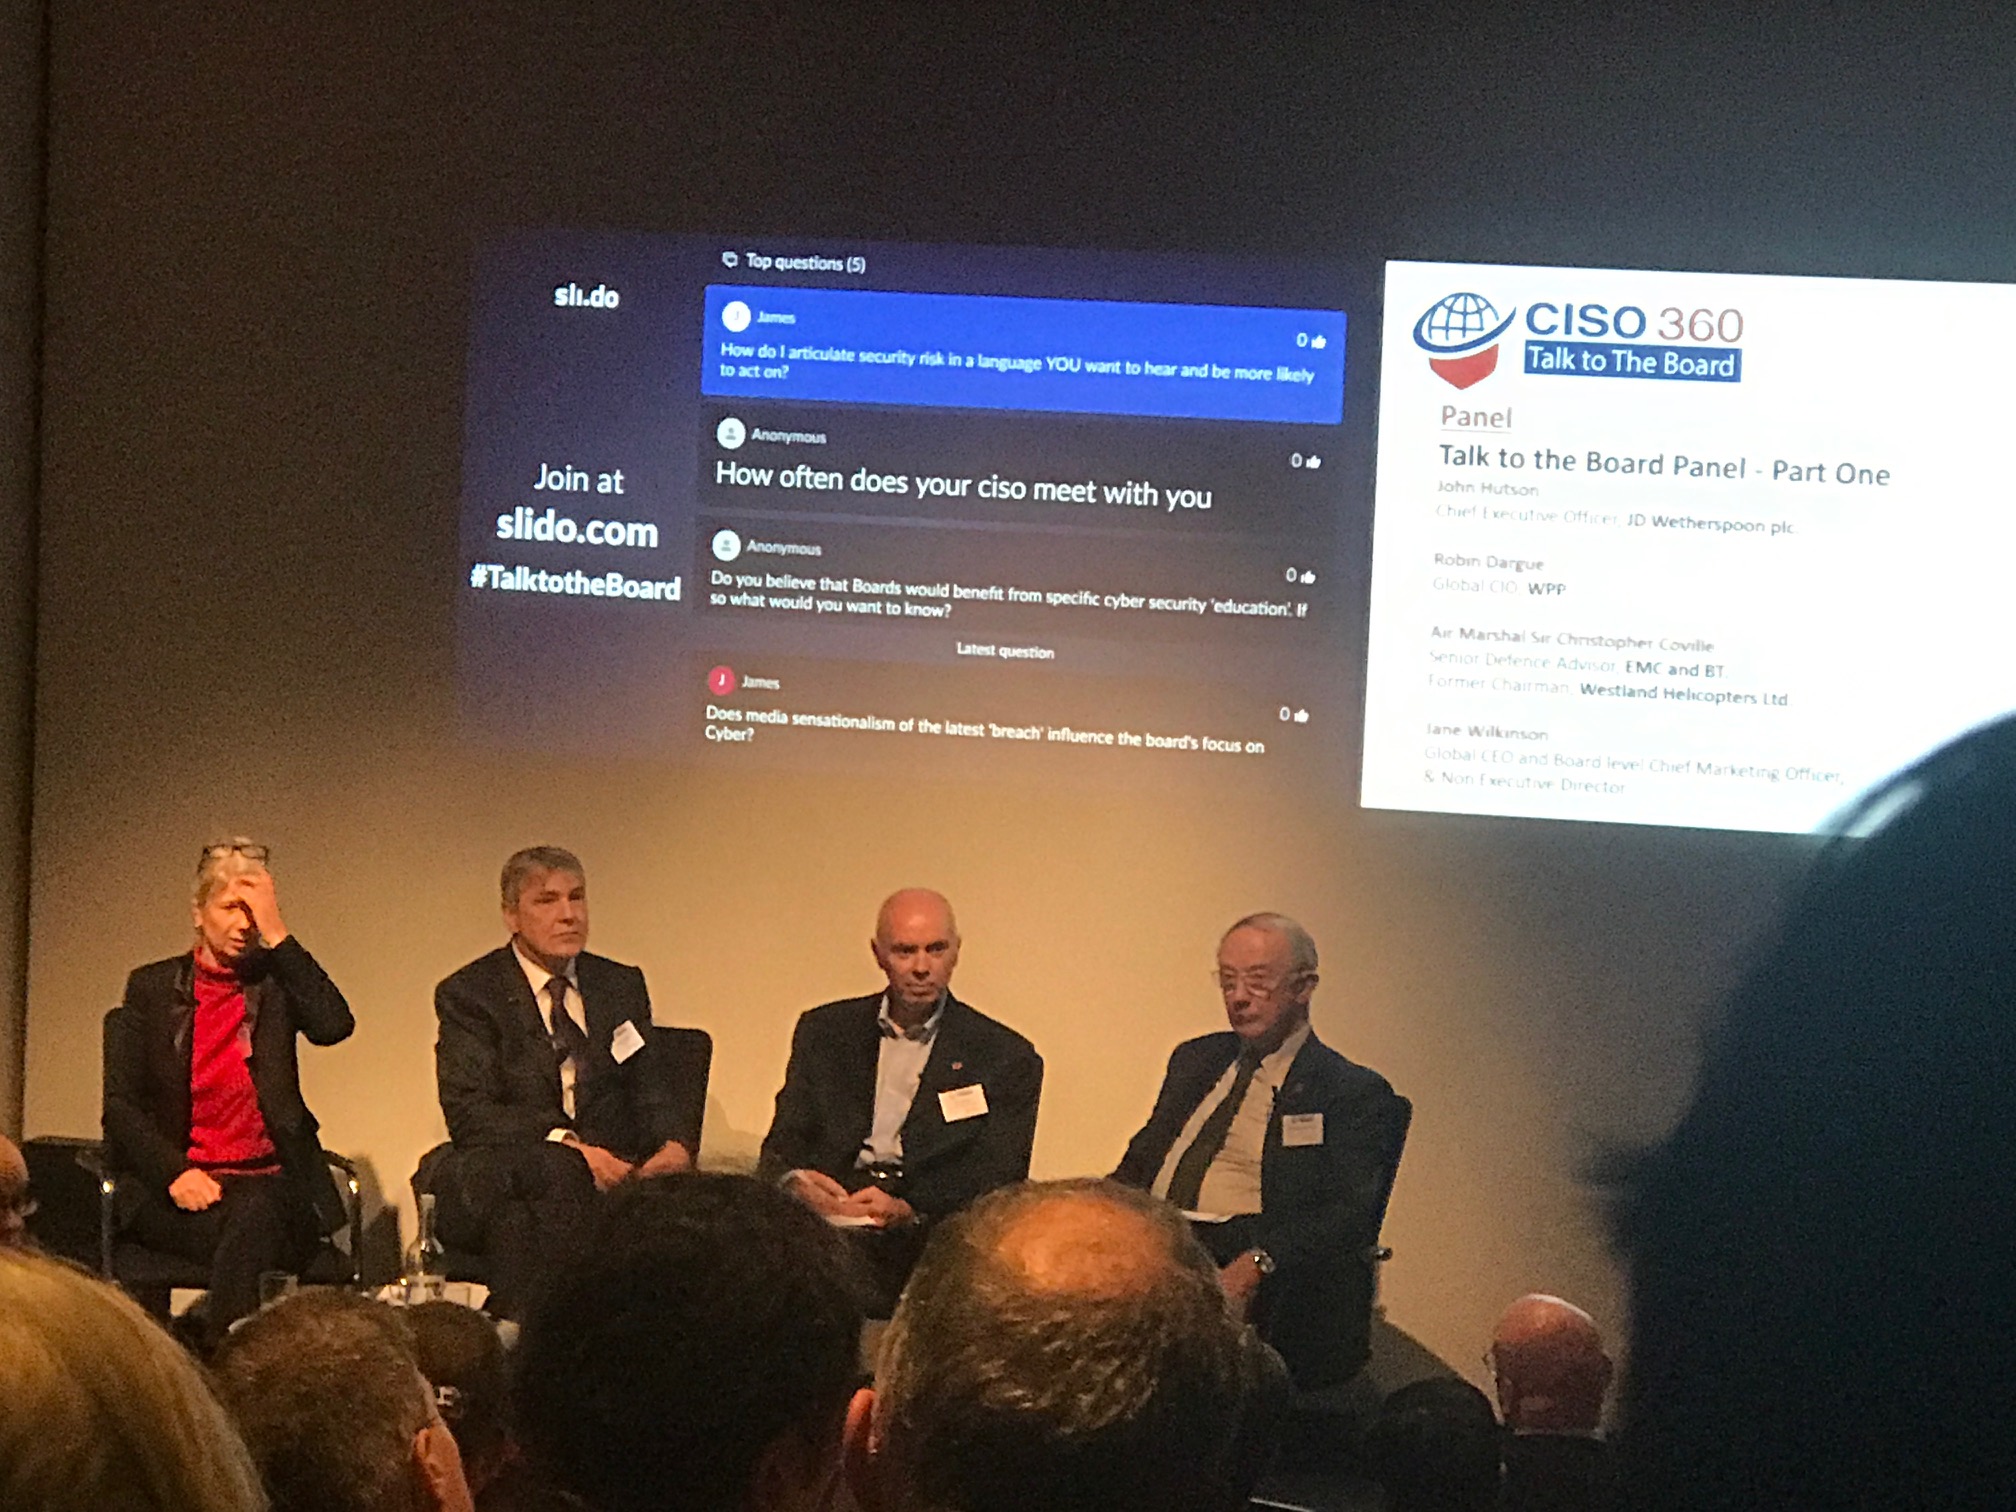
Pulse Conferences is delighted to have presented our 2018 one-day conference, Talk to the Board, a discussion between CISOs and a non-security Board. Talk to the Board is the ultimate ‘sound-boarding’ platform for today’s cybersecurity and digital risk leaders to question a panel of actual Board directors on priority challenges around cyber risk management and business engagement.
Invited guests will be presented with a panel of real Board Directors from large enterprise corporate boards as well as Non-Executive Directors, covering various sectors. These individuals are collectively responsible along with their fellow Board members for the cyber security stance of their organisations. They are only able to make decisions based on the quality and format of the information they receive from those responsible for cyber within their company from the CISO and CIO.
The event is held in a theatre seating style. Guests are invited to talk to the Board and ask the questions they would like to ask their own Board of directors if they had the chance – and with none of the consequences! Board Executives spanning Chairman, CEO, CFO, CIO, CMO, HR roles from well-known organisations will share insights on how CISOs can improve the security leadership offering and vice-versa.
Top of their game CISO/CSOs will also share the steps and approaches taken within their own companies, as well as tips on how to align culture and mindset across security-business technology and legal. Additionally, an investor perspective will be presented, to reflect how investors are increasingly asking Boards about how they are managing and mitigating cybersecurity because of litigation and reputation risk, amidst a fast-moving threat landscape and off the back of digital innovation.
Chaired by
- Marcus Alldrick, Former CISO, Lloyd’s of London. Digital Risk Management, Security and Compliance Advisor
Meet The Board Members
- Mr. John Hutson, Chief Executive Officer, Executive Director, JD Wetherspoon PLC.
- Mr. Robin Dargue, Global CIO, WPP
- Air Marshal Sir Christopher Coville, Senior Defence Advisor, EMC and BT. Former Chairman, Westland Helicopters Ltd.
- Jane Wilkinson, Globel CEO and Board Level Chief Marketing Officer, & Non Executive Director
Meet the Speaker Panel
- Professor Robert Coles, Visiting Professor, Royal Holloway, University of London and CISO, NHS/Director – Data Security Centre, NHS Digital
- Charles Delingpole, CEO and Cofounder, ComplyAdvantage
- Tim Sadler, CEO and Co-Founder, Tessian
- Cath Goulding, Head of Cyber Security, Nominet
- Matt Middleton-Leal, General Manager EMEA, Netwrix
- Ben Bulpett, Security IQ Director, EMEA, SailPoint
- Daniel M. Freeman, Managing Partner, C5 Capital Ltd
- Mark Logsdon, Head of Cyber Assurance and Oversight, Prudential
- Graham Ayre, Senior Auditor, ArgoGlobal – A Lloyd’s of London Syndicate
- Chris Wallis, Founder, Intruder
Email teampulse@pulseconferences.com
Discussion points to cover
- Business engagement, risk and governance
- Digital innovation and M&A risks
- Structures, roles and standards
- Communications and reporting metrics
- Risk management and resilience
Including questions around
- How can CISOs engage in a longer-term security strategy against cyber-crime that the Board and other C-Suite will appreciate?
- How can the CISO best understand information security in the big picture of Enterprise Risk Management frameworks?
- Risk scenario modelling and risk reporting – Board top recommendations to CISOs
- How can the CISO develop an action plan to gain traction with CIO, CTO, CFO, CEO, Audit Committee, Board? How can CISOs improve their leadership offering?
- What’s the right level of communication to business stakeholders? What are the keys to winning budget?
- What can boards do to improve business performance around cyber risk? What do Board members need to know about cyber?
- How are companies managing cyber risk? Tone from the top – how do we build security and resilience into organisational culture?
As a CISO why attend
- A rare chance to question a real Board – with no consequences! Attraction for CISOs and senior cybersecurity attendees is to get a chance to do something they rarely get to do if ever, talk to the board frankly and without real consequences. To share as an audience their joint or differing views on the subject as well as with the panel.
- Unique opportunity to find out what the perspective is of board members towards cybersecurity.
- To appreciate the importance first hand of speaking to the board in a way that makes them understand and care. To tell them what they would like boards to do better with respect to cyber.
- Reciprocal exchange. A chance for the panel of Board Members to explain to CISOs what they would like to hear from them or how they would like CISOs to communicate better. The panel of directors would have a similar and reciprocal opportunity to learn about how CISOs as a group think and feel on the subject.
- Immersive – all invited guests are expected to contribute to the discussions that will be held under the Chatham House Rule. The talks end with a networking reception.
- Designed – to produce practical take-aways on cyber risk and security as part of the Enterprise Risk Management strategy at Board level, and as part of a robust business.
As a Board Member why attend
As Board members well know, given the real threat to customer data, privacy and intellectual property, information security is a reputational risk that is becoming increasingly of interest to a wider, non-security audience. Given that reputation, and ultimately company survival and shareholder investment, is at stake, we are aware for example that Audit and Risk Committees are asking for increased assurance about how cyber risk is managed. This event is a rare opportunity to meet with CISOs from leading businesses and government departments. You will exchange views on emerging expectations and strategy and it is a unique chance to hear directly from cyber security experts on how to manage cyber threats in a consistent, practical and ethical way.
- Gain insights about how CISOs as a group think and feel about current relations with the board, risk metrics, security investment and reporting structures, to better communicate with their own security teams.
- A rare opportunity for the Board (and CISOs) to hear directly from the investor community what new standards and expectations on managing and mitigating cyber risk will be – especially following recent PRI engagements on managing cyber risk in a responsible way. The Board will be held ultimately responsible, financially and reputation-wise.
Email: teampulse@pulseconferences.com
Networking reception
Sarastro – 16:30- 19:00
126 Drury Lane, TheatreLand, London, WC2B 5SU
www.sarastro-restaurant.com
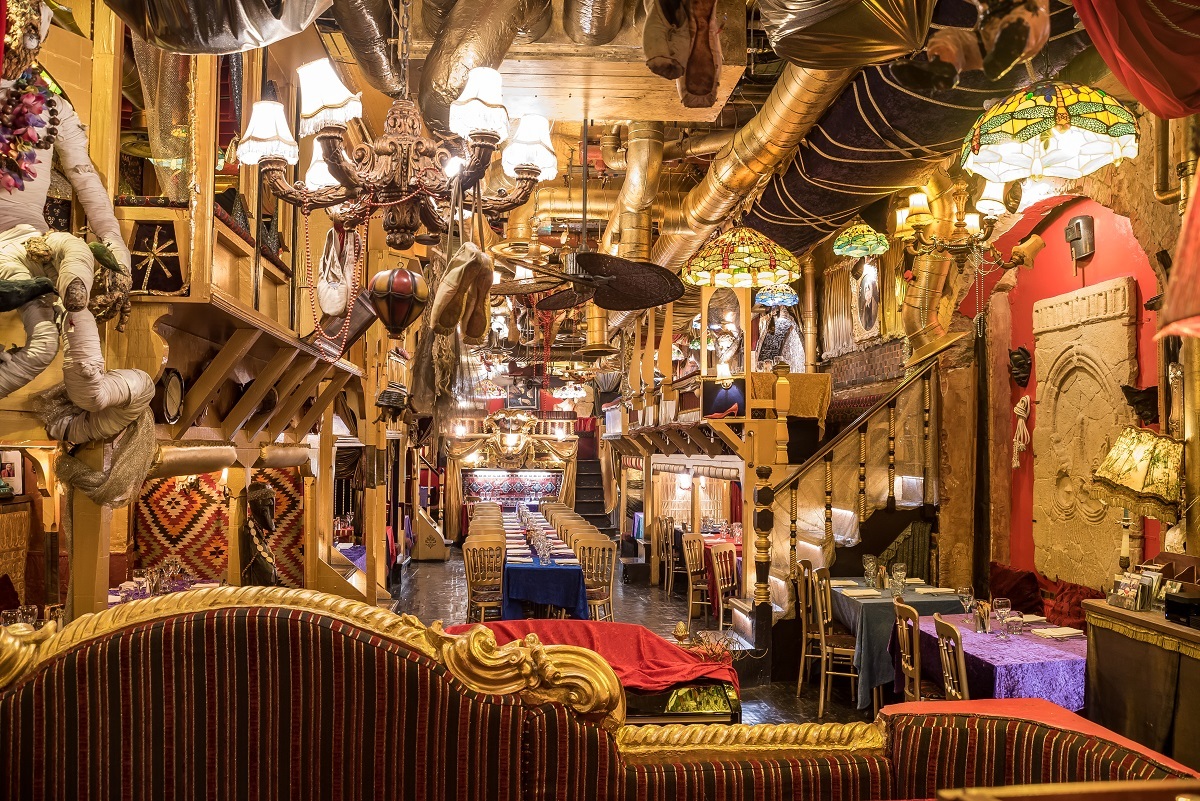
After Talk to the Board discussion all guests, speakers and sponsors are invited to walk across the road for a networking reception at Sarastro restaurant, only a few minutes walk from The London Transport Museum. This enchanted restaurant invites guests into a imaginative and remarkable atmosphere as it was a scene from The Arabian Nights, the interior of Sarastro is ablaze with swirling colour and visual excitement!
Thank you to all the Sponsors of Talk to the Board 2018!
Platinum Sponsor
Gold Sponsors
With thanks to our sponsors
Sponsors
Who attends
By Designation
Participants will include CISOs as well as Board Directors, NEDs and C-Suite
- Chairman
- CEO
- Non-Executive Directors, Board Member, Audit & Risk Committee Member
- CFO, CRO, GC, COO, CTO, CIO, CMO, HR
- Chief Information Security Officer
- Director of Cybersecurity / Head of Cyber Threat Intelligence
- Head of Security Governance
- Director of Digital Risk
- Chief Data Officer
- Chief Privacy Officer
By Sector
All private and public sectors are welcome to attend.
Meet the Speakers
Chairman
Board members
Speakers
Marcus Alldrick
Former CISO, Lloyd’s of London. Currently Digital Risk Management, Security and Compliance Advisor
Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer.
In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.
Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc.

John Hutson
Chief Executive Officer, J D Wetherspoon PLC
Mr. John Hutson serves as Chief Executive Officer, Executive Director of JD Wetherspoon PLC. He Joined in 1991 and was appointed to the board in 1996. He is a graduate of Exeter University and previously worked with Allied Domecq.
Mark Wood CBE
Chairman, NSPCC
Mark Wood CBE is one of the UK’s leading financial figures. He has held several senior positions in global institutions, including Head of Cash Management at Barclays Bank, Chief Executive of Prudential UK and Europe as well as CEO of AXA UK.
In 2006, with £500m of private equity backing, Mark founded Paternoster, which quickly became the market leader in bulk annuities.
A regular media commentator on pensions and insurance, Mark is a Non-Executive Director of the Royal Automobile Club and Chairman of the Board of Trustees of the NSPCC.
He received an Honorary Doctorate in Business Administration from Anglia Ruskin University in 2010.
In 2017 Mark was appointed Commander of the Order of the British Empire in recognition of his outstanding contribution to the British public sector.
Air Marshal Sir Christopher Coville
Senior Defence Advisor, EMC and BT. Former Chairman, Westland Helicopters Ltd.
Air Marshal Sir Christopher Coville was born in Liverpool in 1945, and joined the Royal Air Force in 1964 as a Flight Cadet at the RAF College Cranwell. After flying training, he served several tours of duty as an operational Lightning and Phantom pilot in the Air Defence role. His early career included staff and command appointments, including commanding No 111 (Fighter) Squadron, a spell in the Falkland Islands in 1983 as Officer Commanding Operations Wing, and later command of RAF Coningsby, where he flew the Tornado F3 and displayed the Hurricane and Spitfire of the Battle of Britain Memorial Flight. He is also a qualified helicopter pilot, having converted to Gazelle and Whirlwind. In July 1992, on promotion to Air Vice-Marshal, he was appointed Air Officer Commanding Training Group, with responsibility for all RAF Air and Ground Training, as well as overall supervision of the Red Arrows. In September 1994 he became Assistant Chief of Defence Staff Operational Requirements (Air Systems), in which post he oversaw the largest re-equipment programme for the RAF since the War, and had responsibility for the MOD’s Air Research Programme. On promotion to Air Marshal in 1998, he was appointed as Deputy Commander-in-Chief, Allied Forces Central Europe. In this role, he was responsible for development of NATO’s Combined Joint Task Force (CJTF), and he was involved at the Operational Level of Command in the conflict in the Balkans. Additionally, he was charged with leading the Czech Republic and Polish Armed Forces successful integration into the integrated military structure of NATO. He assumed the appointment of Air Member for Personnel (an RAF Board position as the RAF’s HR Director) and Commander-in-Chief Personnel and Training Command in March 2001, and retired from the regular RAF in May 2003. He continued flying in the RAFVR, on the Tutor aircraft in support of the Air Cadet Organisation, until May 2012, when he finally left the service after 50 years flying in uniform. He has since recommenced gliding with the Devon and Somerset Gliding Club, and is the Hon President of No 2 Flying Training School, the home of Air Cadet gliding.. The Air Marshal was awarded The Queen’s Commendation for Valuable Services in the Air in 1988, the CB in the 1995 New Year’s Honours List and became a Knight Commander of the Order of the Bath in the New Year’s Honours List of 2000. In recognition of his work integrating the Czech Republic’s Armed Forces into NATO, he was awarded the nation’s Gold Commemorative Medal in 2001. He is a Fellow of both the Royal Aeronautical Society and the Chartered Institute of Personnel and Development, and is a founder graduate of the Open University. From 1995-2003, he was President of RAF football, President of Combined Services FA in 2003, and an Honorary Vice-President of the Football Association from 1996-2003. He is now President of the RAF Veteran’s team. Sir Christopher has enjoyed a successful second career in business and in the Third Sector. He is past Chairman of Westland Helicopters Ltd (2005-February 2011), and past Chairman of the European Aerospace Companies’ Rotorcraft Group (2004-12). From 2003-20010 he was President of the Aircrew Association. He was until 2017 Senior Defence and Security Advisor to Dell EMC/RSA, a global ICT Company, where he established a national reputation for his campaign to promote Cyber as a major UK commercial opportunity. Indeed, in recognition of his leadership role in Cyber, her is a member of the Information Assurance Advisory Council (IAAC) community of interest, and is a member of the Security Awareness Special Interest Group (SASIG). In addition, he was until August 2014 Chairman of the Forces Pension Society, and is past-President of the Regular Forces Employment Association and a Life Vice-President of the European Area of RAFA. He sits on the Councils of several civilian and service charities, and has recently embarked on a part time career as a Guest Lecturer on cruise ships. From 2014-2018, he assumed the Chair of the British Helicopter Association, which represents the interests of all civilian helicopter operators and manufacturers, and was a full Council Member of the European Helicopter Association. A keen glider pilot, he was appointed President of Air Cadet Gliding in June 2015. Since 2017, he has been Chairman of the Strategy Board of the Aviation Skills Partnership (ASP).
Robin Dargue
Global CIO, WPP
Robin Dargue is the Group CIO of WPP and the CEO of Coretech. Appointed in February 2014, Robin’s current focus is to execute the transformation of WPP Groups IT environment to enable the group’s current strategic direction.
Robin joined WPP from Alcatel-Lucent, where he held the role of Executive Vice-President for Business and IT Transformation, and was a member of the Alcatel-Lucent Management Committee. Prior to this, Robin was a business leader in both Royal Mail and Diageo, in charge of business and IT-based transformation programmes. At Royal Mail, he oversaw the introduction of a number of new technology-led products and services for customers, while executing the modernisation of the organisation’s technology assets.
Robin’s background and experience brings a real depth of experience of enabling global businesses to define a clear IT Strategy and Architecture, building capabilities to deliver a new way of operating to drive improved business performance. Robin has a degree in computer science from Strathclyde University.
Jane Wilkinson
Global CEO and Board level Chief Marketing Officer, & Non Executive Director
Professor Robert Coles
Visiting Professor, Royal Holloway, University of London and CISO, NHS/Director - Data Security Centre, NHS Digital
Robert Coles is a Visiting Professor at Royal Holloway, University of London, where he is conducting his research into security culture change. He also runs his own consulting business. Prior to this, Robert was the first Chief Information Security Officer at GSK from 2013 to 2018.
Robert held several CISO roles prior to joining GSK. He was the first CISO at National Grid and Merrill Lynch before that. In all these roles, he owned the information security risk and was responsible for providing global leadership. He was accountable to the Executive and PLC Boards for establishing information security strategy and direction. Building global information security capabilities and overseeing all of the information security initiatives across the organisations has been his primary career focus.
Charles Delingpole
CEO and Cofounder, ComplyAdvantage
Delingpole cofounded fintech startup MarketInvoice before going on to set up ComplyAdvantage, a startup that helps finance companies cope with regulation. The company trawls records from around the world to make sure customers are compliant with anti-money laundering and “know your customer” requirements. The company works with over 200 businesses including Azimo and Earthport and has raised $8.2 million from venture capitalists. Cambridge-graduate Delingpole set up The Student Room when he was just 16. The website is now the biggest student forum in the world.
Tim Sadler
CEO, Tessian
Tim is the CEO and Co-founder of Tessian, the world’s first machine intelligent email security platform to automatically prevent security threats like misaddressed emails, data loss and spear phishing. Tessian makes email safe every day at world-leading enterprises and has been recognised as “Best Security Startup” by WIRED, “Best Machine Intelligence Startup” by Legal Geek and “Best Startup – Gold Category” by Info Security Products Guide. Tim holds three Masters degrees in design, engineering and innovation from Imperial College and the Royal College of Art and formerly worked in HSBC’s Global Banking division — Tim was also listed as one of Forbes “30 Under 30” in European Technology for 2017 and named “Young Entrepreneur of the Year” at the 2018 Enterprise Awards.
Cath Goulding
Head of Cyber Security, Nominet UK and Board member of the Women’s Security Society
Head of Cyber Security, Nominet UK and Board member of the Women’s Security Society
Cath has 18 years’ experience in the cyber security profession having worked for both UK Government and the private sector. A thought leader in her field, she frequently speaks at security and internet conferences and has provided articles and comments for multiple publications. Her career was profiled in the Financial Times and she has appeared on the BBC promoting women into the IT profession.
Cath currently works as Head of Cyber Security for Nominet UK, the internet company best known for running the ‘dot.uk’ registry and therefore critical to internet operations in the UK. Prior to joining Nominet, Cath worked at GCHQ holding a variety of posts in the field of cyber security. Cath has a BSc in Mathematics, an MSc in Human Computer Interaction and is CISSP qualified. She was awarded Security Champion at the Women in IT awards 2015 and sits on the board of the Women’s Security Society.
Matt Middleton-Leal
General Manager EMEA, Netwrix
Matt Middleton-Leal is General Manager EMEA and Board member at Netwrix Corporation. With 19 years spent working in the security industry, Matt brings significant experience to his role at Netwrix. He has worked for many organisations, specialising in areas such as risk management, identity and access management, application, network and database security. Matt most recently held the position of V.P. Northern Europe at CyberArk Software, where is oversaw five consecutive years of 45%+ per annum revenue growth. Prior to CyberArk he held the position of Business unit executive at IBM Security Systems. Matt joined IBM from CA where he had spent six years, working on their largest information security projects. Matt is a CISSP® – Certified Information Systems Security Professional.
Ben Bulpett
Security IQ Director, EMEA, SailPoint
Ben is the SailPoint EMEA Security IQ Sales Director, where he is responsible for leading SailPoint’s Identity & Access Governance for Files and Data platform across the EMEA region working with the local sales teams, partners and customers. He works across the organisations lines of business in the evolution of the product and go to market strategy and speaks on the topic of Identity Governance for Files and Data for SailPoint in the EMEA region. With over 25 years’ experience in software sales leadership positions; Ben’s knowledge of Software Identity Market is extensive. Ben has travelled extensively throughout Europe, Middle East & America both through his work responsibilities and with his family. He has spoken at numerous events on matters such as security, identity management, software compliance, system mapping and Global Account Management.
Mark Logsdon
Head of Cyber Assurance and Oversight, Prudential Assurance
Mark has been in the security business for all his working life. His career began in the Royal Navy Submarine Service before later joining the Army before joining a ‘niche’ part of the MoD. He was one of the founder members of the Centre for the Protection of Critical National Infrastructure – CPNI – where he was responsible for teams that gave holistic threat and vulnerability advice to the owners and operators of the Critical National Infrastructure. He left the public sector and joined Barclays to become Director, Information Risk Management, a similar role to what he does today. After 5+ years he took up a senior consulting role at BAE systems. His final assignment there was to deliver IT and IT security for the 2014 NATO conference in south Wales, which remains the largest and most complex international conference the UK has ever held. Before joining Prudential two and half years ago, he was at a small start-up where he created and delivered an international award winning cyber awareness programme. Finally, Mark has been an active member of the White Hat Ball organising committee for 10 years and currently Chairs the Committee. This is a group of risk and security professionals, drawn largely from the City, who come together to raise funds for NPSCC Child Line. To date they have raised over £2M for the charity, which has helped to change the lives of countless vulnerable children.
David Higgins
Director of Customer Development, EMEA, CyberArk
David Higgins is the Director of Strategic Accounts, EMEA at CyberArk. With over 10 years’ experience in Privileged Account Security, David is one of the leading experts in understanding the requirements and drivers for managing privileged access security within an organisation, both private and public. David has led some of the largest design and implementation programs of privileged account security with companies across all sectors, many of which are in the Fortune 100. Leveraging this experience, David now works with clients on best practices around privileged management and driving innovative approaches when looking to reduce the risk associated with privileged escalation and exploitation, even more so as organizations embrace cloud platforms and automated processes.
Graham Ayre
Senior Auditor, ArgoGlobal - A Lloyd's of London Syndicate
Daniel M. Freeman
Managing Partner, C5 Capital Ltd
Chris Wallis
Founder, Intruder
Sponsors
Nominet Cyber Security
Nominet Cyber Security is a leader in helping government and enterprise organisations protect mission critical infrastructure from vulnerabilities including Malware, Phishing, Botnets, Cryptomining, Data Exfiltration and Misconfigurations. Our worldwide patented DNS security platform monitors live inbound and outbound network traffic and analyses billions of packets of DNS data in real time, helping customers detect and block known and unknown malicious threats before they harm your business. Our platform deploys in minutes with no cumbersome endpoint rollout and can either be managed in-house by your security team, or trust the Nominet expertise to manage and analyse your DNS service.
The rich APIs enable integration of curated DNS threat information into existing SIEM solutions and management reporting systems, to speed up response time, stop propagation and provide richer intelligence for forensics.
The UK Government depends on Nominet to protect the UK public sector DNS service to stop the use of DNS for malware distribution and operation. For further information, please visit https://www.nominet.uk/dns-cyber/
Skybox
Skybox gives security leaders the cybersecurity management solutions they need to eliminate attack vectors and safeguard business data and services every day. With unparalleled visibility and context-aware intelligence of the attack surface, Skybox solutions drive effective vulnerability and threat management, firewall management and continuous compliance monitoring. Established in 2002, Skybox is a privately held company with worldwide sales and support teams serving an international customer base of Global 2000 enterprises and government agencies. www.skyboxsecurity.com
IBM Resilient
IBM Resilient’s mission is to help organizations thrive in the face of any cyberattack or business crisis. The award-winning Incident Response Platform (IRP) empowers security teams to analyze, respond to and mitigate incidents faster, smarter and more efficiently. Part of IBM Security, the Resilient IRP also integrates security technologies into a single hub and provides easy workflow customization and process automation. With Resilient, security teams can have best-in-class response capabilities. Resilient has more than 100 global customers, including 30 of the Fortune 500 and partners in more than 20 countries. www.resilientsystems.com
SailPoint
SailPoint: The Power of Identity™
SailPoint, the leader in enterprise identity governance, brings the Power of Identity to customers around the world. SailPoint’s open identity platform gives organizations the power to enter new markets, scale their workforces, embrace new technologies, innovate faster and compete on a global basis. As both an industry pioneer and market leader in identity governance, SailPoint delivers security, operational efficiency and compliance to enterprises with complex IT environments. SailPoint’s customers are among the world’s largest companies in a wide range of industries, including: 7 of the top 15 banks, 4 of the top 6 healthcare insurance and managed care providers, 9 of the top 15 property and casualty insurance providers, 5 of the top 15 pharmaceutical companies, and 11 of the largest 15 federal agencies.
Netwrix
Netwrix Corporation focuses exclusively on providing complete visibility for data security and risk mitigation in hybrid IT environments. The sharp focus enables us to offer much more robust functionality than legacy change auditing tools. Over 160,000 IT departments worldwide have already chosen Netwrix Auditor over change auditing software.
Barclay Simpson
Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury. www.barclaysimpson.com
Idecsi
The IDECSI Personal Security Guardian gives every individual visibility to their security and the security of their critical applications, such as email, collaboration tools, ERP, and more. This includes cloud applications, such as Office 365, where security is a major concern for IT and security leaders. As IT scales and more applications are deployed, companies must expand the detection capability to recognise when accounts have been breached, executives are being impersonated, or documents shared inappropriately. By engaging the users in this process, the organisation can be massively safer, but without significantly increased costs. The security team can focus on genuine breaches without trawling through huge numbers of false positives. Learn more: www.idecsi.com
CyberArk
CyberArk is the only security company laser-focused on striking down targeted cyber threats, those that make their way inside to attack the heart of the enterprise. Dedicated to stopping attacks before they stop business, CyberArk is trusted by the world’s leading companies — including more than 50% of the Fortune 100 — to protect their highest-value information assets, infrastructure and applications.
For over a decade CyberArk has led the market in securing enterprises against cyber attacks that take cover behind insider privileges and attack critical enterprise assets. Today, only CyberArk is delivering a new category of targeted security solutions that help leaders stop reacting to cyber threats and get ahead of them, preventing attack escalation before irreparable business harm is done. At a time when auditors and regulators are recognizing that privileged accounts are the fast track for cyber attacks and demanding stronger protection, CyberArk’s security solutions master high-stakes compliance and audit requirements while arming businesses to protect what matters most.
With offices and authorized partners worldwide, CyberArk is a vital security partner to more than 3,300 global businesses, including:
CyberArk has offices in the U.S., Israel, Australia, France, Germany, Italy, Netherlands, Singapore, Turkey and the U.K. Learn more about CyberArk by listening to Udi Mokady, Chairman & CEO discuss Privileged Account Security.
Venue
Venue
London Transport Museum
Covent Garden Piazza (south east corner)
London, WC2E 7BB
Download event brochure
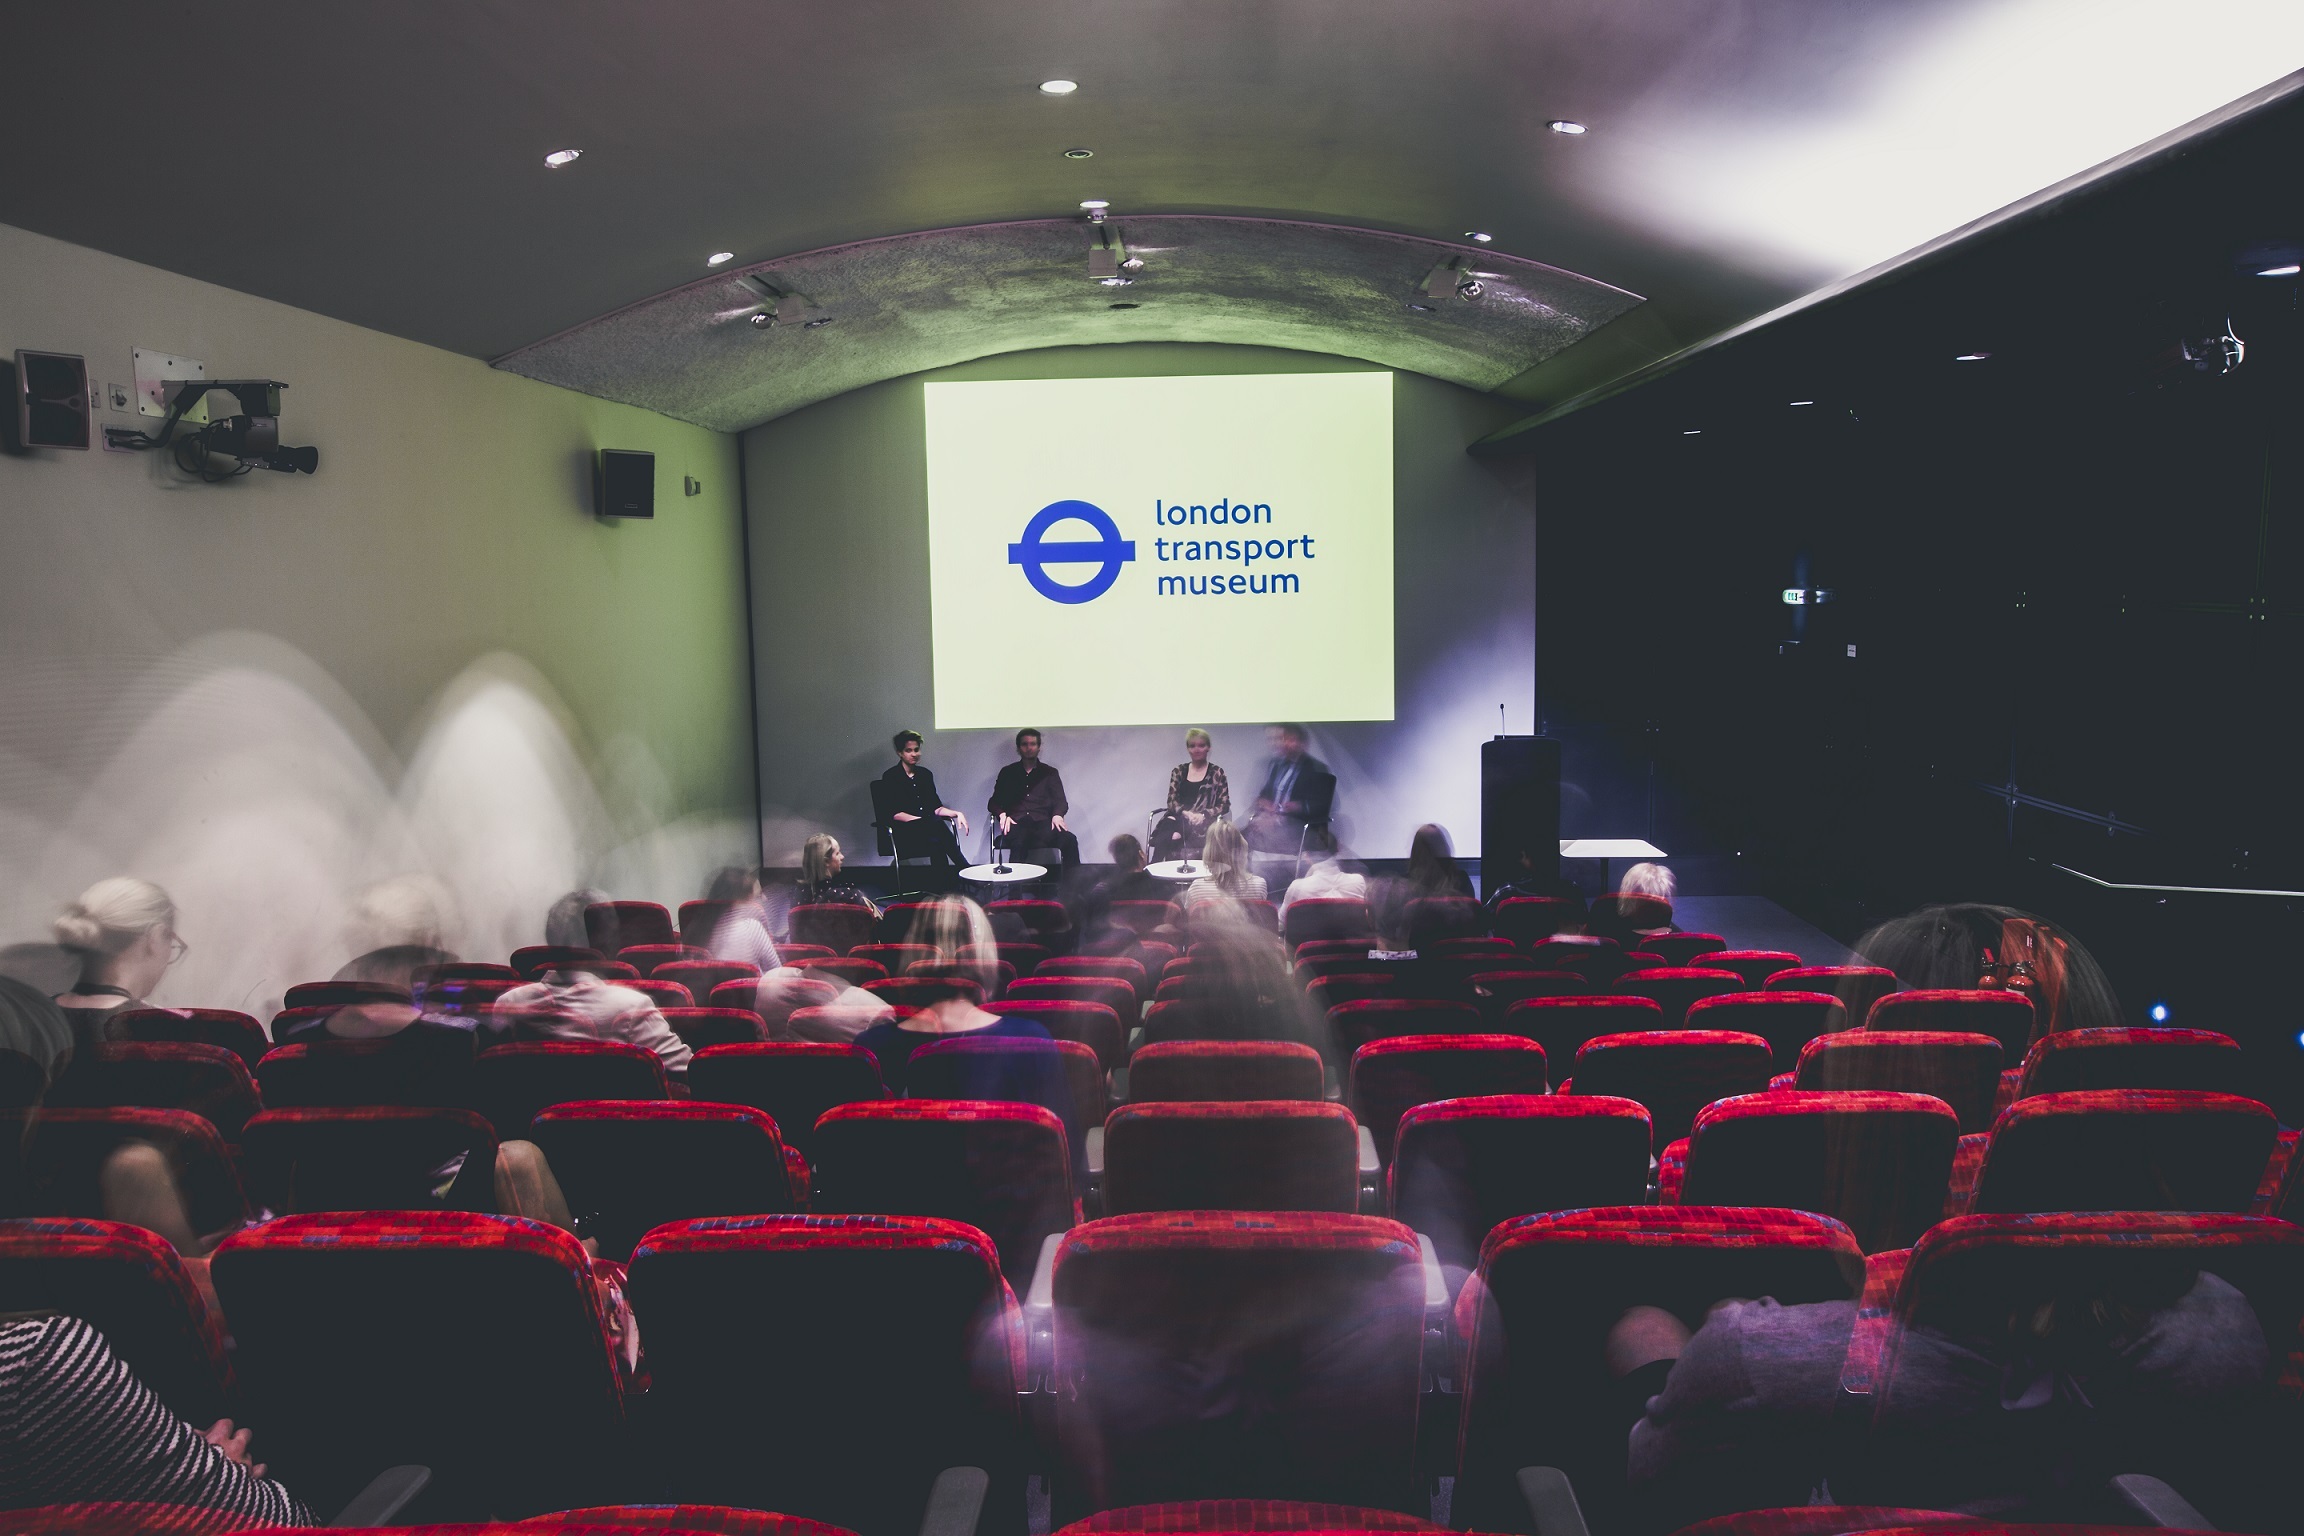
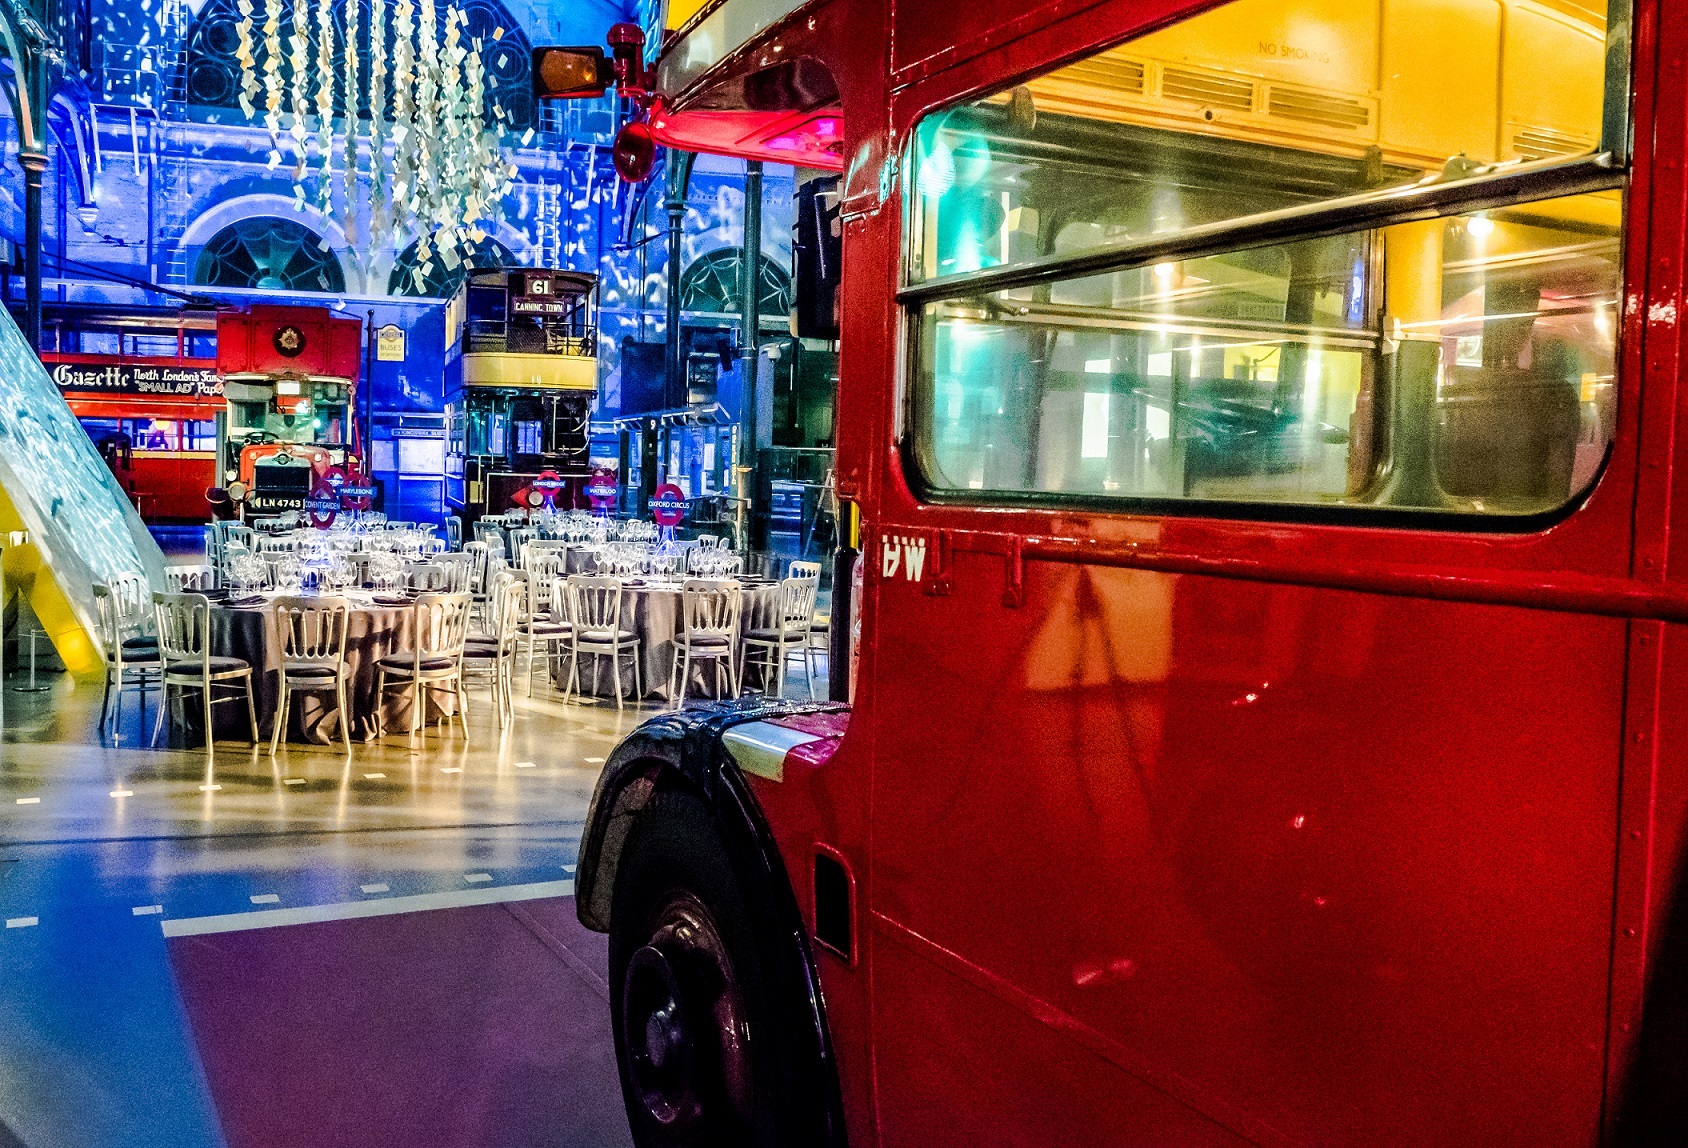
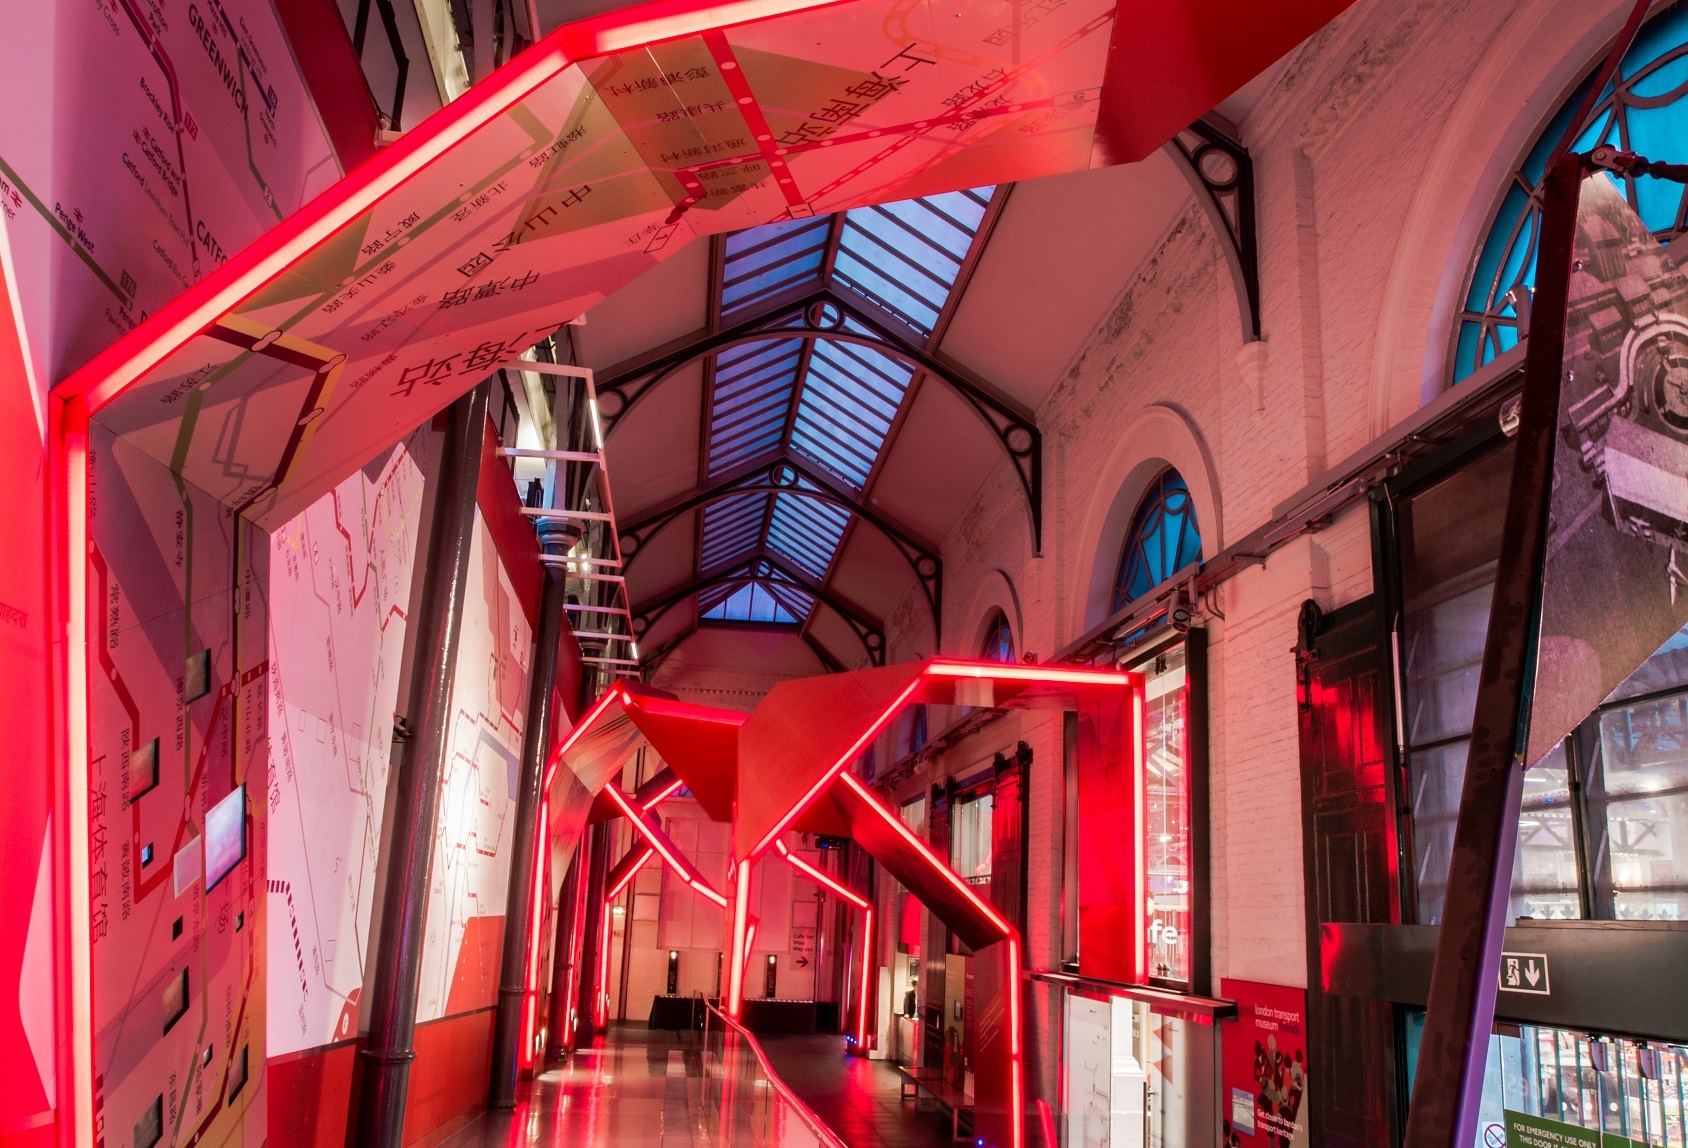
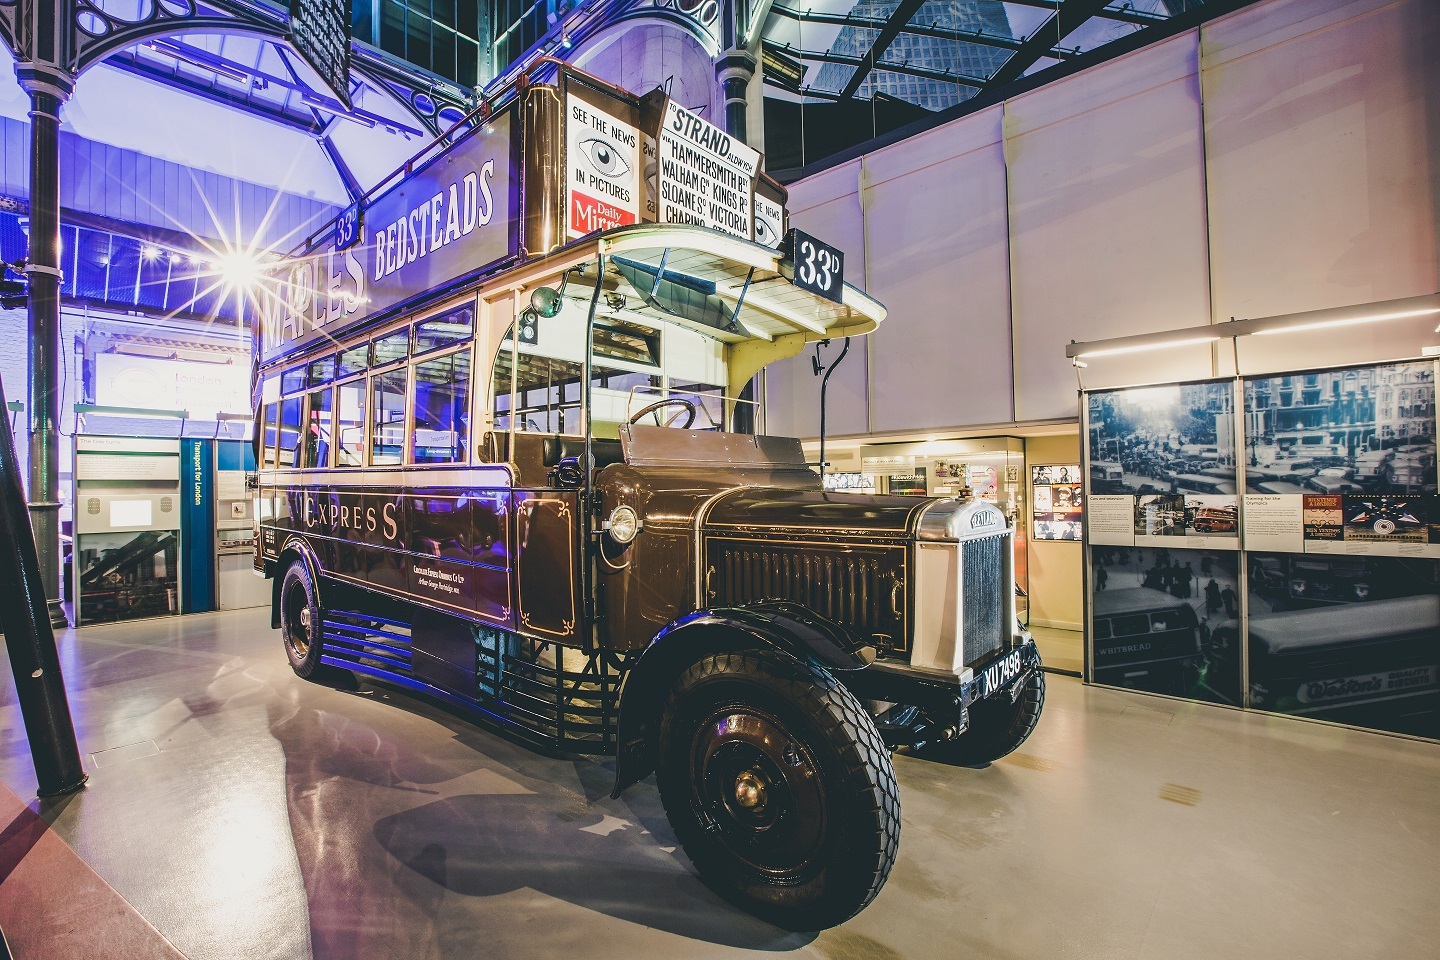
Located in the heart of Covent Garden under the glass roof and cast iron pillars of the original Victorian Flower Market, The London Transport museum’s Cubic Theatre will host Talk to the Board, 6 November. The 121 seat auditorium with adjoining Foyer area is a industry leader for daytime business functions with a newly renovated space and state of the art Audio visual. All guests of Talk to the Board will have free entrance to the museum during the day.
Networking reception
Sarastro
16:50- 19:00
126 Drury Lane, TheatreLand, London, WC2B 5SU
www.sarastro-restaurant.com
After Talk to the Board, all guests, speakers and sponsors are invited to walk across the road for a networking reception at Sarastro restaurant, only a few minutes walk from The London Transport Museum. This enchanted restaurant invites guests into a imaginative and remarkable atmosphere as it was a scene from The Arabian Nights, the interior of Sarastro is ablaze with swirling colour and visual excitement!
Talk to the Board- Downloads
 Download Pulse innovate report - Talk to the Board
 Download Talk to the Board - Event brochure