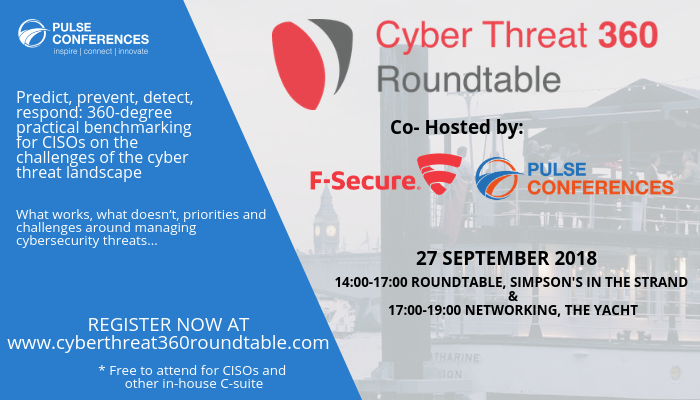
Cyber Threat 360 Roundtable
Co-hosted by
Pulse Conferences would like to thank all guests and co-facilitators who attended the Cyber Threat 360 Roundtable in London 27 September 2018
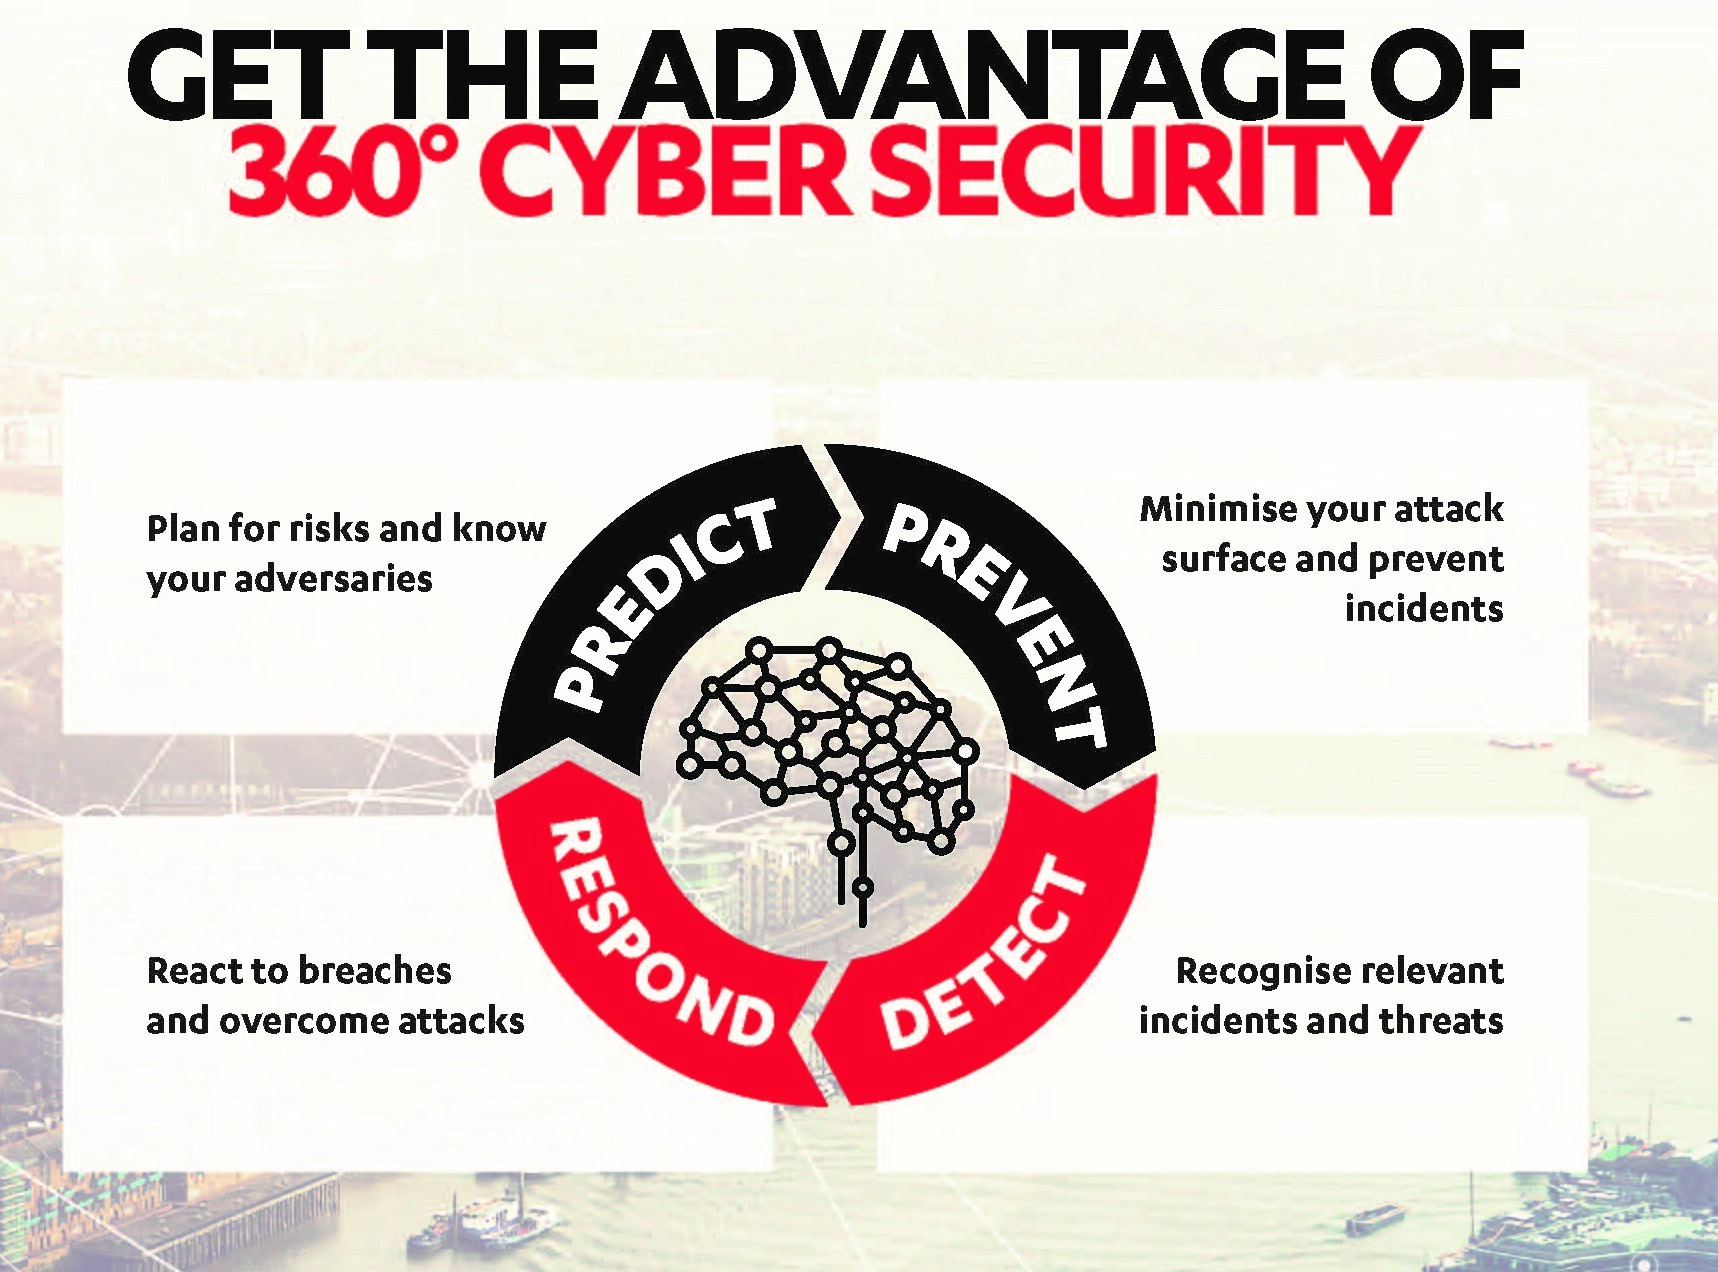
Predict, prevent, detect, respond: 360-degree benchmarking on the challenges of the cyber threat landscape
Timings at a glance:
27 September 2018 – London
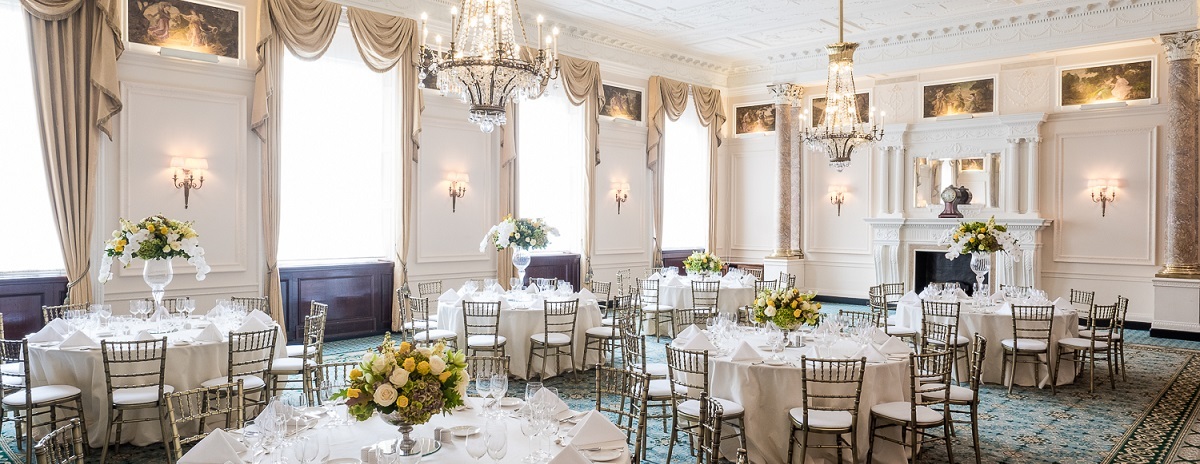
Roundtable discussion – Simpson’s in the Strand – 14:00-17:00
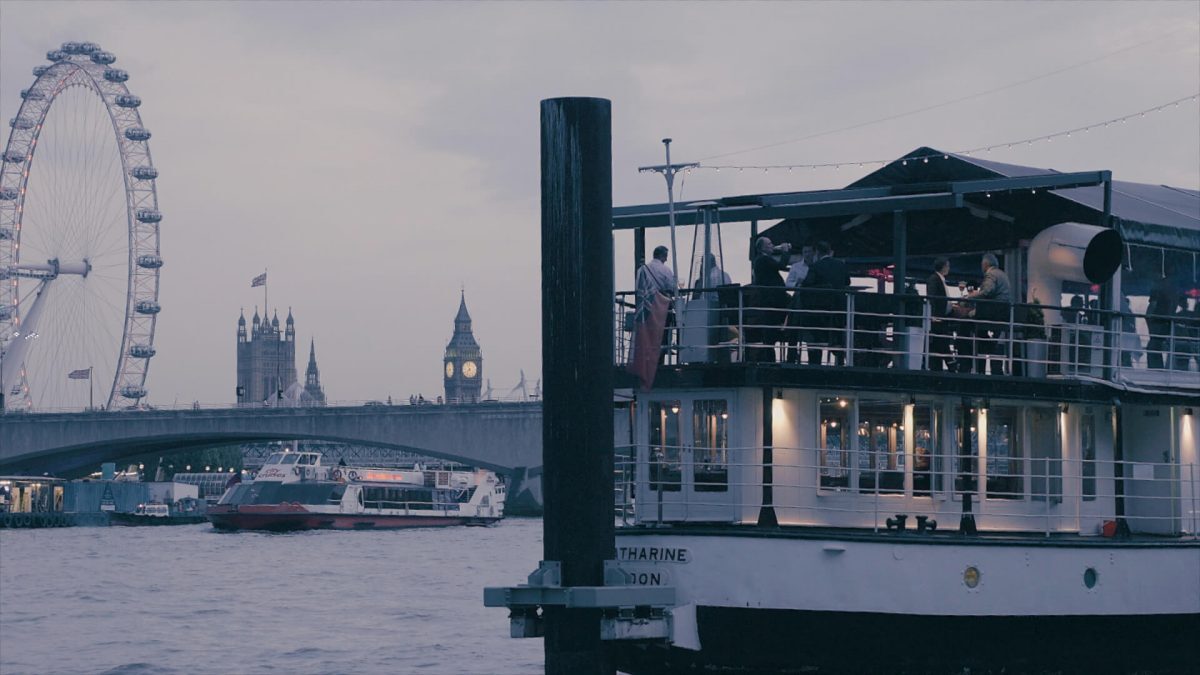
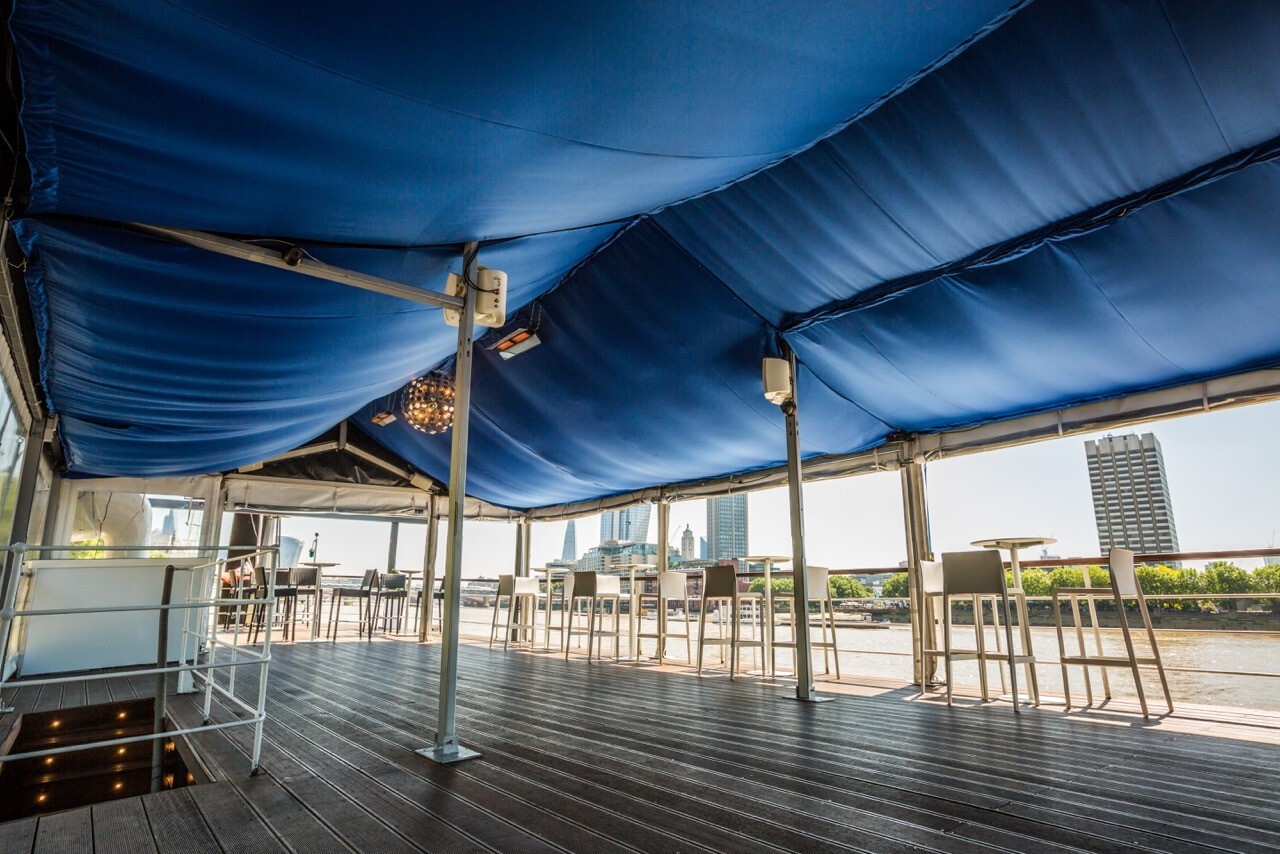
Networking Reception – The Yacht – 17.00- 19:30
Cyber Threat Security 360 Roundtable provided the ideal peer to peer benchmarking opportunity for CISOs, CIOs and other senior risk, responder and technology professionals to examine in-depth and with combined peer group brain power, a multi-faceted approach to managing the challenges of the current and emerging cyber threat landscape.
Complimentary to attend for CISOs and similar senior cybersecurity professionals working in-house for non-vendor, non-consultancy organisations, this is a unique opportunity to connect with peers and expand your trusted professional networks to strengthen capacity.
Topics
A multi-faceted ‘360’ benchmarking exercise for CISOs to exchange experiences on what works, what doesn’t, priorities and challenges around managing cybersecurity threats and breaches.
ROUNDTABLE 1: Prediction
Know your risks, understand your attack surface, uncover weak spots
Understanding the threat landscape. How to focus on those threats that are relevant to our organisation? Is it possible to be predictive in information security? Making best use of available resources. How to justify what security improvements to focus on? How do we quantify the cost of potential breaches to fund a sustainable cybersecurity programme?
ROUNDTABLE 2: Prevention
Minimise attack surface, maximise compartmentalisation and contain breaches
Combating the most common sources of compromise – insider threats and Internet exploits. What are the potential weaknesses in modern organisations that adversaries try to exploit? Are there ways of organising and deploying enterprise systems which reduce impact and reduce time to recover?
ROUNDTABLE 3: Detection
Recognise incidents and threats, isolate and contain them
Do you have visibility beyond the preventive layer? Or the human factor in case of mistakes and unexpected behaviour? How do targeted attacks usually happen? How do you build effective breach detection and response capabilities against advanced targeted attacks?
ROUNDTABLE 4: Response
React to breaches, mitigate the damage, analyse and learn
How do you prepare for the inevitable security incident? How do you select the necessary tools, methods and practices to enable seamless response capability across the organisation? How do you respond to incidents in a way that limits damage and reduce recovery time and costs? • What is the scope, source, magnitude and management response • What data and information should be collected • Who is on the crisis team • At what stage should customers be informed?
Co-Facilitators
- Quentyn Taylor, Director of Information Security EMEA, Canon Europe
- Lee Barney, Director of Information Security, YOOX NET-A-PORTER GROUP
- Graham Edwards, DPO, Nationwide
- Chris Gibson, CISO, The Orwell Group
- Paul Pratley, Head of Investigations & Incident Response, MWR InfoSecurity
- Greg Jones, Principal Consultant & Founder, Digital Assurance, F-Secure
- Mats Palm, Director, Product Management, F-Secure
- Jani Kallio, Vice President Strategic Expansion, F-Secure
Timings – half day
14:00-14:20 Arrivals for afternoon tea and coffee
14:20-14:35 Introductions and objectives setting – co-chairs
14:35-14:50 Keynote / Case study
14:50-15:40 Roundtables 1-4 working each on a chosen 1st perspective
15:40-15:45 Short coffee break and participants rotate to chosen new table. Facilitators remain fixed to their allocated perspective
15:45-16:35 Roundtables 1-4 working each on a chosen 2nd perspective
16:35-16:55 Conclusions – each table shares back key findings to the whole group
16:55-17:00 Close of Roundtable
17:00-19:30 Networking reception – The Yacht
Structure
Two facilitators (a CISO practitioner and a senior strategist from F-Secure) will lead each table. Each of the 4 tables will focus on a given different ‘perspective’ of the cyber
threat landscape to consider. Attendees will be asked to select 2 out of the possible 4 Roundtables when they register. The CISO audience will rotate their choice of tables once. The two Co-facilitators and a note-taker will remain fixed to each table to lead and capture the key discussion points, observing The Chatham House Rule.
Shared output benefits
Notes will be taken throughout the roundtable discussions, observing the Chatham House Rule. Once all the feedback has been compiled and written up, the end-result will form the ‘Cyber threat 360 output report’, a report that will be distributed to all attendees in the weeks following the event with the combined thoughts and conclusions from the participating leading companies.
*Please note that registration for this particular event is only open to CISOs and similar senior cybersecurity practitioners currently working in-house for corporates (financial services, energy, utilities, gaming/gambling…). All online registrations are subject to final approval by Pulse Conferences.
Co-hosted by
360 degree protection – It takes a combination of the latest human expertise and continuously improving technology to comprehensively predict, prevent, detect and respond to threats.
Rest easy – F-Secure’s holistic portfolio of cyber security solutions and services will cover all of your organization’s cyber security needs. Our extensive human knowledge and insight, combined with smart software and cutting edge AI, merge into a single entity, dedicated to protecting you.
The world is becoming digitalized and connected. Due to this, cyberattacks and cyber-crime continue to be among the most critical challenges the world is facing. While the complexity and magnitude of problems increases, expertise is concentrating into a limited number of specialized security companies. For three decades, F-Secure has driven innovations in cyber security, defending tens of thousands of companies and millions of people. We are transforming from an endpoint protection company to a cyber security leader with a broader set of products and services.
F-Secure’s competitiveness is based on extensive experience in cyber security, and a unique combination of man and machine. Our extensive experience, knowledge and insight in cyber security, combined with our global intelligence network, smart software and cutting edge artificial intelligence makes us the perfect trusted cyber security partner for companies of all sizes as well as individuals. We are the proud security advisor to many of the world’s largest and most demanding organizations e.g. in the banking, automotive and airline industries as well as the military and law enforcement sector. Our expertise is continuously developed, as we take on the toughest of assignments.
As F-Secure seeks to accelerate growth, we continue to focus growth investments in corporate security. We provide best-in-class services and solutions to the mid-market, especially for customers seeking to buy prevention, detection and response as a service. We foresee the market moving towards managed endpoint security, and see especially strong growth in detection and response services. As we expand our product and service offering, we are also making it more integrated in order to offer efficient and comprehensive turn-key solutions to our customers and partners.
Summary of key drivers and benefits of the MWR InfoSecurity acquisition
- Digitalization and the rapidly increasing number of cyberattacks create significant cyber security risks for companies, driving customer demand for new types of cyber security products and services.
- One of the fastest growing market segments is detection and response solutions (EDR), and managed detection and response services (MDR). Currently, only a fraction of companies have the capabilities needed to consistently counter targeted attacks.
- F-Secure has a strong offering for detection and response solutions and services and continues to see significant business opportunities in these emerging markets. F-Secure aims to be a key player in this segment. Combining the acquired technologies with F-Secure’s existing capabilities enables the company to offer truly industry-leading detection and response solutions.
- The acquisition makes F-Secure one the few truly global technical cyber security advisors, uniquely positioning it to support both midmarket companies and large enterprises across the globe. It also makes F-Secure the largest European single source of cyber security services and detection and response solutions.
- MWR’s world-class research and experience in securing some of the most challenging and mature enterprise environments makes its threat hunting solution unique. With the acquisition F-Secure gains unparalleled insight from across its cyber security services into the attacker mindset, the challenges SOCs face, emerging TTPs, and the latest response techniques.
Today businesses are challenged by a dynamic advanced threat landscape in which attackers continuously use well-designed technology to circumvent traditional protection. Security perimeters are no longer enough to protect organizations, and developing better security capabilities on their own is out of reach for many organizations. Due to the shortage of skilled cyber security experts in-house there is a huge demand for both products and services to proactively search for newly emerging threats, detect and respond faster and especially stop future incidents. F-Secure’s combination of man and machine – an approach bolstered by F-Secure’s acquisition of MWR InfoSecurity – uniquely positions the company to support businesses to fight advanced attacks with its cyber security products and services.
The combined company has hundreds of the world’s best cyber security consultants, making F-Secure one of the few truly global technical security advisors positioned to help organizations fight today’s most sophisticated threats. Learnings from the most challenging incident investigations and from targeted attack simulations provide insights that feed directly back into product creation, ensuring the company’s detection and response solutions are constantly upgraded to meet the latest threats.
Pulse Conferences is the connective platform for professionals working in governance, security, cyber, risk, audit, legal, compliance, privacy and investigations as well as the lines of business, executive suite and the board itself. Our purpose is to inspire and connect these leaders that form the distinct but connecting backbone of public and private sector organisations alike through ‘live’ community based face to face events – international conferences, localised roundtable discussions and training courses.
Working collaboratively as an industry stakeholder with industry stakeholders, Team Pulse develops and hosts events that respond directly to the ebb and flow of current and emerging business landscapes. We build trusted business communities. Our events are held under the Chatham House Rule.
www.pulseconferences.com
Co-hosted by
Download invitation
Quentyn Taylor
Director of Information Security EMEA, Canon Europe
Quentyn Taylor is Director of Information Security for Canon Europe. He has a wealth of experience in both the IT and information security arenas and, in recent years, has focused his attention on building business relationships across the world.
Quentyn has driven Canon’s strategy to highlight the importance of document security and help business customers to minimise their security risk. Quentyn strongly believes in educating users about the importance of a comprehensive, overall security framework that will allow Canon’s business customers to improve security in a cost-effective way.
During his career, Quentyn has worked in a variety of industries for a number of organisations including outsourced service providers, Internet service providers as well as Dotcom businesses, before moving to Canon in 2000.
Lee Barney
CISO, Net a Porter
Lee Barney is a passionate believer in using Security as a business enabler; he does this through challenging the preconceptions of the industry and by changing the mind set of those who work in Security to be more pragmatic. Having worked in Defence, Consulting, Finance and now Retail, Lee has a breadth of knowledge about what works well and what doesn’t work at all. Lee advocates a healthy relationship with the Chiefs of an organisation pointing out that our industry is built on Executive buy in not scare mongering.
Graham Edwards
DPO, Nationwide
The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He currently holds the position of Director of Data Security at Nationwide Building Society. Graham has a master’s degree in Information Security from Royal Holloway.
John Meakin
Group CISO, GSK
Prior to joining GSK, John was Chief Security & Risk Officer at Burberry, he was responsible for successfully restructuring a significant investment in improved security and also advised the Board on status and remediation of all principal enterprise risks. John was also Chief Security Officer for Richemont International SA in Geneva, with oversight over physical, information and cyber security. He implemented a new strategy for a holistic approach to security (physical to cyber). Previously, he has built and led information and cyber security functions in a range of Banks, notably the Royal Bank of Scotland, Dresdner Bank and Standard Chartered Bank. He has also been Chief Information Security Officer of BP, where he led the cyber response to the 2010 Gulf of Mexico crisis. He started his career in software development for Defence systems and was one of the very first CISOs with Reuters in the late 1980s. John has a Batchelors degree in Chemistry & Physics from Durham University and a Ph.D. in experimental solid-state physics from Cambridge University in the UK.
Paul Pratley
Head of Investigations & Incident Response, MWR InfoSecurity
Paul is a veteran incident responder and researcher, experienced working in and leading high profile data breach investigations including state affiliated, industrial espionage, financial and ideologically motivated attacks.
Paul is currently an Associate Director and Head of MWR’s Investigations & Incident Response (IR) Practice, leading a team of highly skilled and experienced investigators, backed up by a world class IR toolsets and threat intelligence. MWR is listed as an accredited provider of Incident Response services under both the UK NCSC and CREST Cyber Incident Response (CIR) schemes and assists many organisations each year to contain and recover from major computer and network security incidents.
Greg Jones
Principal Consultant & Founder of Digital Assurance, F-Secure
Greg has worked in IT since 1990 and focused within information security for over 20 years having worked at IBM, DEC, KPMG and more recently F-Secure / Digital Assurance. Greg is a very experienced security tester having delivered several hundred security assessments over the course of his career. Greg also sits on the executive board of CREST, a not-for-profit body which provides standards and certification paths for security testers and incident handling.
Mats Palm
Director, Product Management, F-Secure
Mats is heading the F-Secure managed detection and response solution – Rapid Detection & Response Service. A unique and best of breed MDR service on the market. Personally I’ve lived and breathed cyber security for three decades, looking at it from different angles like R&D and sales. Open minded about new things and always ready to have a good discussion around all things cyber!
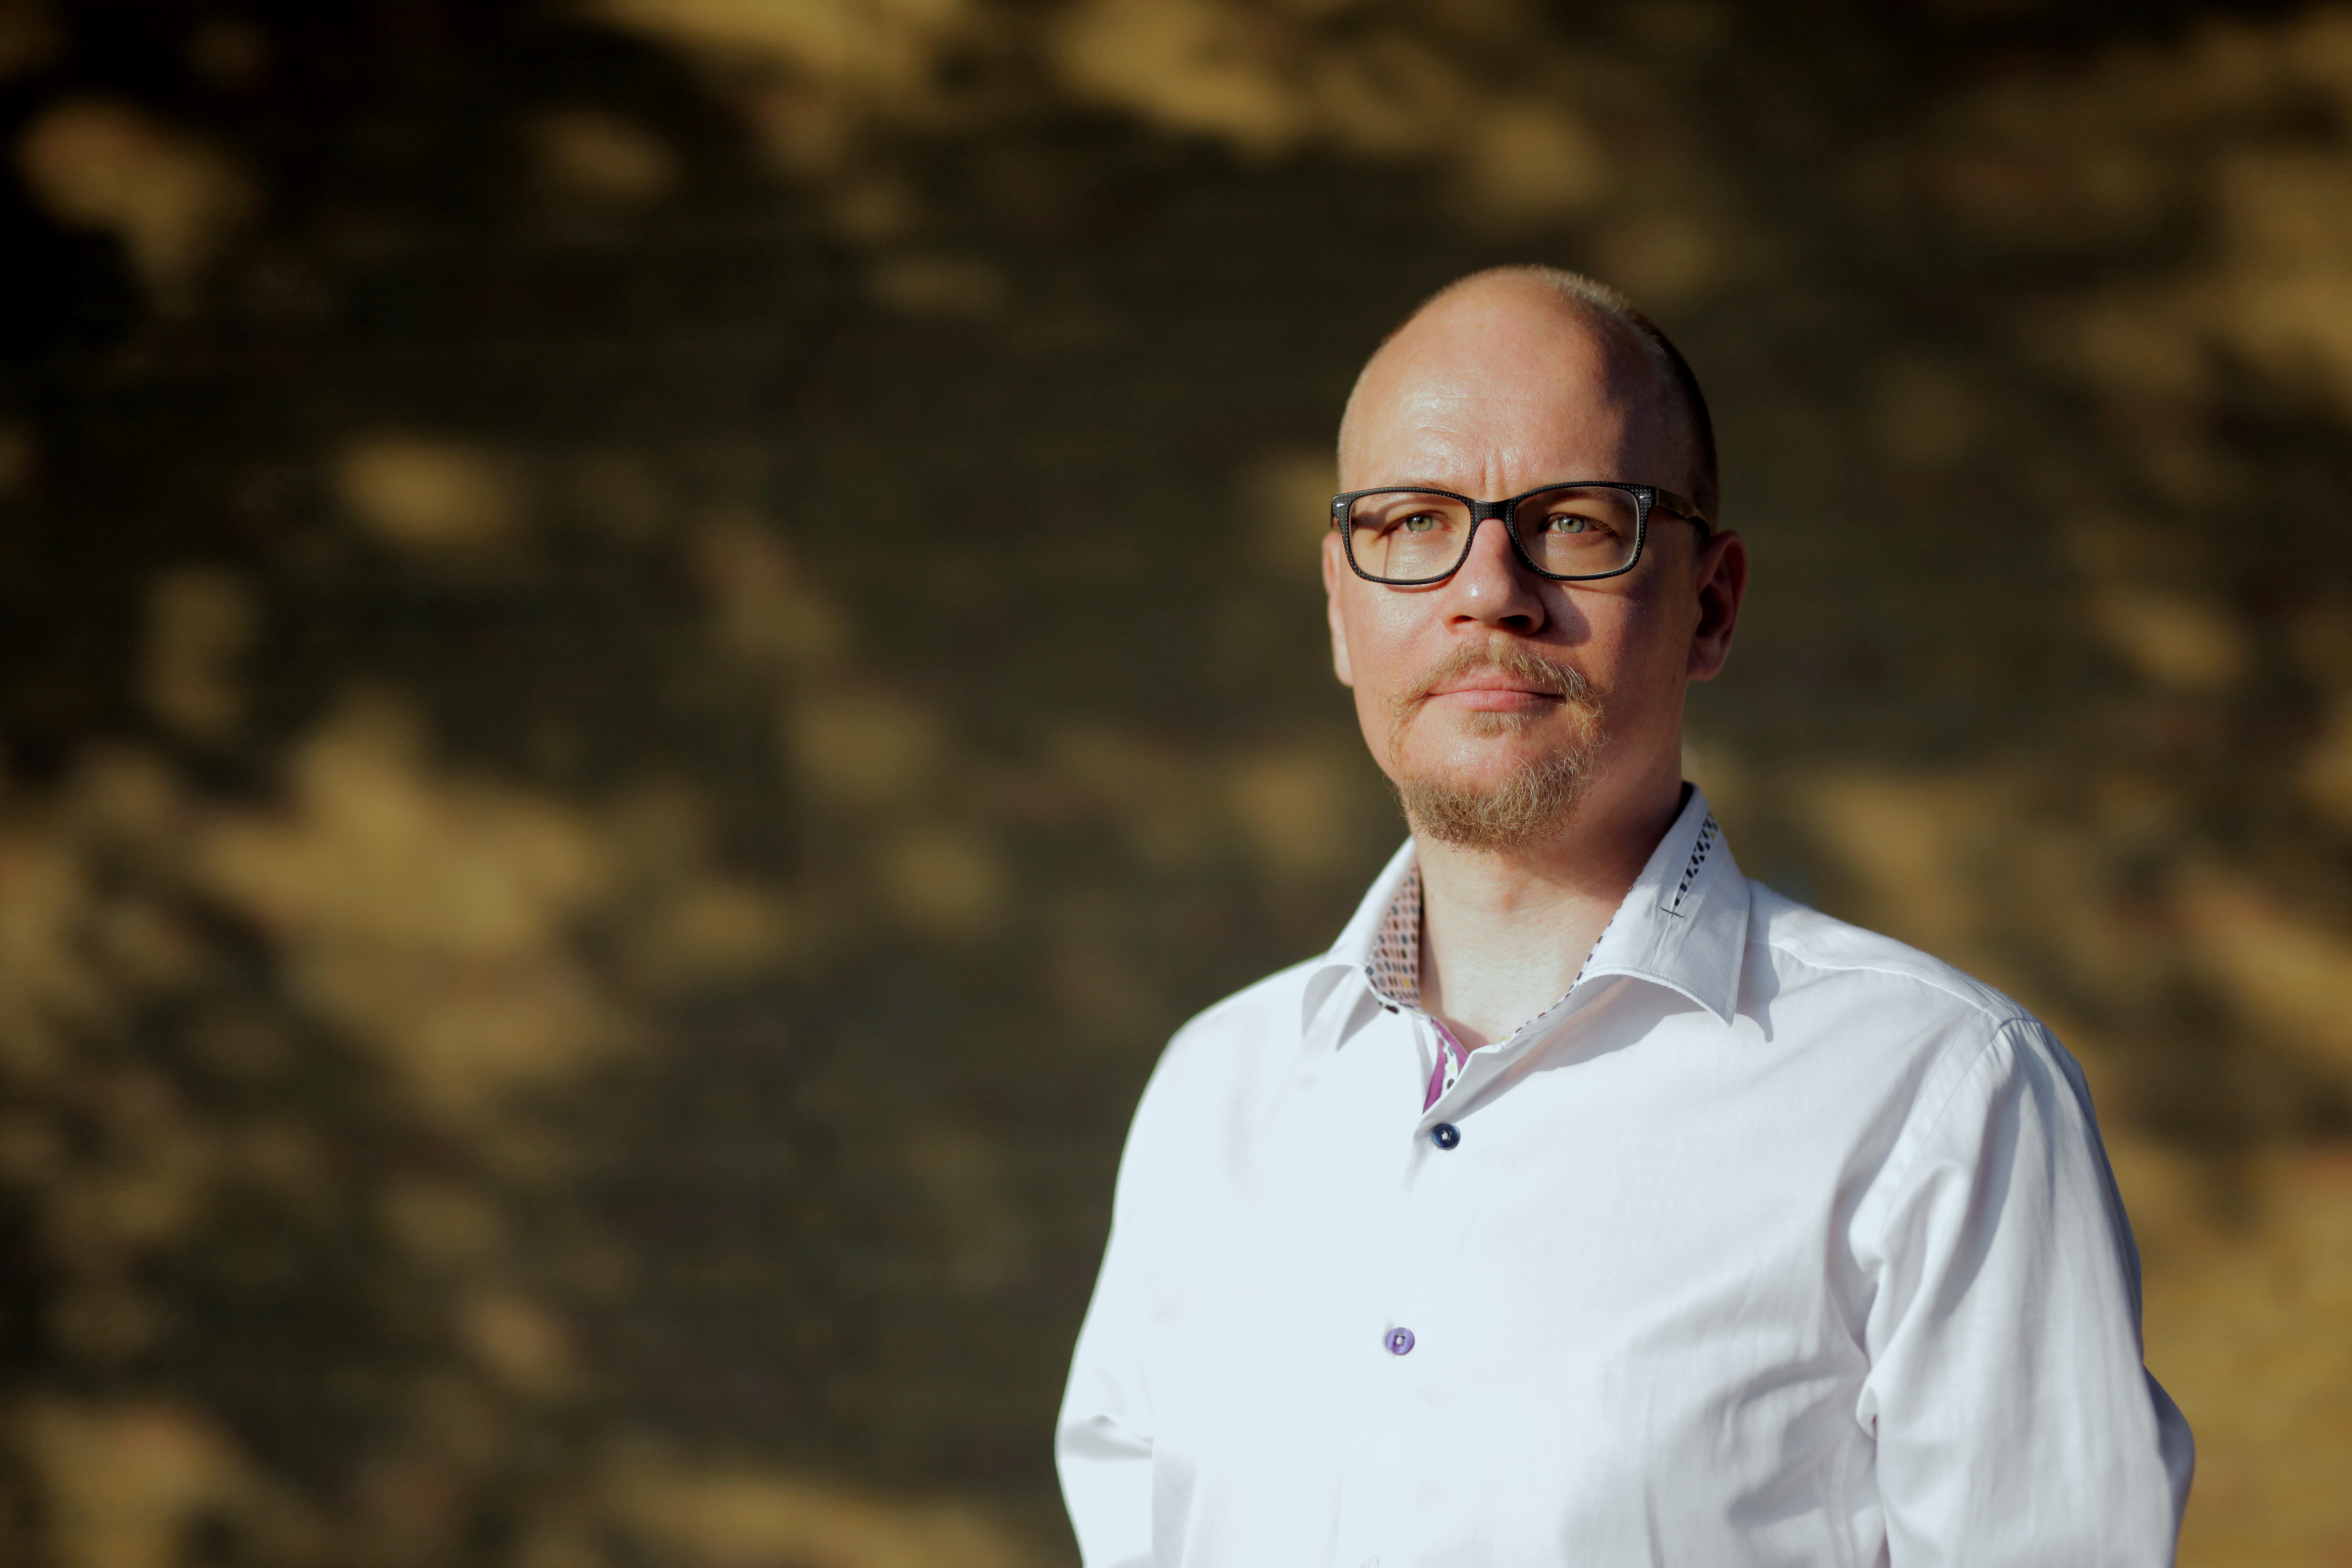
Jani Kallio
Vice President Strategic Expansion, F-Secure
Jani is currently developing F-Secure’s Cyber Security Products and Services business by establishing new partnerships and supporting M&A projects. During his time at F-Secure he built the Security and Risk Management (GRC) consulting practice in the Nordics before moving to M&A projects and relocating to London. Prior to joining F-Secure, Jani held a number of CISO/CRO positions over 15 years at some of the largest Telcos and payment processors in the Nordics. Jani is also a known lecturer, speaker and panellist in the Nordics and an author of the best-selling ERM handbook for business leaders in Finland.