
QSC Europe 2024 – New London dates will be announced soon!
CISO Exchange – London
Wednesday 17 May 2023
The Sheraton, Park Lane, London
We are delighted to announce the next CISO Exchange at QSC London 2023! A select group of CISOs from across industry sectors will again share ideas, strategies and tactics used – what works, what doesn’t, the risks, mitigations, challenges and opportunities that lie within cybersecurity.
Powered by Pulse Conferences, the CISO Exchange, the open discussions are led by experienced CISOs of large organisations – a truly CISO-driven agenda led by CISOs!
Participants of the CISO Exchange are also welcome to join the wider Qualys Security Conference (QSC) sessions.
Registration is now closed
View Full Agenda-17 May 2023View Photo gallery from the 2022 event
Read the 2022 QSC London Report!View the official 2023 QSC London Photos & Video

Hosted by
Powered by
About CISO Exchange at QSC
CISO Exchange is a dedicated part of QSC, an exchange of expertise and ideas on how to better secure our digital assets and help our companies move into this new Digital Age.
About Qualys
- 20+ Security apps Evolutionary single agent architecture
- 10,000 Subscription customers worldwide
- 8+ trillion Data points indexed elastic in search clusters
- 2+ trillion Security events per year
- 6+ billion IP scans and audits per year
- 5+ billion Kafka messages per day
- 99.99966% Six Sigma scanning accuracy
Timings at a Glance – CISO Exchange
09:00-12:45
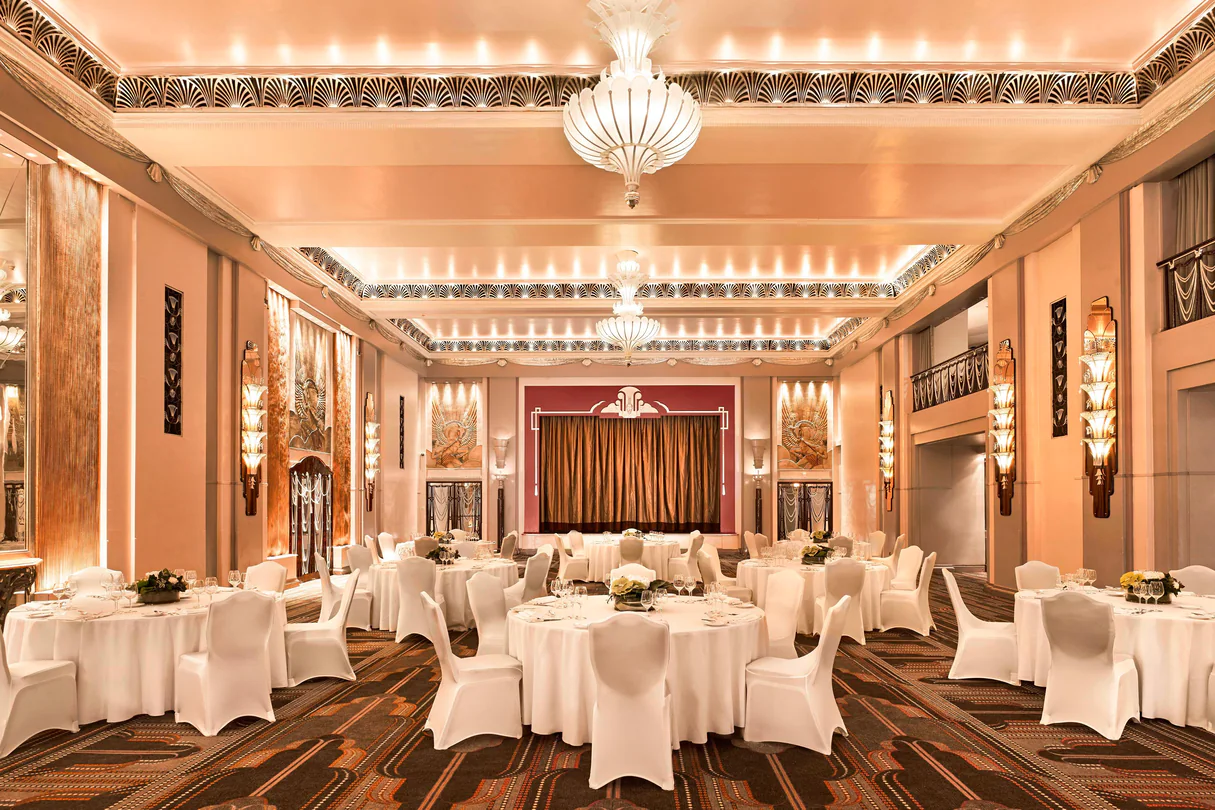
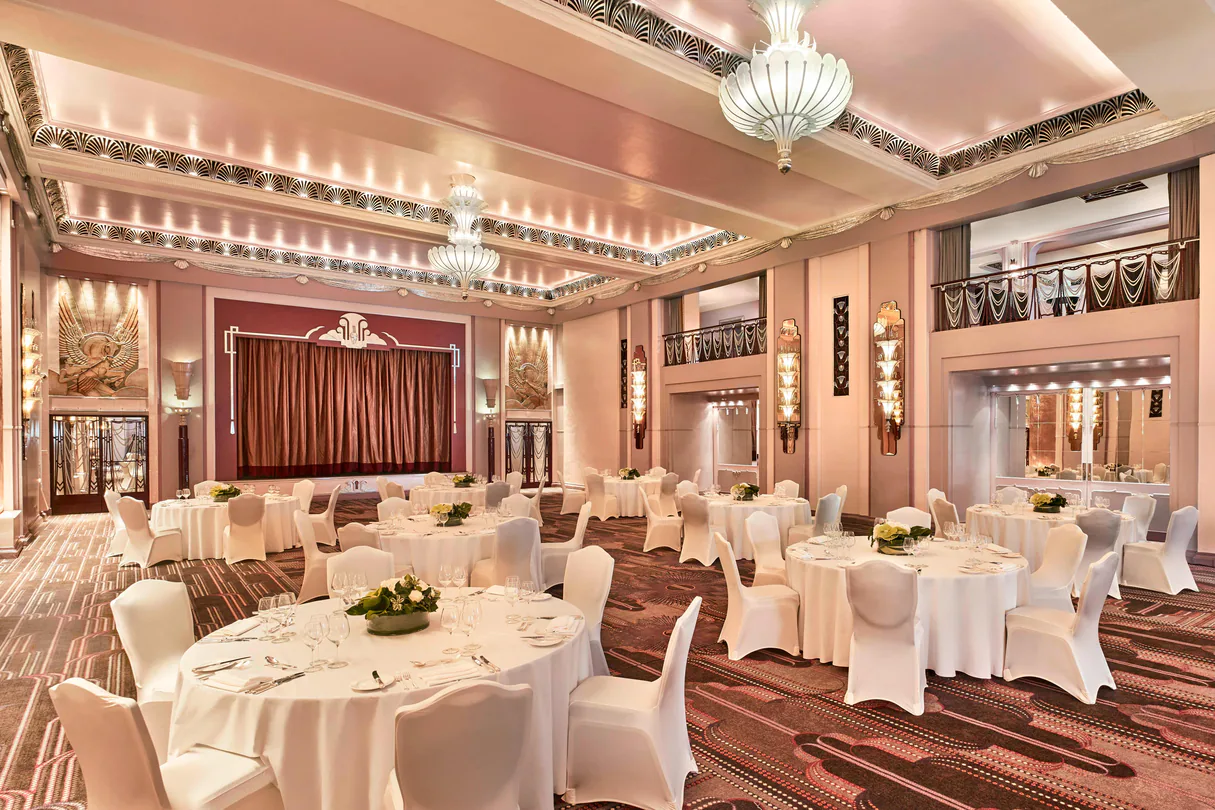
Qualys Security Conference (QSC) Ballroom, Sheraton Park Lane
Not to be Missed Keynotes and Commentaries, including:
09:15-09:45
Qualys Vision of a Simpler Security Landscape
Sumedh Thakar. CEO, Qualys
11:00-11:45
Global Security Landscape Updates
Frank Gardner OBE, BBC’s Security Correspondent & Author
12:45-14:00
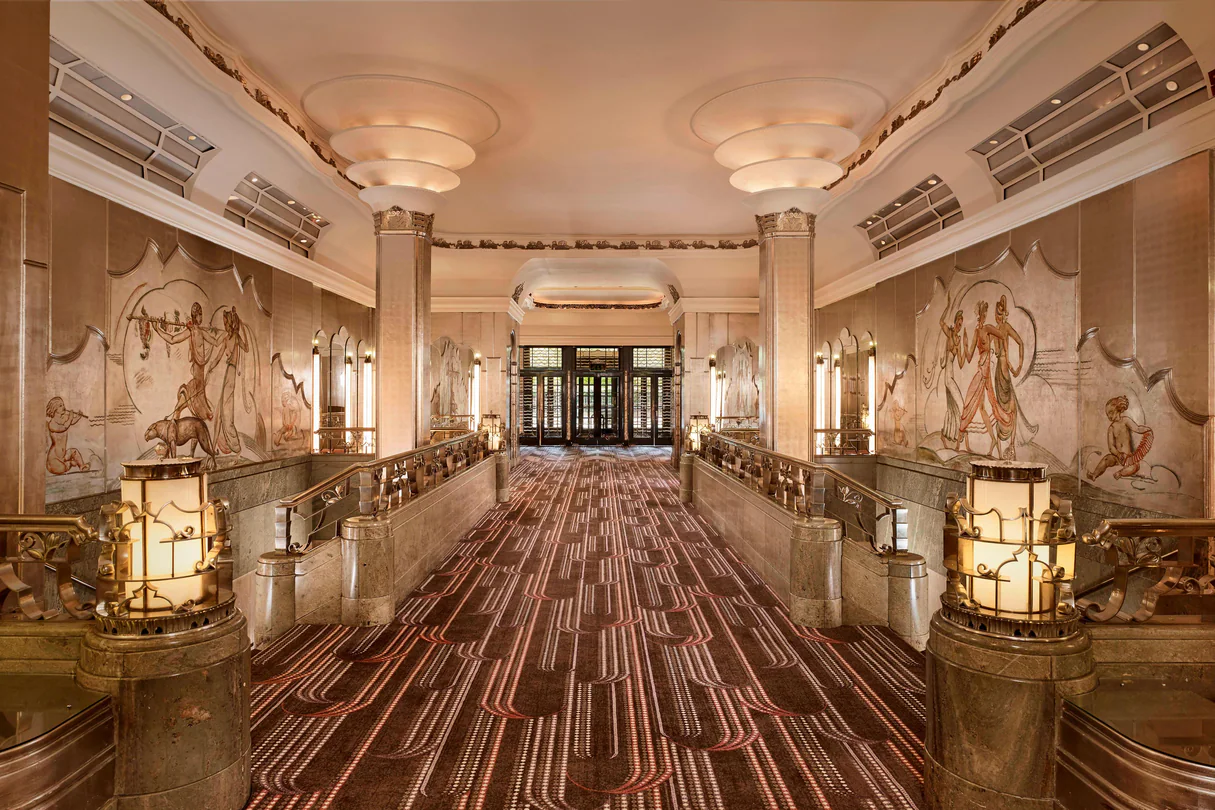
Lunch Ballroom Foyer, Sheraton Park Lane
Networking with CISO peers and 400+ strong QSC participants!
14:00-17:15
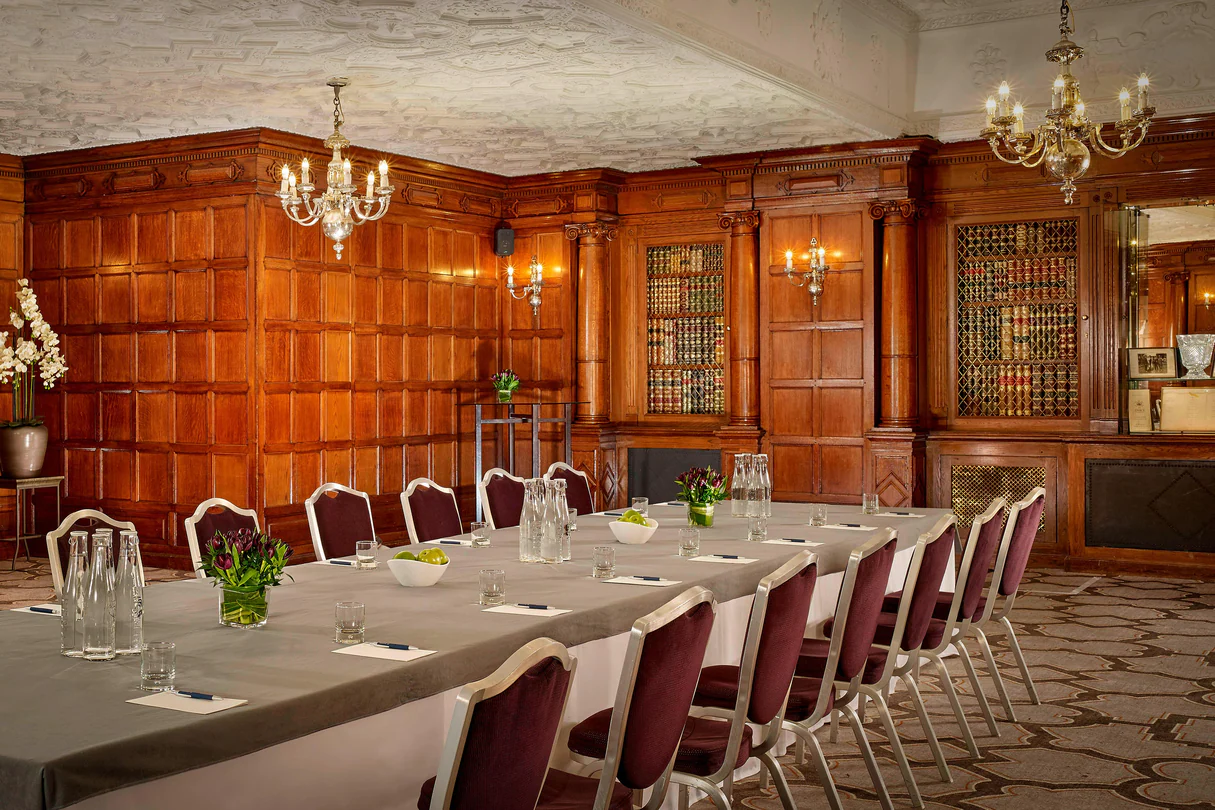
CISO Exchange Tudor Rose Room, Sheraton Park Lane
Open Discussions facilitated by fellow CISOs. Pure benchmarking on priority area topics input by CISOs!
17:15-19:00
Reception Ballroom & Foyer, Sheraton Park Lane
Enjoy drinks, canapes and networking – only steps away from the CISO Exchange.
Vulnerability in Numbers
185,446 – universe of all known vulnerabilities
55,186 (29%) – vulnerabilities with exploit available
0.4% – number of vulnerabilities that cause the most risk
37 – the average time to remediation for all compromised assets
Key Themes CISO Exchange 2023
- The Cyber Race to Keep Up with Digital Transformation
- Who Owns Risk and the Associated Remediation in your Organisation?
- Cyber Insurance: Strategies for Reducing the Impacts of Premiums
- Automation: What are the Limits Versus Goals? What are the Risks and Opportunities for CISOs?
Reflections on QSC London 2022
“It was fantastic to have so many people attend. The conference provided the opportunity to learn from one another, share problems, find solutions, and determine industry trends. For example, there was a lot more interest in automation from CISO than I expected. In cyber security, there is no destination – it’s a journey. We are moving in the right direction regarding how we can simplify security and reduce costs. Qualys is leading the way with innovation and solving problems. We’re hoping to continue and strengthen our association with our customers and be there alongside them on this journey.”
Sumedh Thakar, President and CEO, Qualys
“Events like this that allow those involved in cyber security work to discuss these new challenges are vital. How great to have these essential conversations face to face with an amazingly high-quality group of attendees. I have learnt a lot. I am very grateful to Qualys for the invitation to speak. Talking to attendees, I know that they appreciate the effort that has gone into organising this event. The timing has been perfect.”
John Noble CBE, Non-Executive Director, NHS Digital (and former Director at the National Cyber Security Centre)
“In-person events like this are important because we are fighting against groups working together, sharing all that information. We need to do the same. While events like this are not the silver bullet to sharing, they will help build trust. I’m happy to share my thoughts, learnings and challenges, and I’m also happy to receive knowledge from and engage other companies, so events like this are crucial to help start those conversations.”
Craig McEwan, CISO, Anglo American
“It’s been a very informative day. The highlights for me have been seeing a clear vision from Qualys, and a roadmap for its products. It’s great to see some features in the works that we’ve wanted to produce. And then also talking to the product managers and almost challenging them. So that face-to-face interaction is central to the day’s success.”
Ritesh Patel, Digital Security Principal, BP
“It was good to be on stage, and the feedback from the case-study sessions were brilliant. Lots of people have asked me lots of questions. I attended the conference and the superb training day. For somebody who considers themselves quite a competent Qualys user, I learnt an awful lot about some of the newer stuff that I had never really investigated. At the event, the contact building was terrific.”
Glenn Pegden, Security Vulnerability Manager at Sky Betting & Gaming
“It has been a fantastic event – one of the first conferences we can meet people. It is very good to network with people, and I was delighted to have been invited by Qualys to talk about our experiences at the University of Westminster. In particular, it was fascinating to hear the keynote from John Noble, the ex-NCSC Director. His strategy aligned with what we are doing, so that felt reassuring.”
Thierry Delaitre, Head of IT Developments, University of Westminster
Watch video highlights – CISO Exchange & QSC 2022
Speakers Not to be Missed at QSC and CISO Exchange!
*Further speakers will be announced soon.
QSC Keynote – 09:15-09:45
Qualys Vision of a Simpler Security Landscape
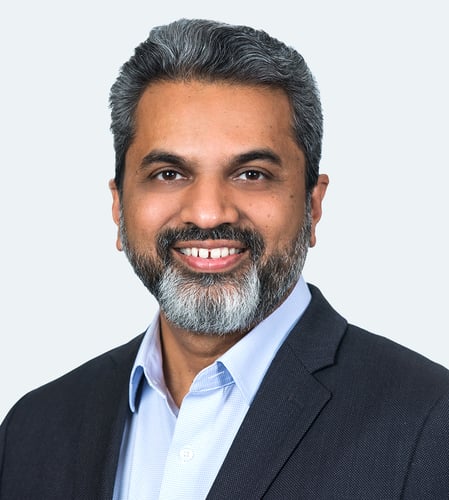
Sumedh Thakar
CEO, Qualys
As CEO, Sumedh leads the company’s vision and strategic direction. He joined Qualys in 2003 in engineering and grew within the company, taking various leadership roles focused on helping Qualys deliver on its platform vision. Since 2014, he has served as Chief Product Officer at Qualys, where he oversaw all things product, including engineering, development, product management, cloud operations, DevOps, and customer support. A product fanatic and engineer at heart, he is a driving force behind expanding the platform from Vulnerability Management into broader areas of security and compliance, helping customers consolidate their security stack. This includes the rollout of the game-changing VMDR (Vulnerability Management, Detection and Response) that continually detects and prevents risk to their systems, Multi-Vector EDR, which focuses on protecting endpoints as well as Container Security, Compliance and Web Application Security solutions. Sumedh was also instrumental in the build-up of multiple Qualys sites resulting in a global 24×7 follow-the-sun product team. Sumedh is a long-time proponent of SaaS and cloud computing. He previously worked at Intacct, a cloud-based financial and accounting software provider. He also worked at Northwest Airlines developing complex algorithms for its yield and revenue management reservation system. Sumedh has a bachelor’s degree in computer engineering with distinction from the University of Pune.
QSC Keynote – 11:00-11:45
Global Security Landscape Updates
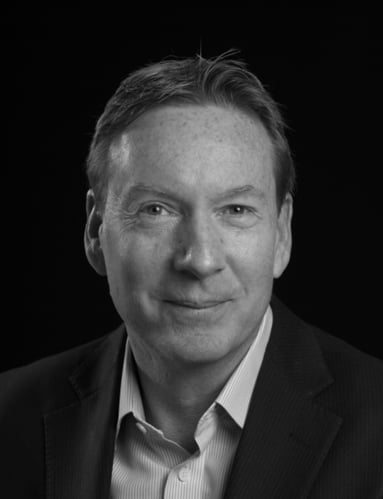
Frank Gardner OBE
BBC’s Security Correspondent & Author
Frank spent nine years as an investment banker in New York, London and Bahrain before switching to journalism and joining the BBC in 1995. Frank has reported extensively on the global ˜War on Terror’ in Guantanamo Bay, Yemen, Afghanistan, Iraq and elsewhere in the Middle East. In 2004 Frank survived being shot six times at close range by Al-Qaeda terrorists in a Riyadh suburb in Saudia Arabia. He went on to write the best-selling book Blood and Sand, the poignant story of what can happen to your belief system when the culture you have embraced ends up trying to kill you. Frank has gone onto write three best-selling spy thrillers Crisis, Ultimatum and Outbreak. He was awarded an OBE in 2005 for services to journalism. In 2018 he was awarded the University of Southern California’s Tommy Trojan Trophy for distinguished speaking. As a career broadcaster and a witty and gifted communicator, Frank shares his passion for the Middle East, travel and adventure. He draws on a unique perspective and understanding of both domestic and international security.
CISO Exchange – Chairperson
Marcus Alldrick, CISO Luminary
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in structured programming methodology. Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services.
CISO Exchange – Co-Speaker
Toks Oladuti, GD CISO, Dentons
Toks is responsible for the global delivery of information security at Dentons, the world’s largest law firm. He has over 20 years’ experience working in security, technology and privacy, across a number of industries. Toks is an experienced and strategic business risk leader. He has a particular passion for team development, business strategy, risk-based metrics and enterprise security culture. Toks has contributed to the business and technology community through information sharing, groups, speaking engagements and multi-industry networking. As strong supporter of education and schools, he has provided support in areas of security, data protection, user awareness and cloud transformation.
CISO Exchange – Co-Speaker
Robert Rodger, CISO, Admiral Insurance
Robert is a career security professional with over 29 years’ experience within banking information and cyber security. With a proven track record of building high performance teams, he delivers a quality and effective security practice and is passionate about building world class security functions, which are a business enablers; delivering security solutions that enable the organisation to explore opportunities which previously they would have been too cautious to exploit, while operationally managing the ever-increasing threat. Robert’s approach to security is that of common sense; efforts must be equally focused on doing the basics flawlessly and driving systemic improvements through the broad exploitation of intelligence, data, automation, and machine learning in a sound security architecture which is driven by business requirements.
CISO Exchange – Co-Speaker
Jonathan Trull, CISO & SVP Security Solution Architecture, Qualys
Jonathan is the Chief Information Security Officer and Senior Vice President for Security Solution Architecture at Qualys. He has more than 20 years of experience in the cybersecurity industry, and his career spans operational CISO and infosec roles with the State of Colorado, Qualys, Optiv, and Microsoft. At Microsoft, Jonathan led the Detection and Response Team (DART), whose members responded to cyber security incidents around the globe ranging from cyber espionage initiated by nation-state actors to ransomware attacks.
Jonathan also serves as an advisor to several security startups and venture capital firms and supports the broader security community through his work with IANS. He is also an adjunct faculty member at Carnegie Mellon University, where he mentors and coaches those attending the CISO Executive Education Program. Jonathan is a frequent speaker at industry conferences such as Black Hat, RSA, and SANS and holds several industry certifications including the CISSP, OSCP, CCSP, and GCFA.
CISO Exchange – Co-Speaker
Giuseppe Brizio, CISO EMEA, Qualys
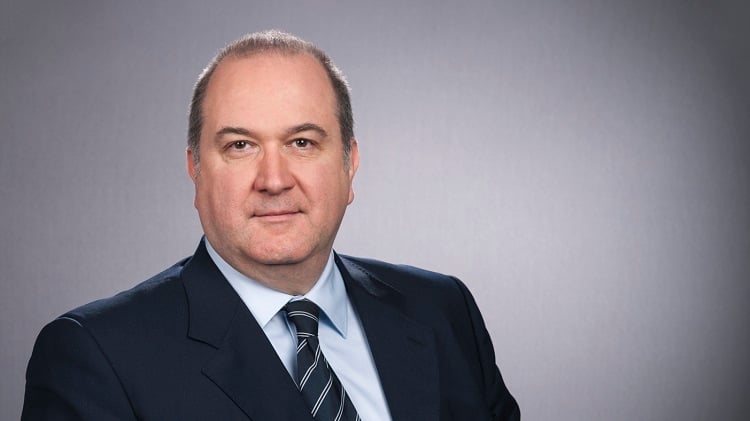
Giuseppe is based out of Greater Paris Metropolitan Region and works at Qualys as Chief Information Security Officer EMEA. He was Chief Information Officer at Nestlé Waters Zone Asia, Middle East, Oceania and Africa. Nestlé Waters. 2012 – 2014. Dubai. CIO in charge of developing Nestlé Waters Zone AOA (20+ Markets) Business Excellence, Information Systems Organization, Digital (eCommerce) and Business Solutions (e.g. MS Dynamics/SAP) Roadmaps across all Business.
CISO Exchange – Co-Speaker
Paul Baird, Chief Technical Security Officer (CTSO) UK, Qualys
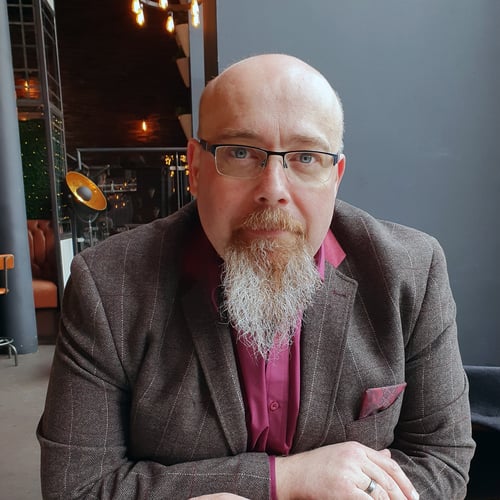
Paul Baird is an IT veteran with over 25 years’ experience, and has spent the last seven years focusing his efforts in cybersecurity. Paul’s background has included building a security ethos and security operations centre (SOC) from scratch for several leading enterprises in the UK housing and automotive industries. Having moved to the vendor side to join Qualys as their Chief Technical Security Officer (CTSO) in 2021, he now drives Qualys’ vision for cybersecurity at C-Level across customers and partners in the UK and North EMEA. He is a people-focused leader and passionate about supporting his team. Paul was awarded a fellowship by the Chartered Institute of Information Security (CIISEC) last year for his continued contribution to cybersecurity.
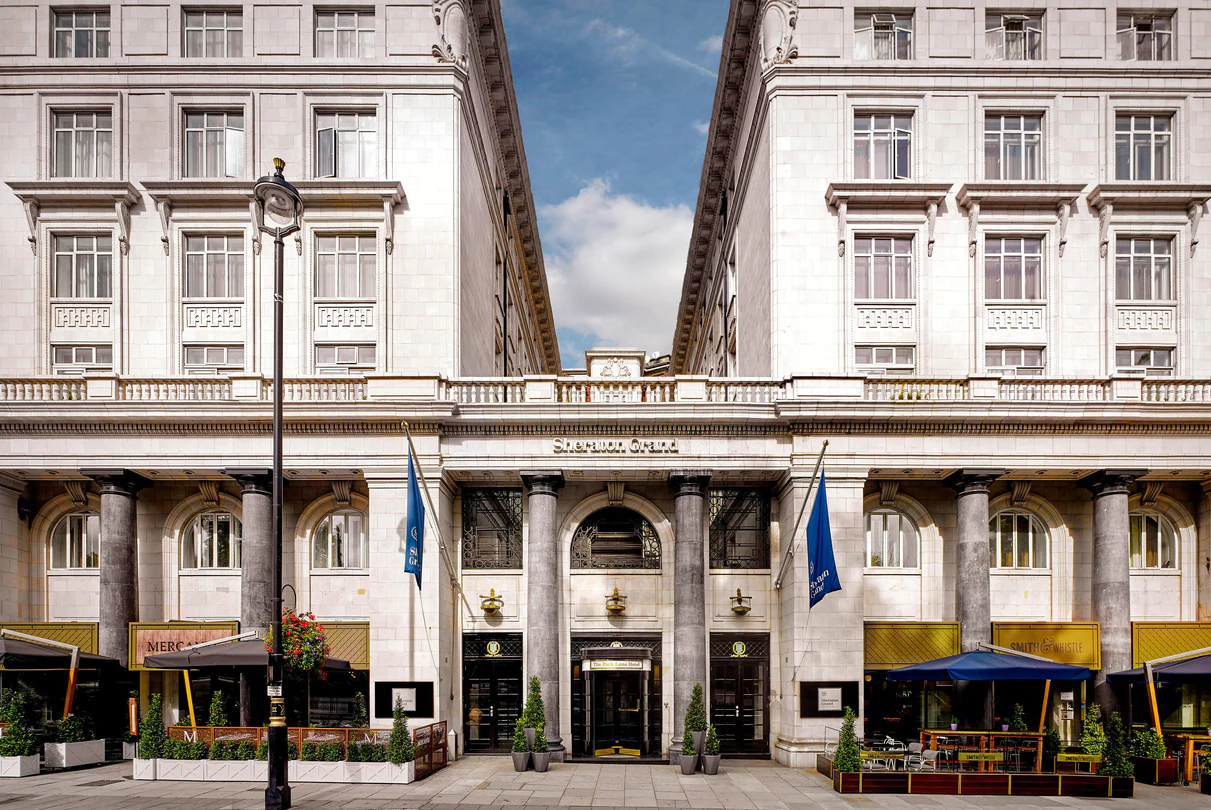
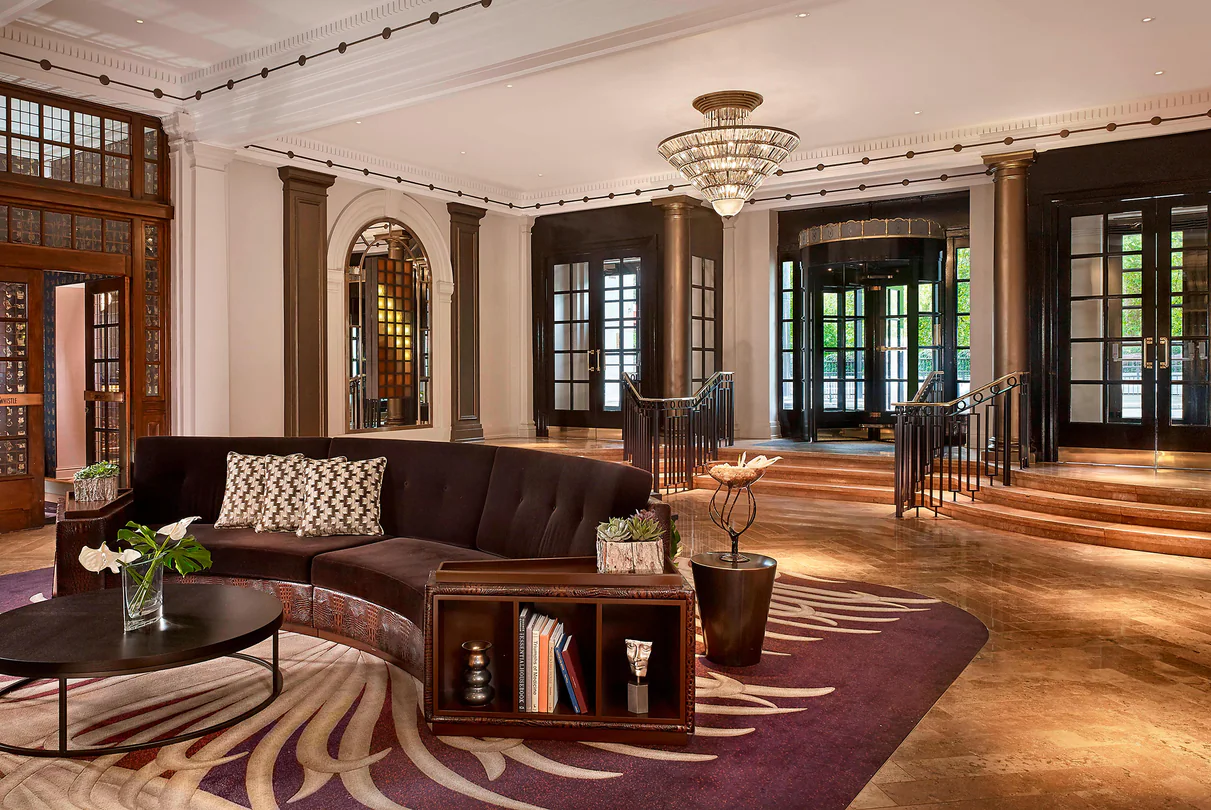
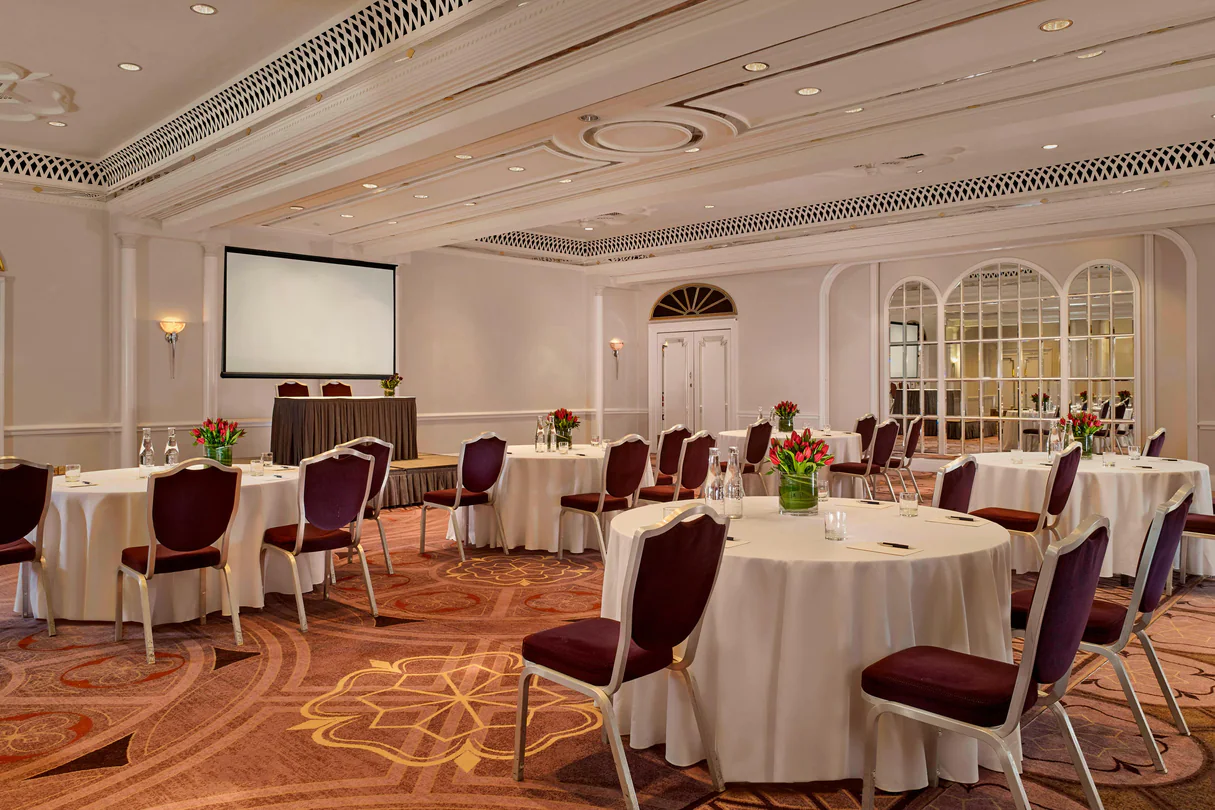
View image gallery from CISO Exchange & QSC 2022
