/uploads/2018/09/ISACA-Rome-logo-from-web.png)
Archive · Middle East
CISO 360 Middle East Congress
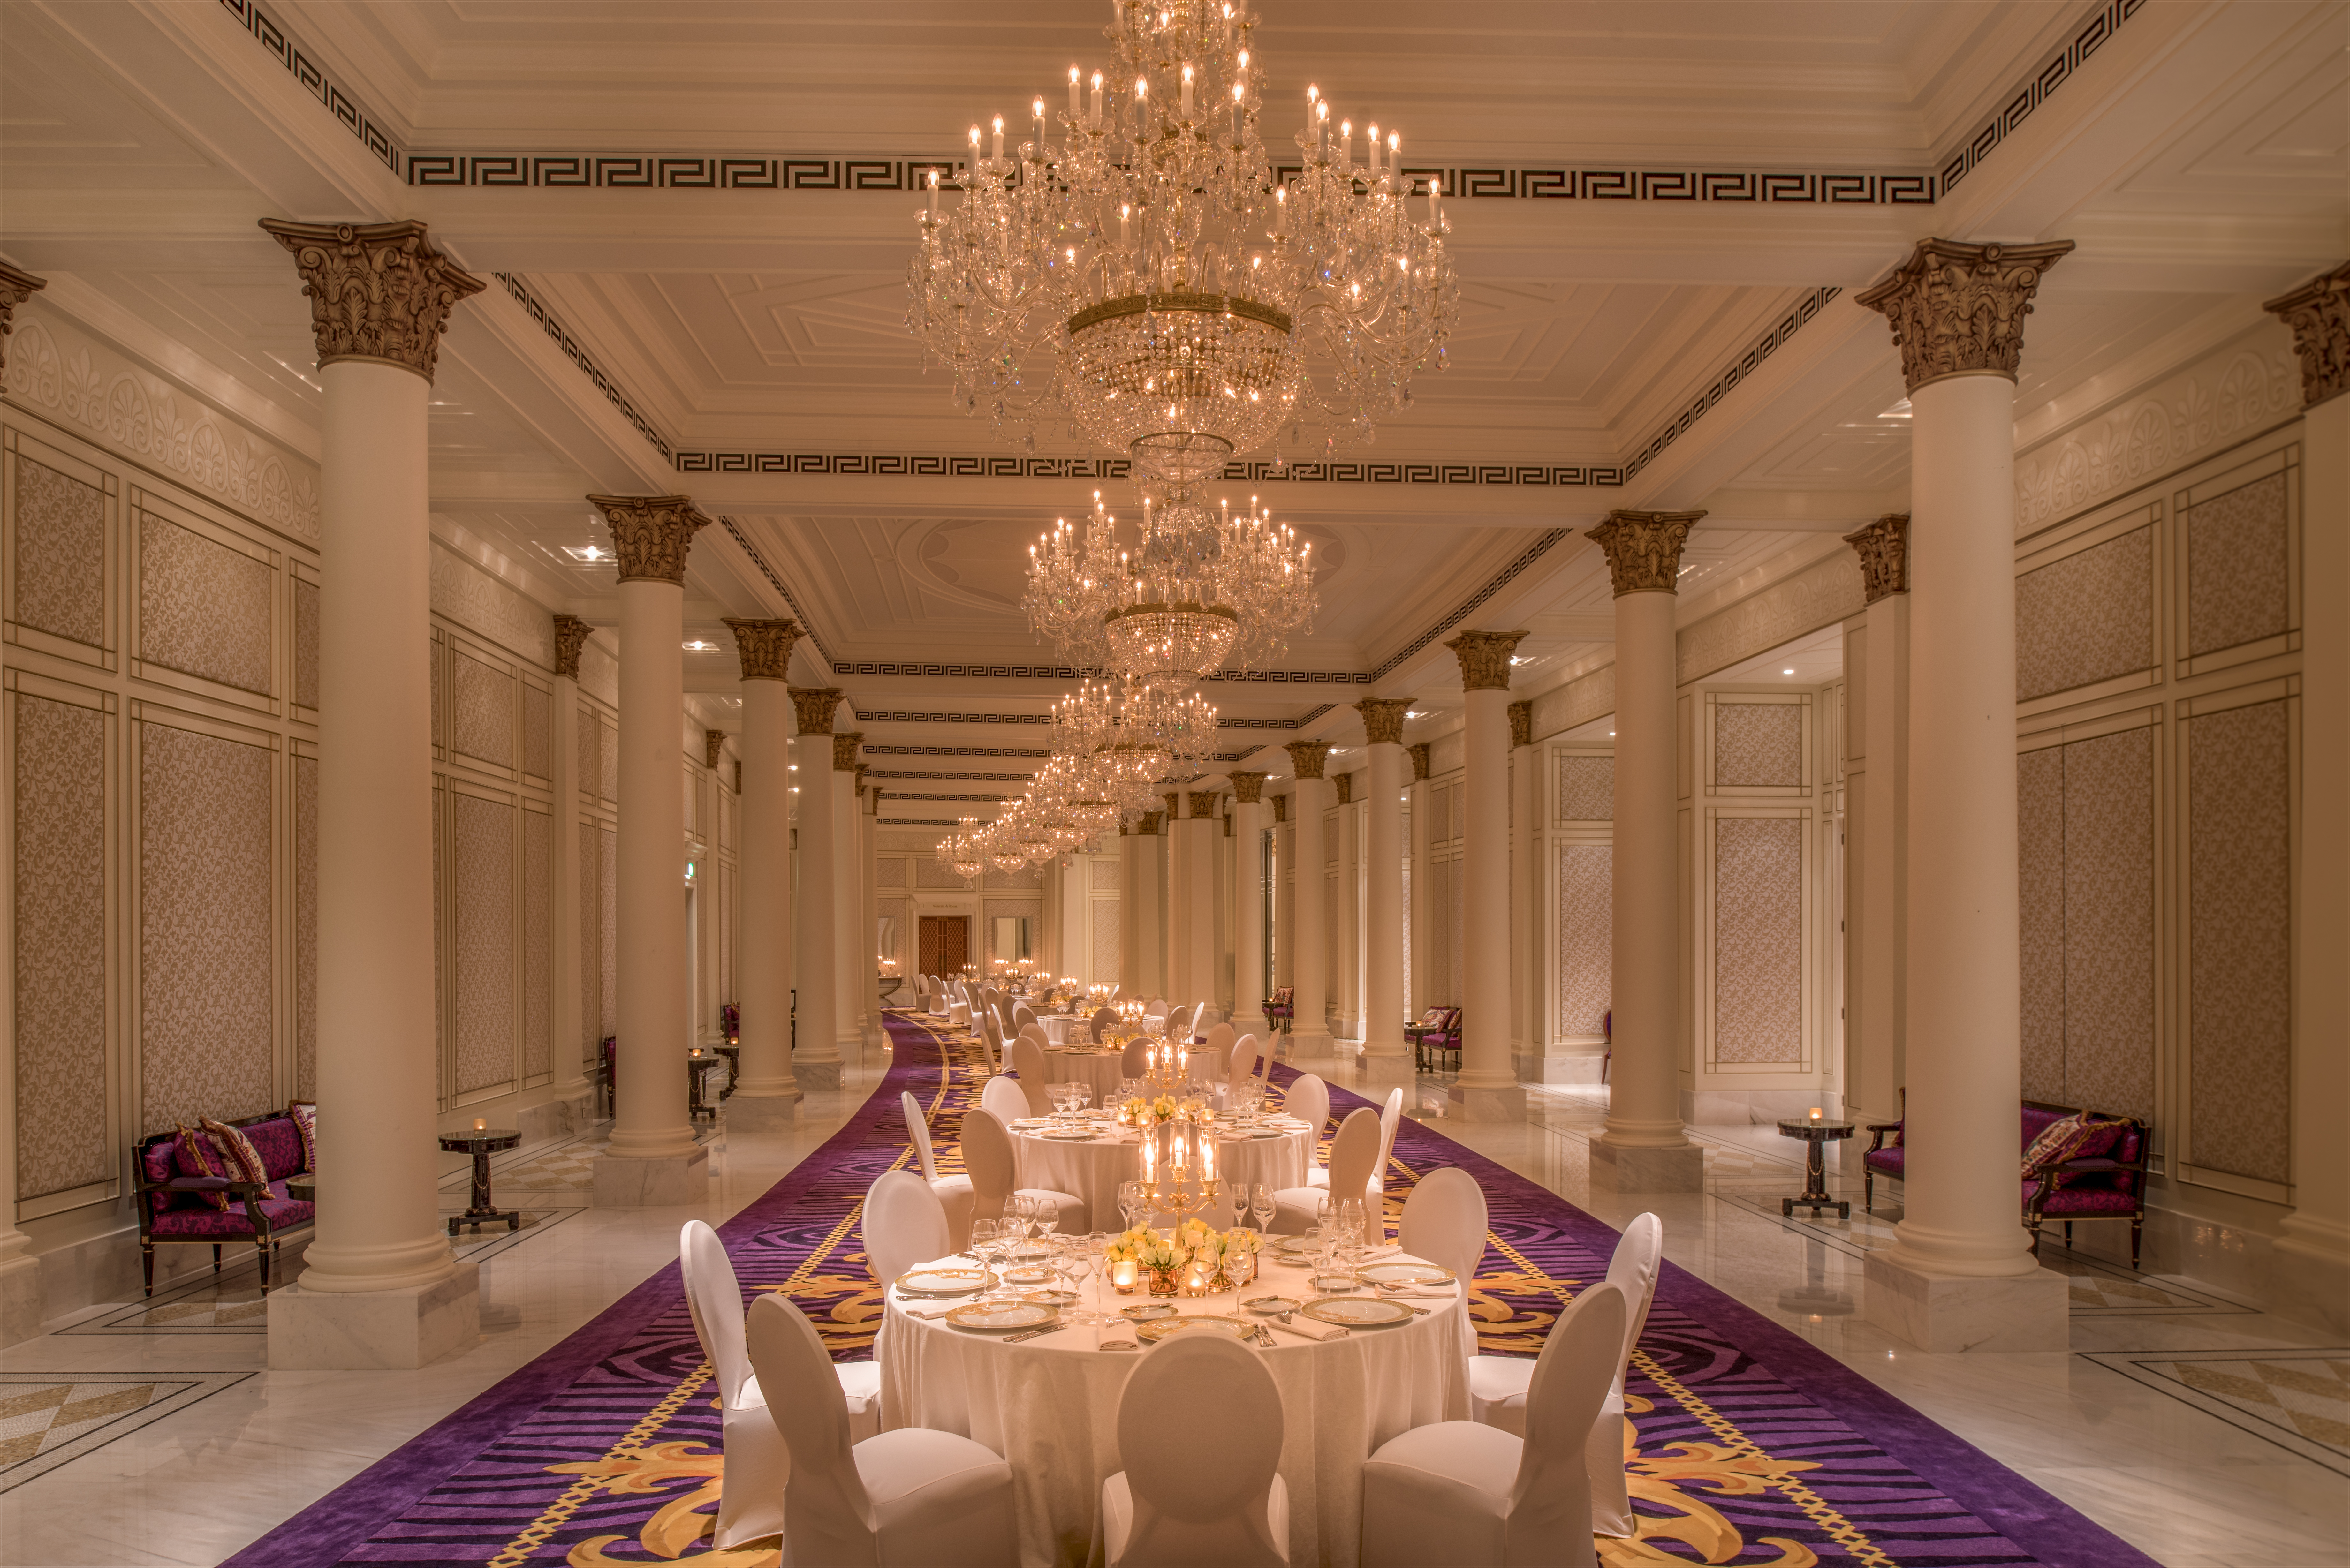
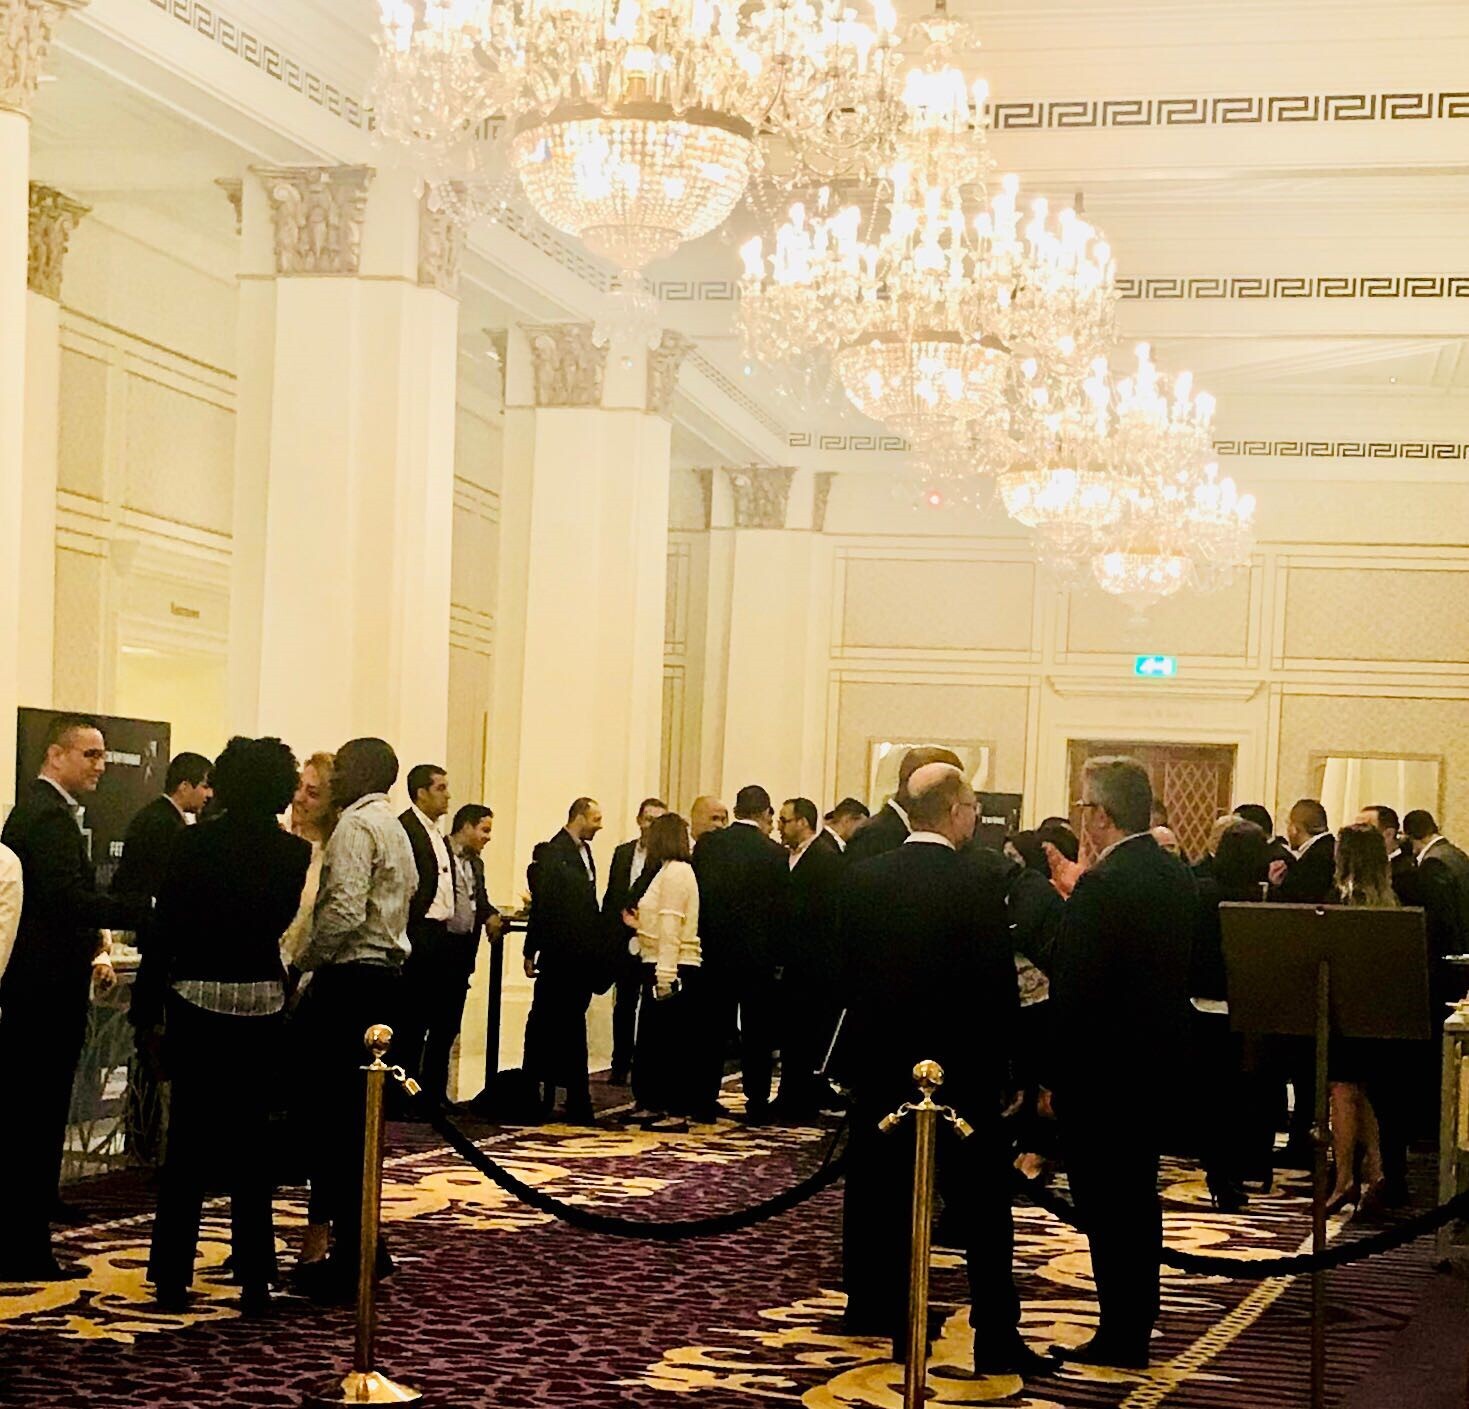
This event took place on 2018 at Palazzo Versace Dubai.
2018 CISO 360 Middle East Congress
Archived event content. Dates, prices and registration links below relate to 2018.
Become a sponsor for the 2nd CISO 360 Middle East Congress 2019Christopher Rollan, Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
Working locally, thinking globally…
The Pulse team has over 10 years’ experience working with senior cybersecurity and governance executives in the Middle East and is well-positioned to deal with enterprise-wide risks across a wide range of markets including: e-commerce, AI, automotive, health, financial services, infrastructure, IoT, mobile, smart city, energy, defense, manufacturing, critical national infrastructure, retail and transport.
CISOs, CIOs and cyber threat intelligence directors will share approaches to emerging cybersecurity challenges pertinent specifically to the Middle East region taking the approach of working locally thinking globally. CISO 360 Middle East follows on from the success of our inaugural CISO 360 Congress in Barcelona.
You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!
Irene Corpuz, Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Future-oriented security and intelligence and creative thinking on technological opportunities in cybersecurity
- Artefacts of Innovation Roundtable – Advanced Technologies, AI, Robotics – CISO and CIO as enablers of business innovation
- Investment Perspective on Harnessing IP in Cybersecurity – Brand protection and investment in cybersecurity
- Cyber Resilience Strategies for the Middle East – live exercises and workshops on crisis planning, open source intelligence tools, IoT in energy and renewables and finsectec
- Securing online commerce – corporate case studies on the risks and opportunities in Cloud, DevOps and Threat Intelligence
- CxO Cyber Risk Governance and Assurance Boardroom – discussion on Governance, Business Engagement and Trust
Agenda at a Glance
Sunday 22 April – Optional Pre-Congress Training & Exercising
Course 1: New Principles for Governance & Strategy in a Crisis
Course 2: Cyber Security for Ports & Vessels
Monday 23 April
Congress Day 1: CISO 360 Middle East Congress
Tuesday 24 April
Congress Day 2: CISO 360 Middle East Congress
Wednesday 25 & Thursday 26 April- Optional Post-Congress Training & Exercising
Course 3: Cyber Security and Infrastructure Standards
Course 4: Cyber Security Assurance, Intelligence and Insider Risk
Course 5: Cyber Attacks – The Risk and the Fix
International speaker panel including…
- Aladdin Dandis, Information Security Manager, Souq.com
- Anshul Srivastav, Chief Information Officer -Information Technology, Union Insurance Company P. S. C.
- Bob Shaw, Senior Security Advisor, United Nations
- Mrs. Bhavani Suresh, President, ISACA UAE Chapter
- Dimitrios Stergiou, Chief Information Security Officer, Modern Times Group MTG AB
- Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7
- Dr. Mohammad Khaled, CIO, IT Digital Transformations, Regulation & Supervision Bureau – RSB
- Dr. Major. Hamad Khalifa Al Huaimi, Head of Telecommunications Security, Abu Dhabi Police GHQ
- Eng. Manan Qureshi, Vice President / Head of Business Continuity, Riyad Bank
- Eng. Joseph Makram, CIO, Egyptian Arab Land Bank
- Irene Corpuz, Section Head – Planning & IT Security & Acting CISO, Western Region Municipality – Abu Dhabi Government
- Jenny Reid, CEO, iFacts
- Jonathan Martin, EMEIA Operations Director, Anomali
- Kumar Prasoon, Group Chief Information Officer (CIO), Al Safeer Group
- Lady Olga Maitland, CEO, Copenhagen Compliance and Defense and Security Forum
- Lee Barney, Head of Information Security, Marks and Spencer
- Michael Waheeb, Head of Information Security, Network International Africa
- Marcus Alldrick, Former CISO, Lloyd’s of London & Current Advisor, Santander
- Dr. Vasileios Karagiannopoulos, Institute of Criminal Justice Studies, University of Portsmouth
- Ray Stanton, SVP/Group Chief Security Officer, TDC Group
- Richard Hollis, CEO, Risk Crew
- Simon Scales, Former Head of Investigations EMEA, BP plc
- Intelligence Specialist, North Cyber Ltd
- Sofiane Chafai, EMEA Advisory Board Member, (ISC)²
- Mr. Satyan Abraham, Director ICT Infrastructure DXB Entertainments
- Mr. Edward Ayman Ganom, CISO The Commercial Bank of Qatar
- Dr. Major Hamad Khalifa Al Nuaimi, Infrastructure Dept. ICT Center Abu Dhabi Police GHQ
- Mr. Tim Sandwell, Director Middle East, Barclay Simpson
For CISOs, CIOs, Cybersecurity and Threat Intelligence Directors… innovators and investors
Advanced technologies innovation workshops
Designed for CISOs and CIOs to reposition as the enablers of business innovation and to ask the right questions of their technical teams: AI; Open source hacking; Business espionage; Cybersecurity policy standards
International multi-faceted speaker panel
Local and global insights and exchange between CEOs, CIOs, CISOs, corporate governance, innovators and investors from around the world
Cyber resilience and Boardroom engagement
Discussion between CISOs and non security board and c-level will break down traditional siloes between business-security-technology-legal! Technology governance, business engagement and trust.
Future facing with an R&D and investment on innovation focus
Natural integration between in-house security, technology innovators and investors. None of the typical industry barrier between buy and sell
Immersive agenda with real-time benchmarking and exciting debates
Dynamic debates, corporate Q&A, on-stage fireside chats, ‘live’ polls
Intimate and inspiring networking – community based trusted ‘closed door’ environment
The entire event is held under the Chatham House Rule. Networking dinners included! Enduring connections guaranteed.
Gold Sponsors
Supporting Organisation
Cyber Security for Ports and Vessels
22 April 2018
Dubai, United Arab Emirates
Download course outlineRegister here
With the increasing use of information and communications technology (ICT) in the port and maritime sectors, and the connection of operational technologies (OT) such as control systems, there is a need to address the cyber security issues. The IMO’s ISPS Code requires port and vessel operators to put in place appropriate controls and supporting business practices to address security risks, including those that are cyber related. This course is based on the UK Department for Transport (DfT) sponsored Codes of Practice for Cyber Security of Ports and Port Systems, and Vessels, that were prepared by the Institution of Engineering and Technology (IET).
The objectives of the course are to enable delegates to:
- understand and appraise the cyber security threats to their port or maritime operations;
- undertake a risks assessment of their cyber-physical systems and operations;
- develop an appropriate and proportionate security strategy, management plan.
About the instructor:
/uploads/2018/01/hugh-Boyes.jpg?width=345&height=500&name=hugh-Boyes.jpg)
Hugh Boyes BSc(Hons) MBA CEng FIET CISSP
Hugh is a Chartered Engineer, a Fellow of the Institution of Engineering and Technology (IET) and holds the Certified Information Systems Security Professional (CISSP) credential issued by the International Information Systems Security Certification Consortium [(ISC)2]. He divides his time between working as a Principal Engineer at the University of Warwick and undertaking cyber security training and consultancy assignments. Hugh is an industry expert on cyber threats to cyber-physical systems, including those in the built environment, ports and maritime sectors. He has written four guidance documents for the IET covering cyber security in the built environment, ports and vessels. His research work focuses on the protection of control systems, whether traditional industrial controls or employing IoT technologies. He is the co-author of British Standard’s PAS 1192-5:2015 [Specification for security-minded building information modelling, digital built environments and smart asset management] and PAS 185 [Smart Cities – Specification for establishing and implementing a security-minded approach]. He regularly reviews standards to assess their handling of security issues and sits on the drafting committee for the forthcoming British Standards BS10754 suite of documents. Hugh is a Member of the Register of Security Engineers and Specialists (RSES).
Cyber Security for Ports and Vessels
Date: 22 April 2018
Location: Dubai, United Arab Emirates
Course length: One day
Price: £800
Register for this course:
To register or find out more about this course please email: sanna.lindstrom@pulseconferences.com
Course Modules
Module 1: The cyber security threat
Using case studies to illustrate the issues, this module will provide a holistic view of the background to and nature of cyber-related threats, vulnerabilities and risks that can affect the port and maritime sectors.
Module 2: Cyber security for ports
This module will examine use and implementation of the DfT/IET Code of Practice for Cyber Security of Ports and Port Systems. It will highlight the steps that port and port facility operators should take to achieve compliance with the ISPS Code
Module 3: Cyber security for vessels
This module will examine use and implementation of the DfT/IET Code of Practice for Cyber Security of Vessels. It will highlight the steps that vessel owners and operators should take to achieve compliance with the ISPS Code.
Module 4: Developing and maintaining cyber security assessment and plan
This module will take delegates through the process required to create the cyber security assessment for the port, port facility or vessel, and the associated cyber security plan. It will examine a typical range of policies, processes and procedures required to support the plan, and outline the recommended approach to implementing and maintaining this suite of documents.
- Individuals complete personal review of skills development
- Course summary and take-aways
Training courses CISO 360 Middle East Congress 2018
*Training details and timings are subject to change.
22 April 2018
Dubai
New Principles for Governance and Strategy in a Crisis
A one-day training course for CISOs, CSOs, COOs, senior managers, as well as regulators, CEOs and board members. New governance principles help senior managers understand strategy and make decisions in a crisis. Delegates will learn the operational decision-making skills for 5 governance principles that underpin security management. The new governance tactics and strategies covered in this course are to support a general crisis governance framework for government and business.
22 April 2018
Dubai
Cyber Security for Ports and Vessels
This course is based on the UK Department for Transport (DfT) sponsored Codes of Practice for Cyber Security of Ports and Port Systems, and Vessels, that were prepared by the Institution of Engineering and Technology (IET). The IMO’s ISPS Code requires port and vessel operators to put in place appropriate controls and supporting business practices to address security risks, including those that are cyber related.
25-26 April 2018
Dubai
Cyber Policy and Standards for Systems Security
This 2-day course focuses on the rapidly changing business and technical environment and how the choice of standards and codes of practice can make a significant difference to the success of your organisation. There are a range of existing cyber security related standards, publicly accessible specifications (PAS) and codes of practice. The choice of whether to implement specific standards can have a significant impact on your organisation’s costs and performance.
25-26 April 2018
Dubai
Catastrophic Risk Theory and Practice for Energy, Leisure and Transportation
The two-day catastrophic risk course covers methodology to quantify risks that threaten critical operations, specially pertaining to energy, leisure and transportation infrastructures. The course takes participants beyond general risk frameworks to understand the value of adding procedures to sustain business operations when catastrophic events threaten the survival of the organisation, services or people.
25-26 April 2018
Dubai
Cyber Attacks – The Risk and the Fix
Over two days, delegates are shown the reality of just how easy real cyberattacks can be – even those with the most devastating effects – and the implementation of simple measures to avoid catastrophic risk. The course is suitable for entirely non-technical officers as well as cyber managers and administrators who wish to develop a sound understanding of just how easy and low-tech the efforts of an attacker can be, and how to implement mitigation or who wish to upgrade their existing skills to become more cost effective for their organisation
Cyber Policy and Standards for Systems Security
25-26 April 2018
Dubai, United Arab Emirates
Download course outlineRegister here
This 2-day course focuses on the rapidly changing business and technical environment and how the choice of standards and codes of practice can make a significant difference to the success of your organisation. There are a range of existing cyber security related standards, publicly accessible specifications (PAS) and codes of practice. The choice of whether to implement specific standards can have a significant impact on your organisation’s costs and performance.
The objectives of the course are to enable delegates to:
- examine the nature and role of standards, publicly accessible specifications and codes of practice;
- review of the security standards landscape;
- understand factors to be taken into account when specifying or implementing standards, both within the organisation and its supply chain.
About the instructor:
/uploads/2018/01/hugh-Boyes.jpg?width=345&height=500&name=hugh-Boyes.jpg)
Hugh Boyes BSc(Hons) MBA CEng FIET CISSP
Hugh is a Chartered Engineer, a Fellow of the Institution of Engineering and Technology (IET) and holds the Certified Information Systems Security Professional (CISSP) credential issued by the International Information Systems Security Certification Consortium [(ISC)2]. He divides his time between working as a Principal Engineer at the University of Warwick and undertaking cyber security training and consultancy assignments. Hugh is an industry expert on cyber threats to cyber-physical systems, including those in the built environment, ports and maritime sectors. He has written four guidance documents for the IET covering cyber security in the built environment, ports and vessels. His research work focuses on the protection of control systems, whether traditional industrial controls or employing IoT technologies. He is the co-author of British Standard’s PAS 1192-5:2015 [Specification for security-minded building information modelling, digital built environments and smart asset management] and PAS 185 [Smart Cities – Specification for establishing and implementing a security-minded approach]. He regularly reviews standards to assess their handling of security issues and sits on the drafting committee for the forthcoming British Standards BS10754 suite of documents. Hugh is a Member of the Register of Security Engineers and Specialists (RSES).
Cyber Policy and Standards for Systems Security
Date: 25-26 April 2018
Location: Dubai, United Arab Emirates
Course length: Two days
Price: £1,500
Register for this course:
To register or find out more about this course please email: sanna.lindstrom@pulseconferences.com
Course Modules
Module 1: The nature and roles of standards
The module will examine the nature and standing of organisations that produce standards, the types of standards produced and the lifecycle of a typical standard from concept through to its replacement or revision.
Module 2: Understanding testing, validation and verification
This module will examine the use of certification to confirm conformance of organisations, processes, products and services to particular standards. It will examine the assessment processes and the potential pitfalls
Module 3: The security standards landscape
There are a range of security standards available covering organisation, personnel, physical and cyber-security. This module will examine a number of cyber security standards, ranging from those produced by international standards organisations to those developed by industry bodies and professional organisations.
Module 4: Choosing and using standards
This module will use case studies to illustrate the selection and use of standards to address security both within your organisation and in your organisation’s supply chain.
- Individuals complete personal review of skills development
- Course summary and take-aways
Cyber Attacks – The Risk and the Fix
25-26 April 2018
Dubai, United Arab Emirates
Download course outlineRegister here
North Cyber advises that this course is suitable for any officials in government, business, critical infrastructure, banking, transportation, energy, shipping and ports, retail, leisure, police, intelligence and security operations whether government or private sector. The case studies and work will be drawn from Europe, Africa, Middle East and South Asia depending on the persons attending and the region where the course is delivered.
Over two days, delegates are shown the reality of just how easy real cyberattacks can be – even those with the most devastating effects – and the implementation of simple measures to avoid catastrophic risk. The course is suitable for entirely non-technical officers as well as cyber managers and administrators who wish to develop a sound understanding of just how easy and low-tech the efforts of an attacker can be, and how to implement mitigation or who wish to upgrade their existing skills to become more cost effective for their organisation. The practical elements are comprehensively taught in a walk-through manner to demonstrate the vulnerabilities in realistic targets. A key theme running through the course is that of workforce vulnerability – no matter how well defended the organisation’s intellectual property is, the staff are the way in.
Day One – The Risk
Focuses on the mindset and techniques of the attacker, whether a cybercriminal, a state actor, a corporate spy or frivolous hacker. Students are equipped with tools and techniques to perform investigations of targets in the preparation for a notional attack, essentially becoming the hacker to demonstrate just how easy those attacks often are due to the visibility of staff and corporate data online.
Introduction to Cyber Risk
- “It’s not about the tech” – why the attackers’ techniques are surprisingly low-tech, and why the information security risk lies with the human workforce, not their computers.
- Real world examples of catastrophic attacks and the vulnerabilities in every organisation.
- One size fits all – the common vulnerabilities used by any attacker against any target: corporate, government and personal.
Attacker Methodology
Part One – reconnaissance
Scoping a target. A practical module demonstrating to delegates how an attacker uses OSINT (open source intelligence) to obtain corporate data and personal details using nothing more than search engines and free, legal tools.
Part Two – Attack
- Compare and contrast of ‘technical’ attacks with low tech and no-tech hacking by social engineering.
- Teach a man to phish. Understanding the myriad ways an attacker uses the freely obtained data to quickly penetrate an organisation through simple influence.
The Persistent Threat of Leaked Data
The permanent threat to corporations that arises from leaks of staff data from breaches such as Yahoo – even when non-corporate in nature, and even when many years old. Delegates are show the surprising amount of leaked data online and what to do about it.
Wi-Fi – the Corporate and Personal Risk
The largely unknown risks of wi-fi, not only as a vehicle for corporate intrusion by attackers but also for tracking the physical movement of individuals and identifying their homes. A practical module in which students are walked through the steps of an attacker breaking into corporate wi-fi and tracking of staff members using freely available tools.
Cyber Attacks – The Risk and the Fix
Name: Cyber Attacks – The Risk and the Fix
Date: 25-26 April 2018
Location: Dubai, United Arab Emirates
Course length: Two days
Price: £1,500
Register for this course:
To register or find out more about this course please email: sanna.lindstrom@pulseconferences.com
Day Two – The Fix
Focuses on mitigating the identified risks. Real world examples of damaging attacks are dissected, with particular emphasis on correct implementation of cyber incident response. Delegates are presented with the most effective measures to mitigate an attack to bring a business back online at minimum expense.
Exercise: Attack the Corporation
WHAT HAPPENS NOW? – The reality of an attack, and the art of incident response.
The Devastation
Lessons learned from a vast number of cyber incident responses, where basic lack of security procedures and response plans allow simple attacks to have catastrophic effect.
Mitigation
From lessons learned in the ‘attack methodology’ modules and further illustrated in ‘What happens now?’ we explore the steps to secure the company. Again, the technical aspect is secondary to the information and ‘human’ security.
- The technical penetration test – learning why most companies waste time and money with incomplete or ineffective testing.
- Cyberattack response plan – The blueprints of the towering inferno. Why you must engage with your incident responders BEFORE an attack, and why incident response should cost thousands not millions.
- Staff data – reducing the target surface by educating the workforce in simple, effective ways that require no technical knowledge.
- Threat intelligence – the utility and strengths of currently available threat intelligence systems.
- ‘Convenience is an attack vector. ‘ Overcoming perceptions of inconvenience by removing certain technical privileges to maximise information security and aiming to become hack-proof.
About the instructors:
North Cyber Limited
North Cyber are team of former intelligence officers with expertise in covert online operations and digital forensics. The company teaches government and corporate clients how find and fix the unseen holes in their security. They specialise in all levels of capability including low-tech and no-tech hacking, using freely available information to circumvent vastly expensive but ineffective security systems. The teaching draws on many and varied real-world examples from the private and government sectors, from the perspectives of the attacker and incident responder. Participants in these courses will evaluate their own experience on the course in gaining additional skills and understanding of the threats to their organisation and they will gain confidence in tackling these catastrophic risks to the comparate or government operation.
New Principles for Governance and Strategy in a Crisis
22 April 2018
Dubai, United Arab Emirates
Download course outlineRegister here
A one-day training course for Regulators, CEOs and Board members, CISOs, CSOs, COOs, senior managers in finance, planning, government policy planners and senior officers in intelligence, emergency services, defence and cyber security, innovators in disruptive technologies, AI, IOT, banking, internal auditors, insurance and financial services, post-graduate students in Masters and higher degree courses, cyber security technology vendors and designers. The course is strongly based on peer-to-peer learning and practical tests to build capability and confidence in their leadership skills and strategic decision making that will benefit the employer and the stakeholders in their organisation. All attendees will have access to the on-line training manual through the Pulse website and will find this manual useful for ongoing reference in the workplace.
New governance principles help senior managers understand strategy and make decisions in a crisis. The five new Governance steps taught in this course build a general crisis governance framework for government and business. Also learned will be the operational decision-making skills for each Governance Principle. Alongside the theory, the know-how is taught through scenario exercises so each participant will become confident over the two days in how to apply the new governance principles for the benefit of their workplace. It is well recognised that when insider threat actors, criminals, terrorists, nation states or natural disasters impact on a country it is the experience and know-how of team leaders that prevent losses and strengthen government and business response. Strategic decision making is rarely offered in training but participants will personally develop new skills when studying each of the five new governance principles and benefiting from peer-to-peer discussions and solutions based on their experience.
About the instructors:
Nigel Somerville MBE MC, Linton Dragon Limited and TEG7 LLP
/uploads/2018/01/Nigel-Somerville.jpg?width=223&height=200&name=Nigel-Somerville.jpg)
Nigel has a UK Military background with significant cross-cutting security experience in the most challenging of land and maritime environments. He holds strategic experience providing ministerial advice to Whitehall, COBR and the Cabinet Office on security risk. Masters educated and appointed to the Register of Chartered Security Professionals (CSyP) his focus is counter-terrorism, crowded space threat management, security by design and the cyber-physical threat within the built environment. He studies the tactics and vulnerabilities that terrorists have exploited in recent complex attacks to inform crisis planning and prevent catastrophic impact.
Dr Sally Leivesley PhD Lond., MSPD, BA(Hons) Qld., FICPEM, FRSA, MACE, MIABTI, Director, Newrisk Limited and TEG7 LLP/uploads/2017/09/dr-sally.jpg)
Sally has a UK Home Office background and trained as a Scientific Advisor to respond to all aspects of nuclear attack and chemical, biological and radiological events. She plans, directs and participates in major exercises concerning critical components of industry and specialises in testing catastrophic threat impacts on critical functions of business. She has experience in all phases of risk assessment, planning, crisis management and post-loss recovery including psychological interventions in communities, post-disaster. Sally is a respected media adviser on public protection and is a member of the Register for Security Engineers and Specialists (RSES).
New Principles for Governance and Strategy in a Crisis
Date: 22 April 2018
Location: Dubai, United Arab Emirates
Course length: One day
Price: £800
Register for this course:
To register or find out more about this course please email: sanna.lindstrom@pulseconferences.com
Course Modules
Module 1: Governance when building a Risk Framework
- Understanding strategy
- Testing strategy with case studies
- Managing internal transformation risks
- Threat intelligence and dynamic risk framework
- Exercise catastrophic risk
- Identifying new Governance Principle 1
Module 2: Trust and Assurance
- Reputation risk
- Assurance testing methodology
- Designing a test
- Exercise Brand Protect
- Identifying new Governance Principle 2
Module 3: Interface with Board and Stakeholders
- Communication skills and crisis leadership
- Reviewing organisation strategy with Board and Stakeholders
- Structuring time-lines, goals, opportunities for growth in the communication
- Exercise Fast Talk
- Identifying new Governance Principle 3
Module 4: Crisis Management and Recovery
- Exercise Insider Threat
- Understanding Sensor and Intelligence Data
- Strategic decisions for brand protection
- Personnel issues and human intelligence during increasing tension
- Team leadership strategy
- Identifying new Governance Principle 4
- Strategic decisions for recovery
- Strategy for pre-emptive systems feedback design
- Identifying new Governance Principle 5
- Individuals complete personal review of skills development
- Course summary and take-aways
Catastrophic Risk Theory and Practice for Energy, Leisure and Transportation
25-26 April 2018
Dubai, United Arab Emirates
Download course outlineRegister here
Energy, leisure and transportation sectors are critical to the productivity of nations in the region. A course on catastrophic risk theory and practical work with case studies is offered to CISOs, CEOs, CSOs, COOs, finance managers, Board Directors, auditors, City Planners and policy experts, intelligence experts, big data analysts, financial technology developers, mobile data and financial services, team leaders and senior managers and first responders to incidents.
Catastrophic risk methodology delivers high value through integrated risk assessments which reduces costs.
The course applies an ‘all-risks’ approach that adds value to commercial and government operations. Through an all-risks approach, business operations can be sustained in many new ways. This novel approach will give course participants an opportunity to be innovative with solutions to prevent and respond to extreme threats.
The two-day catastrophic risk course covers methodology to quantify risks that threaten critical operations of energy, leisure and transportation infrastructure. The course takes participants beyond general risk frameworks they are already using to understand the value of adding procedures to sustain their operations when catastrophic events threaten the survival of the organisation, services or people. Dependence on interconnected activities using cyber platforms which might be private networks, cloud, web based services, mobile devices, as brought a new threat of catastrophic failures. There are also insider risks that may breach defences and geopolitical threats and consequences from world- wide events such as nuclear instability in DPRK which are covered in case study briefings in this course. The world-wide risks to the region’s supply chains, energy security, transportation and important leisure industry will be discussed in the course.
Successful application of catastrophic risk methods can grow the business by increasing the risk appetite for innovative and transformative projects. Entry into new markets and applications of new technology are challenges that may be made easier with the benefit of catastrophic risk knowledge.
About the Instructor
Dr. Sally Leivesley PhD Lond., MSPD, BA(Hons) Qld., FICPEM, FRSA, MACE, MIABTI, Director, Newrisk Limited and TEG7 LLP
/uploads/2017/09/dr-sally.jpg)
Sally has a UK Home Office background and trained as a Scientific Advisor to respond to all aspects of nuclear attack and chemical, biological and radiological events. She plans, directs and participates in major exercises concerning critical components of industry and specialises in testing catastrophic threat impacts on critical functions of business. She has experience in all phases of risk assessment, planning, crisis management and post-loss recovery including psychological interventions in communities, post-disaster. Sally is a respected media adviser on public protection and is a member of the Register for Security Engineers and Specialists (RSES).
Module 2: Risk matrix building and Exercise Hotel Attack
- Building a multidimensional matrix for catastrophic risk
- Using the Catastrophic Risk Index in the matrix
- Calculating consequences to quantify for the business
- Working on sustainability of critical processes and control of operations and services
- Identifying controllable and uncontrollable variables
- Scenario Exercise Hotel Attack cyber and physical threats and risk management processes
- Revisiting the catastrophic matrix design and adding dimensions
- Finding the residual risks in energy, transportation and leisure in well managed operations
Catastrophic Risk Theory and Practice for Energy, Leisure and Transportation
Date: 25-26 April 2018
Location: Dubai, United Arab Emirates
Course length: Two days
Price: £1,500
Register for this course:
To register or find out more about this course please email: sanna.lindstrom@pulseconferences.com
Course Modules
Module 1: Catastrophic case studies and Exercise Degradation
- Catastrophic risk – scope of the course
- Peer-to peer discussion on experiences with catastrophic risk
- Energy distribution, transportation vulnerabilities, leisure market factors
- Developing a Catastrophic Risk Index (CRI) for an industry
- Cost benefits of Health and Safety integration with Risk Management
- Cyber and physical security risks
- Pre-defining catastrophic risk to innovation teams in the business
- Unusual threats to the Built Environment: hotels and offices transport control rooms, energy infrastructure and including renewables.
- Scenario on energy sector and terrorism- Exercise Degradation
- Principles for senior personnel when facing uncertainty in daily risk management
Module 3: Business risk model and Case Studies
- Using case studies to test assumptions of a business risk models
- Participant’s choice of case studies
- Analysis of critical factors and risk management
- Identification of fast track ways to save the business or operation or workforce
- Communication to stakeholders – techniques and assessing stakeholder response
Participant’s presentations of case studies
Module 4: Risk intelligence and Exercise Aviation and Port Attacks
- Quantification of catastrophic risk – testing the matrix
- Quantification of residual risk – testing cost effective controls
- Identifying threat intelligence for energy, transportation and leisure industries
- Controlling insider threats when the insider is not identified
- Scenario Exercise Coordinated Aviation and Port Attacks to test catastrophic risk theory and practice
- How to design, document and apply brief exercises to test sustainability of operations
- Evaluating other forms of testing risk measures for sustainability of business operation
- Course presentations by volunteers of novel solutions to catastrophic risk management that will grow the business
*Individuals complete personal review of skills development
*Course summary and take-aways
Articles & White Papers
Anomali
With thanks to our sponsors and supporting organisation
Sponsors
Join the Pulse Sponsor Community!
Programme CISO 360 Middle East Congress
Archived programme, 23–24 April 2018.
Download Full B Register here (2018 archive)
The CISO 360 Middle East Congress programme will explore how can we leverage the tools within cyber security to drive forward thinking in future generations? What are communications and cultural transformation strategies for reputation and cyber security that work? How can we develop skills for industry focus – ehealth, fintech, renewables and sustainable technologies? What are emerging international public private partnerships? How can CISOs and CIOs use cybersecurity to drive revenue and increase shareholder value?
- Day One: Monday 23 April 2018
- Day Two: Tuesday 24 April 2018
Day One: Monday 23 April 2018
08:30 Welcome coffee and registration
09:00 Chairman’s Opening – Global Risk Horizon 2018 and Beyond
Marcus Alldrick, Former CISO, Lloyd’s of London & Current Advisor, Santander
09:20 Keynote Harnessing technology innovation and cybersecurity skills for the future generations – innovation, robotics, AI
– Skills for industry focus – ehealth, fintech, renewables and sustainable technologies
– International public private partnerships participation
– A government road-map to national security cyber threat
Senior UAE government representative – invited
09:40 Investor 360 Keynote Transformational cyber security investment initiatives – How can security reposition as enablers of business innovation? Is cybersecurity IP the next gold?
Hear the investor perspective on the advanced and emerging technologies that lie within cybersecurity – data analytics, robotics, cloud and assistive technologies. Where are the most patents being filed that directly link to cybersecurity? Is the security industry fully monetizing all the cybersecurity IP out there? How can this be monetized? What is the role of incubators – who are the key market players? Incumbents versus disruptors and game changers
Major technology investor – invited
10:00 Case study how M&S integrate security into rapid development
Agile Security… it’s not an oxymoron, but it is an accurate description of how we secure e-commerce development!
If you have in house software engineers and an ecommerce platform or even a team of developers working on a dynamic website then you will no doubt have pressure to release code quickly – with static code analysis and sometimes overzealous security colleagues, the process of securing that code base can become slow and cumbersome which leads to delays in your release cadence. M&S has developed an agile security process that integrates into the fast-flowing world of modern ecommerce. Lee will explain to you how his team do this and use gamification to ensure the security teams are finding the problems first. Why should I listen to this speaker? Lee has come up with a unique way of using gamification between Blue and Red teams which he has integrated into ecommerce development. A worked example of how M&S integrate security into rapid development and examples of gamification algorithms used in this process.
Lee Barney, Head of Information Security, Marks and Spencer
10:40 Case Study BlockChain, cyber resilience, and continuity
Eng. Manan Qureshi, Vice President / Head of Business Continuity, Riyad Bank
11:10 Morning Coffee Break
11:30 FinSec Panel How are banks and fintechs protecting themselves against organized crime and state nation threats in cyberspace?
– Who are the emerging attackers, what are their motives and what methods do they use?
– What are the new opportunities that will revolutionize payments, what would this mean for online security?
– Can the use of blockchain/distributed ledger technology improve security?
– How is AI being used in authentication?
– What are the key challenges of how sensitive data is protected now?
– Financial regulators – are their demands realistic and achievable?
– Insurance of cyber risk – How to manage the risk and not just transfer it?
Chaired by:
Eng. Manan Qureshi, Vice President – Head of Business Continuity, Riyad Bank
Panellists:
Michael Waheeb, Head of Information Security, Network International Africa
Marcus Alldrick, Former CISO, Lloyd’s of London & Current Advisor, Santander
Anshul Srivastav, Chief Information Officer, Information Technology, Union Insurance Company PSC
Joseph Makram, CIO, Egyptian Arab Land Bank
12:10 Case study How to Secure Your Business on the Cloud – Practical Approach from Strategy to Implementation
Hear how the region’s leading online retailer is approaching cloud security – from strategy to implementation. Why should I listen to
this speaker? You will leave with practical insights on how to promote the commercial advantages of managing information security risks in the cloud.
Aladdin Dandis, Information Security Manager, Souq.com- Subsidiary of Amazon
12:50 Futurist keynote + Panel Security implications of AI, Big Data, IoT, Blockchain
CISO and CIO as enablers of business innovation: What are the risks, opportunities and game-changers of AI, Big Data, IoT, Blockchain?
Cut through the hype and hear strategy and predictions from innovators, investors and CISOs on how disruptive technologies are radically transforming modern business and where the opportunities lie for cybersecurity.
– Futurist view of security implications of AI, Big Data, IoT, Blockchain – predicted game changers?
– How AI will help on achieving UAE 100 years vision which is the first Vision in the world
– Role of innovation in future foresight and future accelerations
– Change management and convergence of security disciplines for next generation security
– Security controls/ standards/ considerations for safe city architecture built based on AI, Big Data, IoT, Blockchain without compromising public safety
– Cyber resilience that became national resilience – what are the strategical actions to be adopted for readiness to response to cyber resilience?
Co-chaired by:
Dr. Mohammad Khaled, CIO, IT Digital Transformations, Regulation & Supervision Bureau – RSB
Kumar Prasoon, Group Chief Information Officer (CIO), Al Safeer Group
Dr. Major. Hamad Khalifa Al Nuaimi, Head of Telecommunications Security, Abu Dhabi Police GHQ
13:20 Lunch
14:40 Diversity in Infosecurity
Irene Corpuz, Head of the IT Security Section & acting CISO, Western Region Municipality Abu Dhabi
15:00 Role-Playing Exercises Threat from business espionage
Hear advanced methods of intelligence gathering, insights on the insider threat and counter intelligence and how security is compromised by human nature with a series of case studies through the medium of role playing exercises and case studies. Why should I listen to this speaker? Learn from real world examples of the sheer breadth of vulnerabilities in almost all organisations, all facilitated by freely and legally obtainable information and how to mitigate the risks.
-Who collects intelligence and why, advanced methods of intelligence collection
– Physical and Information security methods
– Counter intelligence and the insider threat
– How security is compromised by human nature
– Role playing of intelligence gathering techniques and security responses
Robert Shaw, Senior Advisor, United Nations, and Co-Founder, TEG7 LLP
15:40 Afternoon Tea Break
16:00 Panel IoT cybersecurity with energy and renewables
Discuss emerging cyber threats and technical issues and solutions for control room operations relating to AI and IoT challenges.
– Securing data across big data processing and analytics
– Identifying how to mitigate human errors in the energy infrastructure
– Specific cybersecurity challenges with IoT and critical national infrastructure
– Sustain operations under all- hazards events – change management techniques
– New threats from interconnected systems
Led by:
Dr. Sally Leivesley, Director, Newrisk Limited and TEG7 LLP
Ray Stanton, SVP/Group Chief Security Officer, TDC Group (Denmark)
16:30 Open Source Hacking Workshop Open Source Intelligence (OSINT) – penetrating organisations infrastructure cyber vulnerability assessment
No matter how well defended the organisation’s intellectual property is against cyber attack, the staff are the way in. The talk focuses on the mindset and techniques of the attacker, whether a cyber criminal, a state actor, a corporate spy or frivolous hacker, and shows how surprisingly low-tech most attacks are – often deriving cyber attack-enabling information from nothing more than a search engine before launching a devastating exploitation of infrastructure or the human workforce. Why should I listen to this speaker? Hear real world examples from a covert online operations and digital forensics expert on the sheer breadth of vulnerabilities in almost all organisations – all facilitated by freely and legally obtainable information and how to mitigate the risks!
Former Intelligence Officer, North Cyber Limited (UK)
17:10 Close of day one
18:00 Dinner
Day Two: Tuesday 24 April 2018
08:30 Breakfast Briefing – Emerging Risks and Opportunities Training
Robert Shaw, Senior Advisor, United Nations, and Co-Founder, TEG7 LLP
Intelligence Specialist, North Cyber Ltd
Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7
09:05 Chairman’s Re-opening
Marcus Alldrick, Former CISO, Lloyd’s of London & Current Advisor, Santander
09:10 CxO Cyber Risk Governance and Assurance Boardroom
– How can CISOs reposition cybersecurity as a robust business investment strategy to keep the Board happy?
– What do Board members and other GRC assurance leaders need to know to ask the right questions?
Investors are increasingly asking questions of the board about cybersecurity because of litigation risks and disclosures. In this session you will hear and share how to align culture and mindset across security-business-technology and legal. How can CISOs improve their offering? What can CIOs, GCs, CPOs, CROs offer the CISO internally? What will you learn? Practical take-aways on how we can best reposition cybersecurity as a robust business investment strategy.
– How can we take current security practices to create new models and strategies to build security value?
– How can we strive for higher quality security practices, standards and sharing?
– GDPR – challenges for the region
– What best practice security strategy looks like now and how is this rapidly evolving with digital transformation?
– Quantitative risk models applied to security – can we leverage internal knowledge to apply financial risk models
– How can we place measures on controls – balancing process and power to increase the surface areas of attacks?
– How will CFOs, GCs and CCOs provide compliance in the era of digital transformation?
Co-led by:
Jonathan Martin, EMEIA Operations Director, Anomali
Lady Olga Maitland, Chairman, Copenhagen Compliance
Richard Hollis, CEO, Risk Crew
Ray Stanton, SVP/Group Chief Security Officer, TDC Group (Denmark)
09:50 Panel Advancing tomorrow’s holistic security leaders
The tools within cyber security are useful for their forward thinking to 2071 and education and innovation to be competitive in the world with the younger generation. Innovation and harnessing key skills to build the UAE into the world leading nation of technologists. This panel discussion will ask how can we leverage the tools within cyber security to drive forward thinking in future generations?
– Communications and cultural transformation strategies for security/ IoT/ IT/ threat/ response/ intelligence disciplines
– Skills for industry focus – ehealth, fintech, renewables and sustainable technologies
– Defending people, systems and infrastructure – building national resilience
– International public private partnerships participation
– Changes in international salary trends and expectations
– Advancing younger security leaders – passing on the legacy merged with new ways
Chaired by:
Mrs. Bhavani Suresh, President, ISACAUAE Chapter
Panellists:
Aladdin Dandis, Information Security Manager, Souq.com
Irene Corpuz, Section Head – Planning & IT Security & Acting CISO, Western Region Municipality – Abu Dhabi Government
Sofiane Chafai, EMEA Advisory Board Member, (ISC)²
Jenny Reid, CEO, iFacts
Dr. Vasileios Karagiannopoulos, Senior Lecturer in Law and Cybercrime; Director of the Cybercrime Awareness Clinic; Course Leader for BSc Criminology and Cybercrime; Chair of ICJS Ethics Committee, University of Portsmouth
10:30 Keynote + Discussion What makes for a world-class business intelligence, BCP, investigations and cybercrime unit?Insights on managing cybercrime investigations from a highly experienced and sought after investigative and security subject matter expert, who has directed and led law enforcement and corporate investigation teams for nearly 30 years into matters of regulatory compliance, fraud, bribery, corruption, money laundering, employee misconduct and reputational risk across the globe.
– How do you leverage the value and investment from cyber threat intelligence?
– What makes for a world-class threat intelligence team? Who do you share this with internally?
– How does this leverage value and actionable intelligence to the board to advise appropriate strategy?
– Practical steps to conduct an insider threat investigation
– Sharing ROI of strategic decisions made on the back of cybercrime investigations, intelligence, data and the patterns of employee behaviour
Chaired by:
Simon Scales, Recently Head of Investigations EMEA, BP plc.
10:50 Morning Coffee break
11:20 Integrating cyber function into BCP to deal with the massive attacks
Sofiane Chafai, EMEA Advisory Board Member, (ISC)²
11:35 ‘Live’ Response Exercise Shamoon Version X – What is next?
New threats to technology in the region can be reduced by innovative team thinking and effective response planning within companies and government departments. This ‘live’ group scenario exercise draws on 2018 public information on the Spectre threat to hardware. Working in table groups with fellow participants, this is an interactive challenge for participants to build defensive and offensive actions within their organisation to protect against future advanced threats to the sustainability of infrastructure and business operations in the region. You will tasked to deliver information that is vital to CISOs and senior company managers in government, telecommunications, energy, banking and other critical infrastructure.
– Benchmark innovative solutions and assess off-the-shelf solutions currently available
– Integrate business continuity and CISO security to avert a catastrophic threat
– Integrating cyber function into BCP to deal with the massive attacks
– Assess company-wide effects on delivery and supply chain
Co-led by:
Irene Corpuz, Section Head – Planning & IT Security, Western Region Municipality UAE Government
Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7
12:10 Case study Sweden Psychology in practice of social engineering
Social engineering is nothing new, but it has become the “king of attacks”, being (relatively) easy to deploy and requiring minimal commitment from the attackers’ side. Why listen to this speaker? MTG has seen its fair share of social engineering attacks. You will hear how MTG has chosen to deal with this threat. Key takeaways:
– The 6 influence principles (by Dr. Cialdini) and how these principles are utilized to improve the success rate of social engineering attacks
– The driving forces of what makes us “click on the link” and how we should defend against them
– What MTG is doing to prevent these types of social engineering attacks
Dimitrios Stergiou, Chief Information Security Officer, Modern Times Group MTG AB (Sweden)
12:30 Security Collaboration Challenges and best practice
– Why is collaboration across the business essential?
– What needs to be disseminated, what doesn’t and why?
– What are the benefits? What are the obstacles?
– How do you overcome them?
Richard Hollis, CEO, Risk Crew
12:50 Lunch
14:00 Social Media Scandals Human factor – social media risk and policies
– Current figures indicate that over 6,000 tweets are made per second globally, 5 new Facebook profiles are opened every 10 seconds
– Social Media gives a glimpse into the person that will enter your workplace and gives a good indication of whether they will fit the corporate culture of your organisation and if they could pose a possible risk to your organisation
– All it takes is one person to gain media exposure and traction, costing an organisation millions in losses
– Social media scandals cost South African businesses in excess of R500 million during 2016 alone
Jenny Reid, CEO, iFacts
14:20 Case study Understanding hacktivism as a first step to mitigating its cybersecurity implications
Dr. Vasileios Karagiannopoulos, Senior Lecturer in Law and Cybercrime; Director of the Cybercrime Awareness Clinic; Course Leader for BSc Criminology and Cybercrime; Chair of ICJS Ethics Committee, University of Portsmouth
14:40 Artefacts of Innovation Roundtable
CISO and CIO as enablers of business tranformers. How can we truly achieve security by design?
Co-facilitated by:
Kamran Ahsan, Senior Director/Digital Security Solutions, Etisalat Digital
By 2018, it is estimated that 70% of enterprise cybersecurity environments will use cognitive/AI technologies to assist humans in dealing with the vastly increasing scale and complexity of cyber threats. The artefacts of innovation that constitute the transformative digital economy are: big data & analytics; the cloud & mobility; IoT; Artifical Intelligence. Combine peer group brain power on the different risk perspectives associated with each technology to share the latest approaches and updates on security deployments.
Format:
Each of the 4 tables will focus on a given different ‘perspective’ of security. Attendees will select 2 out of the possible 4 roundtables below, rotating in groups. Facilitators and a note-taker will remain fixed to each table to lead and capture the key discussion points, observing The Chatham House Rule. This Roundtable is ideal to benchmark with other CISOs and CIOs to share experiences with peers to strengthen your capacity – including receiving threat intelligence about cloud vulnerabilities, due diligence for 3rd party supply chain, incident response, measures and defending appropriately. Notes will be taken throughout all of the roundtable discussions, observing the Chatham House Rule.
Roundtable 1– Cloud and mobility
Roundtable 2 – IoT
Roundtable 3 – AI
Roundtable 4 – Big data and analytics
15:40 Close of congress, afternoon tea and goodbyes
Speakers
CISO 360 Middle East Congress
Chaired by:
Marcus Alldrick
Digital Risk Management, Security and Compliance Advisor
/uploads/2017/09/Marcus-A.jpg?width=332&height=500&name=Marcus-A.jpg)
Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer. In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.
Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc. Marcus doesn’t have much spare time but what he has he enjoys in Dorset on the South Coast of England where he and his husband live.
International speaker panel
*additional speakers to be announced shortly
Enquire about becoming a speaker
When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.
Experience + value = story.
- do you have a compelling business security story that simply must be told?
- have you recently worked on an innovative security project?
- are you willing to openly share inspiring insights, expertise and ideas to advance the security community?
We are always looking for:
- keynote insights, cutting-edge ‘live’ demos, deep dive workshop ideas
- new best practice case studies, fresh ideas, forward thinking topics on security and governance matters
- sessions with actionable takeaways and positive contributions to the output reports
- the world’s smartest thinkers and doers in security, cyber, privacy, resilience, risk, governance, compliance
We welcome your input into shaping the agenda and speaker panels.
Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.
For further information, please
phone: +44 (0)20 7936 8989
email: sara.hook@pulseconferences.com
Speaker details reflect the 2018 archive.
Aladdin Dandis
Information Security Manager, Souq.com (UAE)
Aladdin Dandis is the Information Security Manager of Souq.com, Subsidiary of Amazon. Previously, he worked in different information security positions such as Jordan eGovernment Program and EHS, under Hakeem program for managing national EHR system. Aladdin is specialized in security and privacy related fields, especially in GRC, Security Architecture and Cloud Security.
Aladdin holds MSc in CIS from University of Sunderland and BSc in Physics from Yarmouk University, and other professional certifications, e.g. CISM, CGEIT, CEH, ISO 27001 LI and TOGAF. Aladdin is also a member of internationally recognized organizations, such as ISACA and ACM.
Anshul Srivastav
Chief Information Officer -Information Technology, Union Insurance Company P. S. C.
A leader with major operating tenets as driving technology transformation through thought leadership, design thinking, innovation, analytics & delivering value to stakeholders. Anshul is a global technology leader and change practitioner who has been instrumental in driving technology transformations for businesses in the range of multi Billion USD as revenues.
Experience has been around taking up strategic technology initiatives, architecting, delivering and managing it at an enterprise level.
Anshul has several notable career accomplishments, wherein he has led, created and launched the key Artificial Intelligence, Blockchain, Cloud, ecommerce, mobile and business intelligence initiatives for various Financial Institutions across the world.
Currently in a leadership role as Chief Information Officer Information Technology and Digital Officer in Dubai, leading the IT Strategy, Technology Transformations, Analytics, software delivery, architecture and Cloud for Union Insurance (UAE, Oman and Bahrain) across all lines of Business (Life, General (P&C) and Health Insurance) Creating and Driving big strategic Initiatives aligning IT transformation to deliver business value. Major Cloud transformations impacted the bottom line of Union by multimillion AED in the first year. Transformation on Digital added multimillion revenues in Life, P&C and Health lines of business.
Bob Shaw
Senior Security Advisor, United Nations
Robert is a security, intelligence and EOD executive with a UK Military background. He has broad strategic and operational experience and has advised senior staff, diplomats and government officials on aspects of security, intelligence, threat analysis, crises management, and resilience strategies. He has been the UN Security and EOD Advisor; Liaison officer for the UNMAS and UNOPS and has experience with NATO, the GCC, African Union, OSCE, EUPOL, FCO and others. Robert is a respected expert, has specialist research background on suicide bombing and has provided thematic briefs on worldwide security issues relevant to UNMAS/UNOPS missions.
Bhavani Suresh
President, ISACA UAE Chapter
Madame Bhavani Suresh is a Well-qualified and talented professional with almost 20 years (around 10 Years in Oil and Gas Field) of experience in various Information Systems fields encompassing, Business Continuity Management, Information Security Management, IT Operations Management, Systems administration, programming, System Analysis, Project management, training users-team members and developing solutions for clients. Expert in Management Systems and has supervised and directed more than 300+ projects including government, semi-governments, multinationals and local organizations in UAE and across the Middle East. These projects focuses on QMS, EHSMS, OHSMS, ISMS, ITSM, BCMS, Project Management and various other Management Systems. Possesses excellent analytical, communication and interpersonal skills.
She is currently the President of ISACAUAE Chapter. An ambassador of International Business Women’s Group and a member of different international organizations. Trained more than 300 Senior Management Engineers/Officers at various levels and functions in the domain of Occupational Health, Safety, Environment, Quality Assurance, Quality Control and conducted numbers of Skill Development workshops. Managed, Conducted, and supervised numbers of certifications and surveillance for IMS. Audits by different Certification bodies at different corporate establishments in GCC and non-GCC Countries.
Provide professional quality and environmental management solutions for total quality management and continual process improvement. Recognize key opportunities and/or challenges of the business and collaboratively establish the best practices, for achieving desired results by facilitating the implementation to increase performance and accomplish functional and organizational goals.
Dimitrios Stergiou
Chief Information Security Officer, Modern Times Group MTG AB (Sweden)
Dimitrios is currently employed as the Group Chief Information Security Officer for MTG.
He is an experienced senior Information security and Risk professional with over 20 years’ experience in Risk Management, IT audits and Information security. Before joining Modern Times Group, Dimitrios held positions at NetEnt, Entraction, Innova S.A and Intracom S.A.
Dimitrios holds a M.Sc. in Information Security and is a Certified Lead Implementer for ISO 27001:2013, Certified Information
Security Manager (CISM), Certified Information Systems Auditor (CISA), Certified Risk and Information Systems Control (CRISC) professional and Certified Information Systems Security Professional (CISSP). He is also a Certified Information Privacy Manager (CIPM) and a Certified Information Privacy Professional / Europe (CIPP/E).
Dimitrios’ Information Security focus lies with: standards compliance, privacy, risk management, vulnerability management, penetration testing and social engineering.
Edward Ayman Ganom
CISO, The Commercial Bank of Qatar
Edward Ayman Ganom is a senior cybersecurity expert with over 15 years of international experience in information security architecture and technology risk management. He currently holds the position of CISO at The Commercial Bank in Qatar. Previously, Edward held several key technology and risk management positions in the financial and public sectors in the USA and the Middle East. He participated in drafting national cyber security policies and strategies and cybercrime legislation. Edward holds two bachelor degrees, one in Electronics Engineering and one in Political Science from two American universities. He is a Certified Information Systems Security Professional (CISSP) and is a recognized speaker at technology, security and risk conferences.
Dr. Major Hamad Khalifa Al Nuaimi
Infrastructure Dept. ICT Center, Abu Dhabi Police GHQ
My team and I manage the wireless telecommunication for AD Police, Starting from the designing of our based location to the activation of the network itself. I had two degrees from HCT ( Higher college of Technology) which are HD higher diploma in science of Network and Bachelor in Network computer, Also I’m pleased with my TNM ( Telecommunication and Network Management) master degree from SYRACUSE University, NY United State of America.
My managerial experience has provided me with most valuable first hand experience of organizational and corporate change and inspired my passionate interest in organization management and administration. In my first management position, with Abu- Dhabi police as a Network Section Manager, from 2005-2009 and 2012 to 2016. However, I spent four months working in one of the Information Technology company in Boston ,MA united state of America, I had the valuable of experience of successfully record of customer satisfaction as well as figured out the differences between the business overseas and my own country. I’m CCNA (Cisco Certified Network Associate) , CCNP (Cisco Certified Networking Professional ) and ITIL certified(Information Technology Infrastructure Library). Moreover, had a successful course training in leadership preparation in Abu Dhabi Police training department.
Dr. Sally Leivesley
Director, Newrisk Ltd
Dr. Sally Leivesley, Director, Newrisk Ltd and Co-Founder, TEG7 Group LLP – advises companies and governments on catastrophic risk where losses to companies and governments may involve critical functions essential for operations and reputation. She runs exercises to stress test critical function failures and resilience capability. Dr. Leivesley is known for her appearances on aviation terror attacks, ISIS, Al Qaeda, Al Shabaab and other international terrorism, cyber breaches, CNI protection and government policy on the BBC World Service, ITV This Morning and other UK based media and European, Middle East and Australian media. She raised the forensic importance of the risk of cyber hijacking of flight MH370 which was the subject of a Discovery Channel documentary and has been a commentator on the risks relevant to Donald Trump economic, terror and nuclear influences during his Presidential campaign and on his election. Dr Leivesley works in conjunction with The Exercise Group7 (TEG7) a London based group of companies that specialise in resilience operations for cyber-attacks, international terrorism and nation state threats and solutions for business and government-critical infrastructure. The focus is on testing through exercises, assurance and pen tests using an integrated approach to all hazards including social factors. (www.Teg7.co.uk) In the UK she has been a member of the technical committee for the first IET (formerly IEE) guidance document on Resilience and Cyber Security of Technology in the Built Environment which was supported by the Centre for the Protection of National Infrastructure. She is also a member of the British Register for Security Engineers and Specialists established to advise at a strategic level on terrorist and other extreme threats to critical infrastructure. She interfaces with a USA company to extend exercising for aviation and energy industries. Dr Leivesley originally trained as a Scientific Advisor with the British Home Office. She is a specialist in CBRN.
Dr. Mohammad Khaled
CIO, IT Digital Transformations, Regulation & Supervision Bureau – RSB
Dr. Mohammad Khaled is the Futurist, Digital Transformation, Information Security Experts, and Corporate Excellence with responsibility for Digital Transformation, Information Security, Excellency and innovation.
Dr. Mohammad Khaled) worked in IT and services transformations along with the Information Security at several mega government organizations, including Department of Energy, Regulation & Supervision Bureau, ALROWAD IT Solutions, Subsidiary of the Privatizations Group of Ministry of Interior), Department of Finance and Abu Dhabi Police. Notable is his 16 years as transformations for previous company & description.
Dr. Mohammad Khaled received PhD first of its domain and aligned with , special training, study abroad in discipline or field from British University in Dubai.
Dr. Mohammad Khaled professional interests focus on Artificial Intelligent, Block chain, Smart Safe City, Cyber Security and Resilience, Future Accelerations, Future foresight and Innovation, and he handled recognized projects were also the following are some of his current publications:
• Role of corporate governance on future foresight, future accelerations and citizens happiness
• Information Sharing Framework for National Resilience
• Governance, Risk, and Compliance in Information Technology: The Establishment of Best Practices for Government Entities
• Governance, Risk and Compliance “GRC” for Internet of Things “IOT”
• Evaluating and Measuring Governmental Smart and online Service in Terms of the Quality -The Case Study of UAE
• Nature and Quality of Smart Government Services: The Case of the UAE Services: The Case of the UAE
• Digital Infrastructure: Enabling Smart City and Safe City for future accelerations and future foresight
• SMART Policing on Smart City and Safe City for people happiness
• BYOD Technological: Next Generation Business Development Programs for Future Accelerations, Innovations and Employee Happiness
• Role of corporate governance on future accelerations and people happiness
• The Best Practices for Establishing and Implementing Smart Government for Special Needs and Disabled People
• Reducing the Experience Gap for Engineering Graduates by the Introduction of Problem-Based Learning Curriculum to the Bachelor of Engineering Degree Courses
• The Best Practices and How to Attract People to Use Smart Government
• Future foreseeing from mobile and smart learning
• Others 9 publications
In addition, Dr. Mohammad Khaled was recently honored with the
• Catalysts Awards 2018 – Government CIO
• Happiness Ambassador from The Way To Happiness Foundations International from USA 2018 on the occasion of the international day of Happiness.
• Abu Dhabi University Alumni Community Ambassador winner for the year 2017.
• Happiness Ambassador because of the international happiness from Corner Stone International Colleague because of getting 98% of student’s satisfaction for the year 2017. Affiliations with Wolver Hampton University UK.
• Future accelerator lead for the year 2017 from London Metropolitan College for my outstanding contribution on the IT industry.
• Youngest Arab achiever awards 2016 for the category youngest Arab leader for outstanding contributions on the government services.
• One of the best 100 Chief Information Officer 2018 over the Middle East.
• One of the best 100 Chief Information Officer 2017 over the Middle East.
• One of the best 100 Chief Information Officer 2016 Middle East.
• Government IT visionary from IDC Award 2015.
• IDC Best Innovation Award for public services sector 2014.
• Supply Chain and Transport Awards 2014 “Best transport technology solutions of the year”.
• Network Middle East Innovation Awards 2014 “Networking Professional of the Year”.
• Channel Meddle East Award 2014 “System Integrator of the Year”.
• Arabian Computer News Arab Technology Awards 2013 “Health Implementations of the year”.
• Arabian Computer News Arab Technology Awards 2013 “Public Sector Implementations”.
• Network Middle East Innovation Awards 2013”Wireless implementation of the year”.
• Others
Dr. Mohammad Khaled know his continues contributions to the IT Industry, assuring the alignment with the governmental and business objectives, as well as Youth Supporting due to his believe that the youth are the future.
George Eapen
Chief Information Security Officer (CISO), GE in Middle East, North Africa & Turkey
In his role, George is responsible for defining Cyber Security strategy for Enterprise IT & OT for the region and provide strategic leadership to IT Security related projects & initiatives for all GE businesses in the region. George is also responsible for protecting GE critical assets in a growing region which spans 18 countries and 7000 work force George joined GE in 2006 with GE Healthcare in India and has since held roles of increasing responsibilities and progressed to his most recent role as Chief Information Security Officer for MENAT. During his tenure with GE, George worked in multiple domains (Product Life cycle management, ERP, Infrasrture, Supply Chain & Commercial IT) and multiple businesses (GE Healthcare, GE Appliances, GE Capital, GE O&G, GE Aviation and GE Corporate) George is a graduate of GE IT leadership program (ITLP), GE Six Sigma Black Belt program and graduate of GE Executive leadership program (CAS)
Eng. Joseph Makram
CIO, Egyptian Arab Land Bank
CIO head of IT at EAL bank joined 2016 till now, Deputy –GM for E-channel at National bank of Egypt from 2008 till 2016
Manager E-channel at Arab bank from 1994 till 2008
Plus other working experiences in IDSC cabinet of minsters , Mantrac
I am PMP certified , MCSD certified
Hold master’s degree from Nottingham university in IT
Hold post graduate diploma in IT
And Engineering degree from AIN shams university
Irene Corpuz
Section Head - Planning & IT Security, UAE Government
Irene is the Head of the IT Security Section and acting CISO at the Western Region Municipality, Abu Dhabi. She is responsible for the execution of the ADSIC Information Security Programme, Security Governance, Risk & compliance to IT Security Policy. She offers 27 years of combined and diverse experience in IT (Security, Operations and Strategy), Quality & Excellence. She has worked in various industries and region and led strategic initiatives in Asia, Middle East, Europe and America. An emerging seasoned speaker on Information & Cyber Security Conferences, Irene has spoken in a number of conferences in Asia, Middle East and Europe. Irene acquired her Masters of Science in IT from University of Wales, and holds the following certifications: ITIL V3, PMP, ISO (QMS and 27k) Lead Auditor and EFQM Assessor.
Jenny Reid
CEO, iFacts
Jenny Reid is the CEO of iFacts, one of the leading online employee screening & engagement service providers in South Africa today. Based on the premise that removing the people risk will ultimately help organisations to prosper, iFacts ensures that companies thrive with honest, ethical and productive employees and services providers.
In 1995 Jenny joined the security industry at an investigations firm, where she was ultimately appointed as Managing Director. During this time she was also the first woman to ever be appointed as President of the Security Association of South Africa. iFacts started in 2001 and Jenny bought it out 100% in.
Never content to rest on here laurels, Jenny has taken the iFacts brand to new heights and is constantly looking for new and innovative ways to ensure companies maintain true value in their organisation and enhance it.
Jenny’s strong leadership style and outspoken views on corporate crime and political corruption have made her a highly sought after local and international conference speaker and NLP coach. She is also part of the Cheri Blair Foundation Mentee Alumni.
Jenny is also the founder of Adventures for Love, an organisation made up of like-minded women who embark on a number of physical adventures around the globe to raise awareness and funds for various charities and conservation efforts. Jenny lives in South Africa with her husband, Neil.
Jonathan Martin
EMEIA Operations Director, Anomali
Jonathan Martin, based in London, is the Anomali Operations Director, covering Europe, Middle East, Africa and India. Before joining Anomali, he was one of the first employees of ArcSight in EMEA, helping to grow the company from its infancy through the acquisition and successful integration into HP’s Enterprise Security Products division.
Prior to ArcSight he worked for British Airways as well as a number of security companies including CyberGuard & Critical Path. Jonathan holds a Bachelor of Science degree in Mathematics from the University of Bradford, UK
Eng. Joseph Makram
CIO, Egyptian Arab Land Bank
Joseph Makram , Chief Information Officer since 2016 at ( Egyptian arab land bank a 138 years old bank) The primary responsibilities to change the bank and people to reach the standards of the 4th industrial era .
With management support we are building a state of art data center ,and all the compass infra structure is done in months , many large projects for ATM ,data cleansing , portal , aml , risk are now in place .
Prior to joining Eal. Bank , Joseph was part of the change mangment and renovation for the largest bank in egypt national bank of egypt, a bank with 450 branch and more then 5 million clients , as a deputy general mamager of e-business he managed many projects Some where nation wide projects And shared in pci certification, and busiding new skills to old and new IT staff.
He also did spend spent 14 years in as manager of e-bussines in arab bank one of largest banks in middle east with 600 branches world wide and he developed many successful projects and was the first bank in 1999 to introduce visa payment online at theses early stage .
Joseph total IT industry experience is more then is 25+ also he holds PMP certification for years and holds his MSc.IT FROM NOTTIGHAM university Uk and many other professionals certifications.
Kamran Ahsan
Senior Director/Digital Security Solutions, Etisalat Digital
Kamran Ahsan brings over 20 years of professional experience primarily focused in Information Security and has served IT service provider organizations in areas of strategic development of security solutions, security risk management, security policies and procedures enforcement, standards and reference architecture development; and security education.
Serving as a Senior Director in Etisalat Digital, he is accountable for the entire business function of Digital Security Solutions for Government, Enterprise and SMB sectors.
Kamran is a frequent speaker on digital security affairs in renowned international and local conferences and workshops. He earned a Masters in Applied Science (MASc.) degree in IT Security from the University of Toronto, Canada in 2002. He is a Certified Chief Information Security Officer (C|CISO) from EC Council, a Certified Payment Card Industry Security Implementer (CPISI) and holds professional certifications in ISO (ISO 27001 Lead Auditor) and the IT Governance Framework (COBIT).
Khaled Almansouri
Former CIO, Etisalat
Kumar Prasoon
Group Chief Information Officer, Al Safeer Group
Kumar Prasoon is the Group Chief Information Officer (CIO) for Safeer Group. In this prominent role, he makes technology recommendations for the group’s executive management on the aspects of business intelligence, cloud computing, enterprise 2.0, integrated systems architecture and virtualization. Kumar Prasoon is an ICT Industry Process Centric seasoned Enterprise Architect and Business Process Management Expert. Kumar Prasoon excels at leading cross-functional teams across Americas, Europe and Asia ; coordinating multiple projects with exceptionally strong understanding of the business issues driving software development based on experience both as a seasoned Enterprise Architect as well as Interface Manager with solid approaches towards Integration Technologies / Service Oriented Architecture using external interfaces concerning Systems Integration / Systems Architecture / System Infrastructure support for Mission Critical Applications. Being the founder of Fuzzy Analytics Framework and Modern Industrial Complex Mathematical Calculus for Emerging Technologies. Mr. Prasoon is also the global leading Industry Researcher, Scientist and Technology Evangelist for Smart Systems, Smart Retailing, Smart Cities , Smart Parking, Smart Engineering, Smart Instrumentation, Smart Metering and Industry Quantum Mechanics employing the Modern Emerging Technologies. He chairs as an advisory board member with numerous national and international consortiums in the capacity of consulting, research and bringing supreme Industry Innovations. Another strong facet is his contribution to the Academia Sector for the Global Universities from Far East to West where he has mentored, coached and executed successful projects with hundreds of incumbents in Bachelors, Masters and Doctorates in Engineering, IT, Business and Management in the areas of Emerging Technologies, Emerging Markets and Emerging Systems.
Lady Olga Maitland
CEO, Copenhagen Compliance and Defense and Security Forum
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.-
Lee Barney
Head of Information Security, Marks and Spencer (UK)
Lee Barney is a passionate believer in using Security as a business enabler; he does this through challenging the preconceptions of the industry and by changing the mind set of those who work in Security to be more pragmatic. Having worked in Defence, Consulting, Finance and now Retail, Lee has a breadth of knowledge about what works well and what doesn’t work at all. Lee advocates a healthy relationship with the Chiefs of an organisation pointing out that our industry is built on Executive buy in not scare mongering. Lee is the Head of Information Security for Marks and Spencer.
Manan Qureshi
Vice President - Head of Cyber Resilience, Business Continuity & Crisis Management, Riyad Bank
Manan is a senior global Cyber/Organizational Resilience, Information Security, GRC executive with over 14+ years of experience leading teams delivering strategic and operational cyber security, business continuity and disaster recovery services to financial institutions and customers worldwide.
In his past tenures he has been based in Singapore & APAC, Europe, Middle East and North America with firms like Accenture, KPMG, Devoteam, HSBC and SocGen and currently manages Cyber + Organizational resilience across operations in North America, UK, Middle East and Singapore.
Manan has been involved in managing service lines, recruiting, growing and retaining talent and introducing innovation across projects of a geo-diverse nature spread across diverse legal and technical jurisdictions.
He is known for his technical brilliance and ability to communicate and deliver to internal and external clients at all levels.
Manan is a thought leader, international speaker and an evangelist on Cyber Resilience, Organizational Resilience and GRC as well as innovative and disruptive technologies.
Michael Waheeb
Head of Information Security, Network International Africa
With more than 10 years’ experience in the Information Security field mostly in the finical sector, Michael is an expert in analyzing, developing, and optimizing Information security management systems. He has a very good knowledge of security standards, monitoring security compliance with laws & regulations.
North Cyber Ltd (UK)
North Cyber are team of former intelligence officers with expertise in covert online operations and digital forensics. The company teaches government and corporate clients how find and fix the unseen holes in their security. They specialise in all levels of capability including low-tech and no-tech hacking, using freely available information to circumvent vastly expensive but ineffective security systems. The teaching draws on many and varied real-world examples from the private and government sectors, from the perspectives of the attacker and incident responder. Participants in these courses will evaluate their own experience on the course in gaining additional skills and understanding of the threats to their organisation and they will gain confidence in tackling these catastrophic risks to the comparate or government operation
Dr. Vasileios Karagiannopoulos
Institute of Criminal Justice Studies, University of Portsmouth
Dr Vasileios Karagiannopoulos holds an LLB from Athens Law School and an LLM in Information Technology and Telecommunications Law and a PhD in Law from the University of Strathclyde, School of Law. He has taught Information Technology Law, Intellectual Property Law, E-commerce Law and Human Rights Law for Strathclyde and Edinburgh Law Schools and is now a Senior Lecturer in Law and Cybercrime working for the Institute of Criminal Justice Studies (ICJS), University of Portsmouth. Vasileios has designed and is the course leader for the new ICJS BSc in Criminology and Cybercrime starting this September. He is also the Director of the Portsmouth Cybercrime Awareness Clinic, a project funded by Hampshire Constabulary, aiming to increase awareness and build resilience to cybercrime in the local community through research and public engagement activities with SMEs and vulnerable populations. Vasileios is the Chair of the ICJS Research Ethics Committee and Vice-Chair of the Faculty Research Ethics Committee and is also an IISP Certified Forensic Investigations Practitioner.
He has published in UK and US peer reviewed journals on the topics of computer misuse law and insider unauthorised access, the impact of social media during the Arab Spring and also Internet regulation in the People’s Republic of China. His new monograph by Palgrave Macmillan, Living with Hacktivism: From Conflict to Symbiosis, focuses on hacktivism and discusses the challenges faced by the US and UK criminal justice systems when dealing with such phenomena. In this book, Vasileios puts forward an alternative rationale and practical responses to hacktivism with the aim of ameliorating the inefficiencies and injustices identified in current approaches.
Ray Stanton
SVP/Group Chief Security Officer, TDC Group (Denmark)
An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CiSO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.
Richard Hollis
CEO, Risk Factory
Richard Hollis is the Chief Executive Officer for Risk Factory Ltd, a unique information security risk management consulting firm specialising in providing cost-effective, independent information risk management services. Richard possesses over 25 years of “hands on” skills and experience in designing, implementing, managing and auditing information security programs.
Over the course of his career Richard has served as Director of Security for Phillips, Paris, and Deputy Director of Security for the US Embassy Moscow Reconstruction Project as well as a variety of sensitive security positions within the US government and military. In addition to his work with Risk Factory, Richard serves on several security technology company boards and security industry advisory councils.
Richard is a celebrated public speaker and seasoned ISACA CISM, CRISC and CSX certifications trainer. Richard has presented to hundreds of audiences across the world on a wide variety of information risk management topics and techniques. As a recognised industry authority, he has published numerous articles and white papers and appeared on national and international broadcast news shows as well as being cited in a wide range of press including the BBC, MSNBC, Radio 4, the Financial Times, Time magazine and various others.
Simon Scales
Former Head of Investigations EMEA, BP plc
Simon A. Scales is a recognised leader in global regulatory compliance, ABC, Fraud, Anti-Tust / Competition and AML investigations 30 years of experience managing complex corporate investigations, including employee misconduct, insider threat and reputational risk. He has successfully managed cross-border assignments around the world, from the UK and Europe to emerging markets including China, India, South America, and the CIS (former Soviet Republics).
As the former Head of Investigations (EMEA) for BP (London, UK), he led investigations into violations of BP’s Code of Conduct and of laws and regulations including the UK Bribery Act, the U.S. Foreign Corrupt Practices Act, and the UK Proceeds of Crime Act. Prior to his position at BP, Simon served as the Director of Global Investigations for TNT NV (Amsterdam, NL), where he was responsible for the management of global investigations and associated TNT group risk, directing investigation teams working in more than 120 countries into ABC, AML, Fraud, Compliance, Reputational Risk, and governance concerns.
Earlier in his career, Simon served as a Detective with the Metropolitan Police and Surrey Police, where he led investigations of major, complex crimes, including the planning and execution of sensitive overt and covert operations for anti / counter terrorism, racial & violent crime and intelligence commands.
Simon has vast public speaking credentials, is a visiting lecturer to the University of Portsmouth (Institute of Criminal Justice Studies), and has had numerous articles published in leading journals and international media. He is a graduate of the University of Nottingham Trent Business School, and a Fellow of the Chartered Management Institute. He is also an alumnus of the Institute of Professional Investigators, a member of the Society of Forensic Interviewers, and a founding member of the Corporate Investigations Council.
Sofiane Chafai
EMEA Advisory Board Member, (ISC)²
Sofiane Chafai is an Information Security professional with over than 20 years of experience in managing ICT and security transformation programs, process and system implementation, business consultancy and business continuity management for a large blue chip companies in Middle East and North Africa in Finance, Telecom, Government Services, Oil and Gas industries.
Sofiane Chafai is contributing to the Information Security Community as (ISC)2 EMEA Advisory Board member, ISACA active member and charter member of the Algeria Information Security Association. The scope of his work includes governance, risk management, compliance, audit and business resilience.
Sofiane Chafai has been involved in several IT audit of the large international banks, Telecoms and mobile companies.
He participated in developing Information Security and compliance framework for government entities, providing assistance for GRC system and process implementation, developing national ePayment and ecommerce systems regulatory framework .
Sofiane Chafai has published multiple articles in magazines and is a regular speaker at international conferences. Sofiane Chafai is fluent in English, French and Arabic.
Satyan Abraham
Director ICT Infrastructure, DXB Entertainments
Satyan holds a Master’s degree in Business Administration from London Business School , UK and a Bachelors in Computer Engineering from Bombay University,
An astute technology leader with over 20 years’ experience across multi-national organizations : Emirates Airline, Compaq, Tandem, DXB Entertainments, Dubai Parks & Resorts, he has led transformational changes across various organizational portfolios, delivering significant cost reductions and building capability of people, processes and technologies
He has extensive experience in the air transportation and entertainment industry , having successfully implemented a number of large-scale IT projects with a direct impact on passengers and customer experience.
He has a strong track record leading organizations from vision through execution. Successfully established operating models through driving consolidation, standardization, architectural road-maps, strategic sourcing, shared services.
He is passionate about digital innovation and his main interest is in contributing to the improvement of customer experience in the entertainment industry through the introduction of innovative concepts and solutions.
Tim Sandwell
Director, Barclay Simpson
Tim joined Barclay Simpson, a governance recruitment company, in 1991 and has gained immense experience in governance recruitment across all sectors. Tim is responsible for Barclay Simpson’s Middle East Division which recruits across all areas of governance including security and resilience, internal audit, compliance and risk.
Tim has an in-depth understanding of the market for governance professionals in international markets and is able to draw on both an extensive network of contacts built up over twenty five years and the experience to advise on the most effective approach to any recruitment challenge. He undertakes both local and global searches and has placed a diverse range of corporate governance executives into the middle East region.
Sponsors
/uploads/2018/09/ISACA-Rome-logo-from-web.png)
/uploads/2017/01/anomali-logo@2x.png)
Anomali @2x
/uploads/2017/08/BeyondTrust-Logo.jpg)
BeyondTrust
BeyondTrust is a global cyber security company dedicated to proactively eliminating data breaches from insider privilege abuse and external hacking attacks. Corporate and government organizations rely on BeyondTrust solutions to shrink attack surfaces and identify imminent threats. The company’s integrated risk intelligence platform presents a unique competitive advantage in its ability to reveal critical risks hidden within volumes of user and system data. This unifies IT and security departments, empowering them with the information and control they need to jointly prevent breaches, maintain compliance, and ensure business continuity. BeyondTrust’s privileged account management and vulnerability management solutions are trusted by over 4,000 customers worldwide, including over half of the Fortune 100.
/uploads/2017/08/BarclaySimpson-logo-new.jpg)
BarclaySimpson
/uploads/2017/08/RiskCrewLogo@1.5x-e1521456105243.png)
Risk Crew
Risk Crew is an elite group of product-independent, information governance, risk, and compliance management professionals. We’re the forerunners in the design and delivery of effective business information and communication technology risk and security solutions. We understand business risk and compliance and so we also excel in the creation of operative controls and processes to cost-effectively comply with legislation, regulation and best commercial practices such as the Payment Card Industry (PCI), Data Security Standards (DSS), the UK Data Protection Act (DPA) and ISO/IEC 27001. Risk Crew take great pride in the depth and breadth of our technical and tactical knowledge and will work to ensure that it’s fully leveraged to provide the greatest benefit to your business objectives. We also put skin in the game and guarantee all of our services. Consequently, we are the selected supplier of choice for hundreds of businesses in virtually every commercial sector across the United Kingdom. www.riskcrew.com
Join the Pulse Sponsor Community!
/uploads/2023/01/all-Sponsors-banner.png)
All Sponsors Banner
ISACA UAEJoin the Pulse Sponsor Community!
/uploads/2017/08/all-Sponsors-banner.jpg)
All Sponsors Banner
Who attends
Designations
- Chief Information Security Officer / Head of Information Security
- Director Cybersecurity / Cyber Threat Intelligence
- Director Security / Security Operations
- Director Monitoring / Response
- Chief Operations Officer / Director Operational Risk
- Director Security Planning / Risk / Innovation
- Director Fraud / Payments
- CIO / Director – ICT / IT Governance
- Chief Risk Officer / Compliance
- Chief IT Auditor / Head IT Audit
- Group Business Director and Senior In-house Counsel
Industries
- Aerospace & Defence
- Automobile
- Banking
- Central Government
- CERTs
- Construction
- Consumer Goods
- Government
- Healthcare & Pharmaceutical
- Industrial Engineering
- Insurance
- Internet
- Legal
- Manufacturer
- Media
- National Law Enforcement
- Energy
- Real Estate & Business Conglomerate
- Regional Government
- Regulator
- Retail
- Software
- Telecommunications
- Transportation/Shipping
- Travel/Leisure/Hospitality
- Utilities
Venue & Accommodation
Palazzo Versace Dubai
Culture Village, Al Jadaf – Dubai – United Arab Emirates
http://www.palazzoversace.ae/en/default.html
CISO 360, Middle East will be hosted at Palazzo Versace Dubai, a 5 star luxury retreat, set in the heart of the Culture Village, less than 15 minutes away from Dubai International Airport. Reminiscent of a 16th century Italian Palace, Palazzo Versace Dubai is a Neoclassical masterpiece with subtle traces of Arabian architecture. Featuring a striking entrance, high ceilings, landscaped gardens, and a range of well-crafted Italian furnishings, the hotel is truly symbolic of the Versace lifestyle.
Accommodation
The hotel’s 215 luxury rooms represent classic Italian design, reflecting the true essence of the Versace brand. Luxury’ lies in the material – parquet flooring, a canvas of elaborate white and cream boiseries, and a pastel palette of silk furnishings. The Palazzo Versace’s rooms and suites are furnished with the Versace Home Collection that features uplifting colours of turquoise, blue, beige, gold, and salmon.
Discounted accommodation rates
Pulse Conferences can offer discounted prices for accommodation at Palazzo Versace at AED 900 / £175, single occupancy per night. Please click on the button below to book or contact sanna.lindstrom@pulseconferences.com for more information.
Archived 2018 accommodation information; these are not current rates.
Conference venue
The magnificent Gala Ballroom at Palazzo Versace provides the perfect setting for the highly anticipated CISO 360 Middle East Congress. All facilities are elegantly furnished and equipped with state of the art audio visual equipment, from inbuilt ceiling speakers, LED TV Screens and iPad for systems control. Wireless internet is available in all public spaces to allow guests to remain connected throughout the duration of the event
In addition, the self-contained Conference Center area features a variety of versatile function spaces for one-to-one meetings as well as the Pre-Function area connected to the Gala Ballroom and meeting rooms. It is the perfect space for the exhibitions, coffee breaks and networking.
Location
Set in the heart of the Culture Village, less than 15 minutes away from Dubai International Airport and 8 minutes away from Burj Khalifa and Downtown Dubai, Palazzo Versace Dubai is conveniently located along the shores of the historic Dubai Creek.
- 15 minutes away from Dubai International Airport
- 8 minutes from Burj Khalifa and Downtown Dubai
- 8 minutes from Dubai International Financial Centre and the Dubai business district
- 3 minutes to the Al Jadaf Metro Station
- 5 minutes to Dubai Festival City Mall and 8 minutes to Dubai Mall
Gallery and resources
Download Presentation materials
Download Articles and whitepapersTestimonials – CISO 360 Series
The source archive includes feedback and videos from CISO 360 events across several years and locations.
“If you want to hear real CISO experiences, you must attend this event!”
Chuan-Wei Hoo, CISO, ST Engineering, Singapore
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
Thomas Foster, SailPoint
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.”
Martyn Booth, CISO, Euromoney Institutional Investor PLC
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
Synack
“Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
Catherine Coale, Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus….”
Joe Breen, Company85
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
James Gosnold, Technology Services Head of Cyber Security, DWP
“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Philippe Besson, Europe Industries- Security Officer, Air Liquide GMS
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Colette Hanley, Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
Ben Bulpett, SailPoint
“By far the best event for 2018 I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Ali Zeb, Group CISO and Group DPO, MS Amlin
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding lineup of events from your organization!”
Christopher Rollan, Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
Ali Zeb, CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”
Joe Dauncey, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
David Colbourne, Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Michael Colao, Head of UK Security, AXA
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
Brian Brackenborugh, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Sérgio Gonçalves, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.”
Chucks Ojeme, CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Quentyn Taylor, Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under Chatham house rules. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during 1×1 networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISO’s across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Stephen Khan, Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
Pedro Cunha, CISO, Credibom
“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
Sponsor testimonial, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”
James Kwaan, President, (ISC)2 Scotland Chapter
“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
Luis Vilares, GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Irene Corpuz, Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!.”
James Chuka, Sailpoint
“I found CISO360 Conference a great place to share ideas about current and future problems”
Sonia Morales, Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Ramón Serres, Head of Information Security, Risk Management and Quality, Almirall
“Pulse organised a fantastic CISO360 conference in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO360 and look forward to this conference going from strength to strength”
FC, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
“Excellent conference, brilliantly put together. Look forward to the next one.”
Anthony Young, Partner, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Irene Corpuz, Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018
“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Sergio Goncalvez, Corporate Security Manager, Logista
“Marvellous event, well-run, packed with useful content you can use”
James Gosnold, Technology Services Head of Security, DWP
Contact
Telephone: +44 (0)20 3455 9444
Email: teampulse@pulseconferences.com
Sponsorship: sponsorship@pulseconferences.com
Pulse Conferences on LinkedIn