
4th CISO 360 Middle East
9-10 February 2023
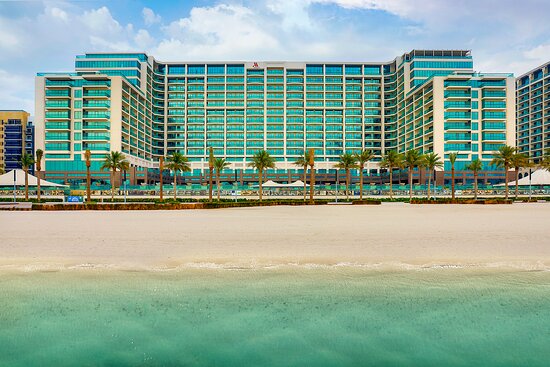
Marriott Resort Palm Jumeirah, Dubai | United Arab Emirates
Cybersecurity Strategies to Build Trust and Resilience
Many thanks to all those who participated in this years’ Conference!
Submit your feedback from the event here.“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!“ Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“ Head of IT, GOPA International Energy Consultants (Abu Dhabi)
Many thanks to those who joined the Middle East’s trusted community for Chief Information Security Officers and leaders in cybercrime, technology, risk and assurance to share strategies and benchmark roadmaps!
The 4th CISO 360 Middle East Conference – Dubai 2023 brought together CISOs and international cybersecurity leaders from the GCC region and from around the world for truly immersive discussions. As today’s CISOs move towards an uncertain future and unknown cyberspace, be privy to threat horizon updates and a toolkit focused agenda designed around CISO priorities! A problem shared is a problem halved!
We compared and shared how fellow CISOs are leading teams and driving their businesses forward, and we heard inspiring technical tactics and visions for the future! We learned from those doing the job day in day out what challenges are faced, with an expanded attack surface created through digital transformation, complex supply chains as well as insider threats. We heard practical tactics on how we can build collective resilience and a culture of good cybersecurity governance to defend our organisations and how we might we tip the scales back in our favour.
Why CISO 360?
- Connect, innovate and leave inspired! Sit with peers who you know are largely facing similar risks and opportunities
- Benchmark in a trusted space! Engage with fellow CISOs, practitioners and for meeting technology luminaries
- Learn from business executives, risk managers and luminaries outside the security ‘echo chamber’
- Engage in meaningful interaction with CISOs, innovators, investors for business and collaboration
Key Themes for Dubai 2023 included:
- Secure Digital Innovation
- Mitigate Cyber Crime
- Achieve Cybersecurity Governance
International Speaker Panel included – Dubai 2023
- Dr. Hoda A. Alkhzaimi, President, Emirates Digital Association for Women (and Co-Chair for Global Future Council for Cyber Security, World Economic Forum) – United Arab Emirates
- Dr. Aloysius Cheang, Chief Security Officer Middle East & Central Asia, Huawei – United Arab Emirates
- Bart Pietruszka, Chief Data & Analytics Officer, HSBC Bank Middle East – United Arab Emirates
- Peter Ling, VP Global Cyber Security Alliances, Mastercard – Canada
- Dr. Abdullah A. I. Alnajem, Chief Cybersecurity Officer – Cybersecurity Department, Gulf General Cooperative Insurance Co. – Kingdom of Saudi Arabia
- Irene Corpuz, Co-Founder, Women in Cyber Security Middle East – United Arab Emirates
- Prakash Padariya, Global Chief Information Security Officer, OYO Group – India
- Rik Ferguson, Vice President Security Intelligence, Forescout – Poland
- Jelena Matone, CISO, European Investment Bank – Luxembourg
- Kais Barakat, Senior Information Security Specialist, Saudi Aramco – Kingdom of Saudi Arabia
- Ibraheem Khan, VP Information Security EMEA, Financial Services Company – United Kingdom
- Sylvain Hirsch, Cyber Security Strategy, Mandiant, now part of Google Cloud – Singapore
- Dr. Robert Coles, Head of Security Strategy, DS Smith – United Kingdom
- Lady Olga Maitland, President & Chairman, Defence and Security Forum – United Kingdom
- Matthias Muhlert, Security Bear – CISO, HARIBO – Germany
- Eng. Majed Alshodari, Co-Founder, Saudi Association for Shared Services; Board, Tatweer Educational Technologies – Kingdom of Saudi Arabia
- Joseph Makram, CIO, Egyptian Arab Land Bank (EAL Bank) – Egypt
- Dr. Viktor Polic, CISO, Head of Information Security and Assurance Services, ILO – United Nations – Switzerland
- Dr. Sally Leivesley, Managing Director, Newrisk London, Member of the Register of Security Engineers and Specialists (RSES) – UK
- Ray Stanton, CISO/CSO, Board Advisor/NED – United Kingdom
- Lorna Trayan, Executive Partner, Security and Risk Management, Gartner – United Arab Emirates
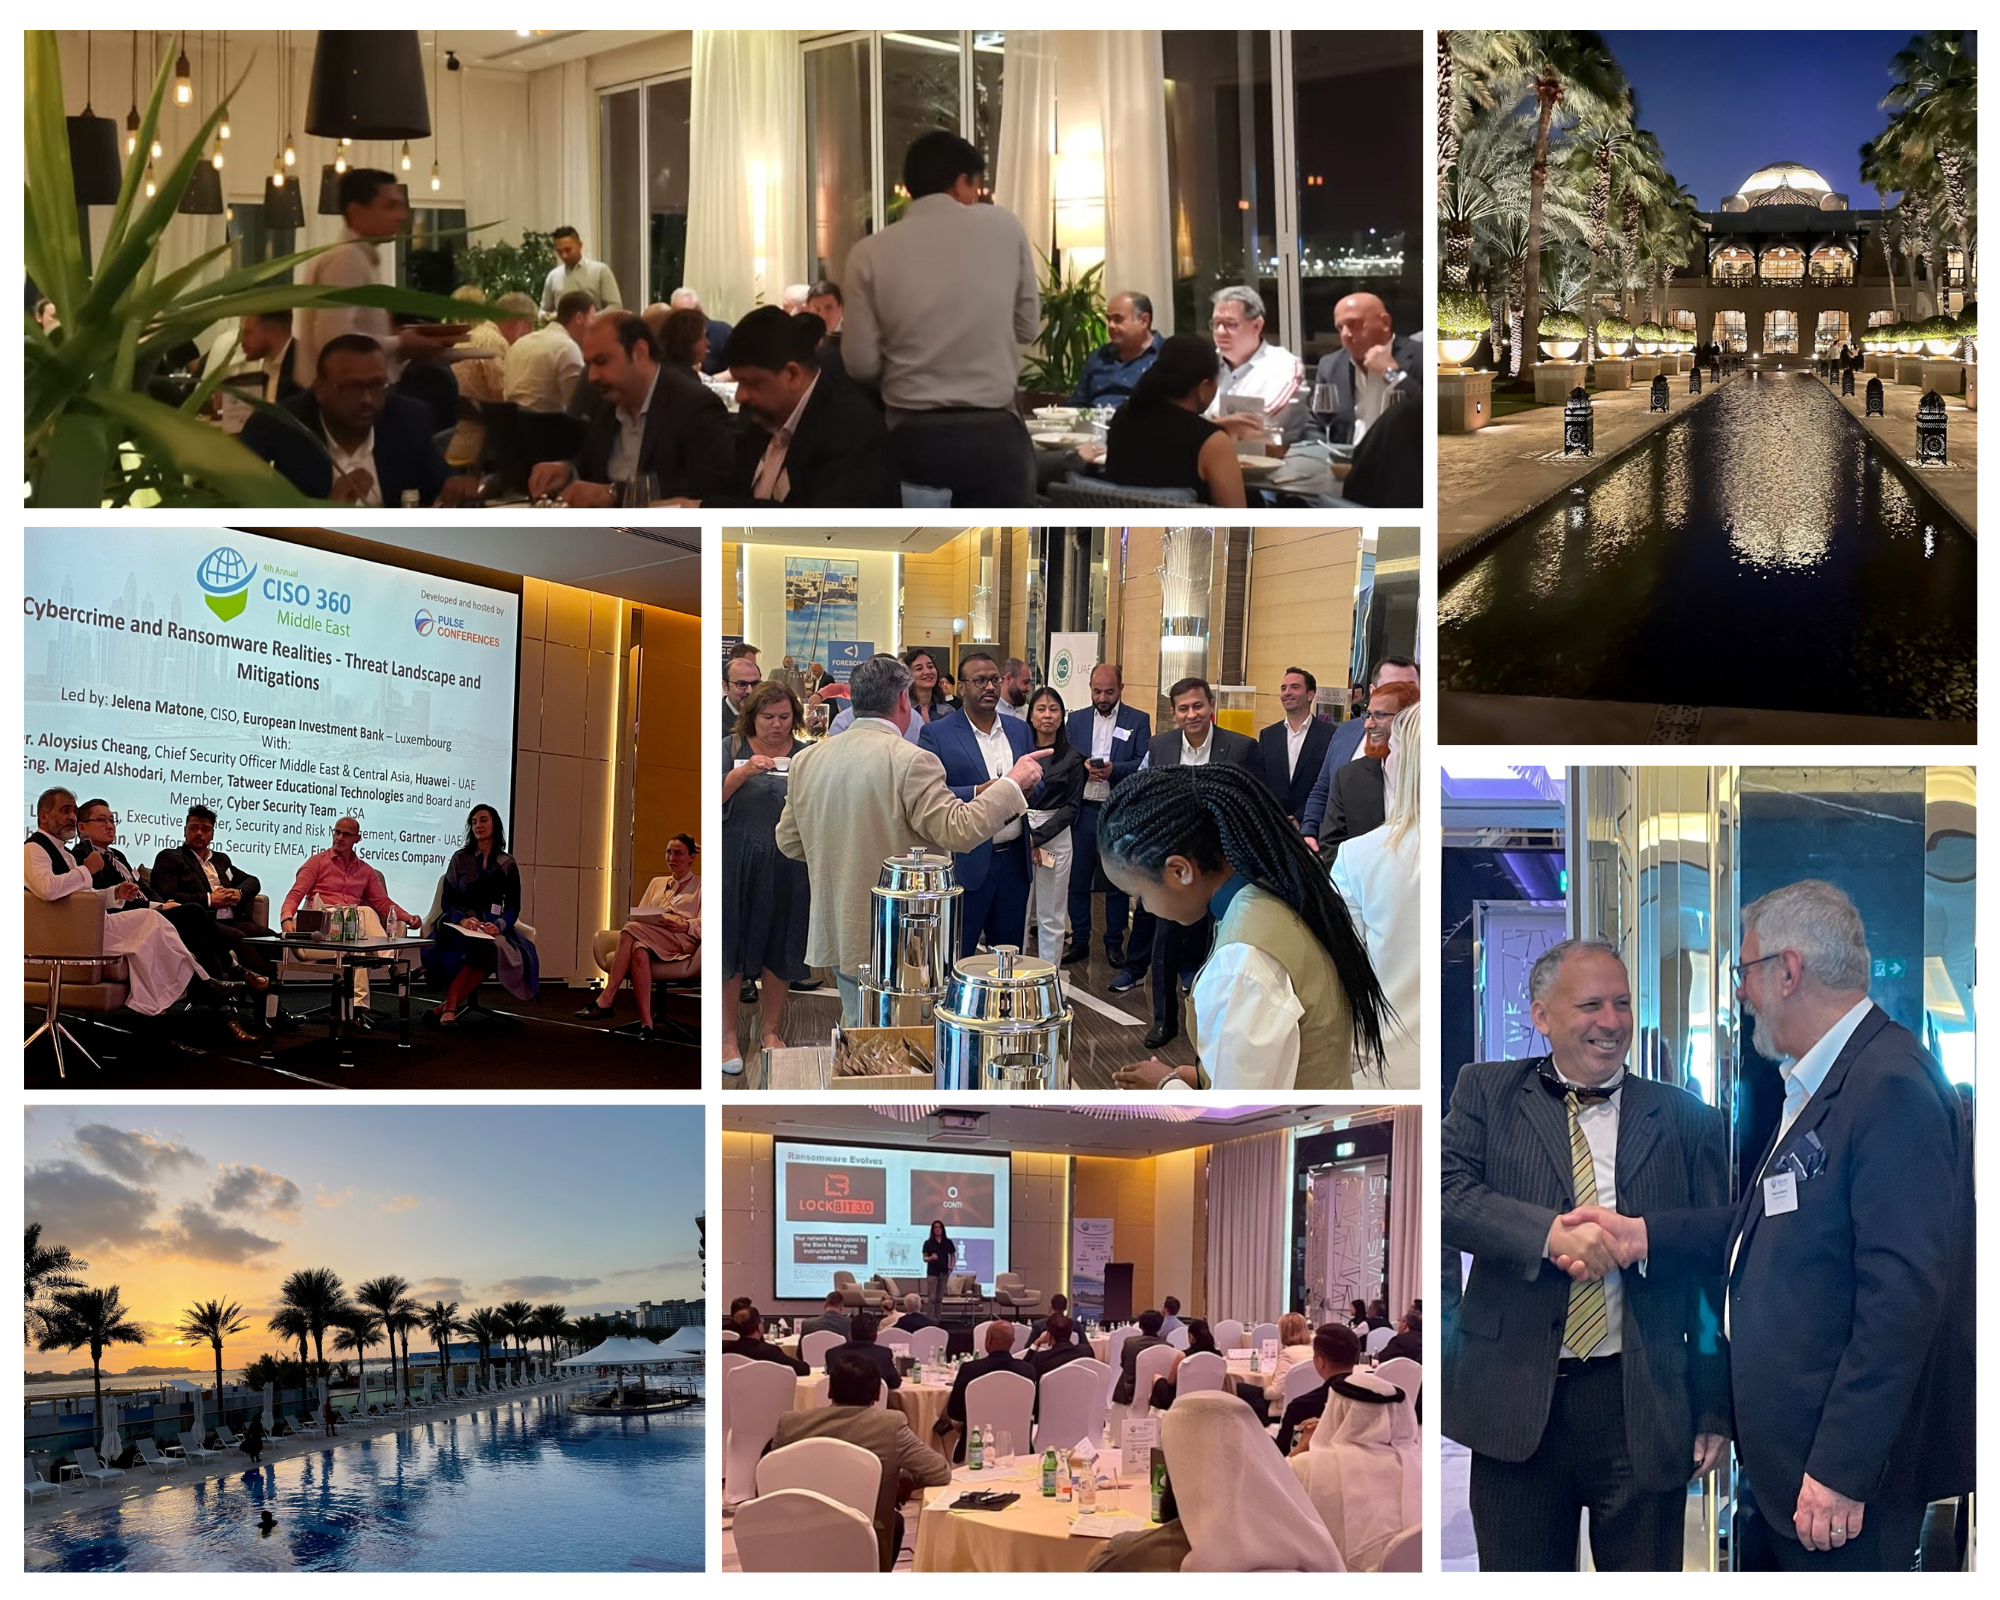
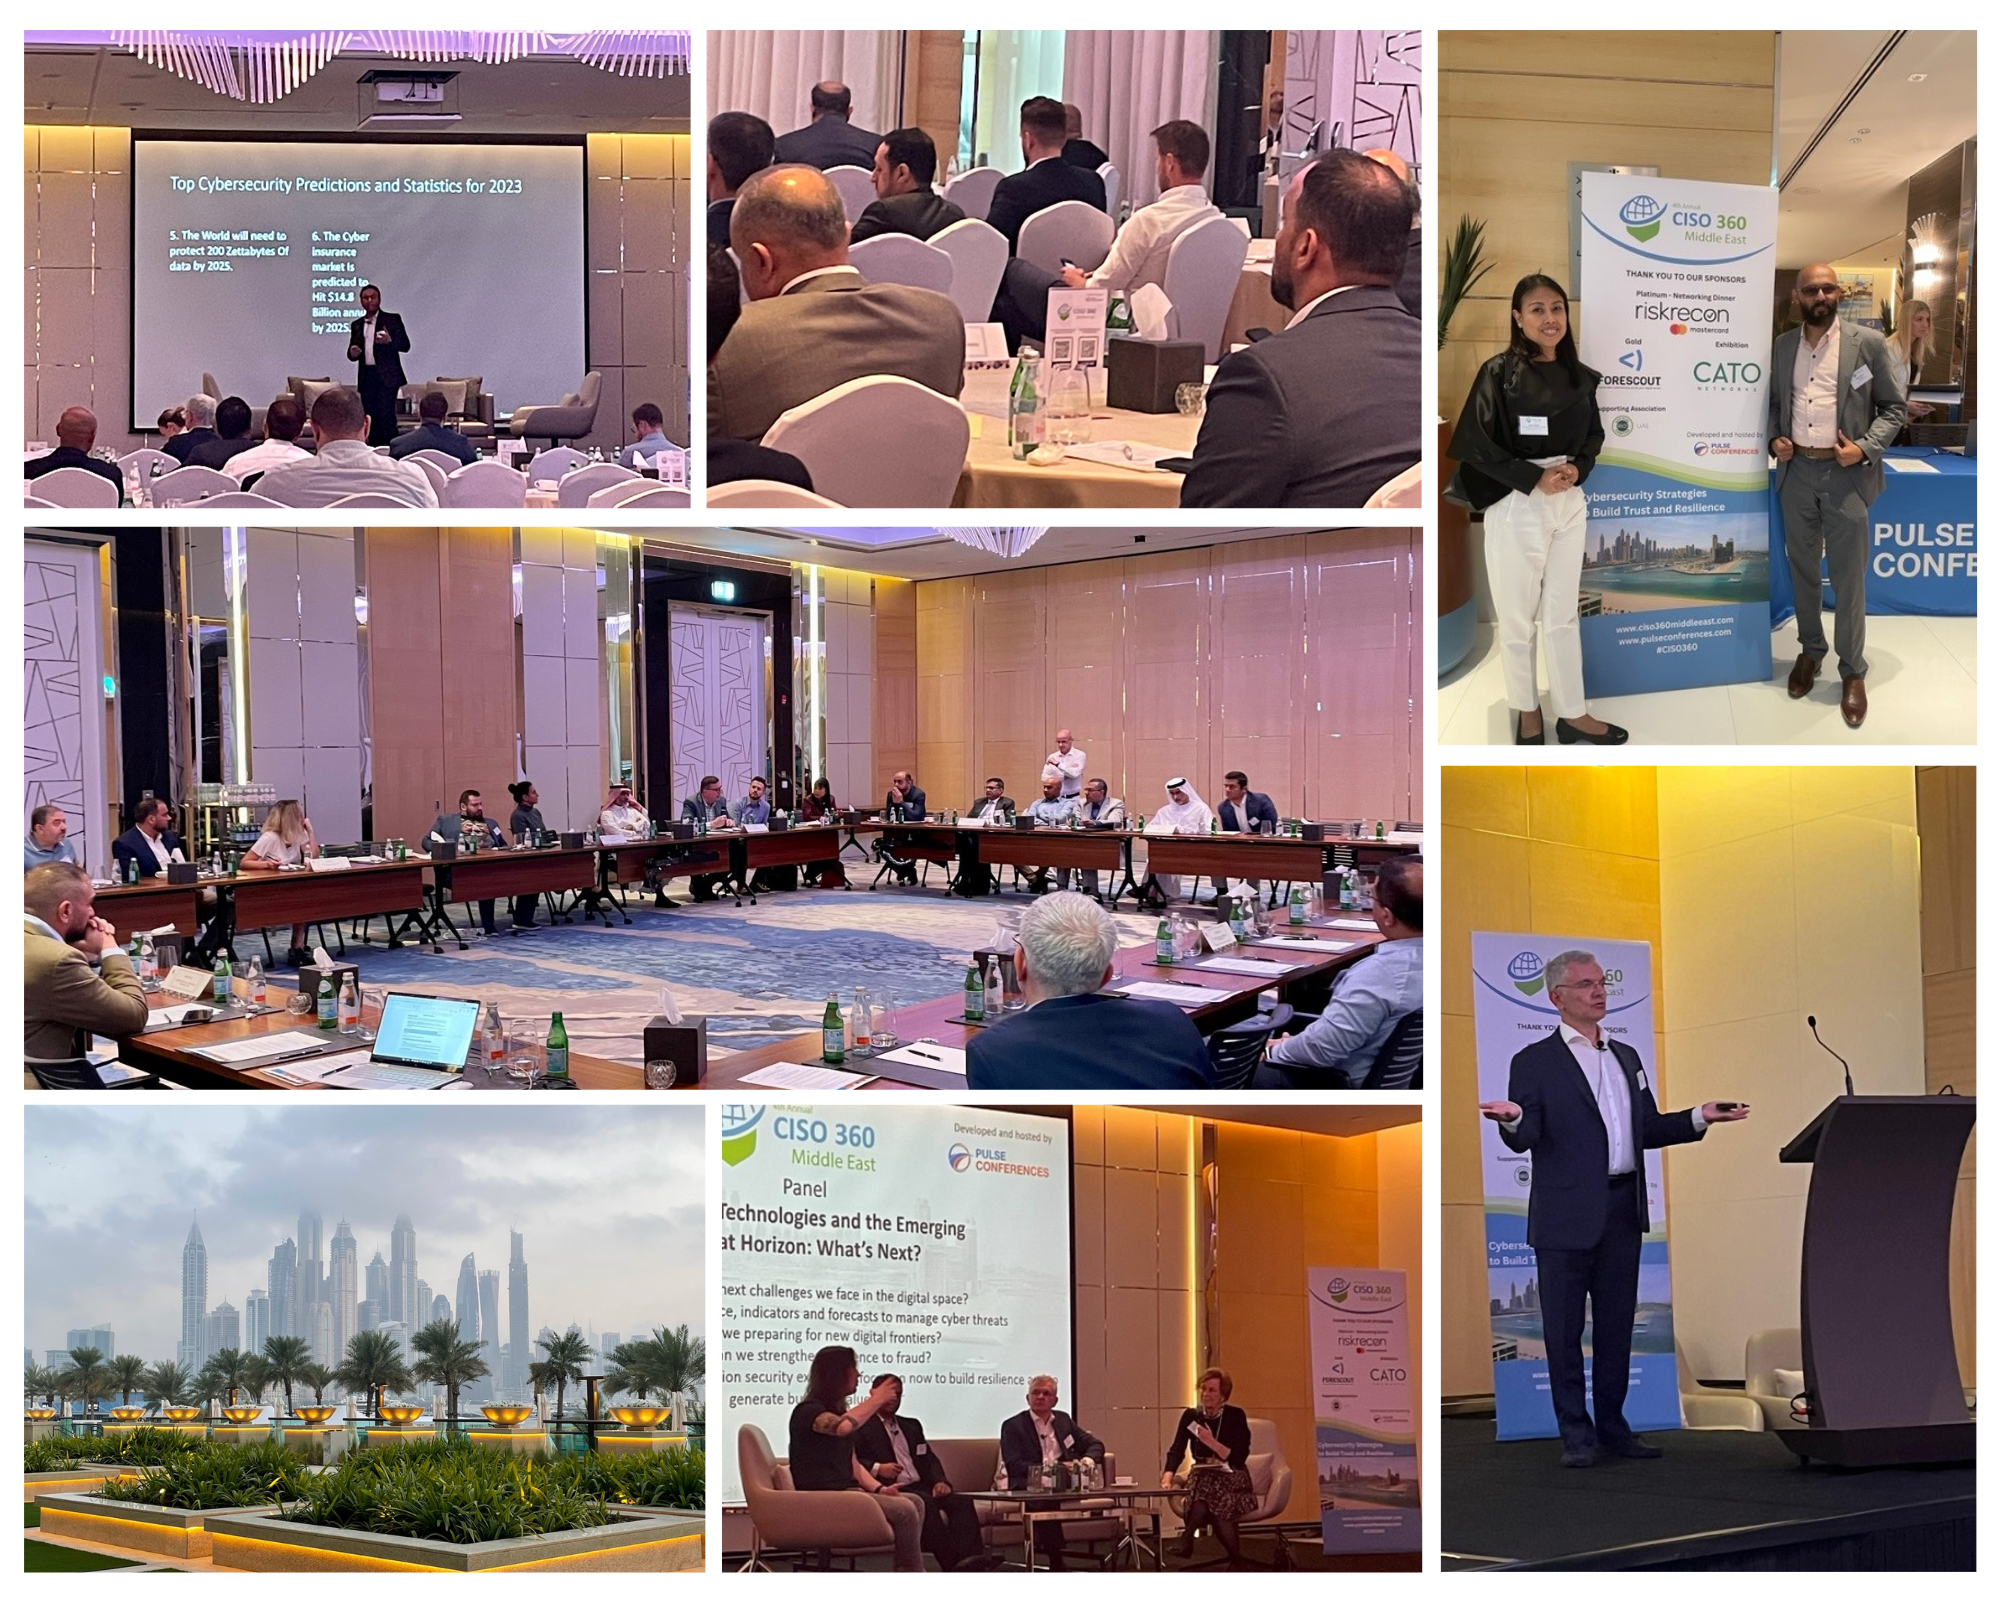
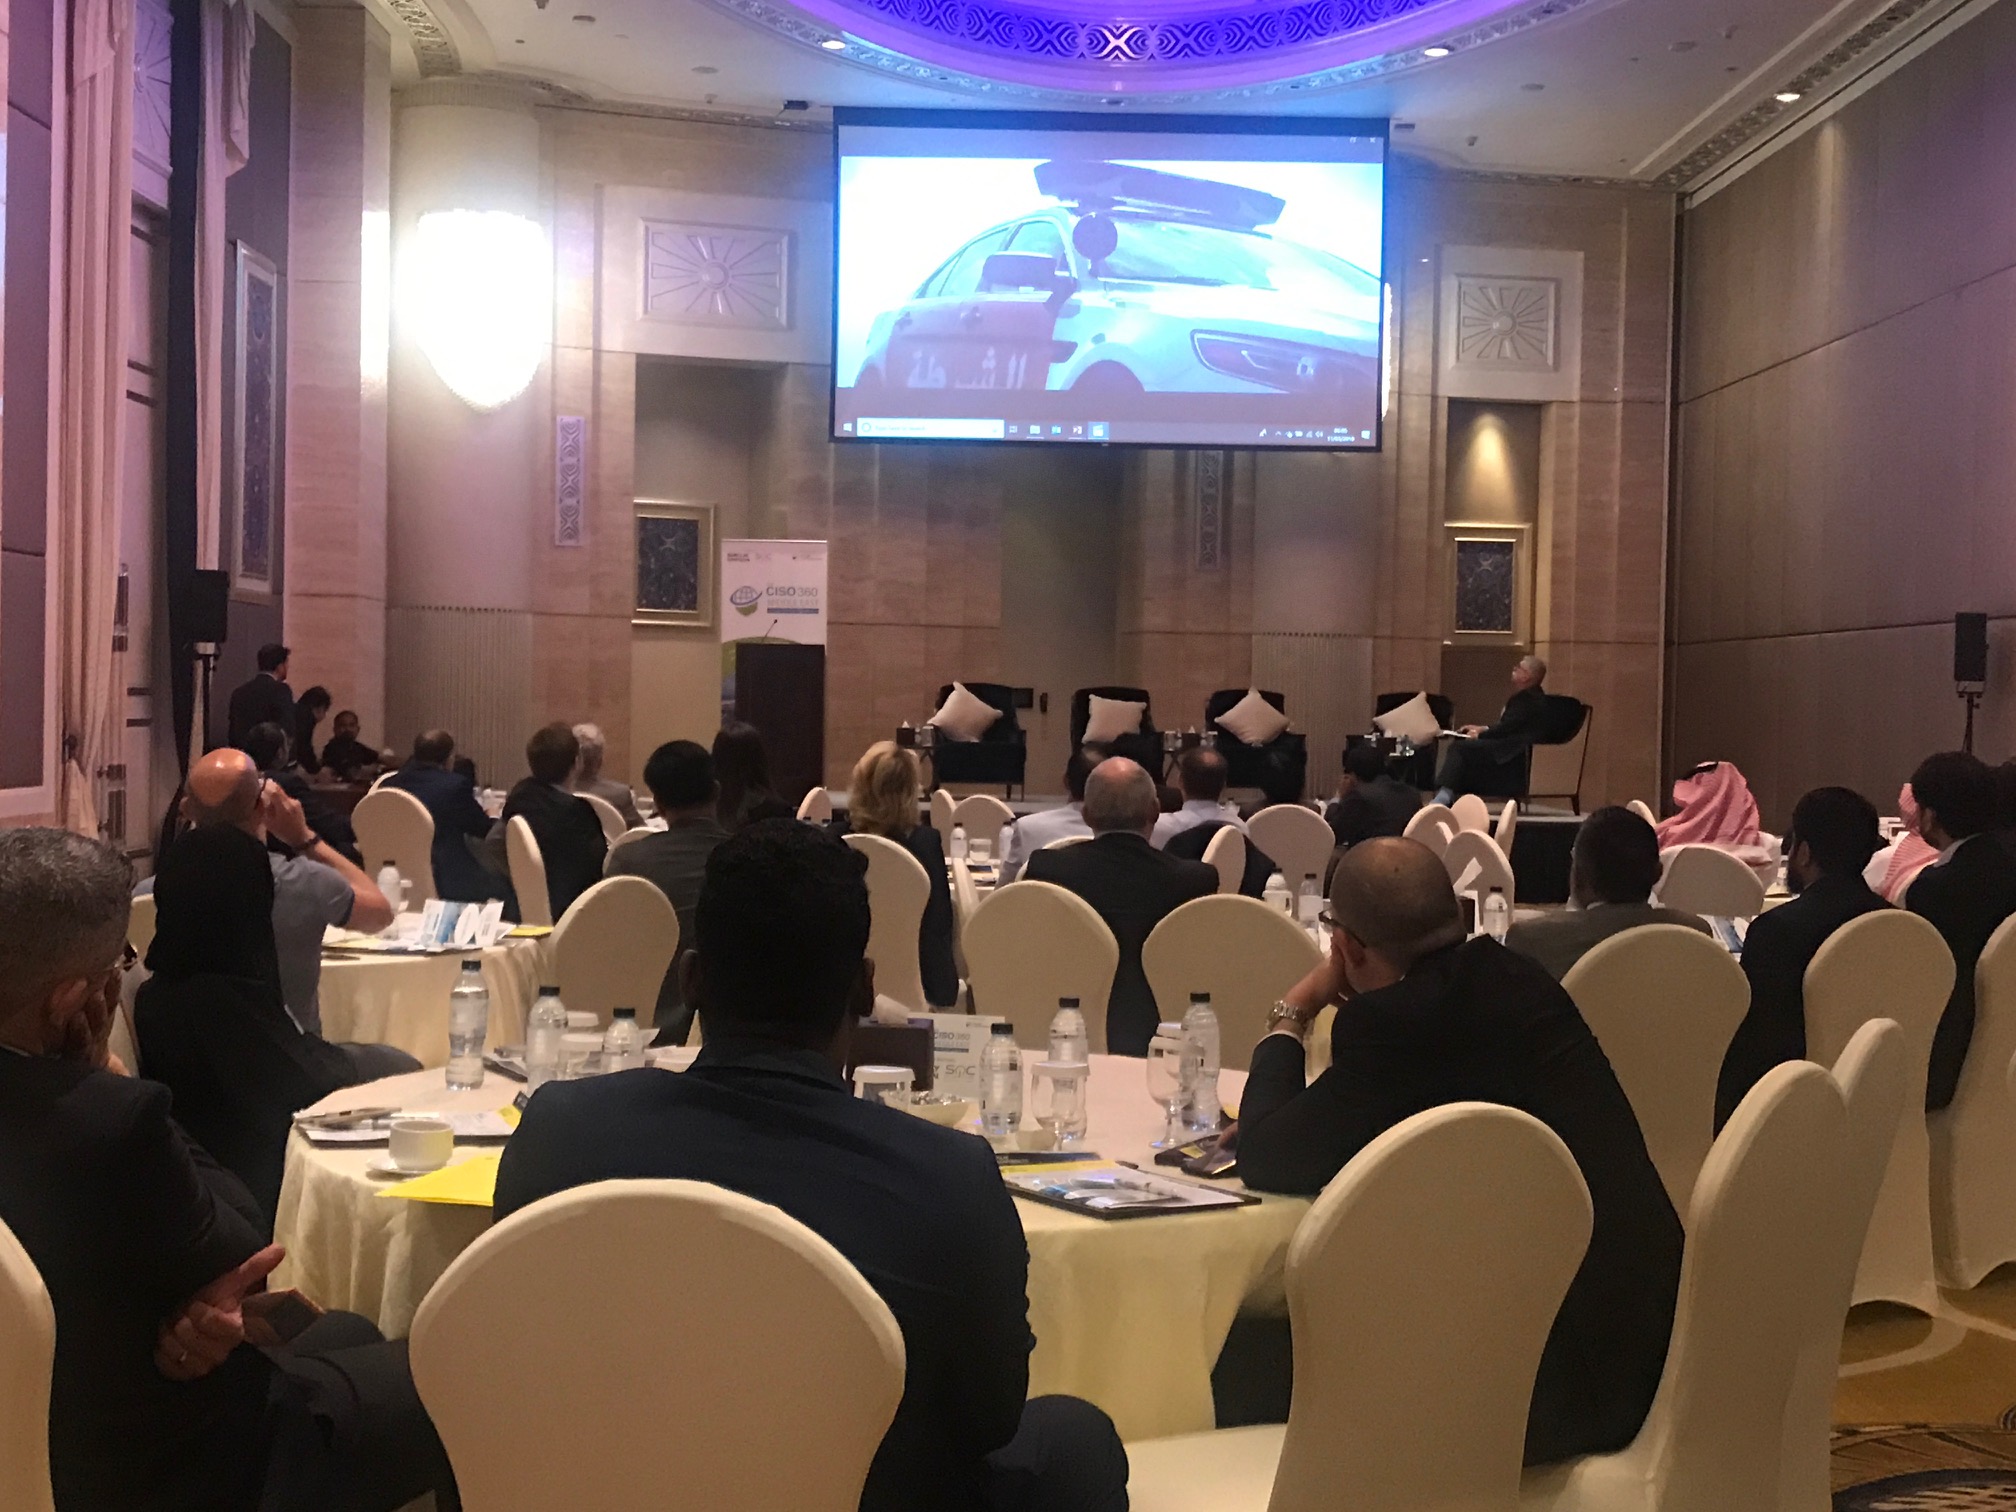
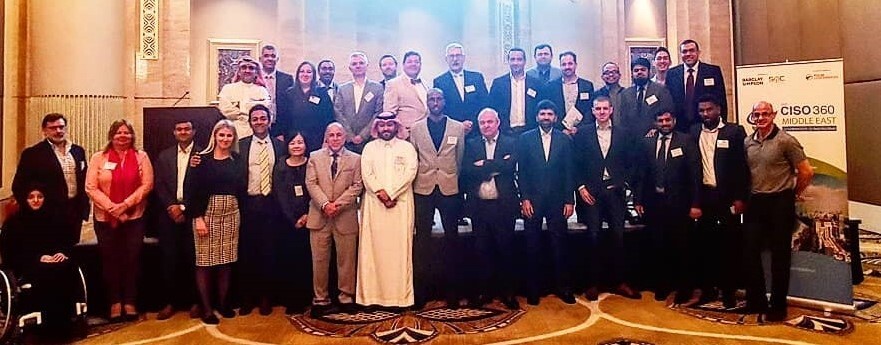
Highlights 4th CISO 360 Middle East - Dubai 2023!
Why CISO 360 Middle East?
The agenda will be as interactive as possible, with limited use of PowerPoint. We appreciate the effort that people have made to take time out of offices and to travel and be present. The Pulse commitment to you is that we will not present a programme that could have been watched online. Our events offer immersion and the opportunity to engage with peers from the host country, region and from around the world in person. You will leave with new professional friends!
Many thanks to our amazing Sponsors and Supporting Associations 2023
Platinum - Networking Dinner
Gold
Exhibition
Supporting Association
With thanks to our sponsors
Multi-event offers
Dr. Abdullah A. I. Alnajem
Chief Cybersecurity Officer - Cybersecurity Department, Gulf General Cooperative Insurance Co. - Kingdom of Saudi Arabia
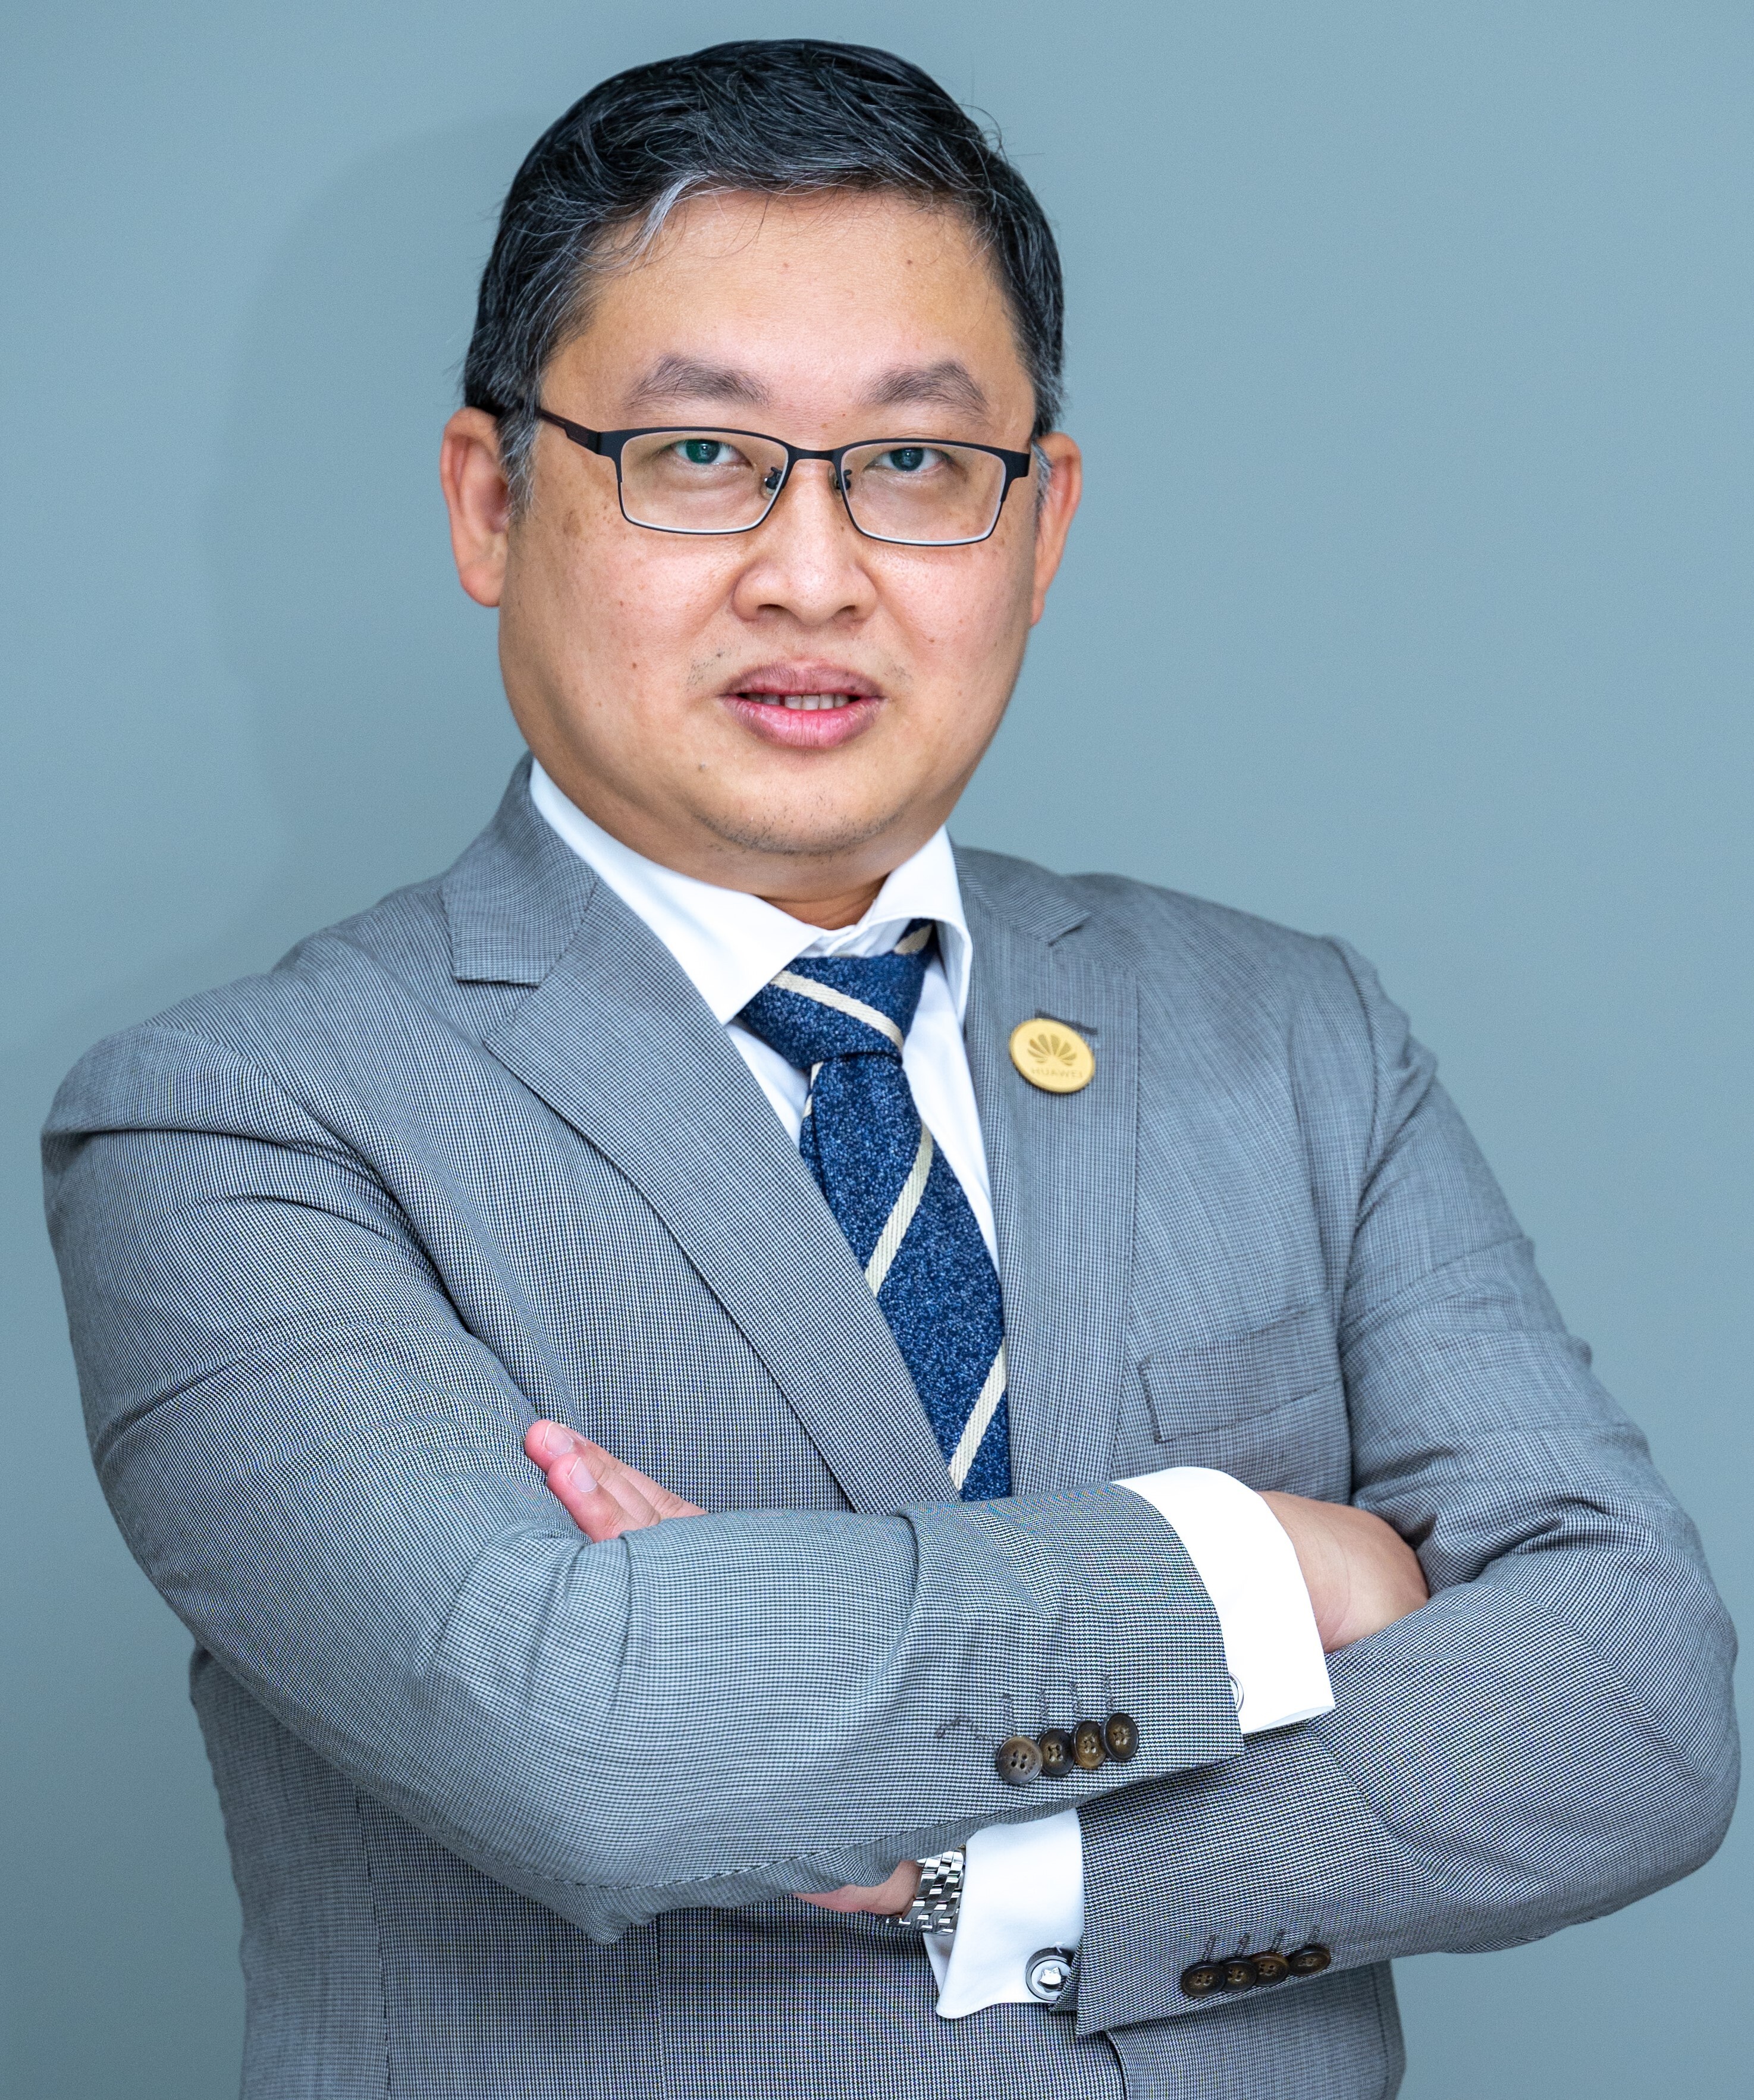
Dr. Aloysius Cheang
Chief Security Officer, Huawei Middle East and Central Asia
Aloysius Cheang is currently the Chief Security Officer of Huawei Middle East & Central Asia responsible for driving the company’s cybersecurity vision of building a safe and secure intelligent connected digital world geographically across 21 countries regionally and functionally across 57 countries globally.
He is a Board Director for UK-based cyber leadership think tank, the Centre for Strategic Cyberspace + International Studies (CSCIS) and most recently, for ISC2.
In his career spanning over 20 years, Aloysius had delivered direct business values in strategic, complex, multi-year and multi-million dollar technology and cyber program for Global 500 organizations worldwide while managing large multi-cultural, multi-disciplinary team spread across 5 continents and 4 major time zones time after time.
Prior to his current appointment, Aloysius was Co-Founder and Managing Director for Cloud Security Alliance Asia Pacific (CSA), the Worldwide Head of Security for Vodafone Global Enterprise and a Security Practice Leader with PricewaterhouseCoopers Singapore, having started his career with DSO National Laboratories in Singapore focusing on Defence R&D.
As a globally recognized cybersecurity expert, Aloysius defined the term “Cybersecurity” having authored the 1st edition of ISO/IEC 27032 “Guidelines for Cybersecurity” and his professional perspectives are highly valued by major international media such as the BBC, Times, Wall Street Journal, ZDNet, ISMG, MSN News, CXO Insights, Teletimes International, Xinhua News, SCMP, Phoenix Media, The Hindu, The Nation, Bangkok Post, Economic Times Daily, China Times, The Straits Times, ChannelNewsAsia, Zawya, The National, Gulf Business, ITP, Telecom Review, Teletimes, The National, Khaleej Times and Al Bawaba.
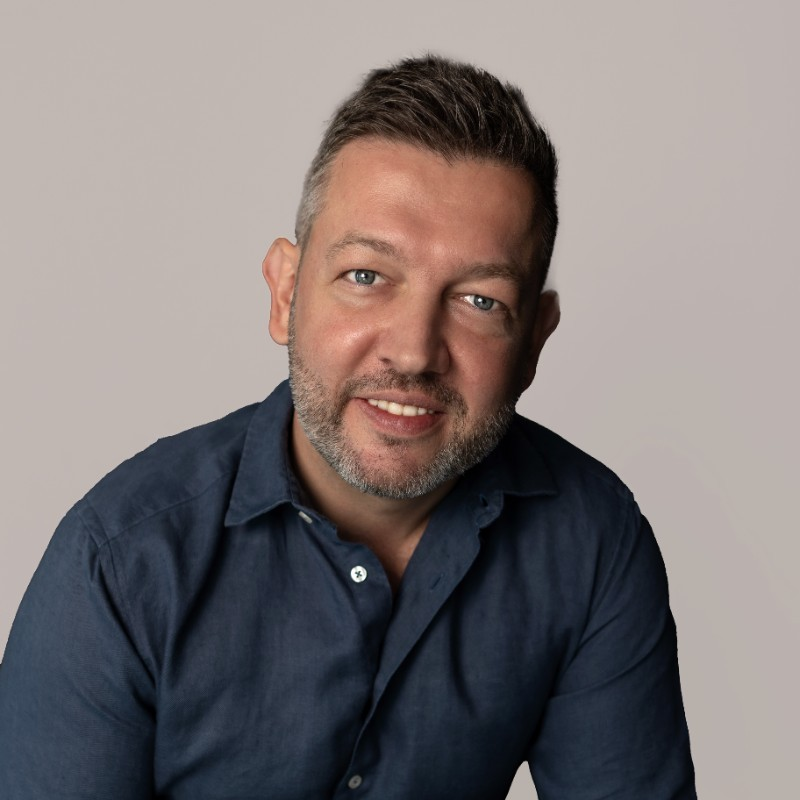
Bart Pietruszka
Chief Data and Analytics Officer, HSBC
Bart is the Chief Data & Analytics Officer at HSBC Middle East. He has been in the region since 2012 having worked in various leadership roles. Throughout his career, Bart worked for international companies, focusing on Finance, IT and Consulting. Bart is a thought leader in CDO & Analytics holding two Master’s degrees: in IT (Scotland) and in Economics (Poland). He is also a public speaker and a data evangelist currently working with big data & analytics experts spanning across all industries.
George Eapen
Global CIO and CISO, Petrofac - United Arab Emirates
Currently serving as Group CIO of Petrofac (FTSE 250) and In this remit, i am leading the Digital transformation of the Company, building best in class Cyber capabilities and develop Digital products to deliver better business outcomes for Customers . I am also driving the Cloud transformation program in the Company where we are upgrading our technology landscape (1000+ Applications) and also implementing ERP Fusion Cloud. I am leading a Global team of 500 IT professionals to support a global work force of 12000 employees based across US to Asia Pacific.
Before joining Petrofac, i spent 13 years with General Electric (GE) where I had an accelerated and diverse career with experience in multiple international executive leadership roles in Cybersecurity, Digital transformation and Technology space. My most recent role at GE was heading Cybersecurity practice for GE International regions ($60B revenue) as a CISO with a team of 100 employees.
George is a graduate of GE IT leadership program (ITLP), GE Six Sigma Black Belt program and graduate of GE Corporate Audit Staff (CAS), a fast track Executive leadership program of GE
George is an International speaker on multiple Cyber Security conferences including IBM Think 2020, Microsoft Ignite 2019, RSA 2022.
George is also Board of Advisor for IBM Security, Continuity Software and Seed Group.
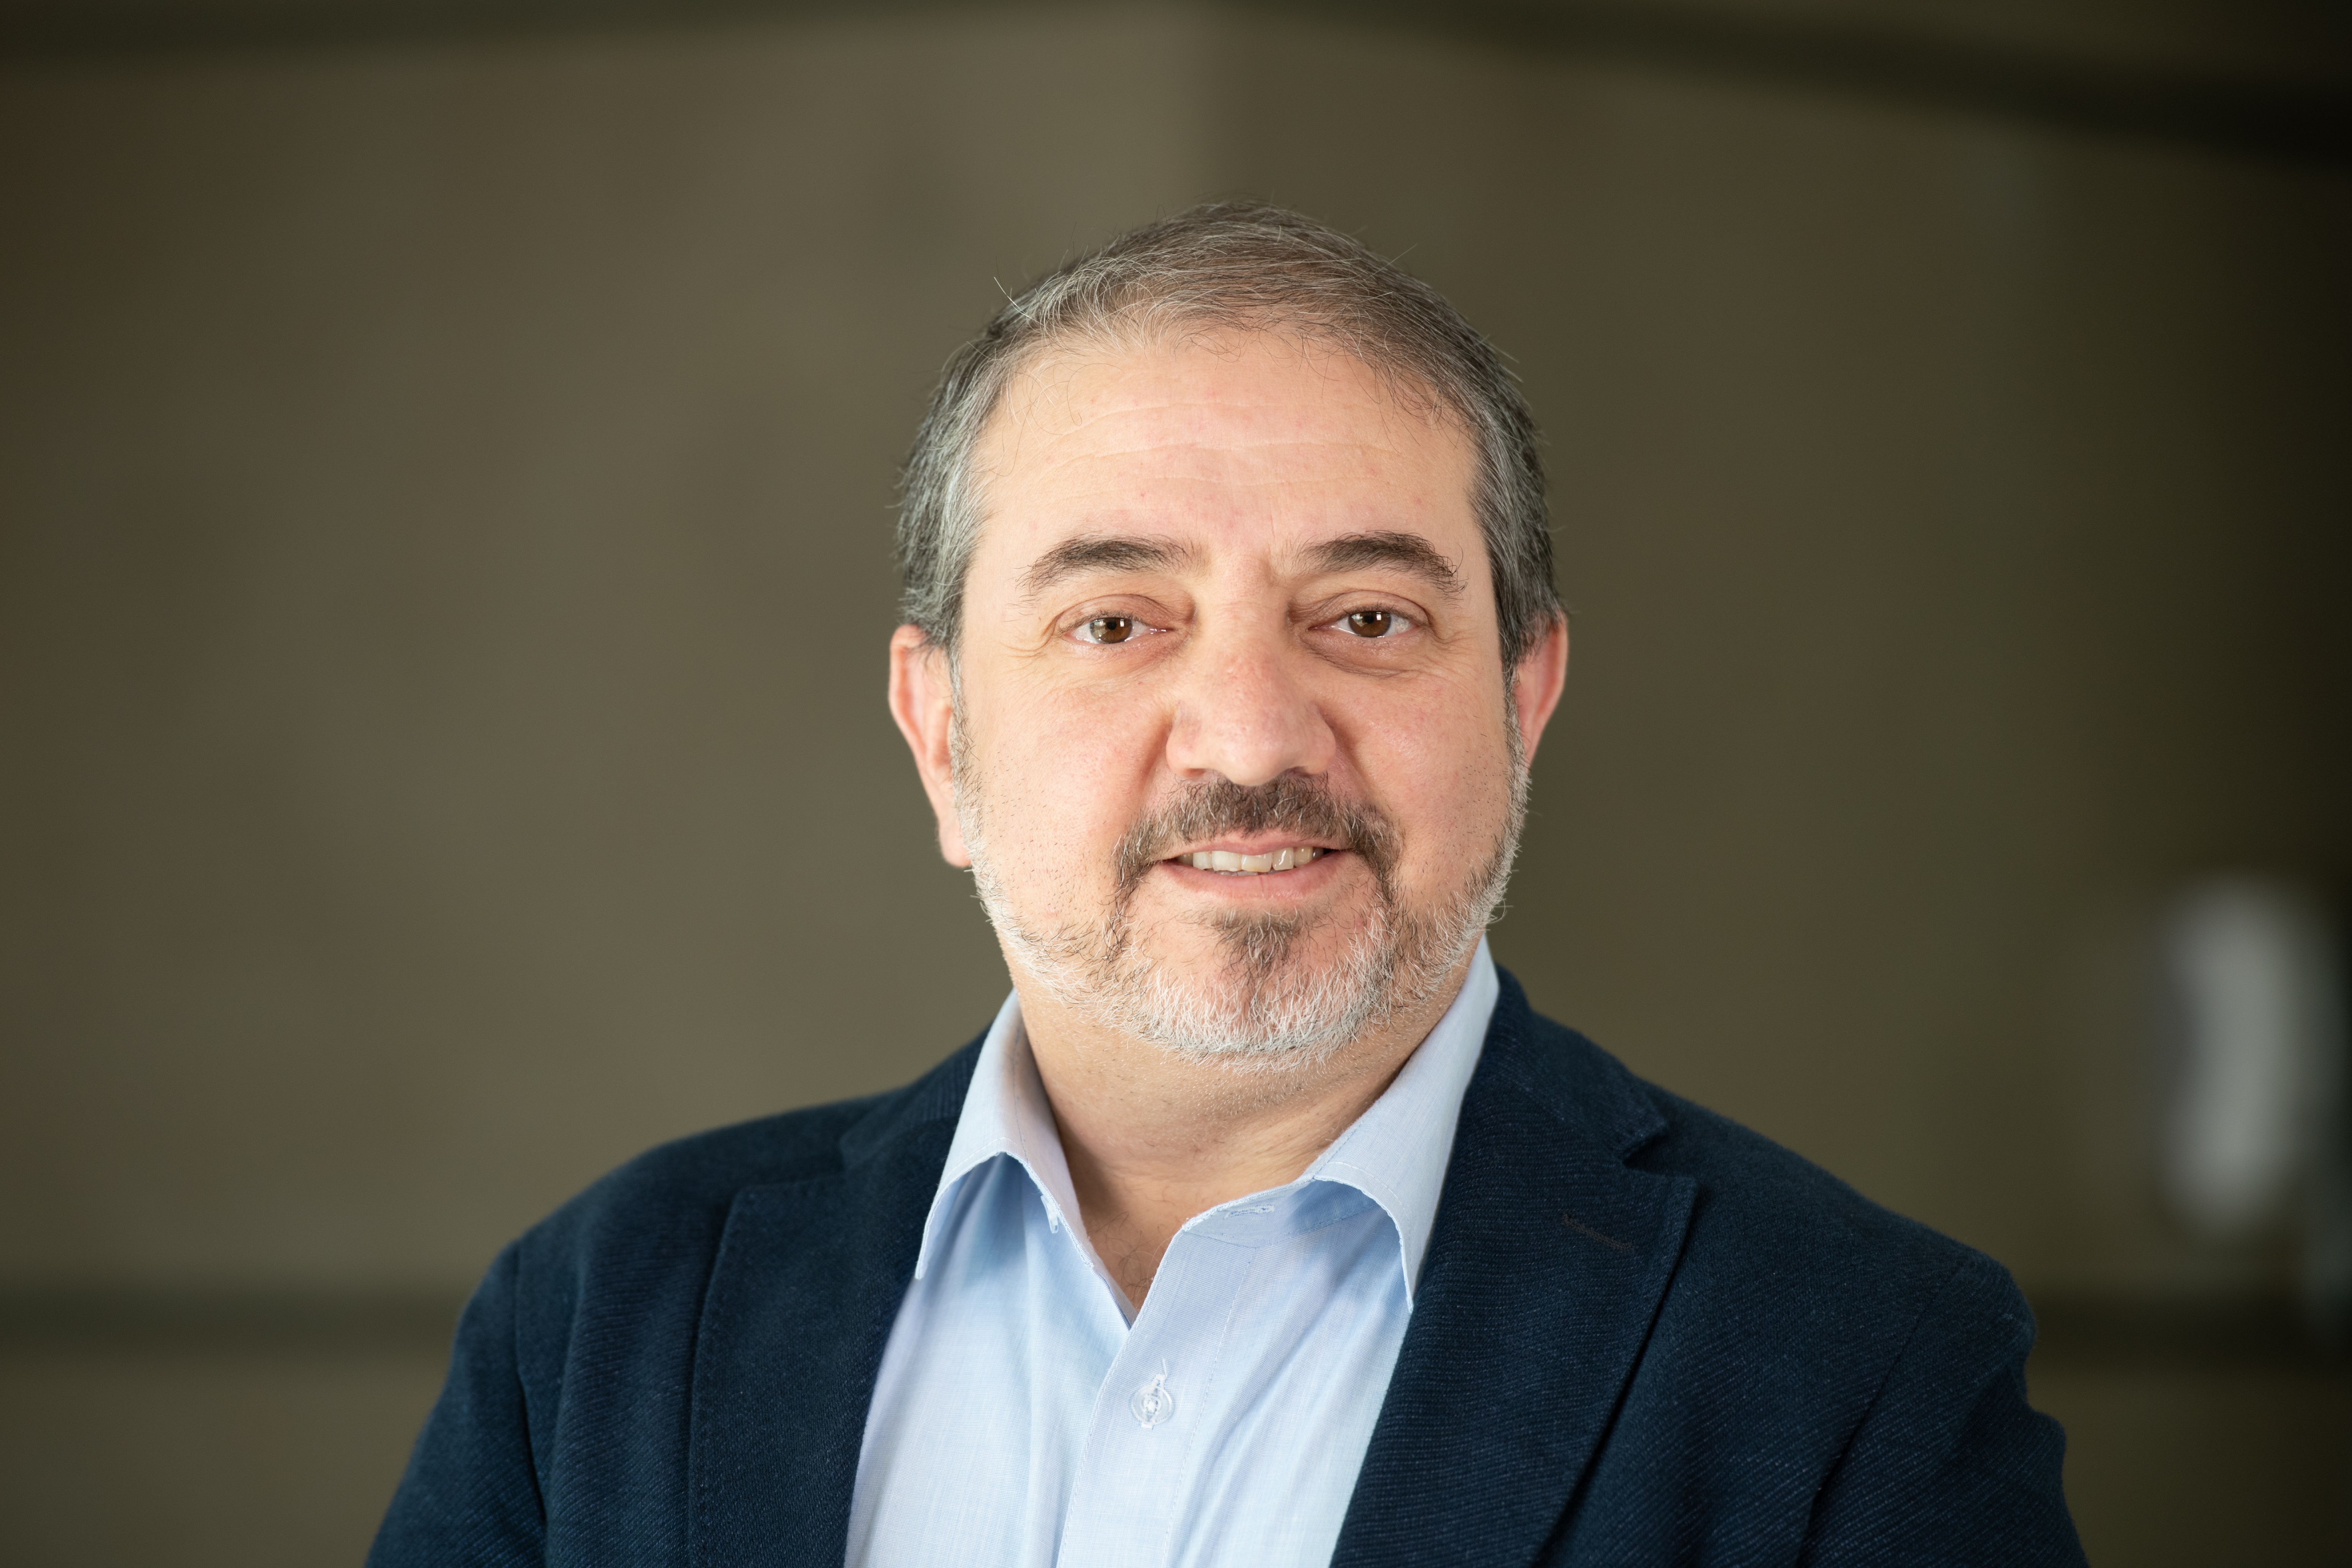
Kais Barakat
Senior Information Security Specialist, Saudi Aramco - Kingdom of Saudi Arabia
Kais Barakat is a senior information security specialist and business process excellence engineer with a successful track record of over 25 years in diversified areas within IT and Information Security. In the last few years Kais played a major role in transforming the Information protection program and GRC functions within Saudi Aramco. Kais is PMP, CISM, ISO 27001, CRISC, COBIT 5.
Ibraheem Khan
VP Information Security EMEA, Financial Services Company - United Kingdom
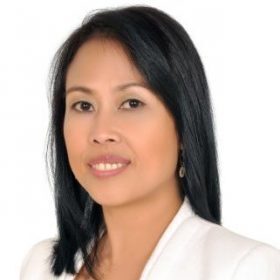
Irene Corpuz
Manager, Co-Founder, Women in Cyber Security Middle East - United Arab Emirates
Irene is responsible for the execution of the ADSIC Information Security Programme, Security Governance, Risk and compliance to IT Security Policy. She offers 27 years of combined and diverse experience in IT (Security, Operations and Strategy), Quality & Excellence. She has worked in various industries and region and led strategic initiatives in Asia, Middle East, Europe and America. An emerging seasoned speaker on Information and Cyber Security Conferences, Irene has spoken in a number of conferences in Asia, Middle East and Europe. Irene acquired her Masters of Science in IT from University of Wales, and holds the following certifications: ITIL V3, PMP, ISO (QMS and 27k) Lead Auditor and EFQM Assessor. Irene is Co-Founder of Women in Cyber Security Middle East, which promotes and increases women’s participation in the field of cyber security. www.womenincybersecurity.me
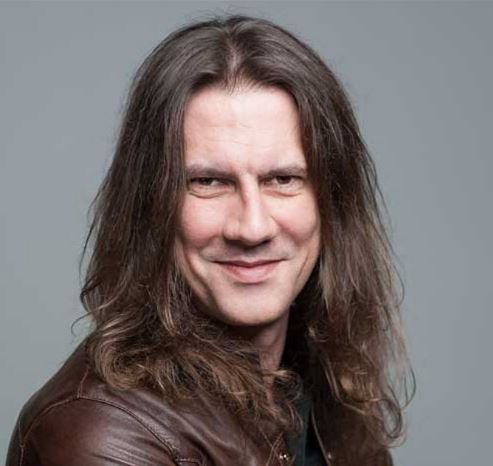
Rik Ferguson
Vice President Security Intelligence, Forescout
Rik Ferguson is the Vice President of Security Intelligence at Forescout. He is also a Special Advisor to Europol’s European Cyber Crime Centre (EC3), a multi-award-winning producer and writer, and a Fellow of the Royal Society of Arts. In April2011 Rik was inducted into the Infosecurity Hall of Fame. Rik isa researcher, storyteller, and futurist. He helps governments, law enforcement, businesses and individuals to understand the complexities of technology, and its intersection with cybercrime, contributing to global initiatives to combat cybercrime and reduce risk through participation at the United Nations, European and national Parliaments. Over his twenty-five plus years of professional practice, he has taken deep dives into the cybercriminal underground and helped the wider world understand the threats of today and how those threats might evolve over time. A recognised futurist and world-renowned speaker, Rik has spoken at global events including RSA Conference, Mobile World Congress, Milken Institute, RUSI, GITEX, Infosecurity, Virus Bulletin, e-Crime Congress, IPExpo, CloudExpo, Webit, GovSec, and many more, and is often quoted by media around the world. Rik joined Forescout in 2022. Prior to assuming his current role, he served as Vice President Security Research at Trend Micro for 15 years Rik Ferguson holds a Bachelor of Arts degree from the University of Wales and has qualified as a Certified Ethical Hacker (C|EH), Certified Information Systems Security Professional (CISSP) and an Information Systems Security Architecture Professional (ISSAP).. We are all connected. Not everyone has positive intentions. I help the rest of us understand the risks and challenges of our digital world.
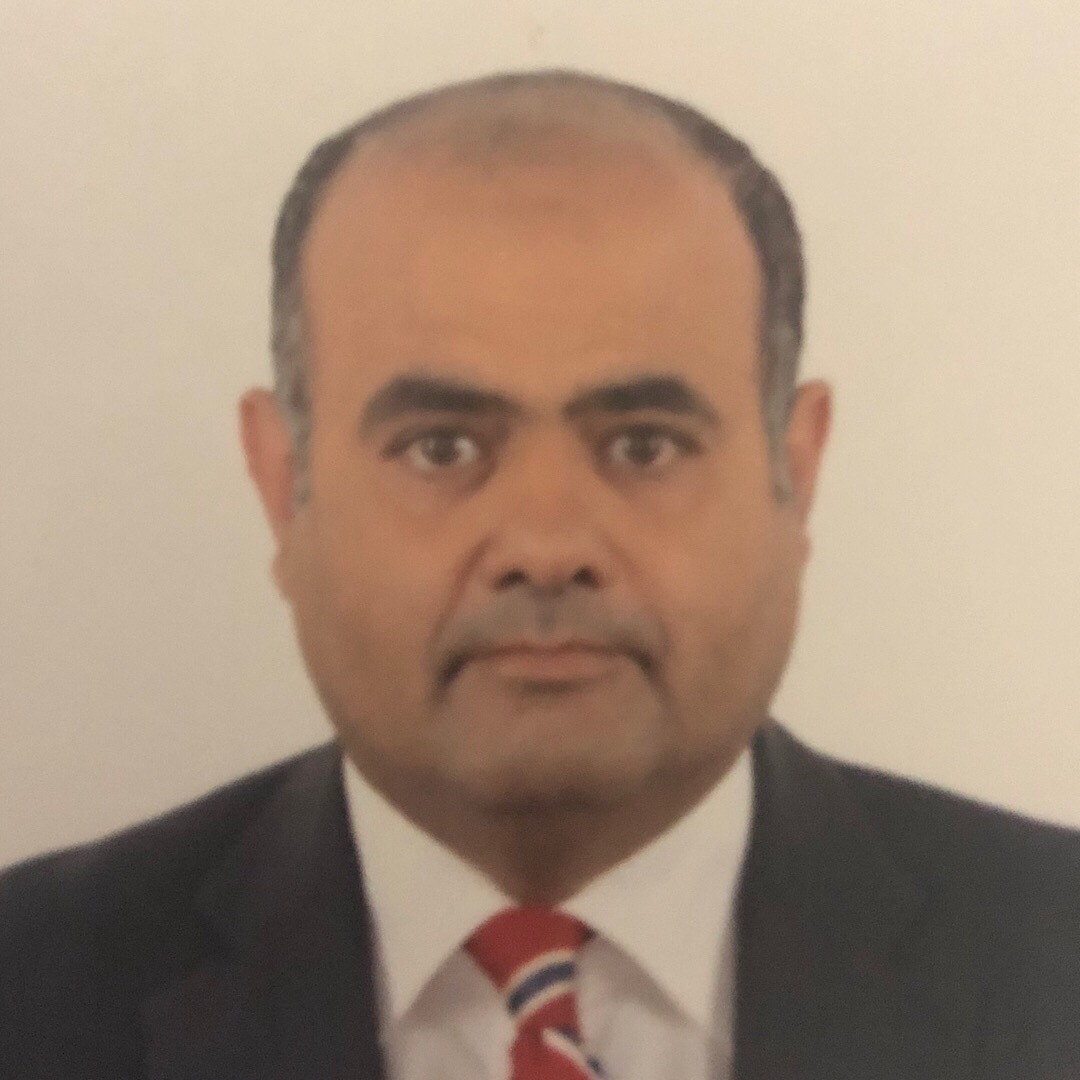
Joseph Makram
CIO, Egyptian Arab Land Bank (EAL Bank) - Egypt
CIO head of IT at EAL bank joined 2016 till now, Deputy –GM for E-channel at National bank of Egypt from 2008 till 2016
Manager E-channel at Arab bank from 1994 till 2008
Plus other working experiences in IDSC cabinet of minsters , Mantrac
I am PMP certified , MCSD certified
Hold master’s degree from Nottingham university in IT
Hold post graduate diploma in IT
And Engineering degree from AIN shams university
Eng. Majed Alshodari
Co-Founder, Saudi Association for Shared Services; Founder, MAITTC Consultancy; Board Member, Tatweer Educational Technologies - Kingdom of Saudi Arabia
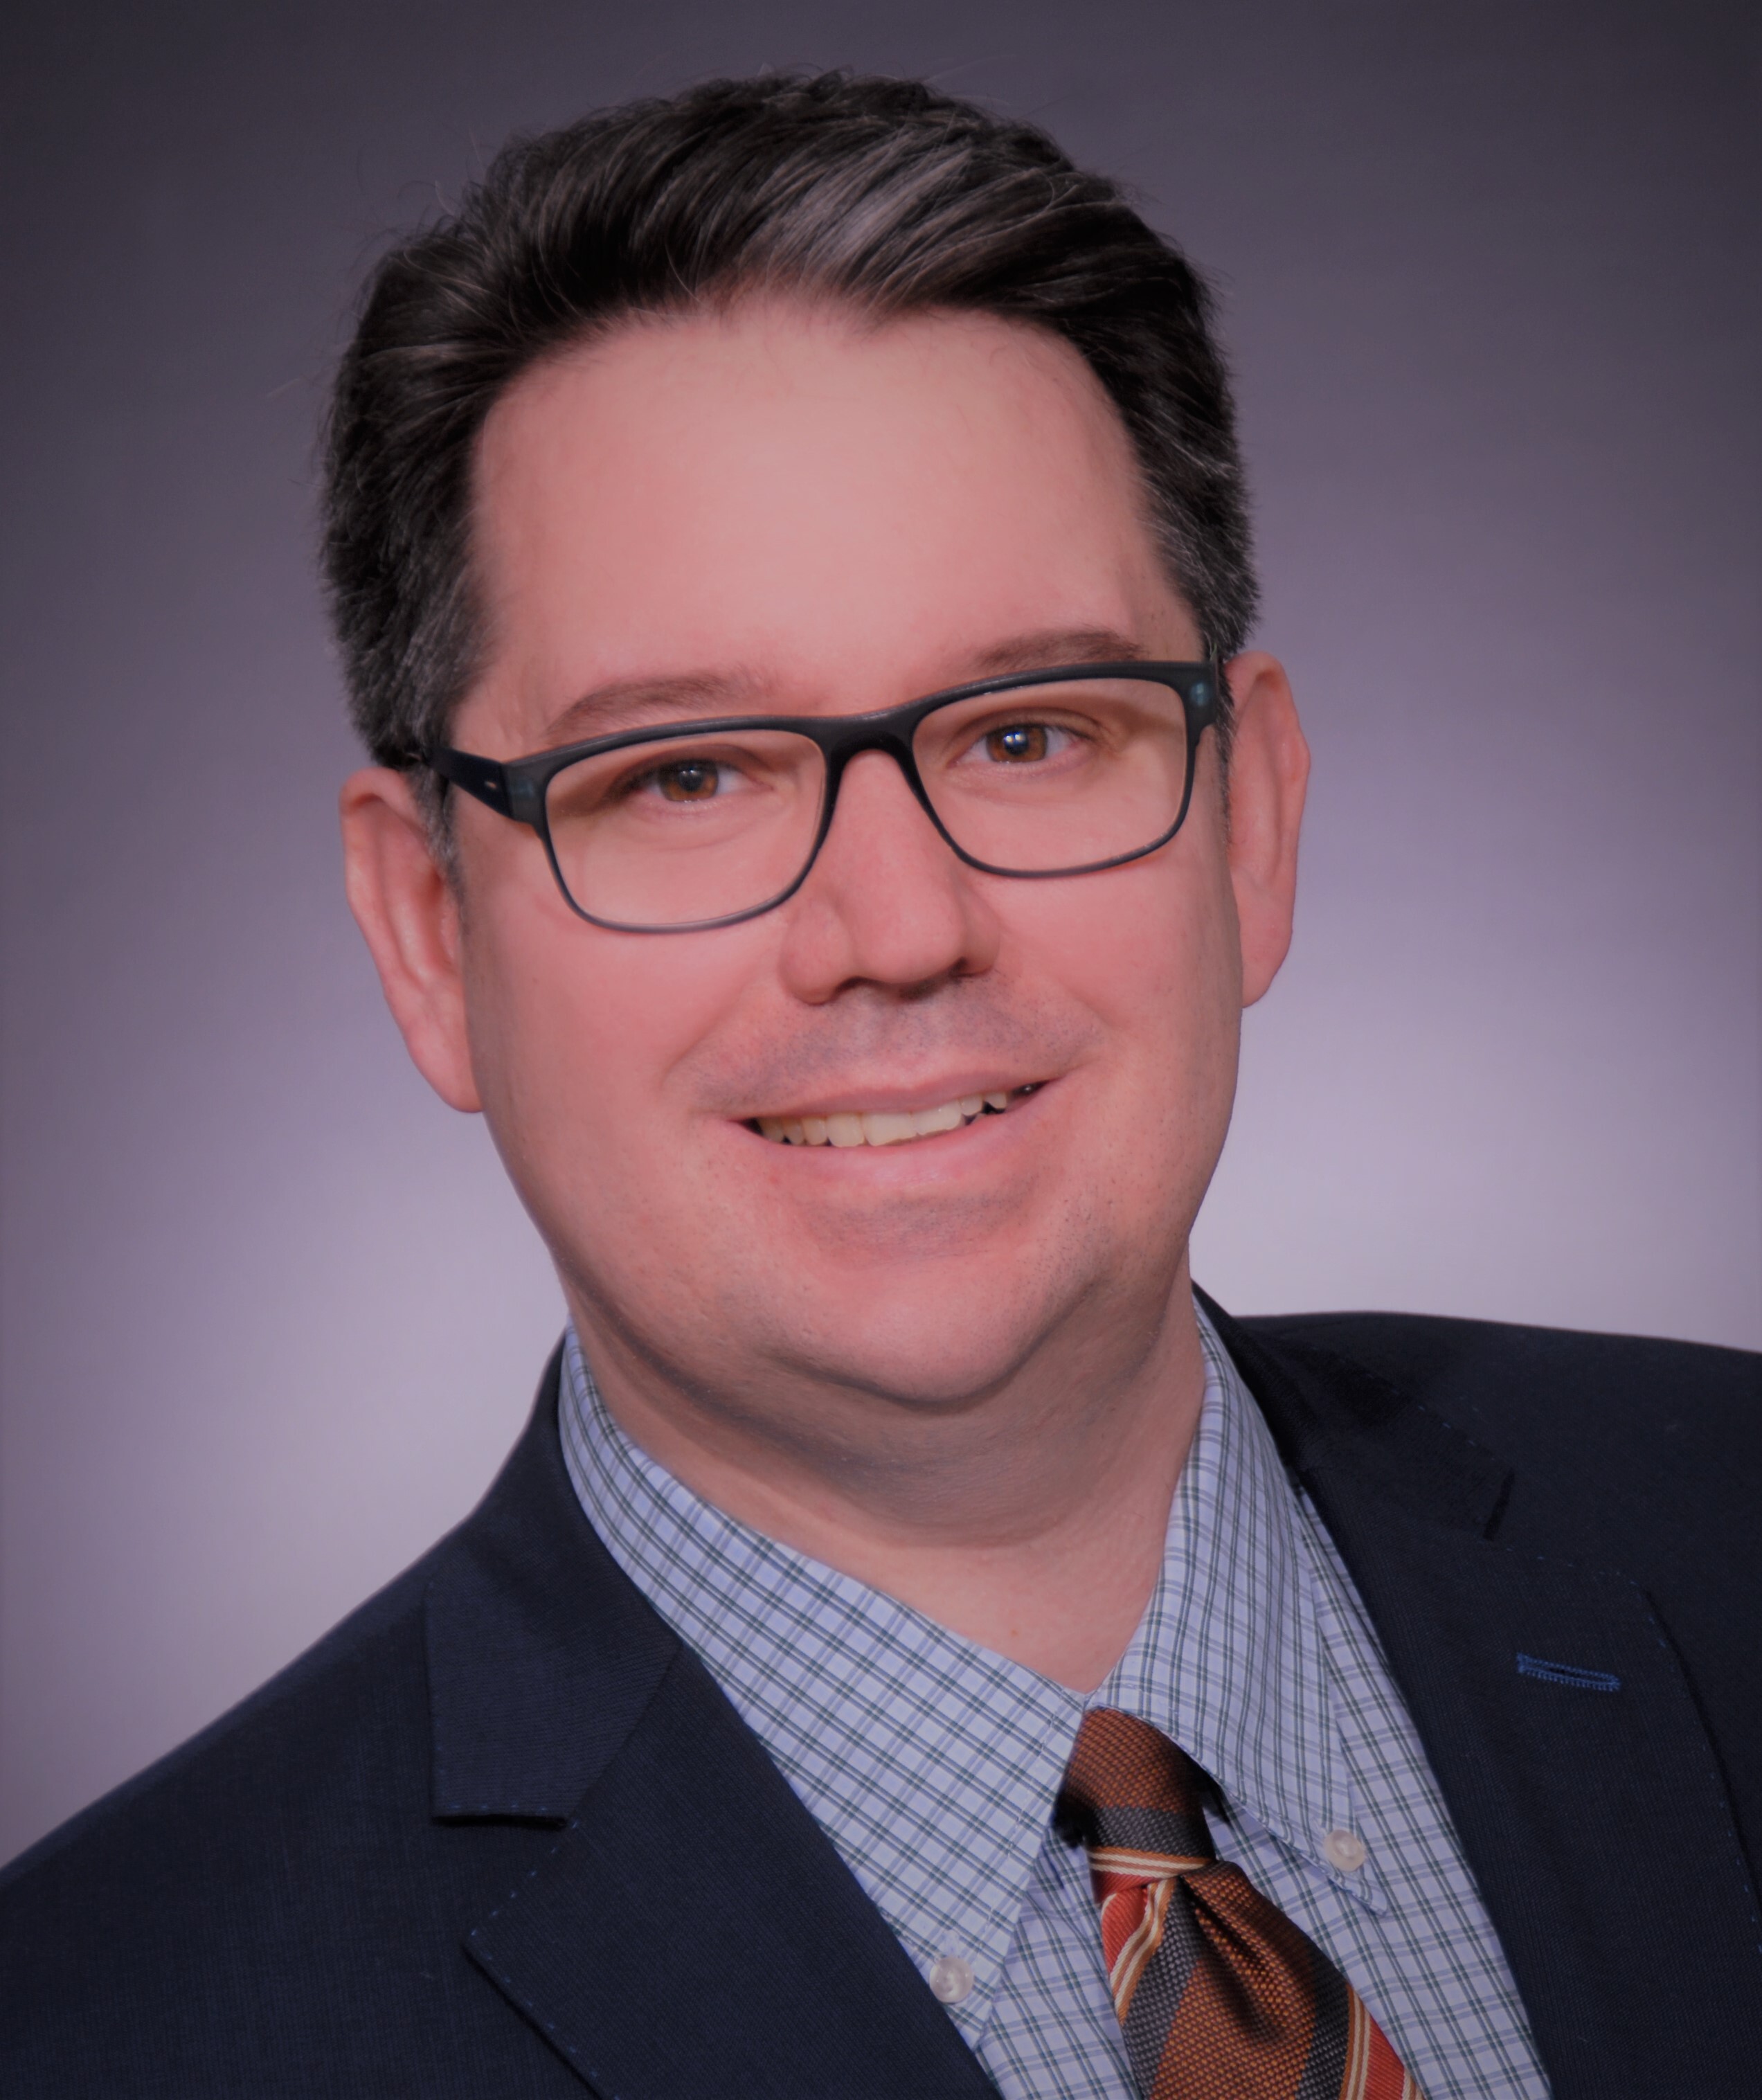
Matthias Muhlert
Security Bear – CISO, HARIBO - Germany
Matthias is a dedicated and highly qualified IT Security Professional with a consistent track record of success spanning over 22 years of diversified experience developing and implementing IT security processes as well as leading IT security governance programs. He brings demonstrated expertise at identifying and mitigating security risks by conducting comprehensive business process reviews and developing appropriate plans and solutions to meet the highest of network protection standards. His leadership, interpersonal communication and negotiation skills allowed him to lead and manage diverse, cross-functional teams in international and multicultural environments, and maintain effective relationships with key project stakeholders as well as C-level decision makers. Main areas of expertise are in the development and implementation of solid IT infrastructure and network security systems, polices, governance and crisis response, with especial skills in security infrastructure, analysis, response, compliance and ISMS according to ISO 27001. Matthias works currently as SecurityBear (CISO) at HARIBO in Grafschaft and is responsible for global information security management in more than 25 countries. After studying Network Computing at the Technical University of Bergakademie Freiberg, he worked as Senior IT Security Consultant and IT Security Trainer in several companies, among others, at Verizon, NESEC GmbH and Kabel Deutschland (Vodafone). Before HARIBO, Matthias worked as Chief Information Security Officer of HELLA and Schaeffler in Germany being responsible for the complete Information Security Management. He holds the following credentials and certifications: ISO 27001 ISMS Manager, CISM, CISSP, PRINCE2 Practitioner, CoBIT Practitioner, EC Council – Certified Ethical Hacker, Checkpoint CCSE PLUS (NG/NGX).
Marcus Alldrick
CISO Luminary - UK
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university.
Progressing from programming into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved financial institutions and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there.
Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now actively volunteers for the heritage Swanage Railway where he is the Commercial Director, Julia’s House, the Dorset and Wiltshire children’s hospice and care provider, a local school as a governor and is a guest lecturer at the University of Portsmouth.
Lady Olga Maitland
President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel - UK
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Lorna Trayan
Executive Partner, Security and Risk Management, Gartner - UAE
A well-versed, adept communicator, with more than 20 years in the Cybersecurity field, Lorna has an MSc, and is CISSP certified. She is currently working in Gartner as a CISO Advisor and Partner. She is a known speaker in security events in the region with several published blogs and articles. She also runs security awareness sessions to Boards of Directors, non-security Executives, VPs and GMs in organizations. Lorna got her B.Sc. in Communications and Electronics Engineering from Ain Shams University, Cairo-Egypt; Computer Networks Diploma from Information Technology Institute (ITI), Cairo – Egypt; M.Sc. in Information Technology and Security from University of Nottingham, Nottingham-UK. Lorna’s journey into security started with her joining Internet Security Systems (ISS) in 2003 after almost two years extensive experience in the network arena. She was responsible for all technical related activities in the region. She moved on to the more specialized security industries of Telco and Financial Institutes and was responsible for six countries. After the IBM acquisition of Internet Security Systems in 2007, she smoothly transitioned into the IBM security environment as a Senior Information Security Specialist for IBM Security Services. Since then, she worked on large and small projects alike with the same dedication and Customer-Satisfaction goal. She got to be known with her extensive knowledge of security products, professional services and managed security services. Her experience in the Gulf and Levant region became unparalleled when it came to information security consultancy. Lorna joined Gartner in 2019 and currently holds the role of CISO Advisor and Partner. She has worked with more than 45 Cybersecurity Leaders/CISOs in the region, across different industries, to help them achieve their security goals and overcome challenges.
Prakash Padariya
Global Chief Information Security Officer, OYO Group - India
Prakash is a senior management executive with over 20+ years of core Information / Cyber Security & Technology corporate experience with leading Fortune 100 multinational corporations & unicorn start-ups like GE, IBM, Target Corporation, PayU, Accenture & Royal Bank of Scotland. His professional experience spans across Banking, financial, telecommunications & IT service industries in India, USA, Europe, Australia, Canada and EMEA.
Prakash has extensive exposure & “hands-on” expertise in leadership at CxO board, Corporate security consulting, Cyber Security, Cyber warfare, Ethical hacking, Surveillance audits, Legal Regulatory Compliance, Computer Forensics, Law Enforcement cyber-crime prevention, Risk & Compliance based on standards & regulatory requirements of ISO27002, PCI DSS, HIPAA, GLBA, FISAP, FSA/FCA, FISMA, OCC, PIPEDA & BASEL.
• 15 Security & compliance global certifications- Certified CISSP, CISM, CISA, CEH, ISO27001:2013, CPISI, Six Sigma Green Belt, CCNA,
• Winner of 24 corporate awards & numerous industry recognitions.
Prakash is currently Senior Vice President & Global Chief Information Security Officer (CISO) at OYO responsible to manage IT, DevOps, DBA, Dialer, Network & Cyber Security operations across 35 countries. Prakash helms a security strategy for OYO’s systems globally, including regions such as India, Southeast Asia, Europe, the US and the UK. Prakash is also responsible for leveraging technologies such as big data analytics and artificial intelligence to enhance cyber security functions from the ground.
Prakash also runs a personal website www.thesecureplanet.com focusing on Information security world. He is a strong supporter of Entrepreneurship & Start-up Ecosystem (IT/Non-IT).
Social: www.linkedin.com/in/prakashp
Personal Web: www.thesecureplanet.com
Peter Ling
VP Global Cyber Security Alliances, RiskRecon, Mastercard - Canada
With 28 years’ experience in the Cybersecurity space, Peter is a seasoned global practitioner and technology pioneer, having created numerous offerings in this space. His background spans from operational security response management, systems engineering, and complex technical vendor integrations — to strategic alliances throughout the security and risk markets. His areas of expertise are in Public Key Cryptography (PKI), Secure Communications, Endpoint Protection and Threat & Risk management. He has developed and brought dozens of security products to market internationally and is on a constant journey, assisting partners and clients as the Cybersecurity market continues to meet the challenges of the day.
Dr. Robert Coles
Head of Security Strategy, DS Smith - UK
Robert is the Interim Head of Information & Technology Security Strategy at DS Smith PLC. He also holds a number of board positions including Chair of Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University of Brighton. Robert has over 35 years of audit, risk and security experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG.
Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School.
Dr Sally Leivesley
Managing Director Newrisk Limited UK, Chair, Permanent Monitoring Panel for Catastrophic Risk, World Federation of Scientists
Dr Leivesley chairs regular international scientific meetings on themes of catastrophic risk covering nuclear; novel coronavirus; resilience of CNI including cyber; and resilience from hazardous near earth objects. The focus of work is generic solutions to catastrophic risks across all disciplines and practical applications to government policy and business resilience. She is an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business. Worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks. As an International media commentator after 9/11 she has provided services for the BBC World Service and other news outlets on extreme threats – cyber; terrorism; emerging conflicts – Kabul 2021 evacuation; South China Sea;; aviation losses; nuclear reactor explosions; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents. She has contributed to journals and books on major incidents including death and injury in disasters and expedient housing post disaster. Director of two disaster recovery units in Australia (weather and chemical incidents) in support of community recovery. Trained by British Home Office as Scientific Advisor, CBRN, and Cold War appointment as SA on all aspects of nuclear war. PhD London University –disasters and catastrophic risk, awarded in field of Economics; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute, and Information Assurance Advisory Council Community. Panel adviser to the first British IET and CPNI supported publication for Cyber Security in the Built Environment.
Sylvain Hirsch
Cybersecurity Strategy, Mandiant (now part of Google Cloud) - Singapore
Sylvain Hirsch is a cyber security professional with extensive experience in incident response, cyber threat intelligence and cyber resilience strategy. He started his journey in cyber security with a master’s degree in digital investigation and identification at the University of Lausanne.
Sylvain worked for Credit Suisse’s Threat Detection and Response team in Zurich and Singapore. He then worked as an Incident Responder at Mandiant in Singapore. In this role, Sylvain led investigations of advanced and persistent threats, performed Purple Team Exercises to identify security gaps, and conducted trainings to enhance organization’s defense and response capabilities. Sylvain is currently part of Mandiant Strategy Services, now part of Google Cloud, helping organizations with their cyber resilience strategy, assessing their cyber maturity, improving their defense and response capabilities, and conducting cyber attack simulations with technical and executive teams.
Sylvain is also actively involved in several cyber communities and is leading a network of more than 200 cyber professionals from the public, private and academic sectors in Singapore.
Sylvain is a guest lecturer at the University of Lausanne and has presented at multiple cyber security conferences over the past 2 years.
Dr. Viktor Polic
CISO, Head of Information Security and Assurance Services, ILO - United Nations - Switzerland
Multi-event offers
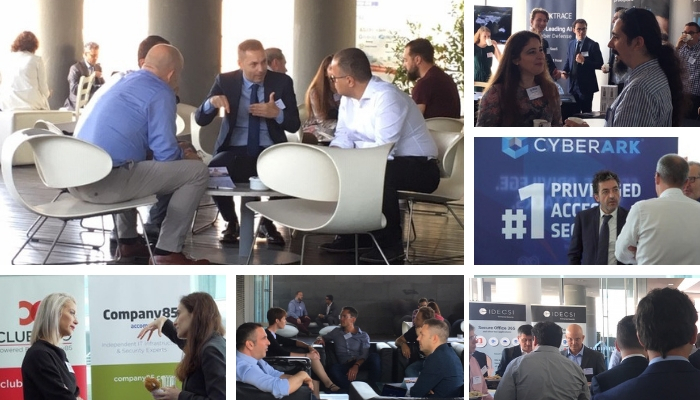
Hub Networking Collage
Sponsors and supporting associations 2023
Mastercard
RiskRecon traces its beginnings to 2011 when our founder, Kelly White, asked himself, “Is it possible to measure the security program quality of any company simply by looking its Internet-facing presence?”
Kelly is a long-time information security practitioner and bank CISO who witnessed first-hand the need for adapting third-party risk controls to meet the new challenges resulting from decentralized IT and SaaS apps. He has many years of hands-on experiencing building big data and analytics solutions to detect fraud and security vulnerabilities in high-velocity transaction environments.
Like most organizations at the time, his bank’s third-party risk management assessments relied heavily on questionnaires and other vendor attestations. This approach worked well ten years ago with a small number of large vendors, mostly in-house deployments, purchases controlled by central IT, and a well-defined set of Internet vulnerabilities. With the decentralization of IT purchasing and rapid adoption of SaaS, this approach was becoming less effective and more resource-intensive.
What if instead of trying to use the “old” risk management model, his institution could trust an objective source that automatically pinpointed specific gaps in any organization’s security programs and performance? Questionnaires and surveys are helpful in evaluating one’s intent but provide little verifiable insight into actual practices and discipline.
After realizing there were no such solution available, he decided to build his own. After testing and validating his solution with many peers, Kelly decided to pursue the idea full time and founded RiskRecon, officially incorporating in October of 2015.
RiskRecon is headquartered in Salt Lake City, UT with a presence in Boston, MA and representatives around the world.
Forescout
Forescout delivers automated cybersecurity across the digital terrain, maintaining continuous alignment of customers’ security frameworks with their digital realities, including all asset types – IT, IoT, OT, IoMT. The Forescout Continuum Platform provides complete asset visibility, continuous compliance, network segmentation and a strong foundation for Zero Trust.
Cato May @10x
UAE
(ISC)2 UAE Chapter
Connect | Educate | Inspire | Secure
Encourage educational and networking opportunities to promote the exchange of ideas, knowledge, and member’s growth within the information security profession in UAE.
Promote adequate communication to keep members abreast of current events in information security by conducting workshops and seminars.
Visit www.isc2.org
Gallery – 4th CISO 360 Middle East 2023

Downloads – 4th CISO 360 Middle East
4th CISO 360 Middle East testimonials
“Very Informative and experienced speakers form all different capabilities and sectors which made the forum extremely worthwhile. Great delegates as well to speak to and were clearly very keen on the content especially the TPRM (Third Party Risk Management) space where Mastercard Cyber & Intelligence fitted in. We went to meet and get connected with senior executives from all verticals/Business areas and we achieved that in spades. Our connections in region were built rapidly and our pipeline as a direct result will get larger whilst we build the Risk Recon brand in Middle Eastern region. ” – John Quinn EMEA Director – Global Cyber Security Partnerships Mastercard Cyber & Intelligence
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” – Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
““I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“ – Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).” – Andreas Prass, CISO & DPO, 360 Treasury Systems AG, Germany
“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.” – Carole Embling, Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” – Jorge Fernandes, CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.” – Matthias Muhlert Security Bear – CISO HARIBO, Germany
“The speakers, the content and the venue was awesome. The line up of speakers and their experience made me to attend the event. Also to gain insights of new security threat landscape.“ – Abdul Saleem, Project Manager, GERAB
“Great networking and learning from various cyber Guru’s!“ – Sajjad Ahmad, Director of security, DP World.
“Very professional speakers, panels are to the point and we discuss what the industry needs now.“ – Joseph Makram, CIO, EAL – Bank
“Very informative, speakers were excellent. Rik and Prakash were the highlights of the event. “ – Mehboob Merchant, Lead Network and Security, SAAL Operating Systems
“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!” – Viktor Polic CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland
“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.” – Richard Bloxam-Rose, Threat and Vulnerability Consultant, Computacenter, United Kingdom
“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” – Deborah Saffer, Global Deputy CISO, Cushman & Wakefield
“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions
“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” – Jonathan Armstrong, CEO, Cordery
“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.” – Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK
“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys
Video testimonials
Community testimonials
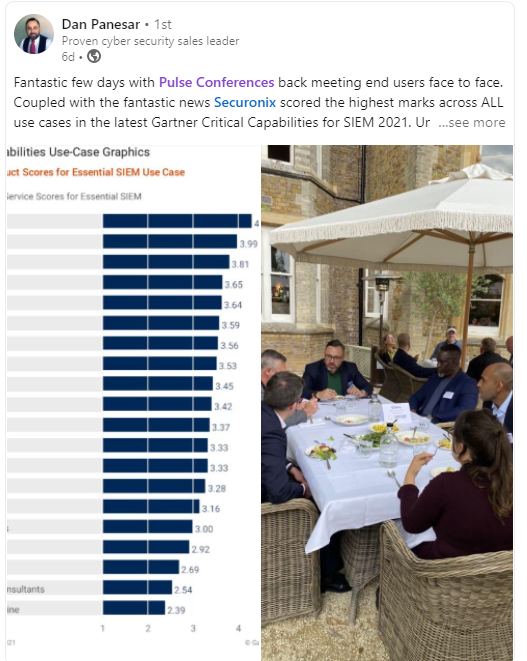
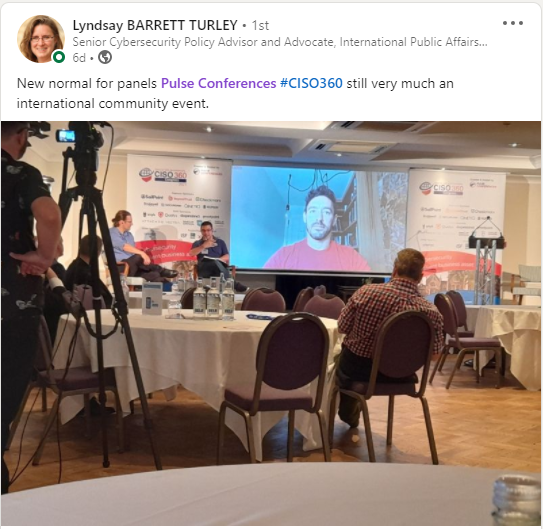
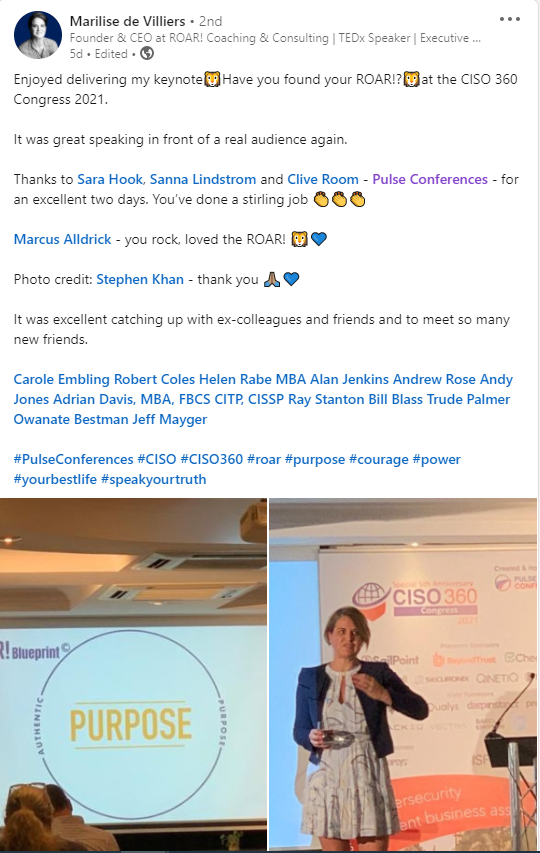
Testimonials – CISO 360 series
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“
Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra
“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim
“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica
“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS
“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World
“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter
“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint
“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018