Archive · CSO 360 Global Congress

CSO 360 Congress Amsterdam

This event took place on 6–7 December 2017 at W Amsterdam.

DATE6–7 December 2017
VENUEW Amsterdam

2017 CSO 360 Congress- Amsterdam

Integrated security, threat and intelligence strategies to protect people, profits and reputation and leverage global business operations

Team Pulse would like to say a massive thank you to everyone who participated in the inaugural CSO 360 Congress hosted 6-7 December 2017 at the 5 star W Hotel in Amsterdam. This event was the ultimate ‘sound boarding’ and connective platform for senior in-house chief security officers, corporate security, resilience, threat management, intelligence and crisis response directors from 15 different countries spanning Europe, Africa, the Middle East, the U.S.

In particular, we would like to thank the expert international speaker panel of security practitioners who openly shared experiences and approaches under the Chatham House Rule. We would also like to thank the official event sponsors, CyberArk, Barclay Simpson, iCetana, SafeHotels Alliance and Control Risks without whom these events would not be possible.

Check out our video from the CSO 360 Congress in Amsterdam and what speakers, sponsors & delegates thought of the event.   

Dank je Amsterdam!

Team Pulse

“Embraces the changing threat environments, great experience, fabulous speakers, pertinent interesting focus”
Special Tribunal for Lebanon (The Hague)

“I just had the best conference ever!”
CCO, BT (Netherlands)

“A great one stop shop of the top CSO minds!”     
VP, Corporate Security and Resilience, Pearson (UK)

“I was extremely impressed by the content, quality, origination and administration of the Pulse product” 
MD, Tierra Nova Solutions (Sierra Leone)

“Simply the best event for security practitioners. Real expertise and knowledge sharing”     
Group CISO, Unipart Group (UK)

“Overall this has been a fantastic event. Awesome speakers addressing a diverse range of interesting and relevant topics.  Also, great job by Team Pulse. We have been looked after so well! Thank you!”
Regional Security Director, Caterpillar Inc (Switzerland)

Key themes

  • Evolving security threat landscape – protecting nations and businesses
  • Integrated threat intelligence and incident response strategies
  • Brand protection – updates and challenges on IP and illicit trade
  • Kidnap and Ransom and insider threat – new tactics
  • Investigations, ethics and compliance
  • Securing and leveraging the new artefacts of business innovation – IoT, AI
  • CSO 360 ‘boardroom’: culture, engagement and monetization of security

Programme at a Glance

Monday 4 December and Tuesday 5 December 2017
(Optional 2-day Training Courses)
COURSE 1: Cyber Attacks – the Risk and the Fix
COURSE 2: Security Leadership and Management Training

Wednesday 6 December
DAY ONE: CSO 360 Congress

Thursday 7 December 2017
DAY TWO: CSO 360 Congress 

Friday 8 December 2017
(Optional One-Day Training Courses)
COURSE 3: Resilience Communications Training – Media, Brand Protection, Crisis Governance
COURSE 4: The Threat from Business Espionage

Included Networking Events – An Integral Part of the CSO 360 Congress Experience 

Tuesday 5 December

19:30-22:00 
Welcome Drinks – The W Lounge Bar


Wednesday 6 December

12:40-13:40 Lunch – The W – kindly sponsored by: 
18:15-20:00
Amsterdam Light Festival Canal Reception – kindly sponsored by: 
20:00-22:30 Boat docks for dinner at the Pulitzer


Thursday 7 December 2017

13:00-14:00 Lunch


Keynotes by:

  • Frank Gardner OBE, Security Correspondent, BBC, Journalist and Author
  • Steven Wilson, Head of European Cybercrime Centre (EC3),Europol

Chaired by:

  • Simon Scales, Former Head of EMEA Investigations, BP plc.

International Speaker panel:

  • Alexander Gaft, Group Director Investigations, VEON
  • Alex Wilson, Security Solution Architect, CyberArk Solutions Ltd.
  • Andy Williams, VP, Business Development and Quality Assurance, Safehotels Alliance AB
  • Crawford Robinson, Head of Group Security Assurance, Investigations & Information Security, British American Tobacco
  • David Langhorn, VP Global Head of Security & Intelligence, IHG®
  • Derek Cheng, Chief Security Officer, TalkTalk
  • Elizabeth Lawler, VP of DevOps Security, CyberArk (& Co-Founder, Conjur Inc.)
  • Graham Edwards, Head of Group Security, Nationwide
  • Gal Messinger, Head of Global Security, Philips Lighting
  • Jeroen Meijer, Senior Partner, Control Risks
  • Maitham Al-Lawati, General Manager, Risk, Compliance & Managed Security Services, Oman Data Park
  • Malcolm Smith, Global Security Director, Sasol
  • Mark Wolsey, Group Security Director, CRH plc
  • Michael Holstein, Head of Security Africa, UNHCR
  • Ned Farmer, Geopolitical Risk Manager, American Airlines and Vice-Chair of the US State Department’s Overseas Security Advisory Council (OSAC) Aviation Security Working Group (ASWG)
  • Neil Jarvis, Director of Information Technology, Aston Martin Lagonda
  • Lady Olga Maitland, Cofounder, Defence and Security Forum & Chairman, Copenhagen Compliance
  • Paul Heffernan, Group CISO, Unipart
  • Peter Drissell, Director Aviation Security, Civil Aviation Authority
  • Richard Sumnall, EMEA Regional Head of Security, Uber
  • Richard Zijdemans, Director of Security EMEA, APAC & Greater China, Medtronic
  • Roeland Stouthart, Head of Information Security, International Criminal Court
  • Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7
  • Simon Hoyle, Senior Vice-President, iCetana
  • Steve Wright, Data Privacy and Information Security Officer, John Lewis Partnership
  • Stuart Seymour, Group Head of Security and Resilience, Centrica
  • Suzanne Oyen, Head of Global Corporate Security, SWIFT
  • Tim Williams, Senior Advisor, Global Risk Intelligence, McDonald’s Corporation
  • Tom Brabers, Representative, ASIS Benelux (and Former Head of Global Security, Geodis Freight Forwarding)
  • Dr. Victoria Baines, Visiting Associate, Oxford Internet Institute
  • Xander C. W. Heemskerk, Director Product Security – Personal Health, Philips

Platinum Sponsor

Pulse Conference Sponsor

Gold Sponsor

Silver Sponsor

Lunch Sponsor

Panel Sponsor

Supporting Association

Training Courses

Optional Training Courses – Monday 4 and Tuesday 5 December 2017

  • COURSE 1: Cyber Attacks – the Risk and the Fix
  • COURSE 2: Leadership and Management Training

COURSE 1: Cyber Attacks – the Risk and the Fix

For Corporations, Governments and Infrastructure

Over two days, delegates are shown the reality of just how easy real cyberattacks can be – even those with the most devastating effects – and the implementation of simple measures to avoid catastrophic risk. The course is suitable for entirely non-technical officers as well as cyber managers and administrators who wish to develop a sound understanding of just how easy and low-tech the efforts of an attacker can be, and how to implement mitigation or who wish to upgrade their existing skills to become more cost effective for their organisation. The practical elements are comprehensively taught in a walk-through manner to demonstrate the vulnerabilities in realistic targets. A key theme running through the course is that of workforce vulnerability – no matter how well defended the organisation’s intellectual property is, the staff are the way in.

Book for the training courses here

Day One – The Risk

Focuses on the mindset and techniques of the attacker, whether a cybercriminal, a state actor, a corporate spy or frivolous hacker. Students are equipped with tools and techniques to perform investigations of targets in the preparation for a notional attack, essentially becoming the hacker to demonstrate just how easy those attacks often are due to the visibility of staff and corporate data online.

Introduction to Cyber Risk

  • “It’s not about the tech” – why the attackers’ techniques are surprisingly low-tech, and why the information security risk lies with the human workforce, not their computers.
  • Real world examples of catastrophic attacks and the vulnerabilities in every organisation.
  • One size fits all – the common vulnerabilities used by any attacker against any target: corporate, government and personal.

Attacker Methodology
Part One – reconnaissance
Scoping a target. A practical module demonstrating to delegates how an attacker uses OSINT (open source intelligence) to obtain corporate data and personal details using nothing more than search engines and free, legal tools.

Part Two – Attack

  • Compare and contrast of ‘technical’ attacks with low tech and no-tech hacking by social engineering.
  • Teach a man to phish. Understanding the myriad ways an attacker uses the freely obtained data to quickly penetrate an organisation through simple influence.

The Persistent Threat of Leaked Data
The permanent threat to corporations that arises from leaks of staff data from breaches such as Yahoo – even when non-corporate in nature, and even when many years old. Delegates are show the surprising amount of leaked data online and what to do about it.

Wi-Fi – the Corporate and Personal Risk
The largely unknown risks of wi-fi, not only as a vehicle for corporate intrusion by attackers but also for tracking the physical movement of individuals and identifying their homes. A practical module in which students are walked through the steps of an attacker breaking into corporate wi-fi and tracking of staff members using freely available tools.

Day Two – The Fix

Focuses on mitigating the identified risks. Real world examples of damaging attacks are dissected, with particular emphasis on correct implementation of cyber incident response. Delegates are presented with the most effective measures to mitigate an attack to bring a business back online at minimum expense.


Exercise
: Attack the Corporation

WHAT HAPPENS NOW? – The reality of an attack, and the art of incident response.

The Devastation
Lessons learned from a vast number of cyber incident responses, where basic lack of security procedures and response plans allow simple attacks to have catastrophic effect.

Mitigation
From lessons learned in the ‘attack methodology’ modules and further illustrated in ‘What happens now?’ we explore the steps to secure the company.

Again, the technical aspect is secondary to the information and ‘human’ security.

  • The technical penetration test – learning why most companies waste time and money with incomplete or ineffective testing.
  • Cyberattack response plan – The blueprints of the towering inferno. Why you must engage with your incident responders BEFORE an attack, and why incident response should cost thousands not millions.
  • Staff data – reducing the target surface by educating the workforce in simple, effective ways that require no technical knowledge.
  • Threat intelligence – the utility and strengths of currently available threat intelligence systems.
  • ‘Convenience is an attack vector. ‘ Overcoming perceptions of inconvenience by removing certain technical privileges to maximise information security and aiming to become hack-proof.

Designed for: North Cyber advises that this course is suitable for any officials in government, business, critical infrastructure, banking, transportation, energy, shipping and ports, retail, leisure, police, intelligence and security operations whether government or private sector. The case studies and work will be drawn from Europe, Africa, Middle East and South Asia depending on the persons attending and the region where the course is delivered.  

About the Tutor
North Cyber Limited are team of former intelligence officers with expertise in covert online operations and digital forensics. The company teaches government and corporate clients how find and fix the unseen holes in their security. They specialise in all levels of capability including low-tech and no-tech hacking, using freely available information to circumvent vastly expensive but ineffective security systems. The teaching draws on many and varied real-world examples from the private and government sectors, from the perspectives of the attacker and incident responder. Participants in these courses will evaluate their own experience on the course in gaining additional skills and understanding of the threats to their organisation and they will gain confidence in tackling these catastrophic risks to the comparate or government operation.

COURSE 2: Leadership and Management Training

Tutor: Dr. Robert Shaw, TEG7 LLP
This training is designed to develop new skills and knowledge for corporate and government personnel that lead and manage teams at all levels.

Module 1 – discusses the perceptions of leadership, management and command. Different levels of management and styles. What people expect from their leaders and differing organisational structures and functions.

  • Overview of leadership management and command and their links to culture
  • Levels of command and styles of management
  • Organisational structures and functions
  • Personnel and organisation expectations

Module 2 – discusses personality types, recruitment strategies and interviewing techniques, managing expectations and attitudes, methods of communication, the threat from disgruntled personnel, the techniques of coaching and mentoring and how to manage change.

  • Personality types and team building.
  • Recruitment strategies and interviewing techniques.
  • Managing expectations and attitudes.
  • Methods of communication.
  • The threat from disgruntled personnel.
  • Coaching and mentoring.
  • Managing change.

Module 3 – is a series of case studies through the medium of battlefield tours, role plays and management exercises.

  • Role playing of management techniques and responses.
  • Theory and practical management exercises.
  • Case studies

About the Tutor
Dr. Robert Shaw, TEG LLP
Robert is a security, intelligence and EOD executive with a UK Military background. He has broad strategic and operational experience and has advised senior staff, diplomats and government officials on aspects of security, intelligence, threat analysis, crises management, and resilience strategies. He has been the UN Security and EOD Advisor; Liaison officer for the UNMAS and UNOPS and has experience with NATO, the GCC, African Union, OSCE, EUPOL, FCO and others. Robert is a respected expert, has specialist research background on suicide bombing and has provided thematic briefs on worldwide security issues relevant to UNMAS/UNOPS missions.

Optional One-Day Training Courses – Friday 8 December 2017

  • COURSE 3: Resilience Communications Training - Media, Brand Protection, Crisis Governance
  • COURSE 4: The Threat from Business Espionage

COURSE 3: Resilience Communications Training - Media, Brand Protection, Crisis Governance

Resilience communications are taught in a fast-track one-day session to develop new skills and knowledge for corporate and government personnel.
Tutor: Dr. Sally Leivesley Newrisk Limited and TEG7 LLP

Module 1 – New Threats – covers on new threats to energy and critical infrastructure, railways, aviation, shipping and ports, construction of buildings and to the financial and government centres of major cities.  Catastrophic hazards that often generate media inquiries include internal issues within the corporation or government department, large transformation projects, major infrastructure construction, terrorism, cyber- attacks, extreme weather events, insider threats, security, organised crime and fraud and events such as Brexit, North Korea’s nuclear weapons programme, mass population movements, and military exercises close to national borders.

  • Overview of regional and local threats to infrastructure and business
  • New threats- cyber, terror, energy, transportation, leisure, finance and banking, building security
  • Emerging events – Nation State hostilities, climate change and severe weather, Brexit,
  • Interpreting threat intelligence and other information
  • Situational awareness
  • Crisis phases and human reactions
  • Critical timelines for Internal and External Communications
  • Team building for successful communications
  • Cues, Signs and Symptoms
  • When should Warnings be given
  • Redressing Errors

Module 2 –  Optimising Communication Strengths is a practice session for all the participants to identify their strengths in contributing to a media and brand resilience process. This could be gathering information and team leadership or presenting information to internal staff, stakeholders or preparation of information for spokespersons to use in media statements.

  • Practice session for all attendees
  • Case studies chosen are relevant to attendees’ industry sectors
  • Building trust with the team and the media

Module 3- Governance for Crisis Communications brings together all the phases of a catastrophic event with new governance principles that will assist in reporting after an incident on how processes were successfully managed to contribute towards the brand protection and resilience operations of the organisation.

  • Governance Principles relevant to the Communications Plan
  • Analysing Feedback
  • Brief Messages
  • Regular timing of messages and trust building
  • Recognising hostility and reducing tensions
  • Assessing effects on the Brand and reducing losses
  • Course Summary and Evaluation
  • Individual completion of self-evaluation of changes in skill levels Modules 1-3

About the Tutor
Dr Sally Leivesley is an expert in catastrophic risk and security for protection of life and critical infrastructure. She provides around 100 interviews to media a year on extreme events and communicates on public safety issues.  She has been providing commentary to the BBC World Service and many other media outlets since 9/11 and commenced her media communications work when tasked with recovering a city after a severe weather disaster. Her media work includes real time commentary during extreme life threatening events such as the Beslan school terror attack and in the immediate aftermath of terrorist and other incidents such as the flight MH17 aviation incident, Mr Litvinenko’s radiation poisoning, natural disasters, threats such as DPRK nuclear programme, terror attacks in France and Brussels, Britain’s 7/7 and 21/7underground rail terror attacks and she covers most major incidents of importance to the public in any year.  She has worked in catastrophic risk assessments and training within critical infrastructure covering many industries including energy, petrochemicals, rail, aviation, shipping, banking, government emergency planning and nuclear, chemical, biological and radiological incidents. (www.Newrisk.com  Recent Media Commentary).

COURSE 4: The Threat from Business Espionage

This training is designed to develop new skills and knowledge for corporate operations and security managers at all levels of management.

Module 1 – discusses what intelligence is, who collects it and methods of intelligence gathering.

  • Overview of intelligence
  • Who collects intelligence and why
  • Methods of intelligence collection

Module 2 – discusses physical and information security methods, the insider threat and counter intelligence and how security is compromised by human nature.

  • Physical and Information security methods
  • Counter intelligence and the insider threat
  • How security is compromised by human nature

Module 3 – is a series of case studies through the medium of role playing exercises and case studies.

  • Role playing of intelligence gathering techniques and security responses
  • Theory and practical exercises
  • Case studies

About the Tutor
Robert Shaw, TEG LLP – Robert is a security, intelligence and EOD executive with a UK Military background. He has broad strategic and operational experience and has advised senior staff, diplomats and government officials on aspects of security, intelligence, threat analysis, crises management, and resilience strategies. He has been the UN Security and EOD Advisor; Liaison officer for the UNMAS and UNOPS and has experience with NATO, the GCC, African Union, OSCE, EUPOL, FCO and others. Robert is a respected expert, has specialist research background on suicide bombing and has provided thematic briefs on worldwide security issues relevant to UNMAS/UNOPS missions.

Articles & White Papers

CyberArk

CyberArk_AWS_Hybrid_WP+11-2017-v4

sr-threat-landscape-devops-report-2018-final-en

wp-CyberArk-Privileged-Account-Security-11-2017-2

wp-Securing+Cloud+Workloads+on+Azure+11-2017+nf


Safehotels:

Responsible Travel -The New Evolution of Hotel Safety and Security

ARISE Case Studies in Disaster Risk Management

Developing crisis management guidelines for the travel and tourism industry

WITH THANKS TO OUR 2017 SPONSORS

Sponsors

Supporting Organisations

CSO 360 Congress Programme

Download the full CSO 360 brochure

Wednesday 6 December 2017

07:30     Coffee and Registration

08:15     Chairman’s Opening
Simon Scales, Former Head of EMEA Investigations, BP plc.

08:30     Opening Keynote Cyber Crime, Terrorism and New Security Challenges for Europe
Steve Wilson, Head of Europol’s European Cybercrime Centre (EC3), Europol

09:00     Strategic Keynote & Q&A Global Security Landscape – What’s Next?
Frank Gardner OBE, Security Correspondent, BBC and Journalist and Author 

10:00     Innovation in Centralized Integrated Corporate Security
Gal Messinger, Head of Global Security, Philips Lighting

10:30      Case Study Insider Threat
Stuart Seymour,
Group Head of Security and Resilience, Centrica

11:00     Morning Coffee Break

11:30     Case Study Big Brand Risk and Opportunity Intelligence
Tim Williams, Senior Advisor, Global Risk Intelligence, McDonald’s Corporation

11:50     Case Study TalkTalk – How we have Transformed our Security Programme
Derek Cheng, Chief Security Officer, TalkTalk

12:20     Case Study Emerging Challenges – Securing People and Assets Globally
Mark Wolsey, Group Security Director, CRH plc.  

12:40     Lunch – Kindly Sponsored by: Safehotels Alliance

13:40Interview Panel Security and Emerging Threats for the Energy and Ports Sector
Led by: Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7
Joined by: Stuart Seymour, Group Head of Security and Resilience, Centrica; Gal Messinger, Head of Global Security, Philips Lighting

14:10     Case Study Transport Security: V2V and V2X Communications
Neil Jarvis, Director of Information Technology, Aston Martin Lagonda Ltd

14:30     Case Study Practical Challenges and Tips on Implementing GDPR
Steve Wright, Data Privacy and Information Security Officer, John Lewis

14:50     Panel Advancing Tomorrow’s Holistic Security Leaders – Silo Bashing Between Security, Business and Legal
Co-led by: Mark Wolsey, Group Security Director, CRH plc and Jeroen Meijer, Senior Partner, Control Risks
Panellists including: Chris Meager, Security & Resilience, Barclay Simpson; Neil Jarvis, Director of Information Technology, Aston Martin Lagonda Ltd

15:20     Afternoon Tea Break

15:50     Case Study Doing Only What You Can Do – A Journey from Physical Security to Corporate Intelligence
David Langhorn MBE, VP Global Head of Security & Intelligence, IHG®

16:10Keynote What Secrets are at Risk as DevOps Goes Mainstream?
Elizabeth Lawler, VP of DevOps Security, CyberArk (& Co-Founder, Conjur Inc.)

 16:30    Case Study London Bridge Scaling a Regional Security Team from Scratch, Integrating with the Business and Cities
Richard Sumnall, EMEA Regional Head of Security, Uber

17:00     Immersive Scenario Panel How do you Maximise the Value and Investment of Threat Intelligence Platforms?
Panellists including: Tim Williams, Senior Advisor, Global Risk Intelligence, McDonald’s; Roeland Stouthart, Head of Information Security, International Criminal Court; Richard Sumnall, EMEA Regional Head of Security, Uber; Tom Brabers Representative, ASIS Benelux (& Former Head of Global Security, Geodis Freight Forwarding); Alex Wilson, Security Solution Architect, CyberArk

17:30                     Close of Day One
18:15-20:00         Canal Cruise Reception – Kindly sponsored by CyberArk
20:00-22:30         Dinner

Sponsorship opportunities

Interested in sponsoring the CSO 360 Congress in Amsterdam?
Contact Clive Room: teampulse@pulseconferences.com 

Thursday 7 December 2017

08:30     Coffee

08:45     Chairman’s Opening
Simon Scales, Former Head of EMEA Investigations, BP plc.

09:00     Case Study Threats to Aviation
Ned Farmer, Geopolitical Risk Manager, American Airlines and Vice-Chair of the US State Department’s Overseas Security Advisory Council (OSAC) Aviation Security Working Group (ASWG)

09:20     Keynote Aviation Security Performance Based Oversight – A Revolutionary Approach to Aviation Security Regulation & Compliance
Peter Drissell, Director Aviation Security, Civil Aviation Authority

09:40    Making CCTV Surveillance Intelligent through AI – Assisted Technology
Simon Hoyle, Director, iCetana

09:50    Updates on Kidnap and Ransom and Movement of People
Michael Holstein, Head of Security Africa, UNHCR

10:10     Immersive Exercise Crisis? What Crisis! The Yin and Yang of Crisis Management
Andy Williams, VP, Business Development and Quality Assurance, Safehotels Alliance AB

10:40     Keynote Innovation in Cybersecurity
Dr. Victoria Baines, Visiting Associate, Oxford Internet Institute

11:00     Morning Coffee Break

11:30     Immersive Exercise Terror Case Studies Underground Rail and Vehicle Ramming Attacks – What’s Next?
Dr. Sally Leivesley, Director, Newrisk Ltd and Founder Member, The Exercise Group7

12:00     Case Study Creating a Truly Integrated Security Team
Richard Zijdemans, Director of Security EMEA, APAC & Greater China, Medtronic

12:20     Immersive Roundtable Discussion Intellectual Property, Security and Brand Protection as a Business Asset

12:50     Case Study Secure IOT: Churchill and Housewives Coming to the Rescue
Xander C. W. Heemskerk, Director Product Security – Personal Health, Philips

13:10     Lunch

14:00     Insights Via Webcast Envisioning the Future of Security in Business 2020 and Beyond
Malcolm Smith, Global Security Director, Sasol

14:20     Crisis Plans – Are They Worth the Paper They Are Written On?
Robin Hamilton, CEO, Aldbury International

14:40     Case Study Importance of Human Intelligence (HUMINT) to Detect Fraud and Corruption
Alexander Gaft, Director Forensic Investigation, VEON

15:00     Cyber Insights Cybersecurity – What’s Next?
Case Study One – TeslaCrypt, Wannacry, NotPetya – Paul Heffernan, Group CISO, Unipart
Case Study Two – Combating Business Email Compromise via DMARC – Maitham Al-Lawati, GM, Risk and Compliance, Oman Data Park

15:30     Afternoon tea break and sponsors’ prize draw

16:00     Panel Transformation and Cyber Risk – How Can Security Reposition as Enablers of Business Innovation
Chaired by: Graham Edwards, Head of Group Security, Nationwide
Panellists including: Neil Jarvis, Director of Information Technology, Aston Martin Lagonda;
Dr. Victoria Baines
, Visiting Associate, Oxford Internet Institute

16:30     CSO 360 Boardroom How can we Engage the Board and How do we Develop a Culture of Trust
Led by: Crawford Robinson, Head of Group Security Assurance, Investigations & Information Security, British American Tobacco; Lady Olga Maitland, Cofounder, Defence and Security Forum & Chairman, Copenhagen Compliance; David Langhorn, VP Global Head of Security & Intelligence, IHG®; Derek Cheng, Chief Security Officer, TalkTalk

17:00     Close of Day Two and Goodbyes

Speakers
CSO 360 Congress Amsterdam

Download the CSO 360 Congress Brochure

Keynote Speaker:
Steve Wilson
Head of European Cybercrime Centre (EC3)
Europol

Steven originates from Ayrshire, Scotland. He was a Police Officer in Scotland from 1985-2015.
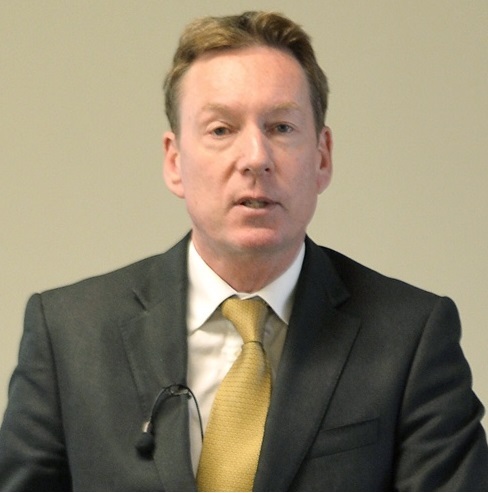
During this time, he served with Strathclyde Police, Scottish Crime and Drug Enforcement Agency, Her Majesty’s Inspectorate of Constabulary and, since 2013, with the reorganisation of policing in Scotland into a national force, Police Scotland. Steven performed a variety of senior Detective roles and was responsible for the national units in Scotland delivering: witness protection, covert technical policing, fugitives, undercover policing, assisting offender programme and all forms of cybercrime and cyber enabled crime including online child protection. Steven was the Scottish representative on UK cyber governmental and policing groups and led on industry and academic partnership groups on cyber resilience in Scotland. Steven has also worked in covert policing, major investigations, sex offender management, Counter Terrorism investigations and represented the UK on International policing matters. Steven commenced as Head of EC3 on 18 January 2016.

Keynote Speaker:
Frank Gardner OBE
Security Correspondent
BBC

Frank Gardner is the BBC’s award-winning Security Correspondent, reporting on a wide range of global security and terrorism stories. He has also written three Sunday Times bestsellers: ‘Blood and Sand’, ‘Far Horizons’, and his debut novel ‘Crisis’, published in June 2016. While filming in Saudi Arabia in 2004 Frank was shot six times at close range by terrorists but survived with major injuries. With a degree in Arabic & Islamic Studies from Exeter University, his passion for the Middle East is undiminished. From 1997-2000 he was the BBC’s Gulf Correspondent in Dubai, then BBC Middle East Correspondent in Cairo. He was awarded the OBE by HM The Queen in 2005 for services to journalism, Honorary Doctorates of Laws from 6 British universities, the McWhirter Award for Bravery, Spain’s El Mundo Prize for International Journalism, the UAE’s Zayed Medal for Journalism, voted Person of the Year by the UK Press Gazette and appointed Distinguished Visiting Professor of 2015 by the University of Southern California. He is currently writing the sequel to ‘Crisis’.
Keynote Speaker:
Gal Messinger
Head of Global Security
Philips Lighting

Visionary leader with 39 years of security expertise both in the public and private sectors STMicroelectronics – 13 years, CSO dealing with Risk Management, Physical & Logistics Security, Brand Protection, Product Security, Business Continuity and Crisis Response, as well as Business and Competitive Intelligence.
Philips Lighting – 1.5 year, CSO of a centralized security department, Cyber and products domain included.
European Semi-conductor Industry Association – ACTF – Founder & Chairman (involved with TAPA DoD/DoJ/ICE/CBP/HLS/FBI/NCIS/ASIS) and SIA/ESIA-ACTF member)
Governmental  Security  – 23 years.
BA & MA studies in International Relations.

Chaired by:
Simon Scales
Former Head of Investigations EMEA
BP plc

Simon has over 30 years significant investigative, security and compliance related experience, formed from an extensive corporate and law enforcement background. He is recognised for having conducted complex Bribery, Corruption, Fraud and Misconduct investigations worldwide, in regulated and non-regulated arenas. He is internationally recognised for his public speaking credentials and his vast experience, having successfully led, directed and managed investigation, ethics, compliance and integrity teams within Europe, the USA, Africa and the Middle East. He has also been instrumental in delivering investigative services to the key emerging markets of South America, India and China.
International speaker panel:

When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.

Experience + value = story.

  • do you have a compelling business security story that simply must be told?
  • have you recently worked on an innovative security project?
  • are you willing to openly share inspiring insights, expertise and ideas to advance the security community?

We welcome your input into shaping the agenda and speaker panels.

Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.

For further information, please

+44 (0)20 7936 8989
or

teampulse@pulseconferences.com

Meet the Speakers – CSO 360 Congress Amsterdam 2017
Partial List

Stuart Seymour

Stuart Seymour

Group Head of Security and Resilience, Centrica

Stuart is the Group Head of Security and Resilience for Centrica and assumed his role on 5 November 2012. Prior to this he was the Head of International Security Operations for Lockheed Martin having been the Regional Security Senior Manager for UK, Europe and the Former Soviet Union, helping to establish Lockheed Martin’s International Security Operations alongside its Director. Before joining Lockheed Martin, Stuart was a Director at The Risk Advisory Group and Kroll. During his time in the Army, Stuart saw active service in Sierra Leone with the UN where he received a High Commissioner’s Commendation, Bosnia and Northern Ireland. He discovered a lost city and Inca road in Bolivia. Stuart was also honoured by being selected to carry The Order of the Garter during the Her Majesty, The Queen Mother’s funeral. Stuart graduated first in his class from the Chilean Army School of Intelligence where he majored in counter insurgency, as well as The Royal Military Academy, Sandhurst and Birmingham University, where he achieved a Starred First Class Honours in Spanish and Hispanic Studies. Stuart is an Army Scholar, English Speaking Union Scholar, on the OSAC UK Executive Committee, been granted the honour of being a Freeman of the City of London and was Master the 15th of the Worshipful Company of Security Professionals between 2015 and 2016. On 2 November 2012 Stuart had the US flag flown above the Capitol in Washington DC in honour and recognition of his service to Lockheed Martin and support to the national security of the United States and its Allies. He is bilingual (Spanish) and also speaks French. Stuart is a keen climber though finds invariably that the older he gets the better he was. He also coaches Windsor Rugby U 10s.

Peter Drissell

Peter Drissell

Director Aviation Security, Civil Aviation Authority

Peter was appointed by the Civil Aviation Authority (CAA) as its first Director of Aviation Security in May 2013. Peter led the transfer of the Aviation Security function (and some 90 posts) from the Department for Transport (DfT) to the CAA, which took place as planned on 1st April 2014. Peter now leads the Aviation Security Directorate within the CAA, as a member of the CAA Executive Committee, developing its regulation and compliance roles within the context of the CAA’s broader aviation regulation responsibilities. A key aim is to evolve aviation security regulation into a process that is more performance and risk based. Before joining the CAA, Peter served for 5 years as the Director Security & Business Continuity for the Home Office. Prior to joining the Home Office, Peter had served for 32 years in the Royal Air Force, from which he retired as an Air Commodore in April 2007. Peter’s last appointment as Air Officer Force Protection combined the roles of Commandant General of the Royal Air Force Regiment and Air Officer RAF Police (formerly Provost Marshal RAF).

Dr. Victoria Baines

Visiting Associate, Oxford Internet Institute

Victoria is an experienced cybersecurity professional with a demonstrated history of working in the internet industry and international law enforcement. Published academic author and futurist with a strong research background. Skilled in Crisis Management and Response, Negotiation, Intelligence Analysis, Strategy Delivery, and Coaching.

Andy Williams

Andy Williams

VP Business Development and Quality Assurance, Safehotel Alliance AB

Andy Williams is VP Business Development and Quality Assurance for Safehotels, an international hotel security certification company based in Sweden. Andy has over 20 years of international safety, security and crisis management expertise within hotel, real estate development and travel security risk management fields. On the Association and volunteer leadership front, Andy has served as a Regional Vice President for ASIS International, the technical review committee for international security standard PSC1; advised the UK government on counter terrorism and public safety initiatives, presented to the EU Council and most recently published a case study paper on crisis management for United Nations UNISDR.

Jeroen Meijer

Senior Partner, Control Risks

Jeroen Meijer serves as a Senior Partner and leads Control Risks’ business in the Benelux (Belgium, The Netherlands and Luxemburg), with offices in Amsterdam and Brussels. With his team, he is responsible for advising Control Risks’ clients on issues related to risk management, security management, crisis management, business continuity and crisis communications. His main competencies and experience consist of developing, implementing and maintaining global risk management, crisis management and crisis communications structures for both corporate and government clients. This includes the design of risk and crisis management strategy and policy, the development of plans, procedures and teams and the execution of scenario-based crisis exercises and training, aimed at developing both individual and team knowledge and skills. In the case of an actual crisis, Jeroen advises and supports clients throughout the different steps of managing the incident. He is also the Americas representative on Control Risks’ global maritime security team. Prior to Control Risks, Jeroen was a communications consultant in The Netherlands, coaching and training leaders in business and government in effective communication with stakeholders through presentation and media training. During his tenure he specialized in reputation management and crisis communication, benefitting from his operational crisis management experience and his expertise in strategic crisis management. In this capacity Jeroen consulted with clients from both the profit and not-for-profit sectors. The first 18 years of his career, Jeroen served as an officer in the Royal Netherlands Navy in numerous management positions in various regions of the world. This career laid the foundations for his extensive operational crisis management knowledge. Jeroen still serves as a lieutenant commander in the Royal Netherlands Navy Reserve, specializing in merchant marine operations in risk areas. Jeroen holds a degree in mathematics from the Royal Netherlands Navy Academy/Delft University of Technology with a specialization in system reliability engineering/integrated logistic support and an honor Master of Arts degree in corporate and crisis communication from the Erasmus University of Rotterdam. He is fluent in both Dutch and English and has a good working knowledge of French and German.

David Langhorn

VP Global Head of Security & Intelligence, Business Reputation & Responsibility - Global Risk - Security & Intelligence Team, IHG®

Richard Sumnall

EMEA Regional Head of Security, Uber (Netherlands)

Prior to his current role with Uber, Richard built and led the EMEA Threat Operations team. Other responsibilities include partnering with legal, policy, communications and operations teams to manage complex security threats in conjunction with government and law enforcement partners.Investigations – Technical investigation and attribution of threats/abuse to individuals; Research – Industry leading information gathering, threat analysis and threat assessment; Law Enforcement Outreach – Proactive relationship building between the business and law enforcement; Law Enforcement Response Team (LERT) – Responding to law enforcement requests in a timely manner

Derek Cheng

Derek Cheng

CSO, TalkTalk

An experienced information security leader with over 19 years of professional experience in information and cyber security, IT, risk management, privacy and data compliance. Derek has recently joined TalkTalk as their Chief Security Officer, where he is building and leading the cyber security strategy and team to protect TalkTalk’s critical infrastructure, assets, and customer data. Previously, he was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, Derek spent over 6 years at Deloitte & Touche where he managed and performed a multitude of information security and risk management engagements for several global Fortune 500 companies across various industries including financial services, technology, consumer business, manufacturing, and public sector. His primary areas of expertise include developing and leading tactical and strategic security strategies, building and maturing security teams, and ensuring executive governance around security to manage risks appropriately. Derek has also published information security articles and white papers and has been a presenter/panellist at CISO conferences. Derek holds a Bachelor Degree in Computer Science from the California Polytechnic State University, San Luis Obispo CA.

Richard Zijdemans

Richard Zijdemans

Director of Security EMEA, APAC & Greater China, Medtronic

Richard is a corporate security specialist with a broad experience in Physical and IT security, Investigations and the development of security infrastructure in the widest sense. He is a true security evangelist, always connecting the field with the business, delivering value added services.

Alexander Gaft

Alexander Gaft

Group Director Investigations, VEON

A fraud prevention and discovery professional, with more than 15 years of proven experience, Alexander is a Certified Fraud Examiner (since 2007). He has been a CISA since 2009. With hands-on experience from both Law Enforcement, Big 4 and Corporate, with in-country, regional and Group roles, he has good insight into CIS/FSU, Central Asia and Eastern Europe. A proven track record in establishing Investigation teams and uncovering material losses.

Graham Edwards

Graham Edwards

Head of Group Security, Nationwide

The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He currently holds the position of Director of Data Security at Nationwide Building Society. Graham has a master’s degree in Information Security from Royal Holloway.

Paul Heffernan

Paul Heffernan

Group CISO, Unipart

Paul is the Group CISO for Unipart Group of Companies. With nine years’ experience in the cyber security world, including consulting to some of the world’s biggest brands, he engages with the business at board level to enable trusted secure commerce. With an ‘ethical hacker’ background, he is able to address complex security challenges but is equally passionate about driving effective change through unambiguous leadership and communication. Paul is a regular speaker at various industry conferences such as the e-Crime Congress, PCI London and the GBI CISO Summit. When he isn’t keeping Unipart safe, you can find him tinkering with code and figuring out how to inspire the next generation of cyber security professionals. Paul is proud to be shortlisted as CISO of the Year 2017. You can reach him on LinkedIn or on Twitter at @pjh_22.

Dr. Sally Leivesley

Dr. Sally Leivesley

Director, Newrisk Ltd, A Founder Member, The Exercise Group7

Sally advises companies and governments on catastrophic risk where losses to companies and governments may involve critical functions essential for operations and reputation. She runs exercises to stress test critical function failures and resilience capability. Dr. Leivesley is known for her appearances on aviation terror attacks, ISIS, Al Qaeda, Al Shabaab and other international terrorism, cyber breaches, CNI protection and government policy on the BBC World Service, ITV This Morning and other UK based media and European, Middle East and Australian media. She raised the forensic importance of the risk of cyber hijacking of flight MH370 which was the subject of a Discovery Channel documentary and has been a commentator on the risks relevant to Donald Trump economic, terror and nuclear influences during his Presidential campaign and on his election. Dr Leivesley works in conjunction with The Exercise Group7 (TEG7) a London based group of companies that specialise in resilience operations for cyber-attacks, international terrorism and nation state threats and solutions for business and government-critical infrastructure. The focus is on testing through exercises, assurance and pen tests using an integrated approach to all hazards including social factors. (www.Teg7.co.uk) In the UK she has been a member of the technical committee for the first IET (formerly IEE) guidance document on Resilience and Cyber Security of Technology in the Built Environment which was supported by the Centre for the Protection of National Infrastructure. She is also a member of the British Register for Security Engineers and Specialists established to advise at a strategic level on terrorist and other extreme threats to critical infrastructure. She interfaces with a USA company to extend exercising for aviation and energy industries. Dr Leivesley originally trained as a Scientific Advisor with the British Home Office. She is a specialist in CBRN.

Steve Wright

Steve Wright

Data Privacy and Information Security Officer, John Lewis Partnership

Steve joined The John Lewis Partnership in April 2016 and is responsible for both the Information Security and Data Privacy, both of these enable the John Lewis Partnership to protect the personal data of our customers and partners, to be compliant with data protection laws and regulations, and to provide trust and transparency – resulting in greater brand experiences across our digital, mobile and ecommerce channels.

Steve is passionate about big data and all things digital. With more than 20 years’ experience, designing, developing, managing and delivering transformational data, governance, privacy and security programmes, Steve’s vast experience as a pragmatic and charismatic leader, ideally places him as a ‘trusted advisor’ at board level on all privacy and security related matters. Steve is also a published author, a non-executive director and is regularly invited to speak at industry events, trade associations and thought leadership working groups, working towards continually finding new ways to increase trust and transparency in respect of consumer services, business functions and product vendors.

Steve strongly believes that governance, cyber security and privacy are all inextricably linked as they share common objectives and principles, and therefore, require satisfactory safeguards and assurances. From a business perspective, this can be achieved by building ‘data trust and assurance’ programmes based on the fundamental principles of transparency, accountability, protection, integrity, confidentially and availability, accompanied by clear policies and delivered through comprehensive training, integrated procedures and a robust compliance regime.

Having once served as a CISO, and held senior roles at, Unilever, Deloitte, PwC, Siemens and Capita, Steve has a full appreciation of what is required to get the job done in a cost effective, pragmatic and timely fashion with a natural ability to lead from the front, to coach others and to take responsibility consistently, courageously and with integrity.

Michael Holstein

Head of Security Africa, UNHCR

Maitham Al-Lawati

Maitham Al-Lawati

General Manager, Risk, Compliance & Managed Security Services, Oman Data Park

Maitham is part of the executive management team that joined to establish the first cloud & managed service provider in Oman. Maitham has more than ten years of professional experience in cyber security.

Suzanne Oyen

Suzanne Oyen

Head of Global Corporate Security, SWIFT

Suzanne Oyen has a degree in Social Sciences and obtained a Master in Criminology with a thesis on Public Private Cooperation in Corporate Security matters. After graduation she joined G4S Cash Services where she had to deal with a series of brutal organized crime attacks on Cash in Transit and had to coordinate both the prevention and the response with the police and security services. In 1999, she became the first Corporate Security Manager of Proximus, Belgium’s premier Mobile Telecom Operator. In 2002, she was asked to set up the Mobbing Department at Belgacom (today Proximus), the main Telecom Operator in Belgium. 14 years ago, she was recruited by the Society for Worldwide Interbank Financial Telecommunication (SWIFT) to Head the EU operations of the Corporate Security Department. Since 2006 she has been appointed as Head of Global Corporate Security with a worldwide responsibility. She regularly participates as speaker at security conferences to share experiences and expertise in the security sector and promotes public private collaboration.

Neil Jarvis

Director of Information Technology, Aston Martin Lagonda

Xander Heemskerk

Director Product Security - Personal Health in the Product and Services Security Office (PSSO) at Philips

Xander Heemskerk is the Director Product Security – Personal Health in the Product and Services Security Office (PSSO) at Philips. In this role he drives the Product Security programs and initiatives for Personal Health and Population Health businesses worldwide. IOT, Mobile Apps and Big data are crucial parts of the Products and Services delivered by Personal Health and Population Health Management.

Prior to Philips Xander was the CSO at TomTom and the CISO at Royal Vopak and has been responsible for Corporate Security, Information Security, Information Risk Management and Product Security strategies, tactics and operations.

Xander has over 25 years’ of experience in almost all aspects of IT ranging from Consulting, Security, Architecture, Performance tuning, Development, Coding, Testing and Operations in different roles and positions at Oracle, Orient Overseas Container Lines (OOCL) ltd, Hong Kong Government, Everett (now PWC), Ricoh and at multiple customers in a consulting role. For Oracle University he provided training classes on Architecture, Security, Performance, High Availability and Identity Management for customers and internal staff.

Xander holds a bachelor degree in Informatics from The Hague University of applied sciences, is a Certified Information System Security Professional (CISSP) since 2002 and has Certified Cloud Security Knowledge (CCSK) since 2013.

Tim Williams

Tim Williams

Senior Advisor, Global Risk Intelligence, McDonald's Corporation

Tim is responsible for standing up an intelligence service to support McDonald’s international lead markets. He previously ran a corporate intelligence boutique in London, providing business & strategic intelligence and political & security risk services to a broad set of multinationals. He has extensive experience building in-house and supplier analyst teams, managing complex projects in high-risk jurisdictions, cultivating human sources, developing business and bringing new products to market.

Ned Farmer

Ned Farmer

Geopolitical Risk Manager, American Airlines

(OSAC) Aviation Security Working Group (ASWG) and on the Executive Board of the OSAC Latin America Regional Council (LARC). Before American Airlines, Ned spent four years at Royal Dutch Shell, where, as the Americas Security Analyst, he was responsible for assessing security and political risks to Shell’s operations throughout the Western Hemisphere. Prior to Shell, Ned spent over two years at Virtual Defense and Development International, Inc. (VDI), where he worked as the principle Security and Intelligence Analyst for the Inter-American Development Bank (IDB). In this capacity, he was in charge of risk analysis covering 26 countries in Latin America and the Caribbean. Ned has also worked in the United States Congress, as an aide to Rep. Ileana Ros-Lehtinen (R-FL), former Chairwoman of the House Foreign Affairs Committee, and at Morgan Stanley. His graduate coursework focused on both European energy security and terrorism, and his thesis analyzed the threat posed by terrorist radicalization among Muslim immigrants in Europe. Ned has studied, worked, and lived in both Europe and Latin America; he has traveled to over 75 countries. Ned received his B.A. in Political Science from McGill University in Montreal, Canada, and his M.A. in International Affairs from American University in Washington, DC. He also studied at the Universidad de Salamanca in Salamanca, Spain. He is fluent in Spanish and proficient in French. Ned was born and raised in New York City.

Robin Hamilton

Robin Hamilton

CEO, Aldbury International

Robin joined the UK Police in 1990 and undertook a wide variety of roles that encompassed patrol, investigation, riot control and covert operations. As a Fulbright Scholar, Robin attended the FBI academy researching Less Lethal technologies. Subsequently promoted to the rank of Superintendent Robin oversaw an Operations & Major Incident Centre. As a designated critical incident & firearms commander he gained an in-depth knowledge of and expertise in managing crises. In 2005 Robin was seconded to the Foreign & Commonwealth Office with responsibility for all aspects of diplomatic security in the Balkans. Robin then moved into commercial security in 2008 first with Fidelity International and then AonHewitt. In 2010 Robin joined GE’s global operations team as regional director of security responsible for delivering physical security, investigation and crisis management across multiple business sectors. Robin is now the CEO of Aldbury International a security and crisis management consultancy that brings this commercial knowledge, expertise and hands-on experience to a wide range of organisations.

Tom Brabers

Representation, ASIS Benelux (& Former Head of Global Security, Geodis Freight Forwarding)

Tom Brabers CPP, CFE represents ASIS Benelux in his capacity as chapter secretary. He is the former Head of Global Security of Geodis Freight Forwarding and now works as an independent consultant in the field of strategic risk consultancy and knowledge brokerage. He has a fascination for the Extended Enterprise and organizational design.

Elizabeth Lawler

Elizabeth Lawler

VP of DevOps Security, CyberArk (and Co-Founder, Conjur Inc.)

Elizabeth Lawler is Vice President, DevOps Security at CyberArk. CyberArk, the market leader in Privileged Account Security, secures secrets and machine identities in highly dynamic DevOps environments at scale. Lawler is responsible for CyberArk’s DevOps business strategy and execution.
Prior to CyberArk, Lawler was CEO and co-founder of Conjur, a DevOps security company acquired by CyberArk in May 2017. Lawler has over 20 years of experience working in highly regulated and sensitive data environments. Prior to founding Conjur, Elizabeth was Chief Data Officer of Generation Health and held a leadership position in research at the Department of Veterans Affairs. She has been a programmer herself and is constantly working to help organizations move to a true DevSecOps delivery model that supports greater business agility.
Elizabeth is a member of the MassTLC Security Advisory Board.

Alex Wilson

Alex Wilson

Security Solution Architect, CyberArk Software Ltd

Alex Wilson is Security Solution Architect at CyberArk Software Ltd. With over 5 years’ experience in Privileged Account Security, Alex is one of the leading experts in understanding the requirements and drivers for managing privileged access security within an organisation. Alex has led some of the largest design and implementation programs of privileged account security with companies across all sectors, many of which are in the Fortune 100. Leveraging this experience, Alex now focuses on privileged account security best practice with organizations embracing Cloud and DevOps.

Sponsors

CyberArk

CyberArk is the only security company laser-focused on striking down targeted cyber threats, those that make their way inside to attack the heart of the enterprise. Dedicated to stopping attacks before they stop business, CyberArk is trusted by the world’s leading companies — including more than 50% of the Fortune 100 — to protect their highest-value information assets, infrastructure and applications.

For over a decade CyberArk has led the market in securing enterprises against cyber attacks that take cover behind insider privileges and attack critical enterprise assets. Today, only CyberArk is delivering a new category of targeted security solutions that help leaders stop reacting to cyber threats and get ahead of them, preventing attack escalation before irreparable business harm is done. At a time when auditors and regulators are recognizing that privileged accounts are the fast track for cyber attacks and demanding stronger protection, CyberArk’s security solutions master high-stakes compliance and audit requirements while arming businesses to protect what matters most.

With offices and authorized partners worldwide, CyberArk is a vital security partner to more than 3,300 global businesses, including:

CyberArk has offices in the U.S., Israel, Australia, France, Germany, Italy, Netherlands, Singapore, Turkey and the U.K. Learn more about CyberArk by listening to Udi Mokady, Chairman & CEO discuss Privileged Account Security.

www.cyberark.com

icetana

iCetana’s innovative dynamic live monitoring system provides a more effective approach to the monitoring of large-scale video surveillance networks. iCetana uses computer vision and machine learning to learn what is normal in a video camera scene and then identifies anything not-normal that requires attention. This provides surveillance operators with an immediate opportunity to assess and action safety, security and operational events before they escalate. iCetana has proven itself in City Centres, transport, shopping malls, campuses and utilities. http://www.icetana.com

Safehotels

Safehotels is the first company to develop an independent, global hotel security Certification standard to enable corporate hotel room bookers and travellers to identify hotels with enhanced and committed security and safety measures. This is turn enhances travel security management duty of care and compliance programs. There are over 55 countries and 100 city destinations with Safehotels Certified hotels, the number of destinations and hotels increase each year. Safehotels is also a member of United Nations UNISDR, ICCA International Congress and Conference Association, verified by a major insurance company and gaining rapid recognition and awareness with major travel management companies within the corporate hotel room booking market. www.safehotels.com

Control Risks

Control Risks is an independent, global risk consultancy specialising in political, integrity and security risk. We help some of the most influential organisations in the world to understand and manage the risks and opportunities of operating in complex or hostile environments.

We support clients by providing strategic consultancy, expert analysis and in-depth investigations through to handling sensitive political issues and providing practical on the ground protection and support.

Our unique combination of services, our geographical reach and the trust our clients place in us, ensures we can help them effectively solve their problems and realise new opportunities across the world. Working across five continents and with 36 offices worldwide, Control Risks provides a broad range of services to help our clients manage political, integrity and security risk. www.controlrisks.com

Supporting Organisations

ASIS International

We are committed to:

We have adopted as our mission to enhance information sharing between public and private sectors. It is our overall goal to promote professionalism in the security management profession and to enhance ethical behaviour.
www.asisonline.org

CSO 360 Congress unites world-class CSOs, corporate security, intelligence and resilience directors to develop best practices and standards. Pulse will position your company and offering as a thought-leader in the security community.

You and your team will be an integral part of the programme and a dedicated networking schedule. We guarantee you will leave Amsterdam with a wealth of new business connections, as well as new professional friends!
Place your CEO and security R&D executives on the podium or co-present a case study with a client. Fine-tune your market solutions, messages and approaches to further enable secure platforms for clients.

No typical industry barrier between buy and sell – natural integration between R&D leaders, CSOs, investigators and threat intelligence directors – we are all part of the security discussion!

Who attends

Why attend

Chief Security Officers / Corporate Security Directors and;

Directors of:
Investigations
Business Continuity
Security Risk Management
Threat Management Intelligence / Cyber Threat Intelligence
Security Operations
Illicit Trade
Loss Prevention
Fraud Prevention
Corporate Crime
Information Security

  • Hear concrete practice strategies from your most senior security peers from around the world – multiple nationalities represented!
  • No vendor centric presentations, in-house security real life experiences from those who lead on the job day in day out on how to protect people, profits, reputation and information.
  • Get insights on the current threat an risk landscapes and examples of how to use horizon scanning effectively to learn from recent incidents and build an integrated incident response capability.
  • Hear how peers are protecting intellectual property.
  • Stay ahead of the competition as security becomes an increasingly important driver of business value.
  • Hear how CSOs can forge new roles and standards in the age of IoT and digital transformation.
  • Embrace technology, change management and winning investment strategies for innovative security.
  • Discuss how are key business areas maturing and how can we stay ahead of change amidst an ever more complex threat landscape and supply chain.

Venue & Accommodation

W Amsterdam 

Spuistraat 175, 1012 VN Amsterdam, Netherlands
http://www.wamsterdam.com/

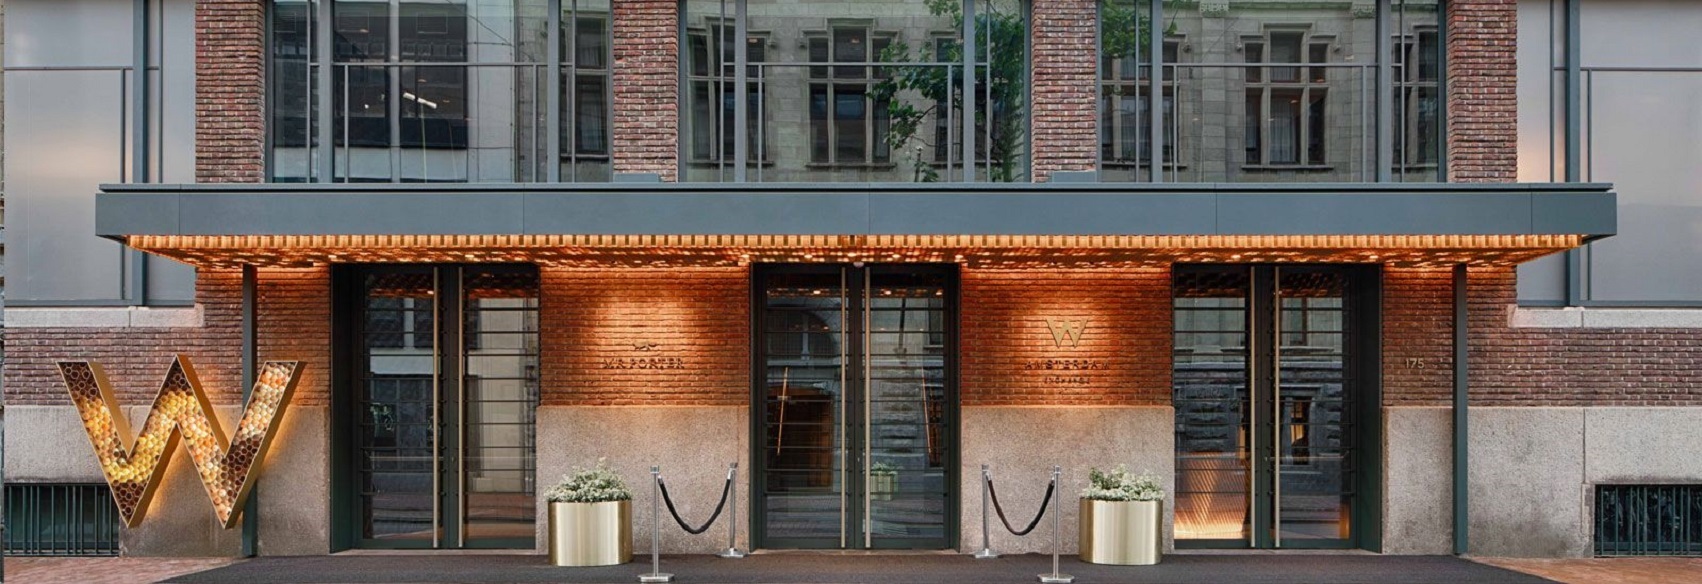
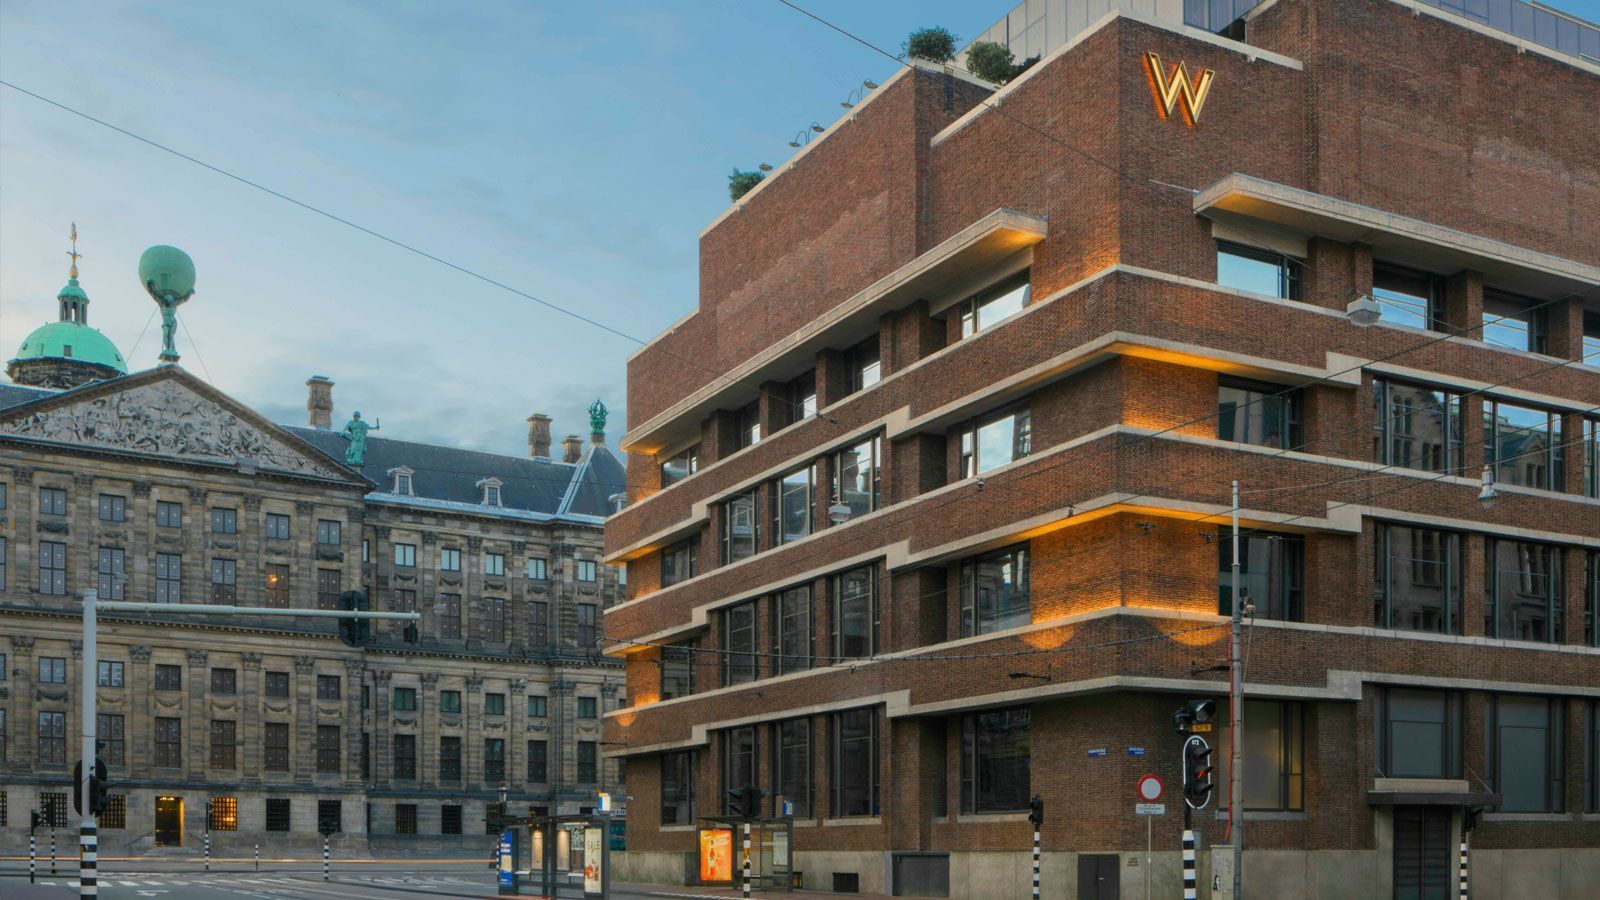
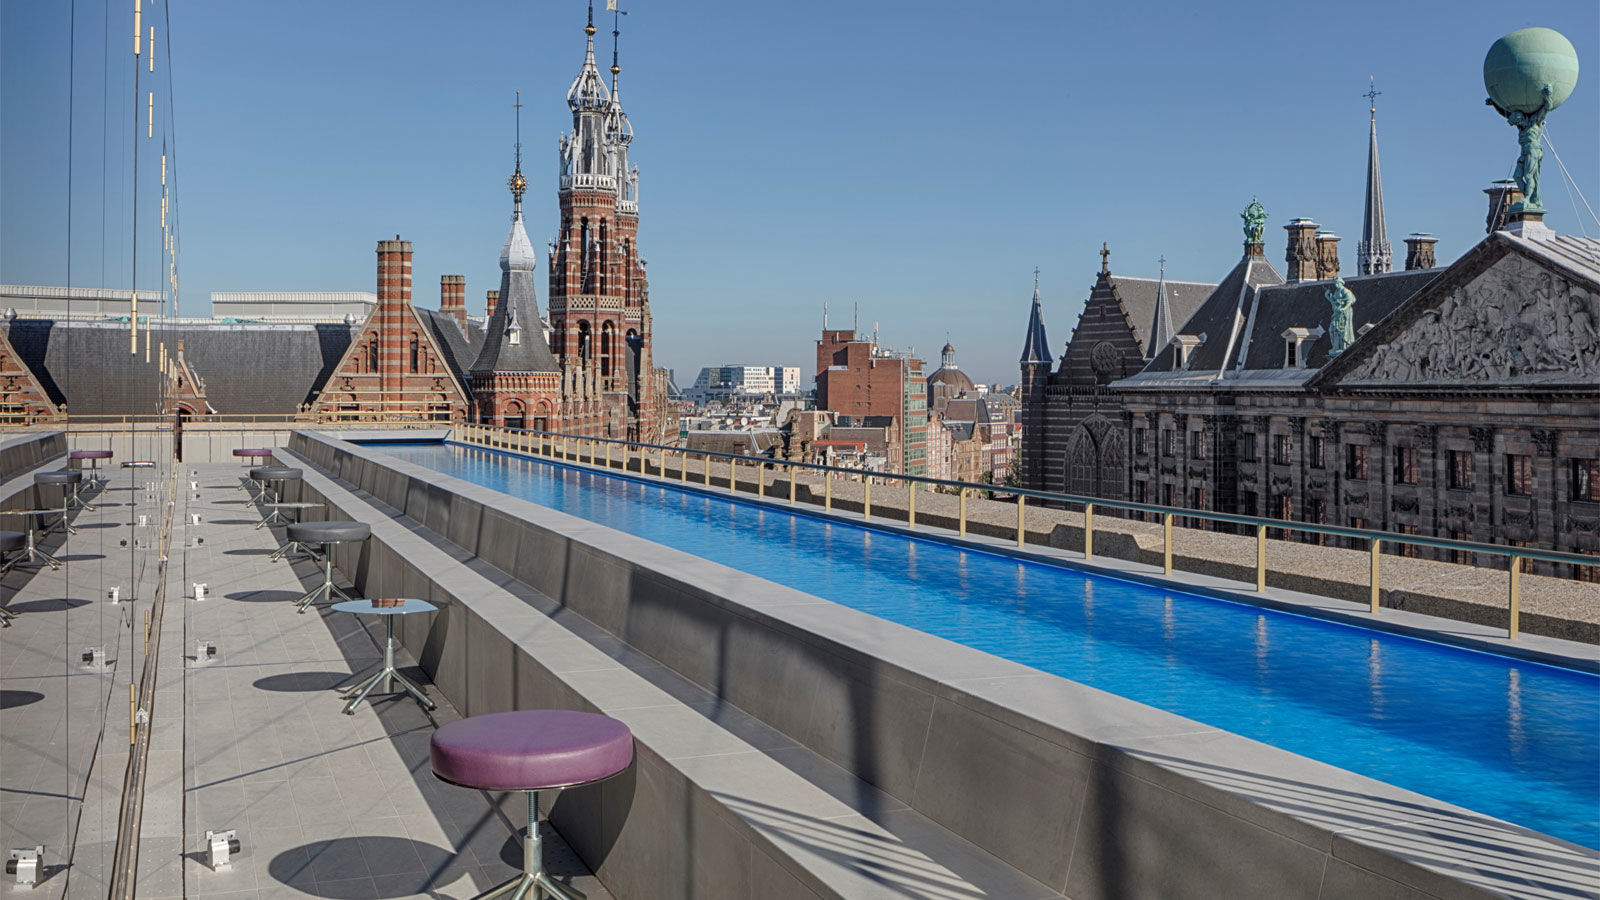
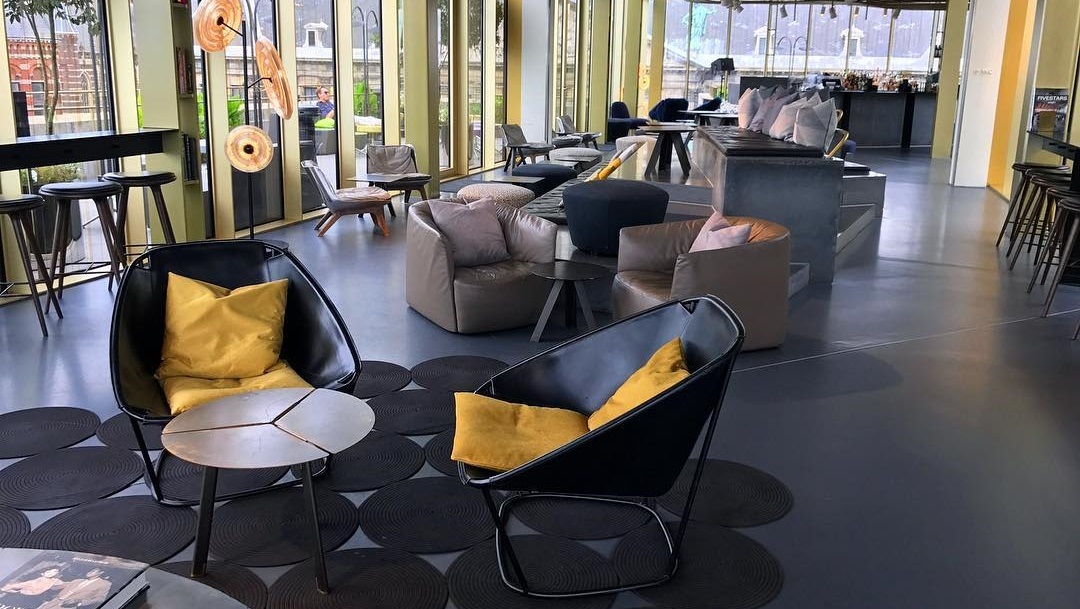
CSO 360 Amsterdam was hosted at W Amsterdam, originally the Royal Dutch Post’s main communication center and the KAS Bank building. Mixing historical Dutch architectural elements with cutting-edge design right next to Dam Square. The W Lounge rooftop bar offers spectacular views between the Royal Palace and the UNESCO-listed Singel canal.

Accommodation at the CSO 360 Congress Venue 

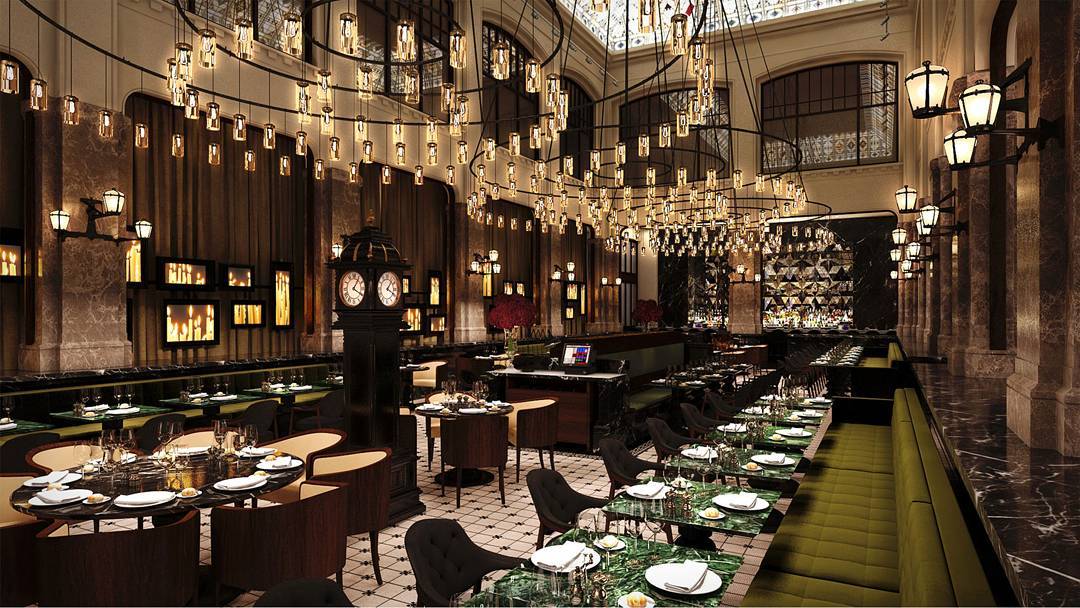
W Amsterdam is split across two unique buildings, a former telephone exchange building and a bank with an intriguing design mix of heritage and contemporary style. The hotel offers 238 stylish guestrooms across the Exchange and the Bank with captivating views, integrated spaces and interesting lines that echo its previous role in connecting the people of Amsterdam.

Pulse Conferences can offer discounted prices at the W Amsterdam of €270 (£242) per night, single occupancy inclusive breakfast. (+ city tax)

Please contact sanna.lindstrom@pulseconferences.com for further details.

Alternative Accommodation 

All of the below hotel options are within a 6-10 minute walk to The W Amsterdam.

The Times Hotel

Hotel CC

Acostar Hotel

Conference venue

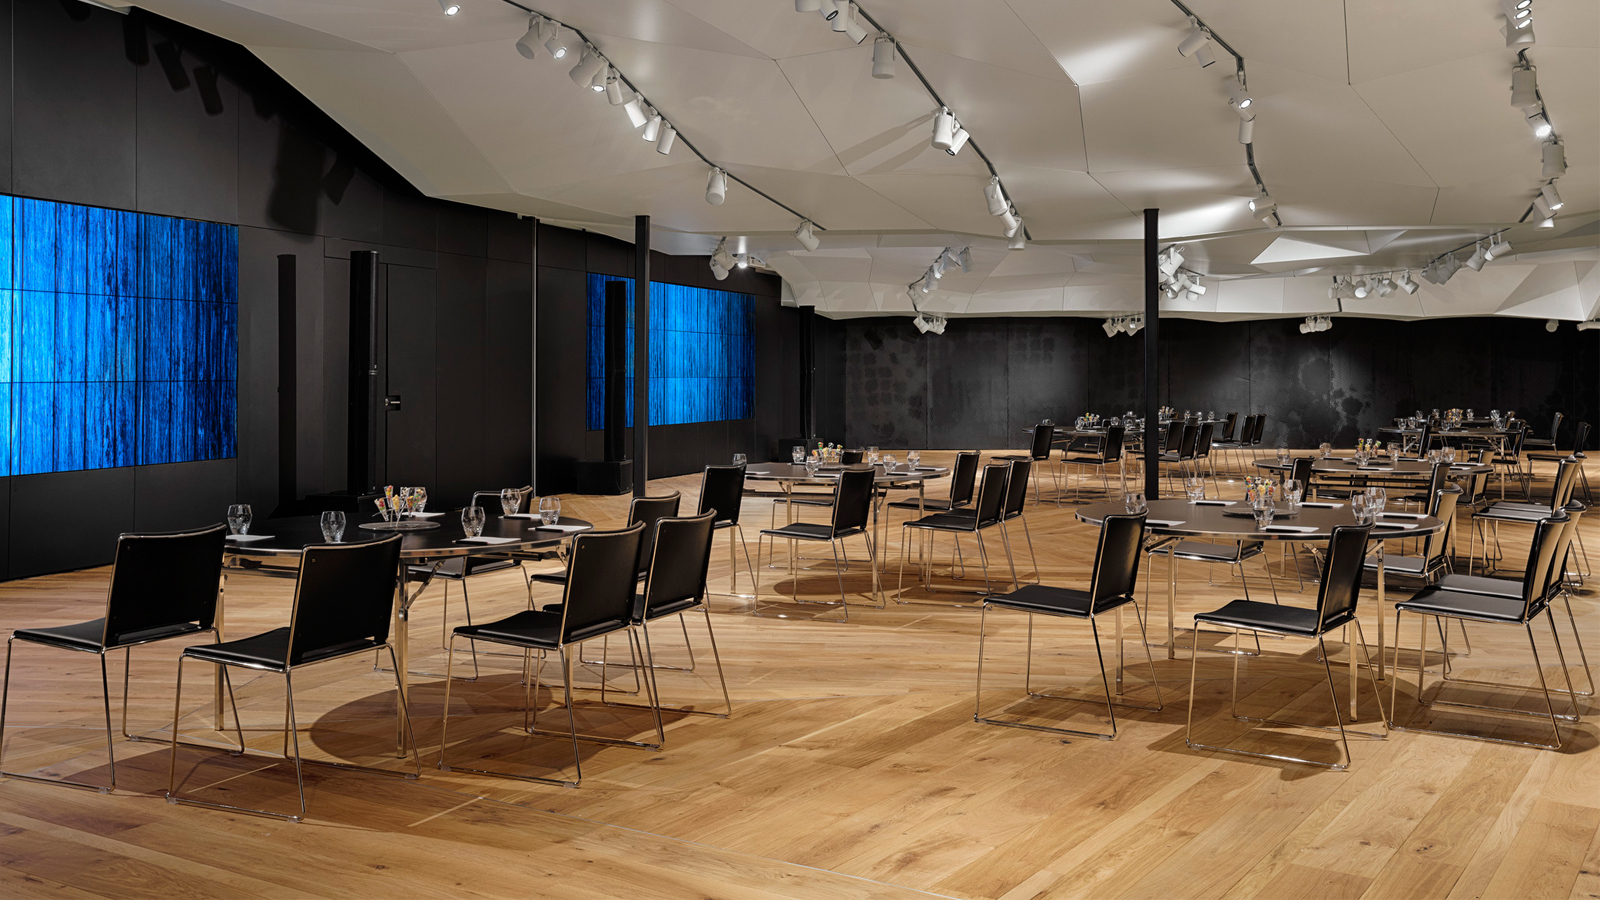
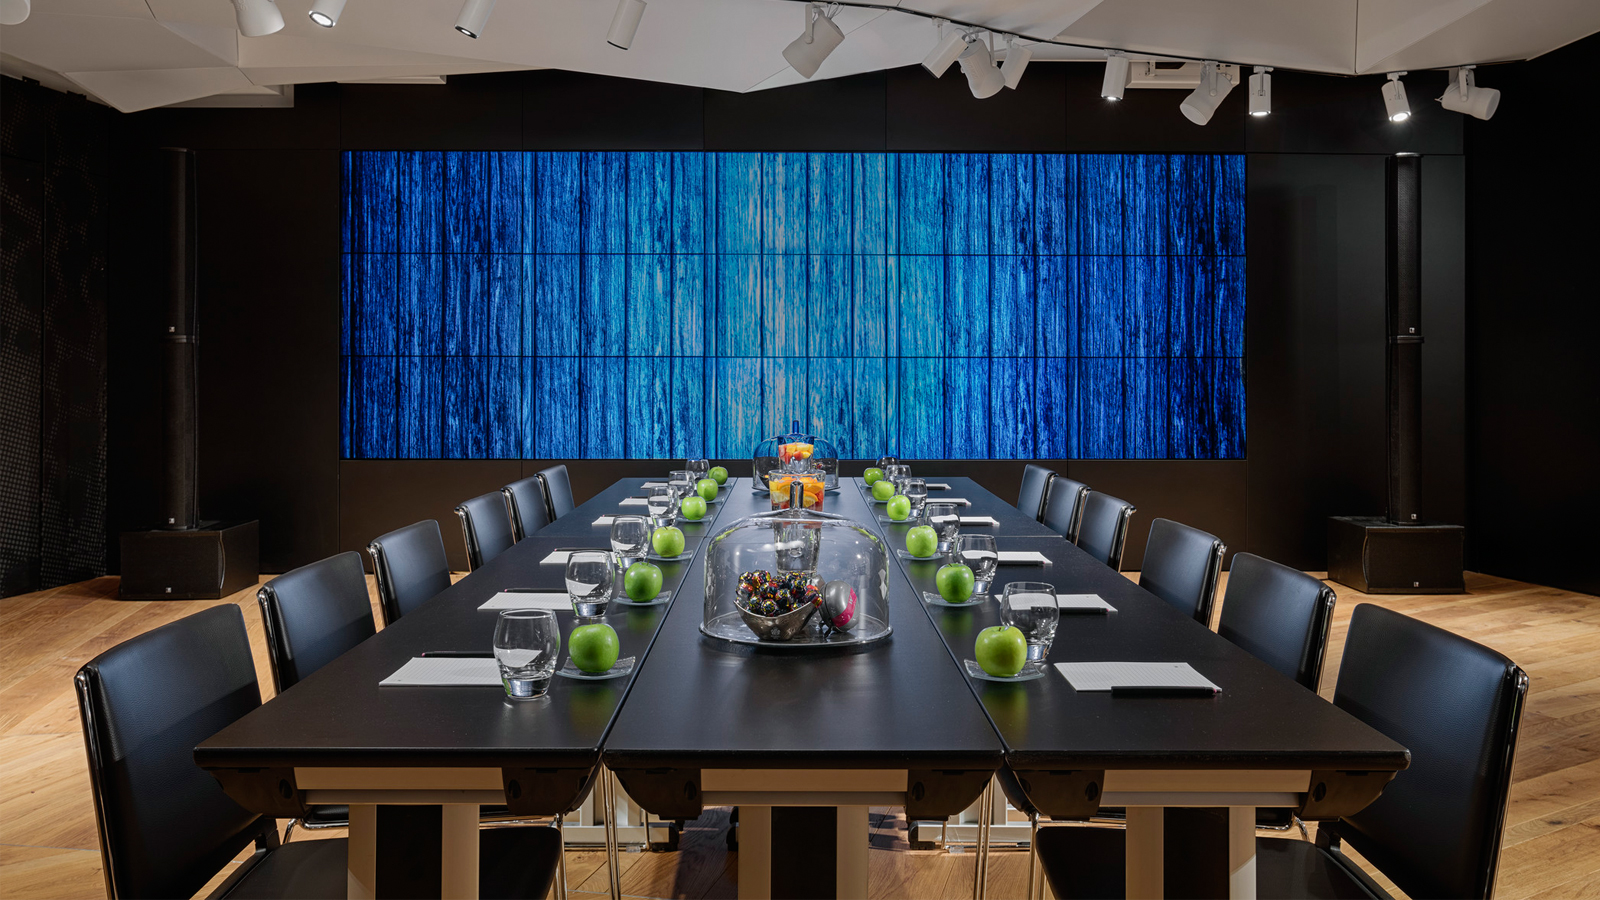
W Amsterdam has newly renovated and modern event spaces over 414 square meters which was the perfect space for CSO 360 Congress in Amsterdam. The hotel has fully adaptable conference equipment delivering flawless audio visual equipment for innovative speaker presentations and panel discussions. Coffee breaks was hosted in the private foyer and the W Lounge is the perfect networking space with unparalleled 360-degree views over the city.

Location

W Amsterdam is located in the city centre just off Dam Square, near the iconic canal district. The hotel is a 5 minute walk from the boutiques of the 9 Streets district and the historical heart of the old town.

  • 2 minutes to the Royal Palace Amsterdam
  • 5 minutes to Amsterdam Floating flower market
  • 11 minutes to Amsterdam Centraal Station
  • 12 minutes to Rijksmuseum
  • 15 minutes to the Van Gogh Museum
W Amsterdam

Testimonials CSO 360 Congress, Amsterdam 2017

“Embraces the changing threat environments, great experience, fabulous speakers,                                                    pertinent interesting focus”

Special Tribunal for Lebanon (The Hague)

“Simply the best event for security practitioners. Real expertise and knowledge sharing”

Group CISO, Unipart Group (UK)

“A great one stop shop of the top CSO minds!”     

VP, Corporate Security
and Resilience, Pearson (UK)

“Overall this has been a fantastic event. Awesome speakers addressing a diverse range of interesting and                                                       relevant topics.  Also,                                                      great job by Team Pulse.                                                     We have been looked                                                 after so well! Thank you!”

Regional Security Director, Caterpillar Inc (Switzerland)

“I was extremely impressed by the content, quality, origination and administration of                                                            the Pulse product”

MD, Tierra Nova Solutions (Sierra Leone)

“I just had the best conference ever!”

CCO, BT (Netherlands)

Video Testimonials