3rd CSO 360 Congress
4-6 December 2019, Kempinski Budapest
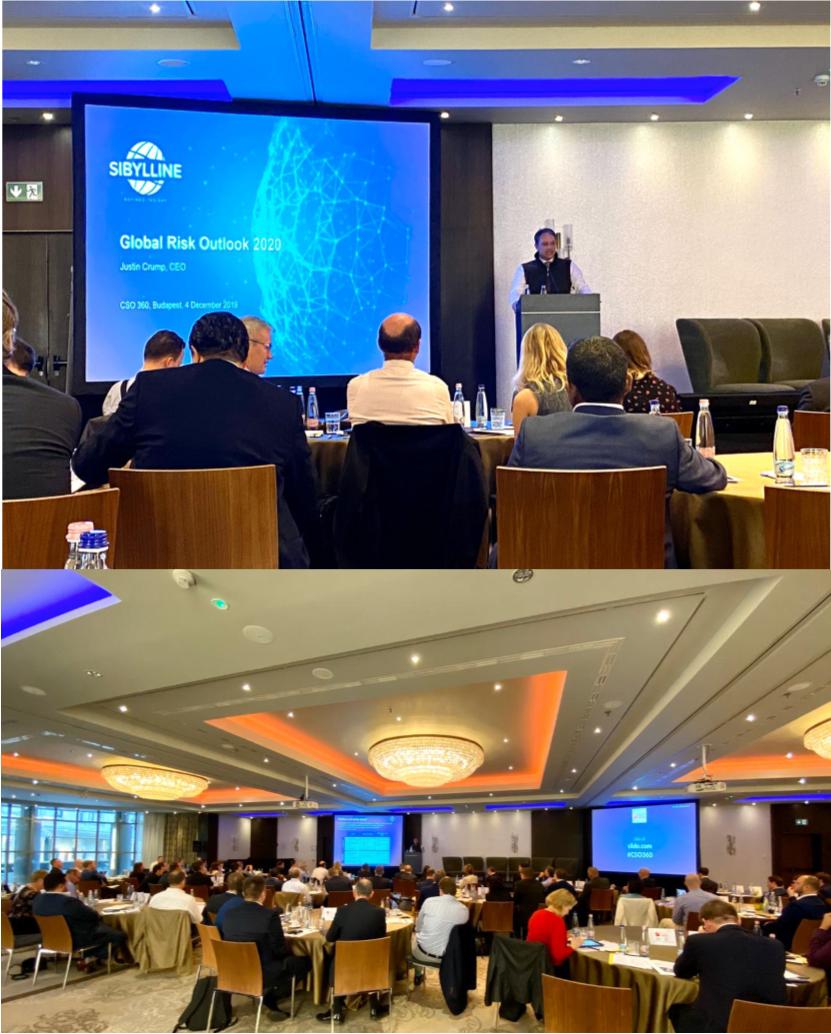
Pulse Conferences would like to thank everyone who participated in the 3rd CSO 360 Congress hosted on 4-6 December 2019 at the Kempinski Corvinus in the wonderful city of Budapest.
“The Pulse 360 CSO Congress provided significant value and information in a short timeframe, particularly with regard to tradecraft, best practices, and networking.” – Claire Prestwood, Senior Security Intelligence Analyst for the Americas, Cargill
“The CSO 360 Conference was a fantastic opportunity to exchange information and perspectives in a collegial environment.“ – Patrick Kane, Senior Director of Security, Atlas Air
“The CSO 360 Conference was a fantastic opportunity to exchange information and perspectives in a collegial environment.“ – Patrick Kane, Senior Director of Security, Atlas Air
Connecting minds on security, resilience, intelligence and investigations priorities to protect people, profits, property and reputation
This trusted, community-based meeting is now an annual fixture in the diaries of Chief Security Officers and directors of intelligence, investigations, resilience and business risk. It enables truly global peer to peer sharing. We pride ourselves not only on who is on stage but who is in the room to bolster stimulating discussion and to share practical use cases on security challenges, successes, strategies and intelligence on the emerging threat landscape.
CSO 360 Congress tackles priority challenges for Chief Security Officers, most of whom oversee diverse areas and teams covering in corporate security, cybersecurity, information security, fraud, physical and executive and travel security, resiliency, forensics and investigations. Held under The Chatham House Rule, the programme offers a silo-busting, integrated and converged security focus to reflect the backdrop of increasing levels of global volatility, uncertainty, complexity and ambiguity.
- Connect with global security leaders
A new expert international panel of security experts will bring real experiences to pool brain power on the sustainability of global business amidst rapidly evolving threat landscapes and changes in geopolitical, technological and financial spheres. - Innovate your security strategy
Partake in this share of strategies, tactics and methods for improving the protection of clients, employees and business partners as well as the security of assets, information and reputation. - Leave inspired for action
Exchange practical approaches, innovation and strategies on the emerging threat horizon. - New for 2019! CSO 360 Roundtable – We have added the Roundtable on Friday morning (6 December)! This is a pure benchmarking discussion held under The Chatham House Rule. No presentations, the attendees set the agenda.
Congress Chairman:
- Simon A. Scales, (former) Head of Investigations (FTSE 100) and Director of Global Investigations (AEX) companies
2019 International Speaker Panel:
- Andy Williams, VP Business Development & Quality Assurance, Safehotels (SWEDEN)
- Anthony Leray-Meyer, Regional Security Manager Western Europe Global Security, Abbott (UK)
- Armin Sick, Manager Aviation Security, Lufthansa (GERMANY)
- Basha Galvin, Head of Investigations, Tullow Oil (& Association of Corporate Investigators)
- Bob Shaw, Senior Security Advisor, United Nations (and Co-Founder, The Exercise Group)
- Cedrick Moriggi, Global Head of Security and Resilience (CSO), LafargeHolcim (UK)
- Dr Christoph Rojahn, Partner, Compliance & Forensic, KPMG AG (GERMANY)
- Claire Prestwood, Senior Security Intelligence Analyst for the Americas, Cargill (USA)
- Crawford Robinson, Group Head of Investigations, British American Tobacco (UK)
- David Jesson, Sr. Analyst, Global Intelligence/ Incident Management, Royal Caribbean Cruise Lines (USA)
- Derek Cheng, CSO, TalkTalk (UK)
- Dvir Rubinshtein, Aviation Security Operation Center Manager & Aviation Security Expert, Security Division, Israel (ISRAEL)
- Eduardo Jany, Executive Officer, Global Security Operations, Bloomberg LP (USA)
- Guillermo Gaspoz, Global Security Advisor, DSM (NETHERLANDS)
- Henry Wilkinson, Head of Intelligence & Analysis, Director, The Risk Advisory Group
- Heimo Grasser, Regional Head of Security CEMA, Medtronic, and Chief Awareness Strategist, SAME Solutions (UAE)
- István Szabó, Chief Security Officer, Budapest Airport (HUNGARY)
- James Richardson, Group Head of Security, The Weir Group (and Chair of SHE EXCOM) (UK)
- Justin Crump, CEO, Sibylline Ltd
- Marcus Alldrick, Digital Risk Management, Security and compliance advisor
- Mark Reading, Managing Director, Seneca Risk (SIERRA LEONE)
- Mark Wolsey, Group Security Director, CRH plc. (UK)
- Matthew Judge, Group Managing Director, Anvil Group (UK)
- Mehdi Khoali, Principal Investigations Officer, African Development Bank (Ivory Coast)
- Mike Croll, Global Security Advisor, International Commission on Missing Persons (ICMP) (Netherlands)
- Mike Lycett, Group Head of Security and Risk, De La Rue (UK)
- Michael Mallard, Security Professional (USA)
- Ned Farmer, Geopolitical Risk Manager, American Airlines (USA)
- Liz Chamberlin, Executive Director, International Security Management Association (ISMA)
- Lady Olga Maitland, Founder, Defense & Security Forum, Chairman, Copenhagen Compliance (UK)
- Patrick Kane, Senior Director of Security, Atlas Air (USA)
- Robert Aldous, Group Head of Operational Security & Intelligence, Prudential (UK)
- Ryan Long, Head of Global Intelligence, McDonald’s Corporation (USA)
- Dr Sally Leivesley, Director, Newrisk Ltd & Founder Member, The Exercise Group7 (TEG7)
- William Sandover, Special Adviser, Intelligence and Analysis, Risk Advisory & International Affairs Adviser, Cathay Pacific Airlines (UK)
Key themes to date for CSO 360 Congress 2019 include
Strategies, tools and tactics required to proactively predict and mitigate threats….
-
- HORIZON – Geopolitical insights into the global security landscape – hotspot mapping and predictions
- LEADERSHIP – Culture, privacy and behaviours, engagement
- INTELLIGENCE – Building effective intelligence; emerging threats
- AVIATION & TRAVEL – Aviation security – decision-making behind the scenes!
- INVESTIGATIONS – Investigations Roundtable
- RISK – Cyber, privacy, data and identity, emerging realities
- PLAN B – Response, crisis, emergency and business continuity
Agenda at a Glance – Budapest 2019
Timings are still approximate
Tuesday 3 December
19:00-21:00 Welcome Reception – Kempinski Budapest Hotel
Wednesday 4 December
Day One – CSO 360 Congress
08:45-09:00 Coffee
09:00 Chairman’s Opening
13:00-14:00 Lunch – Kindly sponsored by: SafeHotels Alliance
17:30 Close of Congress day one
18:00-22:00 Networking – Reception and dinner cruise on the Danube – Kindly Sponsored by: Sibylline
Thursday 5 December
Day Two – CSO 360 Congress
08:45-09:00 Coffee
09:00 Chairman’s Introductions and objectives
13:00-14:00 Lunch – Kindly sponsored by: One Voice
17:15 Close of Congress day two
18:00-21:30 Networking – wine-tasting and dinner
Friday 6 December
CSO 360 Roundtable
Pure benchmarking discussion. Attendees shape the agenda!
08:45-09:00 Arrivals and coffee
09:00-09:15 Chairman’s Introductions and objectives
13:00-14:00 Lunch and goodbyes
Hear directly what speakers, sponsors and delegates thought.
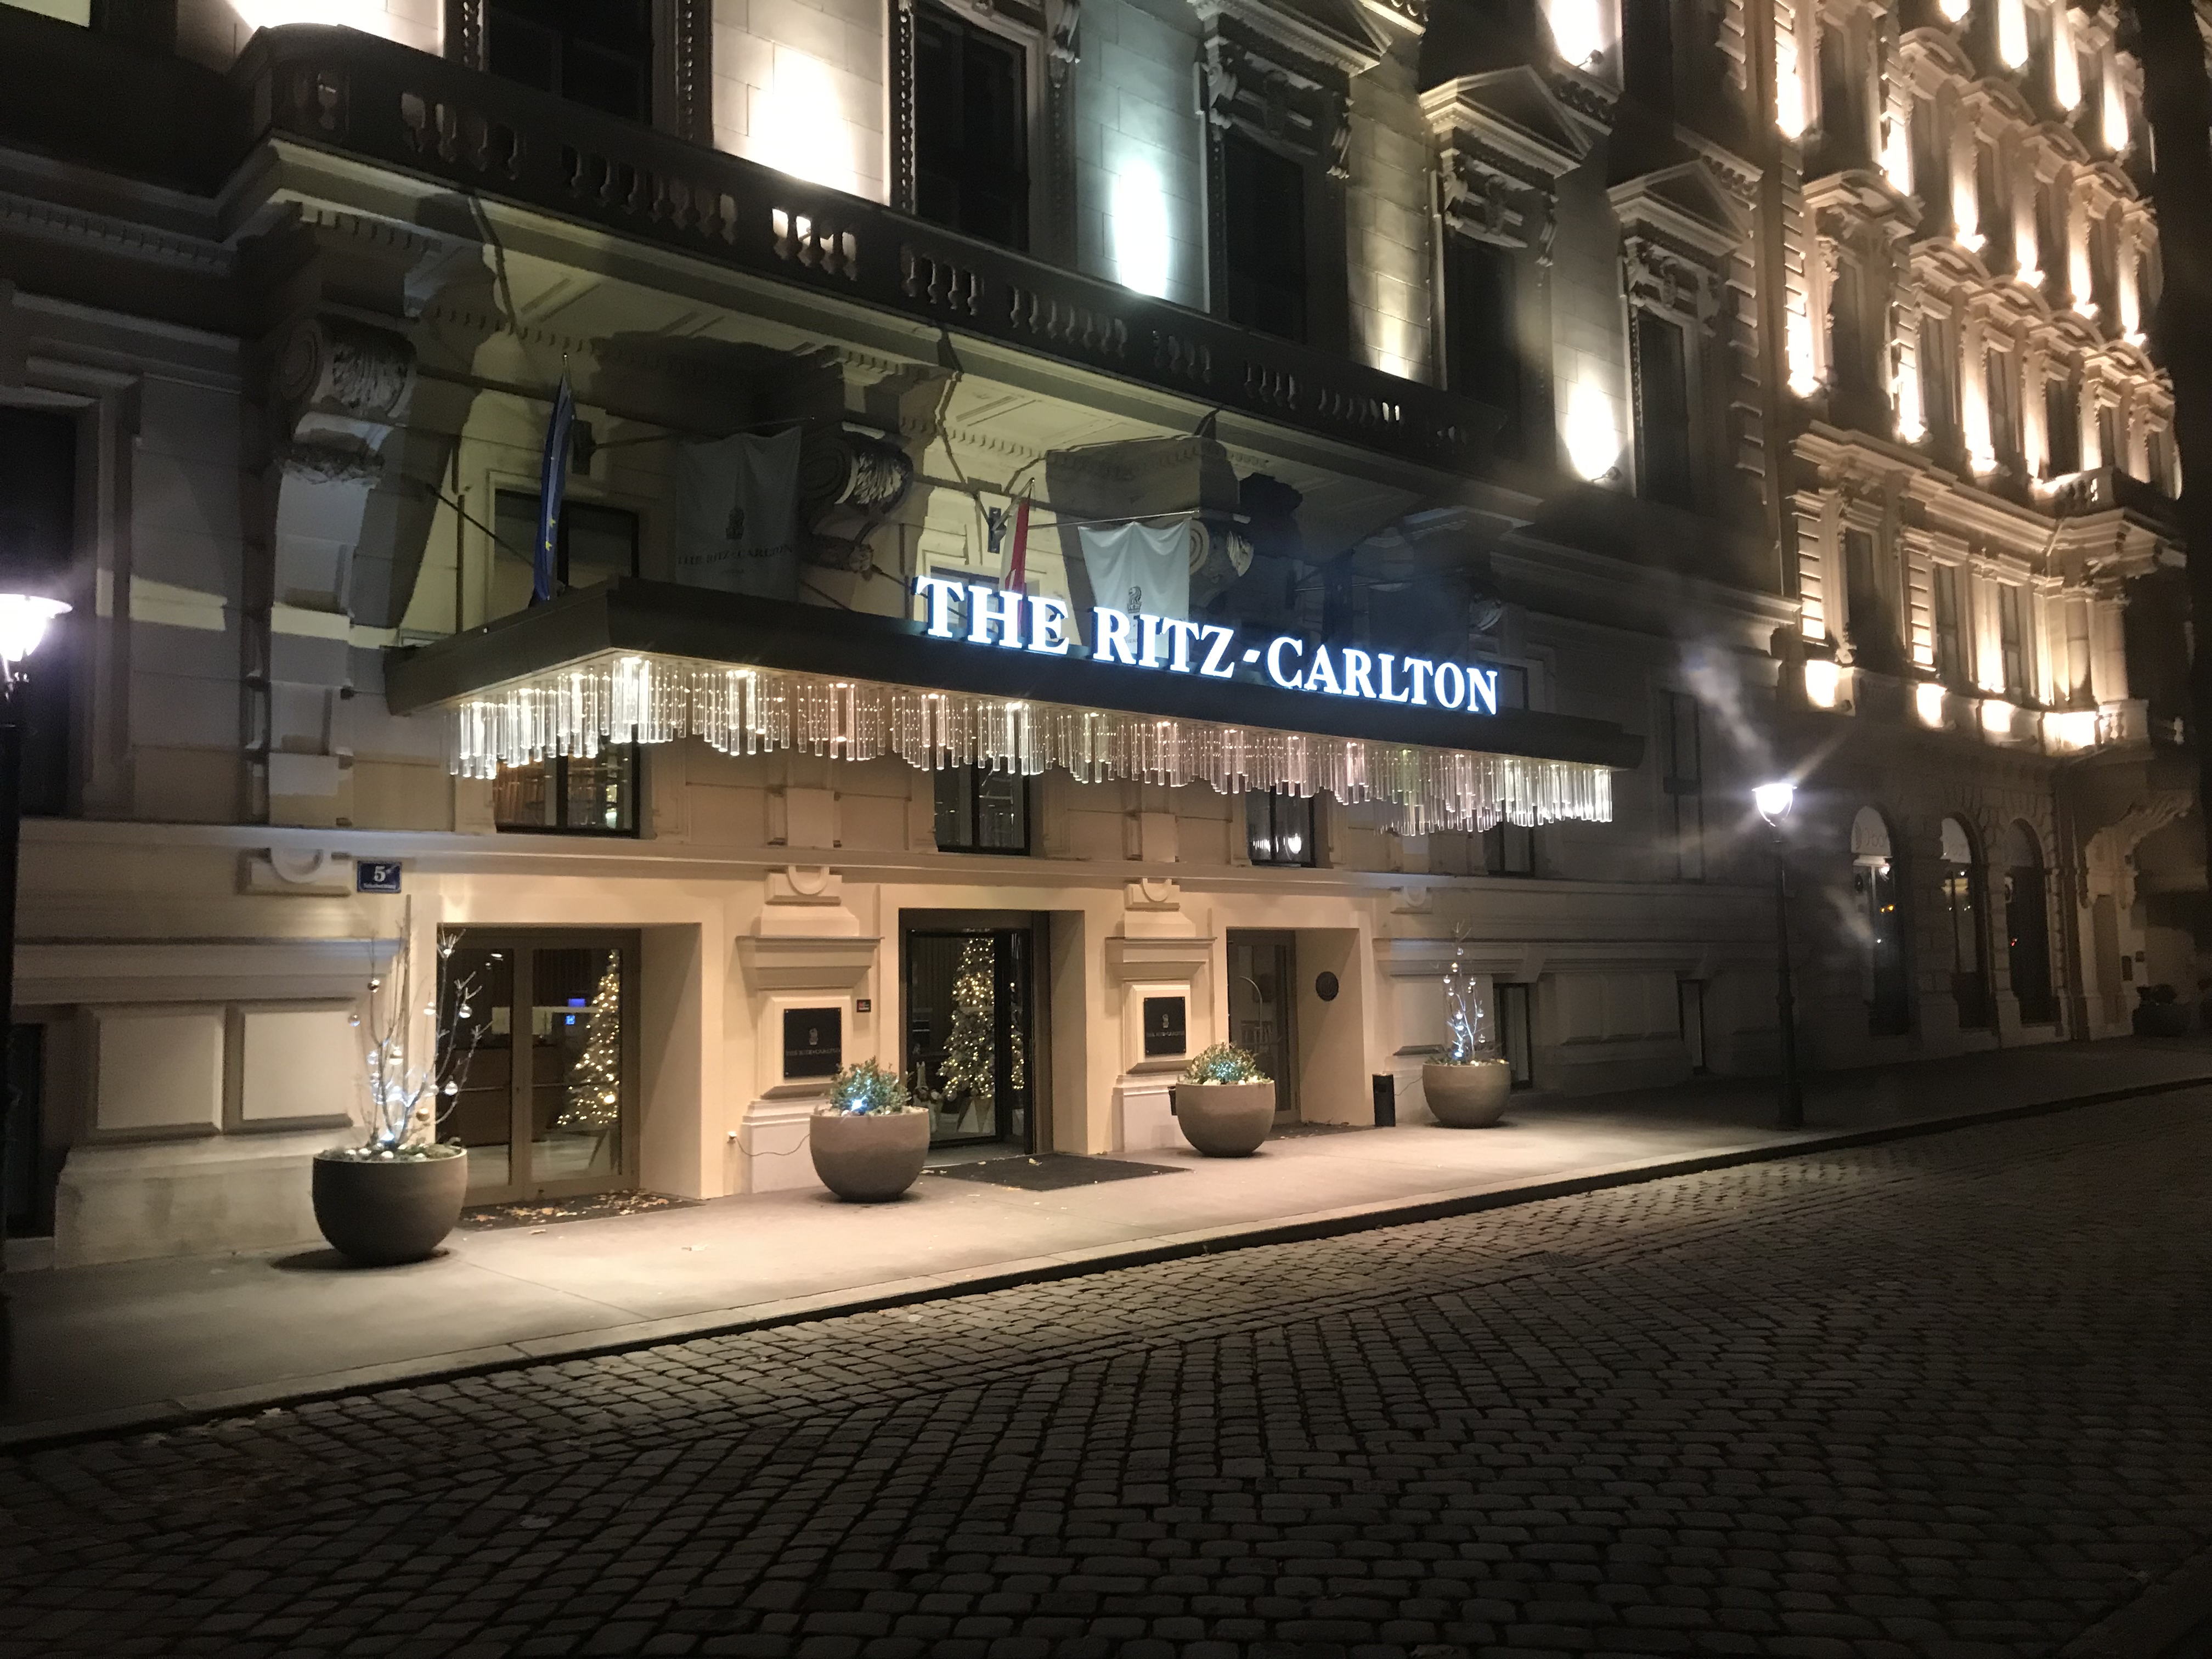
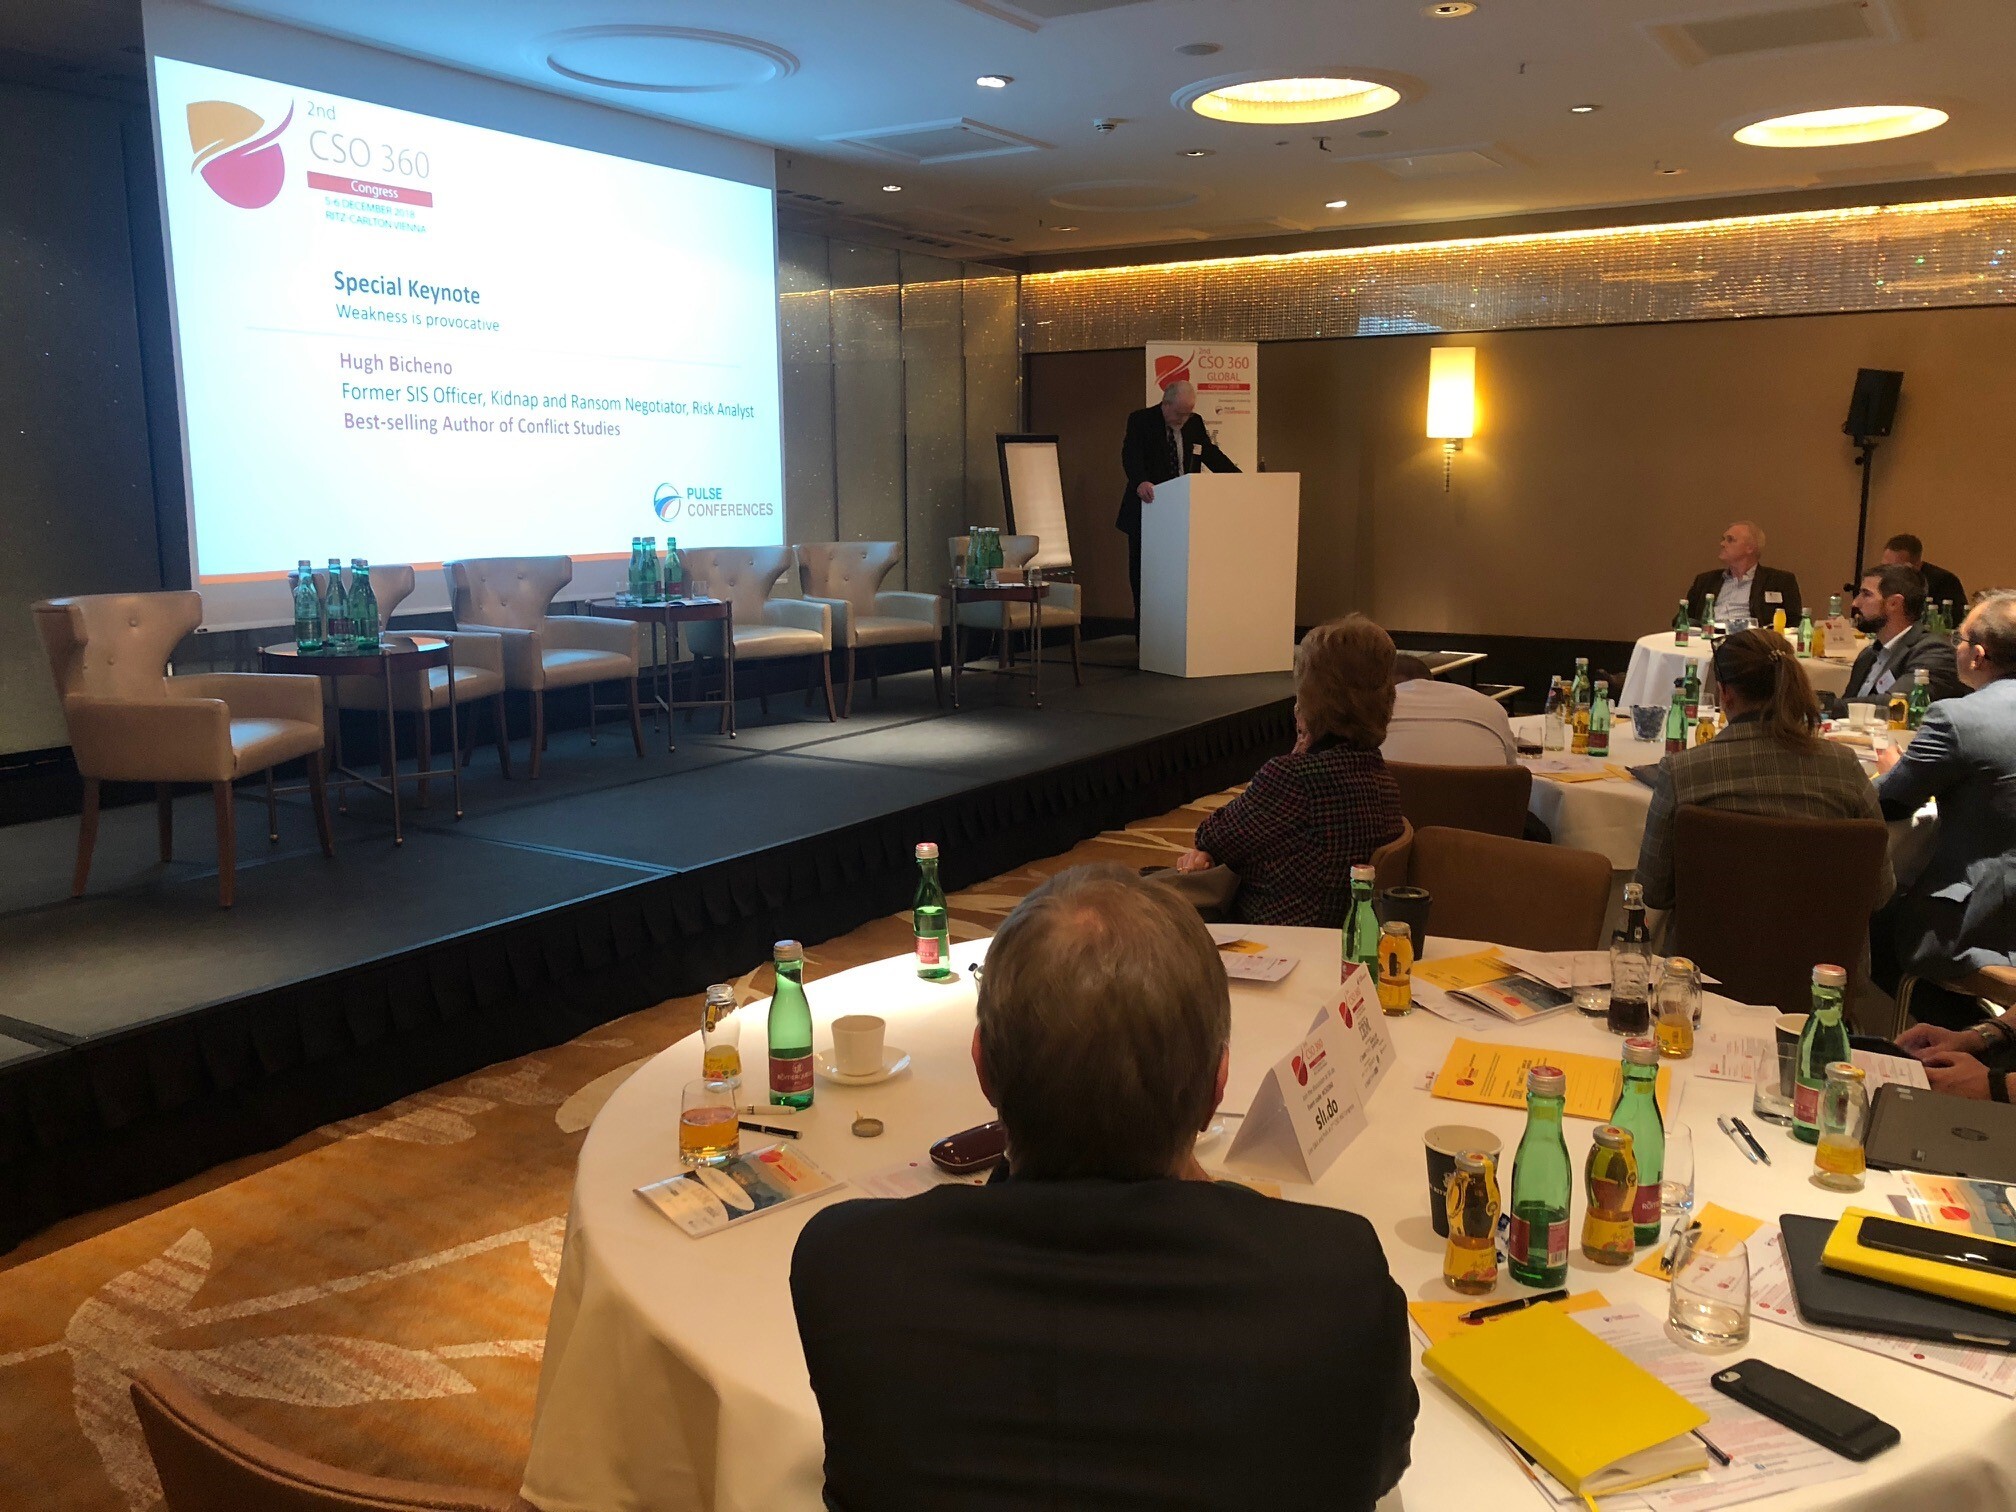
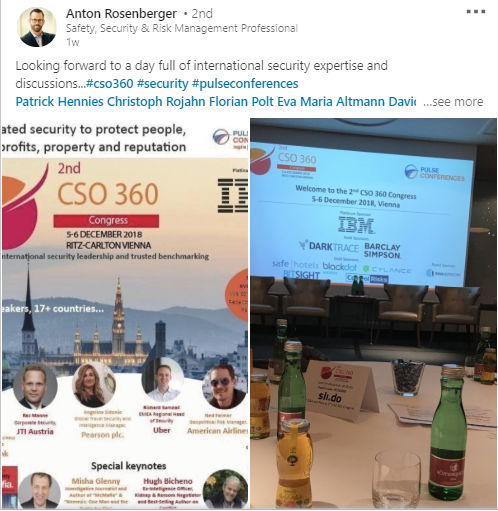
Pulse Conferences would like to thank all speakers, sponsors and delegates who participated in the 2nd CSO 360 Congress, hosted in December 2018 in Vienna. See Archives here.
“Embraces the changing threat environments, great experience, fabulous speakers, pertinent interesting focus”
Special Tribunal for Lebanon (The Hague)
“I just had the best conference ever!”
CCO, BT (Netherlands)
“A great one stop shop of the top CSO minds!”
VP, Corporate Security and Resilience, Pearson (UK)
“I was extremely impressed by the content, quality, origination and administration of the Pulse product”
MD, Tierra Nova Solutions (Sierra Leone)
“Simply the best event for security practitioners. Real expertise and knowledge sharing”
Group CISO, Unipart Group (UK)
“This has been a fantastic event. Awesome speakers addressing a diverse range of interesting and relevant topics. Also, great job by Team Pulse. We have been looked after so well! Thank you!”
Regional Security Director, Caterpillar Inc (Switzerland)
Networking events – an integral part of any CSO 360 Congress experience!
All delegates, speakers and sponsors are encouraged to attend. There is no extra cost.
Our special dinners, receptions and cultural activities ensure that you will leave the event with new professional friends and international contacts!
Pulse Conferences Privacy Policy
To read about Pulse Conferences Privacy Policy and download in pdf format please click below.
Download Privacy Policy
Gold Sponsor
Networking Sponsor
Lunch Sponsors
Panel Sponsors
Cyber Physical Threat – Bridging the Cultural Divide
Written by our inhouse resident editor, Lyndsay Turley, an experienced communicator and cybersecurity advocate for over 15 years.
As a concept, the convergence of cyber and physical security has always been seemed logical. In practice however, while many can agree that the threats to physical and IT infrastructure are increasingly similar, the defences are anything but. Despite many years of talking about convergence, accountability for emerging areas of cyber-physical risk remains unclear. As both operational and IT drive forward technically, the gaping hole in organisational security seems to be widening.
“People can buy commercial drones with awesome cameras; analyse Street View on the Internet; and take advantage of social engineering for intelligence gathering. Things that were the preserve of governments are now cheap and accessible for others. There is a lot out there,” warned one CISO 360 speaker, a former intelligence officer, at our Congress in Rome last month.
Cyber physical threat became a persistent theme at Congress this year, with a role to play in most of the “top 5” concerns to emerge from event discussions – ranging from the human ingenious social engineering, through to the risk of long life IoT encryption becoming obsolete in a quantum era and of course the persistent lack of security by design embedded into the proliferation of connected fridges, kettles, toys and more.
The most telling moment emerged from an interactive group exercise, when the CISOs in the room admitted they were unclear who should or who would be best placed to manage the threat coming from an autonomous drone flying outside of a tall building. The threat was to the safety of the building and the employees within, therefore a physical security issue that was deriving from a sophisticated piece of technology. Questions over accountability for the maintenance of sophisticated air conditioning systems met with similar response, yet all in the room were familiar with infamous case histories of vulnerabilities in these systems that had been successfully exploited.
Discussions pointed to cultural differences between information technology, plant and operational technology, and industrial technology preventing genuine collaboration and leaving different areas of the business to march forward on their own. This was illustrated by Telstra when they put SCADA risk at the top of threat landscape in their Security Report this year citing companies increasing dependency on automation. “Organisations are working with multiple vendors and are not aware of all the possible devices that may reside on the same network. Vendors tend to manage exposures to the outside world which means that overall security is now much more affected by industrial suppliers than before.”
“It is not that the risks aren’t acknowledged but the pressures are changing. Air gap is becoming a dirty word, even for legacy systems, with the pressure to integrate industrial systems more and more,” said one workshop participant, who pointed out that advances in robotics are being made to, for example, avoid the need to shut down for scheduled maintenance, and underpin availability as a key objective for industrial systems. Specialised controllers have become the backbone of process control, including SCADA systems.
“The real challenge is the different priorities, practices, technologies and cultural issues that create real tensions between information technology and operation technology groups,” he said.
Our group did suggest that the timing for a convergence plan, and shared responsibilities may be approaching as the long-established operational priorities around safety concerns, not just economic loss, increasingly become at risk to cyber-attacks. This thought was aptly illustrated by a university researcher who shared his motivation for looking into the security of robotics: “We particularly looked at robots and security because of the fundamental change in how robots are being deployed. They (and the humans operating them) used to be protected in separate spaces, cages. Now humans are not just operating robots they are interfacing with them,” he said. “We need to be fundamentally redesigning cyber-physical systems to, not just avoid concerns, but allow them to achieve their purpose in the case of a hack.”
My observation is that this conversation remains immature despite the decades of talk. We may well be approaching a tipping point for the convergence of cyber-physical risk with the rise of the machines, their autonomy, and their connection to our corporate networks but we haven’t yet figured out how to bridge that cultural divide that appears to be leaving us vulnerable.
The conversation is set to continue. Cyber physical risk and security convergence is a key theme for the upcoming CISO 360 Asia in Singapore this September and CSO 360 Congress in Budapest in December, international think tanks that are developed and hosted by Pulse Conferences. Join us if you can. The more experience, the closer we get to resolution and move the agenda forward as communities.
Pre-Event Pulse Educate Security Courses: Monday 2- Tuesday 3 December
Optional Training courses are offered in Budapest, pre-CSO 360 Congress, by Pulse Educate.
*All courses are subject to a minimum number of registrants
Monday 2 December, 08:00-17:00
Tuesday 3 December, 08:00-15:00
1. OSINT – Advanced Skills for CSOs
COURSE OUTLINE
2. Catastrophic Risk – Media and Reputation in Risk Mitigation
COURSE OUTLINE
3. Physical Security for Workplace and Travel
COURSE OUTLINE
4. The Threat from Business Espionage – Intelligence, Techniques and Responses
COURSE OUTLINE
WITH THANKS TO OUR 2019 SPONSORS
Sponsors
Speakers 3rd CSO 360 Congress
If you are interested in speaking at the 3rd CSO 360 Congress in Budapest this year, please let us know teampulse@pulseconferences.com.
Chaired by:
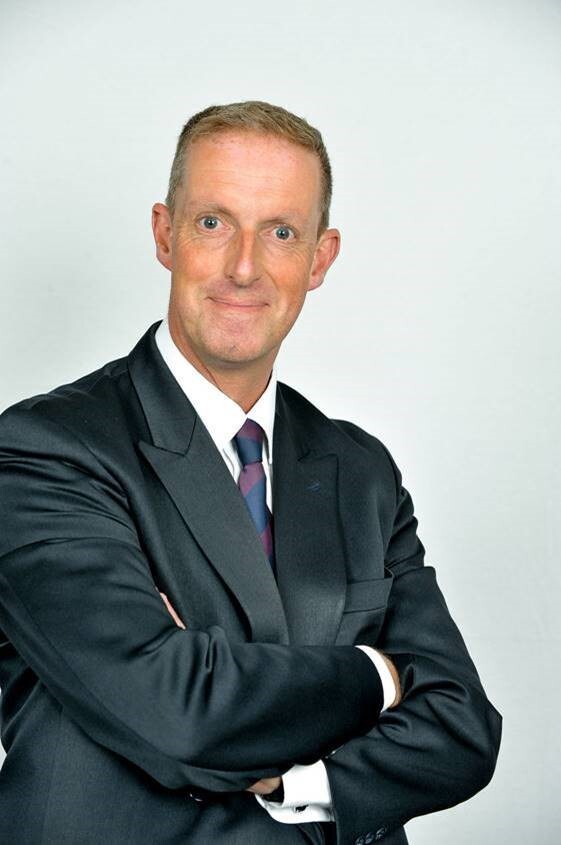 Simon A. Scales FCMI, (former) Head of Investigations (FTSE 100) and Director of Global Investigations (AEX) companies
Simon has over 30 years significant investigative, security and compliance related experience, formed from an extensive corporate and law enforcement background. He is recognised for having conducted complex Bribery, Corruption, Fraud and Misconduct investigations worldwide, in regulated and non-regulated arenas. He is internationally recognised for his public speaking credentials and his vast experience, having successfully led, directed and managed investigation, ethics, compliance and integrity teams within Europe, the USA, Africa and the Middle East. He has also been instrumental in delivering investigative services to the key emerging markets of South America, India and China.
International speaker panel:
When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.
Experience + value = story.
- do you have a compelling business security story that simply must be told?
- have you recently worked on an innovative security project?
- are you willing to openly share inspiring insights, expertise and ideas to advance the security community?
We welcome your input into shaping the agenda and speaker panels.
Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.
For further information, please
+44 (0)20 7936 8989
or
Armin Sick
Manager Aviation Security, Lufthansa
In his role as Regional Security Manager, Armin Sick covers the whole MENA region for the Lufthansa Group. Further, he is responsible for the overflight of conflict zones process and serves as the main point of contact for security departments of other industry partners. Before joining the Lufthansa Group security department in 2014, Armin gained experience in different capacities, including the George C. Marshall European Center for Security Studies and the Berghof Foundation’s team for conflict research in Berlin, Germany. He holds a BA in Political Science, a MA in Peace- and Conflict Studies and is part of a research group at the Federal Academy for Security Policy in Berlin. Since November 2018, Armin is also acting as Vice Chair of the OSAC Aviation Security Working Group (ASWG).
Andy Williams
VP Business Development & Quality Assurance, Safehotels
Andy Williams is VP Business Development and Quality Assurance for Safehotels, an international hotel security certification company based in Sweden. Andy has over 20 years of international safety, security and crisis management expertise within hotel, real estate development and travel security risk management fields. On the Association and volunteer leadership front, Andy has served as a Regional Vice President for ASIS International, the technical review committee for international security standard PSC1; advised the UK government on counter terrorism and public safety initiatives, presented to the EU Council and most recently published a case study paper on crisis management for United Nations UNISDR.
Anthony Leray-Meyer CSC
Regional Security Manager Western Europe Global Security, Abbott
Tony is currently the Regional Security Director for Abbott Laboratories and is based in the UK. He is responsible for the Western Europe region. He had previously served for 23 years in the Australian Army, retiring as a Lieutenant Colonel. He saw operational service with the United Nations in East Timor. Tony has subsequently had seventeen years of commercial experience in providing security operations and risk management, security intelligence, geopolitical risk analysis, crisis management, strategic planning and operational decision support in consulting and corporate security roles in both aviation and health sectors.
Bob Shaw
Senior Security Advisor, United Nations (and Co-Founder, TEG)
Robert is a security, intelligence and EOD executive with a UK Military background. He has broad strategic and operational experience and has advised senior staff, diplomats and government officials on aspects of security, intelligence, threat analysis, crises management, and resilience strategies. He has been the UN Security and EOD Advisor; Liaison officer for the UNMAS and UNOPS and has experience with NATO, the GCC, African Union, OSCE, EUPOL, FCO and others. Robert is a respected expert, has specialist research background on suicide bombing and has provided thematic briefs on worldwide security issues relevant to UNMAS/UNOPS missions.
Basha Galvin
Head of Investigations, Tullow Oil (& Association of Corporate Investigators)
Basha started her career with the Metropolitan Police and moved to the City of London Police Fraud Unit, covering money laundering, trade finance fraud, bribery and corruption. Basha left the police and moved to Citigroup for four years and left in 2006 moving to Barclays plc as Head of Investigations & Whistleblowing for Wealth & Investment Bank. Basha is a seasoned financial crime investigator in the public and corporate sector, Basha has led and managed global investigations teams. During her career Basha has had the opportunity to work in a number of jurisdictions USA, APAC and Europe – developing investigation models and collating evidence for civil and criminal prosecutions. Basha was named as one of the ‘Top 40 in-house’ investigation professionals by Global Investigations Review.
Cedrick Moriggi
LafargeHolcim.
Cedrick Moriggi is a C-Suite Professional (CSO, CISO) with 20+ years of experience in banking, mining, extractive, building, military and service sectors. He is an innovator and results-driven leader who has successfully integrated multi-cultural teams and stakeholders to create, improve, transform, and downsize corporate functions and businesses. Cedrick has extensive consultant and advisor to the chairman, CEO, members of the executive board, and leaders on the protection (Safety and Security), resilience, and recovery of the company’s most valuable assets (human, physical, digital, and reputation. Cedrick holds a Bachelor’s Degree in Economics and Management, an EMBA and is an associate Professor at EDHEC Business. Cedrick has dual Swiss and Italian nationality and has served as an officer in the Swiss Army (antiterrorism, intelligence and military justice as a military judge).
Christoph Rojahn Partner
Compliance & Forensic, KPMG AG
Dr Christoph Rojahn is a Forensic Partner with KPMG in Germany where he specialises in complex and multi-jurisdictional investigations and also leads the firm’s corporate intelligence and corporate security service offerings. He is a graduate of the universities of Oxford, Birmingham and Munich and has more than 18 years of experience in the fields of investigations, intelligence, corporate security and risk management. Dr Rojahn has led assignments in a wide range of different jurisdictions including Russia, India, Turkey and Japan and has lectured and published extensively on issues including FCPA compliance, information security and intelligence methodology. Prior to joining KPMG he worked for several other professional services firms and also was global head of security risk management for a FORTUNE500 financial services provider.
Claire Prestwood
Senior Security Intelligence Analyst for the Americas, Cargill
Claire Prestwood has over twenty years of experience in security issues in the Western Hemisphere. Prior to her position as the Senior Security Intelligence Analyst for the Americas at Cargill, Claire worked as a civilian intelligence officer for ten years with the United States federal government, specializing in terrorist, drug trafficking and criminal threats in the Western Hemisphere. Claire served for three years with the Joint IED Defeat Organization as the U.S. military’s strategic analyst on homemade explosives and improvised explosive devices in the Western Hemisphere. She also served as the Defense Intelligence Agency’s lead analyst on heroin trafficking and production in Latin America, and later led the Immigration Security and Transnational Threats Team in the Office of Intelligence and Analysis at the Department of Homeland Security. Prior to her work as an intelligence officer, Claire was a news researcher and unit coordinator at NBC News in New York.
Claire is an undergraduate of St. Olaf College in Northfield, Minnesota, and has a Master of Public Affairs and a Master of Latin American Studies from the University of Texas. She also has a Certificate in International Migration Studies from Georgetown University. Claire has lived and worked throughout the Western Hemisphere, and is fluent in Spanish and proficient in Portuguese. She is a 2018 recipient of the Office of the Minnesota Governor Community Leadership Award for her work in mentoring young women seeking careers in international security and policy.
Claire is currently a member of the Cargill North America Women’s Network Leadership Team, the Chair Emeritus of the Cargill Working Mothers’ Network, and a member of the Cargill Junior Achievement Corporate Council. She is also a member of the U.S. Department of State Overseas Security Advisory Council’s Latin America Regional Steering Committee, the Global Steering Committee of the Private Sector Intelligence Analysts Roundtable, and leads the Private Sector Latin America Analysts Roundtable. She has published two articles in the Journal of European and American Intelligence Studies: Women in Intelligence: Communicating our Strength, With a Little Help from “The Rock” (June 2018), and More than Just a Myth: Private Sector Intelligence (December 2018).
Crawford Robinson
Group Head of Investigations, British American Tobacco
Crawford has an extensive background in risk and security, having led information security, investigations and assurance programmes in the public, private and charitable sectors. A former police officer, he has served in numerous national and international bodies including the Task Force to establish the International Criminal Court in The Hague, and counter-terrorism support to the US. His commercial acumen at senior levels across a number of FMCG businesses has enabled positive Board level engagement in influencing, establishing and developing security strategy and programmes, operationally embedding these as a true business partner. He currently works for British American Tobacco and for the last 12 months has reported to the ‘Group Designated Officers’ in leading sensitive investigations and supporting the development of business policy and practices. He is a Fellow of the Chartered Management Institute, former Council member of the Risk and Security Management Forum, a Certified Fraud Examiner, a Chartered Security Professional and Freeman of the City of London. He is also a Trustee of three charities. Crawford is also Chief Operating Officer of the recently established Associated of Corporate Investigators.
Chris Meager
Security and Resilience, Barclay Simpson
In May 2017 I reach 20 years working in the security industry, 18 of those recruiting within the corporate security & resilience field. I have placed candidates in senior level and niche roles across 40+ countries and 5 continents in a wide range of industry sectors including oil & gas, mining, pharmaceutical, tobacco, FMCG, food, engineering, technology, telecoms and financial services. In 2013 I joined Barclay Simpson, the world leader in Corporate Governance recruitment, to develop their global corporate security recruitment function. Our consultants, based in offices in London, Hong Kong, Singapore, Dubai and New York work with clients throughout the globe and we place permanent and interim positions within internal and IT audit, risk, security & resilience, compliance, legal, and treasury across all economic sectors. Alongside my work at Barclay Simpson I launched Intelligent Access International in January 2017, connecting CSOs to proven security service providers internationally to save time and money. Why pay for a consultancy to fly halfway around the world, or pay a large mark-up when the project is sub-contracted anyway, when you can utilise a reliable local firm who can fulfil your requirements? Whether it be site security surveys in Turkey, executive protection services in Cote D’Ivoire, threat intelligence in Saudi Arabia, brand protection support in Malaysia, security training in Mexico, crisis management support in Russia or forensic investigations in Ghana; IAI are here to help you identify the best resource for you to use in a specific country.
Dvir Rubinshtein
Aviation Security Operation Center Manager & Aviation Security Expert, National Security Division Israel
Dvir has a military background in the” Israeli Air Force”. He worked as a Security Manager for “ARKIA AIRLINES” & “EL-AL AIRLINES” in Israel and around the world. He was the Security Director of EILAT & OVDA airports in Israel till 2007 and was appointed to his current position at 2008. He is responsible for all operational issues regarding aviation security operation centre and responsible for all security clearance for flights that seeking to enter the Israeli FIR. He is in charge for all the security clearances and approvals on each airline/flight that seek to enter to Israel in advance and in real time. In addition, I perform security consultation visits and audits in airports & airlines around the world that operates flights to Israel. In parallel, I run the aviation security operation centre (ASOC) that responsible for all the Security Aviation industry in Israel.
David Jesson
Sr. Analyst, Global Intelligence/Incident Management Royal Caribbean Cruise Lines
David is a Senior Analyst, Global Intelligence and Incident Management at Royal Caribbean Cruises Ltd. and based in Miami. David served as a Captain in the Fire Department for fifteen years, while also working as a Safety Officer for Corporate Aviation in Wilmington, Delaware. For the past twenty years, he has worked in International NGO security in various senior security management roles for multiple different regions; LATAM, MENA, and East Africa. David was the Chairman of South East Analysts Round Table from 2017-2018, is currently on the Senior Advisory Board for All Analysts Roundtables and Chairs the Africa Group. David has traveled and worked in 77 countries.
Cruise Industry Security – Shipboard and Shoreside
Derek Cheng
CSO, TalkTalk
An experienced information security leader with over 19 years of professional experience in information and cyber security, IT, risk management, privacy and data compliance. Derek has recently joined TalkTalk as their Chief Security Officer, where he is building and leading the cyber security strategy and team to protect TalkTalk’s critical infrastructure, assets, and customer data. Previously, he was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, Derek spent over 6 years at Deloitte & Touche where he managed and performed a multitude of information security and risk management engagements for several global Fortune 500 companies across various industries including financial services, technology, consumer business, manufacturing, and public sector. His primary areas of expertise include developing and leading tactical and strategic security strategies, building and maturing security teams, and ensuring executive governance around security to manage risks appropriately. Derek has also published information security articles and white papers and has been a presenter/panellist at CISO conferences. Derek holds a Bachelor Degree in Computer Science from the California Polytechnic State University, San Luis Obispo CA.
Eduardo Jany
Executive Officer, Global Security Operations, Bloomberg LP
Eduardo Jany is the Executive Officer for Bloomberg, LP Global Security Operations. He has over 25 years of experience in security having led training, consulting and advisory services for international security and law enforcement projects with special emphasis on Brazil for the 2014 World Cup and 2016 Olympic Games.
He retired as a Colonel from the United States Marine Corps having served 33 years of combined active and reserve duty in Special Operations, Anti-Terrorism, Reconnaissance and Infantry assignments and had prior service in the U.S. Army Special Forces. He also retired from law enforcement as a Police Captain after more than 20 years of active police service in Florida, Minnesota and Washington State.
Eduardo received a Master’s in Criminal Justice from the University of Wisconsin, Platteville and attended the University of Minnesota for undergraduate studies. He was a 2013 Senior Executive Fellow at the Harvard University – Kennedy School of Government, the National Defense University National Security Program, and is a graduate of the United States Marine Corps Command and Staff College.
Eduardo earned numerous US and foreign awards and decorations including the Bronze Star Medal, Defense Meritorious Service Medal and the Police Medal of Valor. He is the Chairman of the Overseas Security Advisory Council – -Latin America Regional Council, Chairman of the USVI Public Safety Support Foundation; a member of the FDR Four Freedoms Park Board, the Citizen’s Crime Commission of New York City and is a member of ASIS and the International Association of Chiefs of Police.
Guillermo Gaspoz
Global Security Expert & Advisor, DSM, Netherlands
Security professional experienced in large corporate environments, helping companies drive business goals, protect people and assets and be resilient on operational and strategic levels. Currently driving security programs at DSM, a Dutch company with 23,000 employees in 45 countries focused on animal feed, vitamins, biomedicine and high-performance materials. Previously held roles in private and state-supported entities in the United Arab Emirates and Germany. Born and raised in Argentina, graduated in Political Sciences from Science Po Toulouse, France. Passionate about sound strategic intelligence analysis as key driver for successful security programs. Working toward convergence between the physical and cyber domains, with a technology-driven but human-focused approach. Committed to building a safer and more sustainable and inclusive future for all of us.
Heimo Grasser
Regional Head of Security CEMA, Medtronic, and Chief Awareness Strategist, SAME Solutions (UAE)
Heimo, an accomplished, strategically-minded Corporate Security Expert has been in the Middle East and Africa since 2012. Since 2015 he has covered all physical security aspects for Medtronic across the CEMA region after having gained substantial consulting experience with International SOS and Control Risks. Before moving to Corporate Security, Heimo served more than 10 years in the Austrian military with multiple deployments to hostile environments. Heimo holds a MA in Risk Management and Corporate Security as well as ASIS CPP and CIPP/E certifications. He is a guest lecture for security management at the University of Applied Sciences Vienna and as Awareness Strategist for SAME Solutions on a mission to change the game of physical security awareness training.
Henry Wilkinson
Head of Intelligence & Analysis, Director The Risk Advisory Group
Henry Wilkinson is a Director and Head of Intelligence & Analysis at The Risk Advisory Group (‘Risk Advisory’). Risk Advisory is a global risk consultancy that provides intelligence, investigations and security consulting services to businesses, governments and international organisations. Henry joined Risk Advisory in 2006 and was appointed Head of Intelligence and Analysis in 2012. He has overall responsibility for the group’s worldwide political and security intelligence gathering, risk and threat assessments and analytical products and services. Henry is a specialist on terrorism, geopolitical risks, security affairs, assessments methodology and risk management. He has travelled and worked in Europe, the Middle East, North Africa, Sub-Saharan Africa, Southeast Asia and Latin America, carrying out ground level research and speaking with those shaping events. As an authority in his field, Henry has authored papers on terrorism, geopolitics, and assessments methodology for the Organisation for Economic Co-operation and Development (OECD) and Lloyd’s of London. He has given expert testimony to UK parliamentary committees on security, counter-terrorism and international relations strategy, and presented on assessment methods to the US intelligence community at the Council of Foreign Relations. He has a first class honours degree in War Studies from King’s College London.
James Richardson
Group Head of Security, The Weir Group PLC (and Chair of SHE EXCOM)
James has been Group Head of Security for the Weir Group PLC since 2015 and is the first person in the role. Weir provides engineering solutions to the mining and oil and gas sectors worldwide. He is based in Glasgow but responsible for security and crisis management support for operations in over seventy countries. He also has a central role in Weir’s safety, health and environment strategy.
Prior to Weir, James served for over 20 years in the British Army involving a variety of roles across the Ministry of Defence and UK Government. He has a range of national and international operational and policy experience particularly related to Counter Terrorism. He is a graduate of the University of Manchester, has an MBA from Cranfield and is a member of ISMA.
Justin Crump
CEO, Sibylline
Justin has been CEO of Sibylline, a strategic risk consultancy providing geopolitical analysis, investigative services, threat monitoring, intelligence consulting, training, and embedded personnel, since 2010. Since that time the company has grown from his initial concept into a trusted organisation with more than 60 analysts spread from Singapore to Silicon Valley, and over 100 blue chip clients. As a trusted independent advisor, the company is built on a combination of exceptional people, genuine through leadership and a relentless focus on adding value to clients.
Justin joined the British military in 1995, and has served full and part time up until the present day. His experience includes operational service in the Balkans, Iraq and Afghanistan as well as a tour as the personal staff officer to the Duke of Westminster. Outside the military, Justin has degrees from KCL and the University of Durham, specialising in Islamist extremism and policy issues in the South China Sea. His initial civilian experience was as a front office investment banker, where he was part of the M&A team at JP Morgan Chase and Co.g, gaining valuable insight into the needs of senior business people.
Outside of Sibylline and the Army, Justin is a board member of the Association of International Risk Intelligence Professionals; a member of the Risk and Security Management Forum; an organiser of the International Security Foundation’s annual dinner; a mentor for the UK charity Heropreneurs; and author of Corporate Security Intelligence and Strategic Decision-Making, the first book on the topic. He has on-the-ground experience in over 65 countries, and is a regular print and broadcast media commentator who routinely speaks at both public and private events worldwide.
Jenny Reid
Director, iFacts
Jenny Reid is the CEO of iFacts, one of the leading online employee screening & engagement service providers in South Africa today. Based on the premise that removing the people risk will ultimately help organisations to prosper, iFacts ensures that companies thrive with honest, ethical and productive employees and services providers.
In 1995 Jenny joined the security industry at an investigations firm, where she was ultimately appointed as Managing Director. During this time she was also the first woman to ever be appointed as President of the Security Association of South Africa. iFacts started in 2001 and Jenny bought it out 100% in.
Never content to rest on here laurels, Jenny has taken the iFacts brand to new heights and is constantly looking for new and innovative ways to ensure companies maintain true value in their organisation and enhance it.
Jenny’s strong leadership style and outspoken views on corporate crime and political corruption have made her a highly sought after local and international conference speaker and NLP coach. She is also part of the Cheri Blair Foundation Mentee Alumni.
Jenny is also the founder of Adventures for Love, an organisation made up of like-minded women who embark on a number of physical adventures around the globe to raise awareness and funds for various charities and conservation efforts. Jenny lives in South Africa with her husband, Neil.
Liz Chamberlin
Executive Director, International Security Management Association (ISMA)
Liz Chamberlin is the Executive Director of the International Security Management Association (ISMA). She began her career in law, where she focused on insurance defense litigation, workers compensation, and corporate litigation matters. Ms. Chamberlin graduated from the University of Iowa (B.A., political science and international relations); and from the University of Iowa College of Law (with distinction). She resides in Hampshire, UK.
Mark Wolsey
Group Security Director, CRH plc
After 25 years’ service as an officer in the Royal Marines, Mark made the transition into Corporate Security in 2006. He has been the Director of Global Security at Smiths Group, Cadbury, Philip Morris International and PwC before taking up their present position as Group Security Director at CRH. Specialties: Security of People, property, information and reputation. All levels of investigation (including fraud and corruption), risk assessment and mitigation, contingency planning, crisis management, business intelligence and business continuity.
Mark Reading
Managing Director, Seneca Risk
Mark is a vastly experienced, global risk management professional. He has worked across multiple security disciplines, both corporate and commercial. After 14 years’ operating globally in the oil & gas sector, he co-founded a specialist risk company in W. Africa covering the Gulf of Guinea – from Ghana around the coast to Mauritania; with the Sahel Region added for extra spice. Mark now runs a niche risk business to corporations and individuals focusing on Africa.
Today he will discuss a key learning since sitting, where many of you sit now, high up in corporate security; the learning – ‘ground truth’.
Michael Mallard
Security Professional (USA)
Michael Mallard has 15 years of experience as a security professional in both the military and public sector. Michael has traveled to over 60 countries, served as a diplomat on four continents, and operated in multiple dynamic, unstructured environments. Prior to his security career, Michael worked in the financial services sector in New York, NY.
Marcus Alldrick
Digital Risk Management, Security and Compliance Advisor
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services and sits on the Cymmetria Advisory Board as Chief Risk Officer.
Mike Croll
Global Security Advisor, International Commission on Missing Persons (ICMP) (NETHERLANDS)
Mike, like most in the security business, is male and pale. But he has been on a journey from the Foreign Office, to the European Union, the United Nations and to Facebook and beyond. He’s lived in Africa, Asia, Europe and the Middle East, holding a range of senior appointments and managing international teams often through critical situations.
Mike Lycett
Group Head of Security and Risk, De La Rue International Limited
Mike is the Group Head of Security and Risk for De La Rue. He is situated at the head office in Viables, UK, where he overseas security, business continuity and risk for the Group. Previously he worked at the businesses Kenya site as Head of Delivery Health, Safety, Security and Environment (HSSE). Based in Nairobi he worked within the Delivery function of the business and extensively with third party partners. He is a decorated military veteran of twenty four years’ service, where he was ultimately responsible for commanding specialist close protection operations globally in support of the UK Ministry of Defence, the Foreign and Commonwealth Office and other government departments. Upon leaving the military Mike was then appointed Head of NATO Close Protection Unit working at the headquarters in Brussels, Belgium. Subsequently he then became involved within the global risk environment; coordinating onshore and offshore risk programmes in Africa, anti-illicit trade activities and security and risk awareness training. Mike is a well-qualified security professional, he holds an MBA from Durham University, he is an ASIS Certified Protection Professional (CPP), holds membership of the City and Guild Institute and an ISO lead auditor, to name just a few.
Matthew Judge
Group Managing Director, Anvil Group
Matthew has overall responsibility for delivering continuous growth for the company by meeting the evolving demand for effective risk management solutions from the world’s most prominent organizations.
He is passionate about delivering advanced technology-led operational resilience solutions that give Anvil’s clients the actionable insight they need to ensure their businesses are prepared for anything and continue to thrive in an ever more uncertain world. Having assisted clients directly during a diverse range of major incidents over the last ten years, Matthew fully understands the impact of these events on those affected and their wider business operations.
Matthew is a regular speaker at travel and security conferences, discussing and advising on the subjects of travel risk management, corporate governance, duty of care and operational resilience.
Mehdi Khoali
Principal Investigations Officer, African Development Bank
Mehdi joined the African Development Bank as a young professional in 2004 and has worked in various departments including internal audit, agriculture & agro-business and water supply & sanitation before joining the integrity & anti-corruption department as principal investigations officer.
He has led highly sensitive and complex investigations into sanctionable practices within the Bank and in Bank-financed projects, and participated in settlement negotiations with multinational companies found to have engaged in fraudulent and corrupt practices in Bank-financed activities.
Mehdi participates in the review of policies, guidelines, directives and manuals pertaining to the integrity framework of the Bank; also conducts outreach programs for regional offices, civil society organizations and anti-corruption agencies in African countries, and regularly represents the Bank in various international forums.
Mehdi holds a master’s degree in Mathematics of Finance from Columbia University.
Ned Farmer
Geopolitical Risk Manager, American Airlines
As Geopolitical Risk Manager, Ned designed and implemented the geopolitical risk and security intelligence program at American Airlines. Ned manages the assessment and dissemination of threat intelligence, to mitigate security and political risks to American operations worldwide. Ned is also the current Chair of the US State Department’s Overseas Security Advisory Council (OSAC) Aviation Security Working Group (ASWG) and on the Executive Board of the OSAC Latin American Regional Council (LARC). Ned previously worked at Royal Dutch Shell, the Inter-American Development Bank, the US Congress, and Morgan Stanley. Ned received his B.A. in Political Science from McGill University in Montreal and his M.A. in International Affairs from American University in Washington, DC. He also studied at the Universidad de Salamanca in Salamanca, Spain. His graduate coursework focused on terrorism, specifically radicalization among Muslim immigrants in Europe. He is fluent in Spanish and proficient in French.
Lady Olga Maitland
Founder and CEO, Defence and Security Forum & Copenhagen Compliance
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.-
Patrick
Kane, Senior Director of Security, Atlas Air
Patrick Kane is Senior Director Security for Atlas Air, a US airline conducting cargo and public/private passenger operations worldwide. He is also the past Chair of the OSAC Aviation Security Working Group. He has over 20 years working in private sector corporate security, most of that time focused on international operations and in particular, the protection of crewmembers and traveling staff. Since 1996 Patrick has been a Certified Protection Professional (CPP) in good standing under the auspices of the American Society for Industrial Security (ASIS). He received an International Executive MBA from Instituto de Empresa in Madrid, Spain in 2004. He is also the author of the book Practical Security Training, as well as numerous articles and several security guides, and was a contributing author to the book Personal Security, written by Tanya Spencer. Prior to entering the private sector, Patrick served as an infantry officer in the US Marine Corps. He welcomes questions, comments and suggestions and can be reached at pkane@atlasair.com.
Richard Fitzhugh
Head of Business Resilience, LaFarge Holcim
Richard has over 15 years’ experience in crisis management, business resilience, emergency response, business continuity and ITDR across a wide range of sectors including mining, finance, law, medical and government. In his previous role was employed as the Global Principal in Business Resilience at a FTSE 100 multinational. He is currently Global Head of Business Resilience at LafargeHolcim, responsible for the design, launch and implementation of a new resilience programme across 72 countries with 2,500 operations and over 100,000 people.
He specialises in the design and implementation of business resilience programmes, as well as live response to complex, major incidents ranging from Ebola outbreaks to conflict zone response to catastrophic natural disasters.
His passion is getting Business Resilience on the standing meeting agenda for ExCo and the board, and positioning it as profitable strategic asset.
Ryan Long
Head of Global Intelligence, McDonald’s Corporation
Ryan Long leads the Global Intelligence function at McDonald’s where he helped launch the company’s intelligence program. His team empowers business leaders to make informed decisions and deliver better business outcomes by providing timely, tailored, & trusted intelligence and support around the organization’s people, operations, strategy, and brand. The intelligence function also includes Executive Protection, which focuses on delivering innovative and intelligence-led solutions to support executive risk management. Ryan began his professional career in 2003 as a U.S. Army Intelligence Officer. He’s held a variety of analyst, advisory, and management positions of increasing responsibility in both a reserve and active capacity and deployed multiple times to both Iraq and Afghanistan where he served with distinction while receiving numerous decorations. He currently serves in the Army Reserves where he leads an intelligence organization focused on analytic, counterintelligence, and counterterrorism support to the United States European Command. Ryan recently finished a two-year term as the President of the Association of International Risk Intelligence Professionals (AIRIP), an industry association dedicated to professionalizing intelligence analysis, and is a founding board member of the Veterans Leadership Council, the foremost business network for the current generation of Veteran leaders. Ryan has a bachelor’s degree with Honors in Political Science from the University of Illinois at Urbana-Champaign and a law degree from The John Marshall Law School.
Dr. Sally Leivesley
Director, Newrisk Ltd, A Founder Member, The Exercise Group7 Newrisk and TEG7
Since 9/11, Dr Leivesley has been invited by British and international media to cover public security and risk during and after major terror attacks, cyber breaches, natural disasters and nation state threats (http://www.newrisk.com/recentmediacommentary.html. Exercising and training in catastrophic risk mitigation, exercise testing, industries, supply chains, and smart systems are a current focus of her work as Managing Director of Newrisk Limited and as a founder member of the Exercise Group7 LLP (www.TEG7.co.uk) which also provides education services to Pulse Conferences. Dr Leivesley collaborates with a number of specialists groups on aviation threats, distributed energy systems and megaterrorism and catastrophic risk. She has publications on strategic analysis of technology in the operating environment (ICNS2015), Safety vs Security (NATO SAS-106 2014), and Resilient Core Networks for energy substation distribution for advanced energy grids (IEE PES General Meeting, 2014) and reports from her position as chair of a permanent monitoring panel for catastrophic risk and megaterrorism for an annual scientific meeting.
Dr Leivesley undertook her Doctorate at the University of London, focusing on catastrophic loss events ranging from nuclear war to train accidents. She trained as a Scientific Advisor with the British Home Office which involved scientific analysis of nuclear weapons effects for public survival. She also worked with hazardous industry in Australia and was appointed to lead recovery teams for cities following natural and chemical disasters. In the energy sector she worked on five power stations and she has been contracted to report on all major nuclear disasters including Chernobyl, TMI and Fukushima. She was a member of the technical committee for the first UK guidance document on Resilience and Cyber Security of Technology in the Built Environment published by the IET under sponsorship of the Centre for the Protection of National Infrastructure (CPNI)
Dr Leivesley researches human factor failures, terrorist and hostile nation state threats across physical and cyber security. She is currently researching women in risk, security and smart technology for educational services to women and HR professionals interested in promoting career developments for women and wider diversity in industry. She is a Member of the Register of Security Engineers and Specialists (Institution of Civil Engineers) and serves on the Steering Committee; a member of the International Association of Bomb Technicians and Investigators (IABTI), the Royal United Services Institute (RUSI); the Information Assurance Advisory Council Community of Interest (IAAC); and the Australian College of Education. She holds Fellowships with the Institute of Civil Protection and Emergency Management and the Royal Society of Arts, Manufacturing and Commerce. Dr Leivesley has undertaken research into a new generation of communications in response to catastrophic risks in cyber security.
William Sandover
Independent Security Adviser, Cathay Pacific Airlines
After 29 years in the UK Diplomatic Service, with postings in Austria, Argentina, France and Pakistan, William Sandover served as British Airways’ International Risk Adviser from November 2008 until July 2017.
During his time at BA he designed, developed and implemented BA’s Travel Risk Management Programme and supported changes to the way BA’s crew are supported down route. In November 2015 he was appointed chair of the Global Business Travel Association (Europe)’s Travel Risk Committee.
After leaving BA, William was appointed as Special Adviser, Intelligence and Analysis, to Risk Advisory, London and as International Affairs Adviser to Cathay Pacific Airlines. He is a Director of VChain Technologies which he advises on aviation and government issues. He has spoken at and chaired several conferences on Travel Risk Management.
Sponsors
Sibylline
Since 2006 Sibylline has supported businesses, governments and NGOs through the provision of high-quality risk analysis and due diligence services. We do not believe in one-size-fits-all solutions. Instead, our global source network, professional intelligence analysis processes and specialist expertise allows us to produce high-quality, insightful work that has direct relevance to our clients’ business. Our service lines include: Strategic Geopolitical Analysis, Corporate Investigations and Due Diligence, Threat Monitoring, Training and Consulting, and we can provide Embedded Analysts.
Safehotels
Safehotels is the worlds leading company for independent hotel safety and security Certification. We conduct annual on-site security audits of hotels according to ‘The Global Hotel Security Standard’, awarding Certificates to hotels for independently verified Safety and Security to make it easier for hotel room bookers and corporate business travellers to identify hotels that maintain and invest in high levels of hotel security standard. Most importantly, Safehotels provides enhanced duty of care and due diligence for corporate security travel risk management programs. Founded in Gothenburg Sweden we have global coverage through over 15 hub locations around the world.
www.safehotels.com
CIM
CIM® It’s impossible for a business to safeguard itself against all potential incidents, however preparation and structure can provide a platform to ensure that you are ready for when the time comes. CIM enables companies and organisations around the world to take care of its values and reputation before, during and after an incident. CIM is a complete management system for security, preparedness and crisis management, incorporating all the processes from the bottom to the top of the resilience life cycle. Demonstrating its inherent flexibility and commitment to the core principles of incident and crisis management, the CIM system is used in organisations and blue-chip companies in demanding industries like energy production, offshore engineering, aviation, food production and transport etc. CIM is a modular system and customers can pick and choose which of the 40 modules they feel suits their business best. Some of these, such as the Action Cards and Log modules are used by all customers, whereas some have been created for specific industries which face particular challenges and risks. Read more about CIM, and find an overview of the core modules within CIM here: cim-en.f24.com/cim
One Voice and F24
One Voice Software Ltd. is a subsidiary of F24 Nordics AS. F24 Nordics AS is a technology company, headquartered in Trondheim, and part of the F24 group. F24 Nordics has over 40 employees, and develops and provides software solutions within security, emergency preparedness and crisis management, with our flagship product CIM®. F24 AG has its headquarters in Munich, Germany. Along with its subsidiaries, it supports more than 2,500 companies and organisations in more than 100 countries around the globe as part of the daily communication of critical and confidential information or in the event of a crisis.
Blackdot Solutions
Anvil Group
To operate effectively, every business needs to focus on being more adaptable, more flexible, more resilient. It’s not enough to look at any single aspect in isolation. You need to consider how every part of the organisation can perform no matter what. This may mean ensuring your international travellers and expats can work safely and effectively wherever they are in the world. It may involve making sure your facilities are adequately protected against environmental and manmade risks. Or it could mean focusing on increasing the robustness of your entire end-to-end supply chain. We can help. Anvil delivers advanced business resilience solutions that protect what matters most to you. Using our Riskmatics® technology platform, we enable you to accurately assess both pre-existing and dynamically changing risks, wherever they are on the planet. Our highly experienced analysts are available 24/7 to advise you on the best action to take to keep your people and operations safe. And we provide on-the-ground support to protect your employees, property and business operations. Simply, Anvil puts you in control. From people on the move and products in transit through to investing in new facilities and entering new markets, with Anvil, you’re ready for anything.
Risk Advisory
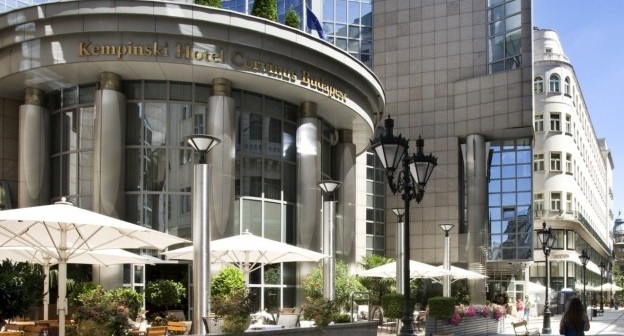
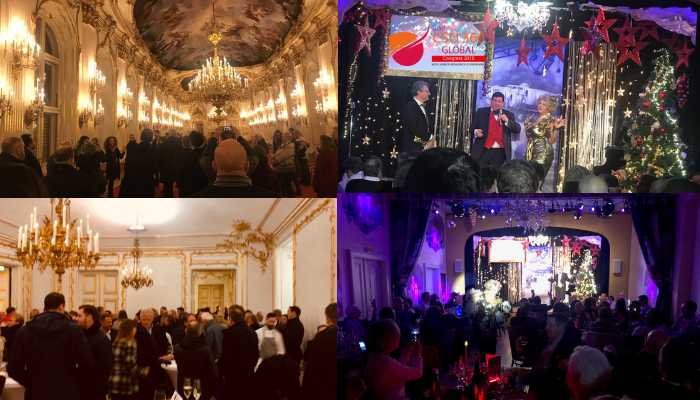
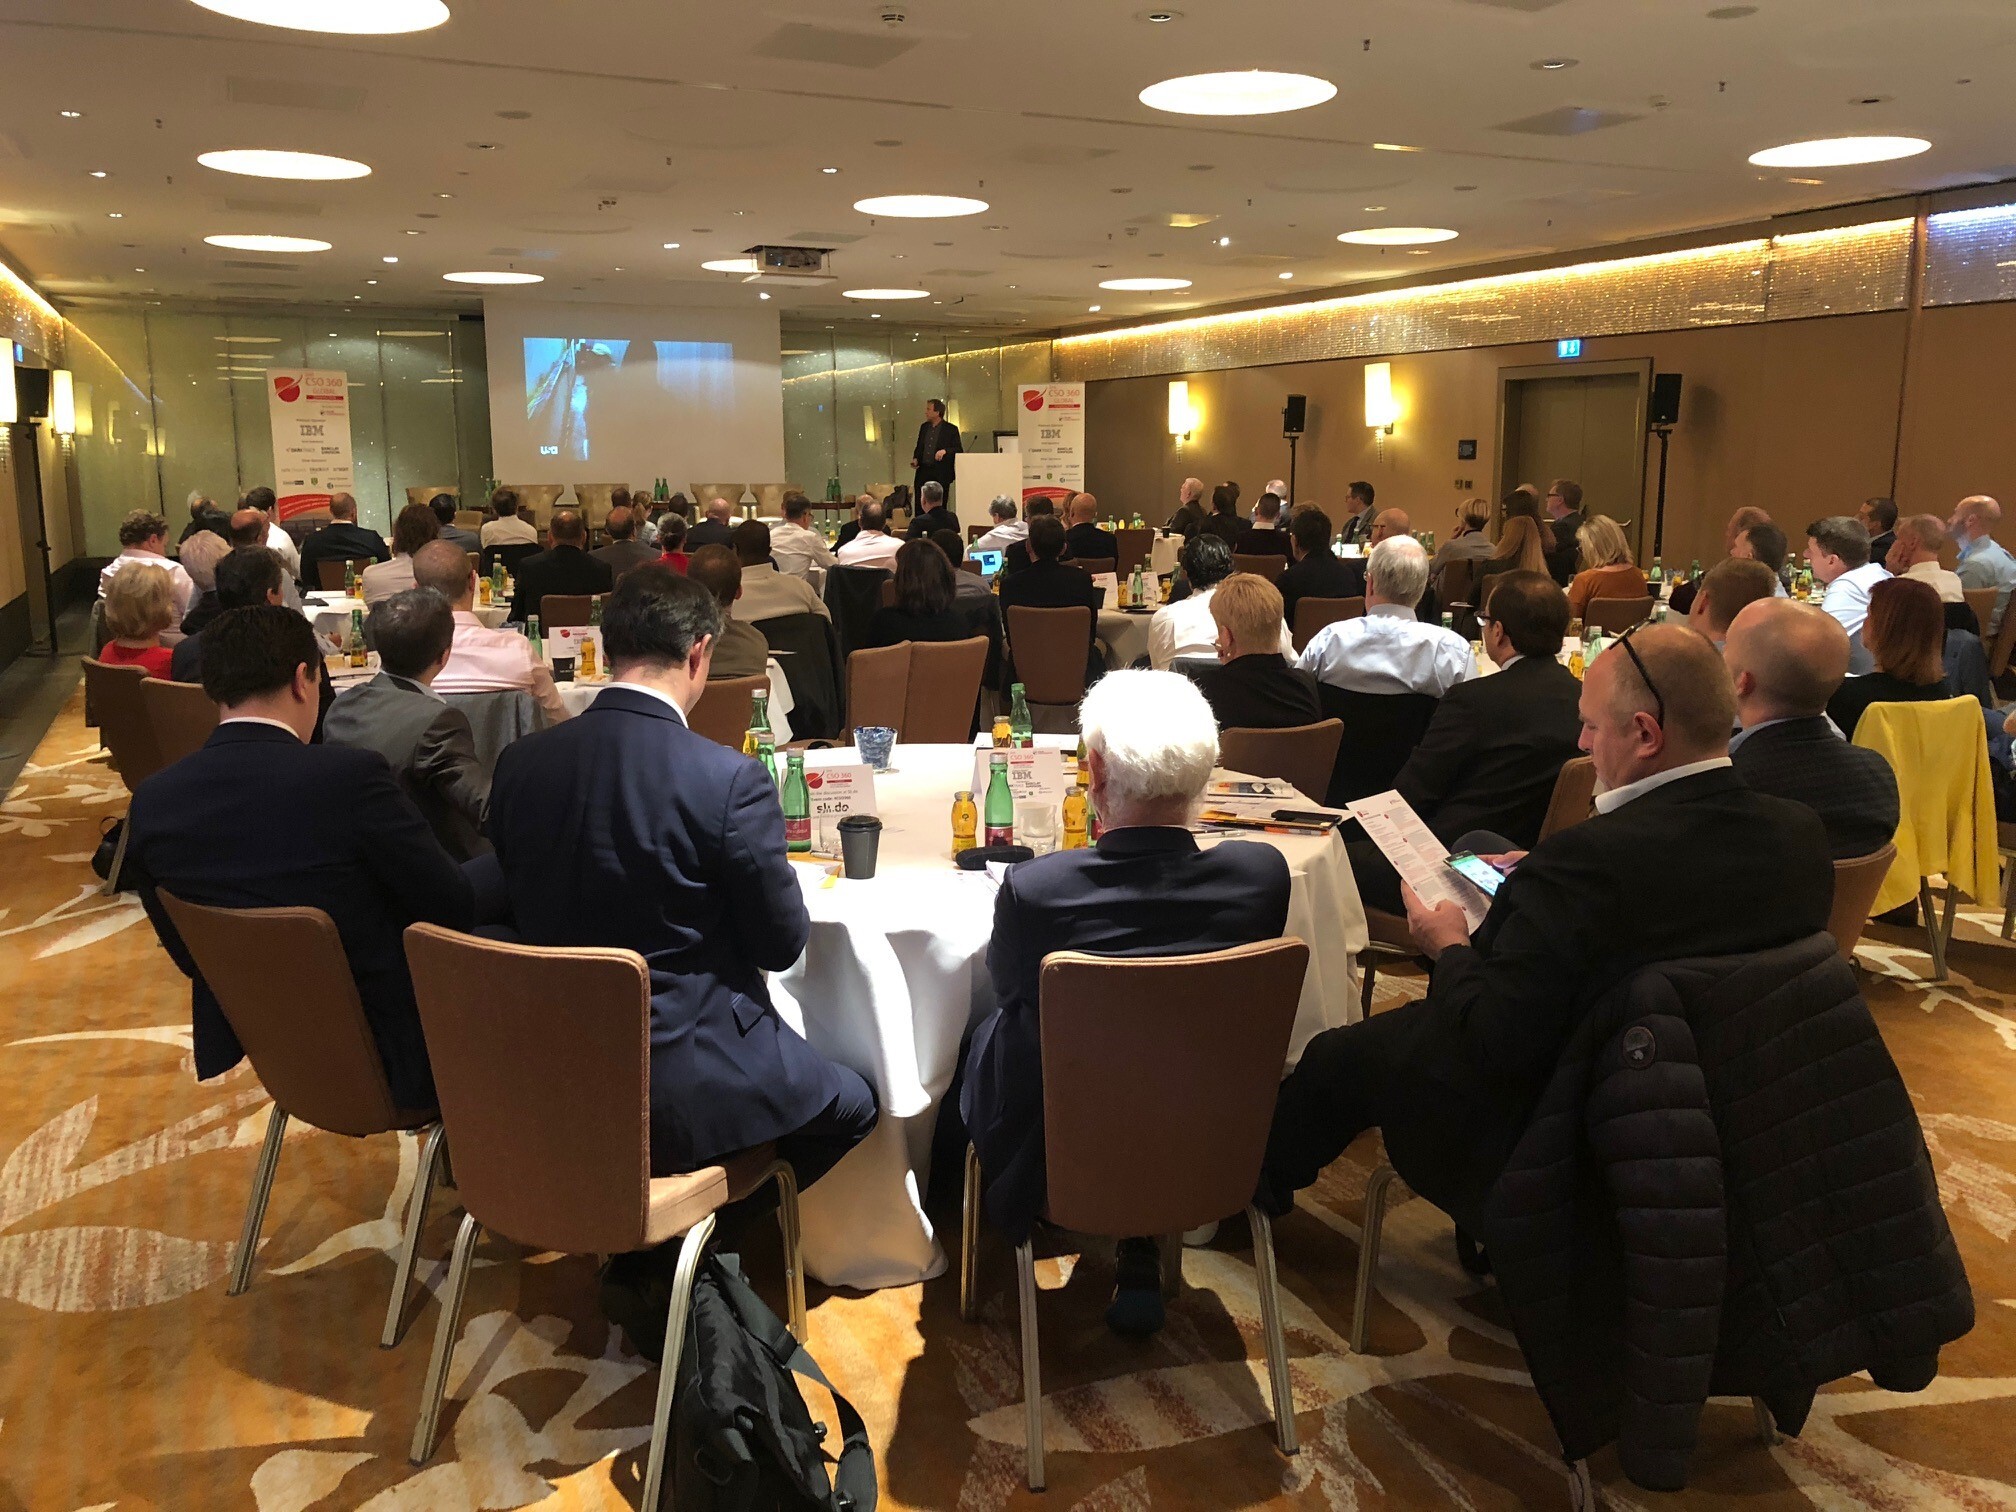
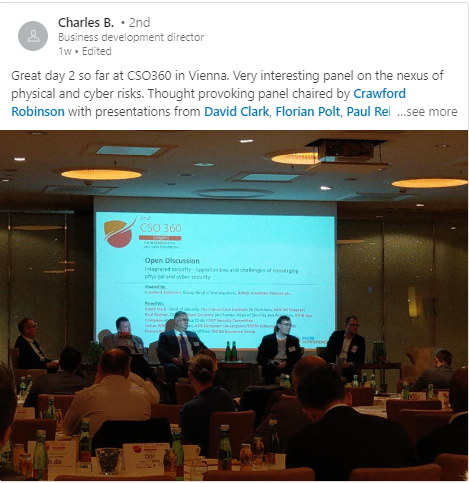
Photos 2nd CSO 360 Congress, Vienna, 5-6 December 2018

 Download 2019 Programme
 On the Pulse Blog: Cyber Physical Threat – Bridging the Cultural Divide
 Download Brochure from 2nd CSO 360 Congress 2018
Download Speaker Presentations from 2nd CSO 360 Congress 2018
Download White Papers & articles from 2nd CSO 360 Congress 2018
Testimonials CSO 360 Congress
 “Great programme, great organisation and great attendance have made discussions useful and passionate! Listening and sharing experiences and ideas on good practices and benchmarking with other businesses! You have made my days in Vienna!”
– Philippe Besson, Europe Industries Security Officer, AIR LIQUIDE
“A great congress, packed with valuable information and insight for CSO’s and their senior security managers.“
– Paul Kelly, VP Global Security Operations, 21st Century Fox
Testimonials 3rd CSO 360 Congress, Budapest, 2019
 “”The Pulse 360 CSO Congress provided significant value and information in a short timeframe, particularly with regard to tradecraft, best practices, and networking.”
– Claire Prestwood, Senior Security Intelligence Analyst for the Americas, Cargill
“The CSO 360 Conference was a fantastic opportunity to exchange information and perspectives in a collegial environment.“
– Patrick Kane, Senior Director of Security, Atlas Air
“CSO 360 continues to provide a great platform for security professionals !“
– Mark Reading, Managing Director, Seneca Risk
“Decades of security experience with a global perspective.“
– David Jesson, Sr. Analyst, Global Intelligence/Incident Management, Royal Caribbean Cruise Lines
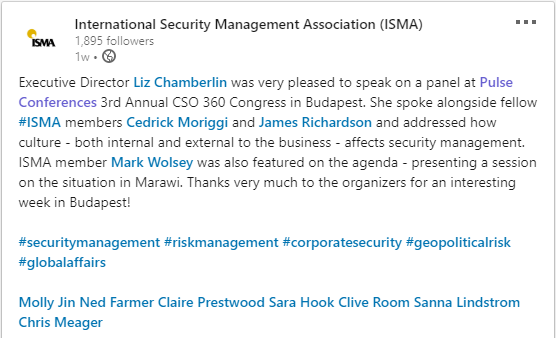
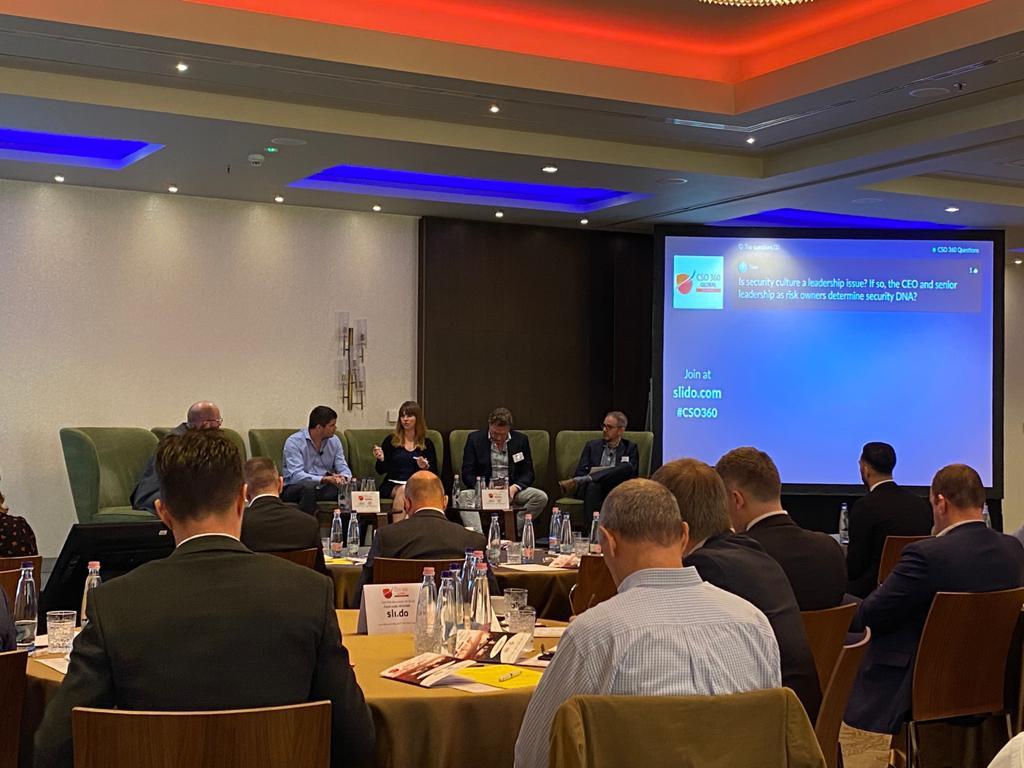
“Many thanks Christoph and to the entire panel as well as the conference organisers. Things continue at pace with some exciting contributions here at CSO 360, including a discussion on diversity in the security profession, something I’m glad to say the ACi sees as a key tenet of its vision and practice.“
– Crawford Robinson, Group Head of Investigations, British American Tobacco