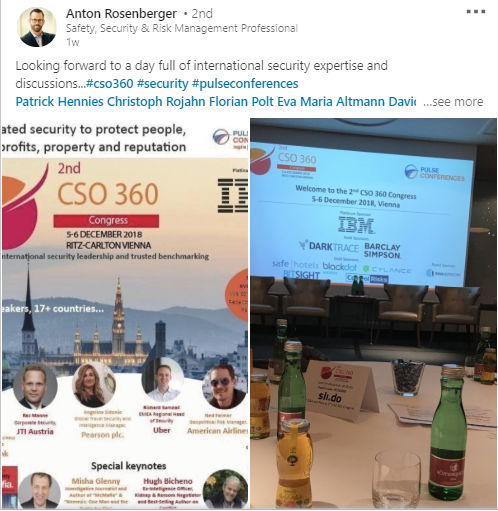
2nd CSO 360 Congress 2018
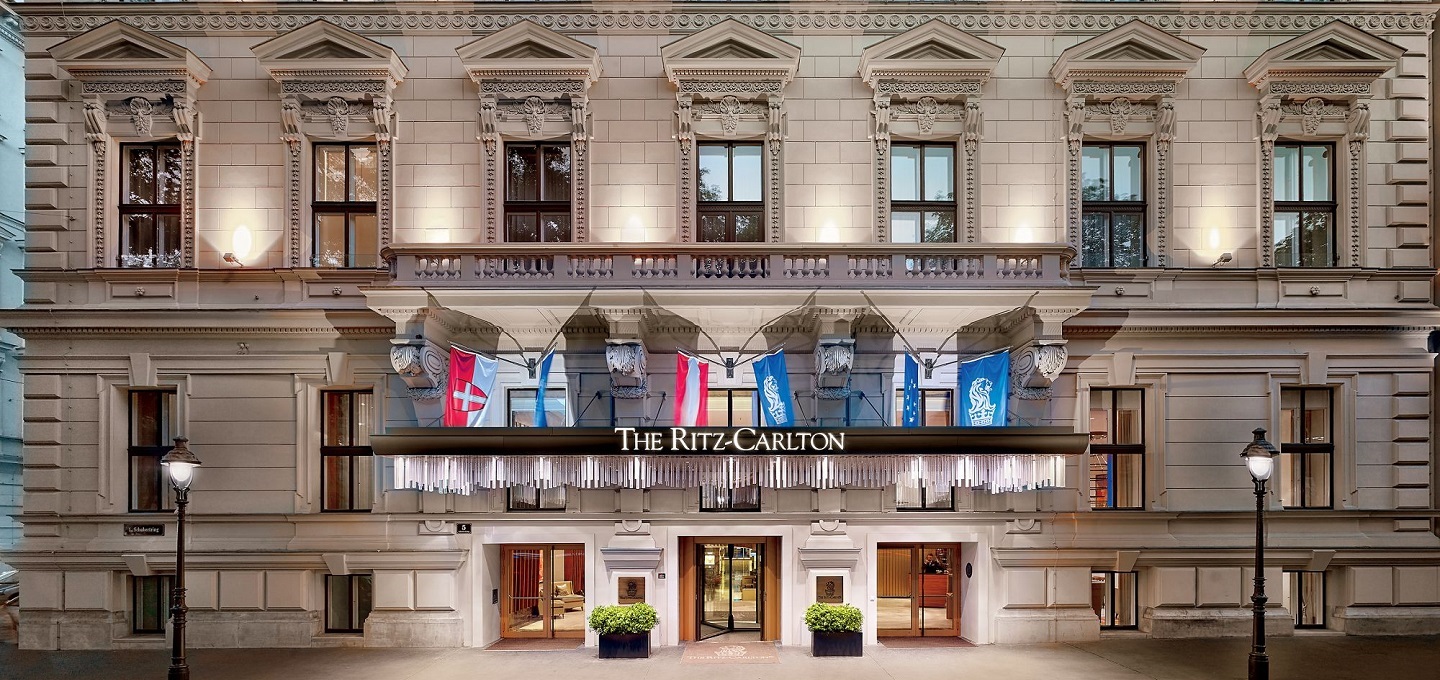
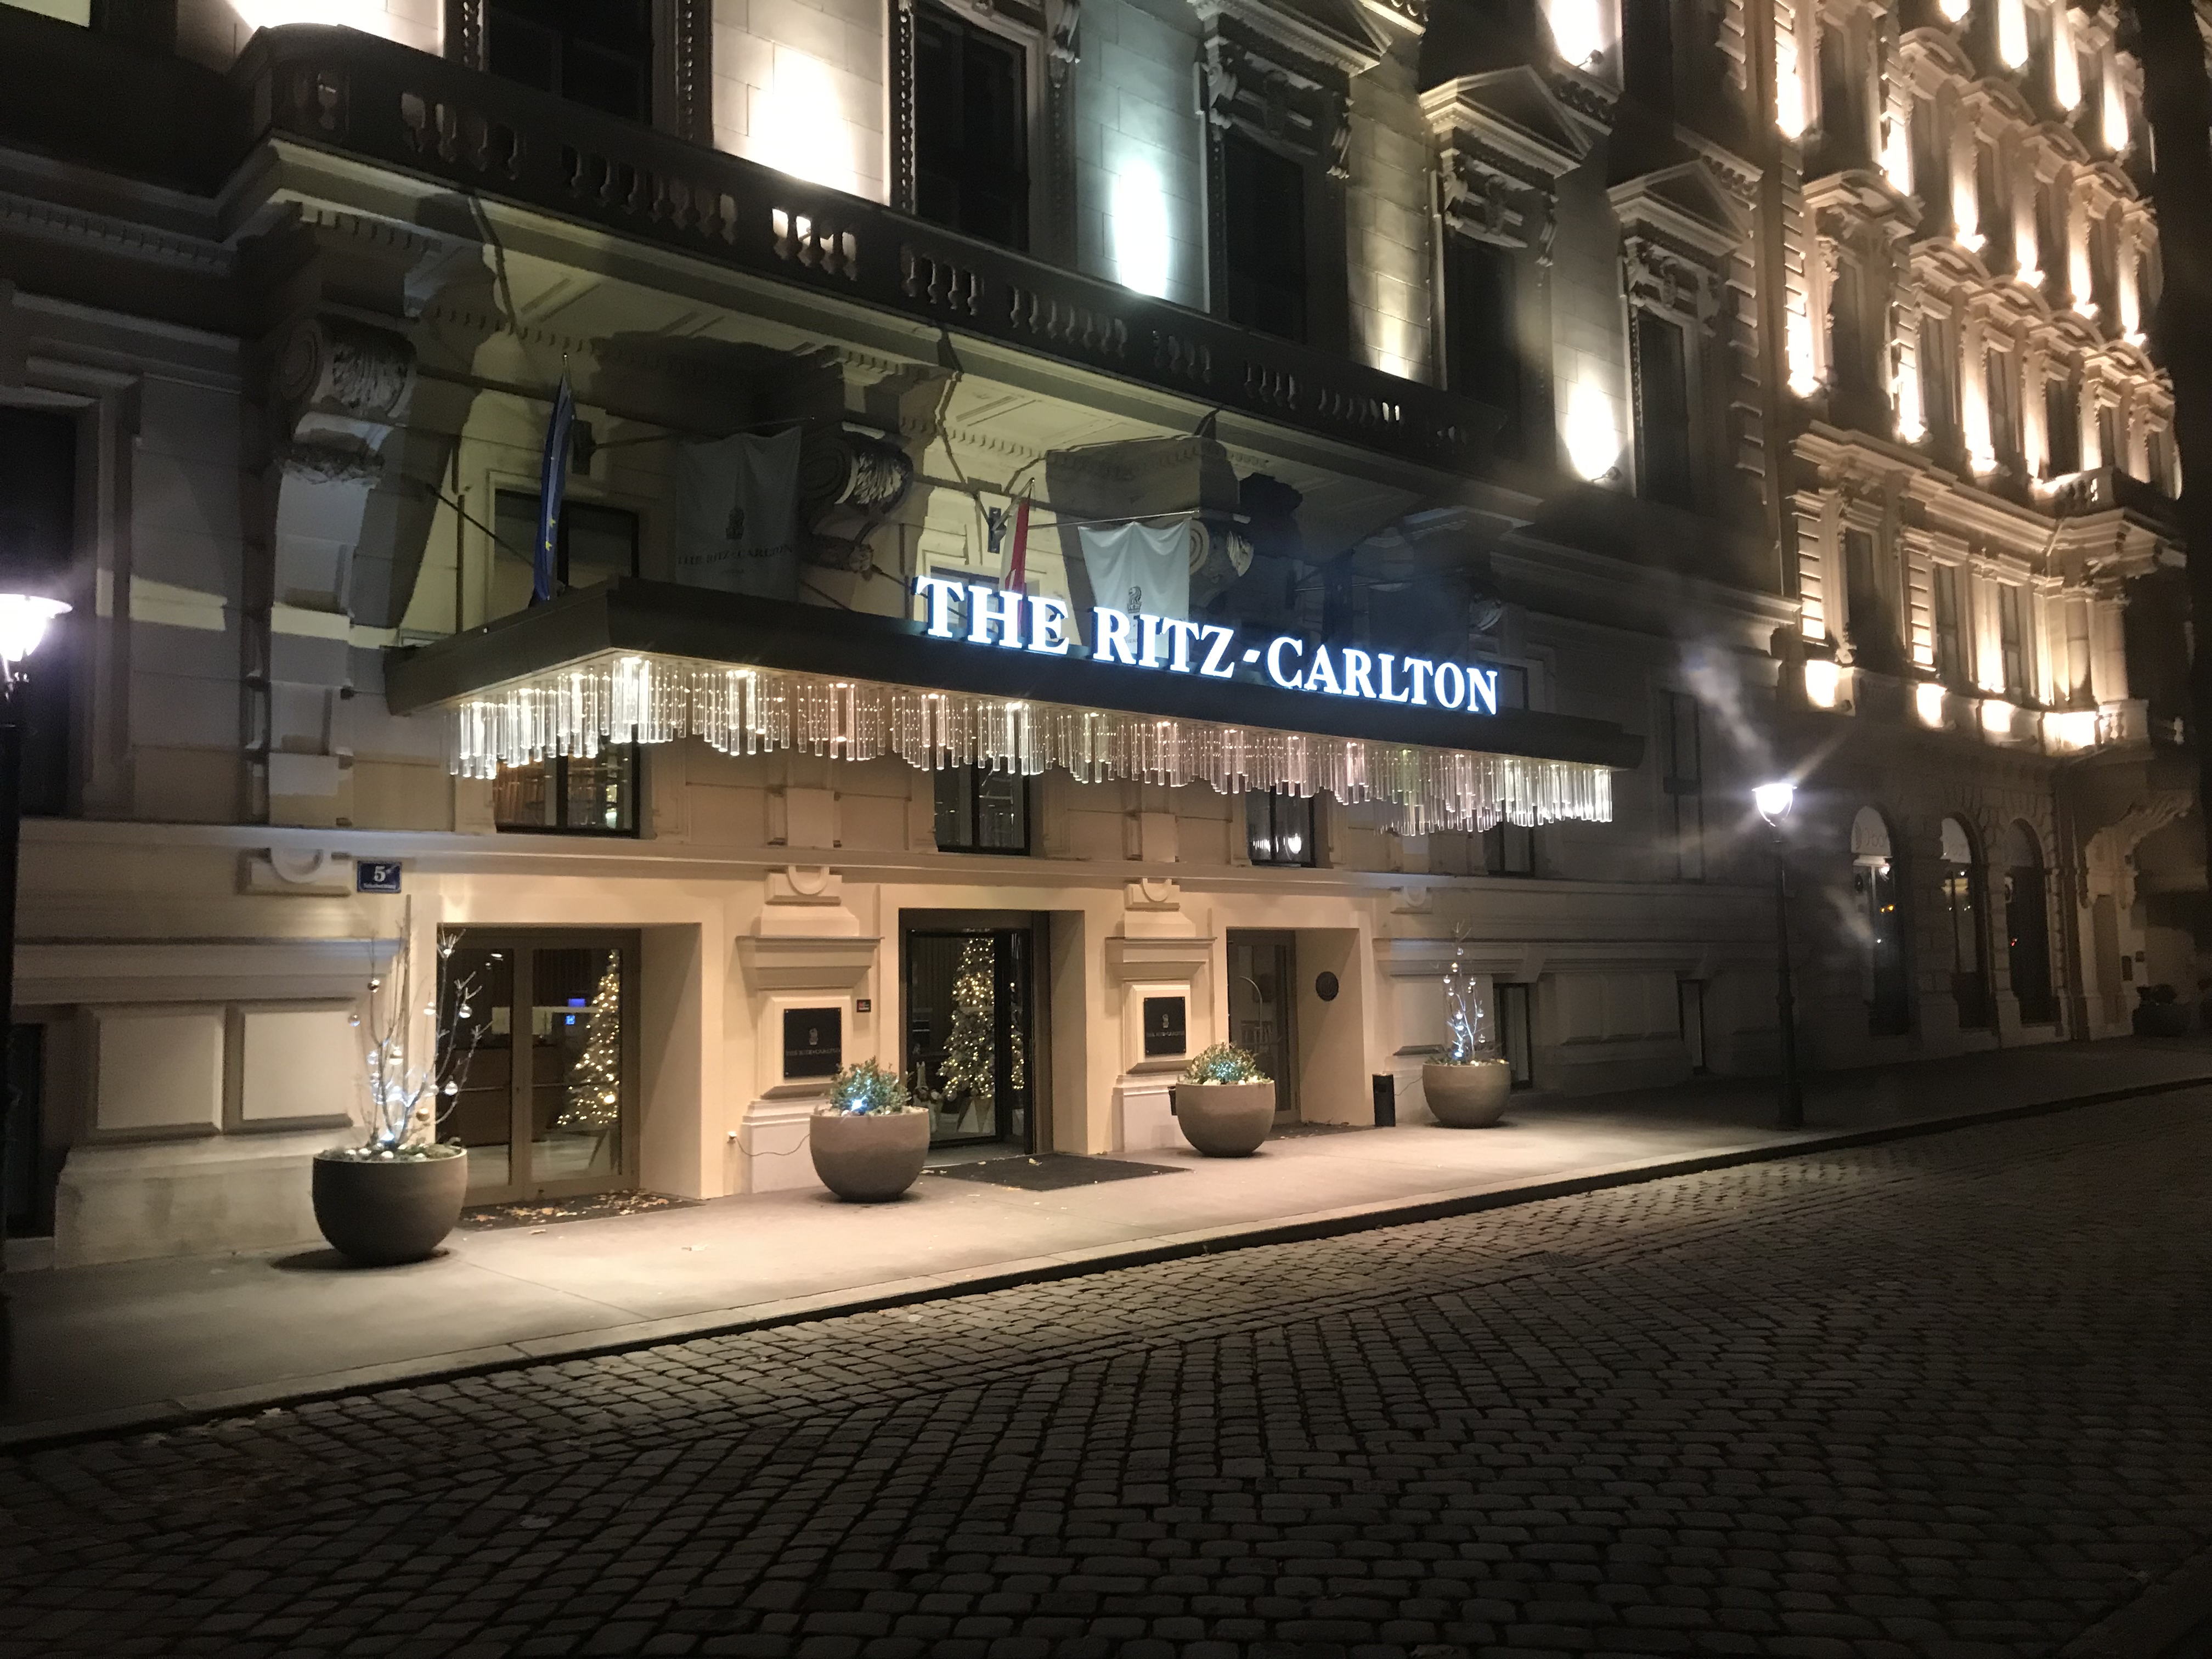
Ritz-Carlton – Vienna
Integrated security strategies to protect people, profits, property and leverage global business operations
Pulse Conferences would like to thank all speakers, sponsors and delegates who participated in the 2nd CSO 360 Congress, hosted 5-6 December 2018 in the wonderful city of Vienna.
This community-based event was attended by senior in-house chief security officers, corporate security, resilience, threat management, intelligence and crisis response directors, which truly enabled global peer to peer sharing – we pride ourselves not only on who is on stage but who is in the room!
This event uniquely tackled priority challenges for Chief Security Officers, many of whom oversee diverse areas and teams covering in corporate security, cybersecurity, information security, fraud, physical and executive and travel security, resiliency, forensics and investigations. We offered a progressively integrated and converged security programme.
- Connect with global security leaders – A new expert international panel of security experts will bring real experiences to pool brain power on the sustainability of global business amidst rapidly evolving threat landscapes and changes in geopolitical, technological and financial spheres.
- Innovate your security strategy – Partake in this share of strategies, tactics and methods for improving the protection of clients, employees and business partners as well as the security of assets, information and reputation.
- Leave inspired for action – Exchange practical approaches, innovation and strategies on the emerging threat horizon.
Speakers confirmed for Vienna, December 2018
Special Keynotes
- Misha Glenny, Investigative Journalist, Leading Expert on Cybercrime and Author of McMafia (UK)
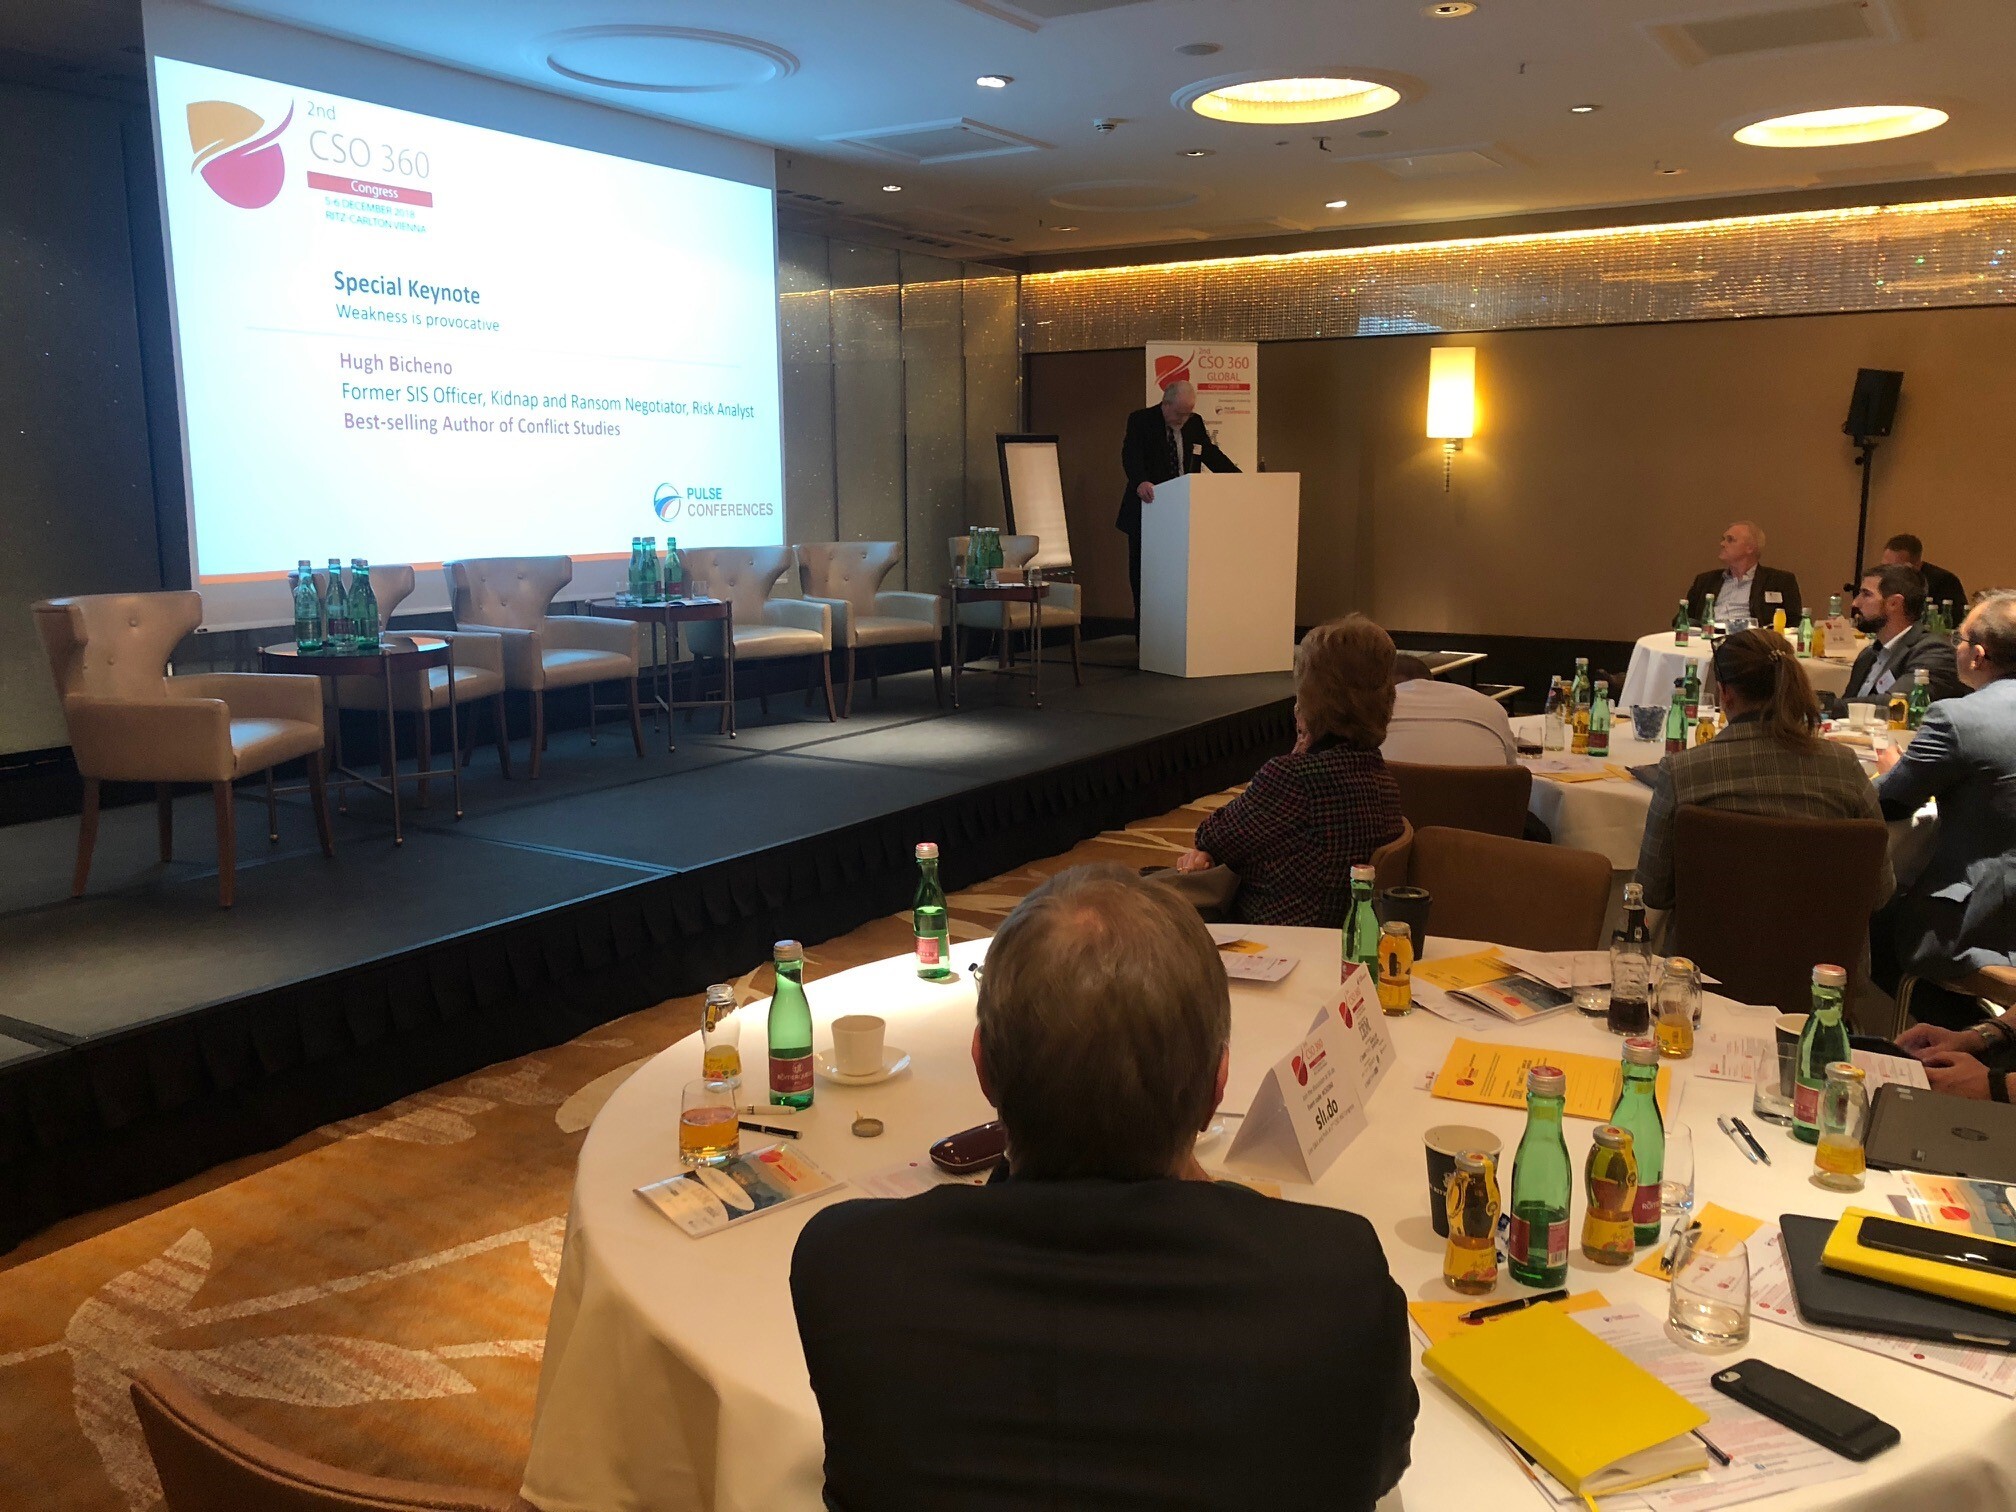
- Hugh Bicheno, Former SIS Officer, Kidnap and Ransom Negotiator, Risk Analyst and Best-selling Author of Conflict Studies
- Lara Symons, Director, Hostage International – on stage interview with Thomas Olsson, a Former Hostage, and his wife, Berit Olsson
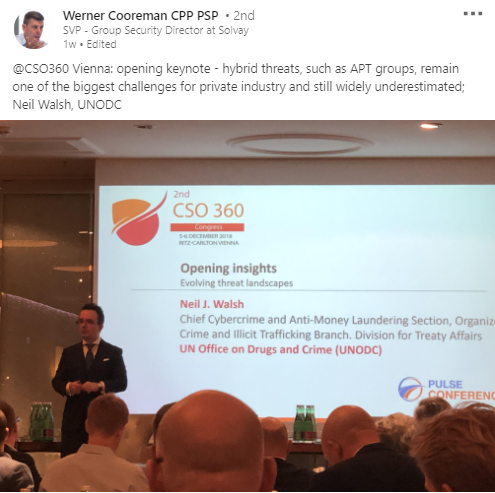
- Neil J. Walsh, Chief Cybercrime and Anti-Money Laundering Section, Organized Crime and Illicit Trafficking Branch. Division for Treaty Affairs, UN Office on Drugs and Crime
International speaker panel
- Andy Williams, VP Business Development & Quality Assurance, Safe Hotels Alliance (SWEDEN)
- Angelina Sidonio, Global Travel Security and Intelligence Manager, Pearson plc. (UNITED KINGDOM)
- Bob Lewis MBE, Former Head of External Cyber Assurance & Monitoring, Barclays (UNITED KINGDOM)
- Cédrick Moriggi, Global Head of Security (CSO), LafargeHolcim(UNITED KINGDOM)
- Crawford Robinson, Group Head of Investigations, British American Tobacco plc. (& Chief Operating Officer, Association of Corporate Investigators) (UNITED KINGDOM)
- Charles Hecker, Senior Partner, Control Risks (UNITED KINGDOM)
- Chris Meager, Security and Resilience, Barclay Simpson (UNITED KINGDOM)
- David Clark, Head of Security, The Francis Crick Institute (& Chairman, ASIS UK Chapter) (UNITED KINGDOM)
- David Nordell, Senior VP for Strategy, Policy and Law, CSCSS / Centre for Strategic Cyberspace and Security Science (ISRAEL)
- Derek Cheng, CSO, TalkTalk (UNITED KINGDOM)
- Dr. Christoph Rojahn, Partner, Head of Corporate Security Solutions, KPMG Germany (GERMANY)
- Florian Polt, Group Security Officer, UNIQA Insurance Group (AUSTRIA)
- Gavin W. Jones, Director of SABRE, Building Research Establishment (UNITED KINGDOM)
- Georges-Pierre Cladogenis, Digital, Global Product Owner, Safety & Security / Program Messenger, Carlson Wagonlit Travel (FRANCE)
- Graham Ayre, Senior Internal Auditor, ArgoGlobal (UNITED KINGDOM)
- Graham Edwards, Recently Director of Security, Nationwide (UNITED KINGDOM)
- Henry Wilkinson, Director of Intelligence & Analysis, The Risk Advisory Group (UNITED KINGDOM)
- James Gooding, Director of Global Intelligence, InterContinental Hotels Group (IHG®) (UNITED KINGDOM)
- James Kwaan, Cyber Security and Privacy Consultant, Lloyd’s Banking (UNITED KINGDOM)
- Jenny Reid, Owner, iFacts (SOUTH AFRICA)
- Jeroen Meijer, Senior Partner, Control Risks (NETHERLANDS)
- Jonathan Watkins, Business Development Director, Blackdot Solutions (UNITED KINGDOM)
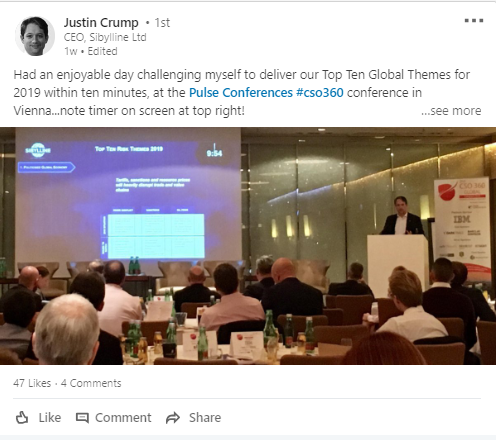
- Justin Crump, CEO, Sibylline (UNITED KINGDOM)
- Lady Olga Maitland, Founder, Defense & Security Forum, Chairman, Copenhagen Compliance (UNITED KINGDOM)
- Michelle Kay, Global Security Manager, Allen & Overy LLP (UNITED KINGDOM)
- Liz Chamberlin, Executive Director, International Security Management Association (ISMA) (UNITED KINGDOM)
- Luke Hull, Consulting Director – Europe, Cylance (UNITED KINGDOM)
- Matthew Drew, Group Security Director, Rolls-Royce (UNITED KINGDOM)
- Mark Lindsay, Senior Corporate Security Manager, Trans Adriatic Pipeline (SWITZERLAND)
- Mark Wolsey, Group Security Director, CRH plc. (UNITED KINGDOM)
- Nick Trigg, Enterprise Risk Management Consultant, BitSight Technologies
- Ned Farmer, Geopolitical Risk Manager, American Airlines (USA)
- Lady Olga Maitland, Chairman, Copenhagen Compliance (UNITED KINGDOM)
- Paul Kelly, Vice President, Global Security Operations, Fox Film, TV and Entertainment (UNITED KINGDOM)
- Paul Reither, CEO (Former Head of Security and Resilience, Oil and Gas), Diamond Advisory (AUSTRIA)
- Peter Drissell, Director Aviation Security, Civil Aviation Authority (UNITED KINGDOM)
- Rayna Milkova, Business & Client Intelligence Unit – Head of Russia & CIS, Deutsche Bank (UNITED KINGDOM)
- Raz Manne, Corporate Security, JTI (AUSTRIA)
- Richard Sumnall, EMEA Regional Head of Security, Uber (NETHERLANDS)
- Richard Schönfelder, Senior Cyber Security Manager, Darktrace (GERMANY)
- Roeland Stouthart, Head of IT, Kosovo Specialist Chambers, (Frmr CISO, International Criminal Courts) (NETHERLANDS)
- Ryan Long, Director of Global Risk Intelligence, Global Safety & Security, McDonald’s Corporation (USA)
- Dr. Sally Leivesley, Director, Newrisk Ltd, A Founder Member, The Exercise Group7 (UNITED KINGDOM)
- Dr. Victoria Baines, Visiting Associate, Oxford Internet Institute (Recently Trust & Safety Manager, EMEA, Facebook) (UNITED KINGDOM)
- Werner Cooreman, Senior Vice President – Group Security Director, Solvay (BELGIUM)
2017 CSO 360 Congress, Amsterdam
Check out the video from last years’ CSO 360 Congress to hear what speakers, sponsors and delegates thought!
“Embraces the changing threat environments, great experience, fabulous speakers, pertinent interesting focus”
Special Tribunal for Lebanon (The Hague)
“I just had the best conference ever!”
CCO, BT (Netherlands)
“A great one stop shop of the top CSO minds!”
VP, Corporate Security and Resilience, Pearson (UK)
“I was extremely impressed by the content, quality, origination and administration of the Pulse product”
MD, Tierra Nova Solutions (Sierra Leone)
“Simply the best event for security practitioners. Real expertise and knowledge sharing”
Group CISO, Unipart Group (UK)
“This has been a fantastic event. Awesome speakers addressing a diverse range of interesting and relevant topics. Also, great job by Team Pulse. We have been looked after so well! Thank you!”
Regional Security Director, Caterpillar Inc (Switzerland)
Key themes for the 2nd CSO 360 Congress – Vienna 2018
- Evolving risks and opportunities for security – protecting nations and businesses
- Integrated threat intelligence, identity management and incident response strategies
- Brand protection – updates and challenges on IP and illicit trade
- Kidnap and Ransom
- Insider threat – new tactics
- Investigations
- Securing and leveraging advanced technologies – IoT, AI, machine learning
- Boardroom: culture and engagement
2018 Programme at a Glance
Tuesday 4 December 2018
Pulse Educate – Half Day Courses Designed for Chief Security Officers
12:00-16:00 – Ritz Carlton Vienna
Option 1: Open Source Intelligence Strategies for CSOs and Security Investigators
Led by: Ciaran Richardson, The Exercise Group 7
Option 2: Resilience Communications Training – Media, Brand Protection, Crisis Governance
Led by: Dr. Sally Leivesley, The Exercise Group 7
Welcome Reception 2nd CSO 360 Congress
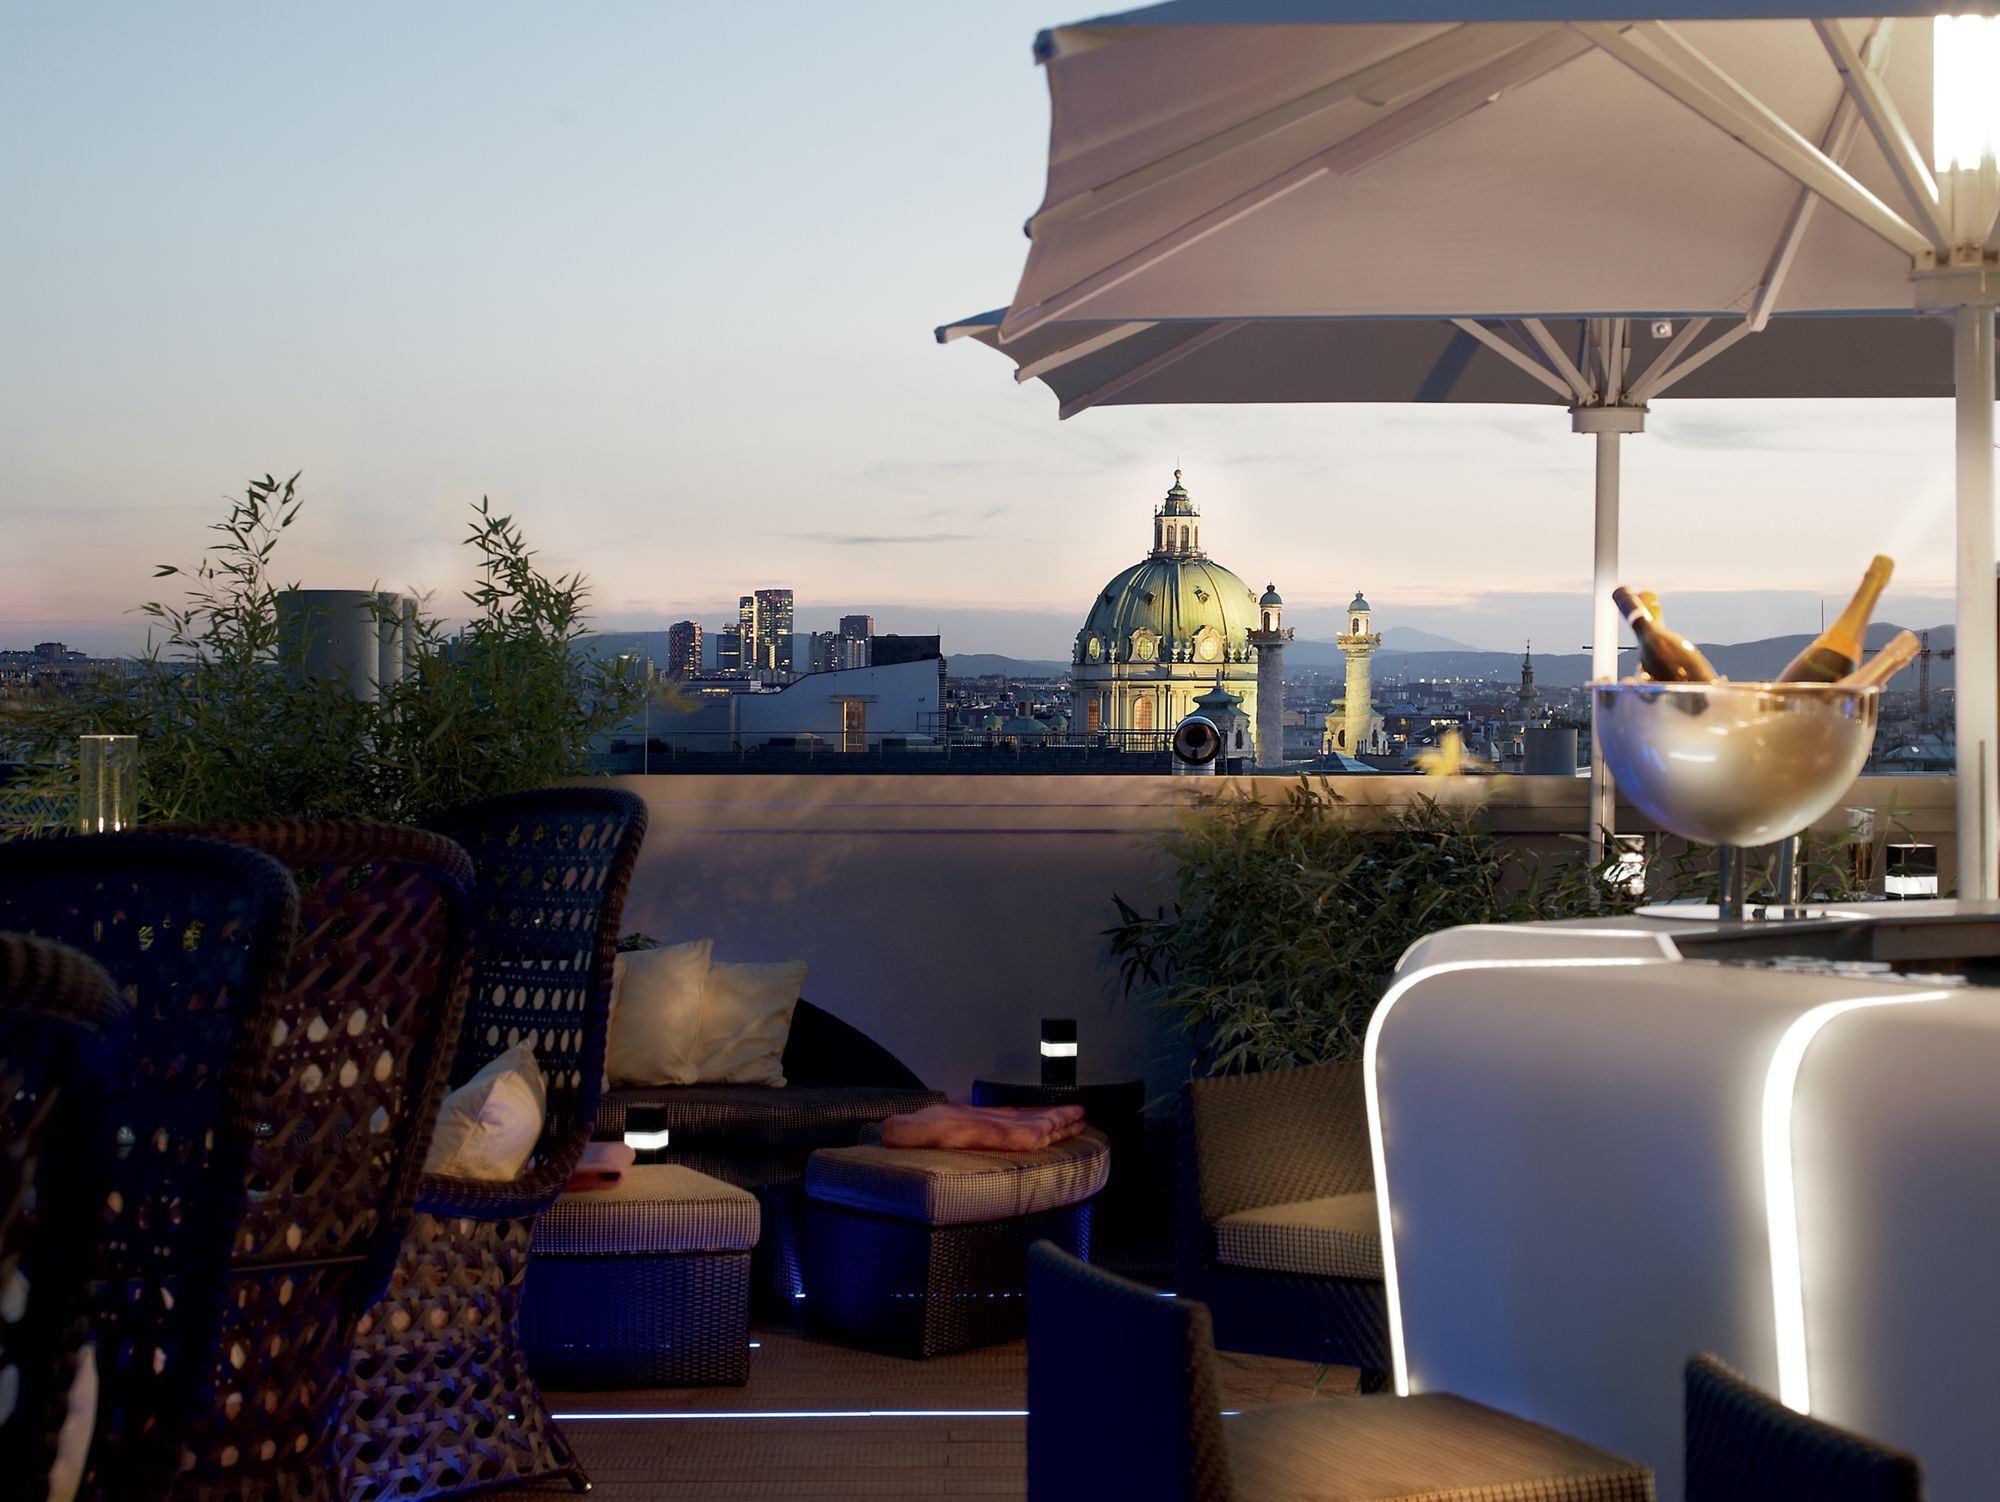
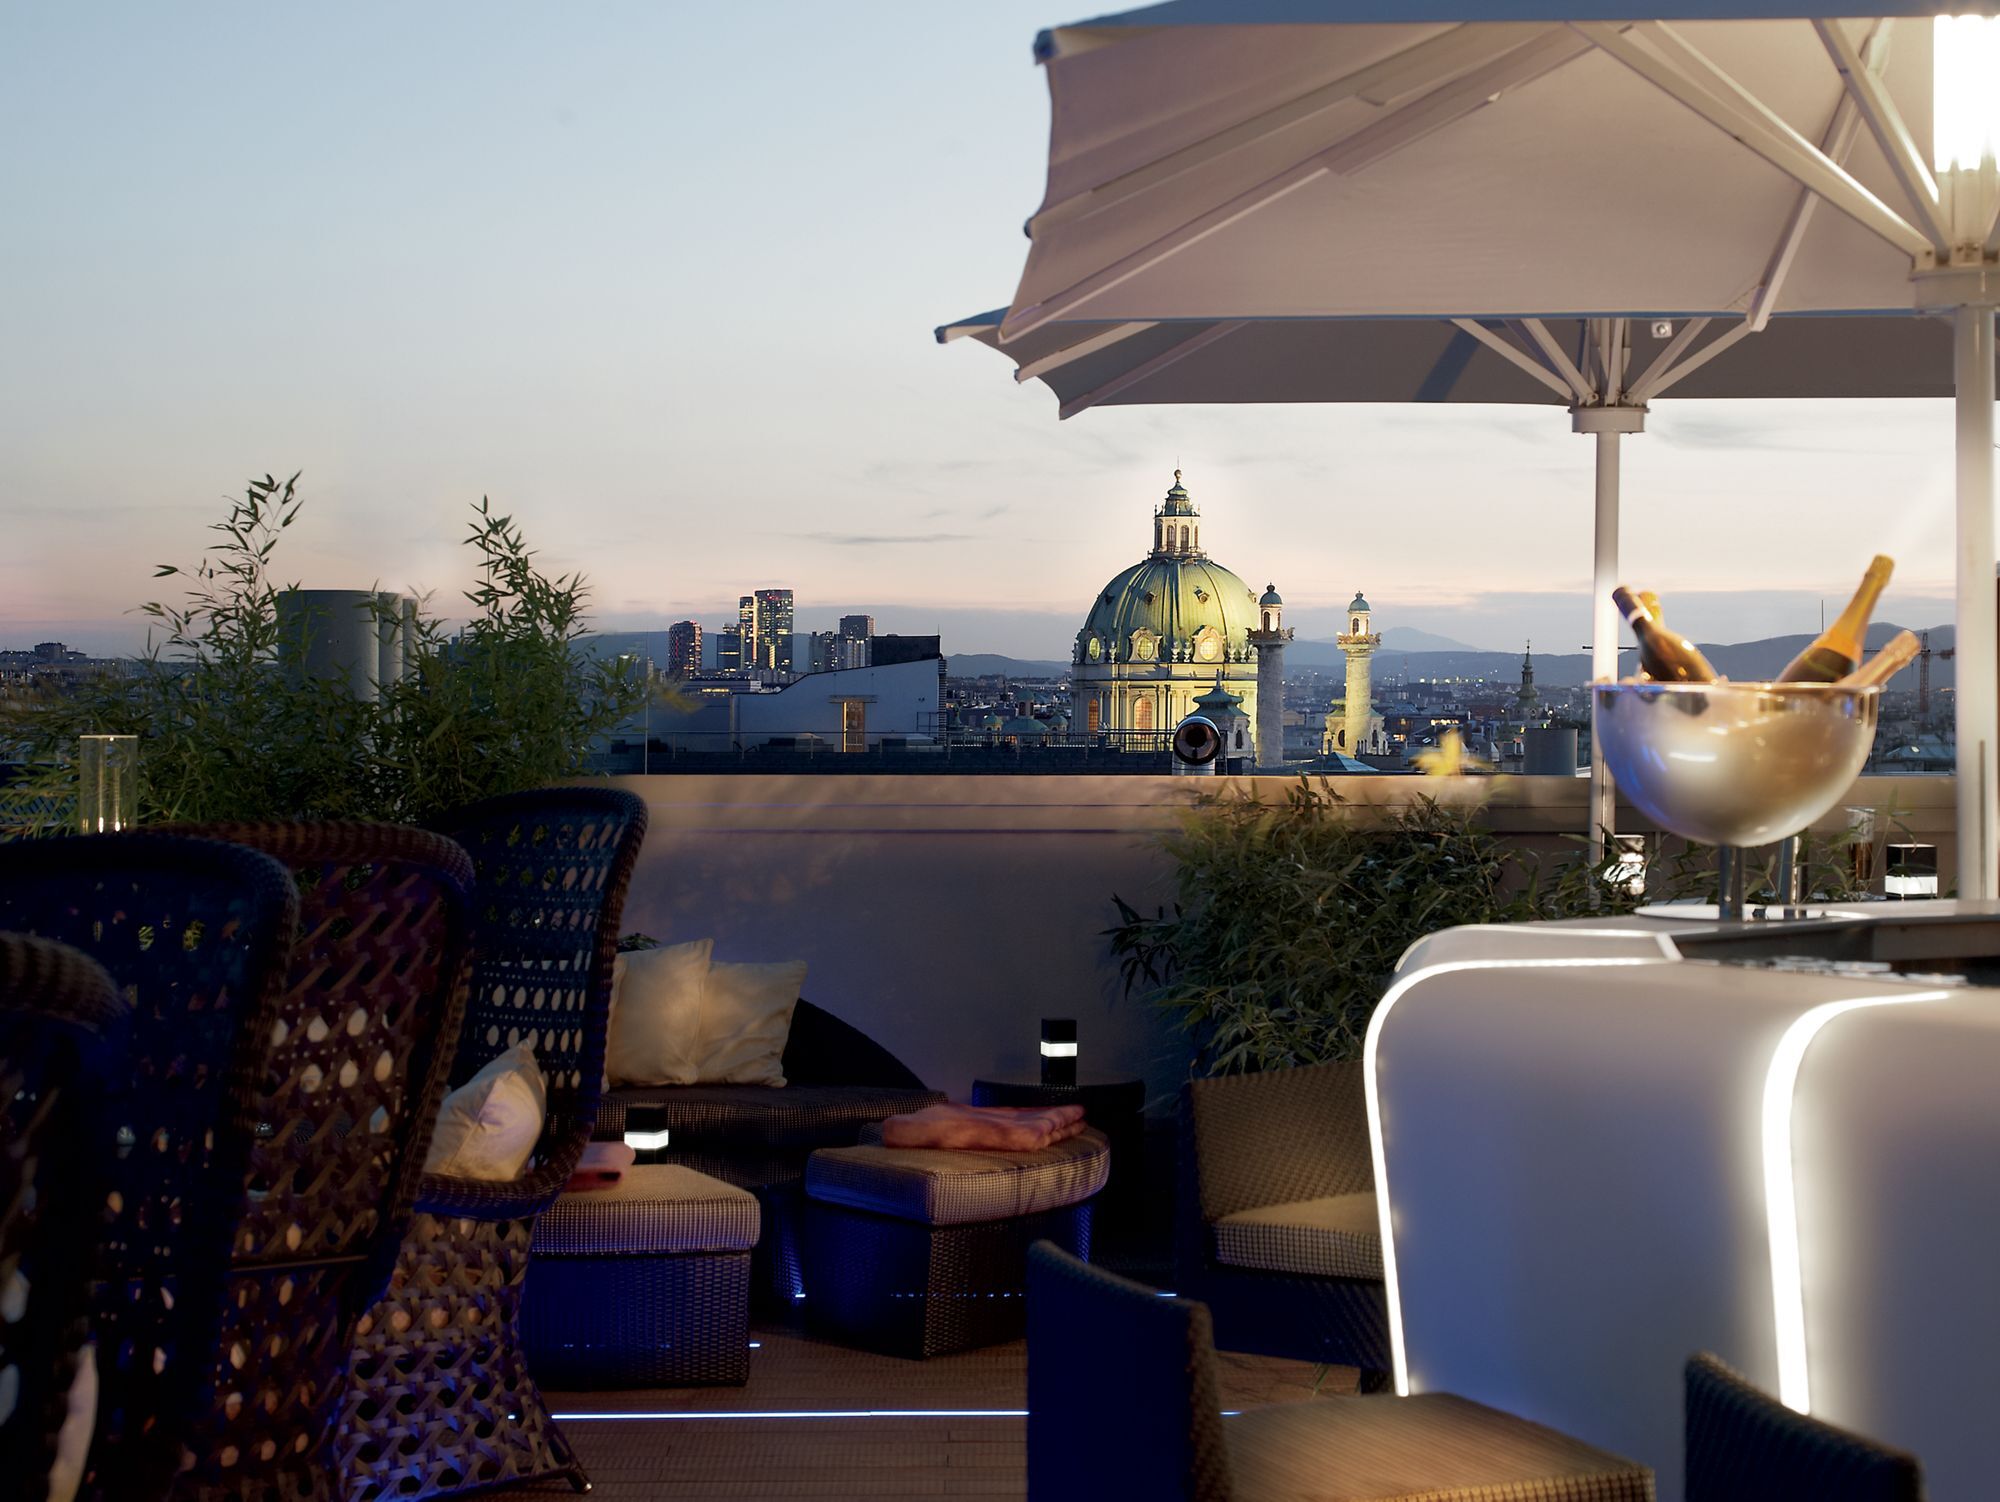
19:00-21:00 – Roof terrace, Ritz-Carlton Vienna
Wednesday 5 December 2018
Day One: CSO 360 Congress
08:00-17:00 – Congress in session – Ritz-Carlton Vienna
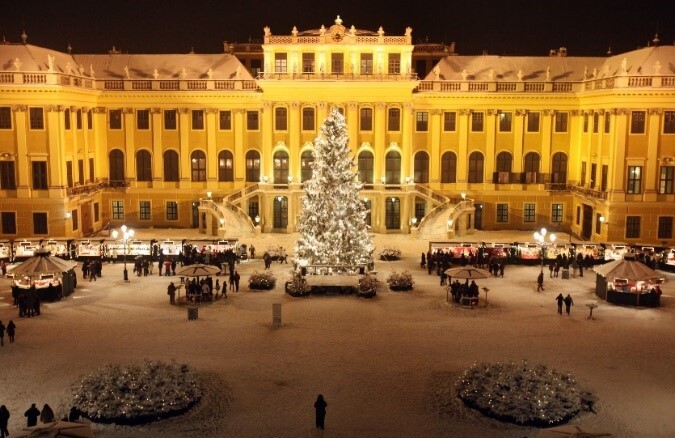
18:00-20:00 – Reception – Schönbrunn Palace – Kindly sponsored by: The Risk Advisory Group
20:00-20:30 – Christmas Markets
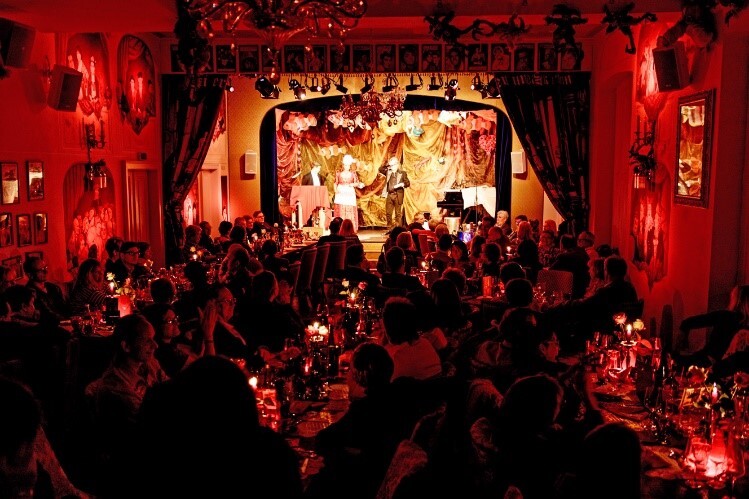
20:40-23:00 – Dinner – wonderfully quirky, theatrical restaurant located a 5-minute walk from the Schönbrunn Palace!
Thursday 6 December 2018
Day Two: CSO 360 Congress
09:00-16:00 – Ritz-Carlton Vienna
16:00 – Goodbyes
View last years' brochure
Networking events – an integral part of any CSO 360 Congress experience!
All delegates, speakers and sponsors are encouraged to attend. There is no extra cost.
We are currently inviting the NEW 2018 international speaker panel.
Please contact teampulse@pulseconferences.com for the most recent agenda or if you are interested in speaking or proposing a speaker.
Receive 2 complimentary books signed by 2 of the keynote speakers at the 2nd CSO 360 Congress!
Book by 31 October 2018 for savings and to receive onsite:
Pulse Conferences Privacy Policy
To read about Pulse Conferences Privacy Policy and download in pdf format please click below.
Download Privacy Policy
2018 Sponsors
Platinum Sponsor
Gold Sponsors
Silver Sponsors
Panel and Reception Sponsor
Supporting Association
Pulse Educate – Tuesday 4 December
Half-day training courses designed for Chief Security Officers
Open Source Intelligence and Cyber Strategies for CSOs and Security Investigators
Tuesday 4 December 2018: 12:00-16:30
Cost: £800
Place: Ritz-Carlton Vienna
*Please note that all training courses are pending a min amount of booked delegates
Over two days, delegates are shown the reality of just how easy real cyberattacks can be – even those with the most devastating effects – and the implementation of simple measures to avoid catastrophic risk. The course is suitable for entirely non-technical officers as well as cyber managers and administrators who wish to develop a sound understanding of just how easy and low-tech the efforts of an attacker can be, and how to implement mitigation or who wish to upgrade their existing skills to become more cost effective for their organisation. The practical elements are comprehensively taught in a walk-through manner to demonstrate the vulnerabilities in realistic targets. A key theme running through the course is that of workforce vulnerability – no matter how well defended the organisation’s intellectual property is, the staff are the way in.
Day One – The Risk
Focuses on the mindset and techniques of the attacker, whether a cybercriminal, a state actor, a corporate spy or frivolous hacker. Students are equipped with tools and techniques to perform investigations of targets in the preparation for a notional attack, essentially becoming the hacker to demonstrate just how easy those attacks often are due to the visibility of staff and corporate data online.
Introduction to Cyber Risk
- “It’s not about the tech” – why the attackers’ techniques are surprisingly low-tech, and why the information security risk lies with the human workforce, not their computers.
- Real world examples of catastrophic attacks and the vulnerabilities in every organisation.
- One size fits all – the common vulnerabilities used by any attacker against any target: corporate, government and personal.
Attacker Methodology
Part One – reconnaissance
Scoping a target. A practical module demonstrating to delegates how an attacker uses OSINT (open source intelligence) to obtain corporate data and personal details using nothing more than search engines and free, legal tools.
Part Two – Attack
- Compare and contrast of ‘technical’ attacks with low tech and no-tech hacking by social engineering.
- Teach a man to phish. Understanding the myriad ways an attacker uses the freely obtained data to quickly penetrate an organisation through simple influence.
The Persistent Threat of Leaked Data
The permanent threat to corporations that arises from leaks of staff data from breaches such as Yahoo – even when non-corporate in nature, and even when many years old. Delegates are show the surprising amount of leaked data online and what to do about it.
Wi-Fi – the Corporate and Personal Risk
The largely unknown risks of wi-fi, not only as a vehicle for corporate intrusion by attackers but also for tracking the physical movement of individuals and identifying their homes. A practical module in which students are walked through the steps of an attacker breaking into corporate wi-fi and tracking of staff members using freely available tools.
- Methods of communication.
- The threat from disgruntled personnel.
- Coaching and mentoring.
- Managing change.
Objectives of course – Designed for CSOs and Security Investigators
- Zero-to-hero teaching approach to tracking down internal and external threats to organisations through:
- Personnel tracking – assessing the vulnerability of the “good guys” (our staff and our senior management/CEO) and tracking down the “bad guys” (would-be attackers.)
- Techniques in finding accessible, sensitive corporate data before the attacker does
- Implementation of free and low-cost, non-technical tools and techniques for CSOs in the collection of potentially useful information for investigative purposes, bolstering investigative (and auditing) capacity at minimal expense with a range of open source tools and methods.
- Clear understanding of the utility of seemingly innocuous open source data in the hands of malicious attacker – whether a technical attack or phishing and social engineering, noting that most attacks take place by exploiting members of staff.
About the Tutor
North Cyber are team of former intelligence officers with expertise in covert online operations and digital forensics. The company teaches government and corporate clients how find and fix the unseen holes in their security. They specialise in all levels of capability including low-tech and no-tech hacking, using freely available information to circumvent vastly expensive but ineffective security systems. The teaching draws on many and varied real-world examples from the private and government sectors, from the perspectives of the attacker and incident responder. Participants in these courses will evaluate their own experience on the course in gaining additional skills and understanding of the threats to their organisation and they will gain confidence in tackling these catastrophic risks to the comparate or government operation.
Resilience Communications Training – Media, Brand Protection, Crisis Governance
Tuesday 4 December 2018: 12:00-16:30
Cost: £800
Place: Ritz-Carlton Vienna
*Please note that all training courses are pending a min amount of booked delegates
Module 1 – New Threats – covers on new threats to energy and critical infrastructure, railways, aviation, shipping and ports, construction of buildings and to the financial and government centres of major cities. Catastrophic hazards that often generate media inquiries include internal issues within the corporation or government department, large transformation projects, major infrastructure construction, terrorism, cyber- attacks, extreme weather events, insider threats, security, organised crime and fraud and events such as Brexit, North Korea’s nuclear weapons programme, mass population movements, and military exercises close to national borders.
- Overview of regional and local threats to infrastructure and business
- New threats- cyber, terror, energy, transportation, leisure, finance and banking, building security
- Emerging events – Nation State hostilities, climate change and severe weather, Brexit,
- Interpreting threat intelligence and other information
- Situational awareness
- Crisis phases and human reactions
- Critical timelines for Internal and External Communications
- Team building for successful communications
- Cues, Signs and Symptoms
- When should Warnings be given
- Redressing Errors
Module 2 – Optimising Communication Strengths is a practice session for all the participants to identify their strengths in contributing to a media and brand resilience process. This could be gathering information and team leadership or presenting information to internal staff, stakeholders or preparation of information for spokespersons to use in media statements.
- Practice session for all attendees
- Case studies chosen are relevant to attendees’ industry sectors
- Building trust with the team and the media
Module 3- Governance for Crisis Communications brings together all the phases of a catastrophic event with new governance principles that will assist in reporting after an incident on how processes were successfully managed to contribute towards the brand protection and resilience operations of the organisation.
- Governance Principles relevant to the Communications Plan
- Analysing Feedback
- Brief Messages
- Regular timing of messages and trust building
- Recognising hostility and reducing tensions
- Assessing effects on the Brand and reducing losses
- Course Summary and Evaluation
- Individual completion of self-evaluation of changes in skill levels Modules 1-3
About the Tutor
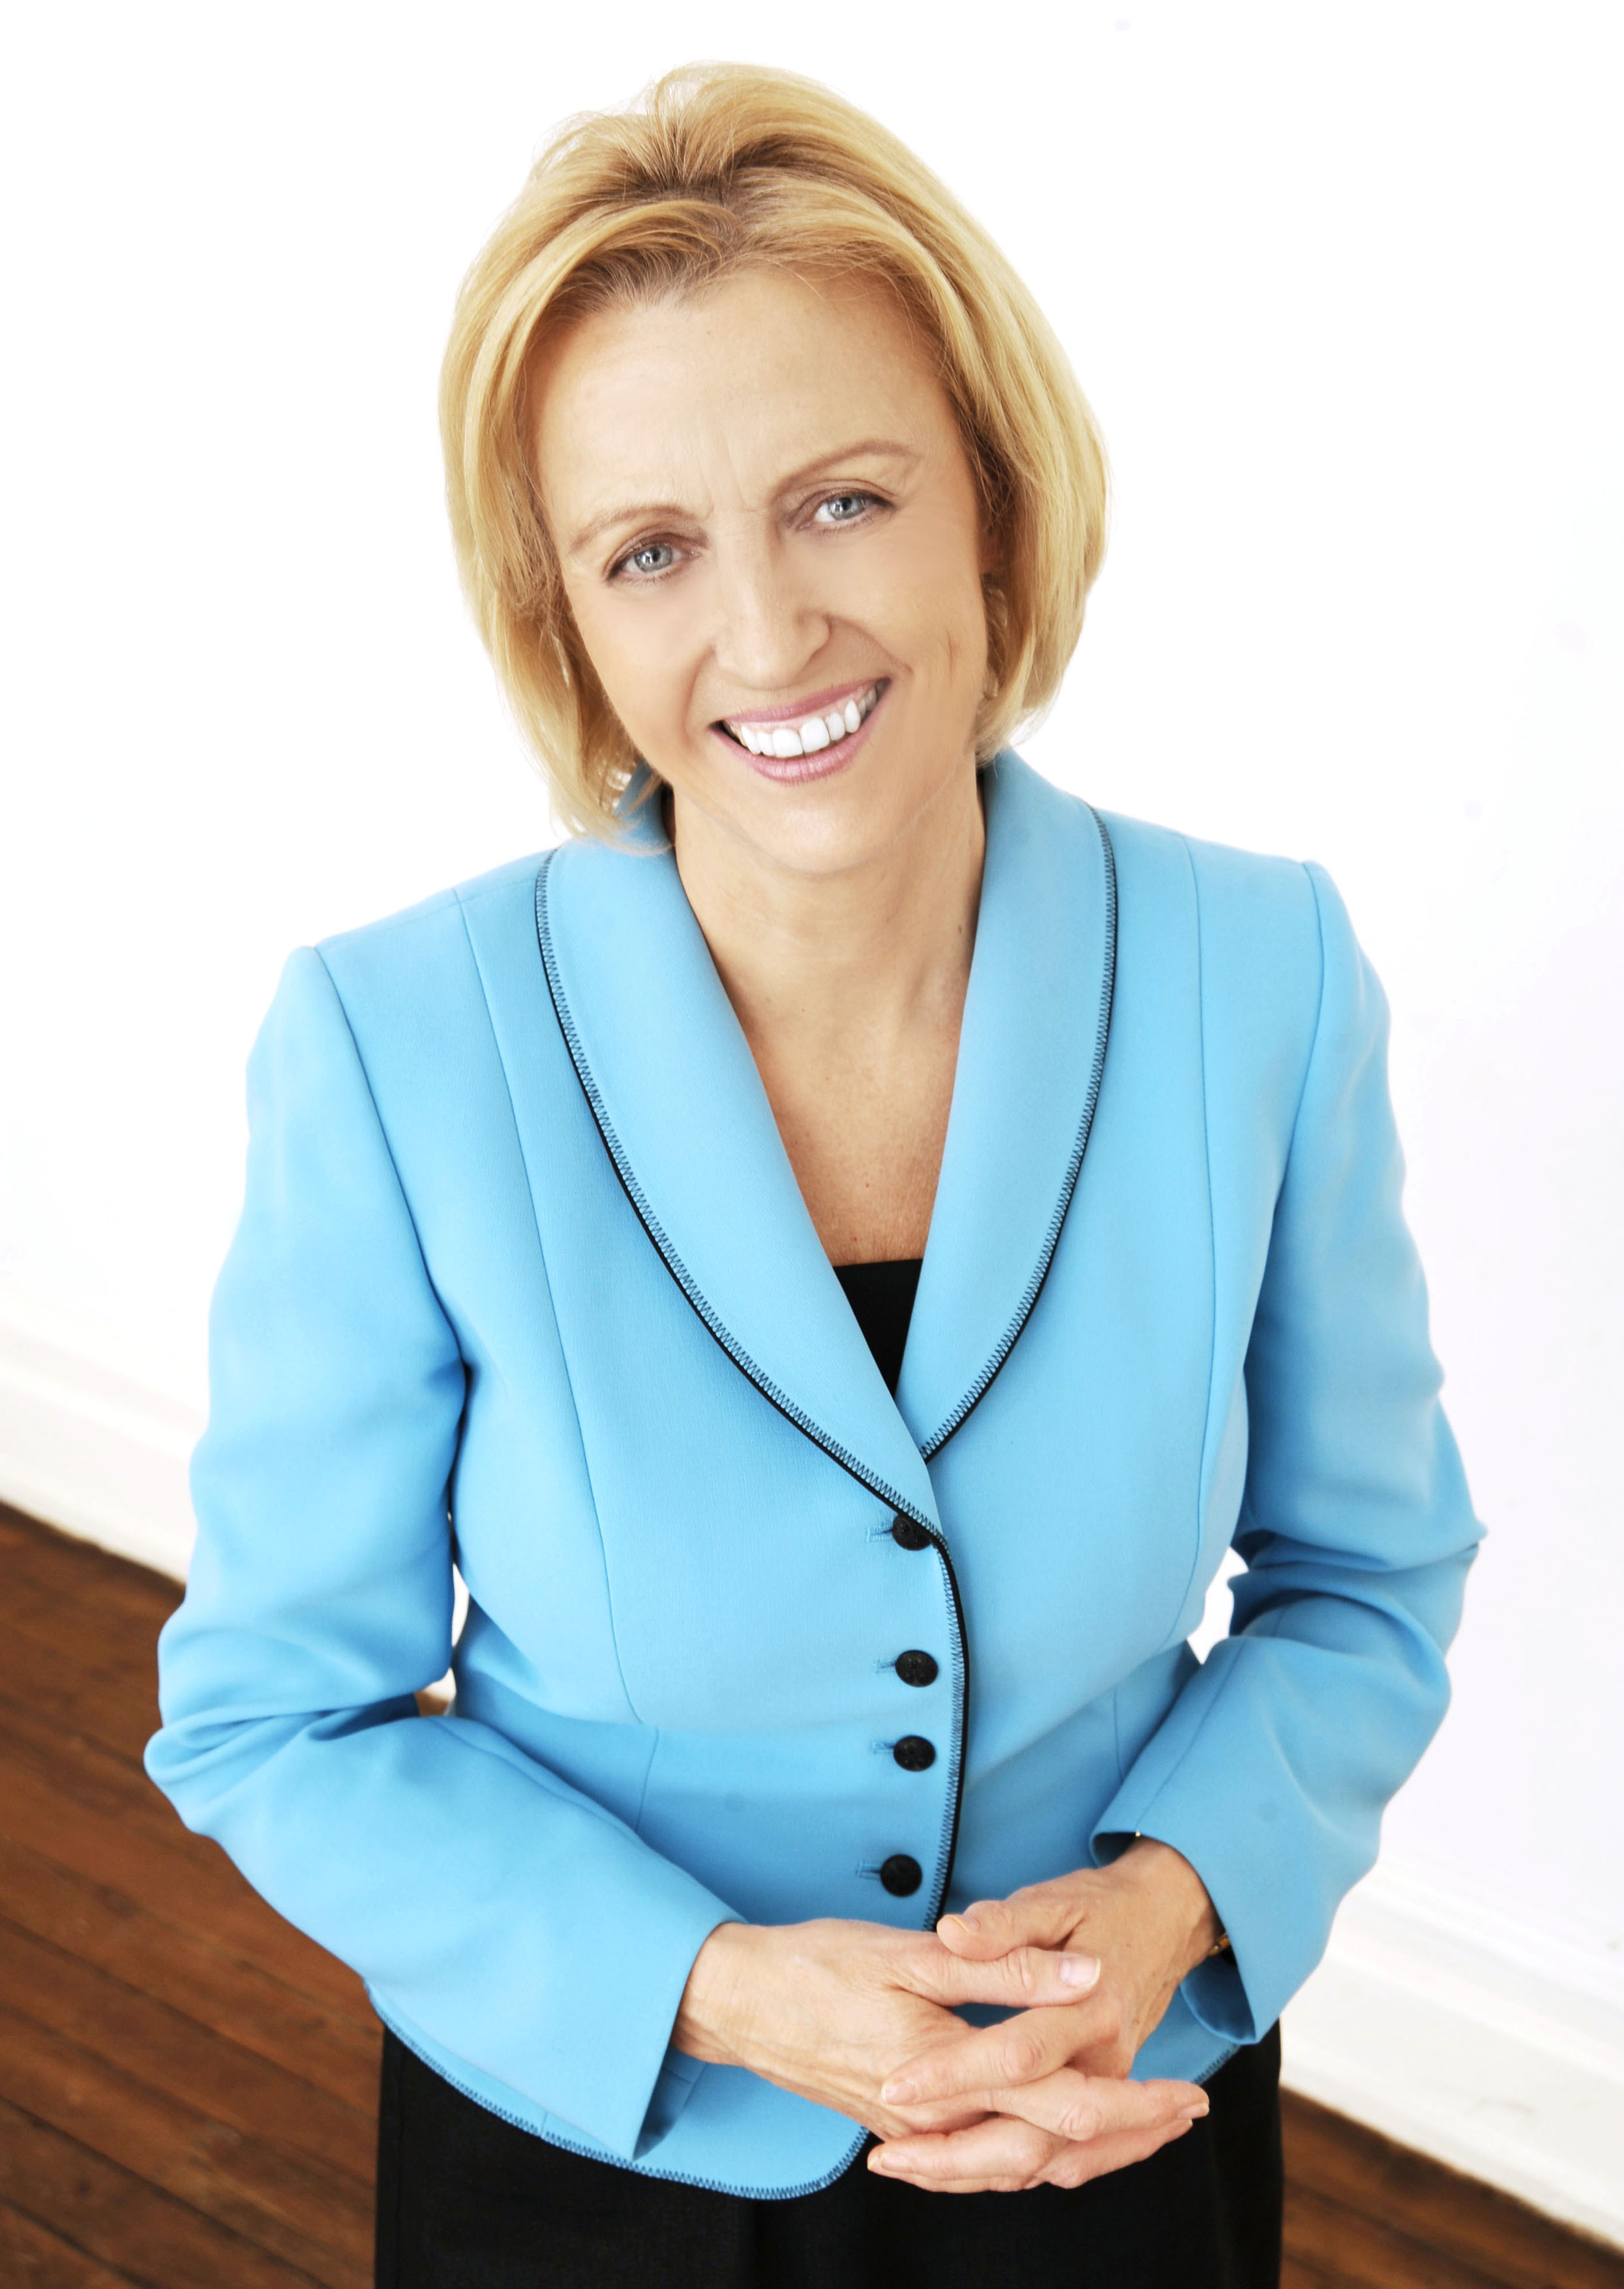 Dr Sally Leivesley is an expert in catastrophic risk and security for protection of life and critical infrastructure. She provides around 100 interviews to media a year on extreme events and communicates on public safety issues. She has been providing commentary to the BBC World Service and many other media outlets since 9/11 and commenced her media communications work when tasked with recovering a city after a severe weather disaster. Her media work includes real time commentary during extreme life threatening events such as the Beslan school terror attack and in the immediate aftermath of terrorist and other incidents such as the flight MH17 aviation incident, Mr Litvinenko’s radiation poisoning, natural disasters, threats such as DPRK nuclear programme, terror attacks in France and Brussels, Britain’s 7/7 and 21/7underground rail terror attacks and she covers most major incidents of importance to the public in any year. She has worked in catastrophic risk assessments and training within critical infrastructure covering many industries including energy, petrochemicals, rail, aviation, shipping, banking, government emergency planning and nuclear, chemical, biological and radiological incidents. (www.Newrisk.com Recent Media Commentary).
Photos 2nd CSO 360 Congress, Vienna, 5-6 December 2018

White Papers and Articles

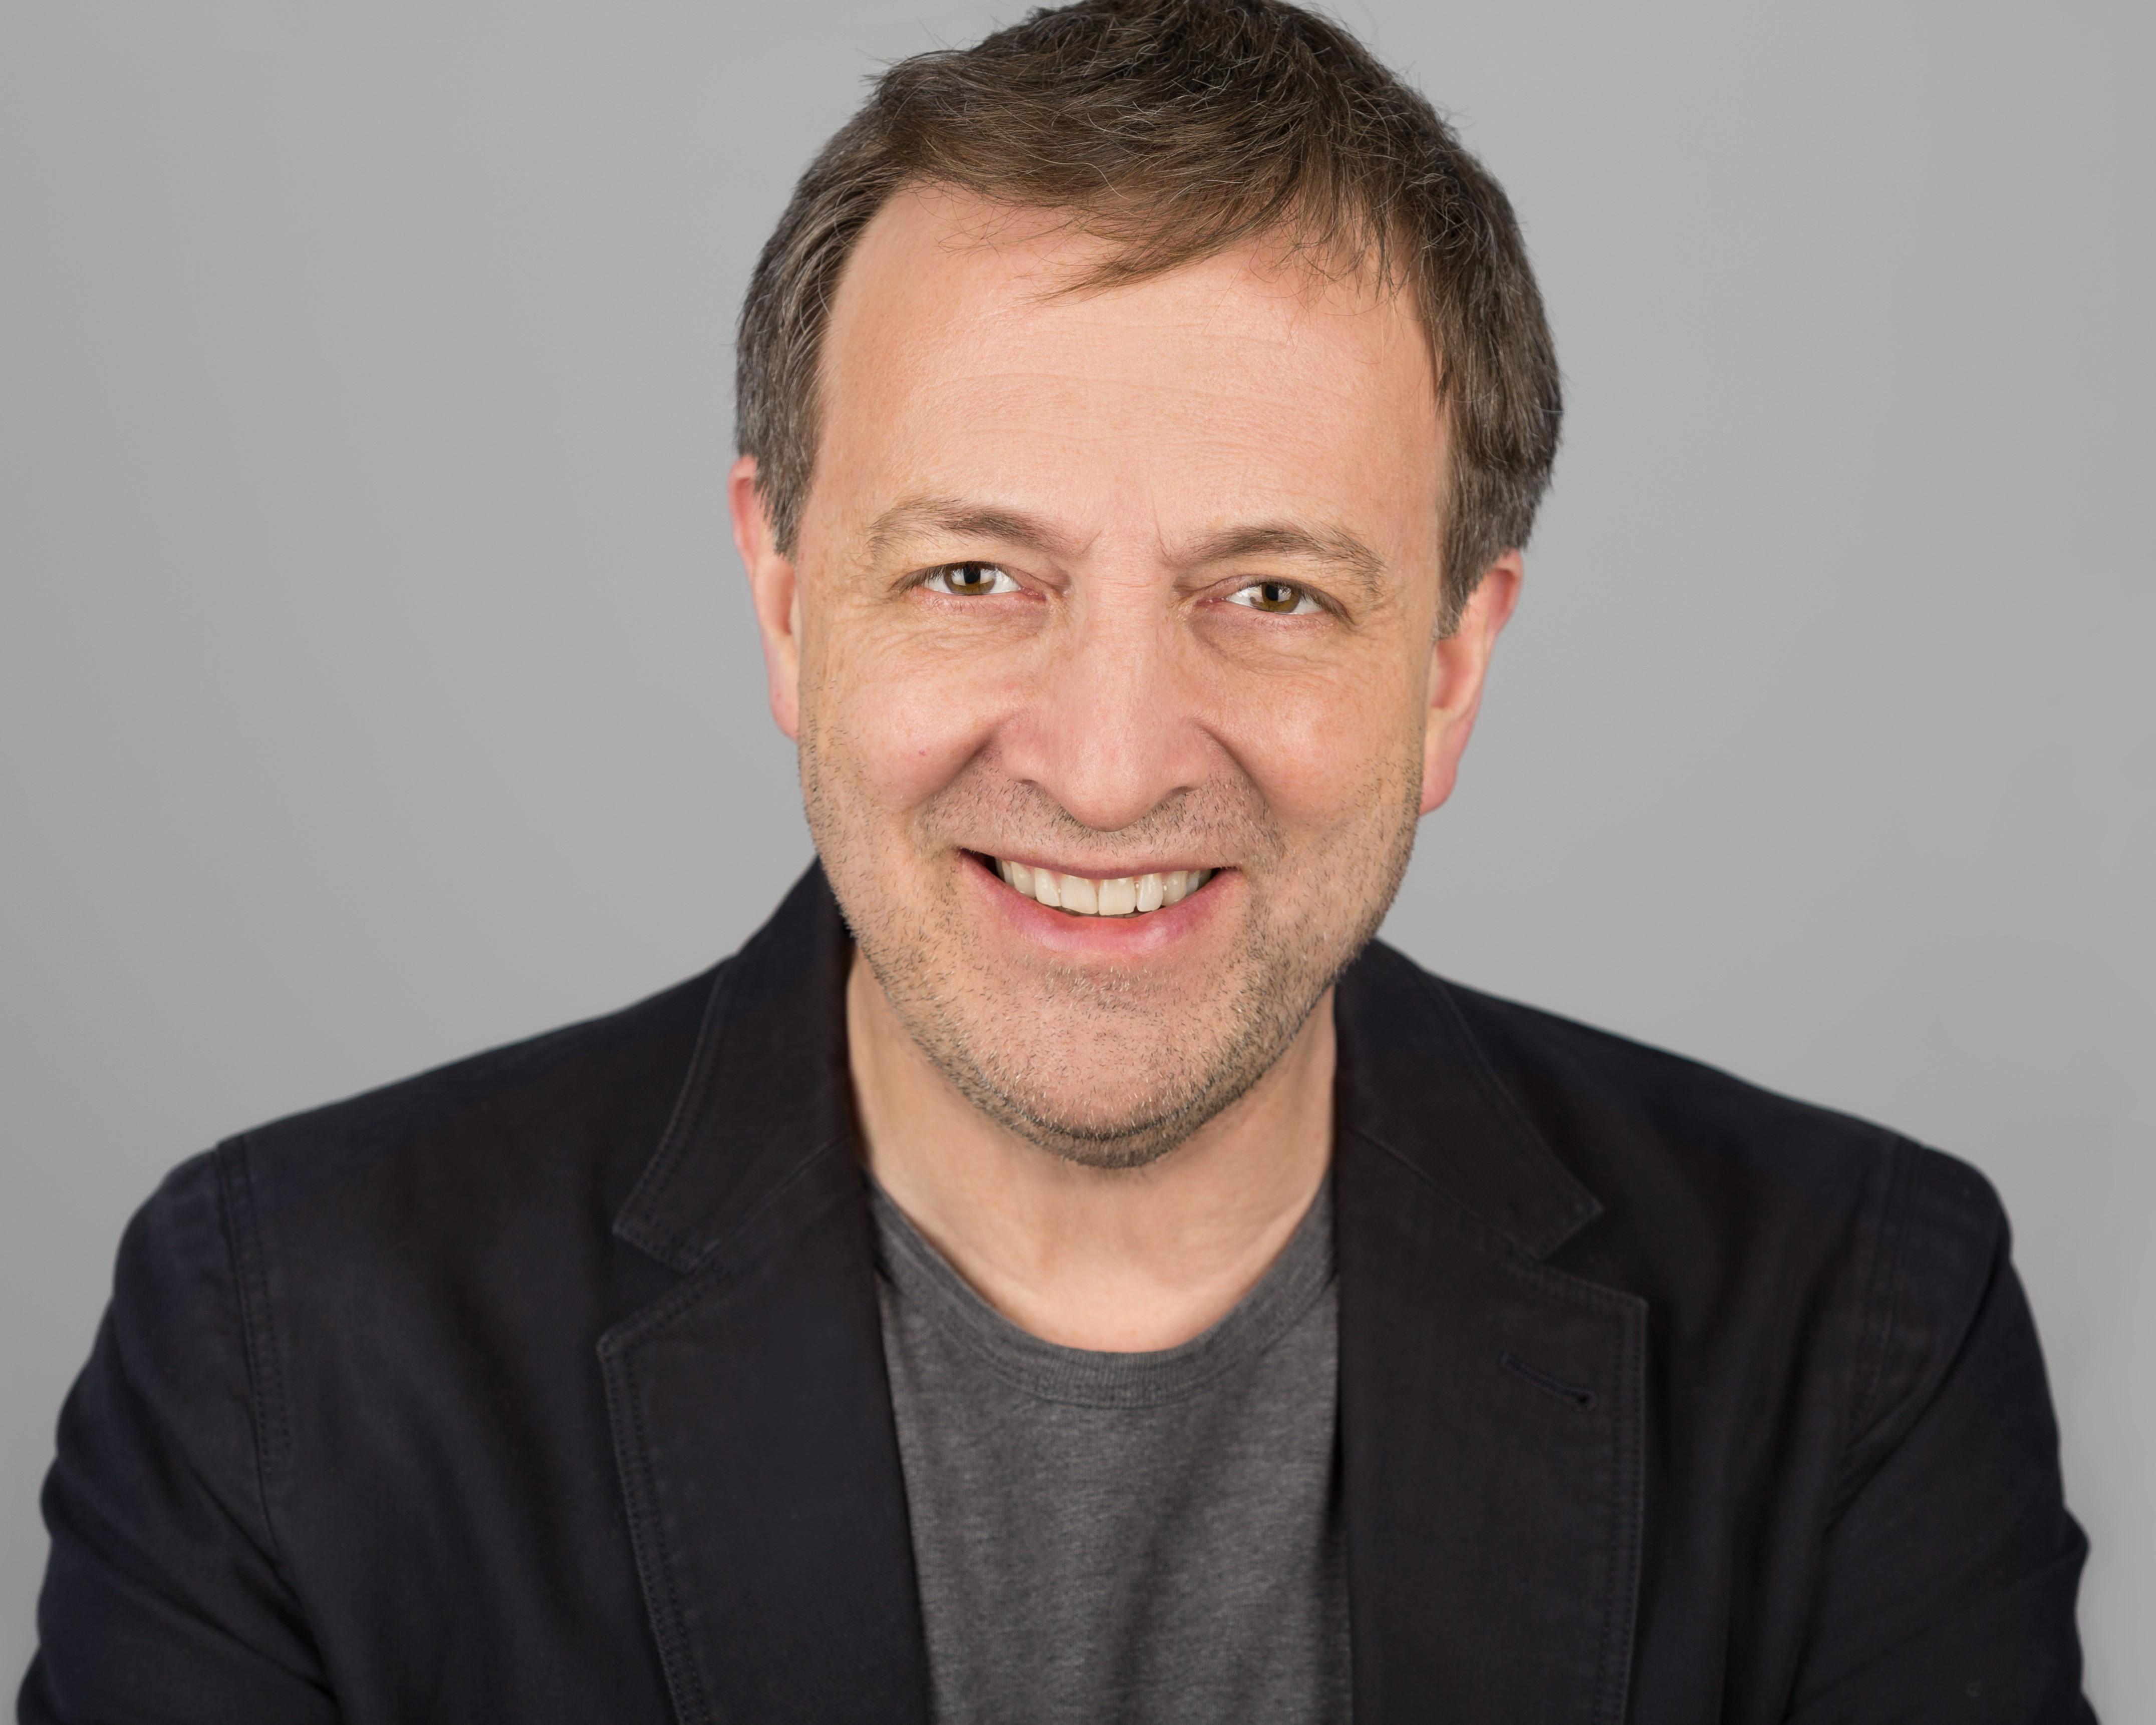 Misha Glenny is an award-winning writer and broadcaster. His bestselling non-fiction book, McMafia, about the globalisation of organised crime has launched this year on the BBC and AMC as a fictional TV Drama series. Glenny’s most recent book, Nemesis: One Man and the Battle for Rio, the biography of the man who ran the largest favela in Rio for five years as head of the cocaine cartel, is also in production as a Hollywood feature film. Like these two works, Glenny’s book on cybercrime, DarkMarket: How Hackers Became the New Mafia, is based primarily on interviews with people activity engaged in criminal activity. Glenny interviewed criminal hackers and intelligence agents in some 20 countries to map the development of cyber malfeasance in the first 12 years of this century. A former BBC Central Europe correspondent who covered the revolutions in Eastern Europe, Glenny won the Sony Gold Award for Outstanding Contribution to Broadcasting for his work during the wars in the former Yugoslavia. He is also a past winner of Digital Security Journalist of the Year. Glenny recently served as a visiting professor at Columbia University’s Harriman Institute where he ran a course entitled Crime, Corruption and Economic Transition. He was voted the best lecturer at SIPA for his work there. Glenny has also worked as a Professor at the London School of Economics and is currently preparing a master’s course for University College London. He is regularly consulted by governments in Europe and the Americas on the Balkans and Eastern Europe; on trans-national organised crime and on cyber security. At present, he is developing and writing two television drama series, one focusing on crime and corruption in Rio de Janeiro, and the second, a political thriller about hackers. He is on the international advisory boards of several major NGOs.
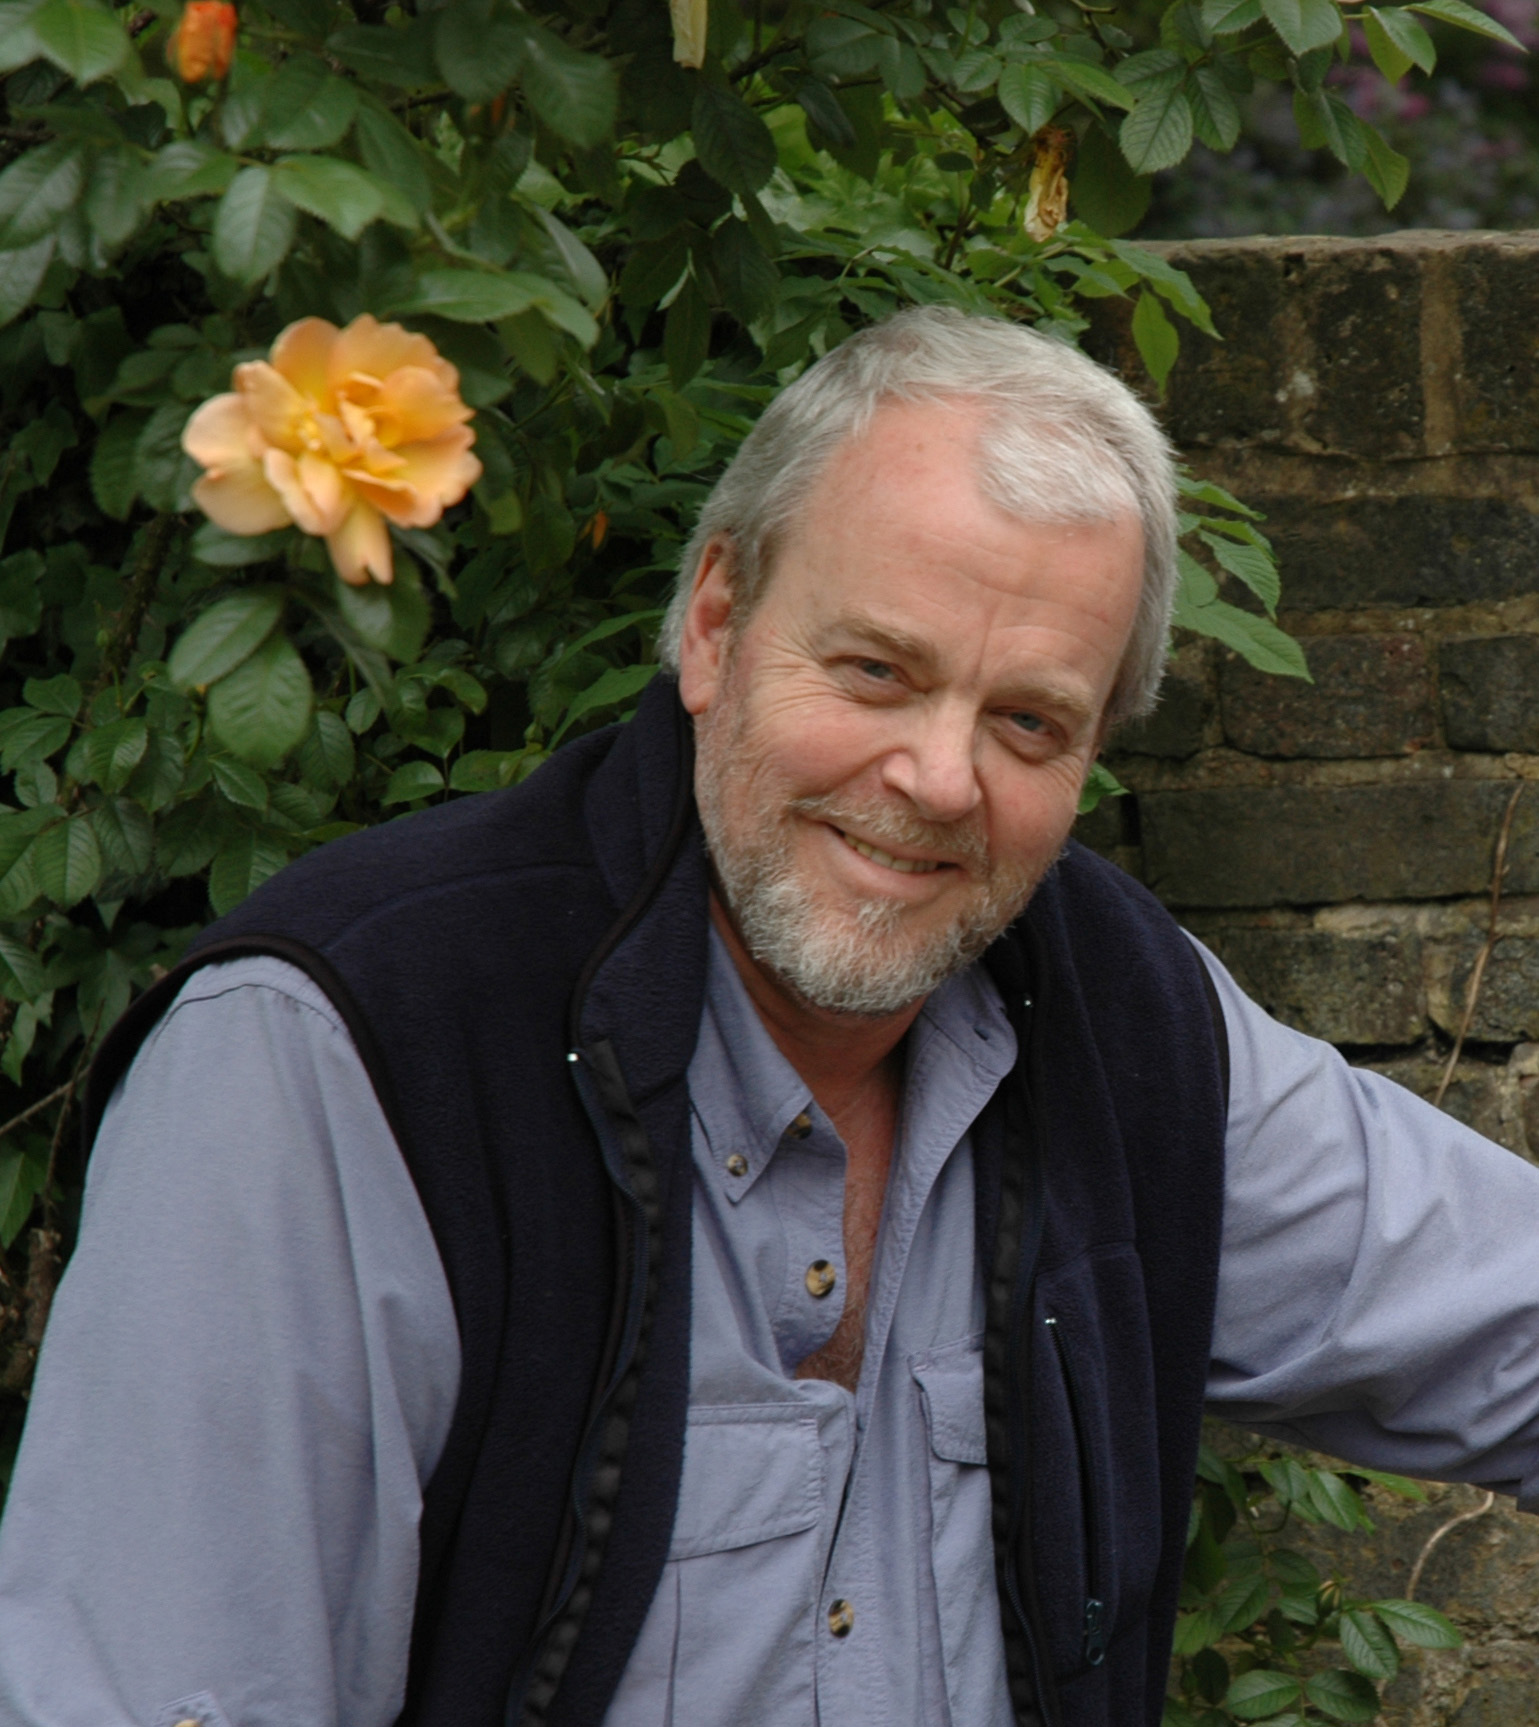 Hugh is a political risk analyst and an historian of conflict, best known for his best-selling Razor’s Edge: The Unofficial History of the Falklands War, and Rebels and Redcoats: The American Revolutionary War. For a full bibliography see:
 She has a distinguished career working in crisis response, having joined Control Risks in 1999 as the Crisis Response Research Manager and was appointed Director of Response Business Operations in 2009. She joined Hostage in February 2017 as their first full-time director, bringing with her an exceptional knowledge of worldwide kidnapping trends and an understanding of the impact that kidnapping has on both corporates and families. She has extensive experience in directly assisting families affected by a kidnap and in supporting former hostages. Lara regularly delivers training in best practice in family support and hostage re-integration. Lara holds first class degrees in Law (University of Oxford) and Political Science (McGill University) and a Masters degree in International Relations (McGill University). She qualified as a solicitor in 1997, and practised as a civil litigator in London. Fluent in French and Spanish, Lara also previously worked at the European Commission in Brussels.
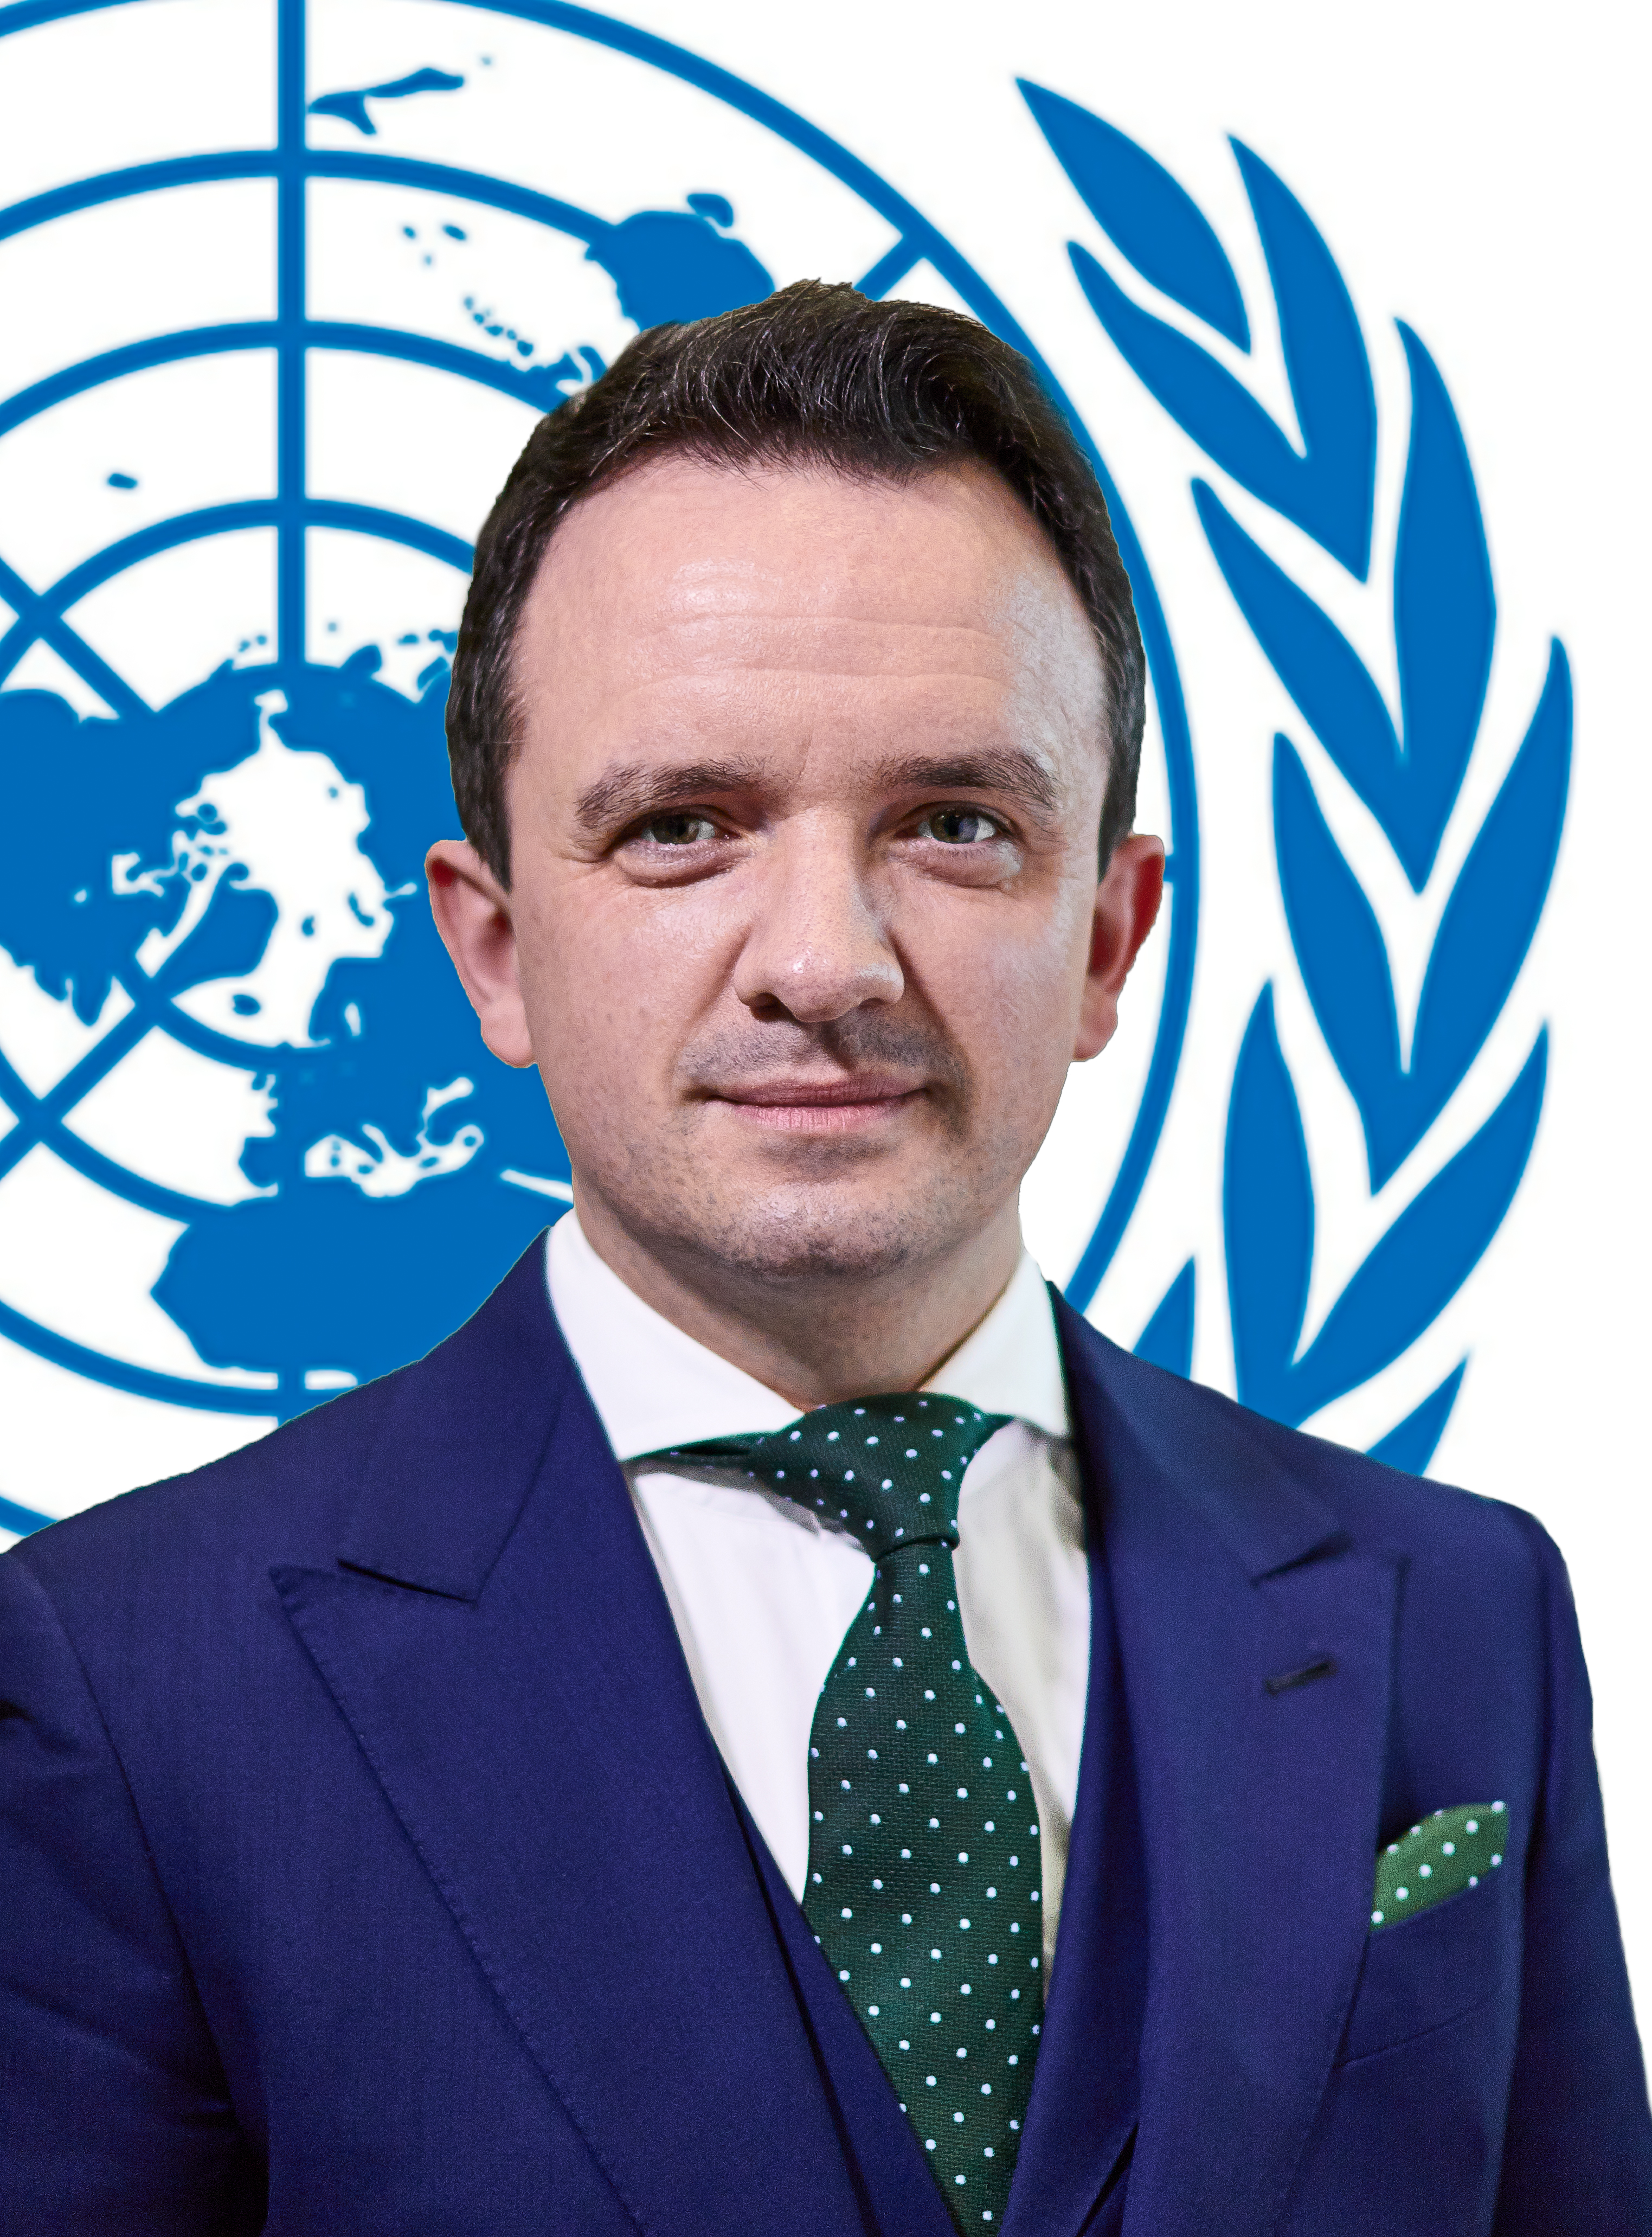 Neil J. Walsh, Chief – Cybercrime and Anti-Money Laundering Section, Organized Crime and Illicit Trafficking Branch, Division for Treaty Affairs, UN Office on Drugs and Crime
 “Great programme, great organization and great attendance have made discussions useful and passionate . Listening testimonials, sharing experiences and ideas regarding good practises , discovering other industries or business ! : you have made my days in Vienna !“