Archive · CISO 360 Global Congress

Flagship 5th CISO 360 Congress - Windsor 2021

This event took place on 7-8 July 2021 at Virtual.

Date7-8 July 2021
VenueVirtual

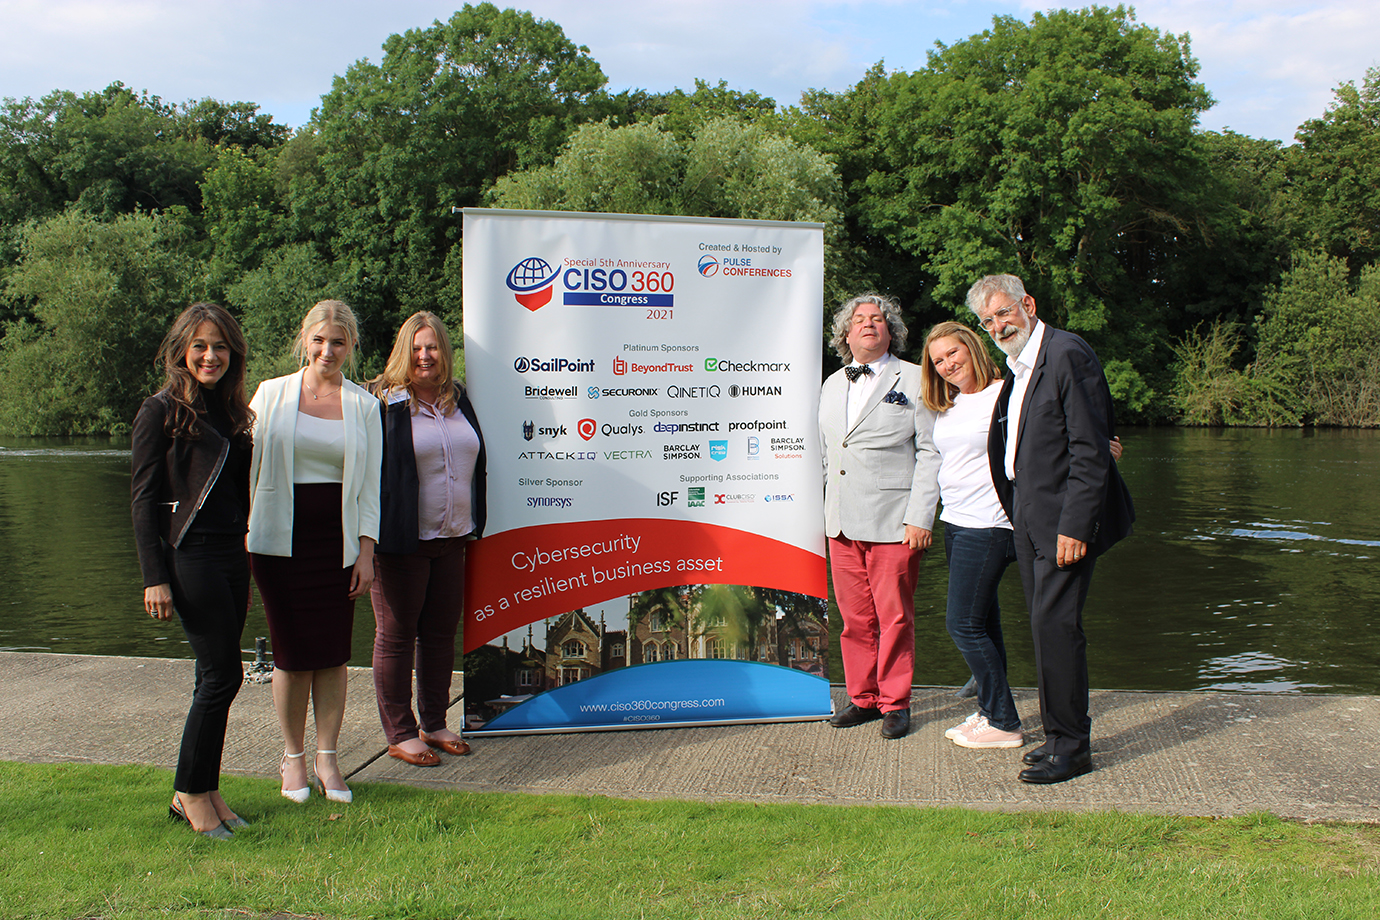
Pulse Conferences would like to thank everyone who participated, in-person or virtually in our very special 5th Annual CISO 360 Congress, 7-8 July 2021!

View recent highlights, testimonials and materials!
5th Annual CISO 360 Congress & Roundtable
7-8 July 2021 – Oakley Court, Windsor, United Kingdom 

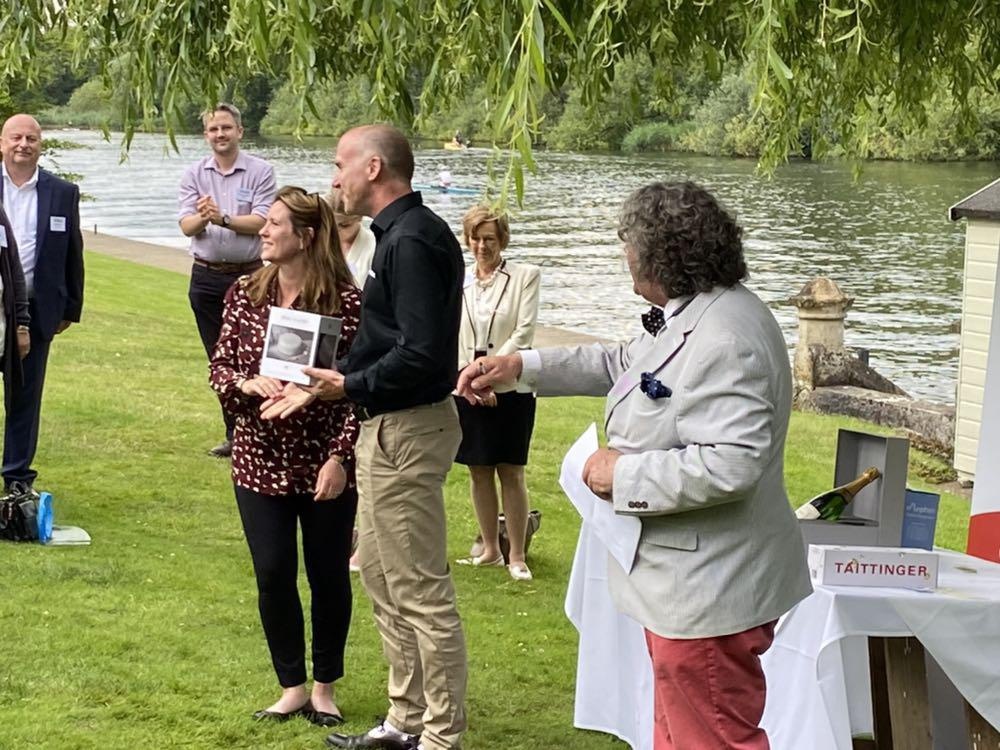
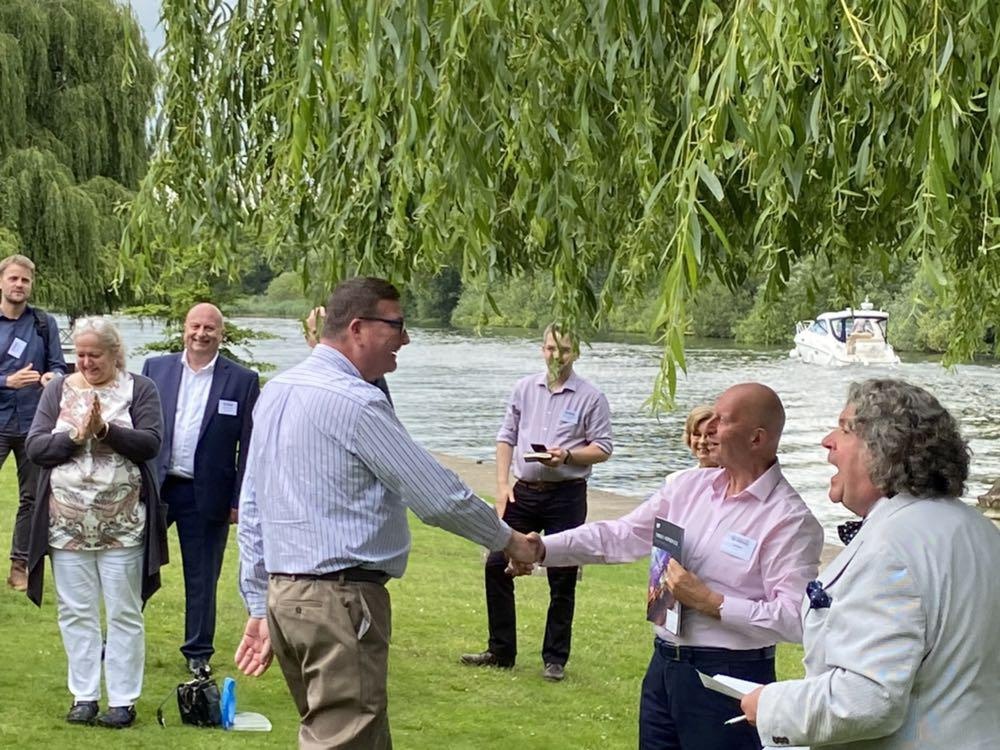
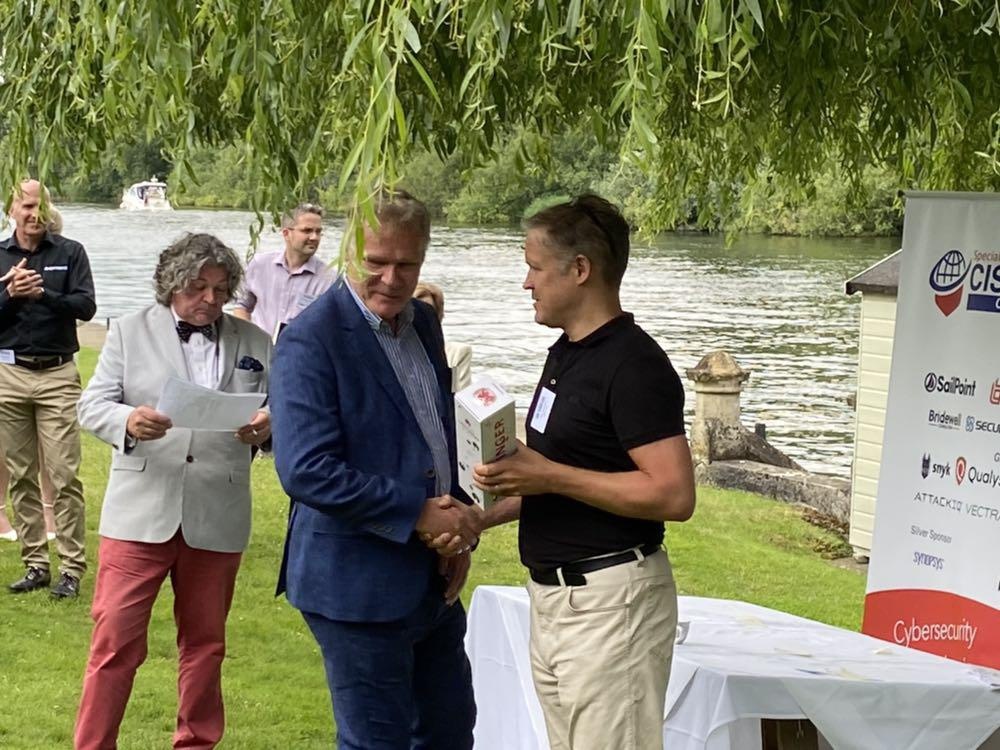
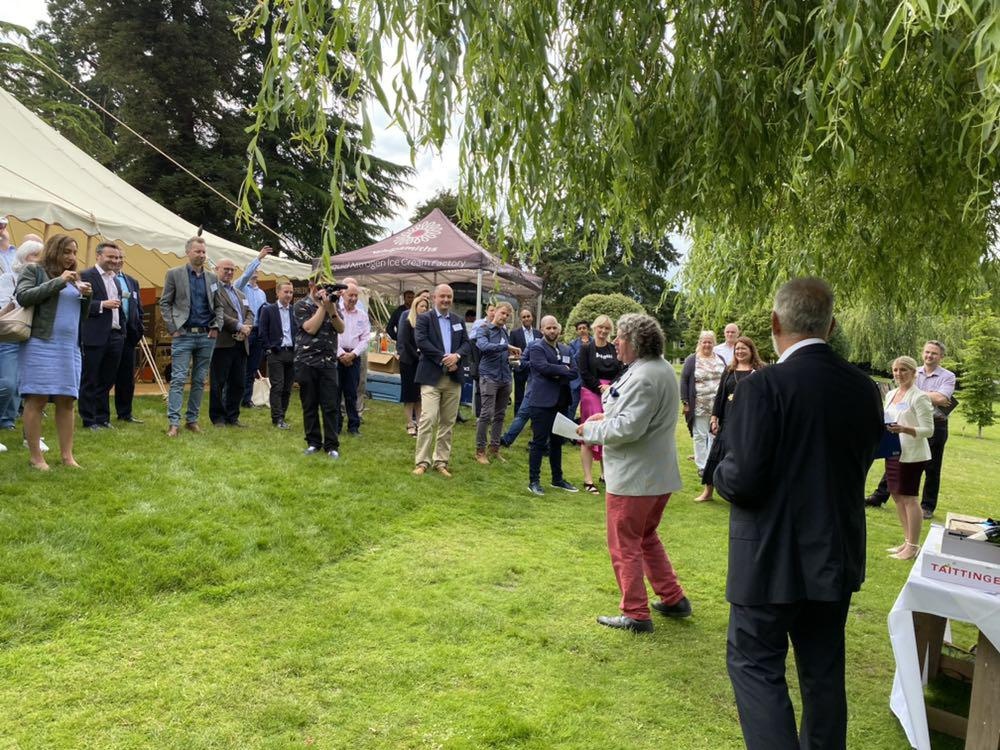
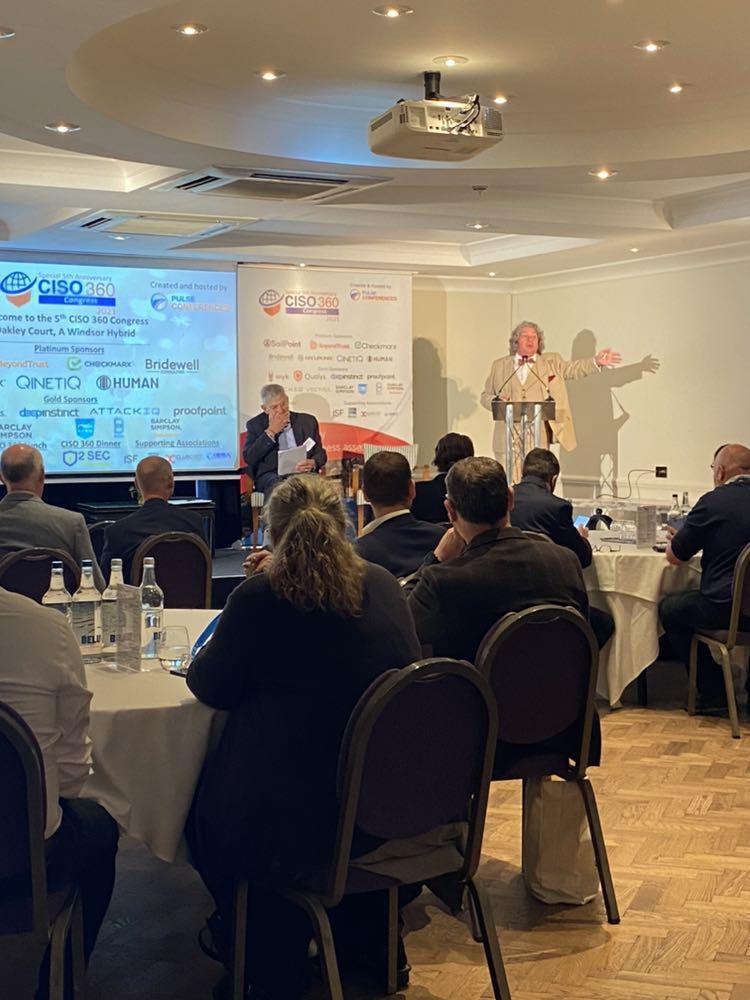
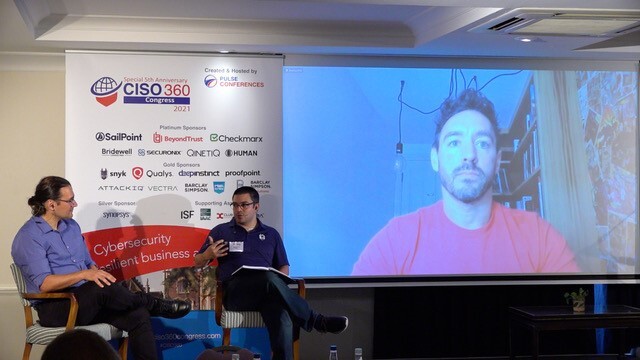
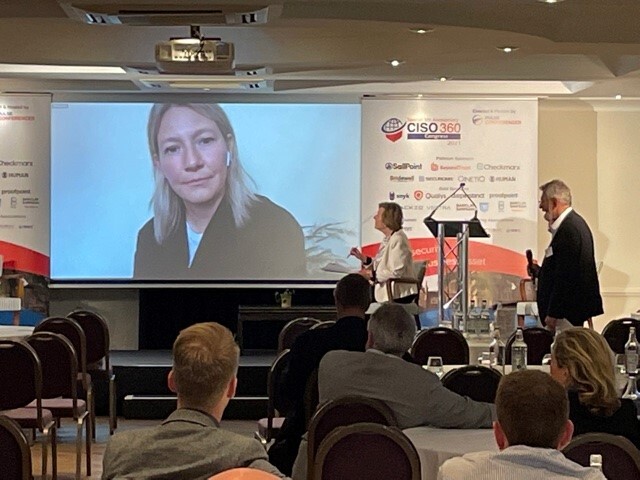
 Recording, Photos, Videos - 5th CISO 360 Congress - July 2021 


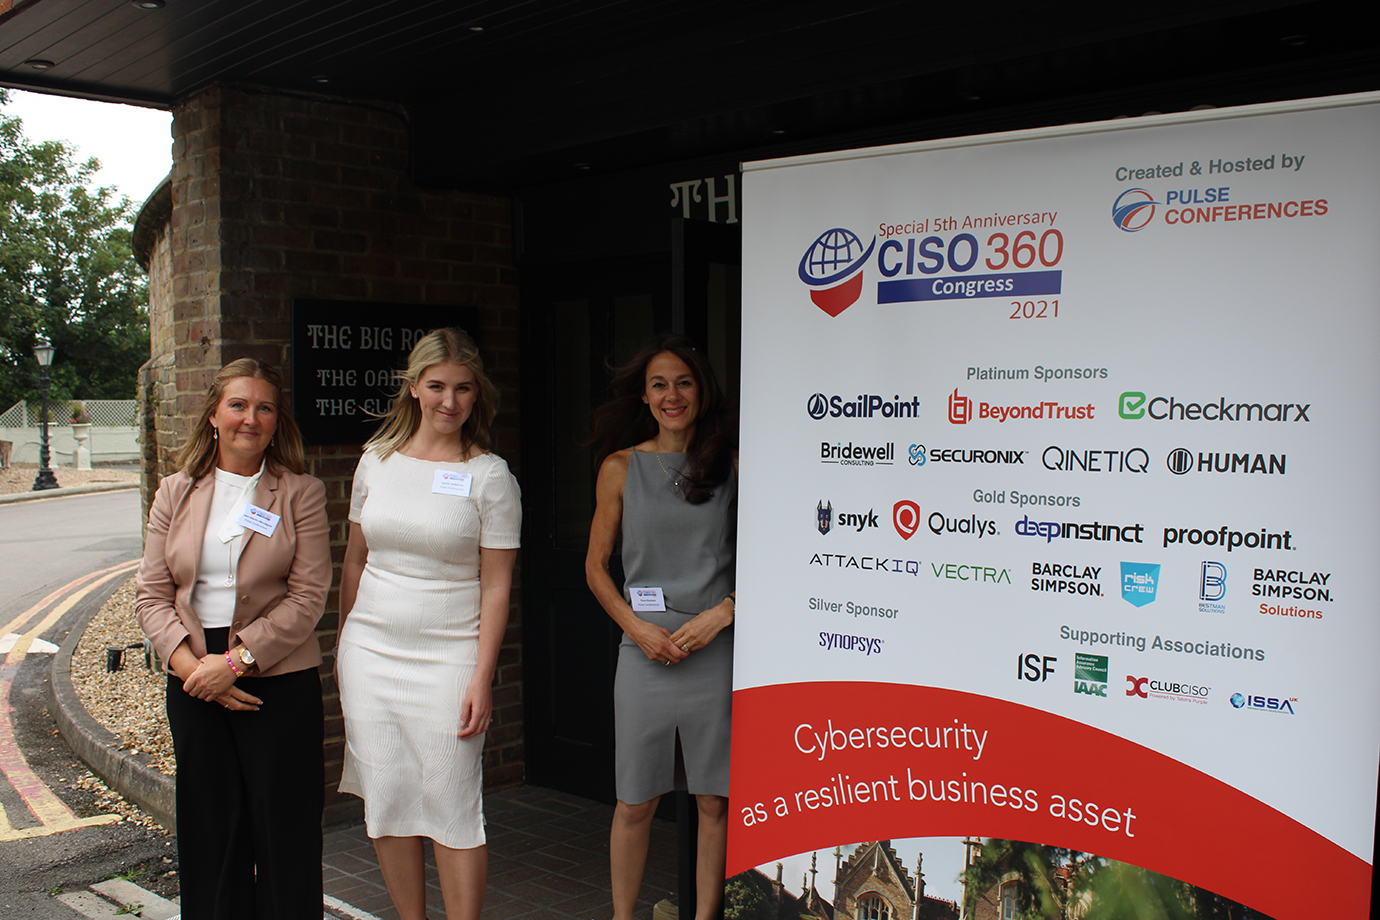
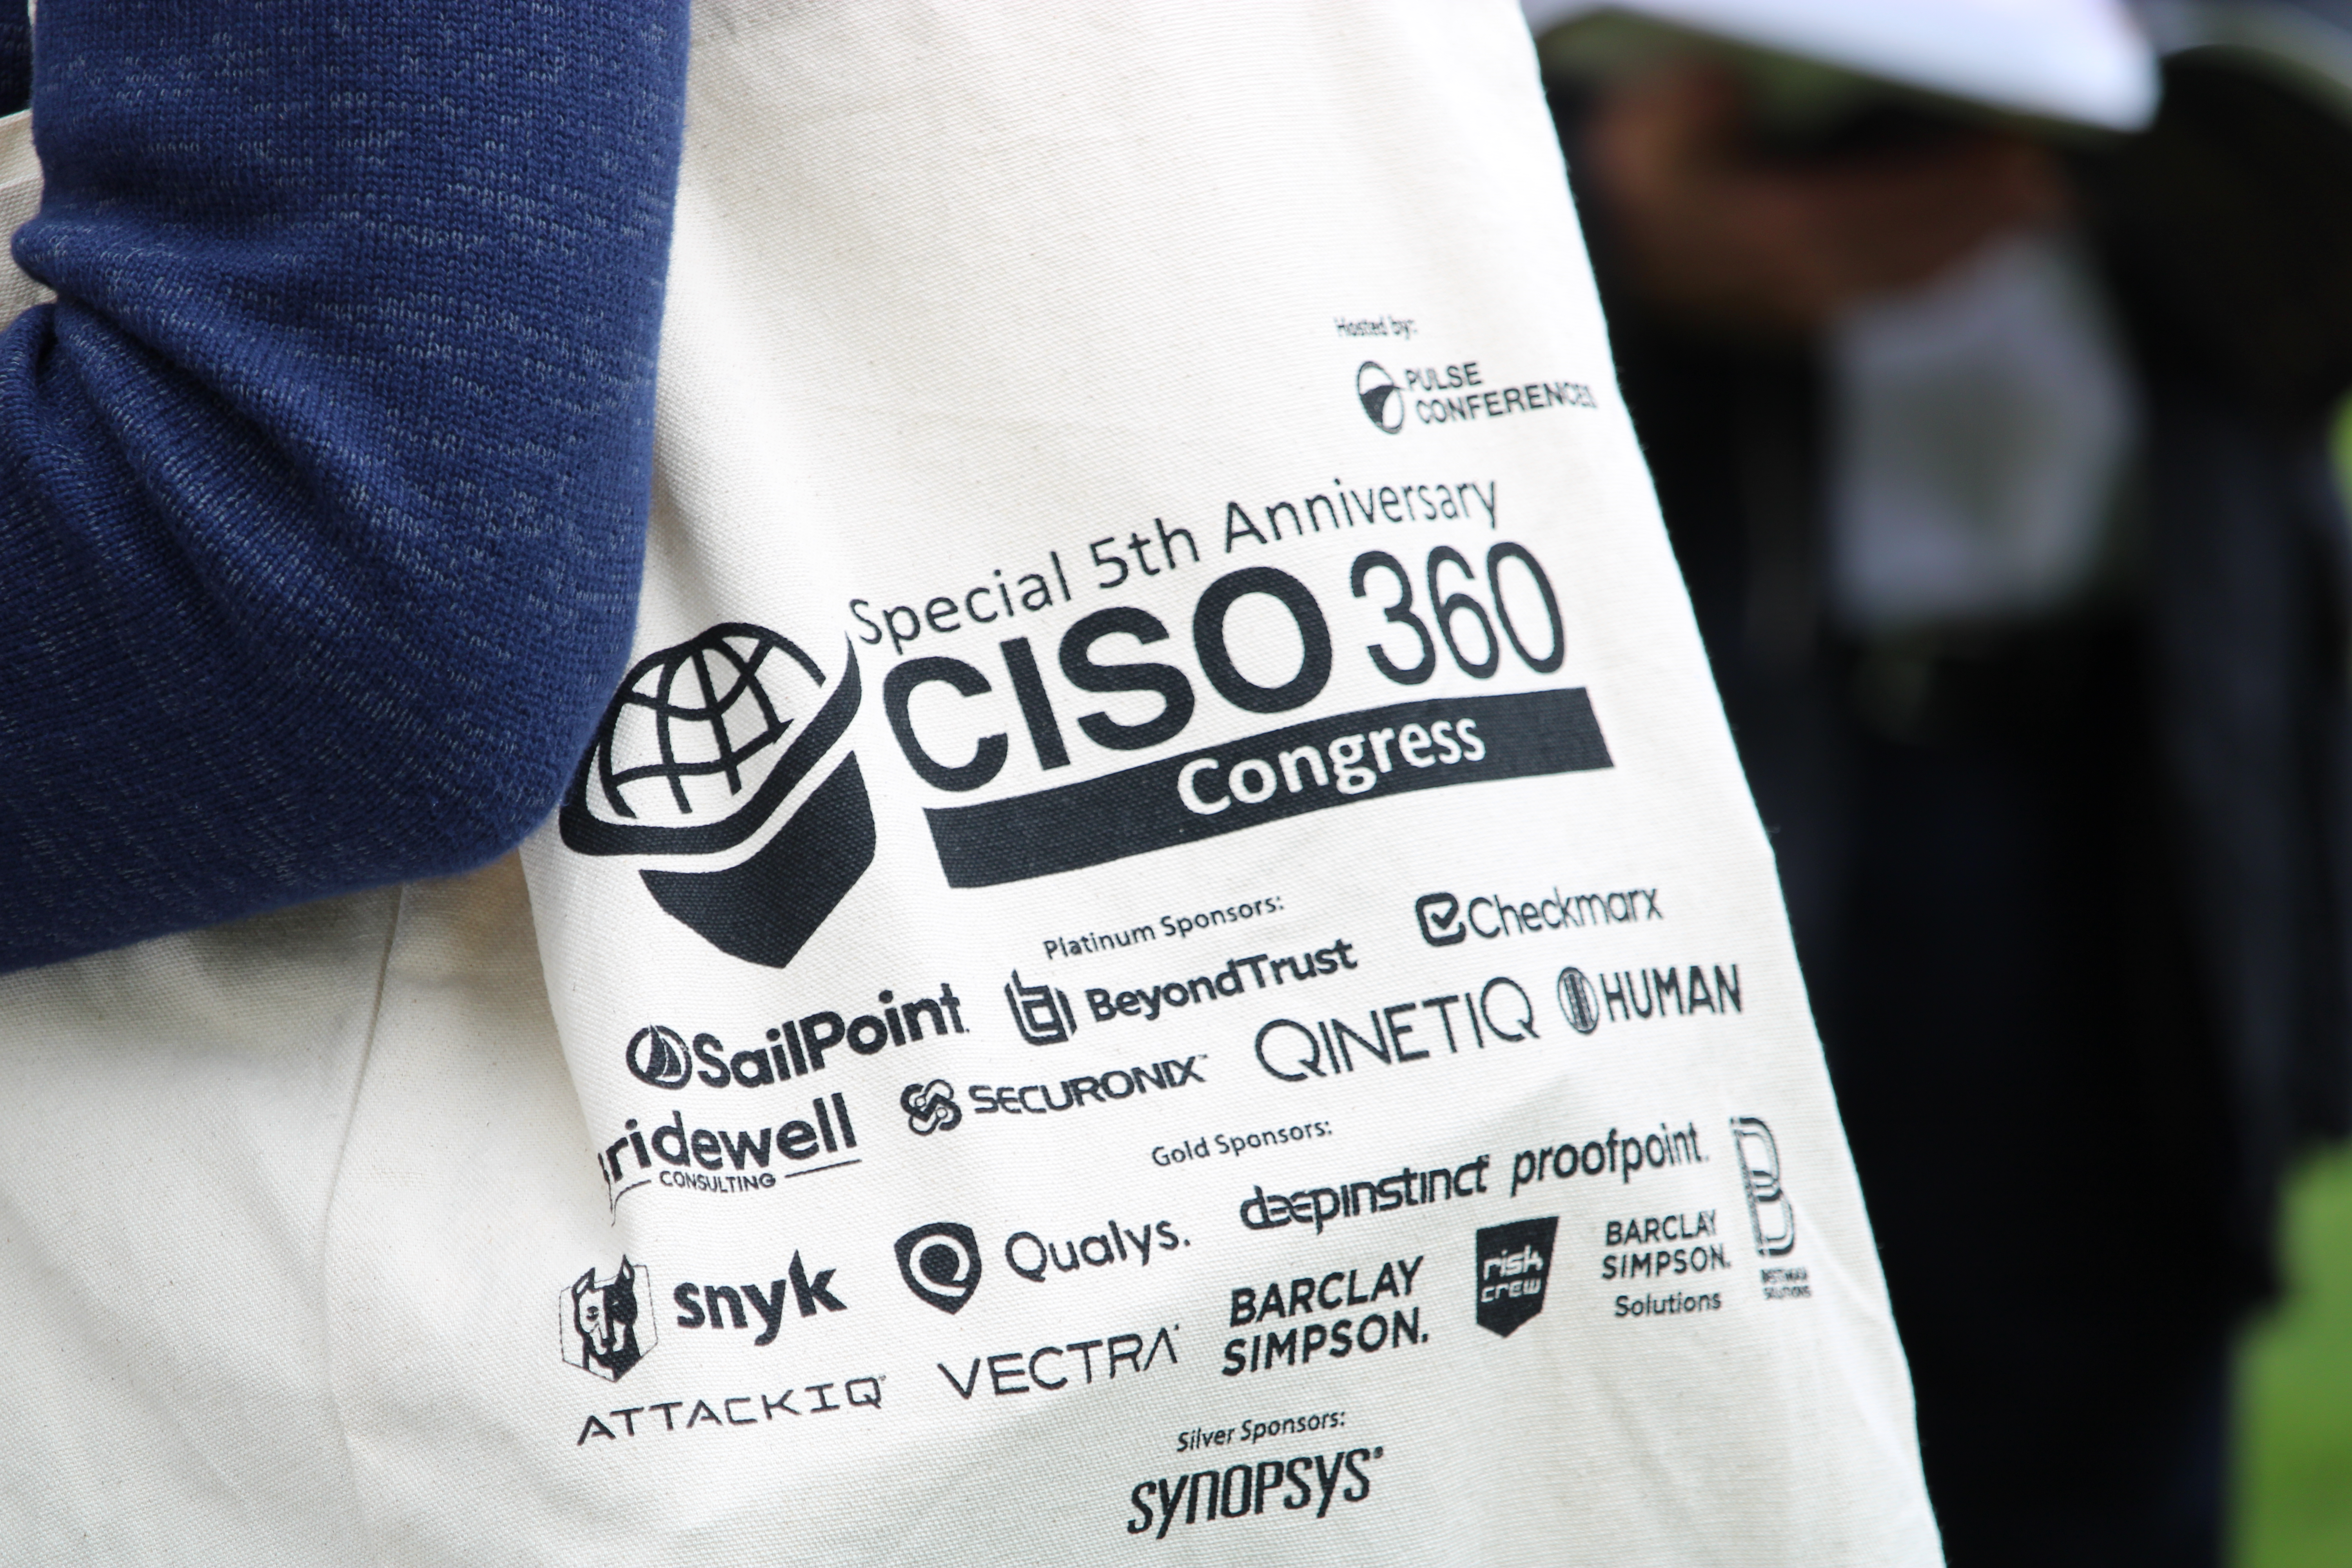
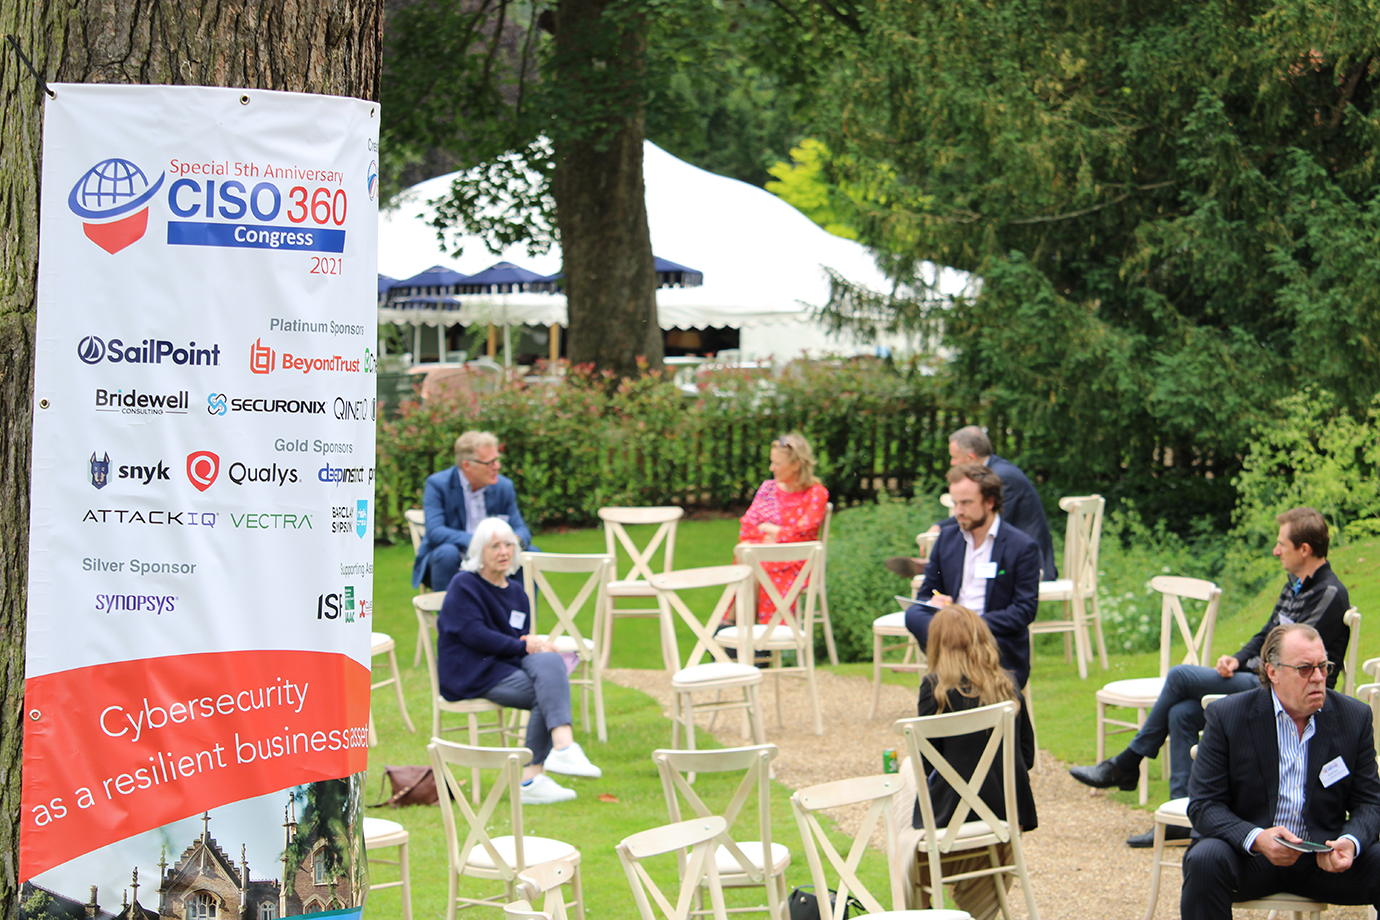
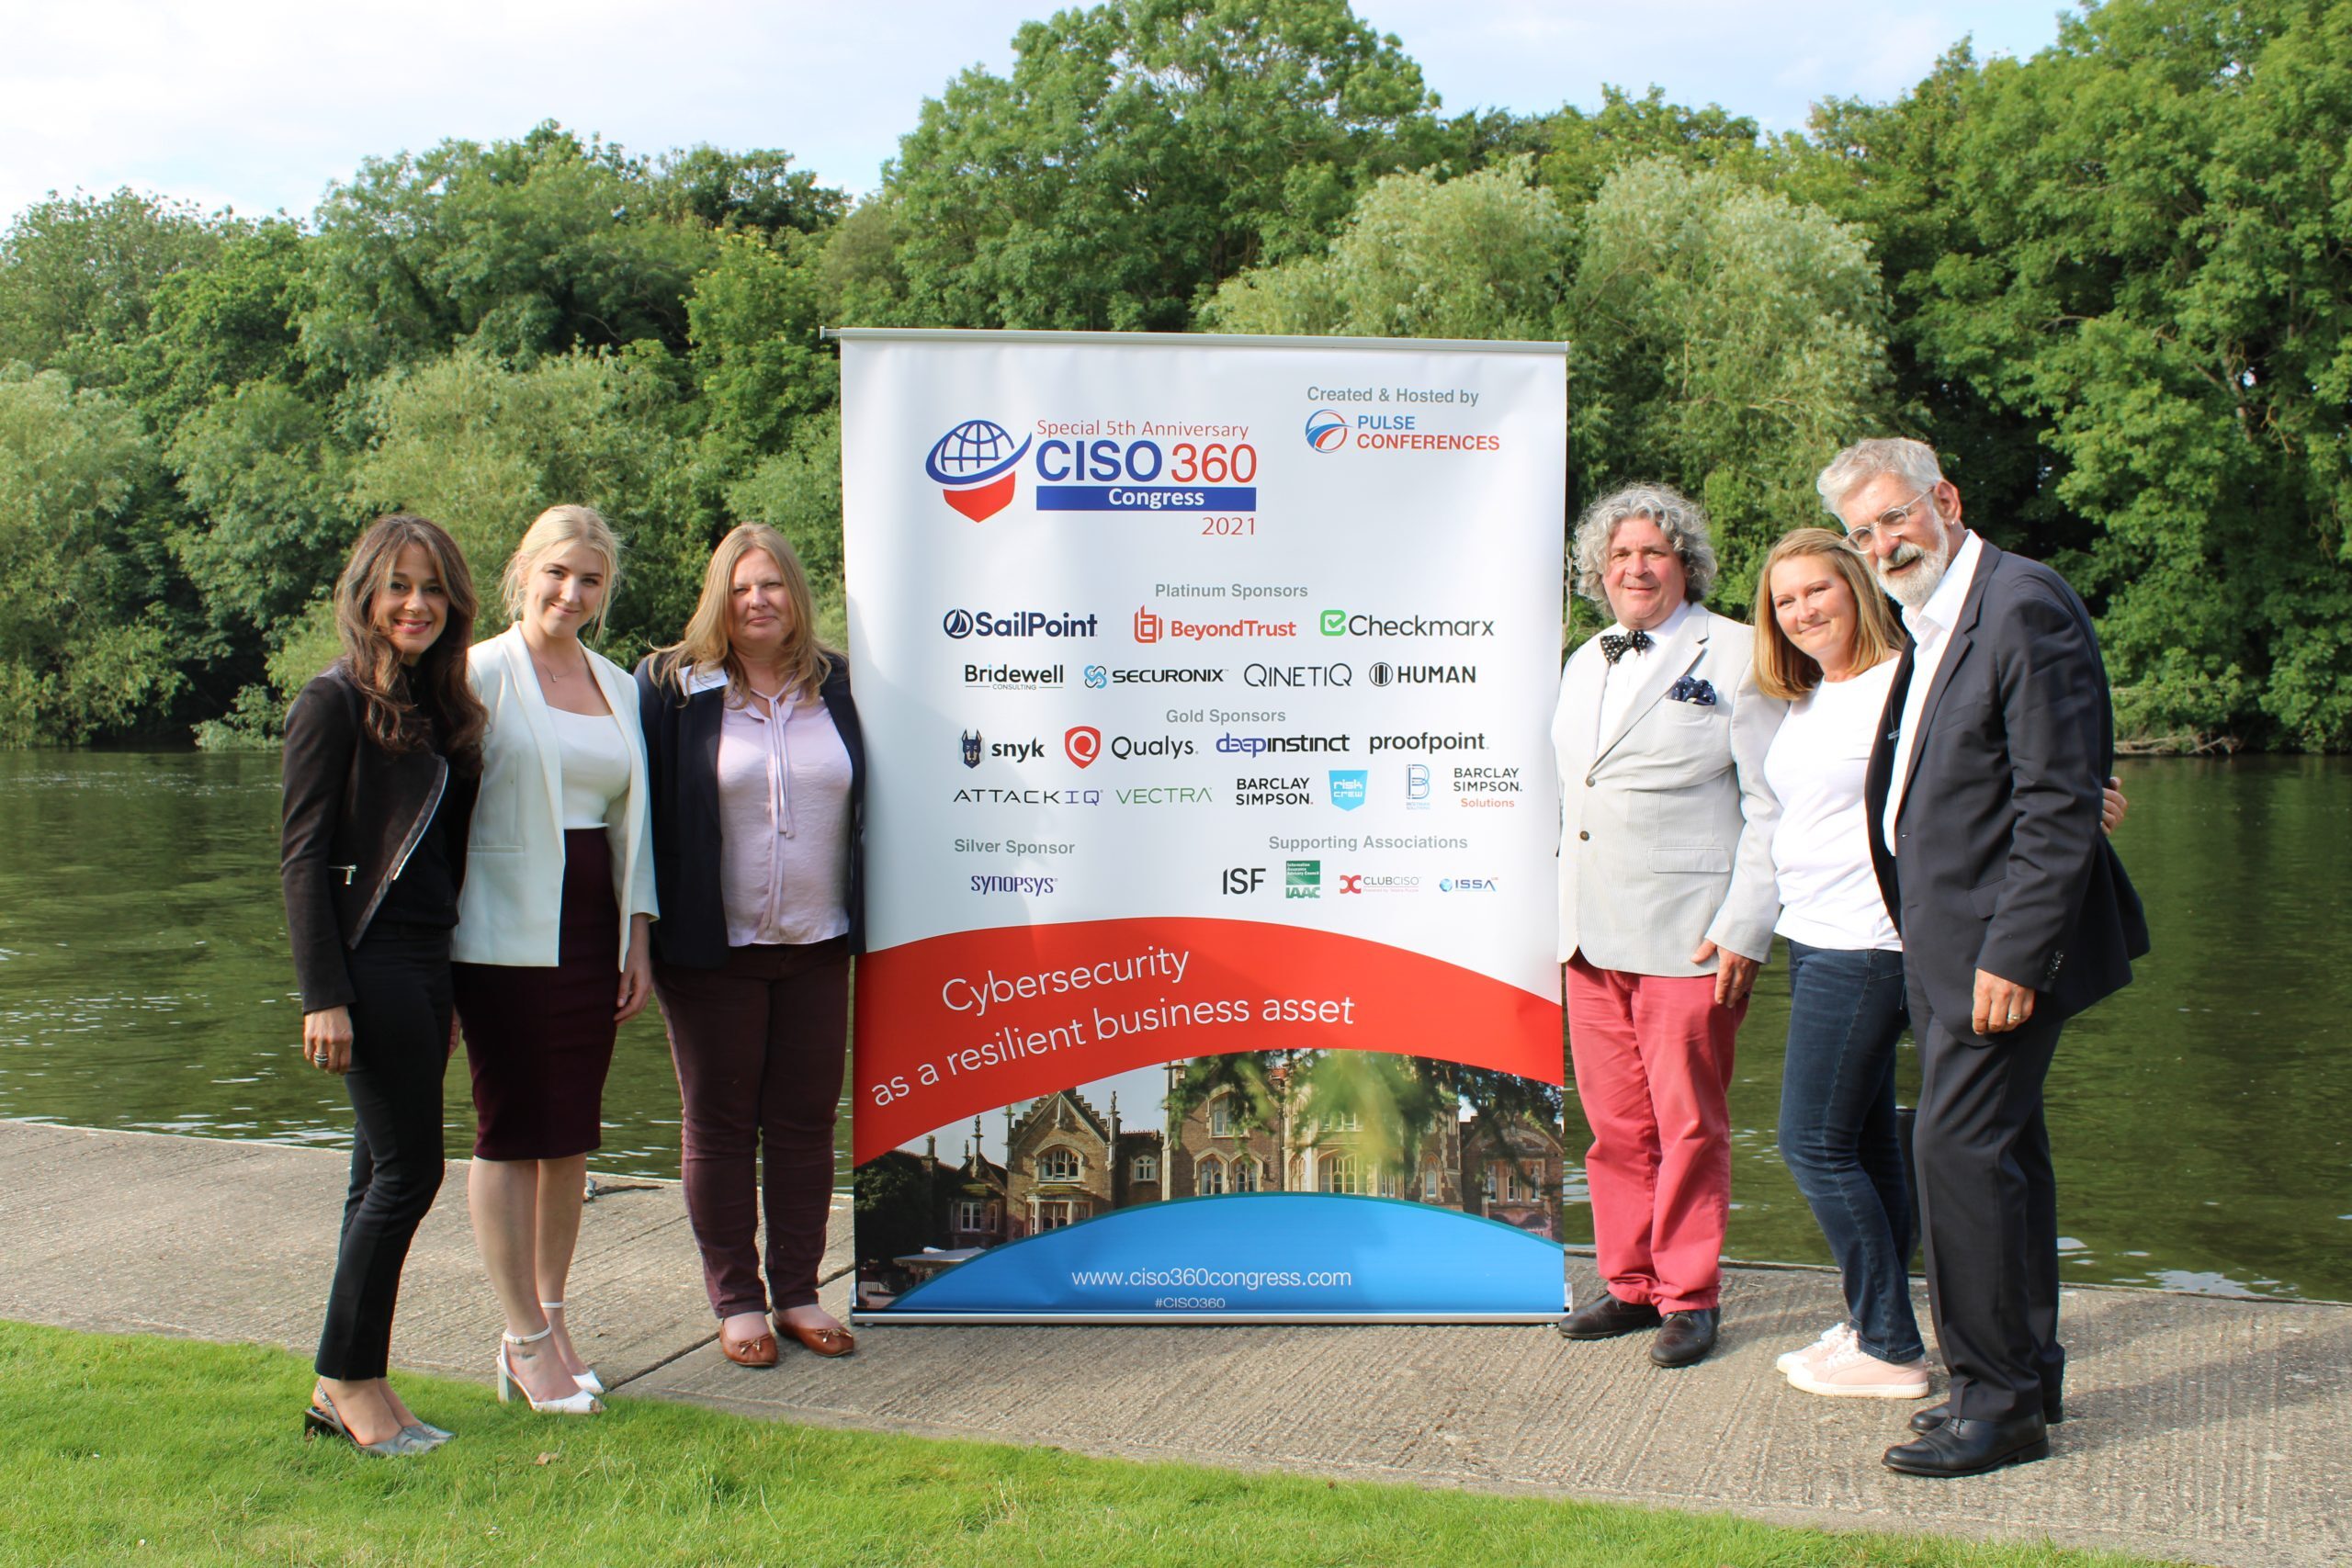
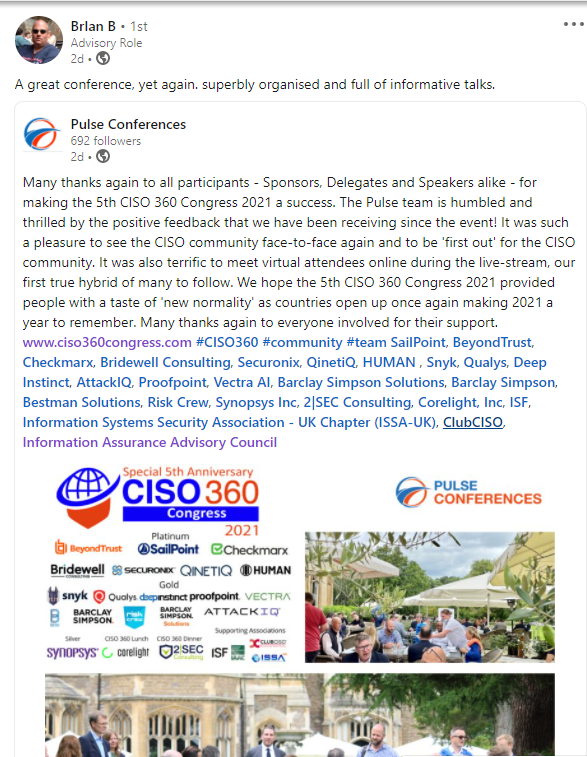
Many thanks to our 2021 Sponsors for enabling CISO to CISO sharing and thought leadership!

Platinum Sponsors

Gold Sponsors

Silver Sponsor

Lunch Sponsor

Dinner Sponsor

Supporting Associations

Virtual Platform – CISO 360 Reunion 14 September.

The CISO 360 Reunion will be hosted on the interactive all-in-one platform, Airmeet!

Airmeet is the fastest growing platform for hosting a rich variety of virtual events, offering a streamlined and intuitive software for real connections. In AirMeet you will be able to interact via the feed or private chat, vote on polls or ask questions directly to the presenter as well as participate in topic roundtables of 8 and network in the 3-min speed- networking sessions. You will get access to the platform 24 h before the event so that you can start networking with fellow participants and have time to look around and get familiar with the areas that we are using.

Live connections at CISO 360 Reunion!

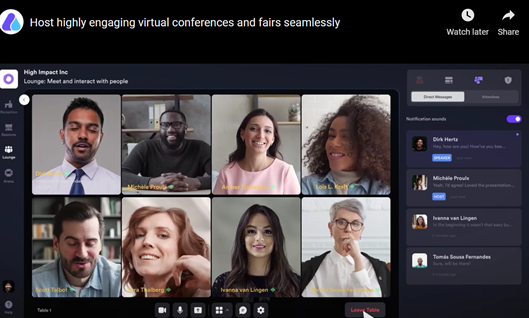
  • The Social lounge provides various networking tables to allow the attendees and speakers of the event to connect with each other when the event is not live (pre-event, post-event and break time). Serendipitous and free flow video encounters with CISO peers on virtual tables and networking lounges, backstage, stage, claps and audience reactions.
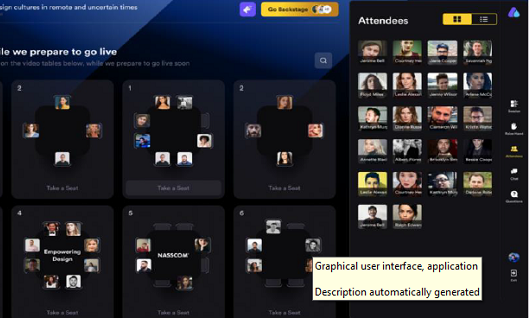
  • Take your seat at ‘tables of 8’ at the start of the event and video chat to peers at your table before the sessions even start much as you would do in a physical conference. You will be returned to the same table during the short breaks between live stream panel discussions, keynotes and case studies. Or, you can roam and visit other tables!
  • Tables are labelled either Topic Tables; Sponsored Rooms and freestyle Networking Tables to give you an indication of what is being discussed. Otherwise, just pop in and see for yourself, get involved.
  •  You can see who is at each table by hovering above their image square. Once you decide which table you’d like to be seated at, select the “Take a seat” button below the table. If you want to leave the conversation, simply say bye to the table participants, and click on the “Leave the table” button in the bottom right.
  • A countdown will be displayed when there are 15 seconds left for the live stage Sessions to commence. Once the session begins, you will no longer be able to access the Social Lounge until the next break.
  • Speed Video Networking – Get matched randomly to meet and greet peers for a set time of 3 minutes per meeting! Follow up by private message afterwards.

Official Video – 5th CISO 360 Congress 2021


Virtual CISO 360 Reunion
14 September 2021, Air Meet Platform
Reunite with or meet new CISOs, cybersecurity practitioners and luminaries for roundtable discussions and panels.

Attend a regional CISO/ CSO 360 Conference 2021/ 2022

3rd Cyber Exchange 360: Talk to the Board, 10 November 2021, London

3rd CISO 360 Middle East, 15 – 16 November 2021, Dubai

5th CSO 360 Congress, 8- 10 December 2021, Madrid

2nd CISO 360 Asia & Oceania, 2-3 March 2022, Singapore

2nd CISO 360 USA, 31 March 2022, New York

Submit a video for the 5th CISO 360 Congress

We would like to widen the debate and hereby invite you as an attendee or speaker of the 5th CISO 360 Congress to submit a short video that will be shared on social media and on the Pulse Conferences website. You can share what sessions you are looking forward to taking part in and challenges you hope to discuss at the CISO 360 Congress or an introduction of what you will presenting at the congress if you are a speaker.

You are invited to send us a video (about 60 seconds!) on an area of cybersecurity of your choice. Be sure to start by telling us a little bit about who you are and why you are interested in your chosen topic.

A Few Tips

Upload a video you record from your phone or computer. Try to find a quiet, well-lit spot and consider what is visible in the background, especially if you are recording at home. Check your sound. It may also help to write your thoughts down before pushing the record button but there is no need to be too scripted. You know what you think! Enjoy the experience. Speak clearly and remember to open with a little bit about who you are and why you are interested in your chosen question.

Speakers – 5th CISO 360 Congress – Windsor/ Hybrid 2021

Chaired by

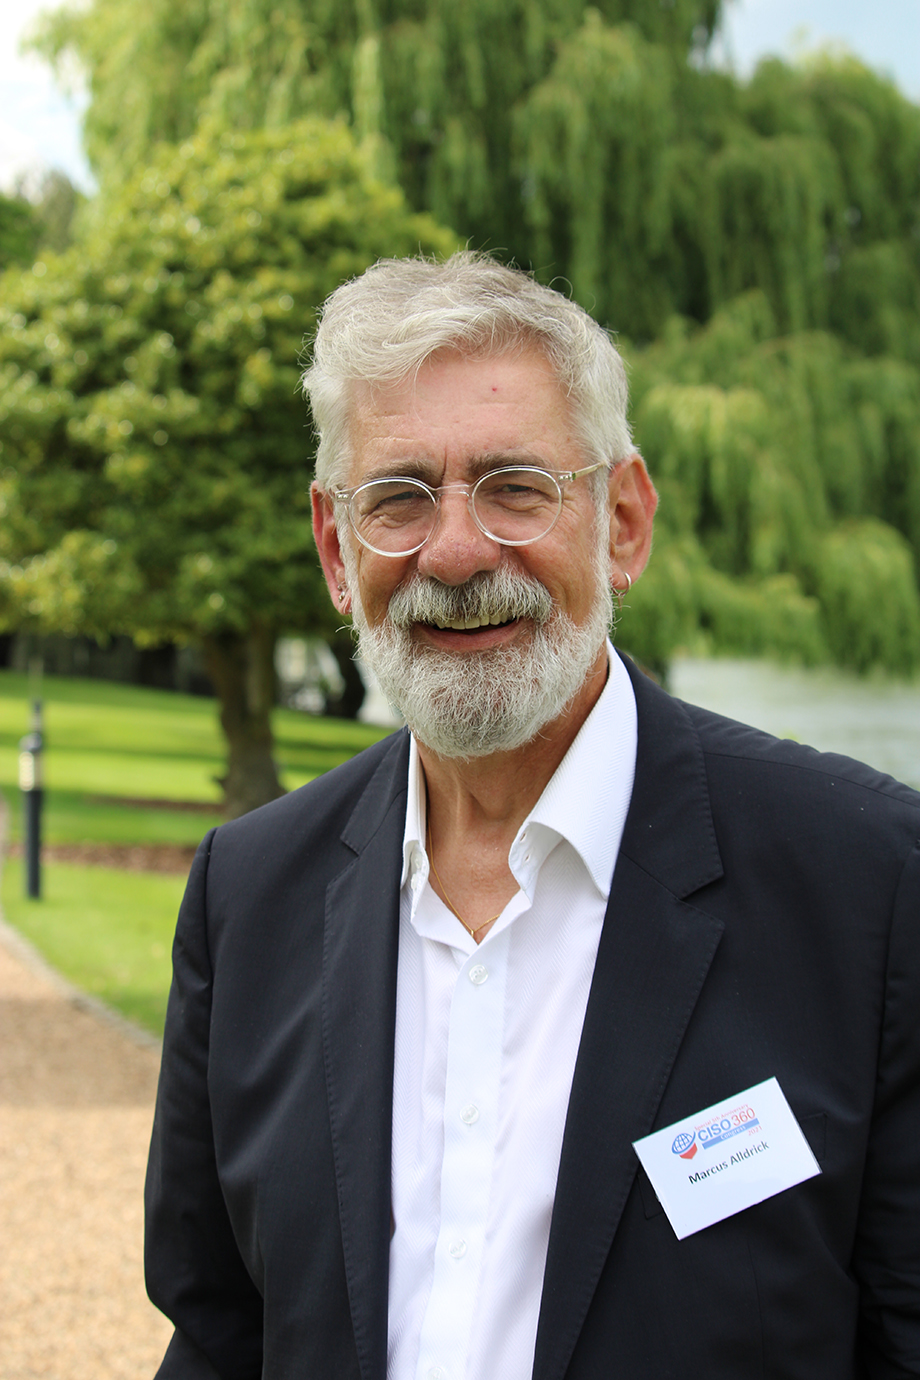
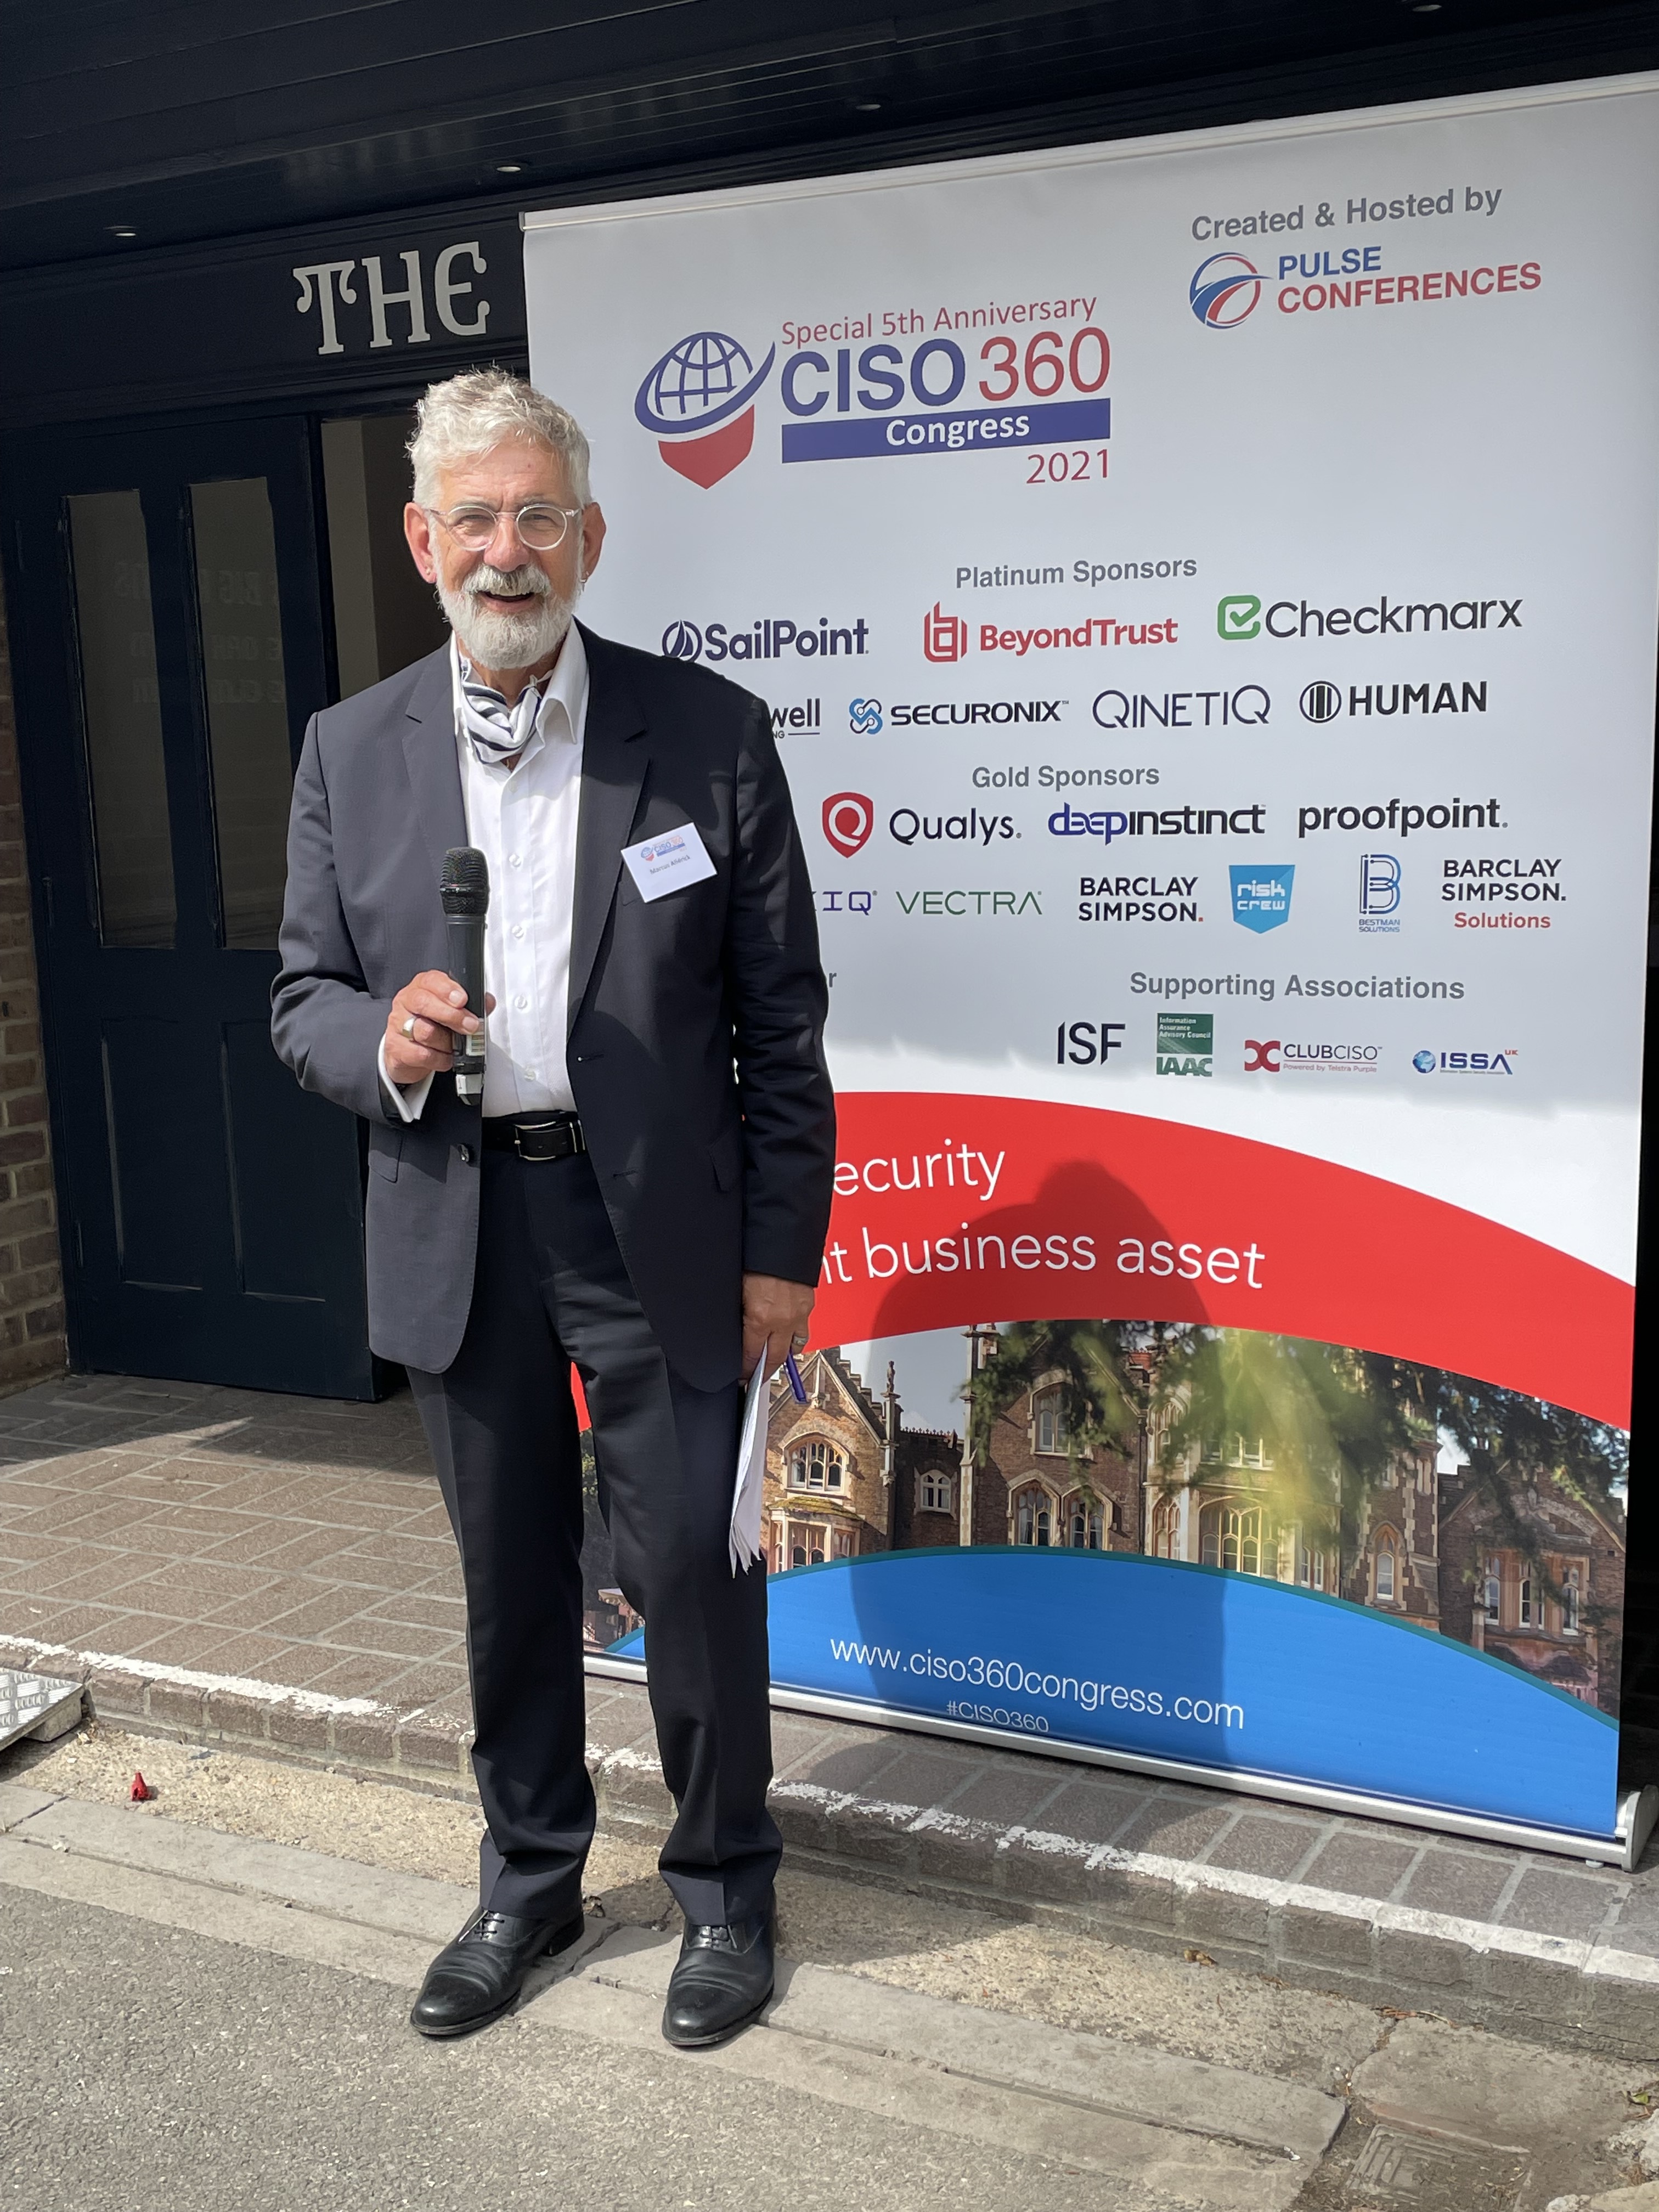
Marcus Alldrick, CISO Luminary
Digital Risk Management, Security and Compliance Advisor
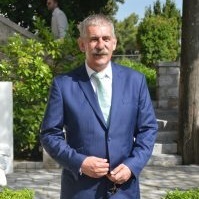
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services and sits on the Cymmetria Advisory Board as Chief Risk Officer.

Keynote

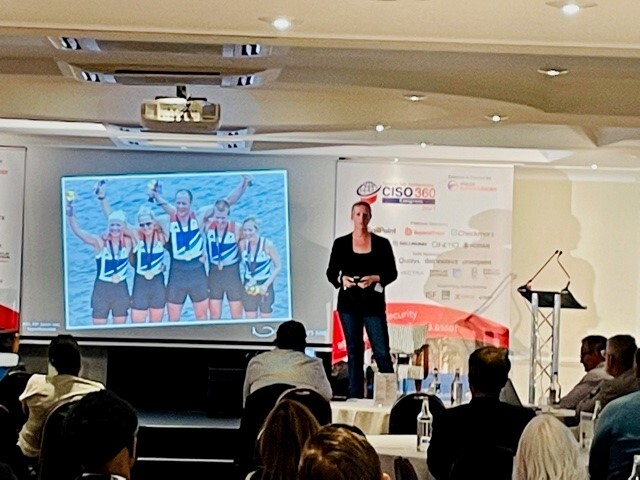
Naomi Riches MBE
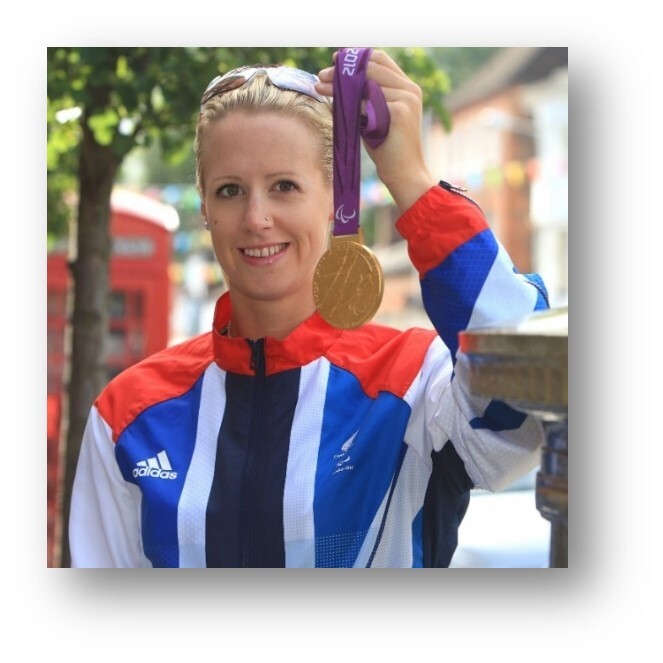
In 2012, Naomi Riches achieved what most athletes only dream of; winning a Gold medal on home water at the London Paralympic Games.

At just 8 weeks old Naomi was diagnosed with Achromatopsia along with a cocktail of other eye conditions; this means that she has no colour vision and is extremely sensitive to light.

During her years in mainstream school she was severely bullied, and her differing needs were not well catered-for. All this led to Naomi under-achieving in many areas and left her with a deficit in self-confidence.

It was during Naomi’s second year of University that she was offered the chance to try out for the Great Britain Adaptive Rowing Team. She seized this opportunity and just 4 months later became a World Champion in Great Britain’s Mixed, Coxed Four. Over the next 10 years ParaRowing developed into a full-time, Lottery-Funded Paralympic Sport, making its debut at the 2008 Paralympic Games in Beijing. Naomi was, in the words of her coach ‘key in the development of Para-Rowing over those 10 years’, winning 6 World Championship titles, Paralympic Bronze in Beijing and Gold in London.

Naomi’s journey was by no means easy, but she was always driven by a burning desire to prove a point; to prove that she is capable of significant achievements despite her visual impairment.

In 2016, Naomi decided to test her resilience a little further. As an athlete she had always completed in crew boats and wanted to take on a greater challenge on her own. Her goal was to row the length of the Navigable Thames in a single scull in an attempt to establish a new Guinness World Record. Naomi covered the 165 miles from Lechlade to Gravesend non-stop, in 47hours 59minutes and 54 seconds and set the Guinness World Record for the first and fastest woman to row the Navigable Thames.

Naomi retired from full time sport in 2013 and began her next chapter in business working for Thomas International. The driving force behind all she does is to empower and enable individuals, teams and organisations to realise their potential and be the best that they can be.

International speaking panel includes:

Speakers

If you would be interested in getting involved as a Speaker, please let us know. We would also very much value your input into companies, topics or specific persons you may like to see present at the event this year.

  • keynote insights
  • innovative best practice corporate case studies
  • strong panel leaders and contributors
  • interviewers and interviewees

The focus is on:

  • actionable takeaways
  • inspiration from the world’s smartest thinkers and doers

Please email sara.hook@pulseconferences.com .

Many thanks
Andy Jones

Andy Jones

Distinguished Analyst, Information Security Forum

Andy is currently responsible for research topics associated with industrial controls systems, including the internet of things. As an experienced practitioner, he has previously held CISO positions for Maersk Line, Unilever and Sainsbury’s, as well as information security positions in British Airways. In previous roles with the ISF, Andy authored many of the ISF thought leadership reports, including the Threat Horizon series, and specialised in legal and regulatory issues. Andy is also a practitioner advisor to the Research Institute in Science of Cyber Security – an academic research institute co-ordinated by University College London. He has previously been a founder member of the Consumer Goods Security Forum, the Thames Valley Chapter of the ISC2 and an advisor to Danish Shipping. Andy is an experienced speaker, having presented at business and industry events across the globe. He holds a degree in Physics and Masters in Business Administration, and is a certified security professional.

Andrew Rose

Andrew Rose

Resident CISO, EMEA, Proofpoint

Andrew is the Resident CISO at Proofpoint, which he joined in 2021 from Mastercard, where he was the Chief Security Officer of their subsidiary firm, Vocalink, a firm which provides the transactional backbone of the financial services industry in the UK.

Prior to that Andrew held the CISO role at the UK’s Air Traffic Control provider, NATS, where he oversaw a security transformation and contributed to the design of the next generation air traffic control system.  Andrew has also held CISO roles at two top tier global law firms, Allen & Overy  LLP and Clifford Chance LLP. In between these roles, Andrew was a Principal Analyst at Forrester Research where he covered the role of the CISO and Security Culture & Awareness as two of his speciality areas.

Andrew was recognized as “European CISO of the year” (2018), and has previously won awards for devising and leading the “Best security awareness program” (2015).

Andrew holds a Master’s degree in information security, is a regular speaker at global security conferences and has contributed to media outlets such as the Wall Street Journal, the Financial Times, the Washington Post, Wired magazine and the Times newspaper.  Andrew also appeared in the CNBC documentary entitled “Rise of the Machines”.

Andrew Rose

Andrew Rose

Resident CISO, EMEA, Proofpoint

With a career spanning over 20 years, Adrian has worked across many sectors from defence to entertainment as a cybersecurity, supply chain and programme/operations management expert. Currently the IAAC (Information Assurance Advisory Council) CEO and a principal consultant, he has significant senior commercial and strategic experience gained: by leading the EMEA region for a global cybersecurity membership organisation; leading and creating multi-disciplinary sales, technology and consulting teams; and managing a consulting business delivering cybersecurity projects to blue-chip organisations globally.

He is an acknowledged leader in information security, a published author and a writer of international information security standards. He holds a BSC(Hons) and PhD from the University of London, a Durham University MBA; the CISSP; an FBCS CITP; and a Visiting Professorship at the University of Sunderland within the Faculty of Computer Science.

Becky Pinkard

Becky Pinkard

Head of Global Cyber Defence, Vodafone

Appointed to the ‘100 Global CISOs for 2020’ list and awarded ‘CISO of the Year, 2020’ by SC Awards Europe, Becky Pinkard is a renowned practitioner and commentator on the information security sector who has been working in information technology and security since 1996. A security transformation expert, Becky’s background and experience to date has provided her with broad information security expertise, coupled with in-depth, technical capabilities around cyber security operations including data monitoring, vulnerability and risk assessment, web application security and policy development. Becky is an active advocate for promoting diversity and inclusion in business and is a co-founder of the ‘We Empower Diversity in Start-ups’ (WEDS) group. She has been a CyLon mentor since 2017, providing cyber security, operations and client success guidance to entrepreneurs. She also co-hosts a monthly podcast, Cyber Warrior Princess, focused on current cyber security related commentary. Becky was a SANS Certified Instructor for over a decade and served as a GIAC Certified Intrusion Analyst advisory board member and on the Strategic Advisory Council for the Center of Internet Security. She co-authored “Nmap in the Enterprise” and “Intrusion Prevention and Active Response, Deploying Network and Host IPS”. Becky has shared her expertise in numerous publications, both written and in live interviews all over the world, including: The Wall Street Journal, Forbes, ChannelPost, The Telegraph, The New York Times, BBC News, Channel 4 News, and more.

Brian Brackenborough

Brian Brackenborough

CISO, Channel 4

Brian began working in the Broadcasting arena in 1999. In 2008 he moved into Information Security working for the much loved Julia Harris. He left the BBC in 2011 to head up the Information Security department at Channel 4. Brian’s best known for his pragmatism, honesty, terrible jokes, rugged good looks, and being a backing dancer for WHAM in the 80’s. He tends to make things up in Speaker Bio’s

Barry Coatesworth

Advisor, Scottish Power Renewables

Carole Embling

Carole Embling

Information Security Manager - Awareness and Training, Financial Institution

Caroline Lawson

Caroline Lawson

CTO and Identity Strategist, SailPoint

Caroline is an experienced Identity Strategist and Sales Engineering Leader with many years consulting and delivery involvement, focusing on large scale Security and IGA platforms within the financial sector.  She sat in the position of the customer for many years leading programmes of work, as well as in leadership positions across the Security Vendor landscape. She graduated from the University of Southampton with a degree in Modern languages, speaking fluent German, Swedish and Dutch and is based in Oxfordshire.

Carolyn Brown

Carolyn Brown

Chief Information Officer, British Medical Association (BMA)

Carolyn is Chief Information Officer at the British Medical Association, the BMA’s mission is to look after doctors so that they can look after you. The CIO is accountable for the development and delivery of the IT Strategy and capabilities which support the BMA Group in the fulfilment of its mission. Prior to this role, Carolyn was CTO of the National Housing Federation from 2017 – 2020, where she worked with business functions to enable digitisation of services for its wide stakeholder communities. Carolyn was Global IT Director at Permira, responsible for global IT strategy, operations and security.

Cedrick Moriggi

Global Head of Security and Business Resilience, LafargeHolcim

Colette Hanley

Colette Hanley

Group Head of Privacy, Nokia

Colette leads security and privacy governance, management and compliance effectively in complex multinational environments. Holding leadership roles in Nokia, Microsoft, global banking, tech start-ups and the gaming industry, she remains responsive to changing corporate priorities and committed to strategic and meaningful improvement. Commercially orientated, she articulates the business value of security and privacy at all levels of an organisation devising pragmatic and creative solutions for complex problems and evolving compliance requirements. Colette ensures security and privacy are embedded in activities, operations, products and services from design to delivery. Her goal is to achieve comprehensive reduction of risk for the business and for the customer while providing confidence that all data-driven innovation is ethical.

David Tyce

Programme Director, Barclay Simpson Solutions

David Tyce is a highly experienced, Programme Director with a proven track record in understanding, prioritising and managing and directing complex, multi-stakeholder projects and programmes. Considerable expertise in the highly efficient and effective delivery of a broad range of initiatives including the management of technology delivery, stakeholder relations, contractual negotiation, organisational change management and communications strategies. Most recently developing and delivering key technology programmes within the financial services sector. An extremely effective leader and team motivator with excellent communication skills developed through a wealth of managerial experience gained across a wide range of challenging environments.

David has spent the past 5 years as a Senior Programme Manager within the Financial Services sector and more recently as the Programme Director for Barclay Simpson Solutions. He has led teams responsible for developing and delivering a range of key technology transformation programmes and the delivery of a Cyber Recovery Vault solution for two major high street banks.

This work was focussed on Business Service recovery in the aftermath of a cyber event or other data/business service denial occurrence. These hugely complex and technologically demanding programmes were designed to deliver significant risk reduction and survivability for the banks in the event of a major Cyber-attack or other data denial occurrence. The work also included detailed cyber threat analysis, service and technology vulnerability assessments, technical architecture design and capability operationalisation within existing and future resilience strategies. Both of these programmes required very strong leadership, resource and stakeholder management skills; both internally and externally.

David has previously led and delivered a range of key technology programmes including the Remediation of Unstructured Information Assets (RUIA) as part of the broader Security of Secret and Confidential Data (SSCD) programme at Barclays Bank; a major, Group wide undertaking. His team delivered the Bolden James and Azure Information Protection (AIP) Information Labelling Tools to over 120k colleagues across the enterprise. He also led the programme charged with the encryption of over 150 million Secret information assets ‘discovered’ through the information asset scanning activity within the remediation programme.

Graham Edwards

Graham Edwards

Head Cyber Security, Yorkshire Water

A successful senior Chief Information Security Officer and Operational Risk Director with a proven track record in multi-cultural and multi-national organisations. Able to bridge technical and business disciplines and communicate at all levels. Extensive knowledge of Information Security, Cyber Security, Physical Security, BCDR, Operational Risk, Crisis Management, Data Protection, Financial Crime and Compliance. The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He then held the position of Director of Data Security at Nationwide Building Society before taking the role as Head of Information Security at Camelot Lottery Solutions. Graham is currently Interim Head of Cyber Security at Yorkshire Water. He has a master’s degree in Information Security from Royal Holloway.

Dinis Cruz

Dinis Cruz

CISO and CTO, Glasswall Solutions

Dinis Cruz is a CISO and Transformation Agent, focused on creating teams and environments where security is an enabler and accelerator for the business, while securing and protecting the digital assets from existing threats. Dinis was nominated for CISO of the Year 2019 at #CyberSecurityAwards. Dinis is also writing a book called Generation Z Developers (but useful for all Generations) available from Amazon: https://www.amazon.co.uk/Gen-Developers-concepts-generation-developers/dp/1724194607

Gabe Barrett

Gabe Barrett

CEO and Founder, Otter Intelligence

Gabe Barrett is the CEO and founder of Otter Intelligence, a workplace consultancy focused on helping leaders build high trust, high performance teams in the context of hybrid working. 

Irish by birth, American by education and a Londoner by choice, Gabe has built distributed teams across the world in a broad variety of workplaces. 

A passionate advocate for diversity, inclusion, equity and belonging, Gabe believes the future of work is up for design so we should make it a good one. 

Greg Kelton

Greg Kelton

Checkmarx

Greg Kelton is responsible for driving success within key accounts in Northern Europe at Checkmarx. Greg advises Checkmarx customers and prospects on best practices for securing code early in the SDLC and ways to bring Security and Developer teams together. Previously, Greg held leadership positions growing several software firms in Europe including Managing Director of Palamida Europe – Open Source Security and MD of Optimost at Autonomy. Greg earned his Bachelor of Science degree in Computer Science from Northeastern University and his MBA in finance and marketing from Georgetown University.

Karl Lankford

Karl Lankford

Regional Vice President, Solutions Engineering, BeyondTrust

Karl is the Director, Solutions Engineering, for BeyondTrust, where he has worked for 6 years. A highly capable security leader, Karl has acquired a wide range of security experience and knowledge over the last decade, working across multiple industries. Karl is a regular speaker at industry conferences, delivering disruptive technical and strategic thought-leadership insight to the international cybersecurity community.

Helen Rabe

Helen Rabe

Global CSO, Abcam

An internationally experienced Information Security professional who specialises in complex strategic deliveries with a strong emphasis on security service management delivery across a broad range of industry and technology sectors., Helen’s wide range of key skills include providing consultative services to core stakeholders, up to and including Partner, C-Suite and Board level. Helen is currently the Global CSO of Abcam. Prior to this she was CISO at CBRE and before this she held the position of Head of Information Security at Costa Coffee.

Jonathan Armstrong

Jonathan Armstrong

CEO and Partner, Cordery

Jonathan is an experienced lawyer with a concentration on technology and compliance. His practice includes advising multinational companies on matters involving risk, compliance and technology across Europe. He has handled legal matters in more than 60 countries involving emerging technology, corporate governance, ethics code implementation, reputation, internal investigations, marketing, branding and global privacy policies. Jonathan has counselled a range of clients on breach prevention, mitigation and response. He has also been particularly active in advising multi-national corporations on their response to the UK Bribery Act 2010 and its inter-relationship with the U.S. Foreign Corrupt Practices Act (FCPA). Jonathan is one of three co-authors of the LexisNexis definitive work on technology law, “Managing Risk: Technology & Communications”. He is a frequent broadcaster for the BBC and other channels and appeared on BBC News 24 as the studio guest on the Walport Review.

Mark Snel

Mark Snel

CISO - Information Security and Corporate Security, Signify (The Netherlands)

Mark has more than 20 years of experience in the information security and information risk management, from technical roles to his recent role as a CISO for Signify (formerly Philips Lighting). He holds a Master of Information Management degree, believe in a business-driven approach to managing information risk, and is always willing to experiment with new ideas to improve our profession.

Marilise de Villiers Basson

Marilise de Villiers Basson

Founder and CEO, ROAR!

I am the founder and CEO OF ROAR! Coaching and Consulting. I am a Mindset and Performance Coach, Best-selling Author, TEDx Speak and Executive specialising in Cyber Security Awareness, Culture and Talent. A few years ago, I had a successful corporate career, as an executive in a Big Four consulting firm. However, my success came at an enormous price. I was on the brink of a nervous breakdown – mentally and physically exhausted. My relationships with the people closest to me were suffering.

I walked away – one of the most difficult things I have ever done – and along the way, learned a critical lesson: it is possible to have a fulfilling, balanced life without sacrificing success. In the process, I created the ROAR! Blueprint, designed to live your best life: on PURPOSE, in your POWER, and with the COURAGE to speak your truth. ROAR is also a four-step process for having courageous conversations – with yourself and others. It stands for Recognise, Observe, Assert, Redirect.

Martyn Booth

Martyn Booth

CISO, Euromoney Institutional Investor PLC (UK)

Martyn is an experienced information security leader and CISO, working at board level to define information security strategy and then manage teams to implement that strategy. Martyn works with clients in a flexible and proactive way to meet stringent security requirements and adaptive needs, enabling businesses to work in a flexible way by reactively designing security processes and technical controls that support the business rather than inhibit it. Specialties: Risk, Compliance, Governance, Awareness, Security Architecture, application architecture, ISO 27001, PCI DSS, policy and information security strategy.

Naina Bhattacharya

Naina Bhattacharya

Chief Information Security Officer (CISO), Danone

Naina Bhattacharya is the Chief Information Security Officer at Danone. She is passionate about diversity and inclusion, with a keen interest in increasing the participation of women in cybersecurity. Naina lives in London and, once Covid lockdown lifts, she is looking forward to croissants and coffee in Paris.

Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.

Paul Baird

Paul Baird

Chief Technology Security Officer, Qualys UK

Paul moved from Scotland to London in the late 90’s to start his first IT job as a systems administrator for Elonex PLC, at the time one of the biggest UK P.C. manufacturers. Being exposed to multiple vendor operating systems and enterprise applications early on in his career gave him the opportunity to learn a broad range of skills in a short period of time which in turn allowed him to shape his career.

Paul has always worked within an I.T. function, having the opportunity to wear many hats has helped him progress into the highest levels of System Engineering / Architecture. Wanting to make the move into cyber he seized the opportunity when it came about and has never looked back. After building a security ethos in a UK FTSE 250 from the ground up he took on the challenge of building a new SOC function within Jaguar Land Rover before his final move to Qualys.

Joining Qualys in February of 2021 as the UK and North EMEA Chief Technical Security Officer Paul is helping to drive Qualys’ vision at C-Level across the customer and partner base. Supporting the Qualys sales teams with his knowledge and experience of delivering cyber security operations to enterprise customers at a global scale. Paul will be representing Qualys at forums and conferences to help support the wider cyber security community.

Paul mantra is “Perfection is not a destination; it is a never-ending journey”

Quentyn Taylor

Quentyn Taylor

Director of Information Security EMEA, Canon Europe

Using the power of stories and his own experience of testing products to destruction; Quentyn has embraced building business relationships across the world whilst driving Canon’s strategy and educating business customers to minimise their security risk. Before joining Canon, Quentyn has worked in a variety of industries such as Internet service providers as well as startup businesses.

Dr. Robert Coles

Dr. Robert Coles

Director, Cumberland House Consulting Ltd, Honorary Professor, UCL and Visiting Professor, Royal Holloway, University of London

Dr. Robert Coles is the Director of Cumberland House Consulting Ltd, specialising in cyber security strategy, programme delivery and Non-Exec and Board Advisory roles. He is also an Honorary Professor at UCL and Visiting Professor at Royal Holloway, University of London. He holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Chair of the Crossword Cybersecurity PLC advisory board, member of the advisory boards for Think Cyber Ltd, UK bank, a US pharmaceutical and the Government of Singapore Ministry of Health and member of the Tech-Nation Cybersecurity judging panel. Robert has over 30 years of cybersecurity experience and has held a number of Chief Information Security Officer positions, including for the NHS and health and care system, GSK, National Grid and Merrill Lynch.  In all these roles, he owned the information security risk and was responsible for providing leadership across the organisations. He was accountable to the Executive and their Boards for establishing information security strategy and direction, building information security teams and delivering the information security change programme. Prior to these CISO roles, he held a number of “head of” roles at Royal Bank of Scotland, and was the first lead partner, and set up, KPMG’s Information Security Services for EMEA. Robert has extensive links with major industry information security networking groups and government security agencies.  He also has links with a number of universities and participates in leading edge research, particularly with Royal Holloway where he is an Executive Sponsor for the Institute of Information Security Innovation, and Cranfield University where he is an executive sponsor for the Cyber Masters Programme. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics.

Oliver Rochford

Oliver Rochford

Security Evangelist, Securonix

Oliver has worked in cybersecurity as a penetration tester, consultant, researcher, and industry analyst for over 20 years. Interviewed, cited, and quoted by media, think tanks, and academia, he has written for Securityweek, CSO Online, and Dark Reading. While working at Gartner, he co-named the Security Orchestration, Automation and Response (SOAR) market, and worked on the SIEM Magic Quadrant.  At Securonix, he works with our users on security operations and threat management topics.

Peter Craig

Peter Craig

Director of Product Marketing - Cybersecurity, HUMAN

Peter is Director of Product Marketing – Cybersecurity at Human. He has worked in cyber security for more than 20 years mainly in product marketing but also in sales engineering and enablement. Peter enjoys helping organisations find the right security product for their business.

Raphael Borrel

Raphael Borrel

CRO, XL Catlin -AXA XL

Raphael Borrel is the CRO of XL Catlin services, an insurance intermediary part of AXA XL. He is also in charge of Information Risk Management at AXA XL globally. He previously worked as a Director of Insurance Strategy Perspectives and big 4 consultancy firms, where he provided advisory to senior management of global financial services companies during mergers and acquisitions,  large scale digital transformation programmes and risk and regulatory transformations.

Ray Stanton

Ray Stanton

Global Partner, IBM

An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK.  He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.

Richard Hollis

Richard Hollis

Director, Risk Crew

Professional information security governance, risk & compliance consultant with over 30 years of hands on skills & experience in:

• Threat Assessments & Risk Analyses
• Supply Chain Information Risk Management
• Information Security Policies & Procedures
• Security Vulnerability Assessments
• Security Penetration Testing
• Advanced Persistent Threats
• Wi-Fi Security Assessments
• Cloud Security Assessments
• Mobile Device Security
• Insider Threat & Data Leakage
• Security Awareness Training

Scott Nicholson

Scott Nicholson

Co-CEO, Bridewell

Scott has a wealth of experience in information security and as Co-CEO, he is responsible for the strategic direction of Bridewell’s services, driving the business strategy forward, as well as overall service delivery. With extensive experience in delivering large-scale transformational projects in highly regulated environments, Scott plays a pivotal role in Bridewell’s continued growth and success, forming strong relationships with industry bodies including the NCSC. Under Scott’s leadership, Bridewell was one of the first organisations in the UK to gain accreditation on the Civil Aviation Authority’s (CAA) ASSURE scheme and has an industry leading 24×7 Managed Detection and Response service.  Scott has been part of the Bridewell team since 2015 having previously spent ten years working within the police service, as well as several years at IBM and Rackspace. He is passionate about cyber security delivering tangible value to clients, developing others and is also a published author and regular guest speaker for industry events.

Shimon Oren

Shimon Oren

VP Research and Deep Learning, Deep Instinct

Mr Oren is a cyber security expert with experience in research and operations, both offensive and defensive. Prior to joining Deep Instinct in 2016 Oren served for 14 years as an officer in the IDF’s elite cyber unit 8200. Oren’s background includes a wide range of cyber security and research positions, where he managed multifunctional teams of hackers, researchers, and engineers. Oren led the development of new methods and tools for the analysis of cyber-campaigns, as well as a series of innovative cyber intelligence collection capabilities. Over the years of has worked extensively with a variety of industry, defence, and intelligence partners and agencies in North America and Europe. He is a recipient of the President of Israel Award for Outstanding Military Service, holds a B.Sc. (Magna Cum Laude) in Electrical Engineering from Ben Gurion University and MBA (Cum Laude) in Finance and Accounting from Tel Aviv University.

Dr Sally Leivesley

Dr Sally Leivesley

Managing Director, Newrisk Limited, London and Chair Permanent Monitoring Panel for Catastrophic Risk Mitigation, World Federation of Scientists, CERN

Unique global specialist in catastrophic risk across industry sectors and disciplines who advises companies and governments.  In cyber security Sally has provided advice across many areas of industry and exercised catastrophic attacks on systems.  Specialised lectures of cyber security and GDPR and other topics have been provided to the British Computer Society and presentations on catastrophic risk and electronic systems disturbances have been given to the IET.  Conceptual work was done over a decade ago on ‘post encryption’ society looking ahead at the changes in security from quantum research.  Chairs Permanent Monitoring Panel for Mitigation of Catastrophic Risk for the WFS (CERN) and is leading remote multinational science meetings on Covid-19 Mitigation – currently 9 International Sessions on the Novel Coronavirus, April 2020-May 202. The Panel also covers meetings on the Themes of  Engineering for Resilience in Infrastructure; Nuclear Conflict Mitigation Risk Management and Planetary Defence against Near Earth Objects (NEOs). She is a Member of the Information Assurance Advisory Council, IAAC community London and panel adviser on the first British IET and CPNI supported publication for Cyber Security in the Built Environment and is currently serving on the revised publication panel. Communicator since 2001 on many international television news outputs including BBC World Service describing live international and UK incidents and all major forms of threat – cyber, terrorism, aviation, Polonium-210 and Novichok poisonings, Chechen terrorist Beslan child hostages, security issue with Iran, DPRK, USA Presidential security, Covid-19, and unexplained incidents such as MH370 leading to media stories in all countries on novel concept of cyber hijack as new risk in civil aviation.  Early in her career she held appointments from Australian State Government Cabinet Offices to lead two disaster recovery units and to modernise an emergency service. In 2021 she has been recognised in a book’ Man on Fire’, Humphrey Hawksley, for provision of advice on EMP weapons and satellite delivery design. Early training by British Home Office as Scientific Advisor for national survival from nuclear, chemical and biological weapons effects, consultant and (Cold War) appointment for operations in nuclear bunkers.  PhD London University on catastrophic risk across all industry sectors, awarded in field of Economics. Innovator of technological solutions to improvised terrorist devices for chemical and explosives weapon’s effects.  Grandfather in CBRN for the British Register of Security Engineers and Specialists RSES, Member 25 years of the International Association of Bomb Technicians and Investigators (IABTI) and Member of the Royal United Services Institute, Member of the Australian College of Education.

Simon Riggs

Simon Riggs

CISO, Avon International Ltd

Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Prior to his current position, Simon was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.

Teagan Erichsen

Teagan Erichsen

Director, Audere International

Teagan heads Audere’s research team and case manages complex due diligence and investigations assignments.  As Head of Investigations she oversees our open source and human intelligence networks, as well as coordinating pre-transactional due diligence and dispute-related engagements. She has particular expertise in multi-jurisdictional asset tracing investigations in conjunction with the legal counsel of corporates and international law firms. She has worked in business intelligence and investigations for eleven years. Prior to this she was the German business development manager at a UK risk consultancy. She has also worked in research with a global private equity firm. Teagan studied International Relations at the University of St Andrews and holds a Masters in the same subject from the LSE. A dual German-American national, she speaks German and divides her time between our New York and London offices.

Tim Holman

Tim Holman

CEO and Founder, 2-sec and President, ISSA-UK

Tim founded 2|SEC in 2011, with the vision of becoming the UK’s best Cyber Security Resilience partner for Financial Services firms in the City. Since then 2|SEC has grown from strength to strength; and engage in a number of high profile Cyber Security projects, including penetration testing of some of the world’s best known brands. Tim is an avid cyclist and winter sports enthusiast. international board. He is the current President of the ISSA-UK.

Tony Johnson

Tony Johnson

Head of Cyber Security Operations, Manchester Airports Group (MAG)

Experienced Information Technology Services Manager with a demonstrated history of working in the airlines/aviation industry. Skilled in Service Delivery, Technical Support, PHP, Enterprise Architecture, and ITIL. Strong information technology professional graduated from Anglia Ruskin University.

Dr. Victoria Baines

Dr. Victoria Baines

Visiting Research Fellow, Oxford Department of International Development

Victoria Baines is a leading author and speaker in the field of cybersecurity. Her areas of research include electronic surveillance and evidence gathering, the changing face of online identity, and the politics of cybersecurity. She has appeared on the BBC, CNN and other major broadcast media outlets as an authority on the misuse of emerging technologies, including Virtual Reality. She serves on the Advisory Board of the International Association of Internet Hotlines (INHOPE). For several years, Victoria was Facebook’s Trust & Safety Manager for Europe, Middle East and Africa. Her work focused on operational support to law enforcement, and strategic engagement with policy makers on criminal activity online. Before joining Facebook, Victoria led the Strategy & Prevention team at Europol’s European Cybercrime Centre (EC3), where she was responsible for the European Union’s cyber threat analysis. She designed and developed the iOCTA, Europe’s flagship product on cybercrime, and authored 2020, scenarios for the future of cybercrime that were the basis for Trend Micro’s successful short film series of the same name. Earlier in her career Victoria was Principal Analyst for online child protection at the UK Serious Organised Crime Agency (SOCA), and was responsible for the UK’s threat assessment of online child safety issues. She began her career in law enforcement in 2005 as a Higher Intelligence Analyst for Surrey Police. In 2008, the International Association for Law Enforcement Intelligence Analysts recognised Victoria’s work for the public sector with an award for outstanding achievement. Victoria is a graduate of Trinity College, Oxford and holds a doctorate in classical literature. She is a Visiting Associate of the Oxford Internet Institute (Oxford University), and a Visiting Fellow at Bournemouth University School of Computing.

ing. Xander C.W. Heemskerk

Director Product Security – Group Security, Philips

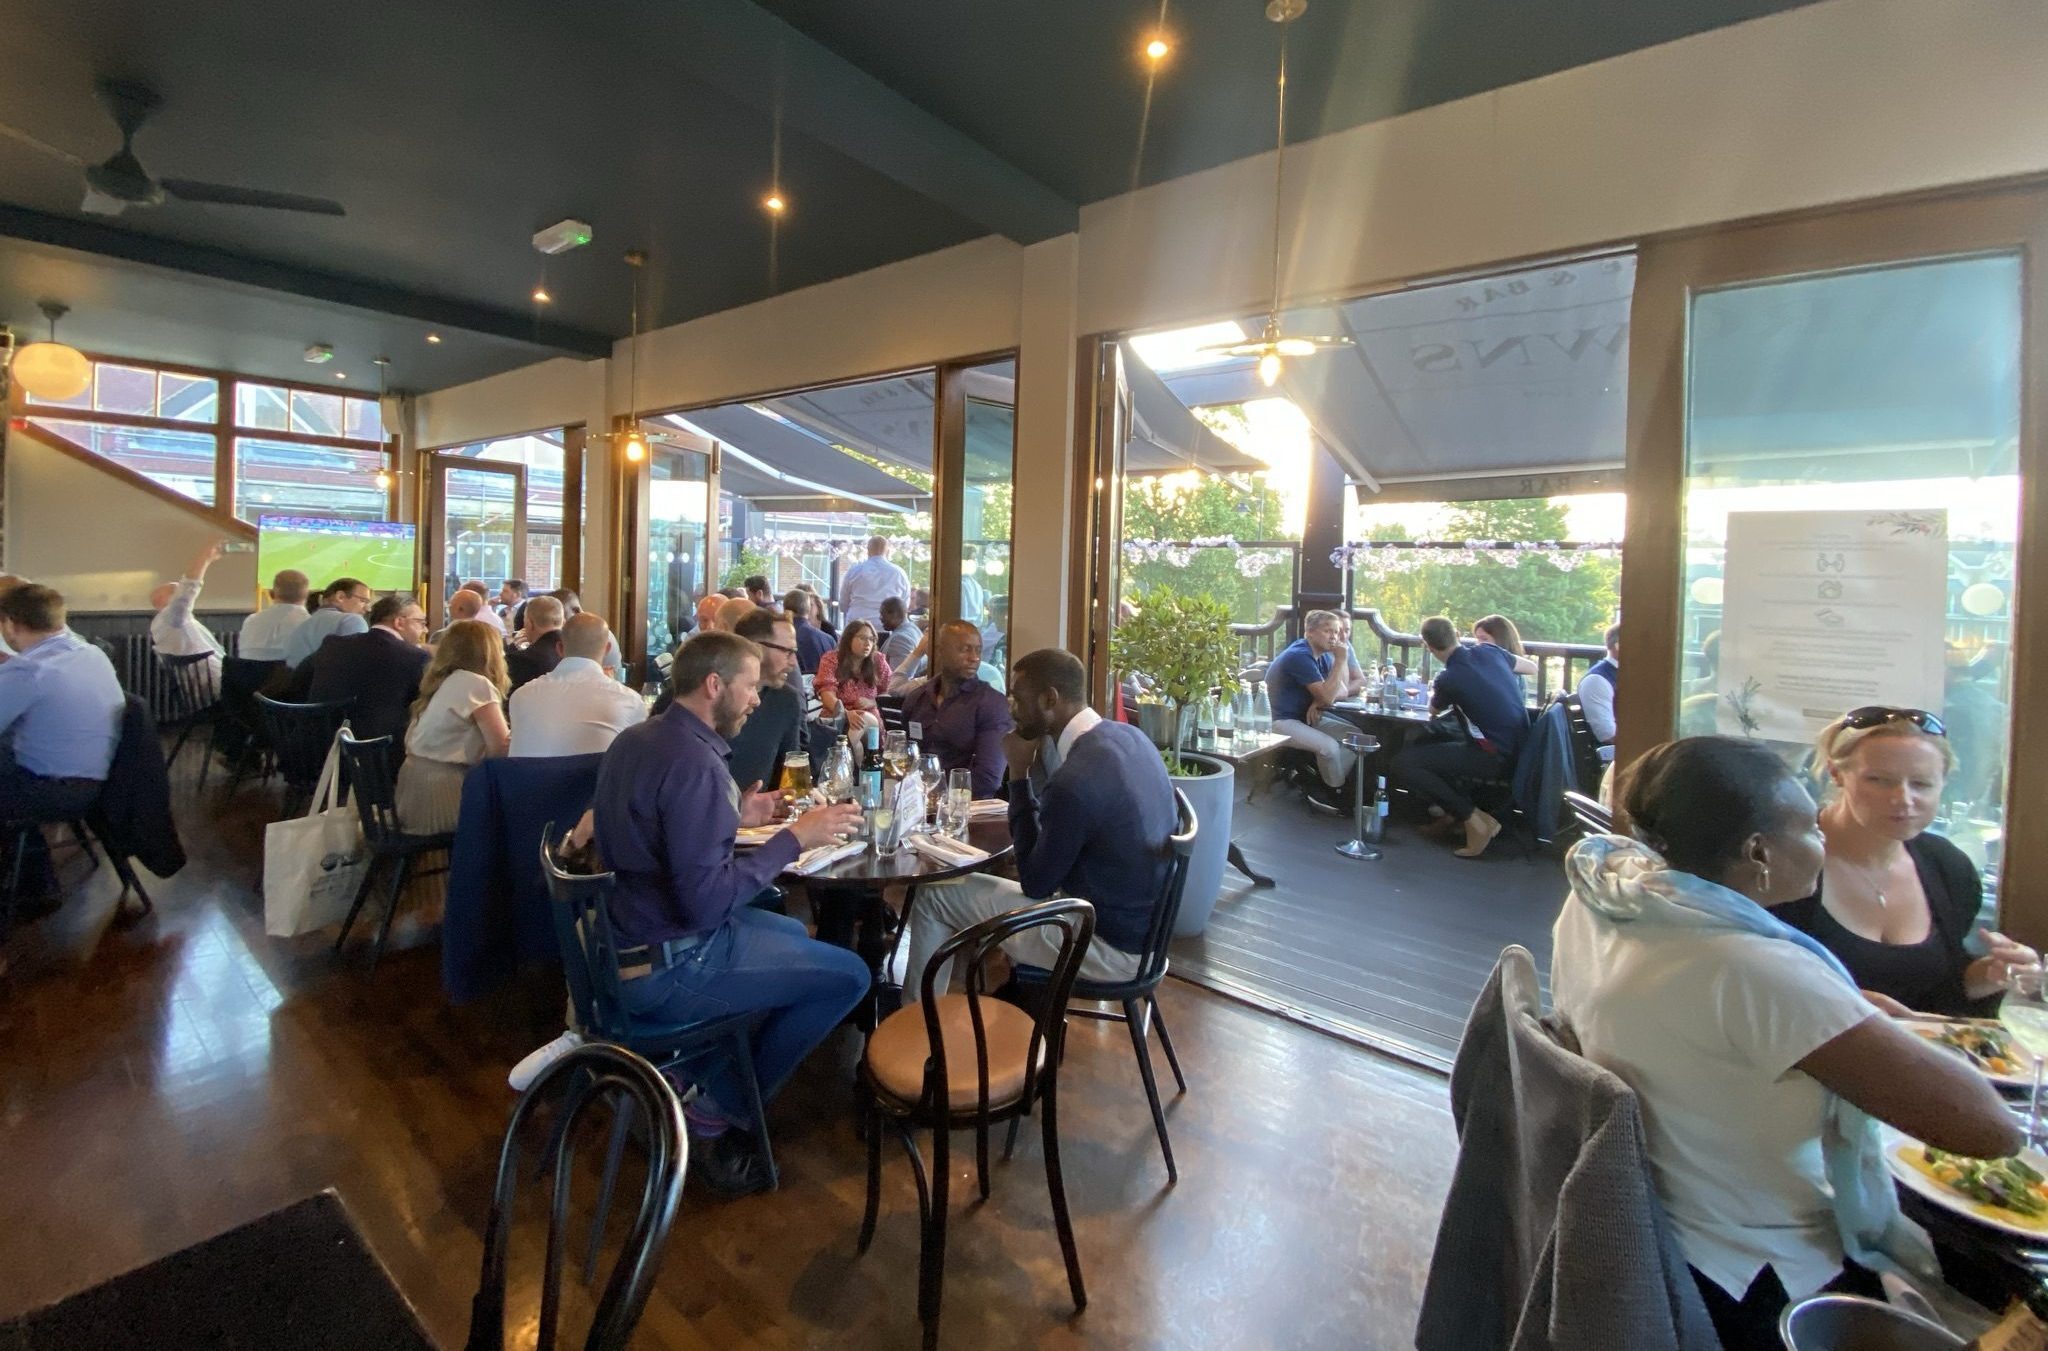
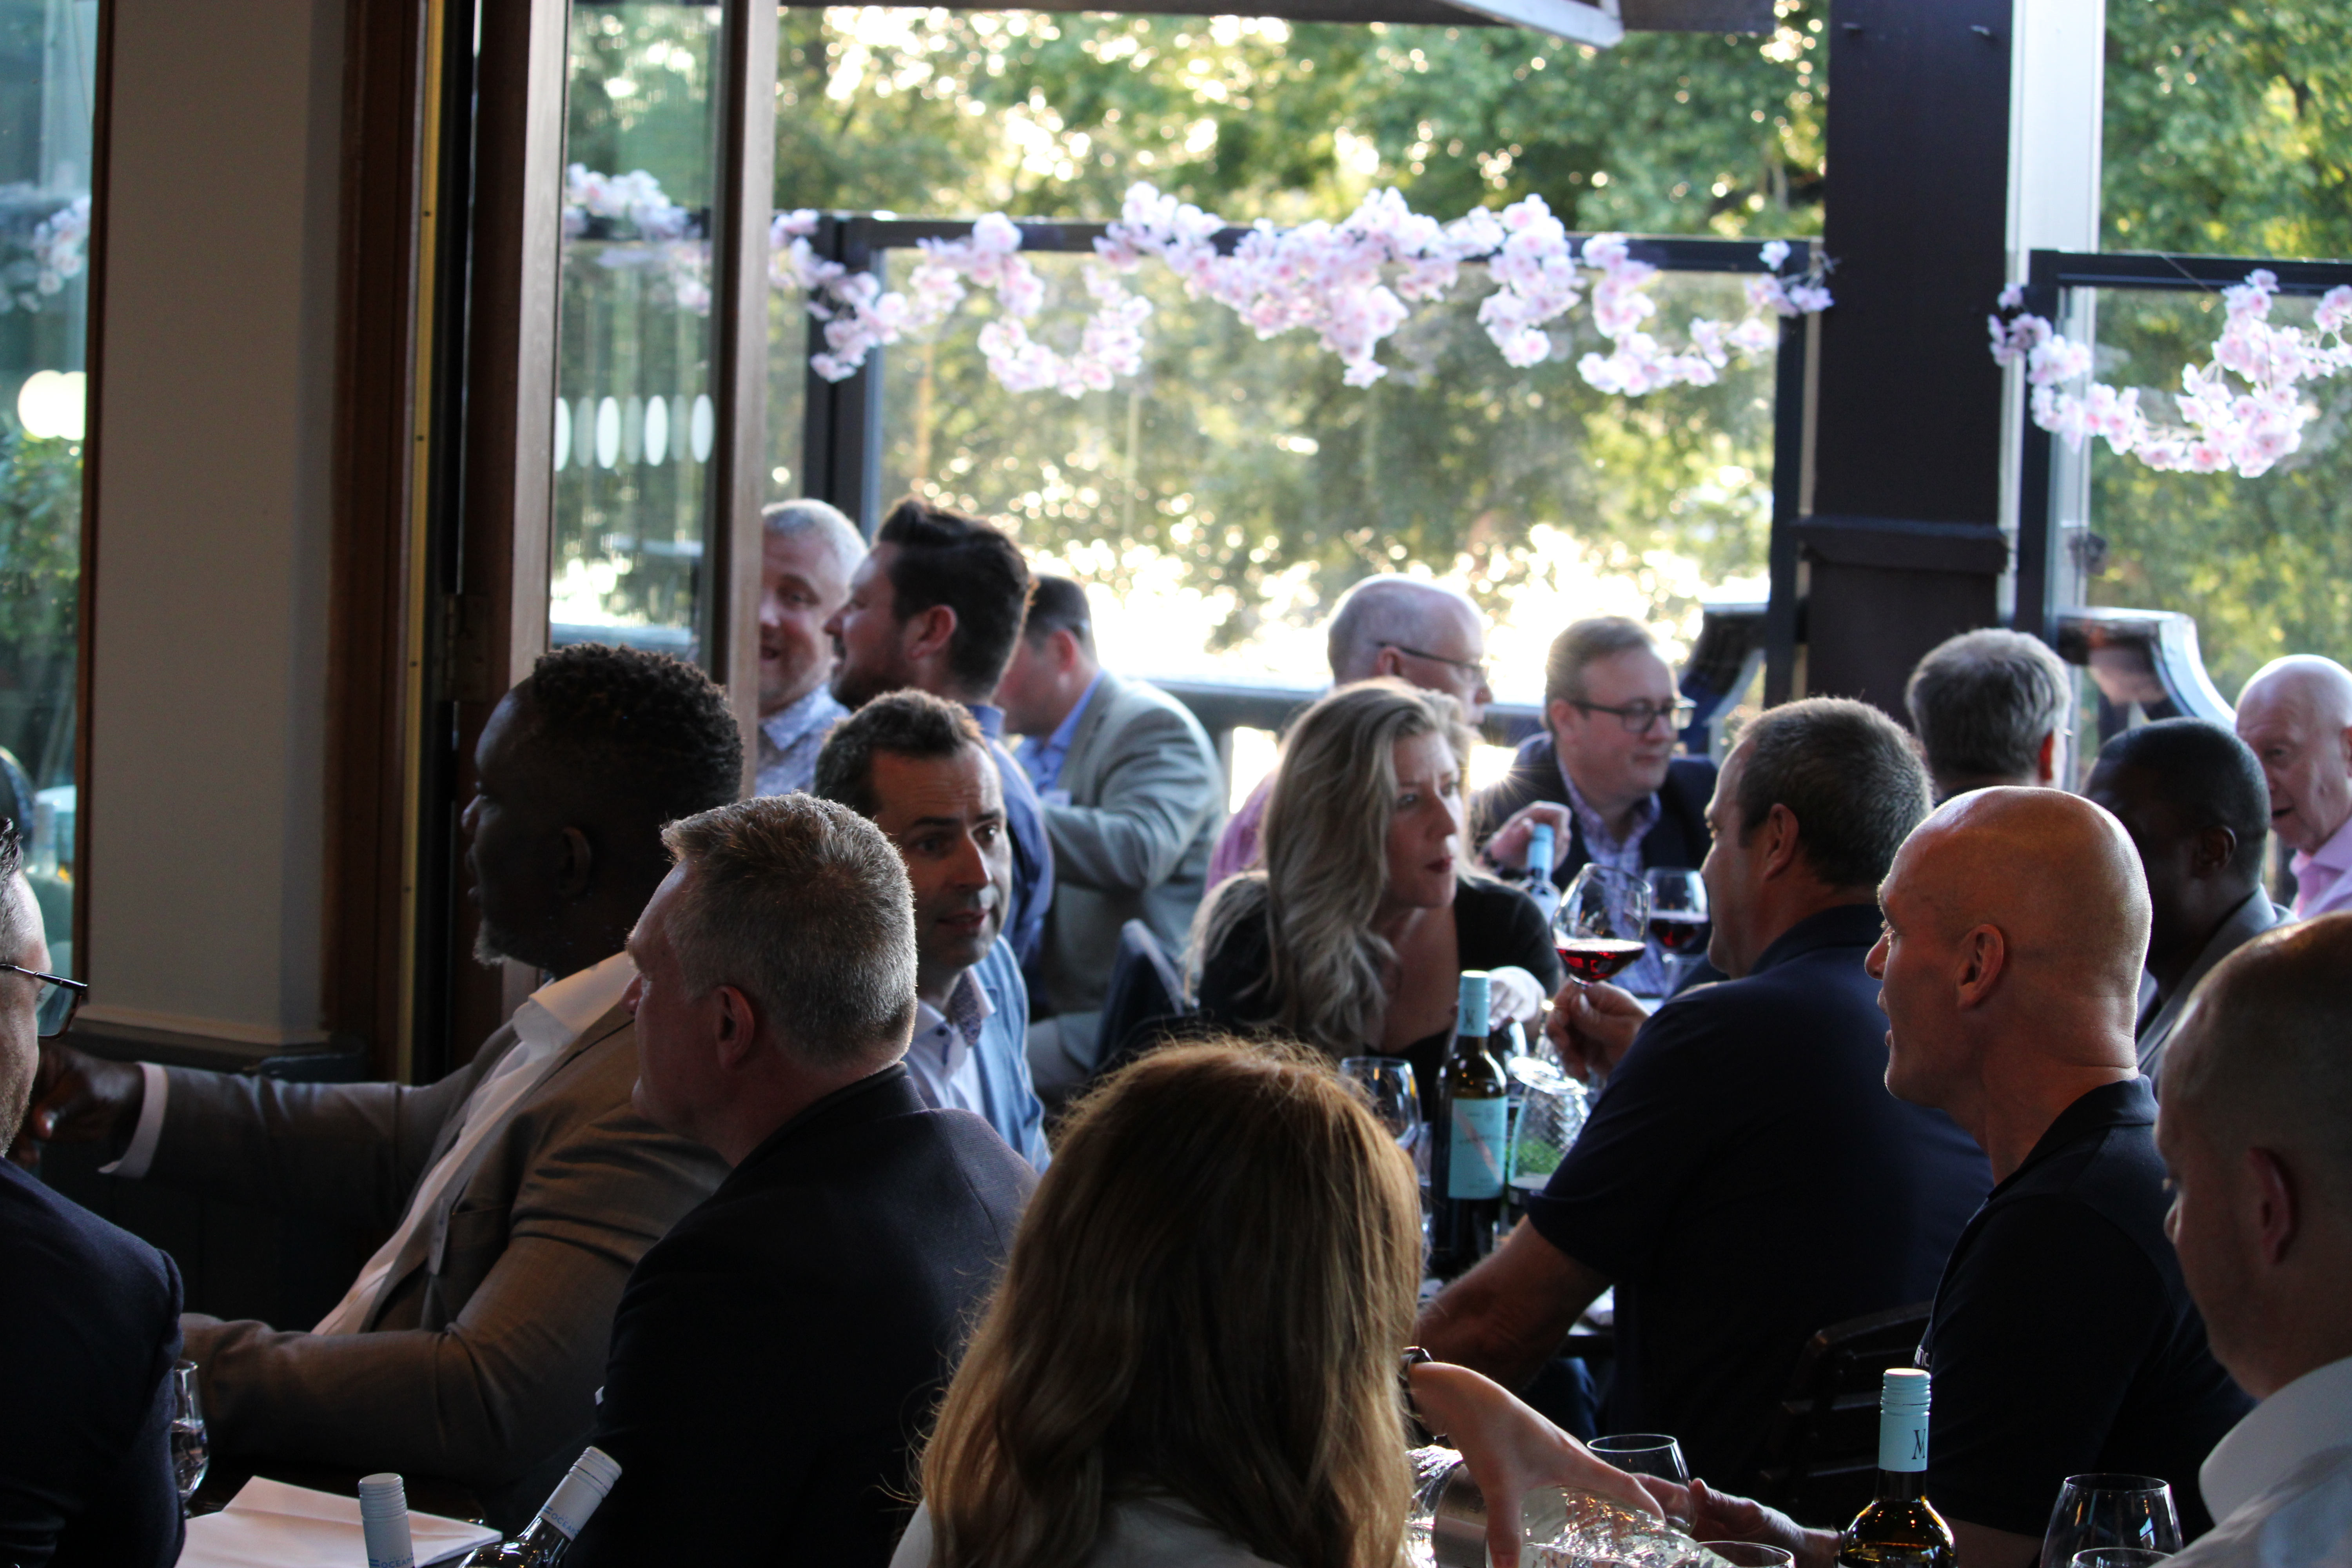
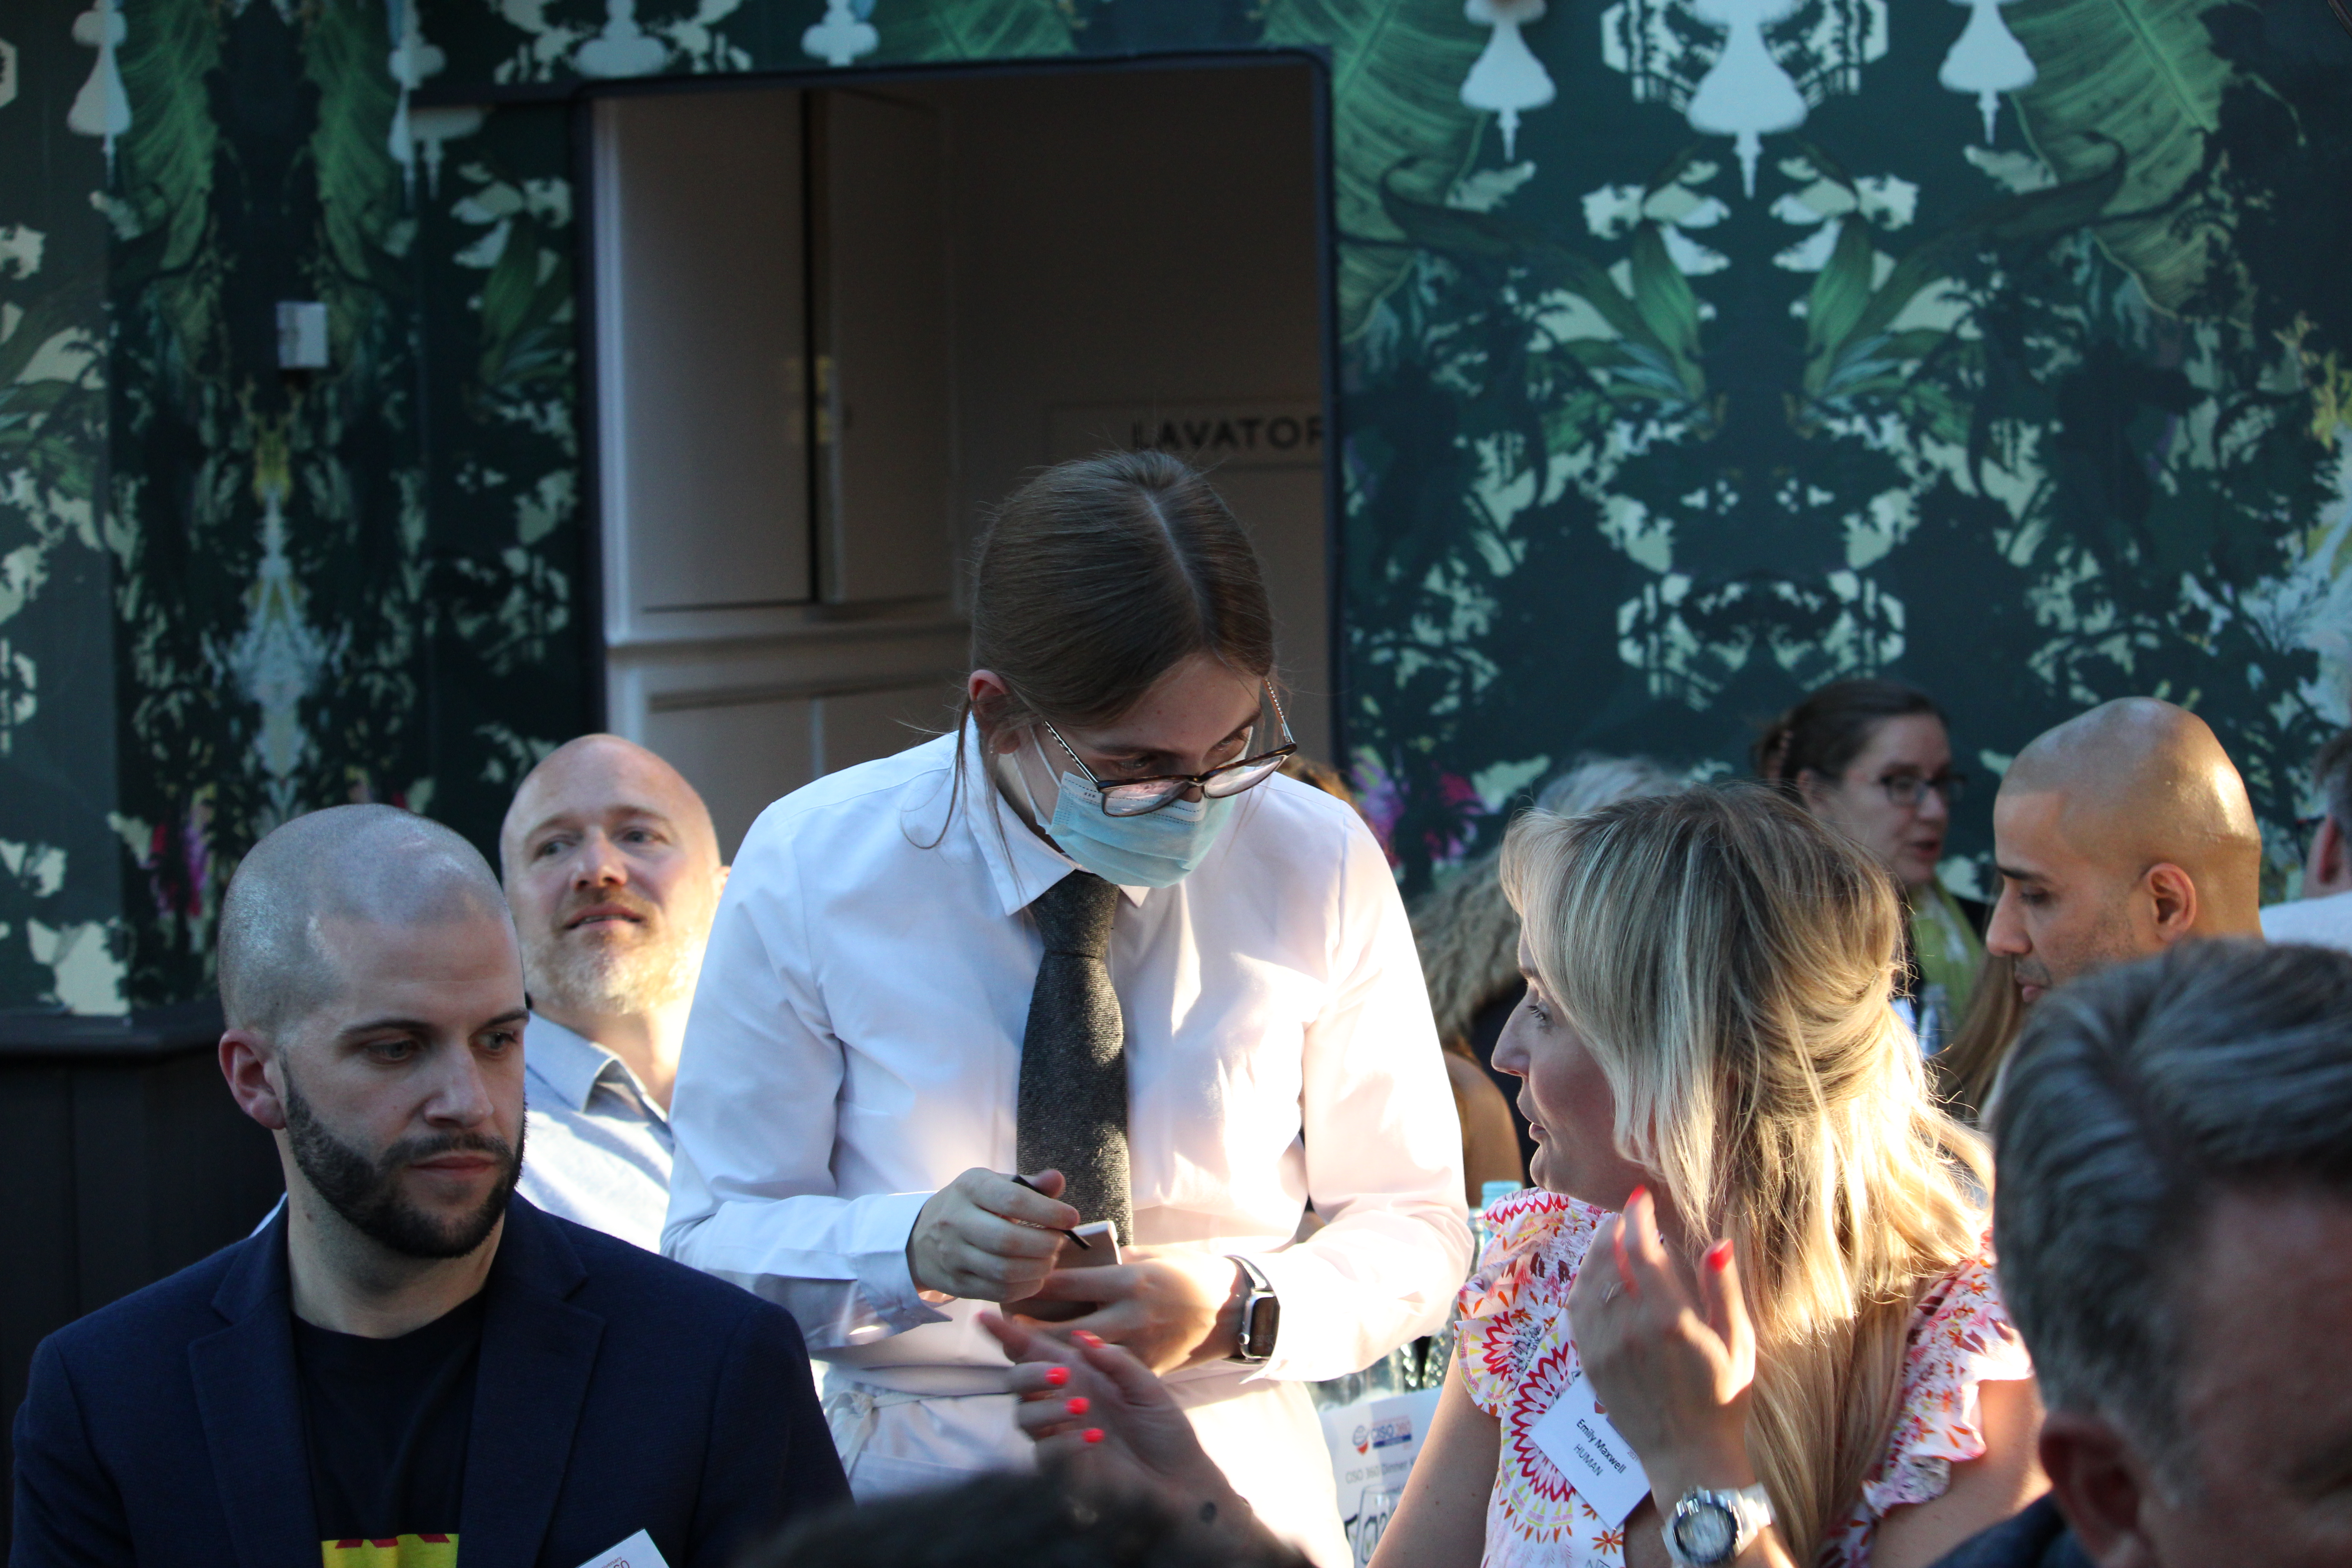
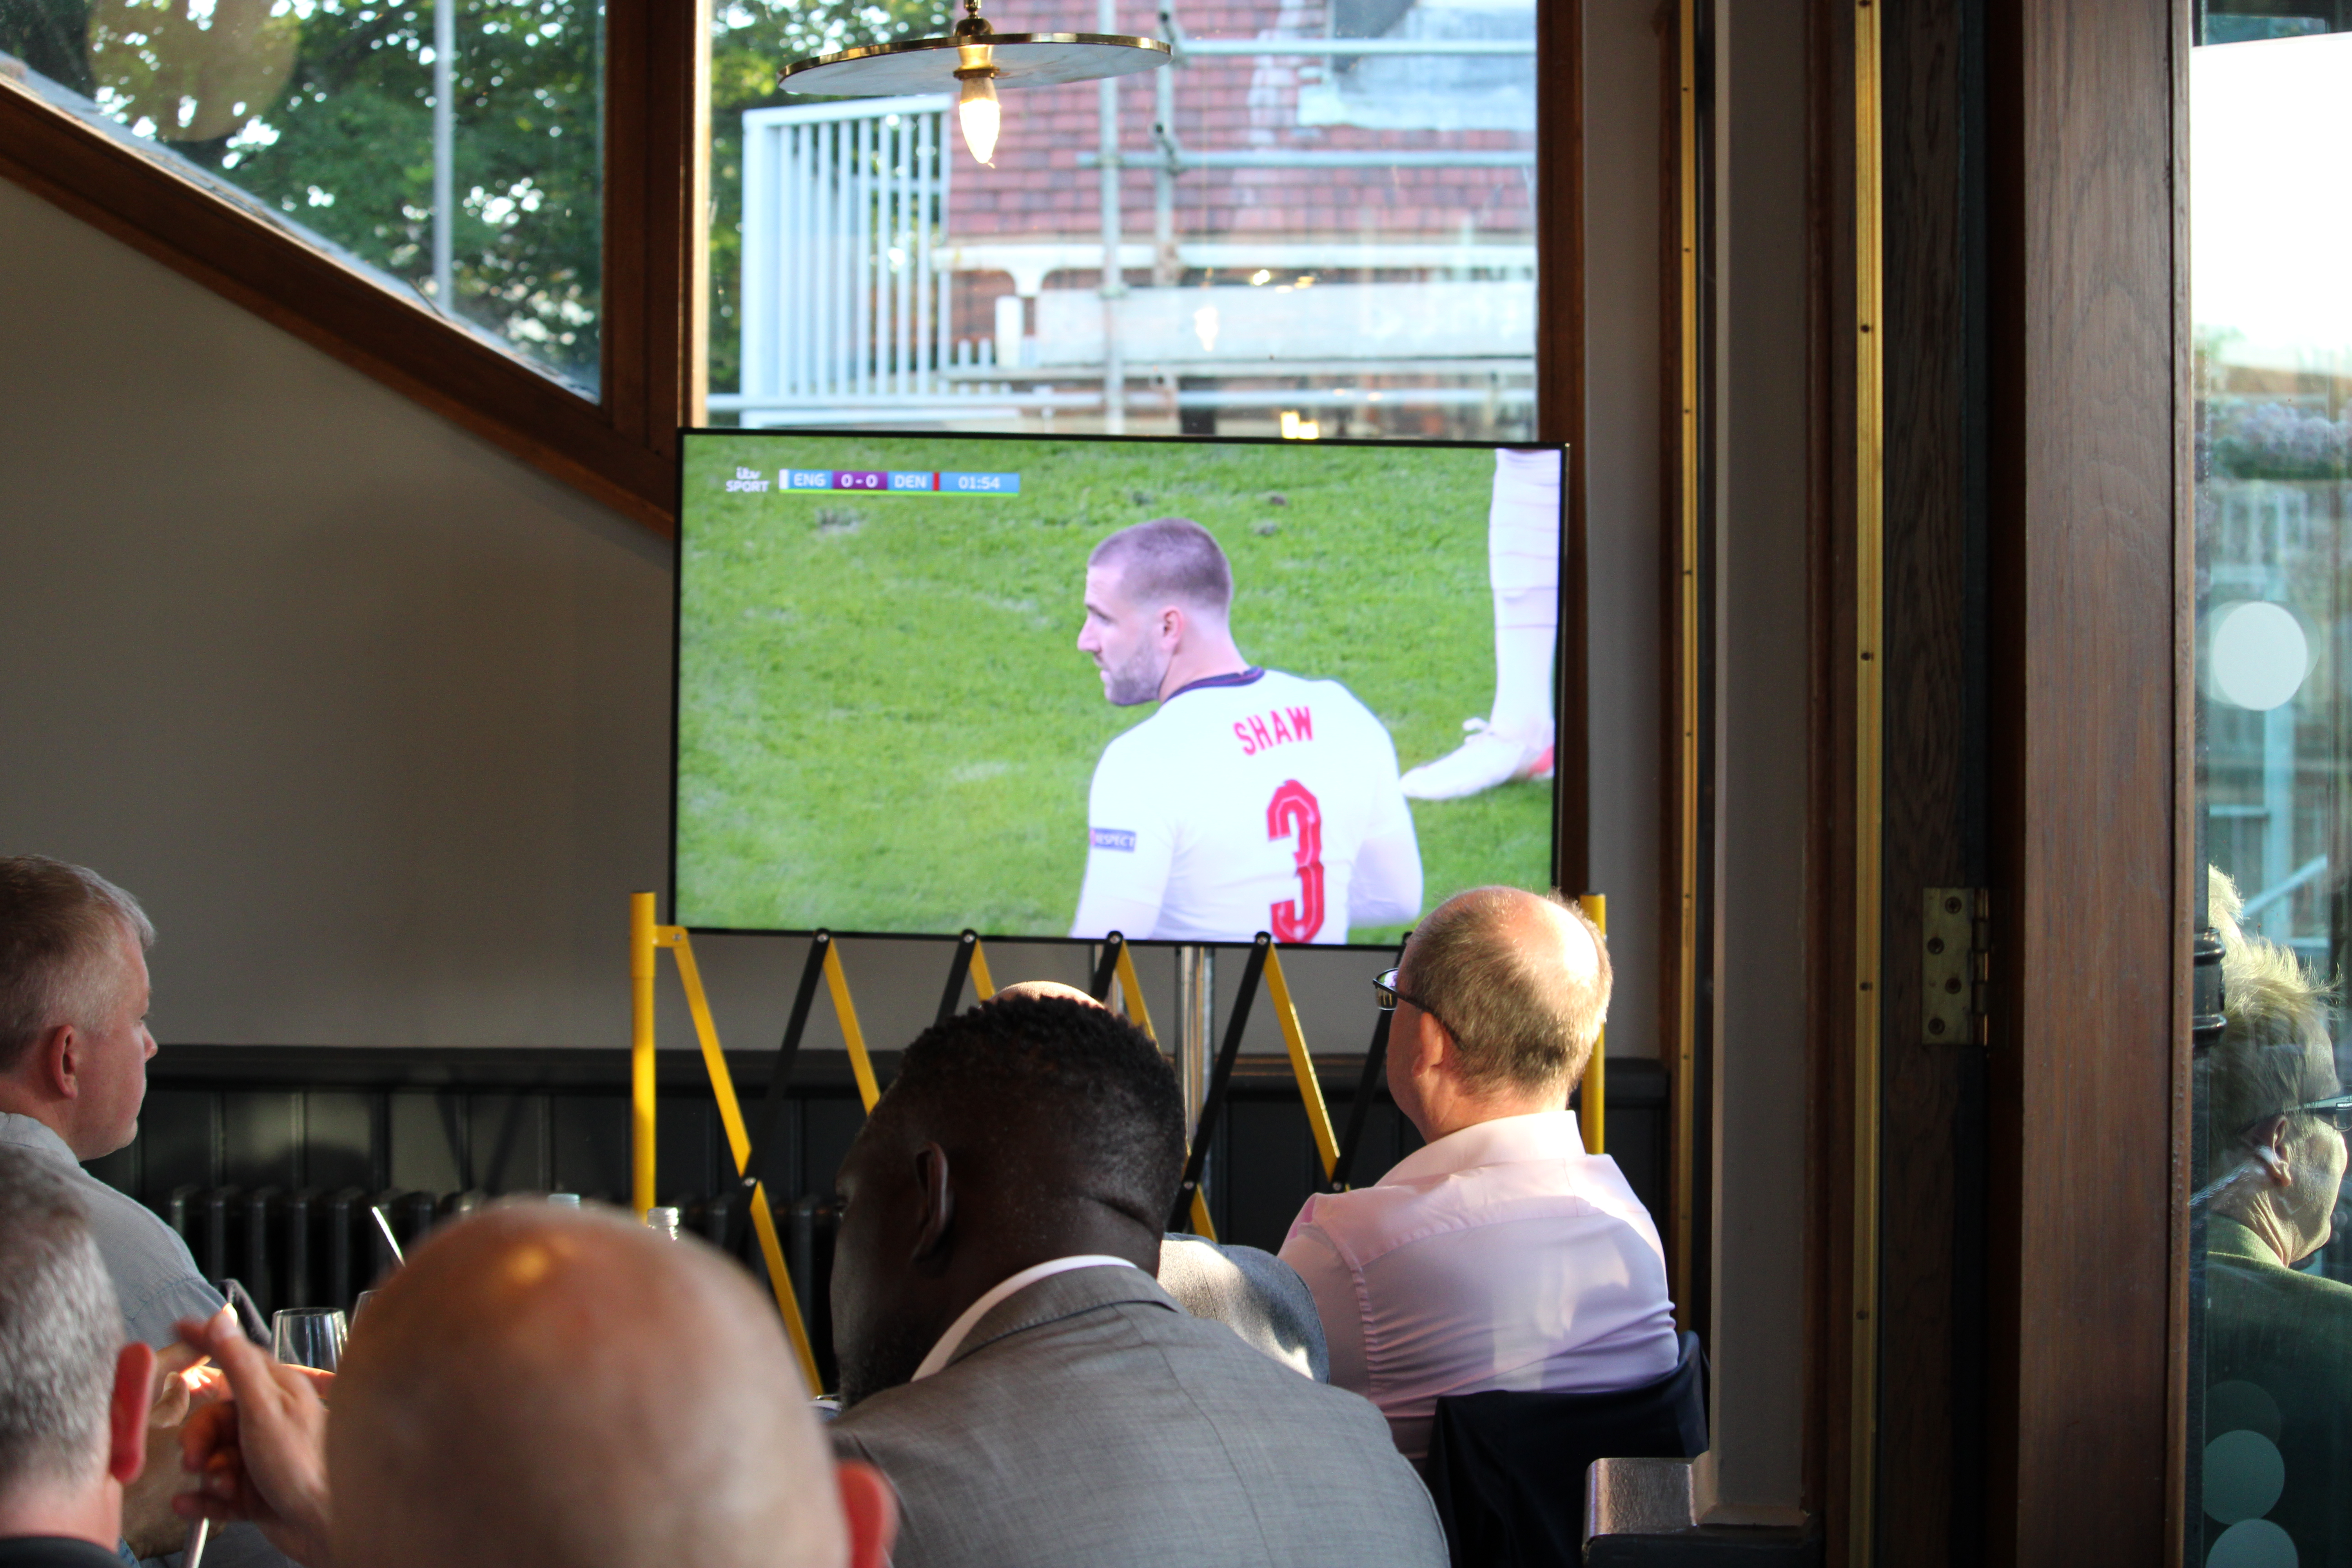
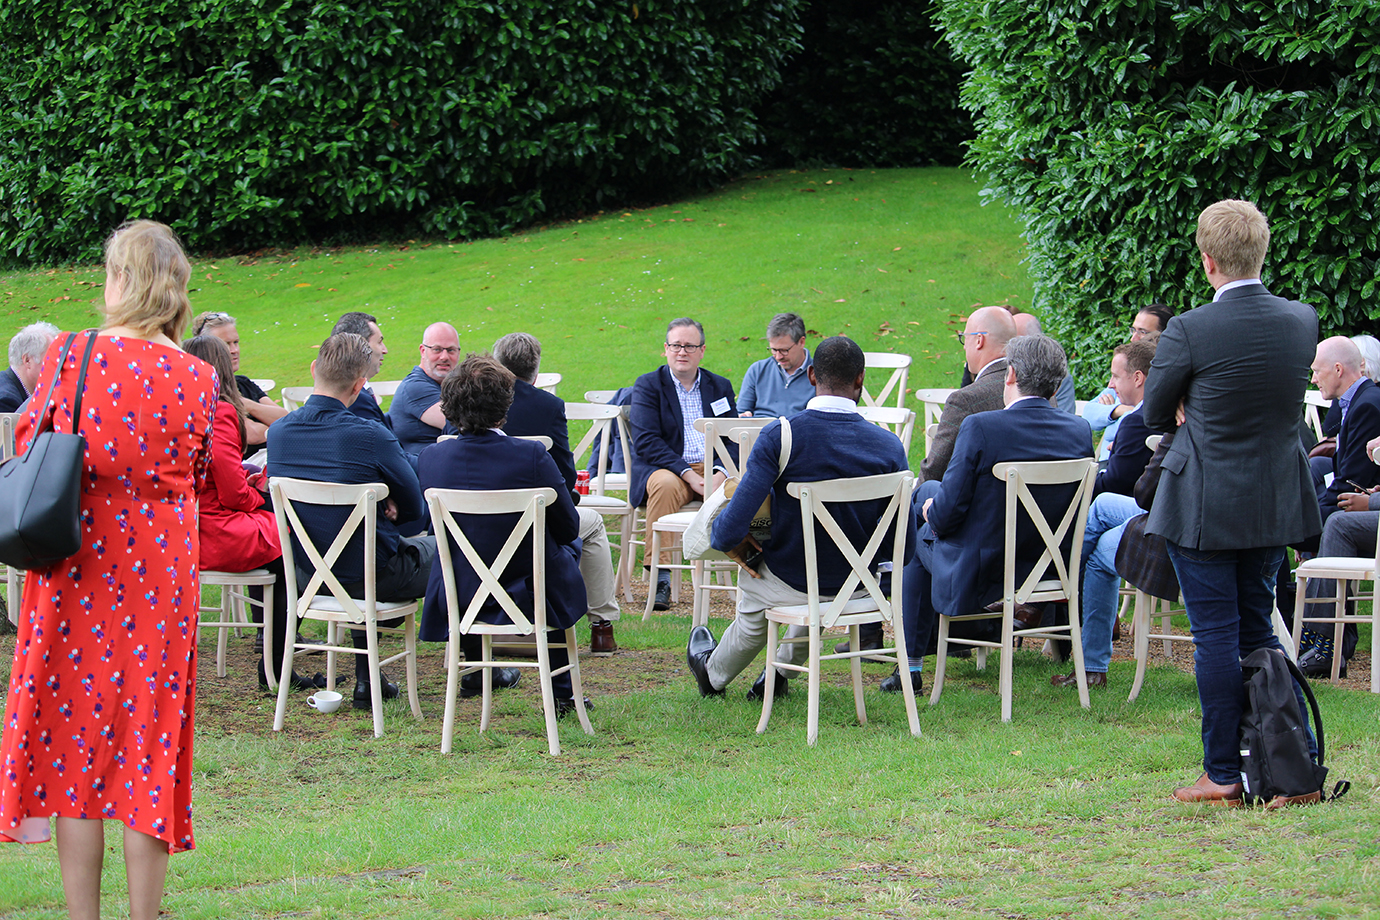
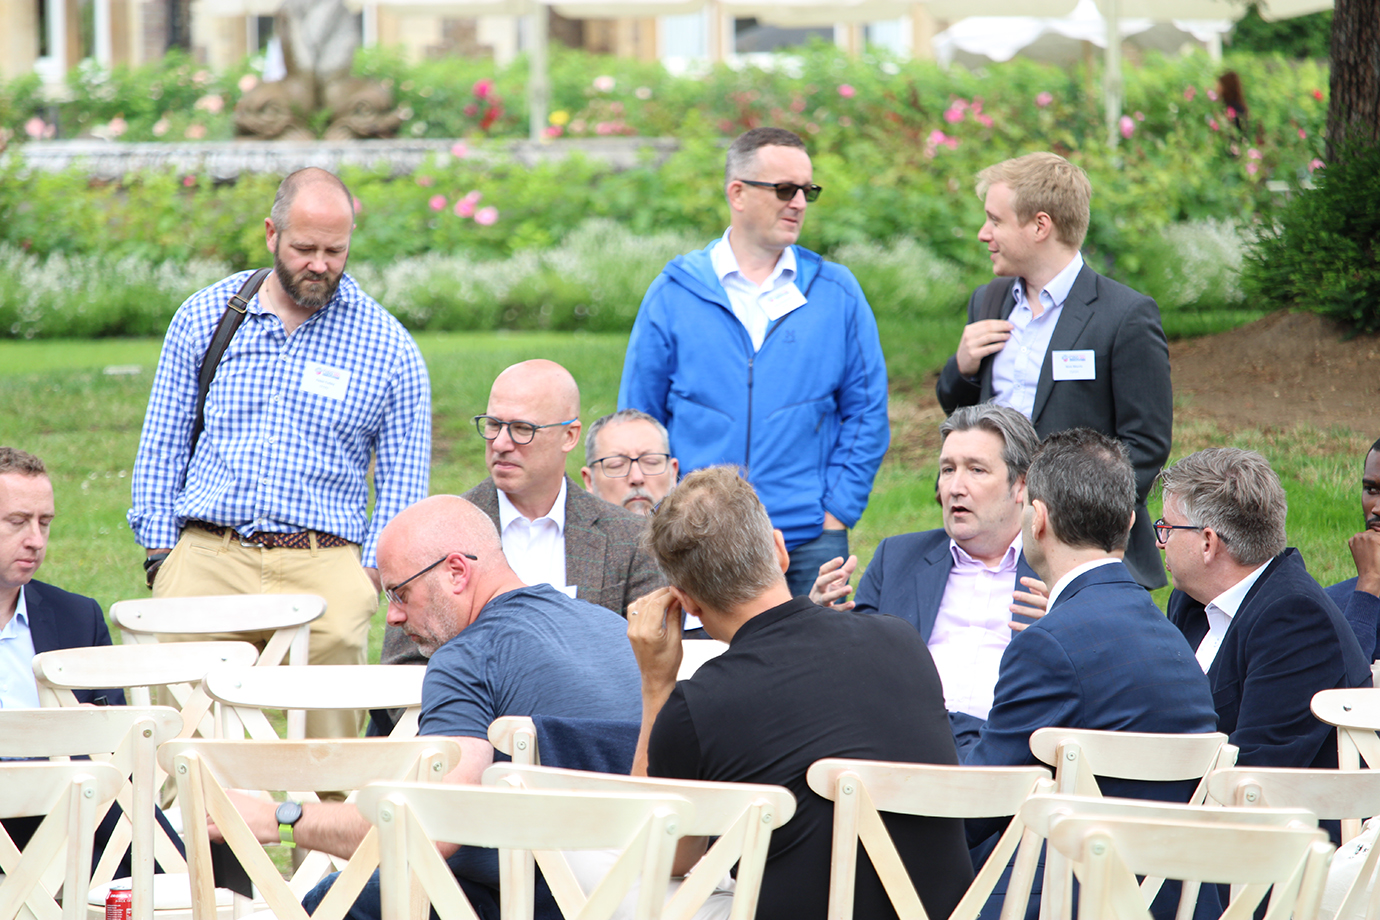
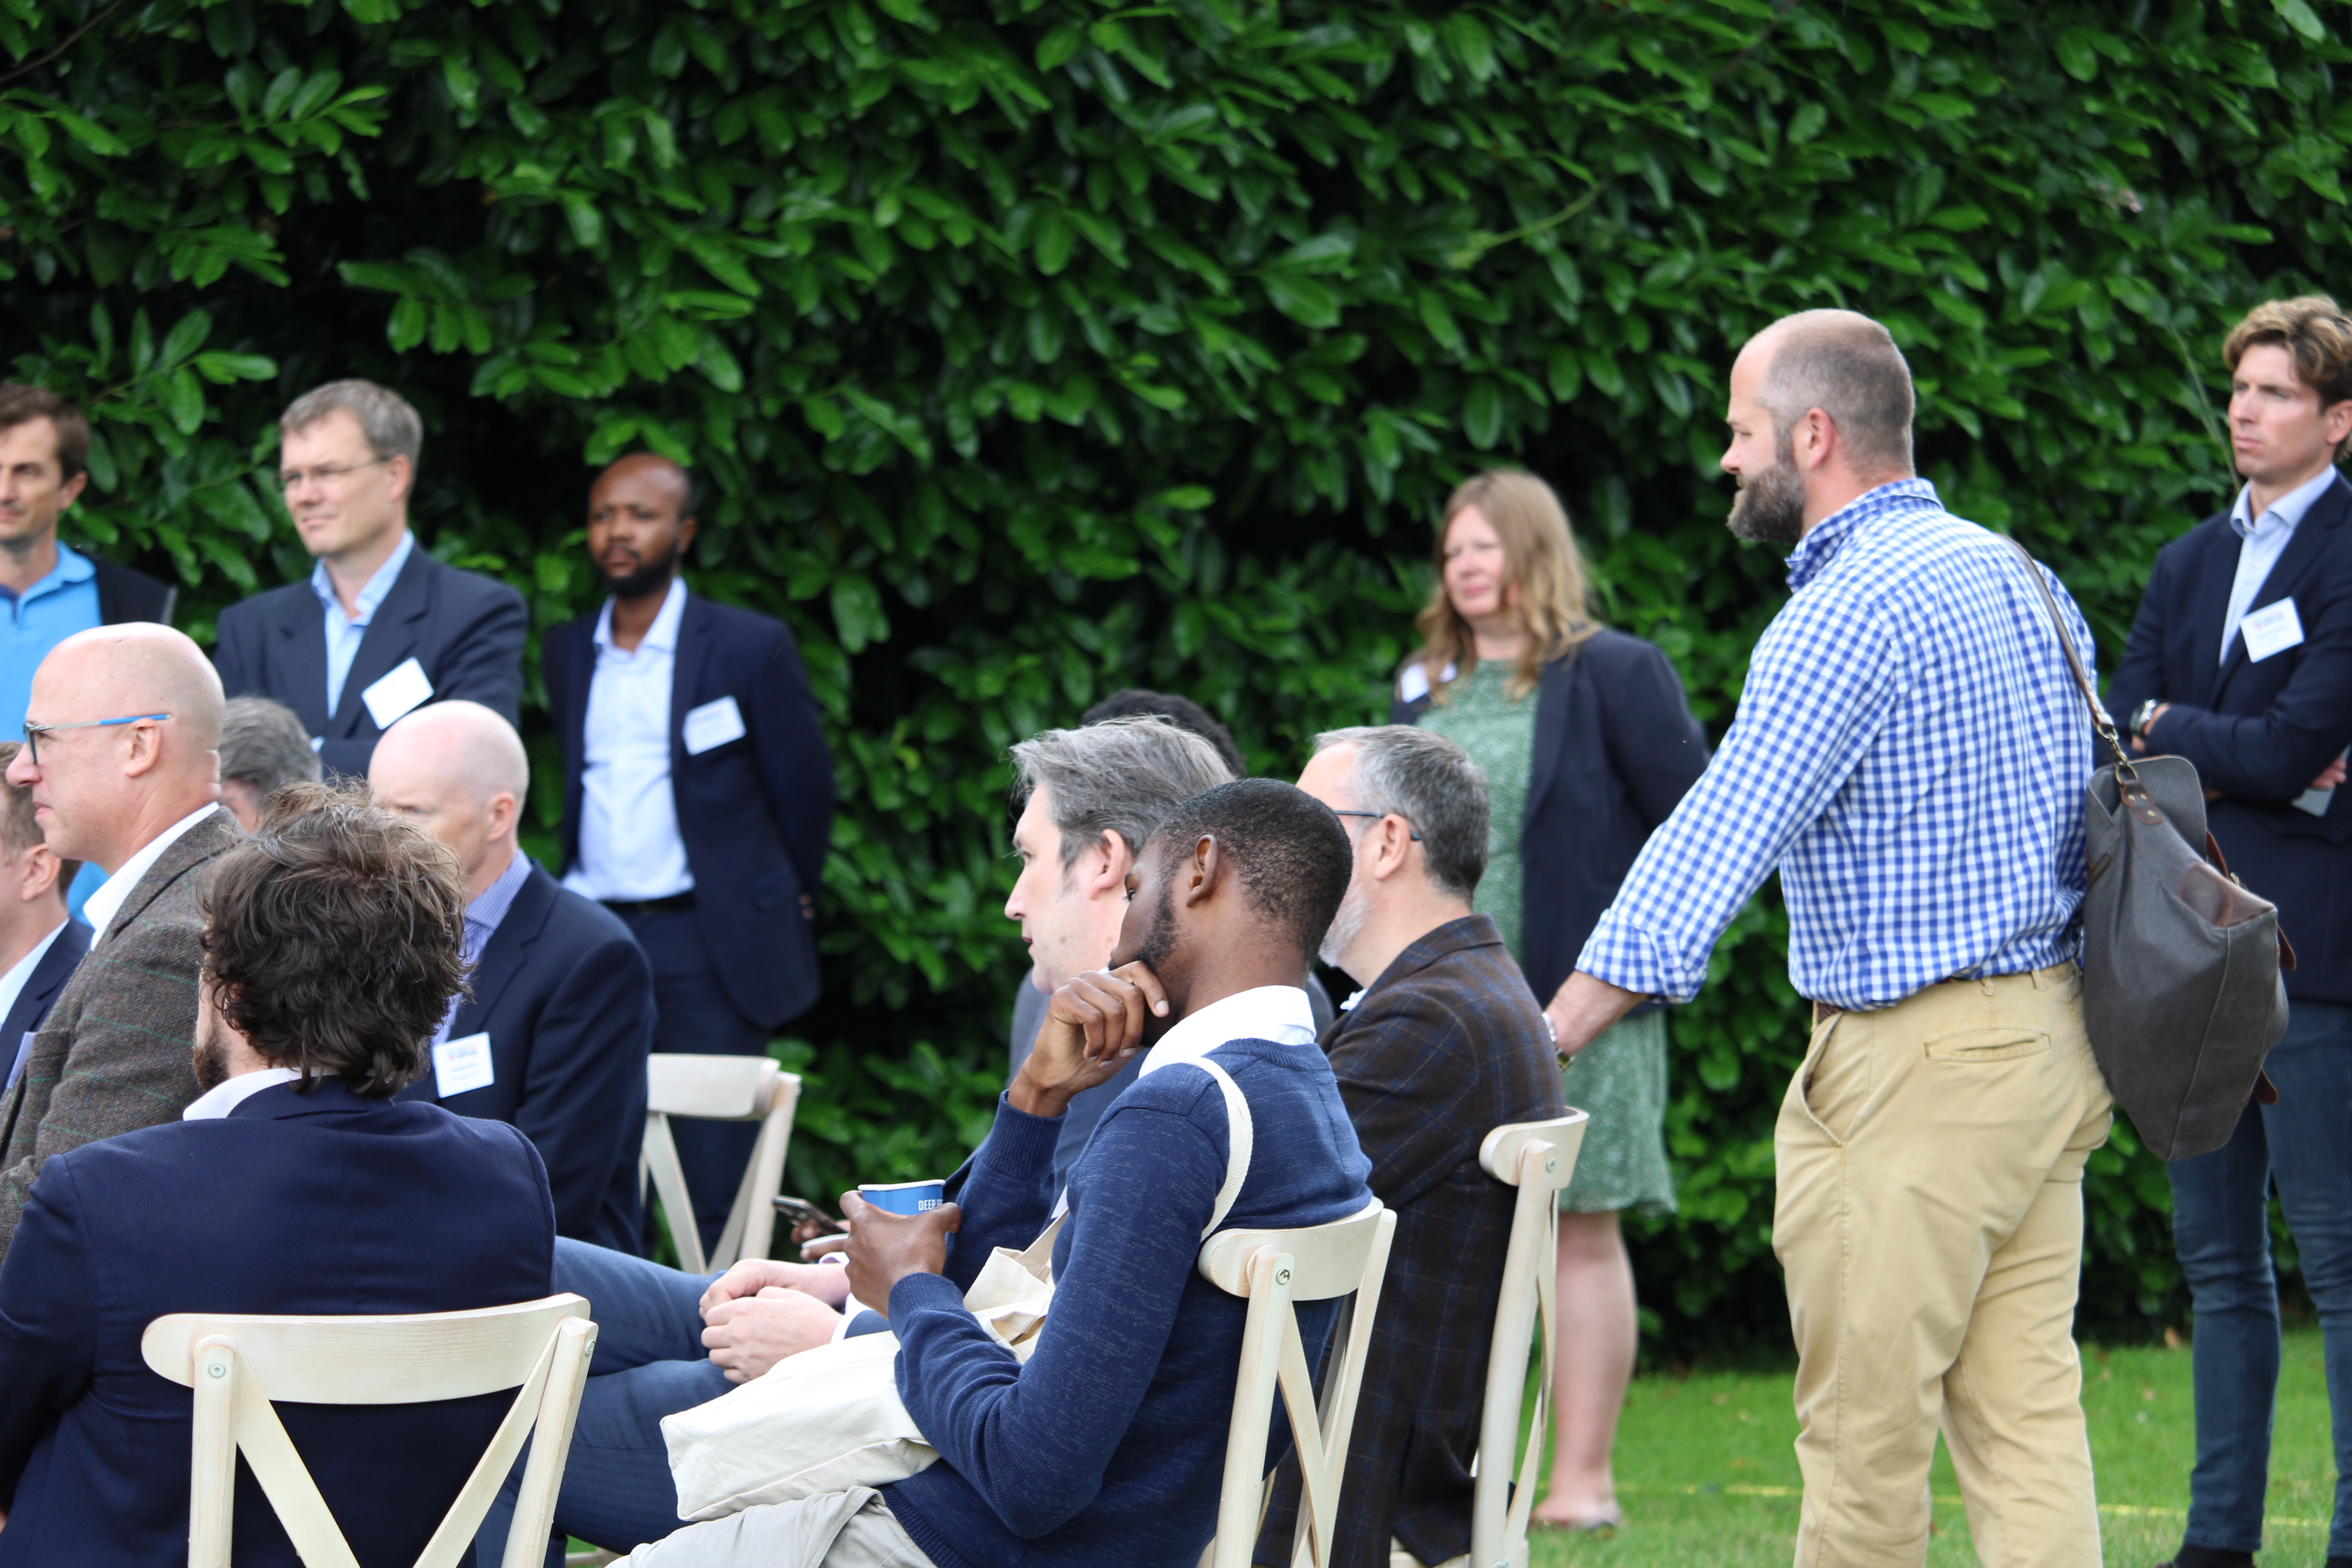
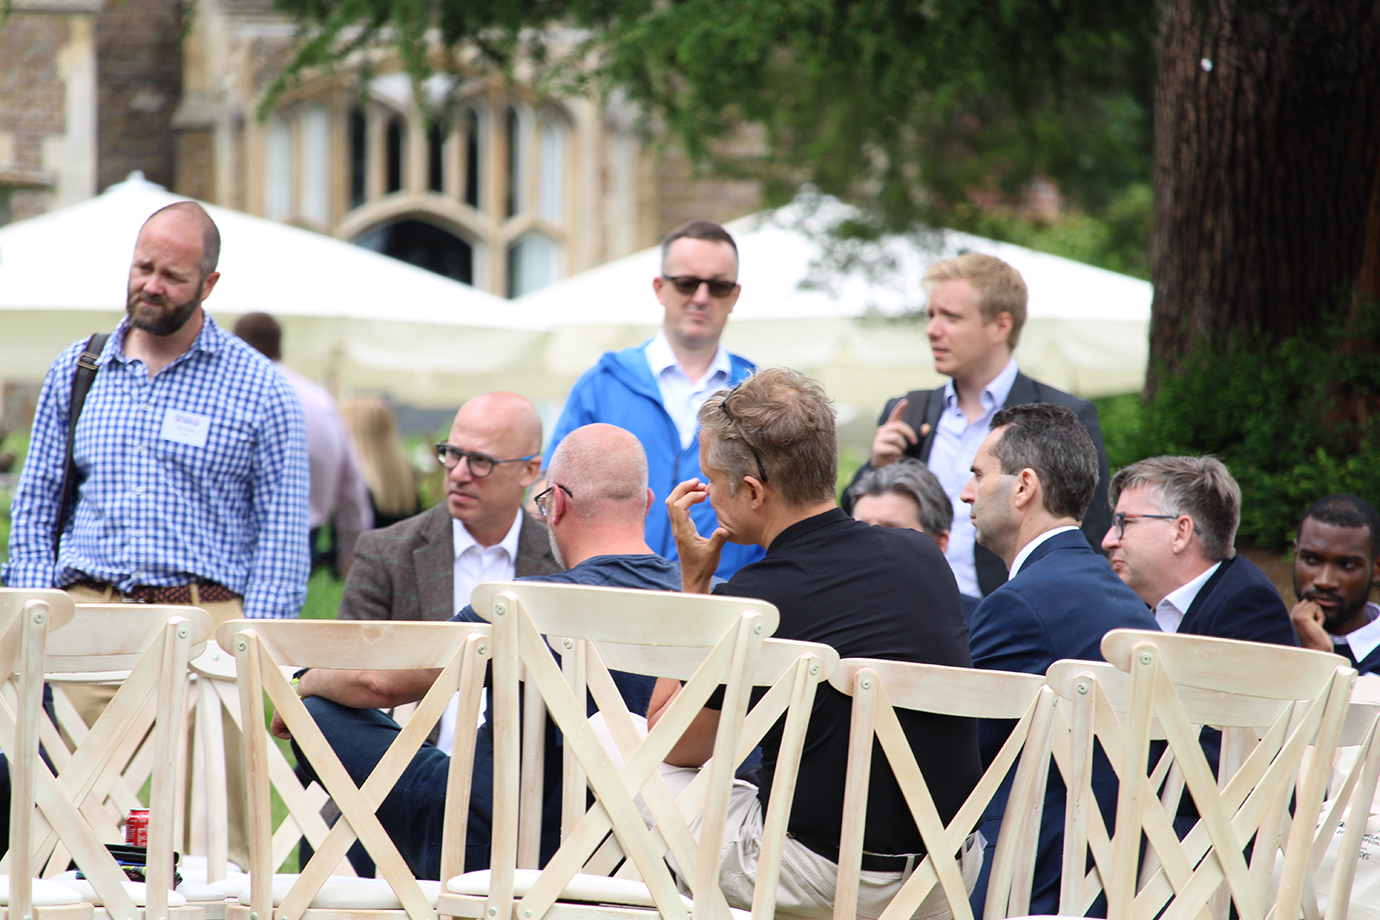
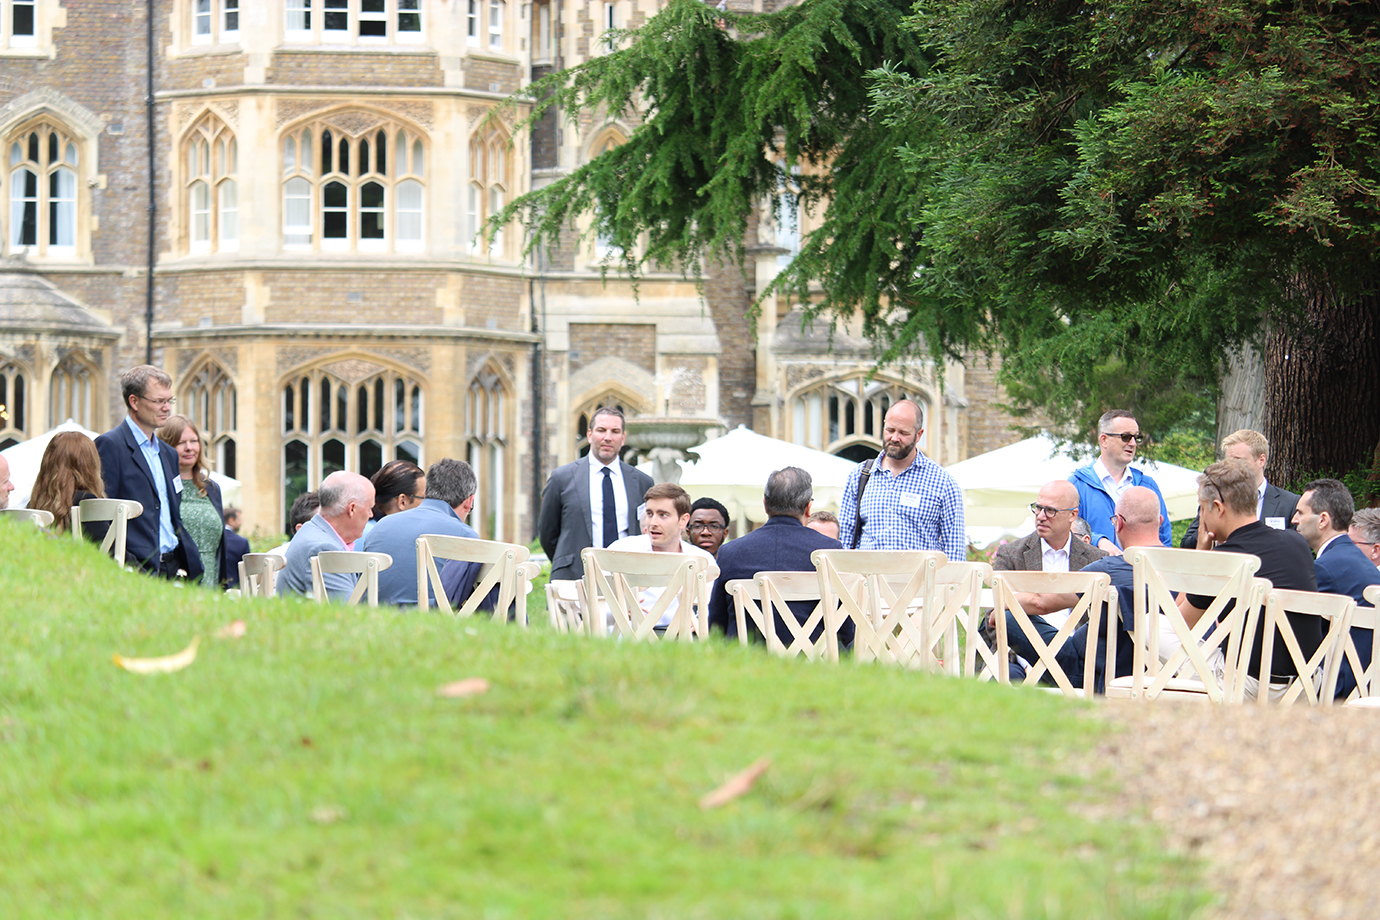
Gallery – 5th CISO 360 Congress – Daytime Networking

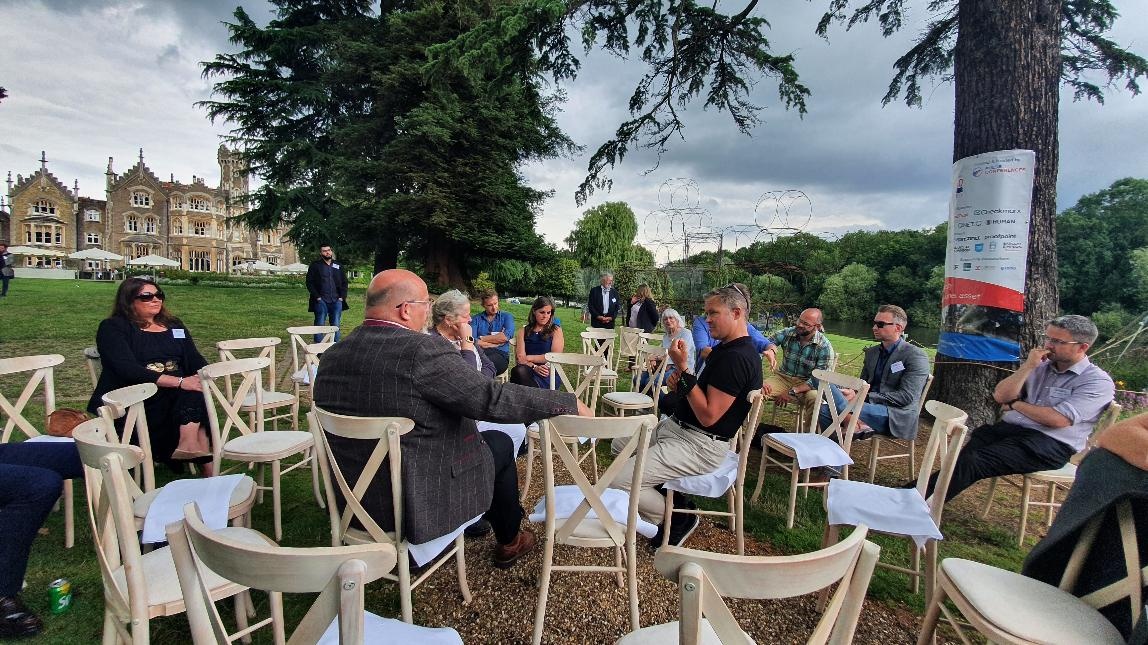
Gallery – 5th CISO 360 Congress – Evening Networking Events

Sponsors

BeyondTrust

BeyondTrust is the worldwide leader in Privileged Access Management (PAM), empowering organizations to secure and manage their entire universe of privileges.  Our integrated products and platform offer the industry’s most advanced PAM solution, enabling organizations to quickly shrink their attack surface across traditional, cloud and hybrid environments.

The BeyondTrust Universal Privilege Management approach secures and protects privileges across passwords, endpoints, and access, giving organizations the visibility and control they need to reduce risk, achieve compliance, and boost operational performance.  Our products enable the right level of privileges for just the time needed, creating a frictionless experience for users that enhances productivity.

With a heritage of innovation and a staunch commitment to customers, BeyondTrust solutions are easy to deploy, manage, and scale as businesses evolve. We are trusted by 20,000 customers, including 70 percent of the Fortune 500, and a global partner network.

www.beyondtrust.com.

Checkmarx

Checkmarx is the Software Exposure Platform for the enterprise. Over 1,400 organizations around the globe rely on Checkmarx to measure and manage software risk at the speed of DevOps. Checkmarx serves five of the world’s top 10 software vendors, four of the top American banks, and many government organizations and Fortune 500 enterprises, including SAP, Samsung, and Salesforce.com. Learn more at Checkmarx.com or follow us on Twitter: @checkmarx.

SailPoint

SailPoint is the leader in identity security for the cloud enterprise. We’re committed to protecting businesses from the inherent risk that comes with providing technology access across today’s diverse and remote workforce. Our identity security solutions secure and enable thousands of companies worldwide, giving our customers unmatched visibility into the entirety of their digital workforce, ensuring that each worker has the right access to do their job – no more, no less. With SailPoint as foundational to the security of their business, our customers can provision access with confidence, protect business assets at scale and ensure compliance with certainty.  For more information please visit  www.sailpoint.com

Bridewell Consulting

Bridewell Consulting is a cyber security services company providing global, 24×7 managed detection and response services and cyber security consultancy. With extensive experience in delivering large-scale transformational projects in highly regulated environments, Bridewell enables organisations to drive strategic change securely, providing a full breadth of end-to-end cyber security services. Its expert team comprises of a diverse range of highly skilled consultants, supported by industry-leading technology, deep technical expertise, accredited methodologies and a client-centric business driven approach. Bridewell delivers a vast number of services across critical national infrastructure, aviation, financial services, government and oil and gas. The company holds several industry accreditations including NCSC, CREST, ASSURE, IASME Consortium, Cyber Essentials Plus, ISO27001, ISO9001 and are a PCI DSS QSA Company.

www.bridewellconsulting.com

Securonix

Securonix is redefining SIEM for today’s hybrid cloud, data-driven enterprise. Built on big data architecture, Securonix delivers SIEM, UEBA, SOAR, Security Data Lake, NDR, and vertical-specific applications as a pure SaaS solution with unlimited scalability and no infrastructure cost. Securonix reduces noise, prioritizes high fidelity alerts, and detects and responds to advanced insider and cyber threats with behavioral analytics technology that pioneered the UEBA category.

For more information visit www.securonix.com

QinetiQ

QinetiQ is an integrated global security and defence company. Operating at the leading edge of science and engineering and employing over 6,000 people, including more than 3,000 scientists and engineers. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way.

Uniting our own and others’ technology and know-how to provide distinctive specialist services and products that address our customers’ most pressing challenges. We are integrated across the life cycle of critical equipment and infrastructure, undertaking creative research and development, enabling test and evaluation and delivering operational readiness through training and rehearsal.

Create it. Test it. Use it.

www.qinetiq.com/en/what-we-do/cyber

HUMAN

HUMAN (formally White Ops) is a cybersecurity company that protects enterprises from bot attacks to keep digital experiences human.  We have the most advanced Human Verification Engine that protects applications, APIs and digital media from bot attacks, preventing losses and improving the digital experience for real humans. Today we verify the humanity of more than 10 trillion interactions per week for some of the largest companies and internet platforms. Protect your digital business with HUMAN.

To Know Who’s Real,  visit www.humansecurity.com

Snyk

Snyk is a developer-first security company that helps software-driven businesses develop fast and stay secure. Snyk is the only solution that seamlessly and proactively finds and fixes vulnerabilities and license violations in open source dependencies and container images. Snyk’s solution is built on a comprehensive, proprietary vulnerability database, maintained by an expert security research team in Israel and London. With tight integration into existing developer workflows, source control (including GitHub, Bitbucket, GitLab), and CI/CD pipelines, Snyk enables efficient security workflows and reduces mean-time-to-fix. For more information or to get started with Snyk for free today, visit https://snyk.io.

Qualys

Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance. For more information, please visit www.qualys.com

Proofpoint

Proofpoint is a leading cybersecurity company that protects organizations’ greatest assets and biggest risks: their people. With an integrated suite of cloud-based solutions, we help companies around the world stop targeted threats, safeguard their data, and make their users more resilient against cyber attacks. Leading organizations of all sizes, including more than half of the Fortune 1000, rely on us for people-centric security and compliance solutions that mitigate their most critical risks across email, the cloud, social media, and the web.

www.proofpoint.com/uk

Vectra

Vectra® protects business by detecting and stopping cyberattacks.

As a leader in network detection and response (NDR), Vectra® protects your data, systems, and infrastructure. Vectra enables your SOC team to quickly discover and respond to would-be attackers – before they act.

 No business or organisation is impervious to cyberattacks. Your existing security tools will prevent 99% of those attacks. But with enough time, bad actors can get past even the most secure barriers. With Vectra, you stop them in their tracks.

 Vectra gives security analysts the ability to rapidly identify suspicious behaviour and activity on your extended network. Whether that activity originates outside the firewall or from within, whether an attack is directed against an on-prem data centre or the cloud, Vectra will find it, flag it, and alert security personnel so they can respond before the damage is done.

 Vectra is Security that thinks®. It uses artificial intelligence and machine learning to improve detection and response over time, eliminating false positives so you can focus on real threats. The result of an unparalleled marriage of security research and data science, Vectra will change the way you think about cybersecurity.

www.vectra.ai

Downloadable assets:

AttackIQ

Adversaries across the globe, from nation-states to criminal organizations, hold our businesses, democracy, and society at risk through cyberspace. Our mission at AttackIQ is to help solve that problem.

www.attackiq.comhttp://www.attackiq.com

Bestman Solutions

Owanate Bestman, founder of Bestman Solutions, has spent almost a decade recruiting in the Cyber Security field. Securing individuals and teams that meet specific technical and/ or leadership requirements for some of the world’s most innovative firms to the mutual benefit of individuals’ career progression and the company’s needs. www.bestmansolutions.com

Risk Crew

Risk Crew is an elite group of product-independent, information governance, risk, and compliance management professionals. We’re the forerunners in the design and delivery of effective business information and communication technology risk and security solutions. We understand business risk and compliance and so we also excel in the creation of operative controls and processes to cost-effectively comply with legislation, regulation and best commercial practices such as the Payment Card Industry (PCI), Data Security Standards (DSS), the UK Data Protection Act (DPA) and ISO/IEC 27001. Risk Crew take great pride in the depth and breadth of our technical and tactical knowledge and will work to ensure that it’s fully leveraged to provide the greatest benefit to your business objectives. We also put skin in the game and guarantee all of our services. Consequently, we are the selected supplier of choice for hundreds of businesses in virtually every commercial sector across the United Kingdom. www.riskcrew.com 

Barclay Simpson

Local knowledge. Global resources. Specialist consultants.

Barclay Simpson is an international recruitment consultancy that specialises in recruiting information and cyber security professionals.
Since 2001, we have provided end-to-end information security recruitment solutions, including permanent, interim and executive hires from analysts through to CISOs, so organisations can create an information security function that’s both fit for purpose and future-proof. Whether sourcing a single hire, an interim manager, or building a security function from scratch, our extensive network and niche specialist knowledge make Barclay Simpson ideally positioned to support your security needs.

Our specialist markets:

Security Leadership: CSO / CISO, Director of Information Security, Head of IT Risk, Head of Security Operations, Head of Security Architecture, Cyber Programme Director
Governance, Risk & Compliance: IT & Cyber Risk, IT Resilience, Information Risk, Security Controls & Assurance, 3rd Party Risk & Supplier Assurance
Security Architecture & Engineering: Security Architecture, Security Engineering, Cloud Security, Application Security, DevSecOps
Cyber Operations & Incident Response: Security Operations, Incident Response, Threat Intelligence, Threat & Vulnerability Management, Penetration Testing
Data Protection & Data Privacy: DPO, Data Privacy, Data Protection, Data Security, Data Governance, GDPR
Cyber Transformation & IAM: Cyber / Risk Transformation, Project & Programme Management, Regulatory Change, Cyber Education & Awareness, Identity & Access Management

Why businesses choose Barclay Simpson for their information and cyber security hiring needs:

Market insight
Specialising in information and cyber security, we provide unique insight into the hiring, skills and remuneration trends within this vast and complex sector.

Local knowledge, global solutions
We have a database of nearly 100,000 professionals and deep, niche networks connecting you to the top local and international information and cyber security professionals.

Competitive intelligence
From market mapping to charting competitor organisational structures and strategies, we’ll benchmark your function against industry leaders to provide you confidence and assurance.

Consultative approach
From business strategy and advisory services through to implementation and transition strategies, our information and cyber security recruitment services are fully tailored to your needs.

http://barclaysimpson.com/CyberSecurity 

Barclay Simpson Solutions

Barclay Simpson Solutions helps empower our clients to achieve business transformation success. We combine our proven industry talent expertise with effective and measurable project & service ownership and reporting. We work in partnership with our sister organisation (Barclay Simpson Associates) to ensure our advisory and project service flexibility utilises industry leading consultants, maintaining our overall strong position in the solutions market. Supporting our clients by providing comprehensive, outcome based engagements operated through a project services (Statement of Work) framework to ensure performance and delivery, Barclay Simpson Solutions provides expertise in project and service outcomes across the following areas, please click on any listed service offering for more information: Project Engagement Services: Governance & Assurance; Cyber Security & Info Sec; Risk & Compliance; Audit.

www.barclaysimpson.com/barclay-simpson-solutions

Synopsys

Synopsys offers the most comprehensive solution for building integrity—security and quality—into your SDLC and supply chain. We’ve united leading testing technologies, automated analysis, and experts to create a robust portfolio of products and services. This portfolio enables companies to develop customized programs for detecting and remediating defects and vulnerabilities early in the development process, minimizing risk and maximizing productivity. We don’t stop when the test is over. As a recognized leader in application security testing, we offer onboarding and deployment assistance, remediation guidance, and training solutions that empower you to optimize your investment.

www.synopsys.com/software

Corelight

From the Acropolis to the edge of space, defenders have sought the high ground in order to see farther and turn back attacks. Corelight delivers a commanding view of your network so you can outsmart and outlast adversaries. We capture, interpret, and connect the data that means everything to defenders.

www.corelight.com

2|SEC Consulting

2|SEC Consulting delivers technical assurance and business advisory services to its global client base; from agile start-ups to FTSE 250 organisations.  Our service offering helps organisations to increase their cyber security maturity through a cost-effective service. This also enables the business to do more with existing budgets. We believe that security measures should be implemented intelligently and effectively; with SMART objectives set. 2|SEC Consulting was formed in 2011 by our CEO, Tim Holman. After a security career spanning 20+ years in consulting roles, Tim identified a gap in the market for specialist cyber security services to work alongside in-house IT departments. Our services have continued to develop to support our clients’ growing needs. From initial technical assurance services such as Penetration Testing to establishing a business advisory team which helps clients achieve cyber security frameworks such as ISO 27001. In 2018, 2|SEC was rebranded to 2|SEC Consulting to better represent the holistic approach we take to cyber security and information security. Our complete service offering is delivered to help protect our clients throughout all stages of the cyber security risk management lifecycle. We are accredited for CREST, CHECK and, Cyber Essentials Plus. Our consultants also hold an impressive range of cyber security qualifications including CISSP, QSA, PA-QSA, PCI QSA, PCI PA-QSA,  PCIP, CISA, CEH, SANS-GIAC and, ISO 27001 Lead Auditor.

ClubCISO

ClubCISO, powered by Telstra Purple, is a global private members forum for information security leaders working in public and private sector organisations. The community is a non-commercial organisation with over 500 members helping to define, support and promote the critical role and value of information security leaders in business and society. ClubCISO provides a forum in which security leaders can build their network, be involved in proactive discussion, solve problems and create practical guidance that moves the industry forward.

www.clubciso.org

IAAC

IAAC is a not-for-profit organisation dedicated to developing the Community of Interest (CoI) needed to build safe and resilient cyberspace.  Representing public, private, academic and many industry sectors, the IAAC Community is engaged in the development of policy recommendations to government and corporate leaders at the highest levels. We identify key issues and navigate their complexity to advance collective understanding, and facilitate guiding research into issues that have yet to be adequately explored.  As a diverse community, IAAC is well positioned to advance cybersecurity and resilience for business and society as a whole, examining key challenges from a non-technical business and policy perspective. Projects range from an understanding of needed skills and behaviours to promoting promising practices across communities.

IAAC is a core contributor to the project to establish the new UK Cyber Security Council and works overall to support the cyber security strategies of the UK and devolved governments, including the efforts of the National Cyber Security Centre (NCSC). There are varied opportunities to get involved from regional and national cyber leadership forums to more focussed programmes and workshops. All are by invitation, with participants able to expand their sphere of influence and contribute to an independent resource for the United Kingdom that serves both economic and public interest. If you would like to get involved, please register to join the IAAC Community of Interest or contact us about sponsoring our aims. www.iaac.org.uk; https://www.linkedin.com/company/information-assurance-advisory-council.  Twitter: @theiaac

ISF

ISF is recognised as a leading, independent, not-for-profit authority on information security and risk management.
The ISF is dedicated to investigating, clarifying and resolving key issues in cyber, information security and risk management and developing best practice methodologies, processes and solutions that meet the business needs of its Members.

ISF Members benefit from harnessing and sharing in-depth knowledge and practical experience drawn from within their organisations and developed through an extensive research and work programme. We provide a confidential forum and framework, which ensures that Members adopt leading-edge information security strategies and solutions.

www.securityforum.org
www.securityforum.org/podcasts-videos/
LinkedIn: information security forum
@SecurityForum

ISSA-UK

ISSA-UK is the leading cyber security networking association here in the UK.  As a not-for-profit organisation we are here to help get cyber security professionals together.  We do this through many of our events run throughout the year from our Chapter meetings to our annual ‘Pitch on the Ship’ event which is a day full of keynote speakers and our infamous ‘Pitch on the Ship’ sessions.   Having welcomed over 1,800 members since our beginnings in 2003, the ISSA-UK chapter is the world’s most successful chapter.  Join us at our next event to find out more and to connect with other cyber security professionals. www.Issa-uk.org. – LinkedIn: ISSA-UK Twitter: @issauk

Who attends

By Designation

  • Chief Information Security Officers
  • Directors of Cybersecurity / Senior Cybersecurity Practitioners
  • Heads of Cyber Threat Intelligence
  • Chief Information Risk Officers
  • CEOs, R&D, CTOs, CIOs, Innovation
  • Chief Risk Officers
  • Chief Security Architects / Heads of Security Infrastructure
  • Directors of Technology Innovation or Directors of Digital Risk
  • Chief Data Officers
  • Chief Privacy Officers

Attendees are from across private and public sectors, including but not limited to:

  • Financial Services and Insurance
  • Energy, Utilities, Power, and Extractive Industries
  • Critical National Infrastructure Companies
  • Pharmaceuticals, Medical, Health
  • Consumer Goods, Electronics, Services
  • Manufacturing, Construction, Engineering
  • Retail, eCommerce
  • Gaming, Gambling
  • Transport, Logistics, Automotive
  • Government, Intergovernment

By Region

  • UK – circa 45%
  • Across Europe – circa 45%
  • Rest of World – circa 10%

Venue and Accommodation

Oakley Court
Windsor Road, Water Oakley, Windsor, Berkshire, SL4 5UR, UK
www.oakleycourt.co.uk

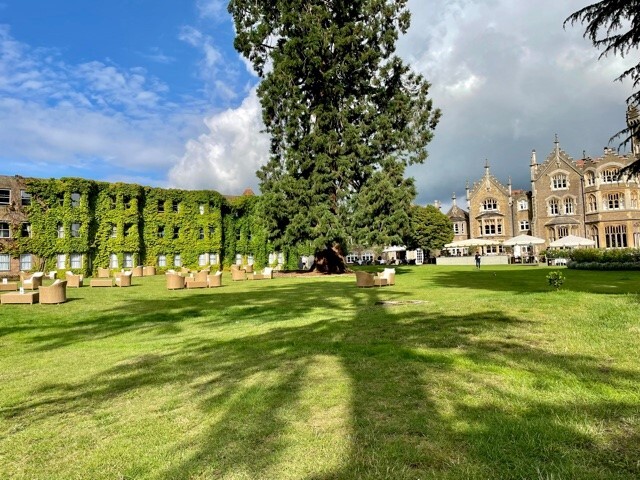
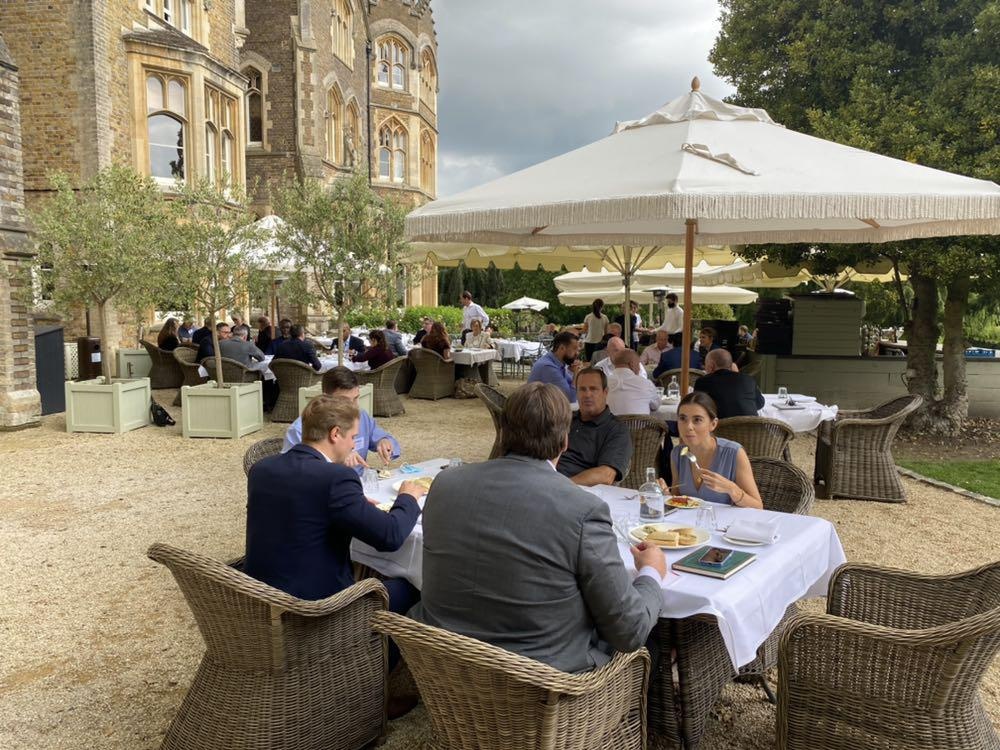
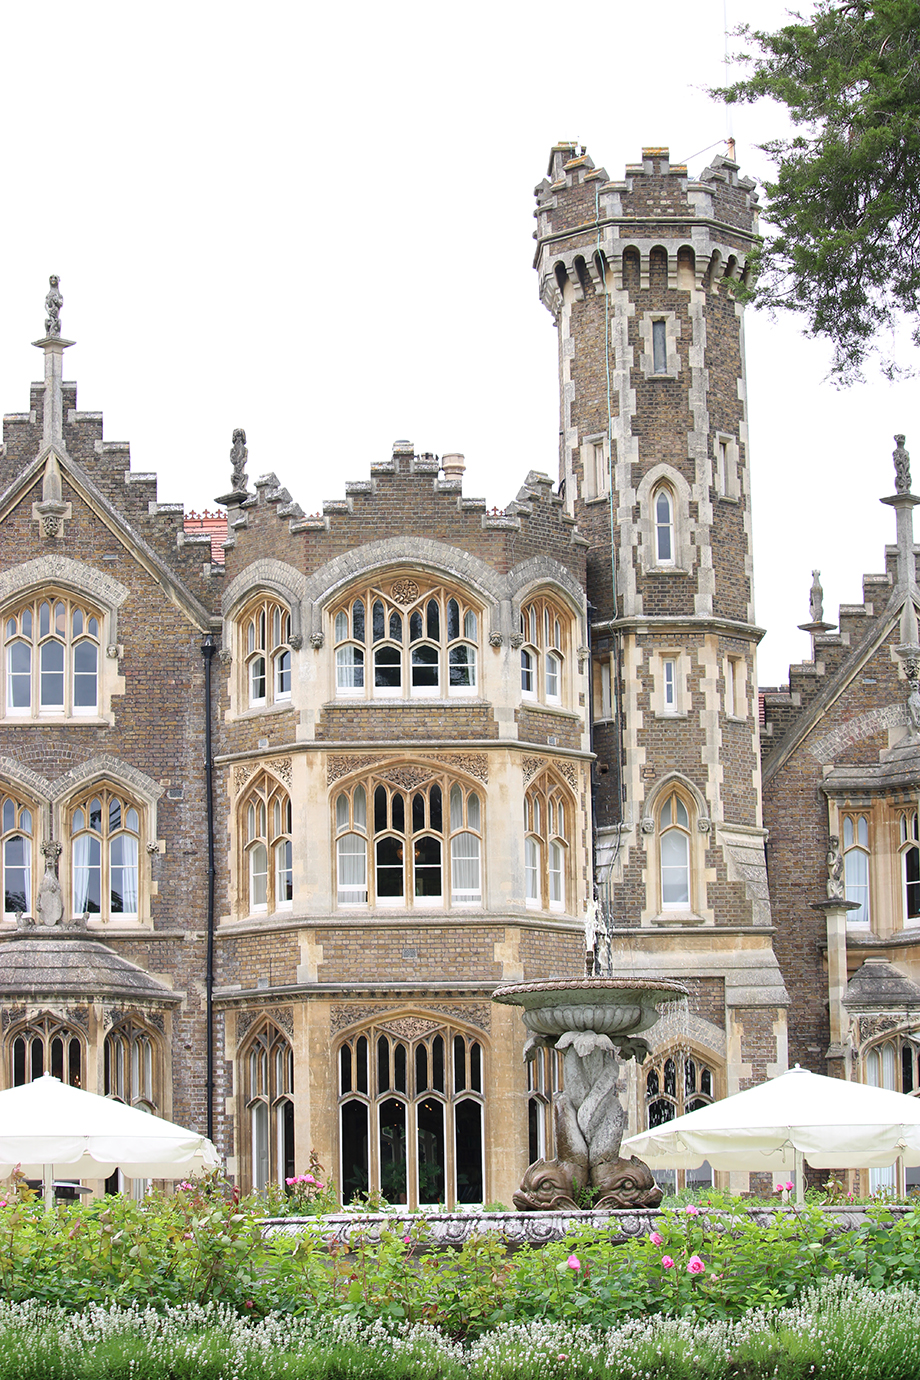
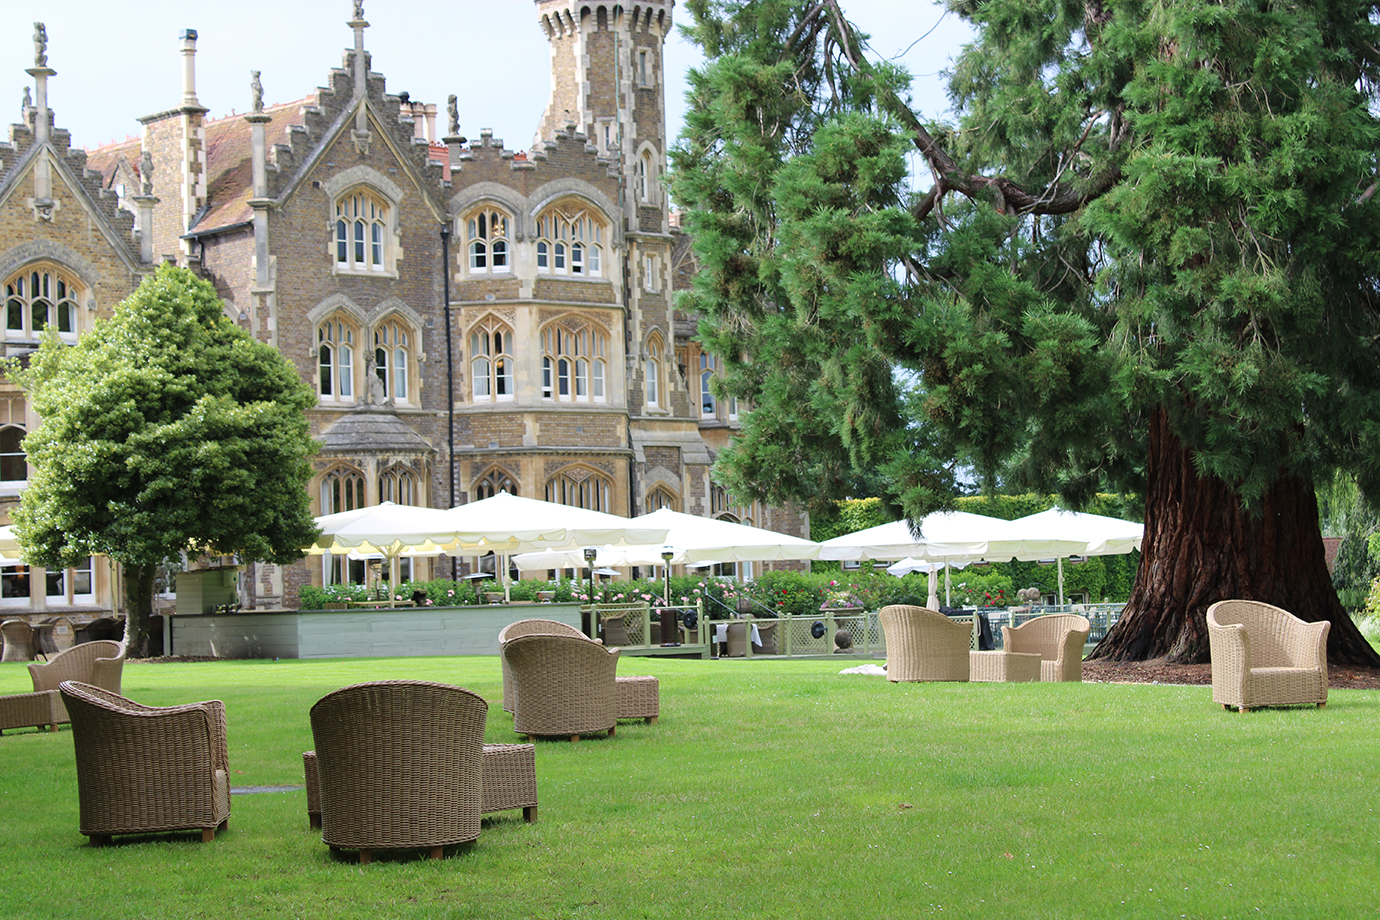
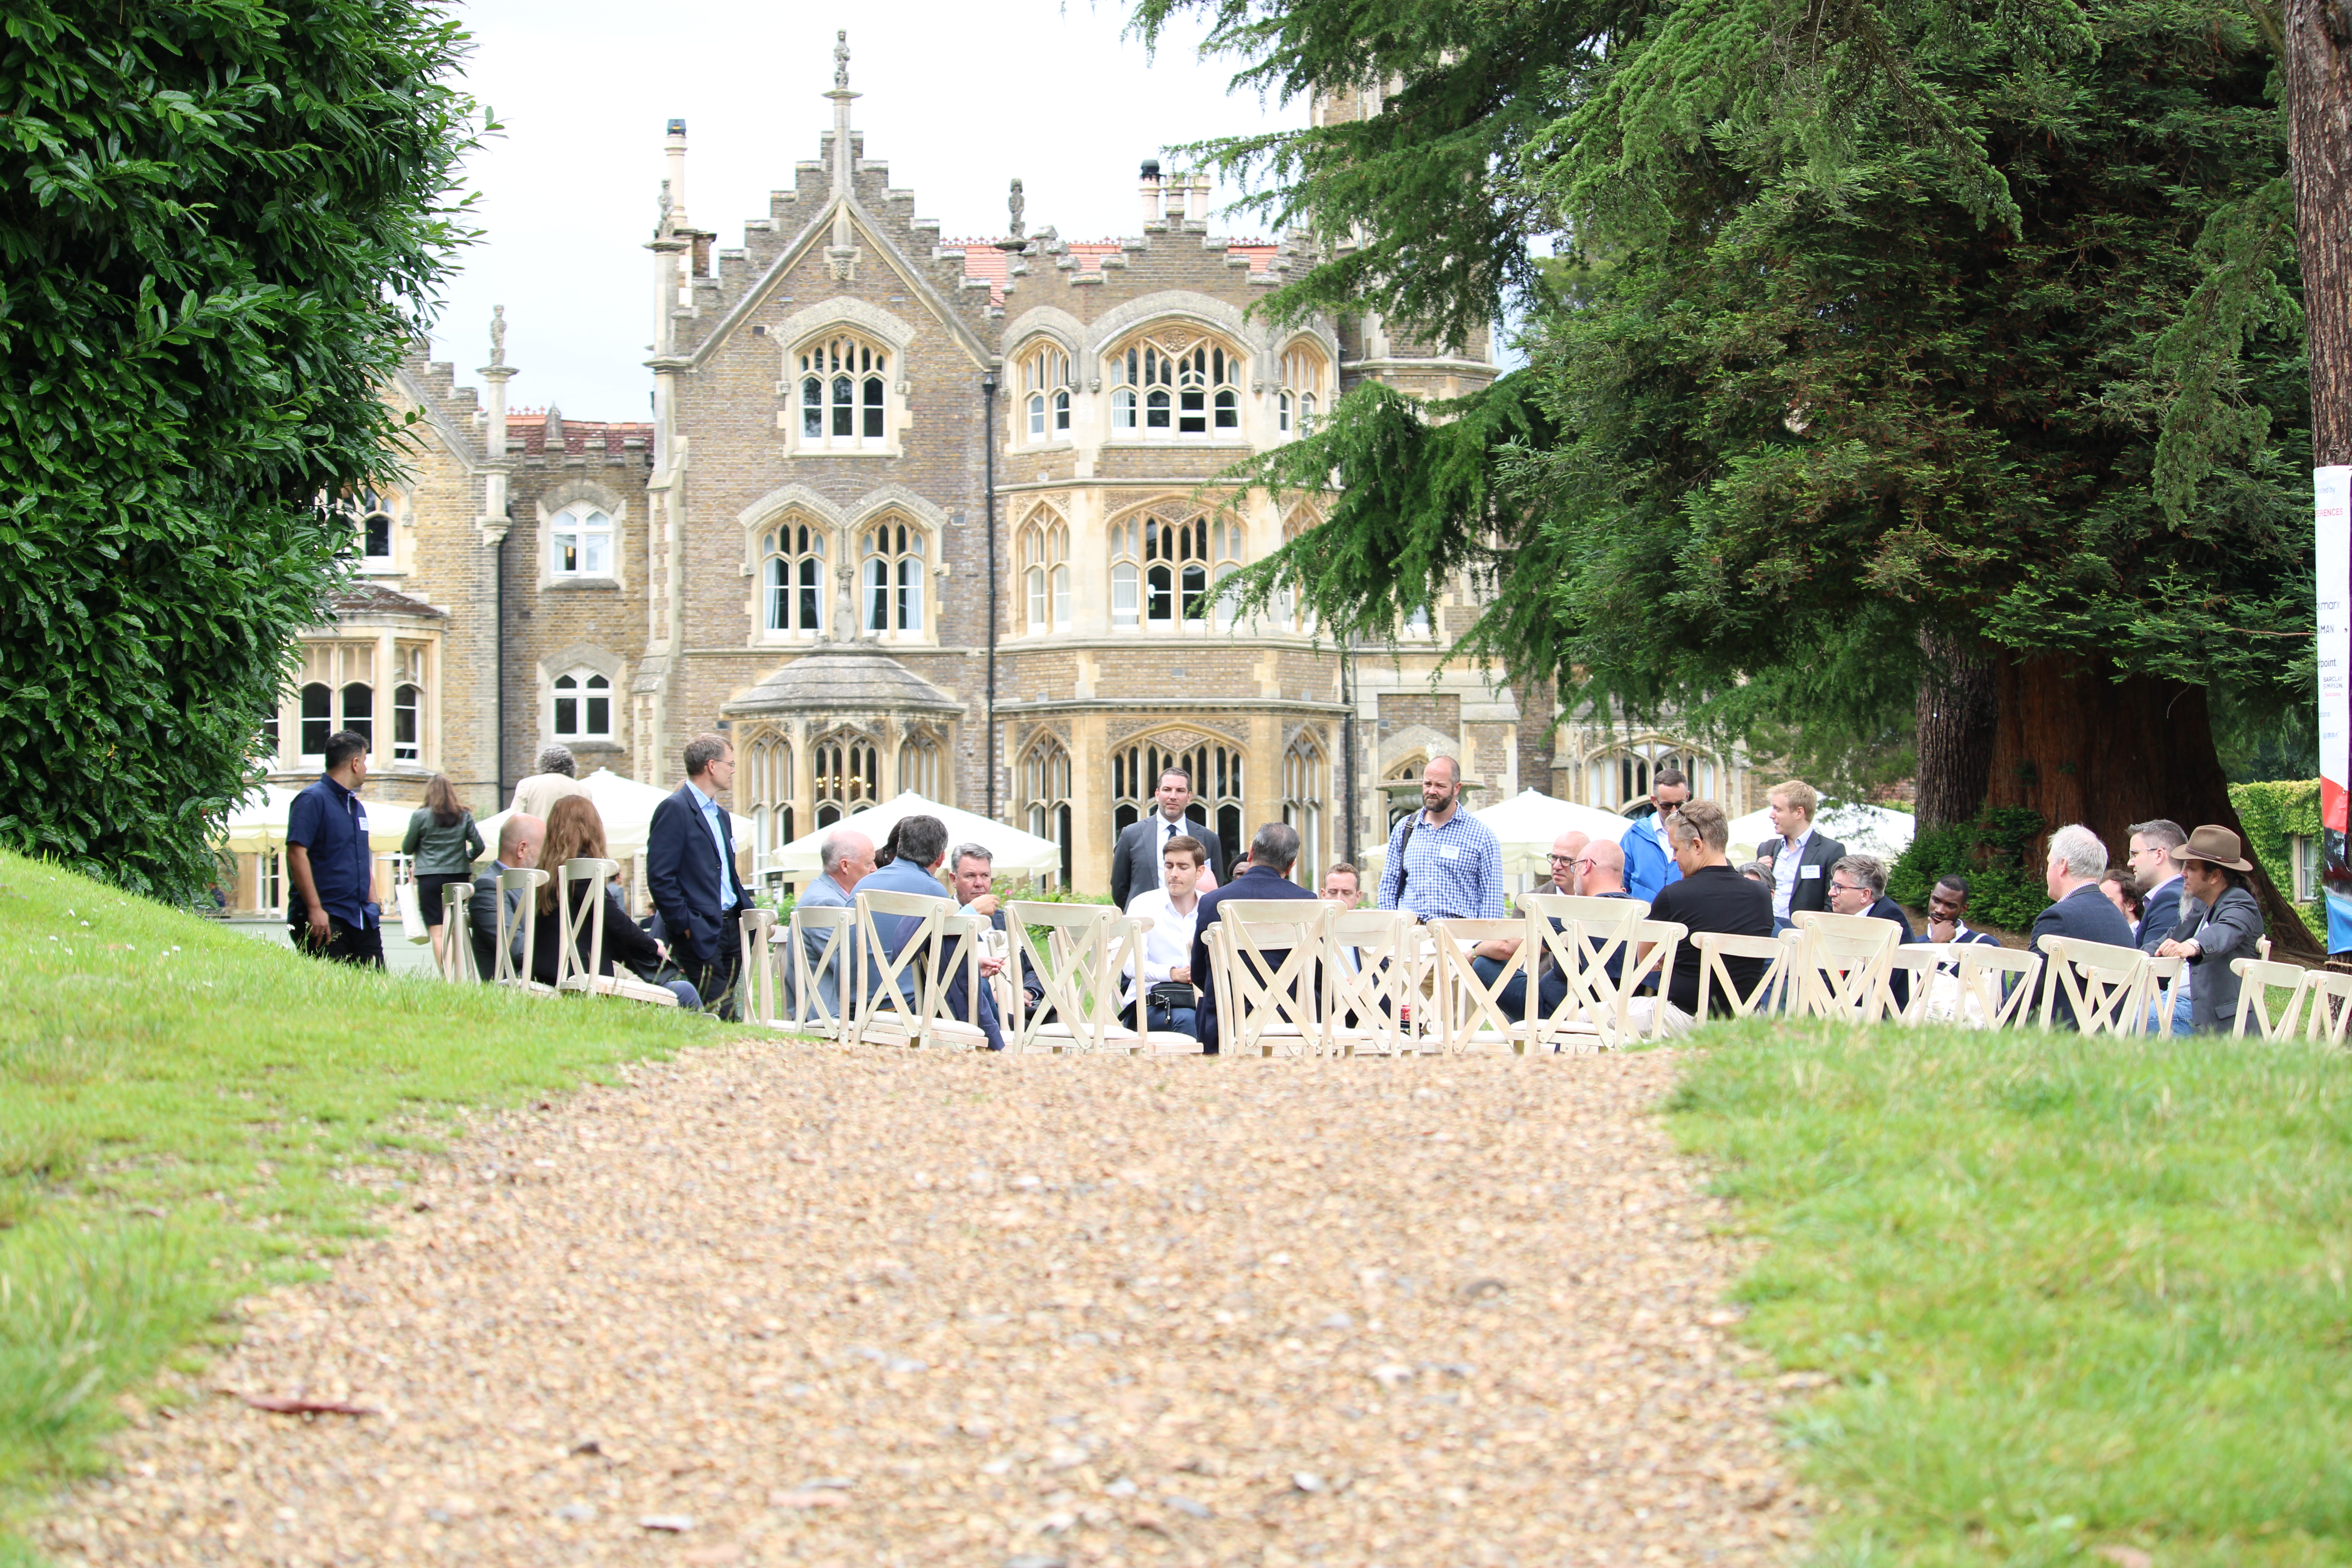
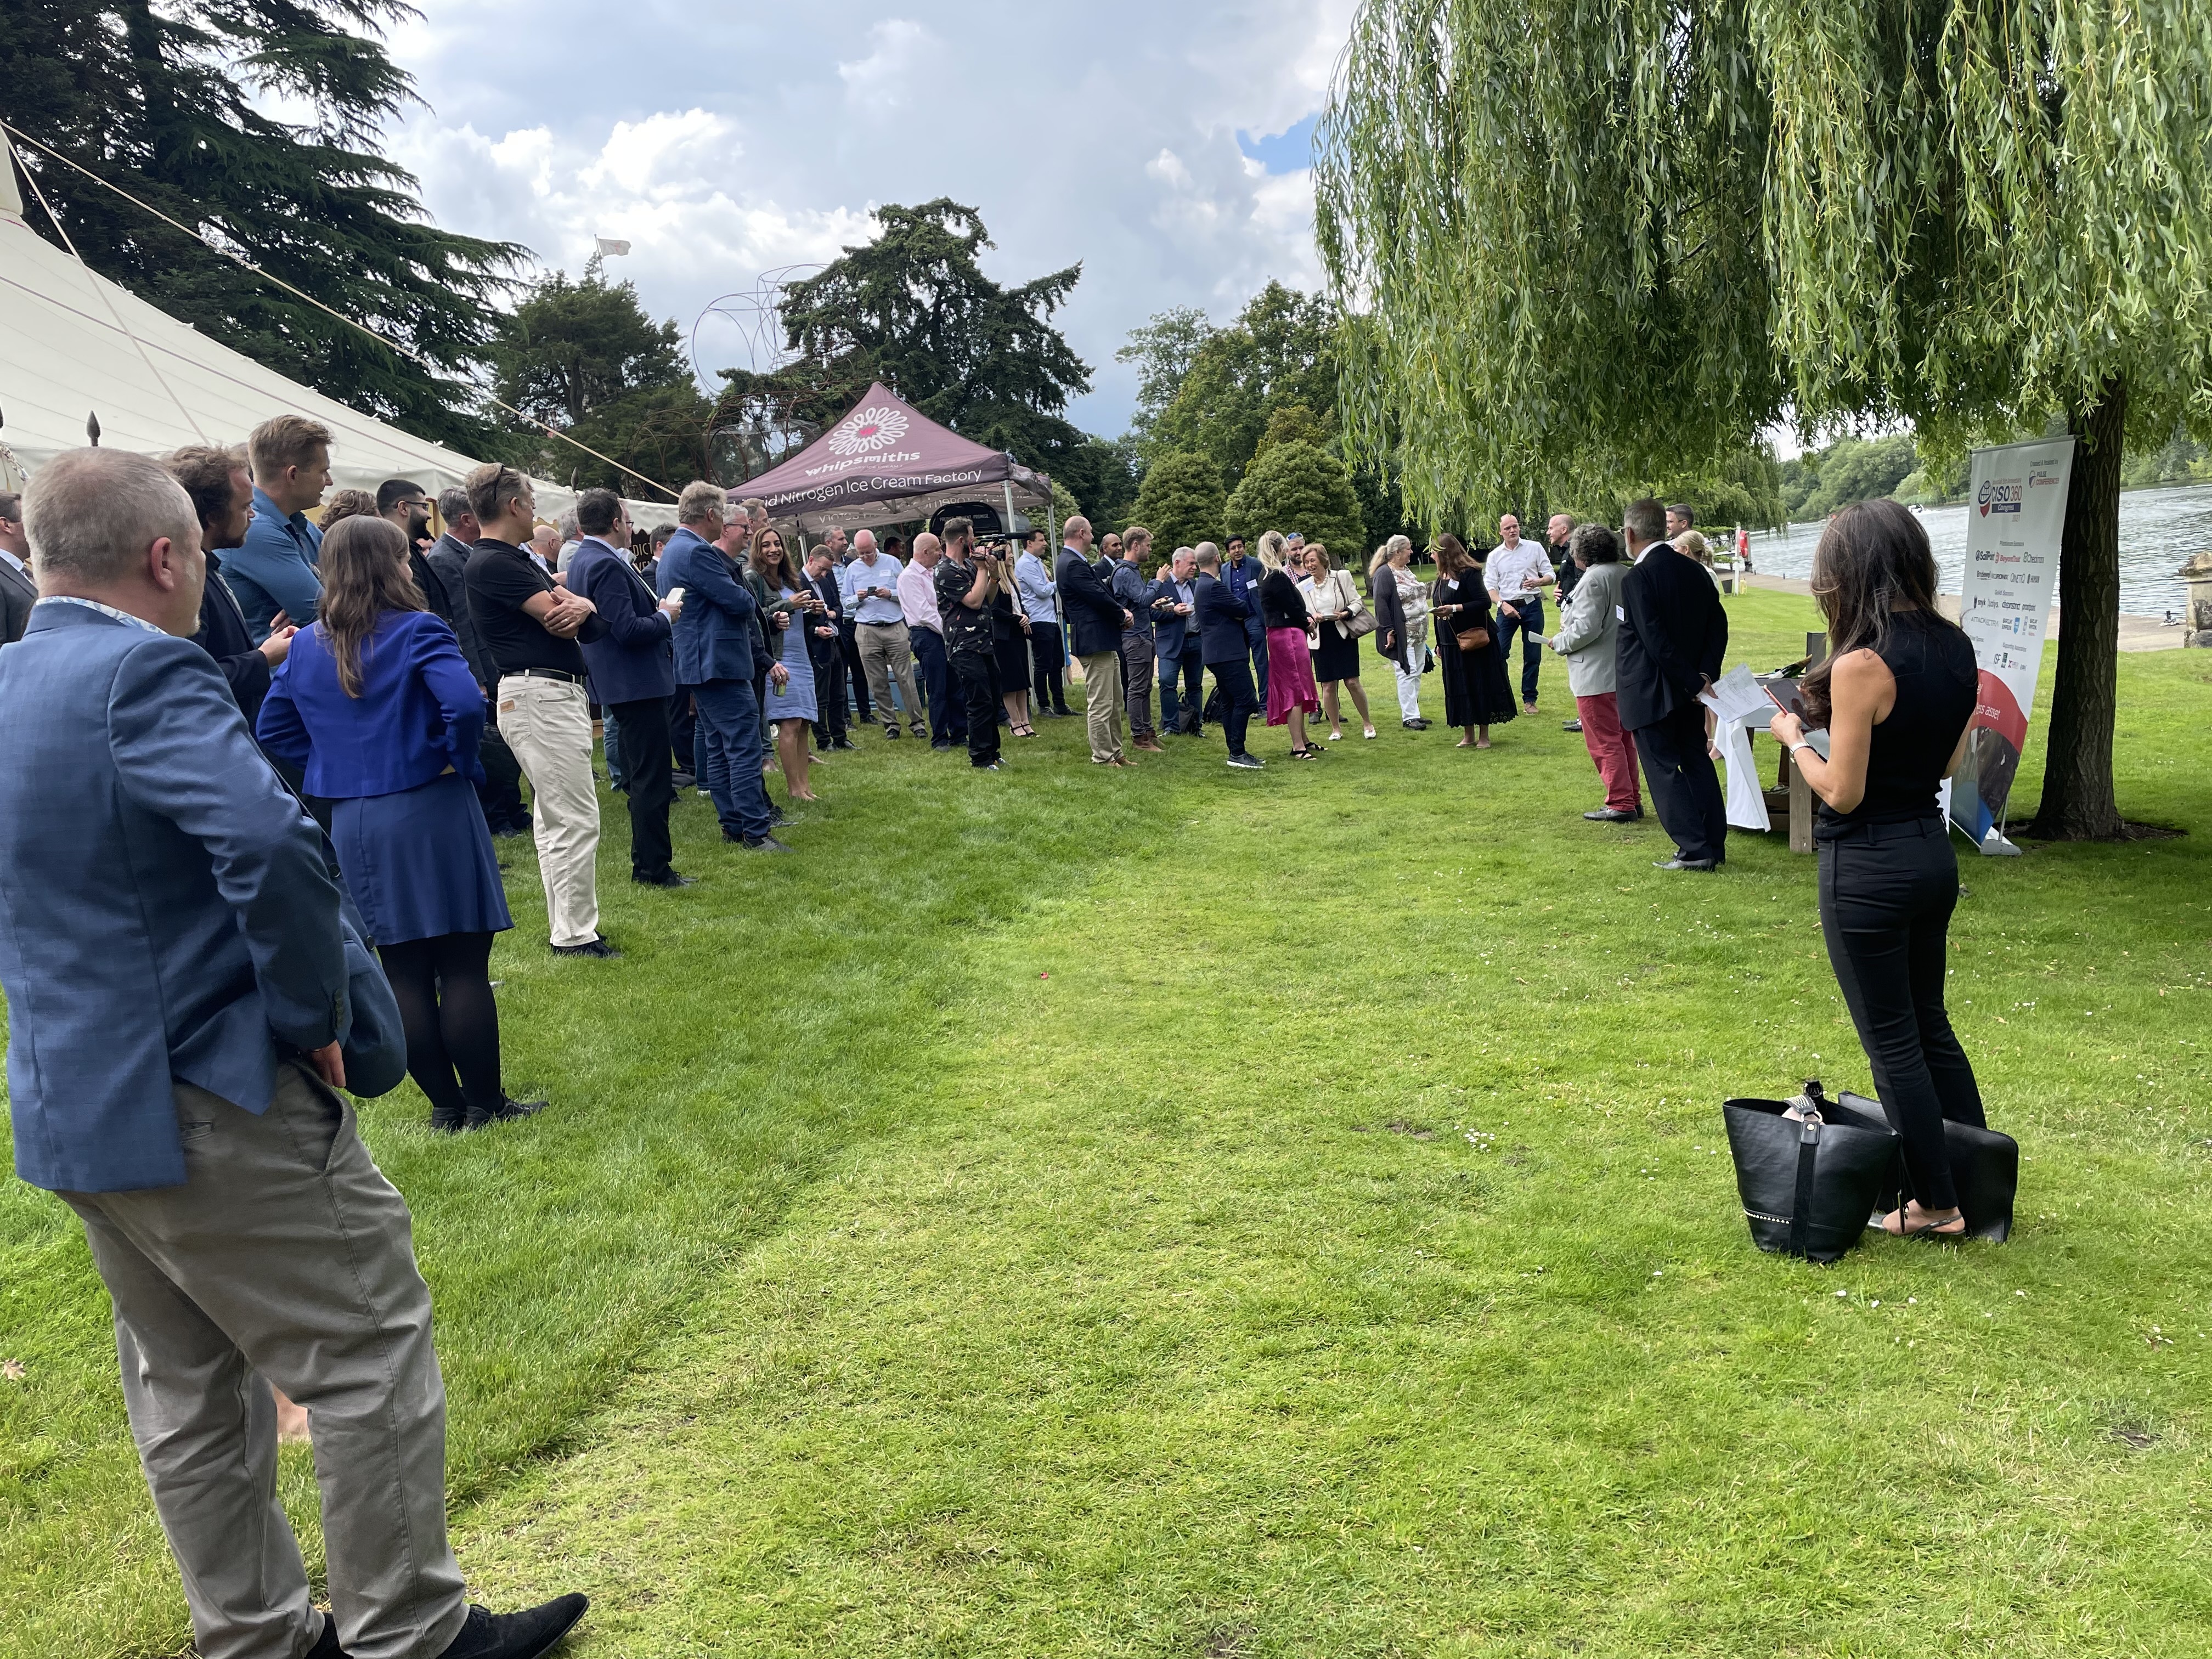
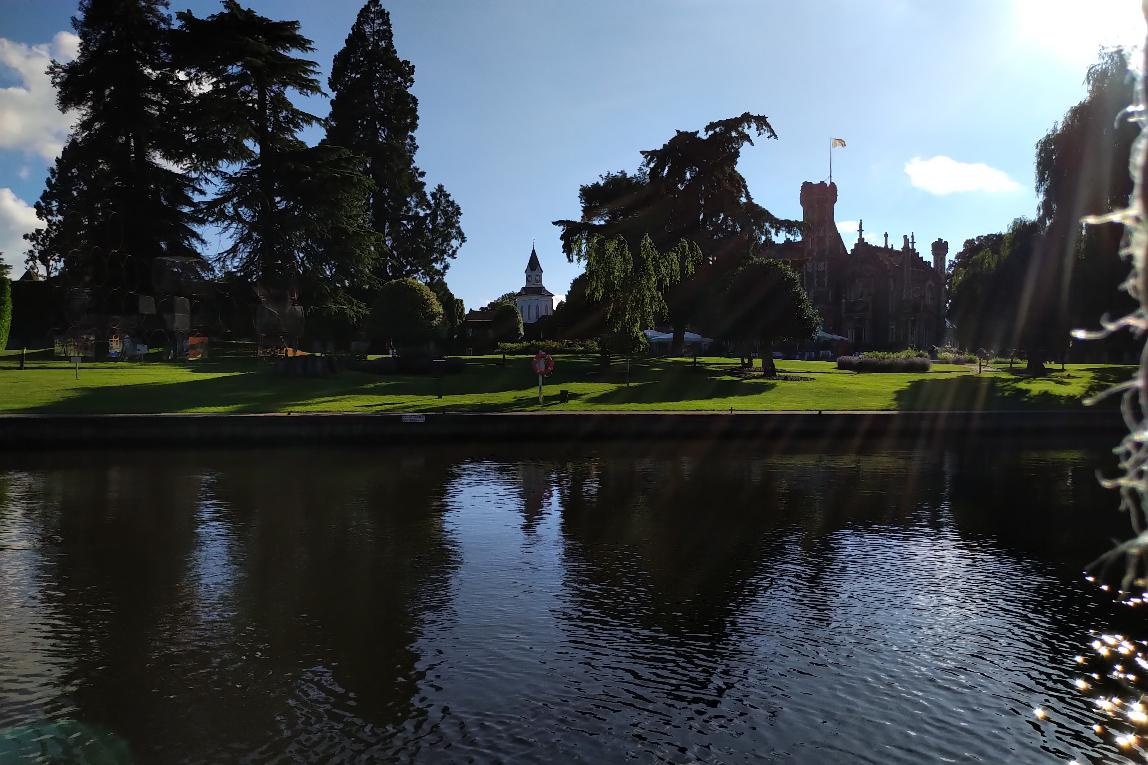
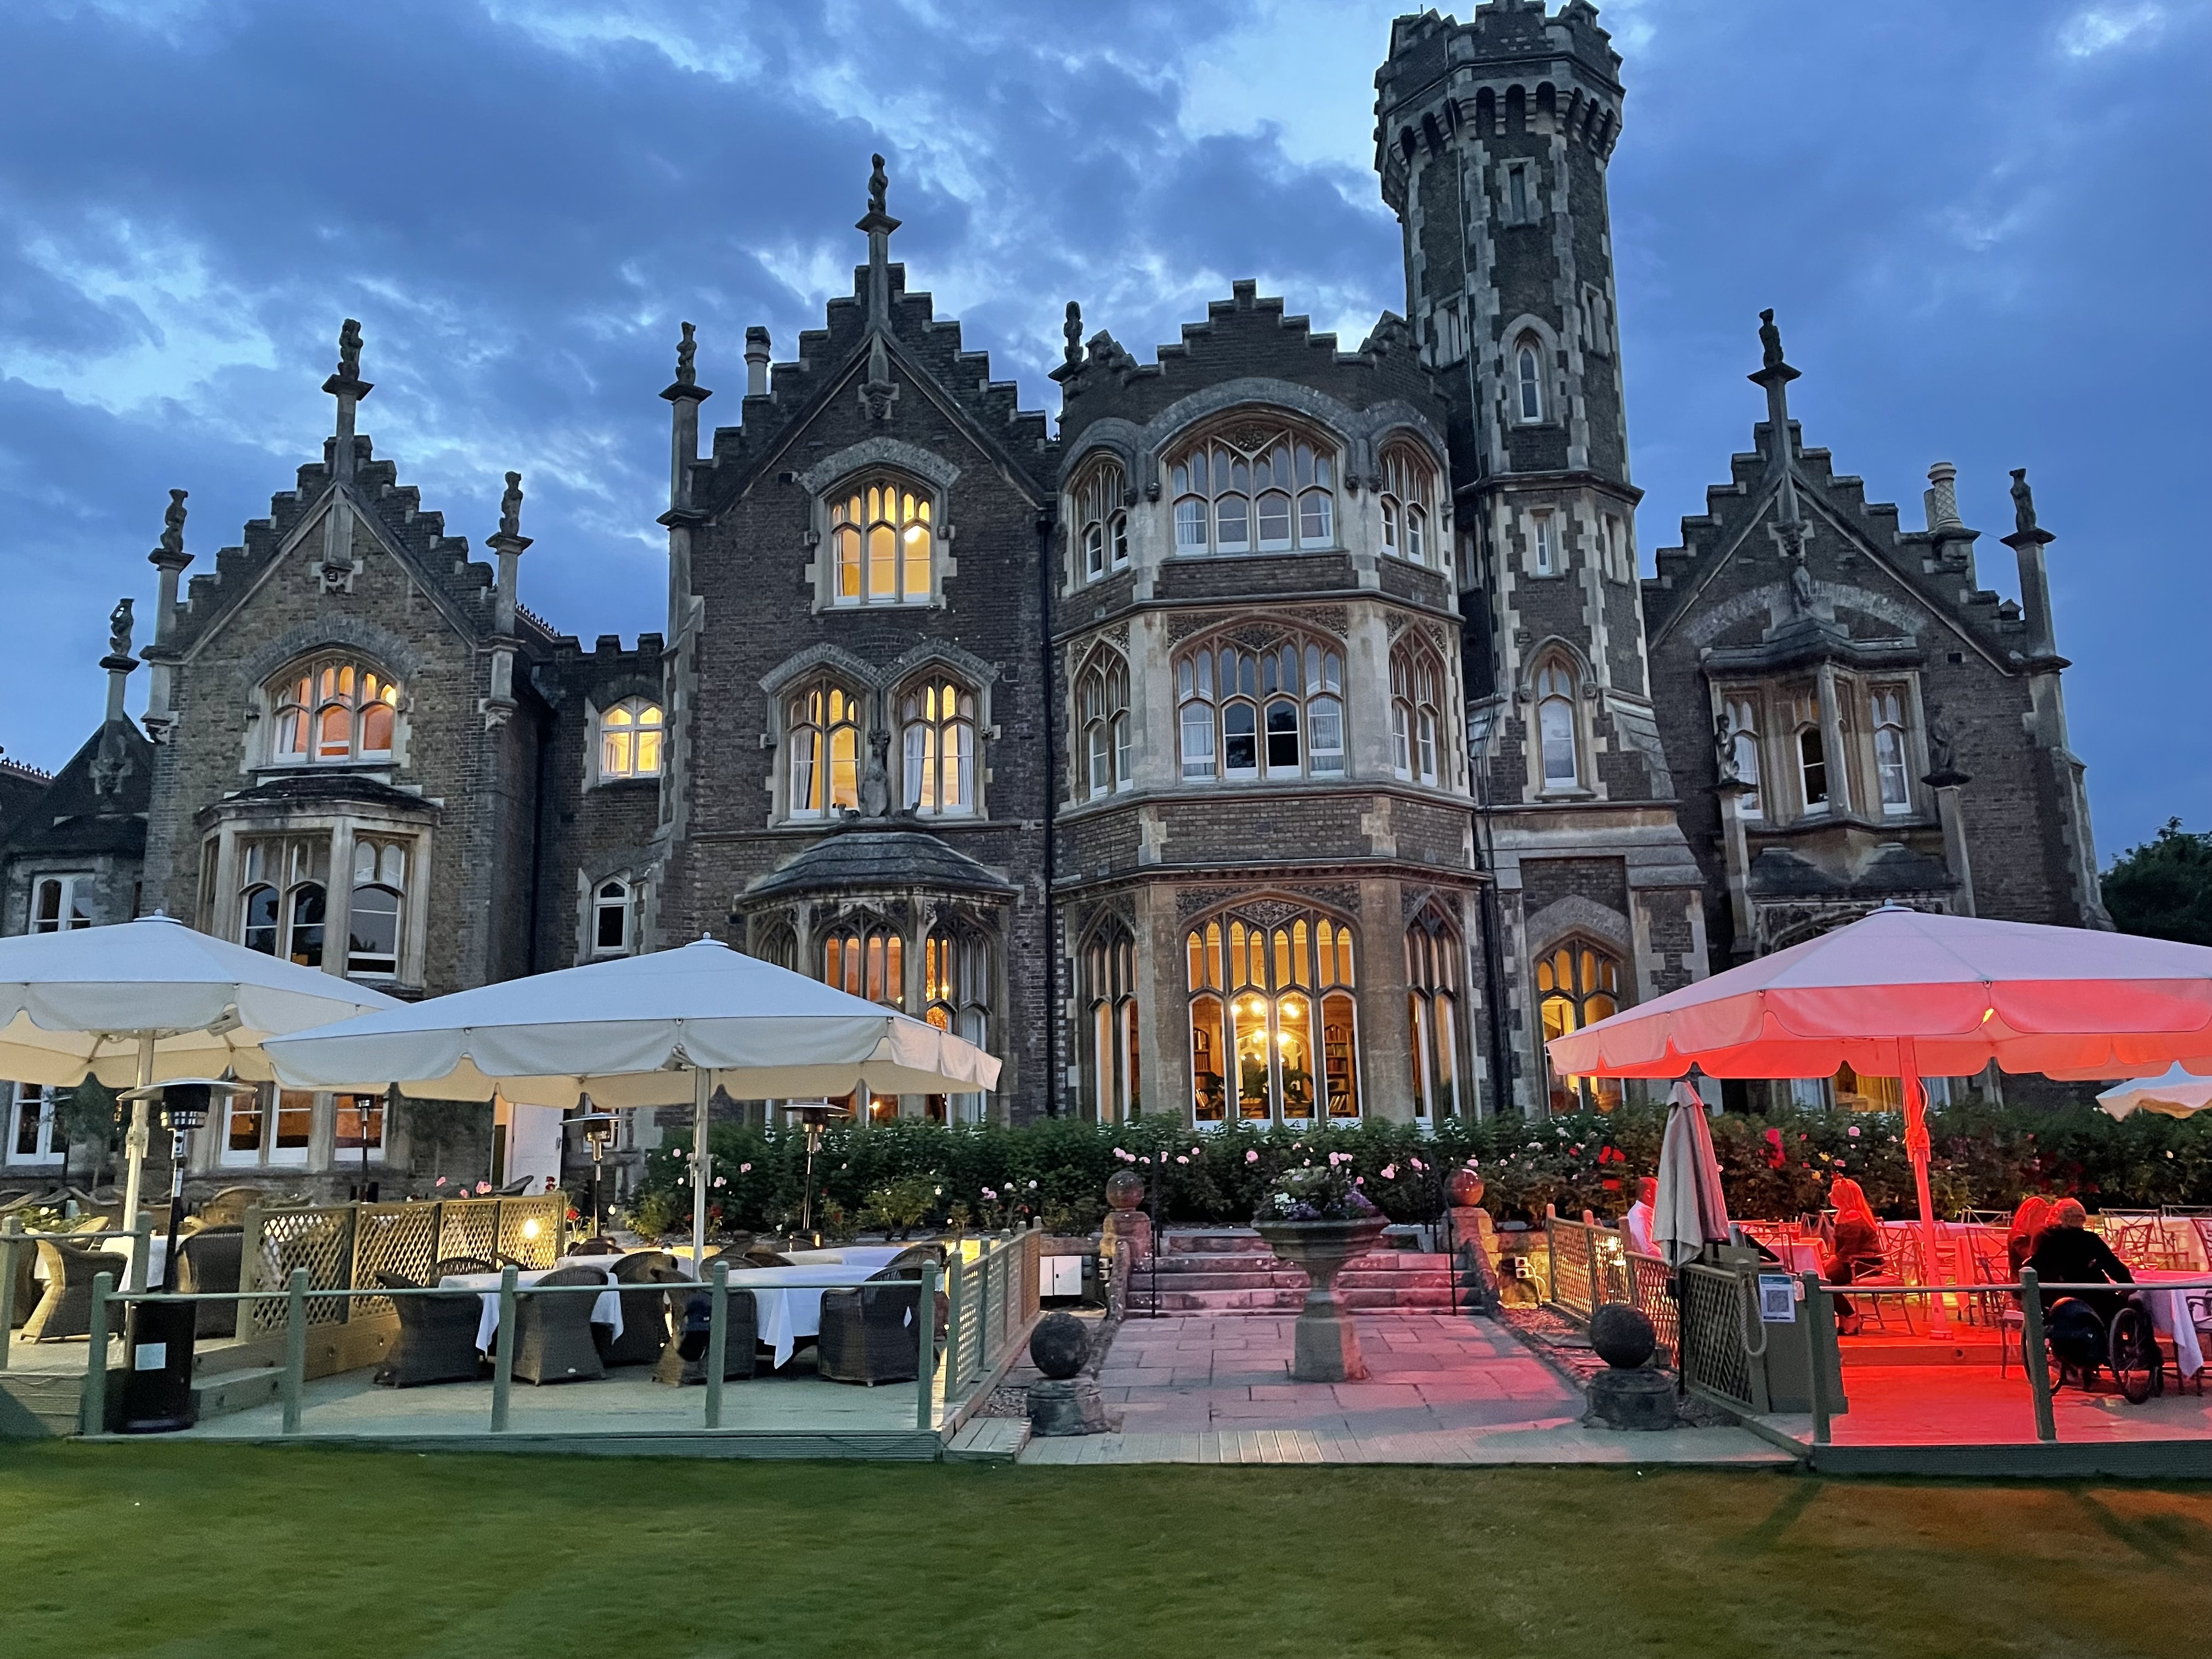
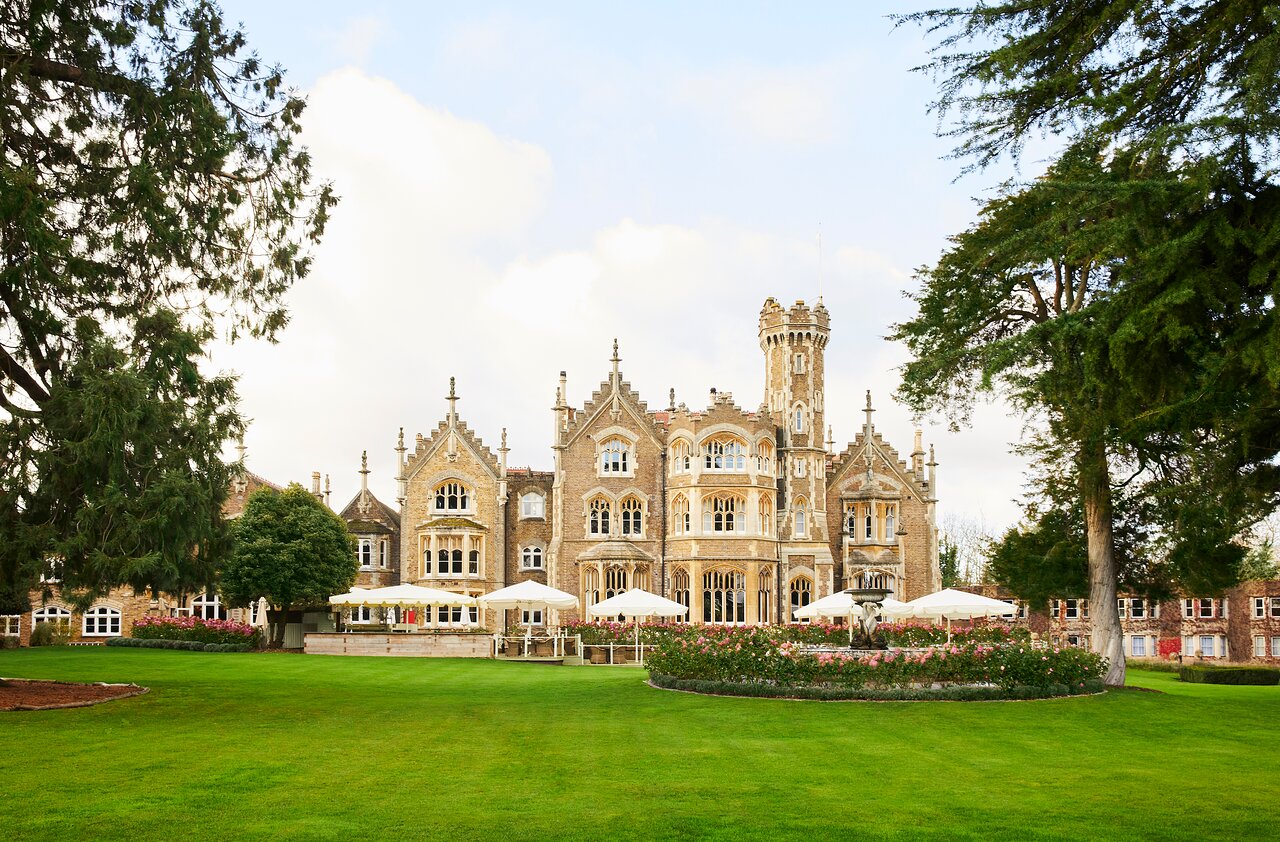
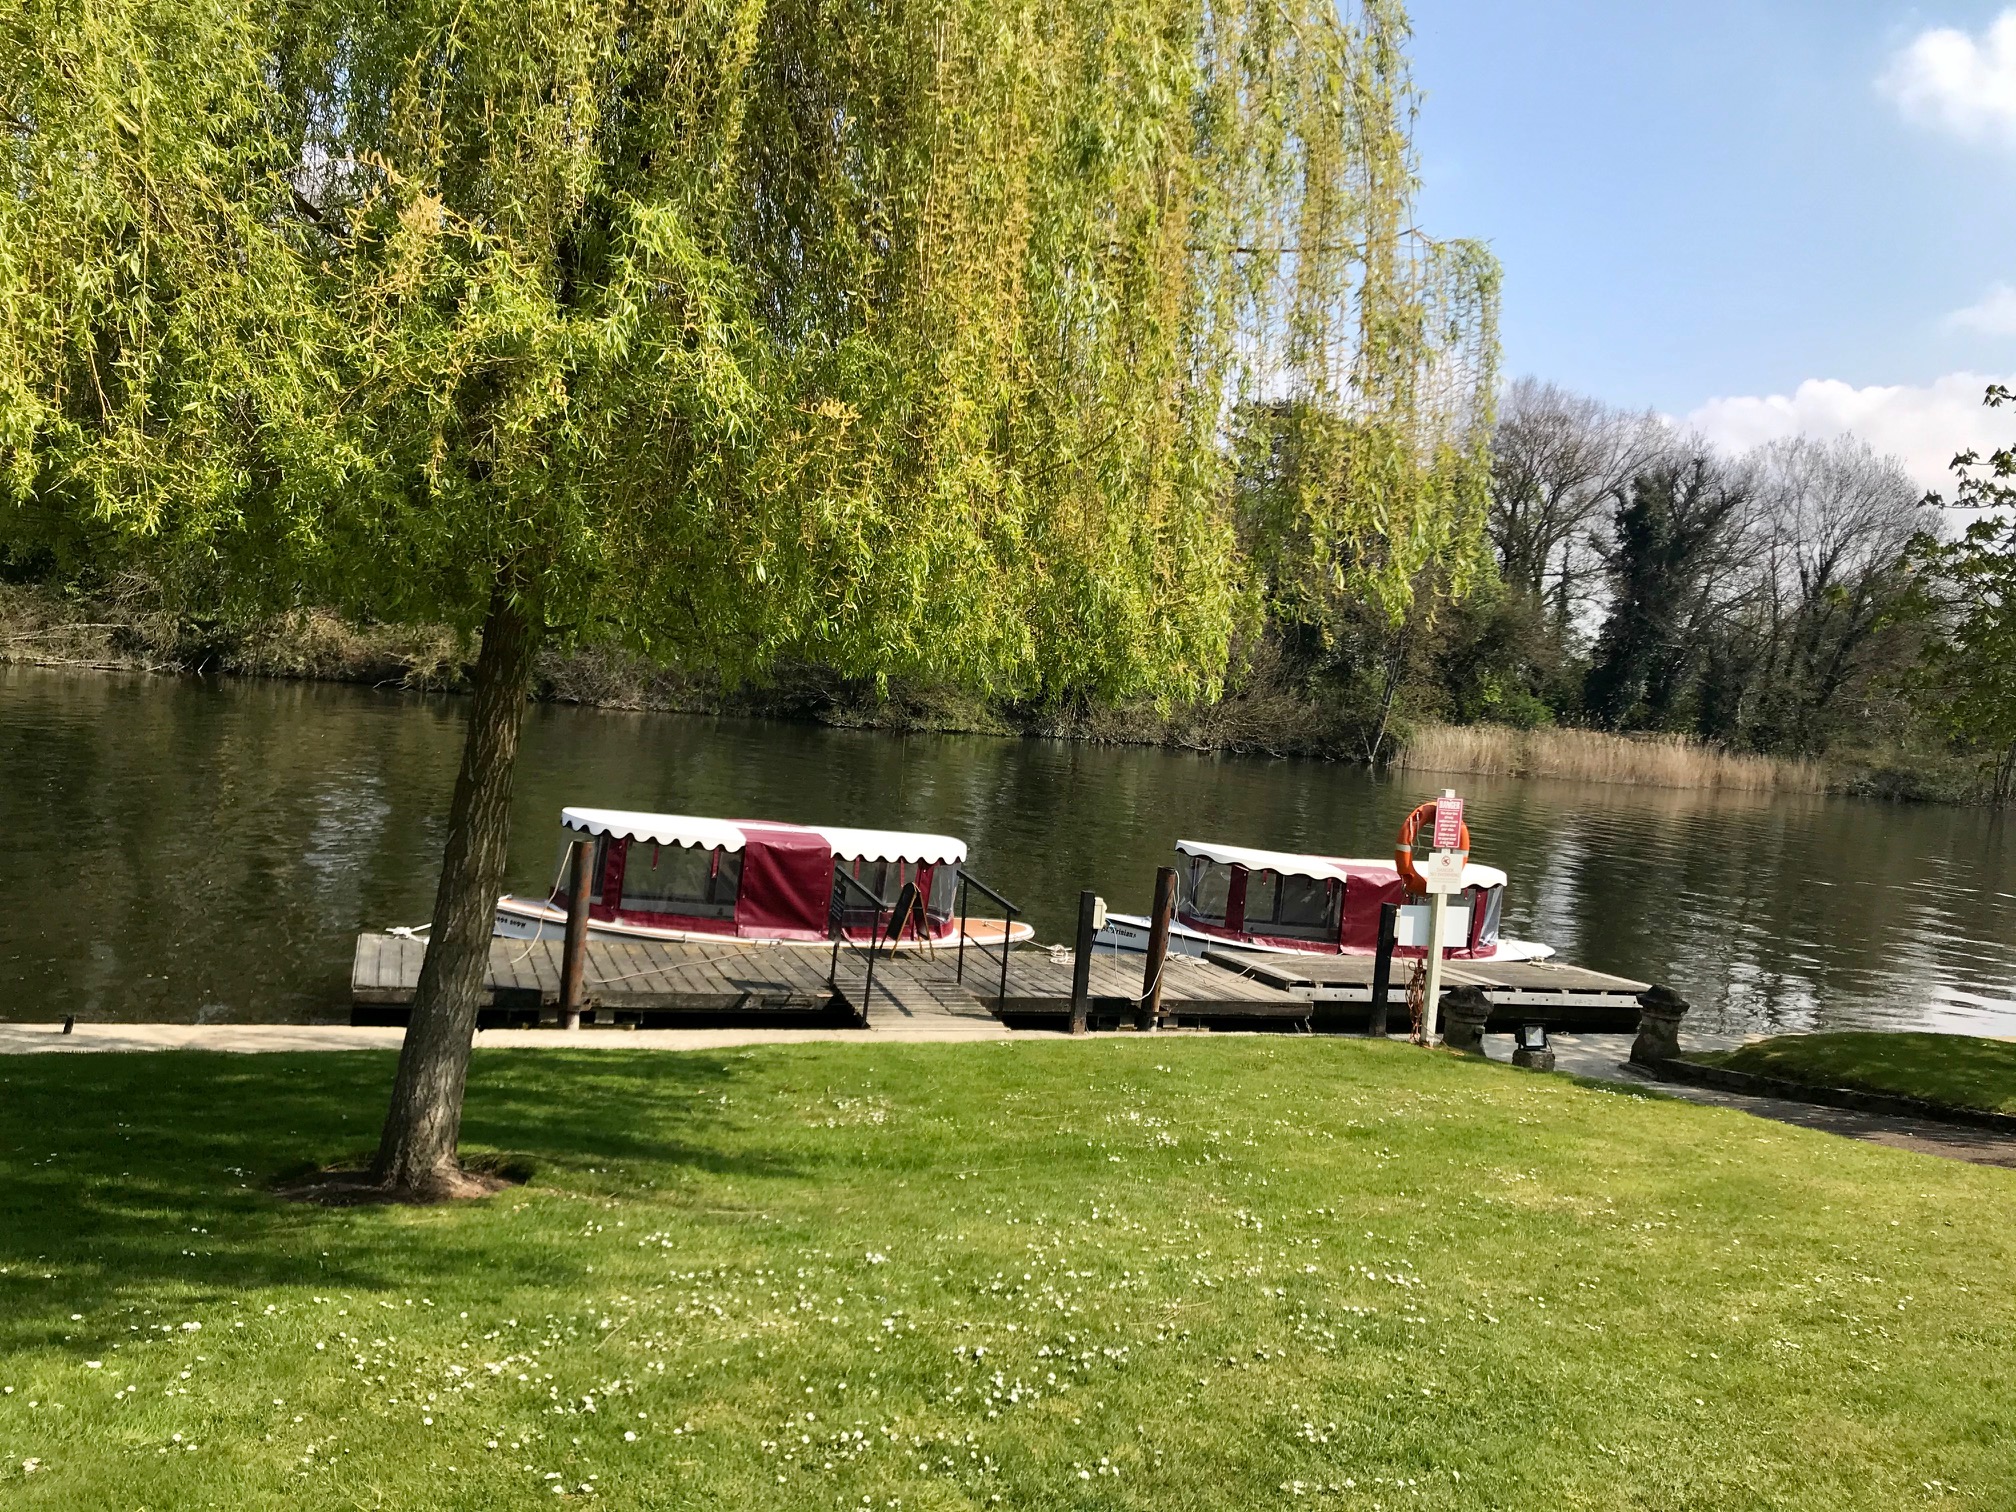
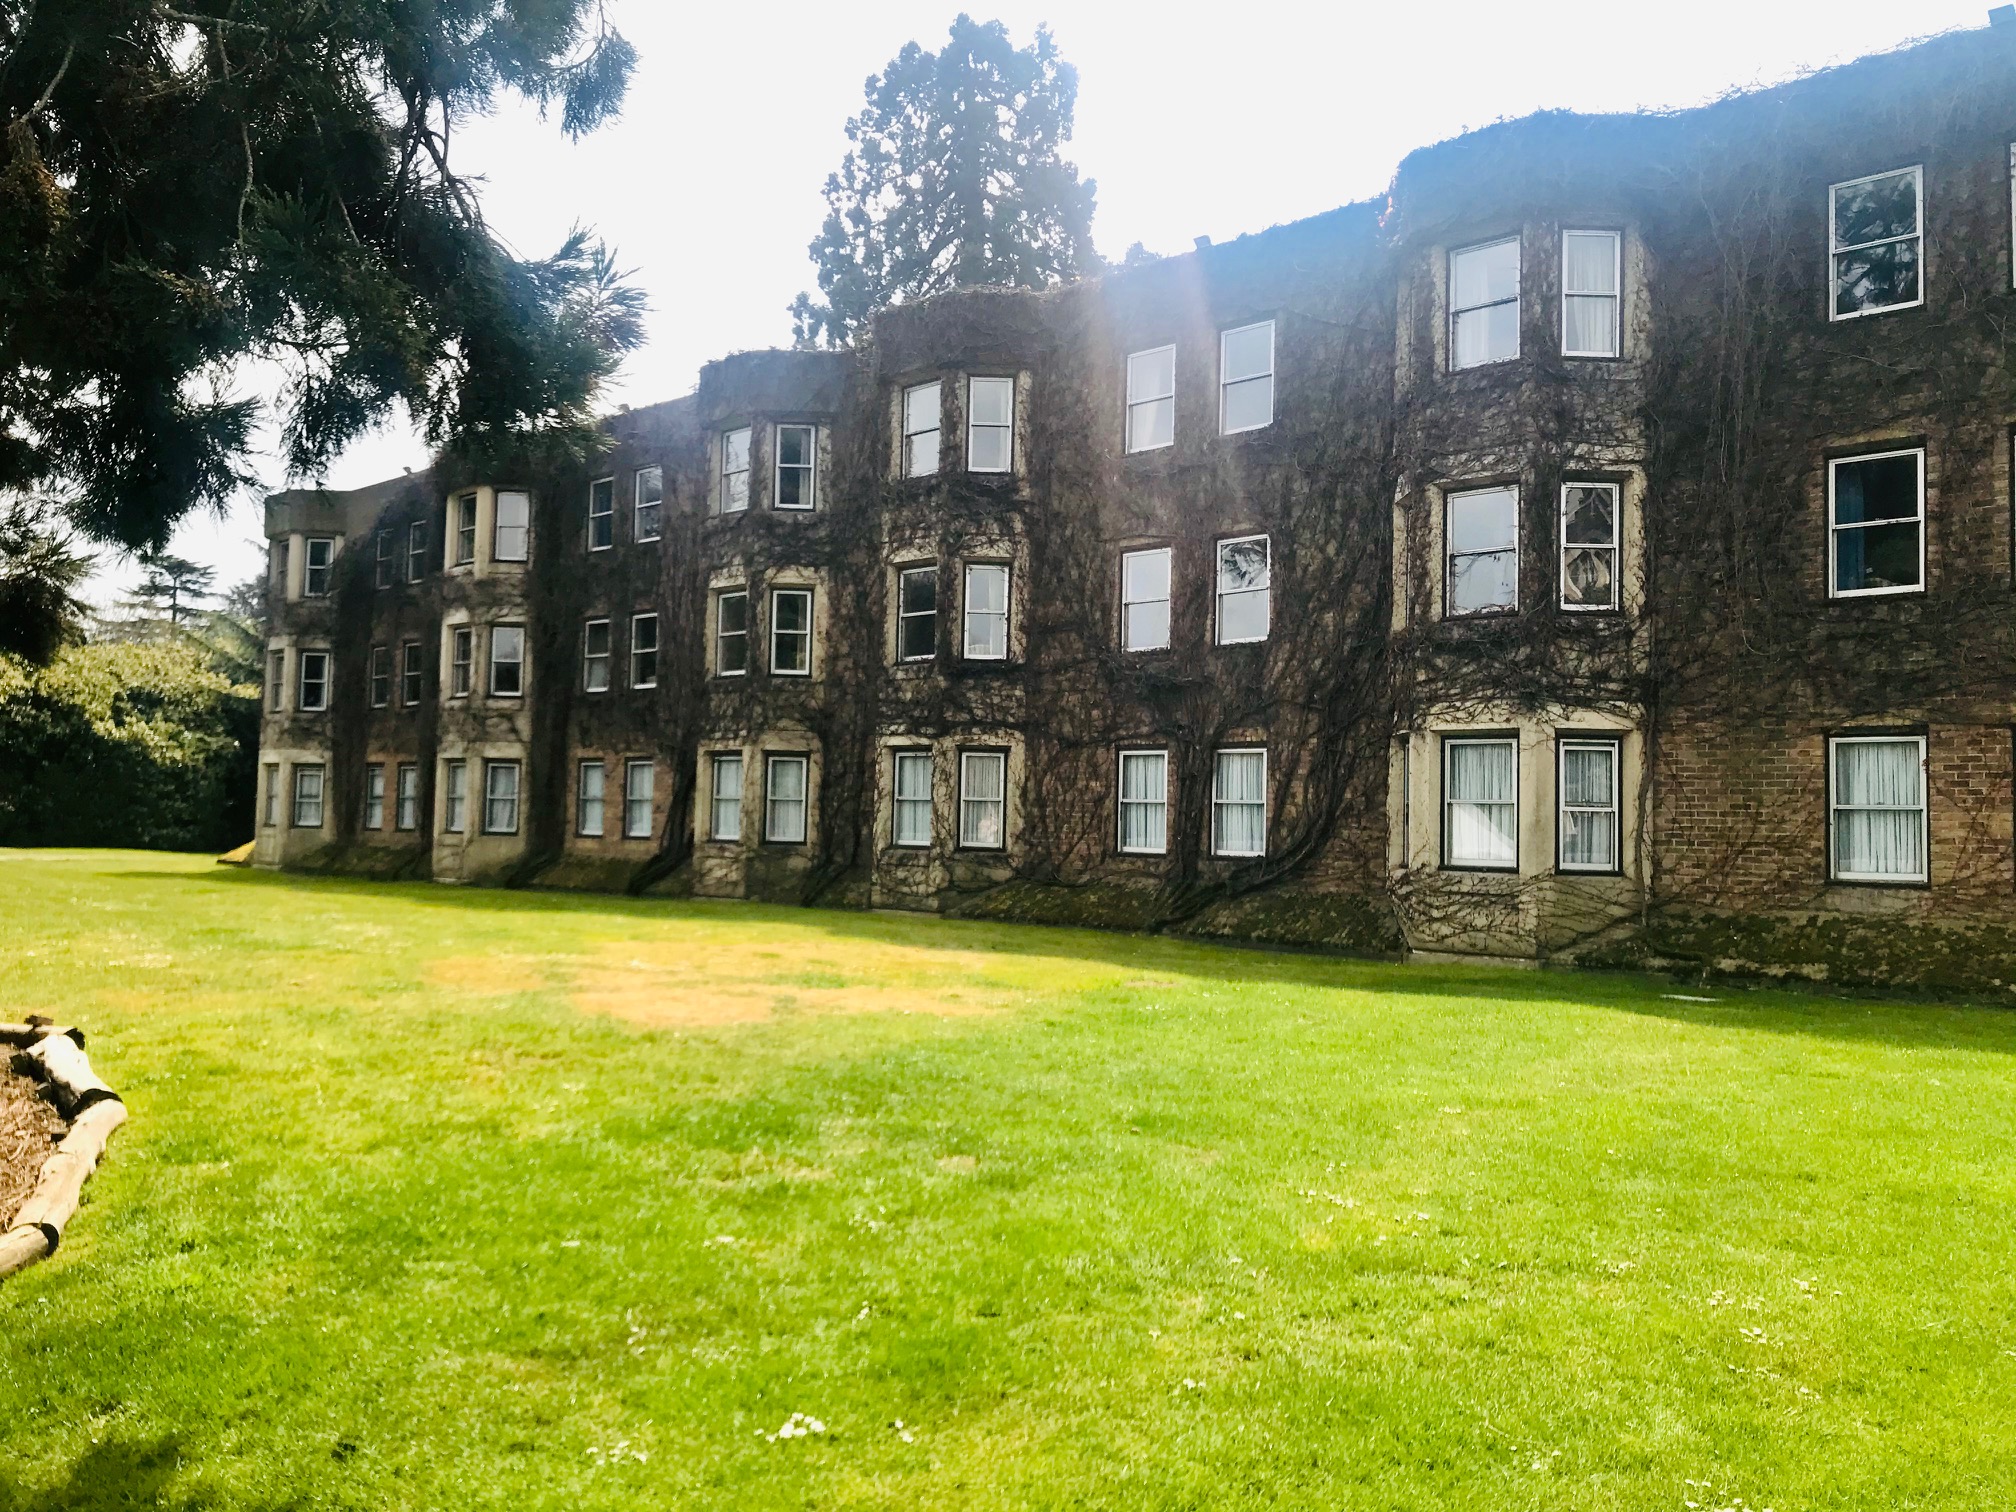
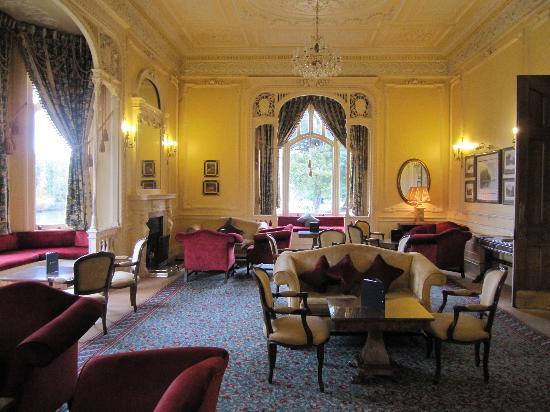
The 5th CISO 360 Congress will be hosted at Oakley Court, a Victorian Gothic Mansion House recently renovated and set in 35 acres overlooking the River Thames, just 10 minutes drive from Windsor in the county of Berkshire. Oakley Court mixes original character with modern luxury and the location has a rich cultural history and has been the setting of many films. It was the castle in The Rocky Horror Picture Show. For those driving to the venue, there is plenty of complimentary parking space available.

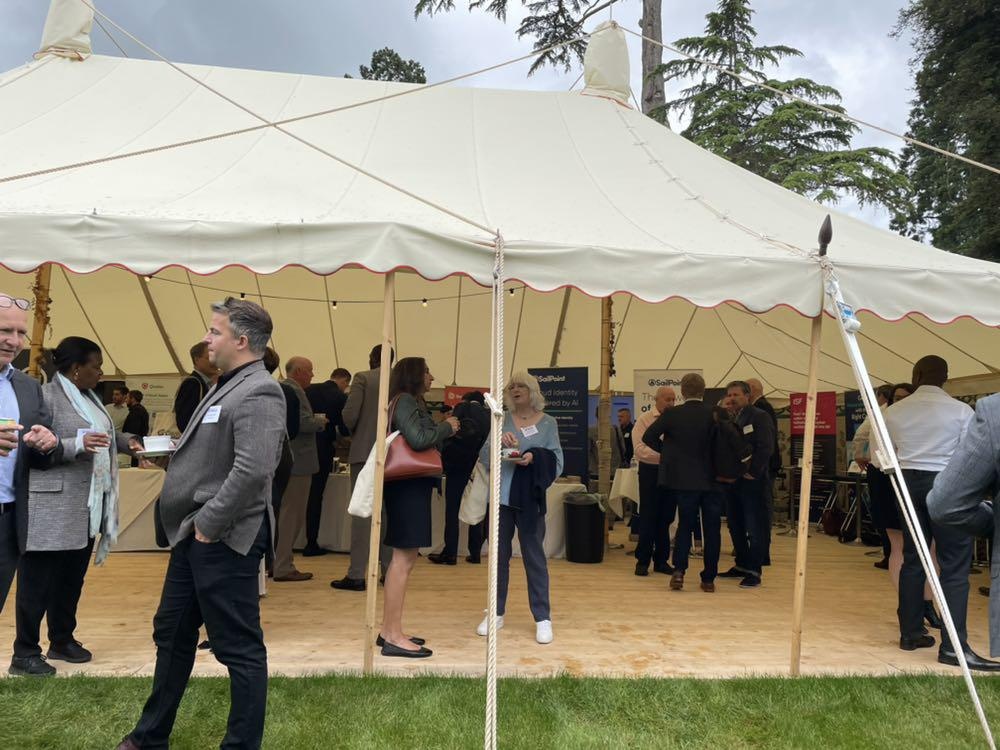
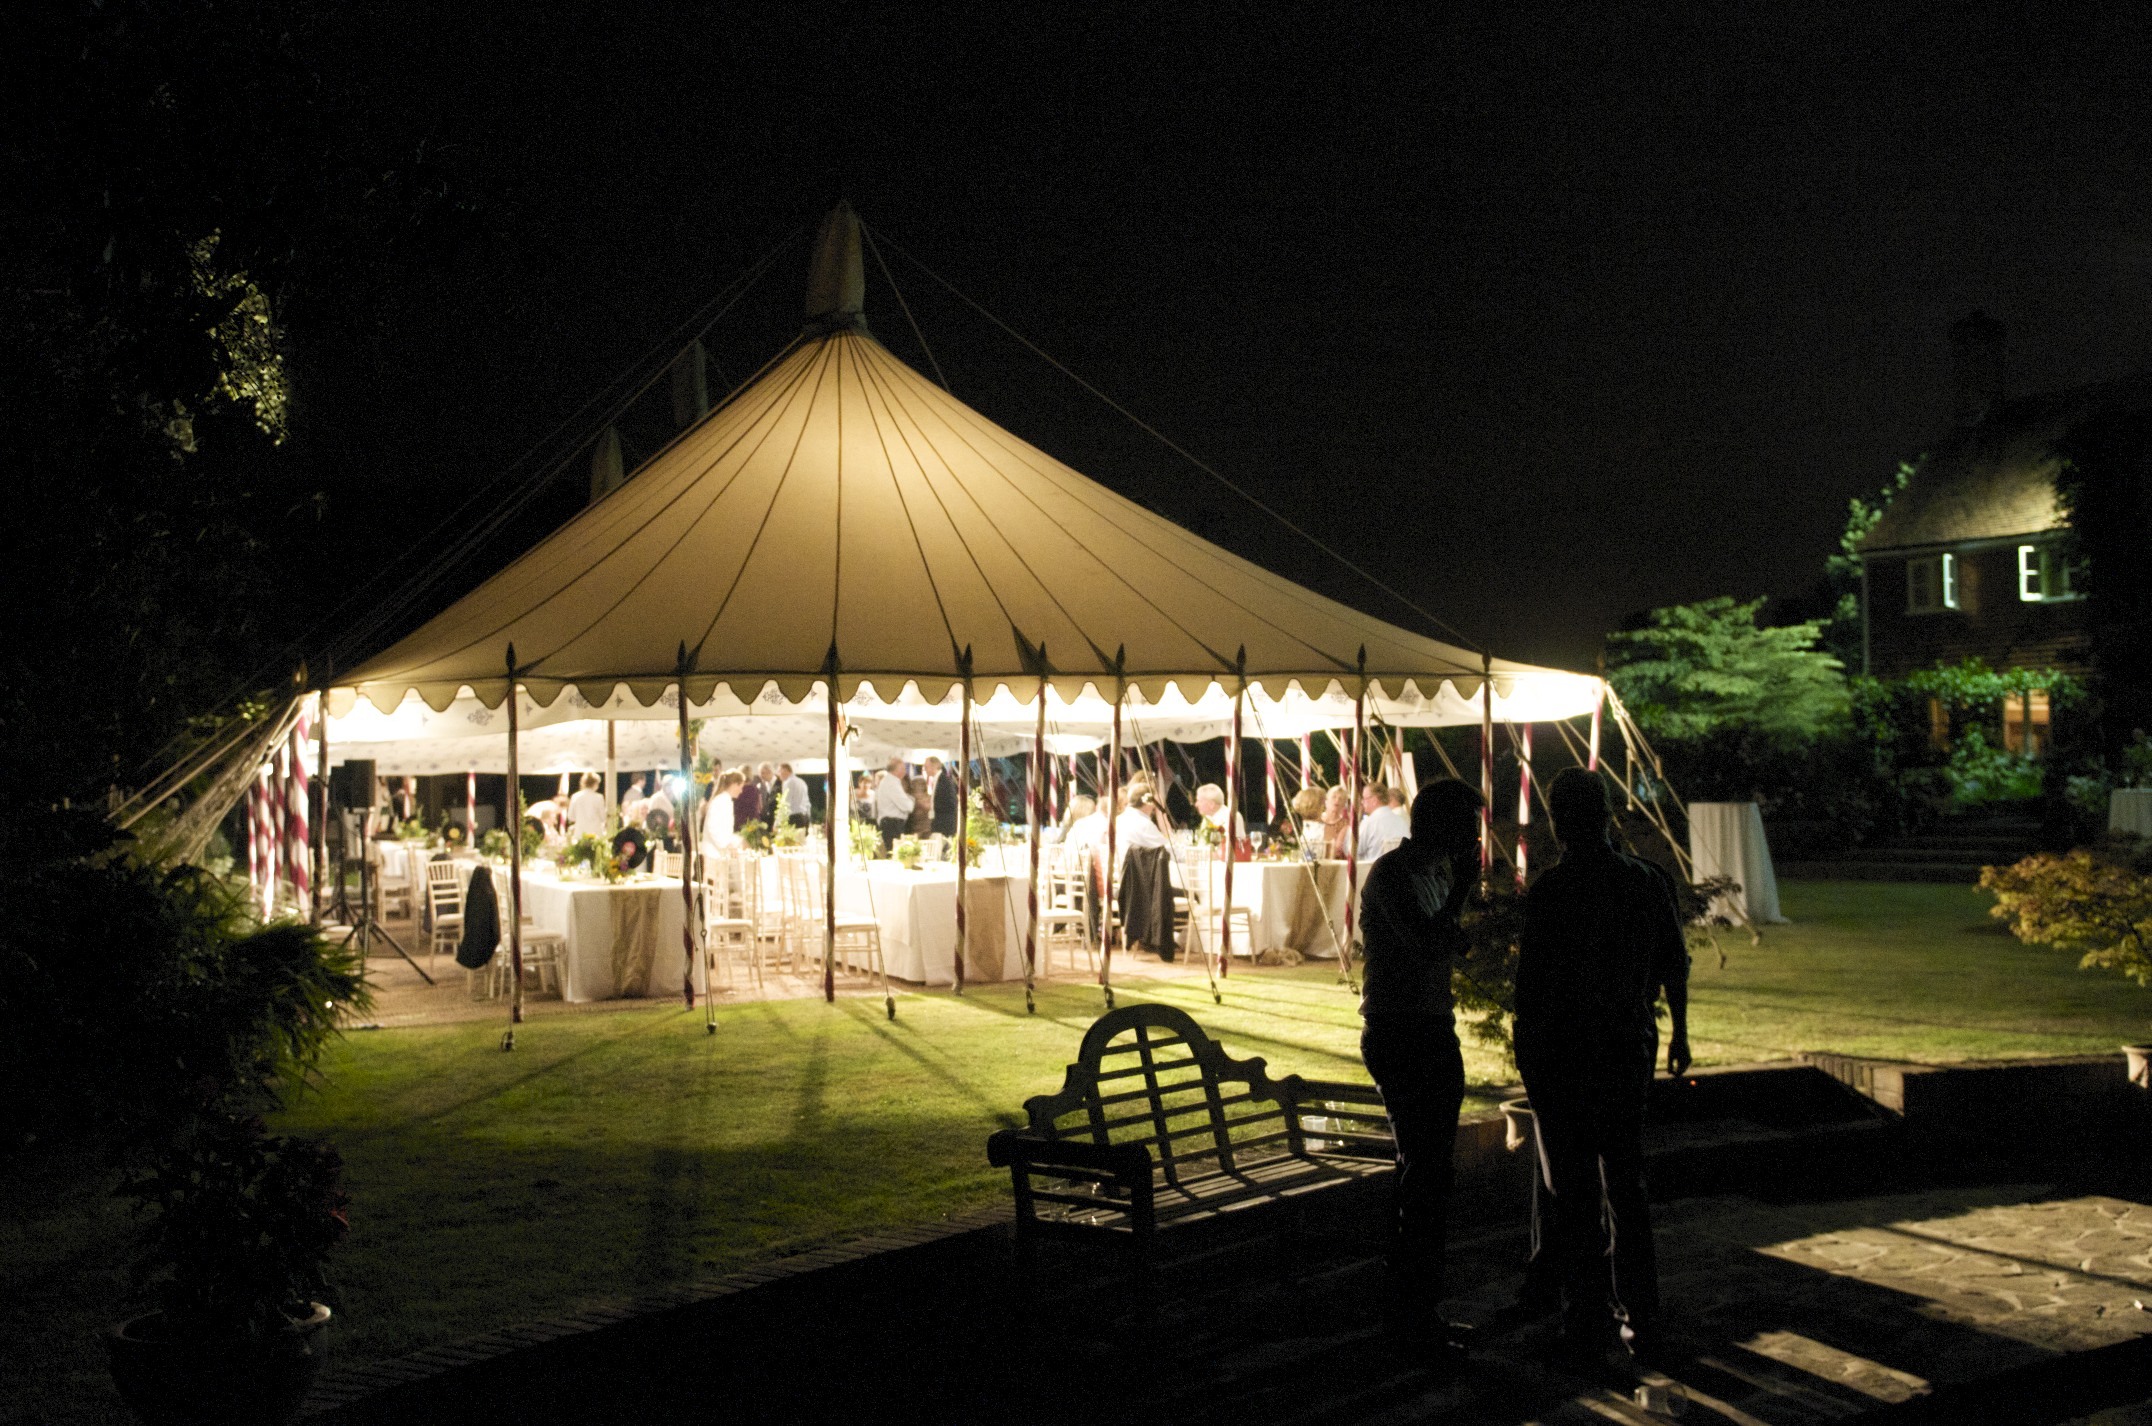
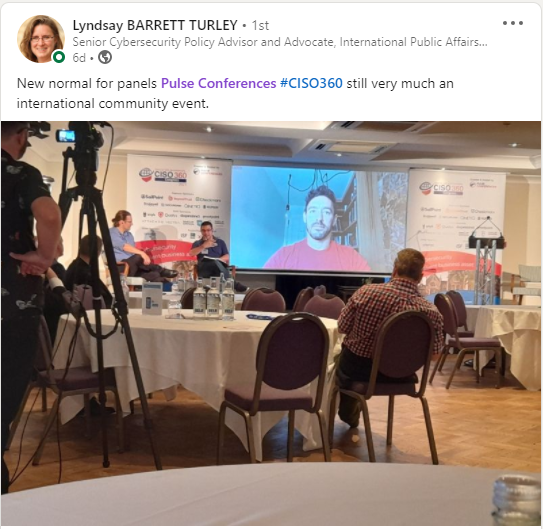
Main event space in the Ballroom and CISO 360 Social Hub in the Grand Marquee

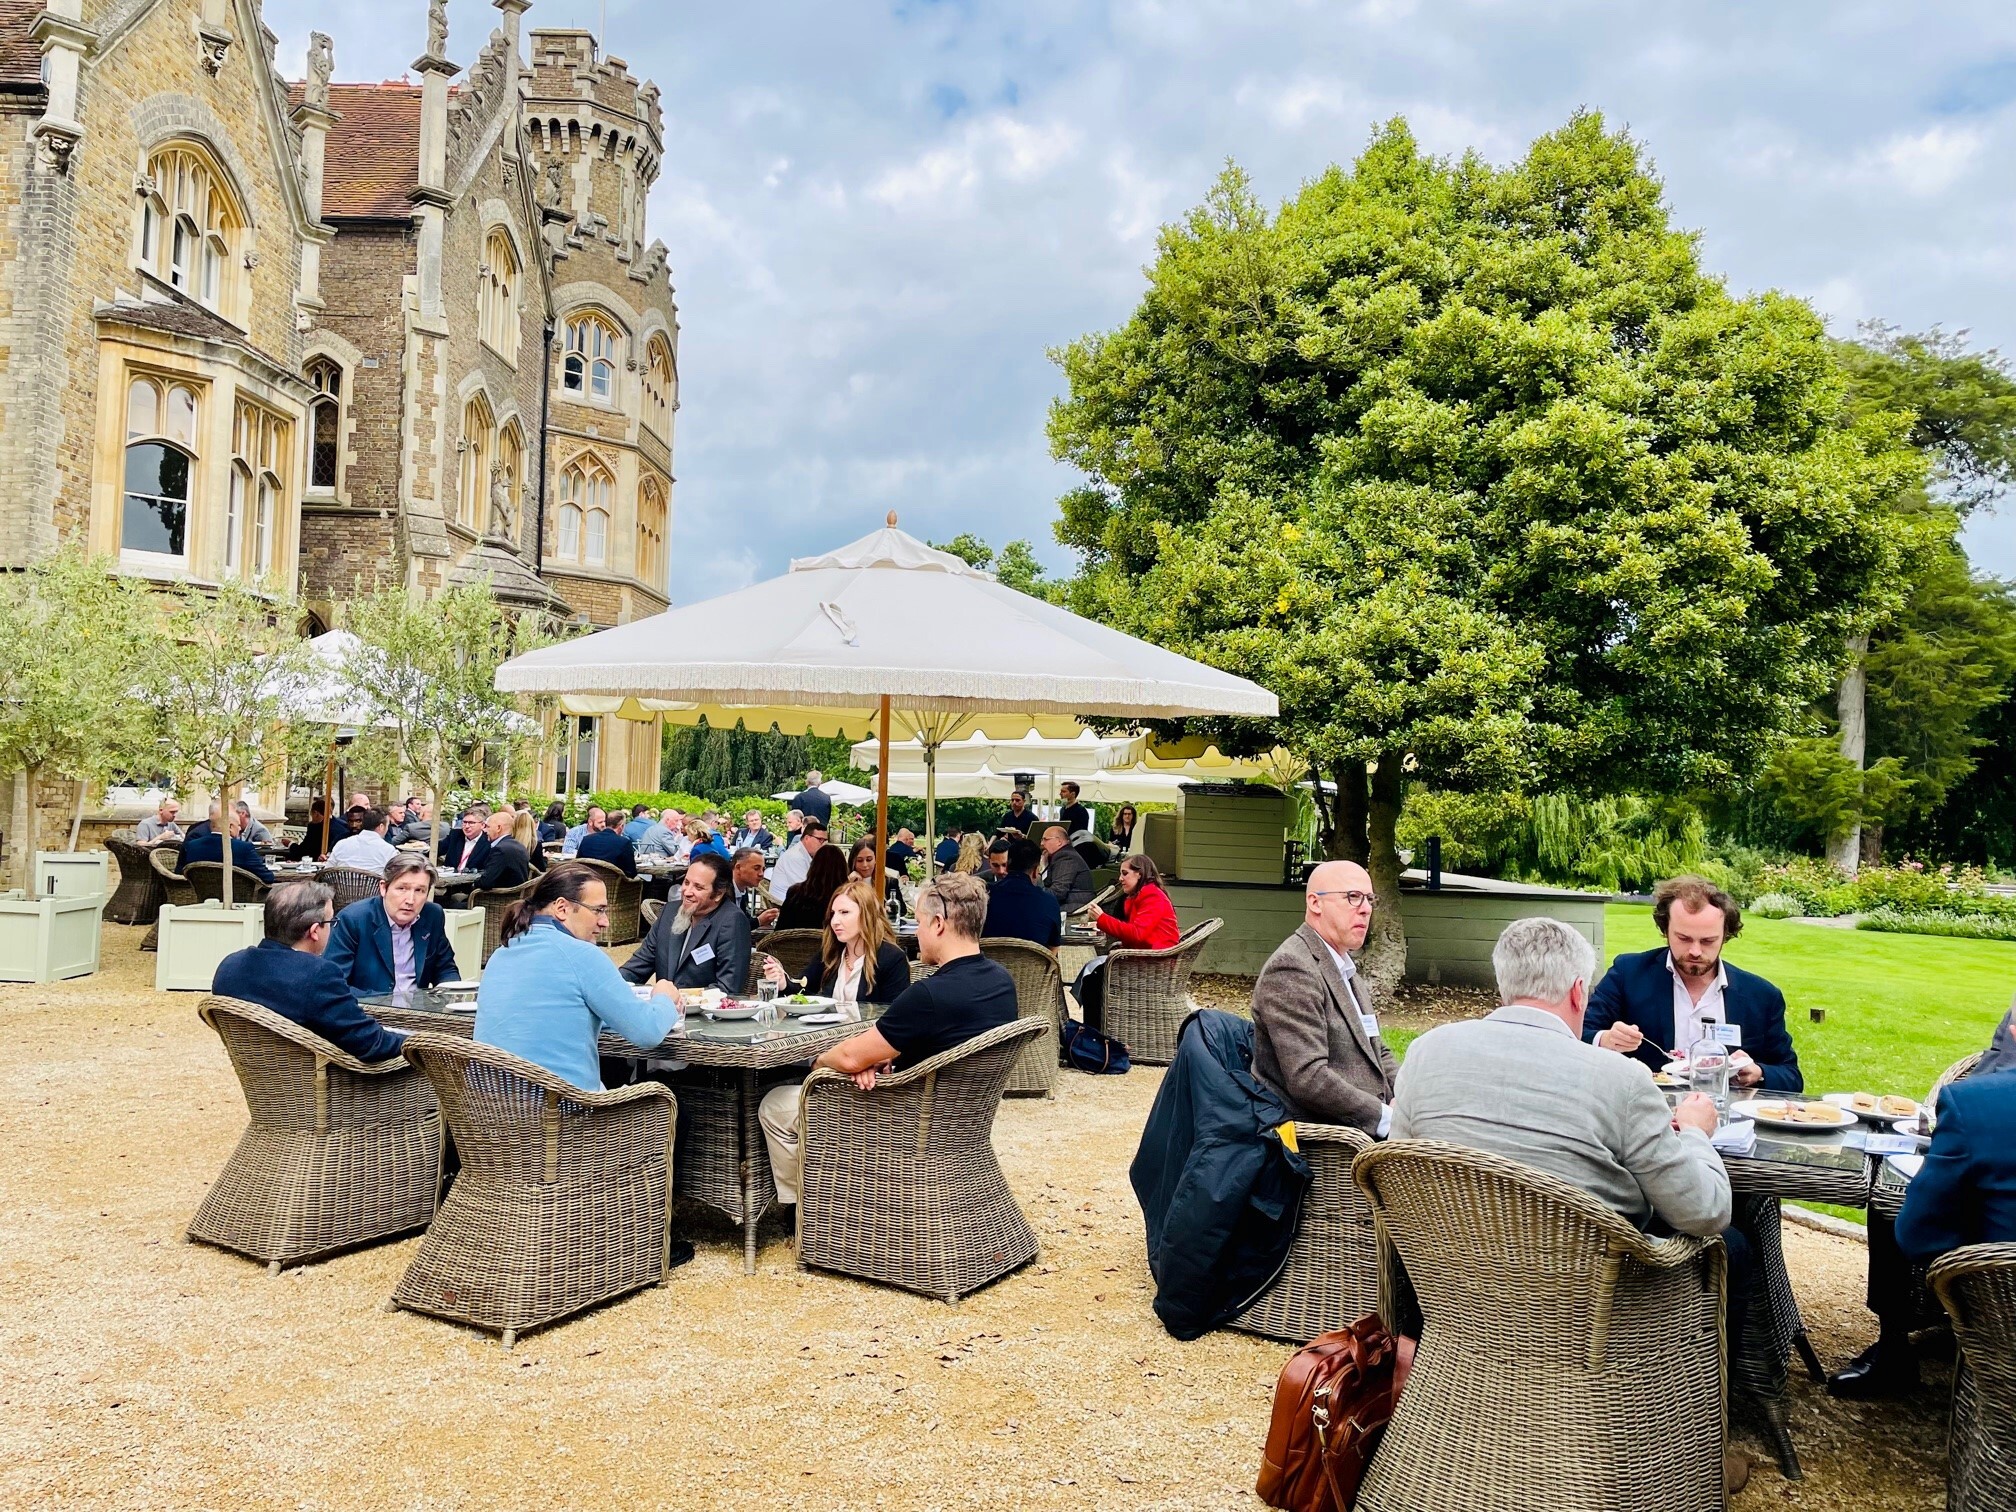
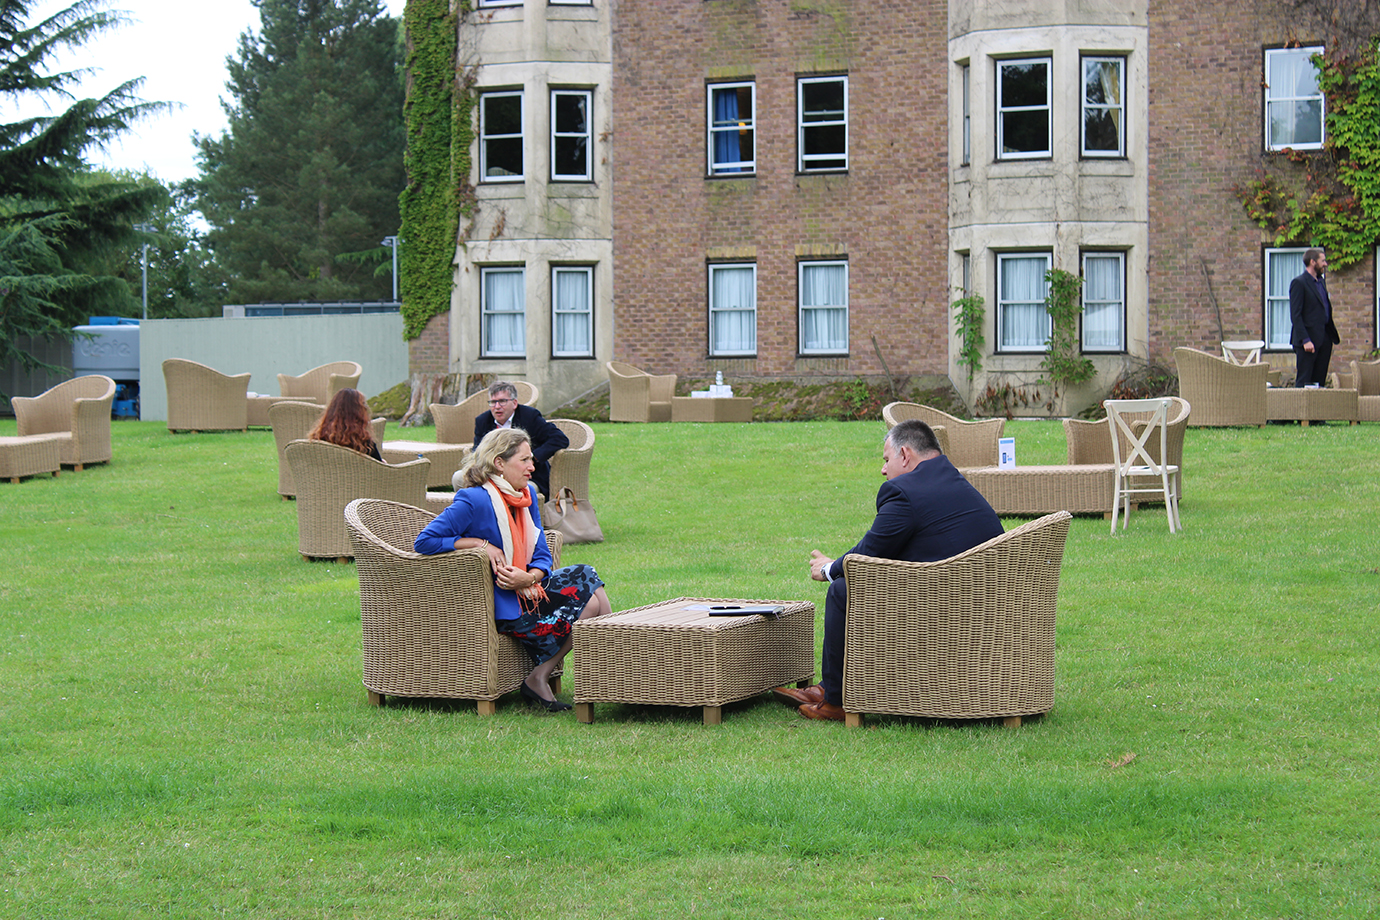
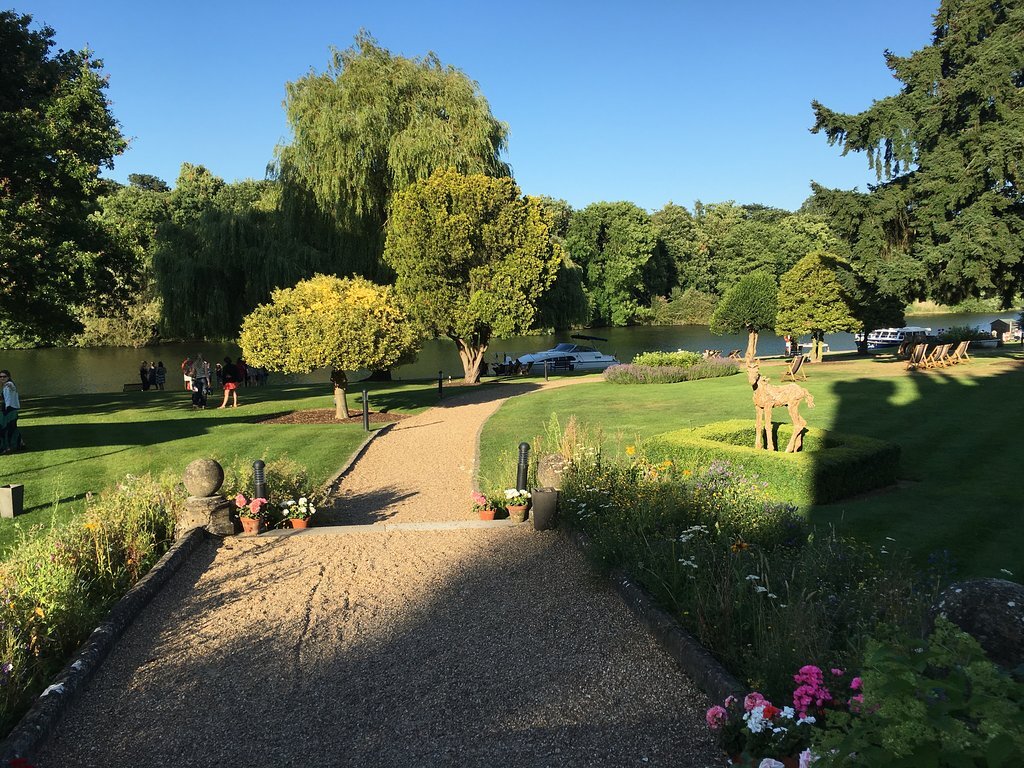
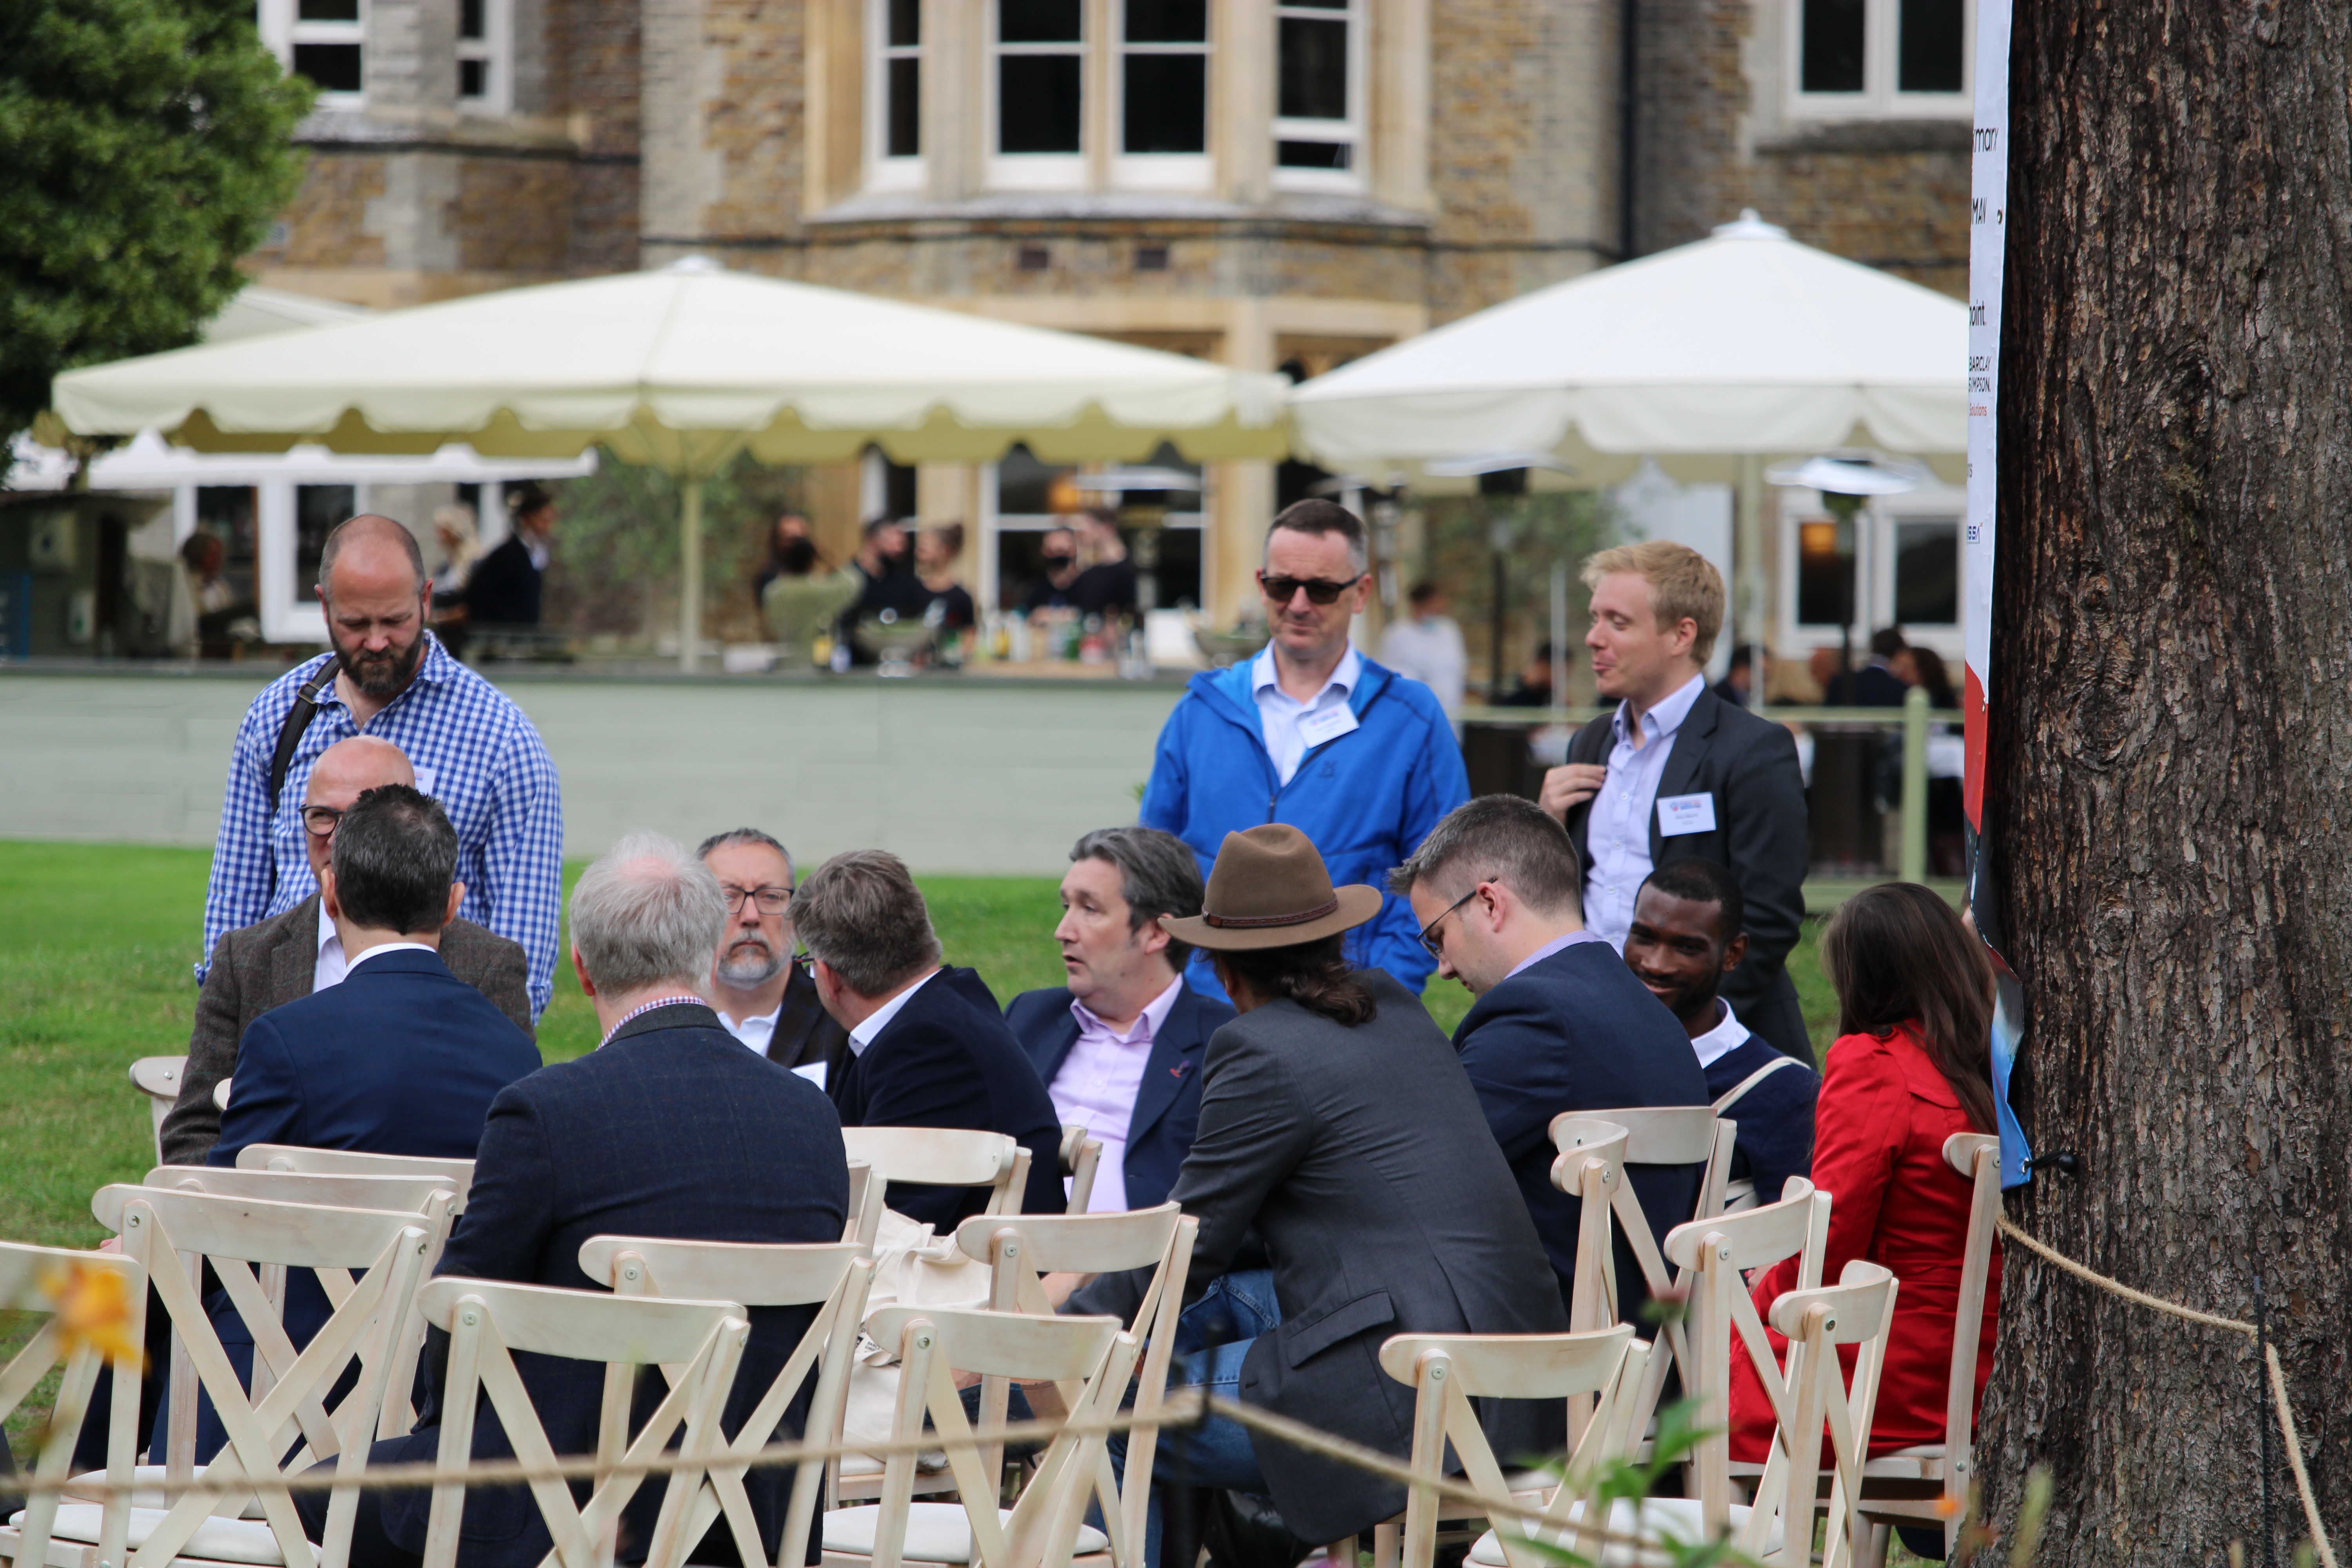
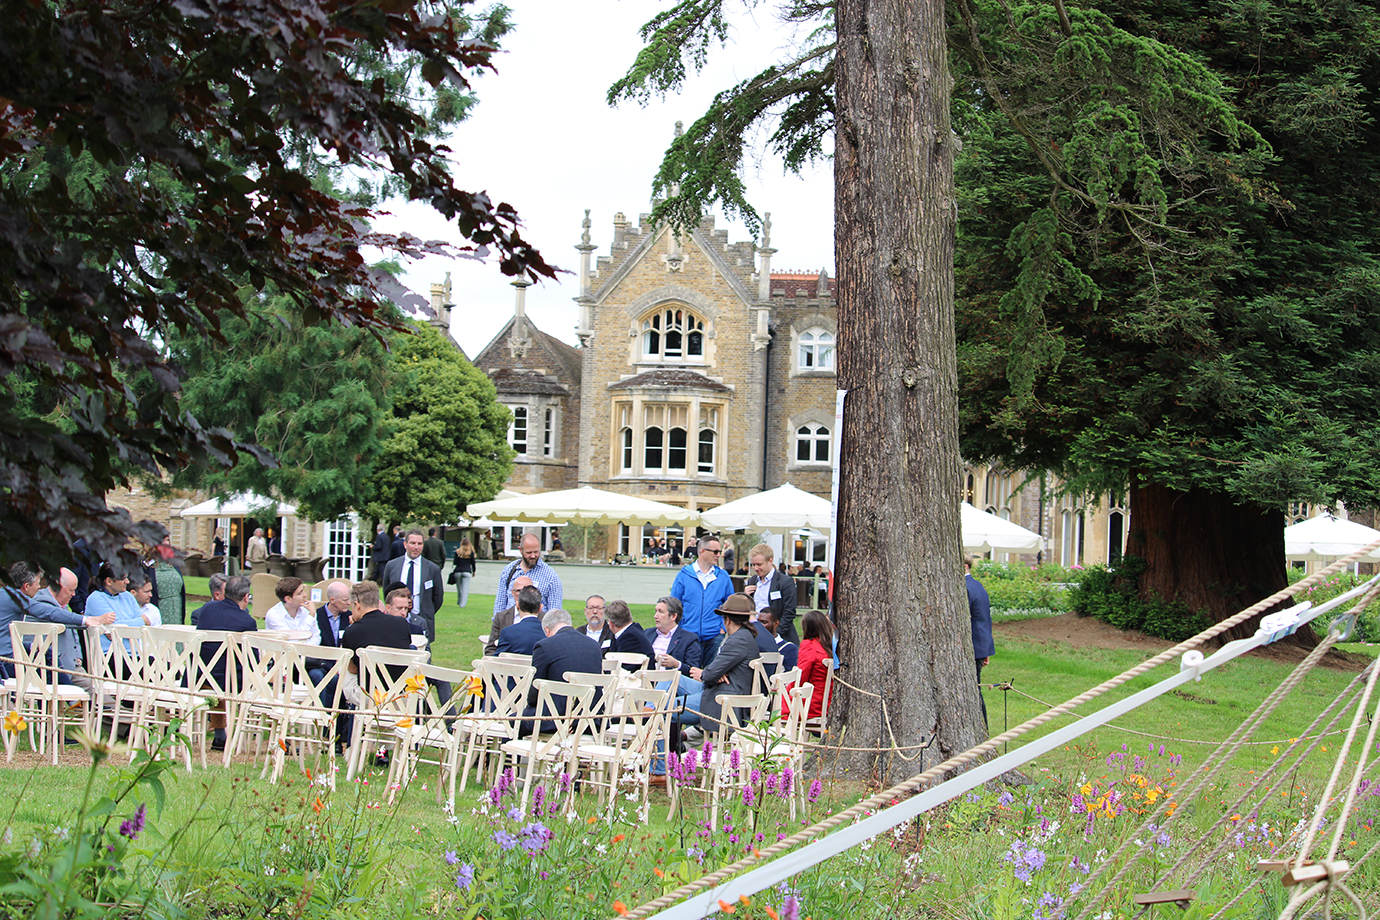
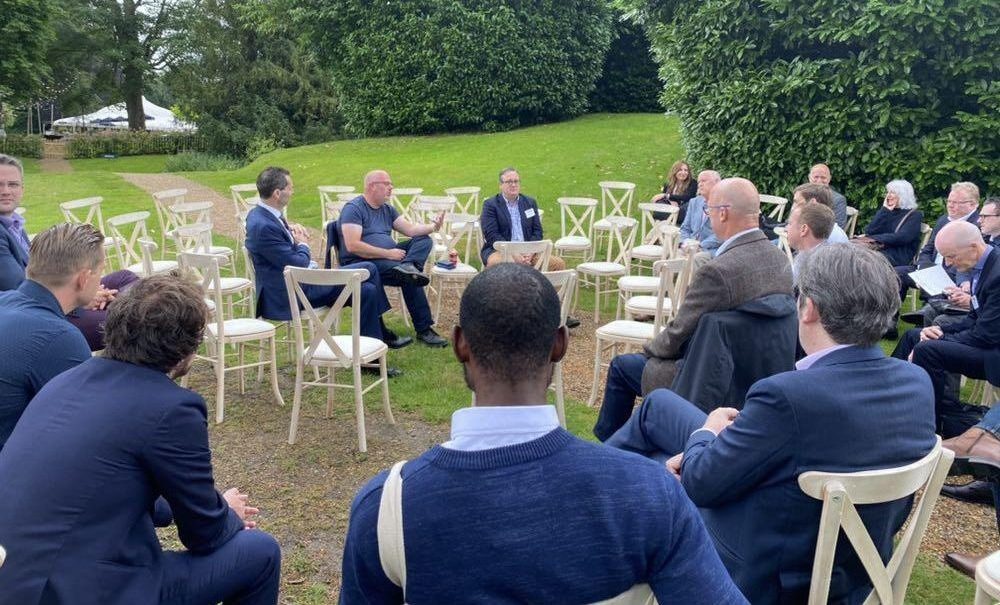
The main Congress will be hosted in Oakley Court’s ballroom “The Big Room” and all our breakout roundtables as well as the lunch will be hosted in the venue’s beautiful gardens (weather permitting). This will provide an airy, well-ventilated experience for participants, and we can take advantage of what should be warm weather in July! All breaks will be hosted in the CISO 360 Security Hub, located in the Grand Marquee in the gardens that looks directly out onto the River Thames.

Accommodation at the Oakley Court or
Castle Hotel, Windsor

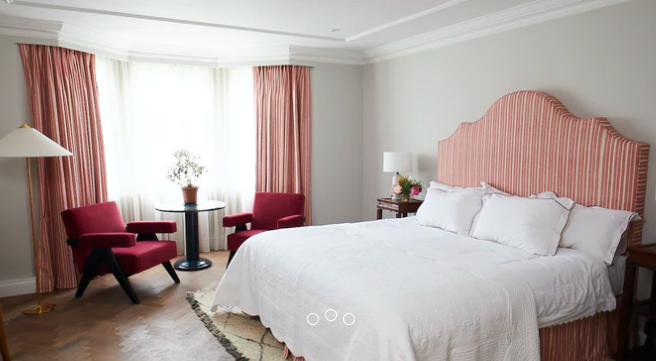
Rooms at the Oakley Court are limited so please get in contact directly with the hotel as soon as possible to secure your accommodation. The accommodation cost ranges from £250 – £400 per night (depending on room type). To book your room at Oakley Court for the CISO 360 Congress, please call +44 (0) 1753609988, email: guestrelations@oakleycourt.co.uk or book directly online www.oakleycourt.co.uk.

Please note that availability is very limited at Oakley Court over the summer months so if you do prefer to stay there, we encourage you to book today!

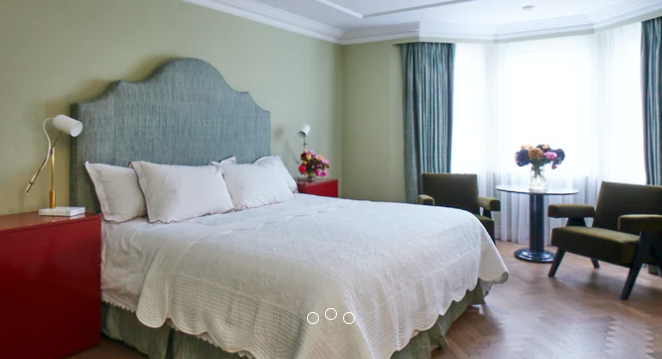
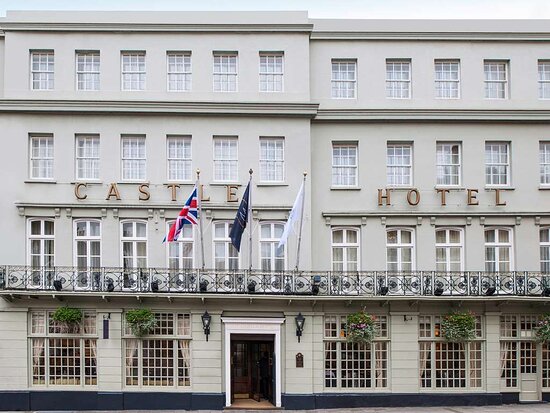
Pulse can also offer discounted accommodation rates at The Castle Hotel which sits along the quintessentially English High Street of Windsor, only 10 minutes drive away from Oakley Court. The main networking dinner for the CISO 360 Congress on Wednesday 7 July will be held in Windsor so this is also a perfect location to stay for the Congress.

The discounted price at the Castle Hotel is:
£149 – Bed & Breakfast per room per night based on single occupancy
£159 – Bed & Breakfast per room per night based on twin/double occupancy

To book your accommodation at the Castle Hotel please email h6618-re@accor.com or call the hotel reception directly +44 (0) 01753 851 577. Please refer to CISO360 to receive the discounted accommodation rate. This discounted room rate is only guaranteed until 16the June and rooms are limited so please book asap.

Castle Hotel Windsor – MGallery
18 High Street, Windsor SL4 1LJ, United Kindom
https://castlehotelwindsor.com/

Accommodation at Oakley Court

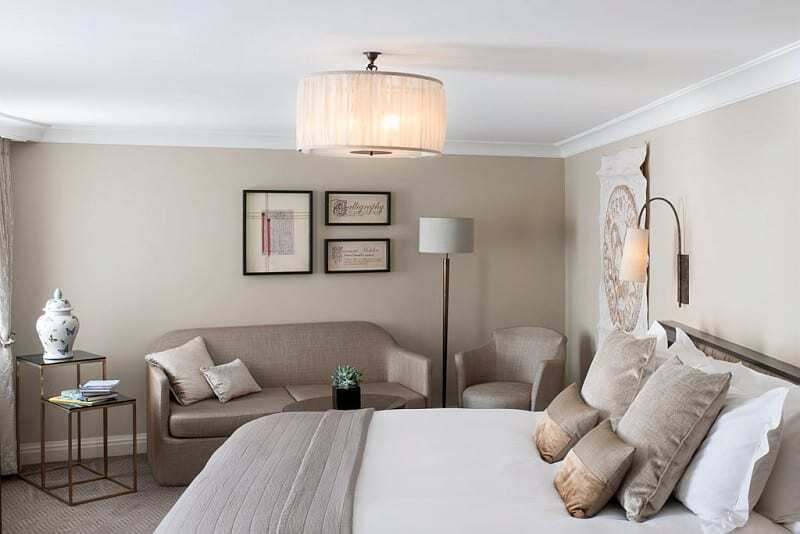
Accommodation at The Castle Hotel

Location

Oakley Court
Windsor Road, Water Oakley, Windsor, Berkshire, SL4 5UR, UK

Oakley Court is conveniently located approximately 45 min drive from central London or just 10 drive from Windsor. There are also direct trains from London Waterloo to Windsor which takes around 55 min, after this, we suggest a short 10 minutes taxi ride to Oakley Court or you can take bus 16 / or 16A which takes you to The Greene Oak (19 min walk from Oakley Court). If you would need further information on how to best get to Oakley Court from your location, please contact the hotel directly at: guestrelations@oakleycourt.co.uk.

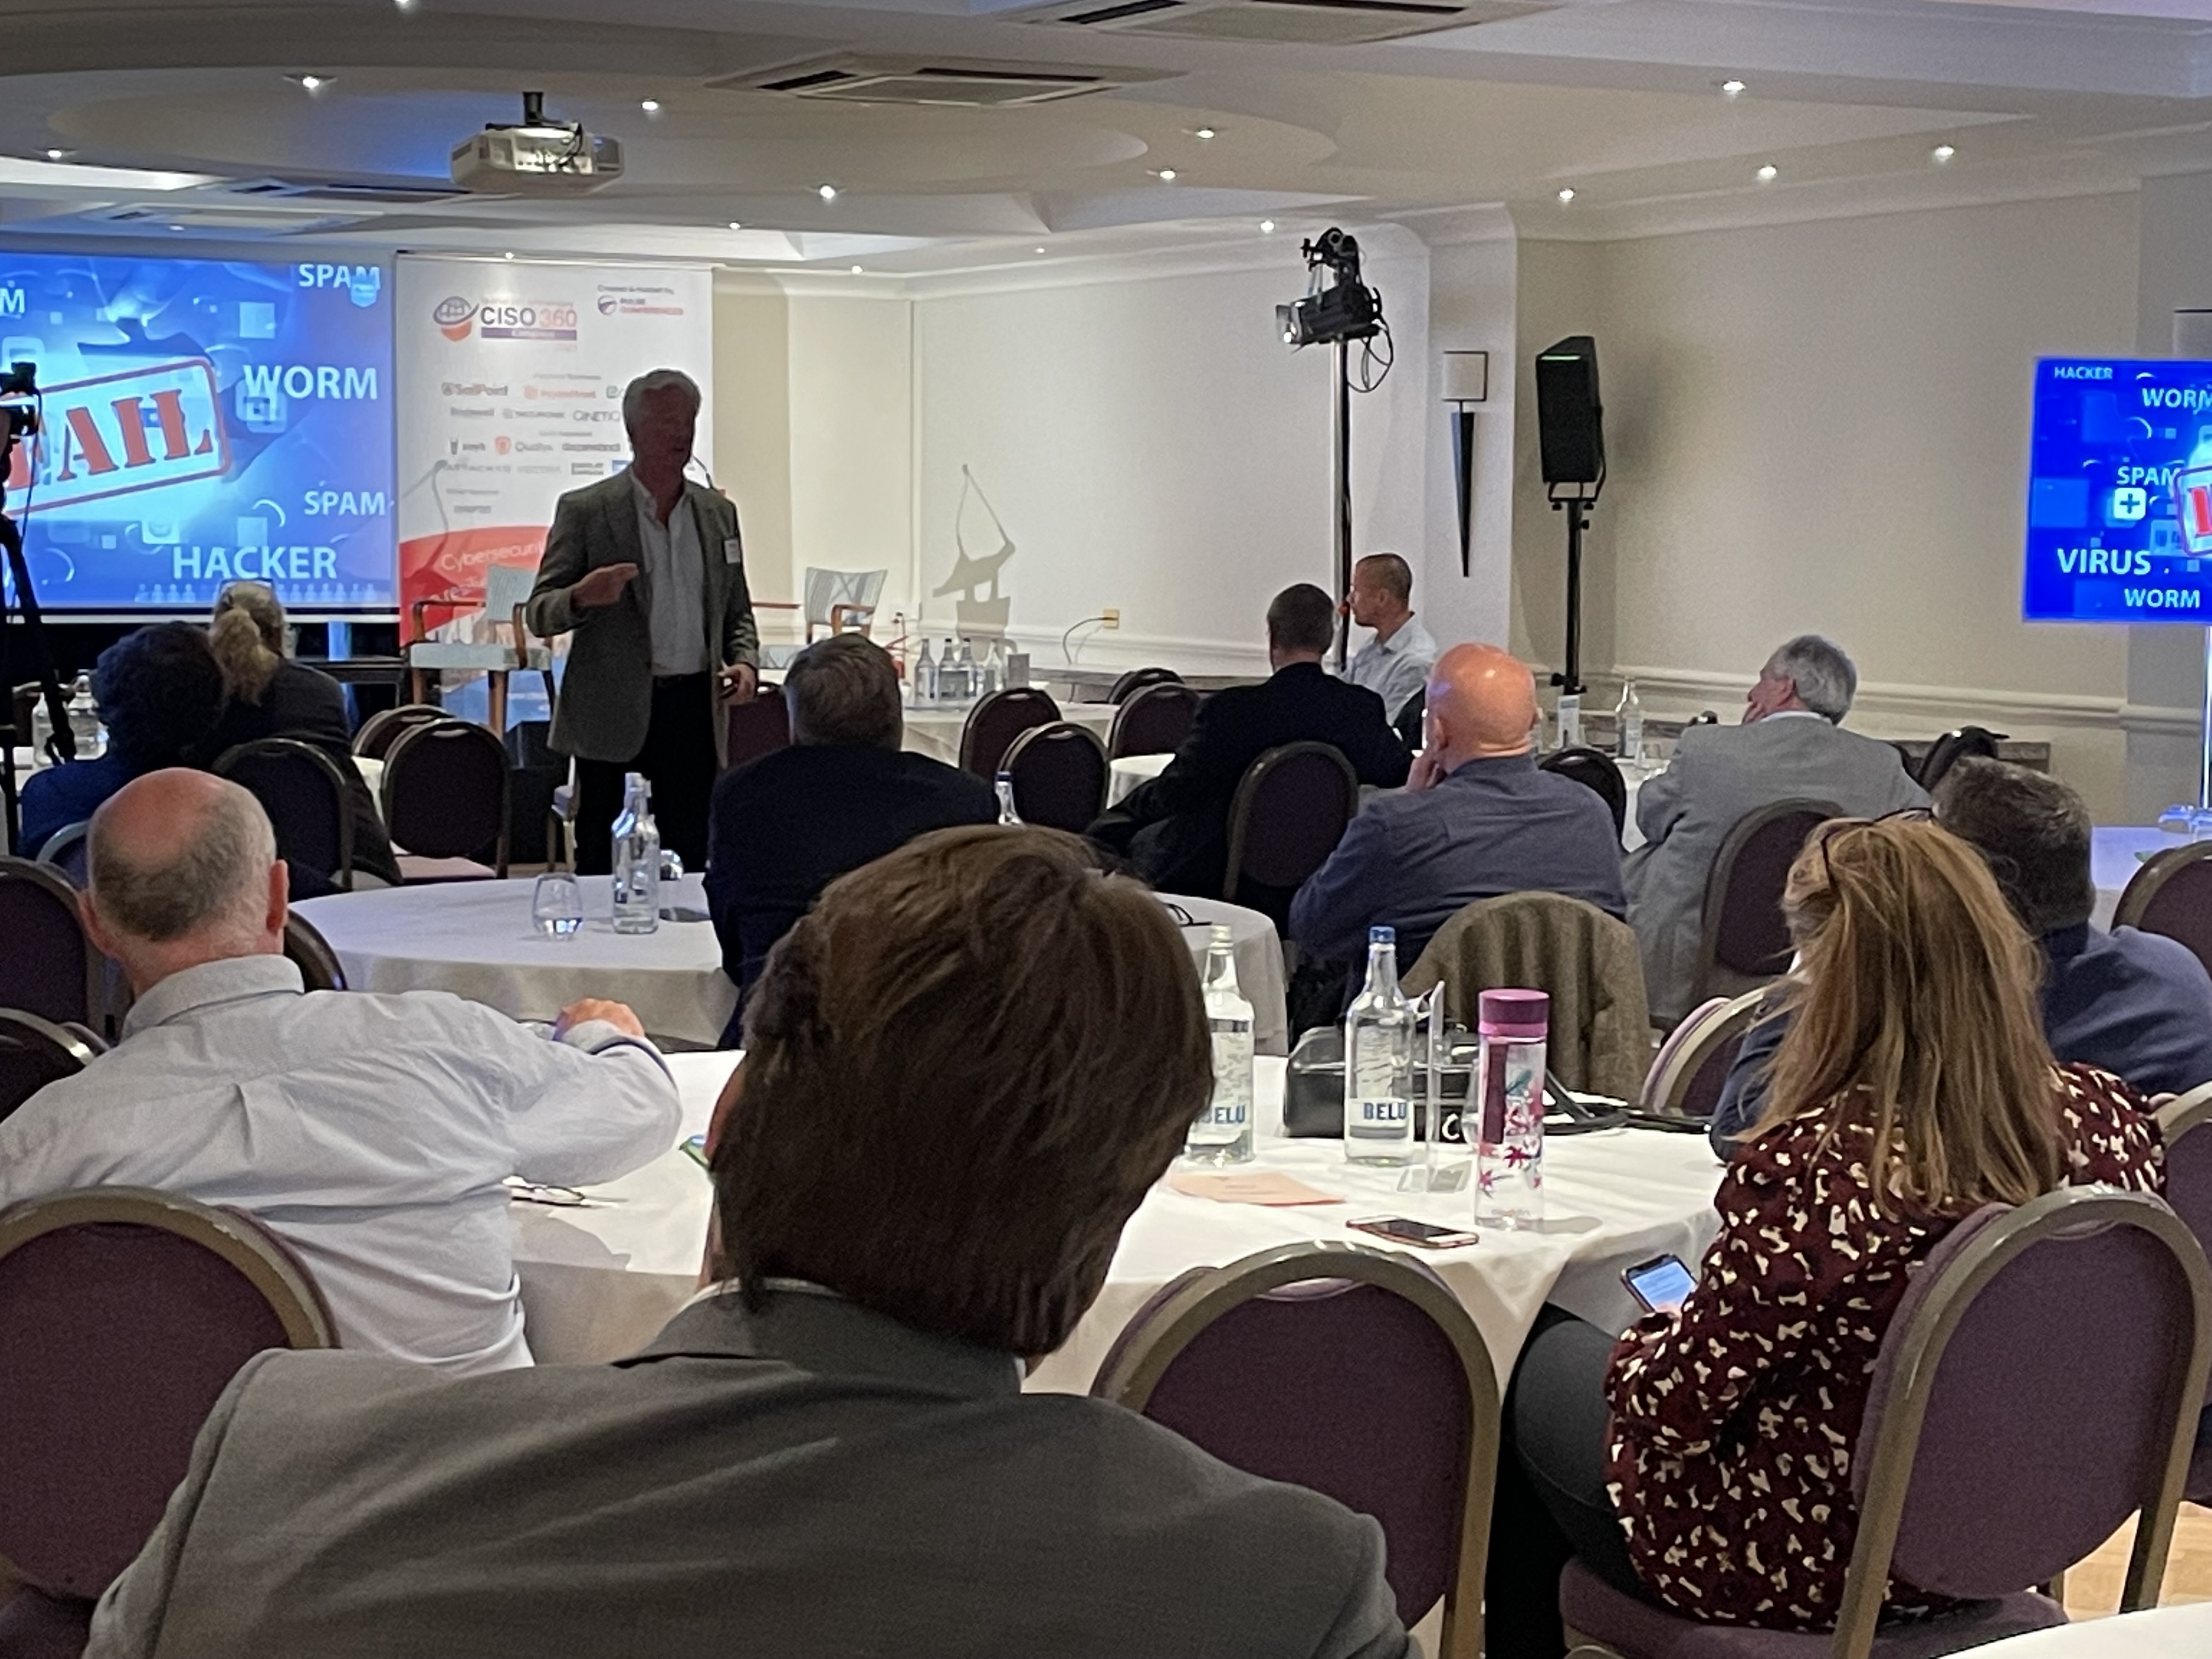
Gallery – 5th CISO 360 Congress – Day One, 7 July 2021

Gallery – 5th CISO 360 Congress – Day Two, 8 July 2021

Gallery 

View Photos - Day One, 7 July 2021View Photos - Day Two, 8 July 2021View Photos - Daytime networkingView Photos - Evening Networking EventsOfficial 5th CISO 360 Congress Video


Testimonials – CISO 360 series

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” – Deborah Saffer, Global Deputy CISO, Cushman & Wakefield


“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions


“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC


“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” – Jonathan Armstrong, CEO, Cordery


“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.” – Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK


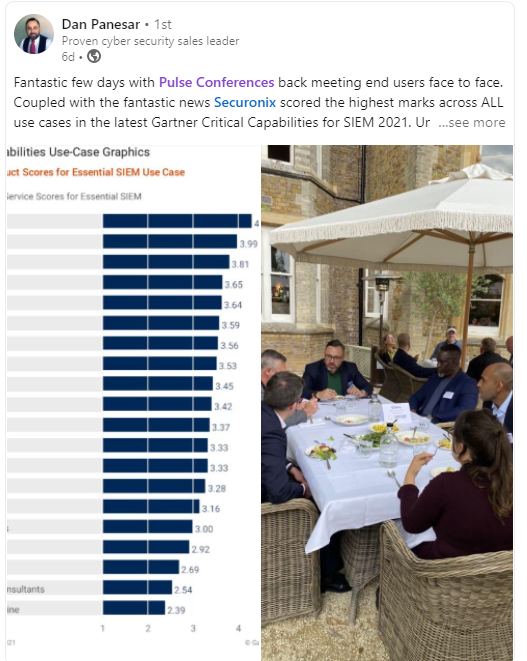
“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys


“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World

“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP

“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint


“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP

“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica


“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack


“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85


“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“

Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin


“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh

— Holly Foxcroft (@holly_foxcroft) 21 June 2018

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London


“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
 

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint


“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin


“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO

— Viktor Polic (@ViktorPolic) 26 June 2018


“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4


“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal


“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller


“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018


“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland


Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018


High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government


“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV


“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum


““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting


Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018


Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
 

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
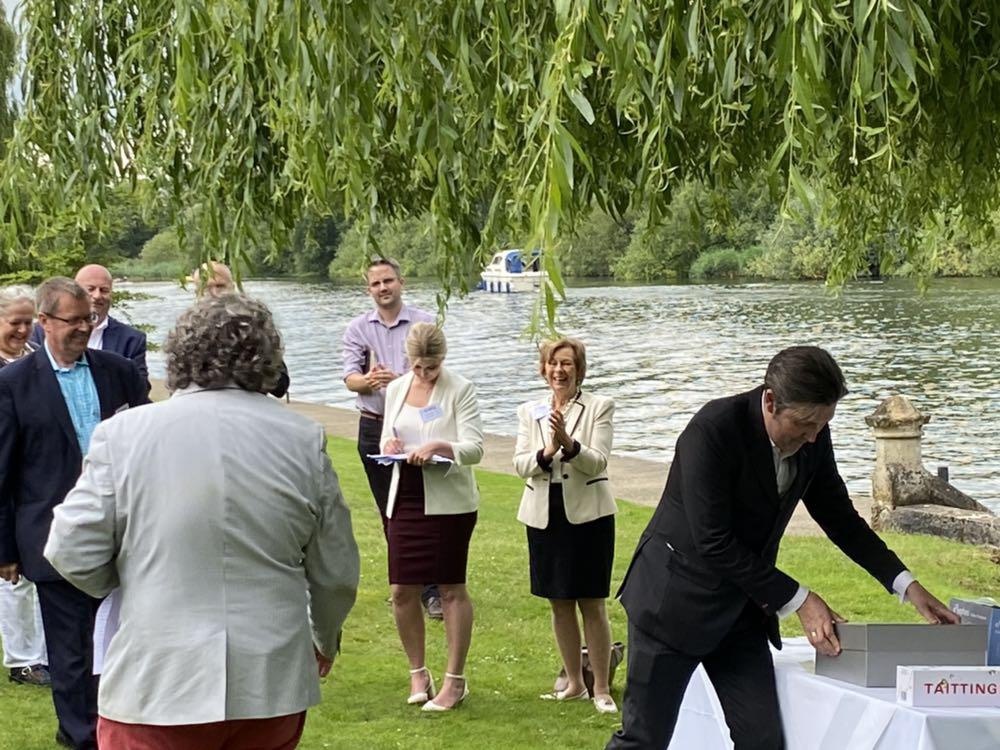
 

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018


“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP