
CISO 360 Congress
To go to the CISO 360 Congress 2018 please click here
Connecting minds, assuring the future
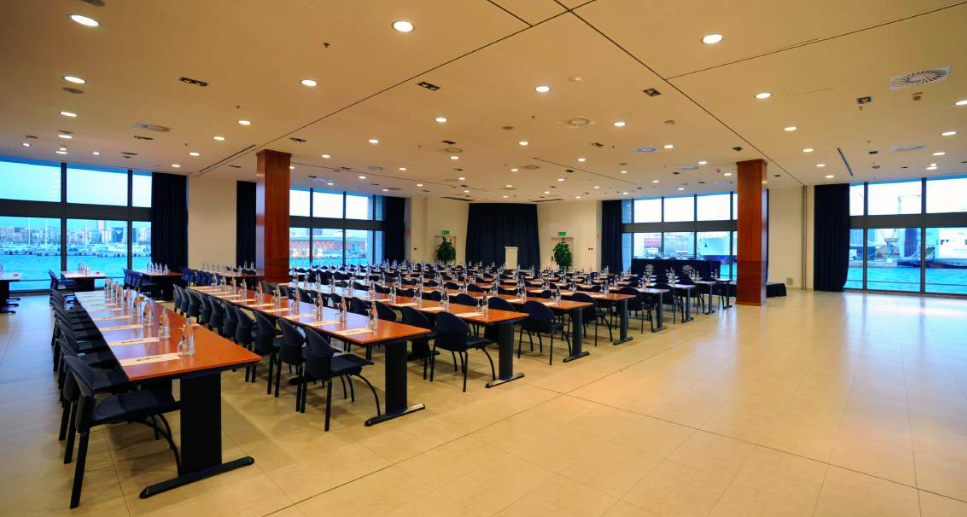
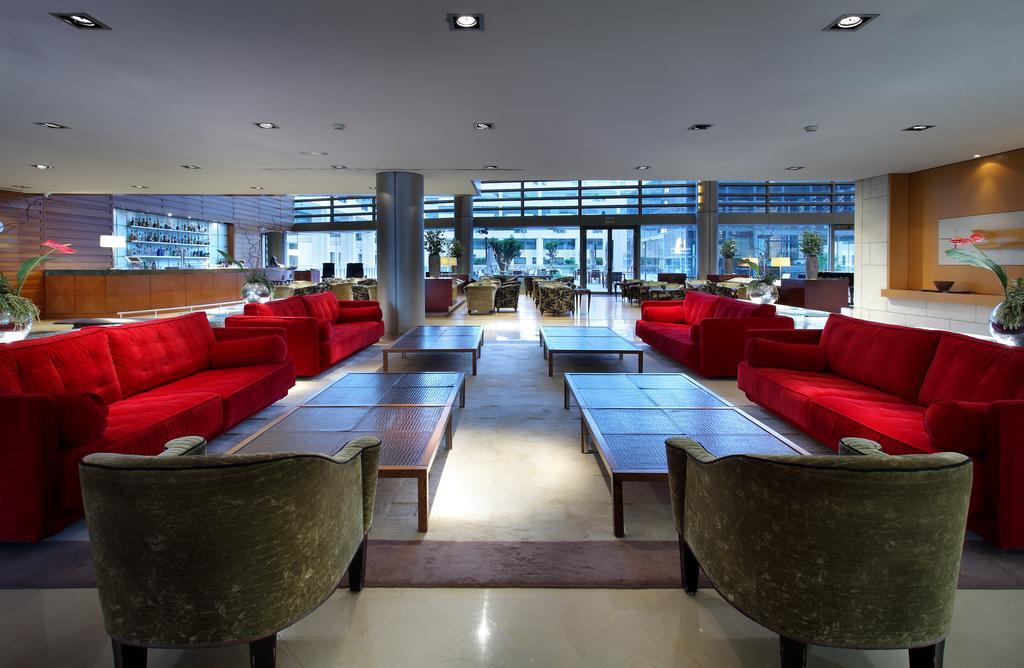
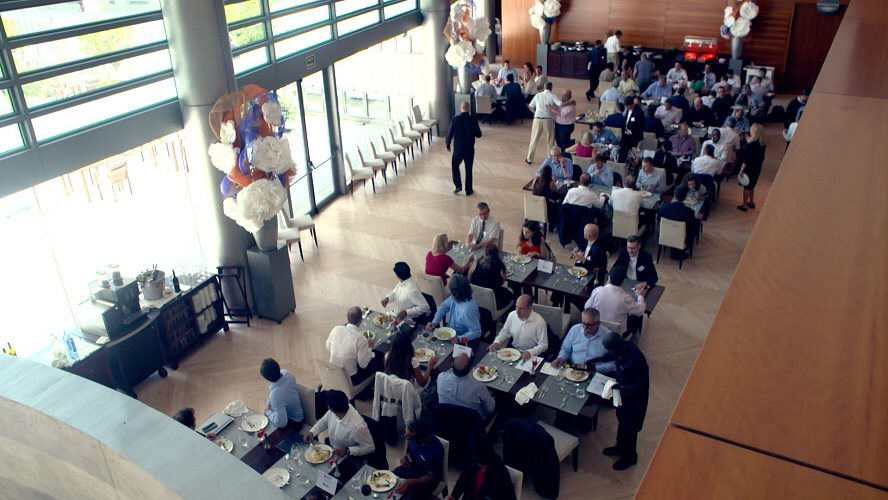
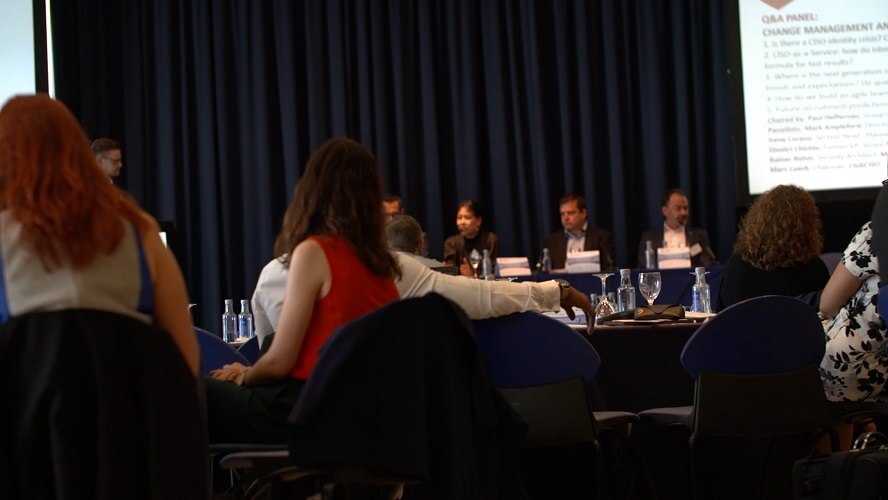
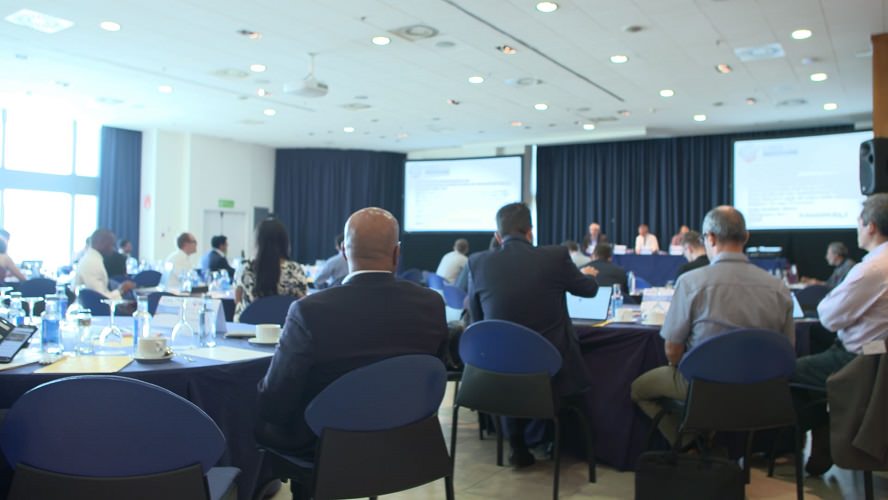
Pulse Conferences would whole-heartedly like to thank everyone who participated in the CISO 360 Congress – Barcelona, hosted 5-7 July 2017 in Barcelona at the five-star Eurostars Grand Marina Hotel. A special thank you goes to the sponsors, speakers and attendees.
Read event testimonials here.
Check out the video from our latest Conference in Barcelona
– CISO 360
A global pre-eminent gathering of chief information security officers, directors of cyber threat intelligence and cybersecurity experts celebrated its launch under the banner of “Connecting minds, securing the future: how to be a world-class cybersecurity leader or risk manager in the age of digital innovation.”
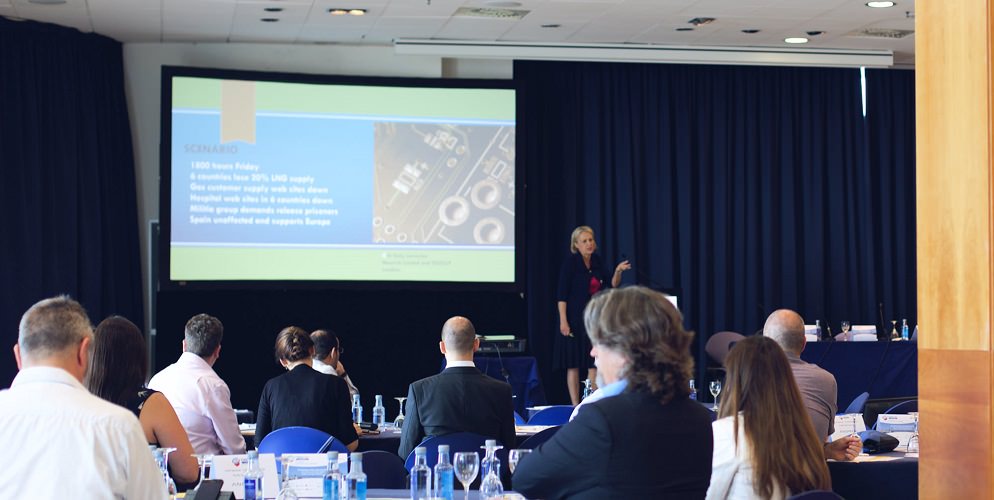
During the Congress on Wednesday and Thursday, an immersive programme and truly international speaker panel spanning 4 continents explored the front line of developments in the changing threat landscape as well as cybersecurity value creation strategies under the 5 key themes outlined below. Over 45 senior cybersecurity directors openly shared experiences, war stories and successes to pool brain power on opportunities and risks for cybersecurity in the era of a fast-moving threat landscape and amidst the challenges presented by digital innovation. The post-event report will be published here shortly.
Practical approaches and strategies shared at the Congress included thought-leadership on:
- How can we protect business assets, brand and reputation as cybersecurity becomes an increasingly important part of the enterprise risk management structure?
- How are key business areas maturing and how can we stay one step ahead of change amidst ever more complex supply chain collaborations and heightened threat radar?
- What is the latest in global regulation, compliance and legislation and how can the CISO achieve a balance between risk-reward?
- How are CISOs forging new roles and standards in the age of IoT and digital transformation and embracing ‘disruptive’ technologies, change management and a winning cybersecurity investment strategy?
The CISO 360 Boardroom, kindly led by Dr. Robert Coles of GSK, and sponsored by Trend Micro on Friday morning was an unprecedented success We urge you not to miss the next Pulse sound-boarding opportunity with security peers on what has actually been achieved by the cybersecurity community, how and why. A ‘must attend’ community-focused event that is hosted under the Chatham House Rule. The output report is now available – to attendees of the event.
2017 DELEGATE SURVEY RESPONSES
96% OF THE ATTENDEES RATED THE CISO 360 CONGRESS ‘GREAT OR EXCELLENT’!
94% WOULD LIKE ATTEND THE NEXT EDITION!
84% RATED THE SPEAKERS TO BE OF ‘EXCELLENT’ QUALITY!
We can’t wait to announce dates for the CISO 360 Congress 2018!
A reminder of our 2017 speaker line-up:
Chaired by: Marcus Alldrick, Head of Digital Risk Management and Compliance, Lloyd’s of London
Boardroom Chaired by: Professor Robert Coles, Chief Information Security Officer/Head of Information Protection & Privacy, GSK
Fireside chats with:
- John Scimone, SVP, Chief Security Officer, Dell (former SVP, Global Chief Information Security Officer, Sony Group)
- Sounil Yu, SVP, Director for Security Innovation, Bank of America
- Freaky Clown (FC), Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
- Dr. Jessica Barker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
International speaker panel:
- Adolfo Hernández, Advanced Cyber Defense Manager, Banco Sabadell
- Alex Quintieri, Head of Cybersecurity, AIA Insurance
- Alex Wilson, Cloud Security Architect, EMEA, CyberArk
- Alexios Fakos, Head of Cyber Defence, Airbus Germany
- Ali Zeb, CISO, MS Amlin
- Anthony Young, Partner, Bridewell Consulting
- Charles V. Pask, Managing Director, ITSEC Associates Ltd
- Charlotte Stephen, Account Executive, Darktrace
- Charlie Bennett, Global Account Director, Trend Micro
- Dr. Cheryl Hennell, Former CISO, Openreach
- Daniel Brunner, Head of Security and Architecture, RUAG AG Switzerland
- Darron Gibbard, Chief Technical Security Officer, Qualys
- Dexter Casey, Interim Group CISO, Centrica
- Dimitri Chichlo, Former VP, Senior Manager Information Security & BCM, Edmond de Rothschild
- Dr. Eduardo Solana, Senior Lecturer of Cryptography and Security, University of Geneva
- Eduardo Di Monte, Security and Business Continuity Director, Agbar
- Fabian Libeau, EMEA Technical Director, RiskIQ
- Gadi Evron, Chairman, Israeli CERT & CEO, Cymmetria
- Graham Edwards, Head of Group Security, Nationwide
- Hugh Njemanze, Chief Executive Officer, Anomali
- Irene Corpuz, Section Head – Planning & IT Security, UAE Government
- James Gill, Advanced Cyber Defense Director, Banco Sabadell
- Dr. John Meakin, Group Chief Risk & Security Officer, Burberry
- Jonathan Armstrong, Partner, Cordery
- Manuel Barrios Paredes, CISO, Informática El Corte Ingles
- Mark Ampleford, Director – Security Division, Barclay Simpson
- Mark Logsdon, Head of Cyber Assurance and Oversight, Prudential
- Michael Colao, Head of UK Security, AXA
- Mike Humphrey, Head of Security, National Crime Agency
- Mun Valiji, CISO, Sainsbury’s
- Nahim Fazal, Head of Cyber Threat Intelligence, Blueliv
- Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance
- Paul Heffernan, Group Chief Information Security Officer (CISO), Unipart Group
- Prudence Smith, Head of User Behaviour, Awareness and Heuristics, Barclays
- Rainer Rehm, Security Architect, MAN Truck & Bus AG
- Ramon Serres, Head of Information Security, Risk Management and Quality, Almirall
- Ramses Gallego, Frmr President, ISACA Barcelona Chapter
- Richard Bell, Chief Information Security Officer (CISO), Transport for London
- Rik Ferguson, Vice President Security Research, Trend Micro
- Professor Robert Coles, Chief Information Security Officer/Head of Information Protection & Privacy, GSK
- Dr. Sally Leivesley, Director, Newrisk Ltd
- Stephen Khan, Head of Security Architecture and Transformation, Royal Bank of Scotland
- Dr. Victoria Baines, Visiting Associate, Oxford Internet Institute
- Dr. Viktor Polic, Adjunct Faculty, Webster University Geneva & CISO, International Labour Organization United Nations
- Vincent Pillay, CISO, Domestic & General
Five key themes
- CYBER THREAT INTELLIGENCE AND THE EMERGING LANDSCAPE
- Partnerships, global practices and resource to build resilience Energy sector focus
- Effectiveness of threat intelligence in mitigating risk
- Integrated cyber-physical security strategies
- SECURING ONLINE COMMERCE IN THE AGE OF IOT AND DIGITAL INNOVATION
- Opportunities and risks for CISOs and directors of cyber threat management
- IoT, AI, big data, block chain – what visionary companies are leading the way in digital innovation and what is the cybersecurity strategy? Financial sector focus
- Trust, identity, payments horizon…Best approaches and innovative technologies for trusted identities and digital securing transactions
- RESILIENCE, LATEST EXPLOITS AND ATTACK TECHNIQUES
- Latest exploits and hacking techniques
- Protecting reputation and intellectual property
- CISO innovation sessions – emerging threats; ransomware, malware
- PRIVACY AND THIRD PARTY RISK
- Practical strategies to approach GDPR to achieve a balance between risk-reward
- Find out how are peers leveraging cost-effective security and privacy
- Cloud, insurance and 3rd party supply chain due diligence
- HUMAN – AWARENESS, LEADERSHIP AND CHANGE MANAGEMENT
- Cybersecurity skills and change management leadership
- Breaking silos – the multi-faceted CISO of today
- What are effective world-class enterprise awareness and collaboration models?
Gold Sponsors
Cocktail Sponsor
Silver Sponsor
Lunch Sponsor
Supporting Associations
Advisory Committee
The CISO 360 Advisory Committee offers wise guidance to ensure the programme is designed ‘by and for’ senior practitioners who are leading security day in, day out. These expert international insights on trends, current realities and breaking news in the information security and cyber risk and resilience industry are critical to the Pulse approach.
Dr. Robert Coles
Chief Information Security Officer/Head of Information Protection & Privacy
GSK
Michael Colao
CISO/ Head of Security
AXA UK
Graham Edwards
Head of Group Security
Nationwide
Gadi Evron
Chairman
Israeli CERT
Lady Olga Maitland
Chairman, Copenhagen Compliance
Founder, Defense and Security Forum
Ray Stanton
Group CISO and Digital Risk Director
National Grid
Dr. John Meakin
Chief Risk & Security Officer
Burberry
Speakers
CISO 360 FAQs
What is the CISO 360 attire?
CISO 360 Congress (5-6 July) – business smart or business casual is most appropriate.
CISO 360 Boardroom (7 July, am) – smart casual is most appropriate.
Networking events (5-6 July, evening dinners, receptions) – smart casual or casual attire is recommended.
Do you have an age requirement for the Conferences?
You must be 18 years of age to attend a Pulse Conferences event and associated networking events.
Can a list of attendees be provided?
We respect the privacy of all registrants and we do not divulge or share registration information. Prior to and once on-site at the congress there will be many ways in which to network with the attendees. Attendee lists will also be available onsite to view.
Is there a deadline for registration?
No, you can register online through the last day of the event, even onsite. However, there are discounts for early registration.
Can I be denied registration for any reason?
Pulse Conferences reserves the right to deny registration to any individual or entity for any reason, at its sole discretion, including past or present failure to meet standards of conduct, and also including (but not limited to) engaging in violent, illegal, threatening or discriminatory conduct or for past failure to pay.
Quota policy
Pulse Conferences has a policy to operate a registrant quota system in order to ensure a balanced delegate base, that is a majority representation from practicing CISOs, heads of cybersecurity or similar from business and government organisations. We have therefore introduced strict quotas for the following:
- Advisories and consultants to the security and risk practitioner communities
- Products and services providers to the security and risk practitioner communities
Once the quota limits have been reached, we will be unable to offer a place at CISO 360 Congress 2017.
Demand for places is high. Anyone wishing to attend is strongly advised to register as early as possible.
No limit is imposed on currently practicing CISOs, Cybersecurity, CDOs and similar.
Do I need a visa to attend the event?
We recommend checking in advance with your country’s local Spanish consulate for details and requirements.
How do I obtain a visa invitation letter?
During the registration process you will be asked if you require a visa letter. In order to request a visa letter from the Pulse Conferences team, please be prepared to provide the following information:
- Full name on passport
- Date and place of birth
- Gender
- Nationality
- Passport number, place and date of issue, and date of expiration
- Are you a government official [yes, no]
Visa invitation letters will be submitted for approval for attendees who have requested a letter and have completed registration data for a full congress pass, including payment. Please note we can only issue visa letters for fully paid attendees and you will need to allow at least two to three weeks for your embassy to process your request.
Certificates at CISO 360 Congress – 2017
Event participants will be provided with an online Certificate of Attendance for CISO 360 Congress 2017 (post-event by soft copy on request to sara.hook@pulseconferences.com). Continuing Professional Education (CPE) credits are accredited by (ISC)² for this event.
Will I need a badge to get in?
Yes, a badge is required for entry into the conference and should please be worn at all times for security purposes. Please pick up your badge at the Pulse registration desk.
Payment terms
- All delegate fees must be paid in advance of the event start date.
- If paying online by credit card, you will receive a payment receipt.
- If requesting to pay by bank transfer, you will receive an invoice on registration.
- All fees must be paid within 2 weeks of registration. If the date of your registration is less than 2 weeks prior to the event start date, payment must be received prior to the event start date.
Cancellation policy
What if I’ve registered but can’t come and do not have anyone to take my place?
Cancellations received between 20 working days and the event start date, no-shows, or people who cannot stay for the event duration, are liable to pay the full conference fee and no refunds will permitted.
What if I’ve registered but can’t come and want to send someone in my place?
We accept substitution delegates. Please let us know in advance with the details of your replacement copied into an email introduction.
If I can’t attend, can I transfer to a future event?
Transfers: if you wish to transfer to a different Pulse event within a 12-month period of the conference you will be invoiced an additional £150 charge to transfer your registration plus any difference in the event prices. You will not incur any additional charges.
In all of the above cases, please inform sara.hook@pulseconferences.com in writing of your transfer plans / cancellation.
Pulse Conferences reserves the right, in advance of the commencement date, to change or cancel any part of its published programme, or cancel the programme in its entirety due to unforeseen circumstances without penalty.
With thanks to our sponsors
2017 Association & Media Partners
Unique sponsorship proposition
Association and Media Partners
Programme
The programme for CISO 360 Congress is currently under development. Please email info@pulseconferences.com to receive the most recent draft agenda.
Provisional Agenda
Day One: CISO 360 Congress – 5 July 2017
LEADERSHIP AND CHANGE MANAGEMENT
- What does good cyber risk management look like?
- Change management for the next generation CISO
- 360 perspective: How can CxOs improve the CISO leadership offering and vice-versa?
- Public/Private: securing critical information infrastructure
LEGAL, PRIVACY AND SUPPLY CHAIN
- GDPR updates and the risk-reward balance
- Third party security: legal, policy, cloud
- Privacy, law enforcement and security
- Intelligence gathering, data and intellectual property theft
CYBER RISK
- Cyber risk and business risk – leveraging security as a business asset
- Top 10 ways to place better measures on controls – can we apply quantitative risk models or safety risk models to security?
- Building robust online brand protection
SECURING DIGITAL INNOVATION
- Security risks and opportunities in business innovation – AI, Big Data, IoT, Blockchain
- Artificial intelligence and the CISO
- Cloud security updates
Day Two: CISO 360 Congress – 6 July 2017
INTEGRATED SECURITY
- DevSecOps – Strategic Lessons Learned for CISOs
- Ransomware – response planning
- Defending against the erosion of brand trust
- Supply chain attacks
- Insider attacks
CYBER RESILIENCE
- How to build a red team
- Mobile application security
- Penetration testing
- Incident Response & Investigations
ONLINE COMMERCE – IDENTITY AND TRUST
- Innovation on the identity and authentication landscape
- Fraud horizon
- Encryption and biometrics updates
Day Three: Friday 7 July 2017 (morning only)
CISO Boardroom
How to reposition cybersecurity as a robust business investment strategy
Led by:
Dr. Robert Coles
Chief Information Security Officer/Head of Information Protection & Privacy
GSK
Gain rare insights into the what, where, how and why.
CISO Boardroom is the ultimate ‘sound boarding’ workshop for today’s cybersecurity and digital risk leaders. All invited guests are expected to contribute to the discussions that will be held under the Chatham House Rule. The talks end with lunch. Designed to produce practical take-aways.
Explore questions such as:
- How can we take current security practices to create new models and strategies to build security value?
- How can we strive for higher quality security practices, standards and sharing?
- What best practice security strategy looks like now and how is this rapidly evolving with digital transformation?
Pre-event: you shape the final agenda. Upon registration you will be asked to subit your top 3 priorities, challenges or questions that you would like to see discussed during the CISO 360 Congress and CISO 360 Boardroom. We thank you in advance for your input. Feedback is confidential and ensures that we directly address your most critical requirements for a fully immersive experience.
Post-event: an output report capturing the key points from the interactive boardroom discussions will be shared after the event. Participants, and a wider group of senior executives with a special interest in these areas, will receive the report not more than 10 days after the event. The report will reflect that the discussions are held under The Chatham House Rule.
Timings:
08:00 Coffee and registration
10:00 Short coffee break
13:00 Lunch
Next round of speaker announcements – to be released shortly
New speakers are in the process of being confirmed every day. Sign up below to receive the latest agenda or for updates on which new security and risk movers and shakers have been announced.
Help shape the agenda and speaker panel
Is there an industry luminary that you’ve always wanted to meet? Is there a company, industry sector or country that is ahead of the curve that you would like to benchmark approaches with?
Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the needs of senior executives.
Pulse Conferences welcomes your input into shaping the agenda and speaker panels for our events.
Enquire about becoming a speaker
When it comes to telling a story, we know that people want to hear about the challenges and failures as well as the successes.
We also believe that Experience + Value = Story.
- Do you have a business story that simply must be told?
- Are you working on an innovative security project?
- Are you willing to openly share inspiring insights and new ideas to advance the security community?
Please call +44 (0)20 7936 8989 or email info@pulseconferences.com for further information.
Agenda and highlights
Download brochureDownload archive
Latest programme timings
Please note the brochure PDF timings may be slightly out of date. To access the very latest programme timings please click here.
Tuesday 4 July
Welcome drinks
19:00-21:00
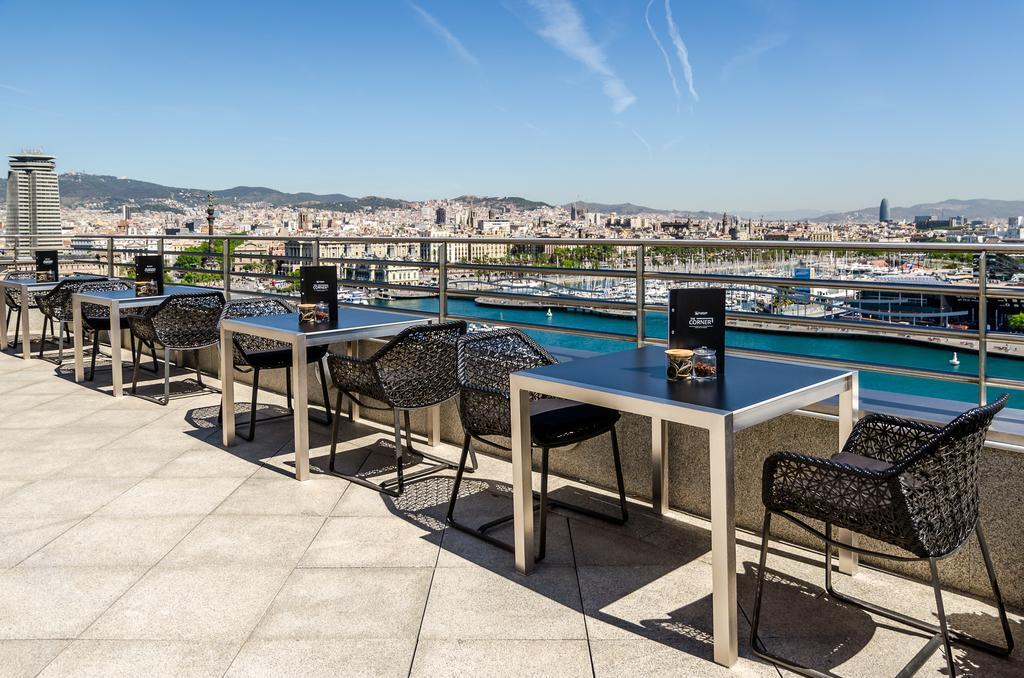
Black Marina Roof Terrace – Eurostars Grand Marina Hotel
Wednesday 5 July
CISO 360 Congress Day One
09:00-09:30
Coffee and registration
09:30
Chairman’s opening
11:10-11:40
Coffee break
13:00-14:00
Lunch
– kindly sponsored by:
16:00-16:30
Afternoon tea break
18:10
Close of day one
18:30-20:30
Cocktail reception
– kindly sponsored by:
21:00-23:00
Networking dinner – Can Travi Nou – 17th Century Catalan Farmhouse
– kindly sponsored by:
Thursday 6th July
CISO 360 Congress Day Two
08:30-08:55
Coffee
08:55-09:00
Chairman’s opening
09:00-09:20
Cyber Threat Intelligence Breakfast Club – kindly sponsored by:
11:00-11:30
Coffee break
13:20-14:20
Lunch
15:50-16:20
Afternoon tea break and Sponsors’ Prize Draw
18:00
Close of day two
18:30-
Networking drinks and dinner at El Cangrejo Loco
Friday 7th July – CISO 360 Boardroom
– kindly sponsored by:
08:45-09:00
Coffee
09:00
Chairman’s opening
13:00-14:00
Closing lunch
Highlights & Benefits
Download brochureDownload archive
5 reasons to attend CISO 360 Congress…
- Thought-leadership discussions –gain rare insights into what leading CISOs are doing – how and why. What works and what doesn’t.
- CISO Innovate sessions – a % of the agenda is dedicated to future-facing technical areas to enable the CISO to ask the right questions of their technical teams.
- Rare cross-functional CxO dimension –the international speaker panel includes CIOs, CTOs, CROs, GCs, CPOs, CDOs and business strategists to reflect the ever-increasing multi-faceted interactions of today’s security leaders.
- Designed ‘by and for’ CISOs, directors of cybersecurity and cyber threat intelligence – compare practical ways in which information security and risk leaders tell us they are adding tangible business value.
- Meet top quality technology R&D innovators and developers who deliver ‘security by design’ – offers a peak into the future of digital innovation, IoT, AI and cloud technologies.
Designed for interaction…
- Enduring connections guaranteed –dedicated networking schedule and a single track programme will ensure you depart at the end of the event with new professional contacts and friends.
- Real-time benchmarking and results-driven –integrated event technology to gain real measures on pertinent questions.
- Fully immersive and interactive –dynamic debates, think tanks, contests, on-stage interviews, fireside chats.
- Open sharing of experiences – the entire event is held under the Chatham House Rule. No press is present.
- Highly researched agenda – stay ahead on how key areas of cybersecurity are maturing.
- Community-focused –partners are welcome to enjoy the included networking events and partner programme.
- Practical take-aways –focus groups will produce best practice output reports delivering an ongoing value-add.
Format
- CISO 360 Boardroom – gain rare insights into what leading CISOs are doing, how, why and what works, and what doesn’t
- Fully immersive and interactive – dynamic debates, think tanks, contests, on-stage interviews, fireside chats
- Real-time benchmarking and results-driven – integrated event technology to gain real measures on pertinent questions
- Open sharing of experiences – the entire event is held under the Chatham House Rule
- Community-focused – partners are welcome to enjoy the networking events
- CISO technology innovation – see live demos
- Rare cross-functional CxO dimension – the speaker panel includes CIOs, CTOs, CROs, GCs, CPOs, CDOs and business strategists to reflect the ever-increasing multi-faceted interactions of today’s security leaders
- Designed by and for CISOs – a multi-faceted ‘tool kit’ engaging a 360 view from architects, business owners, developers, investors and innovators
Privacy, risk and governance
- Jonathan Armstrong, Partner, Cordery will put to bed some of the GDPR “fake news” as well as predictions that are likely to grab the attention in 2018
- Dr. Victoria Baines, Trust & Safety Manager, EMEA, Facebook shares expert insights into the changing dynamics of security and privacy
- Graham Edwards, Head of Group Security, Nationwide will share rare insights into how Nationwide is approaching GDPR risk-reward
- Case study by Stephen Khan, Head of Security Architecture and Transformation, Royal Bank of Scotland who will share results, challenges on successes on effective supply chain management for security
- Further GDPR perspectives from Europe from CISOs of HC Starck (Germany) and Almirall (Spain)…
Cyber threat intelligence, resilience and response landscape
- Don’t miss the fireside chat with John Scimone, SVP, Chief Security Officer, Dell, who was former SVP, Global Chief Information Security Officer at Sony Group, as he talks about how CISOs can prepare for destructive cyberattacks
- Anomali will lead a breakfast discussion on the practicalities and realities of threat feeds
- Case studies by Juan Ramón Caravaca Sánchez, CCO, CISO, Verne Group; Ray Stanton, Group CiSO & Director Digital Risk, National Grid
- Gadi Evron, Chairman, Israeli CERT & CEO, Cymmetria will divulge what works and what doesn’t in relation to threat risk assessments
- Gain rare insights into a day in the life of an Interim Security Director – Dexter Casey, currently with Willis Towers Watson, interacts on threat-hunting
- What does the integrated cyber-physical security space look like today – invited c-level executives
Response, latest exploits and attack techniques
- Hear practical approaches from Irene Corpuz, Section Head – Planning & IT Security, UAE Government on malware Shamoon 2 as it affected some entities in the GCC
- Michael Colao, Head of Security, AXA UK shares tips on how we can avoid getting our data locked down and responses
- Practical strategies in response to the emerging landscape – insights to simplify, automate and reduce response time in incidents or malicious activity by Alex Quintieri, Head of Cyber Security, AIA Insurance Hong Kong
- Followed by scenario planning exploits on insider exploits by Dr. Sally Leivesley, Director, NewRisk Ltd, and latest exploits seen by Daniel Brunner, Head of Security and Architecture, RUAG AG Switzerland
Brand protection / securing online commerce / security as an investment in the age of IoT and digital innovation
- New case studies on secure agile development – Dr. John Meakin, Chief Risk & Security Officer, Burberry and Malcolm Kelly, Global Head of Application Security, HSBC
- What does a world-class transformation strategy look like? What are effective world-class enterprise awareness and collaboration models?
- How can we take current security practices to create new models and strategies to build security value?
- What best practice security strategy looks like now and how is this rapidly evolving with digital transformation?
CISO Boardroom – How to reposition cybersecurity as a robust business investment strategy
Led by:
Dr. Robert Coles
Chief Information Security Officer/
Head of Information Protection & Privacy
GSK
Timings:
08:00 Coffee and registration
10:00 Short coffee break
13:00 Lunch
Gain rare insights into the what, where, how and why.
Pre-event: you shape the final agenda. Upon registration you will be asked to subit your top 3 priorities, challenges or questions that you would like to see discussed during the CISO 360 Congress and CISO 360 Boardroom. We thank you in advance for your input. Feedback is confidential and ensures that we directly address your most critical requirements for a fully immersive experience.
Post-event: an output report capturing the key points from the interactive boardroom discussions will be shared after the event. Participants, and a wider group of senior executives with a special interest in these areas, will receive the report not more than 10 days after the event. The report will reflect that the discussions are held under The Chatham House Rule.
Speakers
If there is someone you would like to see speak or if you are interested in speaking please let us know teampulse@pulseconferences.com.
CISO 360 Asia & Oceania Chaired by
Marcus Alldrick
Digital Risk Management, Security and Compliance Advisor
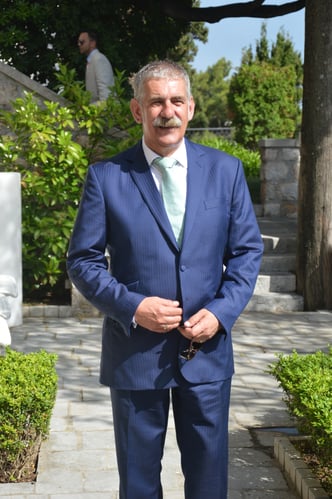
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services and sits on the Cymmetria Advisory Board as Chief Risk Officer.
International speaker panel
Enquire about becoming a speaker
We are always looking for:
- keynote insights, cutting-edge ‘live’ demos
- new best practice corporate case studies, fresh ideas, forward thinking topics on security and governance matters
- sessions with actionable takeaways and positive contributions to the output reports
- the world’s smartest thinkers and doers in security, cyber, privacy, resilience, risk, governance, compliance
We welcome your input into shaping the agenda and speaker panels.
Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.
For further information, please contact Sara Hook
+44 (0)20 7936 8989 or sara.hook@pulseconferences.com
2017 Association & Media Partners
Isc2
Clubciso Logooo
ISACA Barcelona4c Trans
http://www.isacabcn.org/index.php/ca/
Please email info@pulseconferences.com or call +44 (0)20 7936 8989 if you are interested in:
“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
Blueliv (Official Sponsor, CISO 360 Congress 2017)
“Excellent conference, brilliantly put together. Look forward to the next one!”
Anthony Young, Partner, Bridewell Consulting (Official Sponsor, CISO 360 Congress 2017)
Cisco With TM Cisco Blue
Cisco (NASDAQ: CSCO) is the worldwide technology leader that has been making the Internet work since 1984. Our people, products, and partners help society securely connect and seize tomorrow’s digital opportunity today. Discover more at www.cisco.com/sg/security and follow us on Twitter at @Cisco
Gigamon
Gigamon delivers network visibility and analytics for digital apps and services across physical, virtual and cloud infrastructure enabling organizations to run fast, stay secure and innovate.
“Top class speeches and presentations at the CISO 360 Congress! Thanks for such a worthwhile and enjoyable time”
Marketing Director, Blueliv (Official Sponsor)
“Excellent conference, brilliantly put together. Look forward to the next one!”
Partner, Bridewell Consulting (Official Sponsor)
Unique sponsorship proposition
WordItOut Word Cloud
Association and Media Partners
Anomali
Cyberark Logo1
SailPoint
SailPoint’s identity management solutions provide complete visibility into who is doing what, what kind of risk that represents, and allows you to take action. It links people, applications, data and devices to create an identity-enabled enterprise. www.sailpoint.com
Qualys
Qualys, Inc. (NASDAQ: QLYS) is a pioneer and leading provider of cloud-based security and compliance solutions with over 9,300 customers in more than 100 countries, including a majority of each of the Forbes Global 100 and Fortune 100. The Qualys Cloud Platform and integrated suite of solutions help organizations simplify security operations and lower the cost of compliance by delivering critical security intelligence on demand and automating the full spectrum of auditing, compliance and protection for IT systems and web applications. Founded in 1999, Qualys has established strategic partnerships with leading managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, Fujitsu, HCL Technologies, HP Enterprise, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. www.qualys.com.
Darktrace
Darktrace is the world’s leading machine learning company for cyber security. Created by mathematicians from the University of Cambridge, Darktrace’s Enterprise Immune System uses AI algorithms that mimic the human immune system to defend enterprise networks of all types and sizes. Our self-learning approach is the first non-consumer application of machine learning to work at scale, across all network types, from physical, virtualized, and cloud, through to IoT and industrial control systems. By applying its unique, unsupervised machine learning, Darktrace has identified 30,000 previously unknown threats in over 2,400 networks, including zero-days, insider threats and subtle, stealthy attacks. www.darktrace.com.
Trendmicro
As a global leader in IT security, Trend Micro develops innovative security solutions that make the world safe for businesses and consumers to exchange digital information. With over 25 years of security expertise, we’re recognized as the market leader in server security, cloud security, and small business content security. Trend Micro security fits the needs of our customers and partners. Our solutions protect end users on any device, optimize security for the modern data center, and secure networks against breaches from targeted attacks. We deliver top-ranked client-server, network, and cloud-based protection that stops new threats faster, detects breaches better, and protects data in physical, virtual, and cloud environments. www.trendmicro.co.uk
RiskIQ
RiskIQ is the leader in digital threat management, providing the most comprehensive discovery, intelligence, and mitigation of threats associated with an organization’s digital presence. RiskIQ allows enterprises to gain unified insight and control over web, social, and mobile exposures. Our platform combines advanced internet data reconnaissance and analytics to expedite investigations, understand attack surfaces, assess risk, and take action against digital threats. www.riskiq.com
Cymmetria
Cymmetria is a startup offering a pioneering cyber deception solution, based on breadcrumbs and decoys that lead attackers away from valuable targets. With Cymmetria, organisations gain the ability to detect threats, shape attacker behavior, and mitigate attacks. Founded in 2014 by security experts Gadi Evron and Dean Sysman, Cymmetria is changing the asymmetry of cyber security, tilting the traditional security odds so that hackers are the ones left vulnerable. www.cymmetria.com.
NEWEPSBridewellLogoFinal1
Bridewell consultants are highly qualified and motivated cyber security experts. Our focus is to secure our clients’ information, technology, and networks from the many threats that they face. We provide leadership, understanding and solutions to allow our clients to benefit from the huge opportunities that the digital economy brings. We believe a strong defence and better cyber skills are essential in every organisation. We understand cloud technologies, cloud security and how to design, implement and review their deployment for a business. Bridewell are pleased to announce our company and our Audit & Review service has been recognised and certified by the National Cyber Security Centre – NCSC. www.bridewellconsulting.com
Blueliv
Blueliv is a leading provider of targeted cyber threat intelligence for large enterprises, service providers, and security vendors. Its cyber threat intelligence platform and data feed address a comprehensive range of cyber threats to turn global threat data into predictive, automated and actionable intelligence which detects, identifies, and helps stopping cyber threats. www.blueliv.com
Post event report - Coming soon
Testimonials – CISO 360 Series
 “If you want to hear real CISO experiences, you must attend this event!” –Chuan-Wei Hoo, CISO, ST Engineering, Singapore
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” – Thomas Foster, SailPoint
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” – Martyn Booth, CISO, Euromoney Institutional Investor PLC
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” – Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
– Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” – Catherine Coale, Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” – Joe Breen, Company85
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” – James Gosnold, Technology Services Head of Cyber Security, DWP
““A very thoughtful event, great networking and industrial expertise in the room to learn from!” – Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Philippe Besson, Europe Industries- Security Officer, Air Liquide GMS
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” – NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” – Colette Hanley, Chief Privacy Officer, Nokia Group
 “
Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” – Ben Bulpett, SailPoint
“By far the best event for 2018 I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Ali Zeb, Group CISO and Group DPO, MS Amlin
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding lineup of events from your organization!“
Christopher Rollan, Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
– Ali Zeb, CISO, MS Amlin
”Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Joe Dauncey, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
– David Colbourne, Information Security Manager, Lloyd’s of London
“”The best speaker line-up of any security conference in Europe!”
– Michael Colao, Head of UK Security, AXA
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, Brian Brackenborugh, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Sérgio Gonçalves, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” – Chucks Ojeme, CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic
networking opportunities, facilitating very interesting thought provoking conversations”
– Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Quentyn Taylor, Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared
their knowledge and experience with their peers in an open and collaborative manner under Chatham house
rules. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during 1×1 networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISO’s across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
– Stephen Khan, Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
Pedro Cunha, CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
-Sponsor testimonial, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, James Kwaan, President, (ISC)2 Scotland Chapter
“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” Luis Vilares, GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the
Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors,
but with less pressure. Excellent!”
– Irene Corpuz, Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” – James Chuka, Sailpoint
“”I found CISO360 Conference a great place to share ideas about current and future problems”
– Sonia Morales, Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
– Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
– Ramón Serres, Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO360 conference in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO360 and
look forward to this conference going from strength to strength”
– FC, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together. Look forward to the next one.”
– Anthony Young, Partner, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!“
Irene Corpuz, Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018