Archive · CISO 360 Global Congress

2nd CISO 360 Congress Lisbon, 20-22 June 2018

This event took place on 20-22 June, 2018 at Lisbon.

DATE20-22 June, 2018
VENUELisbon

2nd CISO 360 Congress
20-22 June, 2018
Marriott Hotel – Lisbon

Pulse would like to say a massive ‘thank you’ to all speakers, sponsors and delegates of the CISO 360 Congress 2018!

Dates and venue for 3rd CISO 360 Congress are 19-21 June 2019 – Rome! We hope to see you there.


Connecting minds and bridging silos on security by design – CISO as business innovator in the age of advanced technologies

Keynotes by:

  • Steve Wilson, Head of European Cyber Crime Centre (EC3), Europol
  • Chris Mohan, General Manager, Threat Research and Intelligence Security Operations, Telstra
  • Mikko Hypponen, Chief Research Officer, F-Secure
  • Martin Borrett, Distinguished Engineer, CTO, IBM Security Europe, IBM
  • Jonathan Luff, Co-Founder, Epsilon Advisory Partner & CyLon

International Speaker Panel:

  • Adam Drabik, CISO, Opel Vauxhall Finance
  • Aftab Afzal, Vice President EMEA, enSilo
  • Ali Zeb, CISO, MS Amlin
  • Andy Chandler, SVP, Blueliv
  • Ben Bulpett, EMEA SecurityIQ Director, SailPoint
  • Ben Jeffreys, Director, Nominet Cyber Security
  • Beverley Allen, Head of Information Security Assurance, Old Mutual Wealth
  • Brian Brackenborough, CISO, Channel 4
  • Brian O’Toole, CISO, Ericsson
  • Carole Embling, Information Security and Governance Lead, BMJ Publishing Group
  • Dr. Cheryl Hennell, Former CISO, OpenReach
  • Chris Wilkinson, Director for Governance, Risk and Compliance, Bridewell Consulting
  • Colette Hanley, Global Head of Privacy, Nokia Group
  • Conal Doherty, IT / Information Security and Access Control Manager, RES
  • Derek Cheng, Chief Security Officer, TalkTalk
  • Dinis Cruz, CISO, PhotoBox
  • Daniel Brunner, Head of Security & Architecture, RUAG Schweiz / RUAG Defence
  • David Marques, Representative, AP2SI
  • David Higgins, Technical Director EMEA, CyberArk
  • Dr. Eduardo Solana, Senior Lecturer of Cryptography and Security, University of Geneva and University of Applied Sciences
  • Edward Ganom, CISO, Commercial Bank of Qatar
  • Ewen O’Brien, Head of EMEA, BitSight Technologies
  • Francisco Fonseca, CEO, Anubis Networks – a Bitsight company
  • Gadi Evron, Founder and CEO, Cymmetria and Chairman, Israeli CERT
  • George Eapen, CISO & Leader- Digital Technology Leadership Program, MENAT, General Electric
  • Graham Edwards, Group Head of Security, Nationwide
  • Greg Jones, Director and Founder, F-Secure Digital Assurance
  • Holly Foxcroft, Apprenticeship Executive STEM – NeuroDiversity Consultant
  • Kieran Combes, Global Red Team Manager, Marks and Spencer
  • James da Lança, Senior Cyber Security Manager, Darktrace
  • James Gosnold, Head of Cyber Technology Services, DWP
  • James Kwaan, Cyber Security and Privacy, Lloyd’s Banking
  • James Turrell, BISO, John Lewis Partnership
  • Jamie Douglas, Regional Sales Manager, Northern Europe, IBM Resilient
  • Joe Dauncey, Director, Security Engineering, Inmarsat
  • José Alegria, Chief Security Officer, Altice Portugal
  • Justin Shaw-Gray, Sales Director, Synack
  • Holly Foxcroft, Apprenticeship Executive STEM – NeuroDiversity Consultant
  • Lady Olga Maitland, Founder and CEO, Defence and Security Forum & Copenhagen Compliance
  • Marcus Alldrick, Former CISO, Lloyd’s of London, Advisor, Santander
  • Mark Ampleford, Director Security Division, Barclay Simpson
  • Mark Howell, VP UKI / Europe, Attivo Networks
  • Mark Felegyhazi, CEO, Avatao.com
  • Matthias Muhlert, CISO, HELLA
  • Katie Hall, Senior Cyber Security Manager, Darktrace
  • Michael Colao, Head of Security UK, AXA
  • Dr. Mike Humphrey, DSO / Head of Security Standards and Security, National Crime Agency UK
  • Marc Lueck, CISO, Company85
  • Neil Jarvis, Director of Information Technology, Aston Martin Lagonda
  • Nuno Teodoro, Chief Information Security Officer, Truphone
  • Paul Heffernan, Group CISO, Unipart
  • Paulo Moniz, Director – Information Security and IT Risk, EDP – Energias de Portugal
  • Paulo Martins, Head of Information Technology, Cybersecurity Governance Risk and Compliance, Euronext
  • Patryk Pilat, Head of Pre Sales Engineering, Blueliv
  • Paul Brucciani, Business Development Executive, Garrison
  • Peter Connolly, Co-founder, The Exercise Group7
  • Quentyn Taylor, Director of Information Security, Europe, Middle East and Africa, Canon
  • Richard Bach, Co-founder & Director, XQ Cyber
  • Richard Jones, CISO, SecureLink
  • Dr. Robert Coles, Visiting Professor, Royal Holloway, University of London
  • Rob Robinson, Director of Security & Network Services, Company85
  • Robert Shaw, Senior Security Advisor, United Nations
  • Dr. Sally Leivesley, Director, Newrisk and TEG7
  • Professor Sérgio Nunes, Information Security, ISEG – Lisbon School of Economics & Management
  • Stephen Khan, Head of Technology & Cyber Security Risk, Group Information Security Risk, HSBC Holdings plc
  • Tim Holman, Founder and CEO, 2-sec
  • Dr. Victoria Baines, Visiting Associate, Oxford Internet Institute
  • Dr. Vasileios Karagiannopoulos, Institute of Criminal Justice Studies, University of Portsmouth
  • Viktor Polic, CISO, Head of Information Security and Assurance Services, International Labour Organization and Adjunct Professor of Computer Science, Webster University Geneva
  • Yolande Young, Deputy CISO, Confidential

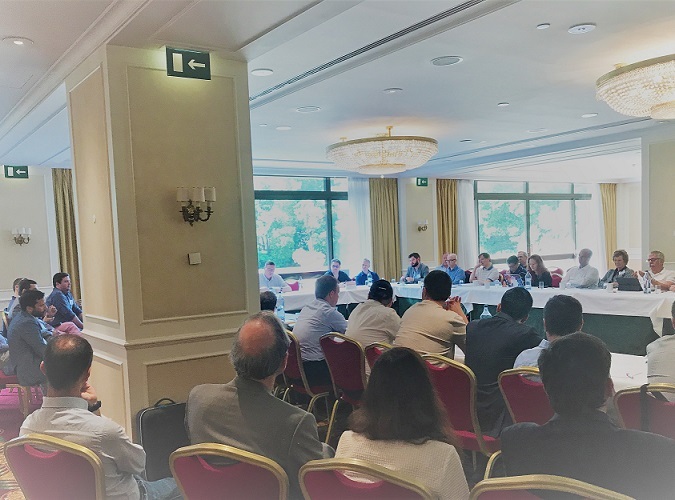
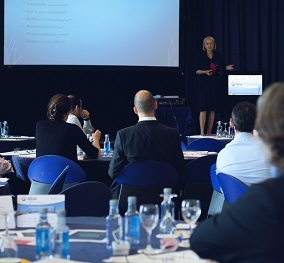
Participants were involved with a range of keynote addresses, topical debates, corporate case studies, deep-dive industry focuses, as well as the number of networking opportunities included in this event experience across two and a half action-packed days in Lisbon.

“Refreshing views of security topics for knowledge improvement!” Pedro Cunha, CISO, Credibom

“By far the best event for 2018 I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Ali Zeb, Group CISO and Group DPO, MS Amlin

What does good security look like? What is the new expectation? The agenda focused on a ‘360’ perspective for CISOs – to journey beyond the security realm. CISO 360 Congress provided a community base for creative thinking on emerging technological risks and on how companies are strategically using cybersecurity as a significant business enabler.

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Quentyn Taylor, Director of Information Security EMEA, Canon Europe

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Sergio Goncalvez, Corporate Security Manager, Logista

A boat cruise reception, seafood dinner, vineyard tour and BBQ, breakfast meet-up, roundtable discussions, extended coffee breaks, prize draw and lunches enabled delegates to network with industry leaders and put themselves at the heart of discussions involving those who make the world’s cybersecurity go around! See the photos here.

“Marvellous event, well-run, packed with useful content you can use” James Gosnold, Technology Services Head of Security, DWP

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” Luis Vilares, GRC Specialist, Euronex

Pulse would like to say a massive ‘thank you’ to all speakers, sponsors and delegates of the CISO 360 Congress 2018!

Many thanks to all Sponsors of the CISO 360 Congress 2018 Lisbon!

Platinum Sponsor 2018

Gold Sponsors 2018

CISO Breakfast Sponsor 2018

Silver Sponsors 2018

Bronze Sponsor

Lunch Sponsors

Panel Sponsors

White Papers for the 2nd CISO 360 Congress

White Papers from Garrison

Find white papers on the Garrison website: https://www.garrison.com/resources.php.
The most relevant articles are:
https://www.garrison.com/documents/CD00000101.pdf
https://www.garrison.com/documents/CD00000128.pdf

2018 Supporting Associations

“AP2SI – Associação Portuguesa para a Promoção da Segurança da Informação is a private, non-profit association created in 2012 by security professionals and other like-minded people. It is focused on raising awareness in Portugal for all matters Information Security and related topics such as cybersecurity or privacy. It does this through the promotion of best practices and the organization and divulgation of events, conferences and other initiatives to bring the topic close to the society.”

www.ap2si.org

With thanks to our sponsors

Platinum Sponsor

Gold Sponsors

CISO Breakfast Sponsor

Silver Sponsors

Bronze Sponsor

Silver & Cocktail Sponsor

Lunch Sponsors

Panel Sponsors

Unique sponsorship proposition

Double Deal?

2017 Association & Media Partners

  • 20-22 June: PROGRAMME 2nd CISO 360 Congress
  • 18-19 June: OPTIONAL PRE-CONGRESS TRAINING: Cyber Attacks – the Risk and the Fix

20-22 June: PROGRAMME 2nd CISO 360 Congress

2nd CISO 360 Congress Programme

Download Brochure CISO 360 Congress 2018

What does good security look like? What is the new expectation? The agenda focuses on a ‘360’ perspective for CISOs – to journey beyond the security realm. CISO 360 Congress provides a community base for creative thinking on emerging technological risks and on how companies are strategically using cybersecurity as a significant business enabler.

To learn more about speaking opportunities or to suggest topics or speakers you would particularly like to hear from please contact: sara.hook@pulseconferences.com

When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.

Experience + value = story.

  • do you have a compelling business security story that simply must be told?
  • have you recently worked on an innovative security project?
  • are you willing to openly share inspiring insights, expertise and ideas to advance the security community?

We are always looking for:

  • keynote insights, cutting-edge ‘live’ demos, deep dive workshop ideas
  • new best practice case studies, fresh ideas, forward thinking topics on security and governance matters
  • sessions with actionable takeaways and positive contributions to the output reports
  • the world’s smartest thinkers and doers in security, cyber, privacy, resilience, risk, governance, compliance

We welcome your input into shaping the agenda and speaker panels.

Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.

For further information, please

+44 (0)20 7936 8989
or
sara.hook@pulseconferences.com

18-19 June: OPTIONAL PRE-CONGRESS TRAINING: Cyber Attacks – the Risk and the Fix

Cyber Attacks – the Risk and the Fix
18-19 June, Lisbon

Over two days, delegates are shown the reality of just how easy real cyberattacks can be – even those with the most devastating effects – and the implementation of simple measures to avoid catastrophic risk. The practical elements are comprehensively taught in a walk-through manner to demonstrate the vulnerabilities in realistic targets. A key theme running through the course is that of workforce vulnerability – no matter how well defended the organisation’s intellectual property is, the staff are the way in.

Register for Cyber Attacks – the Risk and the Fix

Day One – The Risk
• Introduction to Cyber Risk
• Attacker Methodology
Part One – reconnaissance
Part Two – Attack
• The Persistent Threat of Leaked Data
• Wi-Fi – the Corporate and Personal Risk

Day Two – The Fix
• Real world examples of damaging attacks are dissected, with particular emphasis on correct implementation of cyber incident response
• Exercise: Attack the Corporation. The art of incident response
• The Devastation. Lessons learned from a vast number of cyber incident responses
• The technical penetration test – learning why most companies waste time and money with incomplete or ineffective testing

About the trainer:
North Cyber are team of former intelligence officers with expertise in covert online operations and digital forensics. The company teaches government and corporate clients how find and fix the unseen holes in their security. They specialise in all levels of capability including low-tech and no-tech hacking, using freely available information to circumvent vastly expensive but ineffective security systems. The teaching draws on many and varied real-world examples from the private and government sectors, from the perspectives of the attacker and incident responder. Participants in these courses will evaluate their own experience on the course in gaining additional skills and understanding of the threats to their organisation and they will gain confidence in tackling these catastrophic risks to the comparate or government operation.

Details
Duration: 2-day training course
Dates: 18-19 June 2018
Location: Lisbon Marriott
Price: £1,500

Special 5-day package: BOOK TRAINING AND CONGRESS

2nd CISO 360 Congress + Course (18-22 June 2018)

Pay – £2,300 (saving £300)

SPEAKERS
2nd CISO 360 Congress, 20-22 June, 2018 Lisbon

Keynotes by:

Steve Wilson
Head of European Cybercrime Centre (EC3)
Europol

Steven originates from Ayrshire, Scotland. He was a Police Officer in Scotland from 1985-2015.
During this time, he served with Strathclyde Police, Scottish Crime and Drug Enforcement Agency, Her Majesty’s Inspectorate of Constabulary and, since 2013, with the reorganisation of policing in Scotland into a national force, Police Scotland. Steven performed a variety of senior Detective roles and was responsible for the national units in Scotland delivering: witness protection, covert technical policing, fugitives, undercover policing, assisting offender programme and all forms of cybercrime and cyber enabled crime including online child protection. Steven was the Scottish representative on UK cyber governmental and policing groups and led on industry and academic partnership groups on cyber resilience in Scotland. Steven has also worked in covert policing, major investigations, sex offender management, Counter Terrorism investigations and represented the UK on International policing matters. Steven commenced as Head of EC3 on 18 January 2016.

Mikko Hypponen
Chief Research Officer
F-Secure

Mikko Hypponen is a worldwide authority on computer security and the Chief Research Officer of F-Secure. He has written on his research for the New York Times, Wired and Scientific American and lectured at the universities of Oxford, Stanford and Cambridge. He sits in the advisory boards of EUROPOL and the Monetary Authority of Singapore.


Chris Mohan

General Manager, Threat Research and Intelligence Security Operations
Telstra

Chris Mohan has worked for fortune 50 companies security teams, bringing insight and actionable measures to those firms’ security posture and responsibilities. Chris’ career has had him in grow from a world of front line IT operations through to advising and guiding those in boardrooms. His drive is to instil relevant, intelligent and practical security controls and practices that securely enable the business in an unpredictable online world. Chris became one of the few to achieve the prestigious GIAC Security Expert (GSE) certification and holds a number of other security and vendor qualifications.

Martin Borrett
Distinguished Engineer, CTO, IBM Security Europe
IBM

Martin Borrett is an IBM Distinguished Engineer and CTO IBM Security Europe. He advises at the most senior level in clients on policy, business, technical and architectural issues associated with security. Martin leads IBM’s Security Blueprint work and is co-author of the IBM Redbooks “Introducing the IBM Security Framework and IBM Security Blueprint to Realize Business-Driven Security” and “Understanding SOA Security”. He is Chairman of the European IBM Security Board of Advisors, represents IBM at GFCE and ECSO, is a Fellow of the British Computer Society, a Chartered Engineer (CEng) and member of the IET. Martin has a passion for sailing and has represented Great Britain; he is also a keen tennis player.

Jonathan Luff
Co-Founder
Epsilon Advisory Partner & CyLon

Jonathan Luff is the co-Founder of CyLon, the world’s leading cyber security accelerator and seed investment programme, supporting more than 50 startups and creating more than £175m of value since 2015. He is also the co-Founder of Epsilon Advisory Partners, where he works with some of the world’s fastest growing technology companies, including Nest, Dataminr, and Rubikloud.

Before founding CyLon and Epsilon, Jonathan was a senior British Diplomat, serving in a variety of roles including as an advisor to Prime Minister David Cameron.

International speaker panel

Enquire about becoming a speaker

We are always looking for:

  • keynote insights, cutting-edge ‘live’ demos
  • new best practice corporate case studies, fresh ideas, forward thinking topics on security and governance matters
  • sessions with actionable takeaways and positive contributions to the output reports
  • the world’s smartest thinkers and doers in security, cyber, privacy, resilience, risk, governance, compliance

We welcome your input into shaping the agenda and speaker panels.

Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.

For further information, please contact Sara Hook
+44 (0)20 7936 8989 or sara.hook@pulseconferences.com

Speakers

Download brochure

Presentation agenda

Advisory Committee

CISO 360 Congress
(5-6 July) Chaired by:

Marcus Alldrick
Head of Digital Risk Management and Compliance
Lloyd’s of London

CISO 360 Boardroom
(7 July) Chaired by:

Professor Robert Coles
Chief Information Security Officer / Head of Information Protection & Privacy
GSK

Fireside chats with

International speaker panel

Shape the Programme

We welcome recommendations and ‘wish lists’ for new speakers, topics and feedback on innovative formats for these dynamic ‘live’ events.

  • Is there an industry luminary that you’ve always wanted to meet?
  • Is there a company, industry sector or country that is ahead of the curve that you would like to benchmark approaches with?

Read the programme

Enquire about becoming a speaker

When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.

Experience + value = story.

  • do you have a compelling business security story that simply must be told?
  • have you recently worked on an innovative security project?
  • are you willing to openly share inspiring insights, expertise and ideas to advance the security community?

We are always looking for:

  • keynote insights, cutting-edge ‘live’ demos, deep dive workshop ideas
  • new best practice case studies, fresh ideas, forward thinking topics on security and governance matters
  • sessions with actionable takeaways and positive contributions to the output reports
  • the world’s smartest thinkers and doers in security, cyber, privacy, resilience, risk, governance, compliance

We welcome your input into shaping the agenda and speaker panels.

Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.

For further information, please

+44 (0)20 7936 8989
or
sara.hook@pulseconferences.com

20150331_140518_face-1

Adam Drabik

CISO, Opel Vauxhall Finance

Adam has 25 years international experience in managing IT and Information Security mainly in Oil & Gas, Pharmaceutical, Consumer Goods, Telecommunication and Financial Services industries. Founding member of ClubCISO, Consumer Goods Security Forum in the UK and Information Security Forum in Malaysia – peer groups of CISOs and Heads of Information Security formed to exchange good practices and experience within specific focus groups. Adam has significant experience consulting and advising boards of directors of FTSE100/Fortune500 companies on Information Security, Privacy, Risk Management and Resilience. The current role is Chief Information Security Officer at Opel Vauxhall Finance.


Aftab-Afzal-photo

Aftab Afzal

Vice President EMEA, enSilo

VP of EMEA , 20 of year’s experience in the Cybersecurity field, representing leading and disruptive security vendors to assist global organisations in securing digital assets and defending cyber-attacks. Well versed in Endpoint, Network and Internet Defences.

Ali-Zeb

Ali Zeb

Group CISO & Group DPO, MS Amlin

Ali specialises in security transformation of businesses as an executive security consultant and security strategy advisor, delivering global security at strategic, tactical and operational level with security compliance, risk, and audit, across multiple frameworks. He has over 20 years’ experience in IT and Information Security within multiple sectors focusing on bridging the gap between business and security. Alongside heading global security Ali has been appointed as GRC and Group Data Protection Officer for many organisations. Ali is currently Group Chief Information Security Officer and Group Data Protection Officer at MS Amlin. Member of FCA Insurance Sector Cyber Coordination Group (ISCCG), Lloyds Cross Market Cyber Risk Forum and an Advisory Board member for InfoSecurity Europe.

Andy-Chandler

Andy Chandler

Senior Vice President, Blueliv

Andy has over twenty five years’ experience in the technology sector, previous to this he spent over 8 years in the UK military. He most recently has spent the past five years building Fox-IT’s from the Netherlands Web & Mobile Analytics business called DetACT, which provides real-time visibility of all Mobile & Webs events. Andy was also responsible for the creation and lead the threat intelligence proposition called InTELL, the same worked on some of the biggest Global Law enforcement investigations including Target, Swift & the hunt for Slavik and his business club. He also played an integral role in M&A process which culminated in a commercial sale to NCC in Dec 2015.

ben-bulpett

Ben Bulpett

EMEA Security IQ Director, SailPoint

Ben is the SailPoint EMEA Security IQ Sales Director, where he is responsible for leading SailPoint’s Identity & Access Governance for Files and Data platform across the EMEA region working with the local sales teams, partners and customers. He works across the organisations lines of business in the evolution of the product and go to market strategy and speaks on the topic of Identity Governance for Files and Data for SailPoint in the EMEA region. With over 25 years’ experience in software sales leadership positions; Ben’s knowledge of Software Identity Market is extensive.

Ben has travelled extensively throughout Europe, Middle East & America both through his work responsibilities and with his family. He has spoken at numerous events on matters such as security, identity management, software compliance, system mapping and Global Account Management.

ben-jeffreys

Ben Jeffreys Account Director

Nominet Cyber Security

Ben serves as an Account Director of Cyber Security division at Nominet. In this role, he leads the efforts of helping enterprise customers manage their cyber risk and compliance requirements. Prior to joining Nominet, Ben held sales positions at Cognosec, NTT Europe and others, where he was responsible for taking cyber risk solutions to market. Ben holds a BA degree from the Bournemouth University.

Beverley Allen

Head of Information Security Assurance, Old Mutual Wealth

Brian-Brackenborough

Brian Brackenborough

CISO, Channel 4

As the CISO at Channel 4 Television, Brian reports into the Chief Technology Officer and has responsibility for the Cyber Security of the company’s staff, systems and data. During the 6 years that he has worked at Channel 4, Brian has worked to deliver a robust and comprehensive security capability, incorporating not only the technical aspects of his role but also the ongoing governance and assurance necessary to protect the estate. Prior to Joining Channel 4, Brian spent 13 years at the BBC in roles that covered cyber security oversight of areas including Worldwide, Journalism, Monitoring and Radio, rising up to Interim Head of Information Security. In 2017 Brian was nominated as a top 100 global CISO ‘s and was awarded the Unsung Hero award for Media and Entertainment.

Brian-OToole

Brian O'Toole

CISO, Ericsson

Brian has been at Ericsson since 2005, working across several different areas including software development, product management and information security. He has been the CISO since 2015, and he is primarily focussed on Information Security Risk Management in Telecommunications & cyber security strategy

Carole-Embling-e1528827486891

Carole Embling

Information Security and Governance Lead, BMJ Publishing Group

Carole has worked in the world of Information Security since the turn of the century, first in Royal Mail as the Compliance, Communications and Awareness manager for the whole Group, having spent the 20 years ‘learning the business inside out’. She then spent 6 years at Prudential Group Head Office working on group-wide Information Security compliance. Since leaving the Pru in 2014, Carole has worked at BMJ Publishing Group as their Information Governance and Data Protection Lead. As you can imagine much of her time and effort has been taken up in getting a small
Publishing house with an international reputation ready for GDPR.”

CHRIS-WILKINSON

Chris Wilkinson

Director for Governance, Risk and Compliance, Bridewell Consulting

Chris joined Bridewell Consulting in early 2018 as the Director and Practice Lead of Governance, Risk and Compliance, he is responsible for supporting clients with successfully gaining security certifications, such as ISO27001, creating unifying security architectures, and advising on value adding cyber security governance, risk and compliance measures. Before joining Bridewell Consulting, Chris worked in PWC’s Cyber Security Practice focused mainly on public sector and critical national infrastructure providers. Prior to this he worked in KPMG’s Information and Business Protection practice working with multinational telecommunication firms and several major UK government departments. Before working in consulting, Chris served as a Commissioned Officer within the Communications Engineering branch of the Royal Air Force serving in numerous roles within the UK and Afghanistan.

colette-hanley

Colette Hanley

Global Head of Privacy, Nokia Group

Colette has a proven track record of interpreting security and privacy regulatory and industry requirements for the corporate environment. She has held leadership roles in Microsoft, global banking and the gaming industry focussing on designing, implementing and maintaining security and privacy programmes. She has led international Tier 1 organisations to successful PCI DSS certification and managed global ISO/IEC 27001:2005 certification programmes. As Global Head of Privacy for Nokia Group, she is responsible for overhauling privacy across the business and ensuring it becomes embedded in Nokia’s diverse range of activities, operations, products and services. Her motivation and objective is comprehensive reduction of privacy risk for the business and for the individual, as well as confidence that data-driven innovation is ethical. Colette gained a Distinction, MSc. Information Security at Royal Holloway, University of London. She is CISSP, CISM, CIPP, CIPM and holder of BCS Certificate in IT Law.

David-Marques

David Marques

Representative AP2SI

In 1999, designed in and created the first Portuguese data recovery lab. Since then, I’ve been working as Technical Manager of the lab. In 2007, designed a new company department related to computer forensics services and I’ve been working as Technical Manager with it too.
Besides that, I’m leading the R&D projects inside the company. Specialties: Data Recovery; Information Security; Incident Response; Computer Forensics and Log analysis; Cyber Fraud Investigation; Malware and Vulnerability Analysis; ISO27001 Consulting and Auditing; Penetration Testing.

David-Higgins-Bio

David Higgins

Technical Director, EMEA, CyberArk

David Higgins is the Director of Strategic Accounts, EMEA at CyberArk. With over 10 years’ experience in Privileged Account Security, David is one of the leading experts in understanding the requirements and drivers for managing privileged access security within an organisation, both private and public. David has led some of the largest design and implementation programs of privileged account security with companies across all sectors, many of which are in the Fortune 100. Leveraging this experience, David now works with clients on best practices around privileged management and driving innovative approaches when looking to reduce the risk associated with privileged escalation and exploitation, even more so as organizations embrace cloud platforms and automated processes.

Derek-Cheng

Derek Cheng

Chief Security Officer, TalkTalk

Derek is an experienced information security leader with over 19 years of professional experience in information and cyber security, IT, risk management, privacy and data compliance. Derek has recently joined TalkTalk as their Chief Security Officer, where he is building and leading the cyber security strategy and team to protect TalkTalk’s critical infrastructure, assets, and customer data. Previously, he was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, Derek spent over 6 years at Deloitte & Touche where he managed and performed a multitude of information security and risk management engagements for several global Fortune 500 companies across various industries including financial services, technology, consumer business, manufacturing, and public sector. His primary areas of expertise include developing and leading tactical and strategic security strategies, building and maturing security teams, and ensuring executive governance around security to manage risks appropriately. Derek has also published information security articles and white papers and has been a presenter/panellist at CISO conferences. Derek holds a Bachelor Degree in Computer Science from the California Polytechnic State University, San Luis Obispo CA.

Dinis-Cruz_400x400

Dinis Cruz

CISO, PhotoBox

Dinis Cruz is the CISO of the PhotoBox Group and highly involved with OWASP (project leader for OWASP O2 Platform, OWAPS Maturity Models tool and key organiser of the OWASP Summits in 2009, 2011 and 2017).

daniel-brunner

Daniel Brunner

Head of Security & Architecture, RUAG Schweiz / RUAG Defence

Daniel Brunner, Head of Security and Architecture, RUAG AG Switzerland is aSenior Information Security expert & Project Manager with an MBA and 15 years of experience. Recognized ability to manage Complex IT Environments inside multiple business organizations. Specific expertise in Project Management, Risk Management within the IT Domain. ISMS (Information Security Management System) installed and developed during several years. Proven ability to design security solutions with in-depth operational supervision of incidents and emergency disaster recovery. IT Governance and audit conformity experience coupled with investigation coordination with legal departments and Human Resources to produce proof or policies to defend and protect the company from threat – yet still enabling business to continue in a secure manner. He was previously CISO of Leumi Private Bank and has held senior positions at UBS. He is the VP at DEFCON Switzerland.

Eduardo-Solana

Dr. Eduardo Solana

Senior Lecturer of Cryptography and Security, University of Geneva and University of Applied Sciences

Dr. Eduardo Solana is Senior Lecturer of Cryptography and Security in the University of Geneva and in the University of Applied Sciences also in Geneva, Switzerland. Amongst others, he has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has more than twenty years of experience in the fields of cryptography and information security both in the private sector and the academia.

Edward-Ganom

Edward Ganom

CISO, Commercial Bank of Qatar

Edward Ayman Ganom is a senior cybersecurity expert with over 15 years of international experience in information security architecture and technology risk management. He currently holds the position of CISO at The Commercial Bank in Qatar. Previously, Edward held several key technology and risk management positions in the financial and public sectors in the USA and the Middle East. He participated in drafting national cyber security policies and strategies and cybercrime legislation. Edward holds two bachelor degrees, one in Electronics Engineering and one in Political Science from two American universities. He is a Certified Information Systems Security Professional (CISSP) and is a recognized speaker at technology, security and risk conferences.

Ewen-OBrien

Ewen O’Brien

Head of EMEA, BitSight Technologies

Prior to joining BitSight, Ewen was part of the founding team in OpenPages EMEA, the market leading Governance, Risk and Compliance solution, that was acquired by IBM in 2012.He headed up financial services, where he helped expand the business, most notably in Europe, Africa and Asia

FRANCISCO-FONSECA

Francisco Fonseca

CEO, Anubis Networks – a Bitsight company

Francisco has over 15 years’ experience in the telecommunication industry implementing and managing email platforms for corporate and ISP environments. He previously founded Crashless, and worked at Vodafone Portugal. He is also Vice President of the National Association of Young Business People and has taught at Moderna and Nova Universities.

George-Eapen

George Eapen

CISO & Leader- Digital Technology Leadership Program, MENAT General Electric

George Eapen is Chief Information Security Officer (CISO) for GE in Middle East, North Africa & Turkey In his role, George is responsible for defining Cyber Security strategy for Enterprise IT & OT for the region and provide strategic leadership to IT Security related projects & initiatives for all GE businesses in the region. George is also responsible for protecting GE critical assets in a growing region which spans 18 countries and 7000 work force George joined GE in 2006 with GE Healthcare in India and has since held roles of increasing responsibilities and progressed to his most recent role as Chief Information Security Officer for MENAT. During his tenure with GE, George worked in multiple domains (Product Life cycle management, ERP, Infrasrture, Supply Chain & Commercial IT) and multiple businesses (GE Healthcare, GE Appliances, GE Capital, GE O&G, GE Aviation and GE Corporate) George is a graduate of GE IT leadership program (ITLP), GE Six Sigma Black Belt program and graduate of GE Executive leadership program (CAS)

gadi-evron

Gadi Evron

Founder and CEO, Cymmetria

Gadi is the Founder and CEO of Cymmetria, a cyber security startup that is pioneering the space of cyber deception. He is also Founder and Chairman of the Board of the Israeli CERT, Founding Chairman of the Cyber Threat Intelligence Alliance (CTIA), and Founder of the Israeli Government CERT. Gadi is widely recognized for his work in Internet security operation and global incident response, and is considered the first botnet expert. Prior to founding Cymmetria, Gadi was VP of Cybersecurity Strategy for Kaspersky Lab, led PwC’s Cyber Security Center of Excellence (located in Israel), and was CISO of the Israeli government’s Internet operations. He has authored two books on the topic of information security, organizes global professional working groups, chairs worldwide conferences, and is a frequent lecturer.

graham-edwards

Graham Edwards

Group Head of Security, Nationwide

The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He currently holds the position of Director of Data Security at Nationwide Building Society. Graham has a master’s degree in Information Security from Royal Holloway.

Holly-Foxcroft

Holly Foxcroft

NeuroDiversity consultant and Cyber Security Lead, Highbury College

Holly Foxcroft NeuroDiversity consultant and Cyber Security Lead at Highbury College. Holly started her career in electronic and communications warfare. Stepping aside from a technical discipline Holly is a NeuroDiversity Consultant and leads Cyber Security apprenticeships and course development for Highbury College. Holly has worked as a consultant in the cyber security industry alongside employers to engage, recruit and retain a cyber security workforce.

joe-dauncey

Joe Dauncey

Director, Security Engineering, Inmarsat

Joe Dauncey has been working in security for over 20 years, across energy, telecoms, maritime and aviation sectors. Joe led an (award winning) programme of transformational security change in the energy sector, chaired the Energy Networks Association Cyber Security Group, represented security stakeholders on the UK smart metering programme, and is currently embedding Security Engineering capabilities and competencies in the satellite communications sector. Joe has supported a number of academic and research programmes in the field of critical infrastructure and security, but has not yet established a sustainable control for his childrens Internet usage.

James-Kwaan

James Kwaan

Cyber Security and Privacy Consultant, Lloyd's Banking (and President, (ISC)2 Scotland)

James Kwaan has worked for a number of blue chip companies in Simulation, Energy and Financial Services. He is a former director of Information Security (CISO) and Global data protection officer. In his spare time he is President of (ISC)2 Scotland and Vice President of ISACA Scotland. He is a recognised expert in

Information Security and in 2017 was awarded three prizes for his contribution: Malcolm Turner Memorial Prize for outstanding contribution to Risk Management and Information Security, Wayne K. Snipes prize for best European Chapter and Cyber Evangelist of the year at the Scottish Cyber Awards. James is currently working for Lloyds Banking Group.

James_De_Lanca_head_shot

James da Lança

Senior Cyber Security Manager, Darktrace

James da Lança is a Senior Cyber Security Manager at Darktrace. He currently works with a broad range of clients in EMEA. He leads Darktrace’s efforts in Portugal and is responsible for the company’s expansion in the country’s market. Prior to Darktrace, James worked with a number of different start-ups, with a focus on early stage development, before moving into the artificial intelligence industry of cyber defense. He now supports organisations across all verticals in the implementation of Darktrace’s end-to-end detection and response platform, thus managing their enterprise security risks.

James-Turrell-Picture

James Turrell

Business Information Security Officer, John Lewis Partnership

Working within the John Lewis Data Privacy and Information Security Office, James is responsible for PCI compliance and Information Security, both of these areas enable the John Lewis Partnership to protect the data of our Customers and Partners. Working closely with the Data Privacy Office allows a holistic view of compliance to data protection laws, information security frameworks and regulations allowing delivery of the transformation programmes that provide trust and transparency – resulting in greater brand experiences across our digital, mobile and e-commerce channels.

james-gosnold

James Gosnold

Head of Cyber Technology Services, DWP

Technology Services Head of Cyber Security. Developing & delivering live security services for DWP Digital; incubating future technologies that meet Digital 2020 user stories whilst ensuring great outcomes for the customer.

Jamie-Douglas-1-e1528893036173

Mr. Jamie Douglas

Regional Manager, Northern Europe IBM Resilient

Jamie currently heads up IBM Resilient’s business development efforts in the UK. Jamie has over 13 years experience in information security, and has spent the last 3 years working with some of the largest organisations in Europe helping them build out and transform their cyber response capability.

Kieran-Combes

Kieran Combes

Global Red Team Manager, Marks and Spencer

Kieran is the Red Team manager at Marks and Spencer. He has a background in ethical hacking and penetration testing working as a consultant across a wide range of organisations including banking, financial services, government, defence, retail, pharmaceutical and NGO’s.

Having worked in Security for over 10 years Kieran has a wealth of experience in breaking into computer systems and organisations, he now uses that knowledge to develop, prioritise and execute red team scenarios at Marks and Spencer

lady-olga-maitland

Lady Olga Maitland

Founder and CEO, Defence and Security Forum & Copenhagen Compliance

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.-

Matthias-Muhlert

Matthias

Muhlert, CISO, HELLA

Matthias Muhlert is a dedicated and highly qualified IT Security Professional with a consistent track record of success spanning over 19 years of diversified experience developing and implementing IT security processes as well as leading IT security governance programs.
Main areas of expertise are in the development and implementation of solid IT infrastructure and network security systems, polices, governance and crisis response, with especial skills in security infrastructure, analysis, response, compliance and ISMS according to ISO 27001.

Matthias Muhlert works currently as Chief Information Security Officer of HELLA in
Lippstadt and is responsible for global information security management in more than 30 countries.
Before HELLA, Matthias Muhlert worked as department head at the Chief Security Office of UniCredit Bank in Munich being responsible for the complete IT Security Management of several large international branches.

Mark-Howell-6

Mark Howell

VP UKI / Europe Attivo Networks

Mark Howell is the Attivo Networks Vice President of UK and Ireland /European Operations. Mark is responsible for scaling the Attivo customer development efforts around its ThreatDefend™ Deception and Response Platform by leveraging his 20+ years’ experience in developing enterprise and channel distribution partnerships throughout the region.
Prior to joining Attivo Networks, Howell was the UK and Ireland Country Manager for BDNA (acquired by Flexera), where he managed the software supply chain company’s operations in the region for the past two years. Before joining BDNA, Howell was the Country Manager of fast-growing wireless LAN provider Meru Networks (acquired by Fortinet). At Meru, Howell received the International Sales Manager of the Year Award in 2009. Howell also brings extensive experience managing the EMEA distribution channel for Juniper Networks and Cisco.

michael-colao

Michael Colao

Head of Security UK, AXA

Michael has been the head of security for AXA in the UK for more than five years. Prior to that he was a director of Downtown Associates, an information security and privacy consultancy, where he assisted firms in the Lloyd’s Insurance market. Previously to that he was the Global Head of Information Security as well as the Global Head of Privacy and Data Protection for the investment bank Dresdner Kleinwort, Michael has a strong side-interest in computer forensics and in the management of digital evidence. He graduated from the Massachusetts Institute of Technology in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services in London.

Dr. Mike Humphrey

DSO / Head of Security Standards and Security, National Crime Agency

Mike was a police officer for 30 years. The latter 5 years of his career he was a senior officer seconded to a central government agency involved in the security of the Police National Network, a UK wide IP comms and data network. He is now Head of Security at the National Crime Agency. He is a fellow of the Institute of Information Security Professionals (IISP) an elected member of the Information Assurance Advisory Council’s (IAAC) management committee and a Government Liaison Panel representative on the IAAC Board. His qualifications include an MSc in IT Security; ISO27001 lead auditor and a SANS GIAC holder. He has presented at numerous national and international conferences. Mike is currently working on a PhD (part time), at the Defence Academy, Cranfield University, Shrivenham, where he is researching the Critical Success Factors required to improve security incident reporting.

mark-apleford

Mark Ampleford

Director Security Division, Barclay Simpson

Mark is a recruitment and executive search specialist who heads the Security Practice at Barclay Simpson Corporate Governance Recruitment. He has 16 years’ experience of recruiting information security leadership roles in the UK and Europe.

mark-felelegyhazi

Mark Felegyhazi

Founder and CEO, Avatao

“I am interested in building security fundamentals into the software development lifecycle. I believe that giving developers the power to build secure software is the most effective way to protect against cyber attacks. No technology can be as creative and effective as a curious person with solid understanding of security issues. As the CEO of Avatao, I am responsible to build a hands-on, online exercise platform where developers and security professionals can try new security techniques, learn how to use developer tools securely and get to know the basic concepts in software security. In a former life, I was a security researcher at UC Berkeley, USA where our team used large-scale data analysis to understand and disrupt the underground economy of spammers.

Marc-Lueck-photo

Marc Lueck

CISO, Company85

Marc is a senior security practitioner with over 20 years of experience crossing multiple industry sectors, from financial services to publishing. For the past 7 years, he has led security improvement programmes for the likes of Pearson, T-Systems and Symantec. He is currently the CISO at Company85, where he runs the security practice with a focus on ensuring information security enables and supports business goals.

Marcus-Alldrick

Marcus Alldrick

Former CISO, Lloyd’s of London

Having worked in IT for nearly 40 years, specialising in information risk, protection, security and compliance for the latter 26 years or so, Marcus decided to retire in mid-2017 but was quickly lured back to take on an advisory role for a Tier 1 UK bank. At the start of 2018, Marcus also joined the Cymmetria Advisory Board as Chief Risk Officer.

In his previous role at Lloyd’s Marcus was responsible for ensuring that risks to IT and information were understood and correctly mitigated in a cost effective manner throughout the corporation, both in the UK and in its overseas locations. His role extended to providing second line of defence assurance to this effect to Executive, Senior and Line Management. Marcus also had corporate responsibility for Data Protection and Privacy and provided thought leadership on emerging digital related risks pertinent to the Lloyd’s market.

Prior to joining Lloyd’s, Marcus was a Principal Advisor for KPMG, working in IT Advisory and specialising in information security strategy definition and implementation. Before that Marcus was Head of Information Security for Abbey National plc, a leading UK bank, a position he held for six years following seven years as Information Risk and Security Manager for Barclaycard, a leading card issuer and merchant acquirer and part of Barclays plc.

Marcus doesn’t have much spare time but what he has he enjoys in Dorset on the South Coast of England where he and his husband live.

Max_Robin_head_shot

Max Robin

Senior Cyber Security Manager, Darktrace

Max Robin, Senior Cyber Security Manager at Darktrace, has extensive experience in the Cyber Security space, primarily in the world of SaaS and network security across all of EMEA and the US. From spending several years working at the centre of the technology industry in Silicon Valley, he has a firm grip on the challenges modern businesses are facing, and a strong pulse on the issues that are next to come. At Darktrace, Max continues to help organizations of every size and across all sectors to mitigate their enterprise vulnerabilities, both internally and externally.

Neil Jarvis

Director of Information Technology, Aston Martin Lagonda

Neil is one of the few IT Directors with an Information Security background. With over 25 years’ experience in both commercial and government information systems security and a proven track record in the specification, design and implementation of complex IT and security infrastructure solutions to meet business requirements. This experience includes network infrastructure, server infrastructure, operating systems, applications, information security, penetration testing, business requirements gathering, analysis, interpretation and delivery of pragmatic cost-effective solutions.

Nuno-Teodoro

Nuno Teodoro

Chief Information Security Officer, Truphone

Nuno Teodoro is an information security expert with over 10 year of experience having its expertise on Cybersecurity & Threat Intelligence Strategies, CSIRT & SOCs, Data Privacy and Application Security Programs. With a background of B.Sc. and M.Sc. in computer engineering, he is pursuing a Ph.D in Cybersecurity, with several published papers. Currently he is the Global Chief Information Security Officer (CISO) for Truphone, and as served as an Information Security Expert and Information Security Officer in multinational Organizations like Vodafone and Allianz. He is a board member of ISACA Portugal and is currently an invited professor in several universities scoping his lectures in Cybersecurity Strategies and Data Privacy initiatives

Paul-Heffernan

Paul Heffernan

Group CISO, Unipart

Paul is the Group CISO for Unipart Group of Companies. With nine years’ experience in the cyber security world, including consulting to some of the world’s biggest brands, he engages with the business at board level to enable trusted secure commerce. With an ‘ethical hacker’ background, he is able to address complex security challenges but is equally passionate about driving effective change through unambiguous leadership and communication. Paul is a regular speaker at various industry conferences such as the e-Crime Congress, PCI London and the GBI CISO Summit. When he isn’t keeping Unipart safe, you can find him tinkering with code

and figuring out how to inspire the next generation of cyber security professionals. Paul is proud to be shortlisted as CISO of the Year 2017. You can reach him on LinkedIn or on Twitter at @pjh_22.

Paul-at-Garrison-bio

Paul Brucciani

Business Development Executive, Garrison

Garrison was founded in 2014 to solve one of cyber security’s most intractable problems: how to enable users to use the Internet without exposing themselves to its risks. Garrison has developed patented web isolation technology to provide hardware-enforced secure remote browsing for enterprise customers. I joined Garrison in 2017 to develop and manage its business across Europe’s commercial sectors.

My previous experience includes: telecoms and security consulting; account management and mineral exploration – prospecting mainly for gold.

I also like to blog on topics that interest me such as the psychology of risk decision-making, cyber security, forecasting and the utility of allegedly world-saving new technologies. I try to give readers a wryly original point of view that in some way makes their lives better.

Paulo-Martins

Paulo Martins

Head of Information Technology, Cybersecurity Governance Risk and Compliance, Euronext

Experience of more than 15 years in IT Governance, Risk and compliance, auditing, consulting (information systems and processes) and Project Management. Experience in the Stock Market exchange (Euronext), Finance and Banking(Banco BPI) and other markets (Energy, Telecommunications, Government, , Retail). Experience in innovation processes, projects and creative problem solving.

Peter-Connelly-1

Peter Connolly

Toro Risk Solutions Global Limited and TEG7 LLP

Peter has a UK military background and led troops during Counter-Insurgency and CT operations in Afghanistan, Iraq, Northern Ireland, Kenya and Somalia. He now delivers holistic security risk management solutions for CNI, corporates, private wealth firms and major events. Peter specialises in hybrid (physical, personnel and technical) Red Team Penetration Testing which replicates the sophisticated threats facing CNI and businesses. He blends open source research; Wi-Fi attack; hostile reconnaissance; surveillance; phishing; spoofing; social engineering (by phone, online and in person); physical intrusion; and computer network exploitation.

Quentyn Taylorcrop

Quentyn Taylor

Director of Information Security, Europe, Middle East and Africa Canon

Quentyn Taylor is Director of Information Security for Canon Europe. He has a wealth of experience in both the IT and information security arenas and, in recent years, has focused his attention on building business relationships across the world.

Quentyn has driven Canon’s strategy to highlight the importance of document security and help business customers to minimise their security risk. Quentyn strongly believes in educating users about the importance of a comprehensive, overall security framework that will allow Canon’s business customers to improve security in a cost-effective way.

During his career, Quentyn has worked in a variety of industries for a number of organisations including outsourced service providers, Internet service providers as well as Dotcom businesses, before moving to Canon in 2000.

Bob-Shaw

Robert Shaw

Senior Security Advisor, United Nations

Robert is a security, intelligence and EOD executive with a UK Military background. He has broad strategic and operational experience and has advised senior staff, diplomats and government officials on aspects of security, intelligence, threat analysis, crises management, and resilience strategies. He has been the UN Security and EOD Advisor; Liaison officer for the UNMAS and UNOPS and has experience with NATO, the GCC, African Union, OSCE, EUPOL, FCO and others. Robert is a respected expert, has specialist research background on suicide bombing and has provided thematic briefs on worldwide security issues relevant to UNMAS/UNOPS missions.

Robert_Coles

Robert Coles

Visiting Professor, Royal Holloway, University of London

Robert Coles is a Visiting Professor at Royal Holloway, University of London, where he is conducting his research into security culture change. He also runs his own consulting business. Prior to this, Robert was the first Chief Information Security Officer at GSK from 2013 to 2018.

Robert held several CISO roles prior to joining GSK. He was the first CISO at National Grid and Merrill Lynch before that. In all these roles, he owned the information security risk and was responsible for providing global leadership. He was accountable to the Executive and PLC Boards for establishing information security strategy and direction. Building global information security capabilities and overseeing all of the information security initiatives across the organisations has been his primary career focus.

Robert has been working in the field of Information Security for over 30 years, including “head of” roles at Royal Bank of Scotland, and the lead partner in KPMG’s Information Security Services for EMEA.

Robert has extensive links with major industry information security networking groups and government security agencies. He also has links with a number of universities and participates in leading edge research, particularly with Royal Holloway where he is an Executive Sponsor for the Institute of Information Security Innovation, and Cranfield University where he is a External Advisory Board member. He was awarded a PhD in psychology at the University of Leeds in the perceptions of information and IT risk and has published and presented on this and other topics.

Rob-Robinson

Rob Robinson

Director of Security and Network Services, Company85

As an advisor to CISOs and CIOs, Rob has first hand experience of helping security teams assess their position, build their strategy and deliver successful programmes. At Lisbon 2018, Rob will be sharing his experience of working alongside Skanska and the NSPCC to build target operating models for a new era of cybersecurity. Rob has the insider track on CISO thinking on Cloud Security, Supply Chain Risk, GDPR, and Operating Models. Join him and Adam Drabik of Opel Vauxhall Finance on 21st June at 8.20 for a breakfast meet up.

richard-jones

Richard Jones

CISO, SecureLink

Previously the CISO for a large online retailer with revenues approaching £1B, Richard is familiar with the cybersecurity capabilities required to meet the challenges facing digital first organisations. Having worked in IT for much of his career, he has over twenty years of hands on experience to rely upon. Richard was lucky enough to remember a period when IT was merely a recreational activity. A keen 1980’s gamer and C64 programmer, Richard’s IT hobby quickly became a career after short but promising accountancy debut. On the road to his Information & Cyber Security career, Richard got the opportunity to work in various IT Operational roles; starting with desktop and server infrastructure and many years later, leading the network security. Richard has also been fortunate enough to have seen first-hand how our personal and professional reliance on technology has dramatically changed. Only ten years ago, an IT department controlled what a user had access to and how they connected; now the user demands access to applications of their choosing at a time they specify and on a device and platform they mandate. The external perception of information security has also changed dramatically, establishing itself as a key business function; an important business unit adding strategic value – historically seen only as the expensive retrospective checkbox! Now the Group CISO for SecureLink, Richard has the responsibility for directing internal Information Security & Compliance across both European and emerging markets.

Sérgio-Nunes

Professor Sérgio Nunes

Professor – Information Security, ISEG – Lisbon School of Economics & Management

Assistant Professor at University of Lisbon (ISEG) and Atlantica University. More than ten years’ experience as a consultant in the fields of information systems management, IT auditing and information security. Several professional certificates from organizations such as: CISSP, CISA, CISM, CEH, CPTS, APOGEP/IPMA-D, COBIT, ITIL.

Sally-LEIVESLEY

Dr. Sally Leivesley

Director, Newrisk and TEG7

Dr. Sally Leivesley, Director, Newrisk Ltd and Co-Founder, TEG7 Group LLP – advises companies and governments on catastrophic risk where losses to companies and governments may involve critical functions essential for operations and reputation. She runs exercises to stress test critical function failures and resilience capability. Dr. Leivesley is known for her appearances on aviation terror attacks, ISIS, Al Qaeda, Al Shabaab and other international terrorism, cyber breaches, CNI protection and government policy on the BBC World Service, ITV This Morning and other UK based media and European, Middle East and Australian media. She raised the forensic importance of the risk of cyber hijacking of flight MH370 which was the subject of a Discovery Channel documentary and has been a commentator on the risks relevant to Donald Trump economic, terror and nuclear influences during his Presidential campaign and on his election. Dr Leivesley works in conjunction with The Exercise Group7 (TEG7) a London based group of companies that specialise in resilience operations for cyber-attacks, international terrorism and nation state threats and solutions for business and government-critical infrastructure. The focus is on testing through exercises, assurance and pen tests using an integrated approach to all hazards including social factors. (www.Teg7.co.uk) In the UK she has been a member of the technical committee for the first IET (formerly IEE) guidance document on Resilience and Cyber Security of Technology in the Built Environment which was supported by the Centre for the Protection of National Infrastructure. She is also a member of the British Register for Security Engineers and Specialists established to advise at a strategic level on terrorist and other extreme threats to critical infrastructure. She interfaces with a USA company to extend exercising for aviation and energy industries. Dr Leivesley originally trained as a Scientific Advisor with the British Home Office. She is a specialist in CBRN.

Stephen-Khan4-e1528883880761

Stephen Khan

Head of Technology & Cyber Security Risk, Group Information Security Risk, HSBC Holdings plc

Stephen Khan is currently Head of Technology and Cyber Security Risk with HSBC Group Information Security Risk. Before joining HSBC, Stephen was at RBS and held the position of Global Head Security Strategy, Architecture and Engineering; and Global Head of Security Transformation programmes.

Stephen has extensive’ experience in Information and Cyber Security including experience of establishing, delivering, and managing global cyber security organisations & global services for complex global and highly regulated organisations to effectively manage information assurance; privacy; and cyber security risk & Cyber security operations to drive strategic business value.

Stephen’s experience spans across multiple business functions; industry verticals including Finance; Pharmaceutical and Manufacturing.

Stephen combines business acumen and commercial experience with deep cyber security expertise to deliver long term strategic business value by building high performing capable teams and strong stakeholder management.

Stephen is on the board of White Hat Events which runs information security charity events including White Hat Ball; and White Hat Rally to support NSPCC ChildLine & Barnardo’s.

Stephen contributes to the wider Cyber Security community via industry forms, coaching and mentoring future leaders; and executive engagements with his peers across multiple sectors.”

Steve-Wright-photo

Steve Wright

Data Privacy and Information Security Officer, John Lewis Partnership

Steve joined The John Lewis Partnership in April 2016 and is responsible for both the Information Security and Data Privacy, both of these enable the John Lewis Partnership to protect the personal data of our customers and partners, to be compliant with data protection laws and regulations, and to provide trust and transparency – resulting in greater brand experiences across our digital, mobile and ecommerce channels. Steve is passionate about big data and all things digital. With more than 20 years’ experience, designing, developing, managing and delivering transformational data, governance, privacy and security programmes, Steve’s vast experience as a pragmatic and charismatic leader, ideally places him as a ‘trusted advisor’ at board level on all privacy and security related matters. Steve is also a published author, a non-executive director and is regularly invited to speak at industry events, trade associations and thought leadership working groups, working towards continually finding new ways to increase trust and transparency in respect of consumer services, business functions and product vendors.

Steve strongly believes that governance, cyber security and privacy are all inextricably linked as they share common objectives and principles, and therefore, require satisfactory safeguards and assurances. From a business perspective, this can be achieved by building ‘data trust and assurance’ programmes based on the fundamental principles of transparency, accountability, protection, integrity, confidentially and availability, accompanied by clear policies and delivered through comprehensive training, integrated procedures and a robust compliance regime. Having once served as a CISO, and held senior roles at, Unilever, Deloitte, PwC, Siemens and Capita, Steve has a full appreciation of what is required to get the job done in a cost effective, pragmatic and timely fashion with a natural ability to lead from the front, to coach others and to take responsibility consistently, courageously and with integrity.

Tim-Holman

Tim Holman CEO and Founder

2-sec

Tim founded 2|SEC in 2011, with the vision of becoming the UK’s best Cyber Security Resilience partner for Financial Services firms in the City. Since then 2|SEC has grown from strength to strength; and engage in a number of high profile Cyber Security projects, including penetration testing of some of the world’s best known brands. Tim is an avid cyclist and winter sports enthusiast.

Vasileios-Karagiannopoulos

Dr. Vasileios Karagiannopoulos

Institute of Criminal Justice Studies, University of Portsmouth

Dr Vasileios Karagiannopoulos holds an LLB from Athens Law School and an LLM in Information Technology and Telecommunications Law and a PhD in Law from the University of Strathclyde, School of Law. He has taught Information Technology Law, Intellectual Property Law, E-commerce Law and Human Rights Law for Strathclyde and Edinburgh Law Schools and is now a Senior Lecturer in Law and Cybercrime working for the Institute of Criminal Justice Studies (ICJS), University of Portsmouth. Vasileios has designed and is the course leader for the new ICJS BSc in Criminology and Cybercrime starting this September. He is also the Director of the Portsmouth Cybercrime Awareness Clinic, a project funded by Hampshire Constabulary, aiming to increase awareness and build resilience to cybercrime in the local community through research and public engagement activities with SMEs and vulnerable populations. Vasileios is the Chair of the ICJS Research Ethics Committee and Vice-Chair of the Faculty Research Ethics Committee and is also an IISP Certified Forensic Investigations Practitioner. He has published in UK and US peer reviewed journals on the topics of computer misuse law and insider unauthorised access, the impact of social media during the Arab Spring and also Internet regulation in the People’s Republic of China. His new monograph by Palgrave Macmillan, Living with Hacktivism: From Conflict to Symbiosis, focuses on hacktivism and discusses the challenges faced by the US and UK criminal justice systems when dealing with such phenomena. In this book, Vasileios puts forward an alternative rationale and practical responses to hacktivism with the aim of ameliorating the inefficiencies and injustices identified in current approaches.

viktor-polic-1-e1549452362993

Viktor Polic

CISO, Head of Information Security and Assurance Services, International Labour Organization and Adjunct Professor of Computer Science, Webster University Geneva

Dr. Viktor Polic, Adjunct Faculty, Webster University Geneva & CISO, International Labour Organization United Nations. The ILO is a specialized agency of the United Nations. Viktor’s 25-year career in the IT spans different roles across financial, humanitarian, standardization and development multilateral public sector organizations (ITU, UNCC, UNHCR). Viktor conducts research in cryptography, data protection regulation, and risk management. Since the Internet bubble, he is teaching computer science and telecommunications courses as adjunct faculty at Webster University in Geneva. Viktor is a member of the Scientific Committee for Advanced Studies in Information Security at University of Geneva. He advocates for advancement in information security as an author in journals and his personal blog (blog.cybersymbiosis.com), and as a speaker at numerous international security conferences. Viktor holds a Ph.D. in Cryptography and Advanced Protection Systems, MA in Computer Resources and Information Management, and BSc in Computer Science. He is a member of (ISC)2, ISACA and IACR.

Victoria-Baines

Dr. Victoria Baines

Visiting Associate, Oxford Internet Institute

Victoria Baines is a leading author and speaker in the field of cybersecurity. Her areas of research include electronic surveillance and evidence gathering, the changing face of online identity, and the politics of cybersecurity. She has appeared on the BBC, CNN and other major broadcast media outlets as an authority on the misuse of emerging technologies, including Virtual Reality. She serves on the Advisory Board of the International Association of Internet Hotlines (INHOPE).

For several years, Victoria was Facebook’s Trust & Safety Manager for Europe, Middle East and Africa. Her work focused on operational support to law enforcement, and strategic engagement with policy makers on criminal activity online. Before joining Facebook, Victoria led the Strategy & Prevention team at Europol’s European Cybercrime Centre (EC3), where she was responsible for the European Union’s cyber threat analysis. She designed and developed the iOCTA, Europe’s flagship product on cybercrime, and authored 2020, scenarios for the future of cybercrime that were the basis for Trend Micro’s successful short film series of the same name.

Earlier in her career Victoria was Principal Analyst for online child protection at the UK Serious Organised Crime Agency (SOCA), and was responsible for the UK’s threat assessment of online child safety issues. She began her career in law enforcement in 2005 as a Higher Intelligence Analyst for Surrey Police. In 2008, the International Association for Law Enforcement Intelligence Analysts recognised Victoria’s work for the public sector with an award for outstanding achievement.

Victoria is a graduate of Trinity College, Oxford and holds a doctorate in classical literature. She is a Visiting Associate of the Oxford Internet Institute (Oxford University), and a Visiting Fellow at Bournemouth University School of Computing.

Yolande Young

CISO, McKesson

Yolande has had a broad career not only in cyber security and information protection, but also procurement, commercial management and pricing strategy. She is fascinated by the opportunities of the digital economy and how these can be appropriately balanced with individuals’ privacy. She is currently retained by a major telco to advise on a transformation strategy, having recently stepped down as the Chief Information Security Officer for pharmaceutical distributor McKesson’s European region. McKesson is Fortune 5, has revenues of $198bn per annum and operations in 14 European countries, employing 35,000 people.
Yolande served as Global Chief Information Security Officer for FTSE10 consumer goods giant SABMiller until its acquisition by ABInbev. As Global CISO, Yolande briefed the Audit Committee on cyber risk, regularly reported all information security matters to SABMiller’s ExCom, collaborated with Group Legal to implement the privacy policy, cookie policy, consumer data handling policy and information security policy, and mobilised a multi-million dollar capital investment programme to enhance security tooling. She has previously worked for the Metropolitan Police Services as ICT Procurement Director running a department that oversaw £300m in annual spend. Prior to this, she shaped her early career as a Management Consultant for PA Consulting Group and PricewaterhouseCoopers, with clients including PepsiCo, GSK, Tetley Tea, NXP and HMRC. She led specialist teams to drive transformation, cost reduction and security improvements.

John Scimone

SVP, Chief Security Officer, Dell (former SVP, Global Chief Information Security Officer, Sony Group)

John Scimone serves as Sr. Vice President, Chief Security Officer for Dell, where he leads the company’s global corporate security program. John’s responsibilities span the full spectrum of strategy, planning, and operations, aiding Dell’s businesses in the management of security risk across the physical and cyber domains. He is also charged with the advocacy of business resilience, including crisis management, business continuity and disaster recovery. Before joining Dell, John served as the Global Chief Information Security Officer for the Sony Group family of companies, where he was responsible for building Sony’s first global information security and privacy organization and leading strategy, policy, and operations. Prior to joining Sony, he also held a number of leadership positions at the U.S. Department of Defense, including as Director of Security Operations for the Secretary of Defense’s communications office, where he led the facility, personnel, and cyber security programs. John formerly served as a member of a predecessor organization of U.S. Cyber Command, where he led the development of enterprise information security programs that protected information belonging to the DoD’s more than two million employees. John holds a Bachelor of Science degree in Computer Science, with a specialization in Information Assurance, from the Georgia Institute of Technology. He also earned a Master of Arts degree in Strategic Intelligence, with a specialization in Counterintelligence, from the Institute of World Politics in Washington D.C.

Sounil Yu

SVP, Director for Security Innovation, Bank of America

Sounil is a Christian, husband and father with over 30 years of hands-on experience creating, breaking and fixing computer and network systems. As the Executive Director for Security Innovation at a major financial institution, he leads teams to execute innovation initiatives and crazy experiments that reduce risk and tackle hard challenges in infosec. Previously, he helped improve infosec at several institutions spanning from Fortune 100 companies with three letters on the stock exchange to secretive three-letter agencies that are not. Although on occasion he is forced to write about himself in the third person, he would rather meet people in person to share experiences rather than writing it up in a short bio. He lives in Virginia with his wife and their four homeschooled children.

Freaky Clown (FC)

Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

Dr. Jessica Barker

Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

With a background in sociology, psychology and civic design, Dr Jessica Barker specialises in the human side of cyber security. As an independent consultant, Jessica is engaged by FTSE100 companies, central government and SMEs across the defence, health, financial and retail sectors to advise organisations how they can keep their information safe while getting the most out of it. Jessica’s consultancy work involves leading and delivering information security audits, from which she develops roadmaps which take organisations on a journey of improved cyber security maturity. Jessica also specialises in learning and development packages which raise cyber security awareness and improve behaviours.

Adolfo Hernández

Advanced Cyber Defense Manager, Banco Sabadell and THIBER, the cybersecurity think tank

Is the digital fraud, forensic, cyber and threat intelligence manager at Banco Sabadell and Founder member of THIBER the cybersecurity think tank, Internet Security Forum (ISF), ISACA, ISC2, ISMS Forum Spain, Data Protection Institute (DPI), Cyberscurity Center (CSC), Cloud Security Alliance (CSA) and AENOR-ISO CTN7/SC7/GT-25. Adolfo holds a computer science degree. With over 10 years of professional experience in the management of technological risks and cybersecurity in diverse sectors, he is also a regular speaker at various master degree programs in business schools and universities, and at industry events, like TEDx. Follow Adolfo on Twitterhttp://twitter.com/Adolfo_hdez

Alex Quintieri

Head of Cybersecurity, AIA Insurance

Alex Wilson

Cloud Security Architect, EMEA, CyberArk

Alex has over 5 years’ experience in Privileged Account Security. He is one of the leading experts in understanding the requirements and drivers for managing privileged access security within an organisation. Alex has led some of the largest design and implementation programs of privileged account security with companies across all sectors, many of which are in the Fortune 100. Leveraging this experience, Alex now focuses on privileged account security best practice with organizations embracing Cloud and DevOps.

Alexios Fakos

Head of Cyber Defence, Airbus Germany

Alexios lead and conducted several technical security assessments and was involved as trusted advisor in various major Cyber Security Programmes. Before joining Airbus CyberSecurity he has been working for PwC and n.runs. Alexios is member of the Body of Experts on Cyber Forensics lead by German Federal Office for Information Security (BSI) as well board and program committee member of OWASP Germany.

Andreas Wuchner

Project Technology Advisor for the Cyber Resilience Project, World Economic Forum

Ali Zeb

CISO, MS Amlin

Ali Zeb, CISO, MS Amlin specialises in security transformation of businesses, delivering global information security at strategic, tactical and operational level. He has over 16 years’ experience in IT and Information Security within the Finance sector. Alongside heading global security Ali has been appointed as GRC and Data Protection Officer for many organisations. Ali is currently Group Chief Information Security Officer at MS Amlin. Member of FCA Insurance Sector Cyber Coordination Group (ISCCG) and Lloyds Cross Market Cyber Risk Forum.

Andy Archibald

Director Cyber Security, Intelligence and Threat Management, Credit Suisse

Anthony Young

Partner, Bridewell Consulting

Anthony Young, Partner, Bridewell Consulting – commenced his Information Security career in 2003. He worked as a security consultant primarily within central government and the gaming industry where he reduced threat profiles by establishing security frameworks and management systems. In 2008 Anthony established Barclay Simpson’s Information Security contract division. He gained a well-earned reputation for his passion for Information Security and for his ability to source highly skilled information security consultants in short timescales. As data breaches became commonplace, Information Security moved up the corporate agenda and the demand for trusted and skilled security professionals increased. In response to this increased demand, Anthony set up Bridewell Consulting in 2013 in partnership with Barclay Simpson. Four years on Bridewell has established a reputation for delivering excellent services across Governance, Risk and Compliance as well as Penetration Testing services. Bridewell’s philosophy is to work in partnership with our clients and provide them the security personnel and services they require. Retained by clients across Financial Services, Oil & Gas, Media and Government, Bridewell allows them the assurance of having expert security advice on call, without the substantial costs and commitments of employing a permanent in-house security division. Anthony is the Partner in charge or sales and operations at Bridewell Consulting ensuring that all clients receive an excellent service from the delivery team. His ambition is that companies of all sizes are able to build security into their everyday practices, without being burdened by the cost or size of the task. Anthony is also keen to promote the information security profession locally working with organisations across the Thames Valley running a number of briefings and security events.

Charles V. Pask

Managing Director, ITSEC Associates Ltd

Charles V. Pask, Managing Director, ITSEC Associates Ltd – is responsible for delivering global IT Audit and IT Security consultancy services. He was a founding member of the Institute of Information Security Professionals (IISP) and recognised globally as a thought leader in Information Security and IT Controls. Mr. Pask has over 30 years’ experience in IT, IT audit, and IT security, and has previously held Senior IT Auditor positions at Forward Trust Group (subsidiary of HSBC) and Alliance & Leicester Bank plc, and also Group Head of Information Security for Alliance & Leicester (10 years). Mr. Pask was the Global Head of Strategy, Development and Globalisation for the BT Business Continuity, Security and Governance Practice. He was previously a Director with MIS Training, and Director of Information Security Institute (ISI) European and Middle East e-Security Services (2000-2). Mr. Pask has been a member of the ITSEC Common Criteria team working with the UK Government, and a committee member of the APACS Security Advisory Group and the LINK Security Group. Mr. Pask has personally helped over 400 students globally achieve the CISSP training exam.

Charlotte Stephen

Account Executive, Darktrace

Charlotte Stephen, Account Executive, Darktrace – has been an Account Manager at Darktrace for 12 months, working on accounts across the EMEA region. During this time, she has given a number of presentations and technology demonstrations, and used her languages to work with both national and international clients from the public and private sectors. Prior to Darktrace, Charlotte worked in the underwriting department of a global insurance company in Buenos Aires. She holds a BA in French and Spanish from the University of Bristol and a MSc Management from Cass Business School in London.

Charlie Bennett

Global Account Director, Trend Micro

Charlie Bennett, Global Account Director, Trend Micro — is an expert business sales professional with 10 years’ experience in IT Security, Networking and Application delivery solutions. I am conscientious, enthusiastic, and self-motivated individual with exposure to a wide range of areas. Specialties: IT Security, Networking, Application Delivery. The ability to sell complex Managed Service and Professional service projects, with a good understanding of the technology market.

Dr. Cheryl Hennell

Former CISO, Openreach and Former Security Advisor, Virgin Atlantic

Daniel Brunner

Head of Security and Architecture, RUAG AG Switzerland

Daniel Brunner, Head of Security and Architecture, RUAG AG Switzerland is a Senior Information Security expert & Project Manager with an MBA and 15 years of experience. Recognized ability to manage Complex IT Environments inside multiple business organizations. Specific expertise in Project Management, Risk Management within the IT Domain. ISMS (Information Security Management System) installed and developed during several years. Proven ability to design security solutions with in-depth operational supervision of incidents and emergency disaster recovery. IT Governance and audit conformity experience coupled with investigation coordination with legal departments and Human Resources to produce proof or policies to defend and protect the company from threat – yet still enabling business to continue in a secure manner. He was previously CISO of Leumi Private Bank and has held senior positions at UBS. He is the VP at DEFCON Switzerland.

Darran Rolls

Chief Technology and Chief Information Security Officer, SailPoint

Darron Gibbard

Chief Technical Security Officer, Qualys

Before joining Qualys as CTSO, Darron spent the last 25+ years working for a variety of payment services, media and telco organisations providing Cyber, IT and Information security thought leadership and subject matter expertise. His early career was spent working in the vendor marketplace for startups and major security vendors in both a pre and post sales capacity.


David Colbourne

Information Security Manager, Lloyd's of London


Dexter Casey

Interim Group CISO, Centrica

Dimitri Chichlo

Former VP, Senior Manager Information Security & BCM, Edmond de Rothschild

Dimitri is former Senior Manager Information Security & BCM at Edmond de Rothschild in Geneva. Prior to this position, he worked 6 years for ING as Head of Non-Financial Risk Management in Geneva as well, and spent 5 years in Ukraine involved in various international industrial and banking projects. He is currently pursuing an Executive MBA at the INSEAD.

Dr. Eduardo Solana

Senior Lecturer of Cryptography and Security, University of Geneva

Dr. Eduardo Solana is Senior Lecturer of Cryptography and Security in the University of Geneva and in the University of Applied Sciences also in Geneva, Switzerland. Amongst others, he has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has more than twenty years of experience in the fields of cryptography and information security both in the private sector and the academia.


Eduardo Di Monte

Security and Business Continuity Director, Agbar

Eduardo Di Monte, Security and Business Continuity Director, Agbar – is the cibersecurity Coordinator of the Center for Industrial Cyber Security in Chile, representative for the Central & South America Region for the Business Continuity Institute, and Director of Security and Business Continuity at Agbar Group, for Spain and Chile. Telecommunications Engineer and MBA Consortium EuroMBA, specializes in the management of information security, business continuity and security in industrial control systems. With over 12 years of experience in consulting, as well as management, implementation and security strategies and continuity in multiple sectors (energy, tourism, banking, infrastructure and telecommunications). It has multiple certifications: CISSP, LA / LI ISO 22301, MBCI by the Business Continuity Institute, CSSA (SCADA Security Certified Architect) and Advanced Control System Cyber Security Training (US Department of Homeland Security). Regular contributor to events as a keynote speaker (Spain and South America) and professor (UPM and private institutions).

Fabian Libeau

EMEA Technical Director, RiskIQ

Fabian Libeau, EMEA Technical Director, RiskIQ – currently serves as EMEA Technical Director for RiskIQ. He and his team work closely with customers to maximise the value they receive from the RiskIQ solution set. Before joining RiskIQ Fabian was with ArcSight and after the acquisition by HP, with HP Enterprise Security Products for 9 years in different technical roles where he worked closely with enterprise customers to implement Log Management solutions and next generation SOCs. Fabian is a frequent speaker at conferences and is CISSP certified. He holds a masters degree in Physics.

Gadi Evron

Chairman, Israeli CERT & CEO, Cymmetria

Gadi is the Founder and CEO of Cymmetria, a cyber security startup that is pioneering the space of cyber deception. He is also Founder and Chairman of the Board of the Israeli CERT, Founding Chairman of the Cyber Threat Intelligence Alliance (CTIA), and Founder of the Israeli Government CERT. Gadi is widely recognized for his work in Internet security operation and global incident response, and is considered the first botnet expert. Prior to founding Cymmetria, Gadi was VP of Cybersecurity Strategy for Kaspersky Lab, led PwC’s Cyber Security Center of Excellence (located in Israel), and was CISO of the Israeli government’s Internet operations. He has authored two books on the topic of information security, organizes global professional working groups, chairs worldwide conferences, and is a frequent lecturer.

Graham Edwards

Head of Group Security, Nationwide

Hugh Njemanze

Chief Executive Officer, Anomali

Hugh has an illustrious 30-year career in the enterprise software industry. Hugh co- founded ArcSight in May 2000 and served as CTO as well as Executive Vice President of Research and Development. He led product development, information technology deployment, and product research at ArcSight, and expanded these responsibilities to lead all engineering and R&D efforts for HP’s Enterprise Security Products group, the organization that ArcSight became part of post-acquisition. Hugh was recently an advisor and entrepreneur at investment firm, Kleiner Perkins Caufield & Byers (KPCB). Prior to joining ArcSight, Hugh worked as the CTO at Verity, where he led product development, and before that he was at Apple in software engineering, where he was one of the key architects behind the Data Access Language (DAL). Hugh is a CISSP and holds a B.S. in computer science from Purdue University. He was also honored with the Northern California Ernst & Young LLP Entrepreneur of The Year award in 2010.

Irene Corpuz

Section Head - Planning & IT Security, UAE Government

Irene is the Head of the IT Security Section and acting CISO at the Western Region Municipality, Abu Dhabi. She is responsible for the execution of the ADSIC Information Security Programme, Security Governance, Risk & compliance to IT Security Policy. She offers 27 years of combined and diverse experience in IT (Security, Operations and Strategy), Quality & Excellence. She has worked in various industries and region and led strategic initiatives in Asia, Middle East, Europe and America. An emerging seasoned speaker on Information & Cyber Security Conferences, Irene has spoken in a number of conferences in Asia, Middle East and Europe. Irene acquired her Masters of Science in IT from University of Wales, and holds the following certifications: ITIL V3, PMP, ISO (QMS and 27k) Lead Auditor and EFQM Assessor.

James Gill

Advanced Cyber Defense Director, Banco Sabadell

James is Director of the Advanced Cyber Defence del Banco Sabadell. En este rol, es el responsable de los equipos de Gestión de Incidentes y Ciberinteligencia. Tiene más de quince años de experiencia en seguridad, en diversidad de posiciones, en su mayoría en una de las entidades financieras más importantes del mundo, ocupando puestos de responsabilidad a nivel regional y global. Tiene un posgrado en Auditoría Técnica y Análisis forense, además de diversas certificaciones de Seguridad.

Dr. John Meakin

Group Chief Risk & Security Officer, Burberry

Dr. John Meakin, Group Chief Risk & Security Officer, Burberry – is a specialist in information security with more than twenty years experience. He has previously been responsible for leading systems security in Standard Chartered Bank, Reuters, the Royal Bank of Scotland and Dresdner Bank. More recently he was Chief Info Security Officer at BP plc for 3 years and led Deutsche Bank’s development of a new security strategy and innovative security solutions to meet the latest threats. John has been Chief Security Officer for the leading international luxury goods company Richemont, supporting the varying needs of such renowned brands as Cartier, Montblanc, Chloe, etc. He also has a particular interest in better modeling and managing the costs and benefits of security to the business, as well as in shifting the emphasis of commercial security efforts into dynamic management and monitoring rather than static prevention. He has developed a number of award-winning Info Security Risk Management methods and tools during his CISO career. He is a member of the Jericho Forum Board of Management, and advisor to a number of security vendors. He sits on the Microsoft Worldwide CSO Council and the SAP AG Security Advisory Board. He has a PhD in Experimental Solid State Physics from Cambridge University.

Jonathan Armstrong

Partner, Cordery

Jonathan is an experienced lawyer with a concentration on technology and compliance. His practice includes advising multinational companies on matters involving risk, compliance and technology across Europe. He has handled legal matters in more than 60 countries involving emerging technology, corporate governance, ethics code implementation, reputation, internal investigations, marketing, branding and global privacy policies. Jonathan has counselled a range of clients on breach prevention, mitigation and response. He has also been particularly active in advising multi-national corporations on their response to the UK Bribery Act 2010 and its inter-relationship with the U.S. Foreign Corrupt Practices Act (FCPA). Jonathan is one of three co-authors of the LexisNexis definitive work on technology law, “Managing Risk: Technology & Communications”. He is a frequent broadcaster for the BBC and other channels and appeared on BBC News 24 as the studio guest on the Walport Review. In addition to being a lawyer, Jonathan is a Fellow of The Chartered Institute of Marketing. He has spoken at conferences in the U.S., Canada, China, Brazil, Singapore, Vietnam, the Middle East and across Europe. Jonathan qualified as a lawyer in the UK in 1991 and has focused on technology, risk and governance matters for more than 20 years. Jonathan was recently ranked as the 14th most influential figure in data security worldwide by Onalytica in their 2016 Data Security Top 100 Influencers and Brands Survey. Jonathan is a Solicitor of the Senior Courts of England & Wales. In addition Jonathan is admitted as a Solicitor in Ireland.

Malcolm Kelly

Global Head of Application Security, HSBC

Manuel Barrios Paredes

CISO, Informática El Corte Ingles

Manuel is responsible for the corporate security of Informatica El Corte Ingles on 12 countries. Manuel was a professor at the CEU San Pablo University, lecturing in Information Security for the Criminology Degree. Over the last 20 years he has furthered his career in the field of information security for large companies, carrying out consultancy work for governments, intelligence, banking, insurance and critical infrastructure.

Mark Ampleford

Director - Security Division, Barclay Simpson

Mark is a recruitment and executive search specialist who heads the Security Practice at Barclay Simpson Corporate Governance Recruitment. He has 16 years’ experience of recruiting information security leadership roles in the UK and Europe.

Mark Logsdon

Head of Cyber Assurance and Oversight, Prudential

Marc Lueck

Chairman, ClubCISO

Marc is a senior security practitioner with over 20 years of experience crossing multiple industry sectors, from financial services to publishing. For the past 7 years, he has led security improvement programmes for the likes of Pearson, T-Systems and Symantec. He is currently the CISO at Company85, where he runs the security practice with a focus on ensuring information security enables and supports business goals.

Michael Colao

Head of UK Security, AXA

Mike Humphrey Msc. F.Inst.ISP

Head of Security, National Crime Agency

Mike was a police officer for 30 years. The latter 5 years of his career he was a senior officer seconded to a central government agency involved in the security of the Police National Network, a UK wide IP comms and data network. He is now Head of Security at the National Crime Agency. He is a fellow of the Institute of Information Security Professionals (IISP) an elected member of the Information Assurance Advisory Council’s (IAAC) management committee and a Government Liaison Panel representative on the IAAC Board. His qualifications include an MSc in IT Security; ISO27001 lead auditor and a SANS GIAC holder. He has presented at numerous national and international conferences. Mike is currently working on a PhD (part time), at the Defence Academy, Cranfield University, Shrivenham, where he is researching the Critical Success Factors required to improve security incident reporting.

Mun Valiji

CISO, Sainsbury’s

Nahim Fazal

Head of Cyber Threat Intelligence, Blueliv

Nahim is a highly accomplished Cyber Crime consultant with an exceptional track record in developing and delivering highly creative and innovative strategic solutions for Cyber Threat Intelligence & fraud risks emanating from the cyber sphere. Nahim has delivered expansive strategic cyber risk solution blueprints, for not only combating the problems associated with cyber risk but also enhancing business opportunities. Nahim is also a founding director of the European Cyber Security Group. He has penned a number of thought leadership papers on the issue of Cyber security and practical applications of cyber threat intelligence which can be found online. Nahim is a trusted point of contact for Law enforcement agencies in Europe and the USA. He was worked closely with UK fraud Action, ACPO, EUROPOL and key stakeholders within the UK public sector.

Lady Olga Maitland

Founder, Defense and Security Forum and Chairman, Copenhagen Compliance

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.–

Paul Heffernan

Group Chief Information Security Officer (CISO), Unipart Group

Paul Effingham, Group CISO, Unipart Group of Companies – is the Group CISO for Unipart Group of Companies. With nine years’ experience in the cyber security world, including consulting to some of the world’s biggest brands, he engages with the business at board level to enable trusted secure commerce. With an ‘ethical hacker’ background, he is able to address complex security challenges but is equally passionate about driving effective change through unambiguous leadership and communication. Paul is a regular speaker at various industry conferences such as the e-Crime Congress, PCI London and the GBI CISO Summit. When he isn’t keeping Unipart safe, you can find him tinkering with code and figuring out how to inspire the next generation of cyber security professionals. Paul is proud to be shortlisted as CISO of the Year 2017. You can reach him on LinkedIn or on Twitter at @pjh_22.

Prudence Smith

Head of User Behaviour, Awareness and Heuristics, Barclays

Rainer Rehm

Security Architect, MAN Truck & Bus AG

Ramsés Gallego

President, ISACA Barcelona Chapter and Former VP, ISACA International

Ramsés CISM, CGEIT, CISSP, SCPM, Six Sigma Black Belt, who in 2012 was named security strategist and evangelist for Quest Software, a Dell company. Ramsés has served on ISACA’s Guidance and Practices Committee, and the CISM and CGEIT Certification Committees. He is an author of ISACA white papers on geolocation, virtualization and sustainability, and is research director for the ISACA Barcelona (Spain) Chapter. He also served on the planning committee of the inaugural ISACA INSIGHTS conference and chaired the planning committee for ISACA’s Information Security and Risk Management Conference in Europe.

Ramon Serres

Head of Information Security, Risk Management and Quality, Almirall

Ramon Serres, Head of Information Security, Risk Management and Quality, Almirall – is an Industrial Engineer, Master in E-Business, who has led the Information Security function in Almirall over the last three years. His area of responsibility is Information Security, Quality and Risk Management. He is certified by ISACA in IT Governance (CGEIT), Information Security Management (CISM) – with best grade diploma for both in ISACA Barcelona Chapter -, and Cybersecurity (CSX). Given his extensive Business and IT background in various positions and industries he has a valuable expertise ranging from the Security Strategy definition to Program and Project Management, Risk and Value Management, and People Management. Prior to Almirall, he worked for Price Waterhouse Coopers and Henkel.

Richard Bell

Chief Information Security Officer (CISO), Transport for London

TfL is a dynamic and challenging retail and transportation organisation with annual revenue of £4Bn. During this tenure, Richard’s first step was to risk assess the current state of information security at TfL. From that risk assessment he then developed and led the implementation of an effective strategic and tactical response programme to ensure cyber security resilience. Richard has been with TfL since 2004, during which has had responsibility for providing security assurance against some of the most significant risks TfL faced. He is advocator in the harnessing of social media and big data analytics. He has served as a Director for The Security Institute and featured within the IFSEC Global Top 40 of influencers in security 2014 and 2015.

Rik Ferguson

Vice President Security Research, Trend Micro

Rik Ferguson, Vice President Security Research, Trend Micro is one of the leading experts in information security. He is also a Special Advisor to Europol EC3, and a project leader with the International Cyber Security Protection Alliance (ICSPA). In April 2011 Rik was inducted into the Infosecurity Hall of Fame. As a lead spokesperson for Trend Micro, Rik is actively engaged in research into online threats and the underground economy. He also researches the wider implications of new developments in the Information Technology arena and their impact on security both for consumers and in the enterprise. With almost twenty-five years’ experience in information security, Rik has been with Trend Micro since 2007. Prior to assuming his current role he served as Security Infrastructure Specialist at EDS where he led the security design work for government projects related to justice and law enforcement and as Senior Product Engineer at McAfee focused on network security, intrusion prevention, encryption and content filtering.

Dr. Robert Coles

Chief Information Security Officer/Head of Information Protection & Privacy, GSK

Professor Robert Coles PhD joined GSK on 1 October 2013 as their first Chief Information Security Officer. Robert owns the information security risk and is responsible for providing global leadership across GSK. He is accountable for establishing information security strategy and direction, building a global information security capability and overseeing all of the information security initiatives across the company. Prior to GSK, Robert was CISO at National Grid (a major US/UK power Utility) where he created and led the CISO function since 2009. He has also held CISO positions at Merrill Lynch and interim Head of Group Information Security at Royal Bank of Scotland, and was the lead partner in KPMG’s Information Security Services for EMEA. Robert has extensive links with several major industry information security networking groups and government security agencies. He also has links with a number of Universities and participates in leading edge research, particularly with Royal Holloway where he is a visiting Professor. He undertook his PhD in psychology at the University of Leeds in the perceptions of information and IT risk and has published on this topic.

Robert Rodger

CISO, The Bank of Butterfield Group

Dr. Sally Leivesley

Director, Newrisk Ltd

Dr. Sally Leivesley, Director, Newrisk Ltd and Co-Founder, TEG7 Group LLP – advises companies and governments on catastrophic risk where losses to companies and governments may involve critical functions essential for operations and reputation. She runs exercises to stress test critical function failures and resilience capability. Dr. Leivesley is known for her appearances on aviation terror attacks, ISIS, Al Qaeda, Al Shabaab and other international terrorism, cyber breaches, CNI protection and government policy on the BBC World Service, ITV This Morning and other UK based media and European, Middle East and Australian media. She raised the forensic importance of the risk of cyber hijacking of flight MH370 which was the subject of a Discovery Channel documentary and has been a commentator on the risks relevant to Donald Trump economic, terror and nuclear influences during his Presidential campaign and on his election. Dr Leivesley works in conjunction with The Exercise Group7 (TEG7) a London based group of companies that specialise in resilience operations for cyber-attacks, international terrorism and nation state threats and solutions for business and government-critical infrastructure. The focus is on testing through exercises, assurance and pen tests using an integrated approach to all hazards including social factors. (www.Teg7.co.uk) In the UK she has been a member of the technical committee for the first IET (formerly IEE) guidance document on Resilience and Cyber Security of Technology in the Built Environment which was supported by the Centre for the Protection of National Infrastructure. She is also a member of the British Register for Security Engineers and Specialists established to advise at a strategic level on terrorist and other extreme threats to critical infrastructure. She interfaces with a USA company to extend exercising for aviation and energy industries. Dr Leivesley originally trained as a Scientific Advisor with the British Home Office. She is a specialist in CBRN.

Stephen Khan

Head of Security Architecture and Transformation, Royal Bank of Scotland

TJ Campana

Global Head of Strategic Security Threat, HSBC

Dr. Victoria Baines

Visiting Associate, Oxford Internet Institute

Victoria is an experienced cybersecurity professional with a demonstrated history of working in the internet industry and international law enforcement. Published academic author and futurist with a strong research background. Skilled in Crisis Management and Response, Negotiation, Intelligence Analysis, Strategy Delivery, and Coaching

Dr. Viktor Polic

Adjunct Faculty, Webster University Geneva & CISO, International Labour Organization United Nations

Dr. Viktor Polic, Adjunct Faculty, Webster University Geneva & CISO, International Labour Organization United Nations. The ILO is a specialized agency of the United Nations. Viktor’s 25-year career in the IT spans different roles across financial, humanitarian, standardization and development multilateral public sector organizations (ITU, UNCC, UNHCR). Viktor conducts research in cryptography, data protection regulation, and risk management. Since the Internet bubble, he is teaching computer science and telecommunications courses as adjunct faculty at Webster University in Geneva. Viktor is a member of the Scientific Committee for Advanced Studies in Information Security at University of Geneva. He advocates for advancement in information security as an author in journals and his personal blog (blog.cybersymbiosis.com), and as a speaker at numerous international security conferences. Viktor holds a Ph.D. in Cryptography and Advanced Protection Systems, MA in Computer Resources and Information Management, and BSc in Computer Science. He is a member of (ISC)2, ISACA and IACR.

Platinum Sponsor

Telstra

Telstra is a leading telecommunications and technology company with a proudly Australian heritage and a longstanding, growing international business.

Today, it has around 33,000 employees offering consumer, small business and enterprise services, with over 3,000 based in more than 20 countries outside of Australia. Telstra Enterprise is a division of Telstra that provides data and IP networks and network application services, such as managed networks, unified communications, cloud, industry solutions and integrated services. These services are underpinned by our subsea cable network, one of the largest in the Asia Pacific region, with licenses in Asia, Europe and the Americas, and access to more than 2,000 Points-of-Presence around the world.

Our customers are global, our people are local and our assets are anchored in Asia. Over several decades we have established one of the largest subsea cable networks in Asia-Pacific, with a unique and diverse set of infrastructure that offers access to the most intra-Asia lit capacity and largest subsea cable system in Asia Pacific.

The network plays a crucial role underpinning the digital economy in Asia-Pacific, meeting the needs of wholesale and enterprise customers around the world. We also provide sophisticated network application services and have growing interests in software, video delivery, e-commerce and health.

Growing our business globally is a strategic priority for Telstra, and we are focused on being the leading service provider for our customers across Asia-Pacific. We are also seeking to leverage our capabilities and assets to capture connectivity opportunities in industries where technology is creating competitive disruption.
www.telstraglobal.com.

Gold Sponsors

F Secure Red

Rest easy – F-Secure’s holistic portfolio of cyber security solutions will cover all of your organization’s cyber security needs.

Our extensive human knowledge and insight, combined with smart software and cutting edge AI, merge into a single entity, dedicated to protecting you. This is Live Security.

www.f-secure.com

IBM Resilient

 IBM Resilient’s mission is to help organizations thrive in the face of any cyberattack or business crisis. The award-winning Incident Response Platform (IRP) empowers security teams to analyze, respond to and mitigate incidents faster, smarter and more efficiently. Part of IBM Security, the Resilient IRP also integrates security technologies into a single hub and provides easy workflow customization and process automation. With Resilient, security teams can have best-in-class response capabilities. Resilient has more than 100 global customers, including 30 of the Fortune 500 and partners in more than 20 countries. www.resilientsystems.com 

CyberArk

CyberArk is the only security company laser-focused on striking down targeted cyber threats, those that make their way inside to attack the heart of the enterprise. Dedicated to stopping attacks before they stop business, CyberArk is trusted by the world’s leading companies — including more than 50% of the Fortune 100 — to protect their highest-value information assets, infrastructure and applications.

For over a decade CyberArk has led the market in securing enterprises against cyber attacks that take cover behind insider privileges and attack critical enterprise assets. Today, only CyberArk is delivering a new category of targeted security solutions that help leaders stop reacting to cyber threats and get ahead of them, preventing attack escalation before irreparable business harm is done. At a time when auditors and regulators are recognizing that privileged accounts are the fast track for cyber attacks and demanding stronger protection, CyberArk’s security solutions master high-stakes compliance and audit requirements while arming businesses to protect what matters most.

With offices and authorized partners worldwide, CyberArk is a vital security partner to more than 3,300 global businesses, including:

CyberArk has offices in the U.S., Israel, Australia, France, Germany, Italy, Netherlands, Singapore, Turkey and the U.K. Learn more about CyberArk by listening to Udi Mokady, Chairman & CEO discuss Privileged Account Security.

www.cyberark.com

Darktrace

 Darktrace is the world’s leading machine learning company for cyber security. Created by mathematicians from the University of Cambridge, Darktrace’s Enterprise Immune System uses AI algorithms that mimic the human immune system to defend enterprise networks of all types and sizes. Our self-learning approach is the first non-consumer application of machine learning to work at scale, across all network types, from physical, virtualized, and cloud, through to IoT and industrial control systems. By applying its unique, unsupervised machine learning, Darktrace has identified 30,000 previously unknown threats in over 2,400 networks, including zero-days, insider threats and subtle, stealthy attacks. www.darktrace.com. 

SecureLink

SecureLink is the market leading provider of cyber security in Europe. With over 15 years of experience, we are trusted by some of the world’s largest brands. We are experts at designing, delivering, managing and supporting leading cyber security solutions.

Our philosophy is very simple. We empower organisations to protect themselves in an increasingly online world so that they can maintain trust and confidence. Put simply, we safely enable business. securelink.co.uk

Nominet Cyber Security

Nominet Cyber Security is a leader in helping government and enterprise organisations protect mission critical infrastructure from vulnerabilities including Malware, Phishing, Botnets, Cryptomining, Data Exfiltration and Misconfigurations. Our worldwide patented DNS security platform monitors live inbound and outbound network traffic and analyses billions of packets of DNS data in real time, helping customers detect and block known and unknown malicious threats before they harm your business. Our platform deploys in minutes with no cumbersome endpoint rollout and can either be managed in-house by your security team, or trust the Nominet expertise to manage and analyse your DNS service.

The rich APIs enable integration of curated DNS threat information into existing SIEM solutions and management reporting systems, to speed up response time, stop propagation and provide richer intelligence for forensics.

The UK Government depends on Nominet to protect the UK public sector DNS service to stop the use of DNS for malware distribution and operation. For further information, please visit https://www.nominet.uk/dns-cyber/

Bitsight

BitSight transforms how companies manage third and fourth party risk, underwrite cyber insurance policies, benchmark security performance, and assess aggregate risk with objective, verifiable and actionable Security Ratings. BitSight Security Ratings are a daily measurement of an organization’s security performance.

BitSight Discover instantly identifies single points of failure and highlights risky service providers connected to any vendor in the supply chain. With BitSight Discover, organizations can improve assessment processes and continuously monitor their extended ecosystem.

BitSight Sovereign Security Ratings are used to assess cyber risk at a national level. They take the burden of manual collection & analysis from agencies tasked with securing critical infrastructure, providing actionable insight into threats and guiding remediation with the appropriate parties.

www.bitsighttech.com

Barclay Simpson

 Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury. www.barclaysimpson.com 

CISO Breakfast Sponsor

Company85

Company85 is an independent IT infrastructure and security services firm which leads change, strips out cost and safeguards information.

Headquartered in London, we provide data centre, workspace, cloud, security and network services to some of the biggest global organisations in the public and private sector across the UK and the world.

We speak honestly and confidentially to people in all types of organisations about the practical steps they can take to feel confident about their cyber security. Some of the companies who trust us include AstraZeneca, Prudential, Murphy, Tullett Prebon, Cyberark, Hitachi Rail Europe and GSK.

Voted Services Company of the Year (2016 BCS UK IT Awards) and Security Team of the Year in 2016 and 2017 (Computing Security Excellence Awards), Company85 was particularly commended for innovative thought leadership around subjects such as GDPR, and our pioneering vCISO service.

www.company85.com

Silver Sponsors

ExtraHop

ExtraHop provides network security analytics powered by AI, with unprecedented depth and breadth of visibility, advanced behavioral analytics, and investigation automation capabilities. Using real-time analytics and ML-driven anomaly detection, ExtraHop Reveal(x) enables security teams to accelerate investigations, reduce false positives, and optimize the capabilities of expert security analysts.

The ExtraHop Reveal(x) 3-in-1 workflow provides full context, transaction details, and full packets within one click, accelerating investigations and remediation of threats against our customers’ most critical assets. www.extrahop.com

BridewellLogo100px

 Bridewell consultants are highly qualified and motivated cyber security experts. Our focus is to secure our clients’ information, technology, and networks from the many threats that they face. We provide leadership, understanding and solutions to allow our clients to benefit from the huge opportunities that the digital economy brings. We believe a strong defence and better cyber skills are essential in every organisation. We understand cloud technologies, cloud security and how to design, implement and review their deployment for a business. Bridewell are pleased to announce our company and our Audit & Review service has been recognised and certified by the National Cyber Security Centre – NCSC. www.bridewellconsulting.com 

Bronze Sponsor

SailPoint

Silver & Cocktail Sponsor

Cymmetria

 Cymmetria is a startup offering a pioneering cyber deception solution, based on breadcrumbs and decoys that lead attackers away from valuable targets. With Cymmetria, organisations gain the ability to detect threats, shape attacker behavior, and mitigate attacks. Founded in 2014 by security experts Gadi Evron and Dean Sysman, Cymmetria is changing the asymmetry of cyber security, tilting the traditional security odds so that hackers are the ones left vulnerable. www.cymmetria.com. 

Lunch Sponsors

Ensilo Horizontal No Tagline

 enSilo comprehensively secures the endpoint pre- and post-infection. enSilo automates and orchestrates detection, prevention and real-time response against advanced malware and ransomware without burdening cybersecurity staff. enSilo’s single lightweight agent includes next generation antivirus (NGAV), application communication control, automated endpoint detection and response (EDR) with real-time blocking, threat hunting, incident response and virtual patching capabilities. Coupled with patented approach that has full system visibility, enSilo’s endpoint security solution stops modern malware with a high degree of precision and intuitive user interface. Cybersecurity staff with enSilo can effectively manage malware threats without alert fatigue, excessive dwell time or breach anxiety. enSilo’s cloud management platform is flexible and extensible to meet operational needs that stop malware impact. www.ensilo.com 

Blueliv

Blueliv is a leading cyberthreat intelligence provider, headquartered from Barcelona, Spain. We scour the open, deep and dark web to deliver fresh, automated and actionable threat intelligence to organizations, helping protect their networks from the outside in. Blueliv’s scalable cloud-based technology turns global threat data into sophisticated, relevant intelligence. We enable organizations to save time and resource by accelerating incident response performance, providing user-friendly evidence accessible to all levels within cybersecurity operations teams. Our pay-as-you-need solution delivers an accelerated, predictive view of the threat landscape in real-time. We do not believe in a one-size-fits-all approach, and work together to configure a modular solution bespoke to your needs using separate intelligence modules, all backed up by our world-class in-house analyst team. Blueliv has been named a Gartner Cool Vendor and Go-Ignite winner, and been an FS-ISAC affiliate member for several years.

www.blueliv.com.

Panel Sponsors

Sec

2|SEC is a cyber and data security specialist consultancy that works with SMEs and Enterprises to bring security solutions into the broader business strategy. We deliver a range of audit, testing, training and advisory services to support businesses and their IT security objectives.

We want our clients to be able to focus on growing their business and achieve their objectives with comfort that they are not risking the security of their organisation, day to day operations or bringing their reputation into question. Our tailored solutions protect businesses, reduce the risk of security breaches and ensure speedy response and recovery if an incident occurs.

With the right security in place, your business is able to scale fast, with your systems and data safeguarded to the highest regulatory standards. We offer a jargon-free service with fully transparent work plans and budgets to help company’s to align cyber security initiatives to strategic business goals.

www.2-sec.com

AVATAO.COM

Avatao.com Innovative Learning Kft.

Avatao is an online training platform for developing skills to build secure software.

It offers a rich library of 500+ high-quality IT security exercises for software engineers to teach secure programming from design to deployment in a fun and intuitive way.

Topics cover web security, secure coding in Java, C#, python, DevSecOps, secure API design.

Avatao is unique by its ease-of-use, real-world virtual infrastructure and wide range of up-to-date content that gives developers hands-on, actionable knowledge in a real environment.

www.avatao.com.

Attivo Networks

Attivo Networks® is the leader in deception technology for real-time detection, analysis, and accelerated response to advanced, credential, insider, and ransomware attacks. The Attivo ThreatMatrix™ Deception and Response Platform accurately detects in-network threats and provides continuous threat management for user networks, data centers, cloud, branch, IoT, ICS-SCADA, and POS environments. Attivo Camouflage dynamic deception sets high-interaction traps to efficiently lure attackers into revealing themselves. The solution’s advanced attack analysis and lateral movement tracking automate investigation, deliver evidence-based alerts, and in-depth forensic reports. Incident response is simplified with ThreatOps™ playbooks and 3rd party integrations for automated attack blocking, quarantine, and threat hunting.

www.attivonetworks.com

Twitter: https://twitter.com/attivonetworks?lang=en

LinkedIn: https://www.linkedin.com/company/attivo-networks-inc-/

Garrison

Are you brave enough to click this link?

http://bit.ly/2xdmVRw

The risk of malware and data loss makes the web a dangerous place. You could just block access to everything except the trusted cloud services that the business relies on – great for security, but terrible for users.

Ultra-secure browsing solves the problem. Security and enablement in a single package. Silicon Assured Video Isolation (Garrison SAVI®) is a Secure Remote Browsing technology that means risky web content is never processed on the user’s endpoint device. Designed with the user at its heart, patented Garrison SAVI® technology provides hardware-enforced secure remote browsing for enterprise customers. The Garrison SAVI® Isolation Appliance lives in the cloud or the data centre, doing dangerous web browsing for you. Garrison’s unique approach ensures a great user experience is maintained even when deployed across the largest of enterprises, whilst delivering unparalleled security. Click on every link, browse the web with confidence.

www.garrison.com for more information.

Synack

Synack is pioneering a trusted, hacker-powered approach to protecting an organization’s digital attack surface, augmenting security teams with our private crowd of skilled and trusted hackers to provide proactive application and penetration testing services from a truly adversarial perspective.

www.synack.com

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
Blueliv (Official Sponsor, CISO 360 Congress 2017)

“Excellent conference, brilliantly put together. Look forward to the next one!”
Anthony Young, Partner, Bridewell Consulting (Official Sponsor, CISO 360 Congress 2017)

Unique sponsorship proposition

WordItOut Word Cloud

Company85 is an independent IT infrastructure and security services firm which leads change, strips out cost and safeguards information.

Headquartered in London, we provide data centre, workspace, cloud, security and network services to some of the biggest global organisations in the public and private sector across the UK and the world.

We speak honestly and confidentially to people in all types of organisations about the practical steps they can take to feel confident about their cyber security. Some of the companies who trust us include AstraZeneca, Prudential, Murphy, Tullett Prebon, Cyberark, Hitachi Rail Europe and GSK.

Voted Services Company of the Year (2016 BCS UK IT Awards) and Security Team of the Year in 2016 and 2017 (Computing Security Excellence Awards), Company85 was particularly commended for innovative thought leadership around subjects such as GDPR, and our pioneering vCISO service.

www.company85.com

Double Deal?

Anomali

Cyberark Logo1

SailPoint

 SailPoint’s identity management solutions provide complete visibility into who is doing what, what kind of risk that represents, and allows you to take action. It links people, applications, data and devices to create an identity-enabled enterprise. www.sailpoint.com 

Qualys

Qualys, Inc. (NASDAQ: QLYS) is a pioneer and leading provider of cloud-based security and compliance solutions with over 9,300 customers in more than 100 countries, including a majority of each of the Forbes Global 100 and Fortune 100. The Qualys Cloud Platform and integrated suite of solutions help organizations simplify security operations and lower the cost of compliance by delivering critical security intelligence on demand and automating the full spectrum of auditing, compliance and protection for IT systems and web applications. Founded in 1999, Qualys has established strategic partnerships with leading managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, Fujitsu, HCL Technologies, HP Enterprise, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. www.qualys.com.


Darktrace

Darktrace is the world’s leading machine learning company for cyber security. Created by mathematicians from the University of Cambridge, Darktrace’s Enterprise Immune System uses AI algorithms that mimic the human immune system to defend enterprise networks of all types and sizes. Our self-learning approach is the first non-consumer application of machine learning to work at scale, across all network types, from physical, virtualized, and cloud, through to IoT and industrial control systems. By applying its unique, unsupervised machine learning, Darktrace has identified 30,000 previously unknown threats in over 2,400 networks, including zero-days, insider threats and subtle, stealthy attacks. www.darktrace.com.


Trendmicro

As a global leader in IT security, Trend Micro develops innovative security solutions that make the world safe for businesses and consumers to exchange digital information. With over 25 years of security expertise, we’re recognized as the market leader in server security, cloud security, and small business content security. Trend Micro security fits the needs of our customers and partners. Our solutions protect end users on any device, optimize security for the modern data center, and secure networks against breaches from targeted attacks. We deliver top-ranked client-server, network, and cloud-based protection that stops new threats faster, detects breaches better, and protects data in physical, virtual, and cloud environments. www.trendmicro.co.uk


RiskIQ

RiskIQ is the leader in digital threat management, providing the most comprehensive discovery, intelligence, and mitigation of threats associated with an organization’s digital presence. RiskIQ allows enterprises to gain unified insight and control over web, social, and mobile exposures. Our platform combines advanced internet data reconnaissance and analytics to expedite investigations, understand attack surfaces, assess risk, and take action against digital threats. www.riskiq.com


Cymmetria

Cymmetria is a startup offering a pioneering cyber deception solution, based on breadcrumbs and decoys that lead attackers away from valuable targets. With Cymmetria, organisations gain the ability to detect threats, shape attacker behavior, and mitigate attacks. Founded in 2014 by security experts Gadi Evron and Dean Sysman, Cymmetria is changing the asymmetry of cyber security, tilting the traditional security odds so that hackers are the ones left vulnerable. www.cymmetria.com.


NEWEPSBridewellLogoFinal1

Bridewell consultants are highly qualified and motivated cyber security experts. Our focus is to secure our clients’ information, technology, and networks from the many threats that they face. We provide leadership, understanding and solutions to allow our clients to benefit from the huge opportunities that the digital economy brings. We believe a strong defence and better cyber skills are essential in every organisation. We understand cloud technologies, cloud security and how to design, implement and review their deployment for a business. Bridewell are pleased to announce our company and our Audit & Review service has been recognised and certified by the National Cyber Security Centre – NCSC. www.bridewellconsulting.com


Blueliv

Blueliv is a leading provider of targeted cyber threat intelligence for large enterprises, service providers, and security vendors. Its cyber threat intelligence platform and data feed address a comprehensive range of cyber threats to turn global threat data into predictive, automated and actionable intelligence which detects, identifies, and helps stopping cyber threats. www.blueliv.com

2017 Association & Media Partners

THIBER

Anomali

Cyberark Logo1

SailPoint

SailPoint’s identity management solutions provide complete visibility into who is doing what, what kind of risk that represents, and allows you to take action. It links people, applications, data and devices to create an identity-enabled enterprise. www.sailpoint.com


Qualys

Qualys, Inc. (NASDAQ: QLYS) is a pioneer and leading provider of cloud-based security and compliance solutions with over 9,300 customers in more than 100 countries, including a majority of each of the Forbes Global 100 and Fortune 100. The Qualys Cloud Platform and integrated suite of solutions help organizations simplify security operations and lower the cost of compliance by delivering critical security intelligence on demand and automating the full spectrum of auditing, compliance and protection for IT systems and web applications. Founded in 1999, Qualys has established strategic partnerships with leading managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, Fujitsu, HCL Technologies, HP Enterprise, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. www.qualys.com.


Darktrace

Darktrace is the world’s leading machine learning company for cyber security. Created by mathematicians from the University of Cambridge, Darktrace’s Enterprise Immune System uses AI algorithms that mimic the human immune system to defend enterprise networks of all types and sizes. Our self-learning approach is the first non-consumer application of machine learning to work at scale, across all network types, from physical, virtualized, and cloud, through to IoT and industrial control systems. By applying its unique, unsupervised machine learning, Darktrace has identified 30,000 previously unknown threats in over 2,400 networks, including zero-days, insider threats and subtle, stealthy attacks. www.darktrace.com.


Trendmicro

As a global leader in IT security, Trend Micro develops innovative security solutions that make the world safe for businesses and consumers to exchange digital information. With over 25 years of security expertise, we’re recognized as the market leader in server security, cloud security, and small business content security. Trend Micro security fits the needs of our customers and partners. Our solutions protect end users on any device, optimize security for the modern data center, and secure networks against breaches from targeted attacks. We deliver top-ranked client-server, network, and cloud-based protection that stops new threats faster, detects breaches better, and protects data in physical, virtual, and cloud environments. www.trendmicro.co.uk


RiskIQ

RiskIQ is the leader in digital threat management, providing the most comprehensive discovery, intelligence, and mitigation of threats associated with an organization’s digital presence. RiskIQ allows enterprises to gain unified insight and control over web, social, and mobile exposures. Our platform combines advanced internet data reconnaissance and analytics to expedite investigations, understand attack surfaces, assess risk, and take action against digital threats. www.riskiq.com


Cymmetria

Cymmetria is a startup offering a pioneering cyber deception solution, based on breadcrumbs and decoys that lead attackers away from valuable targets. With Cymmetria, organisations gain the ability to detect threats, shape attacker behavior, and mitigate attacks. Founded in 2014 by security experts Gadi Evron and Dean Sysman, Cymmetria is changing the asymmetry of cyber security, tilting the traditional security odds so that hackers are the ones left vulnerable. www.cymmetria.com.


NEWEPSBridewellLogoFinal1

Bridewell consultants are highly qualified and motivated cyber security experts. Our focus is to secure our clients’ information, technology, and networks from the many threats that they face. We provide leadership, understanding and solutions to allow our clients to benefit from the huge opportunities that the digital economy brings. We believe a strong defence and better cyber skills are essential in every organisation. We understand cloud technologies, cloud security and how to design, implement and review their deployment for a business. Bridewell are pleased to announce our company and our Audit & Review service has been recognised and certified by the National Cyber Security Centre – NCSC. www.bridewellconsulting.com


Blueliv

Blueliv is a leading provider of targeted cyber threat intelligence for large enterprises, service providers, and security vendors. Its cyber threat intelligence platform and data feed address a comprehensive range of cyber threats to turn global threat data into predictive, automated and actionable intelligence which detects, identifies, and helps stopping cyber threats. www.blueliv.com

Who attends

By Designation

  • Chief Information Security Officers
  • Directors of Cybersecurity / Heads of Cyber Threat Intelligence
  • Chief Information Risk Officers
  • CEOs, CTOs, CIOs, CROs
  • Chief Security Architects / Heads of Security Infrastructure
  • Directors of Technology Innovation or Directors of Digital Risk
  • Chief Data Officers
  • Chief Privacy Officers

By Sector

  • Financial services – including insurance
  • Energy – power, water and critical national infrastructure companies
  • Extractives – mining, oil and gas
  • Pharmaceuticals and health
  • Consumer goods
  • Manufacturing
  • Retail
  • Transport and logistics
  • Government departments

By Region

  • UK – 45%
  • Cross-Europe – 45%
  • Rest of World – 10%

Why attend

  • CISO 360 technology innovation clinics
    Embedded benchmarking sessions that enable you to ask the right questions of your technical teams.
  • International and multi-faceted
    An exciting international speaker panel of CEOs, CIOs, CISOs, cyber threat, corporate security, anti-fraud directors will break down traditional siloes between business-security-technology-legal.
  • Designed ‘by, with and for’ in-house security leaders
    Sharing live case studies from those who lead on the job day in day out.
  • R&D and investment focus! No typical industry barrier between buy and sell
    Natural integration between inhouse security, technology innovators and investors.
  • Immersive agenda with real-time benchmarking and exciting debates
    Dynamic debates, think tanks, on-stage fireside chats, Sli.do live polls!
  • Intimate and inspiring networking – community based trusted ‘closed door’ environment.
    The entire event is held under the Chatham House Rule. Networking dinners included! Enduring connections guaranteed.

Venue & Accommodation

Lisbon Marriott Hotel

Avenida dos Combatentes 45, Lisbon 1600-042 Portugal
http://www.marriott.com/hotels/travel/lispt-lisbon-marriott-hotel/?scid=bb1a189a-fec3-4d19-a255-54ba596febe2

The 2nd CISO 360 Congress 2018 will be hosted at Lisbon Marriott Hotel, located in the desirable Palma de Baixo district, in the heart of Lisbon’s most popular area for touring and business. The Marriott offers comfortable rooms featuring private balconies and gorgeous views of Lisbon and the lush gardens and pool. The rooms at the Marriott Lisbon offers rooms with floor-to-ceiling windows and private balconies allowing natural light into your restful accommodation with stunning views of Lisbon or the calming garden and swimming pool. All rooms have a spacious work area and Wi-Fi access.

Accommodation at the Congress venue

We have negotiated favourable room rates at the Marriott Lisbon Hotel. Executive rooms – 184€ + taxes (single occupancy) pending availability.
Rooms are limited so we urge you to book soonest and before 29th May 2018. We cannot guarantee room availability or rates.

Alternative accommodation within walking distance of the Congress venue

SANA Metropolitan Hotel – within a 10-minute walk from the Marriott Lisbon.

Discounted rate of 135€ (£119) single occupancy per night + taxes (minimum 2 nights). We cannot guarantee room availability or rates.

Conference venue

All facilities at the Marriott are elegantly furnished and equipped with state of the art audio visual equipment, from inbuilt ceiling speakers, LED TV Screens and iPad for systems control. Wireless internet is available in all public spaces to allow guests to remain connected throughout the duration of the event and the culinary professionals have created inspiring menus for morning and afternoon breaks as well as the buffet lunch.

Location

The Lisbon Marriott hotel is located at Avenida dos Combatentes 45 Lisbon 1600-042 Portugal.

Driving directions from Lisbon Portela Airport (LIS): Take A1 (north) Or ‘Vasco Da Gama’ Bridge; Take second Circular Turn To Eixo Norte/sul towards ‘Santa Maria Hospital’ and turn Right By Catholic University.

Directions from Downtown: Go South Or 25 De Abril Bridge; Follow Direction Praca De Espanha And Take Av. Dos Combatentes. The Lisbon Marriott is on the left side of the avenue.

On-site parking fee: 2.80 EUR hourly, 19 EUR daily
Valet parking fee: 19 EUR daily

Outdoor-Pool-evening-croped

Testimonials – Pulse 360 events

“If you want to hear real CISO experiences, you must attend this event!” –Chuan-Wei Hoo, CISO, ST Engineering, Singapore

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” – Thomas Foster,  SailPoint

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” – Martyn Booth, CISO, Euromoney Institutional Investor PLC

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” – Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building.  Looking forward to the next one.”
– Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” –  Catherine Coale, Company85 

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” – Joe Breen, Company85 

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” – James Gosnold, Technology Services Head of Cyber Security, DWP 

““A very thoughtful event, great networking and industrial expertise in the room to learn from!” – Ryan Chan, Director, Security, Laureate International Universities Malaysia

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Philippe Besson, Europe Industries- Security Officer, Air Liquide GMS

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” – NetClean

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” – Colette Hanley, Chief Privacy Officer, Nokia Group 

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” – Ben Bulpett, SailPoint

“By far the best event for 2018 I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Ali Zeb, Group CISO and Group DPO, MS Amlin

“I would like to extend my appreciation having been given the chance to witness the success of your recent  event. I look forward to a further outstanding  lineup of events from your organization!“

Christopher Rollan, Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
– Ali Zeb, CISO, MS Amlin

”Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Joe Dauncey, Director Security Engineering, Inmarsat

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh

— Holly Foxcroft (@holly_foxcroft) 21 June 2018

“A very engaging, varied and interactive event. The best conference I have ever attended!”

– David Colbourne, Information Security Manager, Lloyd’s of London


“”The best speaker line-up of any security conference in Europe!”
– Michael Colao, Head of UK Security, AXA

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, Brian Brackenborugh, CISO, Channel 4

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – Sérgio Gonçalves, Logista Portugal

“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” – Chucks Ojeme, CISO, Gebauer & Griller


“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought provoking conversations”
– Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Quentyn Taylor, Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018


“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under Chatham house rules. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during 1×1 networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISO’s across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
– Stephen Khan, Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland


Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

“Refreshing views of security topics for knowledge improvement!”
 Pedro Cunha, CISO, Credibom

““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
-Sponsor testimonial, Blueliv

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018


High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018


“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, James Kwaan, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” Luis Vilares, GRC Specialist, Euronext

It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO

— Viktor Polic (@ViktorPolic) 26 June 2018


“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
– Irene Corpuz, Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” – James Chuka, Sailpoint 

“”I found CISO360 Conference a great place to share ideas about current and future problems”
– Sonia Morales, Head of Section, GMV


“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
– Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum


““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
– Ramón Serres, Head of Information Security, Risk Management and Quality, Almirall

““Pulse organised a fantastic CISO360 conference in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO360 and
look forward to this conference going from strength to strength”
– FC, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

““Excellent conference, brilliantly put together. Look forward to the next one.”
– Anthony Young, Partner, Bridewell Consulting

Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!“


Irene Corpuz, Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”  Sergio Goncalvez, Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use” James Gosnold, Technology Services Head of Security, DWP