Archive · CISO 360 Global Congress

8th CISO 360 Global Congress - Flagship for Cybersecurity Leaders

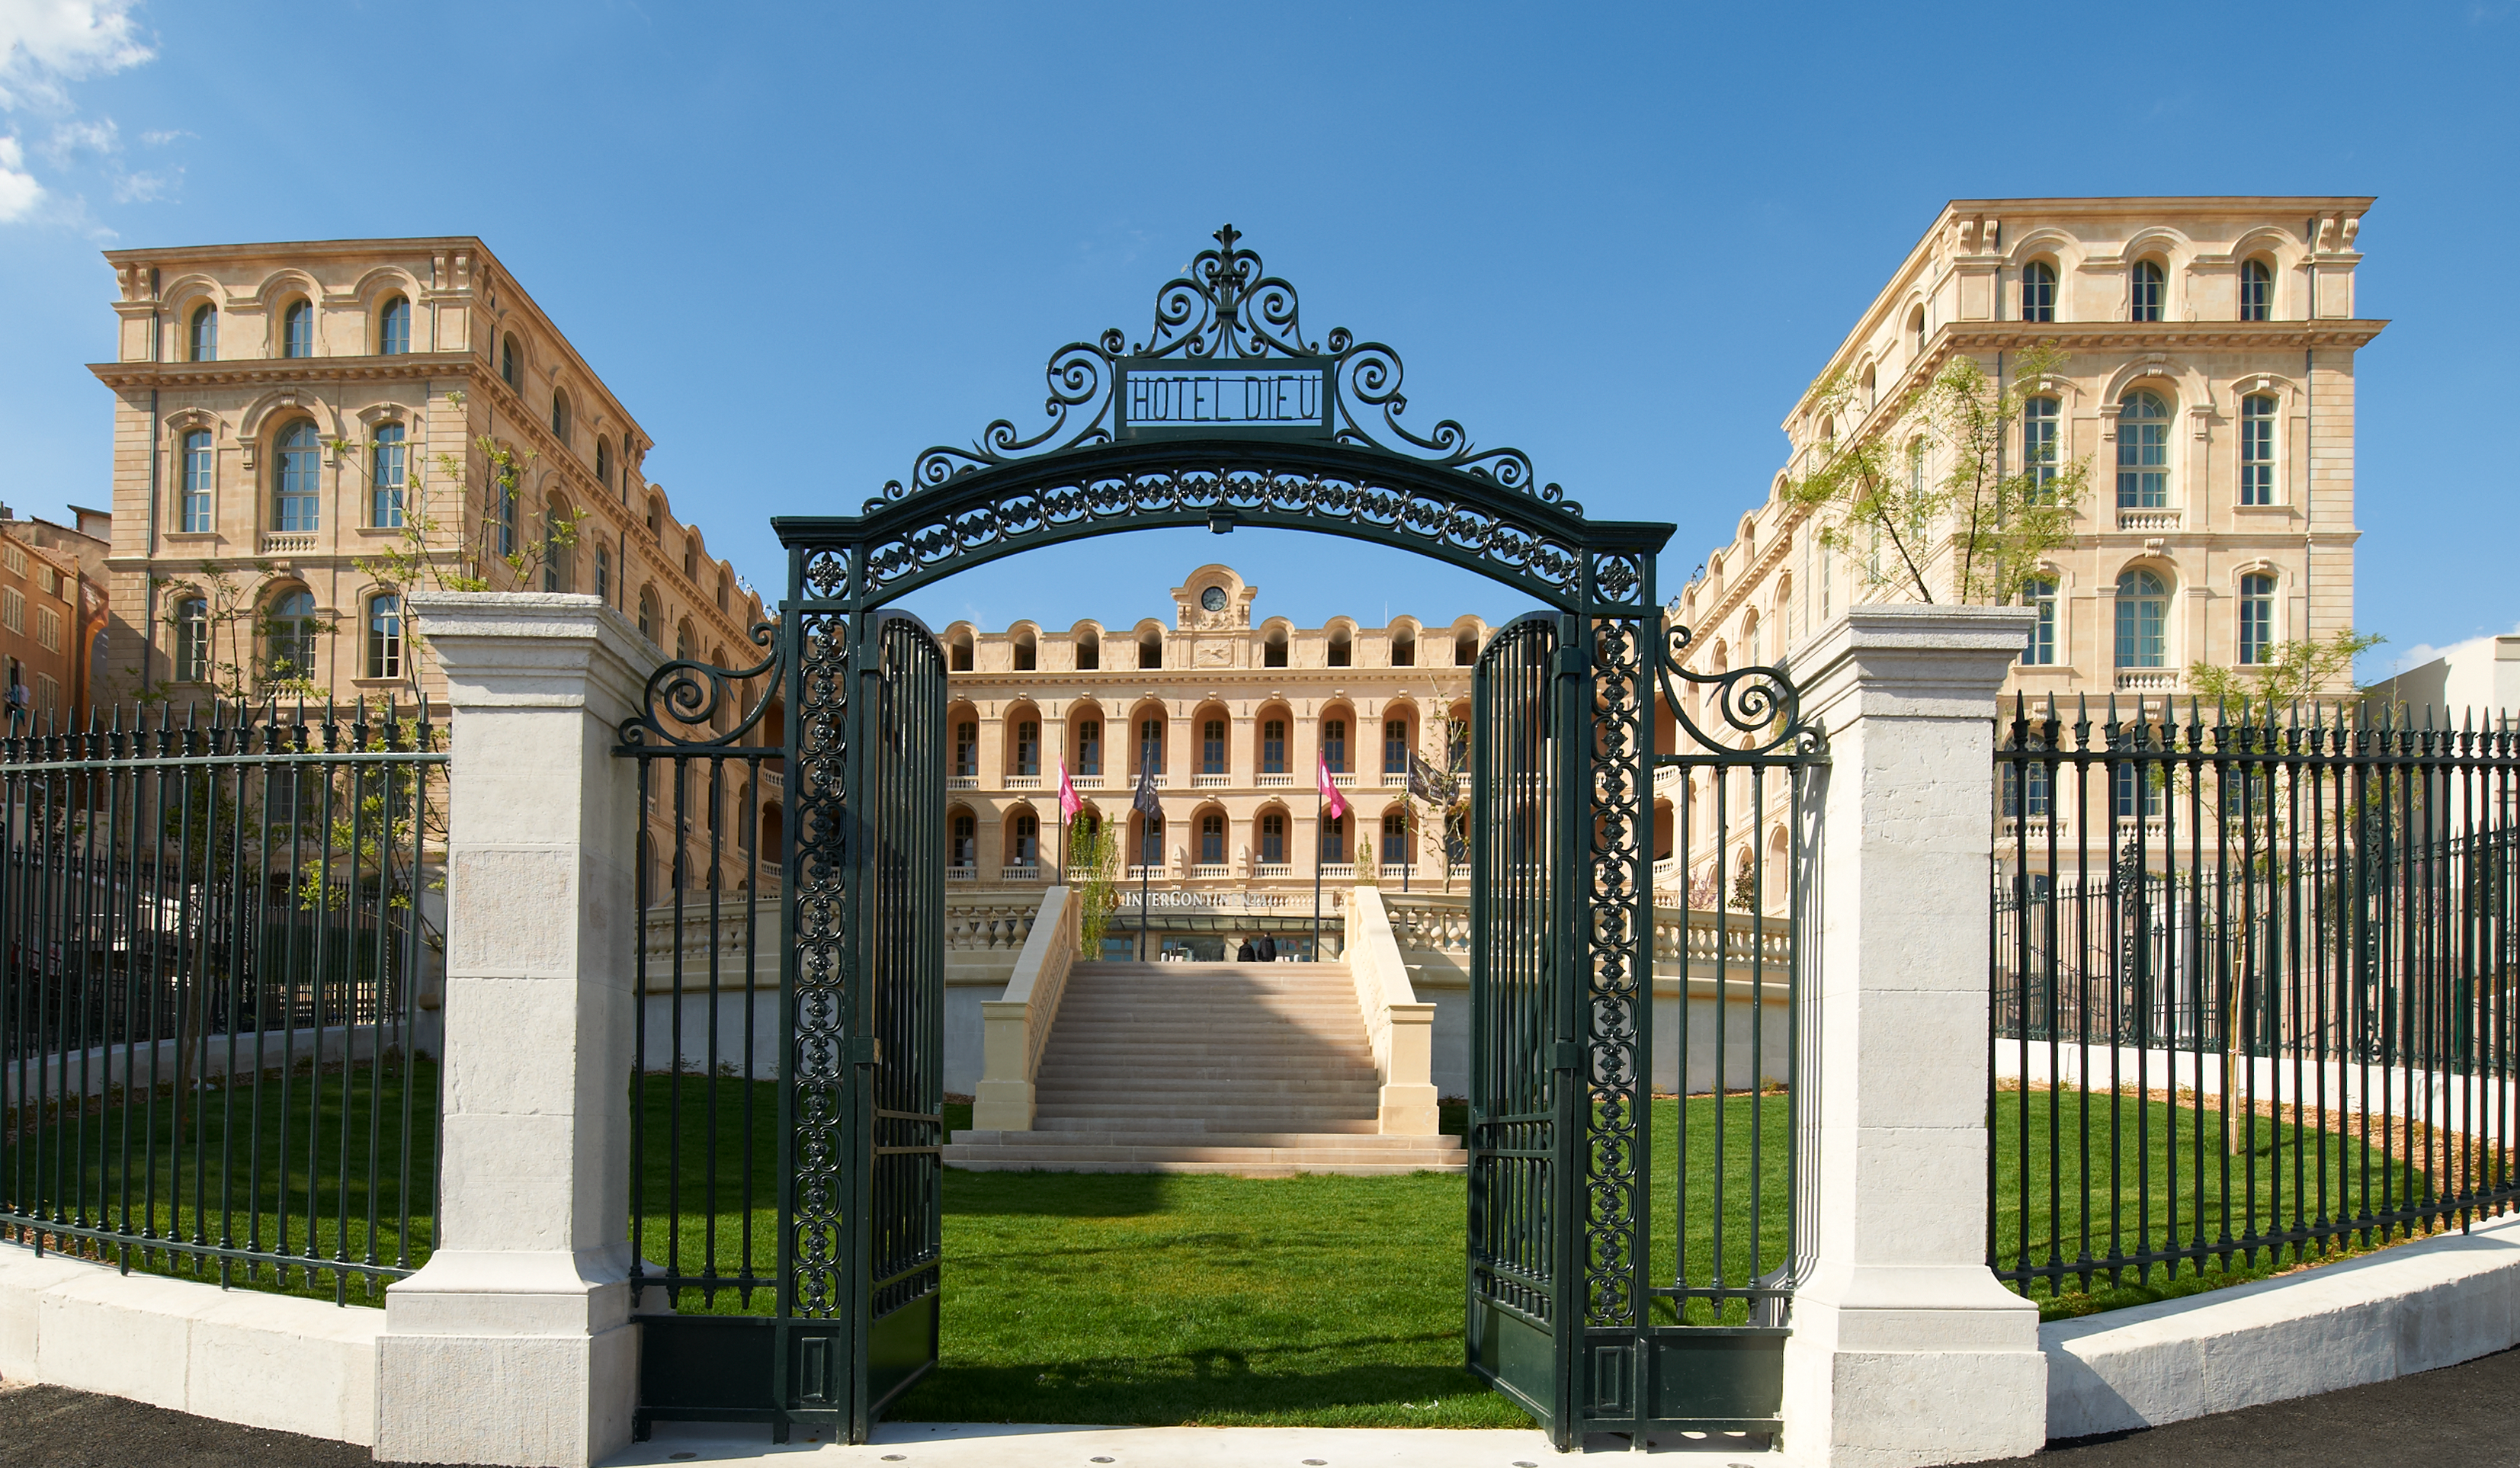
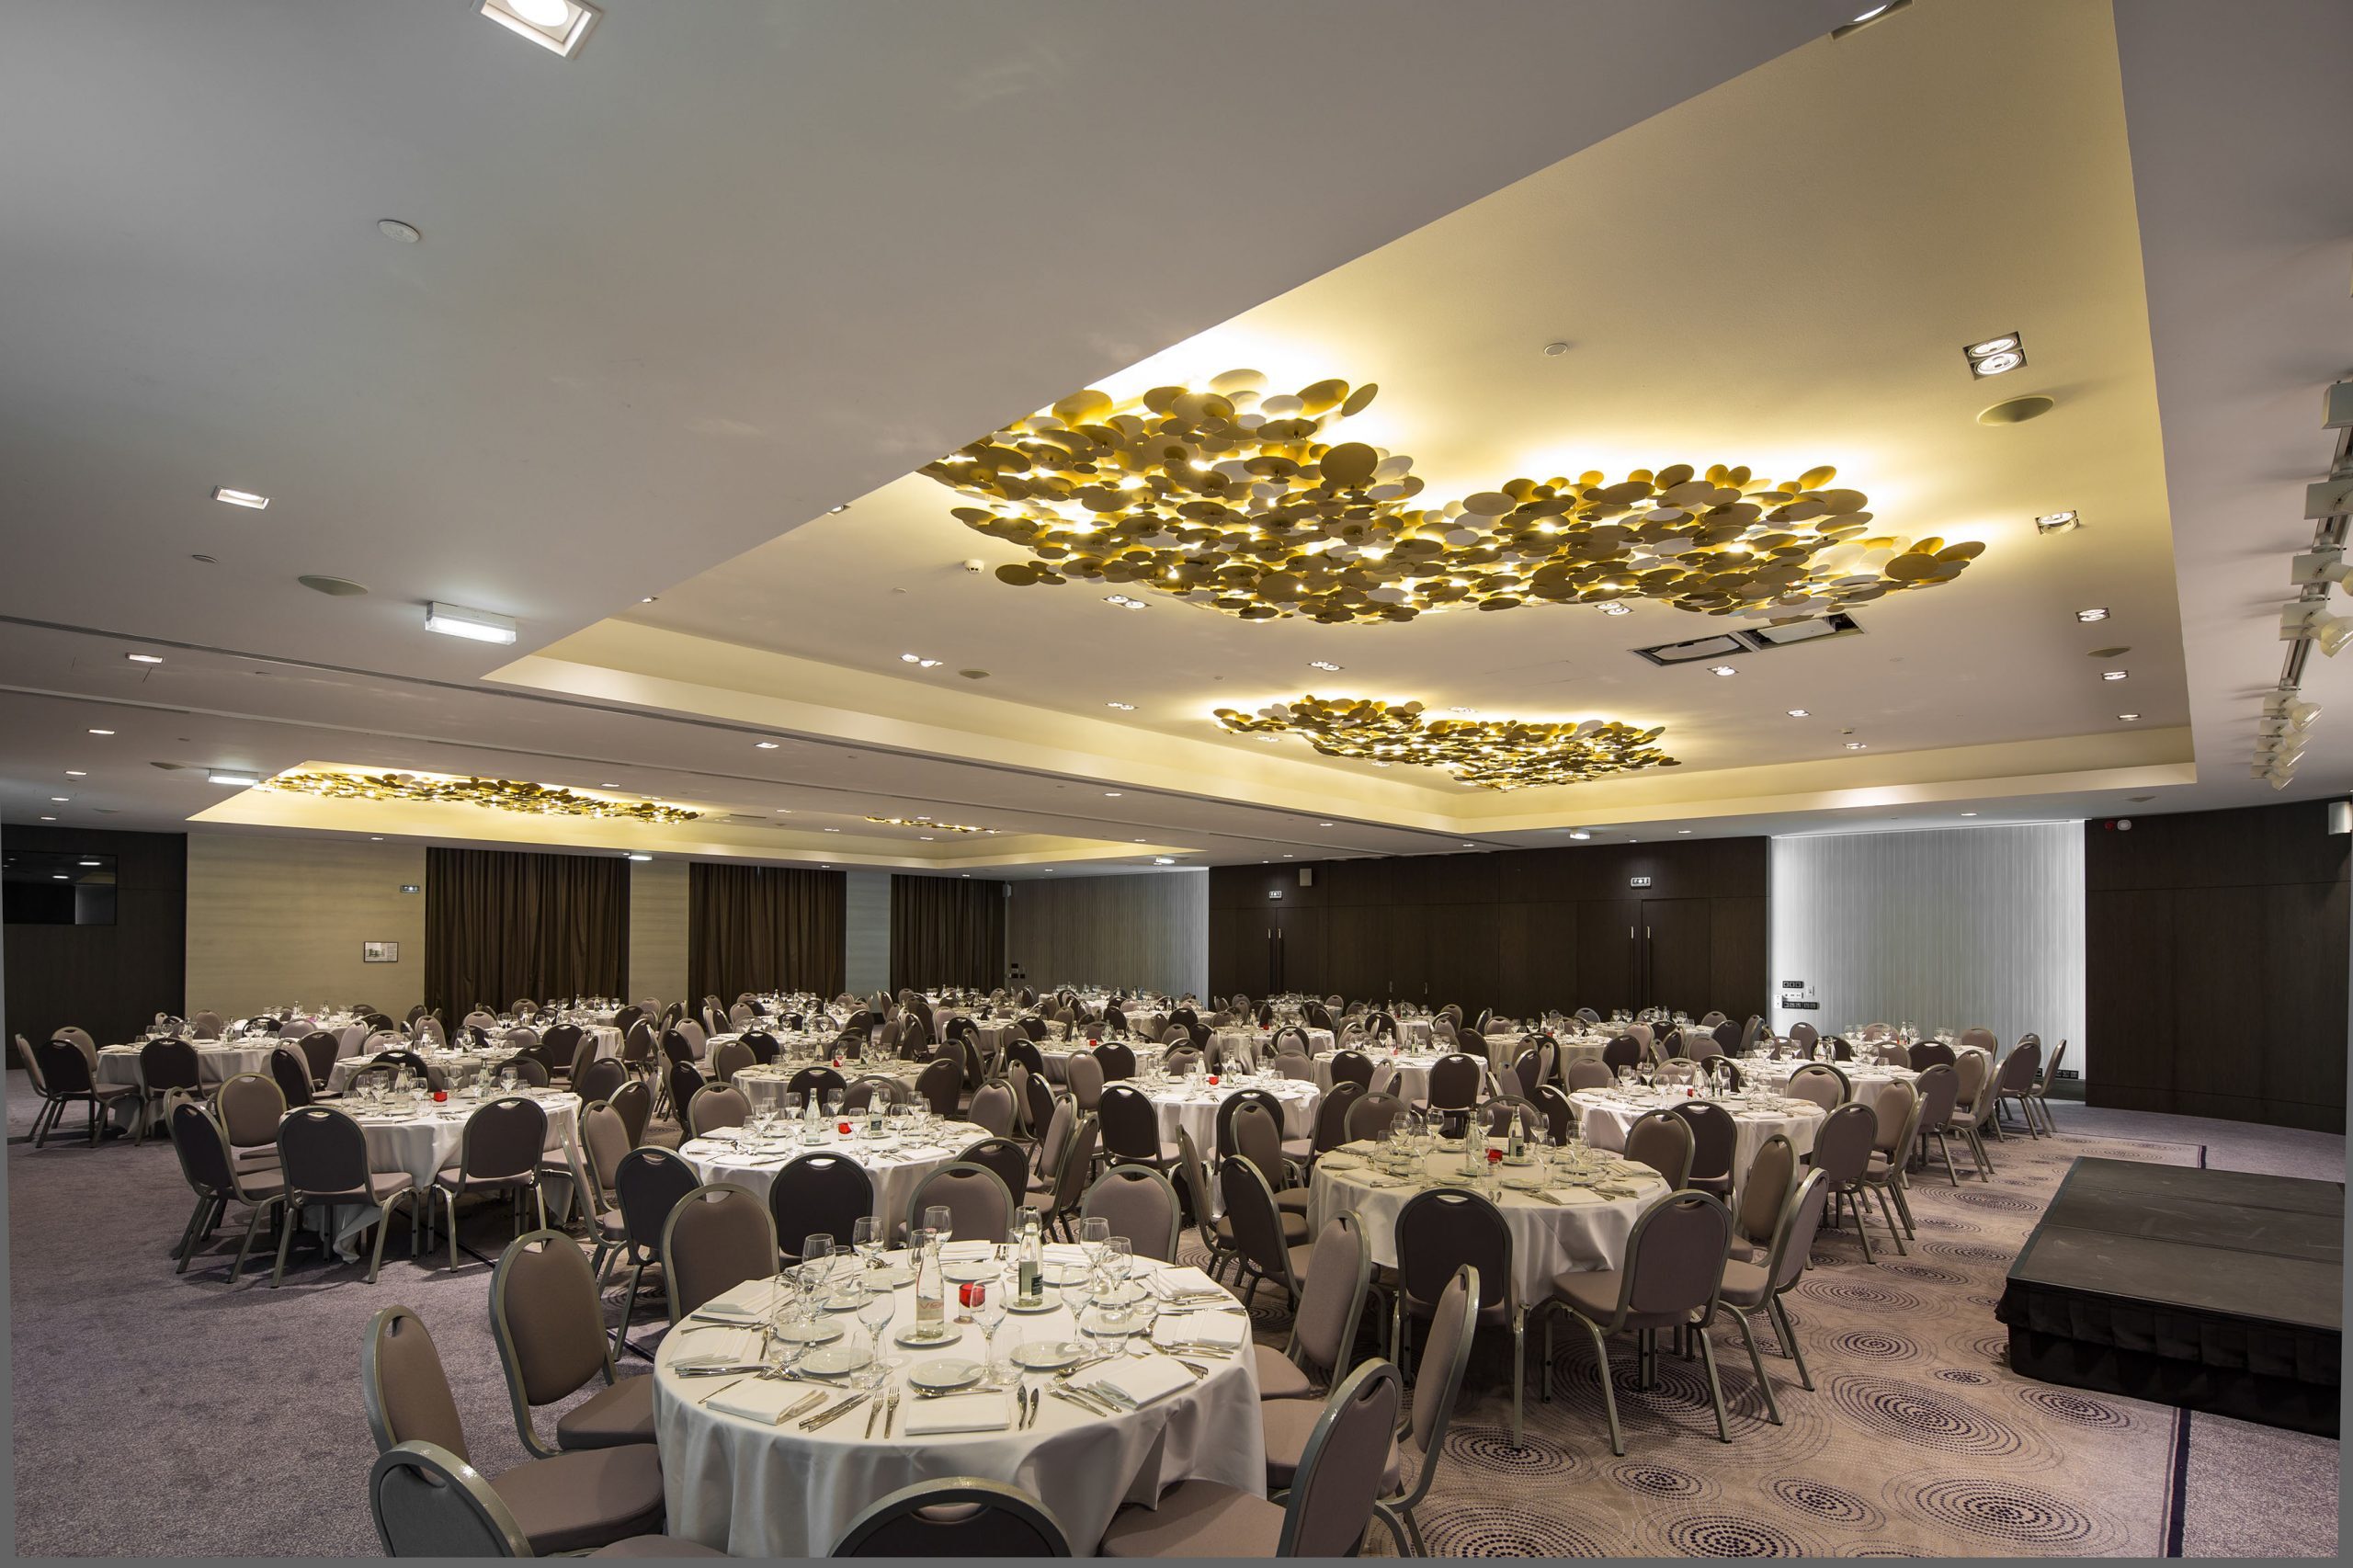
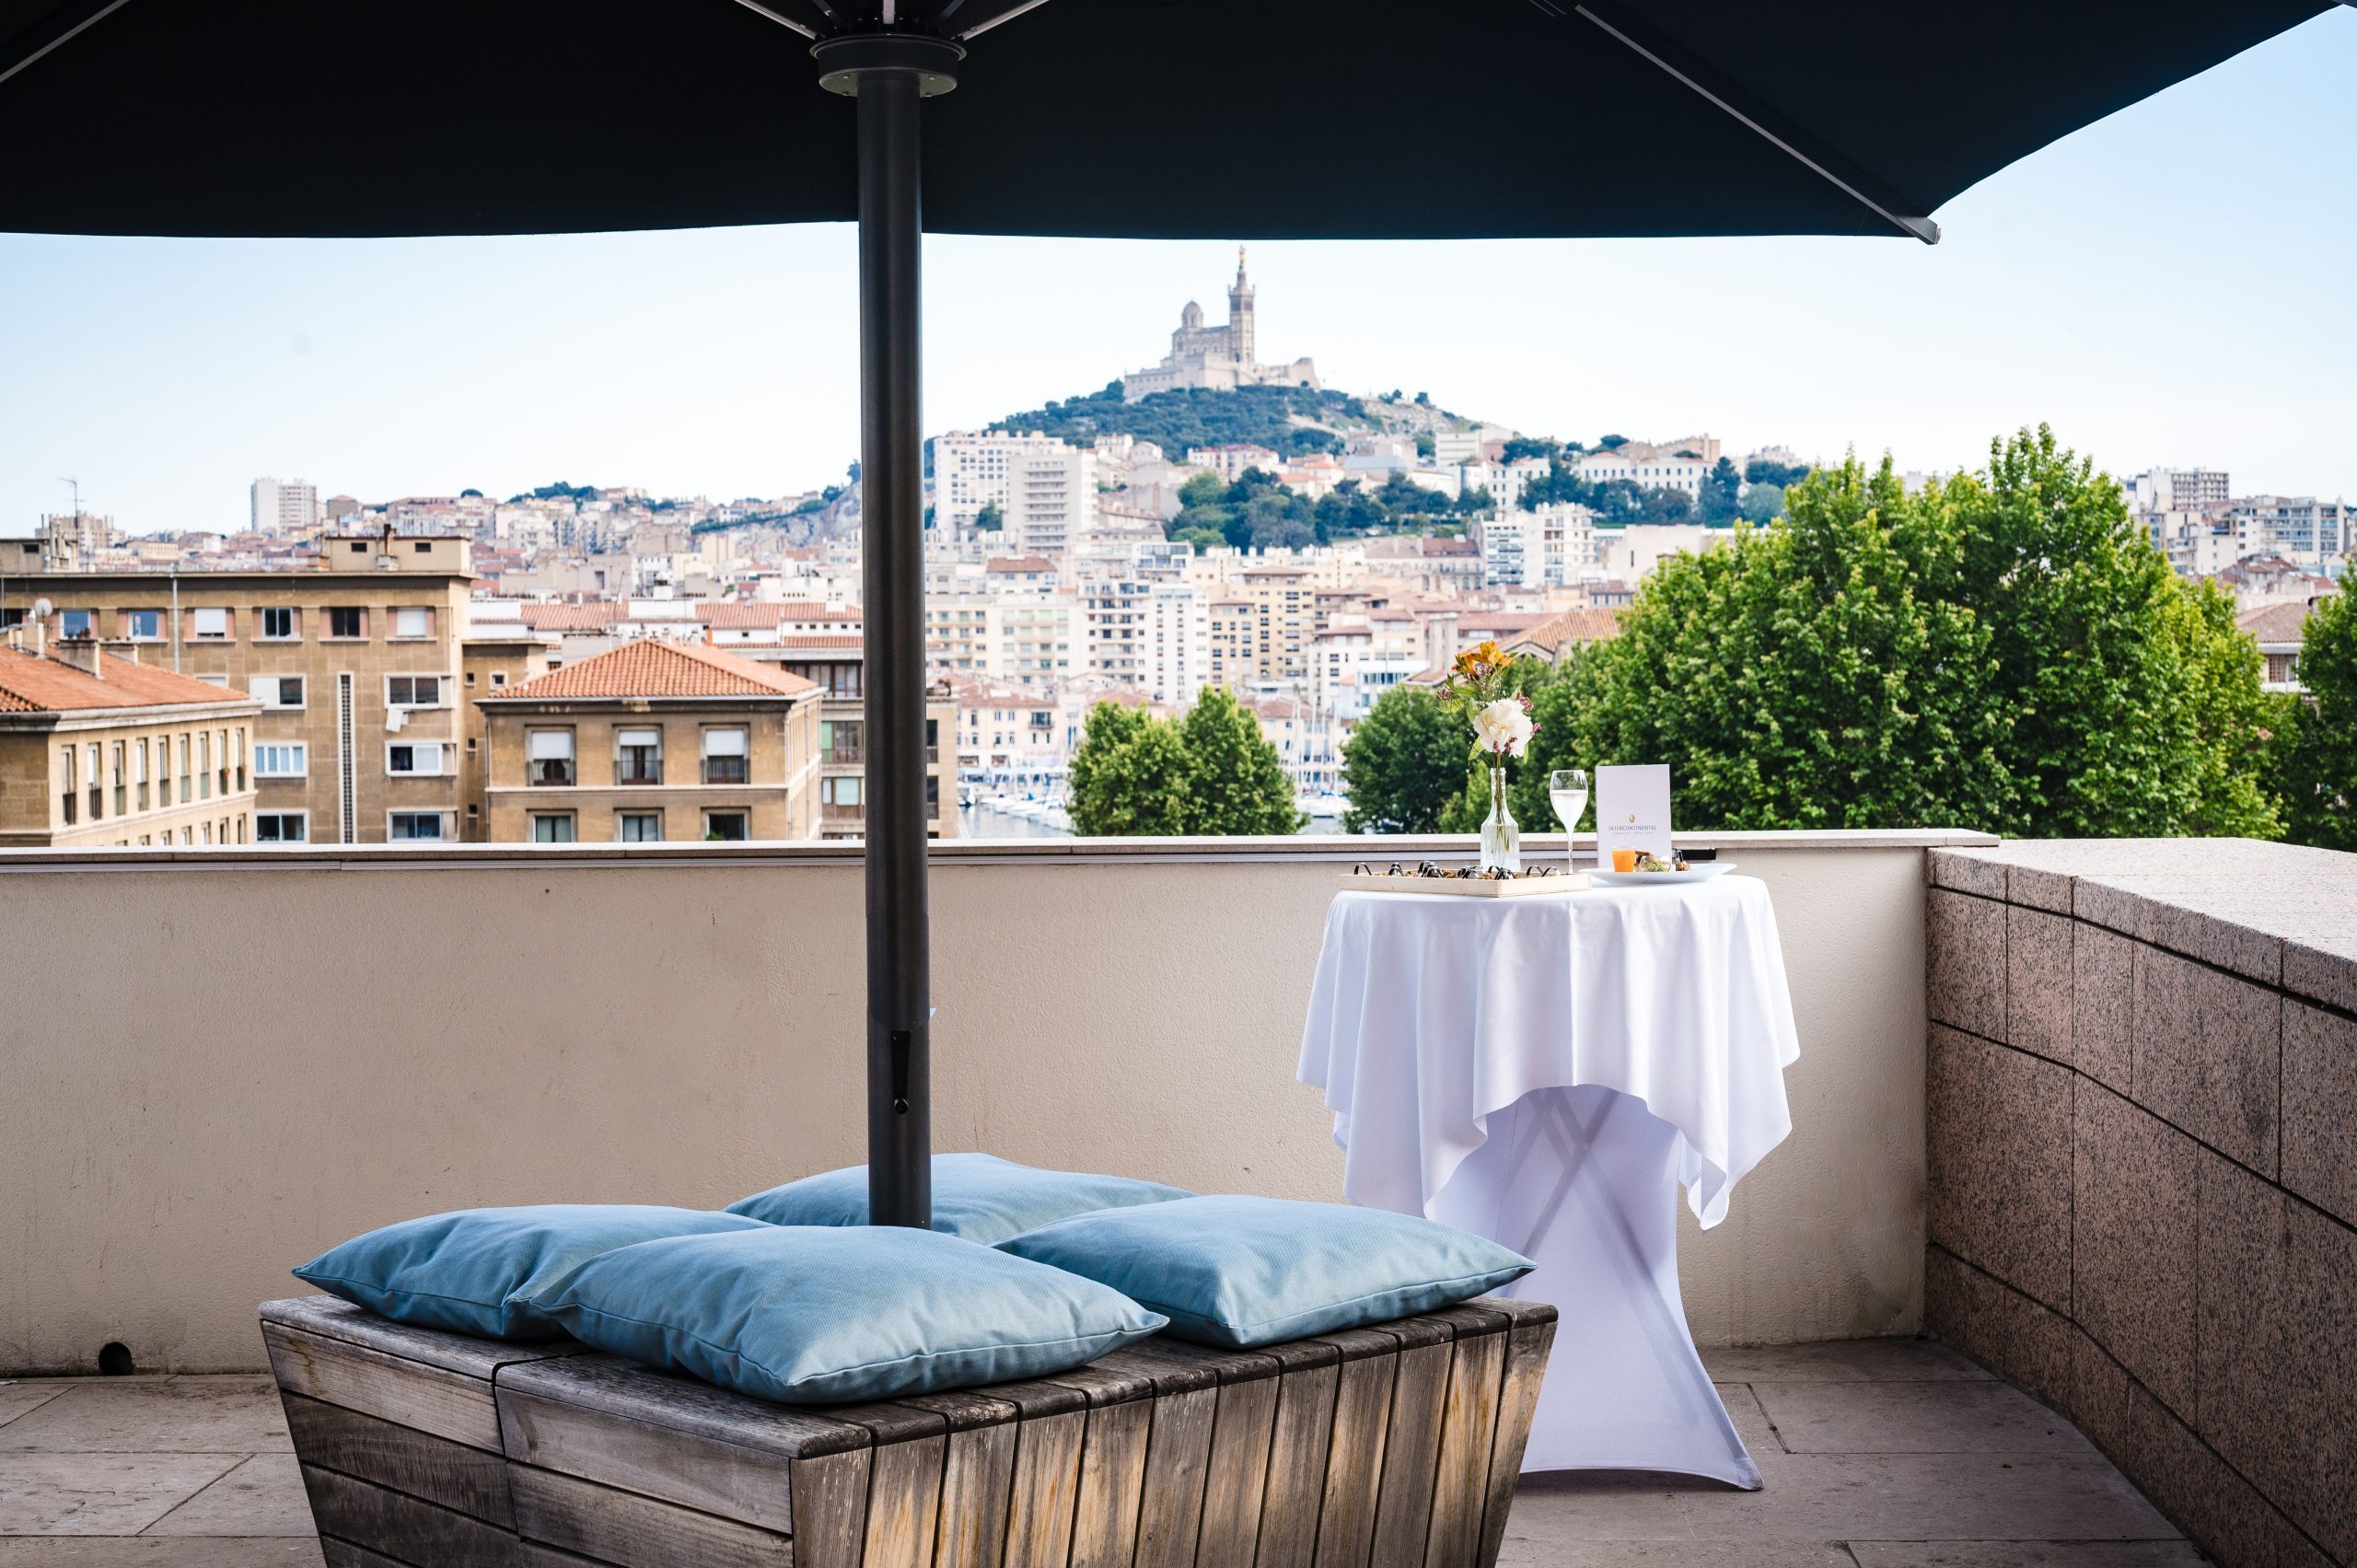
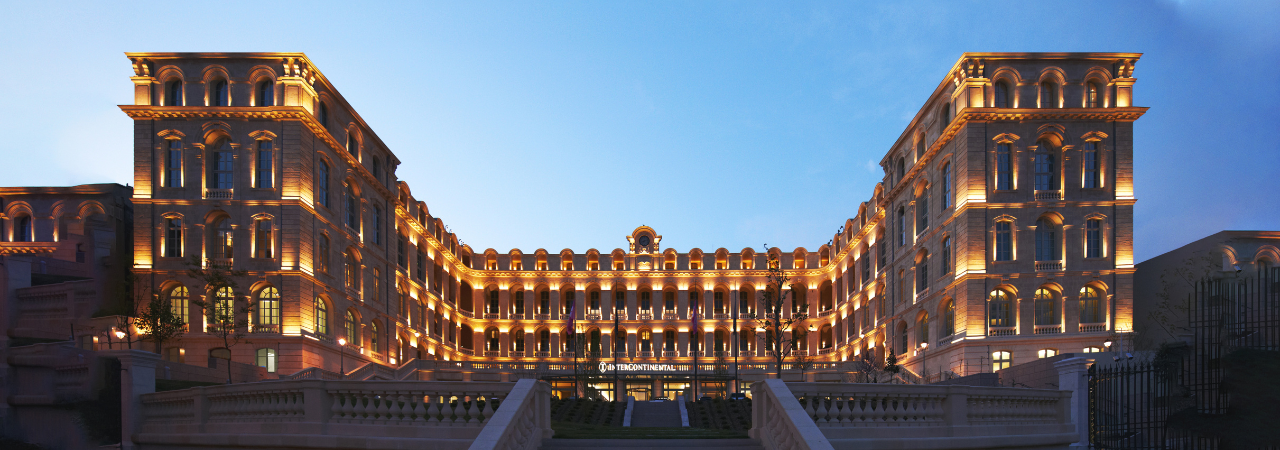
This event took place on 19 – 21 June 2024 at Hotel Dieu Intercontinental Marseille.

Date19 – 21 June 2024
VenueHotel Dieu Intercontinental Marseille

This years’ 8th CISO 360 Global Congress was hosted on 19 – 21 June 2024 at the wonderful Hôtel Dieu InterContinental Marseille in France.

Driving Resilience and Trust in Cybersecurity: The CISO Life Toolkit for Value Creation

Registration is now closed

Gallery - Marseille 2024Link to 2024 Presentations

Marseille played host to strategic conversations with CISOs and cybersecurity luminaries from around the world in the summer of 2024.

Video highlights from this years’ 8th CISO 360 Global Congress

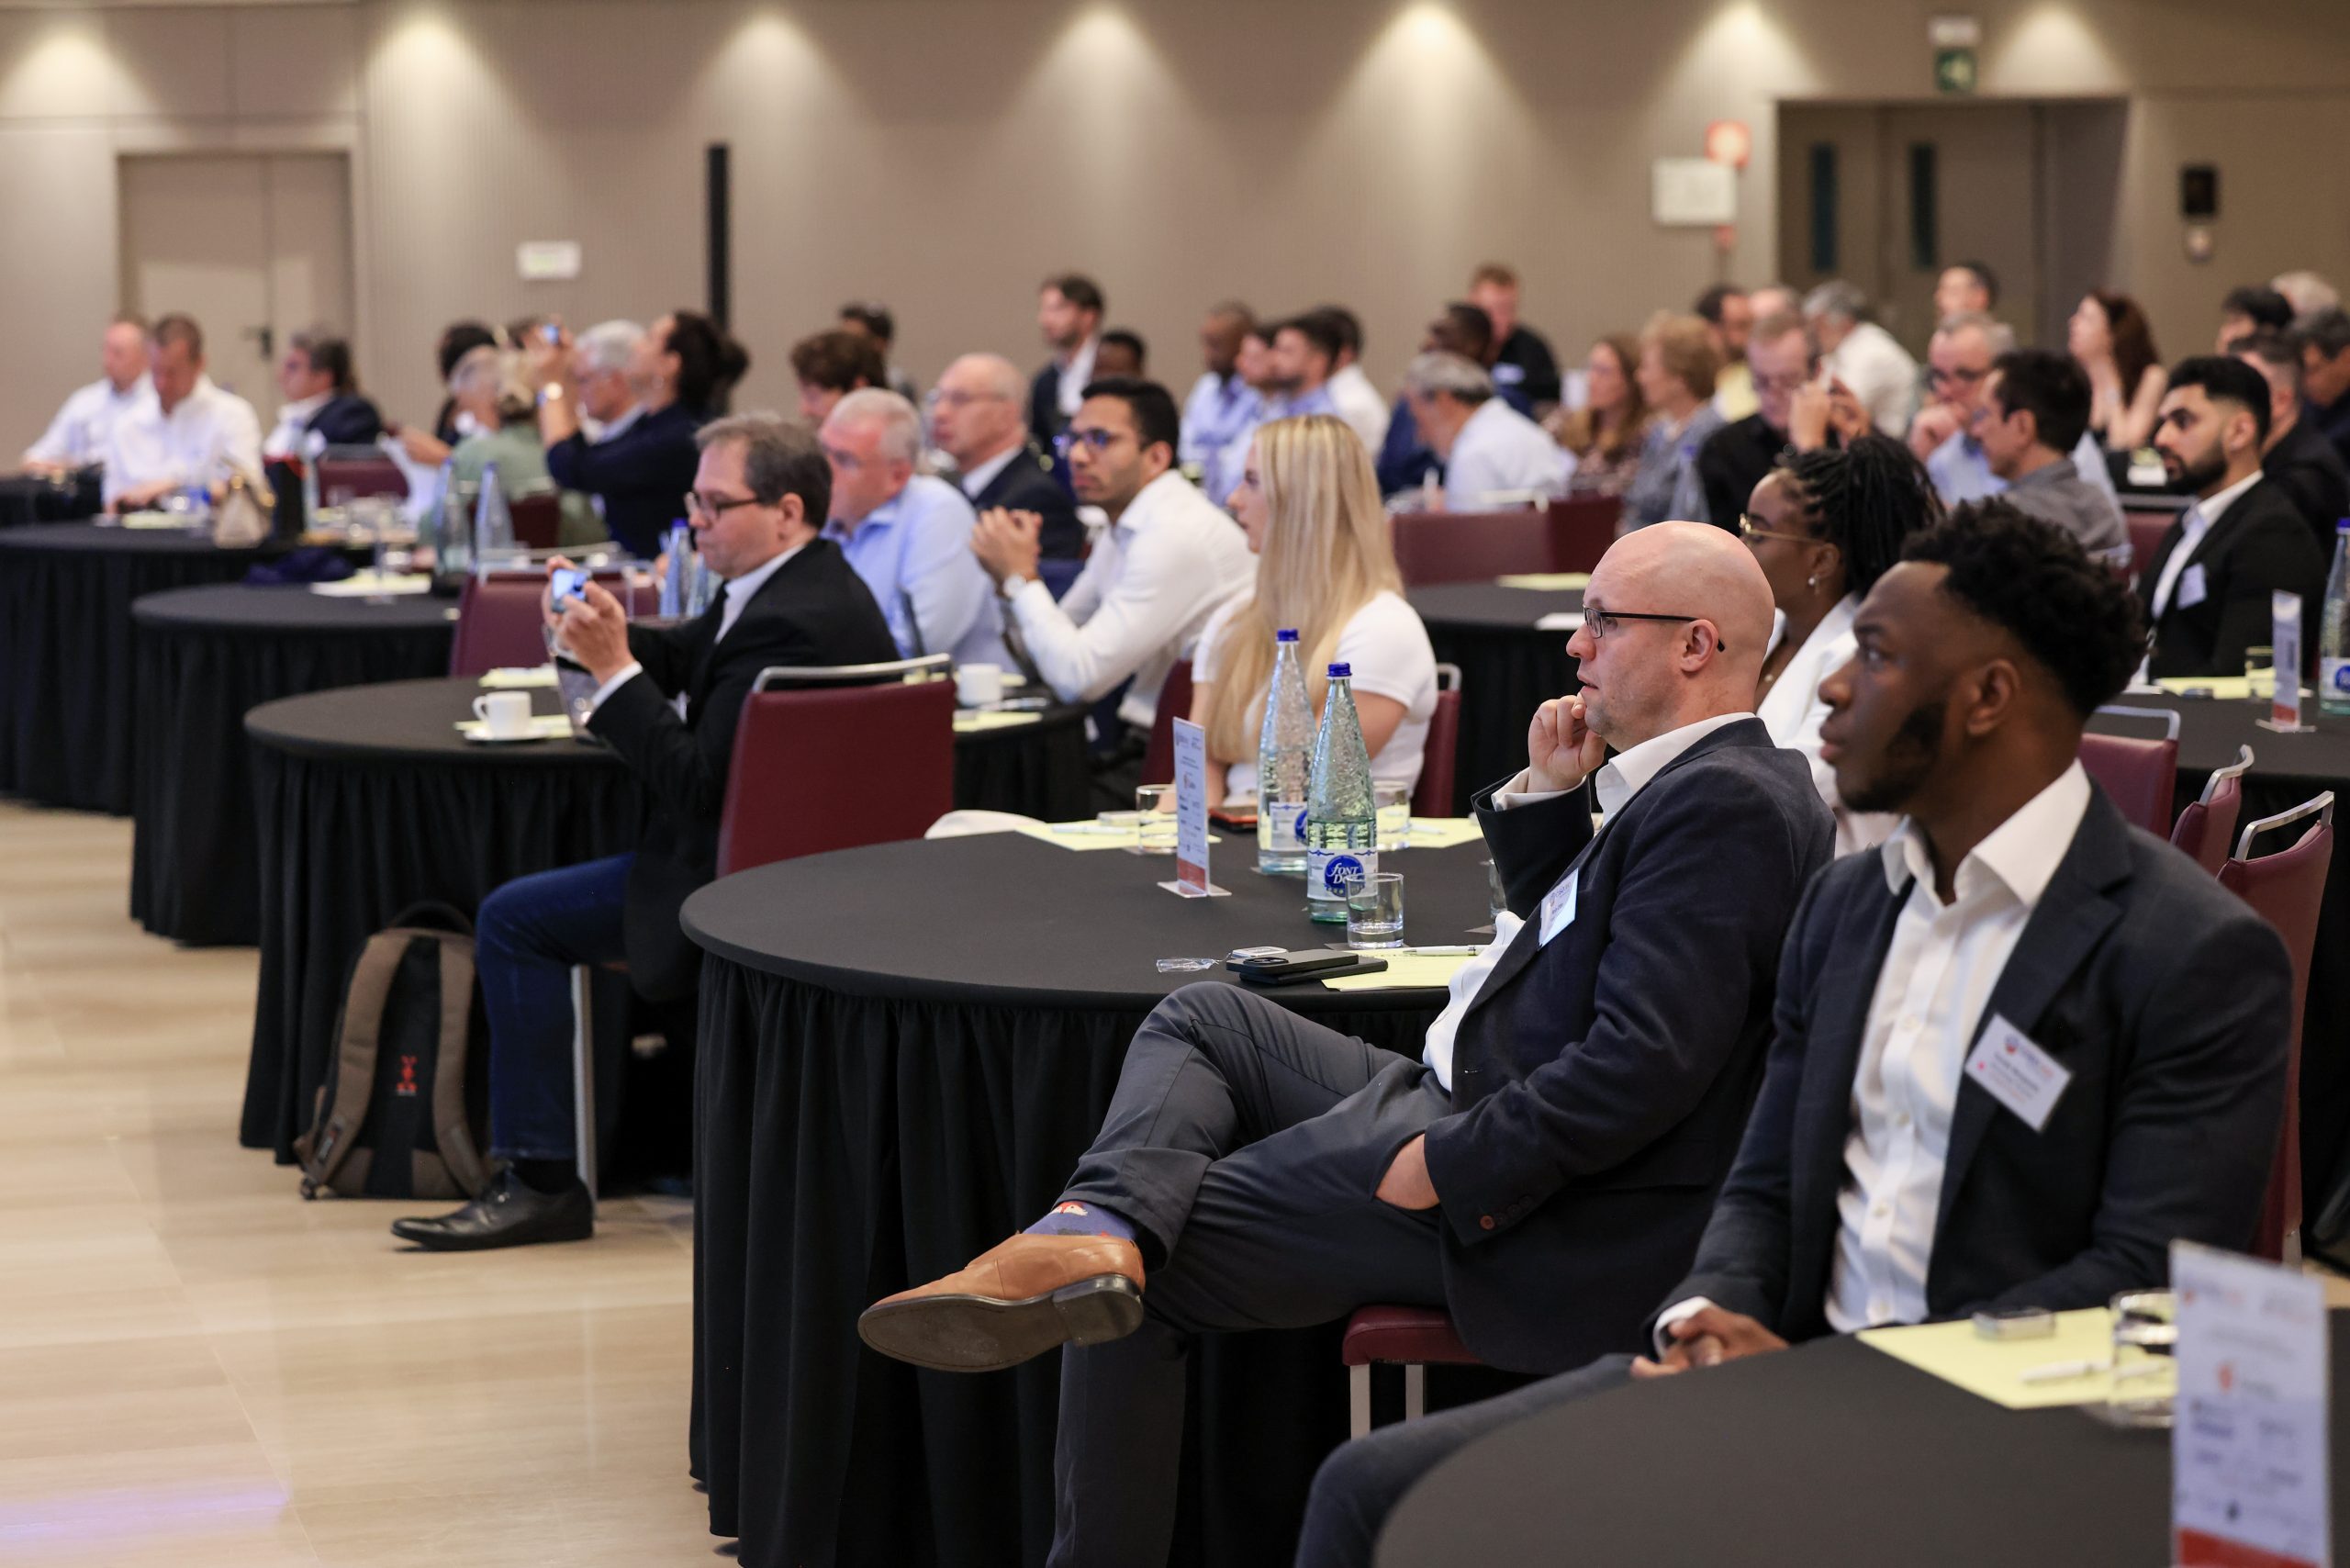
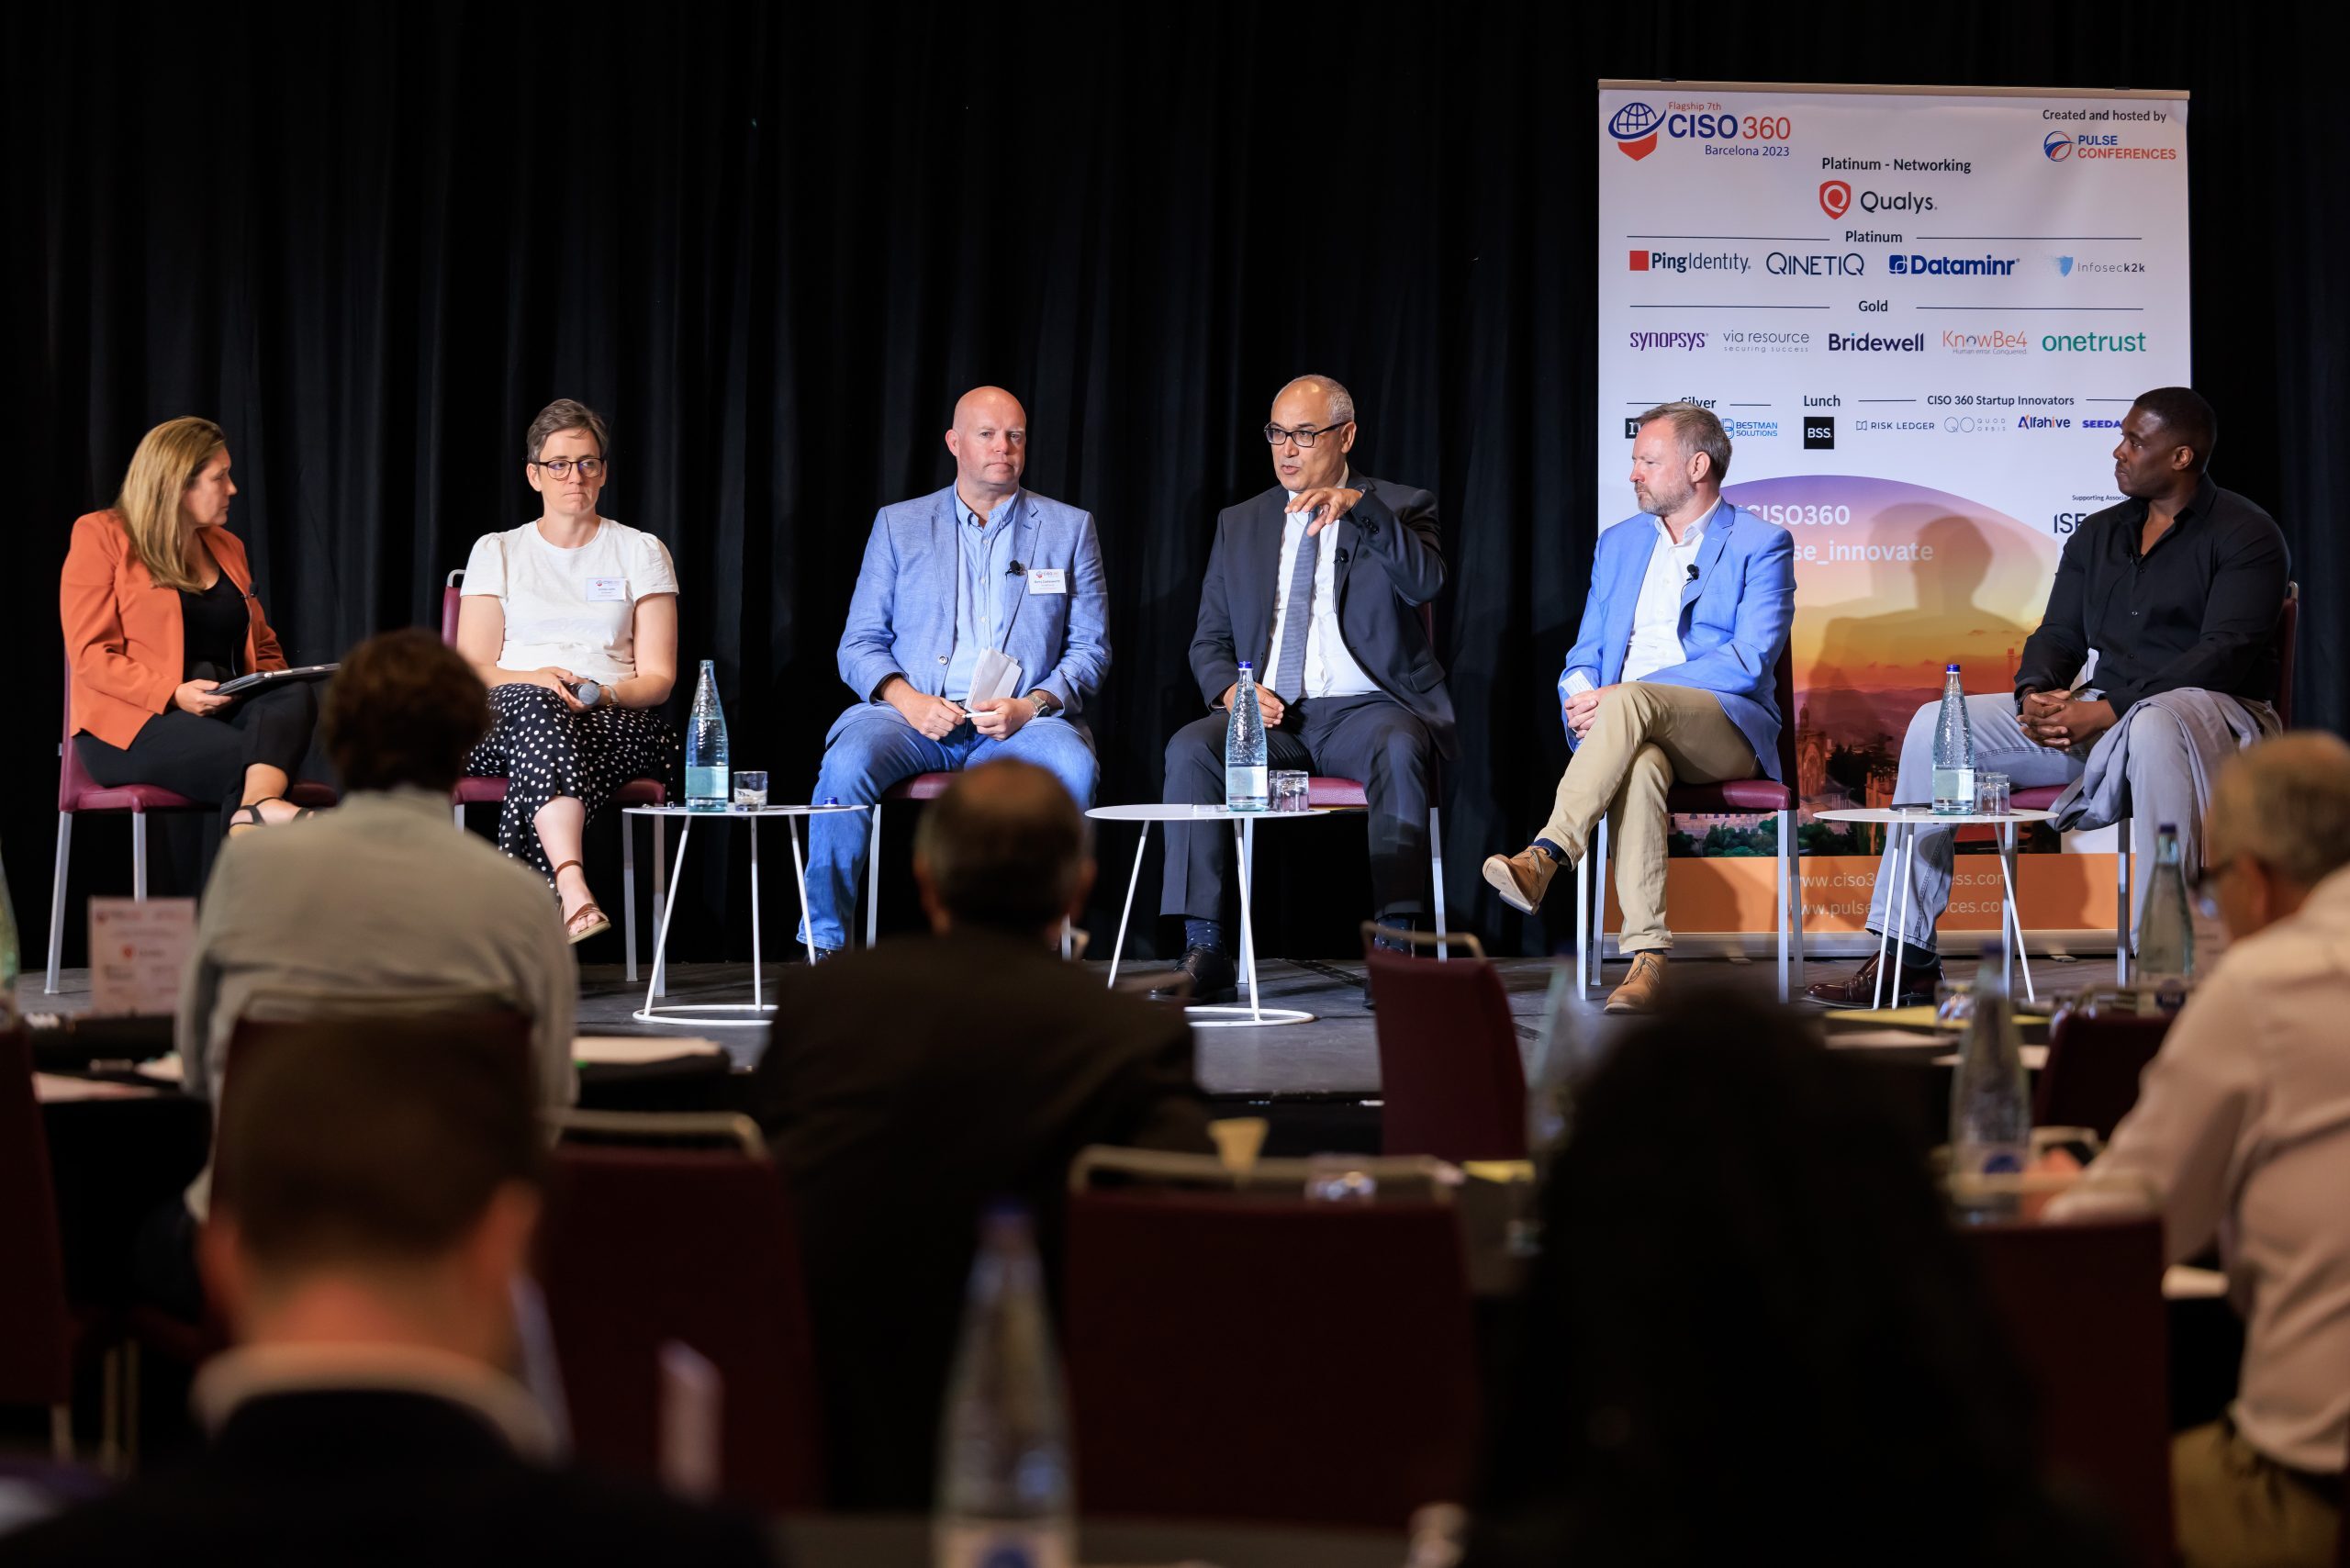
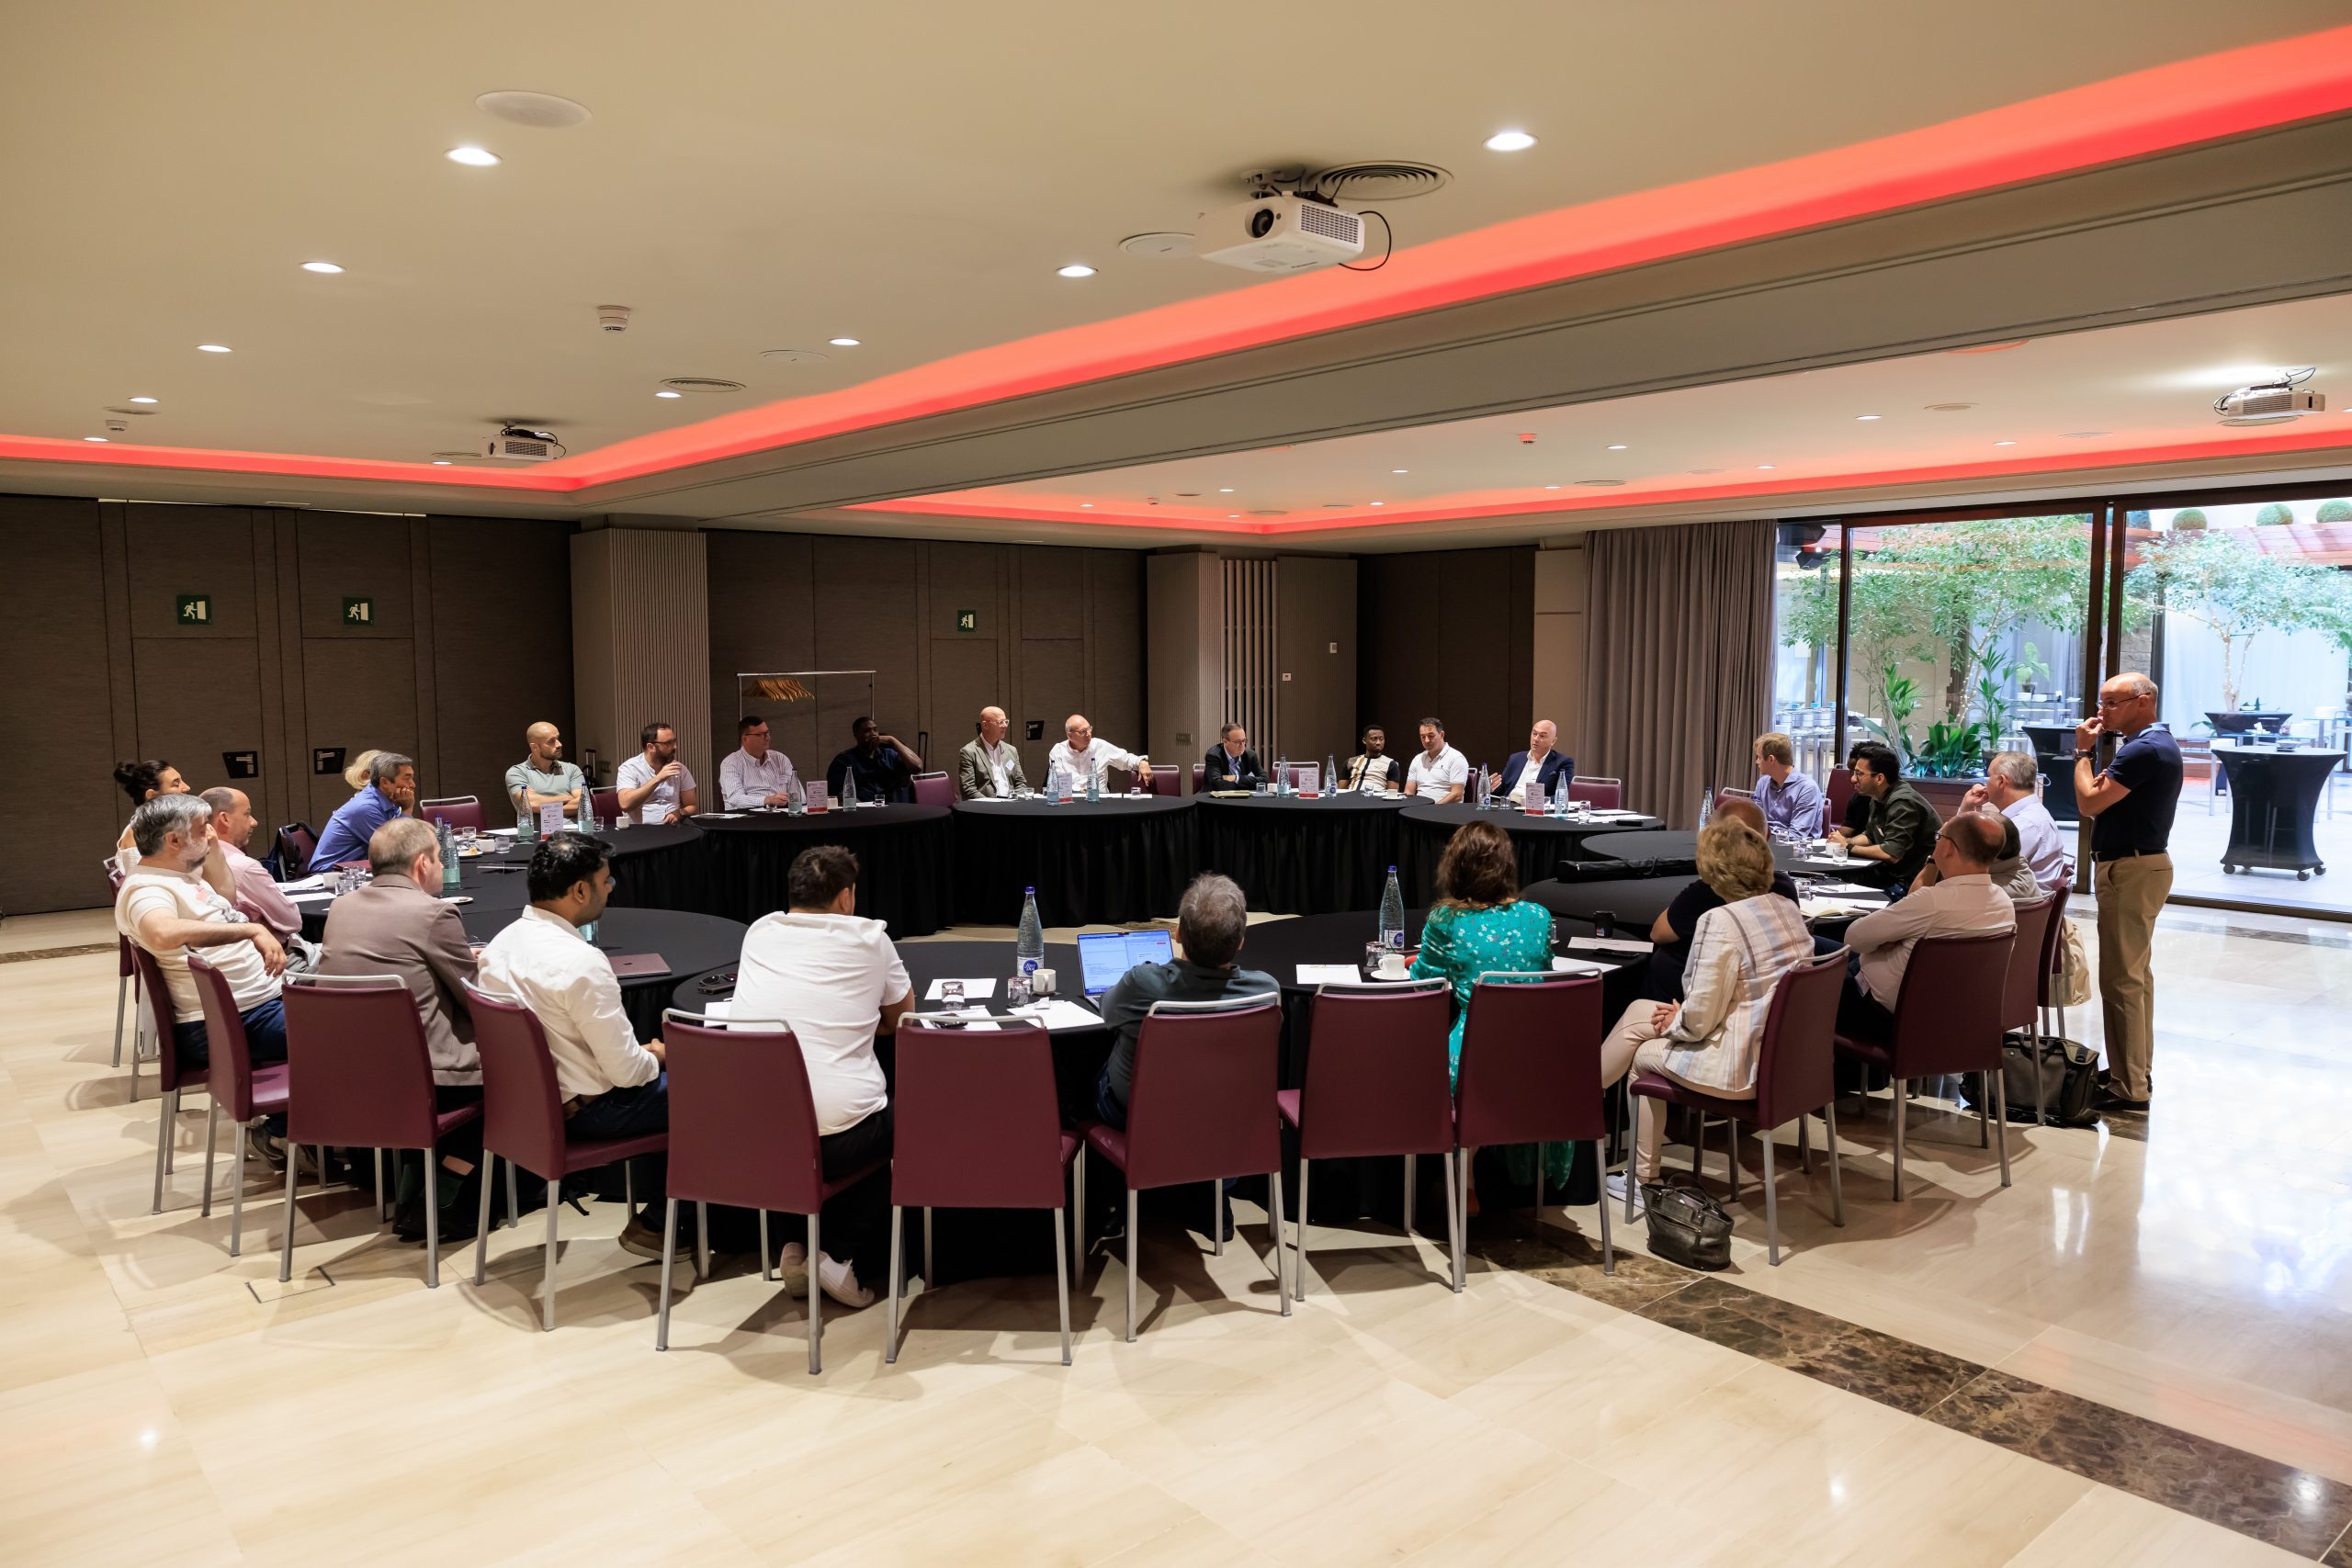
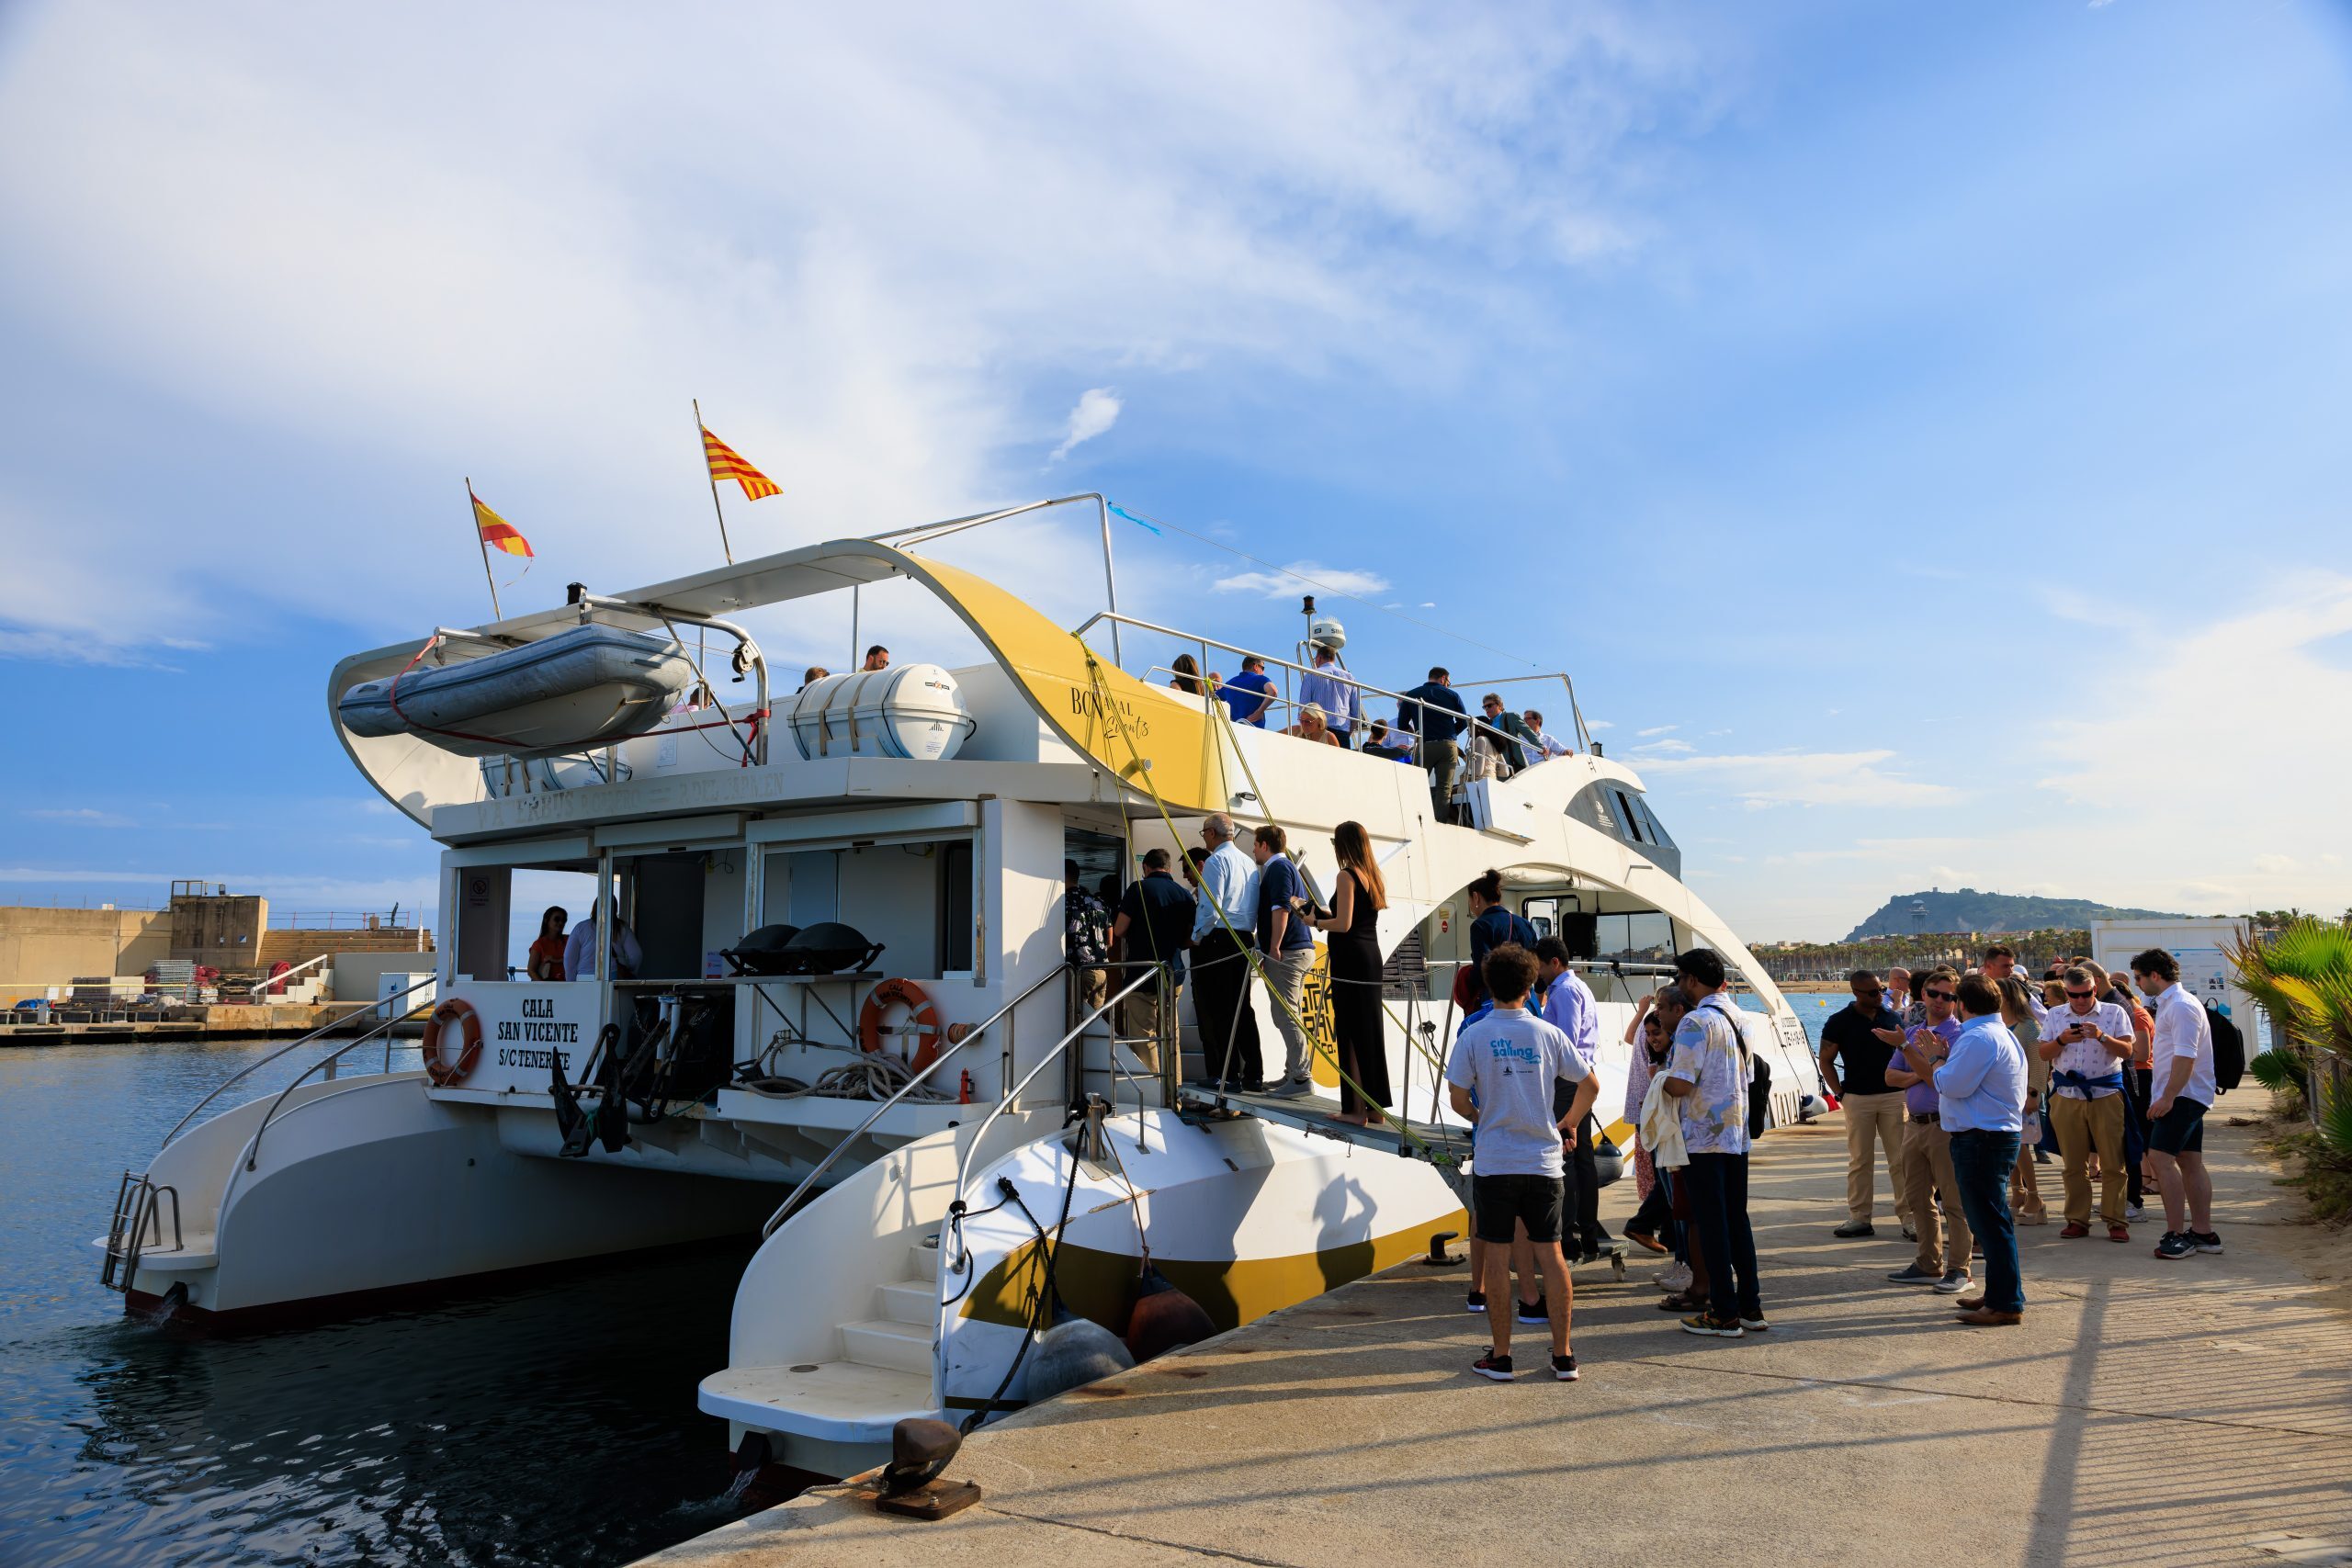
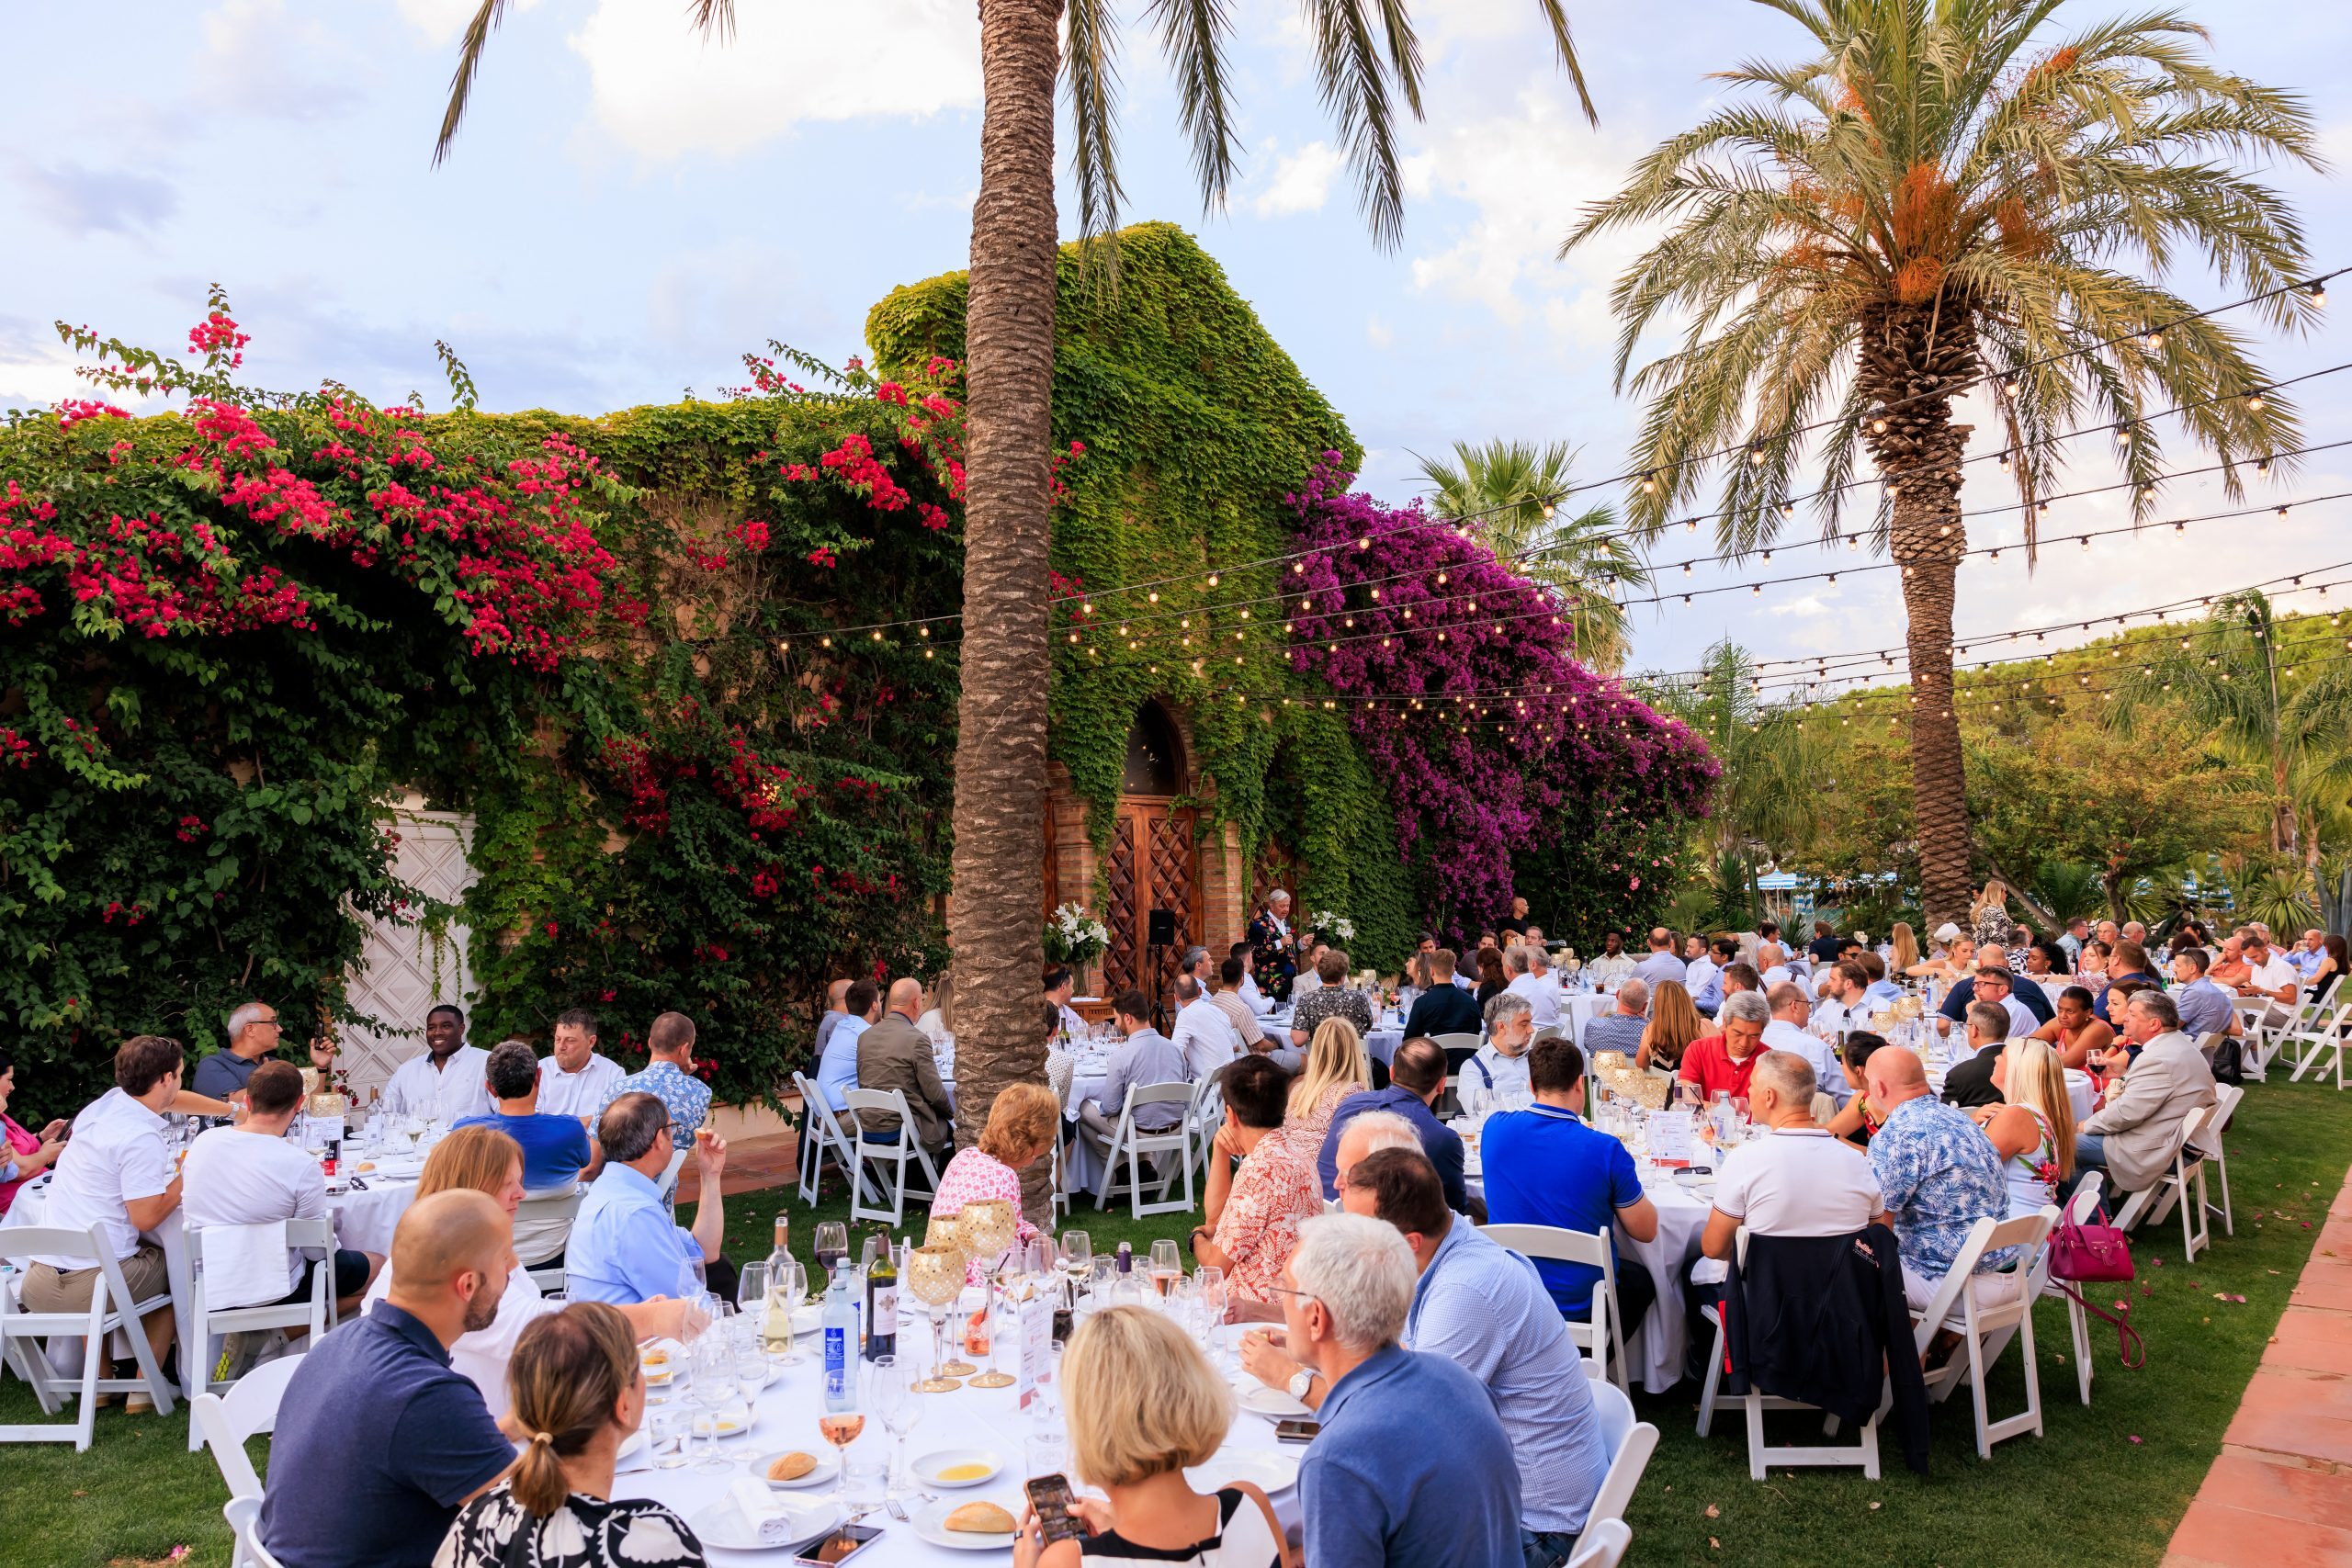
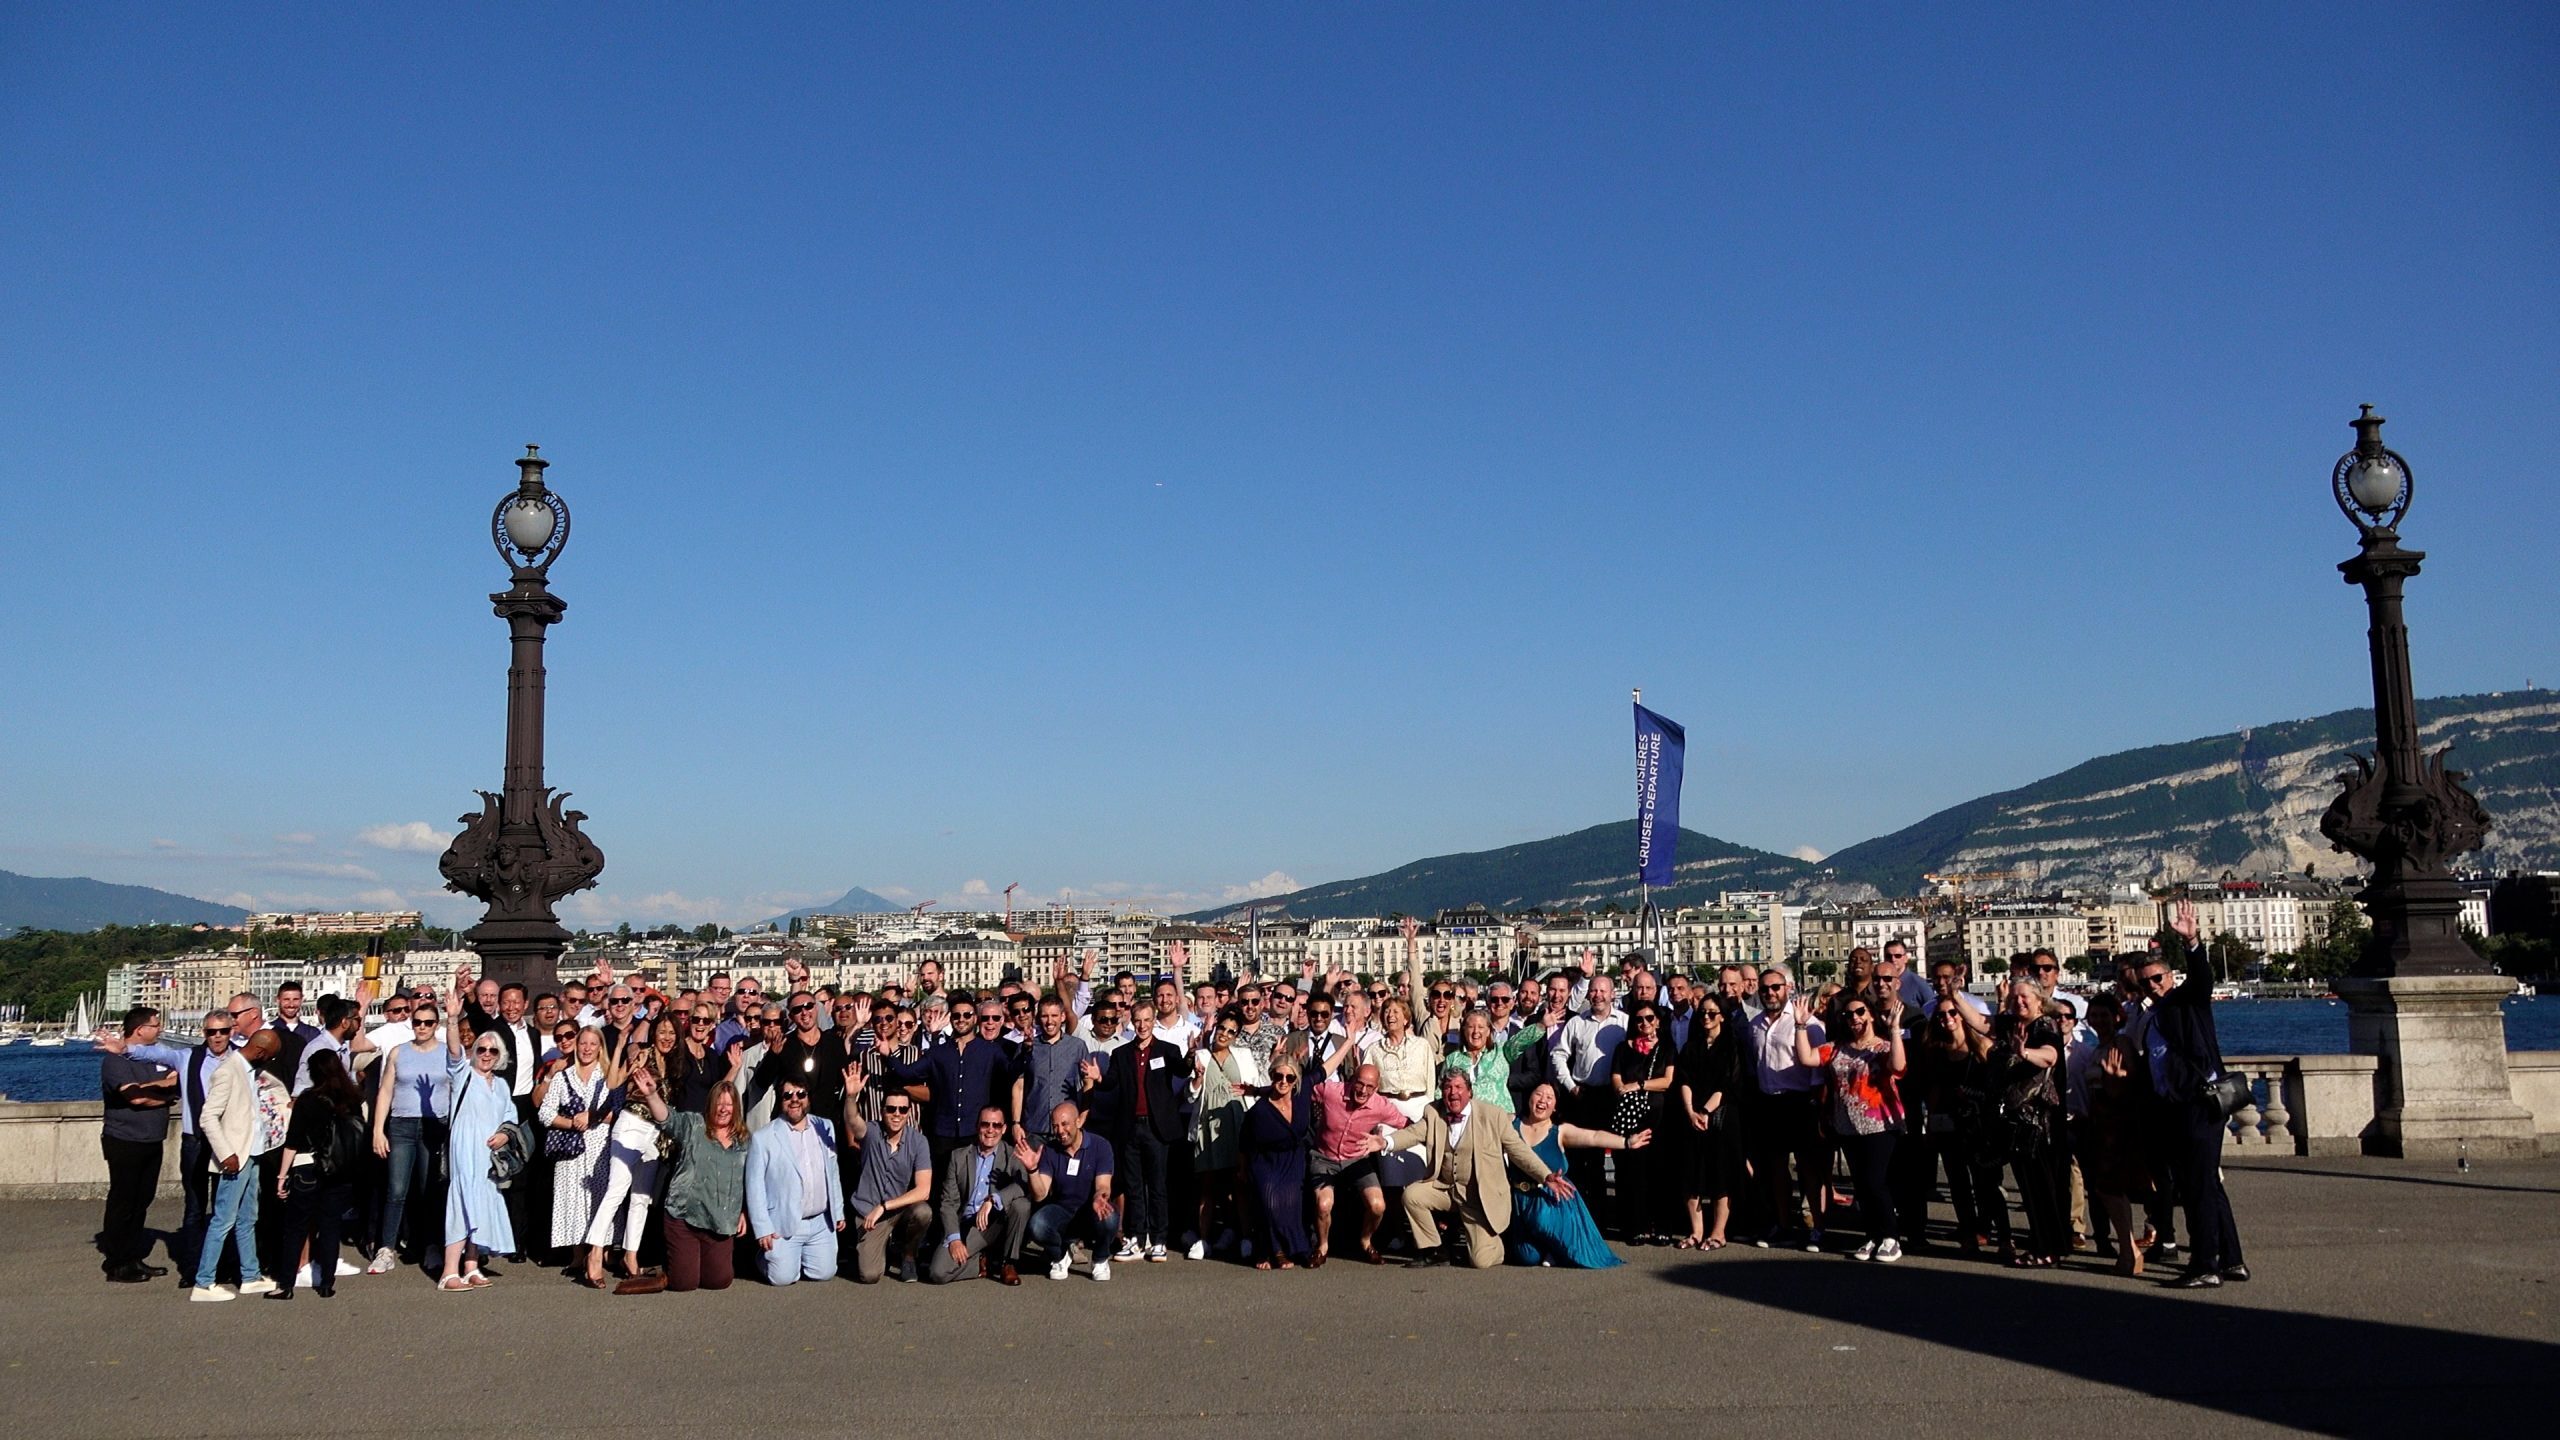
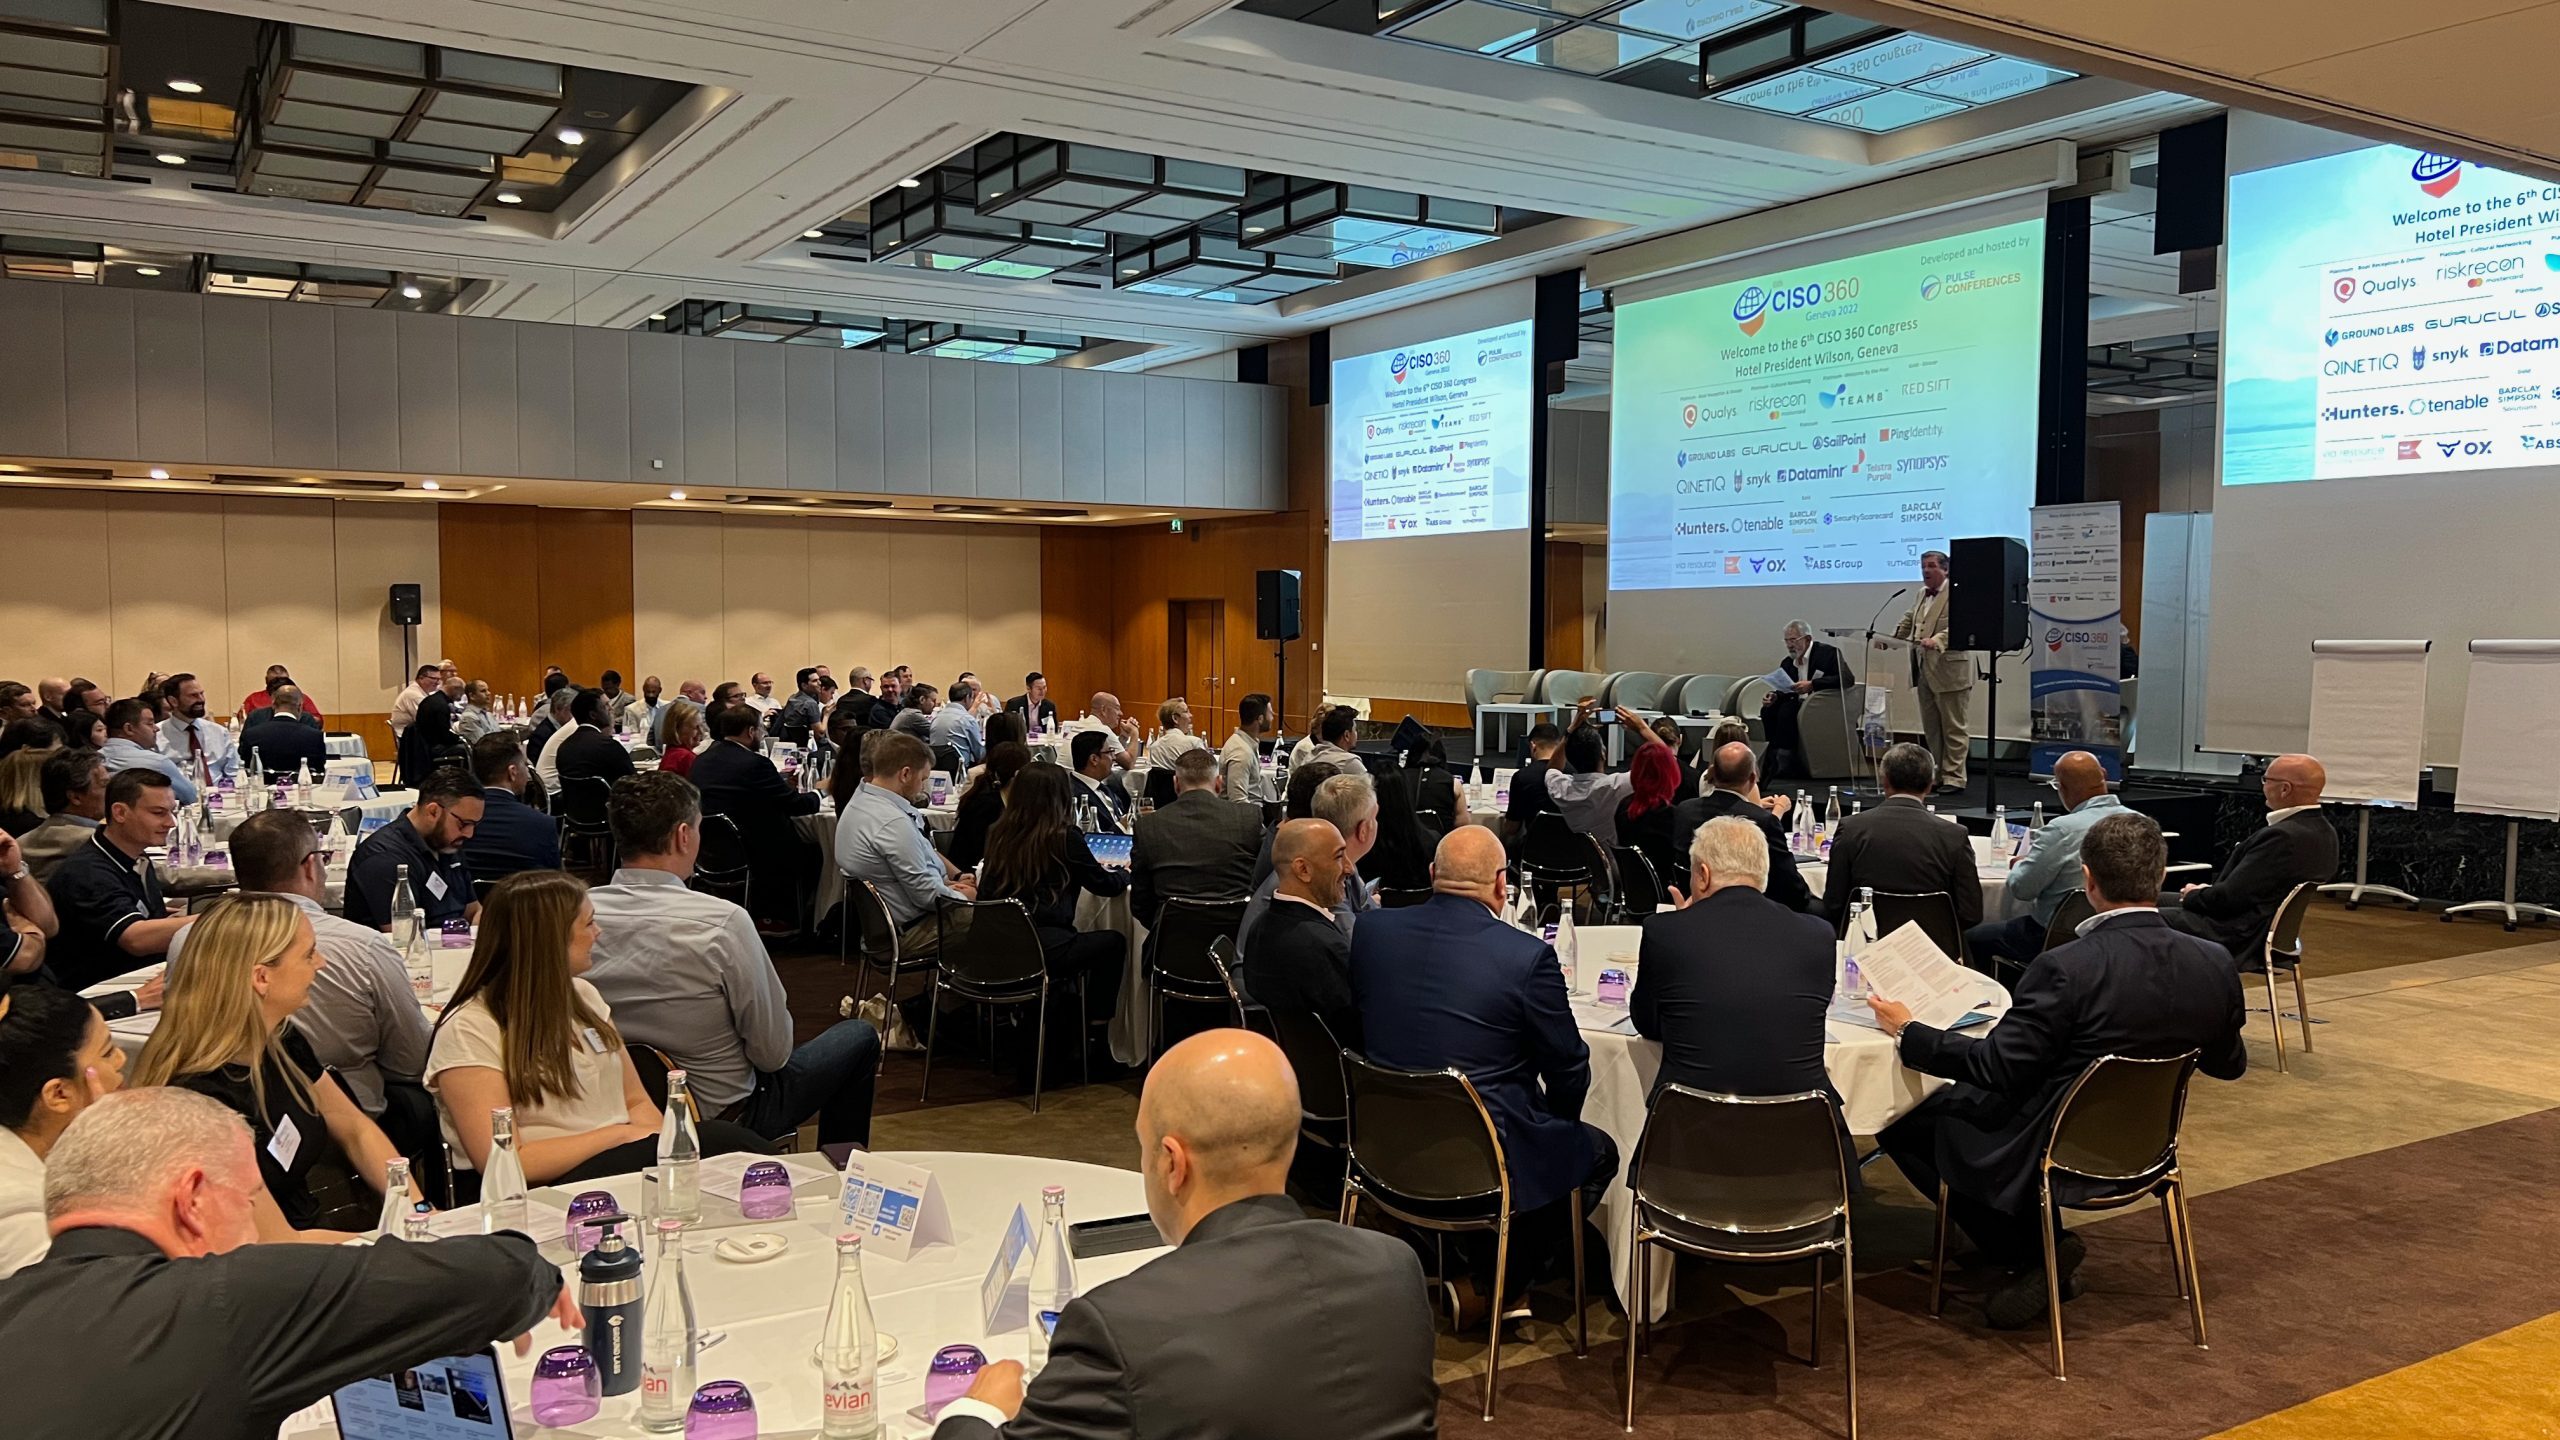
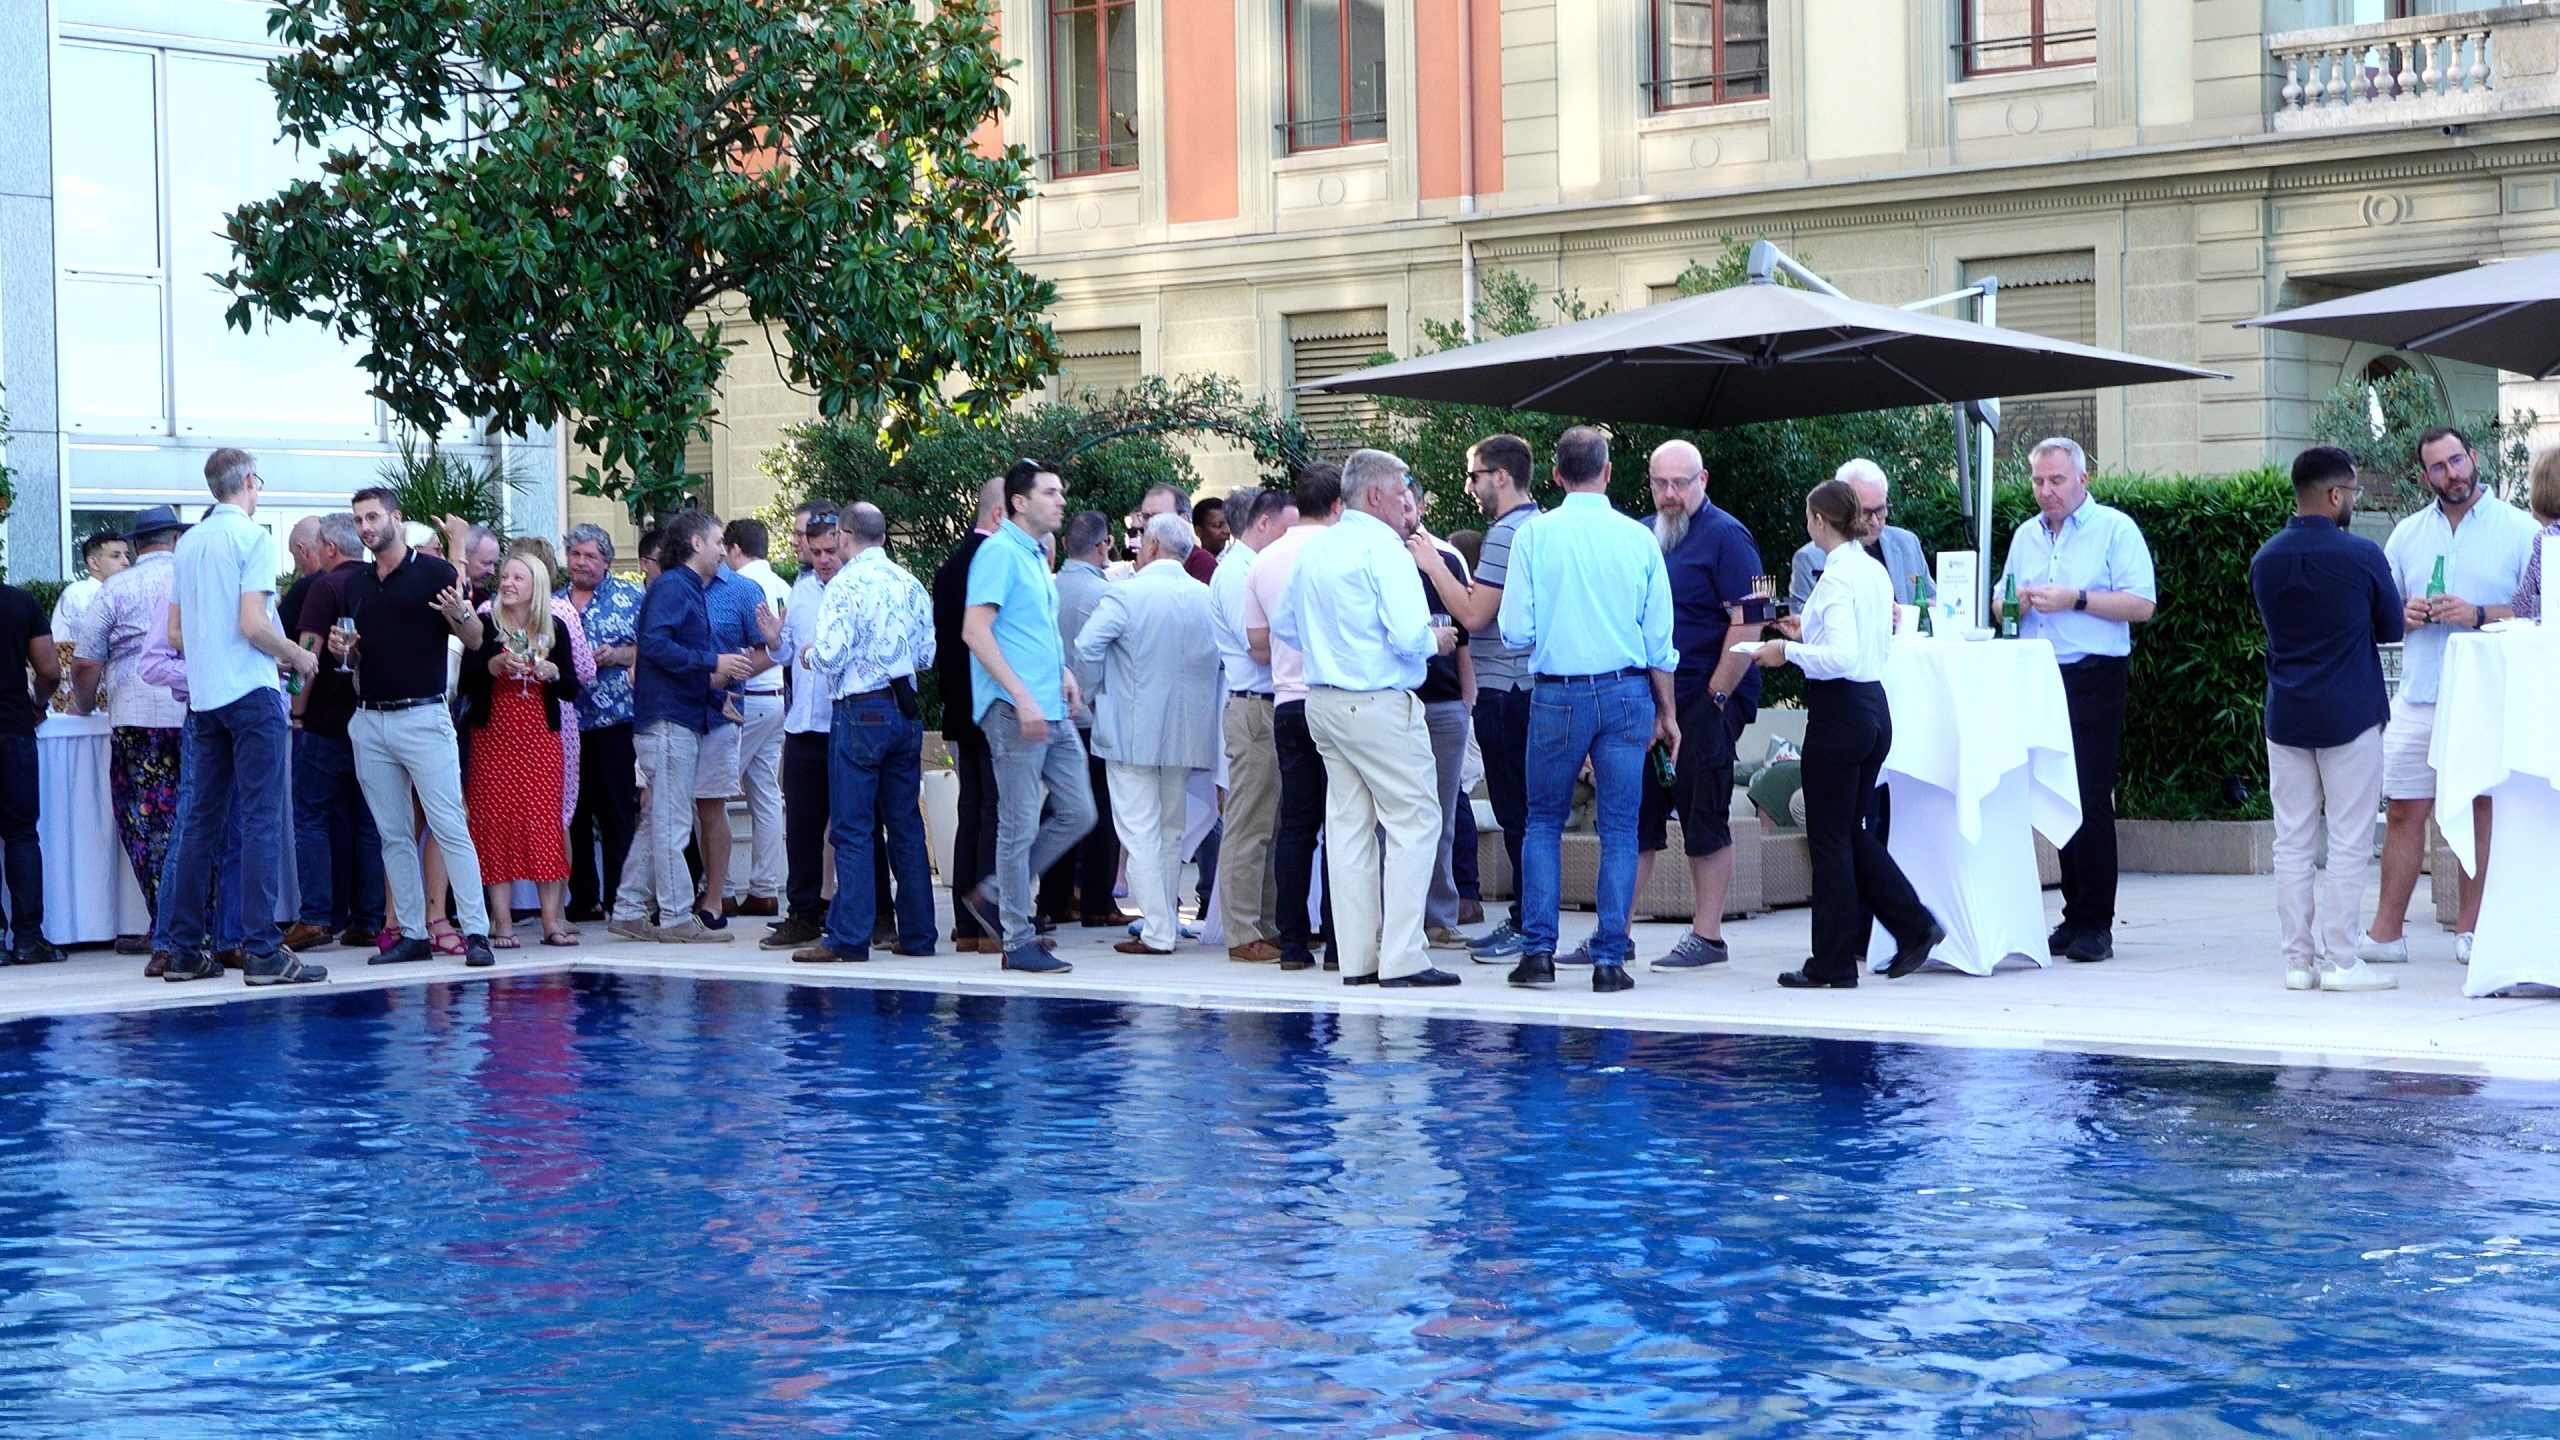
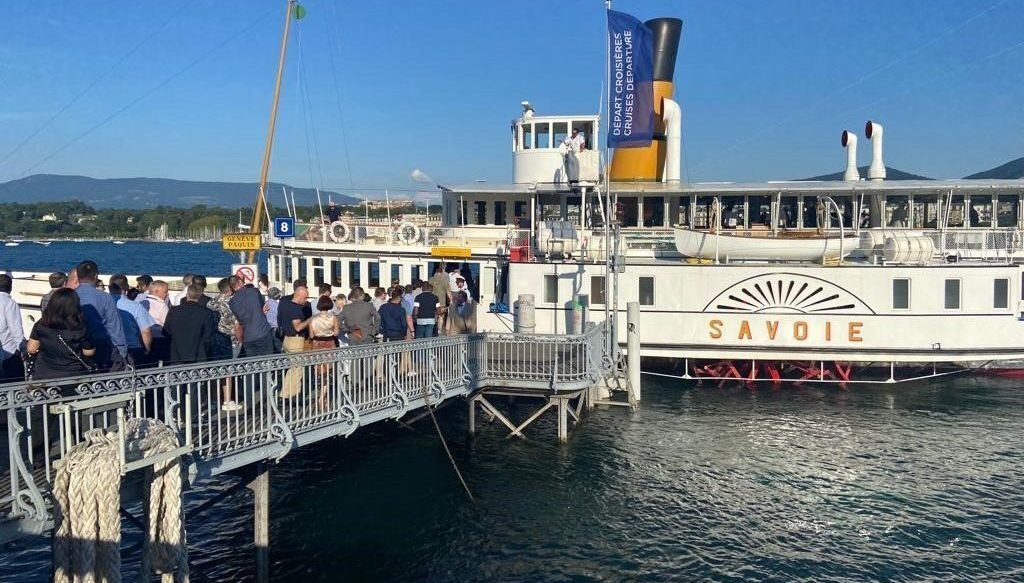
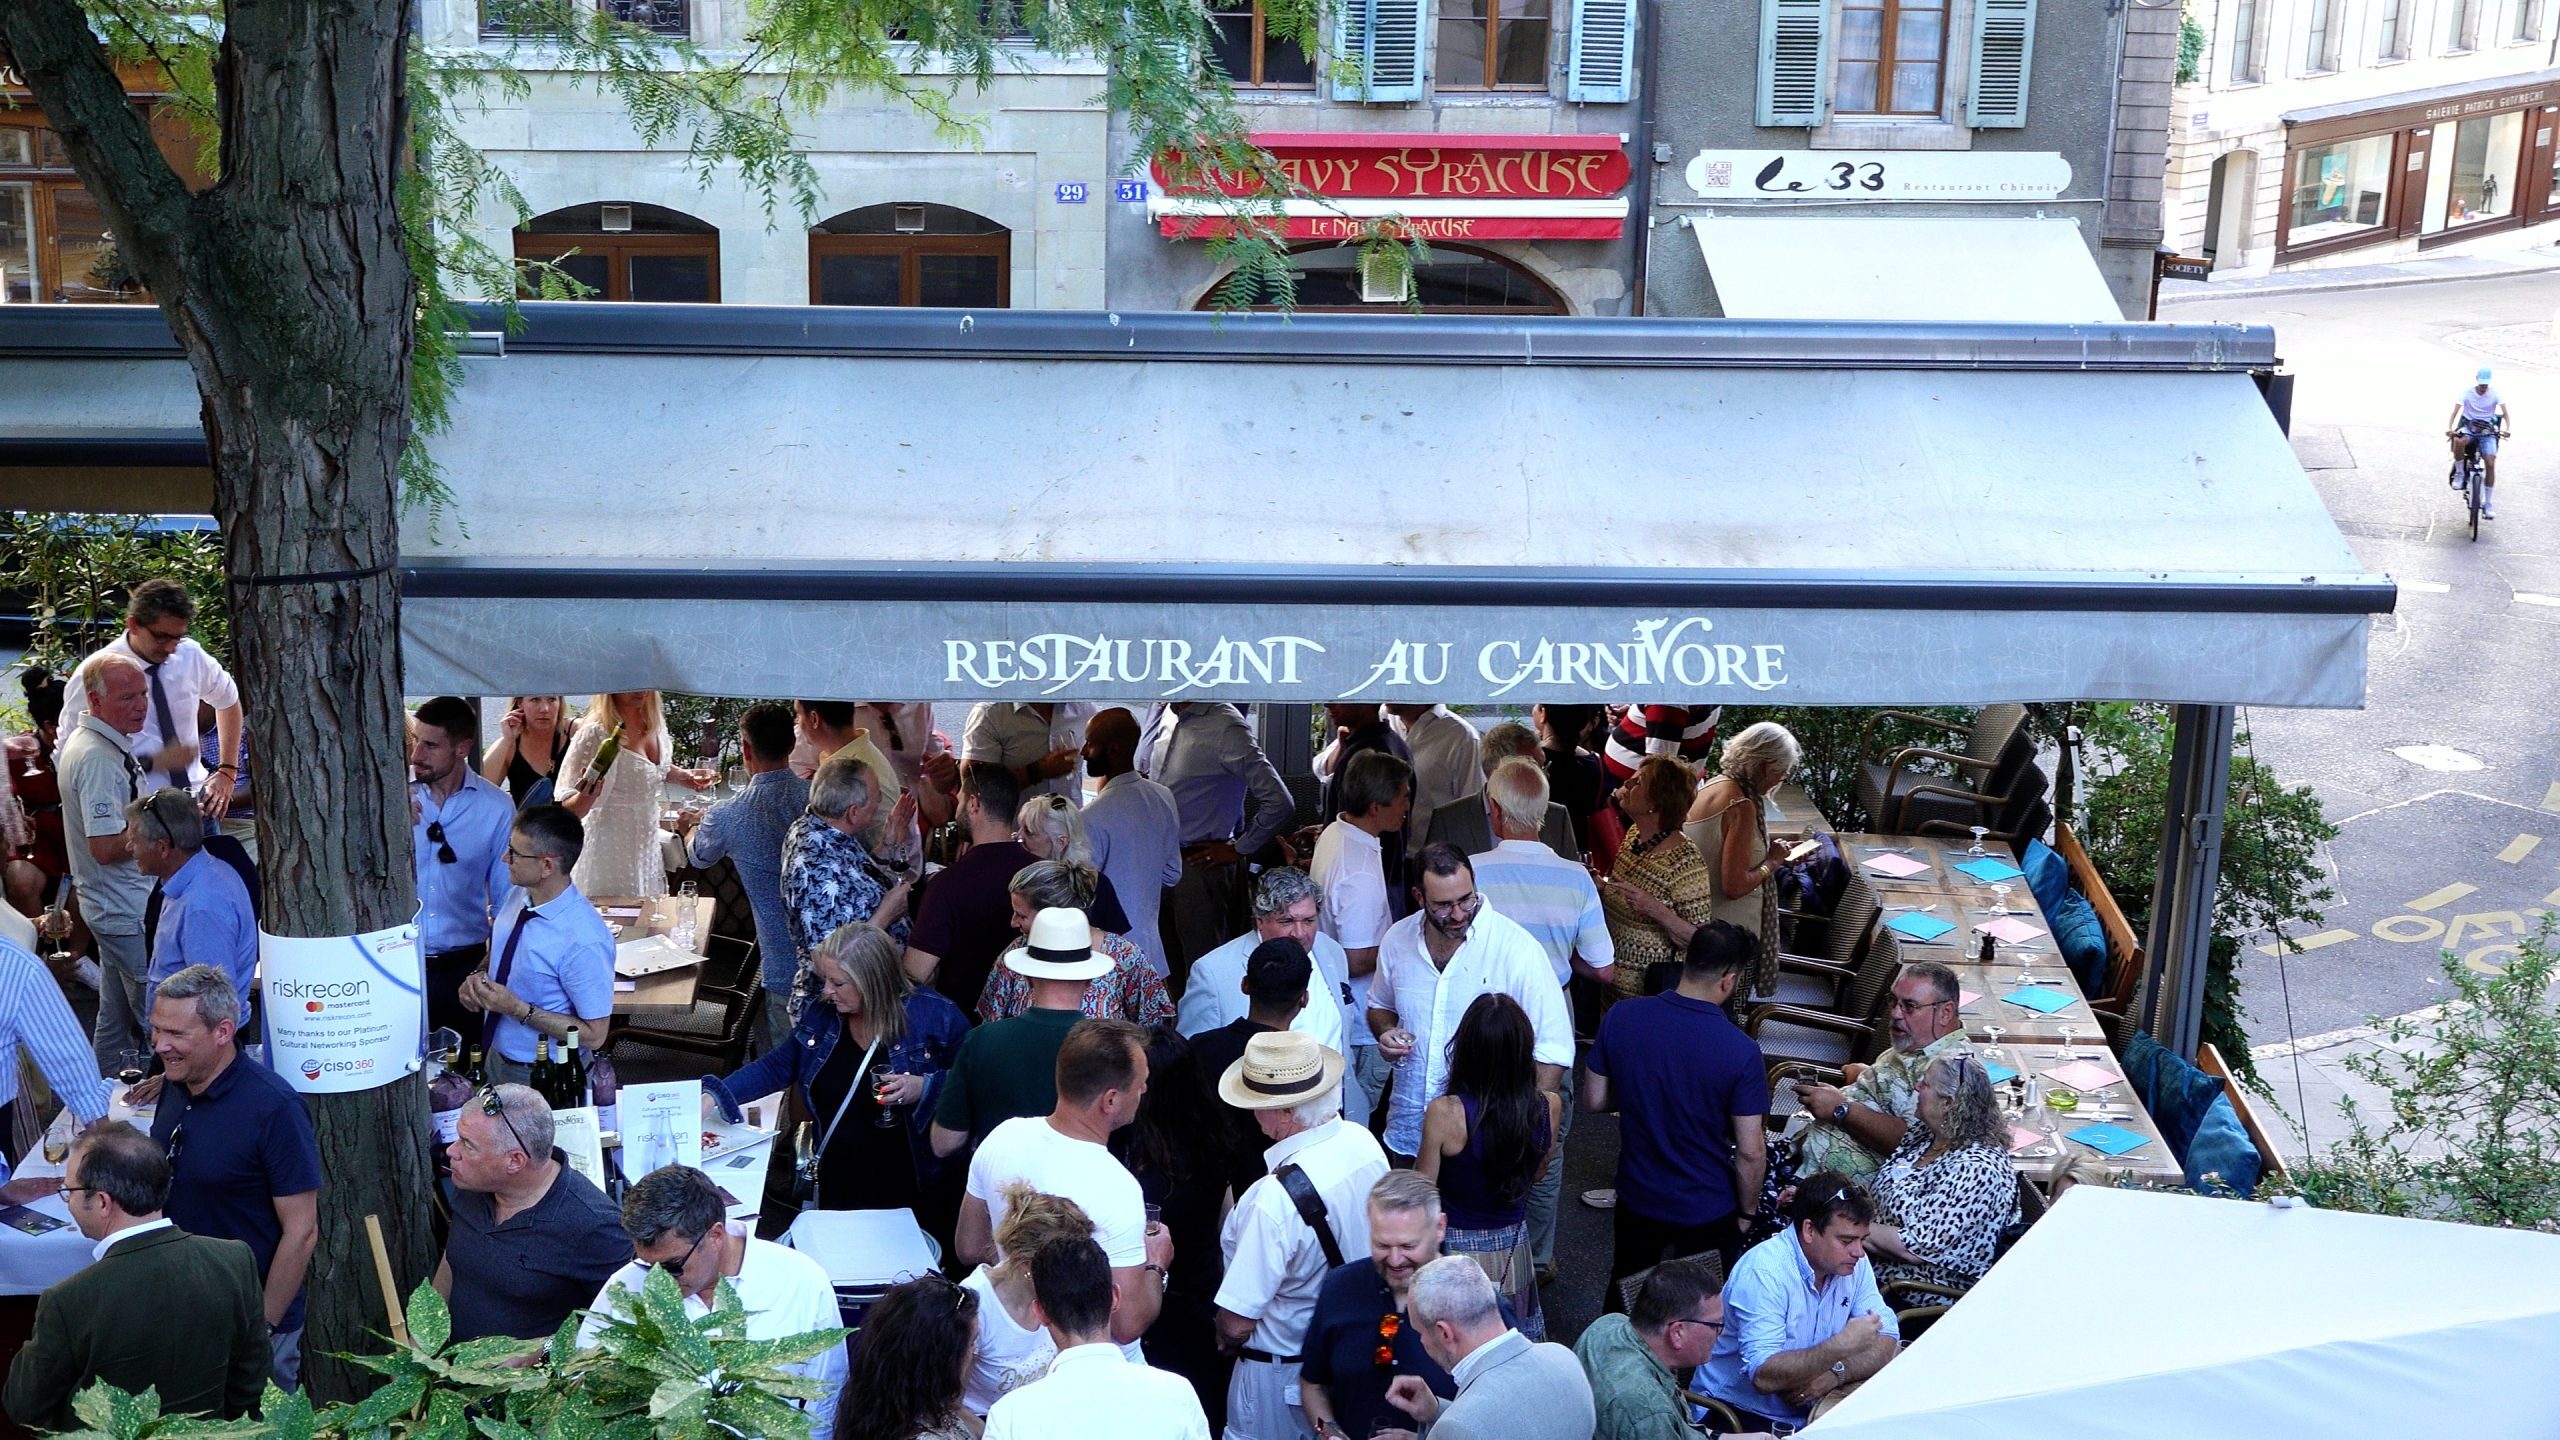
Created and hosted by Pulse Conferences, the 8th CISO 360 Global Congress brought together CISOs and international cybersecurity leaders for a veritable show-stopper.  We heard what plans CISOs are making, what drives them and where their journeys are heading as we benchmark cybersecurity strategies, tactics and tools. We will challenge ideas during  case stories, journeys, fireside chats, table think tanks, and of course the infamous CISO 360 Roundtable (19 June afternoon opener!). We made professional friends during the many evening networking receptions, dinners, tour by boat and cultural experiences that were an integral part of the CISO 360 Congress experience!

Key themes 2024 included:

* AI, Quantum, Crypto 360: Pace and preparations
* Collaboration 360: How can we work better together
* Evolution 360: CISO purpose, mission and scaleup
* Resilience 360: Holistic security, intelligence, threat landscape and mitigations

Read more about the 2024 International Speaker Panel, an impressive list that included the BBC’s Security Correspondent, Frank Gardner OBE. CISOs and subject matter specialists compared and shared how they are leading teams and driving their businesses forward, and visions for the future. Their journeys, predictions and stories will span AI, Quantum Computing, cryptography, OT/ IoT, cloud, cyber geopolitics, supply chain, detection, response and recovery, human security, culture, privacy, robotics. 

  • Be Inspired – Connect, innovate and leave reinvigorated for positive action. Sit with peers who you know are largely facing a similar set of risks and opportunities
  • Build Trusted Contacts in the International Community – Benchmark in a trusted environment with fellow CISOs, senior practitioners and business, risk, technology luminaries
  • Stay Future Facing – Learn from business executives, risk managers and technology luminaries outside the security ‘echo chamber’
  • Be Part of Collaborative Projects – Engage in meaningful interactions with CISOs, innovators, investors and luminaries

Frank Gardner OBE
Security Correspondent
BBC
UK

Jelena Matone
CISO
European Investment Bank
Luxembourg

Nicola Sotira 
Head of CERT
Poste Italiane
Italy

Sybil Kleinmichel    
Managing Expert Cyber Security DACH
Hays AG   
Germany

Carlos Gonçalves
Cyber Threat Intelligence Leader
Banco do Brasil   
Brazil

Derek Cheng
CISO   
Deliveroo         
UK

Lorna Trayan
CISO Advisor 
Gartner              
UAE

Jorge Fernandes       
CISO   
Comissao do Mercado de Valores Mobiliarios
Portugal

Colette Hanley
CISO
Checkout.com             
UK

George Eapen
Group CIO      
Petrofac
UAE

Patrick Kane   
Senior Security Director        
Atlas Air            
United States

Dr. Leila Taghizadeh
CISO IberoLatAm
Allianz
Germany

Michael Colao         
Chief Underwriter – Cyber Risks   
AXA XL       
UK

Michael Beaupre            
Head of Cyber Security           
Hays AG            
Germany

Sandip Wadje
MD, Global Hd Emerging Technology Risks
BNP Paribas            
UK / France

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to the Pulse team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
Ibraheem Khan, VP Information Security EMEA, at a financial services firm

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Dr. Alex Jaimes, Chief Scientist and SVP of AI, Dataminr

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
Gary Penolver, CTO, Quod Orbis

Many Thanks Last Years' 2024 Sponsors

Platinum and Dinner

Platinum and Catamaran Supper

Platinum and Welcome Reception

Platinum

Gold

Strategic Sponsor

CISO 360 Roundtable Sponsor

Silver

Lunch

Networking - Cave Culture

CISO 360 Start Up Innovators

Supporting Organisations

Programme – 8th CISO 360 Congress 2024

The 2024 programme is currently being developed. You can always see the latest Agenda on the Downloads tab.

If you would be interested in getting involved as a Speaker, please let us know. We would also welcome your input on companies, topics or specific persons you would like to see included on the agenda this year. We welcome your input into shaping the agenda sara.hook@pulseconferences.com.

Download Flyer

Agenda at a Glance

Evening social events are included in the CISO 360 experience. All participants are invited and encouraged to join the dinners, cultural activities, and receptions!

WEDNESDAY 19 JUNE – CISO 360 Roundtable

13:00-14:00 Arrivals and Lunch

14:00-17:00 CISO 360 Roundtable Discussions

17:00-19:15 Welcome Reception – Terrace, Hôtel Dieu Intercontinental Marseille – Kindly sponsored by: Bridewell

19:30-23:00 Catamaran Dinner – Kindly sponsored by: Qualys

THURSDAY 20 JUNE – CISO 360 Global Congress Day 1

08:00-17:30 Congress in Session

18:00-19:30 CISO 360 Cave Culture! Cosquer Private group tour. Available to Sponsor!

20:00-23:00 CISO 360 Corniche Dinner! Le Péron – Kindly sponsored by: Dataminr

FRIDAY 21 JUNE – CISO 360 Global Congress Day 2

09:00-16:00 Congress in Session

16:00-16:30 Afternoon Tea & Sponsors’ Prize Draw & Congress Close


Speaking By Invitation – 7th CISO 360 Congress, Barcelona 2023

Our programmes are carefully researched and curated. They are organic to ensure that we can be agile enough to accommodate even the very latest emerging topics on the day of the event itself!

We do not operate a ‘Pay to Speak’ Policy. Our sessions are pre-dominantly led by CISOs and other subject matter specialists that CISOs have informed us they would like to learn from. The format and timing of the sessions that are led by our official event Sponsors is determined by the Speaker who is put forward by the Sponsor, what they will bring to the table in terms of openly sharing and learning and their flexibility on he session formats – for example we favour interactive sessions and case studies that engage the participants. We limit keynotes by PowerPoint.

International Speaker Panel – 7th CISO 360 Congress, Barcelona 2023

Chaired by

Marcus Alldrick, CISO Luminary

Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university.

Progressing from programming into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard.
After seven years in that role he moved financial institutions and became Head of Information Security for Abbey National plc, now Santander UK.
After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there.

Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend.
As well as being a proud member of the Pulse Conferences family, Marcus now actively volunteers for the heritage Swanage Railway where he undertakes various customer facing roles, Julia’s House, the Dorset and Wiltshire children’s hospice and care provider, a local school as a governor and is a guest lecturer at the University of Portsmouth.

International Speaker Panel 2023

Meet the Speakers at 8th CISO 360 Global Congress – Marseille 2024

Congress Chair
Marcus Alldrick, CISO Luminary

Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Progressing from programming into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved financial institutions and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now actively volunteers for the heritage Swanage Railway where he undertakes various customer facing roles, Julia’s House, the Dorset and Wiltshire children’s hospice and care provider, a local school as a governor and is a guest lecturer at the University of Portsmouth.

Roundtable Chair

Dr. Robert Coles, Head of OT Security Strategy, DSSmith plc

Robert has over 35 years of audit, risk and cybersecurity experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG. Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School. Robert also holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, and Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University of Brighton.

Opening Keynote: Global Security Landscape Updates

Frank Gardner OBE
BBC’s Security Correspondent and Author

Frank spent nine years as an investment banker in New York, London and Bahrain before switching to journalism and joining the BBC in 1995. Frank has reported extensively on the global ˜War on Terror’ in Guantanamo Bay, Yemen, Afghanistan, Iraq and elsewhere in the Middle East. In 2004 Frank survived being shot six times at close range by Al-Qaeda terrorists in a Riyadh suburb in Saudia Arabia. He went on to write the best-selling book Blood and Sand, the poignant story of what can happen to your belief system when the culture you have embraced ends up trying to kill you. Frank has gone onto write three best-selling spy thrillers Crisis, Ultimatum and Outbreak. He was awarded an OBE in 2005 for services to journalism. In 2018 he was awarded the University of Southern California’s Tommy Trojan Trophy for distinguished speaking. As a career broadcaster and a witty and gifted communicator, Frank shares his passion for the Middle East, travel and adventure. He draws on a unique perspective and understanding of both domestic and international security.

Meet the 2024 International Speaker Panel (partial list by alphabetical order)

Speaking at 8th CISO 360 Global Congress – Marseille 2024

Our programmes are carefully researched and curated by professionally trained conference producers. They are organic by nature to ensure that we can be agile on the day. We ensure an optimal mix of keynotes, case studies, fireside chats, table think tanks and group roundtables sessions that are pre-dominantly led by CISOs and all our Speakers are subject matter specialists. We don’t do a ‘Call for Speakers’ but we do very much welcome enquiries and recommendations!

Contact: teampulseteampulse@pulseconferences.com.

Alan Jenkins

Alan Jenkins

Independent Trusted Advisor, Interim CISO, Principal Consultant, NED & Mentor (UK)

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

Dr. Alejandro (Alex) Jaimes

Dr. Alejandro (Alex) Jaimes

Chief Scientist & SVP of Artificial Intelligence, Dataminr (U.S.)

Scientist (Deep Learning, Machine Learning, Computer Vision, Artificial Intelligence), speaker, engineering executive. 15+ years of intl. experience in research (Columbia U., KAIST) and product impact at scale (DigitalOcean, Yahoo, Telefónica, IDIAP-EPFL, Fuji Xerox, IBM, Siemens, and AT&T Bell Labs) in the USA, Japan, Chile, Switzerland, Spain, and South Korea. 100+ patents and publications. Columbia University Ph.D..

I leverage large-scale data using a Human-Centered approach to design, build, and deliver business value in novel algorithms for products used by millions of people. Core competencies:

  • Building and managing internationally distributed teams of scientists and engineers.
  • Strategic, technical, and operational leadership to maximize business impact of research.
  • Creating synergies as a catalyst between engineers, designers, product managers, and executives.
  • Communicating across diverse communities (70+ international invited talks).
  • Designing and leading implementation of algorithms, advanced metrics, and A/B tests.
  • Taking on projects that involve multiple stakeholders, delivering solutions that matter at the individual level, work at scale, and make business sense.

Diverse technical skills at the intersection of AI and User Experience across various industries (Cloud, Healthcare, News/Media):

  • Computer Vision, Data Mining & Machine Learning
  • Content Recommendation & Social Discovery
  • Behavioral insights & Product strategy

I like to travel, read, and explore different cultures. I have lived in 8 cities in 4 continents [Bogota, New York, Santiago de Chile, Tokyo, Lausanne, Madrid, Barcelona, Daejeon] and traveled in 80+ countries [Flickr].

Past EU projects: Social Sensor, ARCOMEM, and the CENIT Social Media.

Andrea Litherland

Andrea Litherland

Cyber Threat Intelligence Lead, Financial Services (UK)

A Cyber and Technology executive with over twenty-five years of industry experience leading and implementing successful technical programmes in demanding global financial services environments, Andrea provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and operational cyber security defence.

Andrea maintains a strong emphasis on the continuous improvement of information security controls while partnering closely with internal and peer external organisations in order to achieve enhanced collective protection across the finance sector.

Andreas Wuchner

Andreas Wuchner

NED, Investor, Former CIO and CISO, UBS, Wuchner Securities (Switzerland)

Andreas Wuchner is an experienced and recognized senior executive leader with extensive international general management experience of global diversified businesses and a proven track record. He has held positions in Switzerland, Germany, USA, Australia and the United Kingdom.

Andreas served as General Manager (CIO), Chief Information Security Officer (CISO), Head IT Security & Operations, Head IT Risk Control and Head IT Risk Management / Governance & Compliance for several large scale and international organizations including Novartis Pharmaceuticals, UBS, Deutsche Bank, Credit Suisse and Hewlett Packard. He also served on company advisory and supervisory boards helping cyber start-up organizations with his experience in Strategic planning, go-to Market activities, financing advice for seed funding and round A to C plus product/service design.

As an Angel Investor Andreas invests in Cyber Security organizations where he then participates actively in the growth and future of the organization in scope. With more than 25 years of experience and knowledge in all aspects of Information Security, IT-Security & Information Risk management, Andreas supports clients all over the world with his own 2 companies. His special focus areas are within highly regulated environments such as life science and financial services.

Barry Coatsworth

Barry Coatsworth

Director, Guide house (UK)

Barry is Director with Guide house working within Risk, Compliance and Security. He has over 30 years experience in energy, finance and public sector, and is an internationally recognized cyber security expert and advisor. He was also part of the Industry Advisory Group for the the Cyber Essential Scheme in conjunction with UK’s Department of Business, Energy and Industry Strategy; and as are research advisor to the Parliamentary Office of Science and Technology(POST) on Big data, Ethics and privacy. He has also written a number or articles and is currently working on two forthcoming books

Bev Allen

Bev Allen

Information Security Professional, Quilter (UK)

Bev Allen is an information security professional with more than 35 years’ experience in delivering operational and strategic information security, information risk management, and privacy, including the development and delivery of information security and privacy policies, standards, and security training, in a variety of culturally diverse organisations and industries.

Currently focussing on developing our 3rd party security assurance processes to be more meaningful to both parties, and determining how to do this on a more frequent basis.

Colette Hanley

Colette Hanley

Vice President, Technology Risk, Checkout.com (UK)

Colette leads technology risk, security compliance and data governance for Checkout.com, a cloud-based payments platform. Before joining Checkout.com she held leadership roles at Skype, Microsoft and Nokia. Specialising in pragmatic and creative solutions for complex and evolving compliance requirements, she is passionate about embedding security and privacy in operations, products and services from design to delivery. Her focus is comprehensive reduction of technology-related risk for the business and for the customer. Colette holds an MSc. in Information Security from Royal Holloway and is CISSP, CISM, CIPP, CDPSE.

Daniel Frost

Head of information Security, Sky Broadcast Sky (UK)

Dr. Eduardo Solana

Dr. Eduardo Solana

Senior Lecturer of Cryptography and Security, University of Geneva (Switzerland)

Dr. Eduardo Solana is Senior Lecturer of Cryptography and Security at the University of Geneva. Amongst others, Dr. Solana has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has more than twenty five years of experience in the fields of cryptography and information security both in the private sector and the academia. Dr. Solana is a deeply experienced security practitioner, technical writer and regular speaker at the most relevant conferences and symposia in the field. During his extensive career, he has provided consulting services to multinational organizations and states in security related issues.

Emma Leith

Emma Leith

Director of Consulting, Cyber Security (UK)

Emma Leith is a globally recognized cyber security leader with 17 years’ experience across c-suite leadership positions, consulting and services. As the Director of Consulting at Bridewell, a leading cyber security services company, Emma has full ownership of their consultancy capability working alongside the rest of Bridewell’s board to deliver industry-leading, expert-led consultancy. Emma has a wealth of experience in all areas of cyber security and as the former European CISO for Santander, and Divisional CISO for BP, has provided strategic leadership and led security transformations in a range of contexts, including critical infrastructure and highly regulated environments such as Financial Services, Oil and Gas.

She has previously worked for global consultancies, Deloitte and BT Global Services, and often leverages her deep understanding of the challenges faced by global boards and executives to support their strategic objectives. Emma holds an MSc in Information Security from Royal Holloway, University of London and won CISO Supremo of the year from Unsung Hero Awards in 2020.

George Eapen

George Eapen

Group Chief Information Officer, Petrofac (UAE)

George Eapen is currently the Group CIO for Petrofac, an international provider of energy services, with around 11,500 employees supporting international and national oil, gas and renewable energy companies to unlock more value in key geographies including, Malaysia, India, Middle East, Russia and the CIS, the UK and the Americas. In his current role, George and his team manages IT & Digital strategy for the Company. George also serves on the Global Board of Advisors for IBM Security.

George was previously Chief Information Security Officer for GE Global Regions/ GE International. In that role, George was responsible for defining Cyber Security strategy for Enterprise IT & OT for all the GE regions outside of US which accounted for B revenue for the Company. George has 15 years of global experience (USA, India, Singapore, Italy, China & Middle East) with multiple businesses (Healthcare, Aviation, Oil & Gas,) in diverse IT domains (Software development, Quality, Auditing, Infrastructure, Operations & Cyber Security).

George is a well-known thought leader in the field of Cyber having presented extensively on the topic at over 30 conferences worldwide, including key notes at Microsoft Ignite 2019, IBM Think 2020 and GISEC. George also serves as a Non-Executive Board member for many Cyber Organisations and committees. George is a recipient of multiple awards globally and was also featured in Intelligent CIO, Security Middle East and Cyber Sentinels magazine.

George holds an Electrical Engineering degree from MG University, an MBA from Symbiosis, India and an Executive MBA from MIT Sloan.

Haydn Brooks

CEO, Risk Ledger

Ibraheem Khan

Ibraheem Khan

VP Information Security EMEA, Financial Services (UK)

Prior to his current role, Ibraheem was Head Chair of National Cyber Security Centre and Senior Information Security Officer / Deputy CISO at Channel 4.

James Frampton

James Frampton

Chief Information Security Officer, MUFG Bank EMEA and MUFG Securities International (UK)

James Frampton has a long career in technology leading and is currently the Chief Information Security Officer. James’s career covers retail, recruitment, insurance, banking, technology, and securities sectors and has worked for a range of organisations such as M&S, Diageo, Hays, Misys, ABN Amro and IBM.

James Mason

James Mason

Enterprise Cyber Security, QinetiQ (UK)

“After a strong sales career spanning decades, from selling batteries, to retail/sales management, to being a self-employed Wedding Photographer, I fell into InfoSec accidentally and found a passion for my calling in life, that quickly took off. In 2013, and within only a month in industry, I’d produced a sales plan and a 12 month marketing road-map – including filming a new red teaming video for our pen testing team, who at the time had never had this kind of focus = Legend J. The more that I sat with this team, listening to the daily “whoops” and high-fives, when we’d pwned another global organisation (on day one, black box) as well as truly believing I was selling the best – I wanted part of this too! The question remained, how could I when I regard myself as non-technical? Inspired by some of, and still to this day, the best hackers out there I became obsessed and quickly progressed to a member of the red team (black team – physical breach/Simulated Threat Lead). Working with one of the original red teams (formed circa 2000) that 10yrs before I joined, had a proud “never been caught” red team record, the pressure was genuinely on me. This only fuelled me further and after successfully infiltrating some of the largest banks, insurance, legal, CNI & other sensitive environments, I’m proud of my “never been caught” record to this day too. It could be argued that a great deal of sales people are social engineers anyway, what could go wrong….Thankfully, absolutely nothing (so far!).”

Jelena Matone

Jelena Matone

CISO, European Investment Bank (EIB) and President, Women Cyber Force (Luxembourg)

Respected and leading CISO, awarded the CISO of the year for 2019 in Luxembourg, Sentinel CISO Global 2020, EU CISO 2020, and recently Ambassador of the year 2021 in Luxembourg. Versatile and innovative Cybersecurity professional with emphasis on cyber security risk management, policies and procedures creation, IT/IS security, IT Operations, audit, risk mitigation, business process improvement, IT governance. Passionate about participation and encouragement of women in cybersecurity and in STEM programs.

Prior to current role, served as the Senior Operational Risk and ISO manager for another EU Institution. Earlier in career, managed IT Audit and Compliance for Sobey’s, one of the two national grocery retailers in Canada and Audit, Corporate Development, M&A and growth strategies and IT Audit for George Weston, one of the Canada’s largest publicly traded food processing and distribution companies.

Jelle Wieringa

Jelle Wieringa

Security Awareness Advocate, EMEA, KnowBe4 (The Netherlands)

Jelle Wieringa has over 20 years of experience in business development, sales, management and marketing.

In his current role as Security Awareness Advocate for EMEA for KnowBe4, he helps organizations of all sizes understand why more emphasis is needed on the human factor, and how to manage the ongoing problem of social engineering.

His goal is to help organizations and users increase their resilience by making smarter security decisions. Previously, Wieringa was responsible for building an AI-driven platform for security operations at a leading managed security provider.

Jonathan Luff

Jonathan Luff

Co-CEO, CyLon (UK)

Jonathan is the co-founder of CyLon, which has supported the growth of 100+ cyber security startups across Europe, Asia and the Middle East to a collective valuation of bn+. Before founding CyLon, Jonathan was a senior British Diplomat, serving in a variety of roles for the UK Government, including as an advisor to UK Prime Minister David Cameron. He also co-founded Epsilon Advisory Partners, a strategy and growth firm working with world-leading global technology companies and investors.

Kai Roer

Kai Roer

CEO and Founder, Praxis Security (Norway)

A best-selling author, an award-winning speaker, and a serial entrepreneur, Kai Roer is the CEO and co-founder of Praxis Security Labs, an innovative, research-based security management software company. He is dedicated to improving the knowledge and understanding of the human factors that influence security and the organizational impact they have, and is widely recognized as a leading global authority on the topic of security culture.

Kai Roer has been providing actionable advice founded on empirical evidence to public and private organizations around the world since the 1990s, and has spent the past decades working with the information security community on a global stage. He has written and co-written several best-selling books on leadership and technology, as well as Build a Security Culture (IT-Governance, 2015) and The Security Culture Playbook (Wiley, 2022), which are well-considered as industry-guiding resources on the topic of security culture. He is also a popular keynote speaker, expert lecturer, a frequent guest on podcasts and is often featured in national and international media.

Kai focuses on presenting complex challenges in easy-to-understand language, and explains security in ways that resonate with non-security people. Thanks to his invaluable contributions to the industry and unique background which combines leadership, communication, and technology, Kai has received several awards throughout his career – including the Ron Knode Service Award by the Cloud Security Alliance CSA for his extensive volunteer work for the security community around the world.

When Kai is not working, he enjoys spending time outdoors, riding his motorcycles and BBQing with his family and friends. You can connect with Kai at www.linkedin.com/in/kairoer.

Karl Mattson

Karl Mattson

Chief Information Security Officer, Noname (U.S.)

Karl Mattson is the Chief Information Security Officer at Noname Security. With over 25 years of experience leading innovative and diverse teams of technology and security professionals in financial services, retail and federal government, Karl has a track record of advising CEOs, CTO and investors on strategies for product, market and customer success.

Prior to Noname Security, he served as Chief Information Security Officer at PennyMac Loan Services and City National Bank, and Senior Vice President of IT Risk Management at PNC.

In addition, Karl formerly served as President of the LA Cyber Lab, Financial Services Co-Chair for Los Angeles Infragard, and Adjunct Faculty at the University of Minnesota’s Technological Leadership Institute.

Karl completed eight years of active duty service in the U.S. army. He holds a Bachelor of Business Administration from St. Mary’s University of San Antonio, Master of Business Administration from Auburn University, and a Master of Science in Computer and Information Systems from Boston University. He is a certified CISSP and FBI CISO Academy graduate.

Lorna Trayan

Lorna Trayan

Executive Partner, Security and Risk Management, Gartner (UAE)

Having more than 20 years of experience in the information security industry and the GCC region, Lorna is a Security Executive Partner and CISO Advisor with Gartner, having advised over 45 Cybersecurity Executives/CISOs across different industries in the GCC region. As a sought-after speaker, she has presented at numerous conferences, sharing insights and strategies that help CISOs achieve their objectives.

In addition to her technical expertise, Lorna is also a skilled communicator who excels at distilling complex security concepts into clear, actionable advice for non-technical stakeholders.

One of Lorna’s key responsibilities is running security awareness sessions for Boards of Directors, non-security Executives, VPs and GMs in various organizations.

Marina Nogales Fulwood

Marina Nogales Fulwood

Global Head - Cyber External Engagement - Global Response and Intelligence, Grupo Santander (Spain)

Marina Nogales Fulwood is Global Head of Cyber External Engagement at Grupo Santander, where she leads strategic cyber collaboration initiatives to boost collective defence against cybercrime and foster a favorable regulatory cyber environment for the cyber ecosystem.

Marina manages relationships with Law Enforcement, trust groups and bilateral relationships in the public and private sectors and ensures Santander is a key player in the cyber arena.

Previous to this role, Marina headed Santander’s Global Cyber Intelligence team and was Director of Investigations at K2 Intelligence, where she launched the firm’s Cyber practice, which subsequently became leading cybersecurity firm Bluevoyant.

Mark Logsdon

Mark Logsdon

CISO, NHS England (UK)

Mark is Chief Information Security Officer for NHS England having joined from UKHSA (Test and Trace) where he was head of Cyber Assurance and Oversight. With over 30 years of experience in security, Mark has held a number of high profile roles in the public and private sectors. He has a strong business focus seeing security as a business enabler. At every opportunity Mark seeks to manage the needs of business against those of security and risk. Outside of work, Mark works to raise much needed funds for NSPCC Childline. He is a member and former Chair of the WhiteHat Ball Committee which to date has raised over £2M for the NSPCC. less

Mark Snel

Mark Snel

CISO, Signify (The Netherlands)

I am a passionate leader with over 15 years of experience in the field of Information and Cyber Security. My genuine enthusiasm and energy for this industry fuel my drive to protect organizations from evolving threats and foster a culture of security.

With a strong technical and business background, I have operated on strategic, tactical, and operational levels, enabling me to understand and address security challenges from multiple perspectives. I firmly believe in the value of transparency, open communication, and continuous learning, as they are essential in building robust security programs.

My leadership approach emphasizes factual decision-making, persistence, and effective execution. I thrive on delivering tangible results that positively impact organizations, helping them navigate the complex landscape of cyber threats and compliance requirements.

One of my key strengths lies in my ability to effectively communicate with stakeholders at all levels. I tailor my communication style to suit diverse audiences, making technical concepts accessible and actionable. By fostering collaboration and understanding, I ensure that security initiatives align with business objectives and garner support from key stakeholders.

Throughout my career, I have had the privilege of positively influencing people and organizations. I take great pride in guiding teams toward achieving their full potential and creating a security-conscious culture that safeguards critical assets.

If you are looking for a dedicated and results-driven CISO who values continuous improvement and is committed to securing your organization’s future, I invite you to connect with me. Let’s collaborate and strengthen our collective defenses against cyber threats.

Matthew Brady

Matthew Brady

Security Engineering Manager EMEA, Synopsys (UK)

Matthew has worked at Synopsys since 2018, as Sales Engineering Manager and Subject Matter Expert on SCA for EMEA. He has been involved in the SCA and SBOM strategy at Synopsys, and supported the sales and deployment of solutions to enterprise customers across EMEA. Prior to Synopsys he worked at Hewlett Packard Enterprise since 2010 and has worked as Security Engineer since 1996.

Matt Holland

Matt Holland

CTO and Co-Founder, Seedata.io

Matt has a distinguished 25-year career in cybersecurity, having worked as Chief Information Security Officer in some of the best-known global brands.

Alongside this, he has also assisted numerous startups to achieve success through his mentoring activities within several cybersecurity accelerators. Now, Matt is tackling fundamental gaps in cybersecurity capabilities, delivering a game-changing Automated Moving Target Defence Platform with seedata.io

Monika Atanasova

Monika Atanasova

Global Head of Cyber Third Party Risk Management, Raiffeisen Gruppe (Switzerland)

I am an experienced security strategist in highly regulated sectors, adept in designing and implementing Cyber TPRM strategies and programs, with long term international expertise in contractual negotiations and stakeholder management within electric mobility, cyber security and renewable energies.

Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International (UK)

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.

Owanate Bestman

Owanate Bestman

Founder, Bestman Solutions (UK)

Owanate is the founder of Bestman Solutions, a firm dedicated to helping leaders hire cyber security professionals. He advises CISOs and Executives on market factors that impact their growth plans and designs bespoke solutions to address this. Firmly embedded in the cyber security space, he possesses a global core network of well-respected and proven security specialists. Owanate has spent almost a decade recruiting in the Cyber Security field. Before this, he recruited Technology and Operational Risk specialists and successfully staffed a number of high profile banking regulatory programmes. He is also a keen industry speaker and writer for security associations and international publications. Outside of Security and staffing, Owanate is interested in all things Martial Arts.

Paul Baird

Paul Baird

CTSO, Qualys (UK)

Paul Baird is a highly experienced and accomplished IT and cybersecurity professional with over 25 years of industry experience.

Currently, he is serving as the Chief Technical Security Officer (CTSO) for Qualys. Throughout his career, Baird has demonstrated a deep understanding of cybersecurity and has been instrumental in building several Security Operations Centres (SOCs).

His achievements in the field were recognised in 2021 when he was awarded Fellowship of the Chartered Institute of Information Security Professionals (CiiSec) for his outstanding work in supporting cybersecurity.

Paul Hopkins

Paul Hopkins

Global Head of Cyber Strategy, Architecture and Secure by Design - Head of Cyber Security Networks, Vodafone (UK)

Paul leads a talented team of security architects and consultants designing and securing Vodafone’s systems, products and services. Embedding security across Cloud, IoT, Mobile, Office and Fixed networks, with a diverse range of people, technologies and business applications every day brings new insight and a different perspective. Prior to this Paul was Technical Director for CGI’s UK Cyber Security Practice, and a Principal Security Architect, working on a number of security transformation programmes. Paul has lead a team providing managed security services and incident response, worked as a penetration tester, been a software developer and leader, and started as security researcher in 1992.

Phil Litherland

Phil Litherland

OT Security Product Manager, National Grid (UK)

A senior level Cyber Security & Information Assurance professional with over 30 years’ experience in Technology & Engineering Management, Safety & Security Engineering and IT/OT Security for Critical National Infrastructure environments in the Defence and Civil Nuclear, Pharmaceuticals and Utilities sectors.

Quentyn Taylor

Quentyn Taylor

Senior Director Information Security and Global Response, Canon for Europe, Middle East and Africa (UK)

Quentyn has embraced using the power of stories and his own experience of testing products to destruction, building business relationships across the world whilst driving Canon’s strategy and educating business customers to minimise their security risk. A seasoned presenter to both the board and technical teams, Quentyn is seen as a transformational business leader achieving positive results for the end customer and the company. During his career, Quentyn has worked in a variety of industries for a number of organisations including outsourced service providers, Internet service providers as well as Dotcom businesses, before moving to Canon in 2000.

Rashpal Bhamra

Rashpal Bhamra

IAM Practitioner, Advisor, Investor and Entrepreneur

With just over 15 years in the industry, Rashpal is an experienced cyber-security professional with a detailed knowledge of security tools, technologies, and best practices. He has been a part of the team at RSB Infosec for more than 12 years and has created and deployed security solutions for a diverse range of clients, particularly in the Legal, Financial, and Healthcare sectors. His depth of understanding regarding the value of internal networks, systems, and information has proven vital in helping to protect these assets for our clients. Rashpal’s experience includes IAM Migration and cloud adoption at St. James’s Place Wealth Management, Digital security at BP, IAM review and implementation for the London Metal Exchange and Senior Security Consultant at Bank of America Merrill Lynch. Rashpal is a cybersecurity advisor, Investor and Entrepreneur.

Ray Stanton

Ray Stanton

NED/ Board Advisor / CISO/CSO

An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.

Richard Mackintosh

Director, Quince Group (UK)

Richard Mackintosh, a Director of the Quince Group, and a Senior Adviser to StoneTurn has over 30 years’ experience in security, investigations, insider risk, and intelligence, in the UK corporate and government arenas.
Richard has held security leadership positions in the private sector, including as Director of Investigations and Cyber Intelligence Adviser for BP, and Head of Intelligence for Lloyds Banking Group. At BP Richard established and led the enterprise-wide insider risk programme.

Prior to his roles in the private sector, Richard served in a wide variety of roles concerning national security holding positions in crisis management, civil contingencies and emergency planning, specialist training, physical and security threats, policy and planning, risk management, and media and communications.

The Quince Group helps clients across a wide variety of sectors (including energy, insurance, legal, emerging technologies, and technology startups) to understand and then manage insider risk in a holistic and systematic manner. With a rapidly changing risk landscape driven by technology, geo-politics, and economic and societal factors, understanding the evolution of personnel security (insider) risks is critical for organisations wishing to thrive. It is often the missing or least considered element in security. Working with organisations from small tech startups to large multinationals, The Quince Group approach is designed to help build high trust organisations where security becomes a positive benefit to the bottom line rather than just a cost. Quince assists boards and senior executives to understand the risks and then works with practitioners and stakeholders to design and implement proportionate and adaptive responses. They also assure and improve existing programmes.

Richard is a Senior Adviser to the global advisory firm StoneTurn with a particular focus on helping clients manage multidisciplinary challenges and specifically to develop proportionate and scalable approaches to insider risk irrespective of size or sector.

Dr. Robert Coles

Dr. Robert Coles, Head of OT Security Strategy, DSSmith plc

Robert has over 35 years of audit, risk and cybersecurity experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG. Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School. Robert also holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, and Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University of Brighton.

Rob Otto

Rob Otto

EMEA Field CTO, Ping Identity

Rob is a Principal Architect for Ping Identity in the UK and also the EMEA representative to the Ping Identity CTO Office. Rob has 20 years experience in identity and access management. He has worked on complex implementation projects in the UK, USA, Europe and South Africa. His current area of focus is on applying industry standards like OpenID Connect and OAuth 2.0 to enable businesses to interoperate and securely expose data and API’s. He is specifically focused on using Mobile Applications to deliver elegant Strong Customer Authentication solutions within financial services and other verticals.

Dr Sally Leivesley

Dr Sally Leivesley

Managing Director Newrisk Limited UK, Member of the Register of Security Engineers and Specialists, international media commentator on cyber, catastrophic risks, terrorism and nuclear war (UK)

Dr Leivesley, sally@newrisk.com works on generic solutions to catastrophic risks to critical infrastructure across all disciplines and contributes practical applications to government policy and business. She has been a Panel adviser to for the British IET and CPNI supported publication for Cyber Security in the Built Environment.
As an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business Dr Leivesley has worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks.
As an international media commentator she has commentated for BBC World Service and other news outlets on extreme threats – Chinese spy balloon over USA nuclear missile site, uranium package at London Heathrow airport, cyber; terrorism; aviation losses; nuclear reactor explosions; Kabul 2021 evacuation; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents.

Dr Leivesley has held international scientific meetings on issues of catastrophic risk including risks of emerging nuclear weapons, infrastructure resilience including cyber, Covid-19 solutions and hazardous near-earth objects.
She was director of two disaster recovery units in Australia (weather and chemical incidents) and trained by British Home Office as Scientific Advisor holding a Cold War appointment as on all aspects of nuclear war.
PhD London University; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute for Defence Studies, and the British Information Assurance Advisory Council Community.

Sam Finn

Sam Finn

Director, Via Resource (UK)

Sam joined Via Resource in 2011 as the first Consultant.

With over 10 years of recruitment experience, all of which have been in the Information and Cyber Security field.

Covering a full range of Information Security roles including GRC, Data Protection, Security Operations and many more.

Sam’s main specialism is in Security Operations, Incident Response & Security Engineering. Where he has placed over 100 candidates in the industry and built relationships with teams globally, With certifications including CertRR, CertRP and Diploma in Recruitment Management.

Sami Said

Sami Said

CISO/ CSO - Chief Security Officer, Tunisie Telecom (Tunisia)

With over 29 years of managerial experience in different telecommunication fields, including eight years as Chief Information Security Officer, and Security Executive Director, added to six years as Internal Audit Executive Director, Sami has extensive knowledge of information security, cyber-security, privacy, Internal Audit, Risk Management and Internal Control.

As Telecom Engineer, Sami has also good expertise of telecommunication technologies and trends. He was Mobile O&M Director at Tunisie Telecom and supervised as Regional Director the infrastructure deployment for both fixed and mobile networks in three Tunisian Departments.

Additionally, Sami is an expert assistant at the Tunisian University where he teaches Management Information Systems and Information Security. He holds an MBA of Paris Dauphine University-France and two Telecom Engineering diplomas of SUPCOM Tunisia.

Sami is the winner of The Inspiring Leader of the Year 2022 Award at North AfricaCom Event

Sandip Wadje

Sandip Wadje

Global Head of Technology Risk Intelligence, BNP Paribas (UK)

Cyber & Tech Risk @ BNP Paribas – Crypto / blockchain, AI, Cloud, & Threat Intelligence

– A highly experienced and innovative leader with versatile cyber security, risk, and compliance experience in global Financial Services institutions
– Significant experience in leading large multi-year cyber and risk programmes by proactive engagement with board level business, technology, and RISK executives
– Start-up mind set with proven experience in developing and implementing innovative cyber security solutions in F500 organizations
– Proven experience in hiring exceptional talent in offshore locations to setup Centre of Excellence (COE) capability
– Global mindset: Experience of building and leading multi-cultural teams in Asia, Europe, and USA
– Exceptionally well connected in the industry- strong network of customers, partners, technology providers, and subject matter experts across the globe
– Known in the industry for: Passion, Integrity, Honesty and Technical Knowledge
– Specialties: Security Strategy, Cyber Roadmap, Security Architecture, Cyber Threat Intelligence, Cloud Security, Security Operation Centre, Identity and Access Management, Data Protection (Structured and Unstructured), Social Media Monitoring, External Attack Surface, Vulnerability Prioritization, Cyber Fraud, Financial Crime, Cyber Rating, Digital Risk Analytics, Insider Threat, Incident Response, Merger & Acquisition Due Diligence, Technology Audit and GRC
– Stakeholder coverage: CEO, COO, CFO, CDO, DPO, CTO, CIO, CISO, Risk Management, Compliance, Fraud, Credit Risk, Legal and HR

Simon Riggs

Simon Riggs

Interim CISO and Board Advisor

Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Simon was recently interim CISO at John Lewis, McKesson UK and Avon. Prior to these roles, he was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.

Sounil Yu

Sounil Yu

CISO, JupiterOne (U.S.)

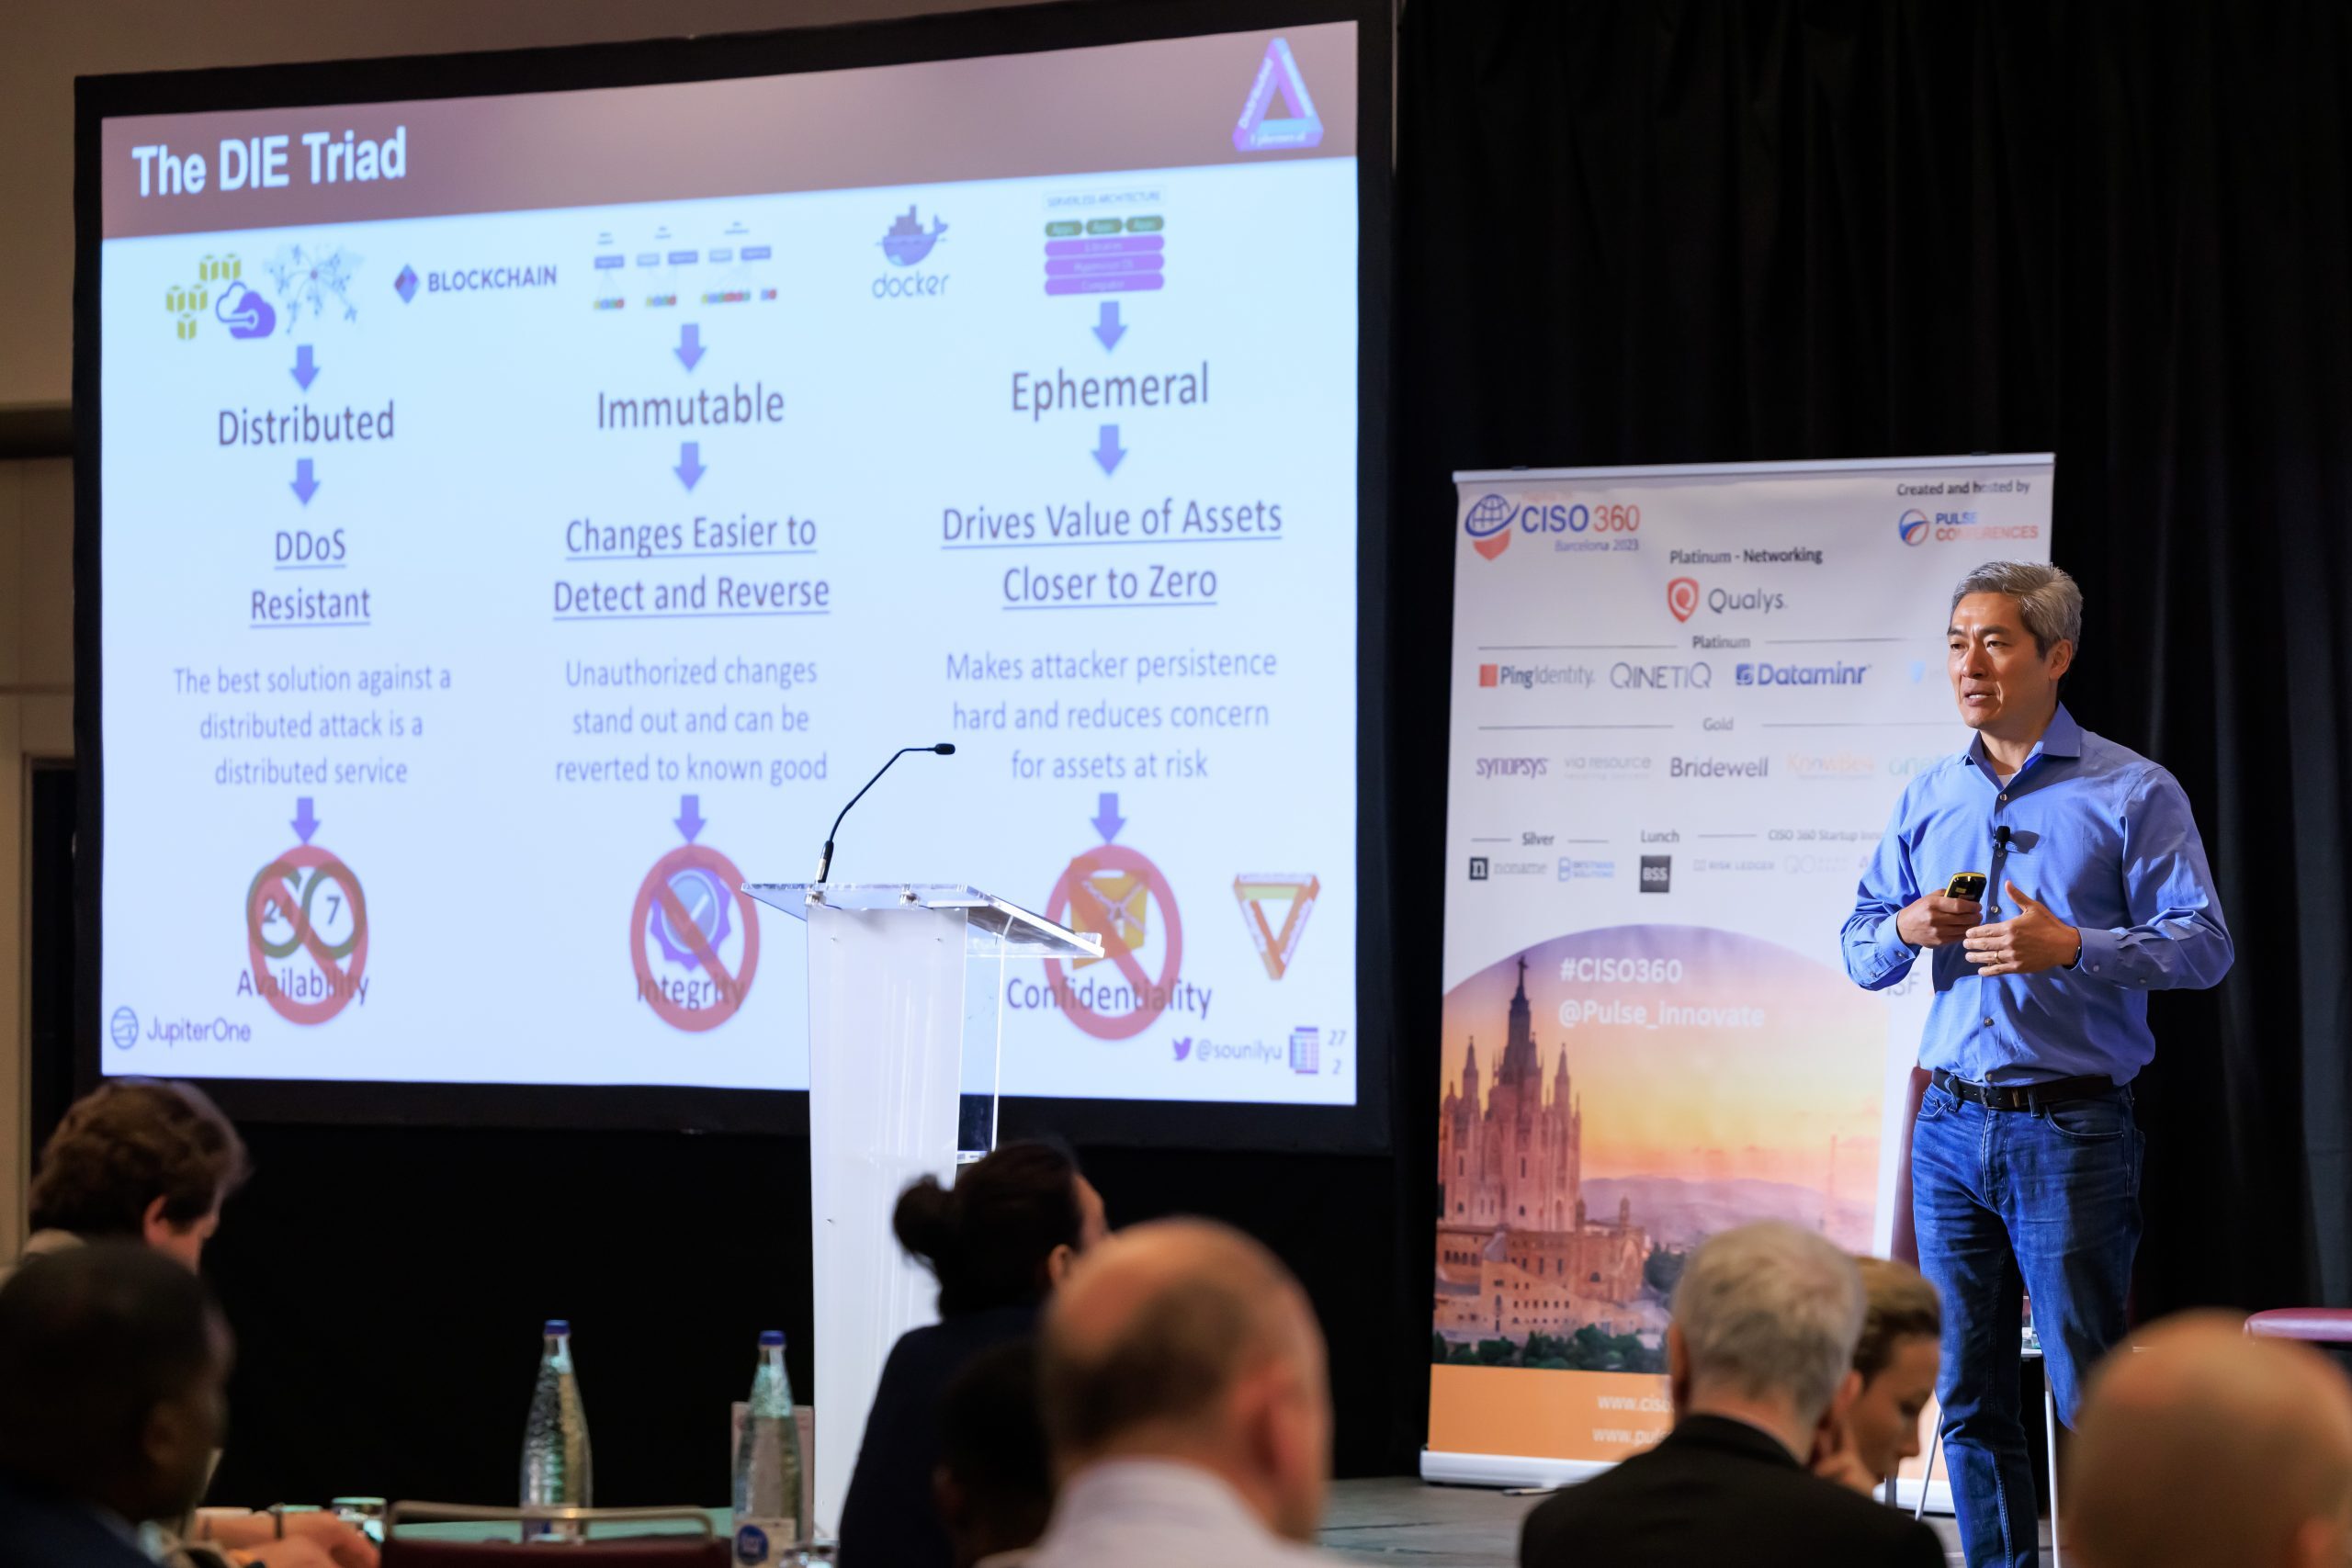
Sounil Yu is the CISO and Head of Research at JupiterOne. He created the Cyber Defense Matrix and the DIE Triad, which are reshaping approaches to cybersecurity.

He’s a Board Member of the FAIR Institute; is a visiting fellow at GMU Scalia Law School’s National Security Institute; guest lectures at Carnegie Mellon; and advises many startups.

Sounil previously served as the CISO-in-Residence at YL Ventures and Chief Security Scientist at Bank of America. Before BofA, he helped improve information security at several Fortune 100 companies and Federal Government agencies.

Sounil has over 20 granted patents and was recognized as one of the most influential people in security in 2020 by Security Magazine, Influencer of the Year in 2021 by SC Awards, a 2021 Top 10 CISO by Black Unicorn Awards, and for Lifetime Achievement in 2022 by the SANS Institute.

He has an MS in Electrical Engineering from Virginia Tech and a BS in Electrical Engineering and a BA in Economics from Duke University.

Thomas Eeles

Thomas Eeles

Security Operations Manager, Right Move (UK)

Thomas has been working in commercial Cybersecurity Incident Response for over ten years, running a CSIRT’s across Europe and responding to hundreds of incidents a year.

Tunde Benjamin

Tunde Benjamin

Cybersecurity Lead, Advantage Smollan

Tunde is responsible for Information Security at Advantage Smollan, a leading Sales, Marketing & Data Company. Prior to joining he worked at Colliers International as Head of Information Security. He has also worked as a Network Engineer at KKR supporting their Infrastructure and Operations.

He holds a CISSP #765107‎ and degree in Computer Systems & Networks from Plymouth University.

Toks Oladuti

Toks Oladuti

Chief Information Security Officer, Dentons (UK)

Toks is responsible for the global delivery of information security at Dentons, the world’s largest law firm. He has over 20 years’ experience working in security, technology and privacy, across a number of industries.

Toks is an experienced and strategic business risk leader. He has a particular passion for strategy and team building and development. His core skillset, developed over the years includes security operations and architecture, risk management and risk driven investment, data protection, compliance and audits, and enterprise culture, awareness and training.

Toks has contributed to the business and technology community through information sharing, groups, speaking engagements and multi-industry networking. As strong supporter of education and schools, he has provided advice in areas of security, data protection, user awareness and cloud transformation.

Dr Viktor Polic

Dr Viktor Polic

CISO, Head of Information Security and Assurance Services, ILO - United Nations (Switzerland)

More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences.

Adam Drabik

Adam Drabik

CISO, Monument Re Group (UK)

Adam has 25 years international experience in managing IT and Information Security mainly in Oil & Gas, Pharmaceutical, Consumer Goods, Telecommunication and Financial Services industries. Founding member of ClubCISO, Consumer Goods Security Forum in the UK and Information Security Forum in Malaysia – peer groups of CISOs and Heads of Information Security formed to exchange good practices and experience within specific focus groups. Adam has significant experience consulting and advising boards of directors of FTSE100/Fortune500 companies on Information Security, Privacy, Risk Management and Resilience. The current role is Chief Information Security Officer at Monument Re Group.

Alan Jenkins

Alan Jenkins

Independent Trusted Advisor, Interim CISO, Principal Consultant, NED and Mentor

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

Alexandra Mercz

Alexandra Mercz

Founder | Board Director (Singapore)

Alexandra Mercz is a cybersecurity and technology expert with extensive experience in multinational financial institutions and startups. She led her career in major financial institutions, excelling as Chief of Staff, managing complex operations and enhancing organizational efficiency. This experience helped her later guide startups in building strong, scalable operations.

Now, Alexandra works as an advisor and independent consultant to both large companies and startups. She uses her vast knowledge to support early growth and establish robust management practices. Her hands-on approach and dedication make her a trusted advisor, helping new businesses thrive. She has worked with notable organizations such as Standard Chartered Bank, BNP Paribas, Siemens, Vodafone, and Carlsberg, making her well-versed in both technology and business.

Alexandra holds several prestigious certifications, including ISO/IEC 27001:2022 ISMS Lead Auditor, Accredited Trainer for ISACA CRISC, Certified Information Security Manager (CISM), and Accredited Board Director. Additionally, she is certified three times by Google Cloud Platform, including as a Professional Cloud Security Engineer, and she is also a certified NIST Cybersecurity Framework Lead Implementer.

She is actively involved in various industry professional bodies and technology networks. Alexandra is a member of the European Women on Boards and serves on the Senior Executive Committee of the Cybersecurity Chapter of the Singapore Computer Society. She founded and led the (ISC)² Singapore Mentorship Program, significantly increasing women’s participation in cybersecurity.

Alexandra is passionate about diversity, equity, inclusion, and belonging (DEI&B). She is committed to breaking down barriers and challenging unconscious biases within the cybersecurity sector. She actively mentors and coaches women, helping them achieve career progression and sharing her experiences. By championing alternative career paths and showcasing female role models, she aims to normalize women’s presence in both leadership and technical roles, contributing to a healthier, more diverse industry culture.

Carlos Gonçalves

Carlos Gonçalves

Cyber Threat Intelligence Leader, Banco do Brasil (Brazil)

Joining us from Brazil, Carlos leads the Cyber Threat Intelligence and Threat Hunting team at the Banco do Brasil. Responsible for defining strategies for security assessments, cyber defense, security automation and threat intelligence, he acts as a technical specialist with the red, blue, automation and threat intelligence teams. Carlos holds an MBS from the Pontifícia Universidade Católica do Rio de JaneiroPontifícia Universidade Católica do Rio de Janeiro.

Chantal Spleiss

Chantal Spleiss

Senior Consultant, DHC AG (Switzerland)

Dr. Chantal Spleiss is an AI expert and Senior Consultant at DHC AG in Switzerland, specializing in Computer System Validation (CSV) in Pharma/MedTech with a strong focus on cybersecurity. With an impressive portfolio of accomplishments and a wealth of knowledge, she is a notable voice in various realms.
In 2024 alone, Dr. Spleiss has made significant contributions to AI and cybersecurity with a strong dedication to advancing the field. She is the lead author of the white paper “AI Resilience: A Revolutionary Benchmarking Model for AI Safety,” published by the Cloud Security Alliance (CSA). Her expertise is further recognized through her role as a Co-Chair of the AI Governance & Compliance Workgroup at the CSA, and as a panelist at Cloud Expo Europe in Frankfurt, where she shared “Insights into AI”.
Her ability to navigate complex landscapes is unparalleled, blending rigorous technical knowledge with a passion for practical, timely results. Dr. Spleiss’s unique approach stems from her diverse experience across life sciences, technical sciences, and finance & MedTech industries, allowing her to connect the dots in innovative ways. She was recently featured in the Frankfurter Allgemeine Zeitung in the article “Männer und Frauen passen doch”, highlighting her role in promoting diversity in tech and her forward-thinking approach to industry challenges. Dr. Spleiss enjoys engaging in wide-ranging discussions about “life, the universe and everything”.
Contact: www.linkedin.com/in/chantal-spleiss

Charlie McAlpin

Charlie McAlpin

Director of Technical Management, Qualys (United Kingdom)

Charles McAlpin is a Director, Technical Account Management, Post-Sales with Qualys, the leading provider of Information Security and Compliance assessment solutions. Charlie’s passion and 15 years of experience in the sector allows him to help businesses to identify critical issues within their security operations and to assist in delivering a strengthened security posture. He has a genuine belief that he is helping his clients to avoid the next cyber attack.

Colette Hanley

Colette Hanley

CISO, Checkout.com

Colette is CISO for Checkout.com, a cloud-based payments platform. Before joining Checkout.com she held leadership roles at Skype, Microsoft and Nokia. Specialising in pragmatic and creative solutions for complex and evolving compliance requirements, she is passionate about embedding security and privacy in operations, products and services from design to delivery. Her focus is comprehensive reduction of technology-related risk for the business and for the customer. Colette holds an MSc. in Information Security from Royal Holloway and is CISSP, CISM, CIPP, CDPSE.

Dean Armstrong KC

Dean Armstrong KC

King's Counsel (Barrister) | Chambers & Partners No.1 Silk for Cryptoassets | Legal 500 No.1 Silk for Crypto and Blockchain | The National Cyber Awards 2023 'Cyber in Law' Award

Dean is a specialist in the law relating to digital assets and the blockchain, encompassing cryptocurrency, non-fungible tokens, and smart contracts. With expertise that spans cyber (digital) law in general, Dean is also able to assist clients with legal matters relating to cyber insurance and the intersection of cyber and data law. Dean has written textbooks on cryptocurrency and the blockchain as well as cyber security, cyber litigation and cyber insurance. He is also highly experienced in international insolvency work, especially involving crypto assets. He is also experienced in cases involving allegations of international and UK fraud.

Ranked by Chambers and Partners and Legal 500 in Band 1 for crypto and block chain assets, Dean is the only silk to lead on the Commercial Bar’s response to the Law Commission on its draft on digital assets. Dean has also advised on the draft of the Virtual Asset Service Provider Rules.

Derek Cheng

Derek Cheng

CISO, Deliveroo (UK)

Derek is an experienced leader with over 20 years of professional experience in cyber security and risk management. He is currently the CISO for Deliveroo, where he is developing and implementing a security strategy and roadmap to support the company’s ambitious goals. Prior to Deliveroo, Derek was the Chief Security Officer for TalkTalk, where he joined post their cyber attack in 2015 to rebuild the brand and protect TalkTalk’s critical infrastructure, assets, and customer data. He is also currently the CISO Advisor for Square Enix West, where he is helping build and steer their cyber security programme, and on the Advisory Panel for AND Digital overseeing their Cyber Security strategy.

Previously, Derek was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, he spent over 6 years at Deloitte where he managed and performed a multitude of information security and risk management engagements for global Fortune 500 companies across various industries.

Dimitri Chichlo

Dimitri Chichlo

CSO, BforeAI (Switzerland)

A French and Swiss citizen, Dimitri Chichlo started his career in Ukraine in 2004, then moved to Switzerland in 2009, working mainly for international financial institutions in the fields of operational risk and cybersecurity. In 2017, he completed an Executive MBA at INSEAD. In 2019, he joined the Supervisory board of Ukreximbank, the third largest and state-owned bank in Ukraine, as vice-chairman and chair of the Operations and Digital Committee, where he remained until May 2023. In 2020, he founded his consultancy practice in cybersecurity and digital transformation, AndSecure. Since February 24th, 2022, he is actively involved into providing humanitarian support to Ukraine. He currently lives in Geneva.

Dr. Eduardo Solana

Dr. Eduardo Solana

Senior Lecturer of Cryptography and Security, University of Geneva (Switzerland)

Dr. Eduardo Solana is Senior Lecturer of Cryptography and Security at the University of Geneva. Amongst others, Dr. Solana has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has more than twenty five years of experience in the fields of cryptography and information security both in the private sector and the academia. Dr. Solana is a deeply experienced security practitioner, technical writer and regular speaker at the most relevant conferences and symposia in the field. During his extensive career, he has provided consulting services to multinational organizations and states in security related issues.

Emma Leith

Emma Leith

Director of Consulting, Cybersecurity, Bridewell (UK)

Emma is a cyber security leader and executive with 18 years’ experience in senior cyber leadership positions, consulting and services. Emma is a Board member and Director of Consulting for Bridewell, a leading cyber security services company, where she has full ownership of Bridewell’s professional services capability. In this role she brings a sustained focus on instilling excellence and providing industry-leading, expert-led delivery of end-to-end services that solve key business challenges. Emma is highly experienced in all areas of cyber security and as the former European CISO for Santander, and Divisional CISO for BP, has provided strategic leadership and led security transformations in a range of contexts.

Fabrice Delhoste

Fabrice Delhoste

CTO & Cofounder, Mindflow (France)

Passionate about human-centered software development, over 22 years of experience in the software industry (Thales, Gemalto).

George Eapen

George Eapen

Group Chief Information Officer, Petrofac (UAE)

George Eapen is currently the Group CIO for Petrofac, an international provider of energy services, with around 11,500 employees supporting international and national oil, gas and renewable energy companies to unlock more value in key geographies including, Malaysia, India, Middle East, Russia and the CIS, the UK and the Americas. In his current role, George and his team manages IT & Digital strategy for the Company. George also serves on the Global Board of Advisors for IBM Security.

George was previously Chief Information Security Officer for GE Global Regions/ GE International. In that role, George was responsible for defining Cyber Security strategy for Enterprise IT & OT for all the GE regions outside of US which accounted for B revenue for the Company. George has 15 years of global experience (USA, India, Singapore, Italy, China & Middle East) with multiple businesses (Healthcare, Aviation, Oil & Gas,) in diverse IT domains (Software development, Quality, Auditing, Infrastructure, Operations & Cyber Security).

George is a well-known thought leader in the field of Cyber having presented extensively on the topic at over 30 conferences worldwide, including key notes at Microsoft Ignite 2019, IBM Think 2020 and GISEC. George also serves as a Non-Executive Board member for many Cyber Organisations and committees. George is a recipient of multiple awards globally and was also featured in Intelligent CIO, Security Middle East and Cyber Sentinels magazine.

George holds an Electrical Engineering degree from MG University, an MBA from Symbiosis, India and an Executive MBA from MIT Sloan.

Ibraheem Khan

Ibraheem Khan

CISO, AltoVita (UK)

Prior to his current role, Ibraheem was Head Chair of National Cyber Security Centre and Senior Information Security Officer / Deputy CISO at Channel 4.

Indy Dhiman

Senior Security Architect, Humana (U.S.)

Jelena Matone

Jelena Matone

CISO, European Investment Bank (EIB) and President, Women Cyber Force (Luxembourg)

Respected and leading CISO, awarded the CISO of the year for 2019 in Luxembourg, Sentinel CISO Global 2020, EU CISO 2020, and recently Ambassador of the year 2021 in Luxembourg. Versatile and innovative Cybersecurity professional with emphasis on cyber security risk management, policies and procedures creation, IT/IS security, IT Operations, audit, risk mitigation, business process improvement, IT governance. Passionate about participation and encouragement of women in cybersecurity and in STEM programs.

Prior to current role, served as the Senior Operational Risk and ISO manager for another EU Institution. Earlier in career, managed IT Audit and Compliance for Sobey’s, one of the two national grocery retailers in Canada and Audit, Corporate Development, M&A and growth strategies and IT Audit for George Weston, one of the Canada’s largest publicly traded food processing and distribution companies.

Jorge Fernandes

Jorge Fernandes

CISO, DPO and Director of the Internal Control Office, CMVM (Comissao do Mercado de Valores Mobiliarios), the Portuguese Securities Supervisor

Jorge Fernandes is the CISO, DPO and Director of the Internal Control Office at CMVM, the Portuguese securities supervisor. He holds a bachelor’s degree in computer science and several certifications in information security and data protection.

Jorge has more than 20 years of professional experience in Information Security in the financial services sector. His experience as CISO includes the European Securities and Markets Authority and the Council of Europe Development Bank. He is currently a member of several European regulatory groups regarding cybersecurity, operational resilience, and the digitalisation of the financial sector.

Julian Meyrick

Julian Meyrick

Cyber Business Risk Advisor, the FAIR Institute

Julian Meyrick helps clients develop their security strategy in the context of the cyber business risks that they face; he has a particular focus on advising boards on the potential business impact of cybersecurity, and on quantifying cybersecurity risk in financial terms. From 2019 to 2023 Julian was the Managing Partner & Vice President for IBM Security’s worldwide Security Strategy Risk & Compliance practice. In 2020 he launched a new offering focused on quantifying cyber security risk in financial terms using the FAIR Institute Open Standard which grew rapidly delivering client projects globally across all industries. In 2021 he was invited to join the FAIR Institute Industry Advisory Board.

In 2012 Julian was selected to lead the integration of IBM’s new IT Security Services organisation in Europe, bringing together security consulting, security implementation services and managed security services into a single team to deliver an end to end service for clients and was promoted to Vice President in 2014. Julian is passionate about attracting talent into the cybersecurity profession and is an Ambassador for the UK National Cyber Security Centre’s CyberFirst programme. In the past he sponsored IBM’s partnership with Salute My Job which has trained over 500 military veterans in cybersecurity. Julian was also IBM’s executive sponsor for the Charter of Trust, a unique initiative by leading global companies to secure the digital world. Julian has lectured both at Oxford University’s Said Business School and Centre for Doctoral Training on Cybersecurity, and also at Warwick University’s MSc Course on CyberSecurity and Management.

Dr. Leila Taghizadeh

Dr. Leila Taghizadeh

CISO IberoLatAm, Allianz (Germany)

With prior experience at SWIFT and EUROCLEAR, Leila has a strong understanding of the challenges faced by organisations in balancing cyber risk and compliance. With a PhD in physics and a background in teaching and research, she is a sought-after speaker on the topic of cyber security for executives. Additionally, her advocacy in the field of AI for good highlights her dedication to using technology for the greater good and promoting sustainable solutions to save the environment and species.

Lorna Trayan

Lorna Trayan

CISO Advisor, Gartner (UAE)

Having more than 20 years of experience in the information security industry and the GCC region, Lorna is a Security Executive Partner and CISO Advisor with Gartner, having advised over 45 Cybersecurity Executives/CISOs across different industries in the GCC region. As a sought-after speaker, she has presented at numerous conferences, sharing insights and strategies that help CISOs achieve their objectives.

In addition to her technical expertise, Lorna is also a skilled communicator who excels at distilling complex security concepts into clear, actionable advice for non-technical stakeholders.

One of Lorna’s key responsibilities is running security awareness sessions for Boards of Directors, non-security Executives, VPs and GMs in various organizations.

Mark Adjei

Mark Adjei

CISO and Head of Cyber Security Risk Advisory and Governance, UBS (UK)

With over 25 years in Cyber & Information Security, I currently lead as CISO and Head of Cyber Security Risk Advisory & Governance at UBS. My journey began in pivotal roles at prominent international financial institutions such as Bloomberg L.P., JP Morgan Chase, and Bank of America Merrill Lynch, evolving through dynamic positions including Cyber and Information Security Risk Manager, Senior IT Security Audit Specialist, Network Security Architect, and Information Security Analyst.

At UBS, I’ve been at the forefront of shaping Cyber Threat Intelligence, Information Security Management, and Cyber & Technology Audit initiatives, crucial in crafting robust security frameworks and reducing risks in cutting-edge technology arenas. I am a proud graduate of South Bank University, London, where I earned both a B.Sc. in Business and Information Technology Management and an M.Sc. in Information Systems Security Engineering.

Holding esteemed GIAC, CISA and CISM certifications, I’ve dedicated my career to aligning security practices with strategic business objectives, ensuring comprehensive risk management. Beyond the boardroom, I’m an avid reader and traveller, passionately mentoring the next wave of cybersecurity talent.

My sporting achievements with the Great Britain American Football Team, coupled with my ongoing coaching role at the London Olympians AFC, reflect my commitment to teamwork and excellence. I look forward to energising our discussions with fresh perspectives on advancing cybersecurity and safeguarding information security in our rapidly evolving digital world.

Markus Härlin

Markus Härlin

Head of Inhouse Consulting Sales and Negotiation, Hays AG (Germany)

Markus Härlin, an experienced B2B sales professional, leads the in-house consulting team at Hays. His expertise lies in selling complex solutions to demanding organizations. Over his 25-year career, he has built the key account management function at Hays, introduced professional negotiation techniques, and is currently deeply engaged in the topic of ‘selling to top decision-makers’.”

Mauro Vezzoli

Mauro Vezzoli

Senior Solution Architect, Picus Security (Italy)

Mauro Vezzoli has been working in cybersecurity for more than 20 years. As a specialist engineer and consultant he is experienced at working closely with clients across industries to design and deliver solutions that meet wide-ranging security needs.

Michael Colao

Michael Colao

Chief Underwriter – Cyber Risks, AXA XL (UK)

Experienced CSO/CISO with than 20 years experience in financial services, Michael has a strong side-interest in computer forensics and in the management of digital evidence. Graduated from the Massachusetts Institute of Technology (MIT) in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services primarily in London.

Mike Beaupre

Mike Beaupre

Head of Cyber Security, Hays AG (Germany)

Michael is a technology leader with over 28 years of experience in guiding international public sector organizations, DAX 30 businesses, and mid-sized international firms through strategic technology initiatives. He is an expert in digitization and IT transformation and a thought leader in cyber security, organizational risk management, and IT compliance. He advises small and large enterprises ranging in size from 20 to 220,000 employees in the medical, pharmaceutical, biotech, translation, and manufacturing industries worldwide, just to name a few. Throughout his career Michael has led complex, diverse organizations toward enhanced operations while saving hundreds of millions in operating costs. He is passionate about mentorship, coaching, and removing cultural barriers. He was born in the USA, raised in Texas, and has travelled the world helping people maximize potential. Michael lives in Germany and is focused on family, volunteer work, and supporting a multitude of international clients at Hays.

Nicola Sotira

Nicola Sotira

Head of CERT, Poste Italiane (Italy)

Head of Poste Italiane CERT. It works in the field of information security and network for more than twenty years’ experience gained in international environments. In the security area he was involved in encryption design and network security, also working in complex infrastructure like mobile and 3G networks. He has collaborated with several magazines in the computer industry as a journalist contributing to the dissemination of issues related to security and legal technical aspects. Teaching Security, since 2005, at the Master in Network Security of the Sapienza University. Member of the Association for Computing Machinery (ACM) since 2004 and promoter of technological innovation, collaborates with several start-ups in Italy and abroad.

Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International (UK)

Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.

Owanate Bestman

Owanate Bestman

Founder, Bestman Solutions

Owanate is the founder of Bestman Solutions, a firm dedicated to helping leaders hire cyber security professionals. He advises CISOs and Executives on market factors that impact their growth plans and designs bespoke solutions to address this. Firmly embedded in the cyber security space, he possesses a global core network of well-respected and proven security specialists. Owanate has spent almost a decade recruiting in the Cyber Security field. Before this, he recruited Technology and Operational Risk specialists and successfully staffed a number of high profile banking regulatory programmes. He is also a keen industry speaker and writer for security associations and international publications. Outside of Security and staffing, Owanate is interested in all things Martial Arts.

Owen Miles

Owen Miles

Deputy Field Chief Technology Officer, Everbridge (UK)

Having worked within the operational resilience and critical event management space for more than 20 years, Owen is a driving force in the evolution of operational resilience practices. During his extensive career at Everbridge, Owen has played a pivotal role in the delivery of the Everbridge Critical Event Management platform, collaborating with, and supporting, over 800 customers across a diverse range of sectors. Known for his deep industry insights, Owen frequently takes the stage as a key speaker at industry events.

Patrick Kane

Patrick Kane

Senior Director of Security, Atlas Air (U.S.)

Patrick Kane is Senior Director Security for Atlas Air, a US airline conducting cargo and public/private passenger operations worldwide. Patrick is heavily focused on developing and implementing mitigation measures to support highly mobile global workforce and multiple travelers, to include pre-travel risk assessments, coordinating secure transportation and journey management, assessing hotel and transportation options.

Patrick currently serves as the Chair of the ASIS International Santa Barbara Ventura Chapter #21 and is the President of the Corporate Executive Protection Leadership Council (CEPLC). He recently spearheaded the creation of a Travel Risk Working Group within ASIS International. Patrick is also the past Chair and Chair Emeritus of the OSAC Aviation Security Working Group. He has over 20 years of experience working in private sector corporate security; most of that time focused on international operations and has personal experience on the ground in more than 70 countries.

Since 1996 Patrick has been a Certified Protection Professional (CPP) in good standing under the auspices of ASIS International. He received an International Executive MBA from Instituto de Empresa in Madrid, Spain in 2004. Prior to entering the private sector, Patrick served as an infantry officer in the US Marine Corps. He welcomes questions, comments and suggestions and can be reached at patrick.kane@atlasair.com or patrick.kane.cpp@gmail.com .

Nick Palmer

Nick Palmer

Senior Solutions and Customer Engineer, Censys (UK)

Nick Palmer is a security IT professional with over two decades of experience in Information Technology and Cyber Security. Nick is a cyber security technologist, security advocate and business problem solver. Previously he has worked for a variety of industry leading companies including: Attivo, Microsoft, TrapX Security, HP. In his role with the technology team at Censys, he helps customers uncover threats and vulnerabilities before they become risks.

Ray Stanton

Ray Stanton

NED/ Board Advisor / CISO/CSO (UK)

An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.

Rogier Fisher

Rogier Fisher

CEO/Co-Founder at Hadrian (The Netherlands)

Rogier is a serial entrepreneur and digital security enthusiast, currently Co-Founder and CEO of Hadrian Security. Hadrian is modernizing offensive security practices with automation, making security teams faster and more scalable.

As a teenager he was acknowledged by large companies like Google, PayPal, Microsoft and Yahoo for ethically breaching their systems. In 2013, at only 17 years old, he was one of the first innovators in the cryptocurrency industry by founding LiteBit, a custody and brokerage platform with over a million traders.

Driven by a passion for company building and startups, Fischer has started angel investing and advising other startups. He founded an angel syndicate and has been investing in healthcare, security, gaming, and deep tech startups.

Ryan Dodd

Ryan Dodd

Founder and CEO, Intangic (U.S.)

Ryan leads data science, technology and product vision for Intangic. He is an entrepreneur with real-world cyber and financial modeling experience. Prior to founding Intangic, Ryan spent 20 years as a hedge fund manager, including with Man GLG, and structuring financial risk products. He created the CyFi™ model at the core of Intangic’s AI-powered SaaS. He also co-authored the first peer-reviewed article on the intersection of cybersecurity and finance in Chatham House’s Journal on Cyber Policy.

Paul Colnan

Paul Colnan

CISO, ION Markets (UK)

Paul Colnan is the CISO at ION Markets, where he oversees the risk, security, compliance and privacy teams. He has 15 years of cyber security experience, including advising some of the world’s largest brands and he works with the board to enable secure and trusted commerce. He has an ‘ethical hacker’ background, which helps him tackle complex security issues, but he also cares about driving effective change through clear leadership and communication. Paul has been a CISO in various sectors, including fintech, logistics, and manufacturing, and before joining ION, he was an Executive Director at JP Morgan Chase, where he held security roles in retail banking, M&A and cloud platform security teams. Paul likes aviation and is pursuing his private pilot’s licence in his spare time.

Air Commodore (Rtd). Peter Drissell

Air Commodore (Rtd). Peter Drissell

Director Aviation Security, UK Civil Aviation Authority

Appointed by the Civil Aviation Authority (CAA) as its first Director of Aviation Security on 1st April 2014. Peter is the Aviation Security Regulator for the UK and overseas cyber security performance of the UK aviation sector. He previously served as Director of Security & Business Continuity for the Home Office for 5 years. Prior to this, Peter had served for 32 years in the Royal Air Force from which he retired as an Air Commodore in April 2007. His last appointments were as Provost Marshal for the RAF and Commandant General of the Royal Air Force Regiment. He has been a Corporate Security Director for 20 years.

Dr Sally Leivesley

Dr Sally Leivesley

Managing Director Newrisk Limited UK, Member of the Register of Security Engineers and Specialists, international media commentator on cyber, catastrophic risks, terrorism and nuclear war (UK)

Dr Leivesley, sally@newrisk.com works on generic solutions to catastrophic risks to critical infrastructure across all disciplines and contributes practical applications to government policy and business. She has been a Panel adviser to for the British IET and CPNI supported publication for Cyber Security in the Built Environment.
As an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business Dr Leivesley has worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks.
As an international media commentator she has commentated for BBC World Service and other news outlets on extreme threats – Chinese spy balloon over USA nuclear missile site, uranium package at London Heathrow airport, cyber; terrorism; aviation losses; nuclear reactor explosions; Kabul 2021 evacuation; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents.

Dr Leivesley has held international scientific meetings on issues of catastrophic risk including risks of emerging nuclear weapons, infrastructure resilience including cyber, Covid-19 solutions and hazardous near-earth objects.
She was director of two disaster recovery units in Australia (weather and chemical incidents) and trained by British Home Office as Scientific Advisor holding a Cold War appointment as on all aspects of nuclear war.
PhD London University; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute for Defence Studies, and the British Information Assurance Advisory Council Community.

Sandip Wadje

Sandip Wadje

Global Head of Technology Risk Intelligence, BNP Paribas

Sandip is a highly accomplished Senior Technology Risk Executive with 23 years of extensive experience in Cyber Security, Operational Risk, IT Risk, Internal Controls, and Compliance.

Since September 2017, he is serving as the Managing Director and Global Head of Emerging Technology Risks at BNP Paribas, where he is focused governance and oversight of emerging technology domains such as Cloud, Artificial Intelligence, Digital Assets, Threat Intelligence, and External Engagements.

Sandip has been instrumental in driving collaboration in European Financial Services community as a member of Financial Services Advisory Group at European Cybercrime Centre (EC3) and as a co-chair of European Financial Roundtable Cyber Experts Group.

Simon Riggs

Simon Riggs

Interim CISO and Board Advisor

Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Simon was recently interim CISO at John Lewis, McKesson UK and Avon. Prior to these roles, he was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.

Sybil Kleinmichel

Sybil Kleinmichel

Managing Expert Cyber Security DACH, Hays AG (Germany)

Sybil has worked in global consulting, banking, insurance, and telecoms during the last 25 years, in both New York and in Germany. As a DQS senior lead auditor, she specialized during the last 15 years in Cybersecurity by auditing information security management systems in global companies from banks to data centers. As a Cyber consultant she implemented several types of ISO management systems and coached board members to optimize business processes by building on core business strengths. As a Business Continuity Manager and Head of Security Audit at a global telecoms company, she built operational Cyber processes and managed the global audit management program. In her last role as Group CISO at a fortune 100 bank in Frankfurt, she implemented Cyber Security, Governance and Risk Management including regulatory reporting on critical cyber incidents.

Sybil joined Hays because Hays puts people in jobs every few seconds, in 33 countries. Hays is the market leader for people placement in Germany and together with Michael Beaupre and Neil Khatod are building the Hays Cyber Channel. Their aim is to become the leading Cyber recruiter with Cyber Advisory Services, to help CISOs spend more time with their families. She feels she can do this with her wealth of experience as an banking CISO, auditor and mentor.

Valerie Ezinmo

Valerie Ezinmo

CISO UK & IRELAND, L'Oréal (UK)

Valerie is a cybersecurity leader with expertise in digital transformation, risk and governance, information security, cloud services and business resilience with significant exposure in multiple industries. A highly motivated problem solver that excellently communicates technical issues and resolution to project teams, customers, stakeholders, and all levels of management.

At Loreal, Valerie is responsible for ensuring the implementation of the Company’s security strategy, providing assurance to the business, stakeholders, and customers covering UK & Ireland. She manages the overall Risk Management/Security in Projects, Compliance Management, Cybersecurity Awareness/Education, Resiliency, Technical & Professional competencies.

Valerie has contributed to the mentorship of young adults in Information Technology, a strong supporter of Women in Technology and has provided advice in areas of Governance, Risk and Compliance, digital transformation and Information Security Management System Implementation and Audit.

Dr Viktor Polic

Dr Viktor Polic

CISO, Head of Information Security and Assurance Services, ILO - United Nations (Switzerland)

More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences.

Sponsors

Qualys

Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.

For more information, please visit www.qualys.com

Ping Identity

Ping Identity is the Intelligent Identity solution for the enterprise. We enable companies to achieve Zero Trust identity-defined security and more personalized, streamlined user experiences. The Ping Intelligent Identity™ platform provides customers, workforce, and partners with access to cloud, mobile, SaaS and on-premises applications across the hybrid enterprise. Over half of the Fortune 100 choose us for our identity expertise, open standards, and partnerships with companies including Microsoft and Amazon. We provide flexible identity solutions that accelerate digital business initiatives, delight customers, and secure the enterprise through multi-factor authentication, single sign-on, access management, intelligent API security, directory, and data governance capabilities.

For more information, visit www.pingidentity.com

QinetiQ

QinetiQ is an integrated global security and defence company. Operating at the leading edge of science and engineering and employing over 6,000 people, including more than 3,000 scientists and engineers. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way.

Uniting our own and others’ technology and know-how to provide distinctive specialist services and products that address our customers’ most pressing challenges. We are integrated across the life cycle of critical equipment and infrastructure, undertaking creative research and development, enabling test and evaluation and delivering operational readiness through training and rehearsal.

Create it. Test it. Use it.

www.qinetiq.com/en/what-we-do/cyber

DTMRMrk Navy B

Unexpected events can radically affect people and operations. Organisations need an early and clear line of sight into developing situations, with additional context, to enhance decision-making as an incident unfolds. Dataminr is recognised as the world’s leading information discovery platform that delivers the earliest warning on high-impact events and emerging risks from public data sources, enabling more effective risk mitigation strategies, faster response, and stronger crisis management. Recently valued at B, Dataminr serves thousands of users spanning hundreds of multinational organisations including more than two-thirds of the Fortune 50 and half of the Fortune 100 companies, public sector agencies, NGOs, and over 650 newsrooms worldwide.

www.dataminr.com/pulse

Infosec K2K V1

Stay ahead of the ever-changing digital landscape with agile security solutions from Infosec K2K, a global leader in preserving the integrity of your sensitive data. Our team of on-demand IAM specialists offers tailored cyber solutions for organisations worldwide, available whenever and wherever you require them. While our comprehensive range of services includes vulnerability management and penetration testing to managed services and assessments, our core expertise lies in delivering customised Identity and Access Management (IAM) solutions.

In today’s rapidly evolving digital era, mastering IAM is essential to safeguard your systems and overcome the challenges posed by unpredictable shifts in demand. At Infosec K2K, we provide unparalleled security solutions tailored to your convenience. Our specialised resource hubs strategically located worldwide ensure that you receive 24/7 support from our cyber security experts.

We have earned a reputation for seamlessly adapting to the dynamic landscape of modern cyber security needs. As your trusted outsourced cyber experts, we take immense pride in offering our clients unmatched flexibility, optimised cost efficiency, international excellence with a local touch, and swift responses supported by superior assistance. In a world of fluctuating requirements and budgets, our team has developed a unique Pay-As-You-Go model to ensure that we support your needs whenever and wherever they arise, from project initiation to delivery and from peak periods to scaled-down project assistance.

www.infoseck2k.com

Bridewell

Bridewell is a cyber security services company that specialises in protecting and transforming critical business functions for some of the world’s leading organisations.

Their consultants work with clients to deliver end-to-end services that solve their security and business challenges. Bridewell’s specialists are highly accredited by major industry bodies and have extensive experience delivering services across cyber security, managed security, penetration testing, and data privacy.

Founded in 2013, Bridewell is headquartered in the UK where it runs a 24/7 Security Operations Centre (SOC) and has a growing presence in the US to further support global clients.

For more information, visit www.bridewell.com

Synopsys

Synopsys builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Our market-leading solutions help developers to secure code as fast as they write it; development and DevSecOps teams to automate testing within development pipelines without compromising velocity; and security teams to proactively manage risk and focus remediation efforts on what matters most. With Synopsys, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.

www.synopsys.com

Via Resource

Via Resource is one of the longest-standing specialist Information Security & Cyber Security recruitment agencies having been founded by Tor Macleod in 2010. Over the last twelve years, they have built a reputation on being experts in the Information & Cyber Security market and have developed unparalleled insight and expertise within the industry, not to mention a vast network of contacts and opportunities for candidates and companies. Via Resource’s USP is working solely in the Information Security, Cyber Security & Data Protection market. They have never moved away from this and never will, which creates a collaborative environment that provides greater opportunities for candidates to find their dream role or clients to find the right person for their business. Whilst they are niche, they do cover the full breadth of Information & Cyber Security including but not limited to; Governance, Risk & Compliance, Security Engineering, Security Architecture, Penetration Testing, Cloud Security, Application Security, Security Operations & SOC, Data Protection & Privacy and many more related areas. Via Resource has built a reputation for providing more than just contingent recruitment services. Whilst they have expertise in Permanent & Contract recruitment, they also spent the last twelve years developing their offerings in Executive Search and Consultant & Managed Services offerings, both of which are offered at the highest level within the industry. The team at Via Resource is built of consultants with in-depth Information & Cyber Security recruitment experience and boasts one of the most experienced teams in the industry, all of whom can provide more than just recruitment services, but aid candidates and clients acting as true consultants.

www.viaresource.com

KnowBe4

KnowBe4 is the world’s largest security awareness training and simulated phishing platform that helps you manage the ongoing problem of social engineering.

The KnowBe4 platform is user-friendly and intuitive. It was built to scale for busy IT pros that have 16 other fires to put out. Our goal was to design the most powerful, yet easy-to-use platform available.

Customers of all sizes can get the KnowBe4 platform deployed into production twice as fast as our competitors. Our Customer Success team gets you going in no time, without the need for consulting hours.

www.knowbe4.com

OneTrust Green Transparent

As society redefines risk and opportunity, OneTrust empowers tomorrow’s leaders to succeed through trust and impact with the Trust Intelligence Platform. The market-defining Trust Intelligence Platform from OneTrust connects privacy, GRC, ethics, and ESG teams, data, and processes, so all companies can collaborate seamlessly and put trust at the center of their operations and culture by unlocking their value and potential to thrive by doing what’s good for people and the planet.

Learn more at OneTrust.com.

Noname

The Complete API Security Platform

Proactively secure your environment from API security vulnerabilities, misconfigurations, and design flaws. Protect APIs from attacks in real-time with automated detection and response.

www.nonamesecurity.com/

Owanate Bestman

Owanate Bestman, founder of Bestman Solutions, has spent almost a decade recruiting in the Cyber Security field. Securing individuals and teams that meet specific technical and/ or leadership requirements for some of the world’s most innovative firms to the mutual benefit of individuals’ career progression and the company’s needs. www.bestmansolutions.com

BSS

BSS helps empower our clients to achieve business transformation success. We combine our proven industry talent expertise with effective and measurable project & service ownership and reporting. We work in partnership with our sister organisation (Barclay Simpson Associates) to ensure our advisory and project service flexibility utilises industry leading consultants, maintaining our overall strong position in the solutions market. Supporting our clients by providing comprehensive, outcome based engagements operated through a project services (Statement of Work) framework to ensure performance and delivery, BSS provides expertise in project and service outcomes across the following areas, please click on any listed service offering for more information: Project Engagement Services: Governance & Assurance; Cyber Security & Info Sec; Risk & Compliance; Audit.

www.bss.uk.com/

Risk Ledger Log

Did you know 60% of organisations have suffered a security breach through a third party? It’s understandable – the traditional processes are broken. Organisations face a burden of ineffective, inefficient admin. ‘Point in time’ cybersecurity assessments make for poor-quality data that goes out of date fast, offering little protection.

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

Interested in learning more? Visit https://riskledger.com/.

QO Blue

Our Continuous Controls Monitoring (CCM) platform is your single source of truth allowing you to see and understand your security and risk posture in real time. We connect to any data source, wherever that may be – on-premise, cloud or legacy to monitor any control and align to any industry framework or bespoke set of KPIs providing you with real time actionable intelligence through customisable reports.

This results in strengthened operational resilience with reduced cyber risk, assurance in critical data, continuous compliance and enhanced cyber resilience removing manual, point in time information gathering with quantitative risk analysis.

For security teams this means they can connect all their security tech to one tool for ultimate visibility to their cyber ecosystem as our platform is completely technology and environment agnostic. Having to report from multiple tools is eliminated and replaced by clear, actionable intelligence designed to your visual preference for Board or operational teams. It also means that security teams receive quantified, and evidence-based output, which is accurate, real time, objective and independent from any interpretation of data and judgement. Plus our service wrap ensures you can focus on the output and not another tool to manage.

The speed of delivery of that information is also key for cyber teams and thus provides early warning of potential security risks, incidents or controls degradation. Plus, our seamless integration means that we can connect to ticketing systems in ITSM tools when thresholds hit, or controls fail enabling automation from data gathering through to incident management.

Taking a holistic approach, the Quod Orbis CCM managed platform is positioned at the forefront of the CCM market. It is not just another new security tool, but a solution that brings together and maximises all of your IT investments.

www.quodorbis.com

Alfahive Cropp

Did you know 60% of organisations have suffered a security breach through a third party? It’s understandable – the traditional processes are broken. Organisations face a burden of ineffective, inefficient admin. ‘Point in time’ cybersecurity assessments make for poor-quality data that goes out of date fast, offering little protection.

Alfahive makes understanding cyber risk more meaningful. Our SaaS platform empowers risk managers with the technology to automate the assessment, quantification and prioritisation of cyber risks. It enables organisations to achieve efficiency gains and cost savings by automating their cyber risk management decisions.

www.alfahive.com

Seedata.io

Seedata.io is tackling the iceberg below the water; those attacks and breaches that run undetected for months (years, even) and fester into incidents that end businesses. Seedata.io uses a range of deception techniques to detect bad actors at the earliest opportunity.

Our SaaS platform automatically deploys an ever-changing collection of moving decoys inside and outside of your network. When unauthorized activity occurs, Seedata.io’s platform springs into action, analyzing the activity and alerting you directly into your existing security platforms.

This approach provides high-fidelity, in-network detection and generates actionable threat intelligence, sourced directly from adversaries targeting your organization.

www.seedata.io

The ISF

The ISF is a leading authority on information security and risk management. A not-for-profit organisation, we provide independent opinion and guidance on all aspects of information security. We deliver practical solutions to overcome the wide-ranging information security and risk management challenges that impact business.

For more information, visit: www.securityforum.org

ClubCISO

ClubCISO is a global community of ‘in role’ information security leaders working in public and private sector organisations, founded and funded by Telstra Purple. We are a community of peers, working together to help shape the future of the profession. We are a non-commercial organisation with over 700 members helping to define, support, and promote the critical role and value of information security in business and society. Through ClubCISO, members can build their networks, support and coach their peers, solve problems, and create practical guidance that moves the industry forward.

For more information, visit: www.clubciso.org

Dataminr

Dataminr is recognized as one of the world’s leading AI businesses. The company’s clients are the first to know about high-impact events and emerging risks so they can mitigate and manage crises more effectively. Dataminr solutions are relied on 24/7 by hundreds of clients in over 100 countries across six continents to help them solve real-world problems. Dataminr is one of New York’s top private technology companies, with over 800 employees across seven global offices.

www.dataminr.com

Qualys

Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.

www.qualys.com

Bridewell

Bridewell is a cyber security services company that specialises in protecting and transforming critical business functions for some of the world’s leading organisations.

Their consultants work with clients to deliver end-to-end services that solve their security and business challenges. Bridewell’s specialists are highly accredited by major industry bodies and have extensive experience delivering services across cyber security, managed security, penetration testing, and data privacy.

Founded in 2013, Bridewell is headquartered in the UK where it runs a 24/7 Security Operations Centre (SOC) and has a growing presence in the US to further support global clients.

For more information, visit www.bridewell.com

Censys

Censys is the leading Internet Intelligence Platform for Threat Hunting and Exposure Management. We provide governments, enterprises, and researchers with the most comprehensive, accurate, and up-to-date map of the internet to defend attack surfaces and hunt for threats. Censys scans 45x more services than the nearest competitor across the world’s largest certificate database (>10B), reducing the likelihood of a breach by 50%.

To learn more, visit censys.com

EVBG Full Color

Everbridge (NASDAQ: EVBG) empowers enterprises and government organizations to anticipate, mitigate, respond to, and recover stronger from critical events. In today’s unpredictable world, resilient organizations minimize impact to people and operations, absorb stress, and return to productivity faster when deploying critical event management (CEM) technology. Everbridge digitizes organizational resilience by combining intelligent automation with the industry’s most comprehensive risk data to Keep People Safe and Organizations Running™.

everbridge.com

QinetiQ

QinetiQ is an integrated global security and defence company. Operating at the leading edge of science and engineering and employing over 6,000 people, including more than 3,000 scientists and engineers. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way.

Uniting our own and others’ technology and know-how to provide distinctive specialist services and products that address our customers’ most pressing challenges. We are integrated across the life cycle of critical equipment and infrastructure, undertaking creative research and development, enabling test and evaluation and delivering operational readiness through training and rehearsal.

Create it. Test it. Use it.

www.qinetiq.com/en/what-we-do/cyber

Ovalix Black

The Ovalix platform provides companies with a clear view of their security process posture by visualizing and analyzing every step and action taken by the security teams. The platform reconstructs your actual processes, identifies and remediates security risks, and enhances efficiency, enabling supreme governance.

www.ovalix.io

KnowBe4

KnowBe4 is the world’s largest security awareness training and simulated phishing platform that helps you manage the ongoing problem of social engineering.

The KnowBe4 platform is user-friendly and intuitive. It was built to scale for busy IT pros that have 16 other fires to put out. Our goal was to design the most powerful, yet easy-to-use platform available.

Customers of all sizes can get the KnowBe4 platform deployed into production twice as fast as our competitors. Our Customer Success team gets you going in no time, without the need for consulting hours.

www.knowbe4.com

Thinkcyber Landscape Black Text Transparent Heavy

ThinkCyber deliver measurable secure behaviour change for their customers, empowering people to protect themselves against cyber threats. Their multi-award winning Redflags® Real-time Security Awareness software applies behavioural and learning science theory to deliver context-sensitive, just-in-time security guidance. For example, when users are about to click links, visit certain web pages, enter their username into a web page, handle attachments, etc.

Redflags® won the Teiss Awards for “Best Cyber Security Training & Awareness Product or Service” in 2024 and techUK Cyber Innovator of the year 2021; it was part of NCSC for Startups Programme and Accenture Fintech Innovation Lab 2022.

www.thinkcyber.co.uk

Picus Security

Picus Security is a leading Breach and Attack Simulation (BAS) vendor, enabling organisations  to test, measure and improve the effectiveness of their cyber security controls through automated and continuous offensive and defensive security testing. Picus’ complete security control validation platform challenges organisations’ cyber-security controls at prevention and detection layers by simulating over 10,000 threats and attack scenarios. This includes the latest types of malware and ransomware as well as MITRE ATT&CK techniques. Crucially, the Picus platform not only identifies defensive weaknesses as well as threat coverage and visibility gaps, it supplies content to help mitigate them too. This includes prevention signatures as well as detection rules for SIEM and EDR tools – removing the need for security teams to create and test their own. Unlike other tools and assessments, Picus enables security leaders to understand and measure an organisation’s cyber security posture at any moment in time. It provides insights into the impact of infrastructure changes and security improvements, and helps guide and prioritise future investment decisions. Gartner, which lists Breach and Attack Simulation as a Top Security and Risk Management Trend for 2021 has named Picus a ‘Cool Vendor’’. The company is cited by Frost & Sullivan as one of the most innovative players in the BAS market. Picus has hundreds of clients worldwide, with offices in EMEA, North America and APAC. Its technology partners include Cisco, IBM, Fortinet, Microsoft, Splunk and VMware.

www.picussecurity.com/

Risk Ledger Log

Did you know 60% of organisations have suffered a security breach through a third party? It’s understandable – the traditional processes are broken. Organisations face a burden of ineffective, inefficient admin. ‘Point in time’ cybersecurity assessments make for poor-quality data that goes out of date fast, offering little protection.

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

www.riskledger.com/

Hadrian From Background Removed

The hackers perspective

Defensive security should be validated by offensive security. Hadrian provides the hacker perspective, revealing the targets and methods that could be used in a real-world data breach. Hadrian’s continuous and comprehensive testing discovers and validates risks completely autonomously.

Hadrian’s platform combines attack surface discovery, automated penetration testing, and threat exposure management technologies in a cloud-based and agentless platform. The cutting-edge technology is constantly updated and improved by Hadrian’s in-house hacker team.

www.hadrian.io/

Thales

Thales is a global technology leader with more than 77,000 employees on five continents. The Group is investing in digital and “deep tech” innovations – Big Data, artificial intelligence, connectivity, cybersecurity and quantum technology – to build a future we can all trust.

In the markets of defence and security, aerospace and space, digital identity and cybersecurity, Thales provides solutions, services and products to help its customers – companies, organisations and governments – to carry out their critical missions.

www.thalesgroup.com

Contrast Security

Contrast Security, a leading application security vendor, offers a unified Runtime Security platform that ensures the security of critical web applications and APIs in market-leading companies. Contrast’s revolutionary technology enhances software to empower developers and protects against exploitation. Contrast’s mission is to democratize software security, enabling outstanding security outcomes for applications.

Our strengths

www.contrastsecurity.com

Threatlocker

The team at ThreatLocker® has been developing cybersecurity tools for decades, including programs to enhance email and content security, and this is our most innovative and ambitious cybersecurity solution yet. We developed this unique cybersecurity system because we believe that organizations should have complete control of their networks and should not have to live in fear of the next malware attack.

We envision a future in which all organizations can chart their own course free from the influence of cybercriminals and the damage their incursions cause, and our team of veteran cybersecurity professionals created ThreatLocker® to make this vision a reality.

www.threatlocker.com

Hack The Box

Hack The Box is the Cyber Performance Center with the mission to provide a human-first platform to create and maintain high-performing cybersecurity individuals and organizations. Hack The Box is the only platform that unites upskilling, workforce development, and the human focus in the cybersecurity industry, and it’s trusted by organizations worldwide for driving their teams to peak performance. Offering an all-in-one environment for continuous growth, assessment, and recruitment, Hack The Box provides solutions for all cybersecurity domains. Launched in 2017, Hack The Box brings together the largest global cybersecurity community of more than 2.8 million platform members. Rapidly growing its international footprint and reach, Hack The Box is headquartered in the UK, with additional offices in the US, Australia, and Greece.

www.hackthebox.com

BSS

BSS are a risk and cyber solutions provider that exists to solve problems. We believe the most successful projects, outcomes and service delivery come from good relationships, the right expertise and clear communications.

BSS provides cyber security solutions and services such as:

www.bss.uk.com

Owanate Bestman

Owanate Bestman, founder of Bestman Solutions, has spent almost a decade recruiting in the Cyber Security field. Securing individuals and teams that meet specific technical and/ or leadership requirements for some of the world’s most innovative firms to the mutual benefit of individuals’ career progression and the company’s needs.

www.bestmansolutions.com

Jericho Security

Jericho Security is a cutting-edge cybersecurity company on a mission to defend the world from the emerging threats of generative AI cyberattacks. Founded in 2023, Jericho Security protects organizations across various industries, such as governments, healthcare, insurance, and charities, from the unprecedented scale and volume of cyberattacks that only AI can unleash.

At Jericho Security, we’ve created our proprietary generative AI, CyberGPT, to simulate attacks, develop innovative defenses, and educate your teams on preventing severe cyberattack losses. Our unparalleled expertise in sophisticated analytics and top-of-the-line educational frameworks enables us to equip organizations with the tools and knowledge necessary to safeguard their digital assets effectively.

 As the cybersecurity landscape evolves, Jericho Security remains committed to staying at the forefront of innovation, leveraging the power of AI to combat increasingly sophisticated threats and ensure a safer digital future for all.

www.jerichosecurity.com

Mindflow

Mindflow is a no-code SaaS platform that enables all enterprise IT professionals to automate their repetitive tasks, reducing the strain on scarce employee development skills and strengthening governance.

www.mindflow.com

Gemserv

Gemserv is an expert provider of professional services and part of the Talan International Consulting Group.

As part of a dynamic global network, we offer combined capabilities in the areas of clean energy transition, cyber security, and wider innovation and transformation through technology.

This offers our clients greater scale and a broad range of capabilities to support the changing needs of their business and empower growth.

We offer purpose-driven impact driven by our mission to make things that matter work better for everyone.

www.gemserv.com

Intangic

Intangic is a cyber risk validation company. Built by world leaders in cyber and data science and validated by one of the world’s largest P&C insurers, Intangic continuously validates the size, cost and structure of large organizations’ cyber insurance programs. The company helps cyber risk programs work best when companies need them the most.

Intangic’s CyFi™ Dashboard gives risk and security teams the power of seeing cyber risk at a unique scale across all threat environments. This enables risk officers at large complex organizations more control to: 1. more accurately price of cyber premiums and determine correct size of coverage tower, 2. avoid losses through an early warning technology that provides risk and security teams with transparent, prioritized actions for detecting and preventing risks, and 3. increase ROI on risk programs by improving how cyber insurance cover is structured.

Alongside Founder and CEO Ryan Dodd, Intangic’s leadership team includes Dana Deasy, the former Chief Information Officer (CIO) of the US Department of Defense and former CIO and MD at JP Morgan Chase as well as Chris Key, the former Chief Product Officer at Mandiant, the worldwide market leader in threat intelligence and expertise gained on the frontlines of cyber security. The company has A+ rated capacity backed by AXA XL.

www.intangic.com

Social

https://www.linkedin.com/company/intangic/

https://www.linkedin.com/in/ryan-dodd-1b2b1857/

ISF Black Removebg Previewcrop

Founded in 1989, the Information Security Forum (ISF) is an independent organisation that is driven by its Members – ranging from Fortune 500 and Forbes 2000 listed corporations, to public-sector bodies and government departments.

Our business-driven solutions provide organisations with the guidance, tools and methodologies needed to tackle the wide-ranging governance, risk and compliance challenges impacting businesses around the world today.

www.securityforum.org

ISC2 Chapters

ISC2 Chapters are comprised of ISC2 members and non-members who are interested in the cybersecurity industry and profession, as well as advancing the ISC2 vision of inspiring a safe and secure cyber world. ISC2 Chapters provide members with opportunities to share knowledge, grow professionally, educate others, and collaborate on projects.

www.isc2chapter-germany.de

To enquire about Sponsorship opportunities for the 8th CISO 360 Global Congress 2024, please contact sponsorship@pulseconferences.com.


Who Joins?

By Designation

  • Chief Information Security Officer (CISO)
  • Chief Security Officer (CSO)
  • Director / Head of Cybersecurity
  • Director / Head of Cyber Threat Intelligence
  • BISO / CIRO
  • CTO, CIO, CRO
  • Chief Security Architect / Senior Security Architect
  • Director / Head of Security Infrastructure
  • Director / Head of Networks, Applications, Cloud
  • Director / Head of Technology Innovation
  • Director / Head of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer

By Sector – example

  • Financial Services – including Insurance
  • Energy – power, water and critical national infrastructure companies
  • Extractives – mining, oil and gas
  • Pharmaceuticals and health
  • Consumer goods
  • Manufacturing
  • Retail
  • Transport and logistics
  • Government departments
 

Registration details

Tier 1: Complimentary
For CISOs and Practitioners

Complimentary delegate Passes are available to book by CISOs and practitioners – i.e. persons who are doing the role of CISO, CSO, cyber threat intelligence professional, risk managers or other in-house executives roles.

*This offer does not apply to persons working in marketing, sales, business development or general management roles for companies providing advisory services or solutions to the security community.
Exceptions may apply for CISOs and senior practitioners working for these types of companies who are actually doing the day to day job of securing their organisation.

* Pulse Conferences reserves the right to approve that registration is under the correct tier. All Attendees at the event must be pre-registered online and pre-approved at the sole discretion of Pulse Conferences.

Registration is now closed

Tier 2: Advisory Pass
Fee: £2,000

We have set aside a limited number of Advisory Passes, designed for executives working at Providers, Vendors, Resellers, Distribution companies. Through this type of participation sponsorship, Executives can still benefit from the business development and promotional opportunity of attending even if their companies are unable to commit to a fully branded Sponsorship this year. This is an opportunity to send Executives to network with participants, to meet new prospective customers and to join the discussions – with a view to fuller sponsorship at future Pulse conferences!

Registration is now closed

Are you already a confirmed Speaker or Sponsor?

Please use the below button to register for the 7th CISO 360 Congress – Barcelona 2023 – only if you are a confirmed Speaker or if you company is a confirmed Sponsor.

Registration is now closed

Inclusions

  • Entry to 7th CISO 360 Congress and Roundtable, 5-7 July 2023
  • Invitation to join the confirmed networking events! Partners are welcome to join these (no cost)
  • Lunches and daily refreshments
  • Certificate of attendance soft copy provided post-event on request
  • Post-event presentation materials (subject to speaker opt-out) and output report
  • Loyalty programme membership for future events and invitation to bespoke community events in your city

Exclusions

  • Travel and accommodation and all other costs associated with planning for / joining the event

Worldwide Terms and Conditions

For purposes of these Terms “Attendee” shall mean all participant types at the event (Speakers, Sponsors, Delegates, Guests, Partners). By participating in this Event, you agree to these Terms.

Payment Policy

  • Payment is due in full at the time of registration. Inclusions and exclusions are listed. Your registration will not be confirmed until payment is received and may be subject to cancellation.
  • All ‘Early Bird’ Discounts must require payment at time of registration and before the cut-off date in order to receive any discount.
  • Any discounts offered whether by Pulse Conferences (including team discounts) require payment at the time of registration.
  • Discounts cannot be used in conjunction with other offers.
  • Methods of Payment:
  • Credit Card – All major credit cards are accepted online. Credit card details will not be accepted via email, phone or fax.
  • Bank Transfer – Please ensure when paying via Bank Transfer that the invoice number is referenced and a cop​y of the remittance is emailed tolindstrom@pulseconferences.com. All bank charges are to be borne by the sender.

Cancellation, Postponement and Substitution Policy

  • You may substitute a Delegate at any time by providing notice to Pulse Conferences. Please let us know the details of your replacement copied into an email introduction.
  • For cancellation of an in-person Delegate place, if a hybrid option exists, you will automatically be transferred to become a virtual Delegate.
  • No credit will be issued for any cancellations occurring within seven (7) days (inclusive) of the event. This also includes on the day cancellations, or Delegates who cannot stay for the event duration. Only a valid doctor’s note will entitle you to a 100% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit.
  • For any cancellations received in writing not less than eight (8) days prior to the event, you will receive a 90% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit. An administration fee of 10% of the contract fee will be retained by Pulse Conferences for all permitted cancellations.
  • For any cancellations received in writing not less than 60 (sixty) days prior to the event, you will receive a 100% credit to be used at another Pulse event which must occur within one year from the date of issuance of such credit. If the Delegate is unable or unwilling to attend another event, then you will receive 90% refund of the fee paid. All refunds will be processed within 2 weeks minus a 10% administration / transaction cost fee that will be retained by Pulse Conferences for all permitted cancellations.
  • Should Pulse Conferences postpone an event for any reason, you will receive a credit for 100% of the fee paid. You may use this credit either for the same event on the new date or for another event, which must occur within one year from the date of cancellation. If the Delegate is unable or unwilling to attend the new date or another event, then you will receive 100% refund of the fee paid.
  • Should Pulse Conferences cancel an event for any reason, you will receive a credit for 100% of the fee paid. You may use this credit for another event, which must occur within one year from the date of cancellation. If the Delegate is unable or unwilling to attend another event, then you will receive 100% refund of the fee paid.
  • Except as specified, no credits will be issued for cancellations. There are no refunds given under any other circumstances. Pulse Conferences is not responsible for any loss or damage as a result of a substitution, alteration or cancellation/postponement of an event.
  • Please note that Pulse Conferences reserves the right to alter or modify the advertised speakers and/or topics if necessary without any liability to you whatsoever. Any changes to the programme will be updated on our website.

Code of Conduct

Pulse Conferences events are intended for networking, collaboration and to provide inspiration amongst the security community. We generally assume that most people are intelligent and well-intended and we are not inclined to tell people what to do. Ensuring the positive and fulfilling experience of each participant in our community is our top priority. Accordingly:

  • All participants are expected to show respect and courtesy to others by abiding by this Code of Conduct to participate in our community.
  • Pulse is dedicated to providing an inclusive and harassment-free experience for everyone, regardless of gender, gender identity and expression, age, sexual orientation, disability, physical appearance, body size, race, ethnicity, national origin, religion (or lack thereof), or other choices.
  • We do not tolerate harassment of or threats (verbal or physical) to our community in any form. Sexual or discriminatory language and imagery is not appropriate for any of our events or for online media.
  • Community participants violating these rules may be sanctioned or expelled from current and/ or future events or venues at the discretion of Pulse Conferences, and without a credit or refund.
  • Pulse Code of Conduct applies during all hours of the event programme as well as the official networking receptions as these are also part of the event.

Please bring any concerns during the event to the immediate attention of our team by emailing teampulse@pulseconferences.com or by calling or texting +44 (0)203 455 9444.

Health and Safety

  • In-person events hosted by Pulse Conferences are organised in accordance with the latest health and safety regulations, guidelines, and recommendations, as directed by the Center for Disease Control and Prevention, World Health Organization, and the government of the host country of specific events. Working with its venues and suppliers, Pulse takes appropriate health and safety measures. Health and Safety measures for each event will be communicated online and in the specific event information that all registered Attendees receive.
  • Pulse Conferences also counts on your commitment. As an attendee, you agree to comply with the following measures:
    • Do not attend the event if you have been in contact with a person carrying covid-19 or suspected of having been infected, or if you are experiencing any symptoms of covid-19 at the time of the event
    • Respect the health and safety requests of Pulse Conferences ambassadors at the event
    • Acknowledge that participation in events and in-person activities brings some risk and you assume responsibility for your own well-being

Force Majeure

Pulse Conferences has the right to virtualise the programme, postpone the date or change the location of the event, if delay of performance is caused by circumstances or events outside of its reasonable control, which shall include but not be limited to industrial action, acts of God, terrorism, pandemic, power cuts or internet failure, civil commotion, refusals to grant licenses or permissions.

Indemnity

  • By registering, the attendee hereby indemnifies and holds Pulse harmless from and against any and all costs, damages and expenses, including legal costs, which are incurred by the client in such a scenario whereby the event is delayed, changed or virtualised due to circumstances outlined above in the force majeure. We advise booking travel or accommodation that is flexible or refundable.
  • In no event shall Pulse Conferences be liable for any claim, loss, liability, damage or cost to persons or property arising from attendee participation in this event.

Use of Multimedia

Attendees are encouraged to capture and their own event experiences in the permitted areas of the event venue, provided it does not defame other event attendees or infringe on copyrighted branding and content. Pulse Conferences leverages social media to post photos and videos to its social media feeds during the event.

By attending the Event, you acknowledge and agree that:

  • Pulse Conferences may edit and use the footage it captures at Pulse Conferences’ events for promotional activities in the course of its business. If you prefer not to be included in footage captured by Pulse Conferences, please let us know in writing before the event teampulse@pulseconferences.com or by calling +44 (0)203 455 9444. Or if you are onsite, you visit the Pulse registration desk upon your arrival. A unique badge will be provided for you.
  • Pulse Conferences disclaims all liability for the capture of your image by attendees in any multimedia format at the event (mobile recording devices).

Pulse Conferences Privacy Policy

To read about Pulse Conferences Privacy Policy and download in pdf format please click below.

Download Pulse Conferences Privacy Policy here

Venue and Accommodation

Hôtel Dieu Intercontinental Marseille

1 Pl. Daviel, 13002 Marseille, France
Read more here

The 8th CISO 360 Global Congress 2024 will be hosted at the Hôtel Dieu Intercontinental Marseille.

The epitome of luxury, the InterContinental Marseille-Hotel Dieu is located in Marseille’s historic Panier district. You can enjoy a pastis aperitif on the terrace with views of Notre Dame de la Garde Basilica before dining on Mediterranean dishes in the Michelin-starred Alcyone restaurant. Work out in the fitness room, swim in the indoor pool, or unwind with a treatment in the chic SPA by Clarins. Five minutes’ walk away, boats line the quay of the Vieux-Port, in the heart of the city. InterContinental Marseille offers two restaurants: the brasserie Les Fenêtres and the gastronomic restaurant Alcyone. Both feature breathtaking views of the Vieux Port and a selection of dishes incorporating the freshness of Provence.

Need Accommodation at the Event Venue?

Please call the Hotel Dieu Intercontinental, Marseille directly on +33 4 13 42 42 42 and ask for Clementine Carton.

Room categories and rates per night offered may vary – based on availability at the time of booking:

*Supplement of € 25.00 is applicable for a double/twin occupancy room.
Family room – € 345,00
Classic Harbour View room – € 455,00
Classic Harbour View Terrace room – € 515,00
Premium Harbour View – € 585,00
Junior Suite Harbour View – € 625,00
Premium Harbour View Terrace – € 665,00
Junior Suite Harbour View Terrace – € 705,00
Prestige Suite – € 1 025,00

Included in the rates:

– American buffet breakfast served in the Restaurant Les Fenêtres
– Complimentary high speed wireless connection (20 Mo)
– Free access to fitness centre (No reservation need)
– Free access to the indoor swimming pool (reservation required, available depending)
*City tax is an additional € 4.32 per person and per day

Alternative Accommodation Recommended – Close by in Marseille

*Special event rates are limited and only guaranteed pending availability at time of booking.
* Preferences of bed type and any other special requirements are subject to availability.

*Guests will have to provide own credit card information to guarantee their bookings.
*Security note: We do not use any 3rd party agencies to book accommodation on our behalf. All accommodation bookings should be made with the venue itself or with Pulse Conferences.

Mercure Marseille 4*
Non-Member Rate: Classic room only € 171.25 | Classic room with breakfast € 192.25
Member rate: Classic room only € 152.45 | Classic room with breakfast € 173.35
1 rue Neuve Saint Martin. 13001 Marseille
+33 4 96 17 22 22.
H1148@accor.com

11 min walk | 4 min taxi

Best Western Plus Hôtel La Joliette 4*
Single occupancy with breakfast € 166. Single occupancy without breakfast € 150.
49 Av. Robert Schuman, 13002 Marseille, France
+33 4 96 11 49 49
reservation@hotel-joliette.com

13 min walk | 5 min taxi

Best Western Hôtel du Mucem 3*
Comfort room with breakfast € 137. Superior room with breakfast € 152.
22 Rue Mazenod, Marseille, 13002 France
+33 491931313
reservation@hotel-mucem.com

13 min walk | 5 min taxi

Hotel Sofitel Marseille Vieux Port 5*
BOOKING FORM
Special rate: € 444.32 | £379.75 per night, per person including breakfast. Cut off date: 26 April 2024.
Minimum stay: minimum stay of 2 nights from 19 June – 21 June 2024.
36 Bd Charles Livon, 13007 Marseille, France
+33 4 91 15 59 00
sofitel.marseille@sofitel.com

27 min walk | 6 min taxi

Conference venue

The venue offers state-of-the-art meeting facilities complemented by expert catering and audio-visual resources.

The 8th CISO 360 Global Congress 2024 will be hosted in Ballroom featuring high-tech facilities and elegant high ceiling. Directly outside the ballroom is the foyer which will offer the ideal setting for our networking hub of the CISO 360 Congress where all coffee breaks will be hosted.

Location – 8th CISO 360 Global Congress

InterContinental Marseille -Hôtel Dieu
1 Pl. Daviel, 13002 Marseille, France
Read more

Marseille Fun Facts!

Marseille is:

  • said to be the sunniest city in France!
  • the second largest city in France (by its population)!
  • widely recognised as the home of French rap and hip hop, producing many of France’s leading rap artists and groups!
  • the oldest city in France! Founded by the Greeks around 600 BC, its rich history spans over 2,600 years, making it a treasure trove! Originally called Massalia, the city played an important role in the ancient world as a major center for trade and commerce. According to legend: a sailor marries a local Gauloise, whose father gave him Marseille as a wedding gift!
  • famous for its street art, which can be found all over the city, particularly in the Cours Julien neighbourhood. The city has a vibrant arts scene and is home to numerous galleries!
  • home to Olympique de Marseille, one of France’s most successful football clubs. The city’s Stade Vélodrome is the largest club football ground in France.
  • known for its unique dialect of French, Marseillese or Marseillais, famous for its distinctive accent and slang
  • known for its diverse cuisine that reflects its rich cultural mix. The signature dish is bouillabaisse, a traditional Provençal fish stew originating from Marseille. Also know for the “panisse”, a chickpea fritter, and the “navettes”, a type of sweet bread flavored with orange blossom!
  • home to traditional soap – Savon de Marseille – made in the city for over 600 years. Traditionally, the soap is made by mixing seawater from the Mediterranean Sea, olive oil and alkaline ash from marine plants in a large cauldron!
  • the location for numerous films and TV shows, including the French Netflix series named after the city. Its scenic locations offer a great backdrop for storytelling!
  • the birthplace of several famous personalities including footballer Zinedine Zidane, French rapper Soprano, and fashion designer Simon Porte Jacquemus!
  • designated a natural area of significant beauty! The Calanques National Park near Marseille is known for its stunning turquoise waters, white cliffs, and rich biodiversity!
  • home to the iconic Notre-Dame de la Garde basilica, a Catholic basilica that overlooks the city from its perch on a hill. The basilica is known for its stunning views and its statue of the Virgin Mary, which is said to protect the city!
  • Said to have been the inspiration for French writer Alexandre Dumas, who spent his childhood in Marseille!
  • home to the world’s largest commercial port, handling over 100 million tons of cargo every year. The port is a major hub for trade between Europe, North Africa, and the Middle East!
  • the vanity of the big cities and the sociability of the fishing villages! It is a city that locals love, or love to hate, and that foreigners love to discover beyond the French Riviera!

View video & image gallery from the 8th CISO 360 Congress – Barcelona 2023

View the highlights video from 7th CISO 360 Barcelona 2023 here

Day One Congress - Wednesday 5 July 2023

Day Two Congress - Thursday 6 July 2023

CISO 360 Roundtable - Friday 7 July 2023

CISO 360 Welcome Reception - Tuesday 4 July 2023

CISO 360 Catamaran & Dinner - Wednesday 5 July 2023 Sponsored by Qualys

CISO 360 Dinner Gran Villa Rosa - Thursday 6 July 2023

View image gallery from the 6th CISO 360 Congress 2022

View the 6th CISO 360 Video here

View Photos - Day one of Congress 6th July 2022

View Photos - Day two of Congress 7th July 2022

View Photos - Welcome By the Pool Reception, Tuesday 5th July 2022

View Photos - Boat Cruise Reception and Dinner, Wednesday 6th July 2022

View Photos - Cheese & Wine Tasting & Walking Tour of Old Geneva & Dinner, Thursday 7th July 2022

View gallery – 8th CISO 360 Global Congress – Marseille 2024

Gallery - Marseille 2024

View video and image gallery – 7th CISO 360 Congress – Barcelona 2023

Gallery and Video - Barcelona 2023

Day One Congress - Wednesday 5 July 2023

Day Two Congress - Thursday 6 July 2023

CISO 360 Roundtable - Friday 7 July 2023

CISO 360 Welcome Reception - Tuesday 4 July 2023

CISO 360 Catamaran & Dinner - Wednesday 5 July 2023 Sponsored by Qualys

CISO 360 Dinner Gran Villa Rosa - Thursday 6 July 2023

<h2><span style=”color: #000000;”>View image gallery from the 6th CISO 360 Congress 2022</span></h2>

View the 6th CISO 360 Video here

View Photos - Day one of Congress 6th July 2022

View Photos - Day two of Congress 7th July 2022

View Photos - Welcome By the Pool Reception, Tuesday 5th July 2022

View Photos - Boat Cruise Reception and Dinner, Wednesday 6th July 2022

View Photos - Cheese &amp; Wine Tasting &amp; Walking Tour of Old Geneva &amp; Dinner, Thursday 7th July 2022

Testimonials – Barcelona 2023

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Thomas Eeles, Security Operations Manager, Right Move

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
Kai Roer, CEO and Founder, Praxis Security

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Bev Allen, Head of Information Security, Quilter

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
Gary Penolver, CTO, Quod Orbis

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
Haydn Brooks, CEO, Risk Ledger

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Dr. Alex Jaimes, Chief Scientist and SVP of AI, Dataminr

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
Paul Baird, CTO UK, Qualys

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Jorge Fernandes, Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
Ibraheem Khan, VP Information Security EMEA, at a financial services firm

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
Jelena Matone, CISO European Investment Bank

Previous years’ testimonials – CISO 360 series
“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).” – Andreas Prass, CISO & DPO, 360 Treasury Systems AG, Germany

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.” – Carole Embling, Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” – Jorge Fernandes, CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.” – Matthias Muhlert Security Bear – CISO HARIBO, Germany

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!” – Viktor Polic CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.” – Richard Bloxam-Rose, Threat and Vulnerability Consultant, Computacenter, United Kingdom
“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” – Deborah Saffer, Global Deputy CISO, Cushman & Wakefield

“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions
“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim


“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” – Jonathan Armstrong, CEO, Cordery

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.” – Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK

“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World

“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP

“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica

“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“

Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh

— Holly Foxcroft (@holly_foxcroft) 21 June 2018

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO

— Viktor Polic (@ViktorPolic) 26 June 2018

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal

“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018

High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV

“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting

Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP
Testimonials CISO 360 Series

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”

CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”

CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”

CTO and Co-Founder, JIT (Israel)

“Great conference!  From the beginning, the level of participant engagement was very high.  The content was very informative and the presenters very knowledgeable.  Every aspect of Global CISO 360 was extraordinarily well done.  I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”

Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”

Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well.  Content and organization made this an excellent event!”

CISO, Infopercept (UK)

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”

Senior Account Executive, Hack the Box (Greece)       

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”

COO, Risk Ledger (UK)

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”

CEO and Founder, Praxis Security

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”

CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”

Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”

Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”

Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”

CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”

Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”

Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”

Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”

Director, Resilient. World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”

Technology Services Head of Cyber Security, DWP (UK)
“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”

Security Operations Manager, Right Move

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”

Regional Executive, KnowBe4 (The Netherlands)

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”

GemServ, a Talan Group company (UK)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”

CTO UK, Qualys

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”

Senior Consultant, DHC AG (Switzerland)

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”

Director of the Internal Control Office, Comiss
ão do Mercado de Valores Mobiliários

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”

VP Information Security EMEA, Northern Trust
“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”

CISO European Investment Bank

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”

CTO, Quod Orbis

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”

Chief Scientist and SVP of AI, Dataminr
“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”

CISO & DPO, 360 Treasury Systems AG, Germany

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”

CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”

Global Deputy CISO, Cushman & Wakefield

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –

CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” 

CEO, Cordery

“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy”

Senior Cybersecurity, Lafarge Holcim

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”

CMO, SailPoint

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”

Director, Bestman Solutions

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”

Director, Security, Laureate International Universities Malaysia

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP

“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica

“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!” Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”,

CISO, Channel 4

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV

“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations” Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Excellent conference, brilliantly put together.”
Director, Bridewell Consulting

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018

High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018

Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP