Thank you to everyone who participated in the 6th CISO 360 Congress, hosted 6-8 July 2022 at Hotel President Wilson, Geneva.
Cybersecurity Leadership and Resilience Strategies
Download Post-Event Materials *CISOs & Cybersecurity Practitioners onlyDownload the Post event report from 6th CISO 360 Congress 2022
CISO & DPO, 360 Treasury Systems AG, Germany
“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive!).”
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.“
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, UK
“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Add 7th CISO 360 Congress – 5-7 July 2023 to your calendar
On 6-8 July, against the stunning backdrop of Mont Blanc and Lake Geneva, the President Wilson Hotel in Geneva played host to strategic conversations with some of the most knowledgeable personalities in the cybersecurity industry from all over the world. Created and hosted by Pulse Conferences, the 6th CISO 360 Congress – Geneva 2022 brought together CISOs and international cybersecurity leaders – from practitioners to luminaries –to compare and share how they are leading teams and driving their businesses forward, as well as their visions for the future.
CISO 360 – Geneva 2022 follows recent successes in Barcelona, Lisbon, Rome and Windsor. View highlights and video testimonials here from the previous CISO 360 Congress, hosted in Windsor last year and see what 2022 holds – www.ciso360congress.com.
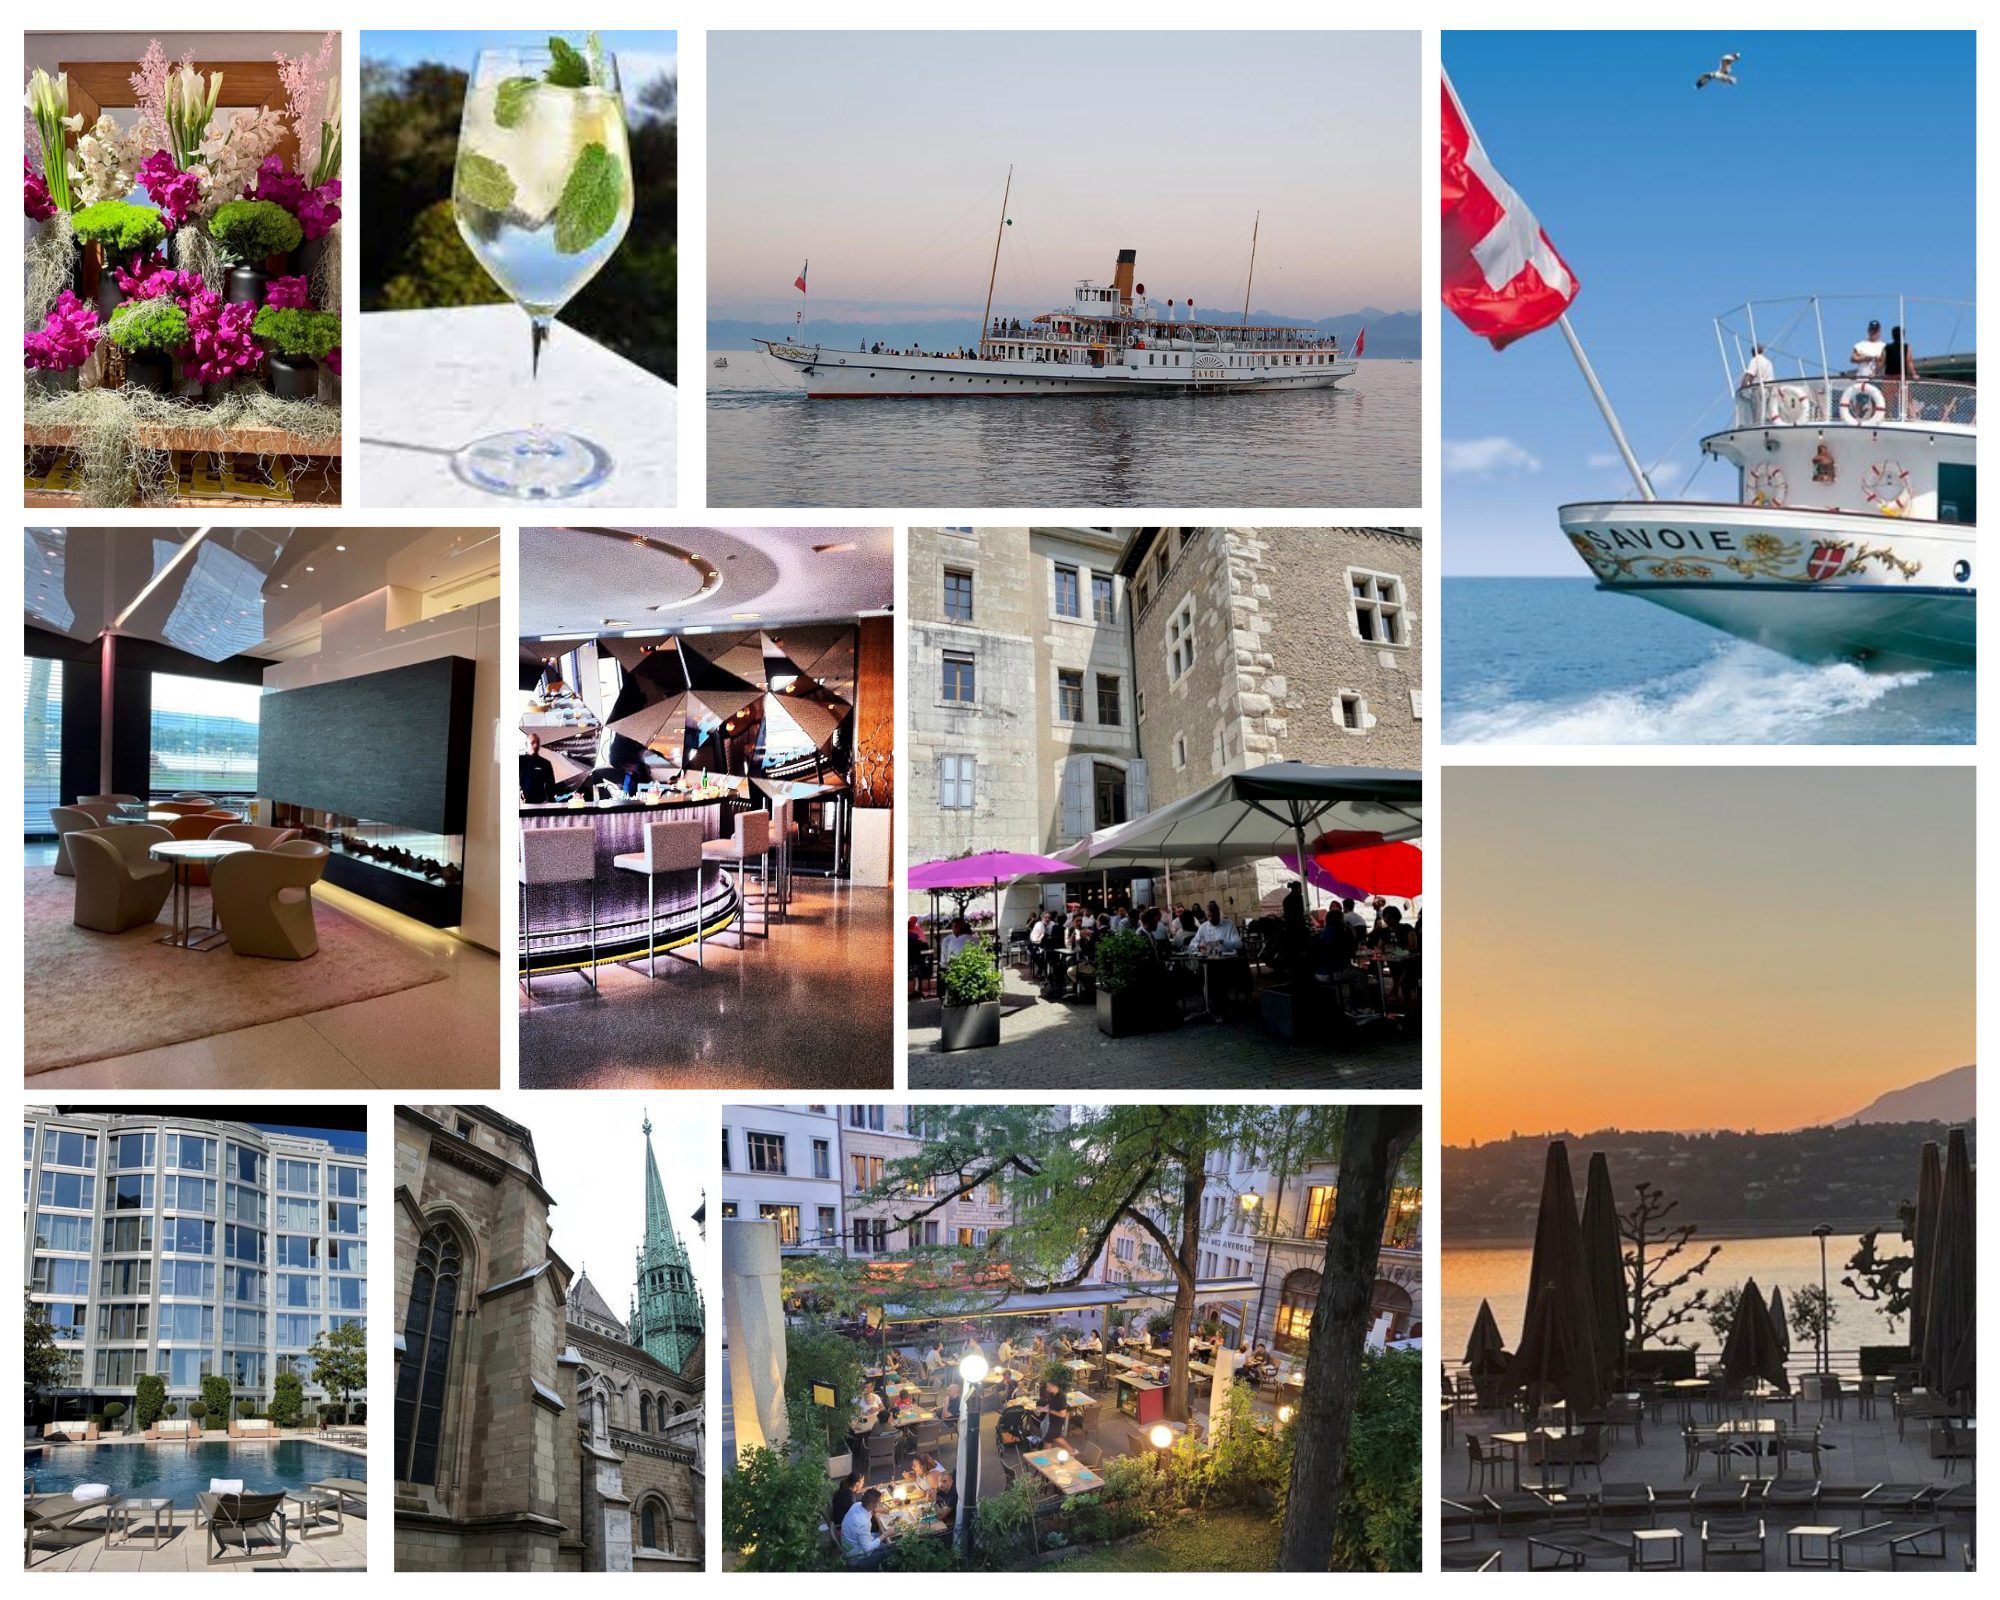
Through keynote lightning talks, case uses, panels, think tanks, fireside chats and during the evening networking receptions, dinners, and a boat cruise, we got to know and challenge ideas. We heard what plans CISOs are making, what drives them and where their journeys are heading. We benchmarked cybersecurity strategies, tactics and tools with peers and we experienced unrivalled learning and engagement. The journeys, predictions and game-changers spanned cloud computing, cyber in geopolitics, supply chain, detection, response and recovery, human security and culture, privacy, IoT, AI, SOC – plus breaking cybersecurity news – during this two and half day interactive programme.
- Connect, innovate and leave inspired. Sit with peers who you know are largely facing a similar set of risks and opportunities
- Benchmark in a trusted space with fellow CISOs, practitioners and for meeting technology luminaries
- Learn from business executives, risk managers and technology luminaries outside the security ‘echo chamber’
- Engage in meaningful interaction with CISOs, innovators, investors and luminaries to collaborate
Pulse would like to say a heartfelt thank you to the International Speaker Panel – Geneva 2022
Keynote Speakers
- Col. Gérald Vernez, Founder and Director, digiVolution Foundation (& Former Cyber Defense Chief, Swiss Armed Forces) (Switzerland) – provisional
- Michael Colao, Global Chief Underwriting Officer – Direct and Indirect Cyber Risks, AXA XL (UK)
- Meyli Chapin, Founder and CEO, Trauma Brace (U.S)
- Sounil Yu, CISO & Head of Research, JupiterOne (U.S.)
CISOs and Senior Practitioners
- Allen Ohanian, CISO, Los Angeles County (U.S.)
- Alan Jenkins, Interim CISO, NED & Mentor (UK)
- Alyssa Miller, Business Information Security Officer (BISO), S&P Global Ratings (U.S.)
- Barry Coatesworth, Director Cyber Security, risk and Compliance, Guidehouse & Recently Advisor, Scottish Power Renewables (UK)
- Bev Allen, Head of Infosec Assurance / CISO, Quilter (UK)
- Carole Embling, Information Security Manager – Awareness & Behaviour Change, Metro Bank (UK)
- David Young, Head of Information Security, Tesco Bank (UK)
- Dimitri Chichlo, Independent Non-Executive Director, JSC Ukreximbank; CEO and Owner, AndSecure (Switzerland/Ukraine)
- Gadi Evron, CISO-in-Residence, Team8, Chairman of the Board, Israeli CERT (Israel)
- George Eapen, Global CIO and CISO, Petrofac (UAE)
- Graham Edwards, Most Recently Head of Cyber Security, Yorkshire Water (UK)
- Ian Amit, Former CSO, Cimpress and Hunters (U.S.)
- Ibraheem Khan, Senior Information Security Officer, Channel 4 & Head Chair, National Cyber Security-MCBIE (UK)
- Jelena Matone, CISO, European Investment Bank (EIB), President, Women Cyber Force (Luxembourg)
- Jeff Schiemann, CISO, A Large Crypto Bank (Switzerland)
- Julia Harris, Information Security Assurance and Compliance Director, Flight Centre (UK)
- Nick Gerteisen, Deputy CISO, Smith + Nephew (U.S.)
- Dr. Abdullah A.I. Alnajem, International Cybersecurity Expert and Inventor (Saudi Arabia)
- Matthias Muhlert, CISO, HARIBO (Germany)
- Owais Ahmed, Senior Associate Director – Information Security Officer & Data Protection Officer, Mizuho Bank Europe N.V. (The Netherlands)
- Dr Runli Guo, CISO, Gett (UK)
- Paul S. Raines, Chief Information Security Officer, United Nations Development Programme (U.S.)
- Peter Ling, VP Global Cyber Security Alliances, Mastercard (Canada)
- Sandip Wadje, Global Head of Technology Risk Intelligence, BNP Paribas (UK)
- Samuel Ubido, Information Security Manager, Uniper (UK)
- Simon Riggs, CISO and IT Risk Officer (Interim), McKesson (UK)
- Xander C.W. Heemskerk, Director Product Security – Group Security, Philips (The Netherlands)
- Thomas Murphy, Strategic Intelligence Manager, Dragonfly (UK)
- Dr Viktor Polic, CISO, International Labour Organization (ILO) – United Nations (Switzerland)
Luminaries and Strategists
- Aubrey Turner, Executive Advisor, Ping Identity (U.S.)
- Bernard Montel, EMEA Technical Director and Security Strategist, Tenable (France)
- Dr Eduardo Solana, Senior Lecturer of Cryptography and Security, University of Geneva (Switzerland)
- Elizabeth Hodges, Security Specialist, Telstra Purple (UK)
- Craig Cooper, Chief Operating Officer, Gurucul (U.S.)
- Gerald Crescione, Lead Programme Manager, Snyk (France)
- Grant Revan, Head of Strategic Engagement, Red Sift (UK)
- Jonathan Luff, Co-Founder, CyLon (UK)
- Nathan Green, Sr. Subject Matter Expert: Cyber & Dark Web, Dataminr (U.S.)
- Manoj Bhatt, IT Principal Lead, Telstra Purple (UK)
- Marcus Alldrick, CISO Luminary (Former CISO and DPO, Lloyd’s of London) (UK)
- Michael Strobl, Senior Engineer, SecurityScorecard (Germany)
- Lucas von Stockhausen, Senior Director of Security Engineering – International, Synopsys (Germany)
- Lady Olga Maitland, President and Chairman, Defence and Security Forum (UK)
- Paul Baird, Chief Technical Security Officer (CTSO), Qualys (UK)
- Paul Kennedy, Head of Cyber Advisory, QinetiQ (UK)
- Paul Squires, Lead Identity Strategist, SailPoint (UK)
- Ray Stanton, Global Partner, IBM (UK)
- Robert D. Rodriguez, Chairman & Founder, SINET & Venture Partner, SineWave Ventures (U.S.)
- Prof. Dr. Robert Coles, Board Director/Governor, University of Brighton (UK)
- Dr Sally Leivesley, Managing Director, Newrisk Limited (UK)
- Stephen Cavey, Co-founder & Chief Evangelist, Ground Labs (Singapore)
- Tim Ward, CEO, Think Cyber (UK)
- Torquil Macleod, Director, Via Resource (UK)
Networking Agenda at a Glance
Tuesday, 5 July – Welcome Reception
19:00-21:00 Welcome By the Pool Reception – Terrace, President Wilson Hotel. Fly in and join this crucial ice-breaker! Kindly sponsored by Team8
Wednesday, 6 July – CISO 360 Congress Day 1
08:00-08:30 Coffee and Registration
08:30-17:30 Congress. 12:30-13:30 Lunch Kindly sponsored by ABS Group
18:00-18:30 Meet Up Drinks Glow Bar President Wilson Hotel. Group walks to the pier
19:00-22:20 Boat Cruise Reception and Dinner – Lake Geneva. Kindly sponsored by Qualys
Thursday, 7 July – CISO 360 Congress Day 2
08:30-08:55 Welcome Coffee
09:00-17:30 Congress. 13:00-14:00 Lunch Kindly sponsored by ABS Group
18:00-20:15 Cheese and Wine Tasting and Walking Tour of old town Geneva. Kindly sponsored by Mastercard
20:15-22:30 Dinner – Café Papon. Kindly sponsored by Red Sift
Friday, 8 July – CISO 360 Roundtable (Morning only)
09:00-12:30 Roundtable Discussion. Topics are based on CISO priorities input in advance.
12:30-13:30 Lunch on the Terrace and Goodbyes
Pulse Conferences would like to thank everyone who participated, in-person or virtually in our 5th Annual CISO 360 Congress, 7-8 July 2021 that was hosted near Windsor in the UK.
View recent highlights, testimonials and materials!
Testimonials 5th CISO 360 Congress - July 2021
Recording, Photos, Videos - 5th CISO 360 Congress - July 2021
We are delighted to welcome our 2022 Sponsors to date!
Platinum - Boat Reception & Dinner Sponsor
Platinum - Cultural Networking Sponsor
Platinum - Welcome By the Pool Sponsor
Platinum Sponsors
Gold & Dinner Sponsor
Gold Sponsors
Silver Sponsors
Lunch Sponsor
Exhibition Sponsor
Many thanks to Supporting Associations!
Gallery – 6th CISO 360 Congress
Day one of Congress
6th July 2022

6th CISO 360 Congress 2022 video
With thanks to our sponsors
Sponsors
Speaker Bios – 6th CISO 360 Congress, Geneva 2022
Download Programme 2022
Chaired by
Marcus Alldrick, CISO Luminary
Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services.
Keynotes
Meyli Chapin, Founder and CEO, Trauma Brace (U.S.)
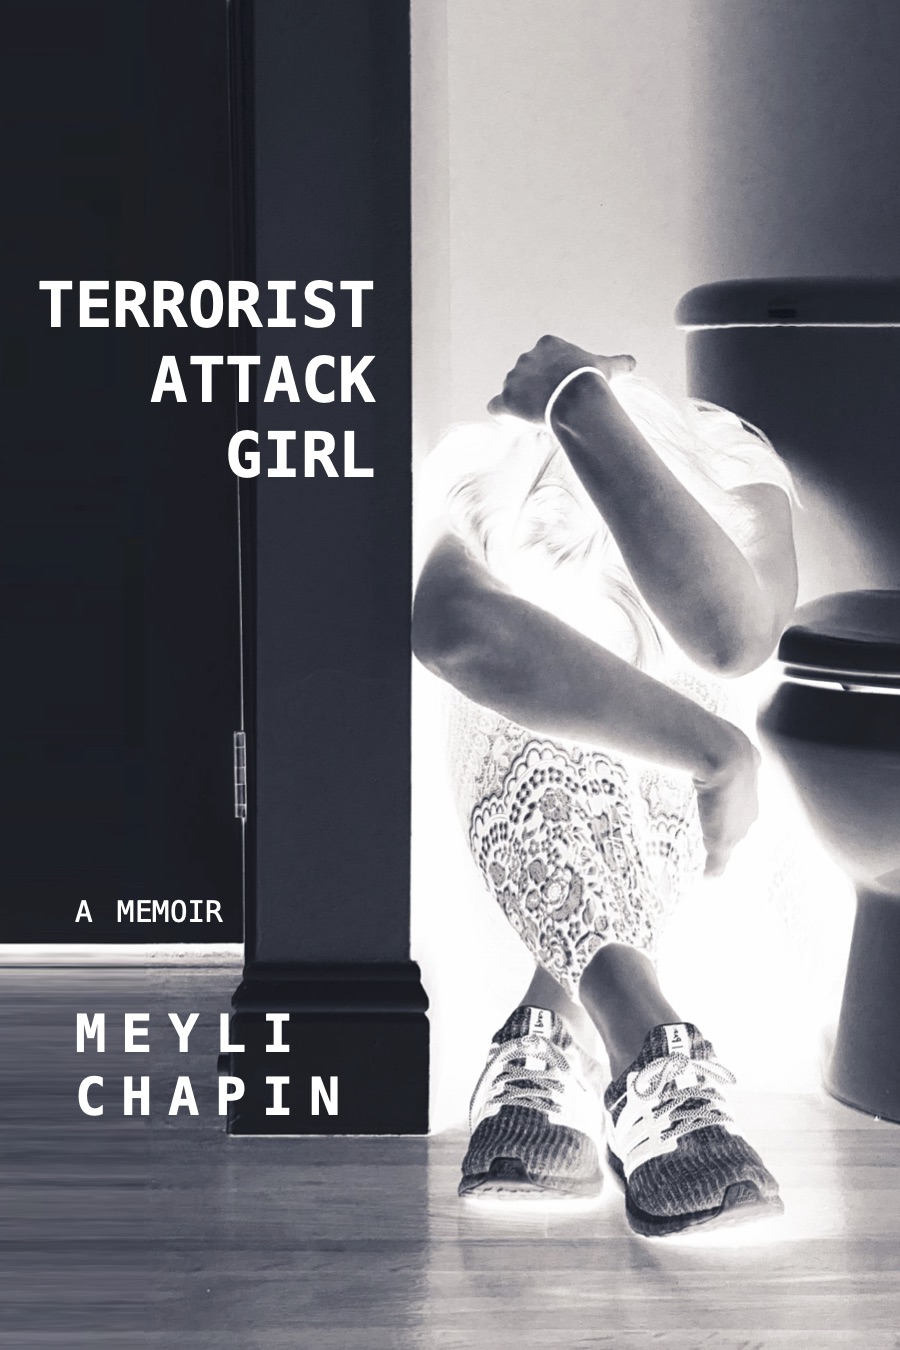
Meyli is a Stanford graduate whose career has spanned consulting and technology, first at Bain and then Google. After spending 17 hours in a terrorist attack while traveling for business, she dealt with heavy fallout in the form of PTSD. Once having overcome PTSD herself, she began to focus on helping others heal. She created an app called Trauma Brace that is actively treating PTSD sufferers across the globe. As the CEO of Brace, Meyli oversees Research and Development, Product Implementation and Marketing. She has also published a book about her experience, called Terrorist Attack Girl, and she often speaks about the intersection between mental health and technology.
“In January of 2019, I was trapped in a hotel room in the DusitD2 in Nairobi for 17 long hours while Al-Shabaab terrorists attacked the property. I was completely alone and certain I was going to die. However, thanks to the incomprehensibly brave men who fought to get us out, led by now-retired SAS operator Christian Craighead, hundreds of us were extracted to safety. After the attack, though, PTSD made me so miserable that I started to wish I had died after all. Aside from the terrorist attack itself, PTSD is the hardest thing I have ever dealt with in my life. So many of us know those stories about extraordinary resilience. Or at least we think we do. But what we usually know is actually just a tiny fraction of the story, a beginning and an end: This person went through something terrible, and now they are amazing. This story is the middle. It’s the nightmares and the flashbacks and the million times I wanted to quit trying, at therapy, at relationships, at life. It’s the dark, ugly truth that we usually try to keep locked away because it’s so painful and embarrassing to drag it into the light. But I wanted to pay tribute to all the other people who are struggling or who have ever struggled. And the only way to do that is to tell the whole truth, middle included, and offer that little bit of empathy, and the flicker of hope. The tunnel may be incredibly long, it may feel bleak and gruelling and insurmountable, but at the end of it, there is light.”
Sounil Yu, CISO and Head of Research, JupiterOne (U.S.)
Sounil Yu is the CISO and Head of Research at JupiterOne. He created the Cyber Defense Matrix and the DIE Triad, which are reshaping approaches to cybersecurity. He’s a Board Member of the FAIR Institute; co-chairs Art into Science: A Conference on Defense; is a visiting fellow at GMU Scalia Law School’s National Security Institute; teaches at Yeshiva University; and advises many startups. Sounil previously served as the CISO-in-Residence at YL Ventures and Chief Security Scientist at Bank of America. Before Bank of America, he helped improve information security at several Fortune 100 companies and Federal Government agencies. Sounil has over 20 granted patents and was recognized as one of the most influential people in security in 2020 by Security Magazine, Influencer of the Year in 2021 by SC Awards, and a 2021 Top 10 CISO by Black Unicorn Awards. He has an MS in Electrical Engineering from Virginia Tech and a BS in Electrical Engineering and a BA in Economics from Duke University.
Michael Colao, Global Chief Underwriting Officer – Direct and Indirect Cyber Risks, AXA XL (UK)
Experienced CSO/CISO with than 20 years experience in financial services. Has a strong side-interest in computer forensics and in the management of digital evidence. Graduated from the Massachusetts Institute of Technology (MIT) in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services primarily in London.
International Speaker Panel 2022
Alan Jenkins
Independent Trusted Advisor, Interim CISO, Principal Consultant, NED & Mentor (UK)
Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.
Allen Ohanian
CISO, Los Angeles County (U.S.)
Mr. Ohanian is the Information Security Officer for Los Angeles (LA) County Department of Children and Family Services (DCFS), the largest child welfare institution in the nation. He has 20 years of experience in information technology, cybersecurity and defense strategies, risk management, forensics, privacy, compliance, cloud security, business continuity, and software engineering in the private and public sectors. Before DCFS, he served as the first Information Security and Privacy Officer at LA County Counsel. He established an Information Security and Privacy program and ensured compliance with legal mandates.
As a scholarly-practitioner, visionary, and innovative Information Security Officer, Mr. Ohanian has architected and implemented cybersecurity and privacy programs from the ground up, interwoven cybersecurity into the business culture, creating a security-conscious enterprise, and assertively achieved the organization’s mission of service excellence through outstanding leadership, governance, strategic planning, business acumen, and cost-saving transformation initiatives.
Mr. Ohanian is an active member of various Cybersecurity taskforce and workgroups, leads and oversees the Countywide Risk Management Cybersecurity Team responsible for developing and implementing administrative, technical, and tactical strategies to assess and reduce cybersecurity risks to County information assets.
Mr. Ohanian has been a keynote speaker and panel member in numerous private and public sector conferences. He is a Ph.D. Dissertation Committee Member for Cybersecurity using Artificial Intelligence at Center for Information Systems & Technology Claremont Graduate University.
Mr. Ohanian has a Bachelor’s degree in Computer Science from Cal Poly Pomona (magna cum laude) and obtained his dual Master’s Degree in Cybersecurity and Business Administration at the University of Maryland (UMUC). He is currently pursuing a Ph.D. in Industrial/Organizational Psychology program.
Alyssa Miller
Business Information Security Officer (BISO), S and P Global Ratings (U.S.)
A life-long hacker and highly experienced security executive, Alyssa Miller has a passion for security which she advocates to fellow business leaders and industry audiences both as a high-level cyber security professional and through her presence in the security community. She blends a unique mix of technical expertise and executive experience to bridge the gap that can often form between security practitioners and business leaders. Her goal is to change the way we look at the security of our interconnected way of life and focus attention on defending privacy and cultivating trust.
Alyssa has always had a driving curiosity to understand how technology works and how existing technologies can be hacked to function in new ways. At the young age of 12, Alyssa got her start by taking a job as a paper carrier to save up enough money to buy her first computer. From the time she brought that computer home from Best Buy, she has taught herself new skills and pushed the capabilities of digital technologies.
A native of Milwaukee, Alyssa began her IT career as a programmer for a Wisconsin based provider of financial software and services. Her passion for security quickly shaped her career as she moved into a leadership role within the ethical hacking team, conducting penetration testing and application assessments along with her team.
Later, Alyssa would expand her view of the security industry by moving into consulting. With her programming background, Alyssa was able to focus her efforts on Application Security. Her continued role as a leader in multiple consulting organizations allowed her to work with high level business leaders to address security at a strategic level.
Today, Alyssa directs the security strategy for S&P Global Ratings as Business Information Security Officer (BISO), connecting corporate security objectives to business initiatives. Additionally, she shares her message about evolving the way people think about and approach security, privacy and trust through speaking engagements at various conferences and other events. When not engaged in security research and advocacy, she is also an accomplished soccer referee, guitarist and photographer.
Aubrey Turner
Executive Advisor, Ping Identity
Aubrey Turner has extensive background successfully delivering strategic, enterprise cyber security solutions to Fortune 1000 companies that addresses business problems, strengthens organizations, reduces risk and delivers positive business outcomes. Aubrey has demonstrated rapport and consensus building with key stakeholders. Additionally, he has proven leadership, communication, management, collaboration and sales skills. Aubrey’s background is comprised of the following:
- 20 years of cyber security experience comprising
- Over 12 years in identity access management starting in the early 2000’s through the present (Deloitte/FishNet Security/Optiv/Ping Identity)
- Five years of experience in data security (governance/DLP) and privacy
- Multi-domain experience also includes risk management, BCP/DRP, network/software security, application security, threat and vulnerability management
- 20 years of customer facing strategic advisory consulting, implementation and solution sales experience
- Experience covering financial services, healthcare, retail, software, telecom and other sectors
- Hold the following certifications: CISSP, CIPP, CISA and CRISC
Barry Coatesworth
Cyber Security Advisor, Scottish Power’s Offshore Renewables & Director, Cyber security, Risk and Compliance (UK)
Barry has over 30 years’ experience in energy, finance, public sector and is an internationally recognized cyber security expert and advisor. Most recently, Barry was the Cyber security advisor for Scottish Power’s Offshore renewables, where he was responsible for the security management, operations and maintenance of their European offshore windfarms, working with multinational teams primarily in the UK, Germany and Spain. He was also part of the Industry Advisory Group for the Cyber Essential Scheme in conjunction with UK’s Department of Business, Energy and Industry Strategy; and as are research advisor to the Parliamentary Office of Science and Technology(POST) on Big data, Ethics and privacy. He has also written a number or articles and is currently working on two forthcoming books.
Bernard Montel
Technical Director EMEA / Security Strategist chez Tenable (France)
Bernard has a Master of Science in Computer Science (Diplôme d’ingénieur), Computer, Network, Security, Artificial Intelligence from
Aix-Marseille University
Aix-Marseille University.
He is passionate about new technologies and Cyber Security.
Bev Allen
Head of Information Security Assurance / CISO, Quilter (UK)
Bev Allen is an information security professional with more than 30 years of experience in delivering operational and strategic privacy, information security and information risk management, including the development and delivery of security and privacy policies, standards, and security training, in a variety of culturally diverse organisations and industries. Currently working with tools to analyse and produce data-based metrics and management reporting, using that data to measure and monitor control performance and gaps, underpin and drive corrective action for security control failures, and to support information security assurance reviews.
Carole Embling
Information Security Manager - Awareness & Behaviour Change, Metro Bank (UK)
Carole has worked in the world of Information Security since the turn of the century, first in Royal Mail as the Compliance, Communications and Awareness manager for the whole Group, having spent the 20 years ‘learning the business inside out’. She then spent 6 years at Prudential Group Head Office working on group-wide Information Security compliance. Carole then worked at BMJ Publishing Group as their Information Governance and Data Protection Lead. She joined Metro Bank in May 2019 as Information Security Manager – Awareness and Behaviour Change.
David Young
Head of Information Security, Tesco Underwriting (UK)
David is an Information Security and Risk specialist with over 20 years experience in both first and second line functions in information security, incident management, audit and risk in the financial services sector and leads the IS function having had senior IS management roles in other financial services companies. Specialities: Information Security direction and management, Audit, Assurance and Risk management, Incident Management and Investigations, Stakeholder Management and Contractual negotiation. Prior to his current role, David was
Senior Manager, IT Security at the
Bank of England, m
anaging and running the teams that provide critical security services to the Bank to manage its security posture to support all Bank staff in their duties. He was
Senior Information Security Manager, Head of IS Policy with
Direct Line Group.
Dimitri Chichlo
Independent Non-Executive Director, JSC Ukreximbank and CEO and Owner, AndSecure (Switzerland/Ukraine)
A French and Swiss citizen, Dimitri Chichlo started his career in Ukraine in 2004, then moved to Switzerland in 2009, working mainly for international financial institutions in the fields of operational risk and cybersecurity. In 2017, he completed an Executive MBA at INSEAD. In 2019, he joined the Supervisory board of Ukreximbank, the third largest and State-owned bank in Ukraine, as vice-chairman and chair of the Operations and Digital Committee. In 2020, he founded his consultancy practice in cybersecurity and digital transformation, AndSecure. Since February 24th, 2022, he is actively involved into providing humanitarian support to Ukraine. He currently lives in Geneva.
Dr. Eduardo Solana
Senior Lecturer of Cryptography and Security, University of Geneva (Switzerland)
Dr. Eduardo Solana is Senior Lecturer of Cryptography and Security at the University of Geneva. Amongst others, he has worked for IBM and PricewaterhouseCoopers where he was Global Subject Matter Expert for authentication solutions. He has twenty five years of experience in the fields of cryptography and information security both in the private sector and the academia. Dr. Solana is a deeply experienced security practitioner, technical writer and regular speaker at the most relevant conferences and symposia in the field. During his extensive career, he has provided consulting services to multinational organizations and states in security related issues.
Elizabeth Hodges
Specialist, Telstra Purple (UK)
IT and cyber security became my unavoidable destiny after falling into this world post-degree. Whilst my knowledge back then extended to ‘you need to shake the mouse to wake your PC up’, I am pleased to say that my 8 years in the industry have seen me come a long way!
Having started at a Chinese SaaS company I was quick to learn about cultural differences, never more so than when I was placed in Copenhagen with a team of Chinese colleagues with pressured and ambitious deadlines. I was defiant in proving that this would be an important experience. I embraced the international cuisine and work ethic and after a rather dubious taxi ride across Shanghai that I would sooner rather forget – I was confident that I had ticked the ‘try different foods’ bucket list box!
Gadi Evron
CISO-in-Residence, Team8 (and Founder, The Israeli CERT) (Israel)
Prior to joining Team8, Gadi held a number of senior positions in the cybersecurity field, and was the founder and CEO of Cymmetria, a startup that develops cyber deception solutions. He also managed the security system for Tehila, Israel’s e-government unit. In addition, Gadi held prominent cyber roles at Citi, PwC, and worked with the World Economic Forum. He founded and managed a number of industry organizations, including the The Israeli CERT and the Art into Science cyber defense conference, and is the author of two books on cybersecurity.
George Eapen
Global CIO and CISO, Petrofac (UAE)
Currently serving as Group CIO of Petrofac (FTSE 250) and In this remit, i am leading the Digital transformation of the Company, building best in class Cyber capabilities and develop Digital products to deliver better business outcomes for Customers . I am also driving the Cloud transformation program in the Company where we are upgrading our technology landscape (1000+ Applications) and also implementing ERP Fusion Cloud. I am leading a Global team of 500 IT professionals to support a global work force of 12000 employees based across US to Asia Pacific.
Before joining Petrofac, i spent 13 years with General Electric (GE) where I had an accelerated and diverse career with experience in multiple international executive leadership roles in Cybersecurity, Digital transformation and Technology space. My most recent role at GE was heading Cybersecurity practice for GE International regions ($60B revenue) as a CISO with a team of 100 employees.
George is a graduate of GE IT leadership program (ITLP), GE Six Sigma Black Belt program and graduate of GE Corporate Audit Staff (CAS), a fast track Executive leadership program of GE
George is an International speaker on multiple Cyber Security conferences including IBM Think 2020, Microsoft Ignite 2019, RSA 2022.
George is also Board of Advisor for IBM Security, Continuity Software and Seed Group.
Gerald Crescione
Lead Programme Manager, Snyk (France)
A former entrepreneur in the Cloud Native space, Gerald Crescione is one of the founders of the open source driftclt tool, and recently joined the DevRel team at Snyk, leading Program Management and the active community of Snyk Ambassadors.
Gérald Vernez
Founder and Director, digiVolution Foundation (Switzerland)
Gérald Vernez studied geology, meteorology and then security policy. After a first career as an engineer and risk manager in industry, he joined the General Staff of the Swiss Armed Forces in 1996. He prepared and trained the Federal Crisis Staff for the Y2K problem, planned the Command & Control organization of the armed forces and developed the Information Operations area. In 2009 he became Chief of Staff of the Armed Forces Joint Staff and in 2011 Deputy Director for the development of the first national strategy for the protection of Switzerland against cyber risks. As the Chief of the Armed Forces’ delegate for cyberdefence since 2013, he planned and coordinated the development of this area. In 2016, while leading the task force that managed the cyberattack against RUAG, he became the DDPS delegate for cyberdefence for which he developed and implemented the first cyberdefence action plan in 2017, ensured its revision in 2018, and then led the development of the new strategy in force since 2021. Expert and trainer in security policy for our digitally mutating society, Gérald Vernez is founder and director of the digiVolution Foundation (www.digivolution.swiss), a new force for strategic thinking and action created at the end of 2020.
Graham Edwards
Most Recently Head Cyber Security, Yorkshire Water (UK)
A successful senior Chief Information Security Officer and Operational Risk Director with a proven track record in multi-cultural and multi-national organisations. Able to bridge technical and business disciplines and communicate at all levels. Extensive knowledge of Information Security, Cyber Security, Physical Security, BCDR, Operational Risk, Crisis Management, Data Protection, Financial Crime and Compliance. The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He then held the position of Director of Data Security at Nationwide Building Society before taking the role as Head of Information Security at Camelot Lottery Solutions. Graham is currently Interim Head of Cyber Security at Yorkshire Water. He has a master’s degree in Information Security from Royal Holloway.
Grant Revan
Head of Strategic Engagement, Red Sift (UK)
Ian Amit
Former CSO, Cimpress (U.S.)
Ian is the former CSO of Cimpress, the world leader in Mass Customization, with over 15 businesses worldwide and remote teams. Before Cimpress, Ian held senior leadership positions with Amazon, ZeroFOX, IOActive and has over 25 years of experience in the security industry as a practitioner. Ian is also the co-founder of DC9723 – the Tel Aviv DEFCON group-and serves as a BSides Las Vegas board member. He is also the creator and co-CEO of The CISO Track – a series of CISO centric curated events.
Jelena Matone
CISO, European Investment Bank (EIB) and President, Women Cyber Force (Luxembourg)
Respected and leading CISO, awarded the CISO of the year for 2019 in Luxembourg, Sentinel CISO Global 2020, EU CISO 2020, and recently Ambassador of the year 2021 in Luxembourg. Versatile and innovative Cybersecurity professional with emphasis on cyber security risk management, policies and procedures creation, IT/IS security, IT Operations, audit, risk mitigation, business process improvement, IT governance. Passionate about participation and encouragement of women in cybersecurity and in STEM programs.
Prior to current role, served as the Senior Operational Risk and ISO manager for another EU Institution. Earlier in career, managed IT Audit and Compliance for Sobey’s, one of the two national grocery retailers in Canada and Audit, Corporate Development, M&A and growth strategies and IT Audit for George Weston, one of the Canada’s largest publicly traded food processing and distribution companies.
Jeff Schiemann
CISO, SEBA Bank AG (Switzerland)
Jeff has more than 25 years’ experience in Information Security and Cyber Risk Management, currently serving as Chief Information Security Officer for one of the first licensed Crypto Banks in Switzerland. Previous roles have included: CRSO, Chief Risk & Security Officer for a Blockchain Accelerator, successfully completing multiple tokenization platforms raising over 500m Euros, Group Security Expert for France telecom, Led the Financialization of Cyber Risk & IT Governance workstreams, as well as Article 29 Work Party representative on GDPR; Global Director of Security, Risk & Compliance built dedicated functions to manage and mitigate supply side risk, negotiated effective contract controls & reporting, successfully implemented enterprise-wide security programs for many of the largest Telecom outsourcing contracts between 2001-2018 (from 100M- 3.4B Euros in value). In addition to his Security experience and certifications, he has a background in UK & EU law, Privacy Law, Financial Regulations, Cyber Risk Management, Negotiation & Conflict resolution. Additionally, he can tell you just how hard you have to hit the ground to get a good bounce (Skydiving), how far you have to sink before you get into trouble (SCUBA diving) and just how close you have to get, to get kicked at by a Giraffe or charged by a Gorilla. Ask him the question “did you see the snake that bit you?” you will find out the real reason why doctors ask this question.
Jonathan Luff
Co-Founder, CyLon (UK)
Jonathan is the co-founder of CyLon, which has supported the growth of 100+ cyber security startups across Europe, Asia and the Middle East to a collective valuation of $1bn+. Before founding CyLon, Jonathan was a senior British Diplomat, serving in a variety of roles for the UK Government, including as an advisor to UK Prime Minister David Cameron. He also co-founded Epsilon Advisory Partners, a strategy and growth firm working with world-leading global technology companies and investors.
Jon Evans
Sr. Director, Industrial Cybersecurity, ABS Group (UK)
Over 20 years experience in OT, IT and ICS with many of the major OEM’s and leading software companies in the world. A dedicated and results-driven sales leader with a strong engineering background in the achievement of profitable business growth through the creation and execution of successful sales strategies. Has extensive experience in rapid transformation of underperforming sales to achieve consistent growth and penetration of untapped international markets for world leading organisations in Power, Oil and Gas Sectors. Possesses excellent interpersonal skills and the ability to communicate concisely and articulately at all levels. Able to develop and maintain mutually beneficial internal and external relationships, having a strong ability to create high value customer focused propositions and tailored client solutions. Significant expertise in navigating the sales cycle among diverse national cultures within Europe, with the primary focus on exceeding expectations for customer service delivery. Enjoys being part of, as well as managing, motivating and training, a successful and productive team, and thrives in highly pressurised and challenging working environments.
Julia Harris
Information Security Assurance and Compliance Director, Flight Centre (UK)
For over 35 years, Julia has been a noteworthy leader in the information security space. You may know her from her work at various financial institutions, telecommunications providers, media companies, charities, a big 4 consultancy, gambling, a government business and now the Travel Industry. Julia can also be credited with contributions to the industry as a speaker at many Global and UK based conferences, such as Infosec at Olympia / Earls Court, Pulse Conferences and at the Information Security Forum’s global congress. Julia tends to specialise in governance, policy, risk and the human aspects of information security.
Julia is passionate about Information Security, and likes to have fun at work and home. She is a member of a number of mentoring platforms and groups to help bring more women into the Information Security profession. Julia is now supporting Flight Centre’s corporate clients in all things infosec.
Julia was a council member for the UK within the Information Security Forum (ISF) for 3 years. She sat on the committee of the British Computer Society (BCS) Information Security Specialist group for many years, and also sat on the Data Protection Expert Panel for the BCS.
Lucas von Stockhausen
Senior Director Engineering, Synopsys (Switzerland)
Lucas von Stockhausen is Senior Director Solutions and Sales Engineering at Synopsys SIG (Software Integrity Group). He has close to 15 years’ experience in Application Security with a deep knowledge of Static, Dynamic and Interactive Application security testing, as well as Software Composition Analysis and Runtime Application Self Protection technologies. He also brings over two decades worth of IT experience in several other roles such as Developer, Consultant, Project Manager and Security Professional.
With his experience, Lucas built a Solution Center of Excellence in Synopsys SIG to work with customers on a successful implementation of their Application Security initiative. Synopsys SIG achieved to be a leader in Gartner Magic Quadrant for Application Security Testing the fifth time in a row in 2021, as well as being a leader in Forrester Wave for Static Application Security Testing and Software Composition Analysis.
Manoj Bhatt
Director for Cyber Security and Networks, Telstra Purple (UK)
Manoj Bhatt is a recognised cyber security leader and awarded in the top 30 cyber security leaders in 2021. Manoj is the Director for Cyber Security and Networks for Telstra Purple in EMEA and is an Advisory Board member for ClubCISO. ClubCISO is a free to join community with over 600+ CISOs worldwide.
Matthew Morton
Senior Security Architect, QinetiQ (UK)
Over a decade of post-graduate experience in Industrial Control and Automation/SCADA/Telemetry. Experience gained across various industries, including oil and gas production, water/sewage treatment, steel production, broadcast, building management and industrial product development. I take a thorough approach to problem solving and attention to detail. I strive for perfection in every piece of work whether it be electrical panel design, technical documentation or PLC programming. Solidified my underpinning theoretical knowledge through a part time (distance learning) MSc in Applied Instrumentation and Control. My interest in the industry goes beyond work commitments, as a member of the IET I’ve attended lectures in Sheffield on a wide variety of industrial sectors and keep up with engineering developments around the globe. I am also a registered STEM ambassador, so if you are a representative for a school in Sheffield then please feel free to contact me.
Matthias Muhlert
CISO, HARIBO (Germany)
Matthias is a dedicated and highly qualified IT Security Professional with a consistent track record of success spanning over 22 years of diversified experience developing and implementing IT security processes as well as leading IT security governance programs. He brings demonstrated expertise at identifying and mitigating security risks by conducting comprehensive business process reviews and developing appropriate plans and solutions to meet the highest of network protection standards. His leadership, interpersonal communication and negotiation skills allowed him to lead and manage diverse, cross-functional teams in international and multicultural environments, and maintain effective relationships with key project stakeholders as well as C-level decision makers. Main areas of expertise are in the development and implementation of solid IT infrastructure and network security systems, polices, governance and crisis response, with especial skills in security infrastructure, analysis, response, compliance and ISMS according to ISO 27001. Matthias works currently as SecurityBear (CISO) at HARIBO in Grafschaft and is responsible for global information security management in more than 25 countries. After studying Network Computing at the Technical University of Bergakademie Freiberg, he worked as Senior IT Security Consultant and IT Security Trainer in several companies, among others, at Verizon, NESEC GmbH and Kabel Deutschland (Vodafone). Before HARIBO, Matthias worked as Chief Information Security Officer of HELLA and Schaeffler in Germany being responsible for the complete Information Security Management. He holds the following credentials and certifications: ISO 27001 ISMS Manager, CISM, CISSP, PRINCE2 Practitioner, CoBIT Practitioner, EC Council – Certified Ethical Hacker, Checkpoint CCSE PLUS (NG/NGX).
Michael Strobl
Senior Engineering Representative, SecurityScorecard (Germany)
Michael has collected experience in various roles at different companies in a variety of technologies over the last 21 years in the Telco, Enterprise Security space.
He has been successfully involved in and leading projects of different sizes from a presale’s perspective over the last 11 years.
Michael owns a Masters equivalent degree in Electrical & Telecommunications Engineering of the Technical University of Munich and has acquired several industry relevant certifications over time i.e. Certified Ethical Hacker (CEH).
Nathan Green
Sr. Subject Matter Expert: Cyber & Dark Web, Dataminr (U.S.)
Nathan Green is a Sr. Subject Matter Expert in cybersecurity risk at Dataminr, a New York-based company that specializes in artificial intelligence to provide real-time information alerts to public and private sector clients. He received an MA in technology & national security studies from Georgetown University’s Walsh School of Foreign Service and a BA from the University of Maine. He also serves on the State Department’s OSAC cybersecurity committee.
Neatsun Ziv
Co-Founder, OX.Security (Israel)
For the past 5 years Neatsun led some of the key innovations in Check Point, where he was the internal founder of Checkpoint’s cloud initiative and is now leading the cyber division of checkpoint. Prior to this, he was the CEO of a cyber security start-up named Vanadium dealing with insider threats and vulnerabilities for 7 years. Previously he worked for MOD, Motorola and Scitex. He holds a BA in math & computer science and an MBA.
Nick Gerteisen
Deputy CISO, Smith + Nephew (U.S.)
Nick is an IT leader with experience in wide range of both technical and non-technical IT Silos. Specific areas of expertise include Enterprise Cyber Security, Medical Device Cyber Security, Secure SDLC, Risk Management, IT compliance activities (SOX 404, HIPPA, GDPR, etc), Enterprise IT service delivery, program management, physical and virtual infrastructure, networking, and SQL oriented databases (development, querying, and management). Prior to his current role, Nick was Director, Global IT Services & Deputy Chief Information Security Officer with the Insulet Corporation and he was also a Teaching Fellow at Harvard University.
Owais Ahmed
Senior Associate Director, Information Security Officer & Data Protection Officer, Mizuho Bank Europe N.V. (The Netherlands)
Owais is currently working as Senior Associate Director – ISO & DPO for Amsterdam, Brussels, Madrid and Vienna branch of a Mizuho Bank Europe N.V. in Amsterdam. Prior to this , he worked in MUFG Bank Europe as Assistant Vice President – IT SOx & Controls Specialist. He also served a leading role as European Information Security Officer EMEA in Kyocera Document Solutions Europe (Group). Owais has presented and attended prestigious business and industry events in the past across the globe. Before pursuing his Double Masters in Cyber Security / Information Security and Privacy at University of Twente in Netherlands and TU Darmstadt in Germany, he was working as a Senior Information Systems Auditor within KPMG’s Information Risk Management Advisory practice. As part of the leadership team, he helped deliver assurance and advisory services to clients in the areas of information technology, enterprise applications, business process control, IT governance, enterprise risk, information security and regulatory compliance.
Lady Olga Maitland
President, Defence and Security Forum and Chair, Board at Algeria British Business Counsel. Board, Copenhagen Compliance and Audere International (UK)
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Paul Baird
Chief Technical Security Officer (CTSO), Qualys (UK)
Paul Baird is an IT veteran with over 25 years’ experience, and has spent the last seven years focusing his efforts in cybersecurity. Paul’s background has included building a security ethos and security operations centre (SOC) from scratch for several leading enterprises in the UK housing and automotive industries. Having moved to the vendor side to join Qualys as their Chief Technical Security Officer (CTSO) in 2021, he now drives Qualys’ vision for cybersecurity at C-Level across customers and partners in the UK and North EMEA. He is a people-focused leader and passionate about supporting his team. Paul was awarded a fellowship by the Chartered Institute of Information Security (CIISEC) last year for his continued contribution to cybersecurity.
Peter Ling
Vice President, Cyber and Intelligence Solutions Global Cybersecurity Alliances and Cyber Resilience Programs, Mastercard
With 28 years’ experience in the Cybersecurity space, Peter is a seasoned global practitioner and technology pioneer, having created numerous offerings in this space. His background spans from operational security response management, systems engineering, and complex technical vendor integrations — to strategic alliances throughout the security and risk markets. His areas of expertise are in Public Key Cryptography (PKI), Secure Communications, Endpoint Protection and Threat & Risk management. He has developed and brought dozens of security products to market internationally and is on a constant journey, assisting partners and clients as the Cybersecurity market continues to meet the challenges of the day.
Paul Raines
Chief Information Security Officer, United Nations Development Programme (NY, U.S.)
Paul Raines is the Chief Information Security Officer for the United Nations Development Programme. In that capacity he is responsible for managing the cyber-security and disaster recovery planning for the Organisation’s 177 locations around the world. His unit is the first and only United Nations unit to be ISO 9001, ISO 20000, ISO 27001 and ISO 22301 certified. His information security unit has won international awards for outstanding performance including an Honors Laureate award from Computer World magazine in 2013 and a 7 time winner of the CSO50 award from CSO magazine—more than any other organisation since the award was established. The CSO award honors the top 50 cybersecurity organisations in the world for business value and thought leadership. In 2020 his unit won a Future Edge 50 award from CIO magazine for technological innovation in developing an incident response and threat hunting platform. Finally, Computer World magazine has twice selected Mr. Raines for its Premier 100 award for being among the 100 most influential IT leaders in the world.
Prior to UNDP, Mr. Raines worked for the Organisation for the Prohibition of Chemical Weapons (OPCW) where he, as well as other members of the organisation, was a joint recipient the 2013 Nobel Peace Prize. Prior to working for the United Nations he was the Chief Information Security Officer for Bloomberg LP, Barclays Capital and the Federal Reserve Bank of New York. He is a graduate of the United States Air Force Academy and Harvard’s Kennedy School of Government. For relaxation he enjoys opera, Shakespearean plays, French wine and sometimes just sitting in a cafe with an espresso and pain au chocolat reading a good book on Roman history.
Paul Squires
Lead Identity Strategist, SailPoint (UK)
Paul is SailPoint’s Lead Identity Strategist in the UK and has more than 20 years’ experience in cybersecurity and identity management. Paul brings this experience as he advises customers on how to meet security and governance goals with IAM programmes. Paul is committed to ensuring that robust identity processes, aligned with the right technologies provide real-world value to customers. He believes that making complex concepts simple to understand for non-specialists is key to allowing these benefits to be realised by all types of organisations.
Ray Stanton
Global Partner, IBM (UK)
An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.
Dr. Runli Guo
CISO, Gett (UK)
Runli, CISSP, CISM, PhD in Artificial Intelligence, is the Chief Information Security Officer (CISO) at Gett, a global technology company providing the ground transportation management (GTM) platform for business travel used by around one quarter of Fortune 500 companies. Runli is evolving the cyber resilience strategy of the business as it grows rapidly in a ripe-for-disruption corporate ground transportation management (GTM) market – estimated to be worth more than $100 billion a year.
Prior to joining Gett, Runli was the Global Head of Digital Cybersecurity Initiatives at Marsh McLennan, a global professional services firm. She is an experienced transformational leader who enjoys problem solving and building cyber security functions from the ground up leveraging technologies, such as big data analytics and artificial intelligence.
In addition to her bachelor’s degree in computer science, Runli holds a PhD in artificial intelligence; she is also a keen promoter for Women-in-Cyber and Women-in-Tech agendas.
Dr. Robert Coles
Honorary Professor at UCL (UK)
Robert is the Director of Cumberland House Consulting Ltd, specialising in audit, risk and cyber security strategy, programme delivery and Non-Exec and Board Advisory roles. He holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Non-Executive Director of Crossword Cybersecurity PLC, and Chair of the Board at Think Cyber Ltd and advisor to the Government of Singapore Ministry of Health. He is also a Governor/Trustee and Audit Committee Member of the University of Brighton. Robert has over 35 years of audit, risk and cybersecurity experience and has held a number of senior leadership positions, including CISO for the NHS and health & care system, GSK, National Grid, and Merrill Lynch and Head of InfoSec at Royal Bank of Scotland, and he was a partner at KPMG. Robert is a Senior Fellow at the Centre for Assurance Research and Engineering at George Mason University, Washington DC. He is also an Honorary Professor at UCL. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics. He continues to undertake research in these areas. He was also awarded an MBA from Manchester Business School.
Robert D. Rodriguez
Chairman & Founder, SINET & Venture Partner, SineWave Ventures (U.S.)
Robert served over twenty-two years as a Special Agent with the United States Secret Service. He is the founder of the Security Innovation NetworkTM (SINET) whose mission is to advance innovation and enable global collaboration between the public and private sectors to defeat cyber security threats. SINET serves as the nucleus that connects builders, buyers, researchers and investors in the cyber security domain. His executive protection experience spanned 10 years at the White House serving Presidents Ronald W. Reagan, George H. Bush, William J. Clinton and numerous Heads of State. During his career he held a number of leadership roles within the Executive Protection, Protective Intelligence, Inspection and Criminal Investigation Divisions. SINET accelerates business opportunities for both small and large companies through their strategic advisory services, community – building activities and networking events. The annual IT Entrepreneurs Forum (ITSEF) at Stanford University, the Innovation Summit at Columbia University, New York and SINET Showcase in Washington D.C. Are supported by the U.S. Department of Homeland Security Science & Technology Directorate, public and private sponsorships and an elite steering committee. Robert is the catalyst who leads and builds global collaboration models that advance innovation and connects the ecosystem of the entrepreneur; academia, science, private industry, investment banking, system integration, policy, innovators, law enforcement, venture capital and the Federal Government to include the civilian, military and intelligence agencies. He is known for building communities of interest and trust between disparate groups. SINET initiatives and advisory services accelerate both large and small companies business growth, increase awareness of innovative Cybersecurity technologies and helps develop relationships between the system integration, industry and Federal Government markets to collaborate on addressing IT Security challenges, needs and opportunities.
In 2001, Robert spearheaded the development of the Secret Service’s first public-private partnership Cybersecurity initiative in Northern California. Since 2005 he has been coordinating the public private sector outreach for the DHS – SRI International Cyber Security R&D Center and the Computer Science Department at Stanford University. He is an advisor to Stanford University Computer Science Department. He served on the US Air Force Advisory Board that helped design a public private construct relative to Cybersecurity and has been called upon numerous times by the Federal Government to help coordinate their private sector outreach. Mr. Rodriguez believes in mutually beneficial relationships that are top down-bottom up and trust based. He serves on the Board of Advisors for The Chertoff Group, as Director Emeritus for the San Francisco Kraft Fight Hunger Bowl, National Cyber Security Hall of Fame Board of Directors and is a certified graduate of the Federal Government’s Senior Executive Service Program. He is a recipient of the 2009 CSO Magazine Compass Award in recognition of outstanding leadership in the security field.
Dr Sally Leivesley
Managing Director Newrisk Limited (UK)
Dr Leivesley has experience in catastrophic risk, global media commentary, government and private sector incidents, exercising and advising on loss prevention and recovery. Her prime focus is on the protection of life and critical infrastructure from extreme threats. She has worked with global USA corporations on risk strategy for catastrophic incidents using exercises with Boards and facilitating executive meetings. In 2021 she presented to the Baker Institute, Rice University on vulnerabilities in the energy sector and nuclear conflict risks in the South and East China seas. In 2015 she presented to the Electrical Infrastructure Security Council’s conference in the Capitol Building on Black Swan risks.
Dr Leivesley Chairs the Permanent Monitoring Panel for Mitigation of Catastrophic Risk for the WFS (CERN) and has led 12 remote multinational science meetings on Covid-19 Mitigation and the Panel has also met on Engineering for Resilience in Infrastructure; Nuclear Conflict Mitigation Risk Management and Planetary Defence against Near Earth Objects (NEOs).
Communicator since 2001 on many international television news outputs including BBC World Service describing live international and UK incidents and all major forms of threat – cyber, terrorism, aviation, Polonium-210 and Novichok poisonings, Chechen terrorist Beslan child hostages, security issue with Iran, DPRK, USA Presidential security, Covid-19, and unexplained incidents such as MH370 leading to media stories in all countries on novel concept of cyber hijack as new risk in civil aviation.
Dr Leivesley received Scientific Advisory Training from the British Home Office to become a Scientific Advisor for national survival from nuclear, chemical and biological weapons effects and in the Cold War she held an appointment as a Scientific Advisor for operations in civilian nuclear bunkers under London.
PhD London University on catastrophic risk across all industry sectors, awarded in field of Economics. Innovator of technological solutions to improvised terrorist devices for chemical and explosives weapon’s effects. Specialist in CBRN for the British Register of Security Engineers and Specialists RSES, Member 25 years of the International Association of Bomb Technicians and Investigators (IABTI) and Member of the Royal United Services Institute, Member of the Australian College of Education.
Sam Ubido
Lead Operational Technology security transformation programme, Uniper (UK)
Samuel Ubido is an Innovative Information Security professional and speaker, with expert knowledge in cyber and physical security in Industrial Automation and Control Systems. He leads the Operational Technology security transformation programme for a Global Energy Company, providing strategic guidance and implementation strategies to mitigate cybersecurity challenges for its UK assets. Sam frequently speaks at international conferences on conversations including cyber security, blockchain, Educational Technology and Diversity and inclusion. He is a D&I and STEM ambassador and an MSc candidate (Software and System Security) at the Department of Computer Science, University of Oxford. Sam is an advocate for inclusive leadership and believes that diversity creates a culture where difference is embraced.
Sandip Wadje
Global Head of Technology Risk Intelligence, BNP Paribas (UK)
Cyber & Tech Risk @ BNP Paribas – Crypto / blockchain, AI, Cloud, & Threat Intelligence
– A highly experienced and innovative leader with versatile cyber security, risk, and compliance experience in global Financial Services institutions
– Significant experience in leading large multi-year cyber and risk programmes by proactive engagement with board level business, technology, and RISK executives
– Start-up mind set with proven experience in developing and implementing innovative cyber security solutions in F500 organizations
– Proven experience in hiring exceptional talent in offshore locations to setup Centre of Excellence (COE) capability
– Global mindset: Experience of building and leading multi-cultural teams in Asia, Europe, and USA
– Exceptionally well connected in the industry- strong network of customers, partners, technology providers, and subject matter experts across the globe
– Known in the industry for: Passion, Integrity, Honesty and Technical Knowledge
– Specialties: Security Strategy, Cyber Roadmap, Security Architecture, Cyber Threat Intelligence, Cloud Security, Security Operation Centre, Identity and Access Management, Data Protection (Structured and Unstructured), Social Media Monitoring, External Attack Surface, Vulnerability Prioritization, Cyber Fraud, Financial Crime, Cyber Rating, Digital Risk Analytics, Insider Threat, Incident Response, Merger & Acquisition Due Diligence, Technology Audit and GRC
– Stakeholder coverage: CEO, COO, CFO, CDO, DPO, CTO, CIO, CISO, Risk Management, Compliance, Fraud, Credit Risk, Legal and HR
Simon Riggs
CISO and IT Risk Officer (Interim), McKesson (UK)
Recognised cyber security MD with over thirty years of industry experience implementing successful programmes in demanding global environments including investment banking, retail, media and FMCG. Simon provides strategic vision, leadership and technology expertise with a proven track record for effective risk management, change delivery and exceptional impact. He has a strong track record of creating and leading sector wide initiatives. Prior to his current position, Simon was regional CISO at Bank of America Merrill Lynch for 9 years, where he had responsibility for all aspects of cyber security in the EMEA region working closely with business and technical leaders. A member of the bank’s information security senior leadership team that directs the enterprise wide prevention and response activities, Simon had an active role in defining the global strategic operating model and setting strategic long-term goals. Previous sector positions have included Bank of England’s industry chair of the Cyber Coordination Group and Chair of CPNI’s Financial Services Information Exchange (FSIE) and Global Head of IT Security at Thomson Reuters.
Stephen Cavey
Co-founder and Chief Evangelist, Ground Labs (Singapore)
As Ground Labs co-founder, Stephen Cavey leads a global team empowering enterprise partners to discover, manage and secure sensitive data across their organizations. Stephen has deep security domain expertise with a focus on electronic payments and data security compliance. He is a frequent speaker at industry events such as PrivSec Global, and his expert analysis has been featured in media outlets including the Financial Times, Entrepreneur, SiliconANGLE, among others. He is also a member of the Entrepreneur Leadership Network and Forbes Technology Council. Prior to Ground Labs, Stephen held leadership positions at Paycorp, an integrated electronic payments solution provider owned by KKR. Stephen also served in engineering roles with Webpay, a payment services provider later acquired by Fidelity, and Webtel, an early Australian ISP.
Thomas Murphy
Strategic Intelligence Manager, Dragonfly (UK)
Thomas leads the strategic intelligence portfolio at Dragonfly, a global political risk intelligence firm. His background is in intelligence. He has extensive experience providing business-enabling security and political intelligence and analysis to some of the world’s most influential organisations. In recent years, he has increasingly worked with CISOs and other cyber professionals to help them understand how the geopolitical threat environment affects the cyber domain. Thomas holds a MA in International Relations from the University of Melbourne.
Tim Ward
CEO and Co-Founder, ThinkCyber (UK)
Tim has worked in IT for more than 20 years in consulting and corporate IT with organisations including Logica, PA Consulting, and was previously Global Head of IT for the cyber division of BAE Systems (Detica). Tim studied Computer Science with AI at the University of Leeds, holds an MBA from the Open University and a Post Graduate Diploma in Entrepreneurship from Cambridge University.
Torquil Macleod
Director, Via Resource (UK)
Tor has spent the last 10 years helping organisations build high performing Information Security teams. His experience spans from the development of large-scale recruitment and training programmes to helping Start-ups make the right security hire. His insight is from first hand experience of the real Cyber Security Skills Market.
Dr Viktor Polic
CISO, Head of Information Security and Assurance Services, ILO - United Nations (Switzerland)
More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences.
ing. Xander C.W. Heemskerk
Director Product Security – Group Security, Philips (The Netherlands)
Xander drives the Product Security programs and initiatives for Personal Health businesses worldwide. Digital Computatonal Pathology & Global Brand Licensing. Solution include Internet of Things (IOT), AI, ML, Mobile Apps, Cloud IAAS, PAAS , SAAS and Big data are crucial parts of the Products and Services delivered by Philips. He has been responsible for Corporate Security, Enterprise Information Security, Information Risk Management and Product Security on strategical, tactical and operational level in different type of organisations and contexts. With over 30 years of experience in all aspects of Information Technology ranging from Consulting, Security, Architecture, Performance, Design, Development, Coding, Testing and Operations, Xander has held different roles and positions at Oracle, Orient Overseas Container Lines (OOCL) ltd, Hong Kong Government, Everett, Ricoh and at 50+ companies in consulting roles. He taught training classes for Oracle University on Architecture, Security, Performance, High Availability and Identity Management and has been with his feet in the mud, but also working on getting the “mud-hole” organised!
Sponsors
Welcome, you are registering as a speaker or official sponsor of the 6th CISO 360 Congress, 6-8 July 2022, Geneva, Switzerland
Qualys
Qualys is a pioneer and leading provider of disruptive cloud-based IT, security and compliance solutions with over 19,000 active customers in more than 130 countries, including a majority of each of the Forbes Global 100 and Fortune 100. Qualys helps organizations streamline and consolidate their security and compliance solutions in a single platform and build security into digital transformation initiatives for greater agility, better business outcomes, and substantial cost savings. The Qualys Cloud Platform and its integrated Cloud Apps deliver businesses critical security intelligence continuously, enabling them to automate the full spectrum of auditing, compliance, and protection for IT systems and web applications across on premises, endpoints, cloud, containers, and mobile environments. Founded in 1999 as one of the first SaaS security companies, Qualys has established strategic partnerships with leading cloud providers like Amazon Web Services, Microsoft Azure and the Google Cloud Platform, and managed service providers and consulting organizations including Accenture, BT, Cognizant Technology Solutions, Deutsche Telekom, DXC Technology, Fujitsu, HCL Technologies, IBM, Infosys, NTT, Optiv, SecureWorks, Tata Communications, Verizon and Wipro. The company is also a founding member of the Cloud Security Alliance.
For more information, please visit www.qualys.com
RiskRecon
RiskRecon, a Mastercard Company, enables you to easily achieve better risk outcomes for your enterprise and your supply chain. RiskRecon’s cybersecurity ratings and assessments make it easy for you to understand and act on your risks, delivering accurate, risk-prioritized action plans custom-tuned to match your risk priorities.
RiskRecon traces its beginnings to 2011 when our founder, Kelly White, asked himself, “Is it possible to measure the security program quality of any company simply by looking its Internet-facing presence?”
Kelly is a long-time information security practitioner and bank CISO who witnessed first-hand the need for adapting third-party risk controls to meet the new challenges resulting from decentralized IT and SaaS apps. He has many years of hands-on experiencing building big data and analytics solutions to detect fraud and security vulnerabilities in high-velocity transaction environments.
Like most organizations at the time, his bank’s third-party risk management assessments relied heavily on questionnaires and other vendor attestations. This approach worked well ten years ago with a small number of large vendors, mostly in-house deployments, purchases controlled by central IT, and a well-defined set of Internet vulnerabilities. With the decentralization of IT purchasing and rapid adoption of SaaS, this approach was becoming less effective and more resource-intensive.
What if instead of trying to use the “old” risk management model, his institution could trust an objective source that automatically pinpointed specific gaps in any organization’s security programs and performance? Questionnaires and surveys are helpful in evaluating one’s intent but provide little verifiable insight into actual practices and discipline.
After realizing there were no such solution available, he decided to build his own. After testing and validating his solution with many peers, Kelly decided to pursue the idea full time and founded RiskRecon, officially incorporating in October of 2015.
RiskRecon is headquartered in Salt Lake City, UT with a presence in Boston, MA and representatives around the world.
Team8
Team8 is a global venture group with deep domain expertise that builds and invests in category-leading companies that solve the world’s toughest cybersecurity problems and change the cybersecurity landscape. Leveraging an in-house, multi-disciplinary team of company-builders integrated with a dedicated community of C-level executives and thought leaders, Team8 provides entrepreneurs with an unfair advantage to accelerate success and helps enterprises digitally transform. Team8’s leadership team represents serial entrepreneurs, industry pioneers and the former leadership of Israel’s elite tech and intelligence Unit 8200. Founded in 2014, Team8 is backed by global companies including Microsoft, Walmart, Cisco, Barclays and Moody’s, among others.
Gurucul
Gurucul is a global cyber security and fraud analytics company that is changing the way organizations protect their most valuable assets, data and information from insider and external threats both on-premises and in the cloud. Gurucul’s real-time security analytics and fraud analytics technology combines machine learning behavior profiling with predictive risk-scoring algorithms to predict, prevent and detect breaches and fraud. Gurucul technology is used by Global Fortune 1000 companies and government agencies to fight cyber fraud, IP theft, insider threats and account compromise. The company is based in Los Angeles. To learn more, visit Gurucul and follow us on LinkedIn and Twitter.
Ping Identity
Ping Identity is the Intelligent Identity solution for the enterprise. We enable companies to achieve Zero Trust identity-defined security and more personalized, streamlined user experiences. The Ping Intelligent Identity™ platform provides customers, workforce, and partners with access to cloud, mobile, SaaS and on-premises applications across the hybrid enterprise. Over half of the Fortune 100 choose us for our identity expertise, open standards, and partnerships with companies including Microsoft and Amazon. We provide flexible identity solutions that accelerate digital business initiatives, delight customers, and secure the enterprise through multi-factor authentication, single sign-on, access management, intelligent API security, directory, and data governance capabilities.
For more information, visit www.pingidentity.com
SailPoint
SailPoint is the leading provider of identity security for the modern enterprise, empowering organizations worldwide to put identity security at the core of their business. With a foundation of artificial intelligence and machine learning, SailPoint identity security delivers the right access to the right identities and resources at the right time.
For more information please visit www.sailpoint.com
Ground Labs
Ground Labs enables organizations to discover and remediate all of their data across multiple types and locations — on servers, on desktops and in the cloud. Ground Labs serves as the most comprehensive and trusted solution in the enterprise to confidently mitigate risk and find sensitive data. Ground Labs’ core focus is to develop technology to meet the increasing challenges of data management and regulatory compliance. This is shown with our flagship products of Enterprise Reconand Card Recon, along with our continued development of future solutions to address the complexities, challenges and intricacies of data discovery. Since the company’s inception, we have remained faithful to our commitment and core focus of discovering data, no matter where it resides. https://www.groundlabs.com/
Snyk
Snyk is a developer-first security company that helps software-driven businesses develop fast and stay secure. Snyk is the only solution that seamlessly and proactively finds and fixes vulnerabilities and license violations in open source dependencies and container images. Snyk’s solution is built on a comprehensive, proprietary vulnerability database, maintained by an expert security research team in Israel and London. With tight integration into existing developer workflows, source control (including GitHub, Bitbucket, GitLab), and CI/CD pipelines, Snyk enables efficient security workflows and reduces mean-time-to-fix.
For more information or to get started with Snyk for free today, visit https://snyk.io.
Synopsys
Synopsys builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Our market-leading solutions help developers to secure code as fast as they write it; development and DevSecOps teams to automate testing within development pipelines without compromising velocity; and security teams to proactively manage risk and focus remediation efforts on what matters most. With Synopsys, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.
DTMRMrk Navy B
Unexpected events can radically affect people and operations. Organisations need an early and clear line of sight into developing situations, with additional context, to enhance decision-making as an incident unfolds. Dataminr is recognised as the world’s leading information discovery platform that delivers the earliest warning on high-impact events and emerging risks from public data sources, enabling more effective risk mitigation strategies, faster response, and stronger crisis management. Recently valued at $4.1B, Dataminr serves thousands of users spanning hundreds of multinational organisations including more than two-thirds of the Fortune 50 and half of the Fortune 100 companies, public sector agencies, NGOs, and over 650 newsrooms worldwide.
QinetiQ
QinetiQ is an integrated global security and defence company. Operating at the leading edge of science and engineering and employing over 6,000 people, including more than 3,000 scientists and engineers. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way.
Uniting our own and others’ technology and know-how to provide distinctive specialist services and products that address our customers’ most pressing challenges. We are integrated across the life cycle of critical equipment and infrastructure, undertaking creative research and development, enabling test and evaluation and delivering operational readiness through training and rehearsal.
Create it. Test it. Use it.
Telstra Purple Red
Powered by Telstra – With two-thirds of the world’s surface within reach of Telstra’s satellite services and 2,000 Points of Presence (PoPs) globally, Telstra Purple pairs the firepower of a global network with the know-how and responsiveness of a local team. It’s why 200 of the world’s top 500 companies are already using our network solutions. And how we’re busy operating across 23 major cities. Because when you’re powered by Telstra’s SD-WAN data centre networking, enterprise wireless LAN and mobile networking solutions, expanding your organisation’s worldwide reach isn’t just a possibility – it’s a promise.
Red Sift
Red Sift enables security-first organizations to successfully communicate with and ensure the trust of their employees, vendors, and customers. As the only integrated cloud email and brand protection platform, Red Sift automates BIMI and DMARC processes, makes it easy to identify and stop business email compromise, and secures domains from impersonation to prevent attacks.
Founded in 2015, Red Sift is a global organization with international offices in the UK, Spain, Australia, and North America. It boasts a client base of all sizes and across all industries, including Domino’s, Telefonica, Pipedrive, Rentokil, Wise, and top global law firms. Find out how Red Sift is delivering actionable cybersecurity insights to its global customers at redsift.com.
Hunters
Hunters is a SOC platform that empowers security teams to automatically identify and respond to incidents that matter across your attack surface. Companies use Hunters to ingest and normalize data across all their security data and tools at a predictable cost. Hunters helps security teams overcome volume, complexity, and false positives by using built-in detection engineering, data correlation, and automatic investigation. Reduce your overall security risk by mitigating real threats faster and more reliably with Hunters than a SIEM solution.
BS White Background
Local knowledge. Global resources. Specialist consultants. Barclay Simpson is an international recruitment consultancy that specialises in recruiting information and cyber security professionals. Since 2001, we have provided end-to-end information security recruitment solutions, including permanent, interim and executive hires from analysts through to CISOs, so organisations can create an information security function that’s both fit for purpose and future-proof. Whether sourcing a single hire, an interim manager, or building a security function from scratch, our extensive network and niche specialist knowledge make Barclay Simpson ideally positioned to support your security needs.
Barclay Simpson Solutions
Barclay Simpson Solutions helps empower our clients to achieve business transformation success. We combine our proven industry talent expertise with effective and measurable project & service ownership and reporting. We work in partnership with our sister organisation (Barclay Simpson Associates) to ensure our advisory and project service flexibility utilises industry leading consultants, maintaining our overall strong position in the solutions market. Supporting our clients by providing comprehensive, outcome based engagements operated through a project services (Statement of Work) framework to ensure performance and delivery, Barclay Simpson Solutions provides expertise in project and service outcomes across the following areas, please click on any listed service offering for more information: Project Engagement Services: Governance & Assurance; Cyber Security & Info Sec; Risk & Compliance; Audit.
TenableNEW Logo2021
A decade ago, we pioneered the IT Vulnerability Management market as the creator of Nessus®, which is now the world’s most widely deployed IT vulnerability assessment solution. Given the rising severity and frequency of cyber attacks which commonly occur due to a lack of basic cyber hygiene, assessing IT devices for issues has never been more important. But now we’re in a new era. Digital transformation has opened up a whole new world of Cloud, DevOps, Mobility and IoT, where everything from containers to conference systems to power grids are now connected devices and part of the new, modern cyber attack surface. An attack surface which is continually expanding and contracting, like a living organism, making it extremely difficult to secure. Just as we pioneered the IT Vulnerability Management market, we are once again at the forefront of innovation in this new era to help organizations of all sizes rethink how they secure the modern digital enterprise as the pioneer of the emerging Cyber Exposure market. Tenable.io, the world’s first Cyber Exposure platform, arms Security with the visibility to see their entire cyber attack surface at all times (from IT to Cloud to IoT to OT) and arms the CISO, C-suite and Board of Directors with the insight to focus on the issues which matter most and make better strategic decisions.
Security Scorecard As Sep
Think Cyber 4x
Think Cyber Security deliver measurable secure behaviour change for their customers. The company’s multi-award winning Redflags™ Real-time Security Awareness product applies behavioural and learning science theory to deliver context-sensitive, just-in-time guidance. For example, when users are about to click links, visit certain web pages, enter their username into a web page, handle attachments, etc. Redflags™ won techUK Cyber Innovator of the Year 2021 and SC Awards Best Professional Training Programme 2020. It offers the toolkit organisations need to: manage operational risk from cyber-attacks directed at staff including phishing and ransomware; meet compliance goals; keep content refreshed and relevant; target specific behaviours and specific users; all whilst allowing staff to get on with their jobs, to achieve business goals.
Via Resource
Via Resource is one of the longest-standing specialist Information Security & Cyber Security recruitment agencies having been founded by Tor Macleod in 2010. Over the last twelve years, they have built a reputation on being experts in the Information & Cyber Security market and have developed unparalleled insight and expertise within the industry, not to mention a vast network of contacts and opportunities for candidates and companies. Via Resource’s USP is working solely in the Information Security, Cyber Security & Data Protection market. They have never moved away from this and never will, which creates a collaborative environment that provides greater opportunities for candidates to find their dream role or clients to find the right person for their business. Whilst they are niche, they do cover the full breadth of Information & Cyber Security including but not limited to; Governance, Risk & Compliance, Security Engineering, Security Architecture, Penetration Testing, Cloud Security, Application Security, Security Operations & SOC, Data Protection & Privacy and many more related areas. Via Resource has built a reputation for providing more than just contingent recruitment services. Whilst they have expertise in Permanent & Contract recruitment, they also spent the last twelve years developing their offerings in Executive Search and Consultant & Managed Services offerings, both of which are offered at the highest level within the industry. The team at Via Resource is built of consultants with in-depth Information & Cyber Security recruitment experience and boasts one of the most experienced teams in the industry, all of whom can provide more than just recruitment services, but aid candidates and clients acting as true consultants.
Ox Security
Ox Security builds security guardrails that empower builders to build securely at their own velocity, while cultivating a stronger and more innovative security culture. They do so by creating out-of-the-box, tailor-made, policy-as-code that empowers application builders to develop, deploy, and operate securely, and prevent security issues before they happen. Founded in 2021 and headquartered in Tel Aviv, Ox Security is funded by Team8 – a venture group that builds and backs technology companies across Cyber, Data and Fintech.
Abs Group
With over 50 years of risk and safety management experience in markets like Marine and Offshore, Oil, Gas and Chemical, Power and Energy and Industrial Manufacturing, we provides a comprehensive portfolio of Operational Technology (OT) cybersecurity consulting, implementation and risk management services. We help organizations, like yours, to successfully navigate today’s growing cyber threats. We focus on OT and ICS systems for critical infrastructure industries, customizing our solutions to fit your operations. Our risk-based solutions cover every stage of the asset lifecycle, from concept and design to operations, integrating cutting-edge technology with an agnostic approach. Our state-of-the-art Industrial Security Operations Center (ISOC) allows us to identify and mitigate attacks in real-time. We focus on stopping the bad guys so you can focus on what really matters: Your Operations.
Rutherford
Rutherford is a specialist recruitment agency, sourcing the best cyber and regulatory talent within professional and financial services. Our team of cyber security headhunters are experts in the field, constantly keeping abreast of the latest changes from the rapidly-evolving space. Over the past decade, our specialist Consultants have built a carefully-curated network of clients, helping them source candidates for a vast range of positions in cyber and information security. We have been known to identify early on the rising stars of the sector and to have strong relationships with the most sought after talent in the market.
ISC2 SuisseRomande Geneva
The Suisse Romande Chapter
As anyone seriously involved in the information security profession can attest, peer networking is an invaluable resource. (ISC)² Chapters provide members with the opportunity to build a local network of peers to share knowledge, exchange resources, collaborate on projects, and create new ways to earn CPE credits!
Isc2 Italy
The (ISC)² Italian Chapter provides thought leadership and guidance for security professionals in Italy. As the only official (ISC)² course provider in Italy (CISSP and, in the near future, CSSLP certifications), the Chapter hosts official trainings for Security Leaders as well as networking opportunities and knowledge sharing. To fulfill its mission, it organizes several initiatives as:
• webinar on a monthly or fortnight base;
• a complete security awareness program for schools (about one hour for kids and up to 2 hours for college students. Up to now this program covered about 58.000 students, teachers and parents;
• conferences. The next will be in the picturesque village of Faenza next September 20;
• whitepaper as the last one on ransomware that you may find at and many other activities including partnership with other organization or association to cooperate to advance our mutual interests to increase the likelihood of each achieving its mission and to amplify our reach in accordance with (ISC)2 directives.
We will wait for you in Faenza (RA), Italy, next September 20 (for further information please stay tuned on www.isc2chapter-italy.it
ClubCISO
ClubCISO, powered by Telstra Purple, is a global private members forum for information security leaders working in public and private sector organisations. The community is a non-commercial organisation with over 500 members helping to define, support and promote the critical role and value of information security leaders in business and society. ClubCISO provides a forum in which security leaders can build their network, be involved in proactive discussion, solve problems and create practical guidance that moves the industry forward.
ISSA-UK
ISSA-UK is the leading cyber security networking association here in the UK. As a not-for-profit organisation we are here to help get cyber security professionals together. We do this through many of our events run throughout the year from our Chapter meetings to our annual ‘Pitch on the Ship’ event which is a day full of keynote speakers and our infamous ‘Pitch on the Ship’ sessions. Having welcomed over 1,800 members since our beginnings in 2003, the ISSA-UK chapter is the world’s most successful chapter. Join us at our next event to find out more and to connect with other cyber security professionals. www.Issa-uk.org. – LinkedIn: ISSA-UK Twitter: @issauk
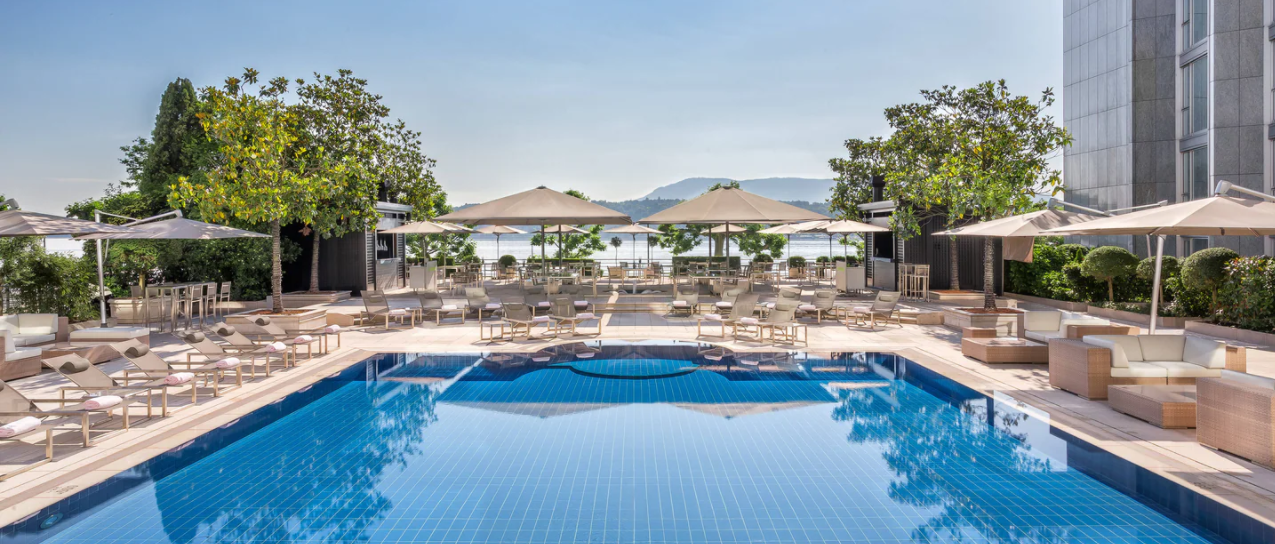
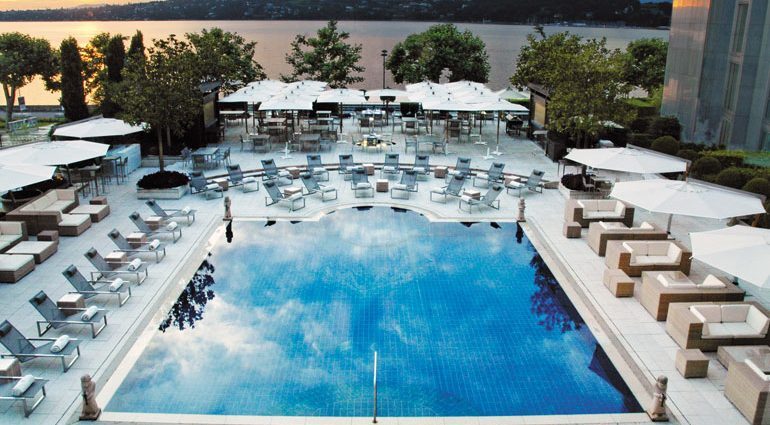
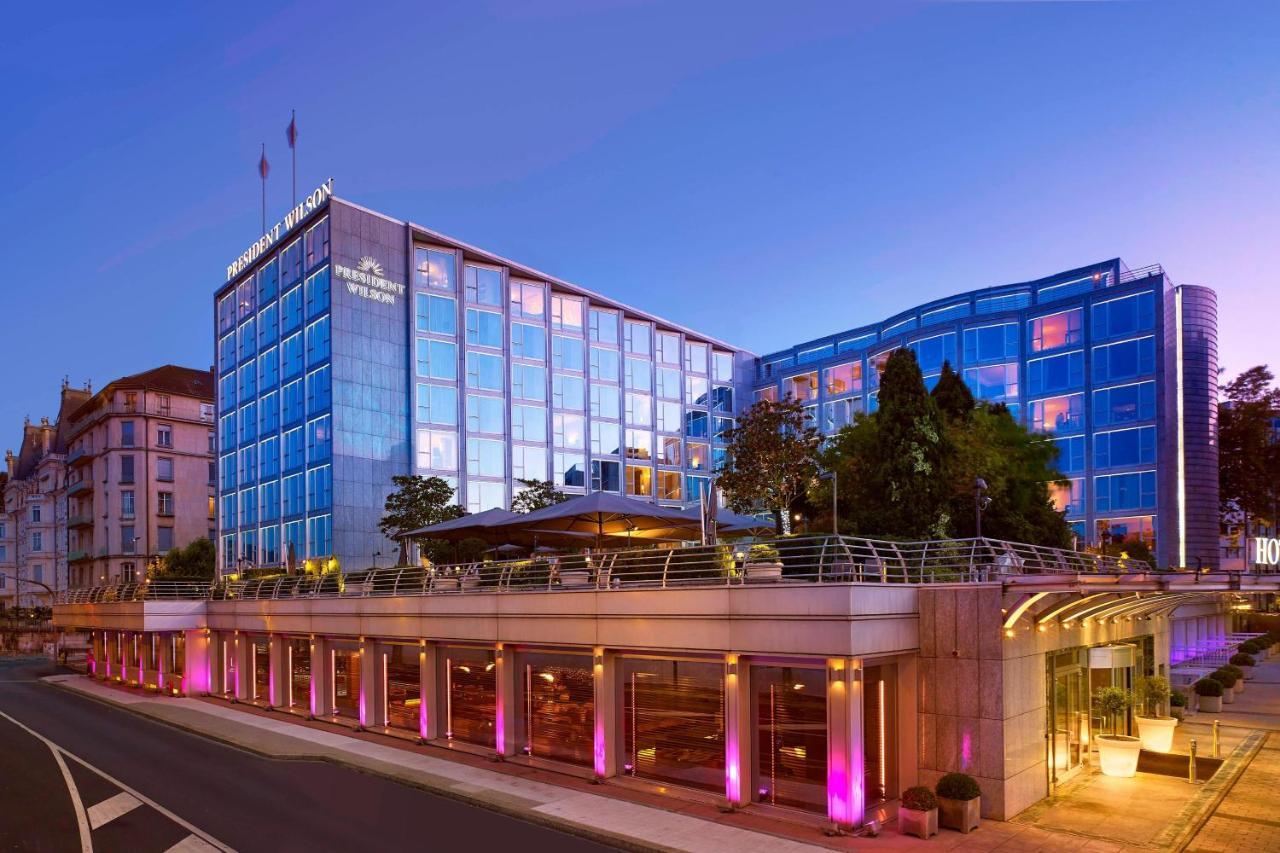
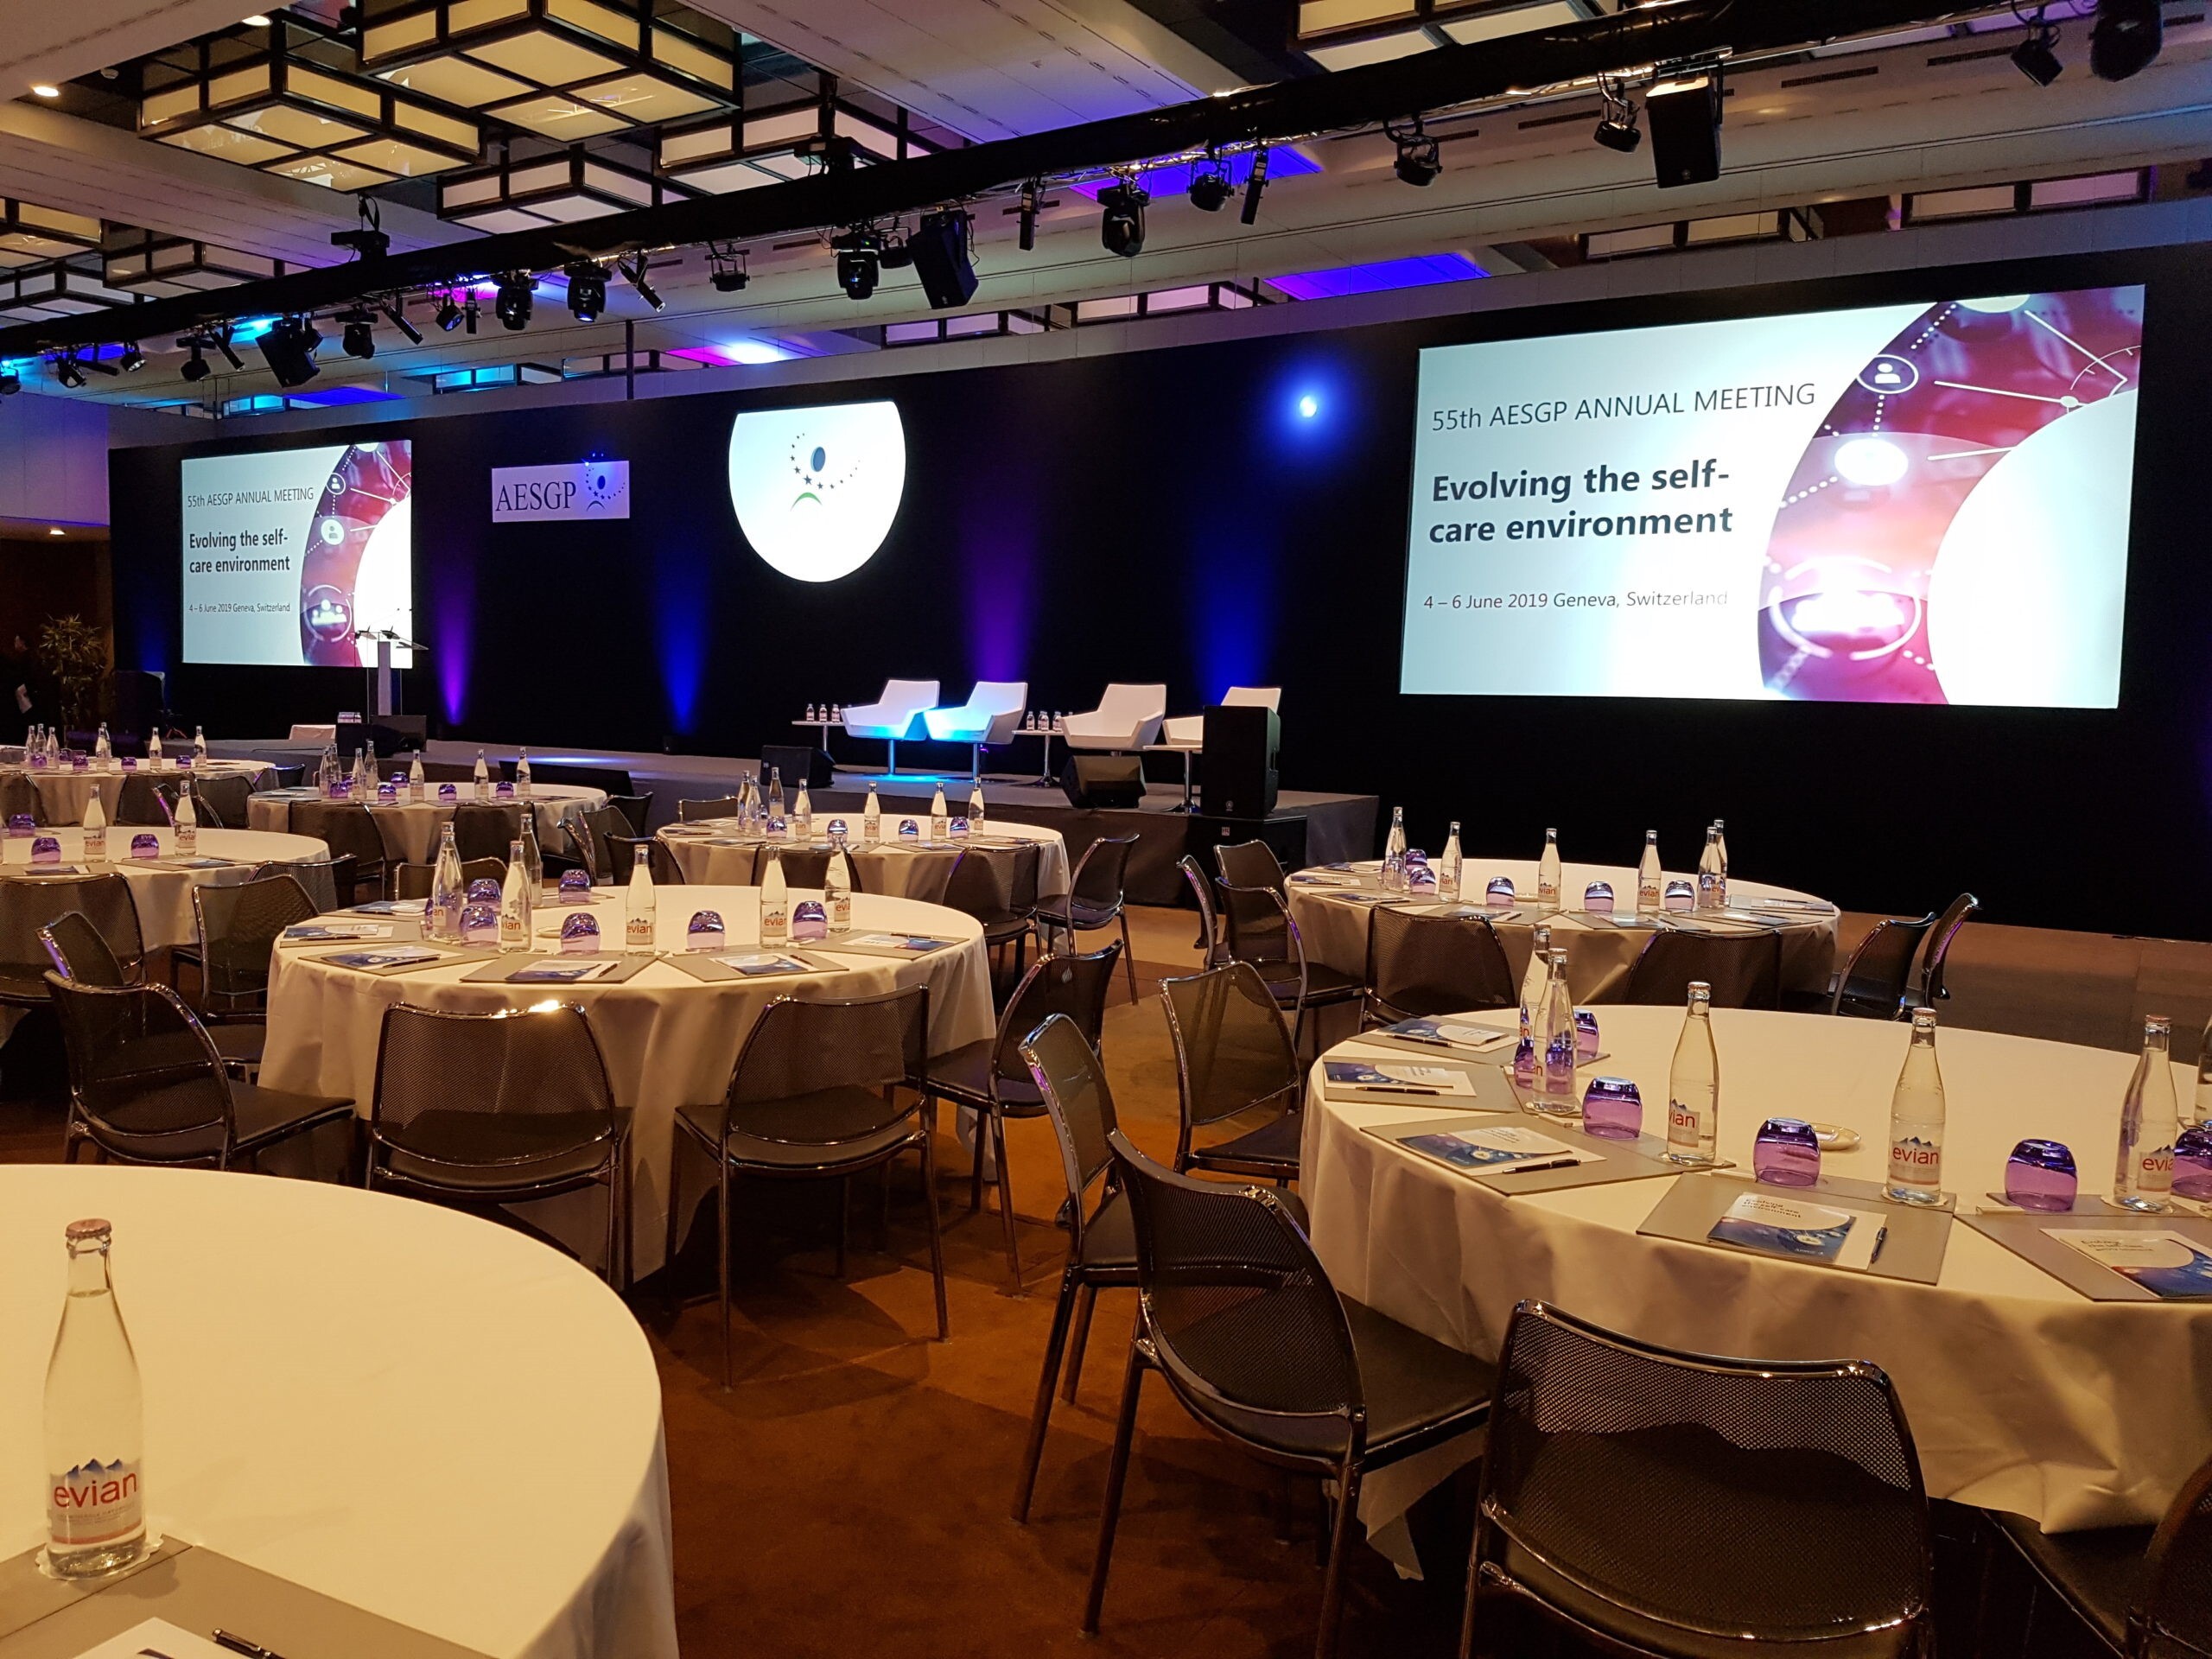
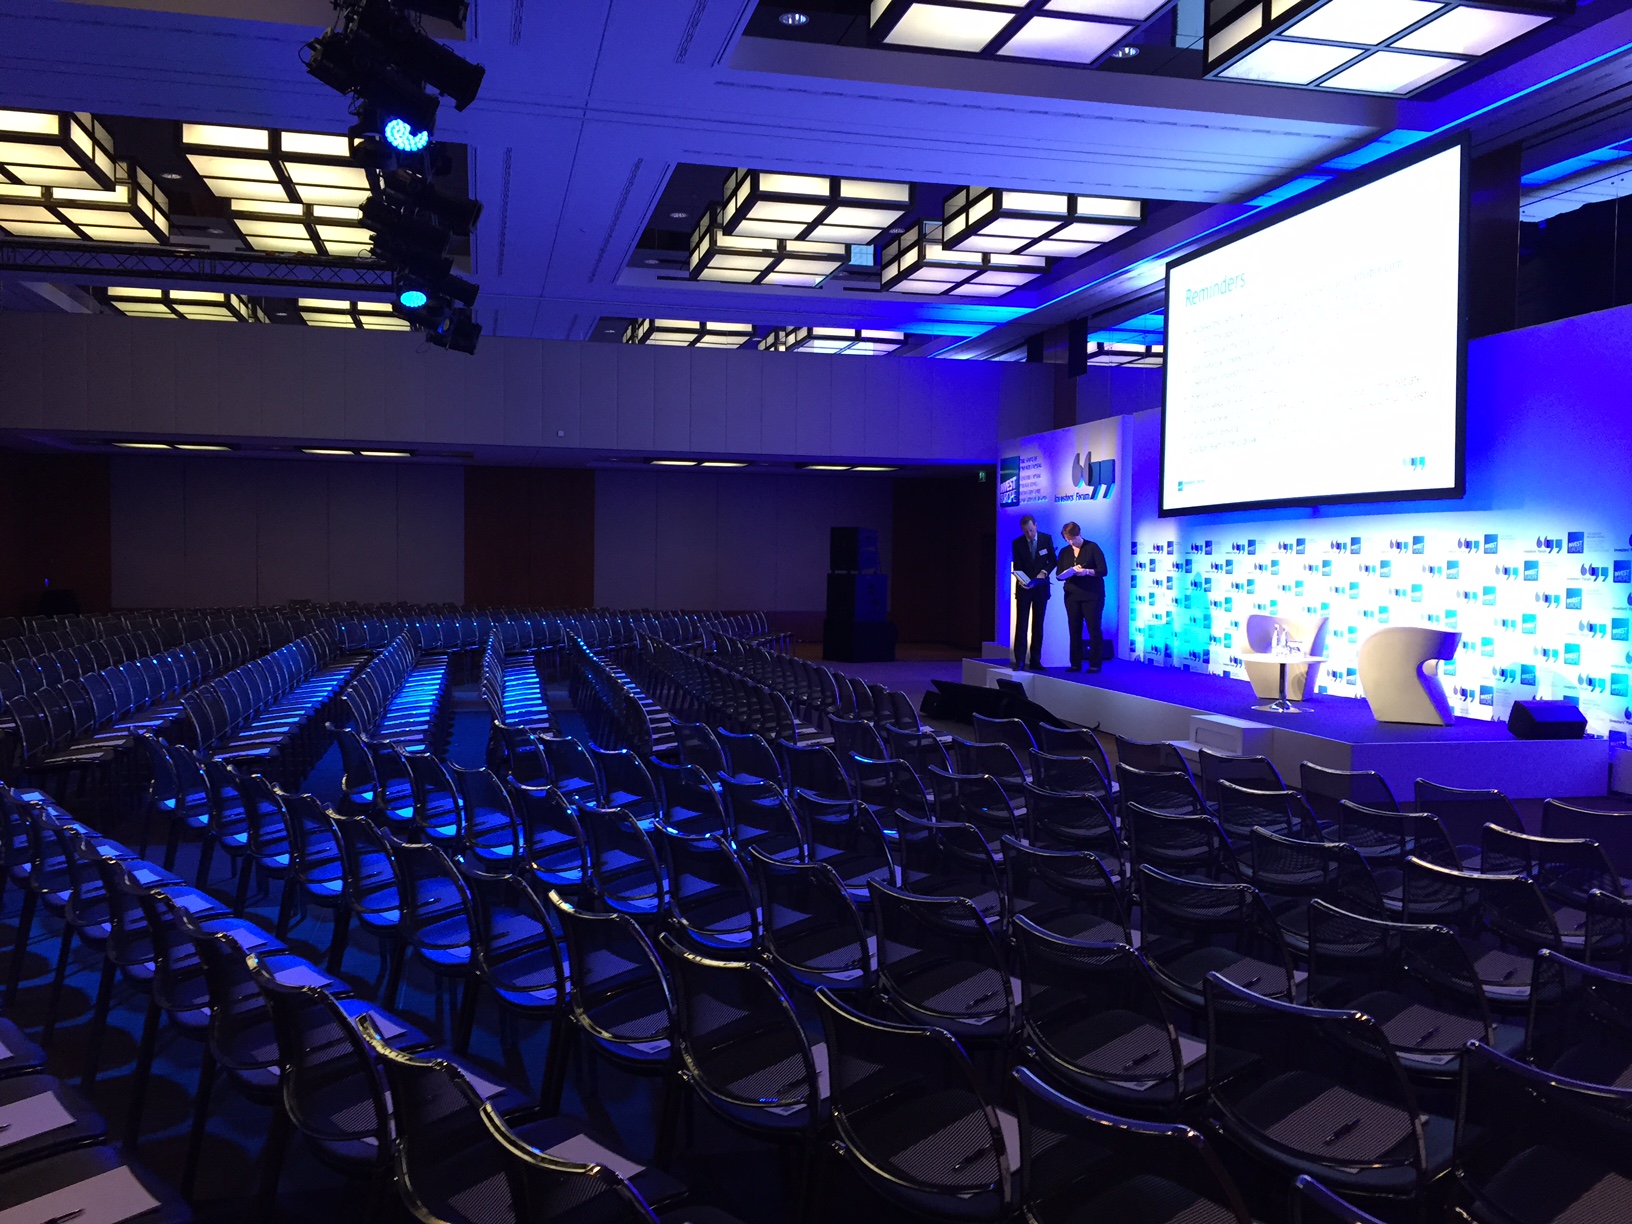
Gallery – 6th CISO 360 Congress
Welcome By the Pool Reception, sponsored by TEAM 8
Tuesday 5th July 2022

Gallery – 6th CISO 360 Congress
Boat Cruise Reception and Dinner, sponsored by Qualys
Wednesday 6th July 2022

Gallery – 6th CISO 360 Congress
Day two of Congress
7th July 2022

Gallery – 6th CISO 360 Congress
Cheese & Wine Tasting & Walking Tour of Old Geneva sponsored by Mastercard
CISO 360 Dinner, sponsored by Red Sift
Thursday 7th July 2022

View image gallery from the 6th CISO 360 Congress 2022
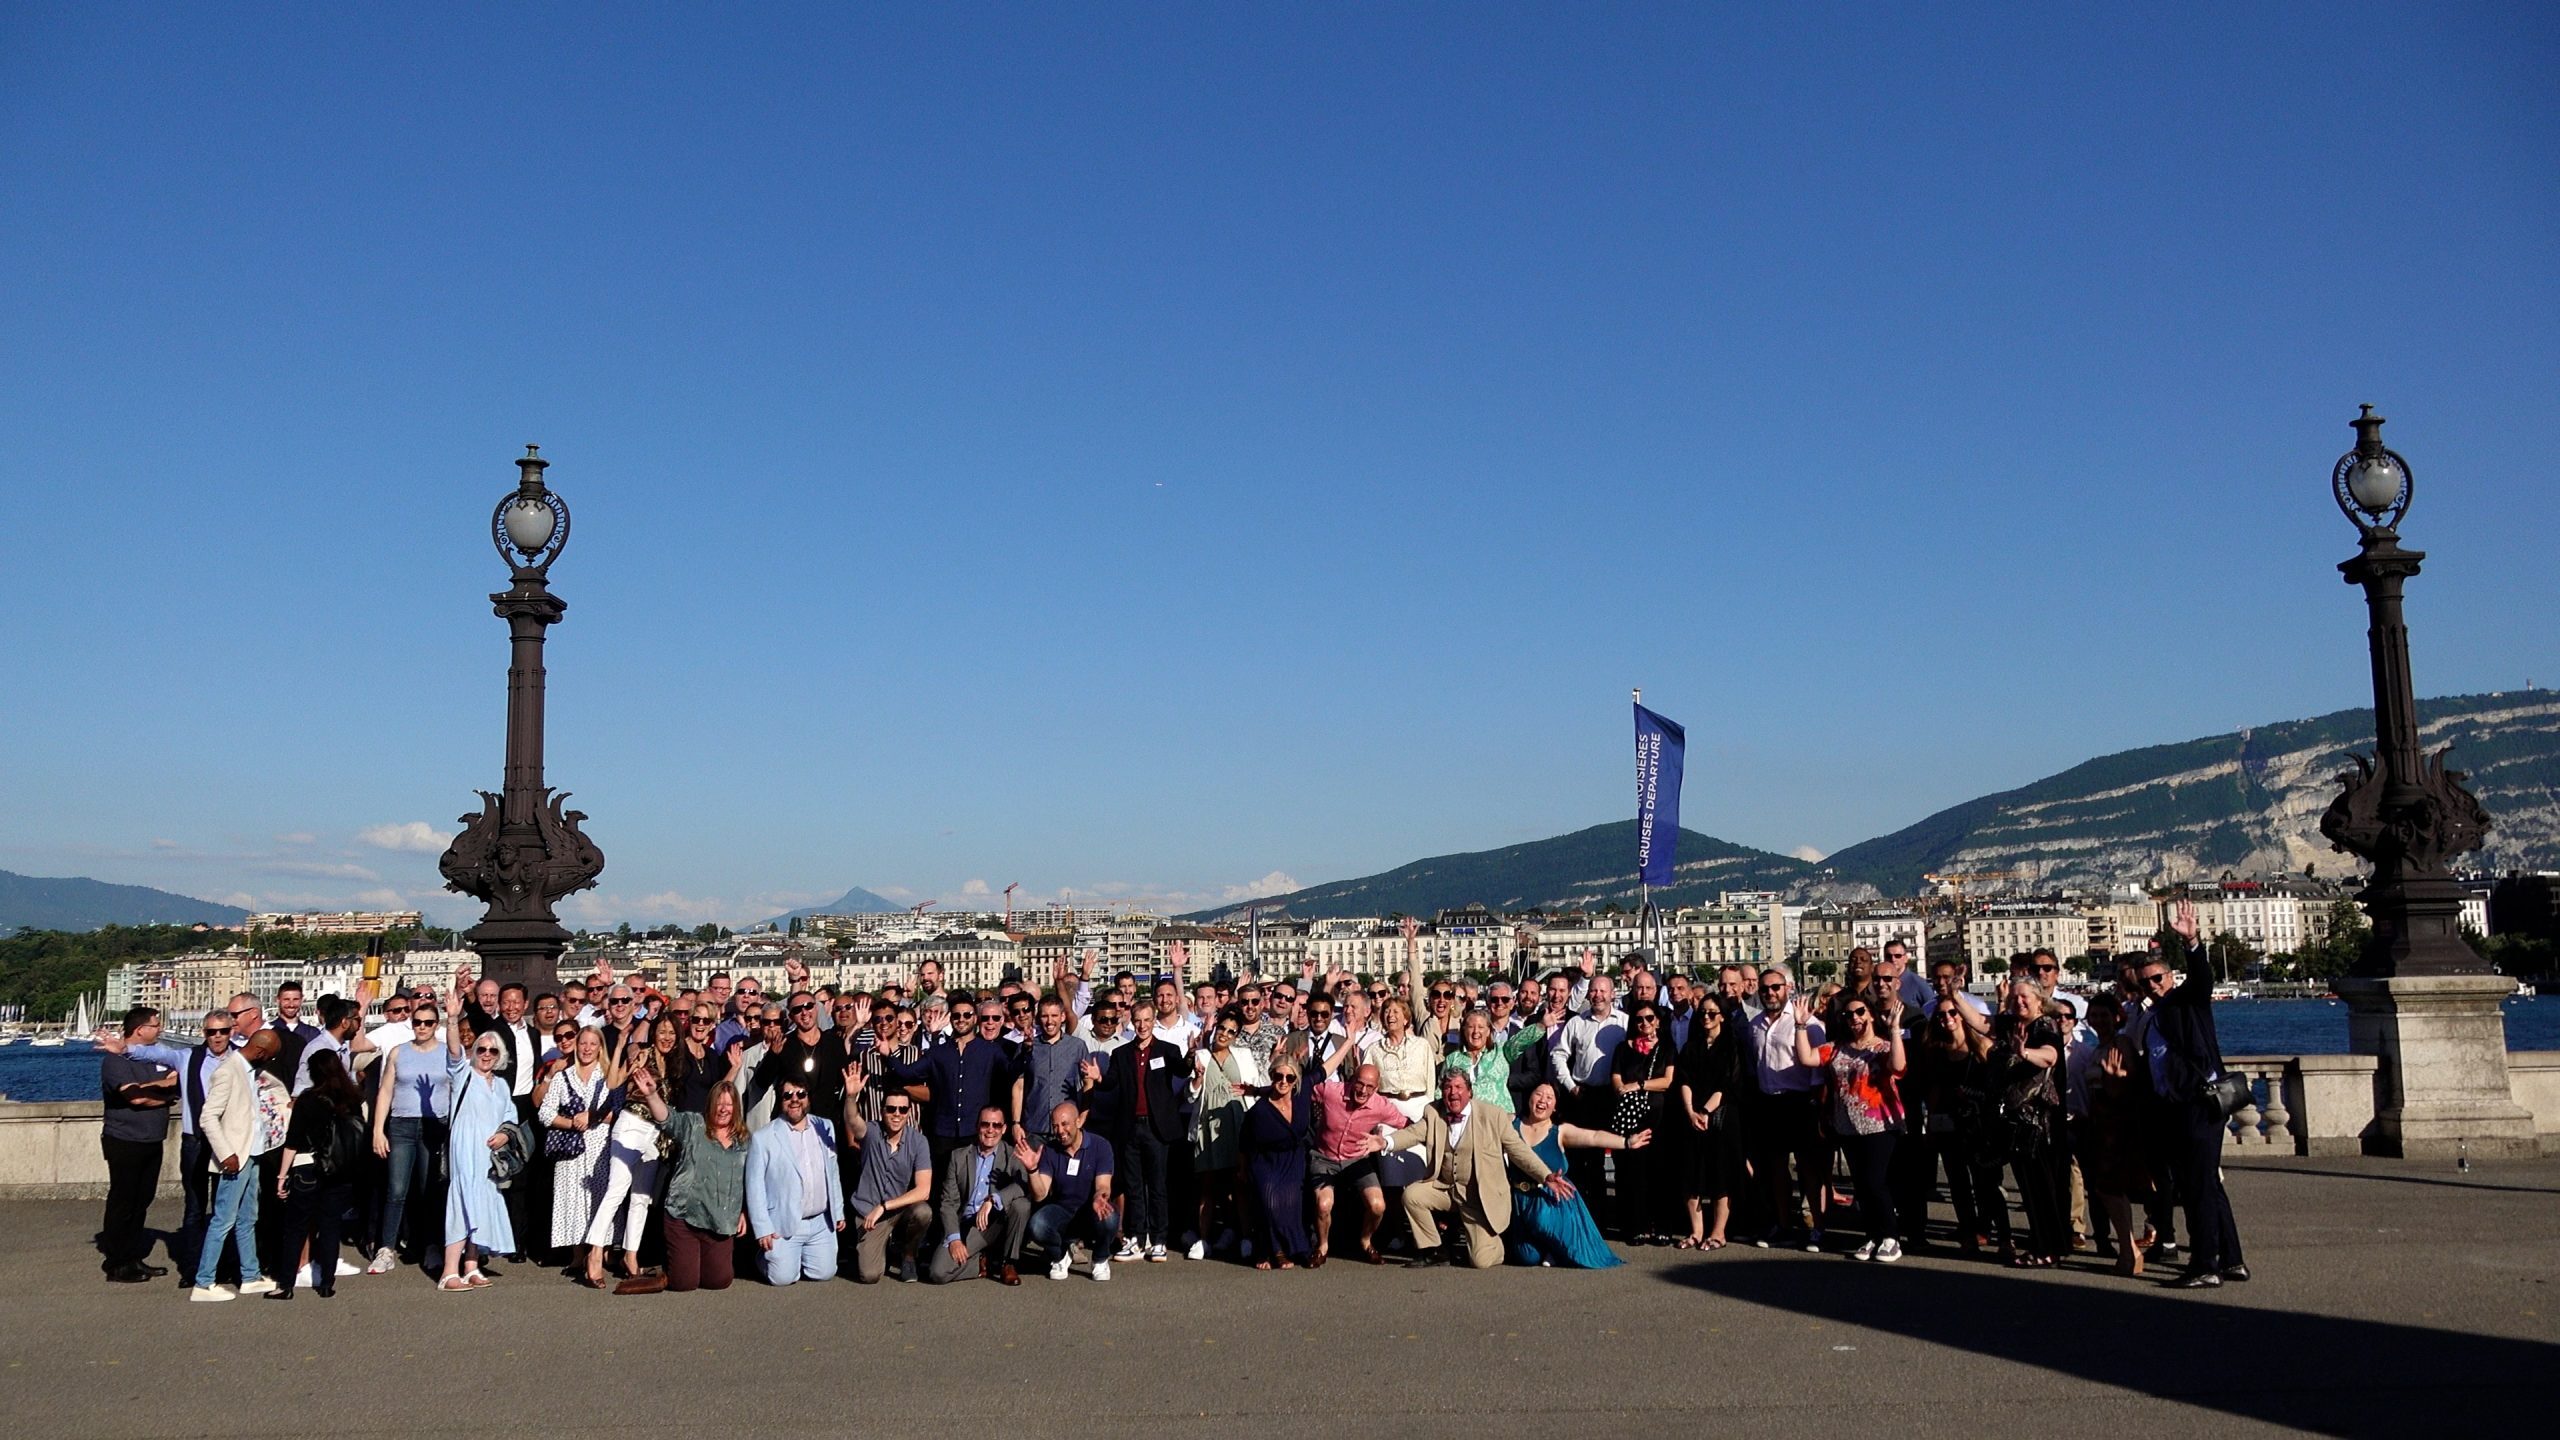 View the 6th CISO 360 Video here
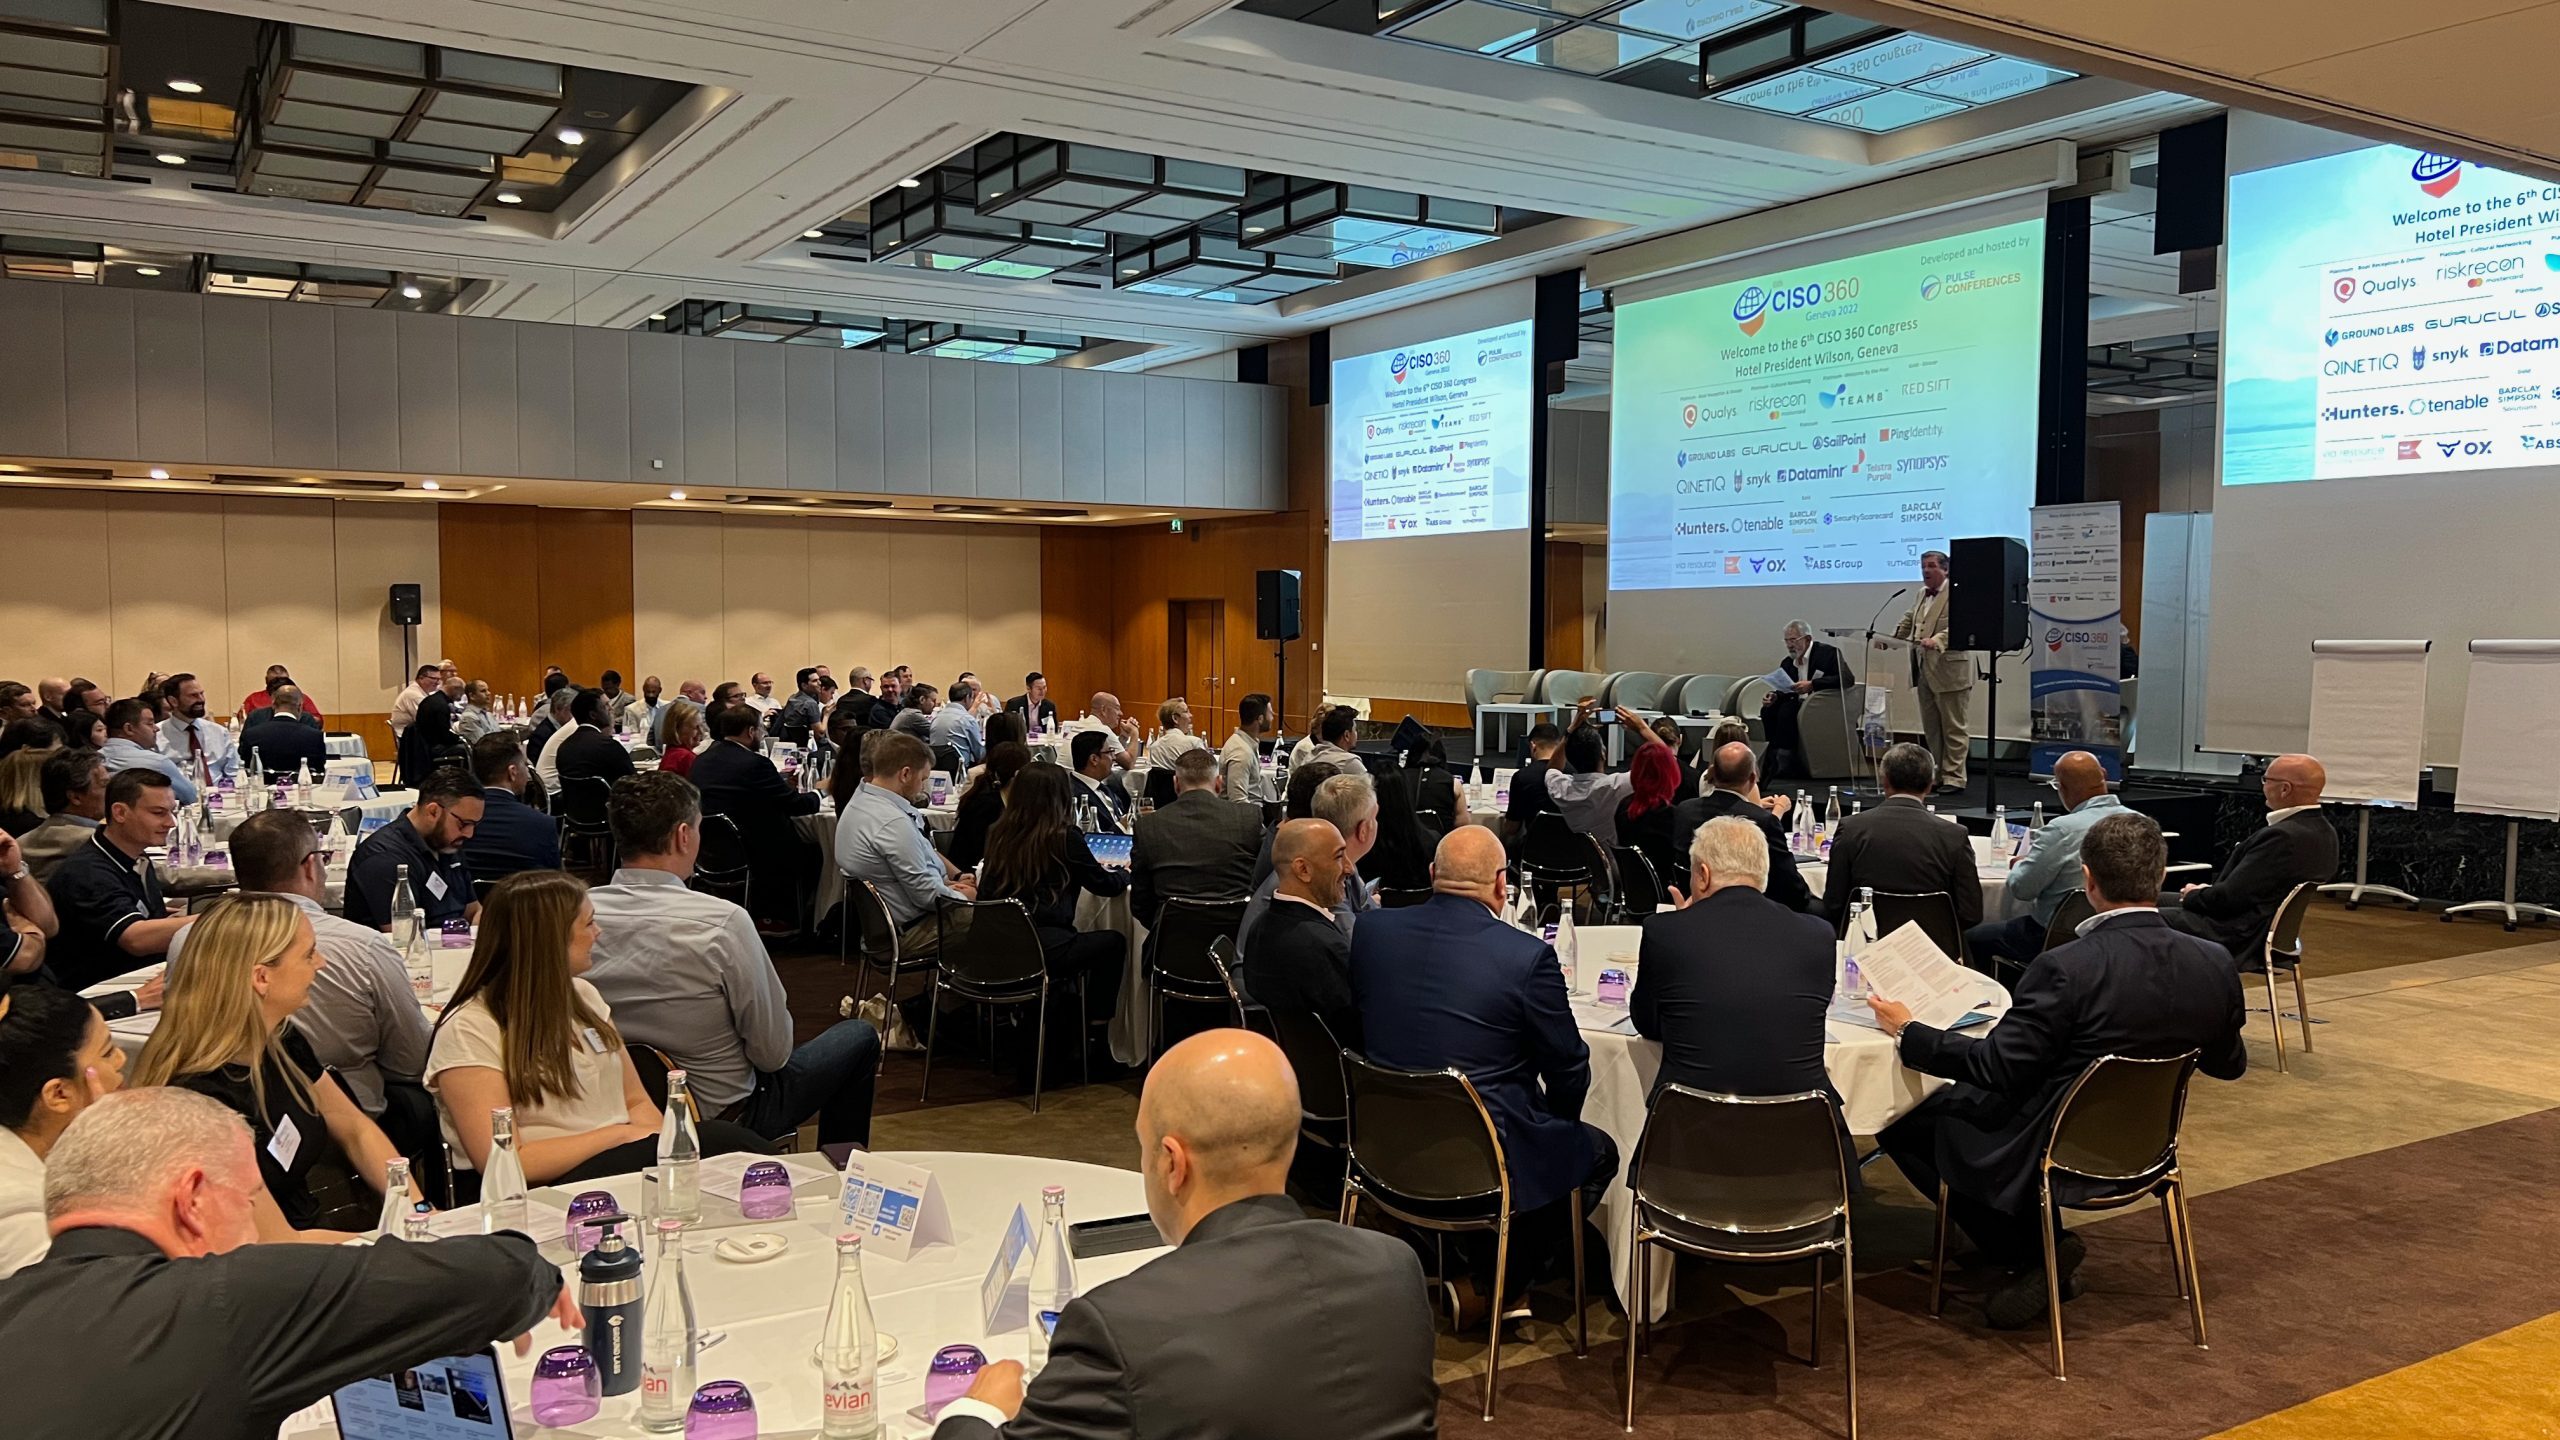 View Photos - Day one of Congress 6th July 2022
 View Photos - Day two of Congress 7th July 2022
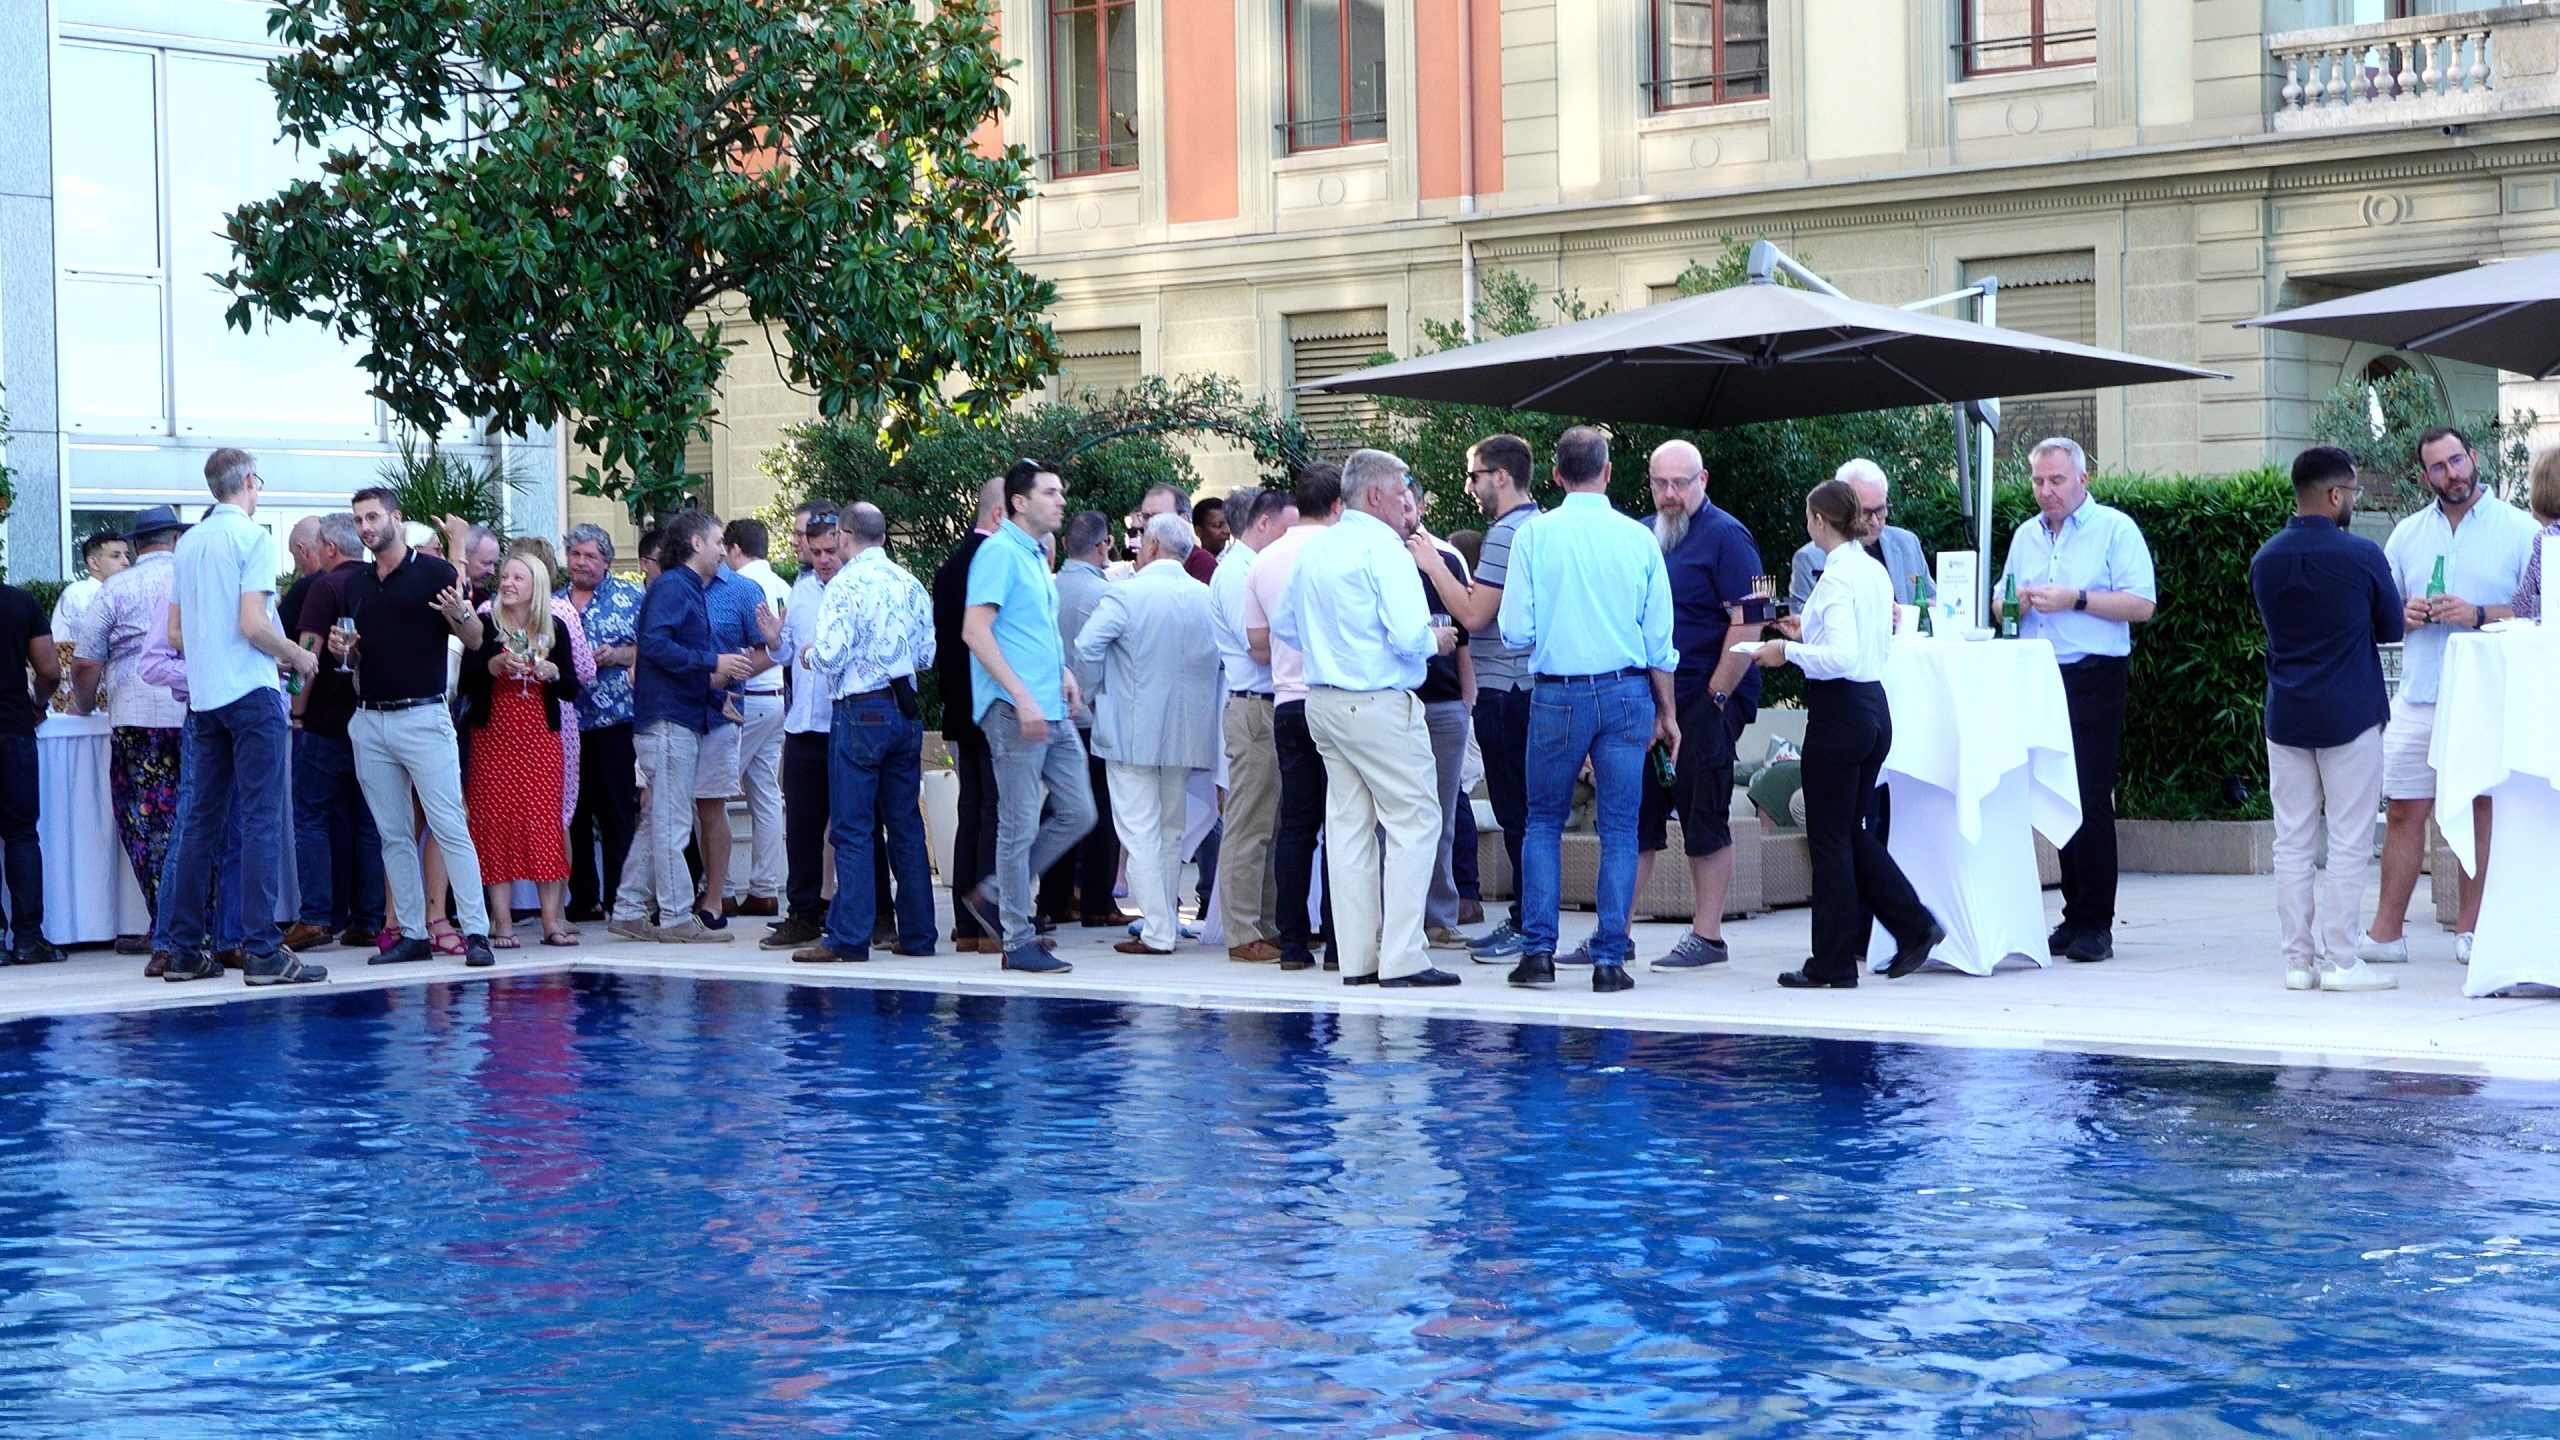 View Photos - Welcome By the Pool Reception, Tuesday 5th July 2022
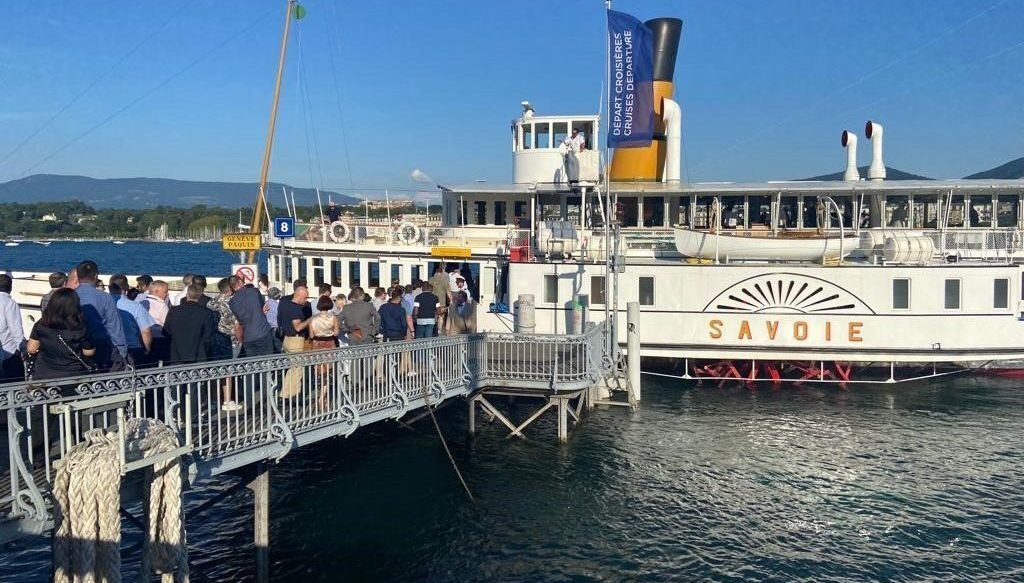 View Photos - Boat Cruise Reception and Dinner, Wednesday 6th July 2022
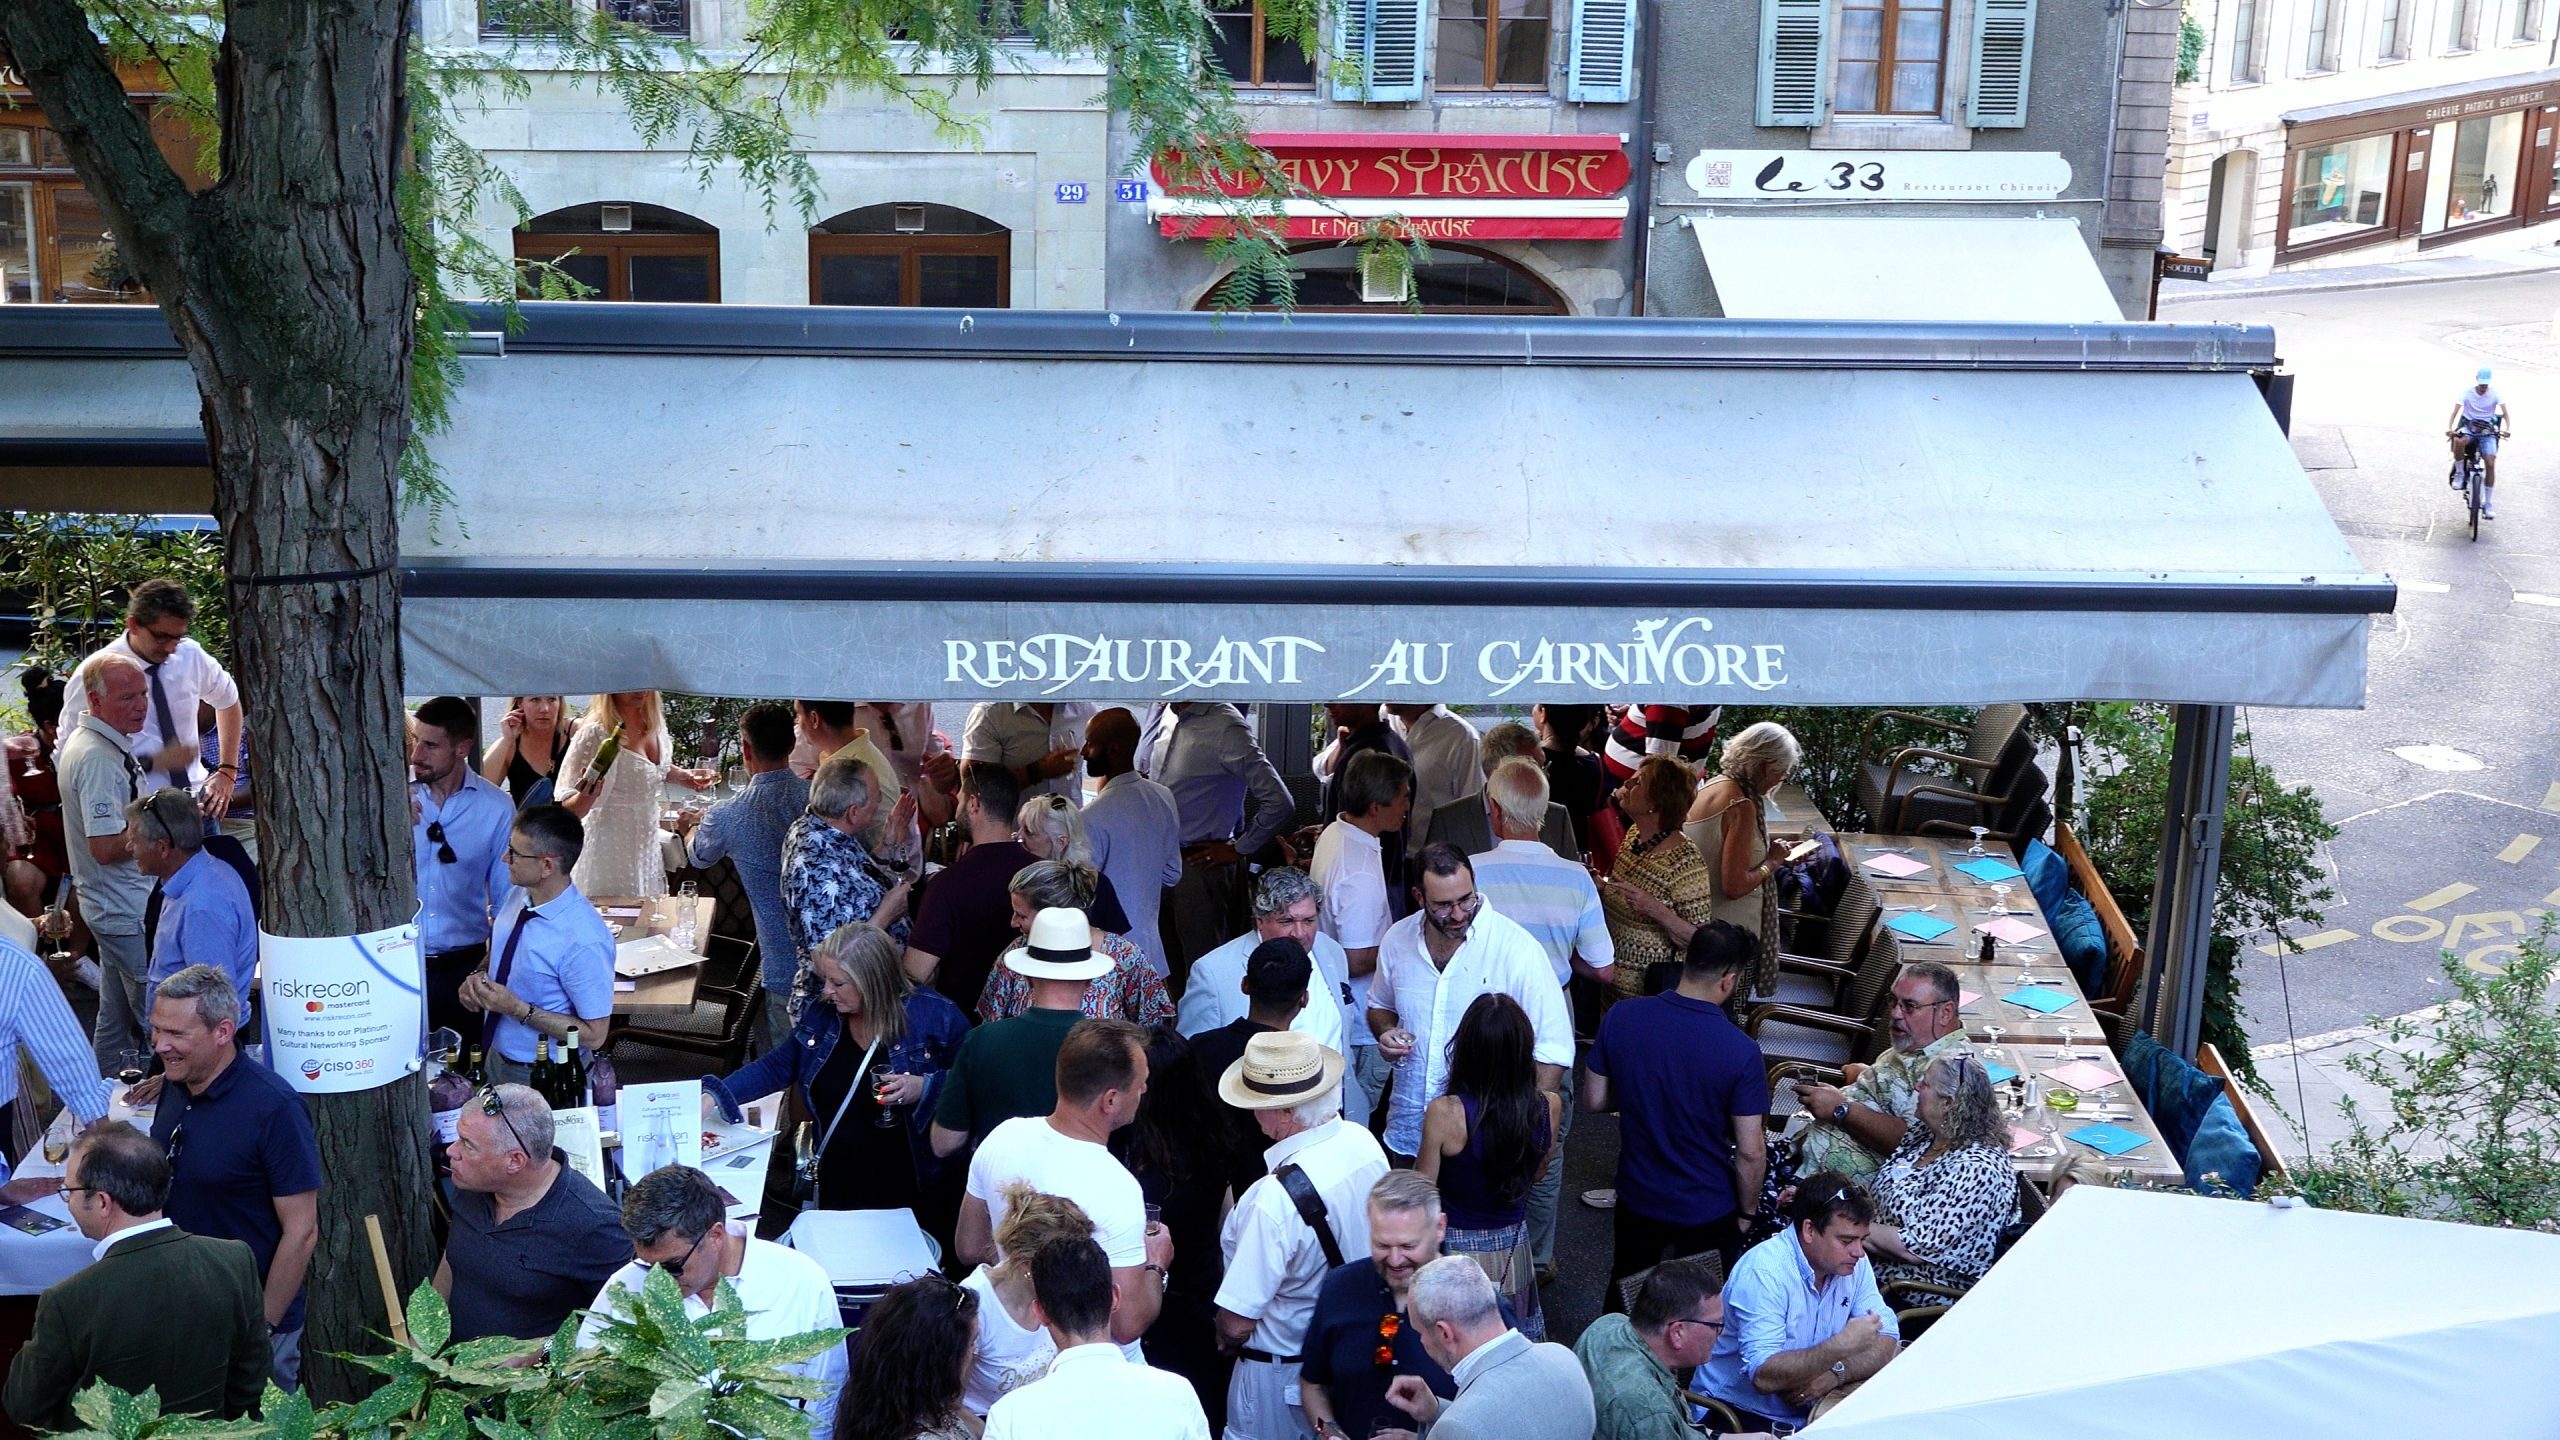 View Photos - Cheese & Wine Tasting & Walking Tour of Old Geneva & Dinner, Thursday 7th July 2022
Testimonials – CISO 360 series
 “One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).” – Andreas Prass, CISO & DPO, 360 Treasury Systems AG, Germany
“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.” – Carole Embling, Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” – Jorge Fernandes, CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.” – Matthias Muhlert Security Bear – CISO HARIBO, Germany
“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!” – Viktor Polic CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland
“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.” – Richard Bloxam-Rose, Threat and Vulnerability Consultant, Computacenter, United Kingdom
 “It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” – Deborah Saffer, Global Deputy CISO, Cushman & Wakefield
“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions
 “Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim
 “Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” – Jonathan Armstrong, CEO, Cordery
“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.” – Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK
“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World
“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
 “A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint
“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra
“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica
“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“
Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter
 “CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint
“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018
“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista
“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP