Archive · CISO 360 Global Congress

Flagship 4th CISO 360 Congress - Hybrid 2020

This event took place on 2nd & 4th December 2020 at Virtual.

Date2nd & 4th December 2020
VenueVirtual

Thank you so much to everyone who participated in the 4th Annual CISO 360 Congress, 2nd & 4th December 2020!

Wednesday 2 December, 10am-5pm GMT
4th Annual CISO 360 Congress Security-Hybrid 2020

Friday 4 December, 3pm-6pm GMT
Avatars CISO 360 Roundtable (3pm-5pm)
The ultimate benchmarking on CISO leadership priorities

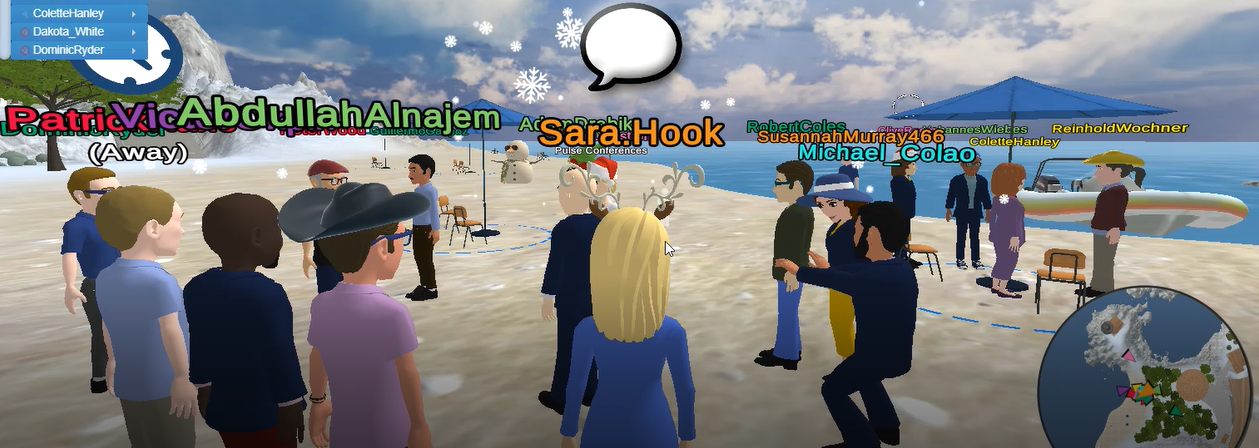
Security Avatars Beach (5pm-6pm)
Networking with CISOs, joined by CSOs

 Watch the 4th CISO 360 Congress 2020 On Demand!


Connecting Minds and Voices: Leveraging Cybersecurity for Trust, Transformation and Resilience

Trusted benchmarking and meaningful interaction for CISOs, cybersecurity practitioners and luminaries

CISO 360 series focused on the canny strategic and practical management of cybersecurity as a resilient business asset. Over 200 CISOs and senior information security practitioners from 25+ countries around the world joined the main fourth chapter of the flagship CISO 360 Congress – Hybrid 2020. 

CISO 360 Congress again offered the cybersecurity community a highly focused, content-led event and a forum in which to present and assess the latest strategies for managing cybersecurity, from culture to supply chain through to innovation, transformation and the maximisation of value. The programme was designed to provide you with critical updates on the emerging opportunity and risk horizon, role expectations and business technologies within the years to come. We invited CISOs to bring their experience to the discussion in a unique closed-door environment at a time when resilience, collaboration and building bridges in the cybersecurity field is more important than ever. Trusted partnerships and connections are vital, internally as well as with supply chains, stakeholders and customers.

The Pulse CISO 360 series is a leading influential community of C-suite and senior cybersecurity executives. Our mission is to forge a fundamentally better way to connect CISOs/CSOs and the most senior decision makers in business, risk and technology and provide access to the intelligence, knowledge and partners they need to move business agendas forward.

“By far the best event this year that I have attended. I always make the effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO MS Amlin

Keynote Speakers included.. 

Kai Roer,

Security Culture Coach / Author / Creator of the Security Culture Framework / CEO of CLTRe AS

Norway

Michael Colao, Chief Corporate Security Officer, AXA
United Kingdom

Sounil Yu, CISO, YL Ventures
United States

Speakers included.. 

  • Chaired by: Marcus Alldrick, CISO Luminary
  • Master of Ceremonies: Clive Room, Pulse Conferences
  • Alyssa Miller, Hacker/Researcher, Security Advocate, Application Advocate, Snyk
  • Anthony Young, Director, Bridewell Consulting
  • Beverley Allen, Head of Information Security Assurance, Quilter (Old Mutual)
  • Caroline Lawson, Field CTO UK, SailPoint
  • Carolyn Brown, Chief Information Officer, BMA
  • Colette Hanley, Group Head of Privacy, Nokia
  • Dominic Trott, UK Product Manager, Orange Cyberdefense
  • Evelyn Lekhtman, Agile Transformational SME, Strategist, Advisor, Agile Coach and Scrum Master (UK)
  • Gadi Evron, Security Expert, Formerly CISO with Israeli Government and CEO of Cymmetria, a cyber deception company (Israel)
  • Graham Edwards, Head of Cyber Security, Yorkshire Water (UK)
  • John Wood, UK Lead, Checkmarx (UK)
  • Jonathan Armstrong, Partner, Cordery (UK)
  • Marcus Dimbleby, VP and UK Leader, Red Team Thinking LLC (UK)
  • Lady Olga Maitland, Founder and CEO, Defence and Security Forum &  Copenhagen Compliance and Chairman, Algeria British Business Council
  • Paul Davies, Senior Solutions Architect, BeyondTrust (UK)
  • Air Commodore (Retired) Peter Drissell, Director, UK Civil Aviation Authority
  • Peter Wood, Partner and Lead Consultant, Naturally Cyber LLP
  • Prof. Dr. Robert Coles, Honorary Professor, UCL and Visiting Professor, Royal Holloway, University of London (UK)
  • Rainer Rehm, CISO, Zooplus AG (Germany)
  • Richard Bird, Chief Customer Information Officer, Ping Identity(USA)
  • Richard Hollis, Director, Risk Crew (UK)
  • Rik Ferguson, Vice President Security Research, Trend Micro and Special Advisor, Europol (Poland)
  • Rob Otto, EMEA Field CTO, Ping Identity
  • Sajed Naseem, CISO, New Jersey Courts (USA)
  • Shan Lee, CISO and DPO, TransferWise (UK)
  • Dr Vasileios Karagiannopoulos, Reader in Cybercrime and Cybersecurity, University of Portsmouth (UK)
  • Dr Victoria Baines, Visiting Research Fellow, Oxford Department of International Development (UK)
  • Dr Viktor Polic, CISO, Head of Information Security and Assurance Services, ILO-United Nations (Switzerland)

CISO 360 Congress – Hybrid 2020 (Wednesday 2 December, 10:00-17:00 GMT)

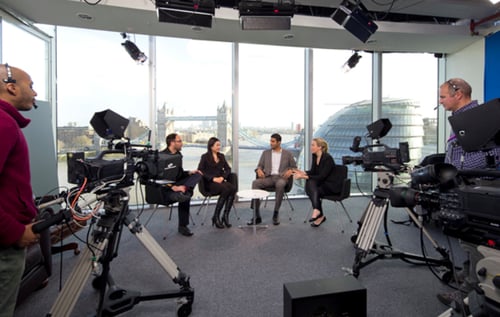
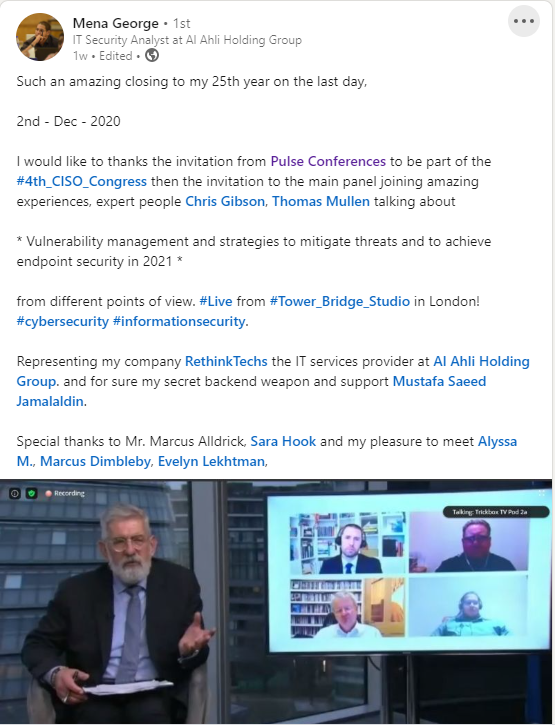
We broadcast Congress live from a Studio in London joined by Marcus Alldrick, our Chairperson, for live interviews fireside chats, case studies and keynotes. Delegates participated in live polls, joined us on the virtual stage, live Q&A, Chat, and in Breakouts where they met peers ‘face to face’.  Video networking with peers took part throughout the event.
 

Friday 4 December, 15:00-18:00 GMT

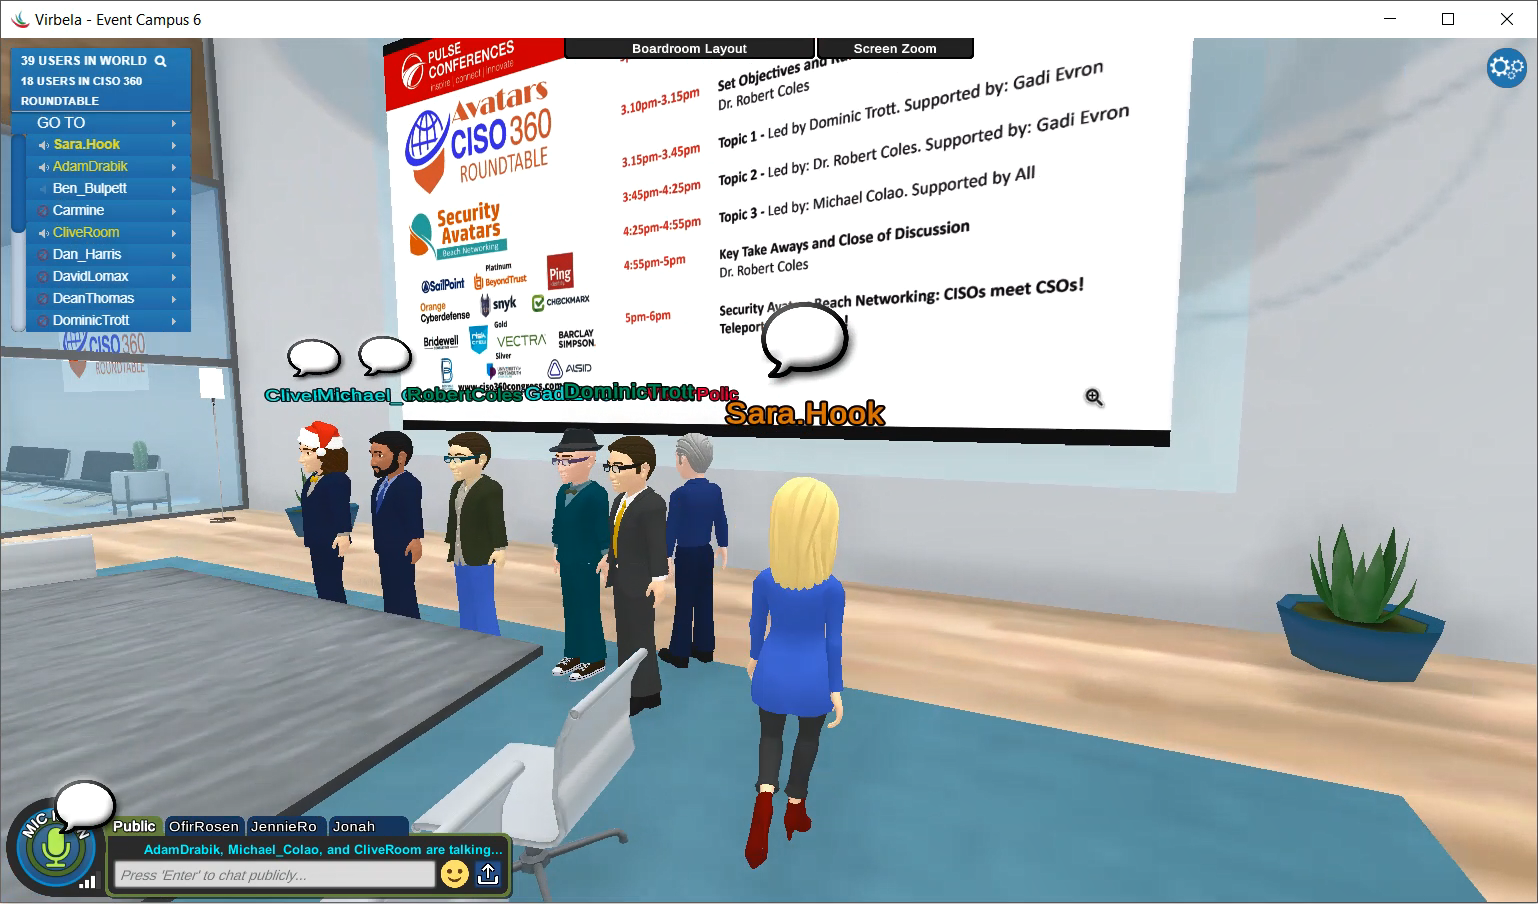
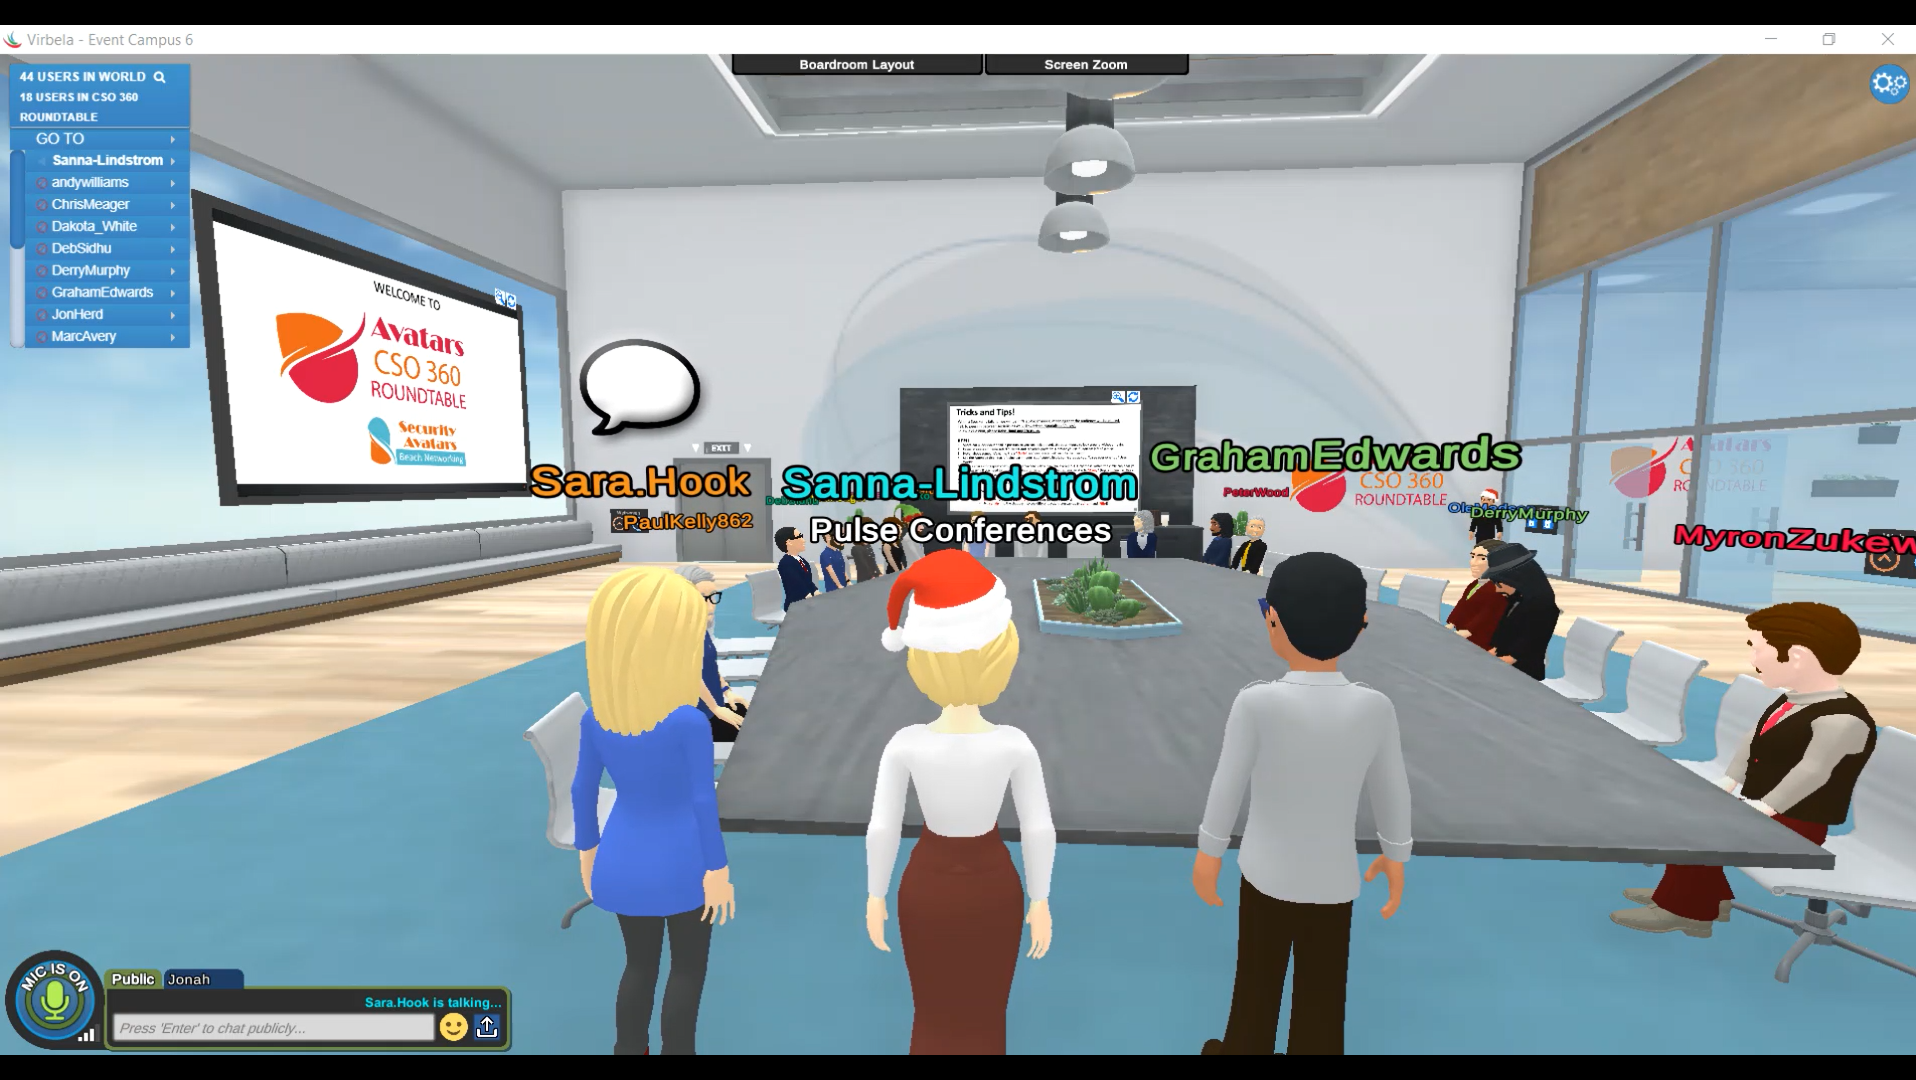
Avatars CISO 360 Roundtable

Followed by: Security Avatars Beach Networking 

Rethinking CISO leadership, culture and behaviours in a distanced world!

  • Led by, with and for CISOs
  • All invited guests invited to contribute to the discussion.
  • The discussion was held under the Chatham House Rule.
  • The talks ended with networking on a virtual beach!
  • Pre-event: You shaped the final agenda by inputting your top 3 current priorities.

The ultimate sound-boarding and benchmarking for today’s CISOs and cybersecurity, cyber threat intelligence leaders, this roundtable discussion was held under The Chatham House Rule. Talks ended with networking on the virtual beach where delegates chatted in private spaces around the island, danced, took speed boats and explored this new avatar world!  Through Avatars, we behaved as we would behave in a physical conference.  

This was about bringing you an innovative collaborative experience that feels safely and strangely familiar. This was about the real people, CISOs leaders, who inhabited the space.  People were surprised at how real it felt, given that the voices are spatial, meaning that as you walk close to someone you can hear one another.
SAVE THE DATE – 2021!
The 5th Annual CISO 360 Congress is booked for 7-9 July 2021 at the VP Plaza Design Hotel in Madrid.

Please save the date! If we cannot host in-person, the event will be digital. Either way it is happening.

Many thanks.
Team Pulse

Sponsorship opportunities

Check out what CISO 360 Congress looks like ‘in-person’! Highlights from 2019


Sponsors 4th CISO 360 Congress 2020

Platinum Sponsors

Gold Sponsors

Silver Sponsors
 

Speakers

The speaker panel and programme is currently being produced. We would very much value your input into companies, topics or specific persons you may like to see present at the 4th CISO 360 Congress – Virtual 2020! Please email:sara.hook@pulseconferences.comwith your thoughts, or if you would be interested in getting involved as a Speaker. Many thanks!

Chaired live from the Studio by:

Chaired by

Marcus Alldrick, CISO Luminary
Digital Risk Management, Security and Compliance Advisor

Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services and sits on the Cymmetria Advisory Board as Chief Risk Officer.

Keynotes by

Kai Roer, Security Culture Coach / Author / Creator of the Security Culture Framework / CEO of CLTRe AS

Kai Roer (author of “Build a Security Culture” by publisher IT-Governance) has over 25 years of experience in cybersecurity, with much of his expertise centered around security culture. He is currently managing director of CLTRe, a KnowBe4 company, where he is responsible for security culture research. Prior to founding CLTRe, Roer created the global de-facto standard Security Culture Framework. His groundbreaking research into security culture metrics provides organisations worldwide with deep insights into the human factors that influence risk and security. Roer is an award-winning specialist on security behaviors and security culture as well as a best-selling author. Roer keynotes at events around the world. He belongs to the Norway Chapter of the Cloud Security Alliance.

Michael Colao Chief Corporate Security Officer, AXA

Michael has been the head of security for AXA in the UK for more than five years. Prior to that he was a director of Downtown Associates, an information security and privacy consultancy, where he assisted firms in the Lloyd’s Insurance market. Previously to that he was the Global Head of Information Security as well as the Global Head of Privacy and Data Protection for the investment bank Dresdner Kleinwort, Michael has a strong side-interest in computer forensics and in the management of digital evidence. He graduated from the Massachusetts Institute of Technology in 1987 where he studied Mathematics and Computer Science. He has since lived in three continents and has lectured globally on security technology issues. Since 1996 has been working in Security and Technology in Financial Services in London.

First Keynote Speakers Announced! 4th CISO 360 Congress – Hybrid 2020

Enquire about becoming a speaker

We are always looking for:

  • keynote insights or cutting-edge ‘live’ demos
  • innovative best practice corporate case studies
  • fresh ideas from future-facing persons and companies
  • actionable takeaways
  • the world’s smartest thinkers and doers in security, resilience, cyber, privacy, resilience, risk, governance, compliance – BUSINESS AND TECHNOLOGY!

Speaker Rules of Thumb when it comes to programming and presenting at virtual events!

  • A virtual presentation should be half the length of a physical one. Focus on the physical presence of you as a speaker; that’s the experience people are not getting when they work from home!
  • Use PowerPoint sparingly, if at all. It is tough to read slides when they are a picture within a picture. People would much rather see your FACE! Place presentation prompts at the same level as your camera!
  • Try to turn a presentation into an interview or a fireside chat. This will increase authenticity and viewer-appeal. TV chat shows are popular for a reason. Pulse will confirm experienced anchors and chairpersons with nerves of steel. People who can listen to the Delegates, adjust their questioning on the fly and manage to keep the audience engaged when things go wrong!
  • Give news. Hold back important announcements to specific points i your session, and only release that news on other channels after the broadcast!
  • Leave plenty of time for questions. Pulse will gather Question Panels for a few Speakers at a time so stay around after your session!
  • Create a rhythm to your presentation. Create a flow between use of slides (if needed) or between yourself and fellow speakers if you are doing a joint session.
  • Content rule of thumb – “say what you can’t show, show what you can’t say”. Use talking heads about the vision but employ videos or a slide for internal cases studies to demonstrate the latest innovation in your office or factory!

We welcome your input into shaping the agenda!

Our programmes are highly researched and “led by, for and with” C-Level practitioners who do the job day in and day out. Programmes are structured and organic to ensure that we remain agile to meet the very latest requirements!

For further information, please contact Sara Hook
+44 (0)20 7936 8989 or sara.hook@pulseconferences.com

Alyssa Miller

Alyssa Miller

Snyk Application Security Advocate

Alyssa Miller (CISM) is a life-long hacker, security advocate, author, and public speaker with almost 15 years of experience in security roles. She has always had a passion for deconstructing technology, particularly since buying her first computer at the age of 12 teaching herself BASIC programming. In her career, Alyssa has performed all forms of security assessments but given her developer background, she has a dedication to application security. She specializes in working with business and security leaders to design and deploy effective security programs that strengthen enterprise security posture. Alyssa is also committed to advocating for improving security practices. Not only does she speak internationally at various industry, vendor and corporate events, Alyssa also engages in the community through her online content, media appearances, and security community activism. Her journey through security was recently featured in Cybercrime Magazine. She’s also been recognized in Peerlyst’s e-Book “50 Influential Penetration Testers”. Alyssa is board member for Women of Security (WoSEC), Advisory Board Member for BlueTeam Con, and serves on the review board for DevSec Con. She is currently an Application Security Advocate for London-based Snyk Ltd.

Anthony Young

Anthony Young

Director, Bridewell Consulting

Anthony Young is a Founding Director at Bridewell Consulting, one of the UK’s leading independent cyber security companies certified by the National Cyber Security Centre (NCSC) and Council for Registered Ethical Security Testers (CREST).
Anthony has been involved in cyber security for more than 16 years, with a background in information security, governance, risk and compliance.
After starting his career with a small consulting company providing advisory services to the public sector, Anthony joined Barclay Simpson to develop its contract information security division. This gave great exposure to understanding large enterprise cyber security requirements, building teams and managing multiple resources across a wide variety of projects.
Anthony founded Bridewell Consulting in 2013, using his consulting, project and resource management skills to build a world-class cyber security company that focuses on customer satisfaction and long-term relationships.

Caroline Lawson

Caroline Lawson

Field CTO UK, SailPoint

Caroline is an experienced Identity Strategist and Sales Engineering Leader with many years consulting and delivery involvement, focusing on large scale Security and IGA platforms within the financial sector.  She sat in the position of the customer for many years leading programmes of work, as well as in leadership positions across the Security Vendor landscape. She graduated from the University of Southampton with a degree in Modern languages, speaking fluent German, Swedish and Dutch and is based in Oxfordshire.

Clive Room

Clive Room

Director of Events, Pulse Conferences

Clive Room began his professional career in 1970 as the original Heinz Baked Beans boy, in an advert that ran for twelve years! The repeat fees kept Clive in a decent school and his Mother in gin until the mid-80s!

After more than 20 years of acting, when the call from Hollywood failed to come, Clive became a Blue Badge Tour Guide, performing all over the UK to a captive audience of fifty Americans a day on a luxury coach with the doors locked. After winning Guide of the Year in 1996, he felt his touring career could get no better, so he made his first foray into the Information Security industry for Portcullis Computer Security, where he was hired (by the hour) as eye candy for their stand at Infosec. He then became Portcullis’ Marketing Manager to the Stars until their acquisition in 2016. At this point he took a short break to find himself, with the aid of a loin cloth and an Indian mystic, up an Airbnb treehouse in the foothills of the Himalayas. There are no known photographs from this period.

Clive joined Pulse from its inception in January 2017 as their Master of Ceremonies and chief bottle washer. This year he is celebrating his 21st year in the industry and says “ as a young man, with most of my life ahead of me, I can not imagine a better job than the one I have now at Pulse Conferences”. Amongst other things, Clive is responsible  for CISO 360’s one-to-one meetings, an area in which he has a great deal of personal experience.

Derek Cheng

Derek Cheng

CISO, TalkTalk

An experienced information security leader with over 19 years of professional experience in information and cyber security, IT, risk management, privacy and data compliance. Derek has recently joined TalkTalk as their Chief Security Officer, where he is building and leading the cyber security strategy and team to protect TalkTalk’s critical infrastructure, assets, and customer data. Previously, he was the Global Head of Security and Risk Management (CISO) at Electronic Arts (EA) where he led a large, global team to protect EA’s intellectual property and sensitive data. Prior to EA, Derek spent over 6 years at Deloitte & Touche where he managed and performed a multitude of information security and risk management engagements for several global Fortune 500 companies across various industries including financial services, technology, consumer business, manufacturing, and public sector. His primary areas of expertise include developing and leading tactical and strategic security strategies, building and maturing security teams, and ensuring executive governance around security to manage risks appropriately. Derek has also published information security articles and white papers and has been a presenter/panellist at CISO conferences. Derek holds a Bachelor Degree in Computer Science from the California Polytechnic State University,

Evelyn Lekhtman

Evelyn Lekhtman

Agile Transformational SME, Strategist, Advisor, Agile Coach and Scrum Master

Agile Leader, Agile Coach & Delivery SME, Transformational Lead, Business Agility Specialist – Helping individuals, teams, leaders and the organisation achieve value add Agility @ Scale. Evelyn is known in industry as an agile coach, transformational leader, delivery SME, facilitator, speaker and practitioner with a trusted pair of hands, an exceptionally positive mindset, an infectious enthusiastic attitude and a great passion for agility. 22 years of Industry experience across large scale financial institutions including investment banks, public sector, aviation, energy including utilities, small and mid-size software houses and consultancies. Today she plays non-exec director level roles, as well as, a senior level agile/business coach helping any size of organisation be adaptable to the changing environments whilst maintaining security, stability and sustainability for both the people, product development, the foundations of the operation and the customer. Certified in SAFe, LeSS, and Scrum. A member of the Heart of Agile Leadership Community. Currently in the process of becoming an Red Team Thinking Coach and a Remote:AF Guide.

Summary of successful impacts:
Involved in an HR transformation which formed part of global transformation which helped the client increase their overall yearly turnover from £1B to £5B in 1 year.
Direct total savings for clients circa £25m over across 4 programmes and 3 transformations.
Direct impact circa 1,600 people improving overall delivery and agility techniques.
Indirect impact circa 5,000 people by influencing, evangelising and sharing stories via Show and Tells to help promote business agility.
Encouraged and trained people in the use of agile techniques and collaboration tools to reduce time spent within the project/programme delivery flow.
Supported technical teams to deliver DevOps toolsets to speed up code check-in to code deploy cycle times and improve overall code and product quality.
Helped multiple teams and leaders to feel empowered and truly experience success by applying agile techniques.

Gadi Evron

Gadi Evron

Domain Lead, Cyber Innovation Lab, Citi

Gadi heads the AppSec, Information Sharing (TI), Incident Response, and Third-party Risk domains for Citi’s global cyber innovation lab in Tel Aviv, looking into new technologies from the idea phase, through technical PoC, to full integration with the bank. He is Chair, RISCC Cyber Risk Council of the World Economic Forum, an advisory council with WEF, discussing, and engaging on cyber risk topics. He is the Founder and Chairman of the Board of the Israeli CERT, Founding Chairman of the Cyber Threat Intelligence Alliance (CTIA), and Founder of the Israeli Government CERT. Gadi is widely recognized for his work in Internet security operation and global incident response, and is considered the first botnet expert. Gadi founded Cymmetria which was acquired in 2019, a cyber security company changing the asymmetry of cyber for the enterprise environments. He has authored two books on the topic of information security, organizes global professional working groups, chairs worldwide conferences, and is a frequent lecturer.

Jonathan Armstrong

Jonathan Armstrong

Partner, Cordery Compliance

Jonathan is an experienced lawyer with a concentration on technology and compliance. His practice includes advising multinational companies on matters involving risk, compliance and technology across Europe. He has handled legal matters in more than 60 countries involving emerging technology, corporate governance, ethics code implementation, reputation, internal investigations, marketing, branding and global privacy policies. Jonathan has counselled a range of clients on breach prevention, mitigation and response. He has also been particularly active in advising multi-national corporations on their response to the UK Bribery Act 2010 and its inter-relationship with the U.S. Foreign Corrupt Practices Act (FCPA). Jonathan is one of three co-authors of the LexisNexis definitive work on technology law, “Managing Risk: Technology & Communications”. He is a frequent broadcaster for the BBC and other channels and appeared on BBC News 24 as the studio guest on the Walport Review. In addition to being a lawyer, Jonathan is a Fellow of The Chartered Institute of Marketing. He has spoken at conferences in the U.S., Canada, China, Brazil, Singapore, Vietnam, the Middle East and across Europe. Jonathan qualified as a lawyer in the UK in 1991 and has focused on technology, risk and governance matters for more than 20 years. In April 2017 Thomson Reuters listed Jonathan as the 6th most influential figure in risk, compliance and fintech in the UK. Jonathan was ranked as the 14th most influential figure in data security worldwide by Onalytica in their 2016 Data Security Top 100 Influencers and Brands Survey. In 2019, Jonathan was the recipient of a Security Serious Unsung Heroes Award for his work in Information Security. In 2020, Jonathan was featured by Onalytica in their Who’s Who in cybersecurity report as one of the world’s top 100 influencers in cybersecurity. Jonathan is a Solicitor of the Senior Courts of England & Wales. In addition Jonathan is admitted as a Solicitor (non-practising) in Ireland.

John Wood

John Wood

Application Security Specialist, Checkmarx

John Wood, the UK Lead at Checkmarx has been working at the forefront of Application Security since 2006, he was responsible for establishing Fortify Software in the United Kingdom and Europe. He has worked on numerous Application Security Projects – good and bad. Areas of special interest are OpenSAMM and the advanced use of measurement and metrics to assist CISO’s in running successful programs of work. He is frequent and entertaining speaker at industry events often using allegories from subjects as diverse as Physics, Geometry, Ethology and Classical Economics to explain the route to successful Application Security. A graduate of Portsmouth University and Queensland University of Technology he holds degrees in Economic History, Entrepreneurship and Technology Management.

Marcus Dimbleby

Marcus Dimbleby

Red Team Thinking

Marcus Dimbleby is a former senior UK military officer and red teamer who has been sharing these techniques with corporations since retiring from the Royal Air Force in 2013. In the RAF, he served across the globe, enjoying tours with the Royal Marines, Royal Navy and U.S. Marine Corps, with whom he deployed to Iraq in 2003. His final tour saw him in an air command role, working closely with the Cabinet Office, and coordinating the air security for the London Olympics 2012 – a natural red teaming event. After retiring as a Wing Commander, Marcus moved into business, initially working for a global consultancy, before moving on to lead major business transformations in the financial sector, focusing on enabling leadership to deal with the complexity of today’s volatile business environment. Marcus now assists organisations with making better decisions faster and provides red team training across the globe.

Dr. Robert Coles

Dr. Robert Coles

Director, Cumberland House Consulting Ltd, Honorary Professor, UCL and Visiting Professor, Royal Holloway, University of London

Dr. Robert Coles is the Director of Cumberland House Consulting Ltd, specialising in cyber security strategy, programme delivery and Non-Exec and Board Advisory roles. He is also an Honorary Professor at UCL and Visiting Professor at Royal Holloway, University of London. He holds a number of commercial board positions including Chair of the Crossword Consulting Ltd Board, Chair of the Crossword Cybersecurity PLC advisory board, member of the advisory boards for Think Cyber Ltd, UK bank, a US pharmaceutical and the Government of Singapore Ministry of Health and member of the Tech-Nation Cybersecurity judging panel. Robert has over 30 years of cybersecurity experience and has held a number of Chief Information Security Officer positions, including for the NHS and health and care system, GSK, National Grid and Merrill Lynch.  In all these roles, he owned the information security risk and was responsible for providing leadership across the organisations. He was accountable to the Executive and their Boards for establishing information security strategy and direction, building information security teams and delivering the information security change programme. Prior to these CISO roles, he held a number of “head of” roles at Royal Bank of Scotland, and was the first lead partner, and set up, KPMG’s Information Security Services for EMEA. Robert has extensive links with major industry information security networking groups and government security agencies.  He also has links with a number of universities and participates in leading edge research, particularly with Royal Holloway where he is an Executive Sponsor for the Institute of Information Security Innovation, and Cranfield University where he is an executive sponsor for the Cyber Masters Programme. He was awarded a PhD in psychology by the University of Leeds for his work on the perceptions of information and IT risk and has published and presented on this and other topics.

Ray Stanton

Ray Stanton

Executive Partner, IBM Security

An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK.  He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.

Dr. Victoria Baines

Dr. Victoria Baines

Visiting Research Fellow, Oxford Department of International Development

Victoria Baines is a leading author and speaker in the field of cybersecurity. Her areas of research include electronic surveillance and evidence gathering, the changing face of online identity, and the politics of cybersecurity. She has appeared on the BBC, CNN and other major broadcast media outlets as an authority on the misuse of emerging technologies, including Virtual Reality. She serves on the Advisory Board of the International Association of Internet Hotlines (INHOPE). For several years, Victoria was Facebook’s Trust & Safety Manager for Europe, Middle East and Africa. Her work focused on operational support to law enforcement, and strategic engagement with policy makers on criminal activity online. Before joining Facebook, Victoria led the Strategy & Prevention team at Europol’s European Cybercrime Centre (EC3), where she was responsible for the European Union’s cyber threat analysis. She designed and developed the iOCTA, Europe’s flagship product on cybercrime, and authored 2020, scenarios for the future of cybercrime that were the basis for Trend Micro’s successful short film series of the same name. Earlier in her career Victoria was Principal Analyst for online child protection at the UK Serious Organised Crime Agency (SOCA), and was responsible for the UK’s threat assessment of online child safety issues. She began her career in law enforcement in 2005 as a Higher Intelligence Analyst for Surrey Police. In 2008, the International Association for Law Enforcement Intelligence Analysts recognised Victoria’s work for the public sector with an award for outstanding achievement. Victoria is a graduate of Trinity College, Oxford and holds a doctorate in classical literature. She is a Visiting Associate of the Oxford Internet Institute (Oxford University), and a Visiting Fellow at Bournemouth University School of Computing.

Air Commodore Peter Drissell MA

Air Commodore Peter Drissell MA

BSc, FCGI, FIoD (Rtd) Director Aviation Security, Civil Aviation Authority

Peter was appointed by the Civil Aviation Authority (CAA) as its first Director of Aviation Security in 2013 and led the transition of operational aviation security functions from the Department for Transport (DfT) to the CAA on 1st April 2014. He took on the additional responsibility for Cyber Security Oversight of the UK aviation sector in 2018. He is a member of the CAA ExCo and a Board attendee. Peter had previously been Director of Security & Business Continuity for the Home Office and, prior to that, had served for 32 years in the Royal Air Force from which he retired as an Air Commodore in April 2007. His last appointments were as Provost Marshal for the RAF and Commandant General of the Royal Air Force Regiment. Peter had served as a Non-Executive Director of Plan UK, an international children’s charity for 10 years, and until 2014 had been a trustee of the City and Guilds Group; he remains on the governing council of that organization.

Peter Wood

Peter Wood

Partner and Lead Consultant Naturally Cyber LLP

Peter’s career spans over 50 years, with experience in network security, social engineering, threat and risk analysis, red teaming, industrial control systems and electronics.

​He founded First Base Technologies, the UK’s first cybersecurity consultancy, in 1989. He provided security testing and guidance for businesses of all sizes for more than 28 years, leading a team of expert penetration testers and consultants.

He is now Partner and Lead Consultant at Naturally Cyber LLP, providing senior management with independent expert advice, guidance on achieving Cyber Resilience, and education on the real cyber risks to business.

Peter is also a world-renowned security evangelist, speaking at major conferences and delivering seminars and webinars. He has appeared in documentaries for BBC television, provided commentary on security issues for TV and radio, and written numerous articles on cybersecurity.

He is a BCS Fellow, a Chartered IT Professional, CISSP, and a member of CIISec, ISACA and Mensa. He is also a visiting lecturer at the University of Sussex, teaching cybersecurity and resilience.

Paul Davies

Paul Davies

Senior Solutions Architect, BeyondTrust

Paul is a highly capable and readily adaptable technical professional, with more than 15 years experience supporting hardware and software solutions globally. Possessing a proven ability to meet and exceed customer demands, and business objectives, in challenging conditions and circumstances. Paul has amassed a wealth of experience working within the Security and Defence sectors, as well as Central Government, Public Sector and Commercial markets.

Rob Otto

EMEA Field CTO, Ping Identity

Rob is a Principal Architect for Ping Identity in the UK and also the EMEA representative to the Ping Identity CTO Office. Rob has 20 years of experience in identity and access management. He has worked on complex implementation projects in the UK, USA, Europe and South Africa.

His current area of focus is on applying industry standards like OpenID Connect and OAuth 2.0 to enable businesses to interoperate and securely expose data and API’s. He is specifically focused on using Mobile Applications to deliver elegant Strong Customer Authentication solutions within financial services and other verticals.

Richard Bird

Richard Bird

Chief Customer Information Officer, Ping Identity

Richard Bird is the chief customer information officer for Ping Identity. He is a cyber security veteran, identity-centric security expert, voice of the customer and an advisor to the global marketplace on solutions for the most challenging business issues faced in today’s world. Richard is a dynamic international speaker and a pragmatic former corporate executive that cuts through the hype and hyperbole of today’s cyber security realities and does it in an engaging and thought-provoking way.

He has spent more than 20 years in corporate business and technology roles within multiple industries. His diverse background includes serving as a chief information officer, a chief information security officer and the global head of identity for JPMorgan Chase’s consumer businesses. Richard’s combination of IT operations and security experience have afforded him the opportunity to be a trusted and strategic advisor to hundreds of companies for topics ranging from identity-centric security, to threat and vulnerability management, data protection and cloud security. Richard is a member of the Forbes Tech Council and a board member for the Identity Defined Security Alliance.

Rik Ferguson

Rik Ferguson

Vice President Security Research, Trend Micro and Special Advisor, Europol

Researcher, writer, filmmaker and presenter Rik Ferguson is the Vice President of Security Research at Trend Micro and a Special Adviser to Europol’s EC3. Rik’s research into the murky world of cybercrime and the cloudy future of technology sees him advise law enforcement, governments and large enterprises alike. A session with Rik will leave you with a lot to rethink.

Richard Hollis

Director, Risk Crew

Professional information security governance, risk & compliance consultant with over 30 years of hands on skills & experience in:

• Threat Assessments & Risk Analyses
• Supply Chain Information Risk Management
• Information Security Policies & Procedures
• Security Vulnerability Assessments
• Security Penetration Testing
• Advanced Persistent Threats
• Wi-Fi Security Assessments
• Cloud Security Assessments
• Mobile Device Security
• Insider Threat & Data Leakage
• Security Awareness Training

Sajed Naseem

Sajed Naseem

Chief Information Security Officer (CISO), New Jersey Courts

Sajed Naseem (“Saj”), is the Chief Information Security Officer (CISO) of New Jersey Courts.  Sajed has over twenty years of experience with information security and information technology across many industries.  As the Chief Information Security Officer (“CISO”) of the New Jersey Courts, Sajed has focused on Cybersecurity Readiness & Performance, Information Governance, and Network Security.  Sajed holds Masters Degrees from St. John’s University and Columbia University.  Sajed routinely speaks at Cybersecurity conferences nationally, Europe and with the New Jersey Bar Association.  Sajed is also an Adjunct Professor at St. John’s University in Information Security since 2010 and a native of New York City.

Sounil Yu

Sounil Yu

CISO, YL Ventures (USA)

Sounil Yu is a Christian, husband, and father with over 30 years of hands-on security experience. He is the creator of the Cyber Defense Matrix and the DIE Resiliency Framework, serves on the Board of SCVX Corp and the FAIR Institute, teaches security as an adjunct professor, co-chairs Art into Science: A Conference on Defense, and advises many startups. He previously served as the Chief Security Scientist at Bank of America, driving innovation to meet emerging security needs and develop alternative approaches to hard problems in security. Although on occasion he is forced to write about himself in the third person, he would rather meet people in person to share experiences rather than writing it up in a short bio. He lives in Virginia with his wife and their four homeschooled children.

Dr. Vasilis Karagiannopoulos

Dr. Vasilis Karagiannopoulos

Reader in Cybercrime and Cybersecurity at the Institute of Criminal Justice Studies (ICJS), University of Portsmouth

Dr. Vasilis Karagiannopoulos is a Reader in Cybercrime and Cybersecurity at the Institute of Criminal Justice Studies (ICJS), University of Portsmouth.Vas graduated from Athens Law School and completed an LLM in Information Technology and Telecommunications Law and a PhD in Law at the University of Strathclyde. He is currently the Director of the Cybercrime Awareness Clinic, which was recently awarded a National Cyber Awareness Award in the National Cyber Awards 2020 sponsored by the National Police Chiefs’ Council. He has also developed and led the launch of the innovative BSc in Criminology and Cybercrime in 2018 and has published in national and international academic journals and magazines on various cyber-related issues. He is currently working on national and international Clinic projects funded by the EU Commission, the UK National Cyber Security Centre and the Centre for Research and Evidence on Security Threats.

Sponsors
SailPoint

SailPoint, the leader in enterprise identity governance, brings the Power of Identity to customers around the world. SailPoint’s open identity platform gives organizations the power to enter new markets, scale their workforces, embrace new technologies, innovate faster and compete on a global basis. As both an industry pioneer and market leader in identity governance, SailPoint delivers security, operational efficiency and compliance to enterprises with complex IT environments. SailPoint’s customers are among the world’s largest companies in a wide range of industries, including: 7 of the top 15 banks, 4 of the top 6 healthcare insurance and managed care providers, 9 of the top 15 property and casualty insurance providers, 5 of the top 15 pharmaceutical companies, and 11 of the largest 15 federal agencies.

www.sailpoint.com

BeyondTrust

BeyondTrust is the worldwide leader in Privileged Access Management (PAM), empowering organizations to secure and manage their entire universe of privileges.  Our integrated products and platform offer the industry’s most advanced PAM solution, enabling organizations to quickly shrink their attack surface across traditional, cloud and hybrid environments.

The BeyondTrust Universal Privilege Management approach secures and protects privileges across passwords, endpoints, and access, giving organizations the visibility and control they need to reduce risk, achieve compliance, and boost operational performance.  Our products enable the right level of privileges for just the time needed, creating a frictionless experience for users that enhances productivity.

With a heritage of innovation and a staunch commitment to customers, BeyondTrust solutions are easy to deploy, manage, and scale as businesses evolve. We are trusted by 20,000 customers, including 70 percent of the Fortune 500, and a global partner network.

www.beyondtrust.com.

Checkmarx

Checkmarx is the Software Exposure Platform for the enterprise. Over 1,400 organizations around the globe rely on Checkmarx to measure and manage software risk at the speed of DevOps. Checkmarx serves five of the world’s top 10 software vendors, four of the top American banks, and many government organizations and Fortune 500 enterprises, including SAP, Samsung, and Salesforce.com. Learn more at Checkmarx.com or follow us on Twitter: @checkmarx.

Snyk

Ping Identity

Ping Identity is the Intelligent Identity solution for the enterprise. We enable companies to achieve Zero Trust identity-defined security and more personalized, streamlined user experiences. The Ping Intelligent Identity™ platform provides customers, workforce, and partners with access to cloud, mobile, SaaS and on-premises applications across the hybrid enterprise. Over half of the Fortune 100 choose us for our identity expertise, open standards, and partnerships with companies including Microsoft and Amazon. We provide flexible identity solutions that accelerate digital business initiatives, delight customers, and secure the enterprise through multi-factor authentication, single sign-on, access management, intelligent API security, directory, and data governance capabilities.

For more information, visit  www.pingidentity.com

Orange Cyberdefense

We are proud of our high-end security research unit, thanks to which we publish regularly white papers, articles and tools on cybersecurity which are widely recognised and used throughout the industry and featured at industry conferences. Overall Orange Cyberdefense has the following

www.orangecyberdefense.com

Bridewell Consulting

Bridewell Consulting is a leading specialist cyber security and data privacy company, focused on delivering outstanding long-term strategic consultancy and solutions to clients. With extensive experience in delivering large-scale transformational projects in highly regulated environments, Bridewell advises on driving strategic change securely. It provides a full breadth of end-to-end cyber security and information assurance services to protect an organisation’s data, reputation, and day-to-day operations. Hiring the best people, Bridewell’s expert team comprises of a diverse range of highly skilled consultants, supported by industry leading technology, deep technical expertise, accredited methodologies and a client-centric business driven approach. This team is propelled by a passion to meet Bridewell’s uncompromising standards, always striving for greatness and going above and beyond expectations. Bridewell is a trusted partner to over 100 clients across the fintech, aviation, critical national infrastructure, technology, and healthcare industries, and works closely with industry bodies and regulators on national frameworks. And its security operations centre gives clients 24/7 peace of mind. Offering the latest cutting-edge technology from a portfolio of vendors, Bridewell has the accreditations to demonstrate its capability including NCSC, CREST, ASSURE, IASME Consortium, Cyber Essentials Plus, ISO27001 and ISO9001.
www.bridewellconsulting.com

Risk Crew

Risk Crew is an elite group of product-independent, information governance, risk, and compliance management professionals. We’re the forerunners in the design and delivery of effective business information and communication technology risk and security solutions. We understand business risk and compliance and so we also excel in the creation of operative controls and processes to cost-effectively comply with legislation, regulation and best commercial practices such as the Payment Card Industry (PCI), Data Security Standards (DSS), the UK Data Protection Act (DPA) and ISO/IEC 27001. Risk Crew take great pride in the depth and breadth of our technical and tactical knowledge and will work to ensure that it’s fully leveraged to provide the greatest benefit to your business objectives. We also put skin in the game and guarantee all of our services. Consequently, we are the selected supplier of choice for hundreds of businesses in virtually every commercial sector across the United Kingdom. www.riskcrew.com 
Vectra

Vectra® protects business by detecting and stopping cyberattacks.

As a leader in network detection and response (NDR), Vectra® AI protects your data, systems and infrastructure. Vectra AI enables your SOC team to quickly discover and respond to would- be attackers —before they act.

Vectra AI rapidly identifies suspicious behavior and activity on your extended network, whether on-premises or in the cloud. Vectra will find it, flag it, and alert security personnel so they can respond immediately.

Vectra AI is Security that thinks®. It uses artificial intelligence to improve detection and response over time, eliminating false positives so you can focus on real threats.

www.vectra.ai

Barclay Simpson

Barclay Simpson is a specialist international corporate governance recruitment company providing contingent and retained permanent recruitment solutions and interim contract services. Our consultants, based in our offices in London, and New York work with our clients throughout the UK, Europe, the Middle East and North America. We recruit for a wide range of leading commercial, banking, financial services, professional services and public sector organisations. We specialise in recruiting for the distinct but interrelated disciplines of Internal & IT Audit; Risk Management; Compliance; Security & Resilience; Legal and Treasury.

www.barclaysimpson.com

Bestman Solutions

Owanate Bestman, founder of Bestman Solutions, has spent almost a decade recruiting in the Cyber Security field. Securing individuals and teams that meet specific technical and/ or leadership requirements for some of the world’s most innovative firms to the mutual benefit of individuals’ career progression and the company’s needs.
www.bestmansolutions.com

University of Portsmouth

The University of Portsmouth is a world-class institute making its TEF Gold teaching accessible to people regardless of their location. Its online, part-time MSc Cybercrime equips students with the criminological and sociological expertise needed to approach the behaviours that lead to deviant and law-breaking actions. The tutor-led course is supported by the university’s award-winning Cybercrime Awareness Clinic, which offers students the opportunity to collaborate remotely with specialists in the field. With all course material hosted online, and a personal adviser assigned to each student, the programme offers a supportive environment for distance learners to succeed.

Alsid

Alsid is a cybersecurity vendor specializing in defending the common denominator of most attacks we see in the wild nowadays: Active Directory (AD) infrastructures. As a fully-automated cloud solution, Alsid for AD provides users with step-by-step, tailored recommendations for hardening their AD, a real-time attack detection engine, as well as capabilities for investigating AD breaches when they unfortunately occur. Whether in the cloud or on premise, Alsid is easy to deploy and operate- no specialized security knowledge required.

Founded in 2016 by two former incident responders from the French National Cybersecurity Agency (ANSSI), Alsid is a hypergrowth cybersecurity vendor headquartered in Paris with a global reach.

Alsid is protecting over 6 million users across the world to help safeguard against advanced attacks. With the numerous recent attacks exploiting Active Directory weaknesses, it’s time to care about your AD security.

Link to the website: https://www.alsid.com/

Who attends

By Designation

  • Chief Information Security Officers 
  • Directors of Cybersecurity / Senior Cybersecurity Practitioners
  • Heads of Cyber Threat Intelligence
  • Chief Information Risk Officers
  • CEOs, R&D, CTOs, CIOs, Innovation
  • Chief Risk Officers
  • Chief Security Architects / Heads of Security Infrastructure
  • Directors of Technology Innovation or Directors of Digital Risk
  • Chief Data Officers 
  • Chief Privacy Officers 

Attendees are from across private and public sectors, including but not limited to:

  • Financial Services and Insurance
  • Energy, Utilities, Power, and Extractive Industries
  • Critical National Infrastructure Companies 
  • Pharmaceuticals, Medical, Health
  • Consumer Goods, Electronics, Services
  • Manufacturing, Construction, Engineering
  • Retail, eCommerce
  • Gaming, Gambling
  • Transport, Logistics, Automotive
  • Government, Intergovernment

By Region

  • UK – circa 45%
  • Across Europe – circa 45% 
  • Rest of World – circa 10%

Testimonials – CISO 360 series

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra

“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim

“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica


“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS

“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore


“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World

“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP

“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint


“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack


“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85


“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“

Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin


“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat

Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh

— Holly Foxcroft (@holly_foxcroft) 21 June 2018

“A very engaging, varied and interactive event. The best conference I have ever attended!”

Information Security Manager, Lloyd’s of London


“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA


“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint


“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin


“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext

It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO

— Viktor Polic (@ViktorPolic) 26 June 2018


“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government


“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4


“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal


“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller


“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe

Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !

— Quentyn Taylor (@quentynblog) 21 June 2018


“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland


Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz

— Quentyn Taylor (@quentynblog) 21 June 2018

“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom

““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv

Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo

— avatao (@theavatao) 21 June 2018


High quality 60mins #CISO360 ⁦@mikko⁩ pic.twitter.com/khkIJhzsBB

— Jonathan Luff (@jjluff) 20 June 2018

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint

“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV


“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum


““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd

““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting


Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!

— Jonathan Luff (@jjluff) 20 June 2018


Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC

— Dr Victoria Baines (@cyberbaines) 21 June 2018


“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)


Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv

— AP2SI (@AP2SI) 22 June 2018


“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!” Corporate Security Manager, Logista

“Marvellous event, well-run, packed with useful content you can use”, Technology Services Head of Security, DWP


Testimonials videos