Thank you for everyone who attended the 2nd CISO 360 Asia & Oceania, 13-14 September 2022, The Fullerton Hotel Singapore
Registration is opening soon
“If you want to hear real CISO experiences, you must attend this event!”
– Chuan-Wei Hoo, CISO, ST Engineering Singapore
“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
– Ryan Chan, Director, Security, Laureate International Universities Malaysia
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
– Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
Pulse Conferences hosted the 2nd edition of CISO 360 Asia & Oceania, a regional Conference in Singapore in September 2022. CISOs, CTOs, CIOs, technology, risk and governance practitioners and leaders from across the APAC and Oceania region and beyond gathered to benchmark progress and approaches to cybersecurity challenges.
An engaging and immersive experience where participants was given the time and space to debate and bond with peers and to have those nuanced conversations. This was the ideal opportunity to meet CISO peers to engage, learn and benchmark security priorities – remembering that someone in this room will have the answer to your biggest challenge!
Led ‘by, with and for’ CISO/CSOs, from across industry sectors, the international speaker panel included leading CISOs from across the Asia and Oceania region, from around the world and from across industry sectors to share their knowledge and experiences. Leading influential community of C-suite and senior cybersecurity executives for quality face-to-face and interactive engagement.
With a focus on leadership strategies, the programme provided critical updates on the emerging opportunity and risk horizon, role expectations and business technologies within the years to come, including AI, machine learning, automation, cloud, mobility and security.
Host Nation and International Speakers Included
- Allen Ohanian, CISO, Los Angeles County (U.S.)
- Chatchawat Asawarakwong, CISO, Kasikornbank (Thailand)
- David Kennedy, Global Chief Operating Officer, Sin7 (New Zealand)
- Dimitri Chichlo, Independent Non-Executive Director, JSC Ukreximbank (Switzerland/Ukraine)
- George Do, Chief Information Security Officer, Gojek and GoTo Financial (Singapore)
- Jelena Matone, CISO, European Investment Bank (Luxembourg)
- Karim Benslimane, Director of Cyber Intelligence, Darktrace (Singapore)
- Kawin Boonyapredeeo, Co-Founder and Advisory Board, Singaporean CIO Network (SCION) (Singapore)
- Lavy Shtokhamer, Managing Director, Global Head, Cyber Defence & Threat Management, Standard Chartered Bank (Singapore)
- Leong Boon Ang, Head of IT Security, National University of Singapore (Singapore)
- Leonard Ong, Senior Director, Regional ISO, Intercontinental & China, GE Healthcare (Singapore)
- Lim Shih Hsienm, Head of Technology Masterplanning, CISO and CSO, Certis Group (Singapore)
- Linda Nguyen Schindler, Programme Head, Ecosystem Development (Singapore)
- Nicholas Gerteisen, Deputy CISO, Smith + Nephew (U.S.)
- Marcus Alldrick, CISO Luminary, Pulse Conferences (UK)
- Lady Olga Maitland, President & Chairman, Defence and Security Forum (UK)
- Peter Ling, VP, Cyber & Intelligence Solutions, Global Cybersecurity Alliances and Cyber Resilience Programs, RiskRecon, Mastercard (Canada)
- Ray Stanton, Global Executive Partner, IBM (UK)
- Dr Sally Leivesley, Managing Director, Newrisk Limited, Member, Register of Security Engineers and Specialists (UK)
- Samuel Bye, Cyber and Tech PI Manager – Asia and Middle East, AXA XL (Singapore)
- Sounil Yu, CISO & Head of Research, Jupiter One (U.S.)
- Stephen Cavey, Co-Founder & Chief Evangelist, Ground Labs (Singapore)
- Tarun Kumar, CISO, Nissan Digital (India)
- Thomas Murphy, Strategic Intelligence Manager, Dragonfly (United Kingdom)
- Tobias Gondrom, Group CISO, Managing Director, United Overseas Bank (Singapore)
- Tony Smith, Board Member, WithSecure and Director, WithSecure Solutions
- Dr Viktor Polic, CISO, Head of Information Security and Assurance Services, ILO – United Nations (Switzerland)
Why Attend?
- CISO-to-CISO benchmarking and learning about what works and what doesn’t – valuable time saved!
- Top speakers from the Asia & Oceania region and from around the world, specifically chosen for the differences they will bring to the table
- Agenda driven and shaped by CISOs – top priorities are input in advance by CISOs
- Evening networking experience included! Engage with 100+ colleagues, peers, and industry thought-leaders at receptions, dinners, and cultural activities. Enduring connections are guaranteed!
- Immersive agenda – enjoy a range of keynotes, topical debates, practical corporate case studies, deep-dive industry focuses, scenario planning and think tanks on emerging priority areas.
- Learning and personal development through relevant high quality speaker sessions, as well as interactive and group engagement opportunities. Follow up services such as Pulse Educate are available for continual development. Bolster your CPE points!
- A 360 perspective – journey beyond the security ‘echo chamber’ to share non-security views from business leaders, board members, innovators, investors, and ministries
- Natural integration between inhouse security, supply chain and technology providers – we are part of the same jigsaw!
- Post conference materials including certificates, reports, and presentation summaries (subject to speaker opt-out) can be provided to help maximise value
- Access to Pulse Security Circle – a rapidly growing and international trusted community for CISOs, CSOs, senior security practitioners, technology luminaries and industry commentators that meets virtually and in-person to share insights and to benchmark strategies
The event is conducted within a trust-based community in an inspiring environment, held under The Chatham House Rule (who says what is unattributed).
Agenda at a Glance 2023
Tuesday 5 September 2023
19:00-21:00 Welcome Reception.
Wednesday 6 September 2023
09:00-17:30 Conference
18:00-21:00 CISO 360 Dinner.
Thursday 7 September 2023
09:00-16:00 Conference
2022 Sponsors
Platinum - Networking Dinner
Platinum
Gold - Networking Welcome Reception
Gold - CISO 360 Dinner Roundtable Discussion
Gold
Welcome, you are registering for an Advisory pass for
2nd CISO 360 Asia and Oceania, 13- 14 September 2022
Welcome, you are booking for a residential package at the Fullerton Singapore for the 2nd CISO 360 Asia & Oceania 13-14 September 2022.
This package includes 2 nights accommodation, single occupancy in a premier courtyard room at the Fullerton Singapore inclusive of breakfast at Town Restaurant and high-speed internet access. (Check in 12th and check out 14th September 2022) Cost is £272 per night inclusive of tax = total of £544
Terms & Conditions
- Credit Card – All major credit cards are accepted online. Credit card details will not be accepted via email, phone or fax.
- Free cancellation 30 days or more prior to check in date. If cancellation occur within 30 days or less to check in date, no refund will be issued.
WITH THANKS TO OUR SPONSORS
All Sponsorship Packages Include
Multi-event offers - Join Pulse Security Circle
Platinum – Networking Dinner
Platinum
Gold – Networking Welcome Reception
Gold
Speakers for the 2nd CISO 360 Asia & Oceania – Singapore 2022
If you would be interested in getting involved as a Speaker, please do let us know. We would also very much value your input into companies, topics or specific persons you may like to see present at the event this year. Please email sara.hook@pulseconferences.com.
Many thanks.
2022 speaker panel so far includes:
Chaired by
Marcus Alldrick
CISO Luminary
 Born at a very early age and growing up in a culture where cyber was a prefix for anything automated, menacing and malevolent (how history has a tendency of repeating itself), Marcus entered the world of Data Processing as it was known back then after graduating from university. Lured by the flashing console lights (it was also the disco era), the whirl of the magnetic tape and the click clack of the keypunch machine (TSO was still a dream), Marcus became a COBOL programmer, becoming prolific in Michael Jackson’s structured programming methodology (who would have known what future lay ahead for Michael). Having moved into analysis and then data architecture Marcus became the first devolved Information Risk and Security Manager for Barclaycard. After seven years in that role he moved banks and became Head of Information Security for Abbey National plc, now Santander UK. After six years at Abbey and a move into consulting for a large UK utilities company Marcus joined KPMG as a Principal Advisor. Eighteen months later he joined Lloyd’s of London as its CISO and subsequently became its Head of Digital Risk Management and Compliance, also embracing responsibility for data protection and privacy, during his 10 years tenure there. Having worked in IT for over 40 years, specialising in information risk, protection, security and compliance for the latter 27 years or so, Marcus decided to leave full-time corporate life and move to the South Coast of England in mid-2017, ever the seafaring Fisherman’s Friend. As well as being a proud member of the Pulse Conferences family, Marcus now undertakes advisory engagements, provides pro bono consulting and volunteering services and sits on the Cymmetria Advisory Board as Chief Risk Officer.
International speaker panel
Allen Ohanian
CISO, LA County (United States)
Mr. Ohanian is the Information Security Officer for Los Angeles (LA) County Department of Children and Family Services (DCFS), the largest child welfare institution in the nation. He has 20 years of experience in information technology, cybersecurity and defense strategies, risk management, forensics, privacy, compliance, cloud security, business continuity, and software engineering in the private and public sectors. Before DCFS, he served as the first Information Security and Privacy Officer at LA County Counsel. He established an Information Security and Privacy program and ensured compliance with legal mandates.
As a scholarly-practitioner, visionary, and innovative Information Security Officer, Mr. Ohanian has architected and implemented cybersecurity and privacy programs from the ground up, interwoven cybersecurity into the business culture, creating a security-conscious enterprise, and assertively achieved the organization’s mission of service excellence through outstanding leadership, governance, strategic planning, business acumen, and cost-saving transformation initiatives.
Mr. Ohanian is an active member of various Cybersecurity taskforce and workgroups, leads and oversees the Countywide Risk Management Cybersecurity Team responsible for developing and implementing administrative, technical, and tactical strategies to assess and reduce cybersecurity risks to County information assets.
Mr. Ohanian has been a keynote speaker and panel member in numerous private and public sector conferences. He is a Ph.D. Dissertation Committee Member for Cybersecurity using Artificial Intelligence at Center for Information Systems & Technology Claremont Graduate University.
Mr. Ohanian has a Bachelor’s degree in Computer Science from Cal Poly Pomona (magna cum laude) and obtained his dual Master’s Degree in Cybersecurity and Business Administration at the University of Maryland (UMUC). He is currently pursuing a Ph.D. in Industrial/Organizational Psychology program
David Kennedy
Global Chief Operating Officer, Cin7 (New Zealand)
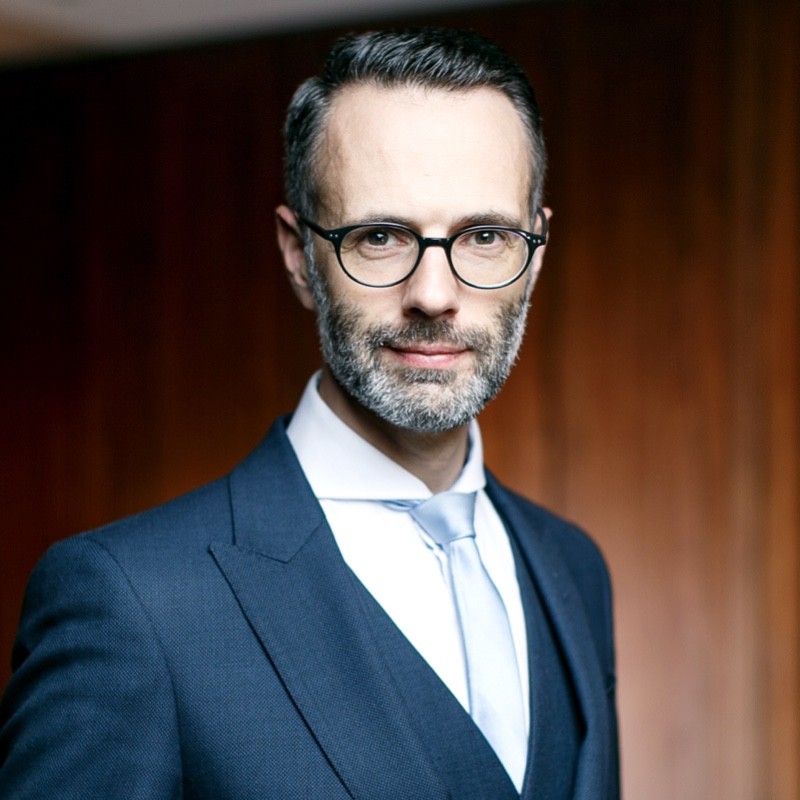
Dimitri Chichlo
Independent Non-Executive Director, JSC Ukreximbank, (Switzerland)
A French and Swiss citizen, Dimitri Chichlo started his career abroad in Ukraine in 2004, working for French industrial and banking groups, then moved to Switzerland in 2009, working mainly for international financial institutions and holding various roles in the fields of risk management and cybersecurity. In 2017, he completed an Executive MBA at INSEAD. In 2019, he joined the Supervisory board of Ukreximbank, the third largest and State-owned bank in Ukraine, as vice-chairman and chair of the Operations and Digital Committee. In 2020, he founded his consultancy practice in cybersecurity and digital transformation, AndSecure (www.andsecure.ch). Since February 24th, 2022, he is actively involved into providing humanitarian support to Ukraine and create a fund dedicated to humanitarian defining (www.demine.foundation). He currently lives in Geneva.
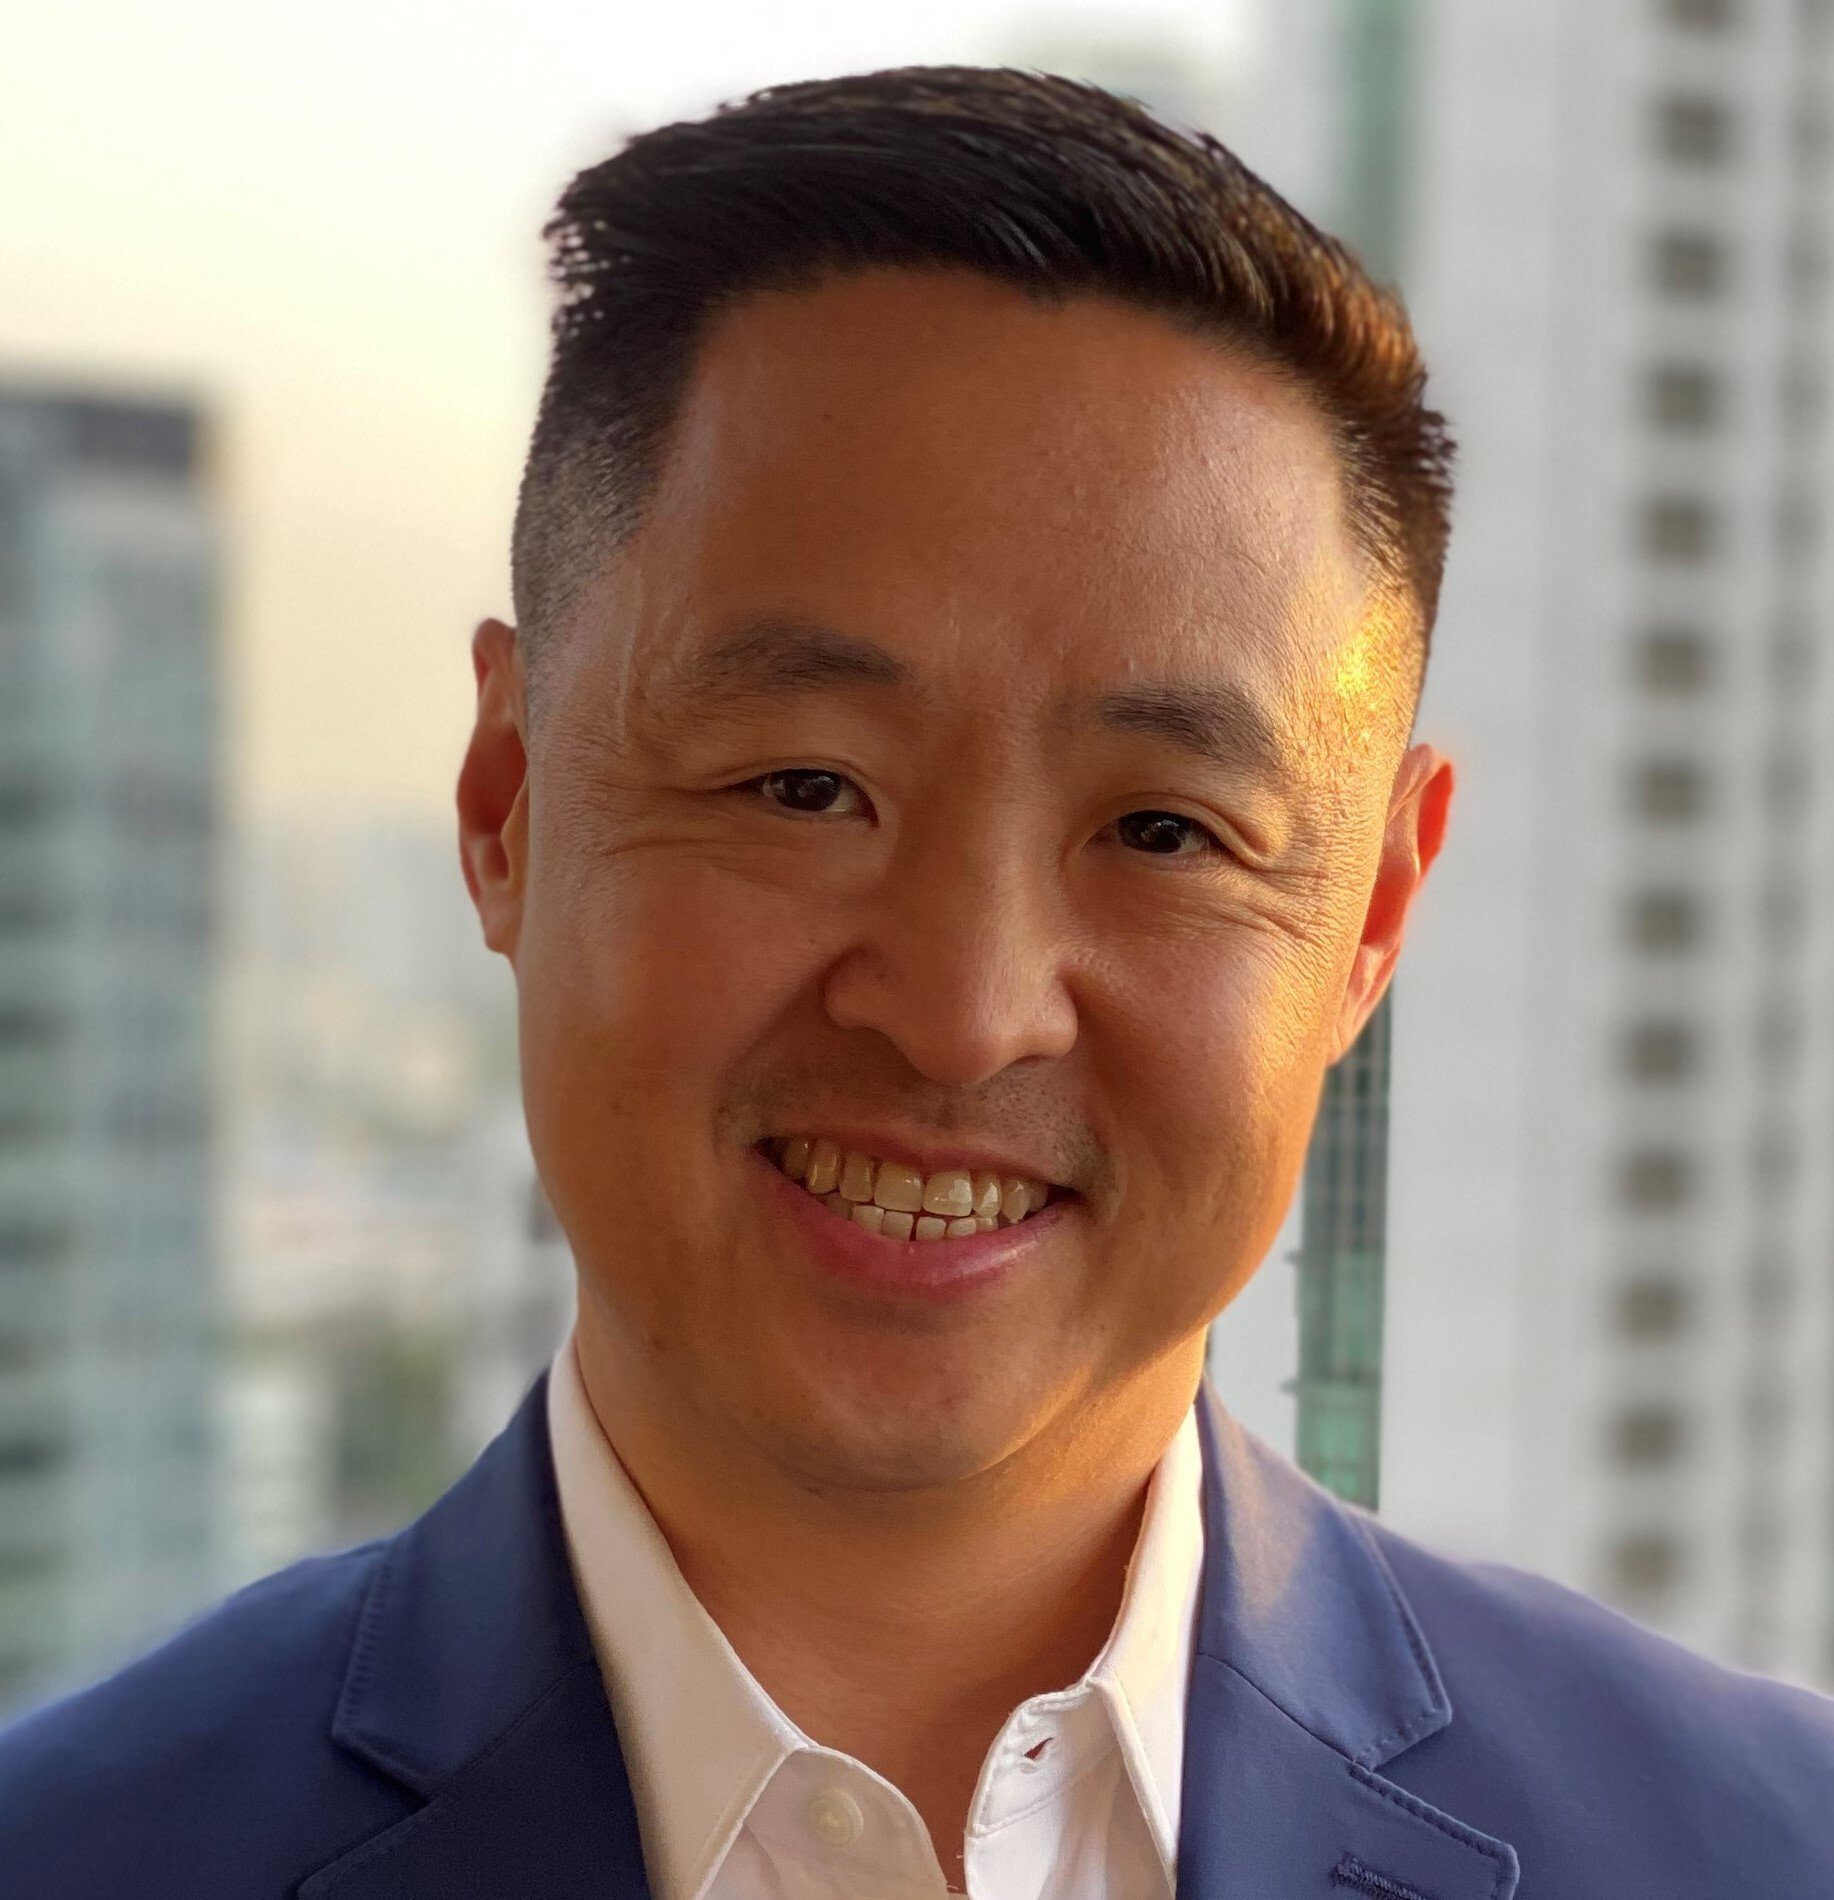
George Do
Chief Information Security Officer, Gojek and GoTo Financial (Singapore)
George has been working in the cybersecurity field for over 25+ years concentrating on the building and operating cybersecurity programs. He specializes in the transformation of cybersecurity, winning customer trust, and ensuring a strong cybersecurity posture for organization. George has extensive experience in maturing global cybersecurity programs and teams. He has extensive experience in securing applications (products and services), securing core IT infrastructure and cloud workloads, and maintaining a robust incident response capability. George leads global teams in cybersecurity, data privacy, governance, risk, compliance (GRC), and implementation of security frameworks, Working closely stakeholders across functions, the global programs he developed has ensured security is baked into products and services at birth. Before joining Gojek and GoTo Financial, George served as the global Chief Cybersecurity Officer (CISO) at Equinix where he built the global cybersecurity program from inception. Previous to that he worked at Exodus (Savvis / Century Link), and Tivo in senior security leadership roles. He began his career at the National Aeronautics and Space Administration (NASA) where he collaborated with senior federal officials to secure government information assets. George serves on customer advisory boards for several cybersecurity firms and is an advisor for venture capital. He is a frequent speaker and panelist at cybersecurity industry events.
C U R R E N T R O L E S
Chief Information Security Officer (CISO) @ Gojek and GoTo Financial Serving as the Chief Cybersecurity Officer at GOJEK and responsible for the development and management of the global cybersecurity program including framework, strategy, and roadmap. Responsible for building trust and security with customers, drivers, merchants, and partners of the GOJEK ecosystem.
Advisor @YL Ventures Serving as an Advisor for YL Ventures with special focus on Cybersecurity. Helping today’s innovative startups become tomorrow’s industry leaders with the capital, connections and experience they need to succeed in the market.
https://www.ylventures.com/people/
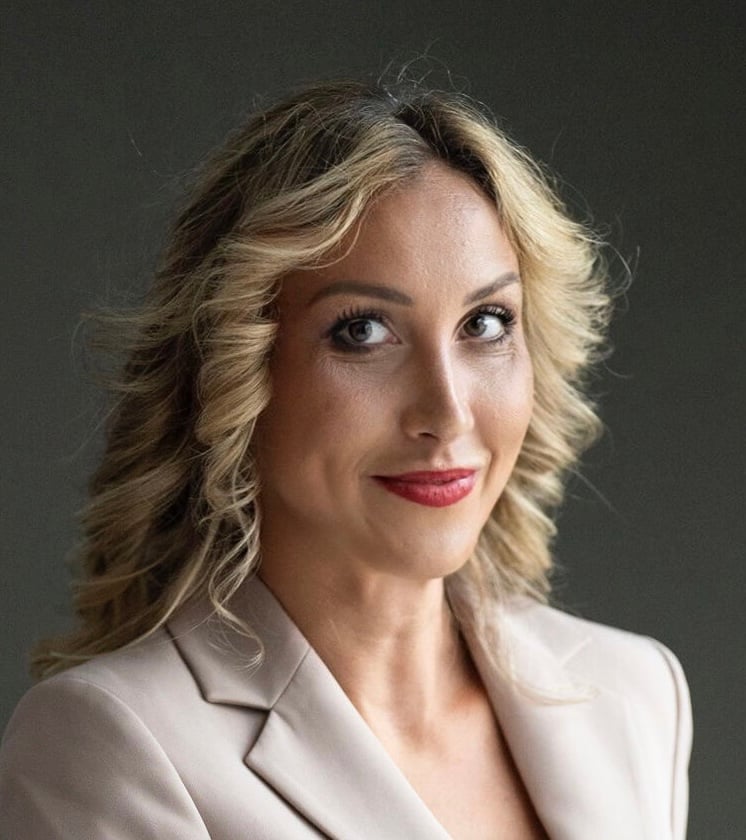
Jelena Matone
CISO, European Investment Bank, (Luxembourg)
Respected and leading CISO, awarded the CISO of the year for 2019 in Luxembourg, Sentinel CISO Global 2020, EU CISO 2020, and recently Ambassador of the year 2021 in Luxembourg. Versatile and innovative Cybersecurity professional with emphasis on cyber security risk management, policies and procedures creation, IT/IS security, IT Operations, audit, risk mitigation, business process improvement, IT governance. Passionate about participation and encouragement of women in cybersecurity and in STEM programs.
Prior to current role, served as the Senior Operational Risk and ISO manager for another EU Institution. Earlier in career, managed IT Audit and Compliance for Sobey’s, one of the two national grocery retailers in Canada and Audit, Corporate Development, M&A and growth strategies and IT Audit for George Weston, one of the Canada’s largest publicly traded food processing and distribution companies.
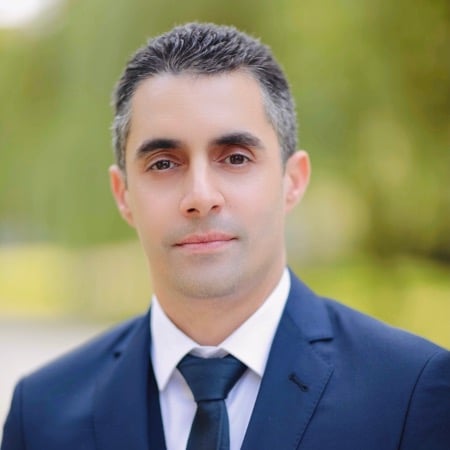
Karim Benslimane
Director of Cyber Intelligence, Darktrace (Singapore)
Karim Benslimane is Darktrace’s Director of Cyber Intelligence, working with clients in the public and private sector to analyse the most sophisticated cyber-threats today, and advising security professionals on the employment of artificial intelligence to strengthen their defensive strategy. Prior to joining Darktrace, Karim was Information & Communication Director at the Singapore Sports Hub, Head of IT at Vinci Stadium, and the IT Research & Development Manager at Stade de France. Karim is a technical specialist in cyber and counter-terrorism exercises with over two decades of experience defending the sports and event industry from sophisticated threats. He has led major IT and cyber security projects for international arenas and events such as the Football World Cup, Rugby World Cup, World Athletics Championships and over 500 games and concerts. He is based in Singapore.
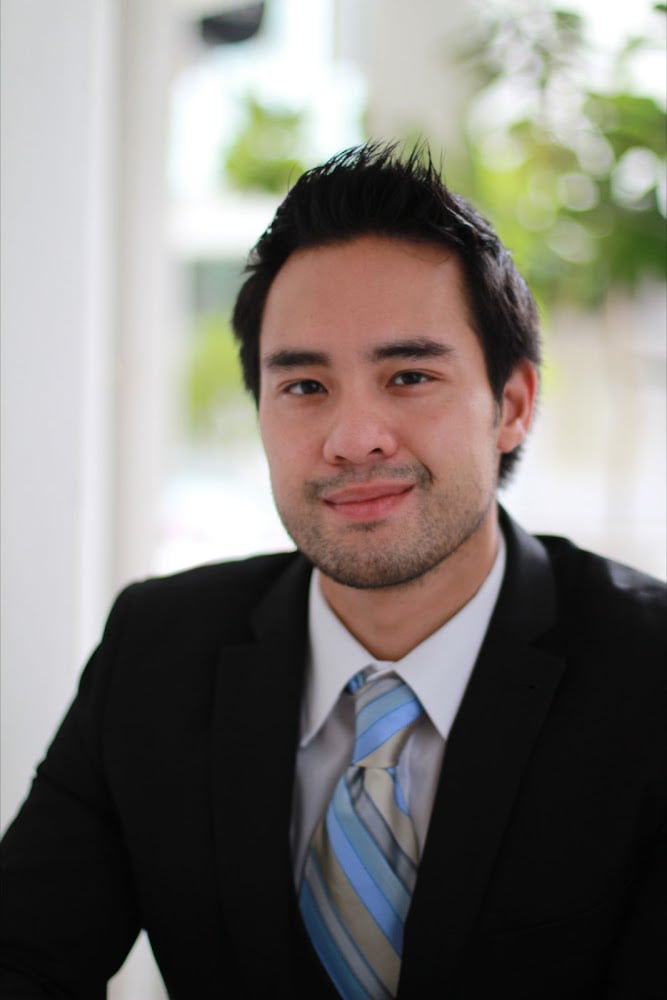
Kawin Boonyapredeeo
Co-Founder and Advisory Board, Singaporean CIO Network (SCION) (Singapore)
Kawin has over 20 years of experience across business management and information technology and security roles, with expertise in building information security programs across the North America and Asia region. He has previously served as Chief Cyber Technologist at Booz Allen Hamilton, CEO of Cybertron in Thailand and Managing Director, APAC at Qualys. Kawin has dedicated his free time serving as co-founder and Executive Committee Member on the (ISC)2 Singapore Chapter. Recently, he is also the co-founder of the Singapore CIO Network (SCION), a group that strives to build a community of like-minded information and cybersecurity professionals in Singapore. He received his Bachelor of Arts in Economics from the University of Pennsylvania, Master’s degree in Business Management and Systems from New York University and had performed his Ph.D. studies and research at Singapore Management University.
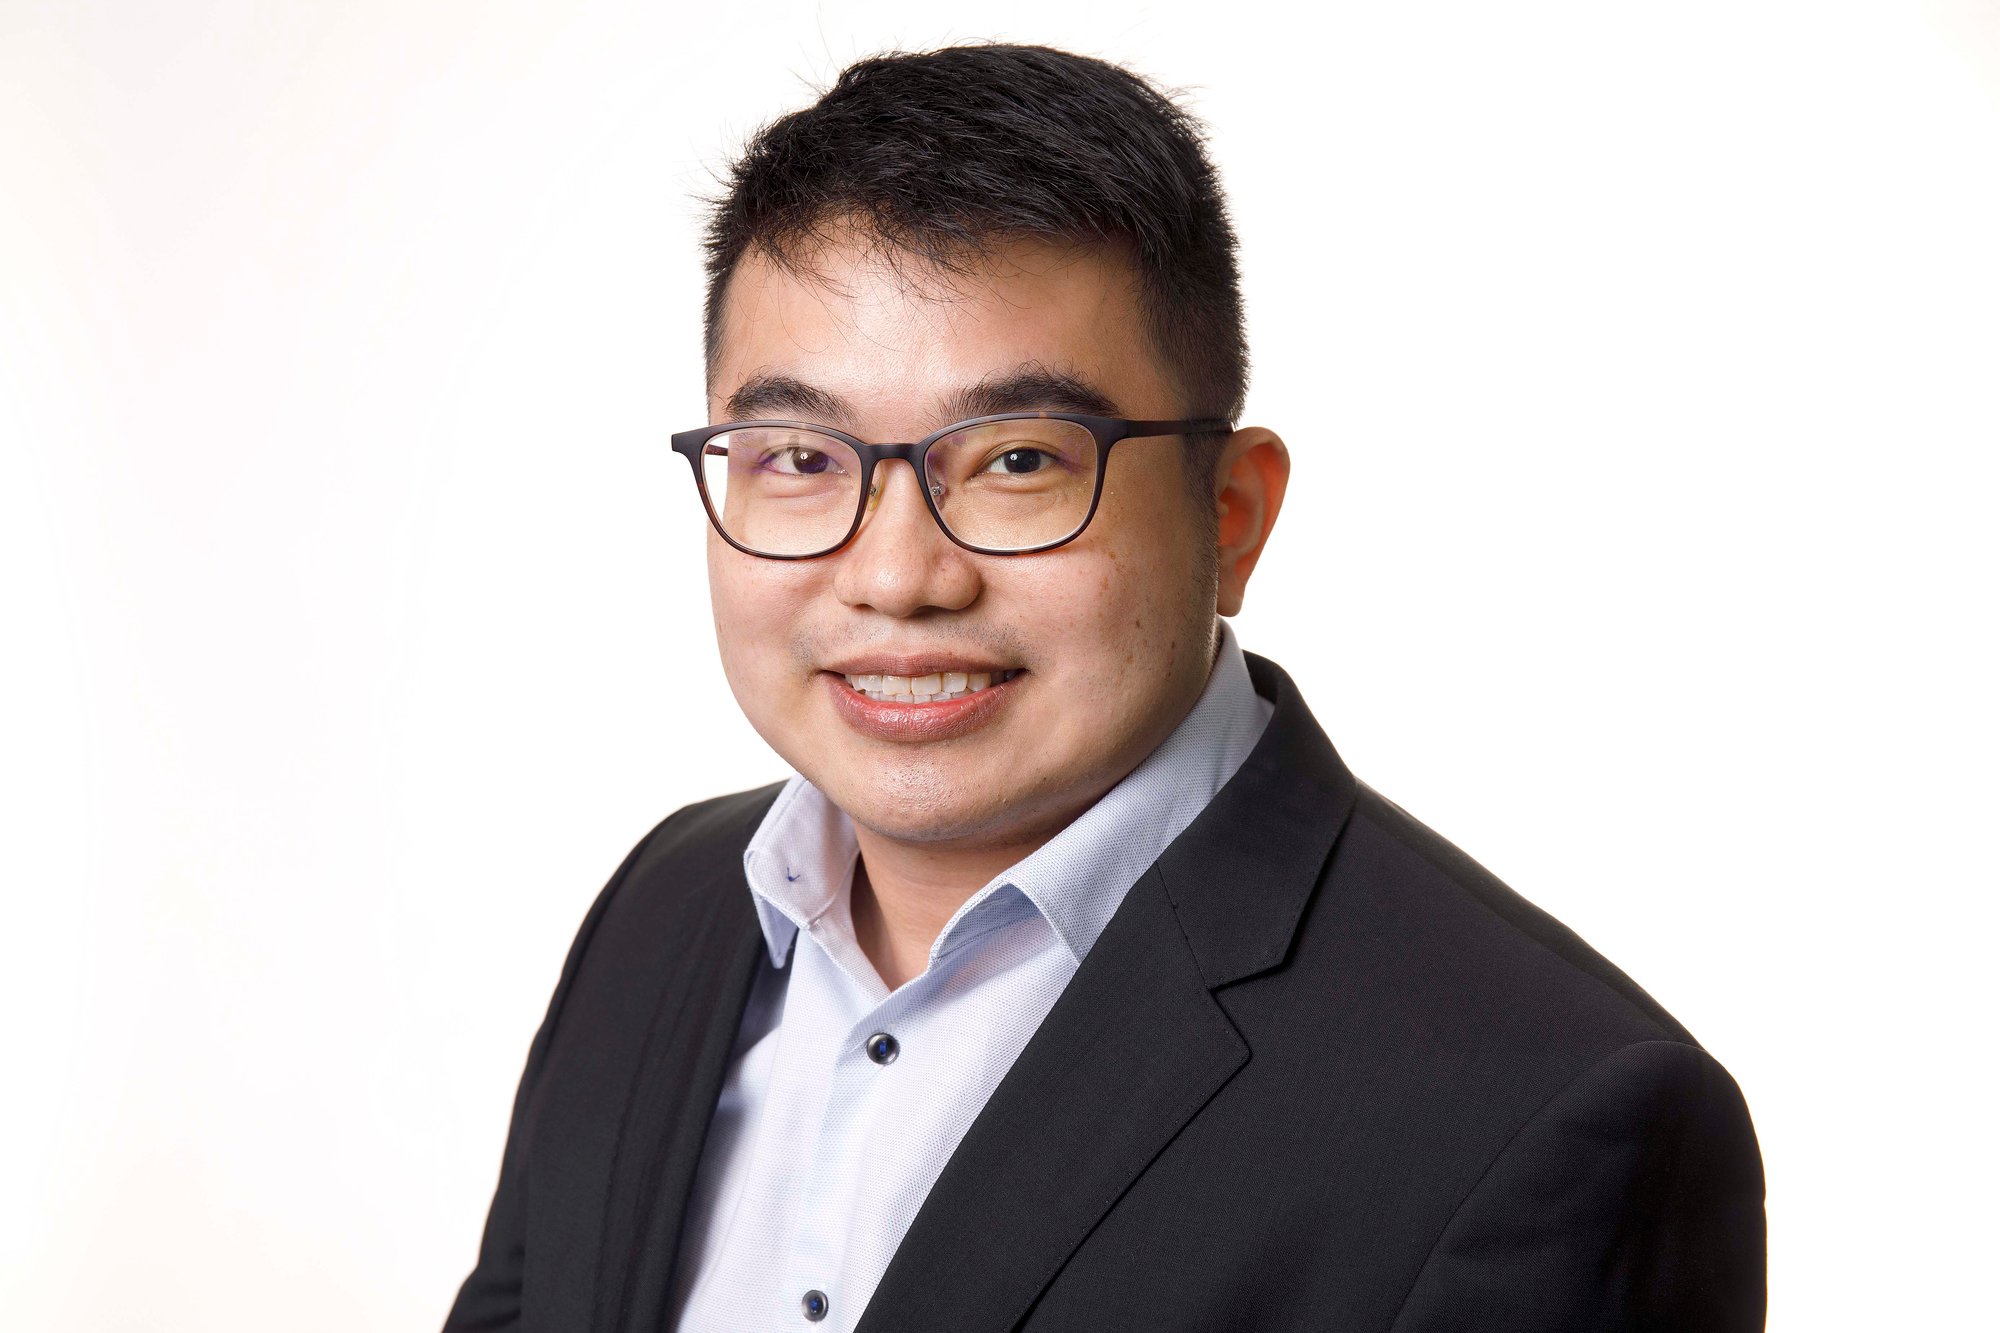
Kevin Pang
Solution Engineer, BeyondTrust (Singapore)
Kevin Pang is an evangelist of BeyondTrust solutions to key enterprise customers in the APJ. He has been in the IT industry for more than a decade and has extensive experience in cybersecurity. Prior to joining BeyondTrust, Kevin was a trusted advisor with a key SI and has more than five years’ experience in the Privileged Access Management domain
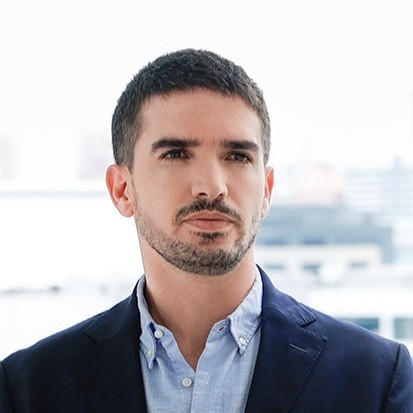
Lavy Stokhamer
Managing Director, Global Head, Cyber Defence and Threat Management, Standard Chartered Bank (Singapore)
With over two decades of experience in both the public and private sectors, leading and managing cybersecurity operations. Lavy is the global head of SCB’s Cyber Defense & Threat management and was previously the head of Israel’s National Cyber Directorate’s CERT. He spent the majority of his career in the financial industry, working for FIBI – First International Bank of Israel – and the led the ISA’s finance cyber division (Israel security agency). Lavy is a senior cybersecurity leader with substantial field experience and an in-depth understanding of the cyber warfare ecosystem at both the corporate and governmental levels, as well as significant expertise in developing world-class cybersecurity services. Expertise in risk management, monitoring and analytics, and intelligence aspects of cyber security. Proven competence and experience in SIEM, SOC, SOAR, and incident response technologies, solutions, strategies, and research, as well as skills and experience with data analytics/big data/machine learning. Lavy is also a venture capital consultant that focuses in identifying innovative Fintech technologies as a mentor in accelerators throughout the world. Contributing to worldwide programs coordinated by FSISAC and the World Economic Forum, as well as confounding Israel’s pioneering finSec national lab (owned by MasterCard Group and Enel X). Lavy earned a bachelor’s degree in information technology and business administration from Herzliya’s Interdisciplinary Center (IDC), one of Israel’s most internationally acclaimed and well-known universities. Lavy is a certified corporate director and an alumnus of the Cyber Security Risk Management program at Harvard University.
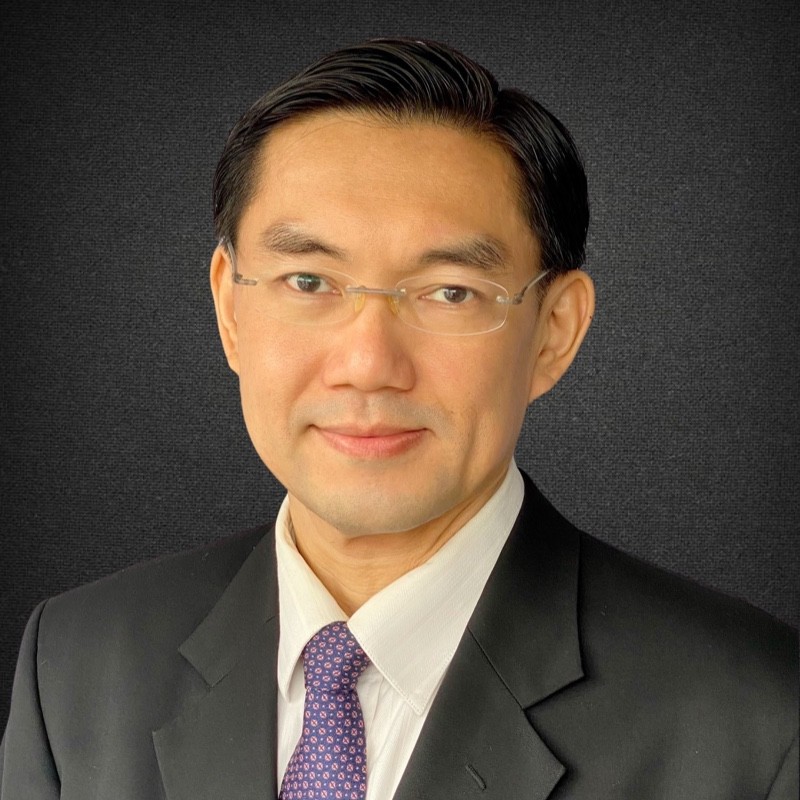
Leonard Ong
Senior Director | Regional Information Security Officer, Intercontinental and China, GE Healthcare (Singapore)
Leonard has over 20 years of experience in Information, Cyber and Corporate Security gained in telecommunication, enterprise, banking, pharmaceutical, healthcare and medical technology sectors. He is the Regional Information Security Officer, Intercontinental & China for GE Healthcare. Prior to that, he was the Group Chief Information Security Officer for a leading vertically integrated healthcare platform in the Asia Pacific. He led Governance, Risk Management, Compliance (GRC) service for Asia Pacific region in MSD International (also known as Merck & Co., Inc.). In his earlier career, He was with Barclays Capital as the Head of Global Information Security Risk & Operation, Asia pacific. Leonard is passionate on volunteering with several International and Singapore-based security associations since 2003. His longest service is with ISACA Singapore Chapter where he has been elected as Chapter President for two consecutive terms. Leonard has also served ASIS International Chapter as Honorary Chairman for 3 years. He is still serving in ASIS International as Community Vice President. Leading information security associations, such as (ISC)2 and ASIS International, have recognized his contributions. He was awarded Information Security Leadership Achievement (ISLA) in Senior Information Security Professional category in 2011 and Professional Certification Board (PCB) Regional Award in 2014. National Infocomm Competency Centre (NICC) has awarded Leonard with ‘IT Specialist of the Year’ in 2005. He was instrumental in achieving K. Wayne Snipes 2013 award for ISACA Singapore Chapter being the best very large chapter in Asia with over 2,500 professional members. International Data Group (IDG) and CEO|CIO Club recognized Leonard with CSO ASEAN Honoree award in 2015 and as ASEAN CSO30 in 2021. Following that, in 2016, He was presented with ISACA’s Paul Williams Award for Inspirational Leadership. Leonard was successfully selected as Finalist in the inaugural AISP-CSA Cybersecurity Award 2018 in senior leaders’ category. In July 2020, Leonard will be inducted into ISACA Hall of Fame. The designation recognizes members who have shown exemplary dedication to advancing ISACA’s purpose through volunteer service, member engagement and other activities. Leonard holds Master of Computing from National University of Singapore (NUS) and is a Fellow with Singapore Computer Society.
Shih Hsien Lim
Head of Technology Masterplanning, CISO and CSO, Certis Group (Singapore)
Shih Hsien joined Certis Group in October 2021 and is responsible for coordinating the technology masterplanning and data governance initiatives, as well as overseeing the CISO and CSO Offices.
Prior to this, Shih Hsien was the Chief Security Officer of SP Group, responsible for managing the cyber and physical security risks for the Group, after relocating back to Singapore in early 2019 from Hong Kong where he headed the information security and data privacy functions for The Hong Kong Jockey Club.
Before Hong Kong, he was part of the MOH Holdings P/L management team in Singapore, responsible for establishing the security technical architecture and policies for Singapore’s National Electronic Health Record (NEHR). Shih Hsien has also previously held senior positions at Singapore Airlines and the Infocomm Development Authority of Singapore (now known as Infocomm Media Development Authority).
Linda Nguyen Schindler
Head of Ecosystem & Partnerships and Member AI Competence Center, German Entrepreneurship Asia (Singapore)
A recovering Silicon Valley lawyer turned Singapore ecosystem builder, Linda was formerly the Programme Head of ICE71 (“Innovation Cybersecurity Ecosystem at BLOCK71”), the region’s first cybersecurity entrepreneur hub.
She is currently Head of Ecosystem & Partnerships and Member of the AI Competence Center for German Entrepreneurship Asia.
German Entrepreneurship Asia is a leading global innovation provider specialized in building collaboration structures between governments, corporates, investors and start-ups in major innovation hubs around the world.
At the AI Competence Center (an initiative funded by the Federal Ministry of Economic Affairs and Climate Action of Germany), we help empower AI innovators and foster a global AI ecosystem.
Leong Boon Ang
Head of IT Security, National University of Singapore
Leong Boon is currently the Head of IT Security at NUS Information Technology, responsible for security governance, risk management, security operations, incident response and user awareness across the entire University.
He has 20 years of experience in cybersecurity, with a keen interest in security incident handling and response. During his 12 years in NUS, he has led many investigations for major cybersecurity incidents, including an APT attack on local universities in 2017.
As a passionate advocate of the subject, he is also an adjunct instructor at Advanced Computing for Executives (ACE) under NUS School of Computing, and a mentor for cybersecurity startups with the ICE71 Accelerate Programme. He also enjoys speaking and has presented at major security conferences such as RSA Conference.
Leong Boon is an alumnus of NUS, having graduated with a Bachelor’s Degree in Computer Engineering. In 2021, he received the CSO30 ASEAN Award, recognizing him as one of the top 30 senior cybersecurity executives in the region.
Dr. Oakley Cox
Analyst Technical Director, Darktrace (New Zealand)
Oakley is a technical expert with 5 years’ experience as a Cyber Analyst. After leading a team of Cyber Analysts at the Cambridge headquarters, he relocated to New Zealand and now oversees the defense of critical infrastructure and industrial control systems across the APAC region. His research into cyber-physical security has been published by Cyber Security journals and CISA. Oakley is GIAC certified in Response and Industrial Defense (GRID), and has a Doctorate (PhD) from the University of Oxford.
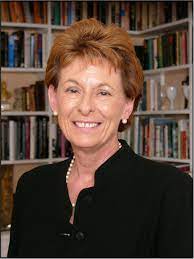
Lady Olga Maitland
Founder, UK Defence and Security Forum and Chairman, Copenhagen Compliance (UK)
Lady Olga Maitland, Founder, Defense and Security Forum and Chairman, Copenhagen Compliance – has wide experience in all major Governance, risk Management and Compliance issues in general and global Fraud and Corruption problems in particular. She is a special adviser to a number of dignitaries and a widely sought after speaker at all Major Conferences on several Corporate Governance issues. Lady Olga is a former British MP for the Conservative party. Prior to her political career she was a reporter for the Fleet Street News Agency, a columnist in the London.
Peter Ling
Vice President, Cyber and Intelligence Solutions Global Cybersecurity Alliances and Cyber Resilience Programs, Mastercard (Canada)
With 28 years’ experience in the Cybersecurity space, Peter is a seasoned global practitioner and technology pioneer, having created numerous offerings in this space. His background spans from operational security response management, systems engineering, and complex technical vendor integrations — to strategic alliances throughout the security and risk markets. His areas of expertise are in Public Key Cryptography (PKI), Secure Communications, Endpoint Protection and Threat & Risk management. He has developed and brought dozens of security products to market internationally and is on a constant journey, assisting partners and clients as the Cybersecurity market continues to meet the challenges of the day.
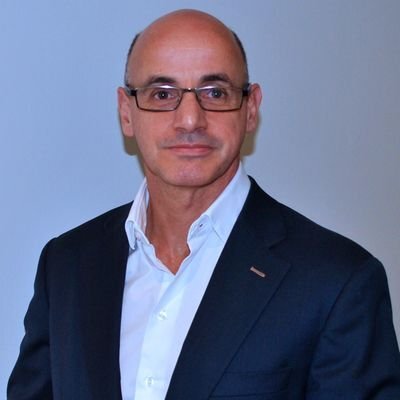
Ray Stanton
Global Executive Partner, IBM (UK)
An experienced Senior Leader & Corporate Executive, Security & Risk Professional, Ray is a globally acknowledged and well-known thought leader; recognised and highly respected as someone who delivers. Ray has sat on global programmes for the World Economic Forum on Cyber Resilience and the Advisory Board for the Information Security Forum. Ray has held Group CISO/CSO & EVP roles for BT, National Grid, Interoute, Redwood Technologies and Airbus UK. He has been fortunate enough to have held global accountability, ranging from consultancy, through to design, build and run of managed services; including full profit and loss ownership for multiple business lines, while combining this experience with protection of Critical National Infrastructure in the Energy and Communications industries.
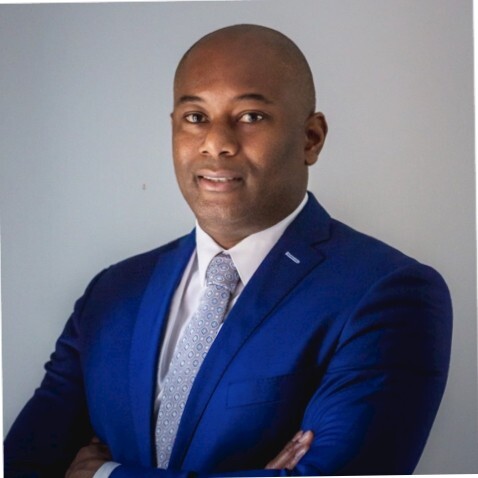
Mark Phillips
VP of Solution Architecture, EMEA and APAC, HUMAN (UK)
Mark joined HUMAN Security in January 2021 to lead and build an international technical sales team across EMEA and APAC. He has held several global and EMEA responsible senior leadership roles at such vendors as Trend Micro, Bitdefender, and Malwarebytes culminating in more than 20 years of experience in cyber security. His role at HUMAN Security focuses him on ensuring HUMAN’s product offerings add maximum value by mapping the technical solution to a business issue.
Samuel Bye
Cyber & Tech PI Manager – Asia and Middle East, AXA XL (Singapore)
Joined AXA XL Singapore as the Cyber & Technology PI Manager for Asia in February 2020. Prior to the move worked for Allianz in London for 7 years where he played a vital role in the development of Cyber & Technology PI portfolio.
Over 8 years of combined Cyber & Technology PI experience and has been specifically hired to drive growth and development of the AXA XL Cyber offering throughout Asia and the Middle East.
Dr Sally Leivesley
Director, Newrisk Ltd, A Founder Member, The Exercise Group7 (UK)
Dr Leivesley has experience in catastrophic risk, global media commentary, government and private sector incidents, exercising and advising on loss prevention and recovery. Her prime focus is on the protection of life and critical infrastructure from extreme threats. She has worked with global USA corporations on risk strategy for catastrophic incidents using exercises with Boards and facilitating executive meetings. In 2021 she presented to the Baker Institute, Rice University on vulnerabilities in the energy sector and nuclear conflict risks in the South and East China seas. In 2015 she presented to the Electrical Infrastructure Security Council’s conference in the Capitol Building on Black Swan risks.
Dr Leivesley Chairs the Permanent Monitoring Panel for Mitigation of Catastrophic Risk for the WFS (CERN) and has led 12 remote multinational science meetings on Covid-19 Mitigation and the Panel has also met on Engineering for Resilience in Infrastructure; Nuclear Conflict Mitigation Risk Management and Planetary Defence against Near Earth Objects (NEOs).
Communicator since 2001 on many international television news outputs including BBC World Service describing live international and UK incidents and all major forms of threat – cyber, terrorism, aviation, Polonium-210 and Novichok poisonings, Chechen terrorist Beslan child hostages, security issue with Iran, DPRK, USA Presidential security, Covid-19, and unexplained incidents such as MH370 leading to media stories in all countries on novel concept of cyber hijack as new risk in civil aviation.
Dr Leivesley received Scientific Advisory Training from the British Home Office to become a Scientific Advisor for national survival from nuclear, chemical and biological weapons effects and in the Cold War she held an appointment as a Scientific Advisor for operations in civilian nuclear bunkers under London.
PhD London University on catastrophic risk across all industry sectors, awarded in field of Economics. Innovator of technological solutions to improvised terrorist devices for chemical and explosives weapon’s effects. Specialist in CBRN for the British Register of Security Engineers and Specialists RSES, Member 25 years of the International Association of Bomb Technicians and Investigators (IABTI) and Member of the Royal United Services Institute, Member of the Australian College of Education.
Stephen Cavey
Co-Founder and Chief Evangelist, Ground Labs (Singapore)
As Ground Labs co-founder, Stephen Cavey leads a global team empowering enterprise partners to discover, manage and secure sensitive data across their organizations. Stephen has deep security domain expertise with a focus on electronic payments and data security compliance. He is a frequent speaker at industry events such as PrivSec Global, and his expert analysis has been featured in media outlets including the Financial Times, Entrepreneur, SiliconANGLE, among others. He is also a member of the Entrepreneur Leadership Network and Forbes Technology Council. Prior to Ground Labs, Stephen held leadership positions at Paycorp, an integrated electronic payments solution provider owned by KKR. Stephen also served in engineering roles with Webpay, a payment services provider later acquired by Fidelity, and Webtel, an early Australian ISP.
Sounil Yu
CISO, JupiterOne, (United States)
Sounil Yu is the CISO and Head of Research at JupiterOne. He created the Cyber Defense Matrix and the DIE Triad, which are reshaping approaches to cybersecurity. He’s a Board Member of the FAIR Institute; co-chairs Art into Science: A Conference on Defense; is a visiting fellow at GMU Scalia Law School’s National Security Institute; teaches at Yeshiva University; and advises many startups. Sounil previously served as the CISO-in-Residence at YL Ventures and Chief Security Scientist at Bank of America. Before Bank of America, he helped improve information security at several Fortune 100 companies and Federal Government agencies. Sounil has over 20 granted patents and was recognized as one of the most influential people in security in 2020 by Security Magazine, Influencer of the Year in 2021 by SC Awards, and a 2021 Top 10 CISO by Black Unicorn Awards. He has an MS in Electrical Engineering from Virginia Tech and a BS in Electrical Engineering and a BA in Economics from Duke University.
Tarun Kumar
CISO, Nissan Digital, (India)
Tarun is a seasoned professional with 23+ years of ‘exclusive’ experience in areas covering Cyber / Information Security, IT Risk Management, Data Protection and Privacy. In his leadership roles, he has had the distinction of building Cyber Security capabilities (people, process & technology) grounds up for organizations (with extensive experience in managing large teams).
Currently he is CISO with a large global automobile major. In his past roles, he has been Director – Cyber Security with Big 4 firm; Global CISO with a leading global Business Process Management (BPM) organization & General Manager – Global Security Services with a large global IT Services organization
Tarun has extensively been involved in providing Cyber / Information Security services to domestic (India) and international clients representing broad industry sectors. He brings a 360 degree experience in Cyber / Information Security as a Provider (Consulting) and Consumer (as CISO) of services. He has extensive experience in establishing Road-Map and Investments for Cyber / Information Security, Security Governance and IT Risk Management practices. His proficiency covers Cyber Security Strategy & Roadmap, Governance, Risk, Compliance & Controls, Threat & Vulnerability Management, Operations, Data Privacy and Business Continuity
Tarun brings in experience of playing an effective change agent by managing cross-functional teams to deploy Cyber / Information Security programs (enterprise-wide) and maturing them
He has been recognized with various industry honours (in India) viz., Visionary CISO Award 2022; Top 100 Infosec Maestros Award 2021, 2014; Top 100 Defenders Award 2020; Top 100 CISO Award 2014, 2012. He brings worldly recognized credentials of CRISC, CISM, CISA, CISSP and ISO27001 LA
Thomas Murphy
Strategic Intelligence Manager, Dragonfly (UK)
Thomas leads the strategic intelligence portfolio at Dragonfly, a global political risk intelligence firm. His background is in intelligence. He has extensive experience providing business-enabling security and political intelligence and analysis to some of the world’s most influential organisations. In recent years, he has increasingly worked with CISOs and other cyber professionals to help them understand how the geopolitical threat environment affects the cyber domain. Thomas holds a MA in International Relations from the University of Melbourne.
Tobias Gondrom
Group Chief Information Security Officer, Managing Director, United Overseas Bank Limited (UOB) (Singapore)
Tobias Gondrom joined UOB in 2018 and is the Group Chief Information Security Officer. He is responsible for ensuring the end-to-end information security in UOB and implementing all cyber security initiatives across the Bank. Tobias has more than 20 years of experience in information security, software development, application security, cryptography, electronic signatures and global standardisation strategies.
Tony Smith
Board Member, WithSecure and Director, WithSecure Solutions
Widely regarded as a passionate cyber security ambassador and global cyber evangelist, Tony Smith is a Board Member and Director at WithSecure – Europe’s largest cyber security specialist.
Working alongside WithSecure’s Managed Services customers around the world, Tony is often a conference speaker or host at corporate events, facilitating discussions between security professionals on the trends, challenges and insights of securing the modern enterprise.
In his spare time, Tony also delivers enthusiastic talks in high schools, providing inspiration and encouragement for today’s young people to pursue a career in cyber security.
With nearly 30 years of corporate experience, Tony is a sports fanatic who brings his effervescent personality to work everyday.
Dr Viktor Polic
CISO, Head of Information Security and Assurance Services, ILO - United Nations, (Switzerland)
More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences.
All Sponsorship Packages Include
Multi-event offers - Join Pulse Security Circle
CISO360 Asia Singapore Full Colour
Platinum – Networking Dinner
RiskRecon
RiskRecon, a Mastercard Company, enables you to easily achieve better risk outcomes for your enterprise and your supply chain. RiskRecon’s cybersecurity ratings and assessments make it easy for you to understand and act on your risks, delivering accurate, risk-prioritized action plans custom-tuned to match your risk priorities.
RiskRecon traces its beginnings to 2011 when our founder, Kelly White, asked himself, “Is it possible to measure the security program quality of any company simply by looking its Internet-facing presence?”
Kelly is a long-time information security practitioner and bank CISO who witnessed first-hand the need for adapting third-party risk controls to meet the new challenges resulting from decentralized IT and SaaS apps. He has many years of hands-on experiencing building big data and analytics solutions to detect fraud and security vulnerabilities in high-velocity transaction environments.
Like most organizations at the time, his bank’s third-party risk management assessments relied heavily on questionnaires and other vendor attestations. This approach worked well ten years ago with a small number of large vendors, mostly in-house deployments, purchases controlled by central IT, and a well-defined set of Internet vulnerabilities. With the decentralization of IT purchasing and rapid adoption of SaaS, this approach was becoming less effective and more resource-intensive.
What if instead of trying to use the “old” risk management model, his institution could trust an objective source that automatically pinpointed specific gaps in any organization’s security programs and performance? Questionnaires and surveys are helpful in evaluating one’s intent but provide little verifiable insight into actual practices and discipline.
After realizing there were no such solution available, he decided to build his own. After testing and validating his solution with many peers, Kelly decided to pursue the idea full time and founded RiskRecon, officially incorporating in October of 2015.
RiskRecon is headquartered in Salt Lake City, UT with a presence in Boston, MA and representatives around the world.
Platinum
Ground Labs
Ground Labs enables organizations to discover and remediate all of their data across multiple types and locations — on servers, on desktops and in the cloud. Ground Labs serves as the most comprehensive and trusted solution in the enterprise to confidently mitigate risk and find sensitive data. Ground Labs’ core focus is to develop technology to meet the increasing challenges of data management and regulatory compliance. This is shown with our flagship products of Enterprise Reconand Card Recon, along with our continued development of future solutions to address the complexities, challenges and intricacies of data discovery. Since the company’s inception, we have remained faithful to our commitment and core focus of discovering data, no matter where it resides. https://www.groundlabs.com/
HUMAN
HUMAN is a cybersecurity company that safeguards 500+ customers from sophisticated bot attacks, fraud and account abuse. We leverage modern defense—internet visibility, network effect powered by collective protection, and disruptions—to enable our customers to increase ROI and trust while decreasing end-user friction, data contamination, and cybersecurity exposure. Today we verify the humanity of more than 15 trillion interactions per week across advertising, marketing, e-commerce and enterprise security, putting us in a position to win against cybercriminals. Protect your digital business with HUMAN. To Know Who’s Real, visit www.humansecurity.com.
Gold – Networking Welcome Reception
BeyondTrust
BeyondTrust is the worldwide leader in intelligent identity and access security, empowering organizations to protect identities, stop threats, and deliver dynamic access to empower and secure a work-from-anywhere world. Our integrated products and platform offer the industry’s most advanced privileged access management (PAM) solution, enabling organizations to quickly shrink their attack surface across traditional, cloud and hybrid environments.
BeyondTrust protects all privileged identities, access, and endpoints across your IT environment from security threats, while creating a superior user experience and operational efficiencies. With a heritage of innovation and a staunch commitment to customers, BeyondTrust solutions are easy to deploy, manage, and scale as businesses evolve. We are trusted by 20,000 customers, including 75 of the Fortune 100, and a global partner network. Learn more at www.beyondtrust.com.
Gold
Darktrace
Visit websiteWithSecureTM
WithSecureTM is cyber security’s reliable partner. IT service providers, MSSPs and businesses along with the largest financial institutions, manufacturers, and thousands of the world’s most advanced communications and technology providers trust us for outcome-based cyber security that protects and enables their operations. Our AI-driven protection secures endpoints and cloud collaboration, and our intelligent detection & response is powered by experts who identify business risks by proactively hunting for threats and confronting live attacks. Our consultants partner with enterprises and tech challengers to build resilience through evidence-based security advice. With more than 30 years of experience in building technology that meets business objectives, we’ve built our portfolio to grow with our partners through flexible commercial models.
www.withsecure.com
Visit website
www.withsecure.com
Photo Gallery – 2nd CISO 360 Asia & Oceania

Gallery from 2nd CISO 360 Asia & Oceania
Downloads 2022
Download 2022 ProgrammeDownload 2022 Attendee Justification / ROI LetterRequest access to presentation materials from CISO 360 Asia & Oceania 2022Downloads – Previous Events
Download 2019 ProgrammeOn the Pulse Blog - A Chat with IBM’s Manan Qureshi on Achieving Resilience Posture
On the Pulse Blog - The vendor innovation hub: A CISO's imperative
Download 2019 materialsOn the Pulse Blog - Innovation Management: Learning How to Fail is the CISO’s Advantage
On the Pulse Blog - Interview with CISO Chuan Wei Hoo
Testimonials – CISO 360 series
 “Amazing speakers, very engaging and educational, professional, and extremely well organized. Looking forward to the next events.” – Allen Ohanian Chief Information Security Officer LA County DCFS
 “If you want to hear real CISO experiences, you must attend this event!” –Chuan-Wei Hoo, CISO, ST Engineering, Singapore
 “One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).” – Andreas Prass, CISO & DPO, 360 Treasury Systems AG, Germany
“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.” – Carole Embling, Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom
“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” – Jorge Fernandes, CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal
“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.” – Matthias Muhlert Security Bear – CISO HARIBO, Germany
““A very thoughtful event, great networking and industrial expertise in the room to learn from!” – Ryan Chan, Director, Security, Laureate International Universities Malaysia
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” – Manoj Wadhowa, Senior Manager, Cybersecurity, EY Singapore
“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!” – Viktor Polic CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland
“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.” – Richard Bloxam-Rose, Threat and Vulnerability Consultant, Computacenter, United Kingdom
 “It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.” – Deborah Saffer, Global Deputy CISO, Cushman & Wakefield
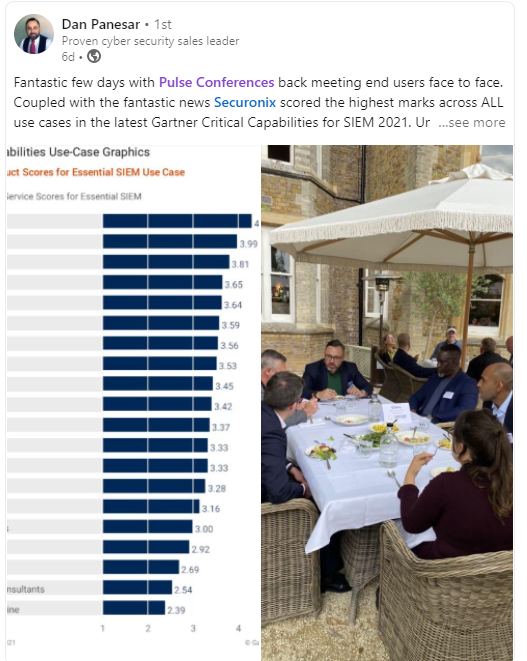
“Where else can you find a higher quality of security leaders all in one place?” – Owanate Bestman, Director, Bestman Solutions
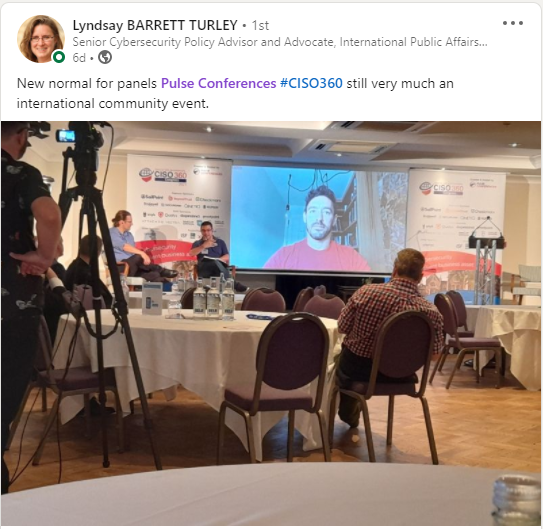
 “Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy” Manish Dave, Lafargeholcim
 “Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” Europe Industries- Security Officer, Air Liquide GMS
“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC
“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.” – Jonathan Armstrong, CEO, Cordery
“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.” – Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK
“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.” – Charles McAlpin, Qualys
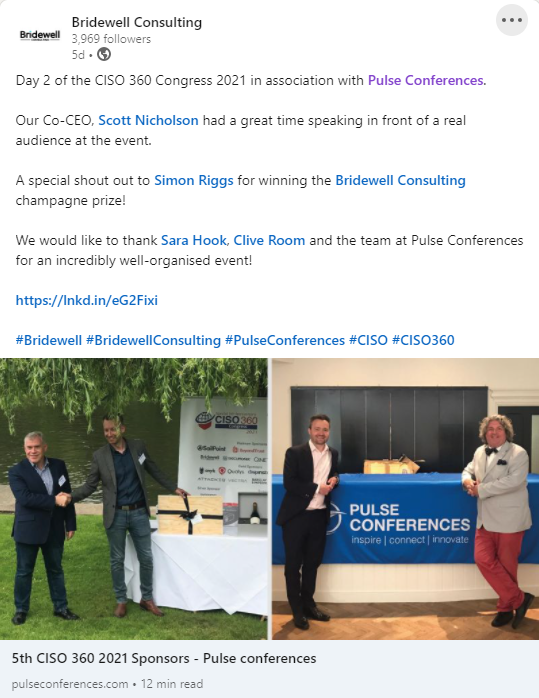
“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.” Chris McCann, Resilient. World
“A meticulous and engaging event highlighting the key security concerns business leaders face today!” Owanate Bestman, Bestman Solutions
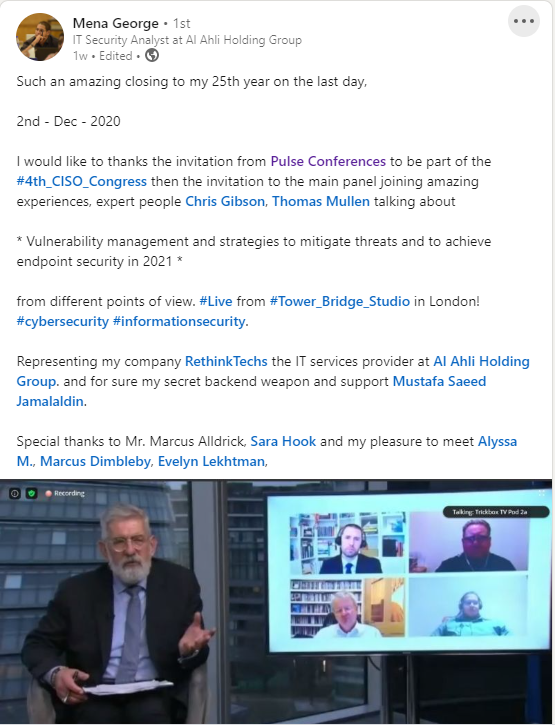
“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.” Technology Services Head of Cyber Security, DWP
“A very thoughtful event, great networking and industrial expertise in the room to learn from!” Ryan Chan, Director, Security, Laureate International Universities Malaysia
“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.” SailPoint
“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the 4th CISO 360 Congress-Hybrid. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.” – Peter Wood, Naturally Cyber LLP
“This was great, we have a lot of good take away’s and loved the lessons learned!” Sybil Kleinmichel, 360 Treasury Systems AG
“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting” Jennie Rogers, Vectra
“Overall Excellent Conference under challenging circumstances” Barbara Aung, Telefonica
“If you want to hear real CISO experiences, you must attend this event!” CISO, ST Engineering, Singapore
“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!” Senior Manager, Cybersecurity, EY Singapore
“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.” Synack
“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.” Company85
“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ” Company85
“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!“
Head of IT, intec, GOPA International Energy Consultants (Abu Dhabi)
 “Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with
CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin
“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”, Director Security Engineering, Inmarsat
Thank you @pulse_innovate for inviting me to speak on #neurodiversity at the #CISO360 Congress in Lisbon. Fantastic to meet so many inspirational Cyber leaders who are actively looking to increase their #diversity and share thoughts on the #cyberskillsgap pic.twitter.com/F8pSrHi5bh
— Holly Foxcroft (@holly_foxcroft) 21 June 2018
“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London
“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA
“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.” NetClean
“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!” Chief Privacy Officer, Nokia Group
“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.” SailPoint
“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!” Group CISO and Group DPO, MS Amlin
“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”, President, (ISC)2 Scotland Chapter
 “CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape” GRC Specialist, Euronext
It was an honour to talk at #CISO360Congress Thank you @pulse_innovate for inviting me. Here are my slides and more details on the topic covered.
https://t.co/MegpeFSAjO— Viktor Polic (@ViktorPolic) 26 June 2018
“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”, CISO, Channel 4
“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.” – CSO, Logista Portugal
“CISO 360 Congress 2019 created a strong platform for peer review, cross pollination of idea and networking.” CISO, Gebauer & Griller
“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Socio-Technical Lead, Redacted Firm Ltd
“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!” Director of Information Security EMEA, Canon Europe
Sad to be leaving #CISO360Congress from @pulse_innovate early as I have to be back in London tomorrow. Defintely the infosec conference of the year so far !
— Quentyn Taylor (@quentynblog) 21 June 2018
“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland
Great to see these kinds of debates at #CISO360Congress this is the model for future security conferences. It’s not all tech we need to develop and grow as an industry pic.twitter.com/tjXBp8SuWz
— Quentyn Taylor (@quentynblog) 21 June 2018
“Refreshing views of security topics for knowledge improvement!”
CISO, Credibom
““Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv
Our CEO @markfelegyhazi on the stage of the 2nd #CISO360Congress along with experts such as #DerekChang of @TalkTalk, #JamesKwaan from @IsacaScotland and #AftabAfzal @ensilo. Thank you all for an inspiring discussion! pic.twitter.com/GroejEJIFo
— avatao (@theavatao) 21 June 2018
High quality 60mins #CISO360 @mikko pic.twitter.com/khkIJhzsBB
— Jonathan Luff (@jjluff) 20 June 2018
“”The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government
“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ” Sailpoint
“”I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV
“Pulse Conferences stand out for being up to the minute with developments and concerns. Fist rate speakers
and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum
““Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall
““Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Head of Ethical Hacking, Redacted Firm Ltd
““Excellent conference, brilliantly put together.”
Director, Bridewell Consulting
Enjoyed presenting @CylonLab and our investor perspective to the #CISO360 conference today. Thanks for all the great questions!
— Jonathan Luff (@jjluff) 20 June 2018
Me using my hands (of course) to talk to leading CISOs from around the world about #cybercrime and #cybersecurity in #VR – and what we can do to prepare for the inevitable challenges. Thanks to @pulse_innovate for giving me the opportunity! pic.twitter.com/d5P2rIjlUC
— Dr Victoria Baines (@cyberbaines) 21 June 2018
“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!” Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)
Proud to have supported #CISO360Congress in Lisbon by @pulse_innovate. Thank you for having us as partners. pic.twitter.com/LerKkCopCv
— AP2SI (@AP2SI) 22 June 2018