Archive · Americas

5th CISO 360 Americas

This event took place on 25-26 March 2025 at InterContinental New York Times Square.

DATE25-26 March 2025
VENUEInterContinental New York Times Square

Thank you to everyone who participated in the 5th CISO 360 Americas

Event Details:
Location:
InterContinental New York, Times Square | New York
Dates: 25-26 March 2025

Post-Event Materials 2025

  • Part of the flagship CISO 360 Global series
  • One Pass, Two Days: The ultimate security co-location with the CSO 360 Americas – Resilience, Corporate Security, Intelligence, Investigations

Highlights Video – 5th CISO 360 Americas

Key Themes and Highlights

5th CISO 360 Americas Conference – Strengthening Cyber Resilience. Time to Redefine.

Led by, with and for CISOs, brought journeys, predictions and game-changers to life. Participants shared ideas and approaches with CISOs from diverse backgrounds and perspectives from around the world. Guests connected with peers in a relaxed setting in the evenings at our included receptions and dinner while enjoying the vibrant atmosphere of New York.

Key themes during the event

  1. AI + Quantum: Integrating the new frontiers in security
  2. Operational Resilience: First-hand experiences of compliance and surviving and thriving in complex and interconnected threat and regulatory landscapes
  3. Threat Intelligence + Fusion: Modernising SOCs
  4. CISO GRC Toolkit: Critical updates. What to work towards in 2025: Core Controls for 2025.
  5. OT-IoT-Cyber: Leveraging and mitigating converging trends, challenges and opportunities
  6. Supply Chain Security: Navigating risks in an interconnected world

Agenda-At-A-Glance

Monday, 24 March
6:00pm – 9:00pm | CSO 360 Welcome Reception
Kick off CSO 360 Americas with networking and introductions in an informal setting.

Tuesday, 25 March
9:00am – 4:00pm | CSO 360 Americas. Focus: Corporate Security, Resilience, Intelligence, Investigations.
Protecting People, Profits, Property and Reputation.

4:00pm – 6:00pm | The Bridge: Cross-Security Roundtable
Group discussion exploring the convergence of physical security, cyber, intelligence, electronic warfare, and product security.

6:00pm – 11:00pm | Networking Reception and Supper
CISOs and CSOs network and engage!

Wednesday, 26 March
9:00am – 5:00pm | 5th CISO 360 Americas. Focus: CISOs and cybersecurity practitioners.
Strengthening Cyber Resilience. Time to Redefine.

5:00pm – 7:00pm | CISO 360 Networking Reception
Unwind and connect with peers over drinks to close out the CISO 360 day.

Recent Speakers


Dr. Jessica Barker MBE
Co-Founder, Cygenta, Leader in the Human Side of Cyber Security (U.S.)


FC
Author of “How I rob banks”, Co-Founder, Cygenta. Frmr Hd Offensive Cyber Research, Raytheon, Ethical hacker (U.S.)


Jelena Matone
CISO
European Investment Bank
(Luxembourg)


Nick Gerteisen
Senior Director Security
Mark43
(U.S.)

The CISO 360 is one of my favourite congress, very good organized, great speakers, very good interaction and sharing of information.
Mark Snel, CISO, Signify (The Netherlands)

Anchor Partners 2025

Many thanks to our 2025 Sponsors

Platinum Protectors

Sapphire Sentinels

Emerald Enforcers

CISO 360 Innovators

Supporting Organisation

With thanks to our sponsors

Platinum Protectors

Sapphire Sentinels

Emerald Enforcers

CISO 360 Innovators

2025 Programme

FLYER-CSO-CISO 360 Americas-25-26 March 2025-NYC by Pulse – Sara

Speakers 5th CISO 360 Americas 2025

If you’re interested in speaking at this event please let us know!

We also welcome your input on companies, topics or persons you’d like to see on the agenda – teampulse@pulseconferences.com.

The 2025 programme is currently in development. The latest event flyer and programme can be found on Downloads.

Meet the International Speaker Panel – 5th CISO 360 Americas 2025

Cyrille VIGNON

Cyrille VIGNON

CEO, GLIMPS (France)

As a student in a school of engineering, Cyrille spent a transformative year in California working as a system architect for Texas Instruments. Immersed in a vibrant startup ecosystem, he was surrounded by passionate professionals and innovative startups like Yahouse and Arguin. This experience, enriched by interactions with dedicated individuals, ignited his ambition to one day start his own company. A few years later, Cyrille was selected to join DGA – Direction générale de l’armement (French Agency for Weaponry)’s cybersecurity reverse engineering team. This role expanded his expertise in reverse engineering and security, fields that were new to him. Working alongside remarkable colleagues, Cyrille learned how passion, kindness, expertise, and fun can combine to produce exceptional results. This ethos is at the core of GLIMPS, and Cyrille’s greatest pride is having succeeded in maintaining this spirit within his company.

Col. Eduardo Jany

Col. Eduardo Jany

Chief Security Officer - SVP Global Safety and Security, News Corp (USA)

Eduardo Jany is the Chief Security Officer – SVP Global Safety and Security for a major global media organization providing security and safety management and leadership for more than ten subsidiary organizations. He is also a respected security and safety consultant and has led award winning units in physical security, protective operations, travel, crisis management and event security efforts covering more than 25,000 people at over 190 offices worldwide through innovative strategies and processes. Eduardo has a special passion and drive for events and has planned and led in numerous security and dignitary protection operations for major events including the FIFA World Cup, Olympic Games, the Boston Pops 4th of July Spectacular, political conventions and well known summits and conferences.

Eduardo retired from law enforcement as a Captain after more than 25 years of police service in Florida, Minnesota and Washington State. He held command and supervisory assignments in patrol, SWAT, canine, narcotics and mounted units. He also retired as a Colonel from the United States Marine Corps having served 33 years of combined active and reserve duty in Anti-Terrorism, Investigations, Reconnaissance, Special Operations and Infantry assignments as well as prior service in the U.S. Army Special Forces.

He received a Master of Science in Criminal Justice from the University of Wisconsin Platteville and attended the University of Minnesota for undergraduate studies. He was a Senior Executive Fellow at the Harvard University Kennedy School of Government, and completed the Kennedy School National and International Security Senior Executive Program, the National Defense University Reserve Components National Security Program, and is a graduate of the United States Marine Corps Command and Staff College and the FBI DSEA and Graduate Academy. He is the Chairman emeritus of the Overseas Security Advisory Council Latin America CIC, the USVI Public Safety Support Foundation and is a member of the Boards of the FDR Four Freedoms Park and the Citizen’s Crime Commission of NYC.
Eduardo is active in several philanthropic organizations including American Corporate Partners, Theater of War and others.

A native of São Paulo, Brazil, Eduardo immigrated with his family to the United States in 1968, was naturalized a U.S. Citizen and speaks fluent Portuguese and Spanish. In his spare time he enjoys family time, weight training, triathlon, motorcycling, and fixed and rotary wing aviation.

Jake Bernardes

Jake Bernardes

CISO, Anecdotes (UK)

Jake Bernardes is a seasoned CISO with extensive experience spanning technical consultancy, advisory roles, and executive leadership. Throughout his career, Jake has worked and lived across the globe, amassing deep insights into building and scaling security programs for growth-stage and enterprise organizations alike. A proven expert in developing robust security and IT functions, Jake equally specializes in driving go-to-market strategies for security-focused products, particularly for international companies expanding into the U.S. market. His holistic approach to cybersecurity enables businesses to align their security posture with operational and strategic goals, ensuring resilience in today’s evolving threat landscape. Jake’s dedication to innovation and his practical understanding of security challenges make him a trusted partner to companies navigating complex regulatory environments and seeking scalable security solutions. He was an early adopter of many GRC solutions and have served in multiple customer advisory boards prior to joining Anecdotes, where he continues to lead with a vision of empowering organizations through smarter, data-driven compliance management.

Sounil Yu

Sounil Yu

Author and Creator of the Cyber Defense Matrix and the DIE Triad. Cofounder of Knostic (USA)

Sounil Yu is the author and creator of the Cyber Defense Matrix and the DIE Triad, which are reshaping approaches to cybersecurity. He’s a Board Member of the FAIR Institute; fellow at GMU Scalia Law School’s National Security Institute; guest lecturer at Carnegie Mellon; and advisor to many startups. Sounil is the co-founder and Chief AI Safety Officer at Knostic and previously served as the CISO at JupiterOne, CISO-in-Residence at YL Ventures, and Chief Security Scientist at Bank of America. Before BofA, he helped improve information security at several Fortune 100 companies and Federal Government agencies. Sounil has over 20 granted patents and was recognized as one of the most influential people in security by Security Magazine, Influencer of the Year by SC Awards, and a Top 10 CISO by Black Unicorn Awards. He is a recipient of the SANS Lifetime Achievement Award and was inducted into the Cybersecurity Hall of Fame. He has an MS in Electrical Engineering from Virginia Tech and a BS in Electrical Engineering and a BA in Economics from Duke University.

Scott A. Hawk

Scott A. Hawk

CISO/Director, Acalvio (USA)

Scott has over 30 years of experience in technology, beginning with classified electronic and software engineering roles supporting programs for the United States Navy. After joining Verizon in 1992, Scott gained increasing responsibility designing, operating, and protecting large global telecommunications network. He has worked in several disciplines around the world, including a multi-year stint in Europe where he ran a global solutioning organization for Verizon. Scott’s experience in cybersecurity began over 25 years ago when firewalls and VPNs became part of modern networking services. In the last 10 years, he has held several cybersecurity leadership roles that included running a global cybersecurity architect team for Verizon. This team consulted to some of the world’s largest and most complex organizations. After retiring from Verizon, he launched a new career as a cybersecurity consultant helping companies build resilient and secure infrastructures to protect their business. Scott currently consults for Acalvio Technologies where he is an evangelist for cyber deception and is passionate about the broad range of use cases it supports. Through his consulting company, he is also working as Virtual CISO, building GRC programs for companies so they can better defend against today’s advanced cyber threats. Scott has a bachelor’s in electrical engineering, a master’s in business administration and a number of industry certifications in leadership, security, and networking.

Dr. Chris Irwin Davis

Dr. Chris Irwin Davis

Associate Professor of Computer Science, The University of Texas at Dallas (USA)

With over a decade of experience in academia, Dr. Davis is dedicated to shaping the next generation of technology leaders through his research, teaching, and mentorship.

Before transitioning to academia, Dr. Davis spent 15 years working within Fortune 500 enterprises, where he honed his expertise in technology strategy, innovation, and leadership at Texas Instruments, Nortel Networks, and others. His extensive industry experience informs his approach to research and instruction, ensuring that his insights remain relevant and impactful.

As a Technology Strategist and Fractional CTO, he continues to advise organizations on aligning their technology initiatives with business goals, helping them navigate complex digital transformations.

Dr. Chantal Spleiss

Dr. Chantal Spleiss

Senior Consultant and CEO, Rocking Wolf Technologies GmbH (Canada)

Dr. Chantal Spleiss is a leading AI expert and senior consultant specializing in compliance for pharma and med-tech, with a strong focus on cybersecurity. Known for her deep technical expertise and practical approach, she is a notable voice in various realms.

In 2024, Dr. Spleiss spearheaded two influential white papers on AI Resilience and AI Risk Management, published by the Cloud Security Alliance (CSA). She also spoke at the CSA Global AI Symposium about AI Resilience Beyond Compliance by Leveraging Diversity.

She serves as a Co-Chair of the AI Governance & Compliance Workgroup at the CSA, and shared her insights as a panelist at the Cloud Expo Europe (Frankfurt) and at the CISO360 Congress (Marseille) discussing insights into AI and best practice resilience with CISOs and regulators.

With a unique background spanning life sciences, technical sciences, finance, and pharma, Dr. Spleiss excels at bridging disciplines to drive innovative solutions. Her expertise has been featured in Frankfurter Allgemeine Zeitung, where she was highlighted for promoting diversity in tech. Dr. Spleiss enjoys engaging in wide-ranging discussions about “life, the universe and everything”.

Connect: www.linkedin.com/in/chantal-spleiss

Meredith Wilson

Meredith Wilson

Founder and CEO, Emergent Risk International (USA)

Meredith Wilson is the Founder and CEO of Emergent Risk International, LLC, which empowers companies to understand and address the impact of geopolitical events on their business. The company specializes in addressing risks and opportunities in emerging markets, political and security risk, and building strategic risk intelligence programs for multi-national companies and organizations. ERI provides consulting, training and advice to some of the largest multi-national companies in the US. Ms. Wilson serves as a political risk and intelligence advisor to executive management and government and has more than 20 years experience in international environments, the energy sector, major corporations and the US intelligence community. Before founding Emergent Risk International, Ms. Wilson worked at the Pentagon for the US Defense Intelligence Agency. In 2007 she moved to the private sector to build a strategic intelligence program at ConocoPhillips. Subsequently she worked in regulatory affairs before moving on to Kosmos Energy to develop a political risk program. She served as a business intelligence advisor to the National Intelligence Officer for Science and Technology and provides briefings to executives and members of the USG and US military. She is a cofounder of the Private Sector Intelligence Council (PSIC), a member of the Board of Directors for the Association for International Risk and Intelligence Professionals (AIRIP), and an Advisory Board member for the Southeastern Analysts’ Roundtable. She has a Bachelor’s Degree in International Relations and a Masters Degree in History. Ms. Wilson has lived and worked in Australia, the UK, Ireland, Vietnam and Malaysia. She also has extensive experience working in the Middle East and Africa. She is available for speaking engagements related to geopolitical events and utilizing intelligence to build better business strategy.

Mike Beaupre

Mike Beaupre

Head of Cyber Security, Hays AG (Germany)

Michael is a technology leader with over 28 years of experience in guiding international public sector organizations, DAX 30 businesses, and mid-sized international firms through strategic technology initiatives. He is an expert in digitization and IT transformation and a thought leader in cyber security, organizational risk management, and IT compliance. He advises small and large enterprises ranging in size from 20 to 220,000 employees in the medical, pharmaceutical, biotech, translation, and manufacturing industries worldwide, just to name a few. Throughout his career Michael has led complex, diverse organizations toward enhanced operations while saving hundreds of millions in operating costs. He is passionate about mentorship, coaching, and removing cultural barriers. He was born in the USA, raised in Texas, and has travelled the world helping people maximize potential. Michael lives in Germany and is focused on family, volunteer work, and supporting a multitude of international clients at Hays.

David K. Young

David K. Young

President, Committee for Economic Development, the public policy center of The Conference Board (CED) (USA)

David K. Young is President of the Committee for Economic Development, the public policy center of The Conference Board (CED).

Previously, David was Chief Executive Officer of Oxford Analytica and responsible for the company’s global strategy and business operations. Founded in 1975, Oxford Analytica is a leading geopolitical and macroeconomic analysis and advisory firm working with a range of governments, multilateral organizations, and multinational companies to navigate critical global issues impacting businesses, governments, and society.

Prior to his time at Oxford Analytica, David was a management consultant at Atos where he advised senior executives on how best to achieve their business objectives by leveraging emerging technologies and a Director at an international charity. He has co-founded a cloud-based, mobile payment company and a boutique due diligence firm, advises multiple early-stage and not-for-profit organizations and continues to speak at prominent international conferences. David has a deep knowledge and appreciation of the work of CED through being a Trustee over the course of the last decade.

David graduated with a BA in government from The College of William and Mary, a MA in international security from the University of London, and a MBA from The McDonough School of Business at Georgetown University.

Haydn Brooks

Haydn Brooks

Co-Founder and CEO, Risk Ledger (USA)

Coming from a background in cyber risk specialising in supply chain security, Haydn quickly recognised the huge process issues, sunk cost, lost opportunities, and valuable business hours wasted by clients and suppliers alike, all trying to run disparate supply chain assurance programmes in a mutually exclusive way. This led Haydn to co-found Risk Ledger, the technology platform that combines a security governance platform with a secure social network. Haydn’s team is innovating and pushing mutual supply chain assurance and security governance into the twenty second century.

Forbes List 30 Under 30 – Manufacturing & Industry
Winner of the 2019 Cyber Den Award sponsored by the UK Government’s National Cyber Security Centre
Winner of the 2019 Most Innovative Cyber Company Award sponsored by TechUK.

Indy Dhiman

Indy Dhiman

Senior Security Architect, Humana (USA)

Indy Dhiman is a cybersecurity leader specializing in AI security modernization and implementation. As Senior AI Security Architect at Humana, she chairs the AI Due Diligence and Data Security Council, leading the development of a comprehensive AI security program.

Ned Farmer

Ned Farmer

Head of Global Intelligence and Security Programs, Transocean (USA)

As Head of Global Intelligence & Security Programs, Ned oversees all aspects of security for Transocean, a world leader in ultra-deep water and harsh environment offshore drilling. Closely supporting senior leadership, Ned is tasked with proactively mitigating geopolitical and security risks to operations worldwide. Prior to Transocean, as Geopolitical Risk Manager at American Airlines, Ned designed and implemented the geopolitical risk and security intelligence program. Ned has also served in a variety of leadership positions within the US State Department’s Overseas Security Advisory Council (OSAC).

Ned previously worked at Royal Dutch Shell, the Inter-American Development Bank, the US Congress, and Morgan Stanley. Ned received his B.A. in Political Science from McGill University in Montreal and his M.A. in International Affairs from American University in Washington, DC. He also studied at the Universidad de Salamanca in Salamanca, Spain. His graduate coursework focused on European energy security and Islamic extremist terrorism in Europe. He is fluent in Spanish and proficient in French.

Lorne Rolinson

CYBER Community Manager and Product Associate, The Hacking Games (UK)

Lorne is a computer scientist with a background in philosophy and a passion for cybersecurity. A recent Oxford graduate, she has been involved in the cybersecurity community since she was 11. Now a Product Associate at The Hacking Games, she explores the intersection of security, technology, and ethics.

Kumar Saurabh

Kumar Saurabh

CEO, AirMDR, Inc. (USA)

Kumar Saurabh is a highly knowledgeable and esteemed leader in the field of enterprise security. As the co-founder and CEO of AirMDR, he leverages his extensive 20-year experience to develop an AI-powered virtual assistant for security operations. This innovative solution not only addresses the pressing issue of cybersecurity resource shortages but also achieves unprecedented levels of productivity. Kumar’s expertise spans from his engineering leadership at ArcSight to co-founding SumoLogic a company that offers cloud SIEM services and his role as CEO of LogicHub, where he focuses on SOAR/MDR. With a master’s in Computer Science from Columbia University, specializing in random algorithms, machine learning, and cryptography, coupled with a Bachelor of Technology in Computer Science from the Indian Institute of Technology, Kharagpur, with a focus on artificial intelligence, algorithms, and machine learning, Kumar’s educational background is truly impressive. Driven by a passion for automation and a humble spirit, Kumar envisions making cybersecurity accessible and effective for businesses of all sizes. His goal is to deliver affordable cybersecurity-managed detection and response without compromising on speed or quality, all through the incorporation of AI.

Mark Adjei

Mark Adjei

Cyber Security Risk Advisory & Governance Leader, Financial Services (UK)

Mark Adjei is a seasoned cybersecurity executive with over 20 years of expertise in Cyber Threat Intelligence, Information Security Management, and Technology Audit. Currently serving as the CISO, Cyber Security Risk Advisory & Governance Lead at UBS, Mark plays a pivotal role in driving strategic initiatives to fortify global financial systems against an ever-evolving threat landscape.

With a proven track record across the financial, professional services, and energy sectors, Mark has led transformative cybersecurity programs, ensuring resilience against emerging threats. A key achievement includes spearheading a comprehensive cyber investigation aligned with global regulatory mandates, significantly enhancing UBS’s security posture. His leadership in Cyber Threat Intelligence Audits and e-banking infrastructure reviews has been instrumental in developing critical risk mitigation strategies, safeguarding assets, and ensuring regulatory compliance.

Recognized for a deep understanding of industry-leading frameworks such as NIST, ISO 27001, and MITRE ATT&CK, Mark employs a proactive approach to cybersecurity governance. His strategic expertise ensures robust security architectures and compliance frameworks that meet the dynamic needs of the global financial sector.

Beyond his professional career, Mark is passionate about coaching American football, where he applies his strategic thinking and leadership skills to the sport. He also actively follows current affairs and technological advancements, staying ahead of industry trends to continuously refine cybersecurity strategies.

Chuck Randolph

Chuck Randolph

Chief Security Officer, Ontic (USA)

Charles is Chief Security Officer at Ontic, a software provider that corporate and government security professionals use to proactively manage threats, mitigate risks, and make businesses stronger. In his role, he leads and oversees the global security and intelligence operations and strategy for Ontic and its clients, delivering innovative and effective solutions that leverage data, technology, and industry standards. Charles is passionate about transforming and enhancing the security profession and advancing its value and impact. He serves on the Board of Directors at the International Protective Security Board, a non-profit organization that promotes excellence and collaboration in the field. Charles also supports the U.S. Department of State’s mission to assist corporations as a member of the OSAC. He is a certified information operations and joint C4I professional, and is a published author and speaker on security topics.

Ryan Long

Ryan Long

Founder + CEO, INTELAB Ventures (USA)

Ryan founded INTELAB with the mission to equip Risk + Intelligence professionals with the tools, resources, and community to accelerate their success. Until March 2024, Ryan was the Head of Global Intelligence + Executive Protection at McDonald’s where he helped design and launch the company’s intelligence program.

Ryan began his professional career in 2003 as a U.S. Army Intelligence Officer and he’s held a variety of analyst, advisory, and management positions in both a reserve and active capacity, to include deploying multiple times to both Iraq and Afghanistan where he served with distinction while receiving numerous decorations. Ryan still serves in the Army Reserves where he commands an intelligence organisation focused on analytic, counterintelligence, and counterterrorism support to the United States European Command.

Ryan is also an active board member of the Association Of International Risk Intelligence Professionals (AIRIP), where he previously served a two-year term as AIRIP’s president. As a Veteran advocate, Ryan is a founding board member of the Veterans Leadership Council, the foremost business network for the current generation of Veteran leaders. Ryan’s latest endeavour is the creation of The Business Of Intelligence, a business podcast focused on discussing and innovating the field of private sector intelligence. Ryan has a bachelor’s degree with Honours in Political Science from the University of Illinois at Urbana-Champaign and a law degree from the University of Illinois-Chicago School of Law.

Patrick Kane

Patrick Kane

Senior Director Security, Atlas Air (USA)

Patrick Kane is Senior Director Security for Atlas Air, a US airline conducting cargo and public/private passenger operations worldwide. Patrick is heavily focused on developing and implementing mitigation measures to support a highly mobile global workforce and multiple travelers, to include pre-travel risk assessments, coordinating secure transportation and journey management, assessing hotel and transportation options.

Patrick currently serves as the Chair of the ASIS International Santa Barbara Ventura Chapter #21 and is the President of the Corporate Executive Protection Leadership Council (CEPLC). He recently spearheaded the creation of a Travel Risk Working Group within ASIS International. Patrick is also the past Chair and Chair Emeritus of the OSAC Aviation Security Working Group. He has over 20 years of experience working in private sector corporate security; most of that time focused on international operations and has personal experience on the ground in more than 70 countries.

Since 1996 Patrick has been a Certified Protection Professional (CPP) in good standing under the auspices of ASIS International. He received an International Executive MBA from Instituto de Empresa in Madrid, Spain in 2004. Prior to entering the private sector, Patrick served as an infantry officer in the US Marine Corps. He welcomes questions, comments and suggestions and he can be reached at patrick.kane@atlasair.com or patrick.kane.cpp@gmail.com.

Steve Hill

Steve Hill

Former Global CISO, Credit Suisse (UK)

Steve Hill is an independent strategic adviser, helping Boards to navigate geopolitics, national security and cybersecurity challenges. Steve served as the Group CISO at Credit Suisse and deputy Group CISO at UBS until August 2024. His previous appointments at Credit Suisse included Global Head of Operational Resilience and Group Head of Technology, Cyber and Third Party Risk.

Steve served in the British Government for over thirty years, including as Deputy Director in the National Security Secretariat of the UK Cabinet Office, with responsibility for aspects of cybersecurity policy. For over thirty years, Steve worked at the Foreign and Commonwealth Office in a variety of National Security roles with a focus on transnational threats including terrorism and weapons proliferation. He served overseas in Vienna, Washington, Dubai, Kabul and New York. Steve is a senior visiting research fellow at King’s College, London. He sits on several global advisory boards including those of Dell Technologies, Venari and Twine.

Dr Sally Leivesley

Dr Sally Leivesley

Managing Director Newrisk Limited UK, Member of the Register of Security Engineers and Specialists, international media commentator on cyber, catastrophic risks, terrorism and nuclear war (UK)

Dr Leivesley, sally@newrisk.com works on generic solutions to catastrophic risks to critical infrastructure across all disciplines and contributes practical applications to government policy and business. She has been a Panel adviser to for the British IET and CPNI supported publication for Cyber Security in the Built Environment. As an Advisor to companies and governments on protection of people and infrastructure and strategies for security and business Dr Leivesley has worked across industry sectors gas and petrochemicals; power distribution; hazardous goods transportation by rail; underground and aboveground rail; underground mines; bulk shipping and banks. As an international media commentator she has commentated for BBC World Service and other news outlets on extreme threats – Chinese spy balloon over USA nuclear missile site, uranium package at London Heathrow airport, cyber; terrorism; aviation losses; nuclear reactor explosions; Kabul 2021 evacuation; South China Sea; Polonium-210 and Novichok poisonings, Beslan siege; Iran; DPRK; USA Presidential security abroad; Covid-19, unexplained incidents such as MH370 and chemical incidents. Dr Leivesley has held international scientific meetings on issues of catastrophic risk including risks of emerging nuclear weapons, infrastructure resilience including cyber, Covid-19 solutions and hazardous near-earth objects. She was director of two disaster recovery units in Australia (weather and chemical incidents) and trained by British Home Office as Scientific Advisor holding a Cold War appointment as on all aspects of nuclear war. PhD London University; Member of the Register of Security Engineers and Specialists RSES; International Association of Bomb Technicians and Investigator; Royal United Services Institute for Defence Studies, and the British Information Assurance Advisory Council Community.

Stephen Khan

Stephen Khan

Chief Business Information Security Officer, Cognizant (UK)

Stephen is an information and cyber security practitioner, and international speaker with 20+ years of experience working for global firms across financial services, healthcare, and defence. Stephen has held senior group level positions at firms including HSBC, RBS, GSK, and Siemens with experience of global regulatory and cyber security frameworks to drive execution and implementation for the management of risks to support business strategies especially as technology and business models are changing at pace. Stephen is passionate about people and shares his knowledge and experience by coaching and mentoring senior leaders, and young people to achieve their potential. He believes people come into the workplace to do their best work, so leaders need to provide a positive empowered culture allowing teams to thrive and deliver the best outcomes through people, process, and technology. He contributes to Cyber Security community as Chairman of Club-CISO advisory board by engaging with 500+ global CISO executives on important matters affecting cyber security and risk leaders and their organisations. He supports the wider industry and academia through his board membership of Research Institute for Sociotechnical Cyber Security (RISCS), and advisory member of ISC2 UK cyber security council. Stephen is former Chairman of White Hat Ball which is a Cyber Security charity supporting the amazing work performed by NSPCC Childline in the protection of vulnerable young people. Stephen’ current role is Chief Business Security Information Officer at Cognizant Technology Services, where he is an amazing team of global business information security officers protecting top tier companies from cyber risks covering UKI, EMEA, APAC, India, Australia across all industry verticals. As one of the largest global professional services companies Cognizant help our clients modernize technology, reimagine processes and transform experiences so they can stay ahead in our fast-changing world.

Sybil Kleinmichel

MD, CISO Office, Commerzbank (Germany)

Thomas Gentsch

Thomas Gentsch

Senior Security Engineer, Stream.Security (USA)

Dr Viktor Polic

Dr Viktor Polic

CISO, ILO - United Nations (Switzerland)

More than two decades of professional experience in information management and governance, with particular focus on information security, risk management and assurance for large multilateral public sector organizations with global presence. Actively contributing to inter-organizational working groups for establishing policies, standards, and guidelines in the area of information security, personal data protection, awareness programs, risk analysis and metrics. Conducting research in cryptography, data protection regulation, and risk management. I’ve started professional career in information technology in the year of the release of Mosaic Web browser, Intel Pentium CPU, Microsoft Windows NT, Debian Linux, Doom computer game… Since the Internet bubble, teaching computer science and telecommunications courses as adjunct faculty at Computer Science Department of Webster University in Geneva. Actively contributing to academic program advancement as a member of the Scientific Committee for Advanced Studies in Information Security at the Department of Management Studies of the Faculty of Economic and Social Sciences at the University of Geneva. Advocating advancement in information security as an author in journals and as a speaker at professional conferences.

Zofia Kolodziej

Zofia Kolodziej

Marketing & Operations Executive, The Hacking Games (UK)

Zofia is a Marketing & Operations Associate at The Hacking Games. She holds a Bachelor’s degree in Psychology with Criminology, as well as a Master’s in Mental Health. Her interest in cybersecurity was sparked when her family became victims of a cybercrime. Having previously worked towards accreditation as a behavioural psychotherapist, Zofia now focuses primarily on the human aspect of cybersecurity. Outside of her professional career, Zofia has an impressive athletic background as a former member of the Polish National Volleyball Team

Platinum Protectors

Sibylline

Sibylline is an intelligence consultancy dedicated to helping security leaders identify opportunities and mitigate risks in their operating environments. We focus on risk, building resilience within organisations and helping them navigate environmental, social, and corporate governance. The firm provides trusted and expert advice to over 200 blue-chip and NGO clients, always focusing on adding value to daily operations as well as strategic and operational planning. Services range from geopolitical analysis and risk modelling through to investigations, training, consultancy on intelligence approaches, and the supply of fully turn-key embedded capability.

www.sibylline.co.uk | info@sibylline.co.uk | LinkedIn| Twitter | +44 (0) 20 3411 0697

AirMDR

AirMDR empowers small to medium-sized businesses with enterprise-grade cybersecurity through its Level 4 autonomous Managed Detection and Response (MDR) solution. Combining advanced AI and human expertise, AirMDR delivers consistent, high-quality threat detection and response, operating at the level of a Tier 3 analyst. With 24/7 coverage, AirMDR’s intelligent virtual analyst handles 90% of cases in under 5 minutes, creates playbooks 20x faster than traditional approaches, and seamlessly integrates with over 200 security tools.

Unlike traditional MDR services, AirMDR eliminates the trade-offs between automation and human oversight. Our solution is backstopped by experienced SOC professionals who ensure accuracy and provide actionable insights for even the most complex threats. This hybrid approach enables businesses to benefit from the speed and scalability of AI while maintaining the assurance of expert human validation.

AirMDR also helps organizations solve the classic “make vs. buy” dilemma in cybersecurity. Instead of building costly in-house SOC capabilities, AirMDR offers a more efficient, cost-effective alternative—reducing security costs by 50% compared to traditional MDRs. Whether you’re addressing cyber insurance requirements, compliance demands, or the need for a rapid, scalable defense, AirMDR is the trusted partner SMBs can rely on.

Visit us at CISO 360 or explore our solutions online at https://airmdr.com/ai-mdr to see how AirMDR redefines cybersecurity with unparalleled precision, speed, and cost-efficiency. Let us help your business stay ahead of evolving threats.

ERI Full Original

Emergent Risk International (ERI), is a global strategic intelligence advisory firm focused on business-centered risk and resilience. Specialized in geopolitical, regulatory and security risks in global business, ERI provides subscription intelligence and analysis, training, consulting and embedded solutions to the world’s leading organizations. For over a decade, ERI has delivered trusted geopolitical insights, trained thousands of intelligence professionals, set standards and led the way.
https://emergentriskinternational.com

Acalvio

Acalvio is the leader in autonomous cyber deception technologies, arming enterprises against sophisticated cyber threats including APTs, insider threats and ransomware. Its AI-powered Active Defense Platform, backed by 25 patents, enables advanced threat defense across IT, OT, and Cloud environments. Additionally, the Identity Threat Detection and Response (ITDR) solutions with Honeytokens enable Zero Trust security models. Based in Silicon Valley, Acalvio serves midsize to Fortune 500 companies and government agencies, offering flexible deployment from Cloud, on-premises, or through managed service providers.

acalvio.com

Risk Ledger Log

Did you know 60% of organisations have suffered a security breach through a third party? It’s understandable – the traditional processes are broken. Organisations face a burden of ineffective, inefficient admin. ‘Point in time’ cybersecurity assessments make for poor-quality data that goes out of date fast, offering little protection. Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost. The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it. With help from insights like this, many of our customers have improved their supplier contracts.

www.riskledger.com

Sapphire Sentinels

Control Risks

Control Risks is a global specialist risk consultancy that provides threat monitoring and security intelligence for the world’s leading organisations.

Think of us as your team of experts on watch for you 24/7, covering all areas of risk, security, crisis management and incident response.

We identify the risks and potential threats you might face; helping you to prepare and respond with the knowledge and skills you need to protect your people, business, data, and assets.

We also watch for any reputation risks. This way, you’ll be ready to make informed decisions about any incidents that may affect your operations – quickly.

We can seamlessly integrate with your existing risk management program and team. Instantly bolstering your capabilities with ‘on-tap’ access to the depth and strength of our risk and security expertise.

www.controlrisks.com/one

Emerald Enforcers

Comcast

Comcast is a global media and technology company. From the connectivity and platforms we provide, to the content and experiences we create, we reach hundreds of millions of customers, viewers, and guests worldwide.

www.corporate.comcast.com

CISO 360 Innovators

Ovalix

Ovalix empowers organizations to confidently embrace AI technology by mitigating associated risks such as data leakage, malicious prompts, shadow AI, and regulatory non-compliance across AI applications ranging from basic LLMs to sophisticated AI Agents. By ensuring robust security, maintaining regulatory integrity, and preventing data breaches, Ovalix enables organizations to unlock the transformative power of AI with peace of mind.

www.ovalix.io

GLIMPS

Founded in 2019 by reverse-engineering experts, GLIMPS offers cybersecurity solutions that use AI to detect and characterize malware in all file flows. Our AI and Deep Learning experts develop innovative solutions designed to strengthen your security while improving your operational efficiency.

www.glimps.re

Streamsec Black

Strike Sh

Who attends

Expected Focuses

  • CISO / Chief Security Officer
  • Cybersecurity / Cyber Threat Intelligence
  • BISO / Chief Information Risk Officer
  • CEO, CTO, CIO, CRO
  • Chief Security Architect / Head of Security Infrastructure
  • Head of Networks, Applications, Cloud
  • Director of Technology Innovation or Directors of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer

Across Industry Sectors

  • Financial Services
  • Insurance
  • Government
  • Energy and critical national infrastructure companies
  • Pharmaceuticals
  • Healthcare
  • Entertainment, Gaming, Gambling
  • Consumer Goods, FMGCs
  • Manufacturing
  • Retail
  • Transport and logistics

Expected Geos

  • 94% North America
  • 3% Central and South America
  • 3% Europe and Asia

Venue and Accommodation

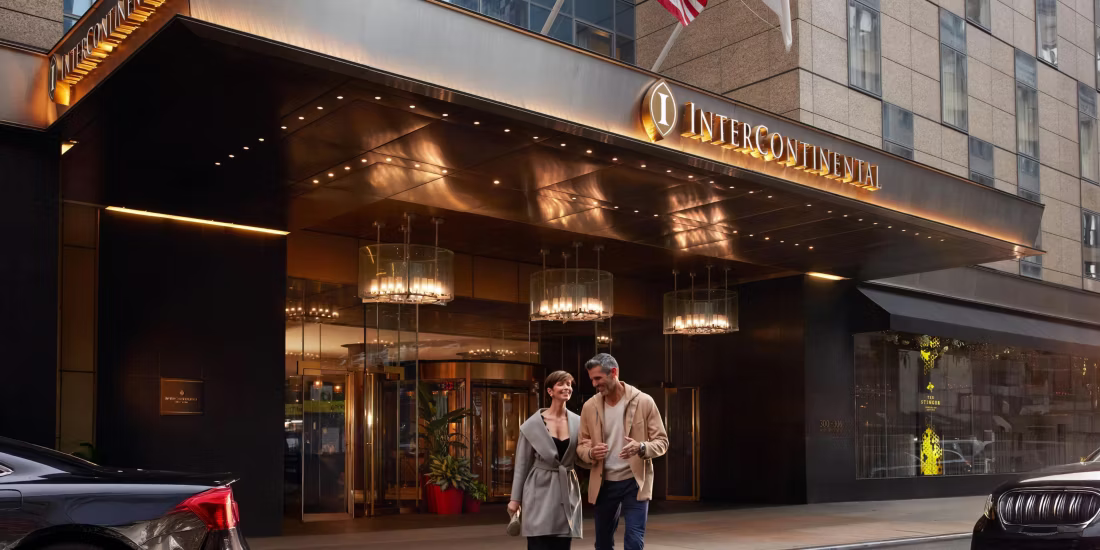
InterContinental
New York Times Square

300 West 44th Street New York, New York 10036 United States
www.ihg.com/intercontinental/hotels/gb/en/new-york/nychc/hoteldetail

The 5th CISO 360 Americas will be hosted at the elegant InterContinental New York, Times Square, a hub of tranquillity nestled in Midtown Manhattan’s Theatre District.

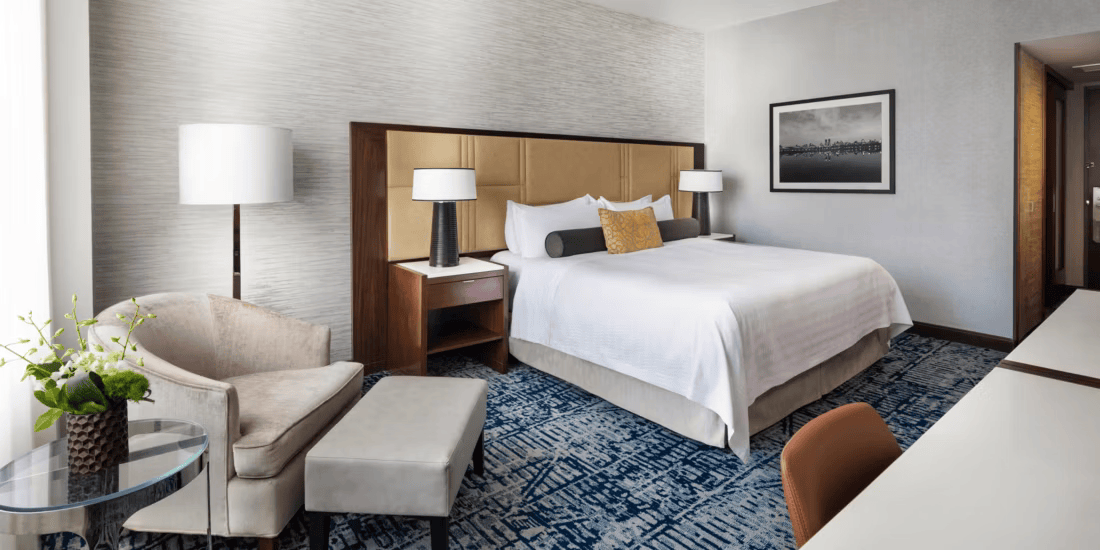
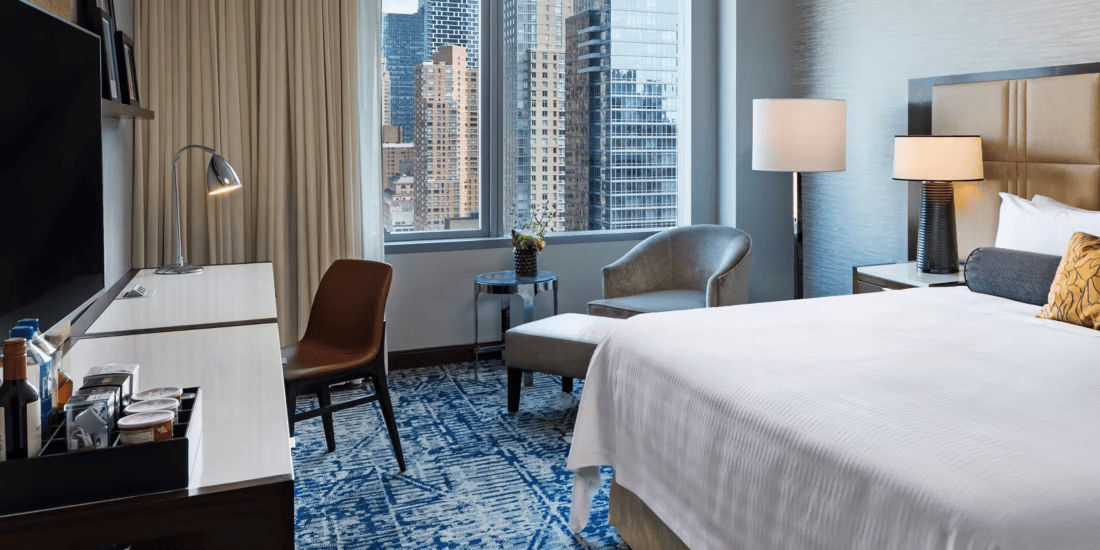
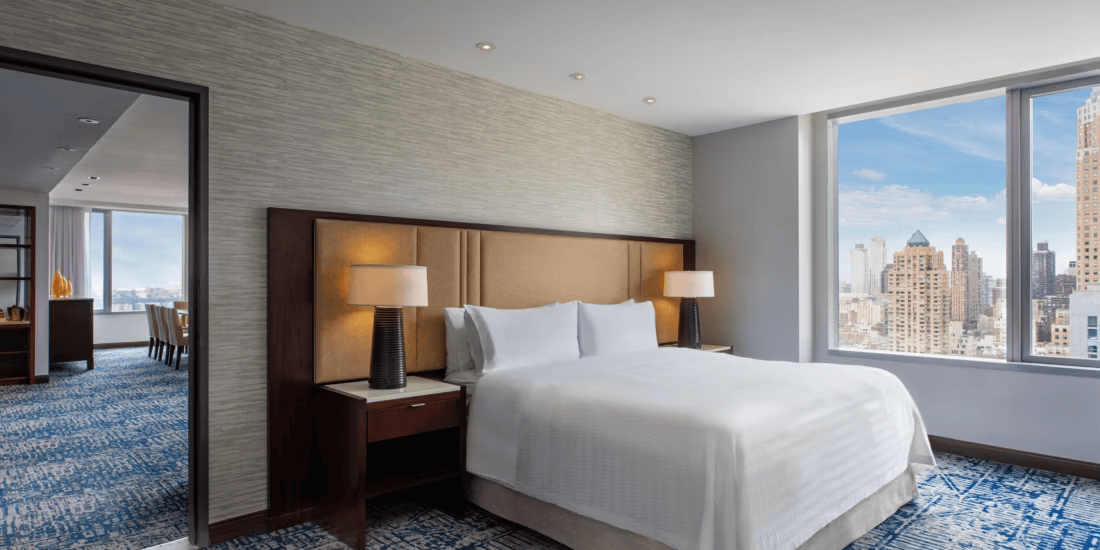
Rising 36 stories above the pulse and pageantry of Times Square, InterContinental offers understated luxury in the bustling sprawl of Midtown. Experience fantastic views of the Manhattan skyline, Hudson River and Broadway Theatre District. Enjoy spacious rooms with stunning views, fine dining, and exceptional amenities.

Discounted Accommodation

Pulse can offer discounted room rates at the InterContinental Times Square for the CISO 360 Americas Conference.

Single accommodation: $381.03 (including occupancy and room tax).
Breakfast Voucher available for: $48.21

Deadline: 17 March 2025

The hotel offers elegantly designed rooms, each with modern amenities, stunning city views, and a serene retreat from the hustle and bustle of the city. Complimentary Wi-fi for all guest rooms and access to the hotel fitness center, available 24-hours, 7 days a week.

  • Waived Destination Fee for Group (value of $35.00++ tax per room, per night)

The booking link for the discounted accommodation has now expired, but room nights are still available by contacting the hotel directly on +001 888-233-9527

Book your discounted accommodation now!

Conference venue

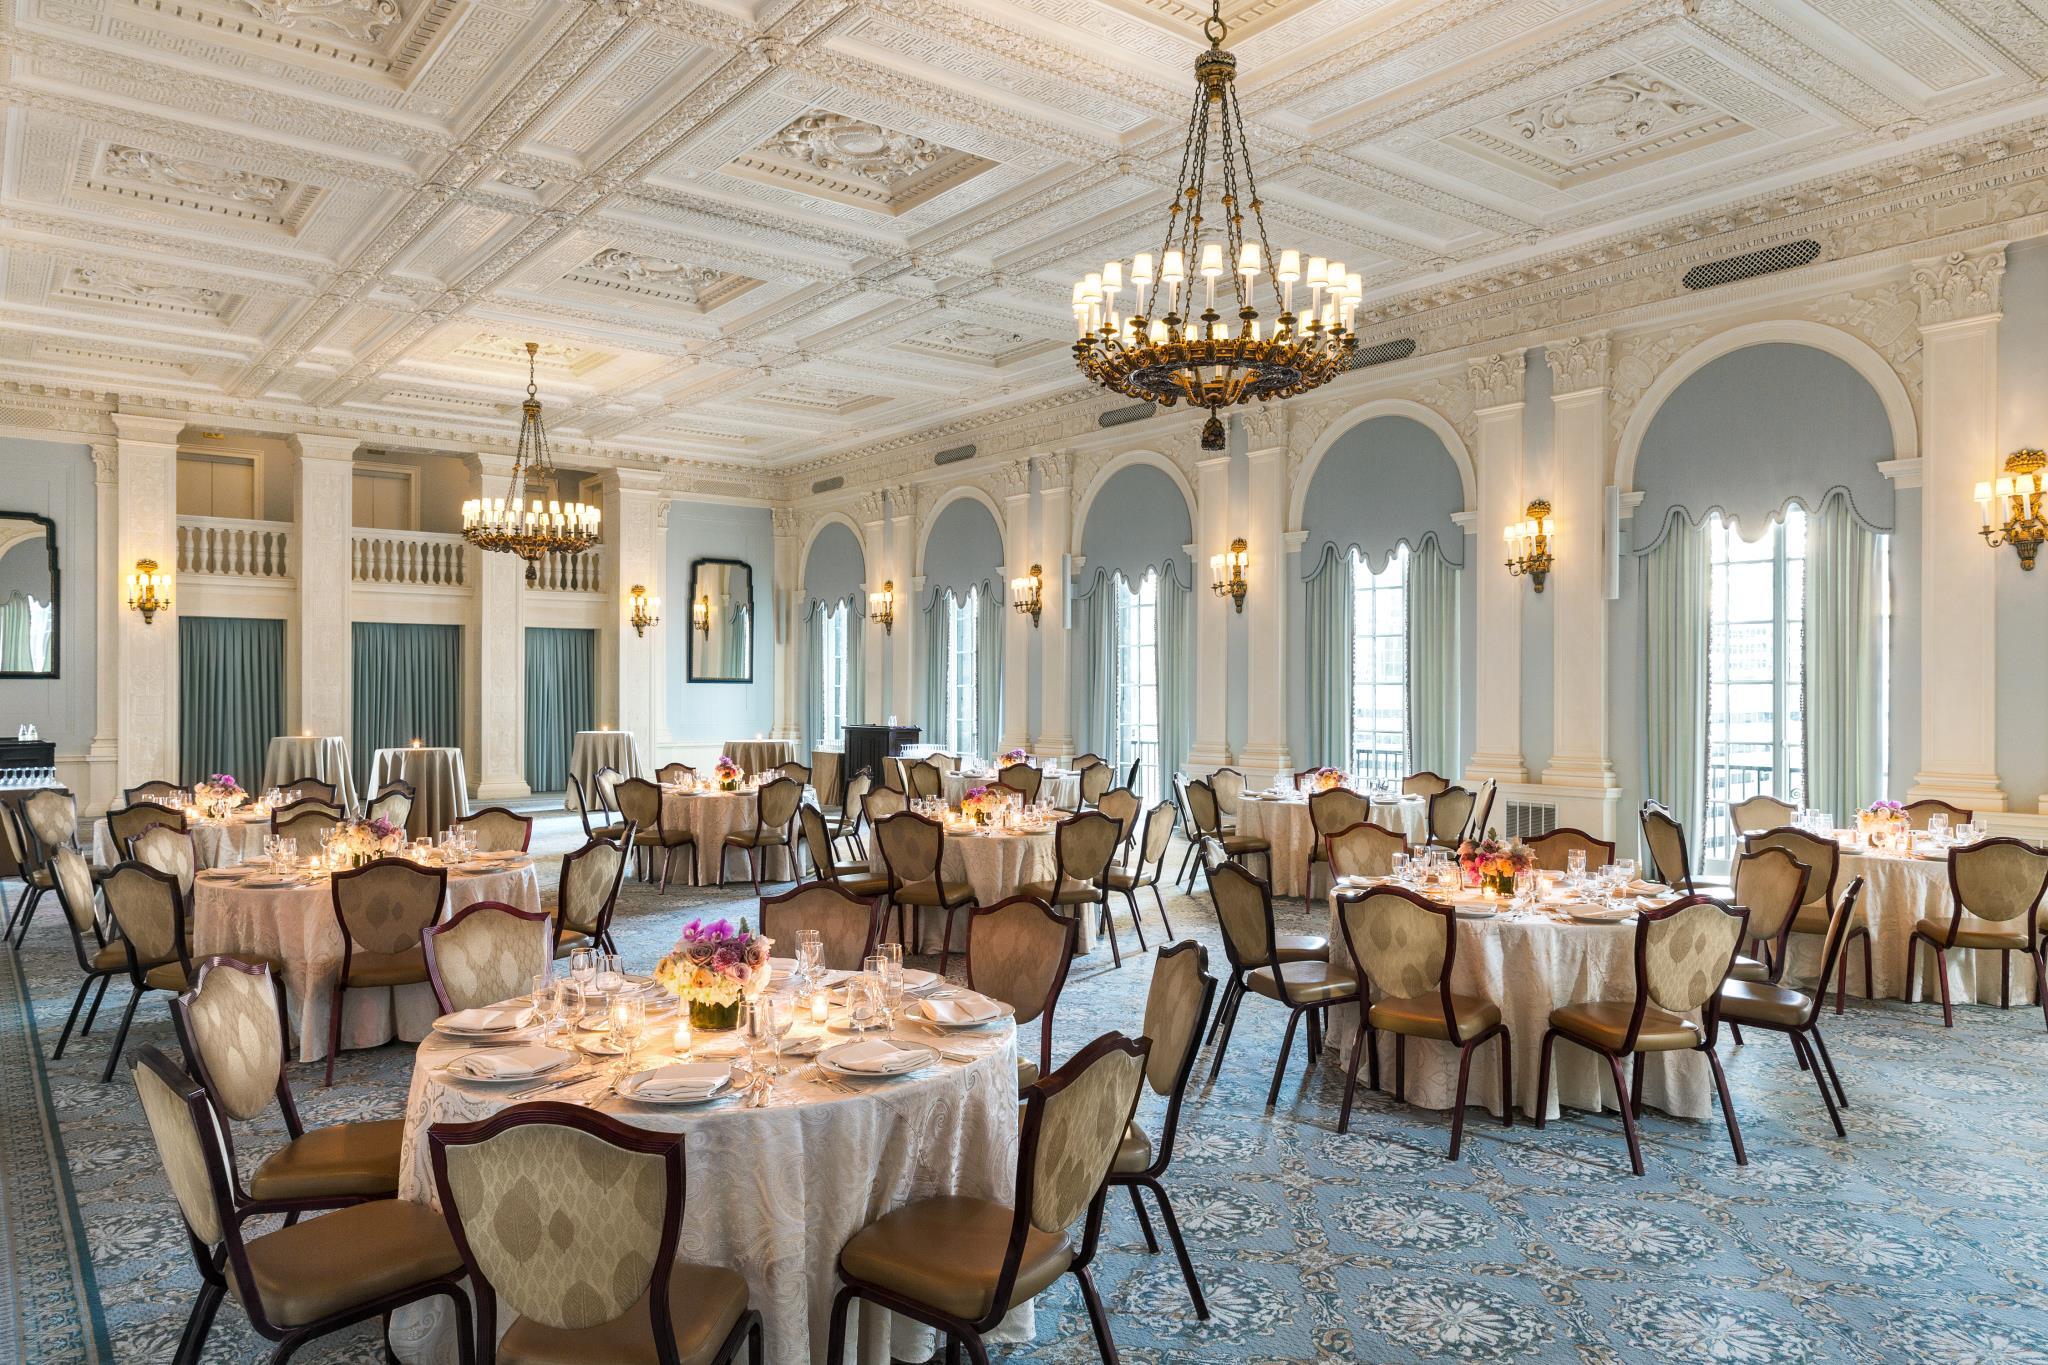
The 5th CISO 360 Americas will be hosted in the Gotham Ballroom.

InterContinental New York Times Square offers state-of-the-art meeting facilities with elegant surroundings and modern amenities. The 10,000 sqft of flexible event space includes the secluded Gotham Ballroom, with ceiling heights of 16.5.

Offering a spacious, yet intimate environment, the Gotham ballroom foyer will host our networking hub providing the ideal setting for seamless networking. This fantastic event space is complemented by expert catering and audio-visual resources.

Location

InterContinental, New York, Times Square
300 West 44th Street New York, New York 10036 United States
www.ihg.com/intercontinental/hotels/gb/en/new-york/nychc/hoteldetail

Located on Eighth Avenue, InterContinental New York Times Square feeds off the energy of this bustling district. You’re steps away from Broadway Theatres, Restaurant Row, Bryant Park, Rockefeller Center and Madison Square Garden. The InterContinental is within 37 metres of a Subway Station and 322 metres from Times Square.

Public Transportation

  • Penn Station, Moynihan Train Hall

  • 8th Avenue & 44th Street A,C,E and 1,2,3

Parking

  • Controlled access to parking.

Networking Dinner – 25 March 2025

  • The Yale Club of New York City, a 15 minute walk from where the event is IHG New York Times Square (walking and driving options will be offered to the group – or meet us there).

    50 Vanderbilt Ave, New York, NY 10017, United States.

intercontinental-new-york-9975465351-2x1-1

Testimonials – CISO 360 Americas

“Exceeded my expectations. Content & quality both were above par”
Yatin Patel IT Sr. Technology Lead PepsiCo (United States)


“Love how global the conversation is at CISO 360 Americas!”
William Lin, Venture Partner, Forgepoint (California, United States)

“Well-organised event with stimulating speakers on interesting topics!”
Rich Warner, Director, New York Metro InfraGard (United States)


“Very Informative, instructive and helpful!”
Schiller Rathjen, Information Security Manager, Ascot Group (United States)


“The conference was a blast! I’ve been to a bazillion conferences, summits, etc., and this one was by far one of my favourites. More intimate than many and great talks too.”
Allan Alford, CISO, TrustMAPP and Host of The Cyber Ranch Podcast (United States)


“The annual CISO360 Global Congress in Europe is one of my favourite events. It was great to speak at CISO 360 Americas in New York! Excellent interaction and sharing of information!”
Mark Snel, CISO, Signify (The Netherlands)


“Great venue, helpful staff and excellent engaging speakers!”
Shantanu Pal, CISO, Blankfein Scholes Capital Management (United States)


“Very interesting agenda – different to the usual agendas here!”
Javier Landin, Director Information Security, MSG (United States)


“Superb presentations and top notch talented leaders in the cybersecurity industry!”
Kobe Schwartz, Director Threat Intelligence, Signify (Israel)


“Smooth running, great venue, sponsors were great!”
Nick Gerteisen, Sr. Director, Cybersecurity, Mark43 (United States)


“Great conference, I learned a lot and met great colleagues!”
Patrick Kane, Senior Director Security, Atlas Air (United States)


In Action

Testimonials – CISO 360 Global Congress

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”
CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”
CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”
CTO and Co-Founder, JIT (Israel)

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”
Regional Executive, KnowBe4 (The Netherlands)

“Great conference! From the beginning, the level of participant engagement was very high. The content was very informative and the presenters very knowledgeable. Every aspect of Global CISO 360 was extraordinarily well done. I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”
Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”
Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well. Content and organization made this an excellent event!”
CISO, Infopercept (UK)

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”
Senior Account Executive, Hack the Box (Greece)

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”
GemServ, a Talan Group company (UK)

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”
COO, Risk Ledger (UK)

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”
CISO & DPO, 360 Treasury Systems AG, Germany

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Director, Security, Laureate International Universities Malaysia

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Director, Bestman Solutions

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
CMO, SailPoint

“Insights and experience shared by industry leaders will definitely help me and my organisation in course correcting the strategy”
Senior Cybersecurity, Lafarge Holcim

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
CEO, Cordery

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”
CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Global Deputy CISO, Cushman & Wakefield

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”
Senior Consultant, DHC AG (Switzerland)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”
Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”
CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”
Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”
Director, Resilient World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
Technology Services Head of Cyber Security, DWP (UK)

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the CISO 360 Congress. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.”
Peter Wood, Naturally Cyber LLP

“Excellent conference”
Barbara Aung, CISO, Telefonica

“This was great, we have a lot of good take away’s and loved the lessons learned!”
Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting”
CMO, Vectra

“If you want to hear real CISO experiences, you must attend this event!”
CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
CMO, NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
CMO, SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
CMO, Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Telstra

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ”
Supporting Organisation, ClubCISO

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”,
President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!”
CISO, GOPA International Energy (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”,
Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
CISO, Channel 4

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ”
Director Sales, Sailpoint

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

CISO 360 Congress created a strong platform for peer review, cross pollination of idea and networking.”
CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
CSO, Logista Portugal

“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Cygenta (USA)

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Cygenta (USA)

“Excellent conference, brilliantly put together.”
Director, Bridewell

“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Director of Information Security EMEA, Canon Europe (UK)

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Corporate Security Manager, Logista (Portugal)

“Marvellous event, well-run, packed with useful content you can use”,
Technology Services Head of Security, DWP

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV (Spain)

“Refreshing views of security topics for knowledge improvement!”
CISO, Bank Credibom (Portugal)

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv