Archive · CSO 360 Global Congress

3rd CSO 360 Congress

This event took place on 2-4 December 2020 at Budapest.

DATE2-4 December 2020
VENUEBudapest

The 4th CSO 360 Congress will take place 2-4 December 2020.
City to me announced soon!

3rd CSO 360 Congress
4-6 December 2019, Kempinski Budapest

Pulse Conferences would like to thank everyone who participated in the 3rd CSO 360 Congress hosted on 4-6 December 2019 at the Kempinski Corvinus in the wonderful city of Budapest.

“The Pulse 360 CSO Congress provided significant value and information in a short timeframe, particularly with regard to tradecraft, best practices, and networking.” – Claire Prestwood, Senior Security Intelligence Analyst for the Americas, Cargill

“The CSO 360 Conference was a fantastic opportunity to exchange information and perspectives in a collegial environment.“ – Patrick Kane, Senior Director of Security, Atlas Air

“The CSO 360 Conference was a fantastic opportunity to exchange information and perspectives in a collegial environment.“ – Patrick Kane, Senior Director of Security, Atlas Air

Connecting minds on security, resilience, intelligence and investigations priorities to protect people, profits, property and reputation

This trusted, community-based meeting is now an annual fixture in the diaries of Chief Security Officers and directors of intelligence, investigations, resilience and business risk. It enables truly global peer to peer sharing. We pride ourselves not only on who is on stage but who is in the room to bolster stimulating discussion and to share practical use cases on security challenges, successes, strategies and intelligence on the emerging threat landscape.

CSO 360 Congress tackles priority challenges for Chief Security Officers, most of whom oversee diverse areas and teams covering in corporate security, cybersecurity, information security, fraud, physical and executive and travel security, resiliency, forensics and investigations. Held under The Chatham House Rule, the programme offers a silo-busting, integrated and converged security focus to reflect the backdrop of increasing levels of global volatility, uncertainty, complexity and ambiguity.

  • Connect with global security leaders
    A new expert international panel of security experts will bring real experiences to pool brain power on the sustainability of global business amidst rapidly evolving threat landscapes and changes in geopolitical, technological and financial spheres.
  • Innovate your security strategy
    Partake in this share of strategies, tactics and methods for improving the protection of clients, employees and business partners as well as the security of assets, information and reputation.
  • Leave inspired for action
    Exchange practical approaches, innovation and strategies on the emerging threat horizon.
  • New for 2019! CSO 360 Roundtable – We have added the Roundtable on Friday morning (6 December)! This is a pure benchmarking discussion held under The Chatham House Rule. No presentations, the attendees set the agenda.

www.cso360congress.com

Congress Chairman:

  • Simon A. Scales, (former) Head of Investigations (FTSE 100) and Director of Global Investigations (AEX) companies

2019 International Speaker Panel:

  • Andy Williams, VP Business Development & Quality Assurance, Safehotels (SWEDEN)
  • Anthony Leray-Meyer, Regional Security Manager Western Europe Global Security, Abbott (UK)
  • Armin Sick, Manager Aviation Security, Lufthansa (GERMANY)
  • Basha Galvin, Head of Investigations, Tullow Oil (& Association of Corporate Investigators)
  • Bob Shaw, Senior Security Advisor, United Nations (and Co-Founder, The Exercise Group)
  • Cedrick Moriggi, Global Head of Security and Resilience (CSO), LafargeHolcim (UK)
  • Dr Christoph Rojahn, Partner, Compliance & Forensic, KPMG AG (GERMANY)
  • Claire Prestwood, Senior Security Intelligence Analyst for the Americas, Cargill (USA)
  • Crawford Robinson, Group Head of Investigations, British American Tobacco (UK)
  • David Jesson, Sr. Analyst, Global Intelligence/ Incident Management, Royal Caribbean Cruise Lines (USA)
  • Derek Cheng, CSO, TalkTalk (UK)
  • Dvir Rubinshtein, Aviation Security Operation Center Manager & Aviation Security Expert, Security Division, Israel (ISRAEL)
  • Eduardo Jany, Executive Officer, Global Security Operations, Bloomberg LP (USA)
  • Guillermo Gaspoz, Global Security Advisor, DSM (NETHERLANDS)
  • Henry Wilkinson, Head of Intelligence & Analysis, Director, The Risk Advisory Group
  • Heimo Grasser, Regional Head of Security CEMA, Medtronic, and Chief Awareness Strategist, SAME Solutions (UAE)
  • István Szabó, Chief Security Officer, Budapest Airport (HUNGARY)
  • James Richardson, Group Head of Security, The Weir Group (and Chair of SHE EXCOM) (UK)
  • Justin Crump, CEO, Sibylline Ltd
  • Marcus Alldrick, Digital Risk Management, Security and compliance advisor
  • Mark Reading, Managing Director, Seneca Risk (SIERRA LEONE)
  • Mark Wolsey, Group Security Director, CRH plc. (UK)
  • Matthew Judge, Group Managing Director, Anvil Group (UK)
  • Mehdi Khoali, Principal Investigations Officer, African Development Bank (Ivory Coast)
  • Mike Croll, Global Security Advisor, International Commission on Missing Persons (ICMP) (Netherlands)
  • Mike Lycett, Group Head of Security and Risk, De La Rue (UK)
  • Michael Mallard, Security Professional (USA)
  • Ned Farmer, Geopolitical Risk Manager, American Airlines (USA)
  • Liz Chamberlin, Executive Director, International Security Management Association (ISMA)
  • Lady Olga Maitland, Founder, Defense & Security Forum, Chairman, Copenhagen Compliance (UK)
  • Patrick Kane, Senior Director of Security, Atlas Air (USA)
  • Robert Aldous, Group Head of Operational Security & Intelligence, Prudential (UK)
  • Ryan Long, Head of Global Intelligence, McDonald’s Corporation (USA)
  • Dr Sally Leivesley, Director, Newrisk Ltd & Founder Member, The Exercise Group7 (TEG7)
  • William Sandover, Special Adviser, Intelligence and Analysis, Risk Advisory & International Affairs Adviser, Cathay Pacific Airlines (UK)

Key themes to date for CSO 360 Congress 2019 include

Strategies, tools and tactics required to proactively predict and mitigate threats….

    • HORIZON – Geopolitical insights into the global security landscape – hotspot mapping and predictions
    • LEADERSHIP – Culture, privacy and behaviours, engagement
    • INTELLIGENCE – Building effective intelligence; emerging threats
    • AVIATION & TRAVEL – Aviation security – decision-making behind the scenes!
    • INVESTIGATIONS – Investigations Roundtable
    • RISK – Cyber, privacy, data and identity, emerging realities
    • PLAN B – Response, crisis, emergency and business continuity

Agenda at a Glance – Budapest 2019
Timings are still approximate

Tuesday 3 December
19:00-21:00 Welcome Reception – Kempinski Budapest Hotel

Wednesday 4 December
Day One – CSO 360 Congress
08:45-09:00 Coffee
09:00
Chairman’s Opening
13:00-14:00
Lunch – Kindly sponsored by: SafeHotels Alliance
17:30
Close of Congress day one
18:00-22:00
Networking – Reception and dinner cruise on the Danube – Kindly Sponsored by: Sibylline

Thursday 5 December
Day Two – CSO 360 Congress
08:45-09:00 Coffee
09:00 Chairman’s Introductions and objectives
13:00-14:00 Lunch – Kindly sponsored by: One Voice
17:15 Close of Congress day two
18:00-21:30 Networking – wine-tasting and dinner

Friday 6 December
CSO 360 Roundtable
Pure benchmarking discussion. Attendees shape the agenda!
08:45-09:00 Arrivals and coffee
09:00-09:15 Chairman’s Introductions and objectives
13:00-14:00 Lunch and goodbyes

Hear directly what speakers, sponsors and delegates thought.


Pulse Conferences would like to thank all speakers, sponsors and delegates who participated in the 2nd CSO 360 Congress, hosted in December 2018 in Vienna. See Archives here.

“Embraces the changing threat environments, great experience, fabulous speakers, pertinent interesting focus”
Special Tribunal for Lebanon (The Hague)

“I just had the best conference ever!”
CCO, BT (Netherlands)

“A great one stop shop of the top CSO minds!”
VP, Corporate Security and Resilience, Pearson (UK)

“I was extremely impressed by the content, quality, origination and administration of the Pulse product”
MD, Tierra Nova Solutions (Sierra Leone)

“Simply the best event for security practitioners. Real expertise and knowledge sharing”
Group CISO, Unipart Group (UK)

“This has been a fantastic event. Awesome speakers addressing a diverse range of interesting and relevant topics. Also, great job by Team Pulse. We have been looked after so well! Thank you!”
Regional Security Director, Caterpillar Inc (Switzerland)

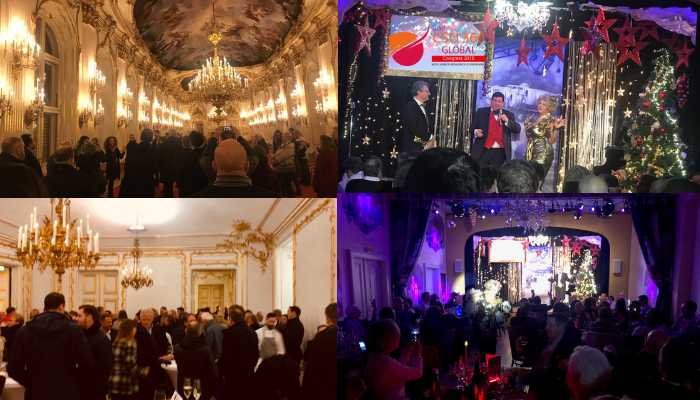
Networking events – an integral part of any CSO 360 Congress experience!
All delegates, speakers and sponsors are encouraged to attend. There is no extra cost.
Our special dinners, receptions and cultural activities ensure that you will leave the event with new professional friends and international contacts!

Pulse Conferences Privacy Policy

To read about Pulse Conferences Privacy Policy and download in pdf format please click below.

Download Privacy Policy

Gold Sponsor

Networking Sponsor

Lunch Sponsors

Panel Sponsors

Cyber Physical Threat – Bridging the Cultural Divide

Written by our inhouse resident editor, Lyndsay Turley, an experienced communicator and cybersecurity advocate for over 15 years.

As a concept, the convergence of cyber and physical security has always been seemed logical. In practice however, while many can agree that the threats to physical and IT infrastructure are increasingly similar, the defences are anything but. Despite many years of talking about convergence, accountability for emerging areas of cyber-physical risk remains unclear. As both operational and IT drive forward technically, the gaping hole in organisational security seems to be widening.

“People can buy commercial drones with awesome cameras; analyse Street View on the Internet; and take advantage of social engineering for intelligence gathering. Things that were the preserve of governments are now cheap and accessible for others. There is a lot out there,” warned one CISO 360 speaker, a former intelligence officer, at our Congress in Rome last month.

Cyber physical threat became a persistent theme at Congress this year, with a role to play in most of the “top 5” concerns to emerge from event discussions – ranging from the human ingenious social engineering, through to the risk of long life IoT encryption becoming obsolete in a quantum era and of course the persistent lack of security by design embedded into the proliferation of connected fridges, kettles, toys and more.

The most telling moment emerged from an interactive group exercise, when the CISOs in the room admitted they were unclear who should or who would be best placed to manage the threat coming from an autonomous drone flying outside of a tall building. The threat was to the safety of the building and the employees within, therefore a physical security issue that was deriving from a sophisticated piece of technology. Questions over accountability for the maintenance of sophisticated air conditioning systems met with similar response, yet all in the room were familiar with infamous case histories of vulnerabilities in these systems that had been successfully exploited.

Discussions pointed to cultural differences between information technology, plant and operational technology, and industrial technology preventing genuine collaboration and leaving different areas of the business to march forward on their own. This was illustrated by Telstra when they put SCADA risk at the top of threat landscape in their Security Report this year citing companies increasing dependency on automation. “Organisations are working with multiple vendors and are not aware of all the possible devices that may reside on the same network. Vendors tend to manage exposures to the outside world which means that overall security is now much more affected by industrial suppliers than before.”

“It is not that the risks aren’t acknowledged but the pressures are changing. Air gap is becoming a dirty word, even for legacy systems, with the pressure to integrate industrial systems more and more,” said one workshop participant, who pointed out that advances in robotics are being made to, for example, avoid the need to shut down for scheduled maintenance, and underpin availability as a key objective for industrial systems. Specialised controllers have become the backbone of process control, including SCADA systems.

“The real challenge is the different priorities, practices, technologies and cultural issues that create real tensions between information technology and operation technology groups,” he said.

Our group did suggest that the timing for a convergence plan, and shared responsibilities may be approaching as the long-established operational priorities around safety concerns, not just economic loss, increasingly become at risk to cyber-attacks. This thought was aptly illustrated by a university researcher who shared his motivation for looking into the security of robotics: “We particularly looked at robots and security because of the fundamental change in how robots are being deployed. They (and the humans operating them) used to be protected in separate spaces, cages. Now humans are not just operating robots they are interfacing with them,” he said. “We need to be fundamentally redesigning cyber-physical systems to, not just avoid concerns, but allow them to achieve their purpose in the case of a hack.”

My observation is that this conversation remains immature despite the decades of talk. We may well be approaching a tipping point for the convergence of cyber-physical risk with the rise of the machines, their autonomy, and their connection to our corporate networks but we haven’t yet figured out how to bridge that cultural divide that appears to be leaving us vulnerable.

The conversation is set to continue. Cyber physical risk and security convergence is a key theme for the upcoming CISO 360 Asia in Singapore this September and CSO 360 Congress in Budapest in December, international think tanks that are developed and hosted by Pulse Conferences. Join us if you can. The more experience, the closer we get to resolution and move the agenda forward as communities.

Pre-Event Pulse Educate Security Courses: Monday 2- Tuesday 3 December

Optional Training courses are offered in Budapest, pre-CSO 360 Congress, by Pulse Educate.

*All courses are subject to a minimum number of registrants

Monday 2 December, 08:00-17:00
Tuesday 3 December, 08:00-15:00

1. OSINT – Advanced Skills for CSOs
COURSE OUTLINE REGISTER NOW
2. Catastrophic Risk – Media and Reputation in Risk Mitigation
COURSE OUTLINE REGISTER NOW
3. Physical Security for Workplace and Travel
COURSE OUTLINE REGISTER NOW
4. The Threat from Business Espionage – Intelligence, Techniques and Responses
COURSE OUTLINE REGISTER NOW

WITH THANKS TO OUR SPONSORS

Sponsorship opportunities

Join the Pulse Sponsor Community!

Programme 3rd CSO 360 Congress

Download 2019 Flyer

Topics for the 3rd CSO 360 Congress in Budapest, 4-6 December 2019 are currently in research.

We would very much value your input into topics, case studies, keynotes and key themes that you would like to see on the new programme.

As the programme is developed, we will continue to add information to this page – check back frequently for updates or contact sara.hook@pulseconferences.com for the most recent draft programme. We also welcome your input and feedback on specific topics and themes for the 2019 programme.

Agenda at a Glance (timings are still approximate)

Monday 2 December
08:00-17:00 Optional pre-congress training courses

Tuesday 3 December
08:00-15:00 Optional pre-congress training courses
19:00-21:00 Welcome Reception – Kempinski Budapest Hotel

Wednesday 4 December – Day One – CSO 360 Congress,
08:45-09:00 Coffee
09:00
Chairman’s Opening
13:00-14:00
Lunch
17:30
Close of Congress day one
18:00-22:00
Networking events/ cultural activity and dinner

Thursday 5 December – Day Two – CSO 360 Congress
08:45-09:00 Coffee
09:00 Chairman’s Introductions and objectives
13:00-14:00 Lunch
17:30 Close of Congress day two
18:00-21:30 Networking events/ cultural activity and dinner

Friday 6 December – CSO 360 Roundtable
Pure benchmarking discussion. Attendees shape the agenda!
08:45-09:00 Arrivals and coffee
09:00-09:15 Chairman’s Introductions and objectives
13:00-14:00 Lunch and goodbyes

Speakers 3rd CSO 360 Congress

If you are interested in speaking at the 3rd CSO 360 Congress in Budapest this year, please let us know teampulse@pulseconferences.com.

Chaired by:

Simon A. Scales FCMI, (former) Head of Investigations (FTSE 100) and Director of Global Investigations (AEX) companies
Simon has over 30 years significant investigative, security and compliance related experience, formed from an extensive corporate and law enforcement background. He is recognised for having conducted complex Bribery, Corruption, Fraud and Misconduct investigations worldwide, in regulated and non-regulated arenas. He is internationally recognised for his public speaking credentials and his vast experience, having successfully led, directed and managed investigation, ethics, compliance and integrity teams within Europe, the USA, Africa and the Middle East. He has also been instrumental in delivering investigative services to the key emerging markets of South America, India and China.

International speaker panel:

Enquire about becoming a speaker

When it comes to telling a story, people want to hear about the challenges and failures as well as the successes.

Experience + value = story.

  • do you have a compelling business security story that simply must be told?
  • have you recently worked on an innovative security project?
  • are you willing to openly share inspiring insights, expertise and ideas to advance the security community?

We welcome your input into shaping the agenda and speaker panels.

Our programmes are highly researched with practitioners who do the job day in and day out. They are organic to ensure that we remain agile to meet the most current requirements.

For further information, please

+44 (0)20 7936 8989
or

teampulse@pulseconferences.com

alan-jenkins

Alan Jenkins

Trusted Advisor, Interim CISO, Principal Consultant, NED

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.

https://www.linkedin.com/in/alanjenkins/

chris-hayes-reliance

 Chris Hayes

Head of Incident Response, Reliance Cyber

https://www.linkedin.com/in/chris-hayes-68815a233/

Chrisi

Chrisi Baetz

CISO

Highly competent, organised, results-driven & innovative CISO with 16 years of international experience in Cyber Security, Risk & Control, Assurance, Governance & Oversight and Compliance in regulated and non-regulated industries (FS, utilities, chemical & manufacturing). Proven track record of delivering business-aligned cyber strategies to protect the businesses’ EBITDA and enable business growth. Strongly collaborates with C-level in highly challenging environments to deliver exceptional client experience. Delivered transformational change in greenfield and brownfield opportunities.

Has a ‘can do’ attitude towards solving complex problems by identifying creative solutions. Recognised for bringing out the best in team members through her excellent communication, motivational and coaching skills to manage teams effectively. She responds to challenges with dedication, perseverance, enthusiasm and pragmatism. Very ambitious and committed to self-development and progression to further deepen her leadership and technical competencies.

Key Achievements:
•Developed and delivered Cyber Security Strategies and Roadmaps at various internationally operating organisations covering both IT and OT to enhance their cyber resilience & protect their EBITDA resulting in an increase of maturity ratings by at least one tier
•Successfully navigated through cyber attacks to mitigate impact on business operations and protect against a financial loss of £120k
•Implemented ISO27001 to enhance the company’s reputation & customer trust and support the bid for a new business
•Delivered first Business Impact Assessment to mitigate gaps and improve the company’s overall business resilience
•Developed new reporting metrics to measure performance against the regulatory NIS-R requirements which were praised by the Drinking Water Inspectorate as an exemplar across the water industry; as a result the regulator asked the other water companies to use the same approach going forward
•Worked in cultural diverse companies which helped me to quickly flex and adapt my style to local communication styles e.g. UK, US, Germany, NL, Middle East (UAE) and Asia (Philippines )
•Built security functions from scratch and successfully moved it into BAU
•Securely manoeuvred through Covid-19

https://www.linkedin.com/in/christianebaetz/

graham-edwards


Graham Edwards

CISO, Domestic and General

A successful senior Chief Information Security Officer and Operational Risk Director with a proven track record in multi-cultural and multi-national organisations. Able to bridge technical and business disciplines and communicate at all levels. Extensive knowledge of Information Security, Cyber Security, Physical Security, BCDR, Operational Risk, Crisis Management, Data Protection, Financial Crime and Compliance. The first 16 years of Graham’s career were spent in the Diplomatic Service engaged in technical security for the Foreign and Commonwealth Office. He then moved to the financial services sector where he has held senior security posts with Abbey National, Standard Chartered, Barclays, RBS, HBOS and ING. Through these roles he has developed a holistic approach to risk management and security, holding responsibility for information risk, IT security, physical security, fraud, money laundering, business continuity planning, compliance, crisis management and intelligence. He has also worked outside of the banking industry as the Group Head of Information Risk for Centrica. He then held the position of Director of Data Security at Nationwide Building Society before taking the role as Head of Information Security at Camelot Lottery Solutions and then Interim Head of Cyber Security at Yorkshire Water. He has a master’s degree in Information Security from Royal Holloway.

https://www.linkedin.com/in/graham-edwards-8a502b2b/

GuidoGrillenmeier_blurpic_BG

Guido Grillenmeier

Principal Technologist, Semperis

Guido Grillenmeier is the Principal Technologist of Semperis in EMEA. Based in Germany, Guido has been a Microsoft MVP for Directory Services for 12 years. He spent 20+ years at HP/HPE as Chief Engineer. A frequent presenter at technology conferences and contributor to technical journals, Guido is the co-author of Microsoft Windows Security Fundamentals. Today he is concentrating on cyber-resilience, with a focus on Directory Services – both on-prem and in the cloud – securing companies around the globe.
https://www.linkedin.com/in/guidogrillenmeier/

Harry-Sweetman-Quest

Harry Sweetman

Public Sector Solutions Lead, Quest

https://www.linkedin.com/in/harrysweetman/

Heather-Lowrie

Heather Lowrie

Frmr CISO, University of Manchester

Heather is a technology, security and risk leader with a proven track record of achievement in government, public and private sectors. She was recognised by her peers as “CISO of the Year 2024” at SC Awards Europe and is a Fellow of the Chartered Institute of Information Security. With experience spanning in-depth engineering to board level management, Heather is adept at setting direction and taking accountability for security in large and complex organisations (> £1bn turnover). She is an accomplished strategist with significant experience of leading through crisis (including managing major cyber incidents), and leading strategic change for digital, AI, security and culture transformations. Heather has expert level understanding of the security implications of transformation and champions “secure by design” and engineering-based approaches to security. She combines people-centric leadership with a strong emphasis on the technical aspects of cyber security and resilience as part of her holistic approach.

https://www.linkedin.com/in/heather-lowrie/

Julian-Meyrick-Headshot

Julian Meyrick

Cyber Business Risk Advisor, Eraneos

A proven consulting and managed services sales leader with experience in winning large complex engagements, working at Board level with a focus on building long lasting trusted client relationships. Works with clients at a global level across all industries on the challenges of protecting client’s intellectual property, assets, brand and reputation from the impact of cyber. Built a global practice to assist clients in the development of security strategy in the context of cyber business risks; with a particular focus on advising Boards on the potential business impact of cybersecurity, and on quantifying cybersecurity risk in financial terms. Builds innovative marketing approaches to build new client relationships and deepen current client partnerships. In demand as a speaker to communicate cyber as a business risk to the C-suite, on conference panels, to analyst meetings, and to colleagues, on stage, on video and on social media. Joined the Tech UK Cyber Management Committee in 2018 and represented the private sector at the World Economic Forum Annual Cybersecurity Meeting in 2022. Leads in a matrixed environment, supporting teamwork and collaboration across globally distributed and culturally diverse teams. Committed to nurturing talent, actively coaching and mentoring members of the wider organization. Male Ally for the Women in Security Excelling programme from 2019 to 2023. Passionate about attracting talent into the cybersecurity profession and has been a member of the UK National Cyber Security Centre’s Industry Advisory Board for their CyberFirst programme since 2018. Founded the IBM UK veterans, Reservists & military spouses network in 2009, which received the MOD Gold Award and is a passionate advocate for training military veterans to help address the cyber skills gap, actively promoting non-profit initiatives such as Salute My Job and Tech Vets. An in-demand lecturer both at Oxford University’s Said Business School and Centre for Doctoral Training on Cybersecurity, and also at Warwick University’s MSc Course on CyberSecurity and Management. Joined IBM in November 1995 after serving six years in the Royal Green Jackets in the British Army, including serving as the Regimental Signals Officer.

https://www.linkedin.com/in/julianmeyrick/

Kevin-Fielder

Kevin Fielder

CISO, NatWest Boxed and Mettle by NatWest

Kevin is an innovative and dynamic security professional, with a passion for driving change by successfully engaging with all levels of the business. He is passionate about the benefits of cognitive diversity as a key ingredient of successful organisations.

Kevin is passionate about physical and mental resilience and wellbeing inside and outside of his work. He is an advocate for men ‘opening up’, and a coach to multiple fighters, including a Kickboxing world champion.

He believes that security should be made a key differentiator to drive sales and customer retention, not just a cost centre.

Kevin has been a board advisor to multiple start-ups and industry groups, such as The Cybermaniacs, LT Harper, ClubCISO, and an advisory council member to ISC2 UK. He has previously been the CISO for FNZ Group and JustEat. He’s currently the CISO at NatWest Boxed, building the UK’s premier provider of banking-as-a-service, and Mettle, a small business bank account by NatWest.

Kieran-B-bridewell

Kieran B.

Head of Security Engineering, Bridewell

Kieran serves as the Head of Security Engineering at Bridewell, where he leads efforts to strengthen digital defences and drive advanced cybersecurity initiatives. Bringing over 12 years of experience from his tenure at Microsoft, Kieran is a recognized expert in state-of-the-art cloud solutions and adept at addressing complex security challenges faced by clients. He holds a master’s degree in mathematics and physics, with a keen interest in the evolving fields of cryptography and quantum computing; so feel free to engage him in discussions about their potential to transform the digital landscape in the coming years!

https://www.linkedin.com/in/kieranbuk/

LM

Lawrence Munro

CTO, Reliance Cyber

https://www.linkedin.com/in/lawrencemunro/

Mark-Adjei-200x280-1

Mark Adjei

Director, Cyber Security Risk Advisory & Governance Leader (GCISO), Financial Services

https://www.linkedin.com/in/mark-adjei-b0035ab/

Mike-Conley-blue-voyant

Mike Conley

Chief Revenue Officer, BlueVoyant

Most recently the executive vice president for managed and cloud services at CDW’s Sirius, Conley also served on the board of directors. Prior to joining Sirius, Conley held the role of senior vice president at Forsythe Technology, now an integrated part of Sirius, where he specialized in emerging technologies and key accounts. He joined Forsythe in 1993 as an account manager and quickly rose through the ranks by serving many of the company’s largest clients, focusing on security strategies.

Conley has been a guest-lecturer for the Northwestern University Kellogg School of Management and the University of Notre Dame Executive MBA Program, educating executive business students about IT issues in business context. He is also a sought-after commentator on technology, including for Tech Talk with Craig Peterson, the No. 1 Saturday morning radio show in the Boston market. Additionally, he has been published in CIO Insight, IT Business Edge, and Information Today.

https://www.linkedin.com/in/michaelconleyit/

quentyn-2

Quentyn Taylor

Senior Director‚ Product, Information Security and Global Incident Response , Canon Europe Middle East and Africa

Quentyn Taylor is Director of Information Security at Canon Europe, Middle East and Africa. Using the power of stories and his own experience of testing products to destruction; Quentyn has embraced building business relationships across the world whilst driving Canon’s strategy and educating business customers to minimise their security risk. Before joining Canon, Quentyn has worked in a variety of industries such as Internet service providers as well as startup businesses.

https://www.linkedin.com/in/quentyntaylor/

Raghu-Nandakumara

Raghu Nandakumara

Head of Industry Solutions, Illumio, the Zero Trust Segmentation company

https://www.linkedin.com/in/raghunandakumara/

roy-whitehead

Roy Whitehead

CISO, CTO, UFORTA

Roy is a veteran Cyber Security, Industrial OT Security, Business and Tech Delivery Leader with nearly 30 years of professional experience in Financial Services, Retail, Travel, FMCG, Manufacturing, Energy, Government, Construction and many more industries.

He specialises in fractional CISO services, IAM, and helping security professionals sell their improvement and transformation programmes to the board.

Roy has also led major digital and business transformation programmes outside of security, giving him a broad perspective on delivering commercial value to the board.

Alongside his work with more established corporates, as a CTO, business owner/founder, he’s also helped a variety of startups mostly related to SaaS to commercially and broadly technically strengthen their pitch decks/value propositions

https://linktr.ee/roywhitehead

Simon-Christoforato

Simon Christoforato

CEO of Vivace - QinetiQ

Simon Christoforato is the CEO of Vivace, a QinetiQ Business unit, delivering the Accelerated Capability Environment (ACE) in partnership with the Home Office. Simon has over 30 years experience in National Security and Defence including the air, land and C4ISR domains. He has a broad background including start-up’s, Strategic Business Development, Systems and Programme Management. He has a proven ability to translate concepts into tangible commercial propositions and passionately believes in the power of collaboration, especially between the Public and Private Sectors to drive mission impact.

https://www.linkedin.com/in/simon-christoforato-5767713/ 

Simon-Hodgkinson

Simon Hodgkinson

Strategic Advisor, Semperis

Simon has 40 years of experience in information technology and cyber security across the software, financial services, and energy sectors. He spent 18 years working for bp in a variety of global roles, including the Group Chief Information Security Officer and VP of Global Infrastructure.

Simon now combines advisory and executive roles for several organisations, including Semperis, Onyxia, Cyera and E&Y.

He has been recognised for his advocacy of diversity and inclusion with several nominations for a top Corporate Ally.

Simon has served as an advisor to NHS Digital and Natural History Museum on cyber security.

https://www.linkedin.com/in/simon-hodgkinson-6072623/

1706037470122

Simon Mair

CISO

Risk, Compliance, and Control Professional with a proven record of providing thought leadership as well as technical expertise throughout the business. Pragmatic solution oriented with an eye towards results.

Strong analytical and technical skills, as well as experience communicating and working with client business leaders, stakeholders, project business sponsors, project IT team, and sales & marketing associates

Creating and executing test plans for operating systems and supporting software as well as IT and SOX controls

Microsoft software including the MS Office suite, especially: Word, Excel, PowerPoint, Visio, Project, and Access

Managing small to medium sized projects and leading teams of technical personnel

Controls, Compliance and Governance within a large organization

Understanding of COBIT, COSO, HIPAA, SOX, PCI, PII, and Privacy concerns

Process understanding, documentation, and improvement using Lean methodologies

Data classifications and best practices for compliance

Reducing risk using project security risk assessments and Outside Service Provider assessments (Third Parties)

RSA Archer eGRC Suite, Qualys Vulnerability Management, McAfee Vulnerability Management

Write and review Policies, Standards, Controls, and processes for IT Security Governance

https://www.linkedin.com/in/simonmair/ 

tim-ward

Tim Ward

Co-Founder and CEO, ThinkCyber

Tim is CEO and Co-Founder (with Dr Mike Butler) of Think Cyber Security Ltd. ThinkCyber offer the next generation in Security Awareness. Their Redflags® software product applies behavioural and learning science theory, in a highly innovative approach to deliver context-sensitive just-in-time guidance.

Tim has worked in IT for more than 25 years both in consulting and corporate IT with organisations including Logica, PA Consulting, Sepura and was previously Global Head of IT for the cyber division of BAE Systems (previously known as Detica). Tim graduated top of his year in Computer Science with AI at the University of Leeds, holds an MBA from the Open University and a Post Graduate Diploma in Entrepreneurship from Cambridge University.

Tim posts daily on security awareness and behaviour change topics on LinkedIn and is proud to have helped ThinkCyber gain significant recognition for their Redflags® product: Teiss Awards for “Best Cyber Security Training & Awareness Product or Service” in 2024, NCSC for Startups Programme, Accenture Fintech Innovation Lab 2022; TechUK Cyber Innovator of the Year 2021; SC Award Europe (Best Professional Training Programme); CyberTech100; TechInvest GovTech Top 10; Finalists in NYC Mayor’s Cyber Security Moonshot Challenge; members of TechNation Cyber 2.0 cohort; members of London Office for Rapid Cybersecurity Advancement (LORCA) cohort 1; Finalists Pitch@Palace 9.0.

https://www.linkedin.com/in/tim-ward-cyber/

tony-ryall-zero-trust-1

Tony Ryall

CEO, Zerotrust Security Solutions

Sponsors

ThreatLocker Wordmark ZTP Color

Risk Ledger

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

Interested in learning more? Visit https://riskledger.com/.

www.threatlocker.com/

Many thanks to the sponsors of our 2024 event!

Quest

Quest is the recognized leader in Active Directory and Entra ID modernization, ITDR and disaster recovery. For 40 years, 145,000 customers and partners have worked with Quest to reduce risk, operate with resilience and grow their mission with confidence. With the most complete set of hybrid AD security controls covering every NIST Cybersecurity Framework pillar, you can identify and prevent potential attacks, detect and block suspicious behavior, and recover 90% faster while saving £17M or more from ransomware attacks. Gartner recognizes Quest every year for ITDR and lists Quest twice as much as any other example vendor in its most recent IAM Best Practices for Active Directory research. For more information, visit Migration and Cyber Resilience for AD, Entra ID & Microsoft 365 (quest.com) 

www.mastercard.us/en-us.html

Bridewell

Bridewell is a cyber security services company that specialises in protecting and transforming critical business functions for some of the world’s leading organisations.

Their consultants work with clients to deliver end-to-end services that solve their security and business challenges. Bridewell’s specialists are highly accredited by major industry bodies and have extensive experience delivering services across cyber security, managed security, penetration testing, and data privacy.

Founded in 2013, Bridewell is headquartered in the UK where it runs a 24/7 Security Operations Centre (SOC) and has a growing presence in the US to further support global clients.

For more information, visit www.bridewell.com

www.emergentriskinternational.com

QinetiQ

QinetiQ is an integrated global security and defence company. QinetiQ has been established as a Cyber Security service provider and thought leader for longer than almost any other company in the world, continually providing assurance and resilience for our customers in a collaborative way. We address today’s rapidly changing cyber security environment, with decades of experience protecting the most highly targeted organisations and securing the most critical operations. With our defence-grade solutions, rigorous threat checks and our understanding of defending against the most persistent threats, we can help you build digital resilience so you can face the future with greater certainty.

www.qinetiq.com/

https://www.qinetiq.com/en/

Visit website

Semperis Full Color

For IT and security teams charged with defending hybrid and multi-cloud environments, Semperis ensures the integrity and availability of critical enterprise directory services at

every step in the cyber kill chain. The world’s leading organisations (representing more than 100+ million identities) trust Semperis to protect their identity infrastructure from

cyberattacks, data breaches, and operational errors. Purpose-built to secure hybrid Active Directory environments, Semperis’ Gartner-recognised, patented identity threat response and detection (ITDR) technology cuts ransomware recovery time by 90 percent.

As a force for good, Semperis hosts the Hybrid Identity Protection (HIP) Conference, HIP Podcast and offers free identity security tools (Purple Knight, Forest Druid). Semperis is headquartered in Hoboken, NJ.

Visit website

Risk Ledger

Risk Ledger helps organisations get their cybersecurity risk assessment tasks done in hours, not days and scale their supplier coverage from 5% to 95% so they can spot more vulnerabilities at just 10% of the cost.

The NHS used Risk Ledger to identify a situation where several third-party suppliers were all dependent on the same fourth-party supplier. They then worked with those third parties to first understand that risk, and then take action to mitigate it.

With help from insights like this, many of our customers have improved their supplier contracts.

Interested in learning more? Visit https://riskledger.com/.

Visit website

Illumio

Illumio, the Zero Trust Segmentation company, stops breaches and ransomware from spreading across thehybrid attack surface. The Illumio ZTS Platform visualizes all communication and traffic between workflows, devices, and the internet in one console, automatically sets granular segmentation policies to control unnecessary and unwanted communications, and isolates high-value assets and compromised systems to proactively or reactively stop the spread of a breach. ZTS is proven to help organizations of all sizes, from Fortune 100 to small business, stop breaches and ransomware in minutes, save millions in application downtime, and accelerate digital transformation projects. Assume breach. Minimize impact. Increase resilience.

www.illumio.com

Visit website

Reliance Cyber

Established in 2003, Reliance Cyber has emerged as a stalwart in the UK cybersecurity landscape. With a rich history spanning nearly two decades, our company has been at the forefront of safeguarding organisations across diverse sectors. From its early days, Reliance Cyber has navigated evolving threats, consistently adapting and innovating to provide cutting-edge solutions. Today, our legacy is one of unwavering commitment, proactive expertise, and a continuous readiness to face the ever-changing challenges of the digital security landscape.

Reliance Cyber is committed to a program of continuous innovation and research to secure our customers, at scale, for a sensible price.

www.reliancecyber.com

Visit website

Gurucul

 Gurucul is a security analytics company founded in data science that delivers radical clarity about cyber risk. Our REVEAL platform analyzes enterprise data at scale using machine learning and artificial intelligence. Instead of useless alerts, you get real-time, actionable information about true threats and their associated risk. The platform is open, flexible, cloud native and cost optimized. Organizations can save 50% or more while achieving complete data control, visibility, searchability, and analytics within a single console. Industry analysts have recognized our platform as a Visionary in the 2024 Gartner(R) Market Quadrant(TM) for SIEM for the third-consecutive year. Our solutions are used by Global 1000 enterprises and government agencies to minimize their cybersecurity risk. To learn more, visit Gurucul.com and follow us on LinkedIn and Twitter. 

Visit website

BlueVoyant

BlueVoyant delivers a comprehensive cloud-native security operations platform that provides real-time threat monitoring for networks, endpoints, and supply chains, extending to the clear, deep, and dark web. The platform integrates advanced AI technology with expert human insight to offer extensive protection and swift threat mitigation, ensuring enterprise cybersecurity. Trusted by more than 1,000 clients globally, and the 2024 Microsoft Worldwide Partner of the Year, BlueVoyant sets the standard for modern cyber defence solutions.

www.bluevoyant.com

Visit website

OnSecurity

OnSecurity is leading the way in pentesting, offering advanced cybersecurity solutions with effective and insightful testing. We make managing and delivering pentests easier with innovative technology, helping businesses of all sizes strengthen their security.

Visit website

Zero Trust Solutions

Zero Trust Solutions are a cyber security consultancy specialising in co-creating zero trust security architectures for enterprises. Our zero trust experts and proven consulting toolkits assess your enterprise maturity against zero trust first principles. Designing the best zero trust architectural implementation and configuration strategies is our forte. The approach is an architectural one, not a single vendor solution. Where clients are missing capabilities, our proprietary methods vet individual technologies against zero trust requirements or complete architectures when we run zero trust architecture RFPs. For existing zero trust projects, we can also reinforce your teams with resourcing and implementation skills.

Zero Trust Solutions empower your teams wherever you are on your zero trust journey.

www.ztsolutions.io

Visit website

Eraneos

Eraneos is an international management & technology consulting group providing digitalization and transformation services, from strategy development to implementation. Eraneos serves clients across three continents where some 1,100 dedicated and highly skilled professionals work jointly to unleash the full potential of digital​. Services range from the development of digital business models and data analytics to cyber security, and from sourcing and IT advisory to the management of complex transformation projects.

eraneos.com

Visit website

Picus Security

Picus Security, the leading security validation company, gives organizations a clear picture of their cyber risk based on business context. Picus transforms security practices by correlating, prioritizing, and validating exposures across siloed findings so teams can focus on critical gaps and high-impact fixes. With Picus, security teams can quickly take action with one-click mitigations to stop more threats with less effort.

Picus Security provides a threat exposure management solution, powered by our Exposure Data Fabric and Numi Ai™ . The platform offers several capabilities including: breach and attack simulation, automated pentesting, cloud security validation, detection rule validation and attack surface management.

The pioneer of Breach and Attack Simulation, Picus delivers award-winning threat-centric technology that allows teams to pinpoint fixes worth pursuing, offering a 95% recommendation in the Gartner Peer Insights Review for the Breach and Attack Simulation category.

www.picussecurity.com

Visit website

Thinkcyber Landscape Black Text Transparent Heavy

ThinkCyber deliver measurable secure behaviour change for their customers, empowering people to protect themselves against cyber threats. Their multi-award winning Redflags® Real-time Security Awareness software applies behavioural and learning science theory to deliver context-sensitive, just-in-time security guidance. For example, when users are about to click links, visit certain web pages, enter their username into a web page, handle attachments, etc.

Redflags® won the Teiss Awards for “Best Cyber Security Training & Awareness Product or Service” in 2024 and techUK Cyber Innovator of the year 2021; it was part of NCSC for Startups Programme and Accenture Fintech Innovation Lab 2022.

www.thinkcyber.co.uk

Visit website

Sphere

 Sphere is positioned to become the go-to global private network for B2B tech marketers. Acting as a ‘little black book,’ Sphere connects members with industry peers, trusted suppliers, contractors, recruiters, and premier events. It fosters a dynamic community where innovative ideas are shared and validated, offering real-time assistance and valuable industry insights.
Created to be more than just a network, Spheres aim is ultimately to equip tech marketers with the tools, resources, and connections they need to thrive. From accessing reliable suppliers to engaging with peers and attending exclusive events, Sphere supports your success in a complex industry. Learn more here: www.the-sphere.network 

Visit website

The ISF

The ISF is a leading authority on information security and risk management. An independent organisation, we provide opinion and guidance on all aspects of information security. We deliver practical solutions to overcome the wide-ranging information security and risk management challenges that impact business.

For more information, visit: www.securityforum.org

Visit website

Who attends

By Designation

Participants will include CISOs and CSOs in addition to:

  • Chairperson
  • CEO
  • Non-Executive Directors, Board Member, Audit & Risk Committee Member
  • CFO, CRO, GC, COO, CTO, CIO, CMO, HR
  • Chief Information Security Officer
  • Director of Cybersecurity / Head of Cyber Threat Intelligence
  • Head of Governance
  • Head of Innovation
  • Director of Digital Risk
  • Chief Data Officer
  • Chief Privacy Officer
  • Heads of Corporate Security/Resilience

By Sector

All private and public sectors are welcome to attend.

Venue  

Science Museum, London

Groups Entrance – Illuminate Science Museum, Imperial College Road
South Kensington, London, SW7 2DD
www.sciencemuseum.org.uk

We are thrilled that the Science Museum in London will be the venue for this years’ 6th Cyber Exchange 360: Talk to the Board. An inspiring landmark with award-winning exhibitions, iconic objects and stories of incredible scientific, technological and medical advancement and achievement.

Click here to view further directions to the Groups Entrance at The Science Museum

Main event space – Illuminate

Illuminate is the world-class event space located in the heart of the Science Museum where the conference will be hosted. This space is a progressive new award-winning venue situated on Levels 4 and 5 of the Science Museum. Among the unique features of this new space is a panoramic window, offering stunning views of the City and an abundance of natural daylight, a key element in ensuring a productive meeting or conference experience.

Networking Reception in Wonderlab: The Equinor Gallery

The networking reception with drinks and canapes at the end of the day will be downstairs in Wonderlab: The Equinor Gallery. “Fuel your imagination and immerse yourself in a world of wonder in the spectacular interactive gallery, Wonderlab: The Equinor Gallery. Get hands-on with real scientific phenomena. Order live experiments at the Chemistry Bar, see live lightning demos at the giant Tesla coil, play with physical forces on giant slides or enjoy a drink under a canopy of stars as the world rotates at the giant interactive orrery!”

Recommended accommodation nearby

If you are traveling to London for Cyber Exchange 360: Talk to the Board, Pulse can recommend a variety of hotels within walking distance to the Science Museum.

The Rembrandt Hotel
www.sarova-rembrandthotel.com
11 Thurloe Pl, South Kensington, London SW7 2RS

Eden Plaza Kensington
www.edenplazakensington.co.uk
68-69 Queen’s Gate, South Kensington, London SW7 5JT

The Queen’s Gate Hotel
www.thequeensgatehotel.com
31-34 Queen’s Gate, South Kensington,

The Gore London – Starhotels Collezione
www.starhotelscollezione.com/en/our-hotels/the-gore-london/
190 Queen’s Gate, South Kensington, London SW7 5EX

Location

Science Museum
Exhibition Road, South Kensington, London SW7 2DD

Science Museum is located in South Kensington with beautiful surroundings and walking distance to some of London’s most famous landmarks such as Royal Albert Hall, Hyde Park, and Kensington Palace.

Directions

By underground
The nearest tube station is South Kensington. This is on the District and Circle lines and is a 5-minute walk from the museum. Gloucester Road tube station is also on the District, Circle and Piccadilly lines and is a 15-minute walk from the museum

By Bus

Bus routes 14, 49, 70, 74, 345, 360, 414, 430 and C1 stop outside South Kensington Underground Station.
Bus routes 9, 10, 52, 452 and 70 stop outside the Royal Albert Hall on Kensington Gore.

By car
The nearest pay and display car parking is in Prince Consort Road and Queen’s Gate. Royal Borough of Kensington and Chelsea have more information about parking near the museum.


2025-05-16-2

Photo Gallery & Video – 6th Cyber Exchange 360:
Talk to the Board 2024

Photo Gallery

54123342375_a517d6b24d_b


Highlights Video

Programme 2024 – 6th Cyber Exchange 360: Talk to the Board

2023 Downloads – 5th Cyber Exchange 360: Talk to the Board

2023 Post-Event Report2023 Brochure2023 Photos2023 Presentation Materials
2023 Video - Coming soon! 


Testimonials Talk to the Board 2024

“Great to be back at a Pulse event! We love this event, TTTB. It’s just so good to be able to network and interact with people and to have relaxed conversations, especially timing-wise towards the end of the year. People have gone through pressures and challenges and the good things that have happened. We can all collaborate and talk to each other. Interesting panel topics that fundamentally pinpoint where we’re heading in 2025!”
James Alliband, Head of Marketing, Risk Ledger

“This is my first time at a Pulse event. It’s been so fruitful and fantastic. I particularly enjoyed the 1-2-1 speed meetings. We covered a lot of ground in a short time. We’ve met some great new contacts, and I’d definitely come again.”
Holly Steele, Senior Vice President EMEA & UK, BlueVoyant

“It was a really interesting panel and great to meet people from across the cybersecurity profession and to hear their concerns and to help them to understand all the different issues that Boards need to deal with and where cybersecurity may rank in their list of priorities.”
Lorraine Heggessey, Former Controller, BBC 1

“Today has been invaluable to us as an organisation! Quest is sponsoring the drinks reception here tonight at Wonderlab. We had a great session in the roundtables and we really appreciate the opportunity to sponsor this event. What a venue in the Science Museum! We hope to be back here next year!”
Tom Etheridge, Head of Manufacturing and Resources UK&I, Quest Software

“Great opportunity to meet CISO peers to understand more about the issues that are effecting our industry and to talk to the vendors about the latest threats.”
Wayne Cook, Cyber Security Manager, Foxtons

Recent Testimonials

“The emerging consensus from Talk to the Board was how challenging it is for CISOs to present cyber risk to the board in an intelligible way for non-technical people. The challenge for the board is then to understand that and take action. Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. It’s great to have board and CISO side of the equation together at this event. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.”
Robert Hannigan, Chairman, BlueVoyant. Former Director, GCHQ

“I wanted to be part of the Cyber Exchange 360 and Talk to the Board event because I’ve always been so fascinated by technology, particularly what it brings on the dark side – the dark underbelly of technology being cyber attacks and the cyber risk. Being from the world of insurance, I was hoping to share some of my experience with assessing risk and managing risk because, fundamentally, this is what the CISOs are trying to do. I think they’re doing an amazing job, but cybercriminals are always faster and quicker than any of us, so we must stay alert. I’ve learnt about how lonely and vulnerable the CISO feels. I’ve been a CEO a few times and always felt the CEO took the can for everything. I thought then that people working lower in the organisation wouldn’t feel so vulnerable. But I was hearing that from some of the attendees, and as boards, we need to think about how we can be more of a support for them so that they don’t feel so lonely and perhaps under threat. If your world is looking at cyber risk and you’re a CISO, I would come to this event and get involved because you are sharing and gaining simultaneously.”
Dame Inga Beale, Former CEO, Lloyd’s of London

“The great thing about Pulse Conferences events is you get a different perspective from our core market. So it’s perfect for me to come here and get that completely different perspective and speak to people at the level that Pulse Conferences attract. Talk to the Board is interesting because the business dimension is the most important thing about cyber security. So, speaking to the board brings me that business dimension to cyber security. As a sponsor, we get so much value out of these events, not just from potential clients but for people to partner with, and we get different perspectives on what the market is and what other people are prioritising.”
Dr. Paul Kennedy, Chief Engineer – Cyber and CEMA, QinetiQ

“This is my second CISO Exchange 360 and Talk to the Board and, once more, it’s a great mix of enterprise professionals, security professionals and senior leaders. It’s always a good atmosphere; people get to ask questions in a setting they might not ordinarily have the chance. I’ve been coming to Pulse Conferences events for a few years now. I think the Pulse team run amazing events. They’re always covering relevant subjects, the audience gets involved, and the speakers are a good mix of generalists and specialists. It’s great to hear from board executives and have CISOs sit alongside them, asking questions. It’s a sort of reversal of the status quo.”
Jonathan Luff, Co-Founder, CyLon Ventures

“The theme of CISO Exchange 360 and Talk to the Board, for me, is absolutely spot on. We must bridge the gap between the IT community and the board members, because we’re all fighting against the same enemy. We have competitors in the business who steal our market share. We have competitors in cyber security who steal our intellectual property and money. And so a competitor is a competitor. Coming here and talking to the board and helping validate what resonates with them to help the IT community have their voice heard by the board members is very special and powerful. We have silos of silos in companies. But criminals don’t have silos. They don’t have borders or boundaries. So, to win the fight, we must come together and build coalitions of capability and bridge across the boundaries we live in so we can stop the enemy and kick them out of our networks and our organisations. This event is fantastic. It’s a great forum. It’s a great opportunity. Anytime you can connect to another individual on a human level, person to person, it’s powerful. Board members and IT people speak different languages. We must learn to communicate effectively to help make rational decisions within a context that matters. So this event, this forum, is exactly what I’m looking for.”
Michael Beaupre, Head of Cyber Security, Hays

“The session Talk to the Board was a rich discussion with two interesting themes emerging for myself. The primary ask from the Board is for them champion the importance of Cyber security and employee Cyber vigilance across the organisation as a cultural norm. To secure this commitment the audience noted the value of having a standing agenda item on the Board annual agenda. The panel also encouraged the audience to craft carefully any presentation to the Board to focus on what outcome they were asking for and to avoid just an information update. Both the audience and panel found the event very interesting and informative.”
Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc, Current Chairman Sustainability and Inclusion Practice, Kantar; Advisor Business, Transformation, McKinsey

“The afternoon discussion with the Board focused on a number of key themes, how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics.”
Deborah Exell, Former Board Member, Head of Human Capital & Business Transformation, Getronics

“I’ve had a few good sessions with various organisations. Looking at what’s going on across the industry and how organisations are doing things slightly differently has been very interesting. The need for greater collaboration is a key message. It is a fantastic event, and the venue at the Science Museum is the perfect size: I’ve had a breadth of conversations, but it’s small enough to have one-to-one discussions.”
Andrew Kelly, Principal Consultant, QinetiQ

“First class organisation and presentations. I would highly recommend Pulse conferences for those Senior Managers who need to get value from their time and attendance and for the quality of guest speakers.”
Ray Jackson, CISO, Telrock Systems Ltd

“It’s a great event with some high-calibre attendees, and the turnout has been impressive. The one-to-ones provide a superb opportunity to spend some focused time with key customers. And it was brilliant to have one of our teams hosting one for the roundtables around CISO practical tips. It’s a unique in that it is a closed community. You get more one-on-one time than you would do at another conference.”
Remco Postma, Sales Leader, SailPoint

“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

“The day has been great. I enjoyed a lot of good conversations. I’ve spent time with interesting companies and interesting people. Pulse always uses thrilling venues, and the Science Museum in London is special. What’s unique is that CISOs can talk to the board – they have opinions and they want to share them, and also listen to the guidance offered.”
Scott Daly, Commercial Manager, HUMAN

“The Talk to the Board session provided a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. By doing so, board members could be better served as CISOs educate and update them about evolving organizational cyber security risk exposures and vulnerabilities. More intriguing, perhaps, was that CISO’s were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”
Graham Joscelyne, Former Auditor General, World Bank and Chair: Audit and Ethics Committee, The Global Fund to Fight Aids, Tuberculosis and Malaria. Current Advisory Committee for Internal Oversight, United Nations (UNRWA)

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Julia Harris, Information Security Compliance and Assurance Director, Flight Centre UK

“It was a fantastic day. It is great to be back in London and meeting people again. Pulse events are always absolutely amazing. As usual it was such a diverse group of people from so many different departments – finance, manufacturing and so on – and they are all at a certain level where you start to understand strategy and where the industry is going in the UK. I probably learnt more than the people I spoke with, so it’s been brilliant.”
Paul Baird, UK Chief Technology Security Officer, Qualys

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Owanate Bestman, Owner, Bestman Solutions

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Deborah Saffer, Global Deputy CISO, Cushman & Wakefield

“I just wanted to say thank you again for another fantastic event. I had a very good time and lots of very useful conversations.”
Charles McAlpin, Qualys

“The agenda of Talk to the Board was a big pull. I’ve heard of Pulse Conferences, but this was my first CISO event. I saw the questions posed and the incredible line-up of people speaking, and I knew I had to be in the room. It’s so rare to have that opportunity to hear it directly from the CISOs and the board. So what more could you ask for if you’re up and reporting to boards and you need to communicate with them effectively? It’s a unique opportunity. What is important for them? For anyone thinking of coming to a Pulse Conferences event, just do it. Block out that time, make the commitment and realise that it’s an investment not only in your company and what your company needs from you but also in your professional development.”
Katherine Leivesley, Head of Legal, Offer and Sourcing, Kingfisher PLC

“As ever, an excellent opportunity to have time in front of executives who are likely to be very similar to the executives that all CISOs are likely to have to bring on side. It gave fascinating insights, and some I will certainly be using in the future.”
Julia Harris, Information Security Assurance and Compliance Director, Flight Centre Travel Ltd

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
Jonathan Armstrong, CEO, Cordery

“Insights & experience shared by Industry leaders will definitely help me & my organization in course correcting the strategy”
Manish Dave, Lafargeholcim

“Marvellous event, well-run, packed with useful content you can use”,
James Gosnold, Technology Services Head of Security, DWP


In Action

Testimonials – CISO 360 Global Congress

“It seemed like everything was perfectly set to ensure a smooth event gathering 100+ valued guests. Loved the energy, the talks, the stands and also the choice of networking activities!”
CISO, Engie (France)

“CISO 360 Global Congress is **the** congress for CISOs and senior cybersecurity practitioners to attend. The scope of topics presented is excellent!”
CISO, DPO and Director of the Internal Control Office, Comissao do Mercado de Valores Mobilia¡rios, Portugal

“CISO 360 is the perfect balance between working, socialising, and networking. So the appealing thing about coming here is you get to meet a load of people that you wouldn’t normally get in front of, so there’s some smaller vendors who if you Google certain area they’re probably not going to come up in the first page and you get to meet them and they get to tell you about their interesting new take on the technology, and you get to do it in a really nice setting, it’s a lovely hotel, the events that Pulse put on outside of the hotel are really good, where you get to socialise with people and after a couple of drinks they kind of tell you a bit more truthfully what their products can do which is really, really useful. And then you get to do the follow-on, the boring stuff where they take you through a slide deck in London afterwards, so you get to meet them properly first, and then learn about the bumph that they’ve got from their sales team afterwards so that’s really cool.”
Security Operations Manager, Right Move

“The CISO 360 Congress provided a unique platform to explore the delicate balance between innovation and practical implementation in cybersecurity. As a startup founder, I found the discussions on DevSecOps challenges and the evolving role of CISOs particularly enlightening. One key takeaway was the constant tension between designing for scale and the risk of over-engineering. In the startup world, we must be agile, forward-thinking, and grounded in current market needs. The debates around Generative AI highlighted this balance perfectly. These events are crucial for widening our horizons and engaging in insightful discussions with peers. They remind us that while pushing the boundaries of technology, we must always keep sight of the practical challenges security leaders face in their day-to-day operations. This blend of innovation and practicality will drive our industry forward.”
CTO and Co-Founder, JIT (Israel)

“As a newcomer to the cybersecurity event scene, CISO 360 was an eye-opener. I expected a highly technical environment but instead found a deeply human-centric experience. It revealed the true challenges and struggles that CISOs face daily. This insight is invaluable for someone in my role, as it helps bridge the gap between our products and the real-world needs of security leaders. The event’s structure, starting with a candid roundtable discussion, set the tone for the entire conference. It allowed us to view subsequent presentations and discussions through the lens of solving real problems.”
Regional Executive, KnowBe4 (The Netherlands)

“Great conference! From the beginning, the level of participant engagement was very high. The content was very informative and the presenters very knowledgeable. Every aspect of Global CISO 360 was extraordinarily well done. I left the event with a better understanding of cybersecurity and a broader network of industry contacts.”
Senior Director Security, Atlas Air (United States)

“Extremely insightful talks and a great way to connect with others in the industry that fostered genuine and open discussions”
Cyber and Geopolitical Risk lead, Sibylline (UK)

“Superb line-up of speakers and topics! The sequence of the ’roundtable’ at beginning, prior to ‘sitting down’ at the conference, was a very good ‘icebreaker’, socially, and this allowed us to get to know one another well. Content and organization made this an excellent event!”
CISO, Infopercept (UK)

“A great experience – I liked the fact that the Pulse team had the energy to support and make this such an experience – everyone was friendly and there to support when needed”
Senior Account Executive, Hack the Box (Greece)

“One of the biggest challenges in our industry is gaining access to open conversations with CISOs without prior introductions. Cold calling and traditional outreach methods often fall short. However, events like CISO 360 create an environment where everyone is approachable, solving this challenge elegantly. The casual atmosphere fosters open dialogue, allowing us to understand CISOs’ current challenges and how we can help. It’s not just about selling; it’s about building meaningful connections. These events provide a unique opportunity to engage in positive conversations and establish good relationships that lead to fruitful collaborations.”
GemServ, a Talan Group company (UK)

“As vendors, we’re often seen as just another salesperson despite our genuine desire to help improve the industry. Events like CISO 360 are invaluable for fostering connections. They open doors to future introductions, lunches, and even inclusion in specialised groups. These connections are the foundation of true industry collaboration. Interestingly, the most effective collaboration often happens off the record – in WhatsApp groups, over coffee, or during casual lunches. These spaces allow security professionals to share challenges without fear of oversharing or repercussions. To truly advance our industry, we need to encourage more of these human-to-human interactions.”
COO, Risk Ledger (UK)

“What I like about this CISO 360 conference is the peer interaction, the themes that we discuss here that are very relevant, the chance to speak openly in a way that you know that people will understand your problems and give you ideas. You can give something back and contribute to what could be the global outcome of the conference. It’s a sum of all the contributions, both people that do the presentations, the questions, the comments that we make. These things are all relevant, the speakers are well chosen, they are respected professionals on their fields, and the organisation is top, and the venue is always very beautiful place, everything is well organised so it’s highly recommended. Every time I attend CISO 360, I meet new people, there are faces that I see from year to year, some well-known. You see people from Asia, from America, from Europe, it’s mainly a European event but you see people coming from other continents, and it’s a very friendly modern atmosphere where people are at ease, everyone respects each other and we know that we can trust these people, we can share our problems, the questions we have, and there’s someone that went through the same thing and can give us an idea of what to do. I’m leaving with lots of new ideas for things that I want to implement and experiment, so that’s why I came, and that’s why people should come to these conferences, it’s great.”
Director of the Internal Control Office, Comissão do Mercado de Valores Mobiliários

“It’s been fantastic to see innovation and start-ups feature at CISO 360 for the first time. It’s good to see that the CISOs are genuinely interested and coming to talk to us. One of the big pluses of this event is that it’s not all jam packed into one day, and there isn’t that intense hard sell aspect that you typically see, which obviously puts people off. It’s been really good to take things more gently to get to know CISOs and vice versa.”
CTO, Quod Orbis

“One of the few must-not-miss events for every CISO. Wonderful opportunity to learn new things, and have in-depth discussions on what really matters, with real practitioners and industry legends (still alive).”
CISO & DPO, 360 Treasury Systems AG, Germany

“A very thoughtful event, great networking and industrial expertise in the room to learn from!”
Director, Security, Laureate International Universities Malaysia

“A meticulous and engaging event highlighting the key security concerns business leaders face today!”
Director, Bestman Solutions

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”
CMO, SailPoint

“Insights and experience shared by industry leaders will definitely help me and my organisation in course correcting the strategy”
Senior Cybersecurity, Lafarge Holcim

“Pulse always delivers the very best events so the fact that this event was impeccably organised wasn’t a surprise. But the fact they delivered such an excellent event at this time with the various rule changes and restrictions placed on them was truly surprising. The team showed great strength of character and the ability to innovate. It was a super event and fun too.”
CEO, Cordery

“Great venue, great speakers, well-chosen themes. Overall, one of the best cybersecurity conferences I ever attended.” –
CISO, DPO and Director of Internal Controls, Comissão do Mercado de Valores Mobiliários, Portugal

“Once you attend CISO 360, you become a part of the family. The socialising offered is the most important aspect. This community building through shared experiences makes it different from other conferences!”
CISO, Head of Information Security and Assurance Services ILO – United Nations, Switzerland

“It is hard to describe what an amazing experience it was to attend, in person, a conference after such a long time. From impeccable and reassuring preconference comms to a beautiful indoor and outdoor setting, excellent speakers and audience engagement, surprisingly unobtrusive vendors where productive conversations were held, without all the sales hype. It will certainly be a conference I will not forget and setting a standard with which, I will hold other conferences to.”
Global Deputy CISO, Cushman & Wakefield

“I’ve really enjoyed the conference, I’ve enjoyed meeting people, learning more about what’s top of mind for CISOs and in the cybersecurity space. The sessions have all been great. There is a great CISO 360 community, it’s very tightly knit – we talk to each other a lot, share a lot of experiences, and that’s fantastic.”
Chief Scientist and SVP of AI, Dataminr

“The people are amazing. CISO 360 gathers the best of the best – the organisations that came here, the speakers are fantastic, the vendors that we can speak to about the products are great. It’s really hard to say no to Sara, Clive and the team. I absolutely love them. The talks have been fantastic and piqued my interest. The most interesting contact has been about management, case studies, third-party risk, and AI. The camaraderie that is achieved through the social networking events is fantastic. We went out on the catamaran and, to be honest, I thought I was going to be sick, mainly because of the boat, but it was still so good. Afterwards the meal sponsored by Qualys was fantastic. These are the smallest things that Pulse do for individuals such as myself that they don’t need to do, but they go out of their way just to make us feel comfortable, especially in a new city as well I’ve never been to before, so massive thanks for that.”
VP Information Security EMEA, Northern Trust

“It’s probably one of the best conferences for cybersecurity professionals. We really get to exchange information with other professors and peers in this industry, we build trust among us in this inclusive environment. We can exchange not only challenges, but celebrate the successes as well. And I would come back any time. We build not only trust and become friends, but also become part of the family. For CISOs it’s one of the most important things. Everybody expects CISOs to be very technical, and we are, but I believe that being very good on the soft skills is vital as well, and building that network is one of the most important things because CISOs cannot work alone. It’s almost impossible that you will know every single answer, so the networking is probably the most important thing in our field to pick up the phone, to say: “Hey, are you having the same challenge, how are you doing things around these problems or issues?” It really does help, and it’s proven itself over and over again. I use the CISO 360 network and call people. Besides information sharing, besides the fact that we all have become friends and family here, I would say we also have great evening events, which is how we build a stronger connection. CISO 360 is the place to be. I recommend it to all of our professionals in cybersecurity.”
CISO European Investment Bank

“This is a very good event for meeting CISOs, security professionals, and the vendors to learn more about what is going on, their challenges, and how to deal with them. This event has a number of really amazing speakers. Some of them have been in this industry for a long, long, long time, they have a broad variety of experiences, they share these experiences and they are still today trying to learn the next thing. There are three big benefits to attending CISO 360. The networking is one. You need to be able to share what you know and learn from others. The content from the stage is a second one, obviously, and the third one is the social aspect. We have a boat trip and wine tasting. Work is fine, but you also need to be personal, you need to bring those connections in because you never know when you need to pick up that phone and say: “Hey, I have this issue, I don’t know who to discuss it with, but I trust you.”
CEO and Founder, Praxis Security

“Thank you for the excellent event and seamless organisation! It was my first time at the CISO 360 and the event was highly inspiring with great networking opportunities.”
Senior Consultant, DHC AG (Switzerland)

“We’ve been with Pulse and the CISO 360 since it started, and it’s been an amazing journey and we’ve created this community and this family, we see new faces, the same faces. And one of the issues we have in our industry is the lack of communication, the lack of talking, so these events are bringing people, bringing our peers out to have those talks, it’s great for vendors, it’s great for the community. If another vendor is thinking about joining this community do it. There is a fantastic community. We get to talk between the vendors as well, meet new people, see old friends, and how they are progressing through the industry as well – they may have moved, gone to new roles, new jobs, new organisations, and it’s great to see them transitioning. So we learn an awful lot as well as the customers do from learning from what we have as a vendor. We talk about diversity an awful lot in this industry and I think Pulse has managed to grab that with its agenda and its itinerary, there is something for everybody throughout the two days, through the day and through the evening as well and I think that’s one of the reasons why it captures such a wide range of audience, it’s because we are talking about so many different topics that are burning, these are topics that customers and vendors are having internally, so Pulse is giving you the opportunity to bring them out and allow people to talk about them.”
CTO UK, Qualys

“It’s a really cool event, a lot of CISOs come to these events and it’s quite a small little community where they all do a lot of learning and a lot of conversations. As a start-up, CISO 360 is a great way to meet people and build relationships within the industry. As a start-up, we don’t have the marketing budgets of big companies, so for us relationships are really important, we need to build trust with the CISOs, they need to trust us before using our products, and that was a really great way to come to an event like this, meet CISOs, teach them a bit about what we’re doing and what we’re trying to achieve with our mission and then from there hopefully get a few using the product. Gather feedback on our products has been really good for two reasons, firstly we’ve got a lot of constructive feedback on what we’re doing, what we’re trying to achieve, and actually new ways which we can achieve that, and secondly we’ve got a lot of people who are willing to try the product and actually join the trial and get using it. It’s a very well organised event with really friendly people. It’s always a great venue as well – they rotate it around different cities and it’s always nice to come to a different part of the world and meet people in a setting that’s not London.”
CEO, Risk Ledger

“I keep coming back to CISO 360, because I learn so much. There is such a breadth of information, people from right across all sorts of industries, and organisational titles. The breadth of the agenda is just amazing, and it’s really fascinating, and so I keep coming back because I want more. I’ve learned so much in the last couple of days about all sorts of different topics, from the really scary from Dr. Sally Leivesley’s presentation to areas about recruiting people, and what makes up a good team, and data governance. There is such a plethora of information, it’s impossible to do without CISO 360, so I come back for more – and I’ll be back next year. I think the atmosphere in this group is really open, it’s very friendly, they’re very welcoming. We like people, we talk to people, and nobody was left alone at the networking events. It’s a very inclusive group, and we welcome new people coming along because we want new experiences, we want to talk to new people. The really good thing about this group is that you can come along and have a really easy conversation about information security, cybersecurity, anything to do with security because this is a really knowledgeable audience, and it makes it easy and it’s very relaxed, you don’t have to fight anybody, everybody understands. It’s simply great.”
Head of Information Security, Quilter

“It was a wonderful event. So good to start to be able to talk to people face to face and to be able to think outside of the “day-to-day responsibilities” box again.”
Information Security Manager – Awareness and Behavioural Change, Metro Bank plc, United Kingdom

“What a week! Such a lovely venue, lovely city, and a fantastic collective of like-minded professionals. This was my first Annual CISO Congress, but not my first Pulse event, and Pulse did not fail to deliver their exceptional services once again. Sara and the team did a wonderful job, and pulled everything off brilliantly.”
Threat and Vulnerability Consultant, Computacenter, United Kingdom

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way. The Pulse Conferences team puts this together from the heart.”
CISO, HARIBO (Germany)

“Where else can you find a higher quality of security leaders all in one place?”
Director, Bestman Solutions

“Probably the one must-attend conference of the year. Excellent speakers, fast-moving pace, differing methods of delivery, just simply the best value usage of my time.”
Information Security Compliance and Assurance Director, Flight Centre UK

“Amazing opportunity to share experiences and to learn in a very nice environment, CISO 360 is a great experience. You meet interesting people and you can learn a lot about cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
Europe Industries- Security Officer, Air Liquide GMS (France)

“Absolutely excellent! The quality of the presentations, and the ideas shared, were first class. Looking forward to implementing what we learned.”
Director, Resilient World

“I found CISO360 2019 extremely valuable for several reasons, primarily networking with industry peers comparing our challenges and successes stories, hearing thought provoking and inspiring content during the conference itself and also hearing updates from vendors and solution providers on their latest capability additions and developments. A very worthwhile investment of my time and I hope the conference continues to grow.”
Technology Services Head of Cyber Security, DWP (UK)

“Pulse Conferences delivered a really enjoyable, informative and immersive experience with the CISO 360 Congress. The virtual platforms were excellent, providing an effective substitute for an in-person experience. The speakers and panel sessions were engaging and knowledgeable and the avatars round-table was both informative and fun.”
Peter Wood, Naturally Cyber LLP

“Excellent conference”
Barbara Aung, CISO, Telefonica

“This was great, we have a lot of good take away’s and loved the lessons learned!”
Sybil Kleinmichel, 360 Treasury Systems AG

“It was great to watch live interviews rather than recorded presentations. The roundtable session on Friday was particularly interesting”
CMO, Vectra

“If you want to hear real CISO experiences, you must attend this event!”
CISO, ST Engineering, Singapore

“The team always do a great job of providing excellent content, great networking, valuable introductions and useful sponsors. The must attend event for a senior information security leader.” CISO, Euromoney Institutional Investor PLC

“This was our first but definitely not our last CISO360! A well planned and executed event with a clear goal of providing tangible value for the participants in combination with a great community feel sure makes it a stand-out event to return to.”
CMO, NetClean

“The best cybersecurity event that I have ever attended. I look forward to seeing you next year!”
Senior Manager, Cybersecurity, EY Singapore

“CISO 360: guaranteed insight and inspiration. A triumph thanks to the Pulse team!”
Chief Privacy Officer, Nokia Group

“Pulse delivers some of the most informative and worthwhile events. Their topics, speakers and ability to engage at the highest level to secure attendance means that you are constantly engaged and come away learning something new and meeting new contacts.”
CMO, SailPoint

“By far the best event all year that I have attended. I always makes an effort to attend CISO 360 as it is not just an event, it is a trusted community that comes together from around the world!”
Group CISO and Group DPO, MS Amlin

“Team Pulse put together a fantastically well organised and thoroughly enjoyable event this year in Rome. The CISO 360 Pulse Conference was most informative, engaging and gave us a great opportunity for learning, networking and relationship building. Looking forward to the next one.”
CMO, Synack

“ Thank you Pulse for the smooth organisation of this huge logistical challenge. My team told me it worked brilliantly and that the networking was one of the most valuable parts of being a sponsor.”
CMO, Telstra

“Excellent event Pulse Conferences, we very much enjoyed the opportunity to meet new contacts in both a professional and social capacity. We also had a large number of new members to ClubCISO, an added bonus…. ”
Supporting Organisation, ClubCISO

“A unique opportunity to share challenges thoughts and ideas with trusted friends, and gain valuable insights.”,
President, (ISC)2 Scotland Chapter

“CISO 360 is a must attend conference to keep up to the latest trends, best practices as well as main security concerns within the cybersecurity landscape”
GRC Specialist, Euronext

“I would like to extend my appreciation having been given the chance to witness the success of your recent event. I look forward to a further outstanding line-up of events from your organisation!”
CISO, GOPA International Energy (Abu Dhabi)

“Excellent event, opportunity to meet likeminded professionals, sharing risk, worries, tools, best practises with CISO from other industries sharing same issues, great eye opener, looking forward to the next event”
CISO, MS Amlin

“Nowhere else will you find such relevant content for CISO’s, shared by leaders in their fields”,
Director Security Engineering, Inmarsat

“A very engaging, varied and interactive event. The best conference I have ever attended!”
Information Security Manager, Lloyd’s of London

“The conference was full of expert speakers. You wouldn’t want to miss any of them. Particularly on the Boardroom/ Roundtable discussion (last day), it is like a strategic planning and facing the board of directors, but with less pressure. Excellent!”
Section Head – Planning & IT Security, Western Region Municipality – UAE Government

“Pulse have raised the bar when it comes to planning and running conference events. Other organisers should take note.”
CISO, Channel 4

“An excellent event in beautiful Rome! I had an amazing time socially and professionally… made so many great connections!. ”
Director Sales, Sailpoint

“The best speaker line-up of any security conference in Europe!”
Head of UK Security, AXA

CISO 360 Congress created a strong platform for peer review, cross pollination of idea and networking.”
CISO, Gebauer & Griller

“CISO 360 is a great experience. You meet interesting people and you can learn a lot about Cyber (risk, security, threats) and share experience and knowledge with top professionals. For me it has been a great experience and pleasure to attend the CISO 360.”
CSO, Logista Portugal

“Pulse Conferences stand out for being up to the minute with developments and concerns. First rate speakers and an agenda that is total appropriate and informative. Excellent buzz and networking.”
Lady Olga Maitland, CEO Copenhagen Compliance; Founder, Defence and Security Forum

“Thank you, Pulse Conferences, for a great event. CISO 360 combined interesting varied talks with fantastic networking opportunities, facilitating very interesting thought-provoking conversations”
Dr Jessica Baker, Co-Founder, Cygenta (USA)

“Pulse organised a fantastic CISO 360 Congress in Barcelona, which brought together some of the world’s most successful CISOs to discuss pressing cyber security issues and share experiences. The agenda was diverse, with senior professionals from across the globe sharing their experiences, and great networking sessions were facilitated by the organisers with good food and flowing conversation. I would highly recommend CISO 360 and look forward to this conference going from strength to strength”
Freaky Clown, Co-Founder, Cygenta (USA)

“Excellent conference, brilliantly put together.”
Director, Bridewell

“Interesting exchange of insights and experiences from different companies, sectors, and levels of maturity. An honour to have been there.”
Head of Information Security, Risk Management and Quality, Almirall

“Great speakers, great venue, intelligent discourse, Pulse CISO 360 Congress has it all!”
Director of Information Security EMEA, Canon Europe (UK)

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”
Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

“I’m very pleased to be part of this extraordinary event – very important to exchange ideas and hear experiences and ideas from peers across sectors!”
Corporate Security Manager, Logista (Portugal)

“Marvellous event, well-run, packed with useful content you can use”,
Technology Services Head of Security, DWP

“The CISO 360 conference brought together a collection world leading experienced security leaders who shared their knowledge and experience with their peers in an open and collaborative manner under The Chatham House Rule. This was complimented with case studies from selected top tier partners and organisations to provoke further debate and discussion during the talks or later during one to one networking conversations. The presentations; case studies; and strategy sessions were practical and relevant because they were born out real world security challenges faced by Global CISOs across multiple sectors. I found the open knowledge sharing; networking; and presentations were very valuable to either validate existing approaches or provoke fresh ideas by getting a different perspective.”
Global Head of Information Security Architecture & Transformation, Royal Bank of Scotland

“I found CISO 360 Congress a great place to share ideas about current and future problems”
Head of Section, GMV (Spain)

“Refreshing views of security topics for knowledge improvement!”
CISO, Bank Credibom (Portugal)

“Top class speeches and presentations at the CISO 360 Congress in Barcelona! Thanks for such a worthful and enjoyable time”
CMO, Blueliv