CISO 360 · CO-LOCATED WITH THE 2ND CSO 360 MIDDLE EAST

7th CISO 360 Middle East

Security and Resilience as Business Enablers: Protecting People, Assets, Information and Operations in a Changing Middle East

Cross-security leadership from Türkiye, the Gulf, the Middle East and EMEA, in one room.

DATES10–11 November 2026
VENUEInterContinental Istanbul, Türkiye
CO-LOCATED WITH2nd CSO 360 Middle East

Gulf, Türkiye and the wider EMEA field, in one room

The 7th CISO 360 Middle East brings together Chief Information Security Officers and cybersecurity leaders from across the Gulf, Türkiye and the wider EMEA field for two days of strategic discussion. Share proven strategies and benchmark security roadmaps with fellow CISOs, resilience experts and technology risk leaders.

With thanks to our 2026 sponsors (partial list)

Platinum Protectors
Illumio

CISO 360 Innovators

Intel 471

Supporting Organisations

ISC2 Türkiye Chartering Chapter

Information Security Forum (ISF)

Why attend?

Strategic insights

See how leading CISOs are advancing their security strategies and shaping cybersecurity in the region.

Diverse learning formats

Case studies, transformation journeys, technical deep-dives, fireside chats and interactive roundtables designed for peer-to-peer learning.

Trusted peer benchmarking

Learn from practitioners facing similar challenges, and connect with peers managing comparable risks under The Chatham House Rule.

Collective defence

Work together on organisational resilience and strong cybersecurity governance against evolving threats.

Innovation and inspiration

Leave with fresh perspectives, practical insights and connections to drive your security agenda forward.

Two events, one location

The 7th CISO 360 Middle East runs alongside the 2nd CSO 360 Middle East at the InterContinental Istanbul. Delegates move freely between the two programmes.

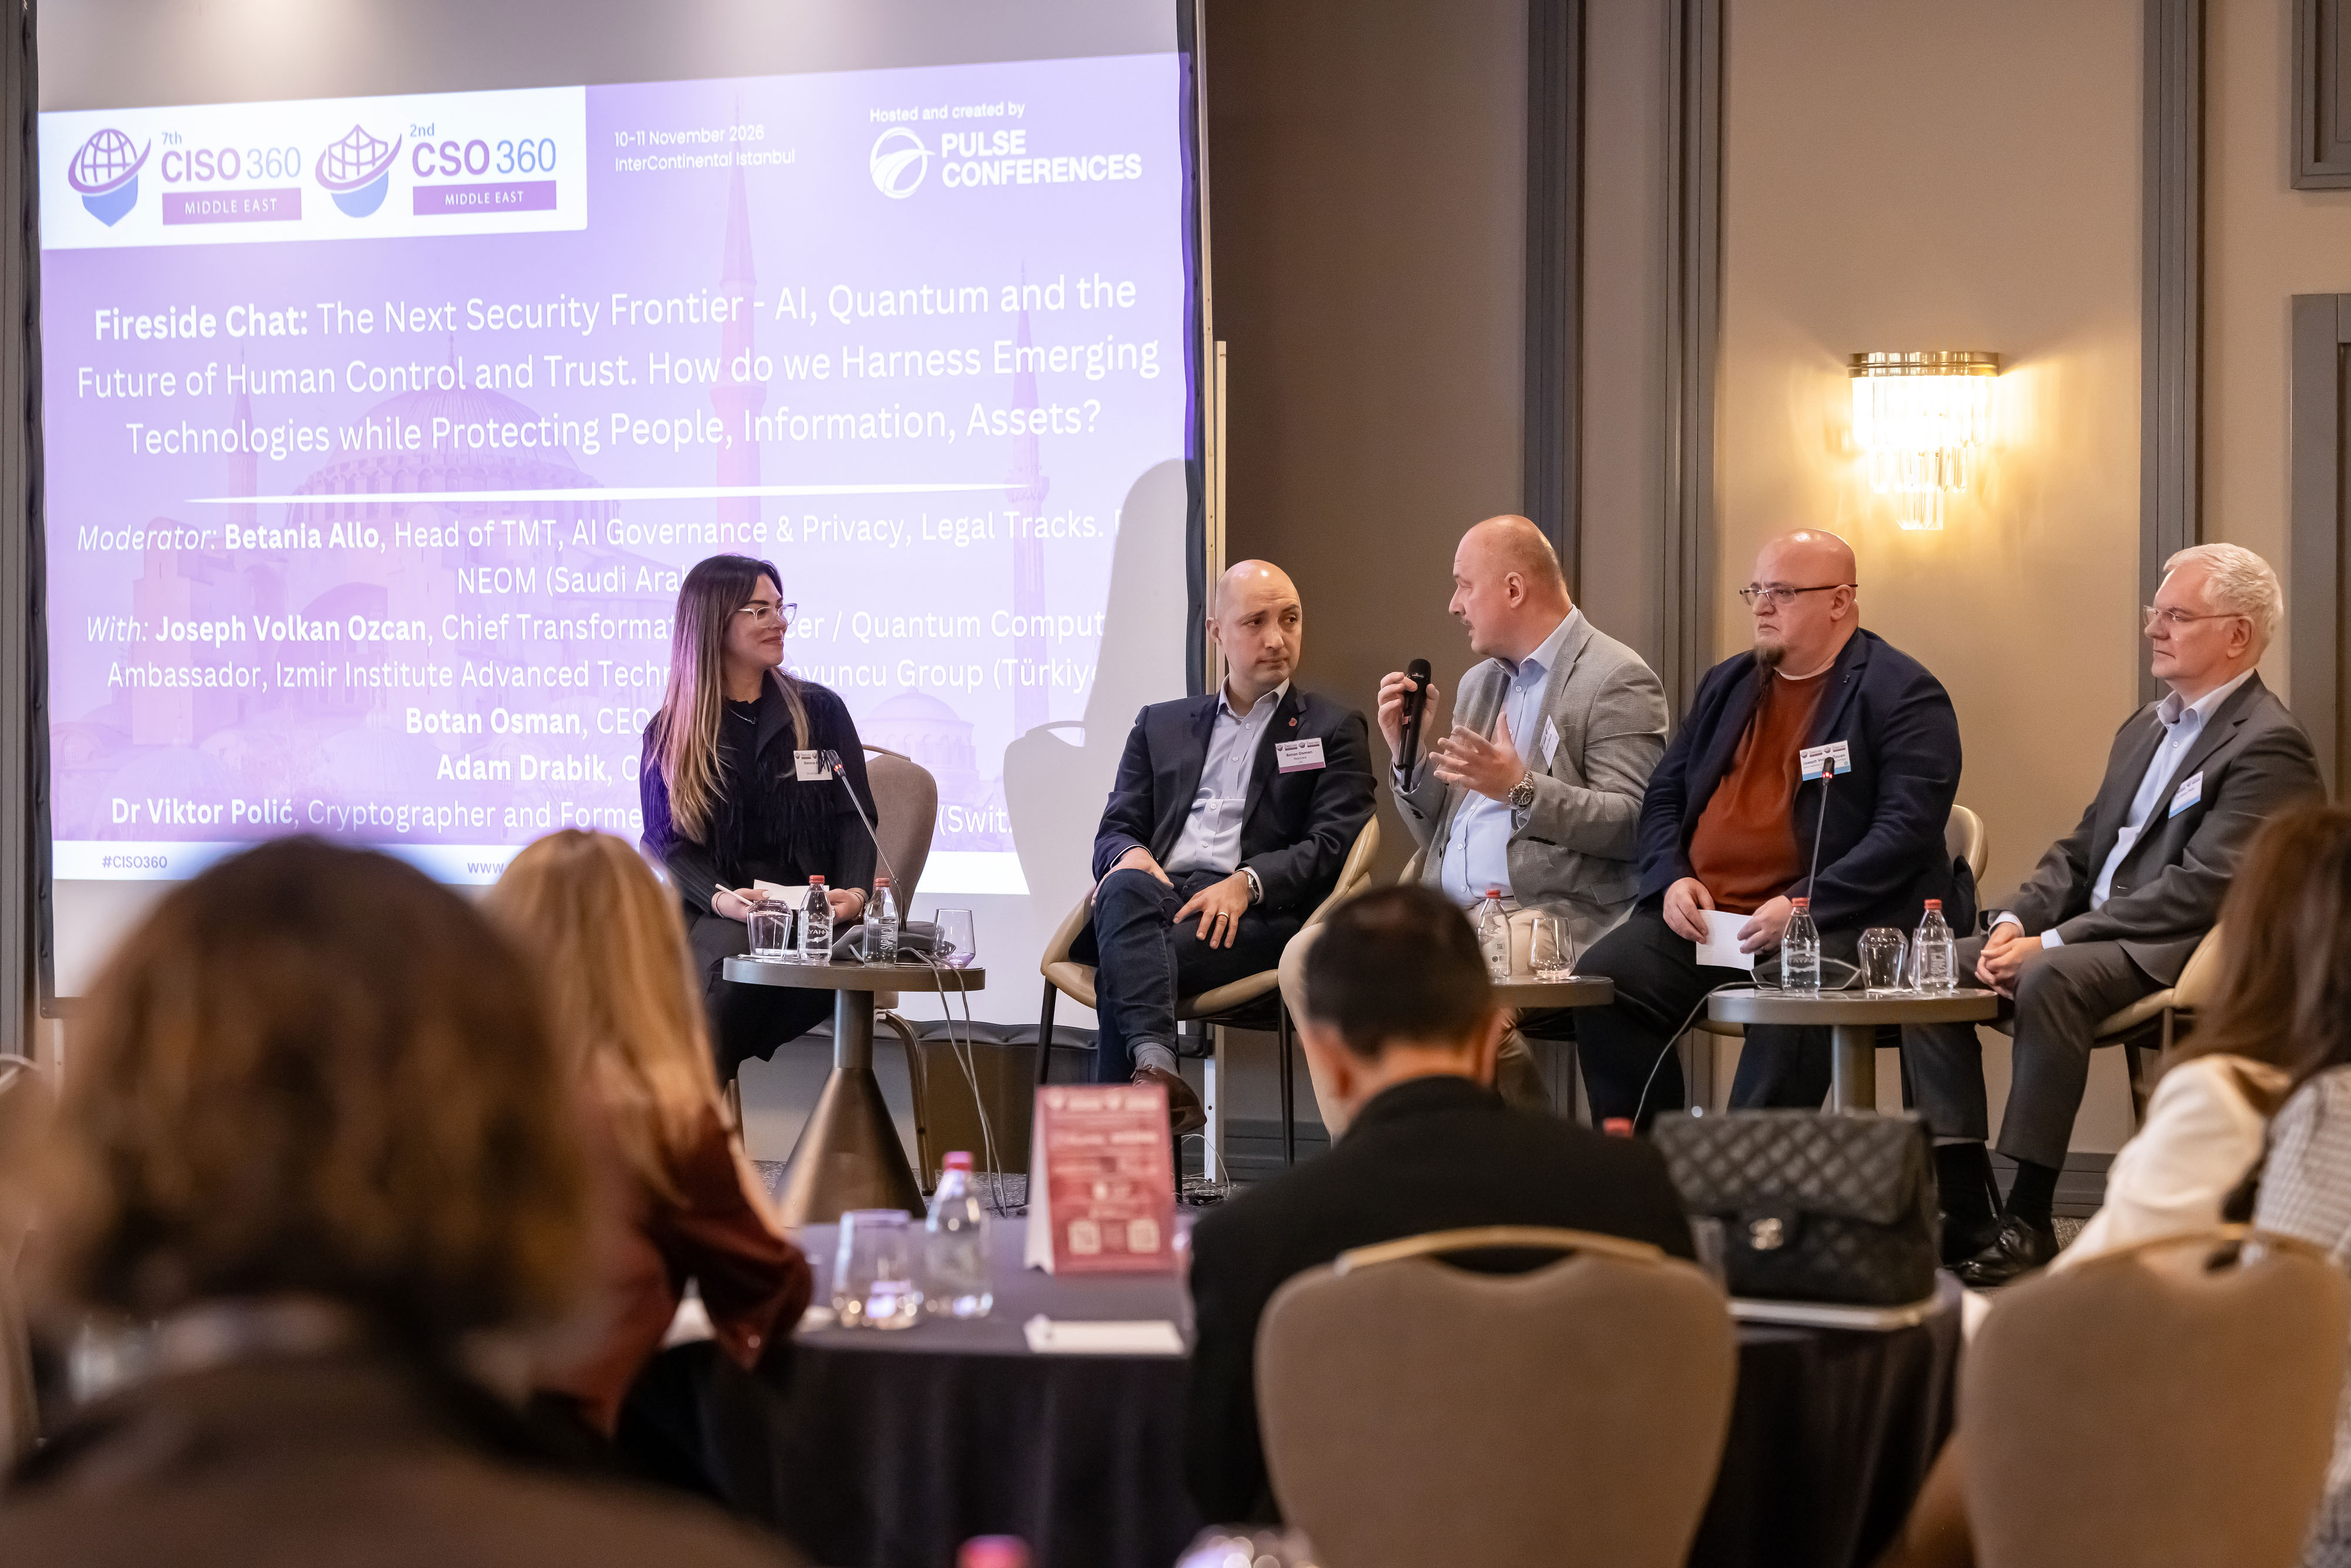
Highlights from our recent Middle East event

Many thanks to our enabling Anchor Partners: Mastercard, Dataminr, Sibylline, Restrata, Reliance Cyber, Qualys, Emergent Risk International, ThreatLocker, Intel 471

Programme 2026

The programme is still in development and speakers are being added, so timings may change.

The event at a glance

  • Monday 9 NovemberEvening networking
  • Tuesday 10 NovemberFull-day conference and roundtables, followed by evening networking
  • Wednesday 11 NovemberMorning roundtables, lunch and networking

Recent programmes

To suggest a topic or speaker, email teampulse@pulseconferences.com.

2026 speakers (partial list)

The 2026 programme is in development. If you would like to speak, or would like to suggest companies, topics or people for the agenda, email sara.hook@pulseconferences.com.

Sultan Altukhaim

Sultan Altukhaim

Head of Security and Compliance (CISO), Google Cloud KSA; Board Risk Committee Member, Tasheel Finance (Saudi Arabia)

Sultan Altukhaim has more than 20 years’ experience in data governance and cybersecurity. He is Cloud CISO at Google Cloud KSA and serves on board risk committees including American Express Saudi Arabia, Arab National Bank and Tasheel Finance. He was previously General Manager of Cybersecurity and Data Governance at the Communications, Space and Technology Commission (CST), and CISO at the Saudi Investment Bank. He holds master’s degrees from Florida Tech and King Saud University and is a graduate of the MISK 2030 Leaders Program.
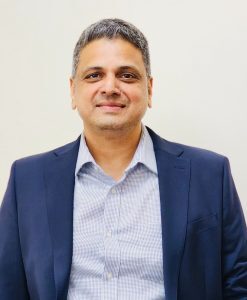
Anoop Kumar

Anoop Kumar

Head of Information Security and GRC, Gulf News Al Nisr Publishing (UAE)

Anoop has more than 25 years’ experience across IT, specialising in information security, cybersecurity, governance, risk and compliance, and business continuity. At Gulf News he established and leads the cybersecurity department, developed the cybersecurity strategy following a major incident, and manages incident response. He has provided strategic security leadership to organisations in the UAE and Qatar.
Dr Viktor Polic

Dr Viktor Polic

CISO, ILO – United Nations (Switzerland)

Viktor has more than two decades of experience in information management and governance, focusing on information security, risk management and assurance for large multilateral public-sector organisations. He contributes to inter-organisational working groups on security policy and standards, researches cryptography and data protection regulation, and teaches computer science at Webster University in Geneva.
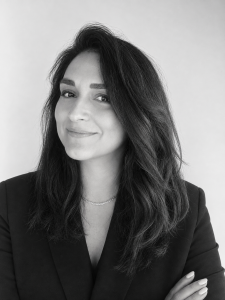
Asimina Basdani

Asimina Basdani

CISO, Head of Information Security Office, IDIKA S.M.S.A. (Greece)

Asimina is CISO and Head of the Information Security Office at the Greek E-Government Center for Health and Social Security (IDIKA), leading cybersecurity across critical national digital infrastructure. She began her career at IDIKA as a network security engineer and holds two master’s degrees. In 2026 she was a finalist for Cybersecurity Woman of the Year, Cybersecurity Woman of the World, and the Women in Cybersecurity Leadership Award at the CISO Awards in Barcelona.
Adam Drabik

Adam Drabik

CISO, Manufacturing (UK)

Gökhan Polat

Gökhan Polat

Director of Strategic Partnerships and Business Development, Defy; Member, ISACA Global Emerging Technologies Advisory Group (Türkiye)

A global contributor to ISACA’s COBIT 7 and AAISM frameworks and an accredited ISACA trainer holding CISM, CISSP, CISA and AAIR credentials, Gökhan brings over 20 years of technology risk management experience, specialising in establishing cybersecurity governance structures across the financial ecosystem. He addresses the governance, machine identity and control requirements of autonomous AI in security operations.
Betania Allo

Betania Allo

Head of TMT, AI Governance & Privacy, Legal Tracks. Ex-NEOM (Saudi Arabia) 

Betania designs and deploys AI governance infrastructure for governments, sovereign entities and regulated enterprises, from policy to operating model to enforcement mechanism. Her work sits at the intersection of AI law, regulatory technology and sovereign AI strategy.

She developed the Intelligent Control Stack™ (ICS), a five-layer governance framework applied across GCC jurisdictions to make AI systems accountable, auditable and regulatable at scale. She delivered Saudi Arabia’s first CAIO-as-a-Service retainer model, advising PDPL- and NCA-regulated organisations on AI risk architecture, and advises UNODC on AI-enabled transnational crime policy across the GCC, where governance gaps carry operational consequences.

She publishes and speaks internationally on AI governance, sovereign AI and agentic policy, including in Security Middle East and Arab News, and at LEAP, Black Hat MEA, WEF-affiliated forums and multilateral UN platforms. She also hosts The Control Plane, a weekly LinkedIn Live applying the ICS framework across domains.

Lawyer; D.Eng. in Cybersecurity Analytics Engineering (candidate), GWU; Master in International Relations, Harvard; LLM in Cyber Law, Syracuse; Postgraduate in Cybersecurity and Compliance, Universitat Internacional de Catalunya.
Joseph Volkan Özcan

Joseph Volkan Özcan

İzmir Institute of Technology (İzmir Yüksek Teknoloji Enstitüsü – İYTE) (Türkiye)

Joseph Volkan Özcan is a senior consultant and doctoral candidate who advises organisations through Quantum Task Force (QTF) / Quantum Strategy Advisory. With more than 25 years of international experience across 45+ countries, he helps banking, aviation, automotive, energy and manufacturing clients in Türkiye, Central Asia, MENA and Southeast Asia navigate quantum computing strategy and enterprise AI adoption.

His earlier leadership roles at Unilever, Indra Sistemas, Kaessbohrer and Maxion Wheels, together with deep SAP programme management expertise, ground his advice in operational reality. He is an ISO 27001 Internal Auditor and Lean Six Sigma Green Belt, and he teaches applied quantum machine learning with Qiskit on the Miuul platform. He holds an Industrial Engineering degree from Istanbul Technical University and a Master’s in International Quality Management from Marmara University. He is completing his PhD at Sakarya University.
Mohamed Amr

Mohamed Amr

Senior Sales Engineer, Illumio (UAE)

Mohamed Amr is an experienced Security Consultant with a strong track record in the information security space. He specialises in introducing innovative, best-of-breed technologies to help organisations meet their compliance and cybersecurity challenges. Mohamed brings cross-industry expertise and a pragmatic approach to building secure, scalable ecosystems.
Philip Jacobs

Philip Jacobs

Distinguished Intelligence Solutions Strategist, Intel 471
Simon Scales

Simon Scales

Conference Chair; Chief Education and Development Officer, Association of Corporate Investigators

Simon has more than 30 years’ investigative, security and compliance experience from corporate and law enforcement backgrounds. He has conducted complex bribery, corruption, fraud and misconduct investigations worldwide, and has led investigation, ethics, compliance and integrity teams in Europe, the USA, Africa and the Middle East.
Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum (UK)

Lady Olga Maitland has wide experience in governance, risk management and compliance, and in global fraud and corruption issues in particular. She advises a number of dignitaries and speaks widely on corporate governance. She is a former British MP and was previously a reporter and columnist in London.
Patrick Kane

Patrick Kane

Senior Director Security, Atlas Air (US)

Patrick leads security for Atlas Air, a US airline operating cargo and passenger services worldwide, with a focus on protecting a highly mobile global workforce through travel risk assessment, secure transport and journey management. He is President of the Corporate Executive Protection Leadership Council, led the creation of a Travel Risk Working Group within ASIS International, and is Chair Emeritus of the OSAC Aviation Security Working Group. He has worked on the ground in more than 70 countries and served as an infantry officer in the US Marine Corps.
Ned Farmer

Ned Farmer

Senior Strategic Intelligence Analyst, Emergent Risk International (US)

Ned manages a globally dispersed strategic intelligence team embedded with a major technology company. He previously led global intelligence for Transocean, designed the geopolitical risk and security intelligence programme at American Airlines, and held leadership positions within the US State Department’s Overseas Security Advisory Council (OSAC).
Mark Wolsey

Mark Wolsey

CEO, Convergent Risk (UK)

Mark served for 25 years as an officer in the Royal Marines, much of it in counter-terrorist operations and intelligence. He has since been Chief Security Officer at Smiths Group, Cadbury, Philip Morris International, PwC and CRH, and has been directly involved in responding to many of the major global crises of recent decades. He has worked extensively in Ukraine since 2014 on crisis and evacuation planning.
Botan Osman

Botan Osman

CEO and Co-Founder, Restrata (UK)

Botan Osman has 20+ years’ experience in the software & security sector. He co-founded the Restrata software venture in 2019. He was previously a government and multinational advisor and exec on technology working on projects with Microsoft, Google, IBM, PwC, Cisco & others.
Milena Maneva

Milena Maneva

Head of BC & Resilience, BGC Group & Cantor Fitzgerald (UK)

Milena is a recognised thought leader in resilience with over 16 years of experience across financial services, brokerage, law, and real estate. Her expertise spans business continuity, crisis management, risk governance, and enterprise resilience. Passionate about unlocking potential, she champions preparedness, adaptability, and collaboration to build resilient organisations and leaders.

Currently she serves as the Head of Business Continuity and Resilience, EMEA at BGC Group/Cantor Fitzgerald, Founder of ResilienceArc, and Chair of Institute of Strategic Risk Management (ISRM) London. Milena also serves as a board advisor and awards judge, and is an active member of ISACA, ISRM, SASIG, BCI and the Virtue Community at The Hacking Games.
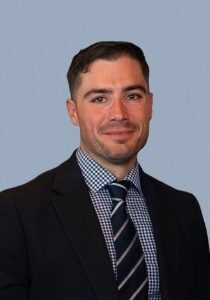
James Sarner

James Sarner

Managing Director, JMS Risk Solutions; Founder, CrossRisk (UK)

James Sarner is the Founder and Managing Director of JMS Risk Solutions, drawing on two decades of operational and strategic leadership experience in security, risk, and resilience. He has held senior in-house leadership roles and advisory positions across national and international organisations, including global technology companies, major hotel groups, large-scale hospitality operations, and complex supply chain environments.

Having built and led enterprise security, risk, and resilience capabilities within highly dynamic, fast-moving organisations, James brings a practical understanding of how businesses navigate operational complexity, organisational change, and uncertainty. He helps leaders make informed decisions by transforming complex and fragmented risk information into clear, actionable insight that supports commercial objectives and sustainable business performance.

James holds an MBA in Risk and Resilience, is a Certified Protection Professional (CPP), and a BSI-certified Lead Implementer of ISO 27001 and ISO 22301. As a registered consultant and full member of the Association of Security Consultants (ASC), he is recognised for his integrity, discretion, and commitment to delivering pragmatic, commercially focused advice to the highest professional standards.

Networking

Two social events are included, and all participants are very welcome. We hope you can join. Both are shared with the co-located 2nd CSO 360 Middle East.

Welcome Reception

  • WhenMonday 9 November, 7pm–9pm
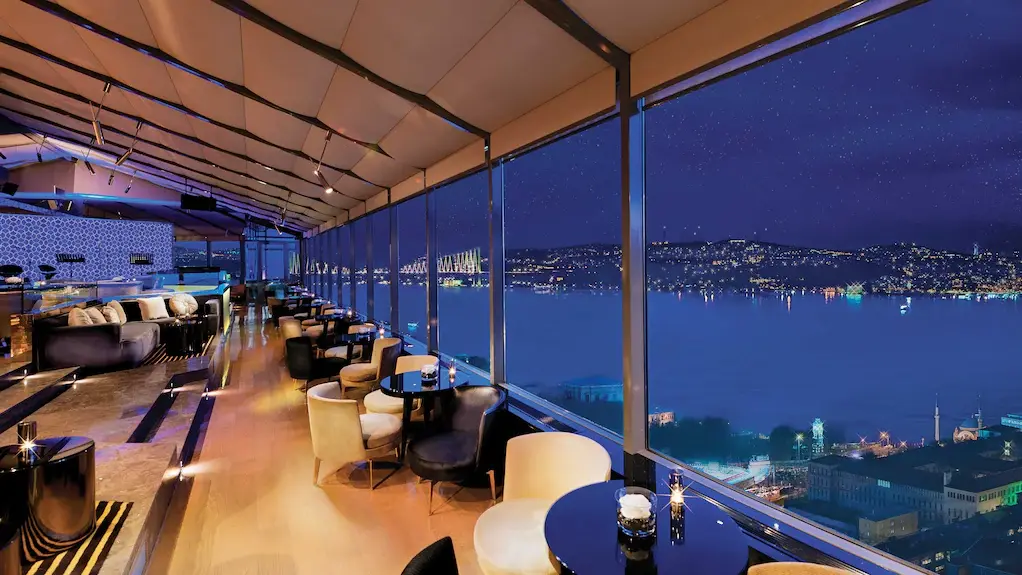
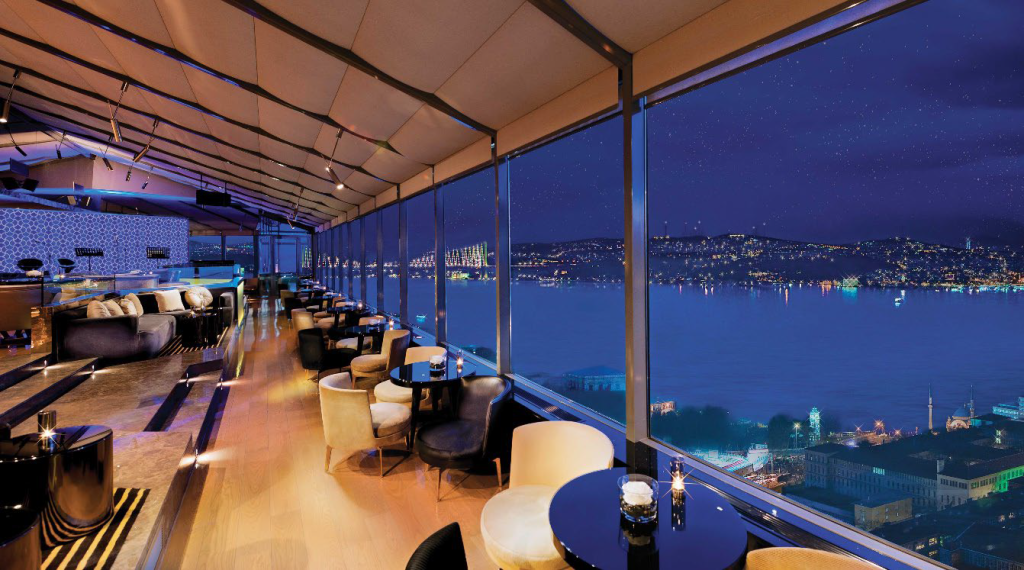
  • WhereCity Lights Bar, top floor, InterContinental Istanbul, Gümüşsuyu Mah. Asker Ocağı Cad. No:1, Taksim 34435, İstanbul

City Lights Bar, InterContinental Istanbul

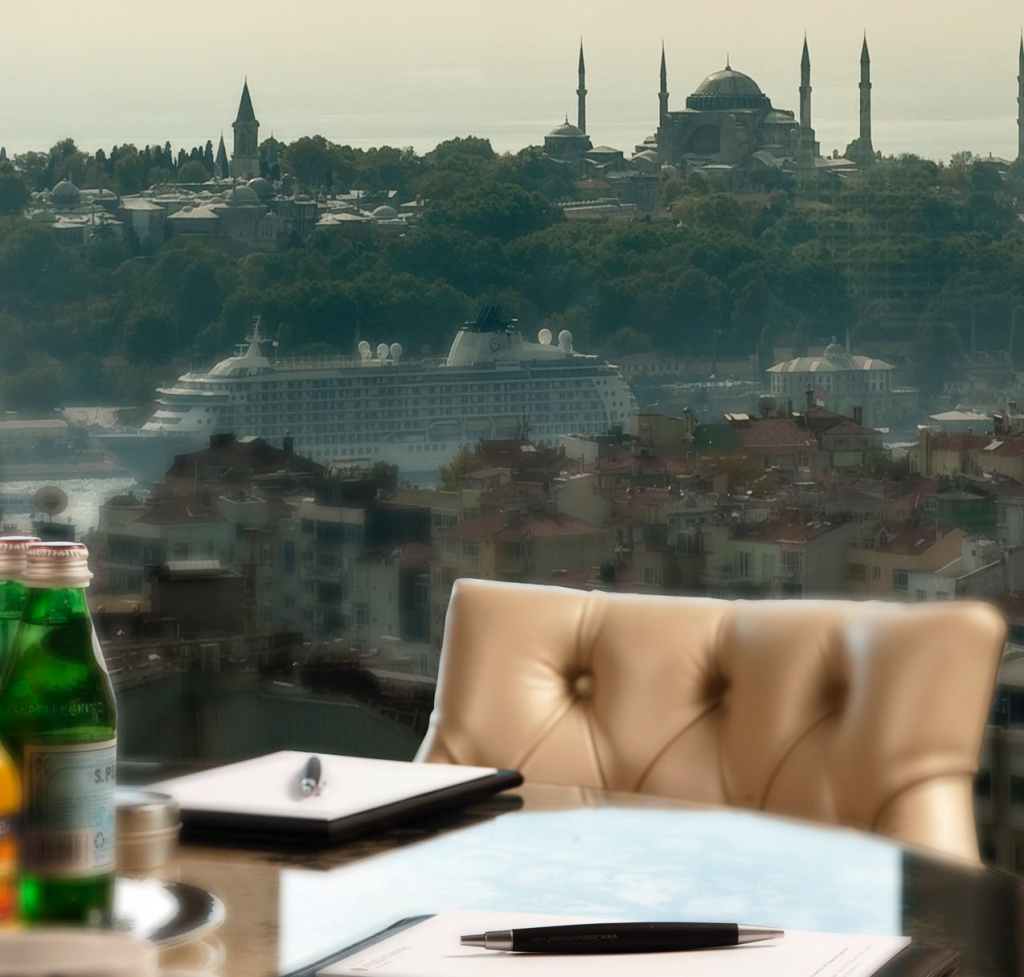
Kick off the event informally with panoramic Bosphorus and city views.

Networking Dinner
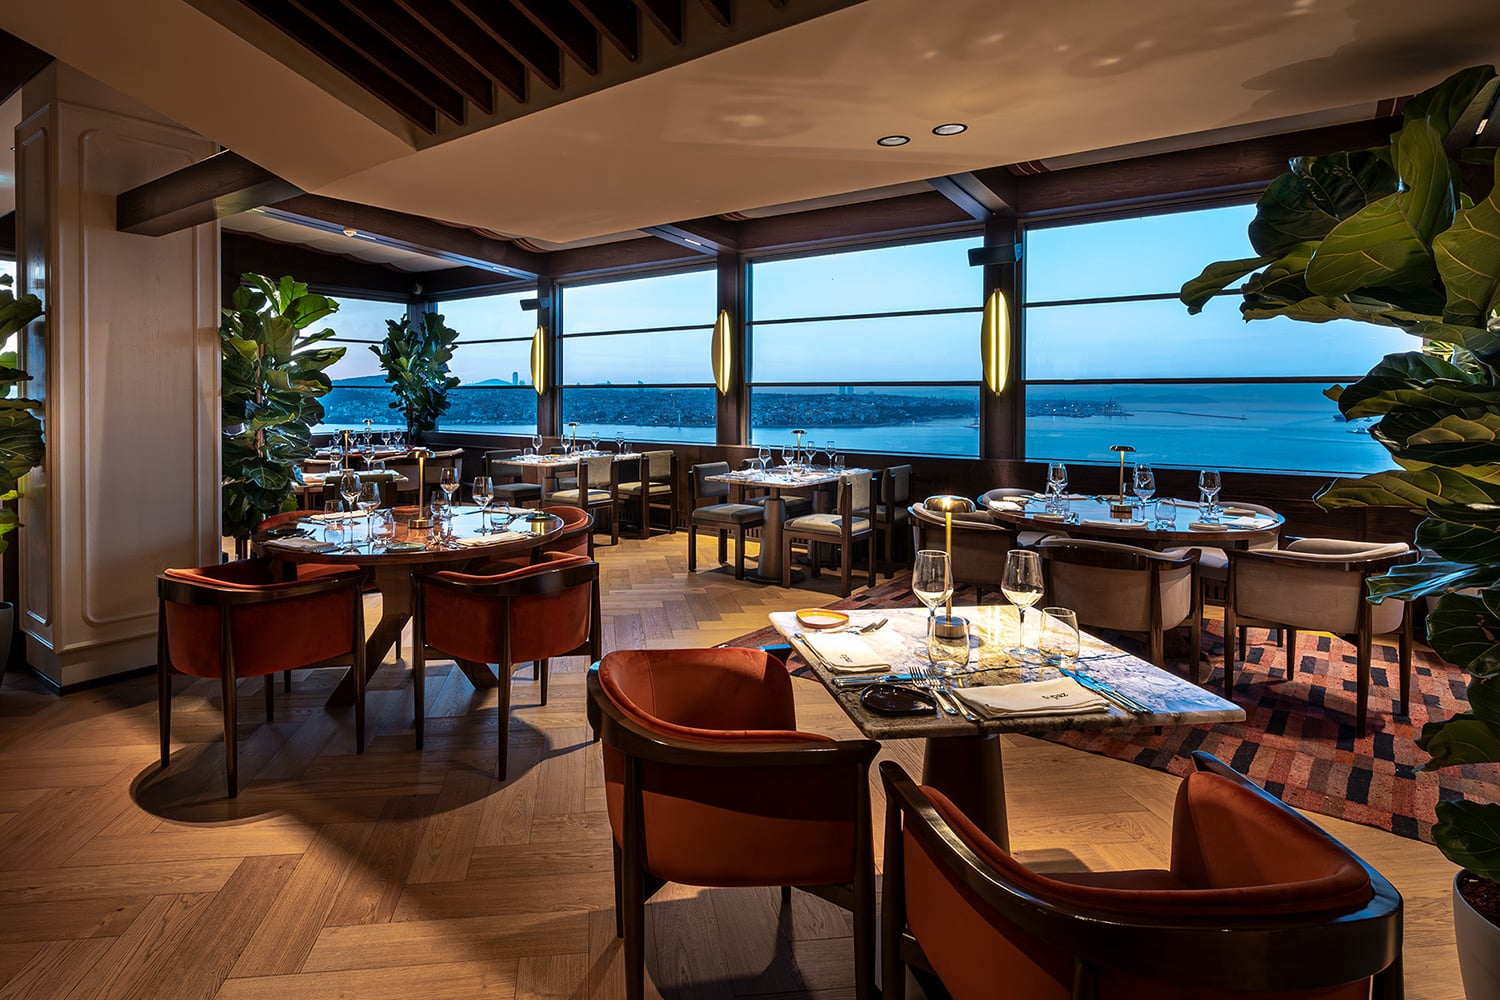
  • WhenTuesday 10 November, 6pm–10.30pm
  • WhereTOPAZ Istanbul, Ömer Avni, İnönü Cd. No:42, 34437 Beyoğlu/İstanbul

TOPAZ Istanbul

An evening of exceptional dining and iconic Bosphorus views.

Interested in hosting a social event next time? Email sponsorship@pulseconferences.com.

Many thanks to the sponsors of the 7th CISO 360 Middle East 2026

Partial list. To find out about sponsorship or to book a meeting with us, contact sponsorship@pulseconferences.com.

Platinum Protectors

Illumio

Illumio

Illumio is the leader in ransomware and breach containment, redefining how organisations contain cyberattacks and enable operational resilience. Powered by the Illumio AI Security Graph, its breach containment platform identifies and contains threats across hybrid multi-cloud environments, stopping the spread of attacks before they become disasters.

Recognised as a Leader in the Forrester Wave™ for Microsegmentation, Illumio enables Zero Trust, strengthening cyber resilience for the infrastructure, systems and organisations that keep the world running.

www.illumio.com

CISO 360 Innovators

QCC Global

QCC Global

QCC Global was founded in 1999 and is the world’s largest and most advanced TSCM services, bug sweeping, TSCM equipment and training, digital forensics and mobile phone forensics company. It holds the largest commercially held arsenal of TSCM equipment and more TSCM engineers than any other provider, all holding current commercial and government vetting.

QCC Global is respected for its pro bono academic and technology contributions to the counter-surveillance, cyber forensics and information security sectors. Its mission: “Keeping your business, your business”.

www.qccglobal.com

Intel 471

Intel 471

Intel 471 equips enterprises and government agencies with intelligence-driven security offerings powered by real-time insights into cyber adversaries, threat patterns and potential attacks relevant to their operations. By integrating human-sourced intelligence with advanced automation and curation, its platform helps teams prioritise controls and detections based on real-time cyber threats, across Cyber Threat Exposure, Cyber Threat Intelligence and Cyber Threat Hunting.

www.intel471.com

Supporting Organisations

ISC2 Türkiye Chartering Chapter

ISC2 Türkiye Chartering Chapter

The ISC2 Türkiye Chartering Chapter is a non-profit professional community initiative dedicated to advancing the cybersecurity discipline across Türkiye under the global standards of ISC2. Currently in its official chartering phase, the chapter serves as a local hub for cybersecurity leaders, practitioners and aspiring professionals to collaborate, share knowledge and strengthen the region’s digital resilience.

Core objectives

  • Professional growth and certification: supporting members through career mentorship, study groups and guidance on achieving and maintaining credentials such as CISSP, CCSP and CC.
  • Knowledge exchange: hosting technical workshops, webinars, panel discussions and research sharing on emerging cybersecurity trends, threats and governance.
  • Community and networking: connecting cybersecurity professionals across government, corporate, academic and independent sectors in Türkiye.
  • Industry awareness: promoting good practice in cybersecurity, privacy and digital trust for organisations and communities throughout the region.
Information Security Forum (ISF)

Information Security Forum (ISF)

Founded in 1989, the Information Security Forum (ISF) is an independent organisation driven by its Members, ranging from Fortune 500 and Forbes 2000 listed corporations to public-sector bodies and government departments.

Its business-driven solutions provide organisations with the guidance, tools and methodologies needed to tackle the wide-ranging governance, risk and compliance challenges facing businesses around the world.
securityforum.org

Why sponsor the 7th CISO 360 Middle East?

The 7th CISO 360 Middle East convenes the people accountable for protecting the enterprise: cybersecurity, information security, networks, applications, infrastructure, cloud, AI security, security operations, cyber threat intelligence, business continuity and anti-fraud, and the executives and board members they report to. Delegates come from Türkiye, the GCC, the Middle East, EMEA and MENA, with strong attendance from Türkiye and the Gulf. The agenda is shaped by the priorities registrants rank when they book.

As a sponsor, you will engage with:

  • CISOs, information security and cybersecurity directors overseeing operational protection and threat intelligence
  • C-suite leaders driving governance frameworks, regulatory alignment and cyber risk tied to business impact
  • Board Directors and NEDs influencing capital allocation and governance decisions

For sponsors, this means direct access to budget holders and buyers in one room; high-trust, senior conversations across the event in addition to the one-to-one meeting programme; and an international delegate base weighted to Türkiye, the Gulf, the Middle East, EMEA and MENA.

94%of recent sponsors would recommend
96%would return

Sponsor feedback, CISO 360 + CSO 360

What sponsorship includes

Meetings arranged for you, end to end

We schedule your one-to-one meetings before you arrive, matched on mutual relevance and selection. Your team arrives with a diary rather than a stand to staff. We regularly deliver 250–270% of the meetings contracted.

Your own event, without running your own event

A curated space, your chosen theme and session type, inside an event already full of the people you want in the room: the depth of a hosted event without the cost, lead time or risk of filling it yourself.

Bring your clients with you

Complimentary places for your existing customers and prospects. They attend as invited guests, in the sessions and at the evening dinners, receptions and cultural activities.

In the room, not waiting outside for the breaks

Networking dinners and cultural visits are part of the event, not an add-on for sponsors. Your team sits among the delegates throughout, learning alongside them in the main conference room.

A two-way conversation about your offering

Our CISOs and CSOs join these events to think aloud about problems they have not solved. Under The Chatham House Rule they will tell you where your category is falling short.

Worked through with you, start to finish

We agree the content, messaging and practicalities with you from signature to onsite delivery and post-event follow-up. You input on theme and delegate profile; we handle everything else.

What we don’t sell

Delegate lists, agenda control and pitching slots are not available at any price. That is why our delegates come back, and why your presence among them carries weight.

What recent sponsors say on camera

What our sponsors say

“The key take-away of CISO 360 is the calibre of the individuals who attend. I’ve done these events over many years and I’m incredibly impressed with the team. I’ve had conversations with people who have budget, make decisions and who want to know about cybersecurity technologies that Mastercard cyber intelligence has.”

John Quinn, EMEA Strategic Alliances Director, Mastercard

“Pulse creates a unique environment for us to interact with the senior leadership team in our customer base and to prospect around new clients. Because of the unique environment people are much more open to talking and discussing issues.”

Matt Middleton-Leal, Managing Director EMEA North, Qualys

“With normal events that we attend, it’s fleeting and you only get moments with your colleagues. CISO 360 gives you the time and bandwidth to go deep into topics and subject areas.”

Torquil Macleod, Director, Via Resource

“First and foremost, you know what you’re going to get with Pulse: the quality of delegate is always high. The agenda is very relevant. A thoroughly successful event for us!”

Dan Panesar, Director UK and Ireland, Securonix

“This is our first time at a Pulse CISO 360 event. Great to get together and we’ve had very effective quality meetings. Great content with workshops and breakout sessions.”

Richard Fridge, Regional Sales Manager, HUMAN

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a one-to-one basis is invaluable. The evening activities really helped build trust and relationships.”

Director, SailPoint

Who attends

Designations

  • Chief Information Security Officer / Head of Information Security
  • Director Cybersecurity / Cyber Threat Intelligence
  • Director Security / Security Operations
  • Director Monitoring / Response
  • Chief Operations Officer / Director Operational Risk
  • Director Security Planning / Risk / Innovation
  • Director Fraud / Payments
  • CIO / Director ICT / IT Governance
  • Chief Risk Officer / Compliance
  • Chief IT Auditor / Head of IT Audit
  • Group Business Director and Senior In-house Counsel

Industries

  • Aerospace and defence
  • Automotive
  • Banking
  • Central, regional and local government
  • CERTs
  • Construction
  • Consumer goods
  • Energy and utilities
  • Healthcare and pharmaceutical
  • Industrial engineering
  • Insurance
  • Internet and software
  • Legal
  • Manufacturing
  • Media
  • National law enforcement
  • Real estate and business conglomerates
  • Regulators
  • Retail
  • Telecommunications
  • Transport and shipping
  • Travel, leisure and hospitality

Venue

InterContinental Istanbul
Gümüşsuyu, Asker Ocağı Cd. No:1
34435 Beyoğlu, İstanbul, Türkiye

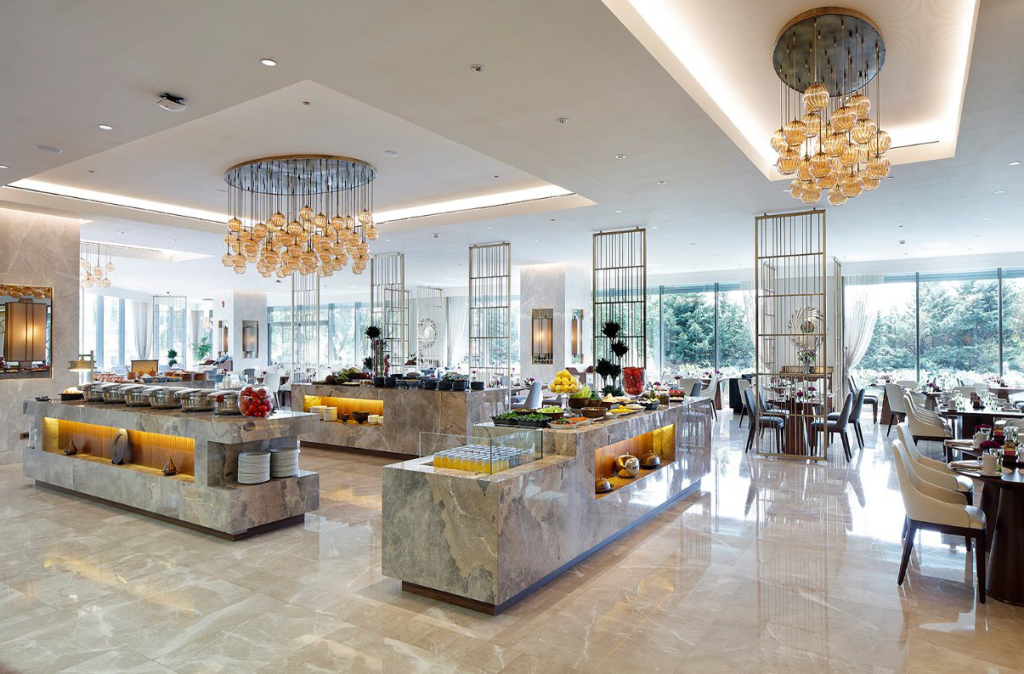
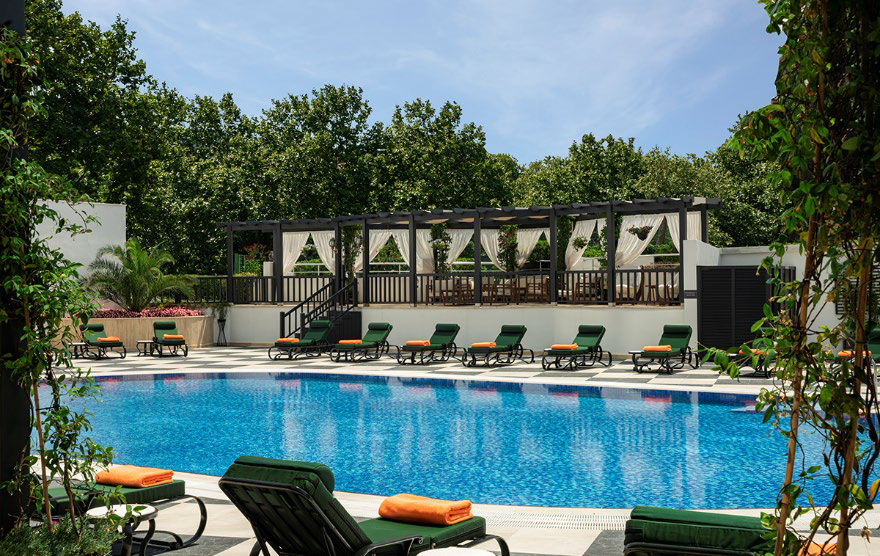
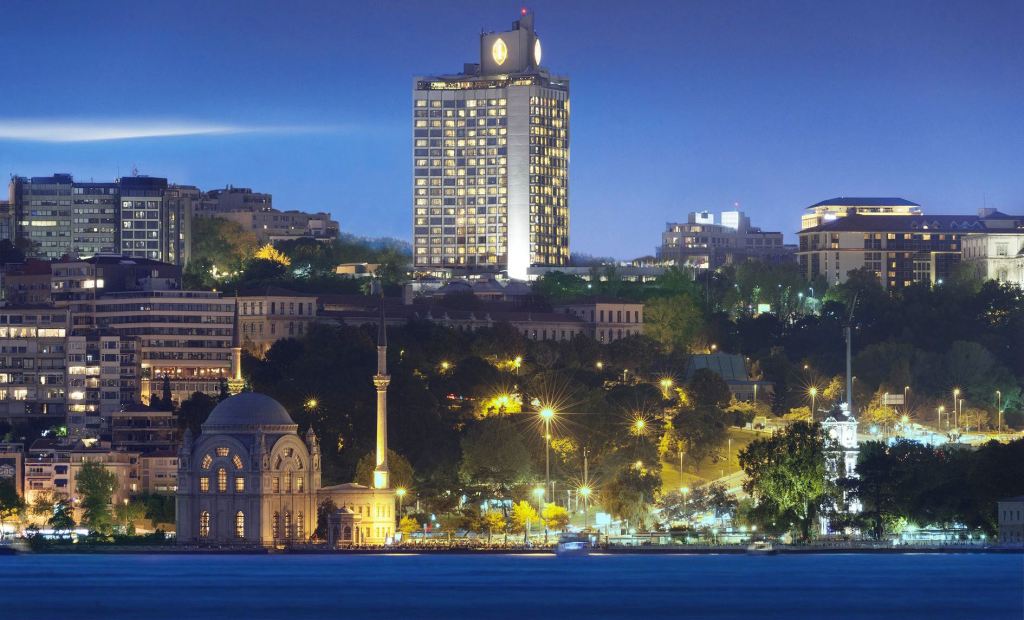
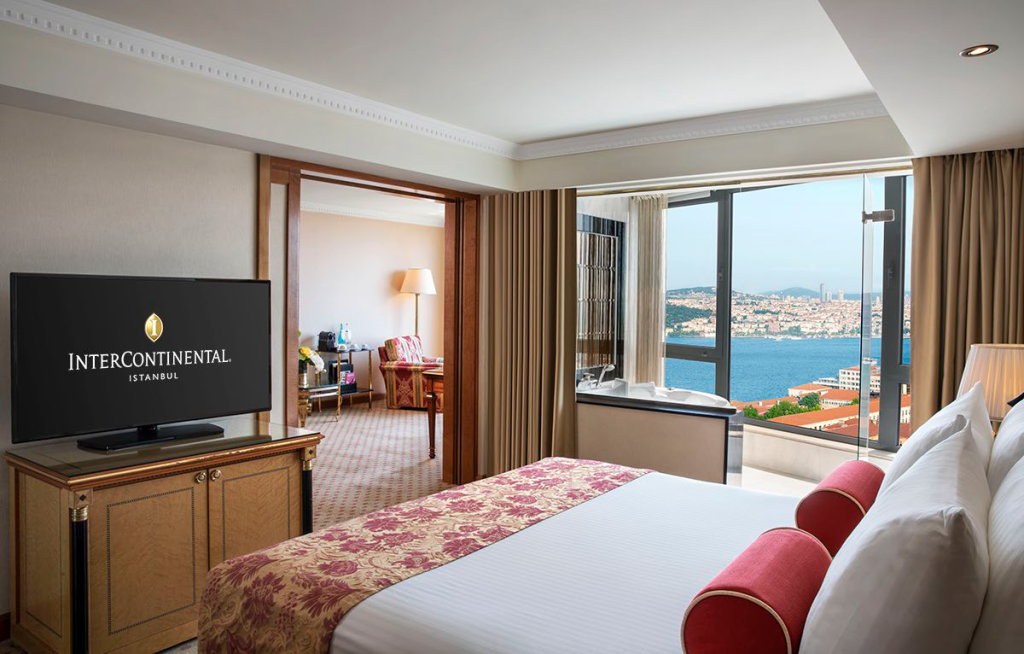
The 7th CISO 360 and 2nd CSO 360 Middle East 2026 are hosted at the InterContinental Istanbul, a five-star high-rise hotel in the Taksim district with views over the Bosphorus and the historic skyline. The hotel has a top-floor City Lights bar, Turkish and international dining, and a spa with an outdoor heated pool and Turkish baths.

Hotel website · View on Google Maps

Discounted accommodation

Pulse Conferences has arranged a discounted bed-and-breakfast rate of EUR 160 (£137.29) per room, per night, for one person. Taxes may apply. Book by 31 October 2026.

The hotel

InterContinental Istanbul

Views over the Bosphorus

Guest room

Suite

Spa and pool

City Lights bar

City Lights bar

City Lights bar

Dining

The event spaces

Event space

Event space

Event space

Event space

Getting there

  • From Istanbul Airport: about 35 minutes by taxi.
  • Metro: Taksim station is directly behind the hotel, about two minutes’ walk.
  • Nearby: Taksim Square is within walking distance; Nişantaşı is a 15-minute walk.
  • Parking: 200 indoor spaces. Self-parking EUR 11.80, plus EUR 5 for valet.

Registration 2026

Pulse Conferences reserves the right to approve that registration is under the correct tier.

Tier 1 Delegate Pass

In-house security practitioners

£495

For in-house practitioners: people doing the role of CISO, CIO, CTO, CSO, cyber threat intelligence professional, risk manager or other in-house executive roles. This rate does not apply to people or companies providing advisory services or solutions to the security community.

Inclusions

  • Entry to the 7th CISO 360 Middle East conference and roundtables (10 November, full day) and roundtables (11 November: morning, lunch and networking)
  • Invitation to all networking activities (9, 10 and 11 November)
  • Access to the co-located 2nd CSO 360 Middle East sessions
  • Post-event presentation materials (subject to speaker opt-out)
  • Certificate of attendance on request. Up to 11 CPE/CPD credits towards (ISC)² (CISSP), ISACA (CISM, CISA, CRISC), EC-Council (CEH), ASIS International (CPP, PSP, PCI) and The Security Institute (CSyP, MSyI, FSyI)
  • Automatic invitation to the Security 360 Circle (monthly virtual roundtables)

Exclusions

  • Travel, accommodation and all other costs of joining the event

Register

Tier 2 Networking Pass

For providers and advisers

£1,995 + applicable tax

A limited number of Networking Passes for senior executives at provider, vendor or distributor companies, or independent advisers to the security community, to benefit from the business development and learning opportunities of attending.

Inclusions

  • Entry to the 7th CISO 360 Middle East conference and roundtables (10 November, full day) and roundtables (11 November: morning, lunch and networking)
  • Invitation to all networking activities (9, 10 and 11 November)
  • Access to the co-located 2nd CSO 360 Middle East sessions
  • Post-event presentation materials (subject to speaker opt-out)
  • Certificate of attendance on request. Up to 11 CPE/CPD credits towards (ISC)² (CISSP), ISACA (CISM, CISA, CRISC), EC-Council (CEH), ASIS International (CPP, PSP, PCI) and The Security Institute (CSyP, MSyI, FSyI)
  • Automatic invitation to the Security 360 Circle (monthly virtual roundtables)

Exclusions

  • Travel, accommodation and all other costs of joining the event

Register

Tier 3 Speakers, Sponsors and Supporting Associations

Pre-confirmed with the Pulse team

By arrangement

If your participation has already been confirmed with the Pulse team, register here.

Register

Terms and conditions

Payment policy

Payment is due in full at the time of registration. Your registration will not be confirmed until payment is received and may be subject to cancellation. Early-bird and other discounts require payment at the time of registration and before any cut-off date, and cannot be combined with other offers.

Credit card: all major cards are accepted online; card details are not accepted by email, phone or fax. Bank transfer: please reference the invoice number and email a copy of the remittance to teampulse@pulseconferences.com. All bank charges are borne by the sender.

Cancellation, postponement and substitution

You may substitute a delegate at any time by notifying Pulse Conferences. No credit will be issued for cancellations within seven days of the event (inclusive); only a valid doctor’s note entitles you to a 100% credit for another Pulse event within one year. Cancellations received in writing at least eight days before the event receive a 90% credit for another Pulse event within one year. Cancellations received in writing at least 60 days before the event receive a 100% credit, or a 90% refund if you cannot attend another event. A 10% administration fee is retained on all permitted cancellations.

If Pulse Conferences postpones or cancels an event, you will receive a 100% credit, or a 100% refund if you cannot use it. Pulse Conferences may alter the advertised speakers or topics if necessary; changes will be published on the website.

Code of conduct

Pulse is dedicated to providing an inclusive and harassment-free experience for everyone. We do not tolerate harassment of our community in any form. Participants violating these rules may be sanctioned or expelled from current or future events without credit or refund. Please raise any concerns with the team at teampulse@pulseconferences.com.

Health and safety, force majeure and indemnity

Events are organised in line with the latest health and safety regulations and guidance of the host country. Pulse Conferences may virtualise the programme, postpone or relocate the event if delayed by circumstances outside its reasonable control. We advise booking flexible or refundable travel and accommodation. Pulse Conferences is not liable for any claim, loss, damage or cost arising from attendee participation.

Use of multimedia and privacy

Pulse Conferences may photograph and film the event and use the footage for promotional purposes. If you prefer not to be included, tell us in writing before the event or at the registration desk and you will be given a distinctive badge. Read the Pulse Conferences privacy policy for how we handle your data.

Video testimonials

Interviews filmed at recent CISO 360 events.

What delegates say

“Very informative and experienced speakers from all different capabilities and sectors, which made the forum extremely worthwhile. Our connections in the region were built rapidly and our pipeline as a direct result will get larger.”

John Quinn, EMEA Director, Global Cyber Security Partnerships, Mastercard Cyber and Intelligence

“Once you attend CISO 360, you become a part of the family. This community building through shared experiences makes it different from other conferences!”

Viktor Polic, CISO, ILO – United Nations

“Very professional speakers, panels are to the point and we discuss what the industry needs now.”

Joseph Makram, CIO, EAL Bank

“Great networking and learning from various cyber gurus!”

Sajjad Ahmad, Director of Security, DP World

“You brought the world’s cyber concern to the UAE for awareness and also brought world experts to provide advice based on their own experience!”

Head of Planning and IT Security, Al Dhafra Region Municipality (UAE)

“The company and the thought-provoking sessions over the course of the conference have been fantastic. It has made me think about cyber risks and resilience in a different way.”

Matthias Muhlert, CISO, HARIBO