CISO 360 + CSO 360

9th Talk to the Board: CISO + CSO 360

Security Talks Business to Board Directors: Balancing Innovation, Trust and Resilience

The only truly 360° on-stage exchange where CISOs and Chief Security Officers engage openly with CEOs and Board Directors.

DATEWednesday 3 November 2027
VENUELondon (venue to be announced)

Save the date: 3 November 2027

The 9th Talk to the Board: CISO + CSO 360 takes place on Wednesday 3 November 2027 in London. The venue and programme will be announced shortly.

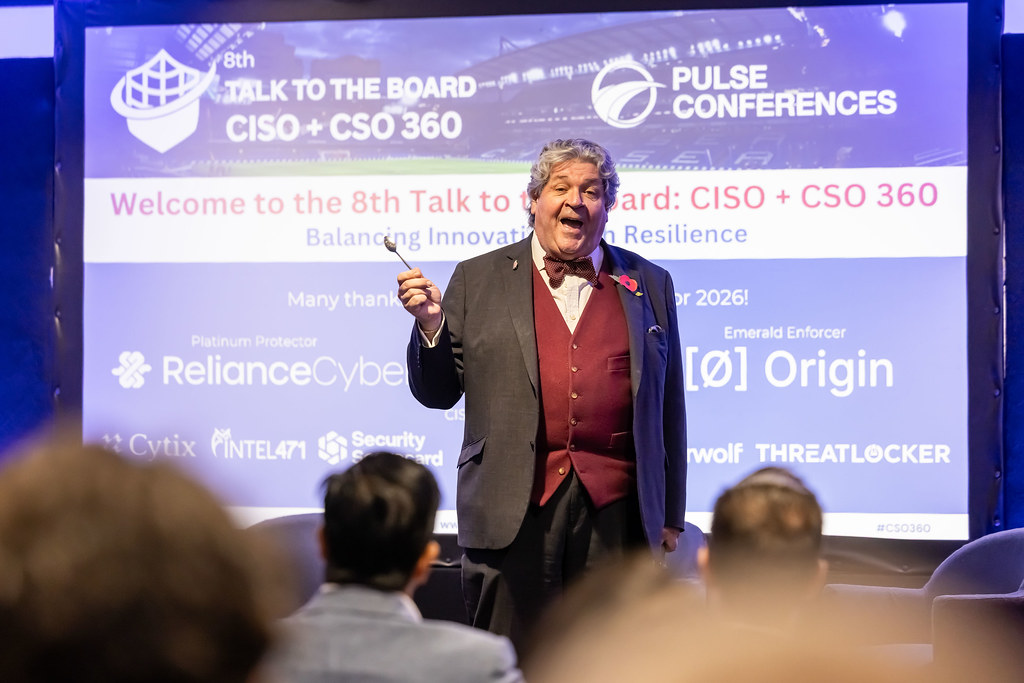
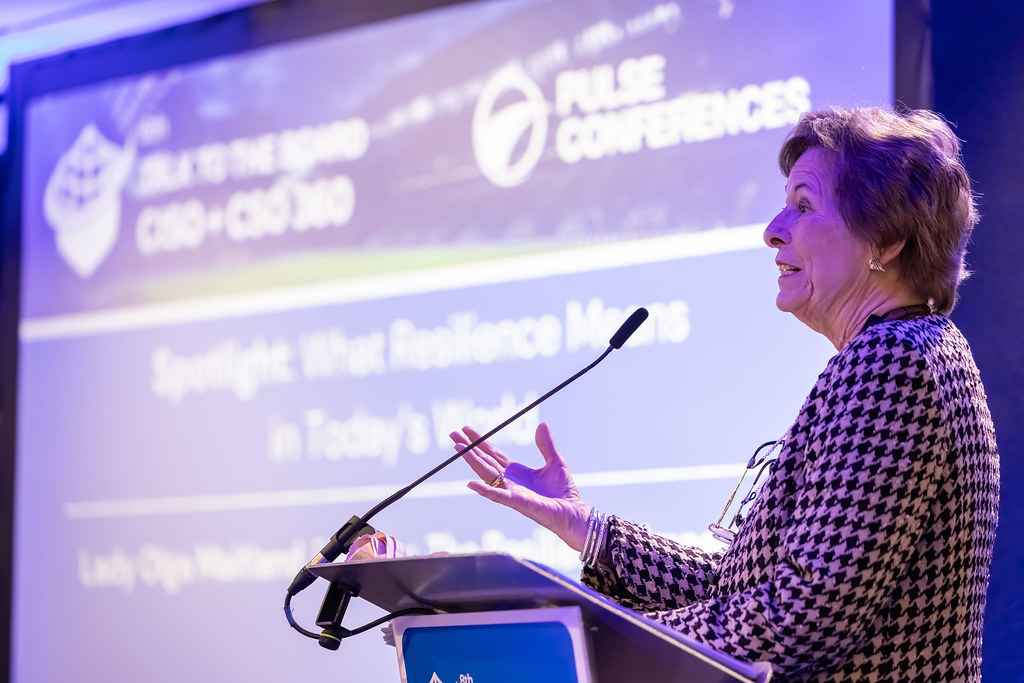
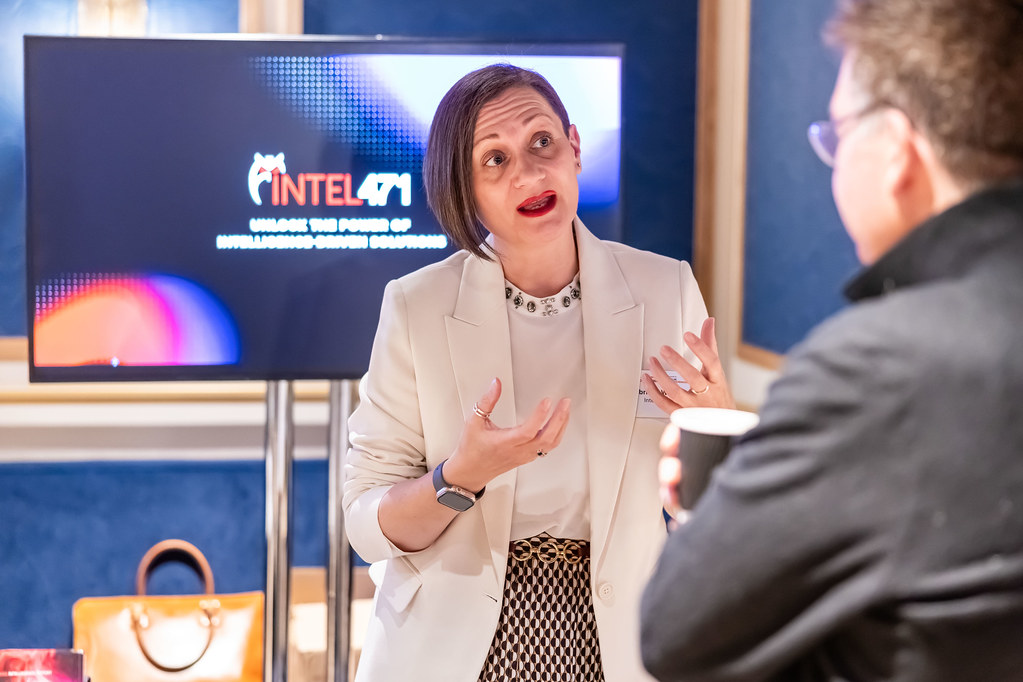
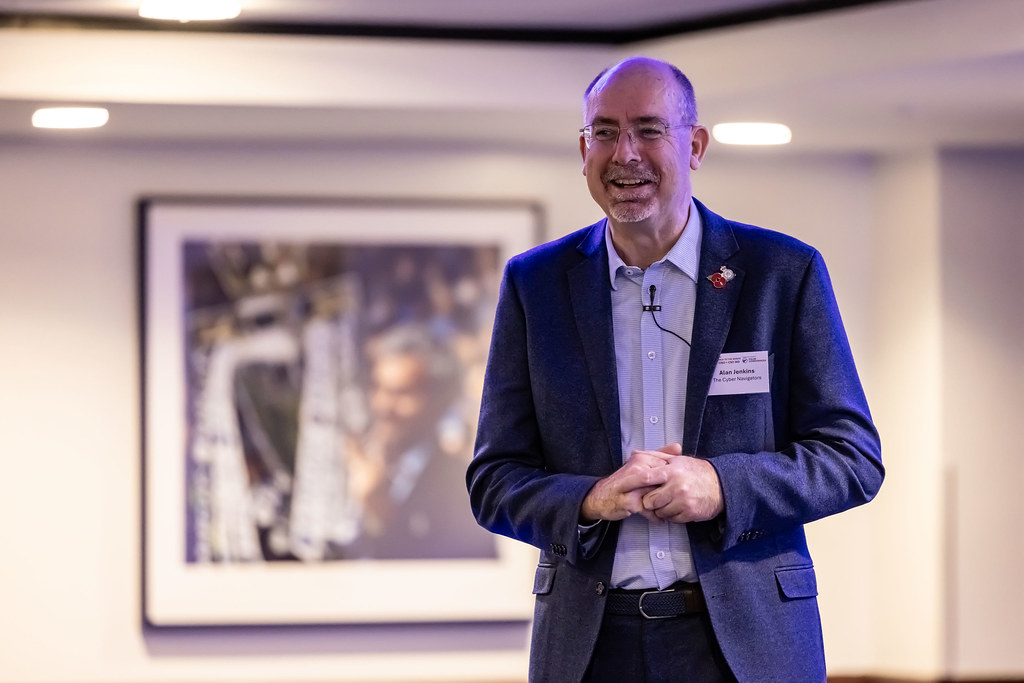
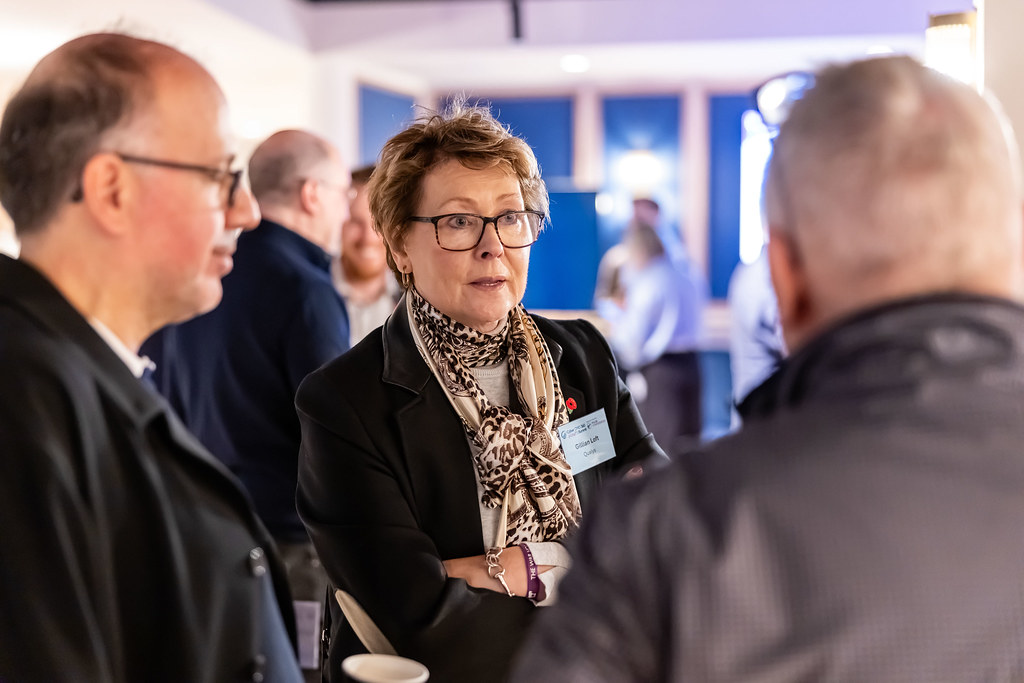
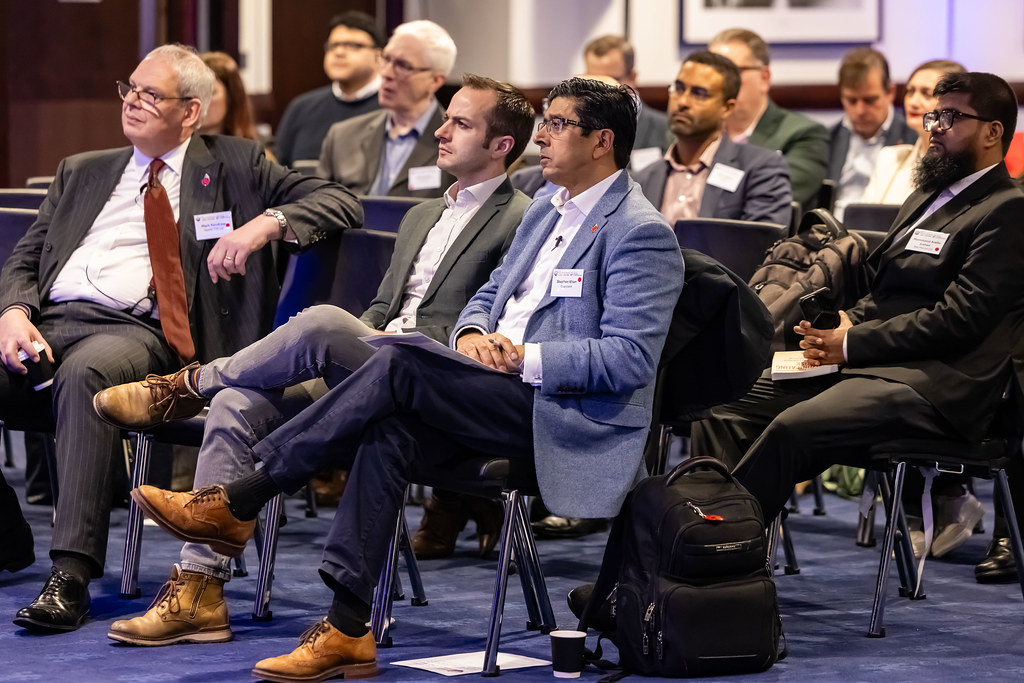
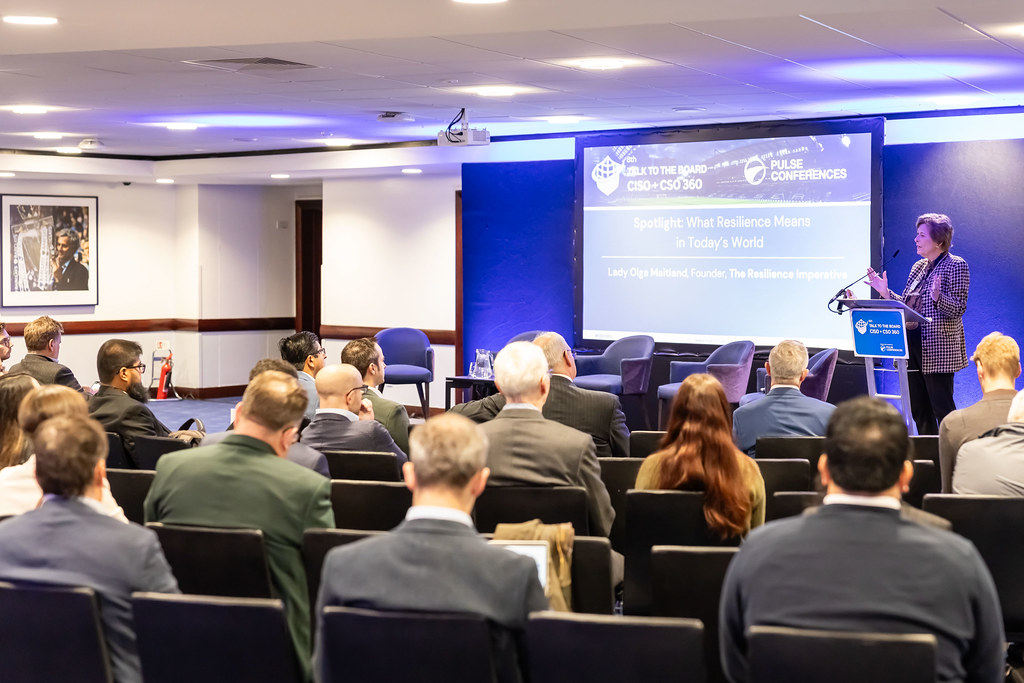
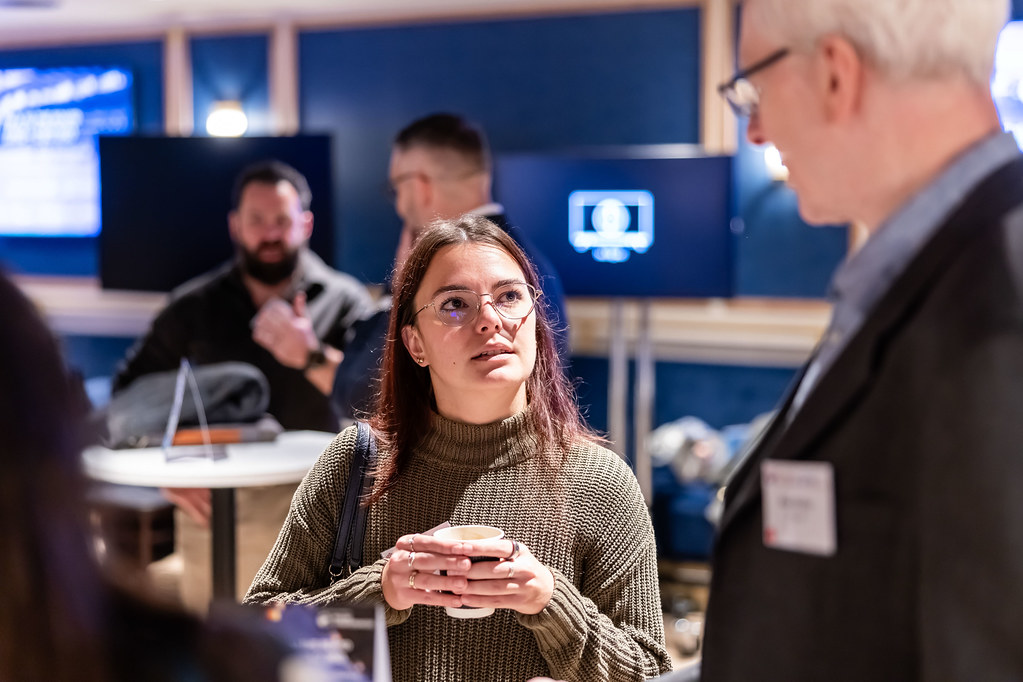
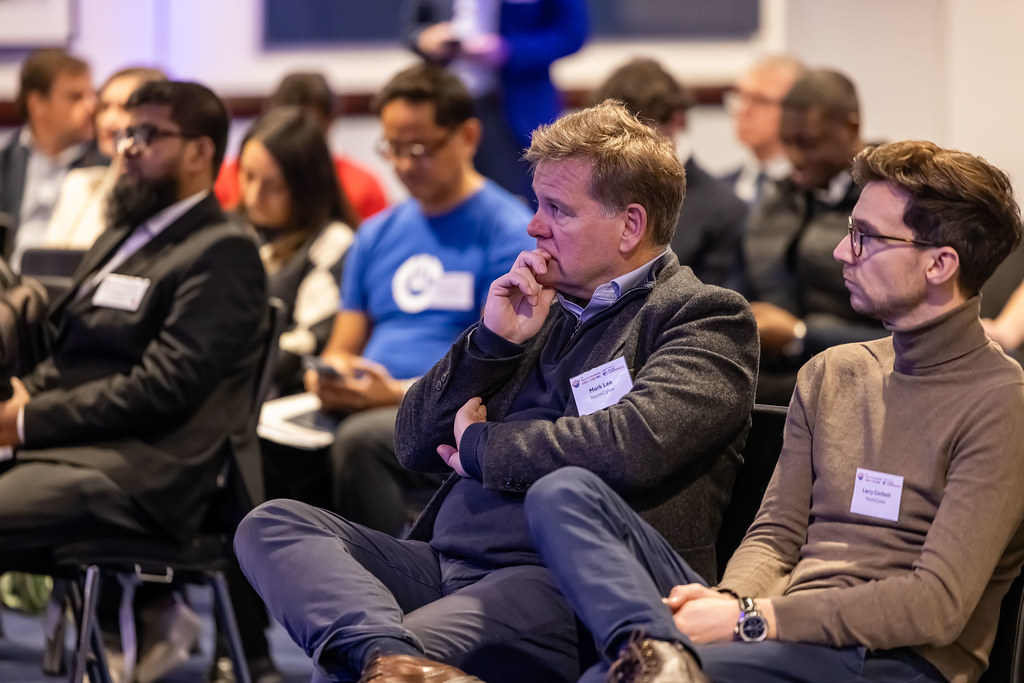
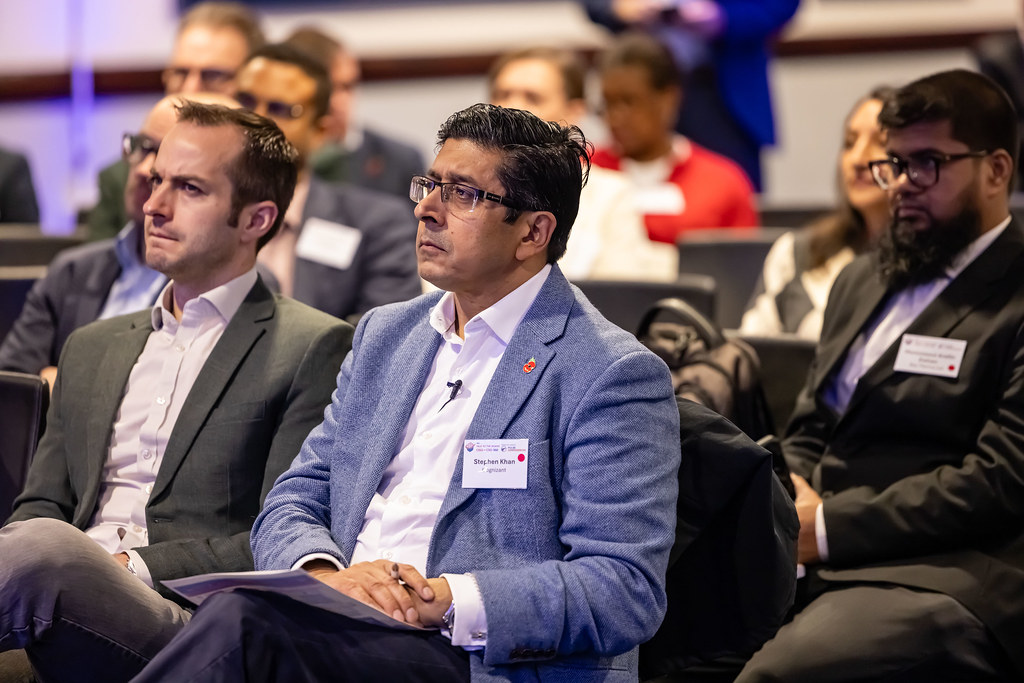
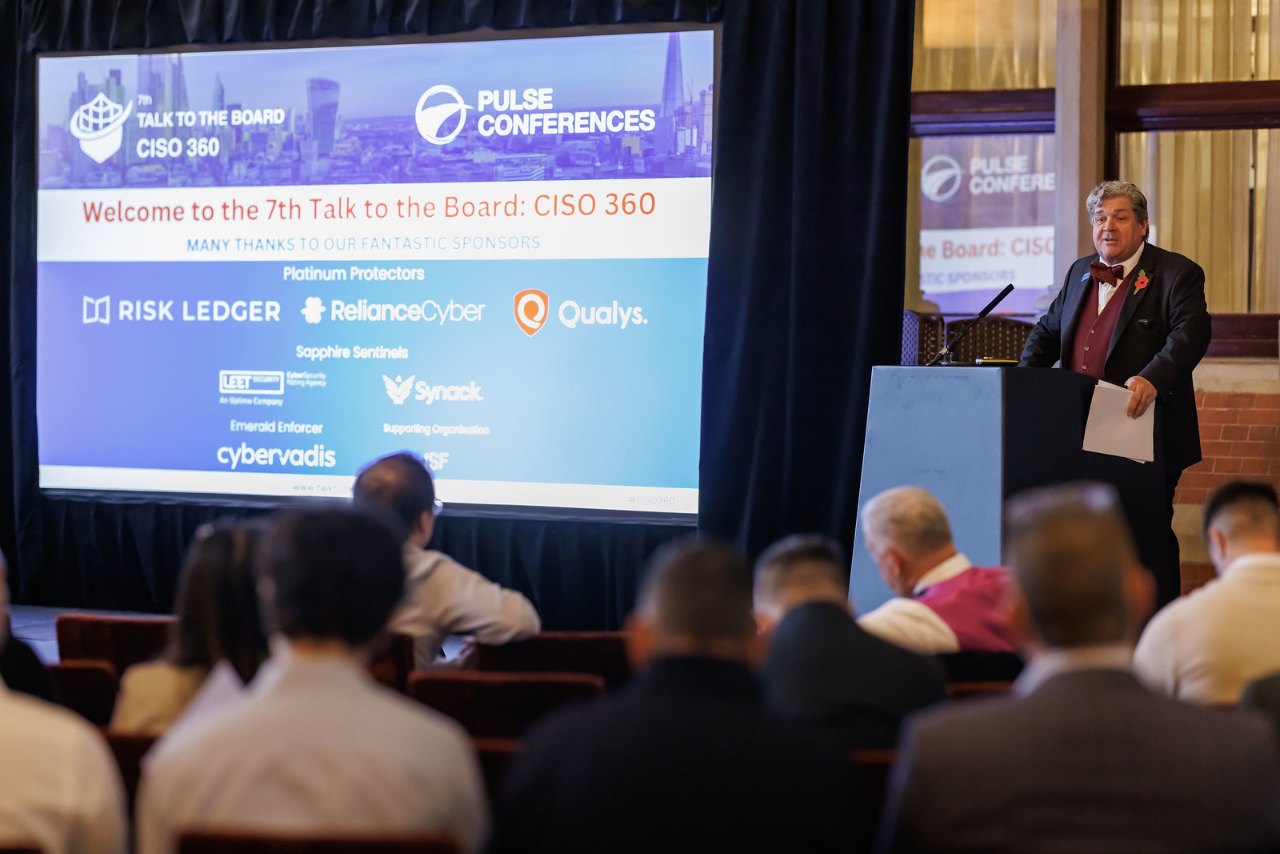
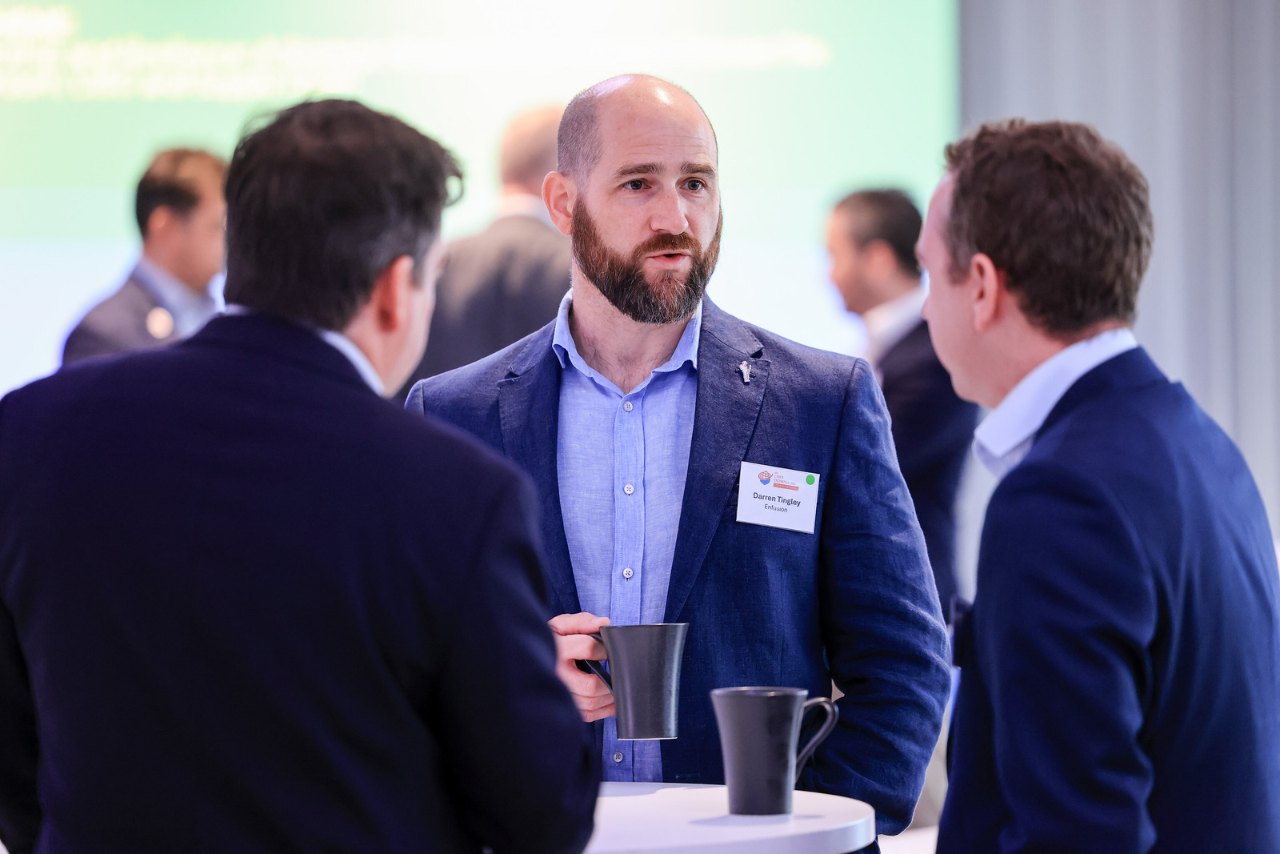
Talk to the Board brings CISOs and Chief Security Officers together with CEOs and Board Directors for an open, on-stage exchange on cyber, physical and geopolitical risk. Photographs from the 2026 edition at Chelsea Football Club are below and on Flickr.

To discuss speaking, email sara.hook@pulseconferences.com. For sponsorship, email sponsorship@pulseconferences.com.

Photographs from 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

View the full album on Flickr

Board Directors and security leaders in a collaborative setting

Cybersecurity and resilience are no longer just technology or security discussions; they are board-level priorities. As cyber and corporate security roles continue to evolve, covering AI, business transformation and GRC, relationships with the Board are changing too.

Talk to the Board is the only dialogue between CISOs, CSOs and Board Directors from across different functional areas. NEDs and the C-suite also take part, encouraging 360 cross-functional dialogue between CISOs, CSOs and the resilience supply chain. Different angles clash and complement each other, and the tensions and different perspectives are both engaging and educational.

With thanks to our 2026 sponsors

Platinum Protector

Reliance Cyber

Sapphire Sentinel

NormCyber

Emerald Enforcer

Origin

CISO 360 Innovators

Cytix

Intel 471

SecurityScorecard

Cyber Rescue Alliance

Cyberwolf

ThreatLocker

Supporting Organisations

Information Security Forum

Key highlights

A unique opportunity

Question a Board without consequences. Gain unfiltered insights by testing the questions you’ve always wanted to ask, and hear Directors’ success and war stories.

Cross-functional perspectives

Hear from non-security leaders, including NEDs and functional heads, on how cybersecurity fits within business strategy, governance and operations.

Master crisis communication

Increase readiness to respond: how can we communicate better during a crisis? Re-energise your approach to leading teams.

Inspire cultural change and well-being

Explore awareness, well-being and transformation campaigns that foster organisational buy-in and collaboration.

Lessons from the top

Directors share stories of success, challenges and growth, with insights into areas such as employee well-being and resilience.

Strategic insights

Gain valuable context on the Board’s view of cybersecurity, corporate security and their future priorities.

Speak business language

Develop communication skills to articulate your challenges in a way that resonates with leadership, so the Board understands your pain points.

What was new for 2026

Fresh boardroom perspectives and AI through the Board’s eyes

The Directors Panel brought voices from across the C-suite, including NED, CEO, CIO, CRO, CMO, CFO and investor views. How do boards view AI for security and security for AI? Do they understand the trade-offs? Where do they see cybersecurity and corporate resilience as a competitive advantage?

Cross-security perspectives

The 8th edition expanded to include CISOs, Directors of Corporate Security (CSOs) and leaders in geopolitical intelligence, resilience and risk. Boards no longer receive risk in separate packets. They receive a ransomware attack linked to organised crime, supply chain disruption driven by geopolitical tensions, insider risk amplified by economic instability, AI-enabled threat actors operating across borders, and physical threats intersecting with cyber compromise.

Inside the Boardroom

Respected CISOs and Corporate Security Directors shared their real board decks, revealing the key messages and reasoning behind decisions.

Bring a Board Director

Delegates were invited to bring a board director to understand the trade-offs between business innovation and resilience, and how CISOs and Chief Security Officers think as a group.

Highlights from a recent Talk to the Board

Many thanks to our enabling Anchor Partners: Mastercard, Dataminr, Sibylline, Restrata, Reliance Cyber, Qualys, Emergent Risk International, ThreatLocker, Intel 471

Programme 2027

The 2027 programme is in development and will be published here. To suggest a topic, or to be considered as a speaker, email sara.hook@pulseconferences.com.

The 2026 programme and speakers are in the 8th Talk to the Board archive.

2027 speakers

Speakers and Board Directors for 2027 will be announced here. To be considered as a speaker, email sara.hook@pulseconferences.com.

See who spoke in 2026 in the 8th Talk to the Board archive.

Networking

Details of the 2027 networking reception will be announced with the venue. Interested in hosting a social event? Email sponsorship@pulseconferences.com.

Sponsorship 2027

Sponsorship of the 9th Talk to the Board: CISO + CSO 360 is now open. To find out more or to book a meeting, email sponsorship@pulseconferences.com or complete the sponsorship enquiry form.

The 2026 sponsors are listed in the 8th Talk to the Board archive.

Venue

The 2027 venue in London will be announced shortly.

Video testimonials

Interviews filmed at previous editions of Talk to the Board.

What delegates and Board Directors say

“Talk to the Board, for me, is absolutely spot on! Coming here and engaging with the board to validate what resonates with them is very special and powerful. We have silos of silos in companies. But criminals don’t have silos. They don’t have borders or boundaries. So, to win the fight, we must come together and build coalitions of capability and bridge across the boundaries we live in. Board members and IT people speak different languages. We must learn to communicate effectively to help make rational decisions within a context that matters. This event, this forum, is exactly what I’m looking for.”

Michael Beaupre, Head of Cyber Security, Hays

“It’s so rare to have that opportunity to hear it directly from the CISOs and the board. So what more could you ask for if you’re up and reporting to boards and you need to communicate with them effectively? For anyone thinking of coming to a Pulse Conferences event, just do it. Block out that time, make the commitment and realise that it’s an investment not only in your company and what your company needs from you but also in your professional development.”

Katherine Leivesley, Head of Legal, Offer and Sourcing, Kingfisher PLC

“The great thing about Pulse is that you get different perspectives outside of our core market. Talk to the Board is interesting because the business dimension is the most important thing about cybersecurity. Speaking to the board brings me that business dimension to cybersecurity.”

Dr Paul Kennedy, Chief Engineer – Cyber and CEMA, QinetiQ

“I wanted to be part of Talk to the Board because I’ve always been so fascinated by technology, particularly cyber attacks and the cyber risk. I’ve learnt about how lonely and vulnerable the CISO/CSO feels. As boards, we need to think about how we can be more of a support for the CISOs so that they don’t feel so under threat. If your world is looking at cyber risk and you’re a CISO or security leader, I would come to this event and get involved because you are sharing and gaining simultaneously.”

Dame Inga Beale, Former CEO, Lloyd’s of London

“Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. Great to have board and CISO side of the equation together. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.”

Robert Hannigan, Former Director, GCHQ

“It was a really interesting panel, Talk to the Board, and great to meet people from across the cybersecurity profession, to hear their concerns and to help them to understand all the different issues that Boards need to deal with and where cybersecurity may rank on their list of priorities.”

Lorraine Heggessey, Former Controller, BBC One

“A rich discussion with very interesting themes emerging for myself. Both the audience and panel found the event very interesting and informative.”

Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc; Chairman, Sustainability and Inclusion Practice, Kantar

“It’s great to hear from board executives and have CISOs sit alongside them, asking questions. It’s a sort of reversal of the status quo.”

Jonathan Luff, Co-Founder, CyLon Ventures

“Talk to the Board provides a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. More intriguing, perhaps, was that CISOs were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”

Graham Joscelyne, Former Auditor General, World Bank; Chair, Audit and Ethics Committee, The Global Fund to Fight AIDS, Tuberculosis and Malaria

“… how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics.”

Deborah Exell, Former Board Member, Head of Human Capital and Business Transformation, Getronics