CISO 360 + CSO 360

8th Talk to the Board: CISO + CSO 360

Security Talks Business to Board Directors: Balancing Innovation, Trust and Resilience

The only truly 360° on-stage exchange where CISOs and Chief Security Officers engage openly with CEOs and Board Directors.

DATEWednesday 4 November 2026
VENUEChelsea Football Club, Stamford Bridge, London
FORMATCISOs, CSOs and Board Directors

Thank you for joining us

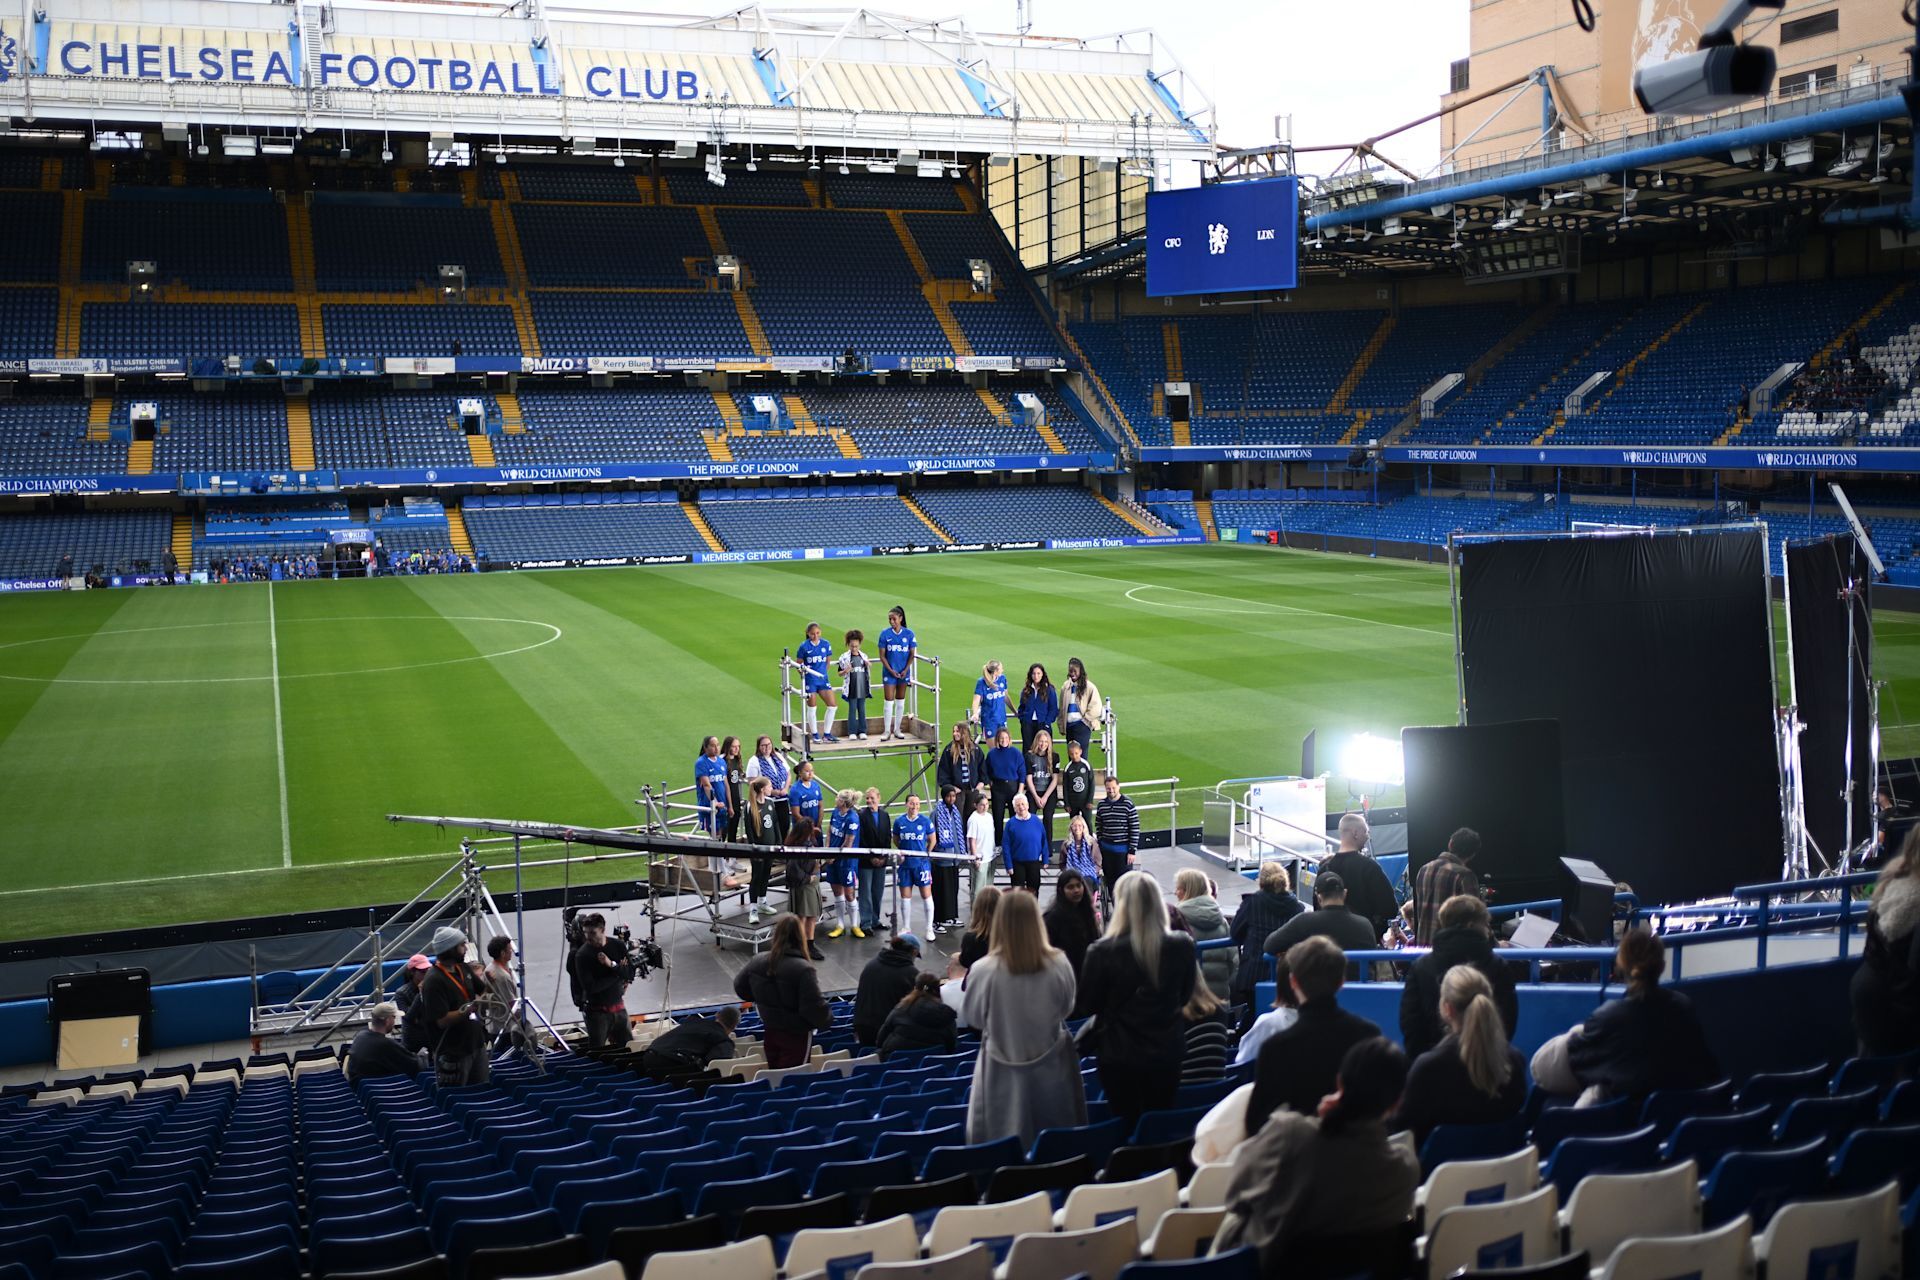
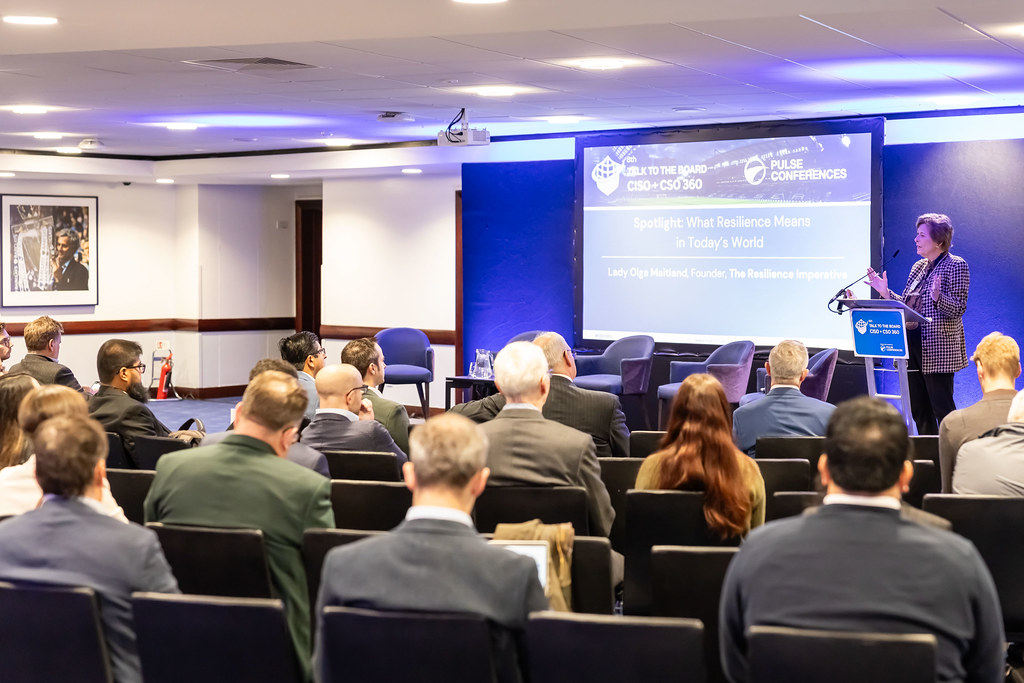
The 8th Talk to the Board: CISO + CSO 360 took place on Wednesday 4 November 2026 at Chelsea Football Club, Stamford Bridge, London. Thank you to everyone who joined us, and to our speakers, Board Directors and sponsors.
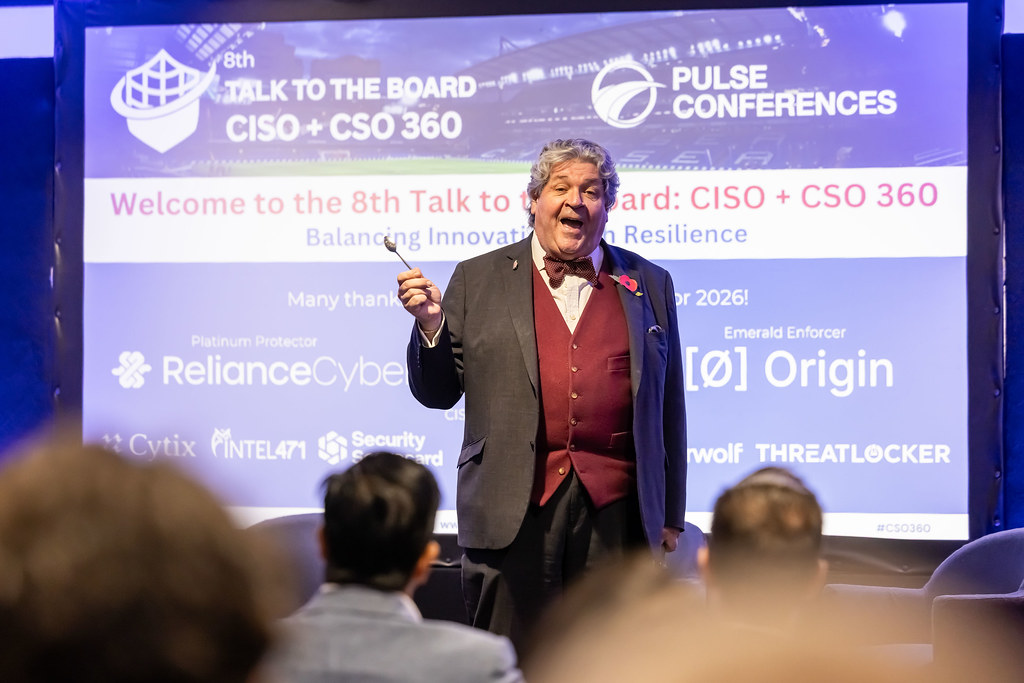
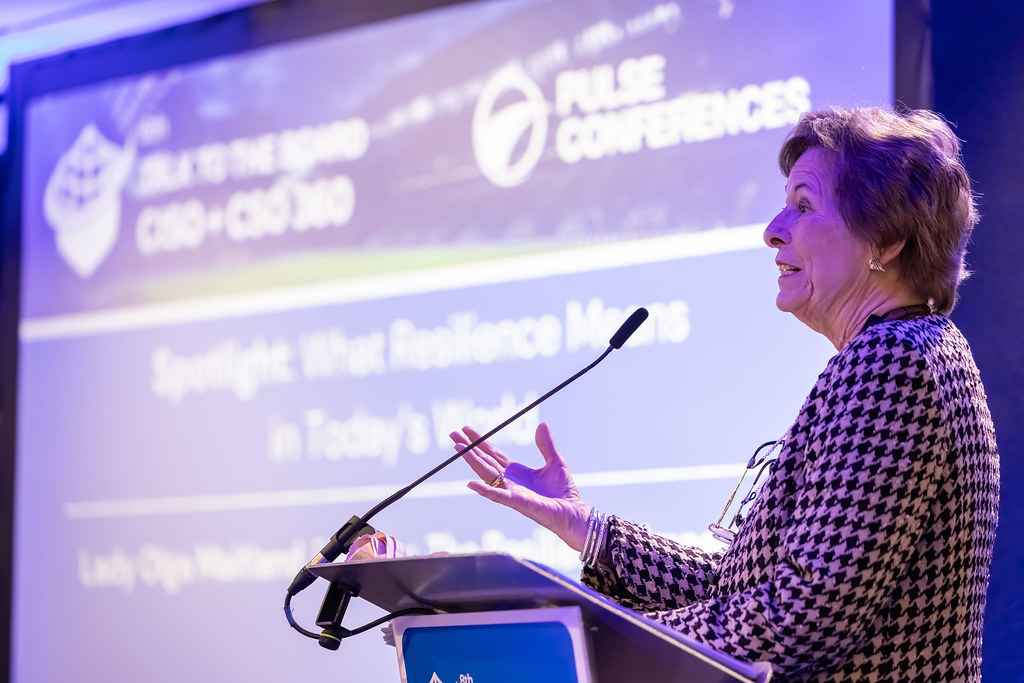
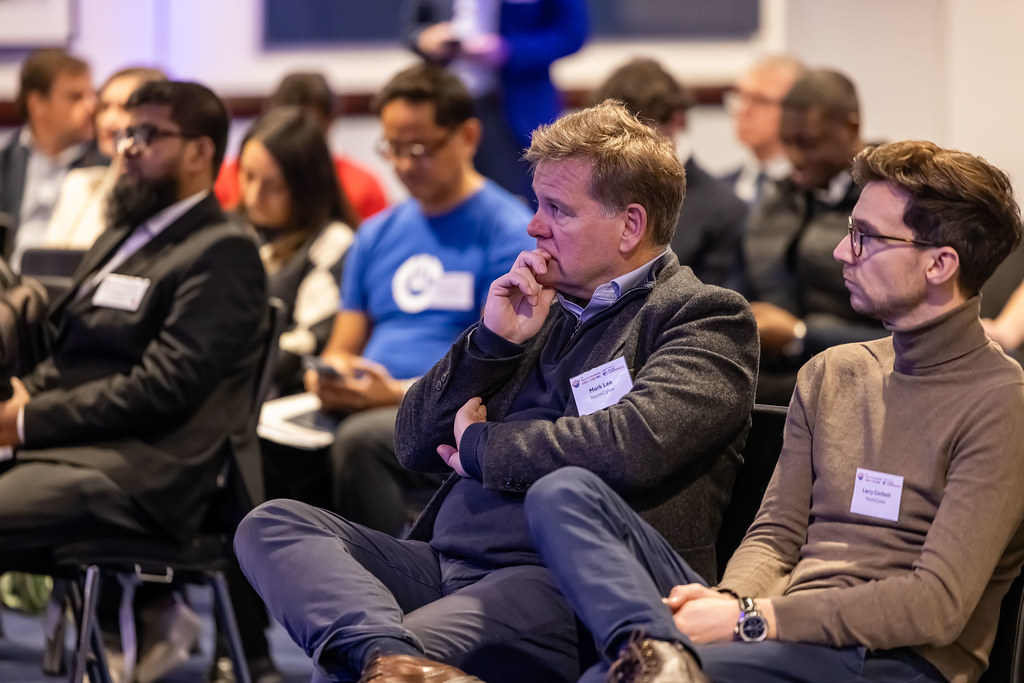
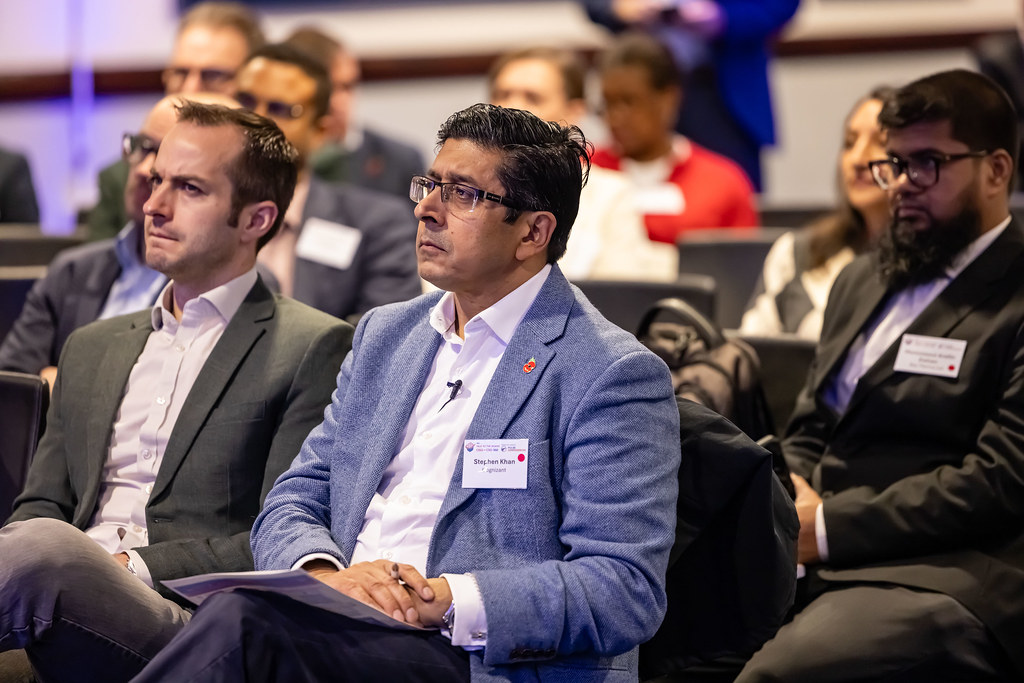
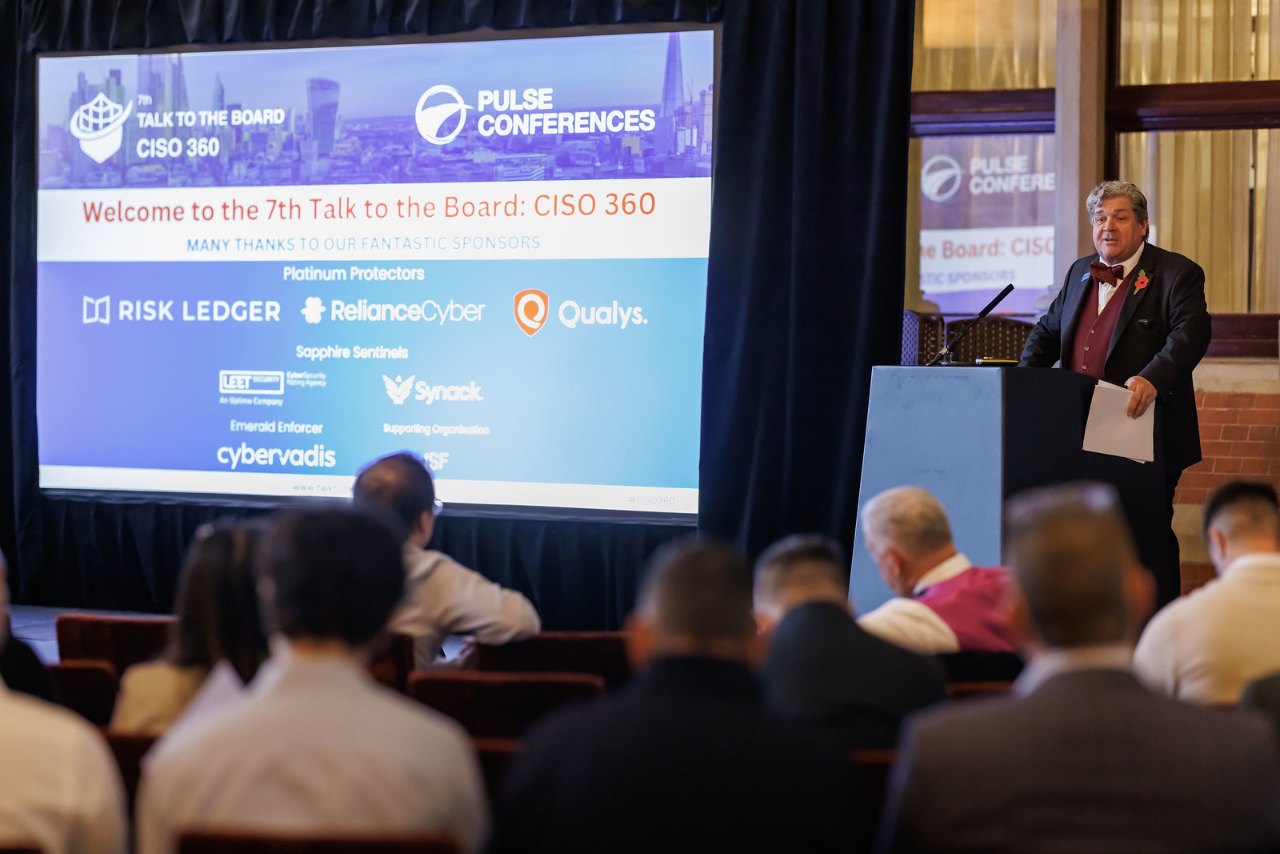
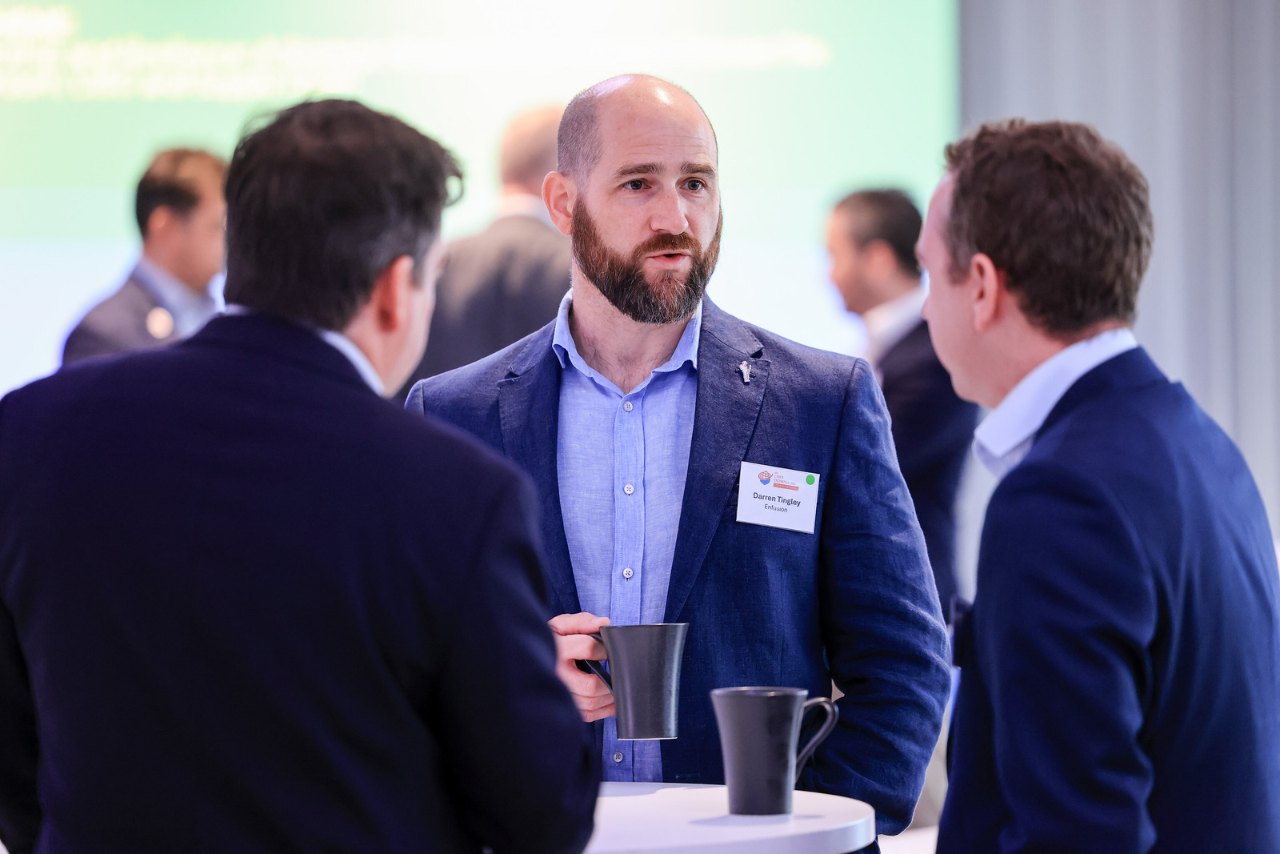
8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

8th Talk to the Board, 4 November 2026

View the full album on Flickr

Board Directors and security leaders in a collaborative setting

Cybersecurity and resilience are no longer just technology or security discussions; they are board-level priorities. As cyber and corporate security roles continue to evolve, covering AI, business transformation and GRC, relationships with the Board are changing too.

Talk to the Board is the only dialogue between CISOs, CSOs and Board Directors from across different functional areas. NEDs and the C-suite also take part, encouraging 360 cross-functional dialogue between CISOs, CSOs and the resilience supply chain. Different angles clash and complement each other, and the tensions and different perspectives are both engaging and educational.

With thanks to our 2026 sponsors

Platinum Protector
Reliance Cyber

Sapphire Sentinel

NormCyber

Emerald Enforcer

Origin

CISO 360 Innovators

Cytix

Intel 471

SecurityScorecard

Cyber Rescue Alliance

Cyberwolf

ThreatLocker

Supporting Organisations

Information Security Forum

Key highlights

A unique opportunity

Question a Board without consequences. Gain unfiltered insights by testing the questions you’ve always wanted to ask, and hear Directors’ success and war stories.

Cross-functional perspectives

Hear from non-security leaders, including NEDs and functional heads, on how cybersecurity fits within business strategy, governance and operations.

Master crisis communication

Increase readiness to respond: how can we communicate better during a crisis? Re-energise your approach to leading teams.

Inspire cultural change and well-being

Explore awareness, well-being and transformation campaigns that foster organisational buy-in and collaboration.

Lessons from the top

Directors share stories of success, challenges and growth, with insights into areas such as employee well-being and resilience.

Strategic insights

Gain valuable context on the Board’s view of cybersecurity, corporate security and their future priorities.

Speak business language

Develop communication skills to articulate your challenges in a way that resonates with leadership, so the Board understands your pain points.

What was new for 2026

Fresh boardroom perspectives and AI through the Board’s eyes

The Directors Panel brought voices from across the C-suite, including NED, CEO, CIO, CRO, CMO, CFO and investor views. How do boards view AI for security and security for AI? Do they understand the trade-offs? Where do they see cybersecurity and corporate resilience as a competitive advantage?

Cross-security perspectives

The 8th edition expanded to include CISOs, Directors of Corporate Security (CSOs) and leaders in geopolitical intelligence, resilience and risk. Boards no longer receive risk in separate packets. They receive a ransomware attack linked to organised crime, supply chain disruption driven by geopolitical tensions, insider risk amplified by economic instability, AI-enabled threat actors operating across borders, and physical threats intersecting with cyber compromise.

Inside the Boardroom

Respected CISOs and Corporate Security Directors shared their real board decks, revealing the key messages and reasoning behind decisions.

Bring a Board Director

Delegates were invited to bring a board director to understand the trade-offs between business innovation and resilience, and how CISOs and Chief Security Officers think as a group.

Highlights from a recent Talk to the Board

Many thanks to our enabling Anchor Partners: Mastercard, Dataminr, Sibylline, Restrata, Reliance Cyber, Qualys, Emergent Risk International, ThreatLocker, Intel 471

Programme 2026

The 8th Talk to the Board took place on Wednesday 4 November 2026 at Chelsea Football Club, Stamford Bridge. Our programmes are organic, so that each edition brings the latest perspectives from CISOs, CSOs and Board Directors.

The day at a glance

  • MorningConference panels and CISO-to-CISO table discussions
  • LunchLunch, and BYOR (Bring Your Own Replacement)
  • AfternoonThe Talk to the Board panel of Board Directors
  • EveningNetworking reception in the Directors’ Lounge, Stamford Bridge

Recent programmes

To suggest a topic or speaker for the next edition, email teampulse@pulseconferences.com.

2026 speakers

Speakers and contributors at the 8th Talk to the Board, 4 November 2026.

Ashley Sweetman

Ashley Sweetman

Director of Cyber Risk Insights, London-based global bank; Author, Communicating Cyber Risk and Cyber and the City

Ashley Sweetman is Director of Cyber Risk Insights for a London-based global bank. He is the author of Communicating Cyber Risk and Cyber and the City and is a Visiting Research Associate with the Emerging Threats Group at the University of Oxford. He holds a PhD in War Studies from King’s College London.
Dr Vasileios Karagiannopoulos

Dr Vasileios Karagiannopoulos

Associate Professor in Cybercrime and Cybersecurity, University of Portsmouth; Co-Director, Centre for Cybercrime and Economic Crime

His research focuses on political cybercrime and regulation, cybersecurity education, online fraud and the role of AI in cybercrime and cybersecurity threats. He is theme lead for cybercrime, online harms and AI for the University of Portsmouth Policing Academic Centre of Excellence, Director of the award-winning Cybercrime Awareness Clinic, and co-chairs the Faculty of Humanities and Social Sciences Ethics Committee.
Stephen Hill

Stephen Hill

Former Group CISO, Credit Suisse

Steve Hill is an independent strategic adviser, helping Boards to navigate geopolitics, national security and cybersecurity challenges. He served as Group CISO at Credit Suisse and deputy Group CISO at UBS until August 2024, and previously spent over thirty years in national security roles for the British Government, including as Deputy Director in the National Security Secretariat of the UK Cabinet Office. He is a senior visiting research fellow at King’s College London and sits on advisory boards including Dell Technologies, Venari and Twine.
Lady Olga Maitland

Lady Olga Maitland

President, Defence and Security Forum
Alan Jenkins

Alan Jenkins

Fractional CISO, The Cyber Navigators

Alan was formerly Group CISO at Babcock International, UK CSO at CSC and T-Systems, an Associate Partner at IBM Security, and served in the Royal Air Force for 21 years.
Burim Bivolaku

Burim Bivolaku

Business Information Security Officer, ICE Exchanges and CCPs, Intercontinental Exchange (ICE)
Deborah Saffer

Deborah Saffer

Director of Information Security, Liberty International Insurance
Daan Gheysens

Daan Gheysens

CEO, Cyberwolf

Daan Gheysens is the CEO of Cyberwolf, a global cybersecurity firm with offices in the United States and Belgium. Cyberwolf delivers all-in digital protection for wealthy families and corporate VIPs, delivered in a private and convenient experience.

Before Cyberwolf, Daan served as Head of Sales and Marketing at Robovision, where he built and scaled the go-to-market for AI-powered solutions in medical imaging and industrial automation. He began his career at Accenture, advising Fortune 500 companies on AI strategy and helping them establish their first AI teams and programmes.
Joe Chittock

Joe Chittock

CIO, Pickering Group

Jonathan Armstrong

Jonathan Armstrong

Partner, Punter Southall
Neil Weller

Neil Weller

Group CISO, OCS Group Holdings
Mark Lee

Mark Lee

Director, NormCyber

Lee brings decades of experience in building new-customer-acquisition sales teams, targeting large UK and global enterprises with managed services. He also has proven expertise executing acquisition strategies for fast-scaling businesses. Prior to joining Norm, Lee served as Managing Director of Nasstar for six years, where he oversaw the company’s managed services and cloud key accounts business, managing half of the company’s revenue. He also spent six years at Intamac Systems, where he was promoted to CEO.
Robert Newby

Robert Newby

Head of Security Business Engagement, Marks and Spencer
Dr Runli Guo

Dr Runli Guo

AI Security and Governance Leader, AI DIONIC
Toks Oladuti

Toks Oladuti

Former Global CISO, Dentons

Toks has been responsible for the global delivery of information security at Dentons, the world’s largest law firm. He has over 20 years’ experience working in security, technology and privacy, across a number of industries.

Toks is an experienced and strategic business risk leader with a particular passion for strategy and team development. His core skillset includes security operations and architecture, risk management and risk-driven investment, data protection, compliance and audits, and enterprise culture, awareness and training.
Tom Berry

Tom Berry

Founder, Be Less Beige Ltd

Tom Berry is a specialist communications consultant and board advisor. He is European Chair of the global PR agency MikeWorldWide and has worked in technology, corporate and crisis communications for 25 years. Tom is also an Independent Council Member for King’s College London, a Trustee for Onvero (The Employers’ Network for Equality and Inclusion) and was a Non-Executive Director for Mental Health First Aid England. As one of the early Advisory Board Members for ClubCISO, Tom has been deeply involved in working with CISOs and security companies to promote the profession. Before working in communications Tom was a journalist for a decade, winning Business Journalist of the Year and Magazine Journalist of the Year awards from the Periodical Publishers’ Association and The Work Foundation.
Thomas Ballin

Thomas Ballin

Co-Founder, Cytix

Thomas Ballin is co-founder of Cytix, a Manchester company that understands the tickets, pull requests and releases moving through a business to identify which changes have introduced risk, and provides the decision layer to validate them. He has spent the past 12+ years across penetration testing, security consulting and product engineering, giving him a broad view of how organisations build software and where that leaves them exposed.
Simon Scales

Simon Scales

Chief Education and Development Officer, Association of Corporate Investigators

Simon has over 30 years’ investigative, security and compliance experience, formed from an extensive corporate and law enforcement background. He is recognised for having conducted complex bribery, corruption, fraud and misconduct investigations worldwide, in regulated and non-regulated arenas, and has led investigation, ethics, compliance and integrity teams within Europe, the USA, Africa and the Middle East.
Thomas Eeles

Thomas Eeles

Head of IT and IT Security, Gumtree.com
Vasilis Razos

Vasilis Razos

Head of Information Security Risk, Informa

Vasilis Razos is Head of Information Security Risk at Informa, a FTSE 100 international B2B events, digital services and academic publishing company. He has 14 years of cybersecurity experience, with a focus on risk management. Before Informa, he worked in global companies in a variety of industries, including financial services and telecoms. Vasilis holds the CISSP and CISSP-ISSMP certifications and is a member of the FAIR Institute for cyber and operational risk management.

Recent Directors on the Talk to the Board panel

  • Susan Hooper, Non-Executive Director, Uber; Non-Executive Director, Chair of the Remuneration Committee, ESG Lead, DNED Workforce, Moonpig
  • Dr Mark Carawan, Board Member and Chair of the Board Audit Committee, The Bank of London Group; Board and Chair of the Risk Committee, Euroclear UK and International
  • Peter Davies, Former CEO, Air Malta; CEO, Airline Management Group
  • Carolyn Brown, CIO, British Medical Association; Board Trustee, Association for Project Management
  • Lorraine Heggessey, Former Controller of BBC One
  • Josephine Fairley, Co-Founder, Green & Black’s
  • Dame Inga Beale, Former CEO, Lloyd’s of London
  • Robert Hannigan, Former Director, GCHQ
  • Mike Coupe, Former CEO, Sainsbury’s
  • Roger Flynn, Former CEO and leader in transformation change, Virgin, British Airways, Prudential
  • Rupert Lee-Browne, Group Chief Executive, Caxton
  • Daniel Bobroff, Founder and CEO, DUWL; Former Co-Founder, ASOS Ventures
  • Laura Tenison MBE, Former Founder and CEO, JoJo Maman Bébé
  • Haydn Brooks, CEO and Co-Founder, Risk Ledger
  • Dr Alan Knight OBE, Group Director of Sustainability, Drax
  • Julian Wheatland, Former Chair, SCL Group
  • John Hutson, Chief Executive Officer, JD Wetherspoon plc
  • Air Marshal Sir Christopher Coville, Senior Defence Advisor, EMC and BT; Former Chairman, Westland Helicopters
  • Robin Dargue, Global CIO, WPP

Networking

The day closed with a networking reception at Stamford Bridge, included in the Delegate Pass and the Networking Pass.

Interested in hosting a social event at a future edition? Email sponsorship@pulseconferences.com.

Networking Reception: Talk to Peers, Talk to the Board

  • WhenWednesday 4 November, 17:00–20:00
  • WhereDirectors’ Lounge, Chelsea FC
  • Hosted byAll 2026 sponsors

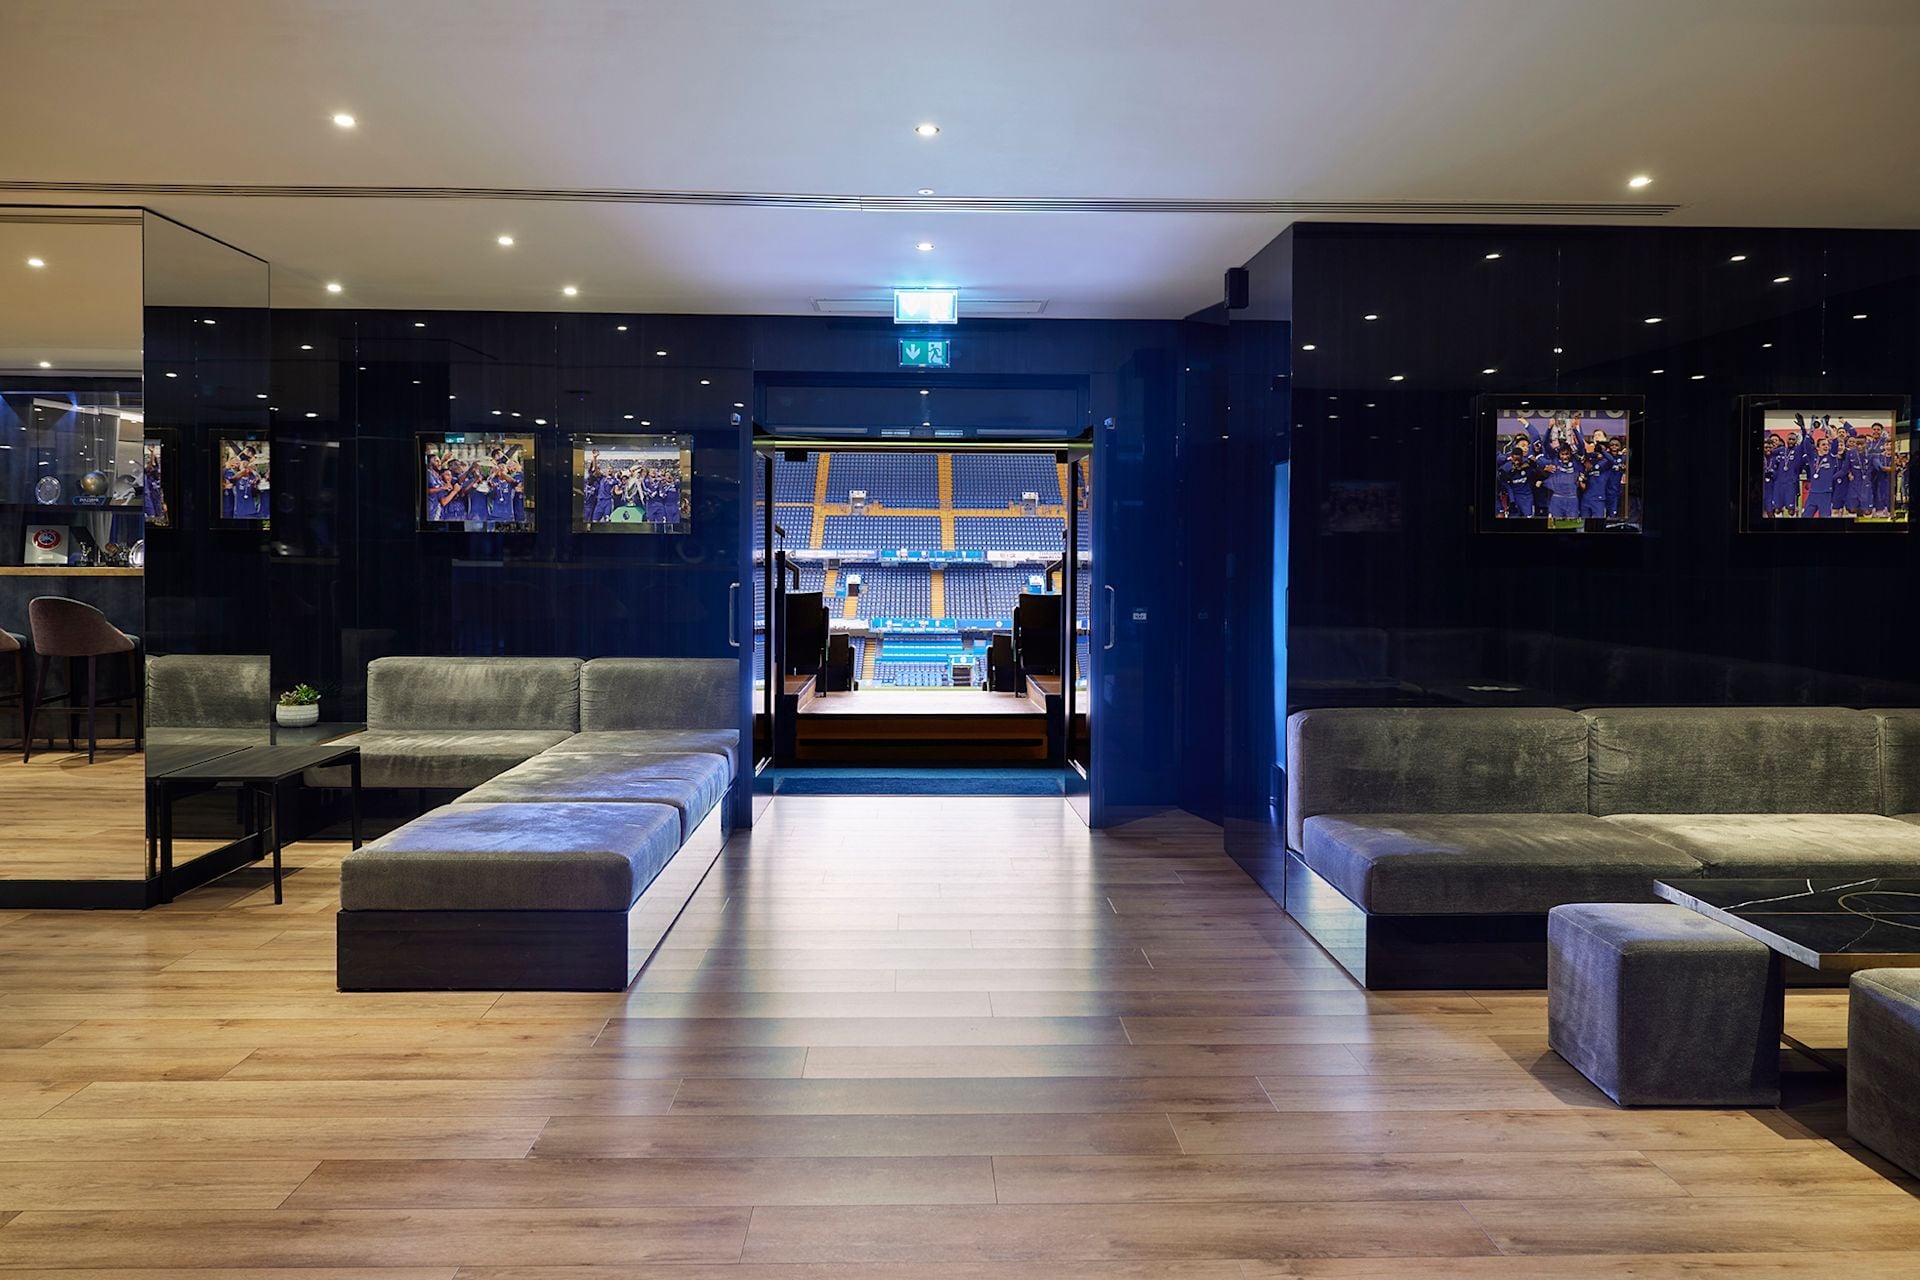
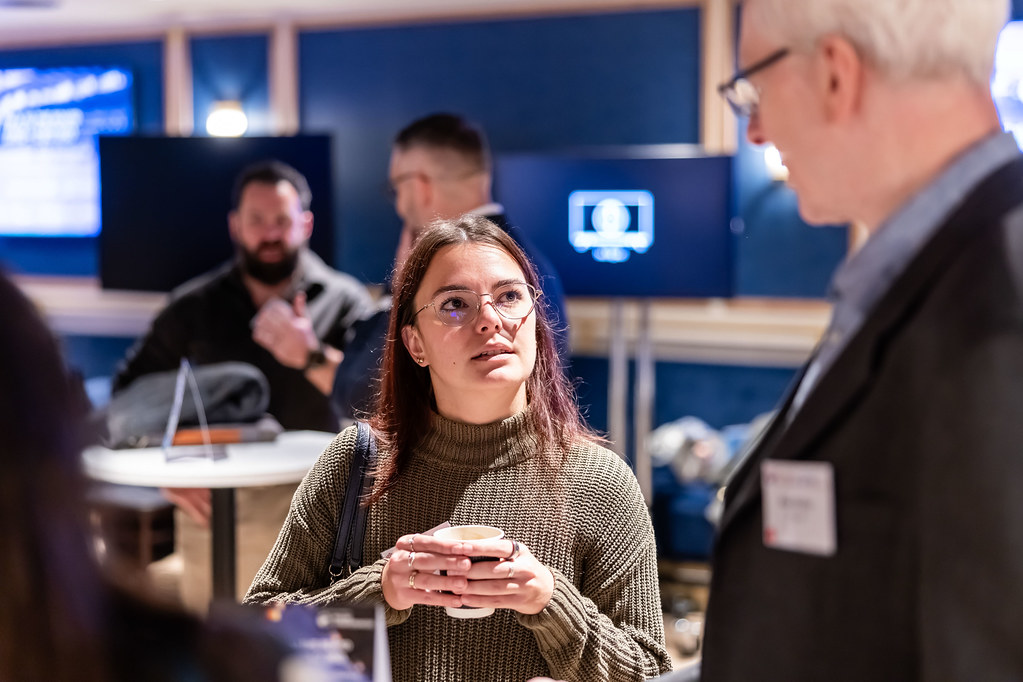
Delegates continued the conversations over drinks and canapés in the aptly named Directors’ Lounge, with direct access to take conversations out into the stands.

Many thanks to our 2026 sponsors

To find out about sponsorship opportunities for the next edition, or to book a meeting with us, contact sponsorship@pulseconferences.com.

Platinum Protector

Reliance Cyber

Reliance Cyber

Reliance Cyber is your specialist cybersecurity operations partner, focused solely on identifying, preventing and responding to breaches. We combine deep engineering and powerful automation with a constant human-in-the-loop approach for all our services. Our best-in-class technology reduces your threat exposure, while our experts work to detect and resolve breaches faster. As your trusted partner in an increasingly complex landscape, we defend your business continuity. We turn your security into a competitive advantage, enabling you to focus on your goals with confidence.

www.reliancecyber.com

Sapphire Sentinel

NormCyber

NormCyber

NormCyber makes cyber resilience measurable, giving CIOs and CISOs a continuous view of where they are exposed, how effectively they are protected and whether resilience is improving over time. At the heart of our approach is the Cyber Resilience Score: a dynamic, CAF-aligned measure that brings together signals from across your security environment to quantify resilience, expose the gaps that matter and demonstrate progress in a language the wider business can understand. Delivered through our UK-based, CREST-accredited 24/7 SOC, our analysts turn that intelligence into prioritised action, continuously reducing risk, strengthening resilience and helping prevent cyber incidents from becoming business disruption. We believe cyber resilience isn’t something you claim. It’s something you prove.

www.normcyber.com

Emerald Enforcer

Origin

Origin

Origin is the endpoint AI observability platform for agentic monitoring and security. It finds the agents in your environment and reconstructs each session from activity captured on the endpoint. The result is a trace that lets security teams monitor agents as they work and investigate any session to see what the agent was asked to do, everything it touched, and what changed.

www.originhq.com

CISO 360 Innovators

Cytix

Cytix

Cytix is the security decision layer for a world where software development never stops. It reads the context behind every ticket, pull request and release, and helps security, engineering and risk teams decide which software changes carry real risk, what response is proportionate, and what evidence to keep. Cytix already powers KPMG and NCC Group’s continuous testing programme, turning software change into security decisions the business can stand behind.

www.cytix.io

Intel 471

Intel 471

Intel 471 equips enterprises and government agencies with intelligence-driven security offerings powered by real-time insights into cyber adversaries, threat patterns, and potential attacks relevant to their operations. By integrating human-sourced intelligence with advanced automation and curation, the company’s platform enhances security measures and enables teams to bolster their security posture by prioritising controls and detections based on real-time cyber threats. Organisations are empowered to neutralise and mitigate digital risks across dozens of use cases across its solution portfolios: Cyber Threat Exposure, Cyber Threat Intelligence and Cyber Threat Hunting.

www.intel471.com

SecurityScorecard

SecurityScorecard

SecurityScorecard is the global leader in threat-informed third-party risk management (TPRM), securing the world’s supply chains. The company delivers a modern, threat-informed approach to TPRM that enables organisations to drive out risk at the source. Through continuous visibility, AI-accelerated intelligence and predictive insights, the platform transforms third-party risk into a competitive advantage, empowering organisations to proactively reduce risk before incidents occur and respond with confidence when they do. Trusted by over 3,300 organisations, including 70% of the Fortune 100.

securityscorecard.com

Cyber Rescue Alliance

Cyber Rescue Alliance

Cyber Rescue helps CISOs demonstrate to the board that cyber risk is decreasing across their organisations, subsidiaries and supply chains. We help organisations worldwide make informed decisions about where to invest in cybersecurity, combining industry-leading technology with expert guidance and executive support. As SecurityScorecard’s Premier Partner, Cyber Rescue provides its VIP Executive Service to hundreds of customers, helping them understand, manage and communicate their cyber risk with confidence.

Cyberwolf

Cyberwolf

Most leaders are well protected at work. But attackers stopped coming in through the company a long time ago. They come in through your personal life: your phone, your home network, your travel data, your public profile, your family’s accounts. That is the gap Cyberwolf closes. We protect the digital lives of executives, board members, high-net-worth individuals and their families, with enterprise-grade security carried by a team of experts who know you.

www.cyberwolf.io

ThreatLocker

ThreatLocker

ThreatLocker is a Zero Trust cybersecurity platform protecting endpoints, networks and cloud workloads. Its Application Control, Ringfencing, Elevation Control, Storage Control and Network Control tools enforce least privilege to help prevent ransomware, data exfiltration and unauthorised access, with central management across on-premises and cloud environments.

www.threatlocker.com

Supporting Organisations

Information Security Forum

Information Security Forum

Founded in 1989, the Information Security Forum (ISF) is an independent organisation driven by its Members, ranging from Fortune 500 and Forbes 2000 listed corporations to public-sector bodies and government departments. Its business-driven solutions provide organisations with the guidance, tools and methodologies needed to tackle wide-ranging governance, risk and compliance challenges.
www.securityforum.org

Why sponsor Talk to the Board?

Talk to the Board: CISO + CSO 360 convenes decision-makers across the full spectrum of enterprise risk: cyber, physical, geopolitical and strategic governance. It is a board-facing security leadership forum.

Integrating risk narratives, sponsors engage with:

  • CISOs and senior cybersecurity practitioners responsible for enterprise cyber resilience
  • Corporate Security Directors overseeing operational protection, and geopolitical intelligence leaders shaping risk foresight
  • GRC C-suite driving governance frameworks, regulatory alignment and risk quantification, tied directly to business impact
  • Board Directors and NEDs influencing capital allocation and governance decisions
  • Investors assessing resilience maturity and cyber posture as drivers of valuation and long-term market confidence

Together, they help boards understand convergence risk, cascading impact and systemic vulnerability. For sponsors, this means direct access to CISOs and C-suite leaders shaping board-level risk narratives; insight into how security investment decisions are evaluated; alignment with cross-domain resilience priorities; and high-trust, senior conversations in addition to the one-to-one meetings.

94%of recent sponsors would recommend
96%would return

Sponsor feedback, Talk to the Board: CISO + CSO 360

What sponsorship includes

Meetings arranged for you, end to end

We schedule your one-to-one meetings before you arrive, matched on mutual relevance and selection. Your team arrives with a diary rather than a stand to staff. We regularly deliver 250–270% of the meetings contracted.

Your own event, without running your own event

A curated space, your chosen theme and session type, inside an event already full of the people you want in the room: the depth of a hosted event without the cost, lead time or risk of filling it yourself.

Bring your clients with you

Complimentary places for your existing customers and prospects. They attend as invited guests, in the sessions and at the networking reception.

In the room, not waiting outside for the breaks

Networking is part of the event, not an add-on. Your team sits among the delegates throughout, learning alongside them in the main conference room.

A two-way conversation about your offering

Our CISOs join to think aloud about problems they have not solved. Under The Chatham House Rule they will tell you where your category is falling short.

Worked through with you, start to finish

We agree the content, messaging and practicalities with you from signature to onsite delivery and post-event follow-up.

What we don’t sell: delegate lists, agenda control and pitching slots are not available at any price. That is why the CISOs come back, and why your presence among them carries weight.

What recent sponsors say on camera

What our sponsors say

“Talk to the Board. It’s been so fruitful and fantastic. We particularly found the 1-2-1 speed meetings useful. We covered a lot of ground in a short time. We’ve met some great new contacts, and I’d definitely come again!”

Holly Steele, Senior Vice President EMEA and UK Marketing, BlueVoyant

“Great to be back at a Pulse event! We love this event, Talk to the Board. It’s just so good to be able to network and interact with people and to have relaxed conversations, especially timing-wise towards the end of the year. People have gone through pressures and challenges and the good things that have happened. We can all collaborate and talk to each other.”

James Alliband, Head of Marketing, Risk Ledger

“The key take-away of Talk to the Board is the calibre of the individuals who attend. I’ve done these events over many years and I’m incredibly impressed with the team. They pulled this off brilliantly! I’ve had conversations with people who have budget, make decisions and who want to know about cybersecurity technologies that Mastercard cyber intelligence has.”

EMEA Strategic Alliances Director, Mastercard

“Pulse has exceeded expectations again in terms of the event they put on Talk to the Board. The content and 1-2-1 meetings are the important factor for us, and on the social side where we get to socialise with CISOs!”

Matt Middleton-Leal, Managing Director, EMEA, Qualys

“We aren’t just doing this Pulse event but we did their New York event at the beginning of the year and we are also signed up to the CISO 360 in Singapore later this year. For me this has been a great opportunity to introduce our CEO, Stephen Cavey, to Pulse and to meet the CISO communities. We’ve come away with some great follow-up opportunities – a really super event!”

Head of Global Marketing, Ground Labs

“With normal events that we attend, it’s fleeting and you only get moments with your colleagues. You don’t really have an opportunity to spend quality time or have the bandwidth to go deep into topics and subject areas. CISO 360 does this in a very unique way.”

Torquil Macleod, Director, Via Resource

“First and foremost, you know what you’re going to get with Pulse, the quality of delegate is always high. The agenda is very relevant. Finally, it’s great to be back face to face to build relationships. A thoroughly successful event for us!”

Dan Panesar, Director UK and Ireland, Securonix

“Excellent value for me and my organisation. Being able to engage senior level execs in the cybersecurity space on a 1-1 basis is invaluable. The evening activities were entertaining and really helped build trust and relationships.”

Director, SailPoint

Venue

Chelsea Football Club
Stamford Bridge, Fulham Road
London SW6 1HS

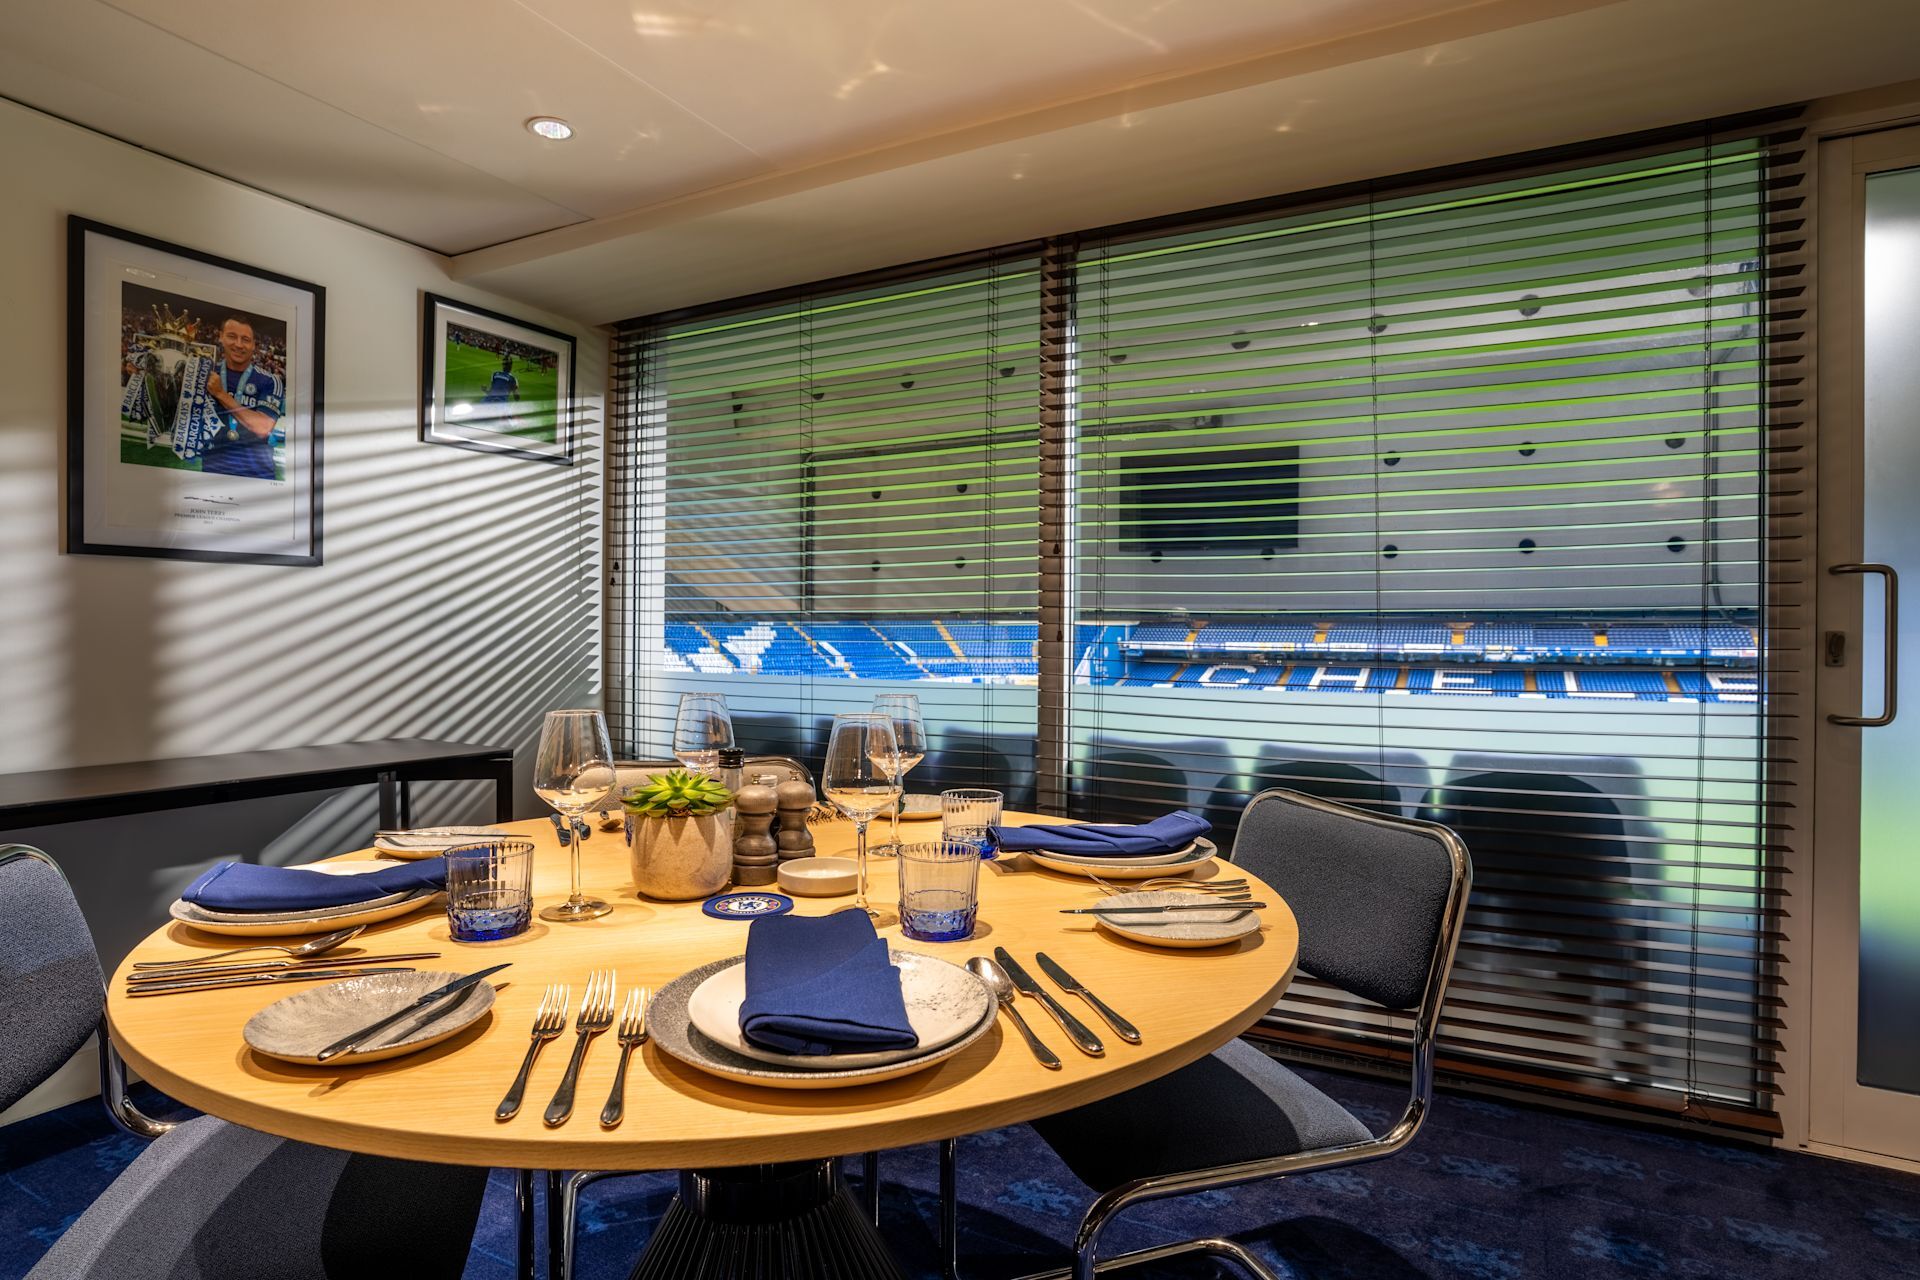
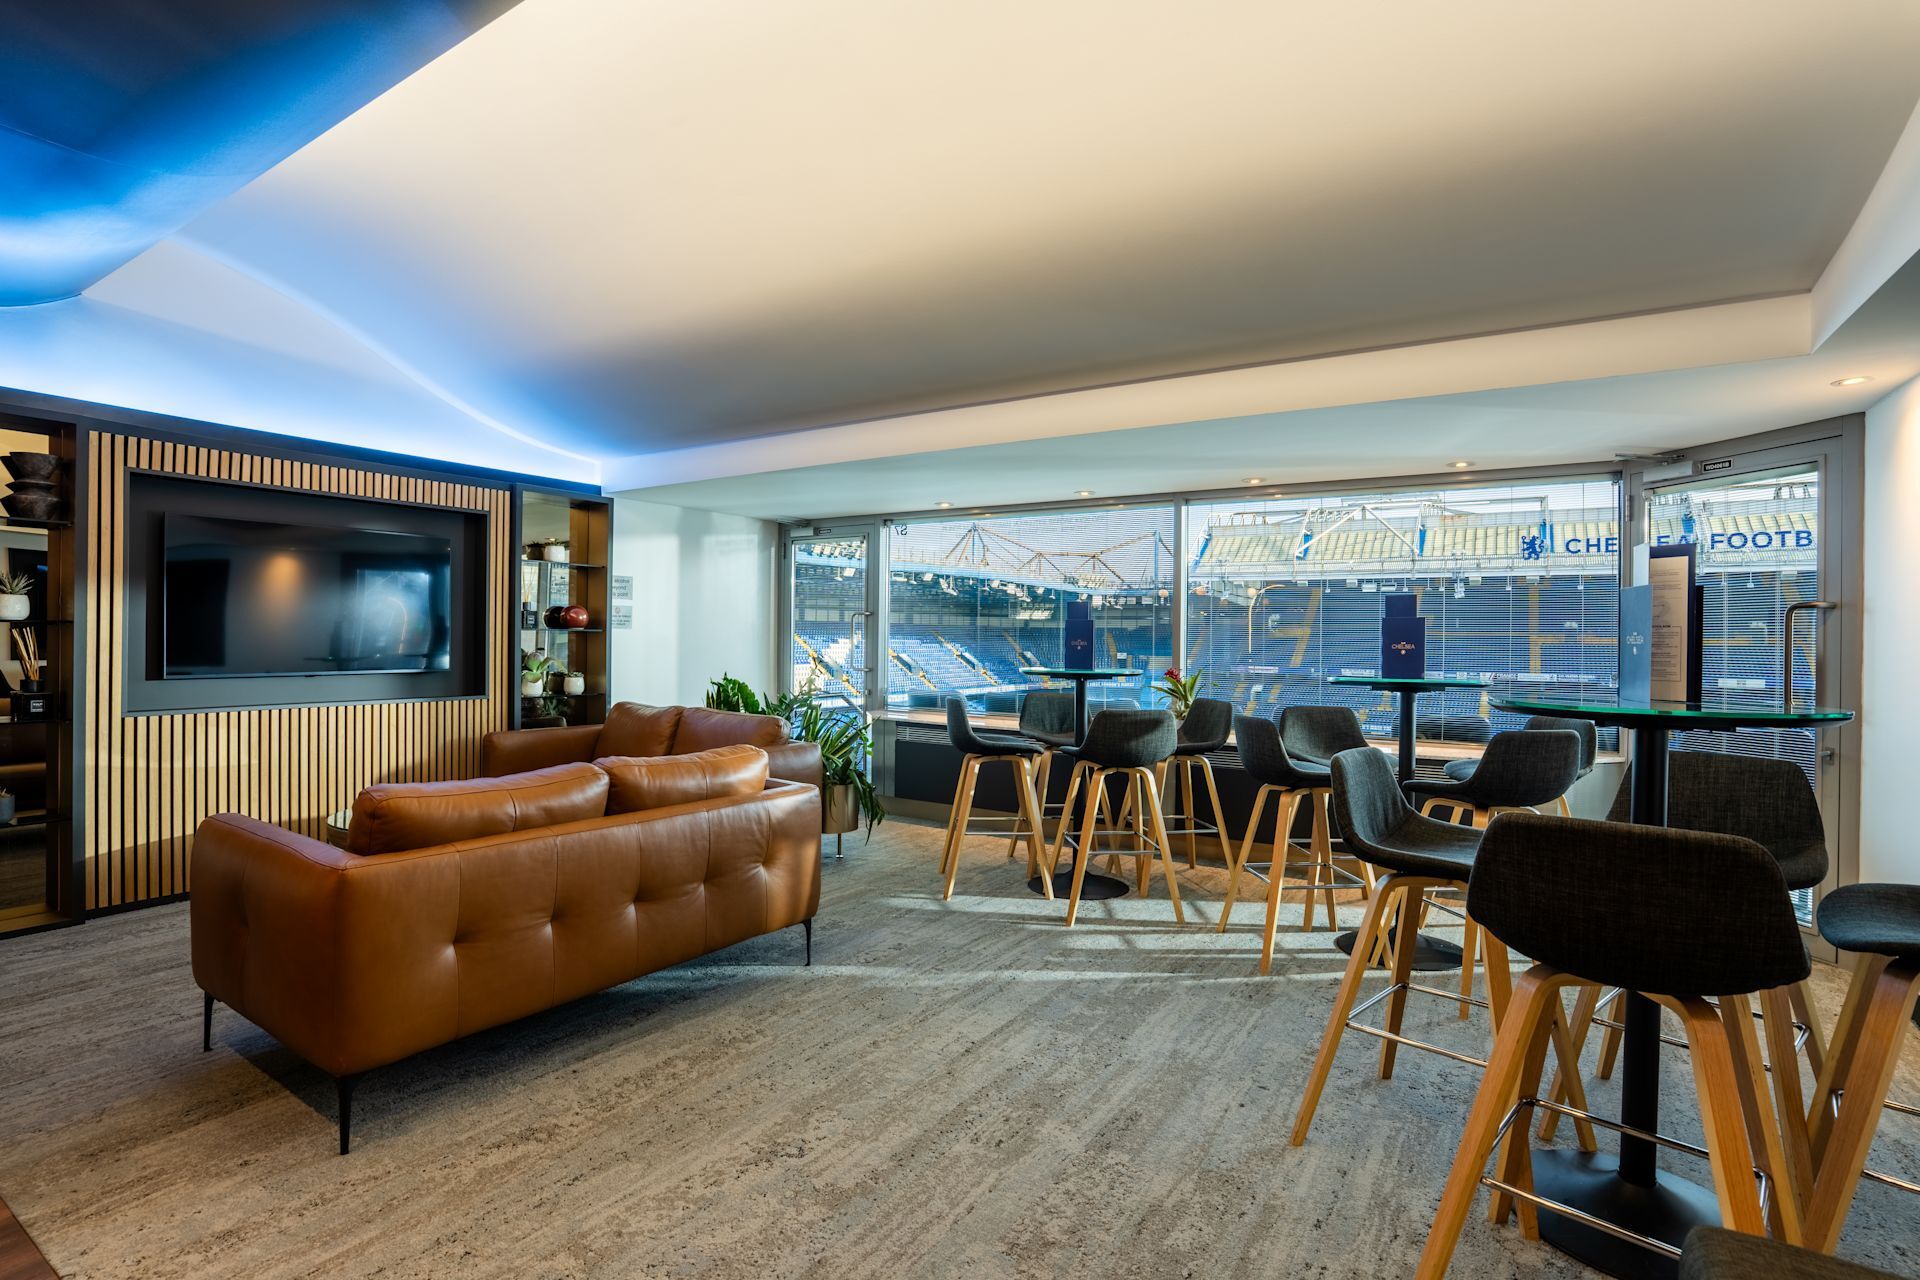
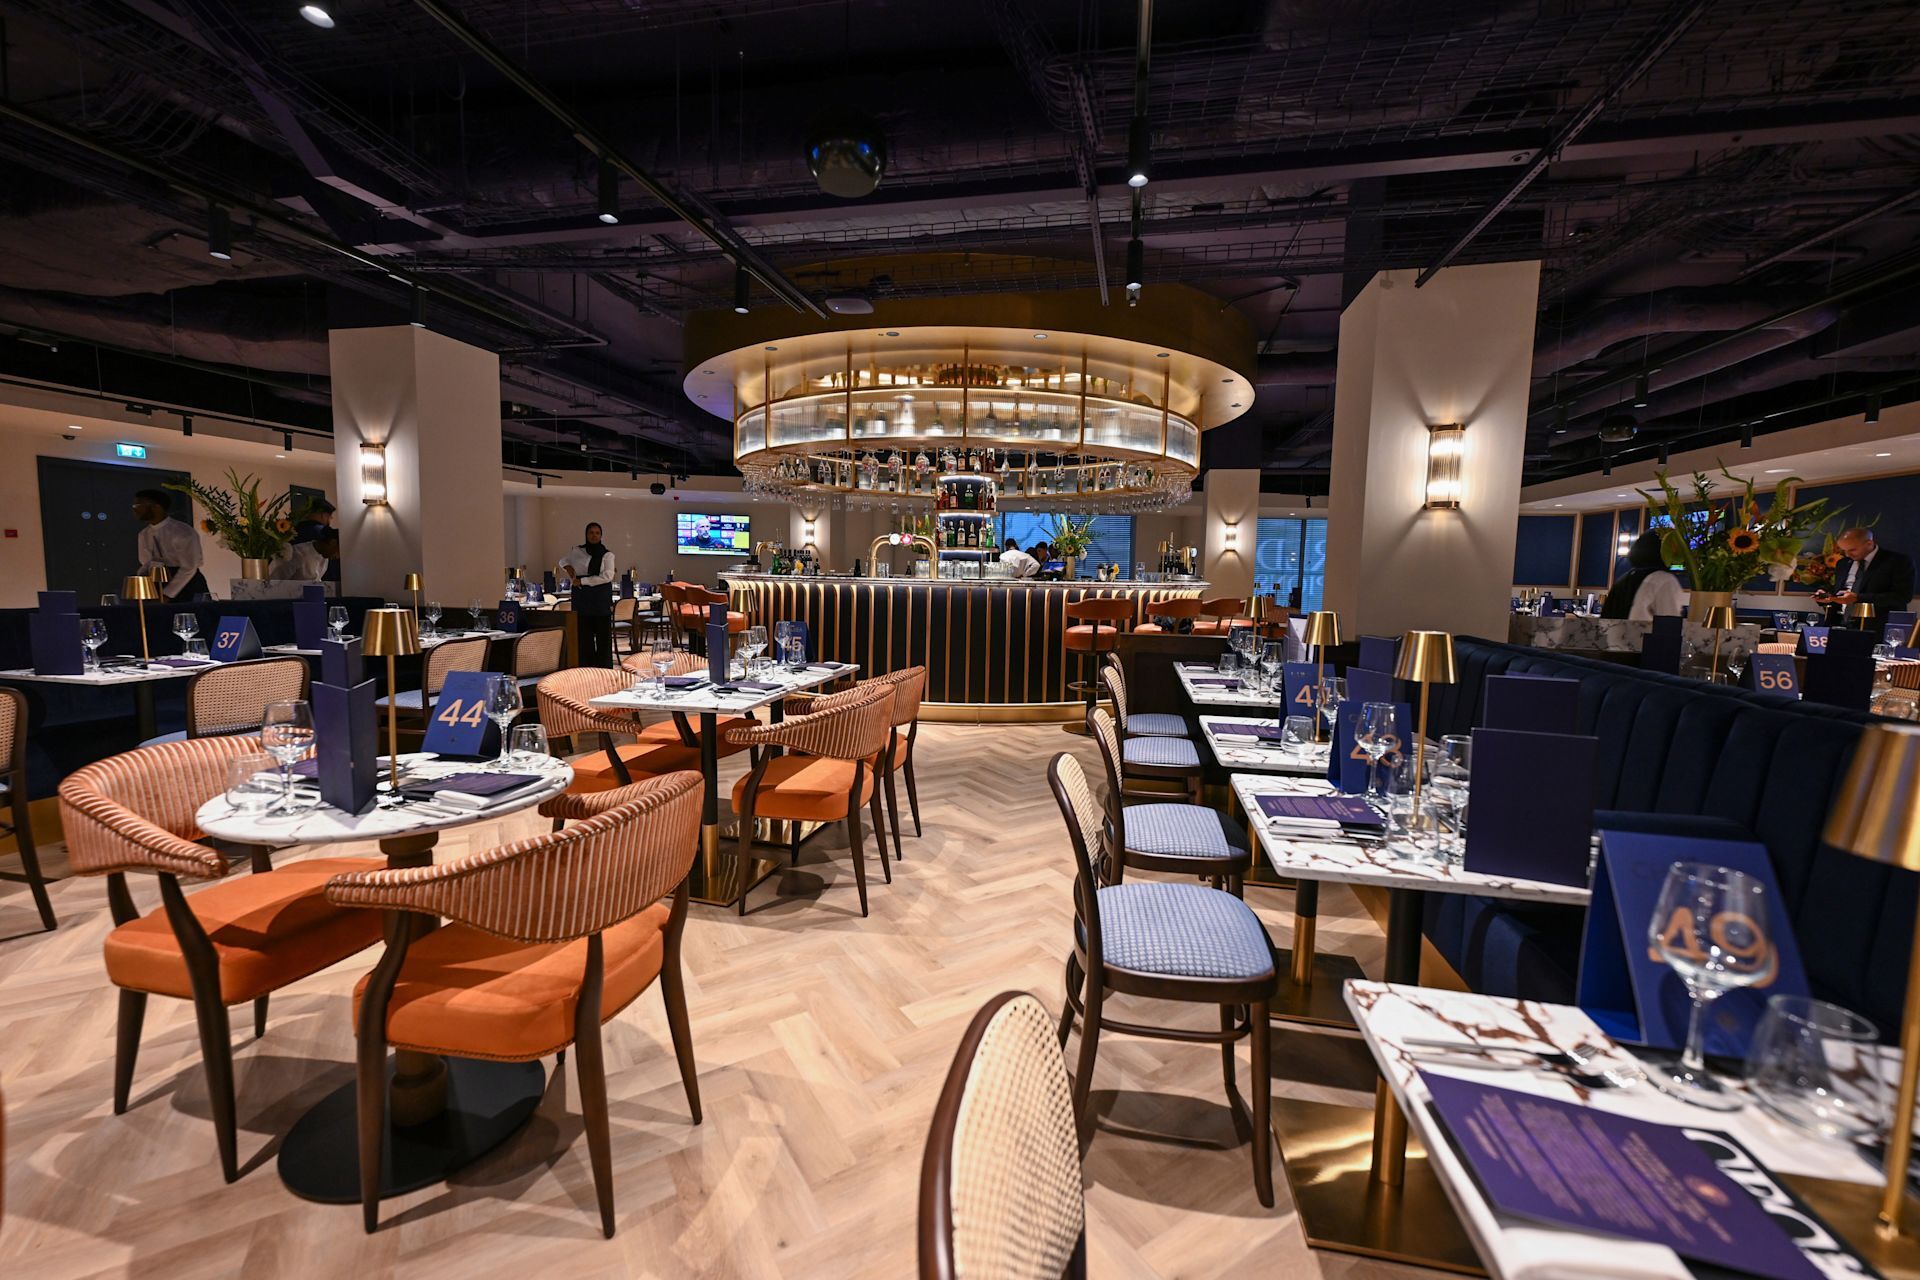
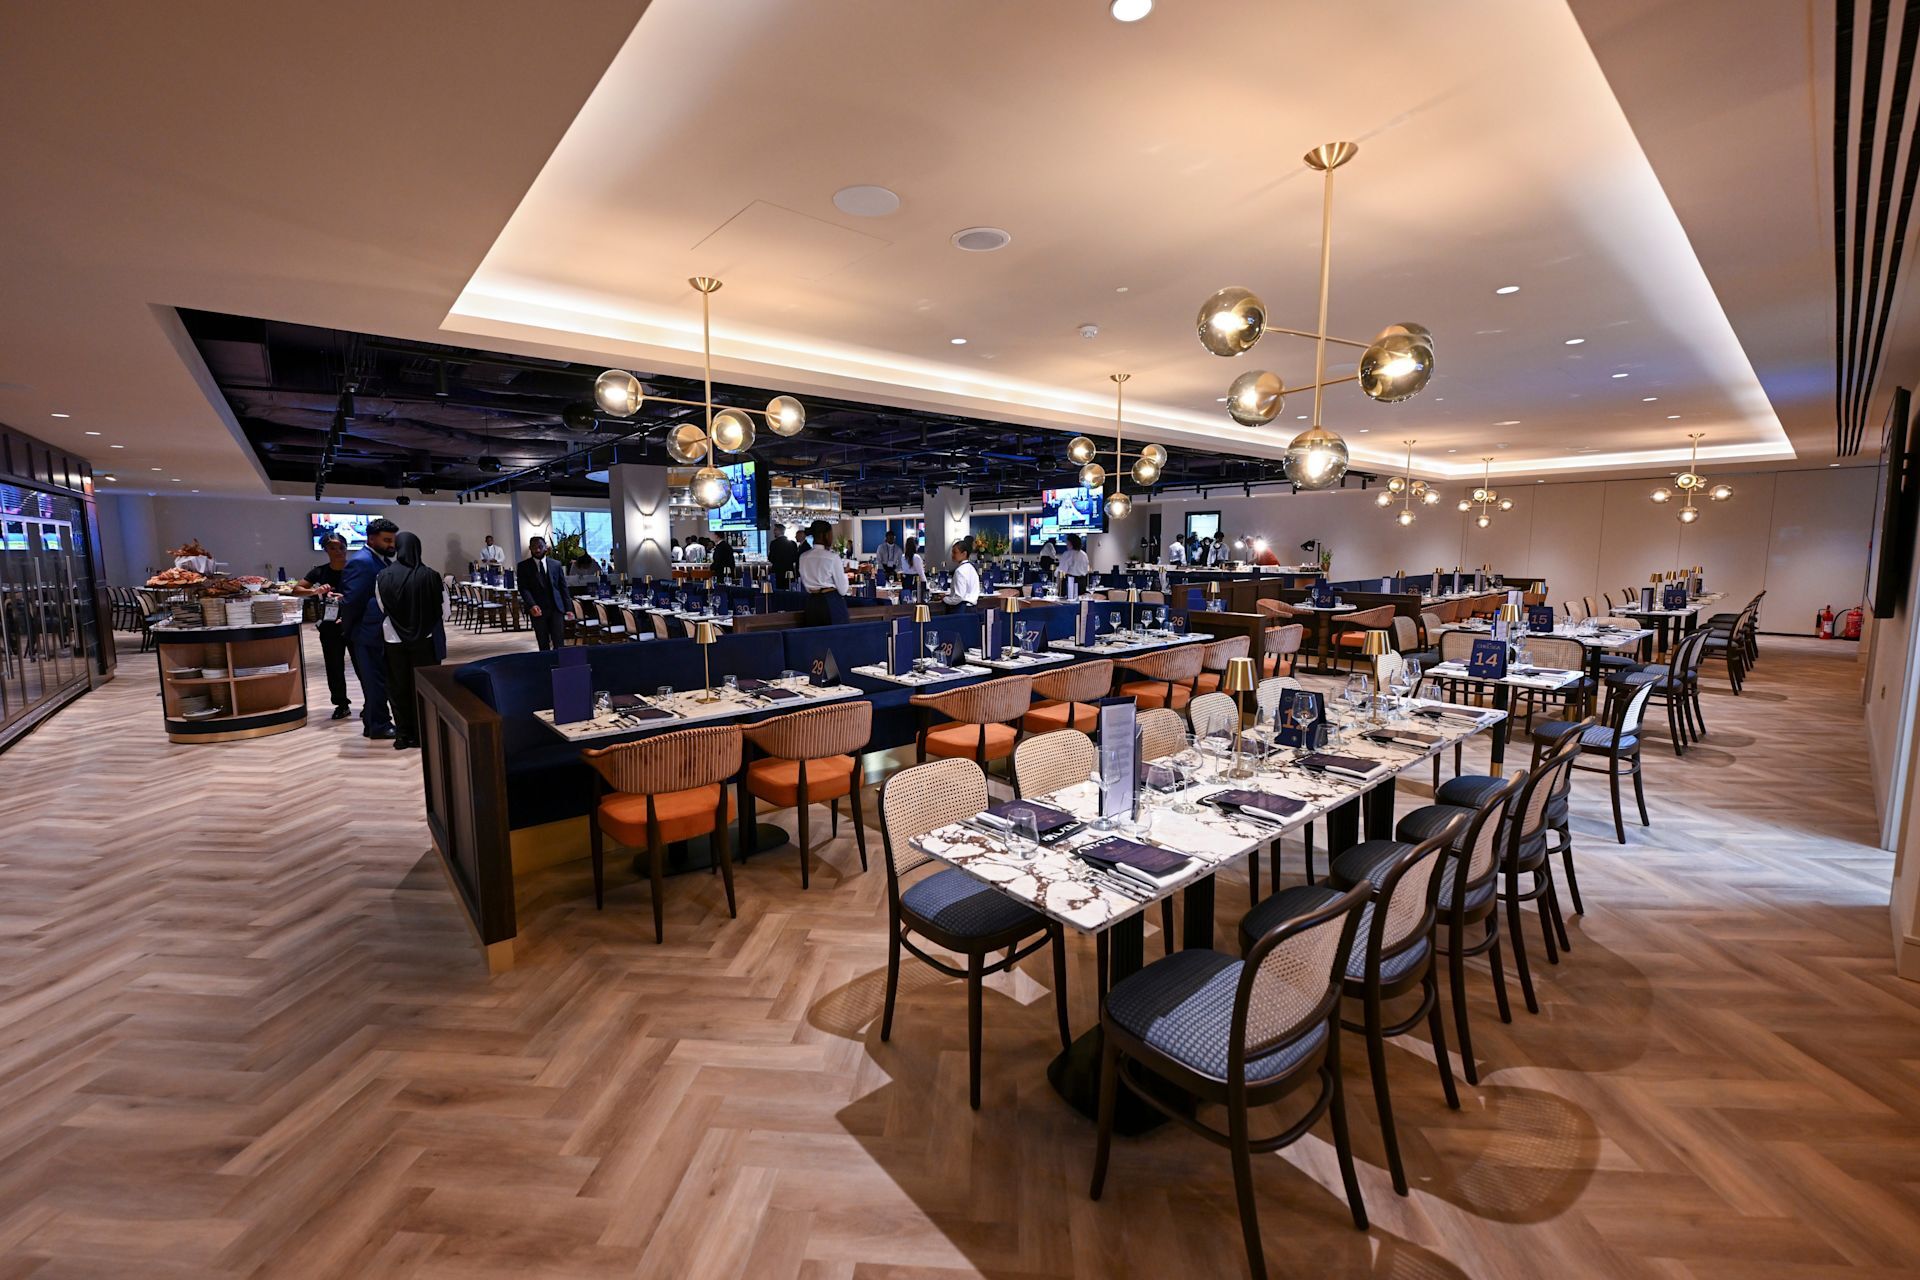
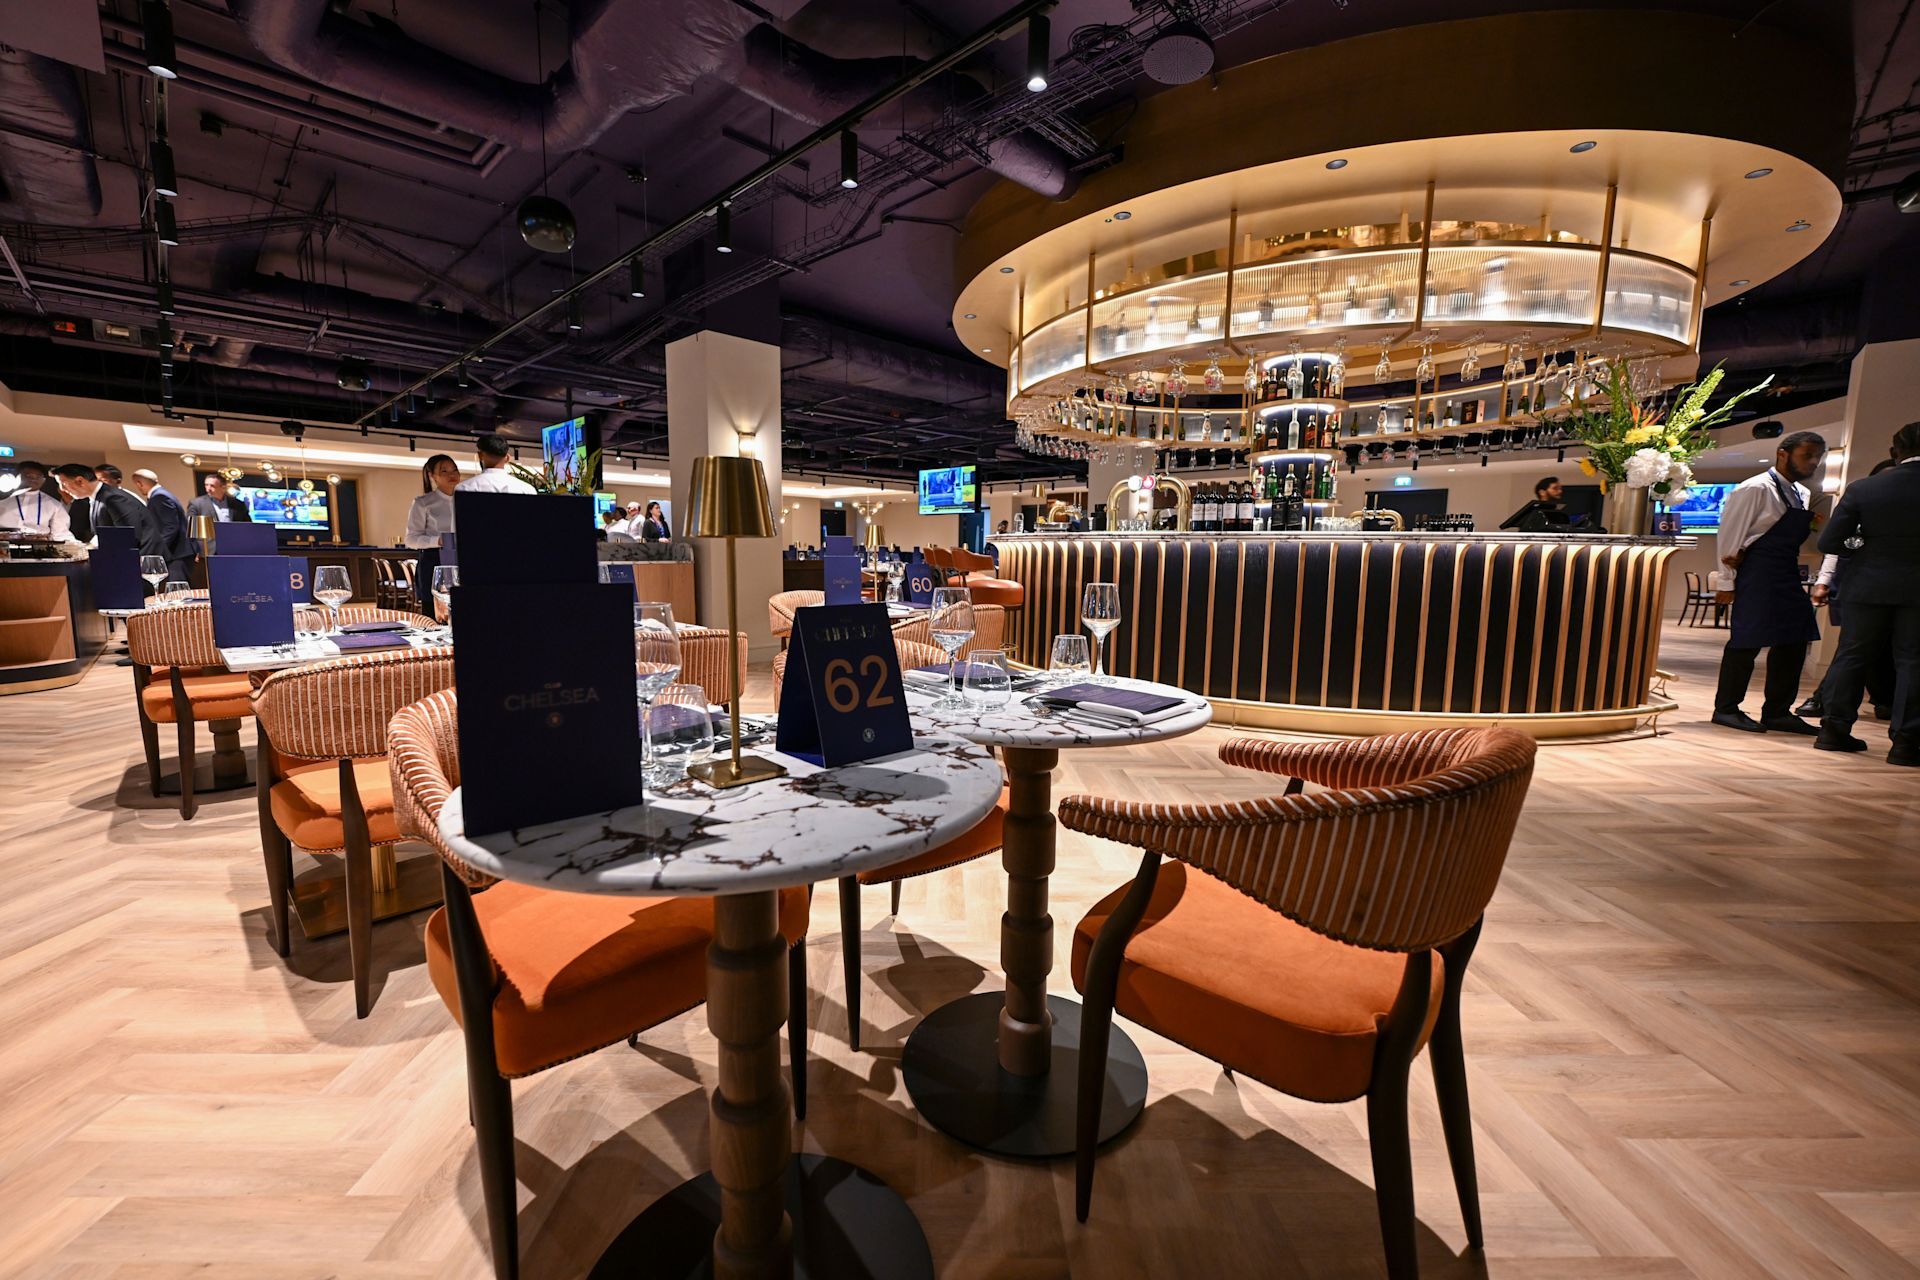
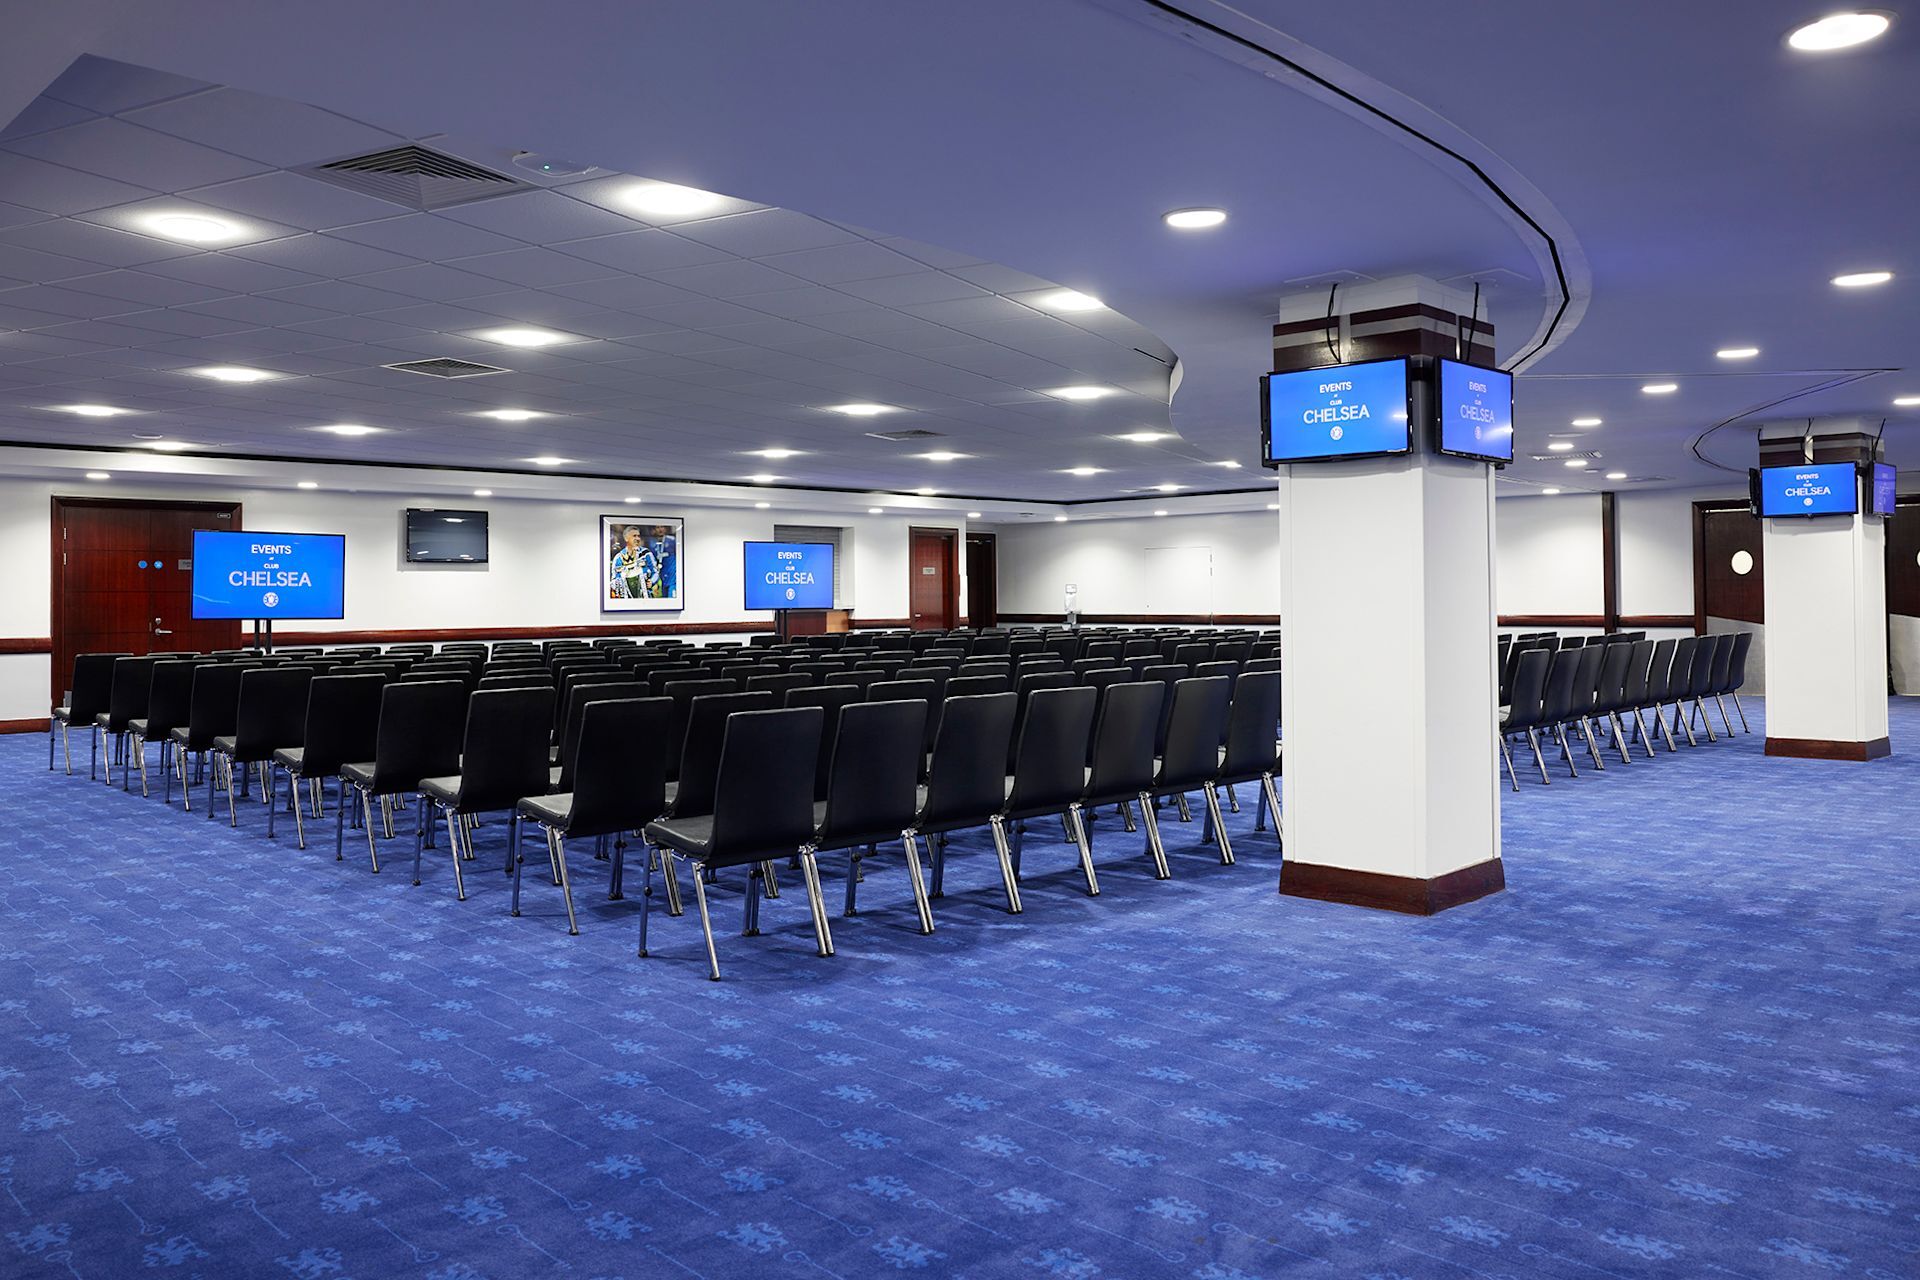
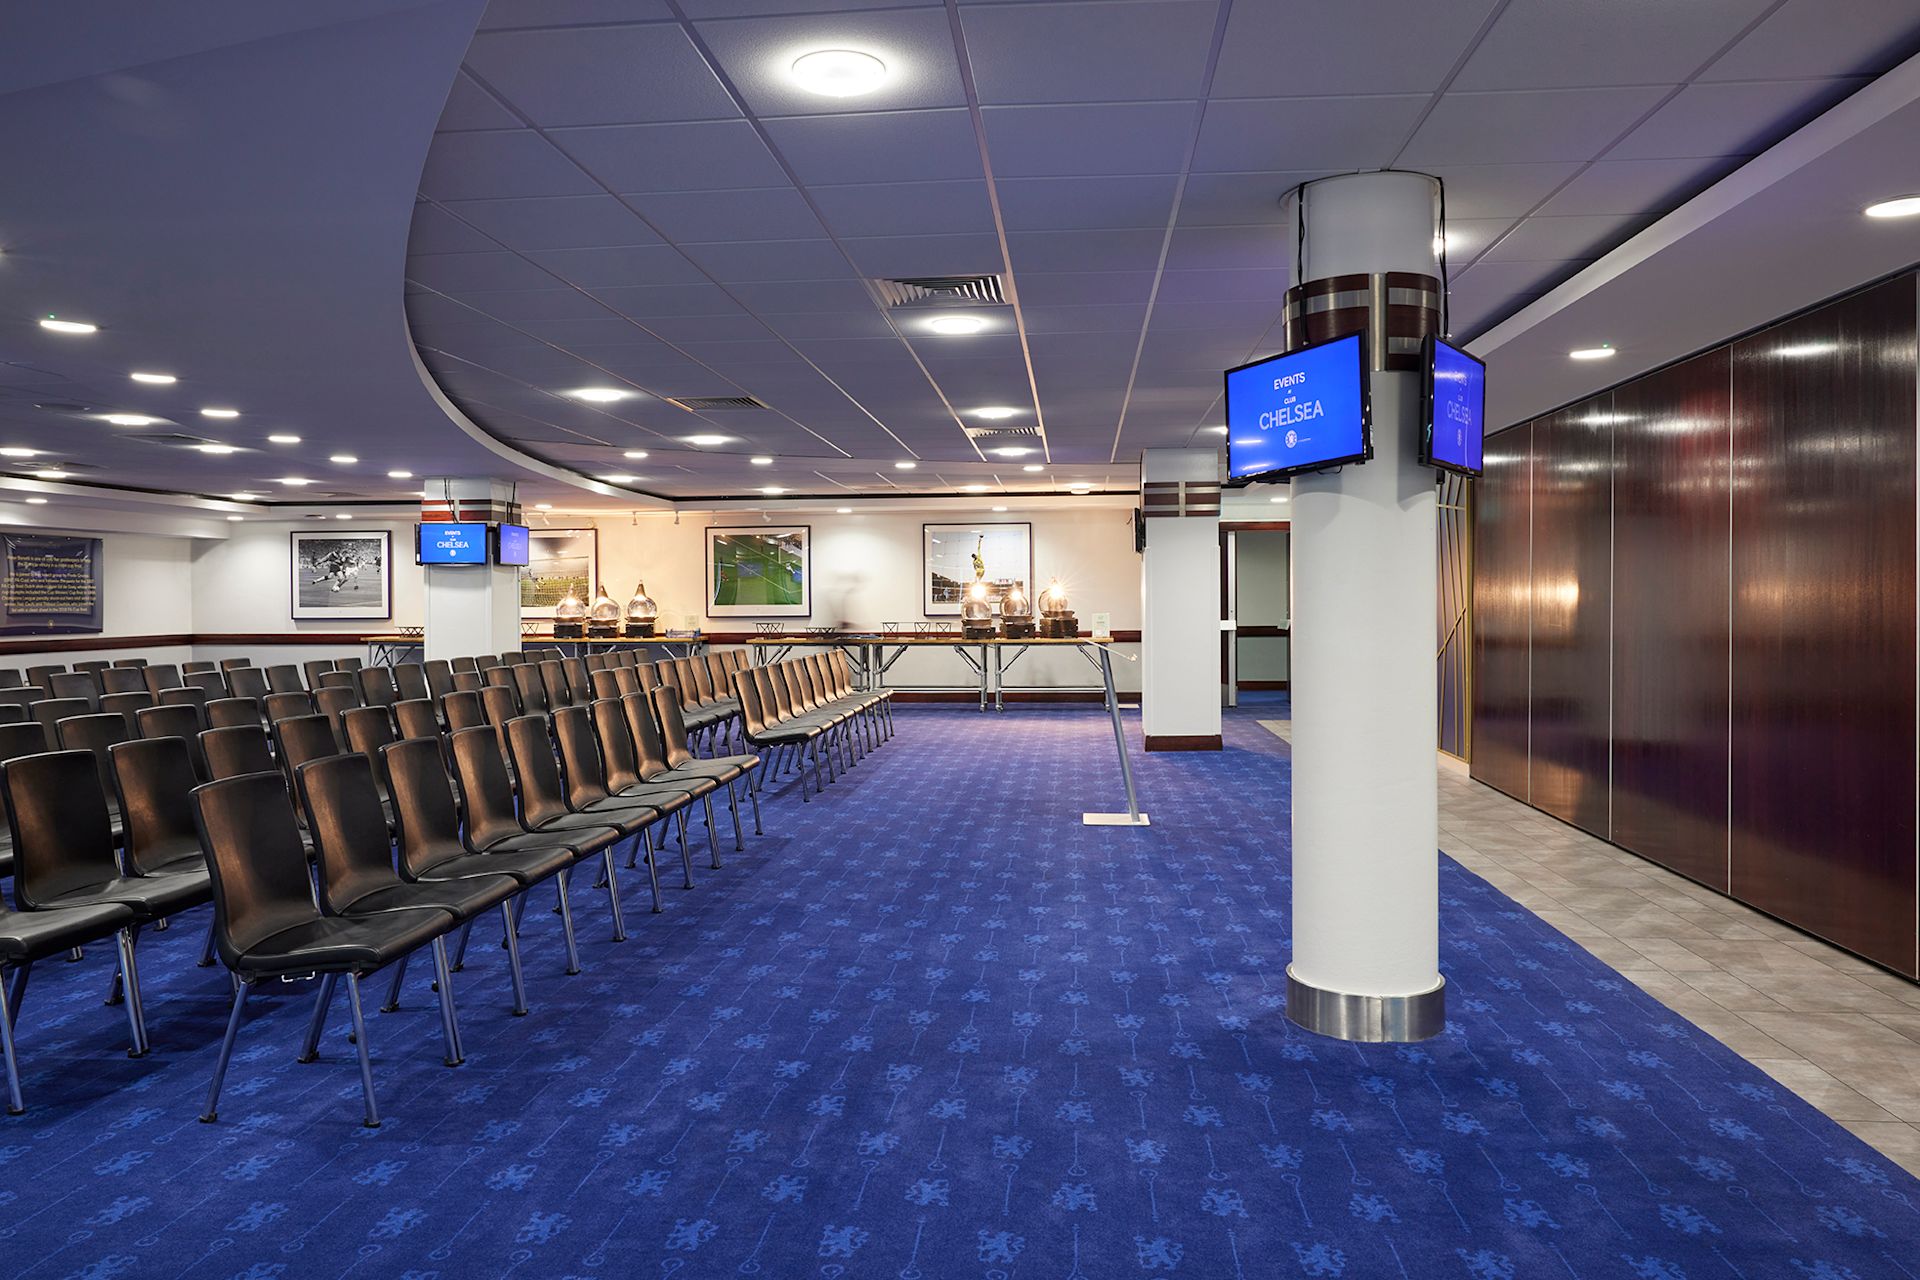
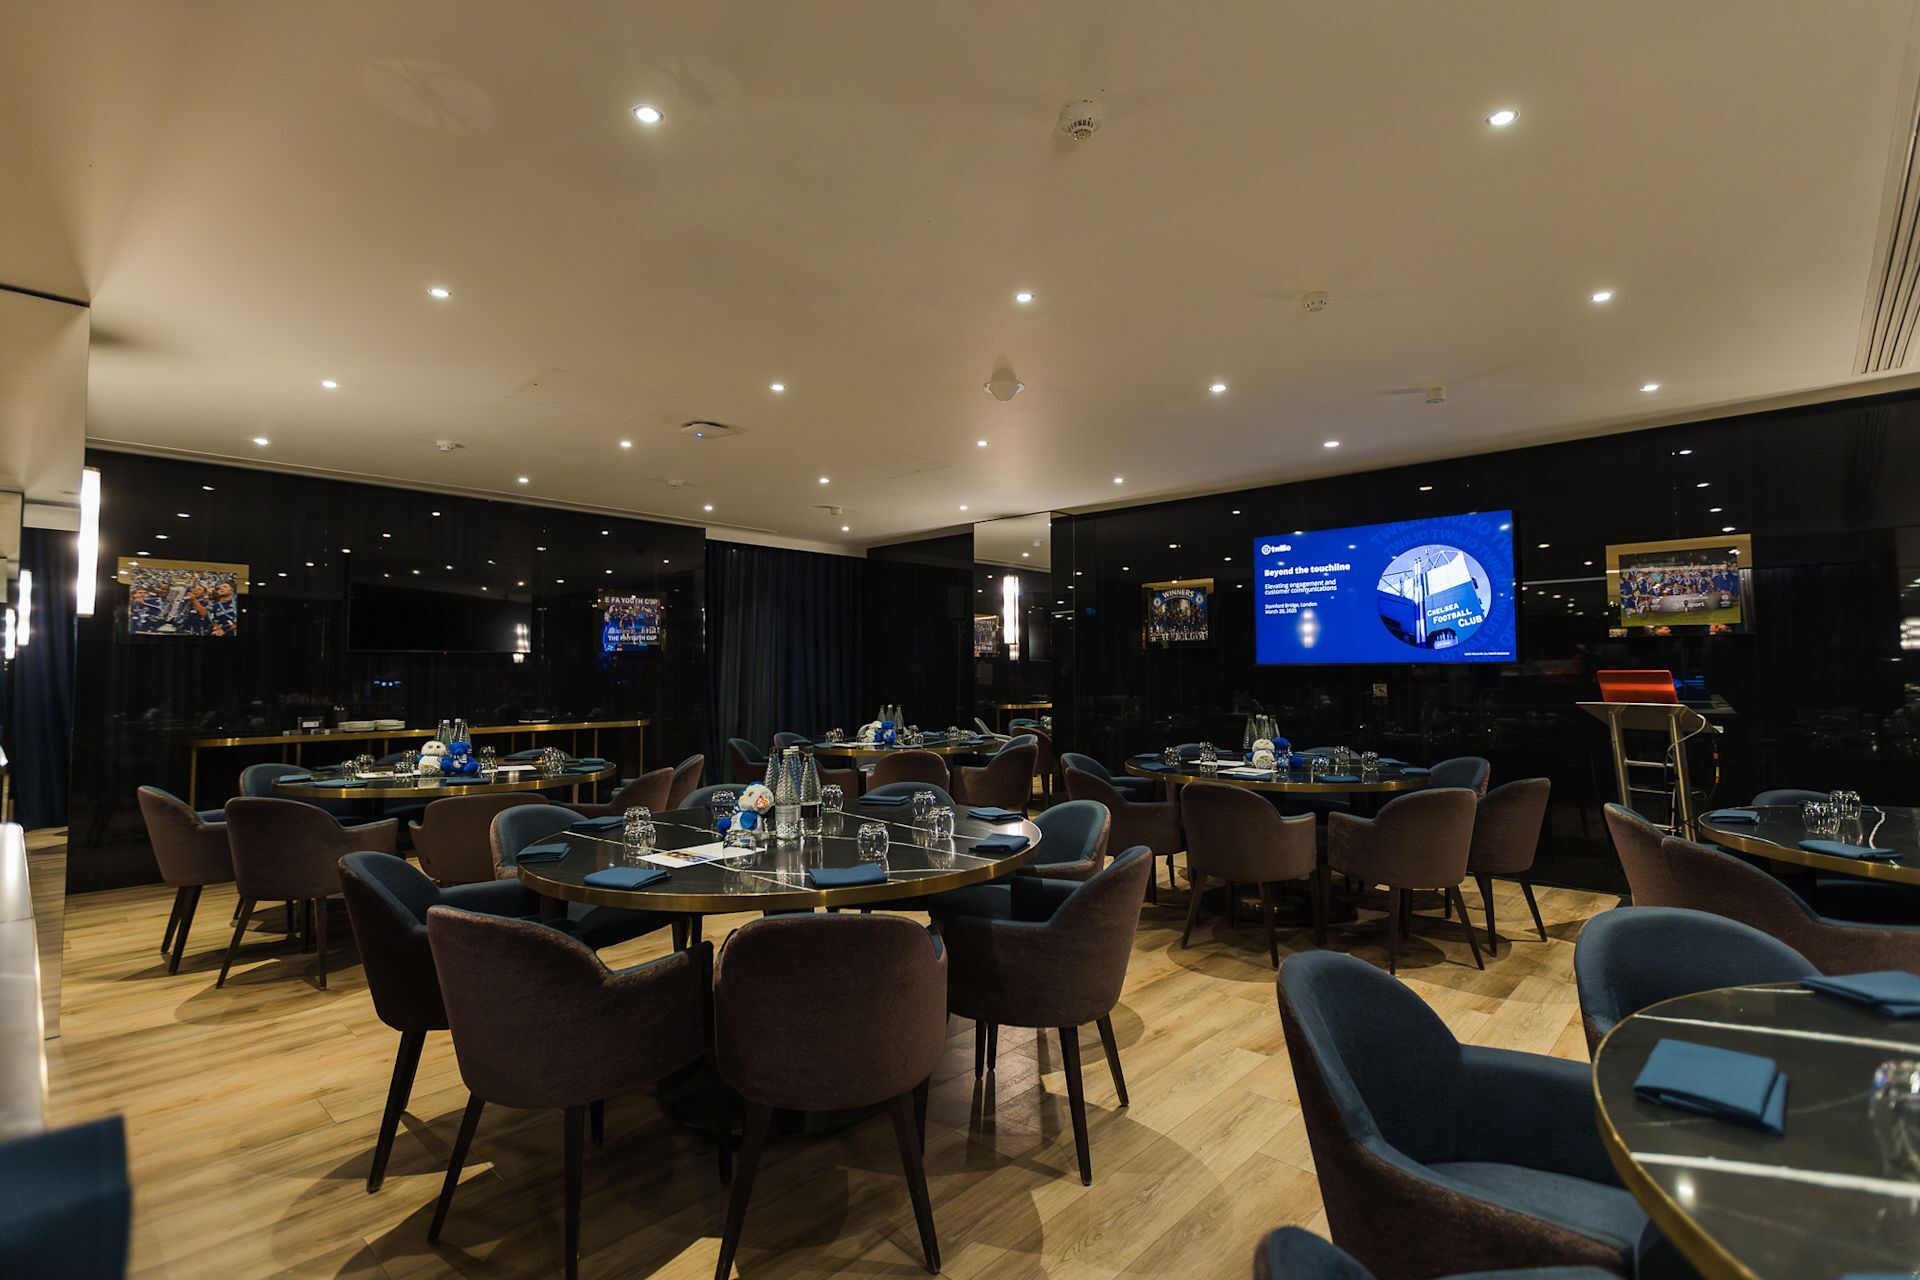
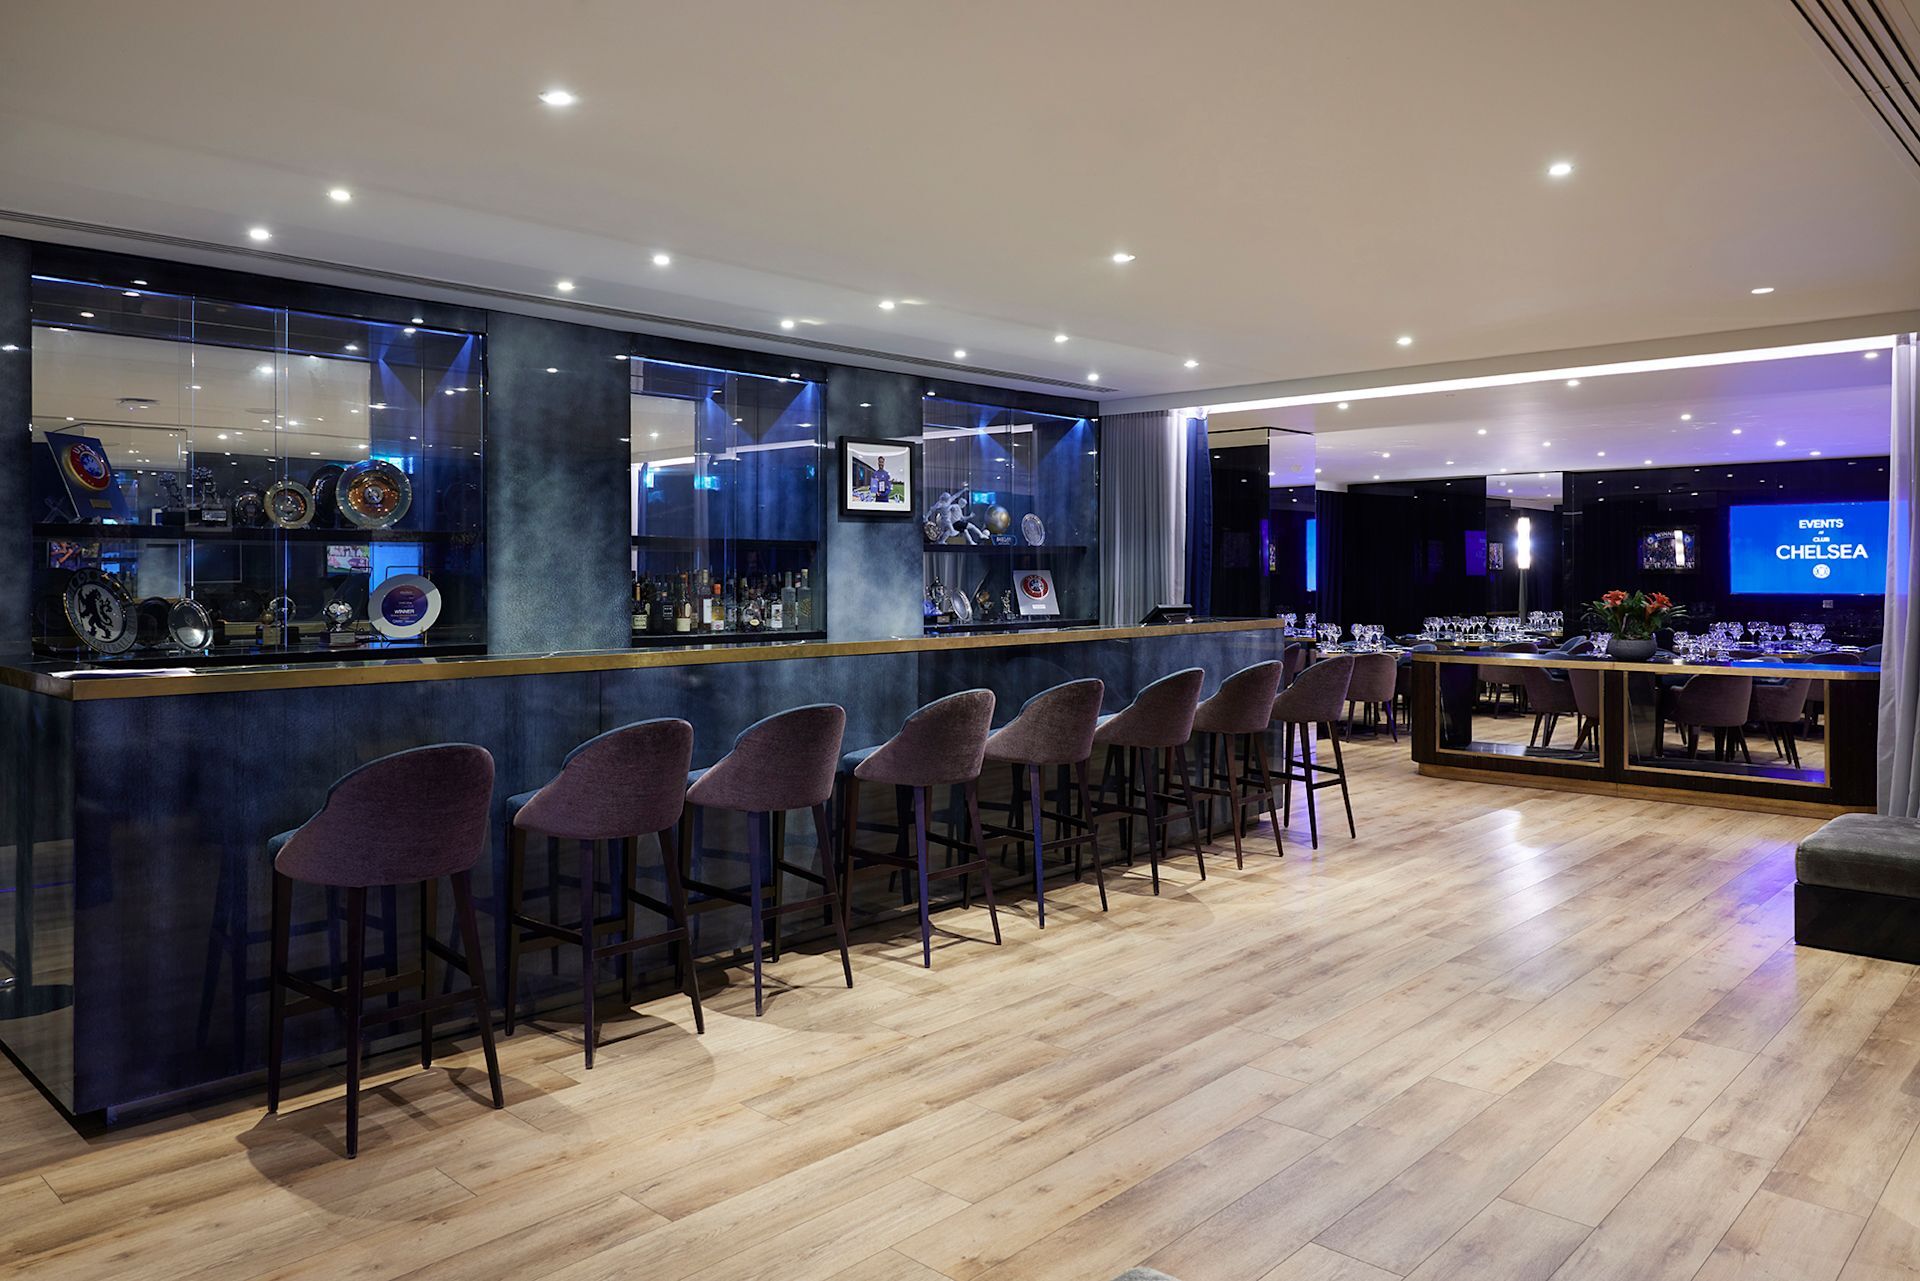
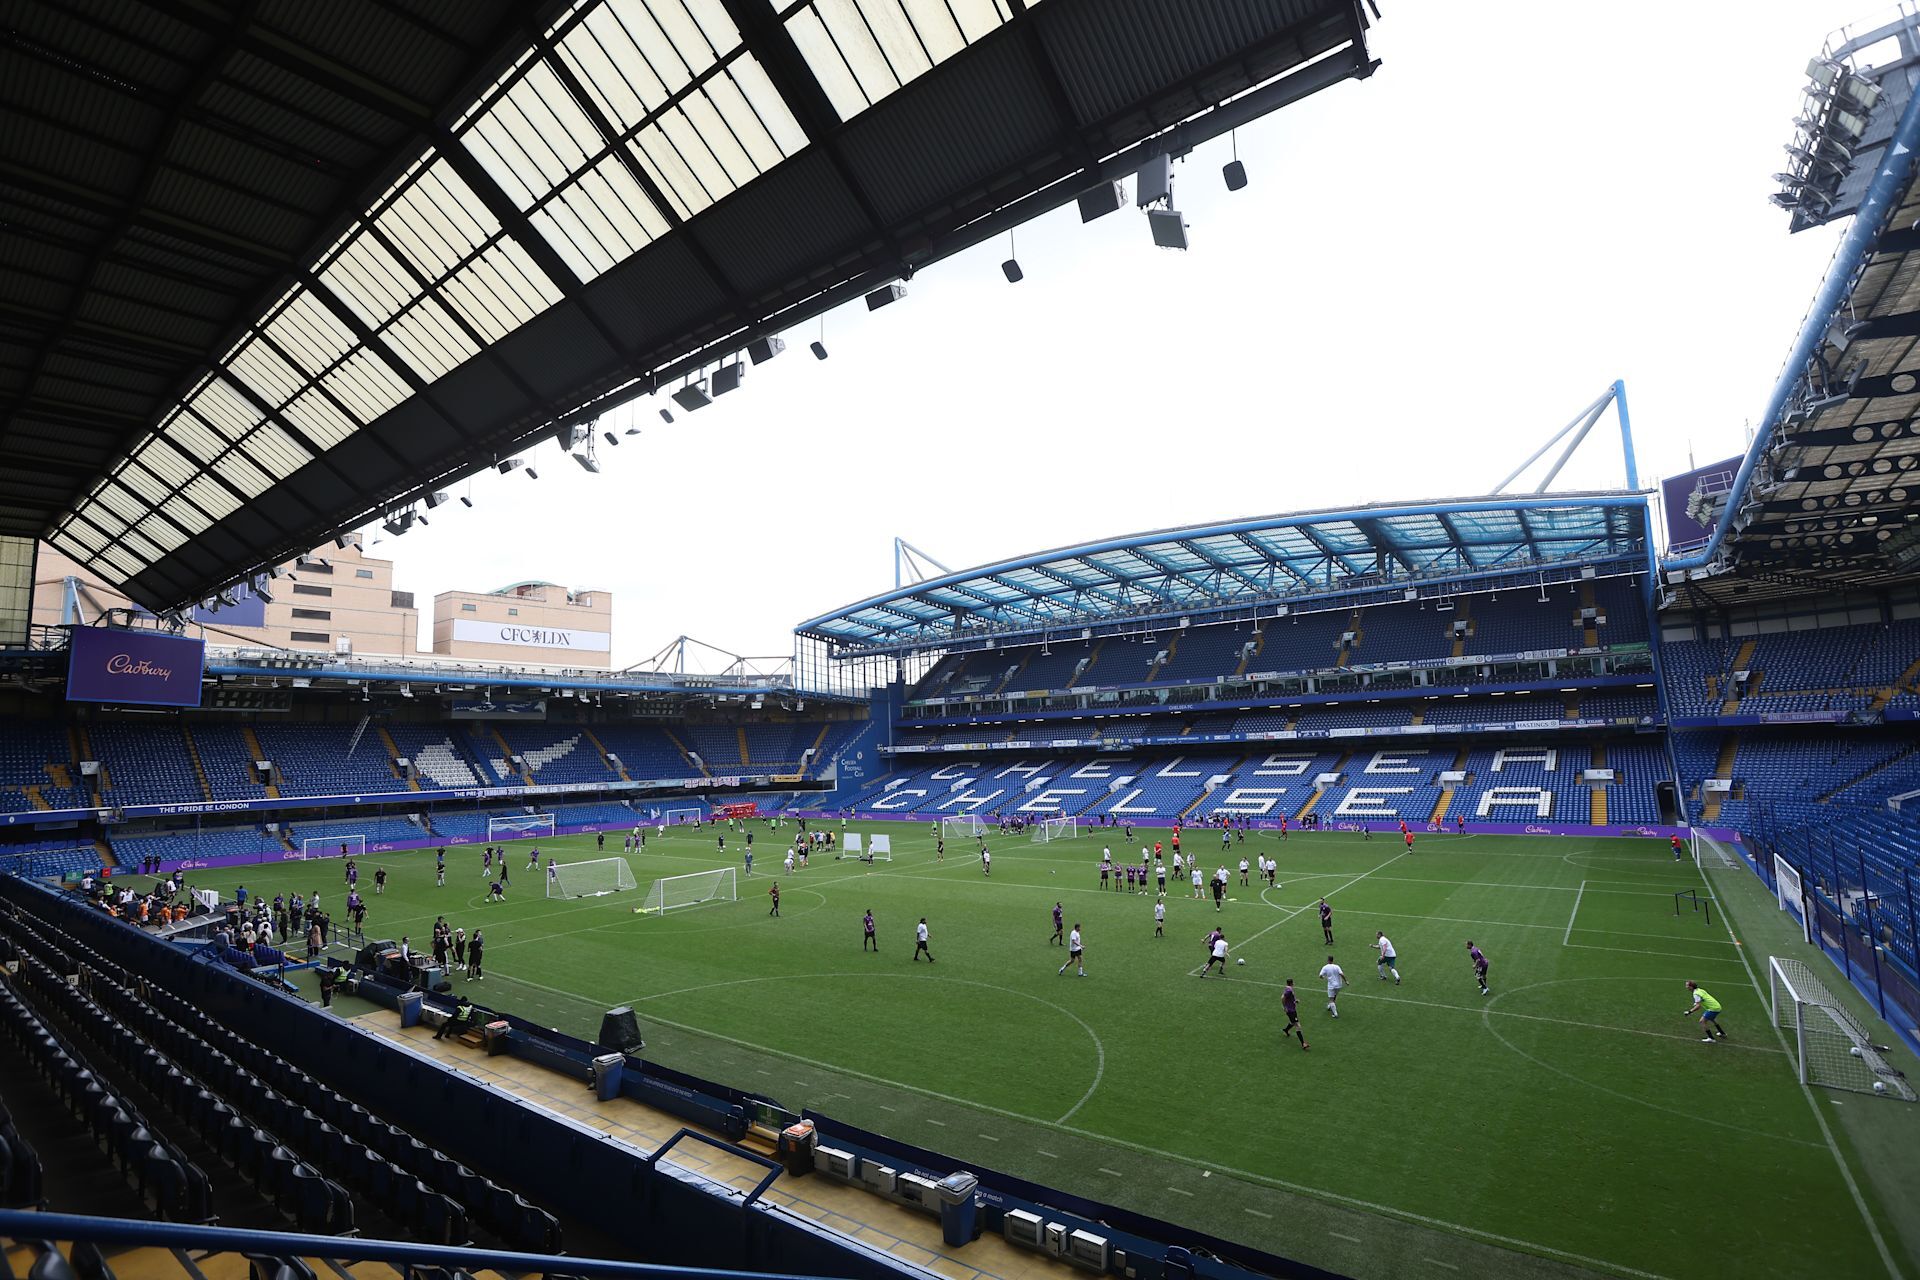
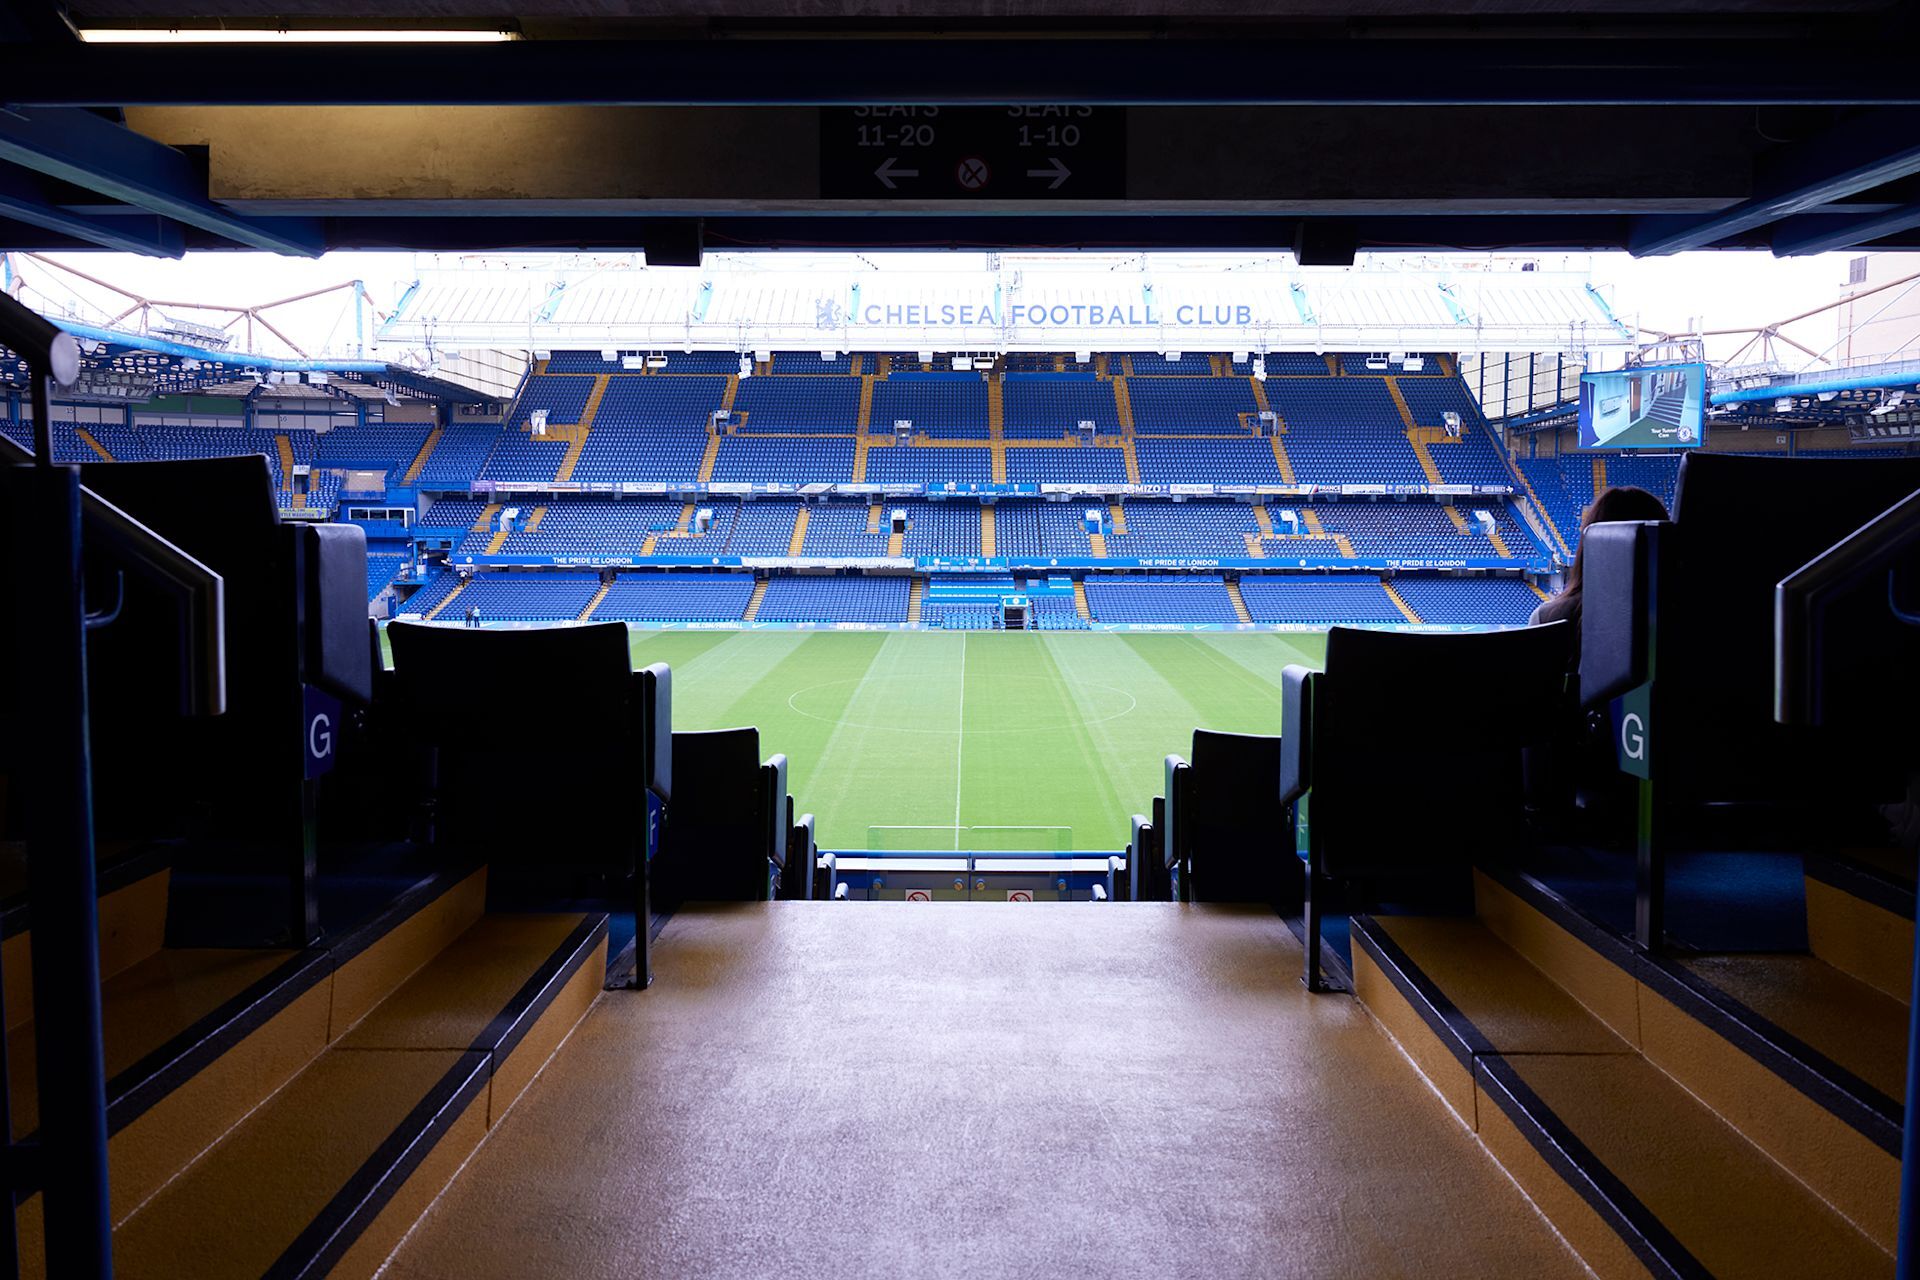
The 8th Talk to the Board took place across the Drake Suite, Harris Suite and the Directors’ Lounge at Stamford Bridge, with outside access to the directors’ terrace and its views of the stadium.

Stamford Bridge

The pitch at Stamford Bridge

View from the Directors’ Terrace

Stamford Bridge stadium

Hospitality overlooking the pitch

Lounge with views of the stands

The event spaces

Harris Suite

Harris Suite

Harris Suite

Drake Suite

Drake Suite

Directors’ Lounge

Directors’ Lounge

Directors’ Lounge

Video testimonials

Interviews filmed at previous editions of Talk to the Board.

What delegates and Board Directors say

“Talk to the Board, for me, is absolutely spot on! Coming here and engaging with the board to validate what resonates with them is very special and powerful. We have silos of silos in companies. But criminals don’t have silos. They don’t have borders or boundaries. So, to win the fight, we must come together and build coalitions of capability and bridge across the boundaries we live in. Board members and IT people speak different languages. We must learn to communicate effectively to help make rational decisions within a context that matters. This event, this forum, is exactly what I’m looking for.”

Michael Beaupre, Head of Cyber Security, Hays

“It’s so rare to have that opportunity to hear it directly from the CISOs and the board. So what more could you ask for if you’re up and reporting to boards and you need to communicate with them effectively? For anyone thinking of coming to a Pulse Conferences event, just do it. Block out that time, make the commitment and realise that it’s an investment not only in your company and what your company needs from you but also in your professional development.”

Katherine Leivesley, Head of Legal, Offer and Sourcing, Kingfisher PLC

“The great thing about Pulse is that you get different perspectives outside of our core market. Talk to the Board is interesting because the business dimension is the most important thing about cybersecurity. Speaking to the board brings me that business dimension to cybersecurity.”

Dr Paul Kennedy, Chief Engineer – Cyber and CEMA, QinetiQ

“I wanted to be part of Talk to the Board because I’ve always been so fascinated by technology, particularly cyber attacks and the cyber risk. I’ve learnt about how lonely and vulnerable the CISO/CSO feels. As boards, we need to think about how we can be more of a support for the CISOs so that they don’t feel so under threat. If your world is looking at cyber risk and you’re a CISO or security leader, I would come to this event and get involved because you are sharing and gaining simultaneously.”

Dame Inga Beale, Former CEO, Lloyd’s of London

“Having a plan prioritising, getting the basics right, not trying to do everything or running off in different directions demands some follow through, both by boards and CISOs. Great to have board and CISO side of the equation together. It shows the maturity of the board-CISO relationship that we’re having much better conversations about this now than we were 10 years ago.”

Robert Hannigan, Former Director, GCHQ

“It was a really interesting panel, Talk to the Board, and great to meet people from across the cybersecurity profession, to hear their concerns and to help them to understand all the different issues that Boards need to deal with and where cybersecurity may rank on their list of priorities.”

Lorraine Heggessey, Former Controller, BBC One

“A rich discussion with very interesting themes emerging for myself. Both the audience and panel found the event very interesting and informative.”

Jeremy Schwartz, Former CEO, The Body Shop, Pandora and Conival plc; Chairman, Sustainability and Inclusion Practice, Kantar

“It’s great to hear from board executives and have CISOs sit alongside them, asking questions. It’s a sort of reversal of the status quo.”

Jonathan Luff, Co-Founder, CyLon Ventures

“Talk to the Board provides a wonderful opportunity for CISOs to hear first-hand how and where they might tailor their Board interaction more strategically to achieve greater impact at this level. More intriguing, perhaps, was that CISOs were urged to also see risks as potential opportunities that, with careful due diligence, might be thoughtfully exploited.”

Graham Joscelyne, Former Auditor General, World Bank; Chair, Audit and Ethics Committee, The Global Fund to Fight AIDS, Tuberculosis and Malaria

“… how to build trust with Board members, what priorities a Board cares most about and how to sustain the conversation as a rolling programme. Such diverse Board representation from Audit, Tech, Sustainability, Risk, Marketing, People and Change meant the participants could fully engage in debate across a range of challenging topics.”

Deborah Exell, Former Board Member, Head of Human Capital and Business Transformation, Getronics